❌

Normal view

“I Don’t Need a SIEM, I Have Ollama!” (Yes, You Do!)

5 November 2026 at 23:27

Warning: this blog is an experiment. The idea for a blog came from a real conversation I had with somebody. The content is researched, debated, refined, “hardened” by a Gemini skill I created (using Gemini 4 Argon). Then Claude Opus 5.5 performed a peer review, and tore some parts to shreds. Then rewrote them. And then I very lightly edited it, and tuned a few jokes. I replaced a food fight joke with a pillow fight joke, specifically. Let me know if this sucks, and I will stop. Promise!

—

A security peer recently shared a proposal they had just heard in the wild: instead of paying for a SIEM, why not load several days of raw log data into a locally run open-weights model, ask it “what looks risky?”, and review whatever the model highlights?

No SIEM ingest tax! No cloud token bills! No SIEM license fees! No writing correlation rules! No tuning anomaly detection! Just a gaming GPU under a desk and pure, artisanal AI-native vibes. Ahhh, magic!

Gemini illustration

Wait. Really?

My first instinct, forged by 24 years of staring at logs since I first met a SIM in January 2002, was to laugh, pour a drink, and move on. Surely everyone knows this is a terrible idea, right? Right?!

Wrong.

If an engineer, an IT director, or a cost-cutting CFO pitches “local LLM as a poor man’s SIEM” in your organization, you cannot just roll your eyes and mutter “hallucinations.” People keep inventing this idea for real reasons. SIEM ingest pricing still hurts: some vendor cost explainer works out 5 TB per day at $2 to $4 per GB as $3.6 to $7.3 million a year on ingestion alone. Detection engineering is still hard work. And yes the AI hype machine has spent two years promising executives that models can “reason over any unstructured data.”

So let’s dissect why dumping a week of raw logs into a local model breaks four basic laws of “operational physics”, and then carve out the narrow 10% where a local model does help with logs. The short version fits on a sticker: the LLM writes the parser, it never runs as the parser. And the twist is that the problem here is “raw,” not “local.”

Token Arithmetic and Naive Chunking (Or: How Big Do You Think 7 Days of Logs Is?!)

Let’s start with grade-school arithmetic, because clearly nobody pitching this architecture has ever opened a calculator…

Forget the enterprise. Take a tiny environment, a single server rack generating a measly 1 GB of raw text logs per day. Seven days of logs is 7 GB of text, or roughly 1.75 billion tokens at 4 characters per token. That is generous, since IP addresses, GUIDs and hex strings tokenize worse than English (Wow, really? Yes, really — at least Claude thinks so! He would know, right?)

Now look at that “free” 8B or 70B parameter model on your GPU workstation. Its usable context window, before the KV cache devours your VRAM and the fans sound like a Boeing 747 on takeoff, is maybe 32K to 128K tokens. You are shoving 1.75 billion tokens through a 128K keyhole, which is about 13,700 full context windows. Painful enough yet?

Well, it gets worse. Assume your box reads a generous 2,000 tokens per second (benchmark your own, I’ll wait). Reading those 1.75 billion tokens takes about 10 days. You need 10 days to read 7 days of logs, so you never catch up! Scale that to the 5 TB per day example above and it is about 20 years of GPU time for each day of logs. Hilarity ensues! Replacing a deterministic stream processor with a token-by-token text predictor is like replacing your municipal water pipes with a guy carrying a silver espresso spoon from a well 10 miles away.

“Fine, Anton,” the DIY enthusiast says, “we’ll chunk the logs into 2,000-line batches and loop the local model over them all weekend!” Or we will get a bigger boat… eh… server rack to run the model.

Chunking naively, by just loading the data in batches, fails hilariously. Here is how:

  • Attack chains get cut. The phish on Tuesday lands in one batch, the lateral movement on Thursday lands thousands of batches later, and no prompt ever sees both. Each batch gets judged alone.
  • Merging the summaries does not bring the signal back. By the time you summarize the summaries, the one quiet line was already dropped in round one. So “naive+” fails as well.
  • Position inside the batch matters. Liu et al.’s “Lost in the Middle” found that models do best when the relevant information sits at the start or end of a long context and degrade sharply in the middle. They tested question answering and key-value retrieval, not logs, but picture a quiet privilege escalation on line 1,482 of your batch. Worst seat in the house.

Researchers keep running into this. Cai, Ryan and Karie note that iterative approach is limited by context capacity and that map-reduce style summarization is computationally heavy (and requires some luck). Even so, that is a proof of concept on up to 20,000 rows per dataset, and they say enterprise volumes remain to be validated.

So smarter chunking exists (reminder: it is not magic, in this area nothing truly is): parse, cluster, then retrieve by entity and time. At that point you are building the first half of a SIEM. Congratulations!

As I wrote in The Ancient Art of SIEM, cost pain is eternal and only the currency changes. In 2003 you ran out of hardware, in 2015 you ran out of cloud budget, and in 2026 you run out of tokens and VRAM.

The Input-Centric Time Machine: Back to 2002 Batch Review

Notice the most revealing phrase in this idea: “load 1 to 7 days of log data… and then review what the model highlights.”

That is not real-time detection. That is batch-mode log archeology! When intruders can go from initial access to data theft in hours (soon: minutes for some incidents), reviewing a week of logs in a batch means you are running a weekly book club about how you got breached last Wednesday. But hey … is your SIEM faster? Well, it should be!

Worse, asking an LLM to “highlight what looks risky” violates the most important lesson of two decades of detection engineering. In Output-driven SIEM, 13 years later, I revisited my favorite 2011 mental model: think about what you want to see at the output before you collect, and AI does not change this. Asking a model to “find risk” in raw logs with zero detection engineering is the ultimate input-centric anti-pattern. It failed with ML in mid-2010s, and LLM is not different (in this regard).

Now, about determinism. The lazy objection is “the answers change on every run,” and a sharp engineer will reply “so pin the seed.” Fair enough! Run-to-run randomness is an engineering problem: Thinking Machines got 80 unique completions out of 1,000 at temperature 0, then 1,000 identical ones after fixing their kernels. But is it actually bad? Maybe if you run 5 times, you will find 2x more “fun” things. But hey … also probably at least 5x more noise.

The harder test is stability. Take the same 48 hours of domain controller logs, shuffle the order or change one irrelevant line, and run it again. Given what we learned, I would bet real money the verdict moves. Well-crafted SIEM rule does not care what order the lines arrive in.

Zero Local Context Equals Hallucinated Risk

Why can’t a local model tell an active nation-state intrusion from Tuesday’s messy IT administration? Because raw logs do not contain your organizational reality! Shocking, eh?

A raw syslog or CloudTrail line says that svc_deploy_04 logged into prod-db-02 at 3:14 AM from an internal jump host and ran an encoded PowerShell script. Is that a five-alarm breach or the legacy billing batch job that Bob in accounting wrote in 2017 and nobody dares to touch? This is a dated example, on purpose. Insert your own fun example involving a shadow AI agent!

In Part 3 of the Stop Building a 2003 SOC series, I argued that the #1 reason AI fails in the SOC is the absence of Context as Code: machine-readable, owned, and expiring knowledge of your assets, business processes, and weird administrative exceptions. In Part 2, we warned about automation bias: humans reviewing plausible, well-written machine verdicts approve them.

Also, the test from Can AI Let You Jump SOC Maturity Levels? applies here: does this exist because someone had to spend time, or because someone had to learn something about us? Writing a parser is a time cost. Knowing about Bob’s job is a learning cost, and no model downloaded from the internet has paid it.

Feed raw logs into a naked local LLM with no CMDB enrichment, no threat intel, no identity graph, and no 90-day baseline, and its only source of “context” is its pre-trained weights. So it flags every scary-looking word (ERROR, DENIED, admin, root, failed) and writes you a convincing fictional thriller about your own network.

The Confused Deputy Trap: When the Attacker Prompts Your “SIEM” via User-Agent

Now put on an attacker hat for 30 seconds. What is a log file?

A log file is untrusted, attacker-influenced input. Every public-facing web server, SSH daemon, API gateway, and email relay faithfully records whatever string an outsider sends in an HTTP User-Agent, a failed username field, or a JSON payload.

Log processors have been attacked through logged strings before (hi, Log4Shell!), but that was a bug you could patch. In a raw-log-to-LLM setup there is no parser boundary to patch, because instructions and data share one channel. You just handed the attacker write access to your detection engine’s prompt!

Summaries are also scary, BTW. Pandey and Bhujang found that the classic “ignore all instructions” override failed completely against the one model they tested, but context manipulation reached 96% success on summarization with no defenses and 38% even with constrained output.

In How to Solve the Mystery of AI Defense in Depth (and my October 2026 collaboration with Usman Chaudhary, The Model Has Preferences, but the Harness Got Controls), I emphasized that a model’s statistical preferences are never a security boundary, and only a deterministic harness is. Feed unparsed logs straight into a local LLM with no harness, and any kid with curl can blind your review or flood your team with fabricated critical alerts…

The Problem Is “Raw,” Not “Local”

Let’s be fair to the local crowd, because they have a point.

  • Local solves a real problem. Logs are full of secrets, PII and internal hostnames. Not shipping them to a third-party API is a legitimate reason to want a model on your own hardware. It also — theoretically — eliminates an endless stream of unpredictable token costs flowing to a frontier model provider.
  • Small models are not the villain. In the same paper, a structured design called Aida (separate agents for investigating, challenging and judging, working through a SIEM) used open-weight Qwen3.5 9B and it was workable for the task they had.
  • “What about an agent querying a log store?” Now we are talking! The model forms a question, a database searches 7 days of logs deterministically, and the model reads a small result. That is a very different architecture, and it needs parsed data, a query engine, detections to start from, retention and access control. Sound familiar?

So keep your local model if you want it. What is missing from this proposal is the SIEM…

The Raw-Logs-to-Local-LLM Delusion Matrix

For explaining this to an enthusiastic colleague (or a budget-slashing executive) without starting a pillow fight:

Wait, Is a Local LLM Good for Anything in Log Land? (The 10% Where It Shines!)

I am a constructive cynic, not a Luddite (At least Gemini 4 Argon thinks so!). As I noted in the SOC maturity post, AI can jump the artifacts, and parsers are on that list (with caveats for tricky log sources). So point your local model at logs as an engineering sidecar, not an ingestion engine:

  • Writing the parser, not being the parser. Instead of feeding 50 million lines from a weird legacy mainframe into an LLM, feed 20 sample lines and ask for a regex, OCSF mapping, or pipeline rule. The LLM writes the code once, and deterministic CPU code parses the 50 million lines at wire speed. This mostly works, I swear.
  • Post-trigger micro-slice investigation. Once a rule or EDR alert fires on a specific host and 15-minute window, pull 200 pre-filtered, enriched log lines and ask the model for a timeline. Those lines still contain attacker strings, so treat the summary as untrusted and let the model request actions only from a closed list.
  • Ad-hoc query translation. Translate an analyst’s question into KQL, SPL, or SQL, so the database searches 7 days of logs deterministically. This also mostly works, but some YMMV.

The Lean Team Reality

What if you are the CISO of a regional insurer or hospital with a small security team, a hybrid stack, strict state regulators, and an MDR provider? When an engineer or cost-conscious VP suggests “let’s dump our noisy firewall logs into a local Ollama box,” they aren’t trying to sabotage your SOC. They have a log source that is too expensive to send to the SIEM, and they want a free way to “keep an eye on it.” Here is how to solve that without a science project:

  • Don’t use a GPU box as a poor man’s data lake. Route a noisy source to cheap, searchable object storage, or strip verbose fields in a pipeline before ingest. This is my old two-tier answer (a SIEM plus a broad, cheap log store), and it has aged well.
  • Hold your MDR to the same standard. When they brag at the next QBR about “AI-powered log analysis,” ask whether deterministic detections run first or whether it is an LLM wrapper over unparsed telemetry. This point alone is worth the price of reading this blog (A.C. — this is me, not AI)
  • Channel the DIY energy. Give your smart engineer 50 anonymized lines from your gnarliest legacy application and ask for three high-signal filter rules you can deploy in your real pipeline.

Action Items for Security Leaders

Is there anything you need to actually do?

  • Run a napkin token audit on any AI log proposal (Monday morning). Before the demo starts, ask: “How many GB per day is the raw source, how fast does the model read, and what deterministic step selects the tiny slice that reaches a context window?” If the answer is “we’ll just load it in batches,” kill the project on the spot. It’s this “just” word.
  • Fix ingest pain with tiering (30-day play). If this idea surfaced because a log source is too expensive for your SIEM, solve that: drop repetitive keepalive chatter, route compliance-only logs to cheap storage, and keep output-driven security data in your detection tier.
  • Make “the LLM writes the parser, never runs as the parser” a standard (architecture play) — that is, if you write parsers at all. Allow LLMs at design time (parsers, mappings, queries from small samples) and at post-alert time (small, bounded, enriched slices), but not as the runtime ingestion or anomaly engine over raw logs. Put it in your MDR requirements too… otherwise they will keep whining that it takes 7 weeks to integrate a log source forever.
  • Test your existing AI log workflows for prompt injection (60-day play). If your SOC or MDR summarizes anything containing attacker-controlled strings, test it in your next purple-team exercise. Do not stop at a naive “ignore instructions” canary, because passing that proves little. Try persona and context-rewriting payloads, plus payloads split across lines.

So, Do You Need a SIEM?

Call it a SIEM or call it a pile of parsers, a query engine, detections and retention. You need those things, and a GPU under a desk does not replace them. By all means run a model next to them, I promise it will be fun!

The part that worries me most is how this fails. A detection rule that misses can be tested, tuned, and re-run. A model that misses hands you a nice summary, and nobody knows what was not in it. As I said in September, skipped maturity used to fail loudly, and now it fails quietly.

We had 23 years of progress, and the best practice is still “have a plan and don’t ingest garbage.” That goes for your context window too.

[A.C. — note to self: this is v6 skill]


“I Don’t Need a SIEM, I Have Ollama!” (Yes, You Do!) was originally published in Anton on Security on Medium, where people are continuing the conversation by highlighting and responding to this story.
AIs Hacking the Law

3 November 2026 at 13:01

In both a 2021 essay and my 2022 book, A Hacker’s Mind, I talk about AIs finding vulnerabilities and exploits—hacking—the legal system.

Here’s some demonstrations of this from Germany:

Legal systems encode the foundations of social order in natural language. Similar to computer systems, the written law can contain vulnerabilities that invite exploitation.1 Courts absorb most exploits through interpretation, and such vulnerabilities rarely surface in the first place. With highly capable AI systems enabling the discovery of vulnerabilities at unprecedented scale, we believe the latter could change.

In testing this hypothesis, we have identified a substantial number of vulnerabilities in the German legal system using LLMs. To our knowledge, none of these have been previously recorded. We share a selection of vulnerabilities below, and present potential exploits for each. We share only those vulnerabilities whose exploitation we believe would not cause serious harm.

We believe that with cheap legal reasoning proliferating, AI systems could jeopardize the functioning of today’s legal systems. In such a world, lawmakers would need to significantly harden the process of legislation, for example by leveraging advanced AI themselves.

Still in its early stages, but definitely something that’s coming.

AI Vulnerability Finding

2 November 2026 at 13:02

A comment:

3% of ‘critical’ software security bugs, in all of recorded history, have been found in the last month. This is on pace to find another ~100,000 bugs this year alone, adding ~26% more vulnerabilities to the all time total Do you realize how fucking insane that is?

Yes. It is a new world out there.

Bloatware in Aftermarket Auto Parts

30 October 2026 at 16:20

This story is interesting:

One Civic owner purchased a cheap aftermarket head unit off Amazon, and decided to have Claude work its magic on it, like it would a smart TV. What was reportedly discovered isn’t surprising, but is worth knowing about.

Among the pre-installed bloatware—­or spyware, if you’re being less charitable­—was a voice assistant equipped with WebView, an Android system component that lets apps display content off the web. This apparently always used about a third of processing power, even while idle, which isn’t great. There were also Baidu location services, a call recorder (!), a DAB radio client that is pretty much useless in the U.S., and Adobe Acrobat, presumably so your passenger can entertain themselves with PDFs on the go.

It’s interesting because it exposes all the insecurities in this piece of IoT software. But I think the real story is that a random person was able to do this reverse-engineering with the help of AI. Expect a lot more stories like this in the future.

Unit 42 Threat Intelligence Highlights - Nov. 2, 2026

3 November 2026 at 00:00

Unit 42 details recent threat intelligence, highlighting cyberespionage, financial extortion, and the rapid adoption of AI across offensive workflows.

The post Unit 42 Threat Intelligence Highlights - Nov. 2, 2026 appeared first on Unit 42.

Unwrapping Retail Peak Season Cyber Threats

28 October 2026 at 19:00

Unit 42 explores key peak shopping season retail cyber threats, from ransomware to AI attacks, and shares how to defend operations and customer trust.

The post Unwrapping Retail Peak Season Cyber Threats appeared first on Unit 42.

Applying Security by Design and Cyber Immunity principles to protect AI systems | Kaspersky official blog

29 October 2026 at 14:07

AI systems are much harder to protect than traditional IT — whether from operator mistakes, malicious interference, or just plain unstable behavior. There are two main reasons for this. First, AI outputs are probabilistic, so the same prompt can give different answers each time you run it. Second, today’s LLMs can’t reliably tell commands apart from data. Despite the demonstrated security issues of AI systems that we’ve covered many times, it’s impossible to ignore the potential economic payoff of adopting them. That’s why many companies are moving beyond simple AI assistants to AI agents. These agents carry out tasks on their own and have direct access to the same tools as humans — from reading databases to changing settings in production processes. Our experts, in their new study, examine how to clearly define and minimize the resulting risks to keep potential problems to a minimum. The approach borrows and adapts the principles of Cyber Immunity and Security by Design.

The basic principles of Security by Design

All the principles of this discipline are universally applicable to the design of any computer system — AI agents included. What differs is how deeply each principle needs to be adapted and reworked for AI scenarios.

  1. Security is a separate and important factor right from the design stage. Security goals and assumptions are set on day one and followed throughout every stage of development. For AI agents, these assumptions should include three key points: (i) the language model is treated as untrusted, (ii) external data of any kind is considered potentially malicious, and (iii) irreversible actions can’t be performed autonomously without mandatory human approval.
  2. The system is designed on the assumption that it will be attacked.
  3. The trusted computing base and attack surface are kept to a minimum. Agents get only the tools they actually need, limited permissions, and the smallest amount of context possible. Security policy enforcement is handled entirely by deterministic components: the policy monitor, the agent harness, and isolation mechanisms (sandboxes).
  4. The principle of least privilege applies. Each agent has its own set of credentials and access privileges (identity), limited to the bare minimum it needs to do its job. If an agent temporarily needs elevated privileges, it gets them only after external approval, and they last exactly as long as the task that requires them.
  5. Components are isolated. In agent-based systems, this is one of the most complex and multi-layered architecture problems. The agent harness should run in an isolated environment (sandbox or virtual machine), and agents should be kept as isolated from each other as possible. Data processing in trusted and untrusted contexts is also kept separate. For example, one agent reads a pull request and writes a draft of the code, while another reviews that work without ever seeing the potentially malicious text of the request.
  6. Default deny is the rule. Security policies follow the rule: anything not explicitly allowed is forbidden. This includes tool calls, interactions between agents, and network traffic.
  7. Defense in depth is in place. Different measures should work at the same time and reinforce each other. Probabilistic defenses — like AI guardrails (a “firewall” for language models) or alignment (the model’s own sense of what’s acceptable and what isn’t) — can’t offer any formal security guarantees. Nevertheless, they make the system more secure overall and serve as a valuable source of telemetry.
  8. The supply chain is protected. Some agents can install skills, libraries, and other software components on their own, so these abilities need strict rules. Either block them completely, or limit them to a closed, pre-approved list of specific versions of specific components. Systems built on cloud LLMs face an extra risk: model updates. One day, the same API request might be answered by a different language model with different security properties.

Pitfalls of AI security

The general principles of Security by Design are well known and look simple on paper. But applying them to AI systems is tricky because agents are incredibly flexible. For example, a security team might believe that an agent on a developer’s computer runs in a sandbox and can’t change anything outside it. But an attacker, or even the agent itself, can come up with dozens of ways around this seemingly solid protection: from running commands through a local MCP server that the sandbox doesn’t restrict, to reconfiguring another AI agent installed on the system. To make things even harder, the range of attack vectors is huge: from arbitrary fields in the agent’s configuration to innocent-looking text strings in a skill file.

One serious problem that designers often underestimate is user fatigue. A busy agent can throw up dozens of requests every minute, asking the user to confirm potentially dangerous actions. Within an hour, the person is clicking Approve on autopilot without reading what they’re approving. That’s why it’s important to carefully tune both how often these requests appear and how they’re worded. Nobody will read a request description that’s too long. And one that’s too short can hide the key details the user needs in order to make the right call.

Vulnerabilities in agents and related tools are a pressing problem — and it’s made worse by how quickly these categories of software evolve and receive updates. Industry-standard platforms and apps — such as LangGraph, MS Semantic Kernel, and Claude Code — have had critical vulnerabilities patched more than once. Architects should always consider swapping a large, do-it-all framework for a compact, stripped-down system that has only the features a specific agent actually needs.

On top of that, carefully implementing standard, long-established security measures in the available tools greatly reduces the damage if an agent is attacked or behaves unexpectedly. One example is a strict allowlist of domains that the web fetch tool can open when asked by the agent. But designers rarely account for the hidden problems and overhead associated with maintaining the list. As a result, it slowly goes out of date and leaves loopholes for attackers. The most striking example is the EchoLeak attack. Microsoft 365 Copilot had a properly implemented and fairly effective allowlist for accessing external sites, but attackers circumvented it through a feature in a secondary tool and the MS Teams domain.

Practical tips for architects and security teams

AI system architects and heads of engineering and security teams should build in agent security from the design stage. They should rely primarily on verifiable, deterministic mechanisms: isolating components, controlling interactions, and keeping the trusted computing base to a minimum.

Key architectural decisions include defining acceptable autonomy for the agents, limiting access to confidential data and dangerous combinations of capabilities, and using sandboxes, separate roles for different models, and access control gateways. Restrictions added as an afterthought reduce risks, but they’re no substitute for secure architecture.

At the organizational and operational levels, companies need to keep an inventory of their agents, coordinate the efforts of security and deployment teams, protect container environments, manage the supply chain (AIBOM), and integrate multi-layered defense.

Observability requires special attention. For AI systems, this should include logging the LLM’s requests, responses, and reasoning, as well as detailed telemetry from the hosts and cloud environments where the agent harness runs.

The hardest part of designing agents is balancing security, performance, and usefulness. To learn how to strike that balance with threat modeling and clearly defined security goals, read the full version of the study.

Banks are blocking AI agents from customer accounts

28 October 2026 at 14:38

This week, Axios reported that major US banks were detecting third-party AI agents operating inside customer accounts. In many cases, customers have given the agents their usernames and passwords so they could act on their behalf. This kind of access can violate a bank’s rules.

Bianco Research president Jim Bianco raised the question during Unchained’s Bits + Bips livestream on October 26:

“Are you protecting me, or are you protecting your own profits?”

Bianco described traditional finance’s business model as “based on laziness.” Customers may leave idle cash in low- or no-interest bank accounts rather than move it into a money market fund. An AI agent could make that move for them. “Now that you’re able to do it, the banks are afraid they’re gonna lose that revenue stream,” he said.

The banks offer a different explanation. JPMorgan Chase CEO Jamie Dimon said the bank wouldn’t allow just any outside agent into its systems because doing so was “too risky for clients and for JPMorgan.”

Both explanations can be true: banks can want to retain deposits while also facing real security problems when software acts through customers’ accounts.

Handing over your banking login introduces another service into the security chain. A vulnerability in that service could expose your credentials or allow your account to be misused. And as Bank of America reportedly pointed out:

 “If you do share your credentials, keep in mind that you’re responsible for activity resulting from that access.”

That’s the bank’s stated position, not a universal ruling on consumers’ legal rights. Still, it’s a warning worth taking seriously.

Pros and cons

An AI agent with permission to make purchases might find and buy an item at a lower price. But giving an agent access to your bank account also means sharing sensitive banking information with a third party. We’ve seen shared AI chats become searchable online too.

Axios reported that many banks allow, or are moving toward allowing, read-only access. This can let a tool analyze transactions without giving it permission to move money.

That’s an important boundary, but it doesn’t make the information harmless. An agent that can read bank statements may still disclose them if it’s compromised or manipulated. Preventing transactions and protecting confidentiality are separate security goals.

How to keep control of your money

For consumers, the practical question is not whether banks have perfectly selfless motives. It’s what access you’re giving away, and what could happen if the agent makes a mistake.

  • Don’t paste banking passwords or security codes into a general-purpose AI assistant. Major banks have explicitly warned customers against sharing their credentials.
  • Use your bank’s approved connection methods rather than giving an agent your login. Where supported, choose read-only access if all you need is analysis or budgeting help.
  • Give agents access to as little sensitive information as possible. An assistant comparing publicly advertised savings rates doesn’t need your bank statements. OpenAI recommends limiting agents to the data and credentials they need for the task.
  • Review consequential actions yourself. If an agent asks for confirmation, check exactly what it intends to do and what information it will share. Don’t treat a confirmation prompt as a formality.

AI can make it easier to compare financial products and spot opportunities you might otherwise miss. But an assistant that finds a better rate and an agent that can act inside your account are different propositions.

Let it help with the homework, but be cautious about handing it the keys.


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

Banks are blocking AI agents from customer accounts

28 October 2026 at 14:38

This week, Axios reported that major US banks were detecting third-party AI agents operating inside customer accounts. In many cases, customers have given the agents their usernames and passwords so they could act on their behalf. This kind of access can violate a bank’s rules.

Bianco Research president Jim Bianco raised the question during Unchained’s Bits + Bips livestream on October 26:

“Are you protecting me, or are you protecting your own profits?”

Bianco described traditional finance’s business model as “based on laziness.” Customers may leave idle cash in low- or no-interest bank accounts rather than move it into a money market fund. An AI agent could make that move for them. “Now that you’re able to do it, the banks are afraid they’re gonna lose that revenue stream,” he said.

The banks offer a different explanation. JPMorgan Chase CEO Jamie Dimon said the bank wouldn’t allow just any outside agent into its systems because doing so was “too risky for clients and for JPMorgan.”

Both explanations can be true: banks can want to retain deposits while also facing real security problems when software acts through customers’ accounts.

Handing over your banking login introduces another service into the security chain. A vulnerability in that service could expose your credentials or allow your account to be misused. And as Bank of America reportedly pointed out:

 “If you do share your credentials, keep in mind that you’re responsible for activity resulting from that access.”

That’s the bank’s stated position, not a universal ruling on consumers’ legal rights. Still, it’s a warning worth taking seriously.

Pros and cons

An AI agent with permission to make purchases might find and buy an item at a lower price. But giving an agent access to your bank account also means sharing sensitive banking information with a third party. We’ve seen shared AI chats become searchable online too.

Axios reported that many banks allow, or are moving toward allowing, read-only access. This can let a tool analyze transactions without giving it permission to move money.

That’s an important boundary, but it doesn’t make the information harmless. An agent that can read bank statements may still disclose them if it’s compromised or manipulated. Preventing transactions and protecting confidentiality are separate security goals.

How to keep control of your money

For consumers, the practical question is not whether banks have perfectly selfless motives. It’s what access you’re giving away, and what could happen if the agent makes a mistake.

  • Don’t paste banking passwords or security codes into a general-purpose AI assistant. Major banks have explicitly warned customers against sharing their credentials.
  • Use your bank’s approved connection methods rather than giving an agent your login. Where supported, choose read-only access if all you need is analysis or budgeting help.
  • Give agents access to as little sensitive information as possible. An assistant comparing publicly advertised savings rates doesn’t need your bank statements. OpenAI recommends limiting agents to the data and credentials they need for the task.
  • Review consequential actions yourself. If an agent asks for confirmation, check exactly what it intends to do and what information it will share. Don’t treat a confirmation prompt as a formality.

AI can make it easier to compare financial products and spot opportunities you might otherwise miss. But an assistant that finds a better rate and an agent that can act inside your account are different propositions.

Let it help with the homework, but be cautious about handing it the keys.


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

Chrome and Firefox updates fix serious security flaws. Install them now

28 October 2026 at 12:13

On October 27, Google issued a new Stable channel update for Chrome.

Most users are on Chrome’s Stable channel. The desktop update brings Chrome to versions 156.0.8078.73/.74 for Windows and Mac and 156.0.8078.73 for Linux. The update includes 52 security fixes, including four rated Critical.

On the same day, Mozilla issued Security Advisory 2026-118, which fixes 167 vulnerabilities. Firefox 159 also introduces several new features.

Both updates will roll out over the coming days and weeks.

How to update Chrome

The easiest option is to allow Chrome to update automatically. But you can end up lagging behind on updates if you never close your browser or if something goes wrong, such as an extension preventing the update.

If you don’t want to wait for the rollout to reach you, manually updating is easy. Open About Google Chrome from Chrome’s settings or Help menu. Chrome will check for updates. If one is available, click Relaunch to apply it.

Chrome version 156.0.8078.74 is up to date

You can find an explanation of the version numbering system and step-by-step instructions in our guide: How to update Chrome on every operating system.

How to update Firefox

To update Firefox, open the browser and click the menu button at the right side of the Firefox toolbar, then go to Help and select About Firefox. The About Mozilla Firefox window will open.

Firefox will automatically check for updates. If one is available, it will be downloaded. Once done, you’ll be prompted to click Relaunch. After Firefox restarts, it will be up to date.

After the update, the version should be 159.0 or later

Technical details

These Chrome and Firefox updates address a familiar problem: browser code mishandling memory while processing web content. Both releases fix use-after-free vulnerabilities, including flaws in page layout, JavaScript processing, and SVG graphics.

A use-after-free vulnerability occurs when a program attempts to access a memory location after it has been freed. That can cause crashes or, in some cases, allow an attacker to run their own code.

There’s another connection between these updates: both Google and Mozilla credit OpenAI Codex Security with finding bugs fixed in these releases. AI can help security teams examine browser code for weaknesses, alongside human code reviews and automated tests that check how software handles unexpected inputs.

Mozilla’s collaboration with Anthropic shows how AI-discovered findings can lead to fixes: researchers validated vulnerabilities before reporting them, giving Mozilla’s team reproducible bugs to investigate, repair, and deliver to users.


Browse like no one’s watching. 

Malwarebytes Privacy VPN encrypts your connection and never logs what you do, so the next story you read doesn’t have to feel personal. Try it free → 

Chrome and Firefox updates fix serious security flaws. Install them now

28 October 2026 at 12:13

On October 27, Google issued a new Stable channel update for Chrome.

Most users are on Chrome’s Stable channel. The desktop update brings Chrome to versions 156.0.8078.73/.74 for Windows and Mac and 156.0.8078.73 for Linux. The update includes 52 security fixes, including four rated Critical.

On the same day, Mozilla issued Security Advisory 2026-118, which fixes 167 vulnerabilities. Firefox 159 also introduces several new features.

Both updates will roll out over the coming days and weeks.

How to update Chrome

The easiest option is to allow Chrome to update automatically. But you can end up lagging behind on updates if you never close your browser or if something goes wrong, such as an extension preventing the update.

If you don’t want to wait for the rollout to reach you, manually updating is easy. Open About Google Chrome from Chrome’s settings or Help menu. Chrome will check for updates. If one is available, click Relaunch to apply it.

Chrome version 156.0.8078.74 is up to date

You can find an explanation of the version numbering system and step-by-step instructions in our guide: How to update Chrome on every operating system.

How to update Firefox

To update Firefox, open the browser and click the menu button at the right side of the Firefox toolbar, then go to Help and select About Firefox. The About Mozilla Firefox window will open.

Firefox will automatically check for updates. If one is available, it will be downloaded. Once done, you’ll be prompted to click Relaunch. After Firefox restarts, it will be up to date.

After the update, the version should be 159.0 or later

Technical details

These Chrome and Firefox updates address a familiar problem: browser code mishandling memory while processing web content. Both releases fix use-after-free vulnerabilities, including flaws in page layout, JavaScript processing, and SVG graphics.

A use-after-free vulnerability occurs when a program attempts to access a memory location after it has been freed. That can cause crashes or, in some cases, allow an attacker to run their own code.

There’s another connection between these updates: both Google and Mozilla credit OpenAI Codex Security with finding bugs fixed in these releases. AI can help security teams examine browser code for weaknesses, alongside human code reviews and automated tests that check how software handles unexpected inputs.

Mozilla’s collaboration with Anthropic shows how AI-discovered findings can lead to fixes: researchers validated vulnerabilities before reporting them, giving Mozilla’s team reproducible bugs to investigate, repair, and deliver to users.


Browse like no one’s watching. 

Malwarebytes Privacy VPN encrypts your connection and never logs what you do, so the next story you read doesn’t have to feel personal. Try it free → 

In an age of AI, deciding what to trust is a foundational skill. Here’s how we’re helping educators teach it.

27 October 2026 at 19:30

Launching the expanded AI Classroom Toolkit with Cyberlite during Global Media and Information Literacy Week 

AI is opening new pathways to information, giving people faster access to answers, ideas, and knowledge. At the same time, it’s making it harder to know whether the content we see is authentic. 

Companies that build AI have a responsibility to make it reliable and trustworthy, and that responsibility doesn’t shift to the people who use it. But AI is already shaping how people search, learn, and encounter information. Helping people navigate that reality means building media and AI literacy (MAIL): the judgment to decide whether and how to use AI and what information to trust. These skills are as foundational as AI safety, and educators are asking for help teaching them. 

That’s why, during Global Media and Information Literacy Week, we’re launching the expanded AI Classroom Toolkit: Unlocking Generative AI Safely and Responsibly, created with the online safety organization Cyberlite. It’s part of Microsoft’s broader commitment to make sure AI strengthens human thinking rather than replaces it. It also reflects Microsoft’s focus on education and empowerment, a core pillar of our Safe Participation Framework. 

Title slide: "Classroom Toolkit – Unlocking Generative AI Safely and Responsibly, 2026 Edition," with Microsoft and Cyberlite logos.

What’s new in the AI Classroom Toolkit

The expanded toolkit adds a deeper focus on critical thinking, verification, and media and AI literacy, helping students judge AI outputs and make informed decisions about what to trust online. Together with the original modules, it’s now a single, classroom-ready resource that covers the core of AI safety and literacy. Realistic, scenario-based lessons and activities help students practice these skills in situations they may encounter online: 

  • The Climate Campaign: Gina enters an online challenge to make a campaign for a cause she cares about and finds that some winning entries use AI to show events that never happened. Students sort a feed of real and AI-made posts and practice lateral reading. The lesson: whether a post was made with AI doesn’t decide whether it’s trustworthy. What it claims, and who is behind it, does. 
  • The Helpful Bot: Alex creates an AI help bot inside his online game, then catches it inventing details and collecting players’ personal information. Students learn why AI can get things wrong, how to trace claims to reliable sources, and why they’re responsible for AI-generated content they act on or share. 
  • What Kind of AI User Are You?: An interactive quiz, hosted by Cyberlite, helps students identify their AI habits, strengths, and potential blind spots, and gives them an AI Type to reflect on and discuss. 

“When we created the first Classroom Toolkit: Unlocking Generative AI Safely and Responsibly with Microsoft in 2023, most of the conversation was about using AI safely. Today, the questions young people ask about AI have grown sharper and more personal, like what to believe online or how far to trust a chatbot’s answer,” said Michelle Yao, cofounder of Cyberlite. 

The toolkit also reflects what young people in our co-design sessions with Cyberlite told us: they want to learn by doing, through games, real-life scenarios, and peer discussion. Teachers don’t need to be AI experts, and students don’t need an AI tool in hand to start. 

That approach builds on the reach and results of the original toolkit. Since 2023, the first version has reached educators in 10 countries and 11 languages, including through government and partner learning platforms. In South Korea, 93% of participating educators reported improved knowledge and understanding of ethical issues, privacy, and bias related to AI. 

“Our hope is that every student leaves a little surer of their own judgment, and that everyone feels more confident deciding how AI fits into their lives,” said Yao. 

Section 2 title slide: "Gina's Fight for the Ocean," with an illustration of a young woman wearing a "Skip Straws" T-shirt.

Literacy works alongside product design and policy

Education is one part of the equation. Our commitment to media and AI literacy also shows up in how we design products and the policies we support.  

Last month, we set out five principles for AI in education, including “AI designed to support students’ learning, not replace their thinking.” We also committed to enforceable privacy, safety, and transparency protections for qualifying educational AI products in US school districts. These protections help schools and families understand how these tools work and the controls available to them. 

Media and AI literacy is now a global priority

The Organisation for Economic Co-operation and Development has released a framework for a MAIL assessment beginning in 2029. As part of its Programme for International Student Assessment (PISA), it will examine how students reflect on, analyze, and evaluate information, including AI-generated information. This week in New Delhi, UNESCO is also launching an AI extension of its “Think Critically, Click Wisely” global curriculum, which Microsoft advised on. 

This growing global focus makes the need for support urgent—educators want help, and many aren’t getting it. In Microsoft’s 2026 AI in Education report, 53% of educators and 77% of students say they haven’t had AI training.  

Closing this skills gap matters beyond the classroom. Healthy societies depend on a shared basis of facts, informed public debate, and confident civic participation. As authenticity gets harder to judge, there’s a risk that people start doubting everything, creating what the Digital Inquiry Group calls a “dangerous declaration of permanent uncertainty.” MAIL offers a way through. It builds the confidence to decide what to trust. 

Media and AI literacy for every age

Across Microsoft, we’re helping people build these skills wherever they learn and find information: 

  • In classrooms: Students debate whether to accept, question, or rework an AI tool’s answers in an AI and Critical Thinking lesson from The Economist Educational Foundation, supported by Microsoft. Available alongside other media literacy lessons in Microsoft Learning Zone, the lesson has reached students in 116 countries. 
  • For content creators: UNESCO, with Microsoft’s support, is developing resources to help creator associations train their members in MAIL and is testing them with creators in Nairobi this week.  
  • In our products: Search Progress, built with input from the Digital Inquiry Group, turns research assignments into source-checking practice in Microsoft Teams for Education. 

What’s next 

Through Microsoft Elevate for Educators and local partners, we’ll bring the AI Classroom Toolkit to new audiences, with more languages and localized content rolling out through 2027. We’ll keep evolving it as technology and educators’ needs change. 

Explore the toolkit and supporting resources for educators today.  

AI will keep changing how people find information and the content they encounter. Our goal is to help people meet that change with confident, informed judgment about the AI they use and the information they trust so they can fully take part in civic and democratic life. 

The post In an age of AI, deciding what to trust is a foundational skill. Here’s how we’re helping educators teach it. appeared first on Microsoft On the Issues.

Ransomware in the Age of AI: How Defenders Can Break the Attack Chain

Ransomware operators are scaling their attacks, and the barriers to entry continue to fall. In the first half of 2026, Flashpoint identified 6,256 ransomware attacks across industries, representing a 45% increase between 2025 and 2026, as Ransomware-as-a-Service (RaaS) operations expanded and threat actors increasingly leveraged AI, stolen credentials, and vulnerability exploits to accelerate their campaigns.

The impact is widespread. Manufacturing accounted for 18% of observed attacks, followed by business services and consulting (13%) and healthcare (9%). Meanwhile, prolific ransomware groups such as Qilin and Akira continue to demonstrate the scale at which these operations can function.

Understanding how ransomware attacks develop, and where they can be interrupted, is critical for defenders.

Introducing Ransomware in the Age of AI: A Survival Guide for Defenders

Flashpoint’s new guide, Ransomware in the Age of AI: A Survival Guide for Defenders, provides cyber threat intelligence professionals, threat hunters, and security leaders with a practical look at the modern ransomware attack lifecycle, from initial reconnaissance and access to incident response and recovery.

Drawing on Flashpoint’s primary-source intelligence and analysis of evolving threat actor tactics, the guide explores how organizations can identify opportunities to disrupt attacks before they escalate, strengthen incident response, and reduce the risk of repeat compromise.

Access the guide to learn:

  • How modern ransomware attacks unfold: Follow the attack lifecycle, from reconnaissance, phishing, and initial access through lateral movement, encryption, and ransom negotiations.
  • Where defenders can intervene: Understand how compromised credential monitoring, vulnerability intelligence, and visibility into underground activity can help identify threats before attackers reach critical systems.
  • How AI is reshaping ransomware operations: Explore how AI-enabled capabilities, commoditized tooling, and RaaS ecosystems are changing the economics and execution of ransomware attacks.
  • How to strengthen response and recovery: Learn strategies for containing active incidents, restoring operations, improving cross-team coordination, and reducing exposure to repeat attacks.

“In H1 2026, Flashpoint observed a 45% surge in ransomware activity, with critical sectors like manufacturing, business consulting, and healthcare taking the brunt of these attacks. As RaaS syndicates like Qilin and Akira scale their operations alongside a 27% rise in infostealers, access is becoming faster and cheaper. Effective defense requires grounding incident response in primary-source intelligence across every phase of the attack lifecycle.”

Ian GrayVP of Intelligence, Flashpoint

Understanding the Modern Ransomware Attack Lifecycle

Ransomware attacks rarely begin with encryption. Long before systems are locked or ransom demands appear, threat actors may be gathering intelligence on potential targets, exploiting exposed vulnerabilities, or acquiring stolen credentials through underground marketplaces.

Flashpoint observed a 27% increase in infostealer operations in H1 2026 compared to H1 2025, underscoring the growing role of compromised identities in the ransomware ecosystem. Stolen credentials and session data can provide attackers with access to organizational environments, potentially allowing them to bypass traditional defenses and establish a foothold.

These initial access methods are increasingly interconnected with broader criminal operations. RaaS groups can leverage specialized tools and services throughout the attack chain, while AI-enabled capabilities offer additional opportunities to automate and accelerate certain activities.

This creates multiple opportunities for defenders to act. Intelligence about exposed credentials, emerging exploitation activity, and threat actor behavior can help security teams identify risks earlier and prioritize defensive action before an intrusion progresses.

The guide examines these opportunities across the ransomware lifecycle, outlining how proactive intelligence and coordinated response can help organizations minimize operational disruption and strengthen resilience.

Build a More Proactive Defense Against Ransomware

As ransomware operations continue to evolve, organizations need visibility into the threats targeting their environments and the intelligence to respond at every stage of an attack.

From identifying compromised credentials and monitoring emerging threats to containing incidents and preventing repeat attacks, a lifecycle-based approach helps security teams make more informed decisions before, during, and after a ransomware incident.

Get the Ransomware in the Age of AI: A Survival Guide for Defenders to explore the modern ransomware attack lifecycle and learn how Flashpoint’s threat intelligence can help your organization anticipate, disrupt, and recover from ransomware attacks.

See Flashpoint in Action

The post Ransomware in the Age of AI: How Defenders Can Break the Attack Chain appeared first on Flashpoint.

Artificial Intimacy: Love and lies in the age of AI 

27 October 2026 at 13:40

AI is becoming a third wheel in relationships, increasingly playing a role in the most intimate parts of our lives.  

It shows up in the flirty first text, the polished dating profile, the therapized language we use with a partner after a fight, the strength we gather after heartbreak, and everywhere in between. For some, AI is a source of companionship itself. And even if you’re not personally an AI user, you may still be dating, loving, arguing with, or trusting someone who is. 

As AI moves deeper into our relationships, it’s reshaping connection, blurring what feels authentic, and creating new ways for intimacy to be exploited. 

AI is starting to replace human interaction 

AI is moving into emotional territory once reserved for other people. For some, it’s no longer just a tool, but a source of support, companionship, and even romantic connection. 

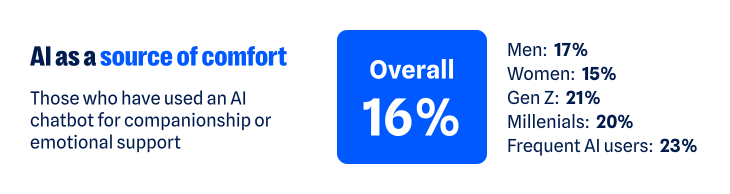
According to our recent research, about one in six have turned to a chatbot for companionship or emotional support. That climbs to about one in five among Gen Z and Millennials, and nearly one in four among regular AI users (those who use AI daily or multiple times a week). The more time people spend with AI, the more likely they are to humanize its role, making room for it as a friend, confidant, advisor, or even partner.   

16% of respondents have used an AI chatbot for companionship or emotional support

As AI takes on more intimate roles, it’s also starting to challenge the boundaries of real human relationships. More than one in three (37%) say having a romantic relationship with an AI chatbot while already in a committed relationship isn’t the same as cheating. That view is more common among men (46% versus 30% of women), Gen Z and Millennials (43% and 45%), and regular AI users (48%). 

27% of respondents do not consider engaging in an AI romance cheating while in a committed relationship

Whether the relationship is platonic or romantic, the more AI is treated like a human, the more personal the stakes become. Just like you have to be cautious when telling a human your deepest, darkest secrets, the experience is similar when using AI. Nearly two-thirds (65%) worry that private conversations they’ve had with AI could be exposed.  

One survey respondent said:

“I have used a chatbot…for emotional support, and it is worrying to think those conversations could be leaked.”

The technology may be artificial, but the relationships people form with AI can feel very real. And as with any relationship, that means there are boundaries to work out, privacy to protect, and vulnerabilities to manage. 

AI is creating new ways to weaponize intimacy 

AI’s growing role in human intimacy also has a darker side. The same technology that can offer comfort, advice, or companionship can also be used to violate the most intimate parts of our lives. 

Non-consensual image abuse, sextortion, and other forms of sexual abuse have long been part of the internet’s dark side. Generative AI has made that content easier to create. Someone trying to exploit another person no longer needs an actual intimate photo, video, or private exchange. A regular photo—or even just someone’s likeness—can be transformed into sexual content they never made, never shared, and never consented to. 

Most people draw a clear line against that, but not everyone does. About one in six people say it’s acceptable to generate explicit images of someone without their permission for personal use. Another 14% are neutral, bringing the share who do not explicitly oppose the behavior to nearly one in three (31%).  

Views differ sharply by age and sex: 

  • Younger adults are more accepting of someone using AI to generate non-consensual content: nearly one in four Gen Z (24%) and Millennials (23%) say it’s okay, compared with 13% of Gen X and just 5% of Boomers+ 
  • Men are also more permissive: more than one in five (22%) say it’s okay, compared with 14% of women 

Attitudes toward the behavior may vary, but the fear of becoming a target is far more widespread. Overall, nearly two-thirds of people (62%) worry someone could create fake nude or sexually explicit photos or videos of them. Women feel this threat more acutely: nearly seven in ten (69%) are concerned, compared with 57% of men. 

69% of respondents oppose generating explicit images of someone without their permission, while 17% are okay with it.

For some, this fear has already become a reality:  

  • One in ten say AI has been used to generate nude or sexually explicit imagery of them without permission 
  • One in ten say someone has threatened to release AI-generated compromising or explicit imagery of them 

As one respondent recounted: 

“I had someone make fake nudes of me using AI on my photos from my social media and threaten to post them on Facebook…[it] made me more cautious about AI.”

The intimate material may be fake, but the fear, coercion, and potential for reputational, emotional, and financial damage are completely real. 

AI is making it harder to know who you’re really talking to  

The threat doesn’t stop with fabricated sexual content. AI is also making it harder to know whether the person on the other side of a screen is who they claim to be. 

Humans have always edited themselves for other people. We choose the most flattering photo, write and rewrite the text before sending it, and present our most interesting selves—especially when forming new relationships. AI dramatically expands what that kind of self-editing can look like, and people aren’t shy about using it: 

  • 54% say AI helps them present the best version of themselves  
  • 47% say using AI to present your “best self” to employers, friends, or romantic partners does not present a false identity 
  • That rises to 58% of both Gen Z and Millennials and 64% of regular AI users 

But where does enhancement end and deception begin? Is an AI-polished dating profile still authentically you? What about a message you didn’t write? A photo that looks like you, only better? 

There’s a flipside to using AI to make ourselves look or sound better: If we can do it, so can everyone else. And people are much less comfortable when they’re not the ones controlling the technology. Two-thirds (67%) worry that an online friend or romantic interest could use AI-generated images, videos, or other content to deceive them.  

Catfishing, fake photos, and lies on dating profiles aren’t new. AI just makes the deception easier. Someone’s photos, backstory, messages, and even their voice can all be faked.  

One person described leaving dating apps after realizing the person they were talking to had gone well beyond simply polishing their profile: 

“[The] dating profile had fake pictures…[it] wasn’t just making true events sound interesting and more flirty, but creating completely false photos and information. Left the dating apps again and needed to reset.”

AI can distort identity in the other direction, too. It can also create a version of us we never chose to put into the world.  

  • 76% worry about someone creating a fake profile pretending to be them 
  • 70% worry about fake images or videos of themselves being created 
  • 71% worry AI-generated content could be used to damage their reputation 
AI is a double edged tool where they feel like they can present their best selves, but also are wary of other people creating fake identities

Relationships are built on mutual trust. AI can distort both sides of the connection: who we think the other person is, and who they think we are.  

AI is quietly finding its way into the space between people  

Not all of AI’s influence on intimacy is so dramatic. Much of it happens quietly, showing up in how people communicate with each other and navigate relationships: 

  • More than one in three have used AI to help write or edit a message 
  • About one in seven have turned to it for advice about a relationship or personal decision 
  • One in ten say it has already changed how they date or communicate romantically—rising to nearly one in five among Gen Z 

The survey responses show what this looks like in real life. For example, one respondent described using AI with their partner as a way to step outside their own point of view: 

“Personally, it has helped me. We use AI in our relationship as a reflection tool, and it has sometimes helped us take on the perspective of the other.”

For another, AI helped them work through jealousy:  

“So, I used to accuse my partner, and I got really territorial about them but once I talked to AI about it, they gave helpful advice and now we are stronger than ever.”

AI is also showing up in other difficult relationship moments. One person said it helped them “stay calm and communicate” when problems came up with their partner; another said it allows them “to pause and refine [their] thoughts” before responding. 

Sometimes the role is simpler. One respondent said AI gives them “new romantic words” for their partner, while another said they’ve asked AI for advice on how to make their partner smile. AI’s growing role in relationships may be unsettling, but the benefits people describe are definitely there. 

AI isn’t just helping people find the right words. It’s also helping them decide what version of themselves to put forward in the first place. More than one in three say it’s okay to use AI to create or improve a dating profile; nearly two-thirds aren’t opposed. One respondent described using AI as a “creative advisor” to polish their profile and come up with conversation starters. 

AI doesn’t have to replace a relationship to help shape it. It can influence how people communicate, what advice they take, and how they choose to present themselves.  

AI’s intimacy problem is ultimately a trust problem 

From connection to deception to outright harm, the same question keeps surfacing: Can I trust what’s in front of me? And would I know if I couldn’t? 

Nearly nine in ten people (88%) say AI is making it harder to tell what online content is genuinely human or real. And 84% say even convincing video evidence no longer necessarily feels like proof. That uncertainty follows people into dating and relationships, where knowing what—and who—to trust is deeply personal. 

AI may make it easier to start a conversation, smooth over a hard one, or feel connected when you’re lonely. But relationships and intimacy of all kinds still come down to trust, and AI is making that trust a little harder to take at face value. 

About the research 

The research in this article is based on a March 2026 survey about AI, identity, and the collapse of digital trust and was conducted among 1,500 respondents in the United States, United Kingdom, Germany, Austria, and Switzerland. The research was prepared by an independent research consultant and distributed via Forsta. 


Something feel off? Check it before you click.  

Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.  

Available with Malwarebytes Premium Security for all your devices, and in the Malwarebytes app for iOS and Android.  

Try it free → 

Artificial Intimacy: Love and lies in the age of AI 

27 October 2026 at 13:40

AI is becoming a third wheel in relationships, increasingly playing a role in the most intimate parts of our lives.  

It shows up in the flirty first text, the polished dating profile, the therapized language we use with a partner after a fight, the strength we gather after heartbreak, and everywhere in between. For some, AI is a source of companionship itself. And even if you’re not personally an AI user, you may still be dating, loving, arguing with, or trusting someone who is. 

As AI moves deeper into our relationships, it’s reshaping connection, blurring what feels authentic, and creating new ways for intimacy to be exploited. 

AI is starting to replace human interaction 

AI is moving into emotional territory once reserved for other people. For some, it’s no longer just a tool, but a source of support, companionship, and even romantic connection. 

According to our recent research, about one in six have turned to a chatbot for companionship or emotional support. That climbs to about one in five among Gen Z and Millennials, and nearly one in four among regular AI users (those who use AI daily or multiple times a week). The more time people spend with AI, the more likely they are to humanize its role, making room for it as a friend, confidant, advisor, or even partner.   

16% of respondents have used an AI chatbot for companionship or emotional support

As AI takes on more intimate roles, it’s also starting to challenge the boundaries of real human relationships. More than one in three (37%) say having a romantic relationship with an AI chatbot while already in a committed relationship isn’t the same as cheating. That view is more common among men (46% versus 30% of women), Gen Z and Millennials (43% and 45%), and regular AI users (48%). 

27% of respondents do not consider engaging in an AI romance cheating while in a committed relationship

Whether the relationship is platonic or romantic, the more AI is treated like a human, the more personal the stakes become. Just like you have to be cautious when telling a human your deepest, darkest secrets, the experience is similar when using AI. Nearly two-thirds (65%) worry that private conversations they’ve had with AI could be exposed.  

One survey respondent said:

“I have used a chatbot…for emotional support, and it is worrying to think those conversations could be leaked.”

The technology may be artificial, but the relationships people form with AI can feel very real. And as with any relationship, that means there are boundaries to work out, privacy to protect, and vulnerabilities to manage. 

AI is creating new ways to weaponize intimacy 

AI’s growing role in human intimacy also has a darker side. The same technology that can offer comfort, advice, or companionship can also be used to violate the most intimate parts of our lives. 

Non-consensual image abuse, sextortion, and other forms of sexual abuse have long been part of the internet’s dark side. Generative AI has made that content easier to create. Someone trying to exploit another person no longer needs an actual intimate photo, video, or private exchange. A regular photo—or even just someone’s likeness—can be transformed into sexual content they never made, never shared, and never consented to. 

Most people draw a clear line against that, but not everyone does. About one in six people say it’s acceptable to generate explicit images of someone without their permission for personal use. Another 14% are neutral, bringing the share who do not explicitly oppose the behavior to nearly one in three (31%).  

Views differ sharply by age and sex: 

  • Younger adults are more accepting of someone using AI to generate non-consensual content: nearly one in four Gen Z (24%) and Millennials (23%) say it’s okay, compared with 13% of Gen X and just 5% of Boomers+ 
  • Men are also more permissive: more than one in five (22%) say it’s okay, compared with 14% of women 

Attitudes toward the behavior may vary, but the fear of becoming a target is far more widespread. Overall, nearly two-thirds of people (62%) worry someone could create fake nude or sexually explicit photos or videos of them. Women feel this threat more acutely: nearly seven in ten (69%) are concerned, compared with 57% of men. 

69% of respondents oppose generating explicit images of someone without their permission, while 17% are okay with it.

For some, this fear has already become a reality:  

  • One in ten say AI has been used to generate nude or sexually explicit imagery of them without permission 
  • One in ten say someone has threatened to release AI-generated compromising or explicit imagery of them 

As one respondent recounted: 

“I had someone make fake nudes of me using AI on my photos from my social media and threaten to post them on Facebook…[it] made me more cautious about AI.”

The intimate material may be fake, but the fear, coercion, and potential for reputational, emotional, and financial damage are completely real. 

AI is making it harder to know who you’re really talking to  

The threat doesn’t stop with fabricated sexual content. AI is also making it harder to know whether the person on the other side of a screen is who they claim to be. 

Humans have always edited themselves for other people. We choose the most flattering photo, write and rewrite the text before sending it, and present our most interesting selves—especially when forming new relationships. AI dramatically expands what that kind of self-editing can look like, and people aren’t shy about using it: 

  • 54% say AI helps them present the best version of themselves  
  • 47% say using AI to present your “best self” to employers, friends, or romantic partners does not present a false identity 
  • That rises to 58% of both Gen Z and Millennials and 64% of regular AI users 

But where does enhancement end and deception begin? Is an AI-polished dating profile still authentically you? What about a message you didn’t write? A photo that looks like you, only better? 

There’s a flipside to using AI to make ourselves look or sound better: If we can do it, so can everyone else. And people are much less comfortable when they’re not the ones controlling the technology. Two-thirds (67%) worry that an online friend or romantic interest could use AI-generated images, videos, or other content to deceive them.  

Catfishing, fake photos, and lies on dating profiles aren’t new. AI just makes the deception easier. Someone’s photos, backstory, messages, and even their voice can all be faked.  

One person described leaving dating apps after realizing the person they were talking to had gone well beyond simply polishing their profile: 

“[The] dating profile had fake pictures…[it] wasn’t just making true events sound interesting and more flirty, but creating completely false photos and information. Left the dating apps again and needed to reset.”

AI can distort identity in the other direction, too. It can also create a version of us we never chose to put into the world.  

  • 76% worry about someone creating a fake profile pretending to be them 
  • 70% worry about fake images or videos of themselves being created 
  • 71% worry AI-generated content could be used to damage their reputation 
AI is a double edged tool where they feel like they can present their best selves, but also are wary of other people creating fake identities

Relationships are built on mutual trust. AI can distort both sides of the connection: who we think the other person is, and who they think we are.  

AI is quietly finding its way into the space between people  

Not all of AI’s influence on intimacy is so dramatic. Much of it happens quietly, showing up in how people communicate with each other and navigate relationships: 

  • More than one in three have used AI to help write or edit a message 
  • About one in seven have turned to it for advice about a relationship or personal decision 
  • One in ten say it has already changed how they date or communicate romantically—rising to nearly one in five among Gen Z 

The survey responses show what this looks like in real life. For example, one respondent described using AI with their partner as a way to step outside their own point of view: 

“Personally, it has helped me. We use AI in our relationship as a reflection tool, and it has sometimes helped us take on the perspective of the other.”

For another, AI helped them work through jealousy:  

“So, I used to accuse my partner, and I got really territorial about them but once I talked to AI about it, they gave helpful advice and now we are stronger than ever.”

AI is also showing up in other difficult relationship moments. One person said it helped them “stay calm and communicate” when problems came up with their partner; another said it allows them “to pause and refine [their] thoughts” before responding. 

Sometimes the role is simpler. One respondent said AI gives them “new romantic words” for their partner, while another said they’ve asked AI for advice on how to make their partner smile. AI’s growing role in relationships may be unsettling, but the benefits people describe are definitely there. 

AI isn’t just helping people find the right words. It’s also helping them decide what version of themselves to put forward in the first place. More than one in three say it’s okay to use AI to create or improve a dating profile; nearly two-thirds aren’t opposed. One respondent described using AI as a “creative advisor” to polish their profile and come up with conversation starters. 

AI doesn’t have to replace a relationship to help shape it. It can influence how people communicate, what advice they take, and how they choose to present themselves.  

AI’s intimacy problem is ultimately a trust problem 

From connection to deception to outright harm, the same question keeps surfacing: Can I trust what’s in front of me? And would I know if I couldn’t? 

Nearly nine in ten people (88%) say AI is making it harder to tell what online content is genuinely human or real. And 84% say even convincing video evidence no longer necessarily feels like proof. That uncertainty follows people into dating and relationships, where knowing what—and who—to trust is deeply personal. 

AI may make it easier to start a conversation, smooth over a hard one, or feel connected when you’re lonely. But relationships and intimacy of all kinds still come down to trust, and AI is making that trust a little harder to take at face value. 

About the research 

The research in this article is based on a March 2026 survey about AI, identity, and the collapse of digital trust and was conducted among 1,500 respondents in the United States, United Kingdom, Germany, Austria, and Switzerland. The research was prepared by an independent research consultant and distributed via Forsta. 


Something feel off? Check it before you click.  

Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.  

Available with Malwarebytes Premium Security for all your devices, and in the Malwarebytes app for iOS and Android.  

Try it free → 

Hiding Capabilities in AI Models

27 October 2026 at 12:01

Interesting research: “AI Models Can Provably Hide Arbitrary Capabilities”

Abstract: Capability evaluations aim to surface dangerous model behaviors before deployment, but their reliability depends on the assumption that hidden capabilities can be elicited. We show this assumption does not hold under adversarial conditions by constructing backdoor attacks that embed encrypted neural networks within host model weights, decrypting and executing them only upon receiving a secret trigger. Using digital lockers, these hidden circuits remain provably hard to elicit and interpret under cryptographic assumptions, even given full access to model weights, extending prior work from hiding fixed strings to arbitrary computations. We implement our proof of concept constructions in PyTorch and evaluate elicitation through fine-tuning, weight noising, gradient-based trigger search, and latent adversarial training, using a small chemical reaction prediction task as a proxy for CBRN-relevant capabilities. Our results demonstrate resistance to these methods and, together with our cryptographic guarantees, reveal a limit of elicitation-based capability audits. We release our models to support the improvement of defenses.

Learning Curves: The future of education, from classrooms to careers, in an AI-driven world

26 October 2026 at 16:00

The rapid diffusion of AI globally and the pace at which AI is developing put us at a societal crossroads. The choices we’re making now will determine who has access to AI and the opportunity it affords. There is perhaps no more important tool than our education systems for addressing the uneven diffusion of AI we’re seeing currently: national adoption runs above 70% in countries such as the United Arab Emirates and falls to low single digits across much of sub-Saharan Africa, close to a tenfold difference. 

The way we teach AI and learn with it will have long-lasting impacts on jobs, the workforce, and our broader economy. Learning Curves: Rethinking Education from Classrooms to Careers in an AI-Driven World is a collection of research-driven essays that can help guide those choices. This book brings together the body of work from the second cohort of Senior Fellows from the Microsoft AI Economy Institute (AIEI), a flagship think tank that produces research and convenes experts to generate insights into how AI is reshaping work, education, and the broader economy. 

In Learning Curves, researchers consider how AI is reshaping the earliest stages of learning and work, from K–12 classrooms and community and technical colleges to college‑to‑work transitions and entry‑level jobs, and what it will take for that transformation to widen opportunity rather than deepen divides across institutions, communities, and countries.  

Below, I share a few of my own reflections that informed my contributions to Learning Curves, a collaborative effort that wouldn’t have been possible without the truly talented, diverse cohort of researchers who contributed to this book.  

The good, the bad, and the ugly: Laying the foundation for AI in K–12 classrooms

Before delving into the specifics of how to incorporate AI in classrooms, we need to ask ourselves whether we’re teaching for knowledge, or for learning.  

The book, the calculator, the personal computer, the internet, the search engine, and the smartphone all arrived in classrooms carrying real promise alongside the worry that they would hollow out young minds. Usually the truth landed somewhere in between, and where it landed depended less on the tool than on the choices the adults made about how to use it. 

The fact is that the AI-native generation is already here, and its members are in classrooms around the world. More than half of US teenagers already use AI chatbots for schoolwork. I’ve personally seen the promise of AI as a force for good in education up close in my own classroom, where I teach a computer science class to elementary school students.  

But of course, the good is only part of the story. We can’t shy away from the downsides of incorporating AI into classrooms. While AI can help with accessibility and individualized learning, it can also create over–reliance, contribute to student cheating, or prevent students from recognizing when information may be false. 

The rapid deployment of AI in K–12 classrooms needs to come with a sober assessment of how that technology impacts all students. This assessment must go beyond the technology itself to encompass how students, teachers, parents, and society use AI.   

AI literacy is only part of the solution

If classrooms are where students learn how to think, teachers are the conduit through which this learning happens. In Learning Curves, Joseph Orero, Senior Researcher in AI at Strathmore University’s School of Computing and Engineering Science, posits that teachers aren’t resistant to AI in classrooms; they just need proper training to help them adequately adapt and teach their students critical skills. His research contribution explores game-based learning with AI-enabled African languages. 

AI usage and adoption worldwide are also dependent on accessibility. Another chapter of the book looks at barriers and opportunities in Arabic education and finds that the primary barrier teachers encountered when introducing AI writing assistants into classrooms was Arabic digital literacy, particularly students’ typing ability.  

Researchers often circled around a similar theme: there is no one-size-fits-all approach to developing AI competency; instead, such an approach must be sensitive to local knowledge and contextualized teaching and learning practices. This means that teachers, in turn, must have training that makes sense for the unique contexts in which their students are learning.  

Frank Nagle, now Microsoft’s Chief AI Economist, Sarah Rodriguez, Associate Professor of Engineering Education at Virginia Tech, and other researchers in Learning Curves make the case that, in many ways, nontraditional pathways such as apprenticeships and two-year-degree programs, particularly those that are virtual, are more nimble and thus better able to adapt their curricula to the rapidly changing field of AI.  

AI Is taught in the classroom, but then what?

Education has never been about simply preparing people for the future of work so they can thrive in the labor market. When considered holistically, it is about teaching students not what to think but how to think. In our AI era, education is one of the core institutions through which the future of work will be built, distributed, and made more (or less) equitable. Successful AI integration remains human-centered by focusing on organizational change, durable human skills like empathy and judgment, strong employer partnerships, and learner needs. 

As research from Laura Nuriski, Head of Program on the Future of Work at the Centre for European Policy Studies (CEPS), highlights, access to AI alone does not ensure successful integration. Technology transfer, data infrastructure, organizational readiness, and a human-centered approach to building and deploying AI are also key indicators of success.  

Whether we’re talking about the classroom or the boardroom, it’s worth keeping in mind that AI tends to do the most good when it strengthens human capability and the most harm when it substitutes for it. That holds as true in a fourth- grade reading lesson as in a software team or a hospital ward. 

The children in our schools deserve tools that serve their learning rather than stand in for it, and that is within our power to provide. Our most successful future with AI will be one that is human-centered, inclusive, and designed to help people thrive. 

The post Learning Curves: The future of education, from classrooms to careers, in an AI-driven world appeared first on Microsoft On the Issues.

AI Halloween videos: Who’s getting your photos?

26 October 2026 at 13:51
.kadence-column480165_4ecc5f-ac > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column480165_4ecc5f-ac > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column480165_4ecc5f-ac > .kt-inside-inner-col{flex-direction:column;}.kadence-column480165_4ecc5f-ac > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column480165_4ecc5f-ac > .kt-inside-inner-col{background-color:#ffe5e5;}.kadence-column480165_4ecc5f-ac > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column480165_4ecc5f-ac{position:relative;}@media all and (max-width: 1024px){.kadence-column480165_4ecc5f-ac > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column480165_4ecc5f-ac > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}

In this article

  • Some Halloween AI video sites ask for personal photos without clearly identifying who runs them.
  • Outside AI providers may also receive your uploads.
  • Before uploading, check who gets your photos, how they’re used, and when they’re deleted.

This Halloween, AI is doing the costumes. Upload a photo and you can become a vampire, surround your dog with pumpkins, or star in a viral “zombie love story:” Your partner has turned, you lower the gun, and the zombie’s leap ends in a hug.

But before you upload, do you know who will receive your photos?

In September, we wrote about more than 100 subscription sites built from the same cheap website kit. With Halloween approaching, we’ve found the same approach being used to sell AI Halloween videos.

We found no malware or phishing on the sites we examined. What concerned us was how little we could establish about who operated them and who would be responsible for the photos people uploaded.

Polished, friendly, and anonymous

These sites look professional and sound reassuring. They promise privacy, have FAQs and refund policies, and some even add consent checkboxes for photos of children. One calls itself “an independent tool with no ties to TikTok or any film studio.”

What they don’t tell you is who is behind them. On the sites we checked, we found no company name, address, or named operator, only a support email on the site’s own domain.

Where do your photos go?

These sites ask for clear, well-lit photos of you, your partner, your friends, your pets, and, with a parent’s permission, your children.

The sites we looked at say they rely on outside AI providers to generate the videos. That means you’re trusting both the website collecting your photos and the providers processing them.

Wherever you upload photos, check who can access them and how they can be used. Scammers can use someone’s likeness to create fake intimate images and demand money to keep them private. In our Face Value report, 10% of respondents said someone had threatened to release AI-generated explicit content of them. We found no evidence of that happening through these Halloween sites, but it’s a reason to be careful where you share your photos.

The sites promise to delete uploads within days, and we have no evidence that they fail to do so. But we couldn’t independently verify those promises. Without an identifiable operator, it’s harder to establish who is accountable for handling your photos and responding to deletion requests.

Google sign-in doesn’t identify everyone handling your photos

These sites use the real Google sign-in window, so you type your password into Google, not the video site. But using Google to sign in doesn’t mean Google endorses the service or guarantees its privacy promises.

Click the app name in Google’s sign-in window and you’ll see Developer info. On one site we checked, the only contact listed was a Gmail address. We saw the same with the September sites. A Gmail address alone doesn’t establish wrongdoing, but it does little to identify the operator.

On another, Google said you were signing in “to continue to neon.tech.” Neon is a legitimate database company and authentication service provider. Its name appearing here doesn’t mean it operates or endorses the Halloween video site.

Login providers can handle Google sign-in on a site’s behalf. Depending on the setup, Google may display the provider’s domain instead of the video site’s name. Here, the sign-in screen gave visitors no clear indication of who operated the Halloween service.

Built from a kit, recycled for the next trend

Sites like these don’t necessarily take a team or months of work. Some use the same $249 website kit we wrote about in September, which promises you can “launch your AI product in one hour.” On one Halloween site, the builders hadn’t even cleared out the kit’s sample content. Hidden in the page was a note saying it was “a demo site” for the template, along with placeholder links like “your-app-name.”

Another site’s code contained remnants of an AI rap and dance video maker, including a “hotel lobby” stage, a recording studio, and AI-written raps. Those remnants suggest the site uses code also intended for other AI video services.

Using a website kit isn’t itself suspicious. But a polished page can be quick to assemble, so its appearance tells you little about the business handling your photos.

Take your time before paying, too

On one site, a single 15-second zombie clip cost $9.99. The pricing page nudged visitors toward bigger packs, bringing the advertised price per video down to $2.99. But that lowest price meant spending $199 on enough credits for roughly 66 zombie films. There were monthly and yearly plans too, costing up to $600 a year.

One site also used countdown offers, reminders in the browser tab, and claims about how many people had made films that day to encourage visitors to buy.

There’s no need to rush. Check the payment terms as carefully as the privacy policy. The sites themselves warn that AI can change faces, so your video may not look much like you. Under the policies we reviewed, credits are returned if a video fails to generate. But if you simply don’t like the result, trying again costs more credits.

Subscriptions renew until you cancel, yearly plans are charged in one go, and some credits expire before you use them.

What to check before uploading your photos

Whichever tool or platform you choose, make sure you’re comfortable with how it will handle your data, your photos, and your payment info.

  • Find out who runs the service. Look for a named operator and clear contact details. If you can’t establish who would be responsible for your photos, consider another service.
  • Check where your photos go. Read the privacy policy for information about outside AI providers, retention periods, and whether uploads can be used for AI training.
  • Look for a deletion process. Check how to request deletion and whether the policy explains what happens to copies held by outside providers.
  • Be especially careful with children’s photos. A parental consent checkbox doesn’t explain how a service will protect them. Only upload other people’s photos with their permission.
  • Read Google’s sign-in window. Check the developer details and any permissions requested. Google sign-in doesn’t replace checking the service itself.
  • Ignore countdowns and check payment terms. Take time to understand the full cost, credit expiry, and whether your purchase starts a subscription.
  • Review your Google connections afterward. Remove services you no longer use from your Google account’s third-party connections. This doesn’t cancel subscriptions or delete photos or other data already held by the service.

How Malwarebytes can help

If you have concerns about a website, Malwarebytes Scam Guard can help you assess it. Malwarebytes Browser Guard helps block known scam and malicious sites.

But these tools can’t verify a service’s photo deletion promises. You should still check who operates it and what its privacy terms say before uploading.


Something feel off? Check it before you click.  

Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.  

Available with Malwarebytes Premium Security for all your devices, and in the Malwarebytes app for iOS and Android.  

Try it free → 

❌