❌

Normal view

Big Tech sues over California plan to limit kids’ scrolling

6 November 2026 at 16:06
.kadence-column485324_750a90-49 > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column485324_750a90-49 > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column485324_750a90-49 > .kt-inside-inner-col{flex-direction:column;}.kadence-column485324_750a90-49 > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column485324_750a90-49 > .kt-inside-inner-col{background-color:rgba(255, 229, 229, 0.83);}.kadence-column485324_750a90-49 > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column485324_750a90-49{position:relative;}@media all and (max-width: 1024px){.kadence-column485324_750a90-49 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column485324_750a90-49 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}

In this article

  • California wants to switch off autoplay and personalized feeds for under-16s.
  • Google, Meta, and TikTok are suing to stop the restrictions.
  • Age checks could raise privacy concerns for adults, too.

Google, Meta, and TikTok filed separate federal lawsuits on November 4, challenging Assembly Bill 1709, which Governor Gavin Newsom signed in September.

The companies argue that the law, due to take effect in 2027, interferes with free speech, overrides parents’ decisions, and conflicts with federal protections for online platforms.

AB 1709 prohibits covered platforms from providing California users under 16 certain

“psychologically exploitative features intended to maximize engagement that foreseeably lead to compulsive use.”

The law specifically includes personalized “addictive feeds” and autoplay. It also allows the attorney general to define additional features through regulations.

It would not ban children from using the platforms. They can keep their accounts if the platform removes the restricted features. Otherwise, the platform must delete the account and associated personal information.

The law also requires age verification before providing the restricted features. The law doesn’t stop children from searching for videos, following creators, or communicating privately. It makes exceptions for certain search-based results, content that a user explicitly requests, and direct private messages, subject to conditions.

California’s argument is that harm is not limited to what children see. It can also arise from how a service encourages them to keep using it, through personalized recommendations and features such as autoplay.

The idea behind the law is straightforward: Instead of relying entirely on teenagers to recognize when to stop, require platforms to remove some of the mechanisms designed to keep them engaged.

The companies’ objections

The companies’ objections fall into several related categories.

Meta argues that deciding which posts to show, and how to arrange them, is protected editorial judgment under the First Amendment. Its complaint accuses California of attempting to appoint itself the

“editor, curator, and controller of online speech.”

TikTok makes a similar argument about its For You feed. It says selecting and arranging videos creates a curated product protected by free-speech rights, not merely a mechanism that the state can redesign at will.

Google likewise argues that YouTube’s recommendations help users find relevant, appropriate material among its vast collection of videos. It also defends autoplay as useful for watching content intended to be viewed in sequence.

The central disagreement is whether these are harmful product features that California can regulate, or editorial decisions protected by free-speech rights. California describes them as potentially harmful product design; the companies describe them as protected decisions about publishing speech.

The companies also raise parental control. Google says parents are best placed to decide what is appropriate for their families. TikTok points to its existing teen-account safeguards and Family Pairing controls, arguing that the law restricts free expression while taking decisions away from parents. Meta adds that personalized features can help deliver age-appropriate experiences.

The business model

There is also a commercial interest at stake: engagement. How often people return, how long they stay, and how much they interact all matter to the platforms’ businesses.

Meta’s annual report says it generates substantially all its revenue from advertising. It also says that changes to its content displays and product features can affect time spent, user engagement, and financial results. That doesn’t establish why the companies sued, but it helps explain why restrictions on recommendations and autoplay could have financial consequences.

If removing these features leads people to spend less time on a service, it could mean fewer opportunities to show ads. Compliance would also require product and operational changes, such as checking users’ ages and providing a different experience to those under 16.

Youth is the future. Big Tech is very much aware of this. Meta’s annual report identifies youth as an investment priority and describes attracting and retaining users as a competitive objective. Restrictions affecting how young people join and use a platform could affect its longer-term audience strategy, too.

What the future will bring

California is challenging an important part of the attention-based business model. Meta’s annual report warns investors that regulation affecting how it displays content or serves younger users could affect user growth, engagement, and financial results.

And then there’s the matter of age verification. The required age checks could affect adults as well as children: a service must verify users’ ages before providing the restricted features. Depending on how the checks work, this could involve sharing age-related information, raising privacy concerns and creating another opportunity for sensitive data to be exposed in a breach.

If it were up to me, platforms would stop designing for compulsive use, whatever the user’s age. Adults deserve a healthier online experience too. Applying those protections to everyone would also remove the need to check someone’s age before deciding whether they can use these features. Platforms might lose some advertising opportunities, but time spent online should not be the only measure of a successful service.


Scammers don’t need to hack you. They just need you to click once. 

Malwarebytes Identity Theft Protection catches suspicious activity before it becomes a problem.

Attacks on supermarket and blood storage systems prompt US warning

6 November 2026 at 13:02

Attackers don’t have to steal information to cause serious harm. Sometimes, changing a temperature setting is enough.

On November 5, the US Cybersecurity and Infrastructure Security Agency (CISA), Federal Bureau of Investigation (FBI), and three other federal agencies issued a warning urging operators to secure industrial refrigeration and cold-chain monitoring systems.

The warning follows cyberattacks on supermarket refrigeration systems across Europe. Separately, France’s national blood service confirmed that the monitoring and control systems at three of its cold-storage sites had been affected. Staff intervened before any blood products or samples were compromised. The incident showed how a connected cooling system can put essential supplies at risk.

On October 13, after the first attacks in France, refrigeration supplier Danfoss advised its Dutch customers to disconnect their systems from the public internet and reconnect only through a secure network.

A Danfoss spokesperson told NOS that most stores followed the advice. When similar attacks reached the Netherlands on November 2, major supermarket chains were reportedly unaffected. At least 17 businesses, mainly butcher shops and small neighborhood stores, had their refrigeration systems compromised.

Danfoss said that the affected systems were still accessible through unsecured connections and used default passwords. The spokesperson said the attacks could have been prevented if the recommended precautions had been taken.

CISA and its partners warned that attackers may exploit authentication bypass flaws, code-injection vulnerabilities, or weak configurations in refrigeration controllers. Successful attacks could let them change temperatures or force equipment into continuous heating or defrost cycles.

The agencies recommend reducing that risk by keeping control panels off the public internet, isolating operational equipment from business networks, changing default passwords, using strong authentication, patching firmware, and replacing unsupported devices. They also recommend setting safe operating limits and alerts for temperature changes outside those limits.

What about home appliances?

You don’t need an industrial refrigeration unit to adopt some of these precautions.

  • Check whether you need remote access. If you never use a device while away from home, disable that feature. Check the manufacturer’s instructions first; disabling remote access may also affect alerts or smart-home integrations.
  • Check who can access the appliance, including suppliers, and how that access is protected.
  • Change default passwords and secure the associated account. Use a strong password and enable two-step verification wherever the appliance or app supports it. Protecting the app account matters as well as protecting the appliance itself.
  • Keep firmware and apps updated. Turn on automatic updates where available, and don’t ignore manual update prompts.

CNET Editors' Choice Award 2026

“One of the best cybersecurity suites on the planet.” 

According to CNET. Read their review →


Phone return scams: where a real delivery and a fake return end up in a bill for you

5 November 2026 at 23:18

A caller offers you a free phone upgrade or an exclusive deal from your mobile provider. A new phone arrives at your home. So far, everything seems to check out.

Then comes another call: There’s been a shipping mistake. You received the wrong phone, and the company needs you to send it back. You send it back, but the phone never reaches your provider, leaving you with a large charge or long-term contract to pay.

Now police are warning about this scheme after residents lost devices and were left facing the associated payments.

How phone return scams work

The scam usually starts with a call from a spoofed number. In the US we’re seeing several examples in anonymized Malwarebytes Scam Guard records of the impersonated company being Canadian mobile provider Rogers.

The Canadian Anti-Fraud Centre warns:

“After collecting personal information required for credit checks, they’ll order a new phone in your name.”

Next, a genuine device arrives through a legitimate delivery service. That delivery makes the next part of the story easier to believe.

The caller gets back in touch and claims something went wrong. Perhaps the company sent the wrong device, or an extra phone arrived by mistake. To put things right, you need to send it back using the label or shipping QR code they provide.

The shipping label is the real trick. Rather than directing the package to the provider’s returns facility, it sends the device to an address chosen by the criminals.

The result: You no longer have the phone, but your provider has not received it back. Victims can be left facing a contract, financing agreement, or monthly payments for the missing device.

How to stay safe

The most important protection against most types of scams is having someone you can trust and help you decide whether something is a scam. Malwarebytes Scam Guard can be that partner if you’re on your own.

You don’t need to decide on the spot about whether a caller sounds convincing. Break the conversation and verify the offer separately. Pause and check if you encounter any of the following:

  • An unexpected call offering a free phone, loyalty reward, or unusually attractive upgrade.
  • A caller asking for personal, financial, or account information to arrange the offer.
  • A follow-up call claiming the wrong device was shipped or that another delivery mistake needs correcting.
  • Instructions to use a return label or QR code supplied by that caller.
  • A return destination that you have not confirmed directly with your provider.

If you’ve already sent a phone, contact your mobile provider immediately using verified contact details. Explain that you believe you were targeted by a phone return scam, identify the affected orders, and ask for a fraud investigation.

If you shared your account password or PIN, change it through the provider’s official channels. Rogers advises customers who disclosed their credentials to reset them and contact customer service to check for unauthorized transactions.

Keep the evidence: messages, emails, the shipping label, tracking details, order confirmations, bills, and a timeline of the calls. These records can help support a billing complaint and fraud report.


Something feel off? Check it before you click.  

Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.  

Available with Malwarebytes Premium Security for all your devices, and in the Malwarebytes app for iOS and Android.  

Try it free → 

NIKKE PC launcher compromise put players’ passwords and personal files at risk

5 November 2026 at 23:06

Players of Goddess of Victory: NIKKE are being urged to check their PCs after attackers tampered with files used by the game’s Windows launcher. Opening the launcher could allow malicious software to run, potentially exposing much more than a player’s game account.

The incident occurred as part of a supply-chain attack, where services or software used by the company in question is compromised. In practice, this meant that instead of persuading players to download a fake game or install a suspicious add-on, the attackers compromised resources used by the legitimate launcher. Players could therefore encounter the threat simply by opening software they already trusted.

Game publisher Level Infinite has released fixes and added a malware-checking feature to the official PC client. However, fixing the delivery mechanism does not undo an infection, nor does it recover passwords and other information that may have been stolen.


Breaches happen every day. Don’t be the last to know.


Independent researcher MotherSphere identified malicious code in four JavaScript files hosted on Level Infinite’s official content delivery network (CDN).

Players should be aware of a discrepancy in the published timelines. Level Infinite says malicious-program distribution began on October 30, while MotherSphere reports evidence of the remote-control agent running as early as October 23.

According to the researcher’s analysis, the distributed remote-control agent supported commands to:

  • Run programs and system commands.
  • Browse folders and download files.
  • Take screenshots.
  • Retrieve saved NIKKE login credentials.
  • Collect browser passwords and cookies.
  • Search for developer credentials, API tokens, and other secrets.
  • Collect cryptocurrency wallet-extension data.

The number of compromised PCs and the full extent of any data theft remain unclear.

How to stay safe

Mobile-only players are not affected, according to Level Infinite, so they do not need to take any additional security measures.

Level Infinite says it replaced three abnormal script files early on November 4, then refreshed the CDN’s cache for the remaining file later that day. MotherSphere subsequently reported that all four files were clean on the four CDN servers checked.

If you opened the Windows launcher during the period identified above, take the following steps.

  • Close the launcher and check your PC. MotherSphere’s report includes user-reported Malwarebytes detections for traces associated with the attack.
  • Follow the removal instructions published by NIKKE carefully.
  • Secure your accounts from a clean device. Do not change passwords on a computer that may still be compromised.
  • If a cryptocurrency wallet or its recovery phrase may have been exposed, use a clean device to move funds to a newly created wallet with a new recovery phrase.
  • Level Infinite asks players who believe they were affected, including those experiencing problems with external accounts or financial losses, to contact its customer support team, so keep relevant records without handing over personal information.

Please note that the NIKKE wiki’s unofficial cleanup guidance recommends scanning with Malwarebytes. Although the guide describes this as a one-time free option, Malwarebytes Free lets you continue running manual scans and removing detected malware after the Premium trial ends. The trial provides additional features, including real-time protection, so decide what is best for you.


From reporting threats to removing them.

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

Scammers use AI-generated images of missing pets to extort owners

5 November 2026 at 22:34

When your pet goes missing, it can be totally heartbreaking.

So hearing that they’ve been found is no doubt very welcome news. Even better to see a photo of them looking safe and well.

But while the photo may look exactly like your pet, that doesn’t mean the person who sent it has your pet or even ever saw it.

The BBC reports how criminals are sending owners AI-generated images of their missing pets, demanding money for their return, and sometimes threatening to harm the animals when owners refuse to pay.

The BBC interviewed two targets of this scam who were both contacted after posting a missing pet message on social media. The scammers sent them pictures of their beloved pets and demanded a ransom for their safe return.

Messages like these exploit two powerful emotions in quick succession: relief that a beloved pet has been found, followed by fear that something terrible will happen unless the owner acts immediately.

The scam typically follows this pattern:

  • A scammer finds a missing pet appeal, which is typically posted to social media or local sites with an accompanying photo and contact details.
  • The scammer contacts the owner and claims to have found the animal. An image fabricated with the help of AI makes the claim appear more convincing.
  • They ask for money which may be described as a reward or as payment for emergency treatment.
  • They add pressure. They might refuse to meet until payment arrives, or threaten to sell or harm the pet.

Our data backs this report up. Over the last month, people anonymously submitted three distinctive types of pet related scam attempts to Malwarebytes Scam Guard:

  • “We found your missing cat” message, with photos: Someone claimed to have found a user’s missing cat and had images of it.
  • Found pet callback lure: A voicemail claimed to have found a lost cat and supplied a callback number.
  • Humane Society impersonation and payment demand: A caller claimed a missing cat needed emergency surgery, and demanded successive Zelle payments.

How to stay safe

Sadly, while it can be very useful to use social media to retrieve lost pets, it also attracts scammers and other abuse.

You don’t have to stop asking for help online, but you can put some safeguards between an unexpected message and any payment.

  • Keep some identifying details private. Leave a distinctive feature out of the public description so you can ask a supposed finder about it later.
  • Do not pay in advance to secure a reunion. Be particularly wary of someone who insists that you send money before they will let you see the animal. Arrange any legitimate handover in a safe, public location, and verify that it is your pet before paying a reward.
  • Verify veterinary claims independently. If someone says your pet is at an animal hospital, find the hospital’s contact details yourself and call it directly. Do not rely on the number or payment link in the message.
  • A second pair of eyes can help you assess a demand without the same emotional pressure. Malwarebytes Scam Guard can help you identify whether a message might be a scam and how to proceed.
  • If someone is threatening your pet, remember that when they make threats to your pet, it is very likely they don’t have a clue where it is either, so don’t let them extort you.

Something feel off? Check it before you click.  

Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.  

Available with Malwarebytes Premium Security for all your devices, and in the Malwarebytes app for iOS and Android.  

Try it free → 

Vizio, Samsung smart TVs seem to ignore tracking opt outs

5 November 2026 at 13:10
.kadence-column484998_59baca-d5 > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column484998_59baca-d5 > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column484998_59baca-d5 > .kt-inside-inner-col{flex-direction:column;}.kadence-column484998_59baca-d5 > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column484998_59baca-d5 > .kt-inside-inner-col{background-color:rgba(255, 229, 229, 0.83);}.kadence-column484998_59baca-d5 > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column484998_59baca-d5{position:relative;}@media all and (max-width: 1024px){.kadence-column484998_59baca-d5 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column484998_59baca-d5 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}

In this article

  • Automatic Content Recognition (ACR) sends viewing data from your smart TV to third parties.
  • Vizio and Samsung TVs both appeared to send this data even when researchers opted out of ACR.
  • Only four out of eight smart TVs appeared to completely honor ACR opt-out.

If you thought that opting out of surveillance on your smart TV would give you your privacy back, think again.

A study by researchers at Northeastern University found that some smart TVs still seem to send information about what you’re watching to third parties, even after you pressed the opt-out button.

The study, ‘Watching the watchers‘, tested twelve smart TVs from ten manufacturers to find out how well they respected opt-outs from automatic content recognition (ACR). ACR is a TV feature that captures audio and/or video content from smart TVs and uploads it to a third party (typically the TV manufacturer).

The third party converts this content into digital fingerprints to understand what you’re watching, and can then use it to send targeted advertising or allow others to do the same. It’s on most if not all smart TVs, and 82% of US households had a smart TV as of last year.

The test took in the eight operating systems behind roughly 95% of US smart TVs, and ran ten viewing scenarios on each of them. These ranged from viewing antenna TV through to viewing via screen mirroring from another device. The researchers tested viewing the first-party streaming services provided free with the manufacturers’ operating systems, along with sessions using third-party streaming apps. And they tested sessions where the TV was connected to another device via its HDMI port.

The study ran all of its tests both with ACR left on, and with the opt-out setting selected. The whole test involved over 5,000 automated sessions.

Vizio continued to send 100% of what looked like traffic when viewing its first-party streaming services and antenna-based TV services, even after people had opted out, the study said. It also sent the same amount of traffic when idle. However it didn’t send any ACR traffic for third-party streaming data, according to the report.

Samsung did appear to leak some traffic from third-party streaming services after the researchers opted out of its ACR function. They tested 30 runs of Samsung’s built-in streaming service after opting out of ACR, and found that it still showed traffic “consistent with ACR”.

After opt-out, the Samsung TV’s Tizen OS seemed to send ACR-related traffic about Netflix in 7% of runs, YouTube in 10% of runs, and Tubi TV in 20%. It sent ACR 60% of the time from HDMI sessions. Like the Vizio TV, it also sent ACR traffic for all of its first-party streaming sessions.

Late last month, a researcher reverse-engineered a Samsung Smart TV and cast doubt on whether disabling ACR worked on the device.

There was good news, though. Four smart TV operating systems went completely silent after the researchers turned off ACR: LG’s WebOS, Sony’s Google TV OS, Amazon’s FireTV OS, and Supersonic’s VIDAA OS.

Encryption is a research challenge

Vizio agreed to pay $2.2 million in a 2017 FTC settlement over charges that it collected viewing histories on eleven million smart TVs without user consent. At the time, it agreed to allow people to opt out of ACR.

The Vizio TV that the researchers tested sent traffic to Kinesis, an Amazon-run data ingestion service that the manufacturer uses to analyze data from its smart TVs. The researchers noticed no dip in traffic to this domain when they opted out of ACR on a Vizio TV. They said:

“The opt-out setting has no observable effect on traffic sent to this endpoint. However, we cannot inspect the payload due to encryption so we cannot confirm whether this violates the FTC settlement.”

That’s a challenge to this research because most smart TVs encrypt their ACR traffic, including Samsung. So the researchers had to infer that this was ACR traffic based on signals such as where it was being sent, along with timing, volume, and protocol details.

One exception was Supersonic’s VIDAA OS, which sent ACR data to servers unencrypted. The servers responded unencrypted with a genre for what they recognized. Anyone watching the network could see it all, they warned. And because the servers didn’t require a login at the time of the test, over 57 million ACR detection results from other people’s TVs were accessible.

Vizio’s first-party streaming service WatchFree+ also dropped unencrypted titles of any show or channel being watched into online communications with the free TV service provider. There’s no way to turn that off, the researchers warned.

Walmart acquired Vizio for $2.3 billion in 2024, partly to help “advertisers to meaningfully connect with customers at scale and boost product discovery”.

The retailer also runs Walmart Connect, a retail media business that uses its customers’ data to help other businesses target them with ads.

Walmart was particularly interested in Vizio’s advertising business it, said at the time:

“Pairing it with Walmart Connect will be impactful and allow us to invest in our business even further on behalf of our customers.”

What smart TV owners can do

What can you do to protect yourself from a smart TV that might be sending your viewing data elsewhere? The researchers have some suggestions:

  • WebOS (LG), Fire TV OS, Google TV on Sony, and VIDAA OS on Supersonic all appeared to honor ACR opt-out, so selecting it on these TVs should be safe.
  • Disconnect the TV from the internet and use an external streaming device. That way the TV can’t send back data, even if it picks it up from the HDMI connection.
  • Use a blocklist. This takes a little more technical knowledge. If you run an internet router that can accept blocklists, then you can add a list of known ACR endpoints that will stop your TV’s traffic reaching them. The researchers provide one here.

Stop threats before they can do any harm.

Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →

The fake $750 Apple Cash reward that pays out nothing

4 November 2026 at 19:49
.kadence-column484244_4b5e59-45 > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column484244_4b5e59-45 > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column484244_4b5e59-45 > .kt-inside-inner-col{flex-direction:column;}.kadence-column484244_4b5e59-45 > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column484244_4b5e59-45 > .kt-inside-inner-col{background-color:rgba(255, 229, 229, 0.83);}.kadence-column484244_4b5e59-45 > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column484244_4b5e59-45{position:relative;}@media all and (max-width: 1024px){.kadence-column484244_4b5e59-45 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column484244_4b5e59-45 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}

In this article

  • A fake $750 Apple Cash offer funnels users toward app and game promotions
  • Its device checks, countdown, and “spots left” claims aren’t real
  • Users get no reward and may share information or spend money in games

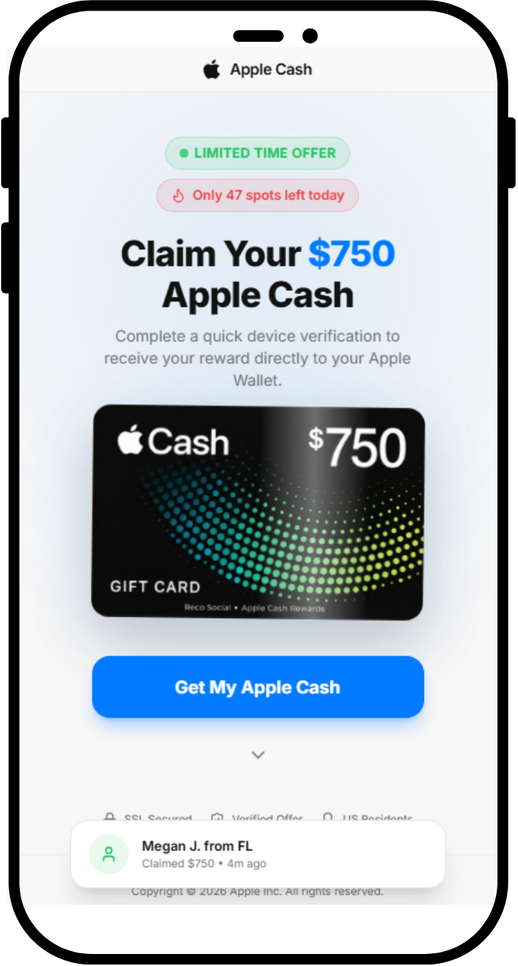
A page we found promises a $750 Apple Cash reward if you complete a quick “device verification.” There is no reward, and the page does not verify your device. Instead, it sends you to app offers through affiliate tracking links.

The page is not affiliated with Apple. If you’ve landed on a page like this, close it.

The fake page promises $750 in Apple Cash

Why Apple makes such good bait

Apple is one of the world’s most recognized brands, and scammers use that familiarity to make fake offers seem credible. Apple’s own scam guidance lists fake promotions offering free products and prizes among common tricks.

Current Apple news gives scammers useful cover. The new iPhone Duo is in the headlines, and we recently found a fake preorder page whose code tried to exploit older iPhones as soon as the page opened. With the iPhone Duo starting at $1,999, a promise of $750 in Apple money may catch people’s attention.

The word “verify” may also sound timely. Starting November 9, Green Dot Bank, which issues Apple Cash, will require some users to verify their identity before they can reload their balance. A fake page asking people to “verify your device” to get Apple Cash may seem more plausible in that context.

Apple Cash isn’t an Apple Gift Card

The page blurs two different things:

  • Apple Cash is money you send, receive and spend through Apple Wallet.
  • An Apple Gift Card adds money to your Apple Account balance for Apple purchases.

Apple warns that its gift cards can only be used for Apple purchases, and that someone asking you to pay them with one is probably a scammer. But neither Apple Cash nor an Apple Gift Card comes from a website that “unlocks” it after you install an app.

The fake site leans hard on Apple’s name. It calls the app it promotes an “Official Apple Partner” that is “Verified by Apple Cash,” and its footer claims “Copyright © 2026 Apple Inc.” None of that is true.

A “verification” that verifies nothing

We looked at the code behind the page’s three steps: Eligibility Check, Verify Device and Claim Reward.

The eligibility check is a timer. The four items that tick green, including “Location: United States,” are just labels that light up on a schedule. The page never checks where you are or what device you use. Everyone passes in under four seconds.

It tells users to download an app for “device verification”

The device verification is an app install. The page tell users to download an app called Reco Social, then tells them to create an account, and install and play a game. We found no evidence that Reco Social or its developer created or operated the fake reward page.

When you tap Download & Open App, the page opens a link in a new tab. Five seconds later, it starts showing “Verifying device…”. Nothing is being verified. The page has no way of knowing whether you installed anything, created an account or played a game.

The reward is the same link again. Ten minutes after you tap the button, the page moves on by itself and announces “Device Verified Successfully,” whether or not you installed anything. The Claim Your $750 button doesn’t add anything to your wallet. It opens the same link as the download button.

Fake urgency

The page is built to stop you from thinking too long:

  • “Only 47 spots left today” always starts at 47. It drops by one every 30 seconds and stops at 3, so it never runs out.
  • The “claimed $750” pop-ups are generated at random from a list of 15 first names and 15 US states, with a random “minutes ago.” Every visitor sees a new one every 8 to 15 seconds.
  • The 10-minute “Session Expires” countdown doesn’t end anything when it hits zero.

Who gets paid?

The download button doesn’t go directly to the App Store. It first goes through a tracking link on taprkr[.]com. These links can be used in affiliate marketing to credit clicks and installs to whoever sent the traffic.

The link carries a label, “recosocial-cpr.” CPR can stand for “cost per registration,” a deal where a promoter earns money when someone signs up. That label alone doesn’t confirm how this offer pays.

The destination varied in our tests. The link led to an offer labeled “playful-rewards-revshare” on iPhone and an ad network on PC. A revshare (revenue share) deal usually pays the promoter a cut of what users later spend, such as on in-app purchases.

The tracking labels suggest that promoters may earn money from registrations or spending in promoted apps, but they don’t confirm how this offer pays. Users don’t receive the promised $750.

We have no evidence that Reco Social or any app at the end of these links is behind the fake Apple page. Deceptive affiliate promoters can send traffic to legitimate apps because they may earn money for installs or signups regardless of how users were persuaded.

The page also loads a TikTok tracking pixel, which advertisers use to measure campaigns. This could mean the operators are measuring traffic from TikTok, but it doesn’t show where the link was shared.

What’s the harm if it’s “just” an app install?

Compared to a page that steals passwords or card numbers, this one can look harmless. But you still pay a price:

  • You give away personal data. Creating an account means handing over your email address, phone number or social login to a service you only signed up for because of a lie.
  • You may be encouraged to spend. Many mobile games make their money from in-app purchases, and with a revenue-share deal, someone profits when you spend.
  • You may be set up for the next scam. Fake reward offers often come in chains. The next one may ask for your Apple Account details, card number, or a “small processing fee.”
  • You lose time chasing a reward that was never coming.

How to stay safe

Keep these points in mind if you come across an Apple Cash or other Apple-related offer online:

  • Don’t expect an app install to pay you in Apple Cash. Be suspicious of any “Apple” offer that asks you to download a third-party app, create an account or play a game to receive Apple Cash or an Apple Gift Card.
  • Verify Apple Cash only in Settings. The real identity check is in Settings > Wallet & Apple Pay > Apple Cash. Treat any website or message that asks you to “verify” Apple Cash somewhere else as suspicious.
  • Be extra careful around launches and holidays. iPhone Duo deals, giveaways and preorder offers will keep circulating. Go to apple.com or the Apple Store app yourself instead of following links.
  • Check the address bar. Apple’s website is apple.com. A page on a domain like applecashgiftcard[.]com is not Apple, however much it looks like it.
  • Treat countdowns and “spots left” as red flags. Fake urgency is there to rush you past the moment you’d ask, “Why would anyone give me $750 for this?”
  • Already installed an app from a page like this? You didn’t earn a reward, so you can delete the app. Delete any account you created through it, cancel any subscriptions in your App Store settings, and change that password on any other accounts where you reused it.
  • Never pay with gift cards, and never pay to receive a prize. As the FTC puts it, “No real business or government agency will ever tell you to buy a gift card to pay them.” If a “reward” asks for a fee, your card details or gift card codes, it’s a scam.
  • Report it. Apple asks people to forward suspicious Apple-themed messages to reportphishing@apple.com. You can also report the ad or post to the platform where you saw it and, in the US, report fraud at ReportFraud.ftc.gov.

How Malwarebytes helps

Malwarebytes can help block known scam pages. Use Browser Guard with a supported browser, or Web Protection in Malwarebytes for iOS when browsing with Safari.

If you’re not sure whether a link, text or offer is real, you can ask Malwarebytes Scam Guard before you click.


CNET Editors' Choice Award 2026

“One of the best cybersecurity suites on the planet.” 

According to CNET. Read their review →


mSecure tells users to change passwords but won’t say why [updated]

4 November 2026 at 18:02

Password manager mSecure has warned current and former customers to protect the confidential information stored in its app after detecting “suspicious activity.”

But its advice about what users should do comes without an explanation of what happened or whose information might be at risk.

The warning leaves users to decide whether to replace credentials—and whether it’s safe to store replacements in mSecure.

While those are perfectly reasonable questions, mSecure’s warning does not answer them.

In an email published by The Hacker News and sent to customers on November 3, mSecure’s developer, mSeven Software, said:

“mSeven Software (‘mSeven’) recently learned of suspicious activity associated with the mSecure password management application. In response, mSeven quickly launched an investigation, took steps to mitigate the issue, and engaged external cybersecurity experts to assist.”

The notice recommends that customers “immediately take steps to protect all confidential information” stored in mSecure. Those steps:

“may include changing passwords, resetting or re-enrolling two-factor authentication methods, or removing existing passkeys.”

But the notice does not identify the suspicious activity, when it occurred, which systems were involved, or whether anyone accessed customers’ stored information. The Register, which also reviewed the email, noted that the company had not explained whether customers’ secrets were exposed.

How to be safe

Because the scope of the incident is unknown, we recommend prioritizing your most important accounts while mSeven investigates.

Changing your mSecure password alone may not be enough if someone has already accessed your account. mSecure’s documentation explicitly warns that someone may already have made a backup of its contents. That guidance does not establish what happened in this incident.

Users should not have to wait for a completed forensic investigation before receiving useful guidance. They need to know who should act, which credentials need attention, and whether the tool they would normally use to manage those changes remains safe to use.

Until mSeven provides those answers, our advice is to prioritize your most important accounts, replace the relevant credentials through official services, and avoid destructive account resets:

  • Change passwords through each service’s official website or app, beginning with your primary email, financial accounts, work accounts, and accounts used to recover access to other services. Use a new, different, strong password for each.
  • Review two-factor authentication stored in the vault. If that could be compromised by unauthorized access, consider re-enrolling that account’s authenticator through the service’s security settings.
  • For passkeys stored in mSecure, use each website or app’s account-security settings to remove the old registration and create a replacement with a different provider as a precaution. But make sure another working sign-in method is available first.
  • Think carefully about where replacement credentials go. The notice does not establish whether saving new credentials in mSecure is safe. For users rotating important accounts now, using a different password manager temporarily is a reasonable precaution.

We’ll keep you posted if we learn more about this incident, so stay tuned.

Update November 6, 2026

According to follow-up messages attributed to mSecure support and reproduced by multiple customers on the company’s forum, the incident affects only users who synchronized with mSecure Cloud. We have not located a directly published company statement confirming that scope.


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

Chrome 157 fixes 213 security issues, including 7 critical flaws

4 November 2026 at 13:16

On November 3, Google issued Chrome 157 to the stable channel for Windows, Mac and Linux. The update is rolling out over the coming days and weeks.

Most users are on Chrome’s Stable channel. The desktop update brings Chrome to versions 157.0.8103.38/.39 for Windows and Mac and 157.0.8103.38 for Linux. It includes 213 security fixes, including seven vulnerabilities rated Critical by Google.

Chrome for Android was also updated to 157.0.8103.38. It will become available on Google Play over the coming days.

How to update Chrome

The easiest option is to allow Chrome to update automatically. But you can end up lagging behind on updates if you never close your browser or if something goes wrong, such as an extension preventing the update.

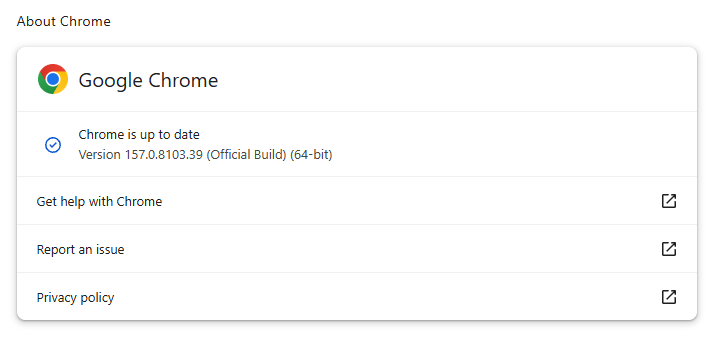
If you don’t want to wait for the rollout to reach you, you can update manually. Open About Google Chrome from Chrome’s settings or Help menu. Chrome will check for updates. If one is available, click Relaunch to apply it.

Chrome 157.0.8103.39 is up to date

You can find an explanation of the version numbering system and step-by-step instructions in our guide: How to update Chrome on every operating system.

Technical details

Some of the security fixes deserve a closer look.

Google rates seven vulnerabilities in the update as Critical. One, a memory corruption flaw in ANGLE, affects Chrome for Android. It could potentially allow a remote attacker to run code outside the sandbox through a specially crafted HTML page.


Mobile protection, anywhere, anytime.

.wp-block-kadence-advancedbtn.kb-btns400740_ab89fd-c4{gap:var(--global-kb-gap-xs, 0.5rem );justify-content:center;align-items:center;}.kt-btns400740_ab89fd-c4 .kt-button{font-weight:normal;font-style:normal;}.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0{margin-right:5px;}.wp-block-kadence-advancedbtn.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0 .kt-button{color:#555555;border-color:#555555;}.wp-block-kadence-advancedbtn.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0 .kt-button:hover, .wp-block-kadence-advancedbtn.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0 .kt-button:focus{color:#ffffff;border-color:#444444;}.wp-block-kadence-advancedbtn.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0 .kt-button::before{display:none;}.wp-block-kadence-advancedbtn.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0 .kt-button:hover, .wp-block-kadence-advancedbtn.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0 .kt-button:focus{background:#444444;}
ul.menu .wp-block-kadence-advancedbtn .kb-btn400740_68fb6a-2d.kb-button{width:initial;}.wp-block-kadence-advancedbtn .kb-btn400740_68fb6a-2d.kb-button{color:var(--color-neutral-10);background:var(--color-brand-blue-60);border-top-left-radius:40px;border-top-right-radius:40px;border-bottom-right-radius:40px;border-bottom-left-radius:40px;padding:var(--kb-btn-padding);margin:var(--kb-btn-margin);box-shadow:1px 1px 2px 0px rgba(0, 0, 0, 0.2);}.wp-block-kadence-advancedbtn .kb-btn400740_68fb6a-2d.kb-button:hover, .wp-block-kadence-advancedbtn .kb-btn400740_68fb6a-2d.kb-button:focus{box-shadow:0px 4px 0px 0px var(--color-brand-blue-90);}Try it now

CVE-2026-121229: Memory corruption in ANGLE, which could allow a remote attacker to potentially execute arbitrary code outside the sandbox via a crafted HTML page.

ANGLE is Chrome’s graphics translation layer. A buffer overflow occurs when a program puts more data into an area of memory than it can hold, overwriting data in adjoining memory. An attacker can exploit this to make the vulnerable process run malicious code.

Chrome vulnerabilities that enable remote code execution outside the browser sandbox are particularly valuable to attackers because they can turn a visit to a malicious or compromised website into direct code running on the underlying operating system, often without requiring additional exploitation steps.

CVE-2026-121035: Use-after-free in Prerender.

Chrome’s Prerender component helps pages open faster by loading and preparing a page in the background before you navigate to it. If you then visit that page, Chrome can display the prepared version almost instantly instead of loading it from scratch.

This goes beyond just downloading content: Chrome also starts rendering the page and running its JavaScript.

A use-after-free vulnerability occurs when a program attempts to access a memory location after it has been freed. That can cause crashes or, in some cases, allow an attacker to run their own code.

CVE-2026-121156: Buffer overflow in Dawn.

Dawn powers WebGPU in Chrome, allowing websites to use a device’s graphics processor for rendering and computational tasks. It checks and translates WebGPU instructions into commands that the device’s underlying graphics system can understand.

A buffer overflow occurs when a program writes more data to a block of memory than it can hold. This can cause a crash or, in some cases, allow an attacker to run code.


Stop threats before they can do any harm.

Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →

A hidden backdoor put 1.3 million TV boxes to work for criminals

3 November 2026 at 15:11
.kadence-column484175_1ef361-88 > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column484175_1ef361-88 > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column484175_1ef361-88 > .kt-inside-inner-col{flex-direction:column;}.kadence-column484175_1ef361-88 > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column484175_1ef361-88 > .kt-inside-inner-col{background-color:rgba(255, 229, 229, 0.83);}.kadence-column484175_1ef361-88 > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column484175_1ef361-88{position:relative;}@media all and (max-width: 1024px){.kadence-column484175_1ef361-88 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column484175_1ef361-88 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}

In this article

  • Google says Videostrong backdoored 1.3 million certified Android TV boxes and sold criminals access to the botnet.
  • The takedown disrupted the botnet, but the backdoor remains in infected boxes’ firmware.
  • Suspect your box? Disconnect it and ask the seller about a fix or replacement.

Most malware needs you to click something. This one came in the box.

Google’s Threat Intelligence Group (GTIG) says it has high confidence that Android device maker Videostrong Technology built and ran the XCPE backdoor for financial gain. Videostrong sold access to criminal affiliates, who loaded their own malware modules onto the boxes.

GTIG found that the backdoor, called x.cpe (or com.oemservice in some builds), sits in the firmware with system-level privileges. If someone uninstalls it, it reinstalls itself from the /oem/ partition when the device reboots. It could also switch off Google Play Protect app verification, allowing it to install more software without asking.

Google says Videostrong got past its compatibility and security tests by loading the malicious code after the device’s first boot. This allowed the devices to remain part of the residential proxy network.

Residential proxy networks rent out ordinary home IP addresses to customers. That makes their traffic appear to come from a legitimate consumer connection rather than a data center. This can help cybercriminals evade IP-based fraud controls and reputation systems.

The problem for users

Here’s what the backdoored set-top boxes could mean for their owners:

  • Your home internet connection could be used by others. Residential proxy modules routed other people’s traffic through infected boxes and their owners’ home IP addresses.
  • Ad fraud. Modules generated fake ad views and clicks in the background.
  • Spying and remote access to your device. Google observed operators capturing live screenshots, injecting keystrokes, collecting account and device information, and opening reverse shells.
  • More malware. Some affiliate modules were backdoors that could load further modules.
  • Your IP address could be linked to activity you didn’t start. Proxy traffic can include attempts to guess account passwords, for example, and may make your home IP address appear in connection with that activity.

How to stay safe

Google and its partners took legal action to take down the domains and servers Videostrong used to control the botnet. Google says it has banned Videostrong and its future subsidiaries and affiliates from making certified Android devices, and strengthened firmware integrity checks for certified Android TV devices.

The takedown only cuts the current connection to the malicious servers. It doesn’t remove the backdoor from infected devices, and can potentially be exploited by other criminals. If you think your box may be affected, disconnect it and contact the seller or manufacturer to ask for clean firmware or a replacement. Uninstalling the app won’t remove the backdoor from the firmware.

Google hasn’t published a complete list of affected models, so owners may not be able to tell from the model name alone whether their box is infected. If you decide to replace your box:

  • Buy from a reputable manufacturer.
  • Be cautious about “free TV” boxes. We’ve previously reported on Superbox and similar devices.
  • Be cautious about apps that pay you to share your bandwidth. They can route other people’s traffic through your internet connection.
  • Stick to trusted app stores and keep Google Play Protect switched on.
  • Isolate the box. Put TV boxes and other IoT gear on a separate network or VLAN with restricted outbound access. This doesn’t keep the devices themselves safe, but it does keep other devices separate.

Scammers know more about you than you think. 

Malwarebytes Mobile Security protects you from phishing, scam texts, malicious sites, and more. With real-time AI-powered Scam Guard built right in. 

.wp-block-kadence-advancedbtn.kb-btns97520_6de029-2f{gap:var(--global-kb-gap-xs, 0.5rem );justify-content:flex-start;align-items:center;}.kt-btns97520_6de029-2f .kt-button{font-weight:normal;font-style:normal;}.kt-btns97520_6de029-2f .kt-btn-wrap-0{margin-right:5px;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button{color:#555555;border-color:#555555;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:hover, .wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:focus{color:#ffffff;border-color:#444444;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button::before{display:none;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:hover, .wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:focus{background:#444444;}
ul.menu .wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button{width:initial;}.wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button{color:var(--color-neutral-10);background:var(--color-brand-blue-60);border-top-left-radius:40px;border-top-right-radius:40px;border-bottom-right-radius:40px;border-bottom-left-radius:40px;padding:var(--kb-btn-padding);margin:var(--kb-btn-margin);box-shadow:1px 1px 2px 0px rgba(0, 0, 0, 0.2);}.wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button:hover, .wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button:focus{box-shadow:0px 4px 0px 0px var(--color-brand-blue-90);}Try it now

Hackers put porn on public billboards and claim it was “far too easy”

3 November 2026 at 13:01

While digital billboards are supposed to grab your attention, recent reports from Egypt, Malaysia, and Brazil described them doing so with explicit footage.

The cyberattacks were claimed by a group called Leakers$, which said it exploited software used to send content to LED displays.

The group said it did not hack into individual billboards to show the pornographic footage, but that it accessed the software used to send the content.

For example, on October 29, explicit footage appeared on a large billboard overlooking one of Egypt’s busiest highways. Videos circulating online showed the attackers’ aliases and a Telegram channel address overlaid on the footage. Some motorists stopped to record it.

Egyptian authorities said the billboard’s operator suffered a website compromise, resulting in unauthorized footage appearing in several countries simultaneously. Similar events were reported in Malaysia and Brazil. The attackers also claimed access to systems in Iraq and China, but those claims are less firmly corroborated.

Speaking to The Cairo Report, a representative of Leakers$ claimed the group found thousands of exposed systems during roughly two hours of automated scanning. The representative described a vulnerability in content-transmission software and weaknesses accessible through the systems’ own web pages and interfaces.

That is the group’s account, but if it is accurate, it helps explain the apparent ease and reach of the attack:

  • Internet exposure makes targets discoverable. Attackers can scan for reachable management systems rather than physically approach individual screens.
  • Repeated software weaknesses can scale. Finding a flaw in software used across multiple installations can create opportunities far beyond one billboard.
  • Content-management access is the prize. Someone who gains control of the system that publishes advertisements may be able to replace legitimate content without touching the display itself.

This is another example of how convenient remote management can expose systems to attack. Recent attacks on refrigerated systems in European supermarkets demonstrated a similar risk. The cooling systems are internet-connected, so mechanics can remotely diagnose and fix problems.

What should be done

The risk of food waste or dangerous traffic situations should be a warning to review what organizations need to do to prevent their systems from being hacked and abused.

Regarding digital billboards, the Out of Home Advertising Association of America’s security guidelines tell operators not to rely on manufacturers’ default passwords or reuse passwords across displays. They also recommend restricting access to management services, using multifactor authentication, and protecting remote connections with a VPN.

But the practical response is less about protecting a giant television and more about securing a remotely managed computer system:

  • Restrict management access rather than leaving it open to the public internet.
  • Replace default and reused passwords and enable multifactor authentication.
  • Keep signage software, controllers, and networking equipment updated.
  • Check who has access, including suppliers, and how that access is protected.
  • Monitor systems and rehearse a way to stop unauthorized access quickly.

These same basic rules can be applied to smart household appliances.


What do cybercriminals know about you?

Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.

Revolve card breach: 1.5 million people may be affected

3 November 2026 at 12:26
.kadence-column484007_649ea4-04 > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column484007_649ea4-04 > .kt-inside-inner-col{flex-direction:column;}.kadence-column484007_649ea4-04 > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column484007_649ea4-04 > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column484007_649ea4-04{position:relative;}@media all and (max-width: 1024px){.kadence-column484007_649ea4-04 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column484007_649ea4-04 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}
.kadence-column484007_683ec9-3f > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column484007_683ec9-3f > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column484007_683ec9-3f > .kt-inside-inner-col{flex-direction:column;}.kadence-column484007_683ec9-3f > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column484007_683ec9-3f > .kt-inside-inner-col{background-color:rgba(255, 229, 229, 0.83);}.kadence-column484007_683ec9-3f > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column484007_683ec9-3f{position:relative;}@media all and (max-width: 1024px){.kadence-column484007_683ec9-3f > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column484007_683ec9-3f > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}

In this article

  • Fashion retailer Revolve said customers’ payment card numbers and expiration dates were stolen
  • Data at risk includes card numbers and expiration dates, customer names and addresses
  • Affected customers should watch their statements and consider asking issuers for new cards

Online fashion retailer Revolve Group said customers’ payment card numbers and expiration dates were stolen. In its customer notification letter filed with the Massachusetts Attorney General, Revolve told recipients the incident involved their names, addresses, and payment card details.

What was stolen?

The at-risk data includes customer names and contact information, payment card numbers, and card expiration dates. The breach only affected customers who had saved their payment card as a payment method in their Revolve account.

A filing on the Texas attorney general data breach website lists 127,200 affected Texans, but not a nationwide total. We found the figure of 1,515,073 in data returned by the site when searching for Revolve. That data labels it as the total number of people affected, but the figure isn’t displayed on the public listing. Other sites have repeated it, though they appear to rely on the same Texas record. The SEC filing did not give a number of affected people, and Revolve has not confirmed the total.

Revolve’s SEC filing does not mention card verification value (CVV) numbers. These three-digit security codes printed on the back of payment cards (four digits on the front for American Express cards) are an extra layer of security for card-not-present transactions.

It is also unclear whether the card numbers were fully visible or masked, or whether Revolve or a third-party payment processor held them.

Even without a CVV, card numbers and expiration dates may be enough to make purchases at some online stores. And scammers who know your real card details and contact information may be able to send more convincing phishing messages to trick you into revealing your CVV.

How did they get the data?

Revolve has not said how the attackers accessed the saved payment data. In its SEC filing, Revolve said it believes an unauthorized actor may have obtained the data “through automated means.” Records on the Texas attorney general’s site indicate that the incident happened on September 11 and was discovered on September 29.

No group has publicly claimed responsibility for the theft.

What Revolve customers can do now

Revolve said it has taken extra security measures following the breach, although didn’t say what those are.


Breaches happen every day. Don’t be the last to know.


If you have saved payment information in your Revolve account, your details may have been among those stolen. Fraud can often begin within days of a breach. If you’re concerned about your card details being exposed:

  • Read your statements line by line to identify even small charges that you don’t recognize. Criminals will often make a small charge using stolen card details to see if the card works.
  • Look for unfamiliar merchant names on your statement.
  • Report unauthorized charges to the card issuer immediately.
  • Consider removing saved cards from shopping accounts. You could use a password manager instead, some of which will store autofill data for payment cards.
  • Ask your card issuer to cancel your card and reissue with a new number so that the old number becomes unusable.

Also, don’t immediately trust calls, texts, or emails about the incident. Scammers can use stolen information to make themselves sound convincing. If someone claims to be calling from your card issuer, call the number printed on your card to check.

If you’re unsure about a message or link, check it with Malwarebytes Scam Guard.


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

5 stars for sale: Inside the underground fake review trade

2 November 2026 at 15:24

Recently, our team exposed sophisticated scam kits designed to steal sensitive data and trick consumers. But underground marketplaces are not just for malware and stolen passwords. They also offer services designed to manipulate your opinion of the products and services you buy every day.

In our latest research, we examined cybercrime forums where sellers advertise illicit “reputation management” services. For the right price, these underground operators offer to flood a product with glowing, five-star ratings or remove negative reviews. This shadowy industry works both ways—artificially boosting reputations and deliberately hiding legitimate complaints.

A major shift we are seeing in this space is the adoption of new technology. We also found that cybercriminals are using AI to automate these fake review campaigns. This could allow them to quickly generate realistic, human-sounding feedback in large volumes without much manual effort.

5 stars as a service

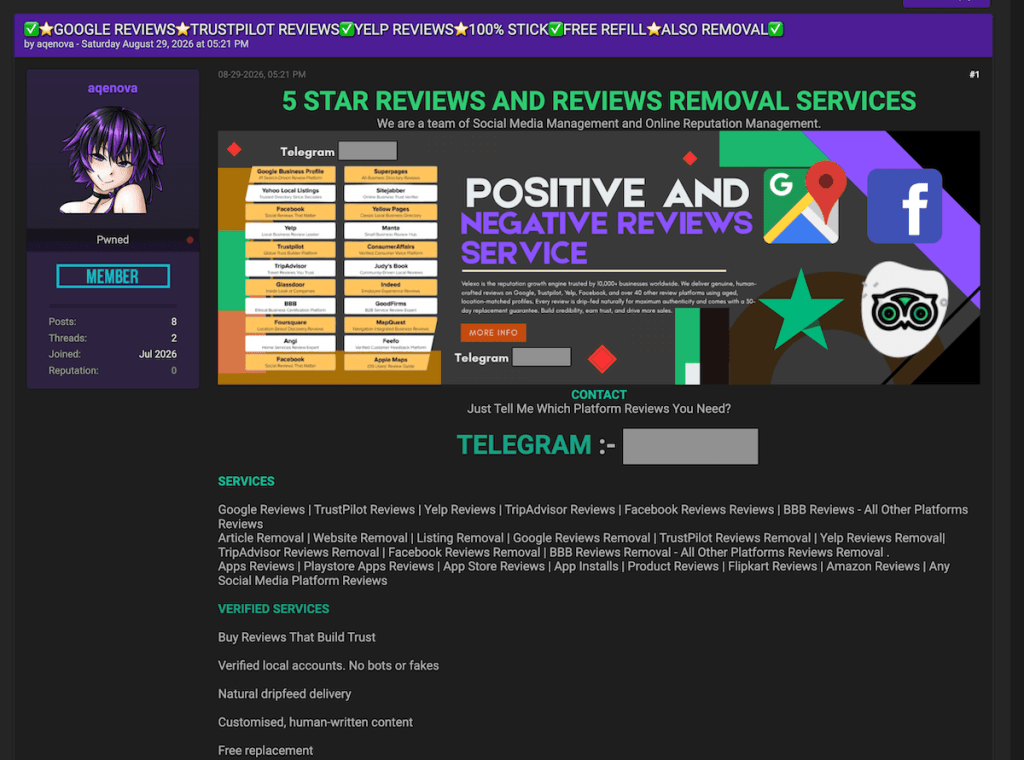
In the first example, discovered on a major English-language underground forum, a seller operating under the handle “aqenova” advertises both five-star review generation and negative review removal services. 

The seller’s operations span widely used platforms, including Google, Trustpilot, Yelp, and various mobile app stores. By simply asking prospective buyers, “Just tell me which platform reviews you need?” the seller presents reputation manipulation as something buyers can just order on demand.

Five-star reviews and removal services

Decoding the seller’s FAQ 

Analyzing another seller’s (TrustForge) “Frequently Asked Questions” section revealed some surprising details about how these operations reportedly run behind the scenes. 

First, the seller emphasizes that real people manually post these reviews, offering a guarantee for both successful delivery and “non-drop”—meaning the platform won’t flag and remove the feedback later. 

Remember, a real person posting a review doesn’t mean they’re a real customer. The important question is whether they actually used the product or service and are describing an honest experience.

Second, it appears this is a well-coordinated team effort rather than a solo operation, as the seller charges an extra fee if a buyer wants the main operator to write the review text personally. 

However, what caught our attention most was their confidence in beating platform checks. The seller guarantees their fake reviews will stay active, claiming they rely on a closely guarded “private method.” According to TrustForge’s own statements, this method has allowed them to post more than 10,000 fake reviews.

Reputation management FAQ

The clean-up crew: Making bad reviews disappear

A single negative review is often all it takes to create a bad first impression of a product or service. When those negative comments start to pile up, they can completely ruin a business’s reputation and bottom line.

Recognizing how desperate businesses can be to protect their image, our research team discovered underground services specifically offering to remove “fake” or “unfair” reviews from major platforms like Google and Trustpilot. 

Of course, the boundary between what is genuinely fake and what a business simply considers “unfair” can be blurry. Businesses can legitimately challenge fabricated reviews, but these services raise concerns about whether genuine customer complaints could also be targeted.

If legitimate customer complaints disappear, consumers lose information that could help them decide where to spend their money. 

An offer to remove “fake” or “unfair” Google reviews
An offer to remove ”fake” or “unfair” review Google reviews

On average, having a single review removed through these underground services costs between $100 and $200. However, the pricing jumps dramatically depending on the platform.

For instance, one seller advertised Airbnb review removal for around $1,100 per review.

When you check a business’s reviews, you’re looking for patterns in other customers’ experiences. If genuine complaints disappear, you could miss repeated problems with refunds, product quality, or customer service.

$1,100 to remove a “fake” or “unfair” Airbnb review 

Artificial intelligence, artificial reviews

During the last few months, our research team spotted an interesting thread on an underground forum where two users discussed using AI to mimic human E-E-A-T.

E-E-A-T stands for Experience, Expertise, Authoritativeness, and Trustworthiness. It is a quality evaluation framework outlined in Google’s Search Quality Rater Guidelines, which human evaluators use to assess content quality. E-E-A-T itself is not a direct ranking factor.

In the discussion we observed, one user asked the community if it was possible to use AI to effectively fake these qualities when writing product reviews and artificially boost website rankings. The answer was a resounding yes. 

Another user claimed they had never experienced problems getting Google to index their completely AI-generated reviews.

AI vs. E-E-A-T
AI vs. E-E-A-T

Behind the scenes: The IP addresses for fake reviews

To keep fake reviews from being flagged and deleted, scammers need to look like everyday consumers. To help do this, they can use something called “residential and mobile proxies,” which route their traffic through other internet connections to disguise where it comes from.

Think of an IP address as your computer’s caller ID. When scammers use bulk IP addresses from giant data centers, platforms may spot and block that traffic as coming from commercially hosted infrastructure. Residential proxies, on the other hand, route traffic through real, physical home internet connections—just like the Wi-Fi you use in your living room. Mobile proxies work the same way, but use real cellular networks.

Our team recently discovered a seller on an underground forum acting as a direct supplier of these residential and mobile connections. The seller explicitly advertises them as perfect for running fake review campaigns.

Residential and mobile advertised for fake review campaigns
Residential and mobile proxies advertised for fake review campaigns

How to avoid being misled by fake reviews

The main goal of this research isn’t to make you panic or stop trusting every online review you read. We want to raise awareness about what happens behind the scenes, so you can make more informed buying decisions.

If a product or offer seems too good to be true, but is backed by a mountain of perfect five-star reviews, take a moment to pause. Scammers often use these artificially boosted ratings to make a bad deal look reassuring.

Read recent reviews and some of the middle-rated ones, rather than relying on the overall score. Look for recurring details about the things that matter to you, such as durability, delivery, or getting your money back.

Look for repeated wording or sudden bursts of glowing feedback. These signs don’t prove a review is fake, but they’re reasons to take a closer look. Check the seller’s contact details and return policy, too.

Malwarebytes Browser Guard can also help block scam, phishing, and malicious websites you may encounter while shopping.

Unsure about an offer, even with glowing reviews? Share the link or a screenshot with Malwarebytes Scam Guard for help checking for signs of a scam before you buy.


Stop threats before they can do any harm.

Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →

Applebee’s customer data exposed by password left in app

2 November 2026 at 15:22

Applebee’s has fixed a security flaw that exposed customers’ personal information after a researcher discovered a database password embedded in the restaurant chain’s Android app.

The researcher, Robert Wiggins, found the password with help from AI. It gave him access to an internal Applebee’s customer database. A password written directly into an app’s code or configuration is known as a hardcoded credential. Anyone who extracts it may be able to use it to access the system.

The exposed database contained:

  • Names, email addresses, and email-verification status
  • Dates of birth, phone numbers, and ZIP codes
  • Veteran status
  • Account-creation dates and login counts
  • IP addresses from customers’ most recent logins, which can indicate their approximate location

TechCrunch independently checked Wiggins’ findings. It created an Applebee’s account with dummy information, which Wiggins successfully retrieved from the database.

According to TechCrunch, Wiggins could not find a suitable way to report the issue to Applebee’s or its parent company, Dine Brands, so he asked the publication to help contact them. TechCrunch held its story until the fix was confirmed. Applebee’s confirmed on October 29 that it had addressed the issue.

It’s unclear how many customers’ records were in the database. Dine Brands says it has not found evidence of unauthorized access, but its investigation is ongoing.

How to stay safe

The database fields described by TechCrunch did not include payment card details or account passwords. That does not tell us whether anyone accessed the database before the fix, so customers should watch for targeted scams.

Names, email addresses, phone numbers, and other personal details could help scammers make messages look relevant and convincing.

  • Be wary of unexpected Applebee’s-themed emails, texts, or calls. Be especially skeptical of messages offering refunds or compensation, warning that your account will be closed, or asking you to “verify” payment details.
  • Check security notices through a route you trust. Open the app directly or visit Applebee’s website yourself rather than following a link in an unexpected message. If necessary, contact the company using details you find independently.
  • Unsure whether a message is a scam? Check it with Malwarebytes’ Scam Guard for an assessment and advice on what to do next.
  • When sharing personal information, consider why the company needs it and whether you trust it to keep the information safe.

Link Checker

Unsure where a link goes? We’ll check it.


Fake PDF and search tools hijacked searches for 13.4 million Chrome users

30 October 2026 at 16:25

Ads promoted browser extensions as tools to find manuals, convert PDFs, or make searches safer. But many of these extensions sent users’ search queries through servers controlled by their operators.

Socket researcher John Tuckner identified 319 extensions with an estimated 13.4 million installs over a decade. The extensions hijacked users’ default search settings and routed their searches through servers controlled by the operators before sending them to Yahoo or Bing. This gave the operators access to users’ queries and let them earn referral payments.

Socket says the extensions were promoted through ads on networks including Google Ads, promoting tools such as “manual finders,” “PDF converters,” “safe search,” and “AI search.”

The extensions were listed in Google’s official store, but most were unlisted. That means people with a direct link could visit a listing and install an extension, while ordinary searches in the store would not show it. An ad offered help with an immediate task, a landing page encouraged installation, and the official store provided a familiar place to complete it.

Search hijacking

The main risk was that operators could see what users searched for. Searches can reveal health worries, financial problems, workplace interests, or other personal matters. Socket says queries were often associated with a unique identifier, which could let the operators link a user’s searches over time.

The proxy could also choose where to send a search. Socket says this could potentially direct users to phishing or malware pages, but it did not find evidence that the extensions had done so.

What should users do?

If your searches start going astray, or you installed a search, PDF-converter, manual-finder, or security extension after clicking an ad, check what’s installed.

  • Review your extensions. Enter chrome://extensions in Chrome’s address bar. Remove extensions you don’t recognize, no longer use, or don’t trust. To remove one, select Remove and confirm. If you’re unsure about an extension, check it against the list at the end of Socket’s blog.
  • Check your search settings. In Chrome, at the top right, select More (the three-dot menu), then Settings > Search engine. If Chrome says an extension is controlling a setting, review or remove that extension. The absence of this notice doesn’t confirm that all your extensions are safe.
  • Run a Malwarebytes scan to check for malicious extensions and other malware that could be affecting your device.

From reporting threats to removing them.

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

Photo ID, bank checks, face scan? The UK’s age-check options

30 October 2026 at 14:00

As preparation for the UK’s planned social media ban, Ofcom has set out four ways social media platforms could check whether users are aged 16 or over. The government and Parliament will decide how the ban works in practice.

Ofcom is the regulator for the communications services in the UK. The BBC reports that Ofcom identified four ways to check someone’s age that it considers “highly effective.”

Here’s what those checks would involve:

  • Photo ID matching: Comparing a live image of you with the photo on an identity document, such as your passport, and checking the age information on that document.
  • Bank-based checks: Using age information your bank already holds about you, with your consent.
  • Facial age estimation: Using technology to estimate your age from your face. Ofcom says this technology has improved recently.
  • Digital ID services: Using a digital identity service to prove your age, rather than presenting a physical document.

Let’s think through what those checks could mean.

Challenges

The challenge isn’t simply checking someone’s age. It’s doing so without turning everyday internet use into an identity check.

Photo ID matching brings highly sensitive documents and facial images into the process, which raises questions about how that information is handled and protected. The risks aren’t hypothetical: as I reported last year, a breach at a third-party support provider for Discord exposed government ID images belonging to around 70,000 users.

Banking-based checks can be more privacy-preserving if they return only confirmation that someone meets the age threshold, rather than exposing financial information. But the important questions are what information each party receives, what gets retained, and whether the check can be linked to someone’s activity.

Facial age estimation can avoid uploading an identity document, but it still processes a sensitive image and makes an imperfect prediction. Ofcom acknowledges that some technologies can be wrong by a few years around age 16, so people near the threshold may face an additional verification check.

I would expect these checks to stop some underage access but not eliminate it.

Previous restrictions have been followed by workarounds, including increased VPN use, borrowed credentials, and migration to services outside the restrictions. The danger is treating a successful age gate as proof that children are now safe, when it might push them into less regulated spaces.

The effectiveness depends on how the checks are implemented. A VPN may help someone avoid a check triggered by their apparent location; it won’t, by itself, bypass an identity or facial check that is still required.

Similarly, Ofcom says matching a live image to an ID is intended to make it harder to borrow someone else’s document. We shouldn’t assume every workaround defeats every method. But Ofcom accepts that some motivated children will get through. The meaningful test is how much harm these measures prevent, weighed against the privacy risks and barriers they introduce— not whether every user has completed a check.

My personal preference is double-blind verification: a provider confirms that you meet the age requirement without learning which service you’re accessing, while the service receives proof of age without learning your identity. Proving you’re old enough shouldn’t mean revealing who you are.


Scammers don’t need to hack you. They just need you to click once. 

Malwarebytes Identity Theft Protection catches suspicious activity before it becomes a problem.

Binance hit by largest-ever crypto theft, with $6.3 billion stolen

30 October 2026 at 13:24
.kadence-column482616_9de20c-07 > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column482616_9de20c-07 > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column482616_9de20c-07 > .kt-inside-inner-col{flex-direction:column;}.kadence-column482616_9de20c-07 > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column482616_9de20c-07 > .kt-inside-inner-col{background-color:#ffe5e5;}.kadence-column482616_9de20c-07 > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column482616_9de20c-07{position:relative;}@media all and (max-width: 1024px){.kadence-column482616_9de20c-07 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column482616_9de20c-07 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}

In this article

  • Attackers stole $6.3 billion from the Binance cryptocurrency exchange
  • Binance says user funds are safe, but watch out for fake support or recovery offers from scammers
  • Users should check their accounts and use official Binance channels.

Binance says a security incident affected approximately $6.3 billion in cryptocurrency. Its initial investigation points to a compromised DevOps engineer’s laptop as a possible entry point.

The exchange says it has frozen around $3 billion with help from blockchain partners. It has promised to cover all losses using its emergency fund and company funds. Binance is reportedly the largest cryptocurrency exchange by daily trading volume.

What happened?

In an update on October 30, Binance said attackers may have used a compromised laptop belonging to a DevOps engineer to access a service container and submit unauthorized withdrawal transactions. The company said:

“We have found no evidence of any wallet private key leak.”

This doesn’t mean that one employee could simply transfer billions of dollars. Binance co-CEO Richard Teng told BleepingComputer the attacker did not simply use one engineer’s permissions. The incident involved a more complex process, rather than a single “one-click” action. Binance also said investigators had identified additional breach points.

Blockchain intelligence firms TRM Labs and Chainalysis have linked the theft to TraderTraitor, a North Korean hacking group associated with previous cryptocurrency thefts. TRM Labs estimates that about $6.36 billion left Binance wallets across ten blockchains, with most of it moving within about 20 minutes.

What should Binance users do?

Binance says approximately $3 billion has been frozen on-chain, while blockchain analysts have reported somewhat different totals. For now, those figures should be treated as developing estimates rather than a final accounting of recovered funds or the exchange’s ultimate losses.

Binance.com users (Binance.US was not affected) should check their accounts, avoid follow-up scams, and respond quickly if they spot signs of a separate compromise.

  • Go directly to official updates. Open the Binance app or navigate to its support site yourself. Avoid logging in through unexpected messages claiming that you must urgently verify your account or claim compensation. Binance has asked customers to rely on official channels.
  • Review your account and report anything unexpected. Check your transaction history and account security settings. If you find activity you do not recognize, contact Binance through its official support service. Binance’s support center includes options to disable an account and reset a password or two-factor authentication.
  • Never give anyone your authentication codes. Treat requests for login codes as a warning sign, even if the person claims to be helping with the incident.
  • Be wary of anyone promising to recover cryptocurrency. The FBI published a warning in 2023 that fake recovery services target people who have already lost cryptocurrency.
  • Preserve evidence if you lose money to a related scam. Keep messages, wallet addresses, transaction details, and information about anyone offering recovery services.

Pro tip: Unsure whether a message is a scam? Check it with Malwarebytes’ Scam Guard for an assessment and advice on what to do next.


Link Checker

Unsure where a link goes? We’ll check it.


Hackers steal and publish data on 41,000 Homeland Security workers

30 October 2026 at 12:33
.kadence-column482644_f2c16d-bc > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column482644_f2c16d-bc > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column482644_f2c16d-bc > .kt-inside-inner-col{flex-direction:column;}.kadence-column482644_f2c16d-bc > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column482644_f2c16d-bc > .kt-inside-inner-col{background-color:#ffe5e5;}.kadence-column482644_f2c16d-bc > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column482644_f2c16d-bc{position:relative;}@media all and (max-width: 1024px){.kadence-column482644_f2c16d-bc > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column482644_f2c16d-bc > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}

In this article

  • Hackers published work details and internal group memberships for more than 41,000 DHS workers.
  • The data could enable targeted scams, harassment, stalking, or physical threats.
  • DHS employees should follow agency guidance, verify unexpected contact, and report threats to security.

A group of hackers calling themselves the Department of Peace says it stole and published the personal details of more than 41,000 people working for the US Department of Homeland Security (DHS). The department says it is aware of a potential breach.

The group, which also claimed the theft of contract documents from the DHS in March, gave the data to Swiss hacktivist maia arson crimew, who published it in collaboration with the transparency collective DDoSecrets. The latter also published the BlueLeaks data dump that listed law enforcement officers’ details in 2020.

The aim of publishing the data was to replace “anonymity with accountability,” DDoSecrets co-founder Emma Best said in an online statement.

According to TechCrunch, timestamps on the records suggest the data was taken around mid-August. The group said it had launched the attack in response to a July 17 statement by DHS Secretary Markwayne Mullin, in which he promised to “turn up the heat” with traffic stops.

What was stolen?

The data files published online, which the publishers have called “Icepick,” span staff at nearly 7,000 offices. They include the names, work email addresses, phone numbers, office addresses, job titles and membership in internal DHS groups. The employees impacted include almost 6,600 Immigration and Customs Enforcement (ICE) employees. ICE is the DHS unit responsible for immigration enforcement and deportations in the US.

The dataset also carried details of over 21,000 Customs and Border Protection (CBP) employees, along with information on people who work at the Cybersecurity and Infrastructure Security Agency (CISA).

The data dump revealed less information than the ShinyHunters’ FBI data heist in September, which reportedly contained Social Security numbers, emergency contacts, medical records and home addresses. Nevertheless, this is more than just a phone book of folks in the DHS.

For one thing, it doesn’t take much to cross-reference data. Reuters matched six DHS employees’ data to credit bureau records and breach data from a dark web intelligence platform. Online activists regularly use open-source intelligence (OSINT) to “doxx” people from very few clues, meaning that even a leak of basic identity information can put someone in danger. In fact, the creators of a separate searchable version say they added information through automated and manual research. So some details shown in that version may not have come from the data stolen from DHS.


Breaches happen every day. Don’t be the last to know.


The data in this case also included membership of groups within Active Directory, a Microsoft tool that contains identity information about computer users. Active Directory controls who can access different internal tools, services, and third-party software within an organization.

The files listed over 200 CBP users in a group that could access the facial recognition tool Mobile Fortify. Other groups reference a service called Penlink, which the company claims can track the location data of hundreds of millions of mobile devices.

According to the Guardian, job titles in the data dump show which agents were assigned to sensitive jobs such as special operations, surveillance, and undercover work.

How did they get the data?

The Department of Peace said that it got to the information via a single sign-on (SSO) service provided by identity company Okta. SSO is a prized target for hackers because a single authentication can get a user into many different workplace services and applications.

Okta says it has no evidence its data or systems were compromised, but that doesn’t rule out someone abusing a DHS account with stolen credentials.

DHS told reporters it was aware of a potential breach. One DHS employee whose data showed up in the breach told Reuters they hadn’t heard anything about it.

What DHS employees can do now

The leaked records include work contact details and internal group memberships. This information could help attackers create convincing messages or calls, and may expose some employees to unwanted attention or threats. DHS has warned about the risk of harassment, stalking, and physical harm. It is not yet clear whether the leak has led to specific threats or affected any operations.

If you work for DHS:

  • Follow security advice and instructions from the DHS.
  • Treat unexpected calls, emails, and texts about your role or colleagues with caution. Verify them through a contact method you already trust, and never share passwords or MFA codes.
  • Change any personal passwords you’ve reused for work, and turn on MFA where available. Follow your agency’s process for work accounts.
  • Report suspicious contact or threats to your agency’s security team. If you believe there’s an immediate danger, contact law enforcement.

Do you think your information might have been leaked in a data breach? Check out the Malwarebytes Identity Theft Protection service.


Someone’s got their eye on your personal information. Make sure it’s us.


Malicious Firefox extensions impersonate popular crypto wallets

29 October 2026 at 15:06

Socket’s threat researchers found three malicious Firefox extensions that impersonated the Phantom, Jupiter, and Bitget crypto wallets.

Once installed, the malicious extensions stole recovery phrases and private keys, which would provide the attacker with full control of a wallet.

A crypto wallet is an app, browser extension, or physical device that lets you manage cryptocurrency such as Bitcoin. Despite its name, it doesn’t actually hold your coins. Those are recorded on a blockchain, a shared digital record of transactions. Instead, the wallet manages the secret digital keys that let you access and spend them.

When you create a wallet, you may be given a recovery phrase: a list of words you can use to restore access. Write it down and store it offline. It’s a backup of your keys, not just an ordinary password. Anyone who gets hold of it can take control of your funds, which is why fake wallet extensions try to steal it.

Cybercriminals listed three fake wallet extensions on Firefox Add-ons, impersonating Phantom, Jupiter, and Bitget. The genuine wallets offer extensions for other browsers: Jupiter lists Chrome, Brave, and Edge; Bitget’s extension is for Chrome; and Phantom says its Firefox extension is no longer supported.

The malicious extensions looked for 12-, 15-, 18-, and 24-word recovery phrases, as well as Ethereum and Solana private keys. They could read input fields, detect pasted text, and scan screens displaying recovery phrases.

A recovery phrase or private key is a bearer secret: whoever holds it controls the wallet and can move its assets. The Phantom variant’s backend logged captured secrets, sent them to a Telegram bot, and automatically moved funds to hardcoded payout addresses. Those addresses covered Ethereum, BSC, Polygon, Arbitrum, Optimism, Base, Avalanche, Solana, and Bitcoin. The Phantom variant could read a phrase both when it was typed during import and when it was displayed on a reveal screen.

How to stay safe

Socket says all three listings were live on Firefox Add-ons during its analysis and have since been removed. But if you find one of these extensions in your Firefox browser, you should:

  • Remove the extension. Use the three-dot menu next to it and choose Remove.
  • If you ever entered a phrase or key, create a new wallet on a clean device and move your assets immediately. Treat the old wallet as compromised.
  • In the future, install wallets only from the vendor’s official website link, not from store search results.
  • The fake Phantom listing asked to access data on all websites and had no privacy policy. These are warning signs to look out for.
  • Use an up-to-date, real-time anti-malware solution that blocks malicious websites.
Malwarebytes blocks phantom.bonto.io
Malwarebytes blocks bonto.io subdomains

Never enter your recovery phrase on a website. Enter it only in the official wallet app when restoring. Wallet support will never ask for it.

IOCs

The malicious extensions:

  • Phantom impersonator: add-on ID 3092199
  • Jupiter impersonator: add-on ID 3092666
  • Bitget impersonator: add-on ID 3092059

Subdomains:

  • bonto[.]io
  • phantom[.]bonto[.]io
  • jupiter[.]bonto[.]io
  • bitget[.]bonto[.]io
  • coinbase[.]bonto[.]io
  • exodus[.]bonto[.]io

IP addresses:

  • 104.21.34[.]69
  • 172.67.155[.]198

From reporting threats to removing them.

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

❌