Accelerating the Migration to the Post-Quantum Era
The promise of quantum computing brings an unprecedented paradox. While it will unlock revolutionary breakthroughs in science, materials discovery and medicine, it simultaneously poses an existential threat to the mathematical foundations of modern cybersecurity.
For decades, the global economy has relied on public key cryptography to safeguard everything from personal privacy to national security. This cryptography is built on mathematical problems that are computationally infeasible for classical computers to solve but that quantum computers can solve efficiently, rendering today’s cryptographic protocols obsolete.
Using Shor’s algorithm, a sufficiently powerful quantum computer could factor the large prime numbers that underpin public key cryptography, in minutes. These are tasks that would take today’s most advanced supercomputers a millennium to crack. This capability would effectively turn our strongest digital defenses into open doors, creating a period of vulnerability leading up to Q-Day – the day today’s encryption is broken.
The Migration Crisis: Why Traditional Strategies Fail
For CISOs and technical leaders, the transition to post-quantum cryptography (PQC) is not a simple patch-and-deploy exercise. It is a multiyear transformation that requires updating cryptography across every device, application, certificate and infrastructure component in the enterprise.
Most enterprises today are constrained by cryptographic debt – years of accumulated, undocumented and deprecated encryption protocols buried deep within legacy applications, third-party software libraries and unmanaged IoT devices. This creates a vast and largely invisible attack surface that traditional vulnerability scanners were never designed to detect.
The challenge is compounded by the absence of a unified source of truth. Existing tools offer a fragmented "outside-in" view of the environment. They may identify devices on the network, but they lack visibility into cryptographic libraries embedded within live traffic. Without a real-time Cryptographic Bill of Materials (CBOM), security teams are forced to rely on manual, point-in-time audits that become outdated almost immediately. Spreadsheets cannot scale to this problem.
This visibility gap makes it impossible to prioritize remediation, leaving sensitive data exposed to harvest now, decrypt later (HNDL) attacks. In these attacks, adversaries intercept and store encrypted data today with the intent of unlocking it once quantum computing capabilities mature.
Operationally, traditional migration approaches are equally unworthy. Manually updating cryptography across thousands of global endpoints and branch offices often requires disruptive rip and replace strategies that threaten uptime and demand specialized expertise that is in extremely short supply. Organizations need a way to bridge today’s classical infrastructure with a quantum-resilient future without disrupting business operations or exhausting IT resources.
At Palo Alto Networks, we believe global enterprises cannot afford to wait. Our new Quantum-Safe Security solution is designed to remove these operational roadblocks by making cryptographic discovery, risk assessment and transition both continuous and actionable. We empower enterprises to gain real-time visibility into cryptographic risk and begin building agentic resilience at enterprise scale by integrating with existing security and infrastructure systems, including security information and event management (SIEM), load balancers, endpoint detection and response (EDR), as well as Application Vulnerability Management (AVM) tools.
The Four Stages of Cryptographic Inventory & Remediation
Palo Alto Networks Quantum-Safe Security is built around four foundational stages.
1. Continuous Discovery through Ecosystem Ingestion
Visibility is the first line of defense, but in a complex enterprise, true visibility requires more than a periodic scan. It requires continuous, high-fidelity ingestion of cryptographic intelligence across the environment.
Our solution acts as a central nervous system for your cryptographic posture, ingesting telemetry and logs directly from PAN-OS NGFW and Prisma® Access, enriched with data from a broad ecosystem of third-party security solutions, simplifying Day 0 onboarding. By leveraging your existing network infrastructure as sensors, we provide a comprehensive view of the cryptographic behavior of all assets without the operational friction of deploying new software.
To eliminate blind spots, we go beyond our own telemetry to ingest critical information from your existing systems you rely on. This includes syncing with configuration management database (CMDB) and asset management platforms to align cryptographic data with business inventories, integrating with EDR and access control solutions to monitor endpoint behavior, and aggregating data from network clouds and log platforms. The result is a unified intelligence layer that reflects how cryptography is actually used across the enterprise.
By synthesizing these data streams, we deliver a multidimensional view of cryptographic exposure:
Discovery – Identification of every application, user device, infrastructure component and IoT device.
Behavior – Analysis of traffic metadata, including protocols, key exchangemechanisms, encryption algorithms, hashes, certificates and tunnels.
Context – Precise attribution of hardware models, cryptographic libraries (such as deprecated OpenSSL versions), and browser versions in use.
2. Risk Assessment & Prioritization
Not all data is created equal, and a successful migration requires a surgical focus on where the exposure is most acute. Our Quantum Safe Security solution quantifies risk by correlating cryptographic strength with business criticality, providing a clear, prioritized view of current risk and where remediation matters most.
Assets are categorized into strategic zones, starting with immediate exposure risks caused by deprecated protocols that are vulnerable to classical exploitation today. From there, the solution addresses long-term harvest now, decrypt later threats. As threat models evolve, the risk engine is designed to expand to emerging vectors like identity and authentication integrity, anticipating risks such as “Trust Now, Forge Later" attacks that could undermine digital trust at scale.
At the same time, the solution validates and tracks quantum-secure assets that have successfully transitioned to post-quantum or hybrid-PQC algorithms. By correlating this intelligence with business criticality and data shelf-life, security leaders can make informed decisions. For example, a crown jewel asset containing data that must remain confidential for a decade or more, is flagged as a high HNDL risk today and elevated to the top of the migration queue.
3. Comprehensive Remediation
Moving from a vulnerable state to quantum resilience is a structured journey. Our comprehensive remediation framework guides organizations through three critical stages, supported by automated workflows and prioritized recommendations at every step.
Current State to Quantum Ready: The first stage focuses on infrastructure modernization. Usingcontinuous discovery insights, the solution provides hardware and software recommendations required to support next-generation cryptographic protocols. An asset reaches a Quantum Ready state once it has the underlying hardware and OS capabilities to support post-quantum algorithms, even if those protocols are not yet activated.
Quantum Ready to Quantum-Safe: Transitioning to a Quantum-safe state requires activation and configuration of post-quantum defenses. Our solution provides data configuration and certificate compliance guidance to enable PQC/Hybrid-PQC algorithms to be correctly implemented across the estate.
Virtual Patching via Cipher Translation: For all current and especially legacy systems or IoT devices that cannot be upgraded, we provide an accelerated path to quantum-safety. Through Cipher Translation, the infrastructure acts as a proxy, providing agentic remediation that reencrypts vulnerable traffic into quantum-safe standards (such as ML-KEM) in real-time at the network edge. This approach instantly moves legacy assets from a high-risk current state to a Quantum-safe posture without a single line of code change.
4. Governance: Continuous Crypto-Hygiene & Global Compliance
Quantum readiness is not a one-time event; it is a strategic enterprise transformation that requires continuous oversight to prevent the re-emergence of vulnerabilities. Our governance framework provides the guardrails for your migration through two critical layers of management:
Continuous Crypto-Hygiene & Ongoing Management: Maintaining high-fidelity visibility is essential to preventing the accumulation of "crypto-debt." Our solution automates real-time mapping of all cryptographic dependencies, ensuring your CBOM remains dynamic and accurate as your environment evolves. Furthermore, we introduce Active Drift Detection, which automatically detects and can even block the use of weak or noncompliant ciphers in real-time, preventing developers or third-party services from accidentally introducing insecure protocols.
Global Crypto-Compliance Enforcement & Reporting: As regulatory pressure from governments (like the US Commercial National Security Algorithm Suite 2.0) mounts, organizations must demonstrate measurable progress. Our solution will provide Automated Framework Auditing, offering continuous, native mapping of your environment against global standards, including NIST, FIPS 140-3, and DORA.
Architecting a Quantum-Resilient Enterprise
The transition to quantum-safe security is far more than a technical upgrade. It represents a fundamental shift in how organizations protect the longevity and integrity of their digital assets. Achieving quantum resilience is a multiyear effort that requires both advanced technology and strategic partnership.
That's why Palo Alto Networks has established Integrated Quantum Practices, bringing together technology, partners and professional services to help organizations navigate the complexity of this transition with confidence. By combining deep cryptographic visibility with intelligent, agentic remediation, organizations can systematically retire their cryptographic debt and build resilience into their security architecture over time.
This proactive approach does more than mitigate emerging risk. It establishes a foundation of digital trust that is resilient against the threats of tomorrow, enabling your most sensitive intellectual property to remain secure for its entire shelf life, even as cryptographic standards evolve.
Secure Your First-Mover Advantage: The Quantum Readiness Assessment
Don’t let the complexity of the quantum transition stall your organization’s progress. Begin your path to resilience with a Quantum Readiness Assessment, a focused engagement to clarify current exposure and identify the most critical areas for action. To go deeper, watch the Quantum-Safe Summit on demand for expert perspectives on cryptographic risk and quantum readiness.
The Palo Alto Networks Quantum-Safe Security solution is expected to be generally available to customers on January 30, 2026, with additional integration enhancements planned for April 2026.
Forward-Looking Statements
This blog contains forward-looking statements that involve risks, uncertainties and assumptions, including, without limitation, statements regarding the benefits, impact or performance or potential benefits, impact or performance of our products and technologies or future products and technologies. These forward-looking statements are not guarantees of future performance, and there are a significant number of factors that could cause actual results to differ materially from statements made in this [blog. We identify certain important risks and uncertainties that could affect our results and performance in our most recent Annual Report on Form 10-K, our most recent Quarterly Report on Form 10-Q, and our other filings with the U.S. Securities and Exchange Commission from time-to-time, each of which are available on our website at investors.paloaltonetworks.com and on the SEC's website at www.sec.gov. All forward-looking statements in this blog are based on information available to us as of the date hereof, and we do not assume any obligation to update the forward-looking statements provided to reflect events that occur or circumstances that exist after the date on which they were made.
Other noteworthy stories that might have slipped under the radar: Cloudflare WAF bypass, Canonical Snap Store abused for malware delivery, Curl terminating bug bounty program
To all those who are fighting the good fight in the world of cyber, keep collaborating to ensure our world never succumbs to the chaos of the Upside Down.
Researchers found a method to steal data which bypasses Microsoft Copilot’s built-in safety mechanisms.
The attack flow, called Reprompt, abuses how Microsoft Copilot handled URL parameters in order to hijack a user’s existing Copilot Personal session.
Copilot is an AI assistant which connects to a personal account and is integrated into Windows, the Edge browser, and various consumer applications.
The issue was fixed in Microsoft’s January Patch Tuesday update, and there is no evidence of in‑the‑wild exploitation so far. Still, it once again shows how risky it can be to trust AI assistants at this point in time.
Reprompt hides a malicious prompt in the q parameter of an otherwise legitimate Copilot URL. When the page loads, Copilot auto‑executes that prompt, allowing an attacker to run actions in the victim’s authenticated session after just a single click on a phishing link.
In other words, attackers can hide secret instructions inside the web address of a Copilot link, in a place most users never look. Copilot then runs those hidden instructions as if the users had typed them themselves.
Because Copilot accepts prompts via a q URL parameter and executes them automatically, a phishing email can lure a user into clicking a legitimate-looking Copilot link while silently injecting attacker-controlled instructions into a live Copilot session.
What makes Reprompt stand out from other, similar prompt injection attacks is that it requires no user-entered prompts, no installed plugins, and no enabled connectors.
The basis of the Reprompt attack is amazingly simple. Although Copilot enforces safeguards to prevent direct data leaks, these protections only apply to the initial request. The attackers were able to bypass these guardrails by simply instructing Copilot to repeat each action twice.
Working from there, the researchers noted:
“Once the first prompt is executed, the attacker’s server issues follow‑up instructions based on prior responses and forms an ongoing chain of requests. This approach hides the real intent from both the user and client-side monitoring tools, making detection extremely difficult.”
How to stay safe
You can stay safe from the Reprompt attack specifically by installing the January 2026 Patch Tuesday updates.
If available, use Microsoft 365 Copilot for work data, as it benefits from Purview auditing, tenant‑level data loss prevention (DLP), and admin restrictions that were not available to Copilot Personal in the research case. DLP rules look for sensitive data such as credit card numbers, ID numbers, health data, and can block, warn, or log when someone tries to send or store it in risky ways (email, OneDrive, Teams, Power Platform connectors, and more).
Don’t click on unsolicited links before verifying with the (trusted) source whether they are safe.
Reportedly, Microsoft is testing a new policy that allows IT administrators to uninstall the AI-powered Copilot digital assistant on managed devices.
Malwarebytes users can disable Copilot for their personal machines under Tools > Privacy, where you can toggle Disable Windows Copilot to on (blue).
In general, be aware that using AI assistants still pose privacy risks. As long as there are ways for assistants to automatically ingest untrusted input—such as URL parameters, page text, metadata, and comments—and merge it into hidden system prompts or instructions without strong separation or filtering, users remain at risk of leaking private information.
So when using any AI assistant that can be driven via links, browser automation, or external content, it is reasonable to assume “Reprompt‑style” issues are at least possible and should be taken into consideration.
We don’t just report on threats—we remove them
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
The intersection and evolution of operational technology (OT) and information technology (IT), as well as the cybersecurity risks associated with both are becoming increasingly critical business challenges for organisations of all sizes, across all geographies.
As digital transformation expands into OT environments, convergence with IT systems is inevitable. This convergence may generate exciting business opportunities, such as creating new sources of income and improving business outcomes, but it also presents new cybersecurity risks and complexities, for which many industry leaders are not prepared.
Why Is OT/IT Convergence So Complex?
There are many overlapping forces driving the OT and IT worlds together, creating a hairball of complexity from varying sources:
People: OT and IT communities are historically different in many ways (technological, operational, regulatory and culturally) and have different priorities and focuses.
Technology: The age of technology in OT environments means that legacy equipment and machinery are often incompatible with the latest IT software, increasing their vulnerability to cyberthreats.
Mindsets: Historically, ‘secure by design’ has not been a focus in OT. System uptime and employee safety have traditionally been prioritised over cybersecurity in OT environments, unlike IT where cybersecurity is ingrained.
Understanding the Risk and Impact
OT/IT cybersecurity is a strategic issue, not just a technical requirement, and it must be designed into systems as early as possible. The consequences of not acting from the start far outweigh any advantages gained by disregarding the issue.
This is particularly true for critical infrastructure, such as water purification systems, power grids, air traffic control systems, communications networks and battlefield command-and-control systems, all of which are open to potential cybersecurity risk. Always assume that your adversaries are willing to exploit your Achilles heel when it comes to securing OT/IT systems.
Key Attention Areas in OT/IT Convergence
All senior business leaders should consider the following areas with OT/IT convergence and cybersecurity:
Mindset: Industry leaders need the right mindset to balance cybersecurity best practices with a seemingly endless number of new devices and data sources caused by OT/IT convergence.
Technology: Technologies, such as artificial intelligence, machine learning and cloud computing, represent both opportunities and threats in the world of OT/IT cybersecurity. Modern technology systems must be built with tomorrow’s security risks in mind.
Compliance: The NIS Directive and its follow-on NIS2 Directive outline the responsibility for organisations to take reasonable steps toward a solid cybersecurity posture. This applies to the increasingly digital OT world because of the classification of many OT systems as a critical infrastructure.
Teams: Organisations need to recognise and confront the cultural silo separating OT and IT teams in order to reduce complexity, promote collaboration and achieve a reliable, frictionless state of OT/IT cybersecurity.
The cloud, data and device proliferation: When digital OT systems are infected, the attacks easily and quickly move laterally over a mesh of intersecting networks, carrying ‘digital germs’ with them. The risk here is high, particularly with the huge proliferation of devices and data from converged workloads in the cloud.
The future: There is a growing urgency from business stakeholders to make OT systems more digitally driven to ensure agility and efficiency. Boards that are now prioritising OT/IT cybersecurity are making a strong statement about the business implications to this strategy.
Next Steps
To help you understand and prepare for the cybersecurity risks inherent at the intersection of OT and IT, we have captured insights and recommendations from forward-thinking industry experts in a new guide: Executive Edge: Peer Insights - Complexity at the intersection of IT and OT.
This Peer Insights guide for C-suite executives explores how to streamline security, reduce complexity, and anticipate threats across the IT/OT environment, ultimately helping you drive change within your organisation.
In my journey to explore how I can use artificial intelligence to assist in penetration testing, I experimented with a security-focused chat bot created by Jason Haddix called Arcanum Cyber Security Bot (available on https://chatgpt.com/gpts). Jason engineered this bot to leverage up-to-date technical information related to application security and penetration testing.
For those of us in cybersecurity, there are a lot of unanswered questions and associated concerns about integrating AI into these various products. No small part of our worries has to do with the fact that this is new technology, and new tech always brings with it new security issues, especially technology that is evolving as quickly as AI.
A common use case for LLMs is rapid software development. One of the first ways I used AI in my penetration testing methodology was for payload generation.
This blog will cover how to root an AVD emulator and a physical Pixel 6. But before we cover those topics, let's cover what it is we will be doing and some of the pro/cons of rooting an Android phone.
VirusTotal has incorporated a powerful new tool to fight against
malware: JA4 client fingerprinting. This feature allows
security researchers to track and identify malicious files based
on the unique characteristics of their TLS client communications.
JA4: A More Robust Successor to JA3
JA4,
developed by
FoxIO, represents a significant
advancement over the older JA3 fingerprinting method. JA3's
effectiveness had been hampered by the increasing use of TLS
extension randomization in https clients, which made
fingerprints
less consistent. JA4 was specifically designed to be
resilient to this randomization, resulting in more stable and
reliable fingerprints.
Unveiling the Secrets of the Client
Hello
JA4 fingerprinting focuses on
analyzing the
TLS Client Hello packet, which is sent unencrypted from
the client to the server at the start of a TLS connection.
This packet contains a treasure trove of information that can
uniquely identify the client application or its underlying
TLS library. Some of the key elements extracted by JA4
include:
TLS
Version: The version of TLS supported by the
client.
Cipher
Suites: The list of cryptographic algorithms the client can
use.
TLS
Extensions: Additional features and capabilities supported
by the client.
ALPN
(Application-Layer Protocol Negotiation): The
application-level protocol, such as HTTP/2 or HTTP/3, that
the client wants to use after the TLS
handshake.
JA4 in Action: Pivoting and Hunting on
VirusTotal
VirusTotal has integrated JA4
fingerprinting into its platform through the behavior_networkfile
search modifier. This allows analysts to quickly
discover relationships between files based on their JA4
fingerprints.
To find the JA4 value, navigate to the "behavior" section of
the desired sample and locate the TLS subsection. In addition
to JA4, you might also find JA3 or JA3S there.
Example Search: Let's say you've encountered a suspicious
file that exhibits the JA4 fingerprint
"t10d070600_c50f5591e341_1a3805c3aa63" during VirusTotal's
behavioral analysis.
You can click on this JA4 to pivot using the
search query
behavior_network:t10d070600_c50f5591e341_1a3805c3aa63
finding other files with the same fingerprint This search
will pivot you to additional samples that share the same JA4
fingerprint, suggesting they might be related. This could
indicate that these files are part of the same malware family
or share a common developer or simply share a common TLS
library.
Returns files that match the
JA4_A and JA4_C components of the JA4 hash while allowing
for variations in the middle section, which often corresponds
to the cipher suite. This technique is useful for identifying
files that might use different ciphers but share other JA4
characteristics.
YARA hunting rules using the
"vt" module can be written to
automatically detect files based on their JA4 fingerprints.
Here's an example of a YARA rule that targets a specific JA4
fingerprint:
This rules will flag any file submitted to VirusTotal that
exhibits the matching JA4 fingerprint. The first example only
matches "t12d190800_d83cc789557e_7af1ed941c26" during
behavioral analysis. The second rule will match a regular
expression /t10d070600_.*_1a3805c3aa63/, only matching JA4_A
and JA4_C components, excluding the JA4_B cipher suite. These
fingerprints could be linked to known malware, a suspicious
application, or any TLS client behavior that is considered
risky by security analysts.
VirusTotal's adoption
of JA4 client fingerprinting will provide users with an
invaluable tool for dissecting and tracking TLS client
behaviors, leading to enhanced threat hunting, pivoting, and
more robust malware identification.
Microsoft introduced Data Protection Application Programming Interface (DPAPI) in Windows environments as a method to encrypt and decrypt sensitive data such as credentials using the…
Qakbot, familiarly Qbot, has been a major cyber threat since 2007, infecting victims’ computers to steal financial information and distribute additional malware payloads like ransomware. As a result of the takedown, more than 700,000 infected devices worldwide were identified and cleaned of the malware. The DOJ also announced the seizure of $8.6M in cryptocurrency in illicit profits.
While there is no doubt that the Qakbot takedown is a major win in the fight against cybercrime, it may only provide short-term relief in the fight against a notoriously resilient cybercriminal ecosystem.
‘Swiss Army knife’
A Swiss Army knife of cybercrime tools, Qakbot was a complex malware that opened remote access to victims’ systems, stole credentials and financial information, and downloaded additional malware payloads. Its modular architecture enabled frequent updates to add new capabilities over its 15+ years of operation.
“The collaborative endeavors of these authoritative bodies exemplify the power of a comprehensive, multi-agency approach, designed to maximize its impact..”
Ian Gray, VP Of Intelligence
Qakbot has been a versatile workhorse for cybercriminals. Its banking trojan functionality has been used to pilfer payment information and intercept financial transactions. As a loader, it distributed ransomware such as ProLock to extort victims.
Qakbot has also powered large-scale spam email campaigns and brute force attacks. Its worm-like spreading kept it entrenched in infected networks. By providing the backdoor access and distribution channel for other malware, Qakbot played a key supporting role in the cybercrime ecosystem. Botnets like Emotet and TrickBot operated similarly, loading additional threats onto compromised systems. These jack-of-all-trades botnets have proven lucrative for their criminal operators.
A history of temporary relief
Prior botnet takedowns like Emotet and TrickBot have shown that sophisticated malware operations can often rebuild infrastructure and return from disruptions in new forms.
In the case of Emotet, the botnet came back online in 2022 using new techniques after its infrastructure was dismantled in 2021. TrickBot also persisted despite takedown attempts and remains an active threat. This resiliency highlights the challenges law enforcement faces in permanently eliminating cyber threats.
While takedowns temporarily degrade capabilities, dedicated cybercriminal groups adapt to avoid further disruption. New malware families also inevitably emerge to fill the gaps left by larger takedowns. For example, BazarLoader and ZLoader rose to prominence as loader malware after the Emotet takedown.
Yet despite their disruptions, resilient botnets often return and new ones emerge. After prior actions against Emotet and TrickBot, the lingering demand in underground markets brought them back in adapted new forms. Bots remain attractive tools for cybercriminals thanks to their versatility, automation, and money generating potential.
While Qakbot’s infrastructure was disrupted, its operators may attempt to rebuild or evolve their techniques. Sustained pressure on botnet financial flows, developer communities, and other aspects of the cybercrime supply chain is needed to deter future attacks. For now, the coordinated Qakbot takedown bought time and degraded the capabilities of a dominant cybercrime player.
The fight against cybercrime must be persistent and comprehensive
The Qakbot takedown was effectively coordinated among global governments, including France, Germany, Latvia, Romania, the Netherlands, the UK, and the US, as well as the private sector. The collaborative endeavors of these authoritative bodies exemplify the power of a comprehensive, multi-agency approach, designed to maximize its impact.
Law enforcement and the private sector should to continue coordinating takedowns while also focusing on detecting new malware variants early, disrupting communication channels, and following the money trails of criminal enterprises.
Cyber hygiene and threat awareness across organizations must also improve to reduce vulnerability to malware infections, including loaders and trojans that distribute threats like Qakbot. Technical controls like endpoint detection, network monitoring, and patching are also key.
Ultimately, defeating cybercrime requires comprehensive strategy across law enforcement operations, cybersecurity practices, and international collaboration. The Qakbot takedown represents meaningful progress, but the world must remain vigilant against an adaptable threat landscape.
Get Flashpoint on your side
Flashpoint Ignite enables organizations to proactively identify and mitigate cyber and physical risk that could imperil people, places, and assets. To unlock the power of great threat intelligence, get started with a free Flashpoint trial.

 Login

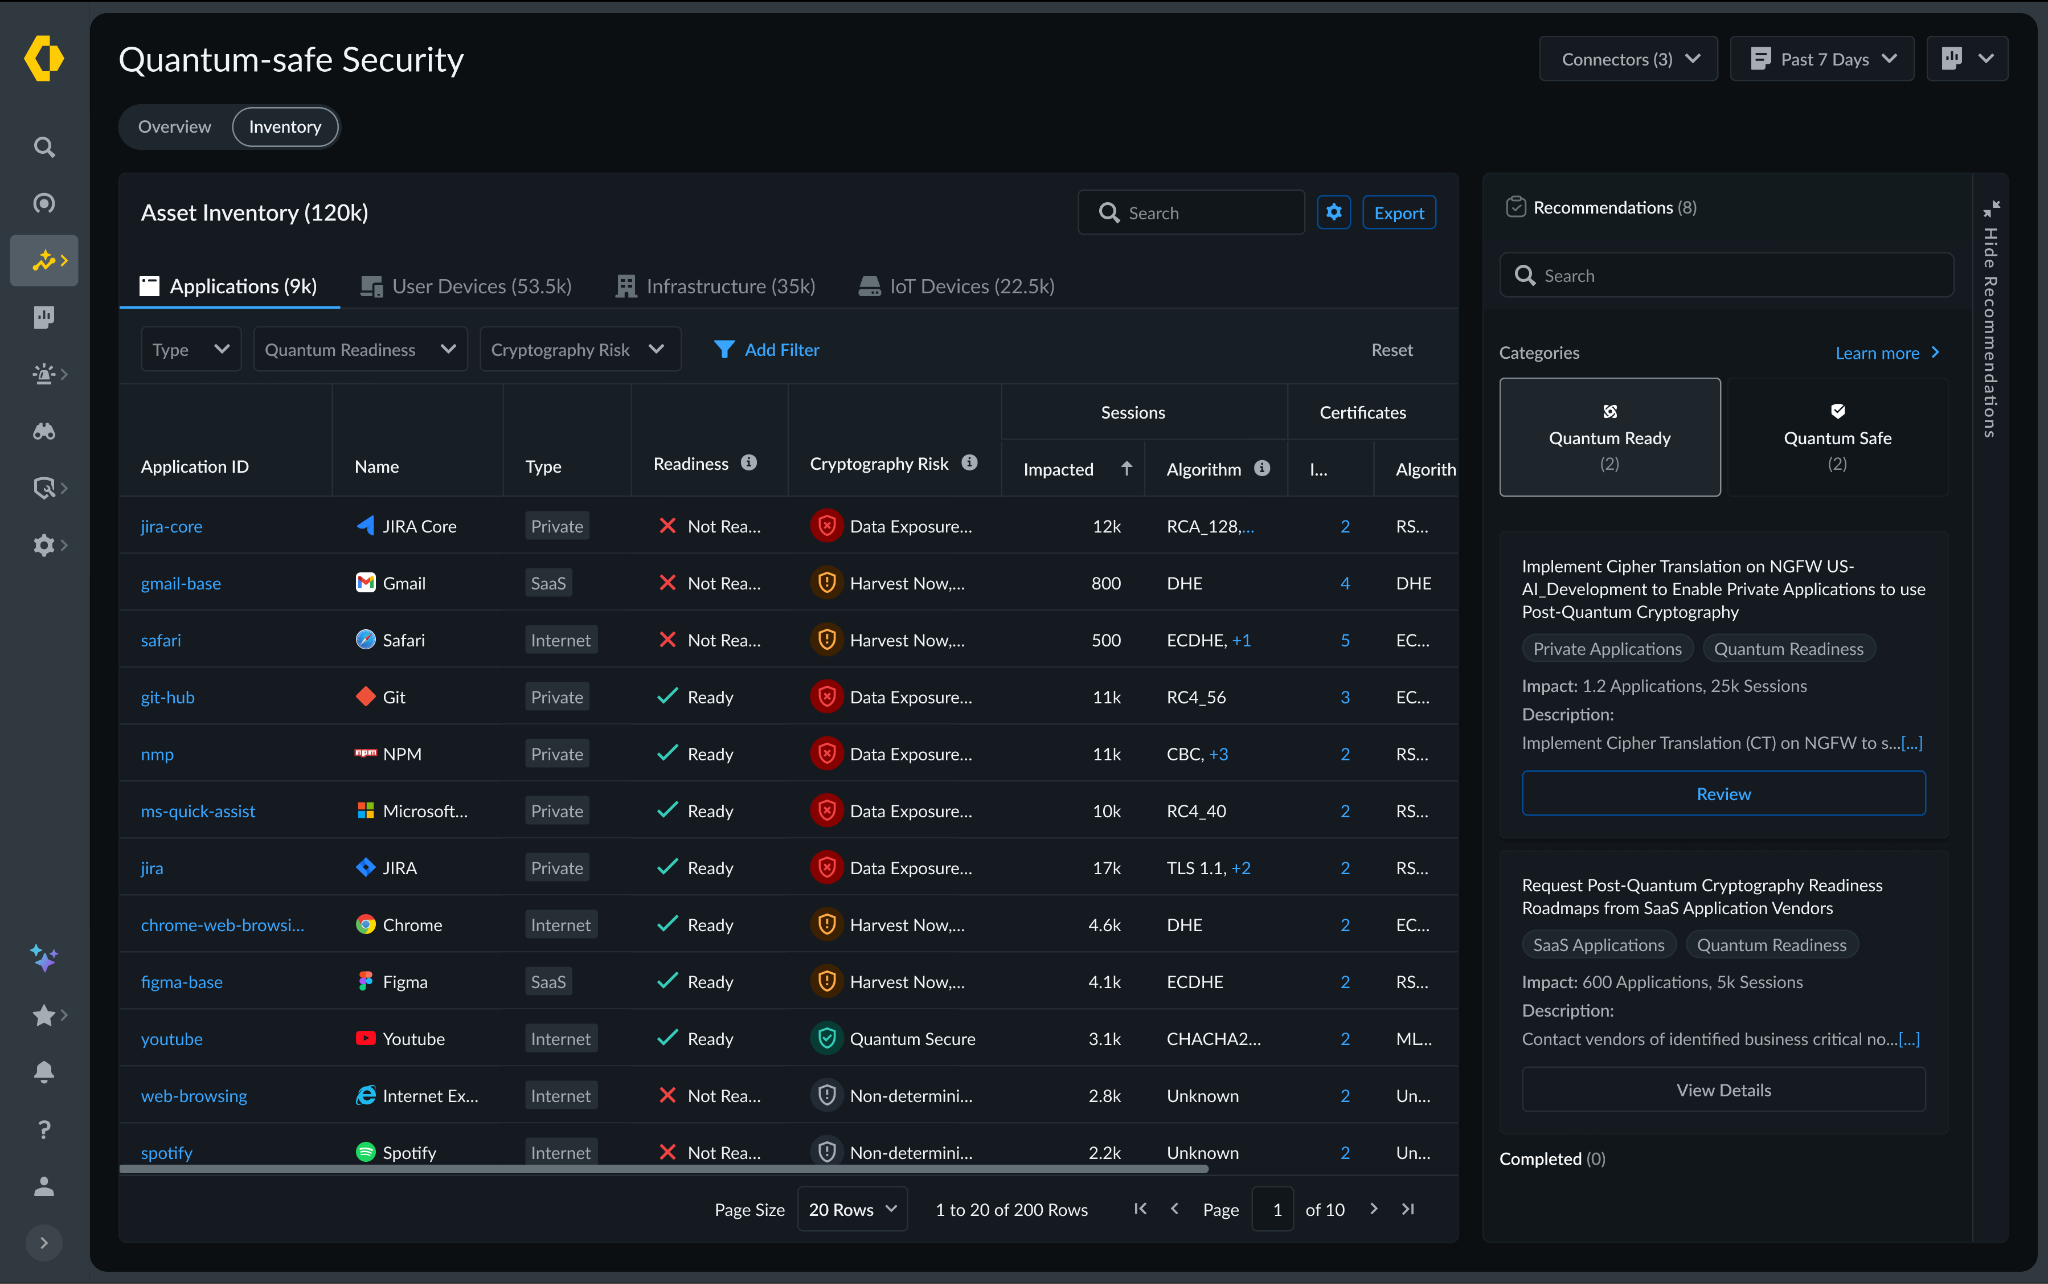
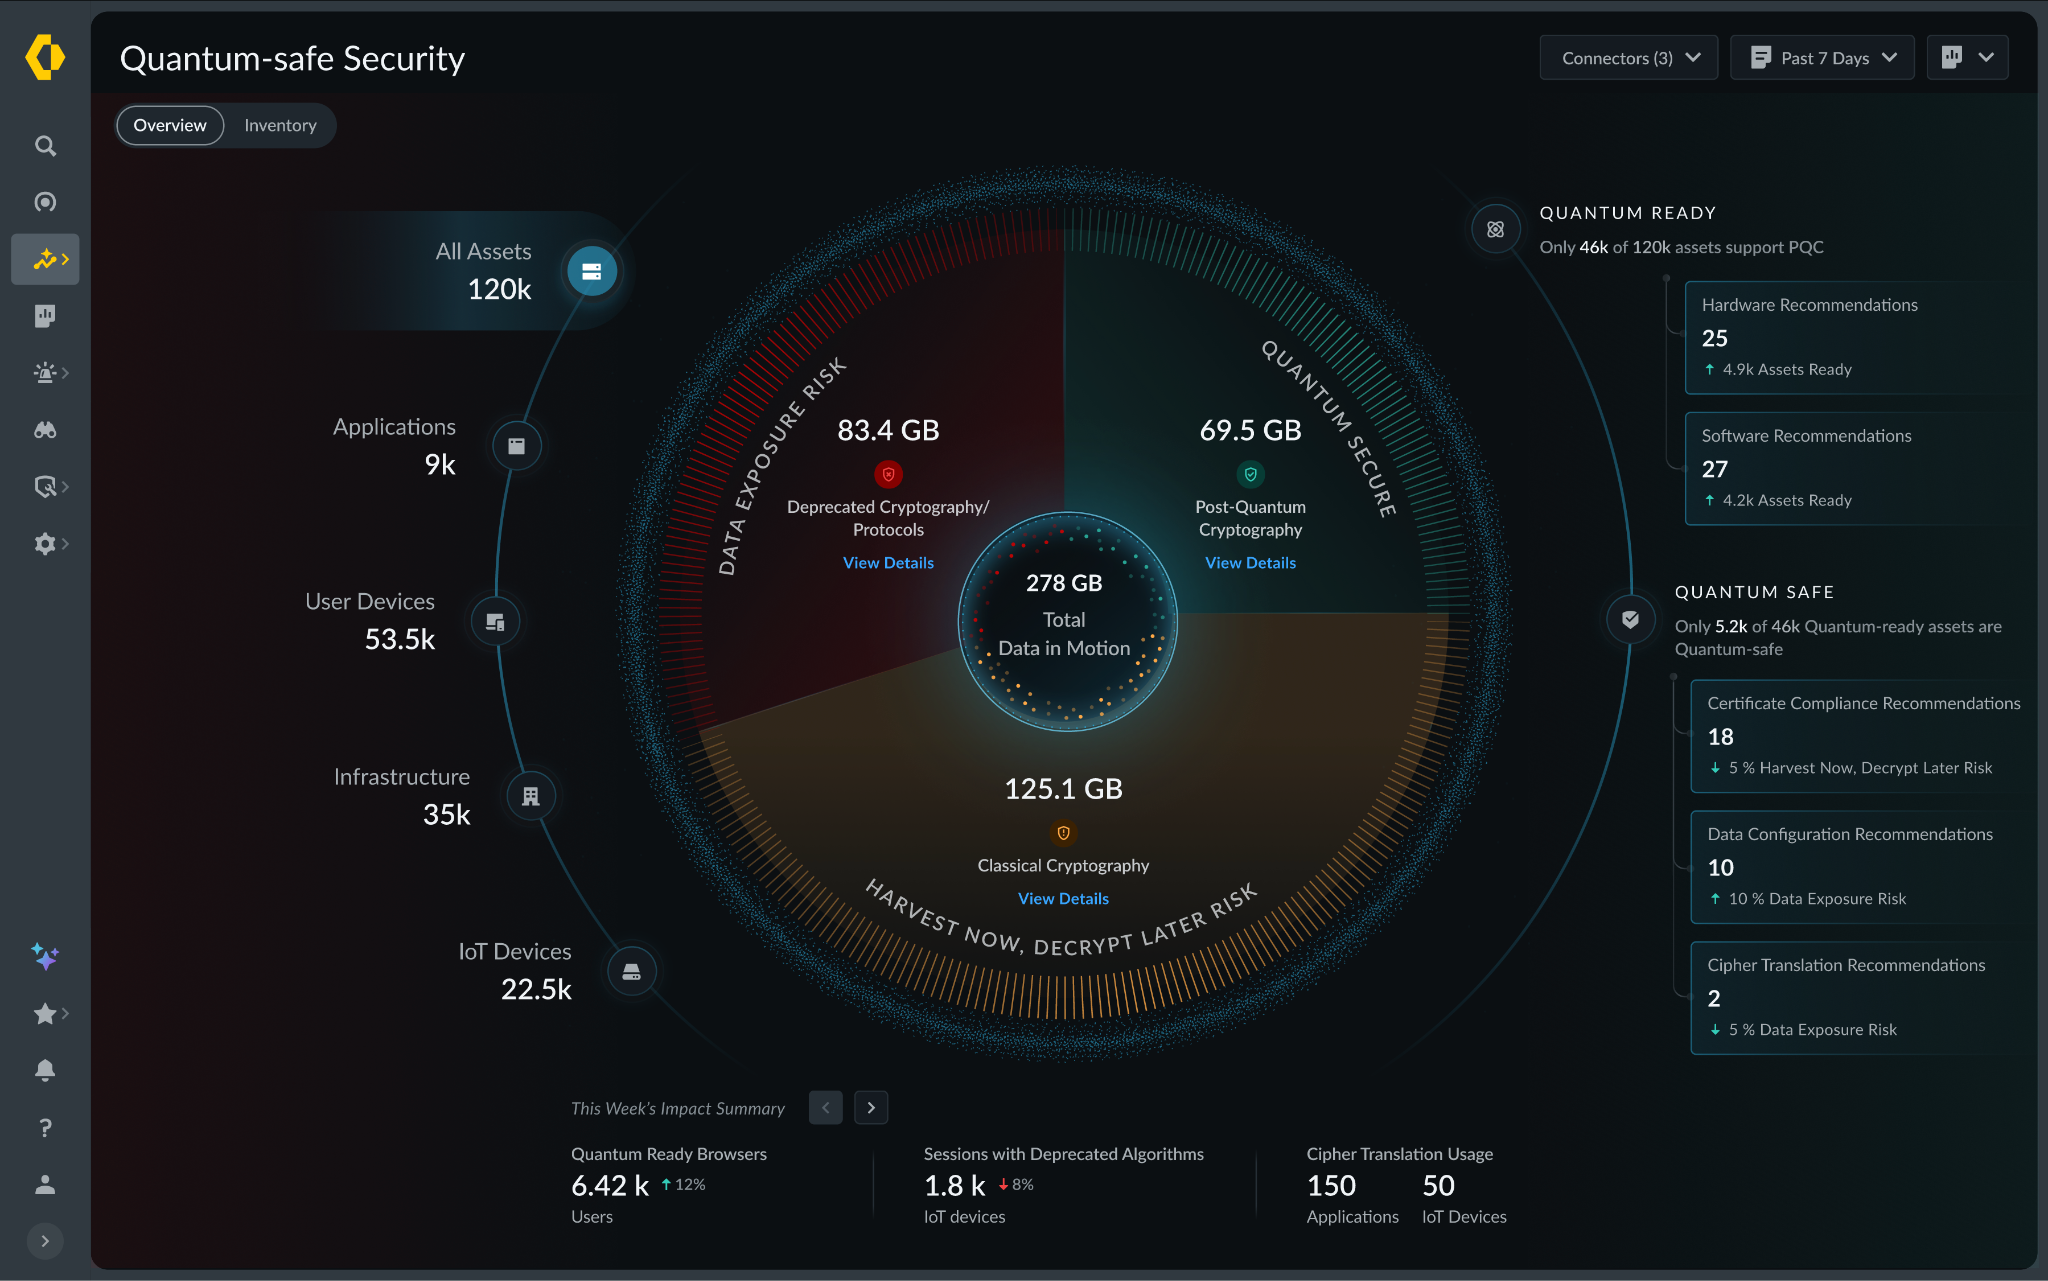
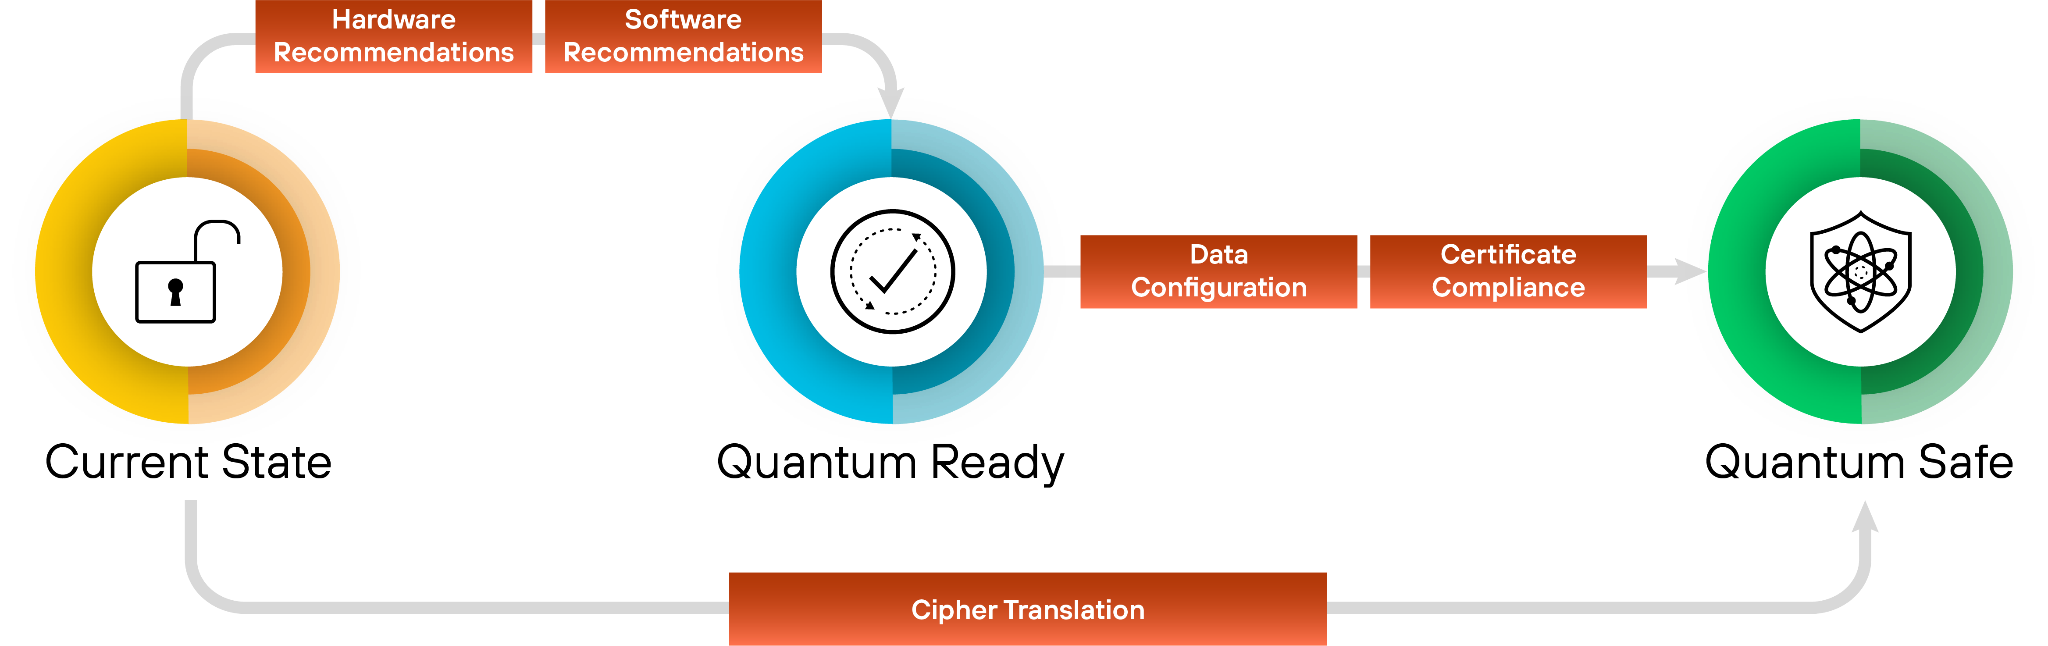
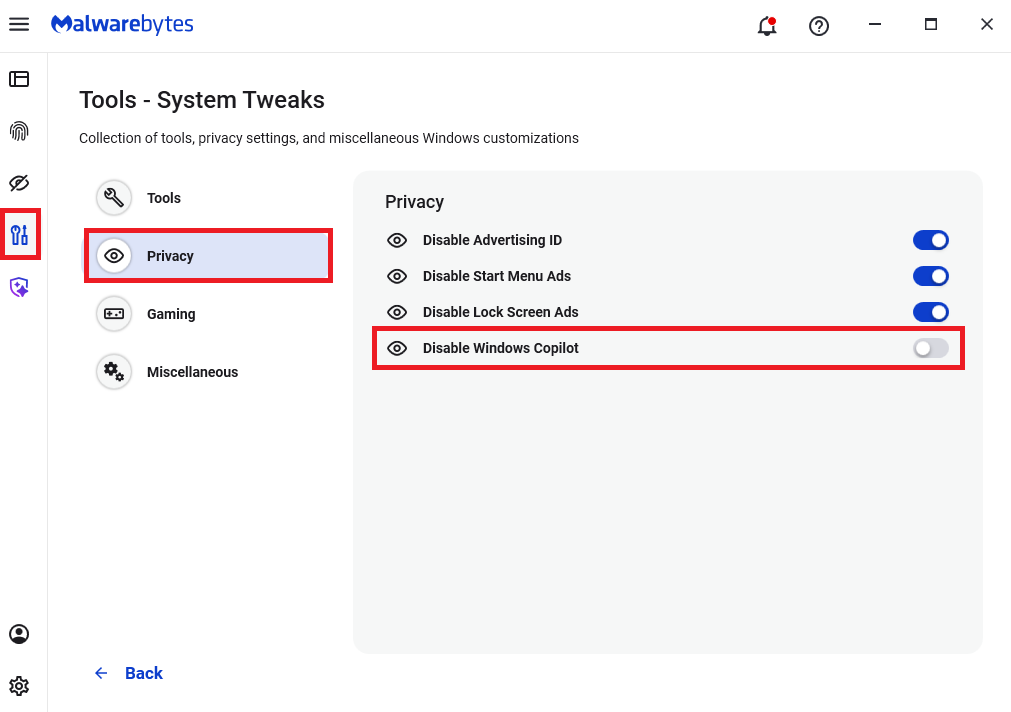
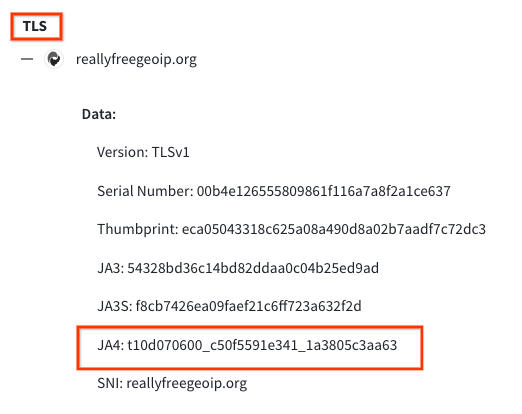

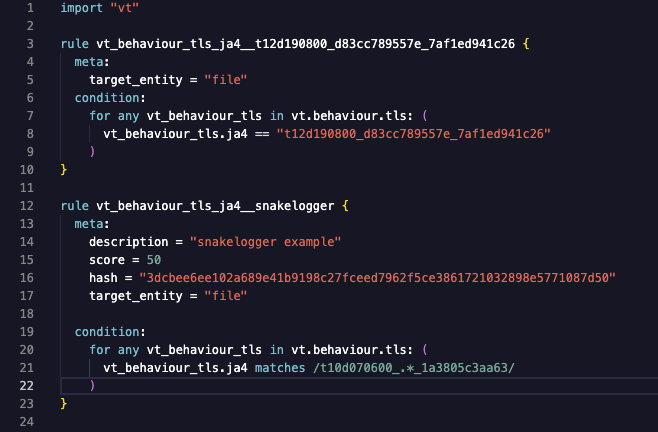


 Table Of Contents

