Matter-gebruikers kunnen inbouwapparaten makkelijker koppelen met NFC. Dit vervangt bluetooth, waardoor het apparaat bij de set-up geen stroomvoorziening nodig heeft. De functie zit in Matter 1.6, dat woensdag is uitgekomen voor fabrikanten.
Sometimes it happens. You’re happily playing a game on your phone or laptop when suddenly alarms pop up out of nowhere:
“Your device is infected!”
“Your iCloud is full!”
“Your account is restricted for watching porn!”
Some games can be played for free if you agree to watch ads, and in others you can get extra lives, perks, or boosters by watching ads. That’s fine, as long as you’re given a choice and the ads are legitimate.
Unfortunately, cybercriminals sometimes manage to buy advertising space and use it to defraud gamers.
Let’s look at some examples.
The iCloud storage scam, or its OneDrive equivalent, is a well-known and long-running scam that claims you need to expand your storage or all your files will be deleted. The websites these messages link to come in many forms, but they all ask for personal and payment details to complete the upgrade.
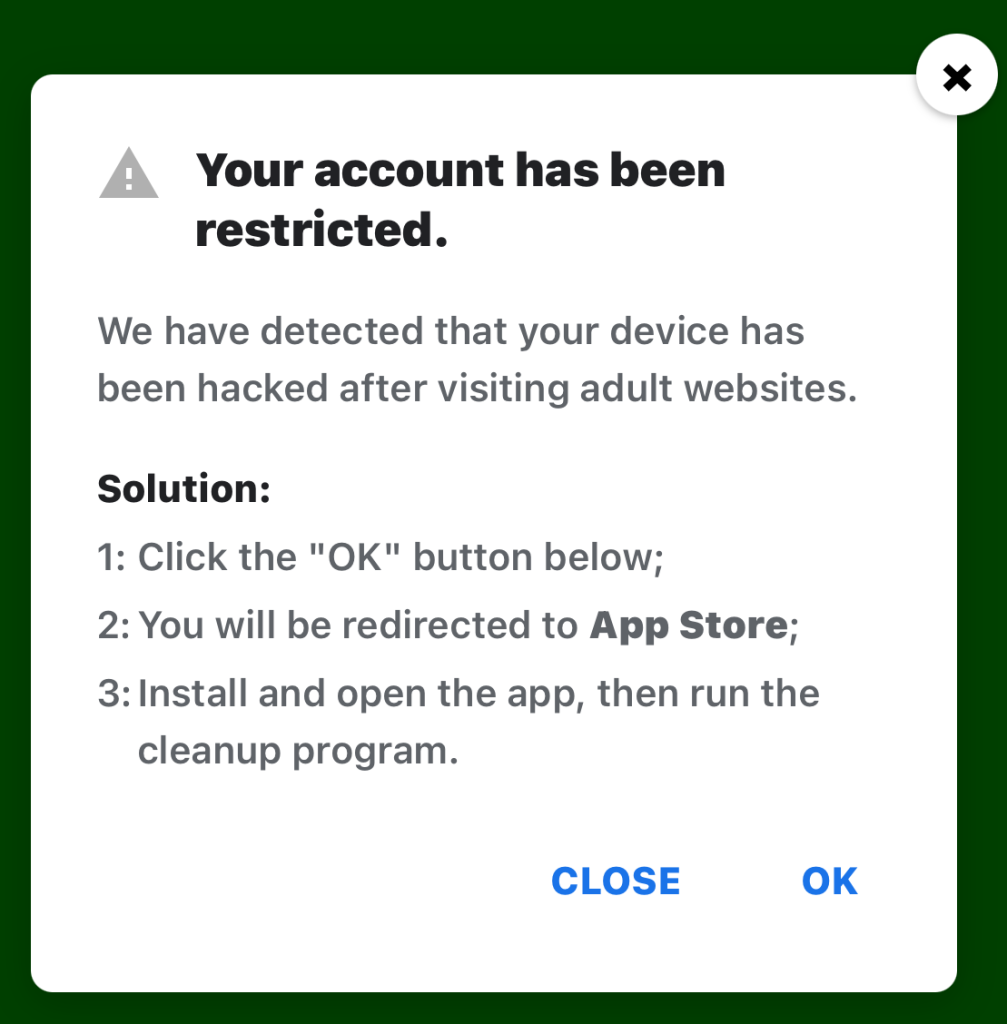
“Your account has been restricted. We have detected that your device has been hacked after visiting adult websites. Solution: 1:Click the “OK” button below;
2:You will be redirected to App Store;
3:Install and open the app, then run the cleanup program.”
This ad is a scam and uses a classic scare tactic. It falsely claims your device has been hacked and tries to pressure you into clicking “OK” and installing a cleanup app.
Messages like this sometimes claim to be from your ISP, a “Security Department,” or a generic “Safety Center.”
“Apple Security Alert 8 viruses have been detected on your iPhone. Now iOS is damaged by 72%. Further damage to the system will result in device lockup and loss of all data within two minutes. Please click the button below to remove all viruses.”
This is another fake warning, commonly used by scammers to trick users into clicking links or downloading unnecessary or harmful software. Apple doesn’t send alerts like this, and these messages use vague threats to get your attention.
What kind of app you’re really installing if you follow the instructions depends on your device and your location. If you’re “lucky,” it’s just adware, but you might just as easily end up with an infostealer.
In many cases, you’ll end up with fleeceware, a type of deceptive mobile app where developers lure users in with short free trials that quickly convert into hidden subscription fees, sometimes costing hundreds of dollars per month. These apps often offer some functionality to stay on the barely legal side of things, but at wildly inflated prices.
How to stay safe
The best response to these messages is simply to ignore them.
Real system alerts come from the OS, not from inside a game window or browser tab. Here’s a simple test: If you can switch apps and the “warning” disappears with the browser/game, it was not a system‑level alert.
Check the destination URLs before proceeding. Apple, Google, and major ISPs use predictable domains. A familiar-looking URL is not proof that a message is legitimate, but if the URL looks suspicious, it should definitely be treated as a scam.
You may arrive at something that looks like the official App Store or Google Play Store. Be wary of lookalike app stores and unofficial download sites, but if you are on the real store, the app is generally safer to install. However, it’s still worth checking reviews, permissions, and the developer before proceeding.
Visit the official website of the organization the message claims to be from and log in there. If there’s a genuine problem with your account, storage, or device, you’ll find information about it through official channels.
Use an up-to-date, real-time anti-malware solution on your devices that can detect and block malicious apps.
Scammers know more about you than you think.
Malwarebytes Mobile Security protects you from phishing, scam texts, malicious sites, and more. With real-time AI-powered Scam Guard built right in.
Threat actors are already gearing up for this year’s biggest football (soccer) event, the World Cup 2026. With millions of fans looking for ways to stream matches online, many will turn to IPTV apps to watch live TV broadcasts over the internet. It’s no surprise, then, that cybersecurity researchers have discovered multiple campaigns over the past few months where malware was disguised as fake Android IPTV apps.
In this post, we discuss what IPTV apps are, how criminals use fake versions to spread malware, what this malware is capable of, and, most importantly, how to avoid becoming a victim.
What are IPTV apps?
IPTV stands for Internet Protocol Television. This technology delivers TV content over the internet instead of through cable, over-the-air antennas, or satellites. Naturally, the simplest and most common examples of IPTV are the official platforms of TV networks, which can include both websites and dedicated apps.
However, alongside official options, pirate IPTV services also exist. They usually lure users with free or dirt-cheap access to content that can otherwise be hard to find without expensive subscriptions — most notably broadcasts of various sporting events; football matches in particular.
As is typically the case with pirated content, these apps are blocked from official app stores, forcing users to download them from third-party sites. Consequently, the risk of using these services isn’t tied to IPTV technology itself, but rather to the fake apps and modified APK files distributed under the guise of well-known platforms — both official and pirated.
Massiv banking Trojan disguised as IPTV apps
For instance, in February researchers found the Massiv banking Trojan distributed under the guise of fake IPTV apps. Even then, experts noted that this wasn’t the only malware leveraging this tactic — several others were also spotted in the wild. The primary targets of these IPTV-mimicking malicious fakes have mostly been users in Portugal, Spain, France, and Türkiye.
In most cases, the discovered fake IPTV apps lacked the advertised functionality, so users didn’t get access to any content after installing the apps. Instead, the fake app would open the website of a legitimate IPTV service in a built-in browser to mimic normal functioning and avoid raising user suspicion.
Of course, the most interesting activity happened out of the user’s sight. These are some of the features the malware did have:
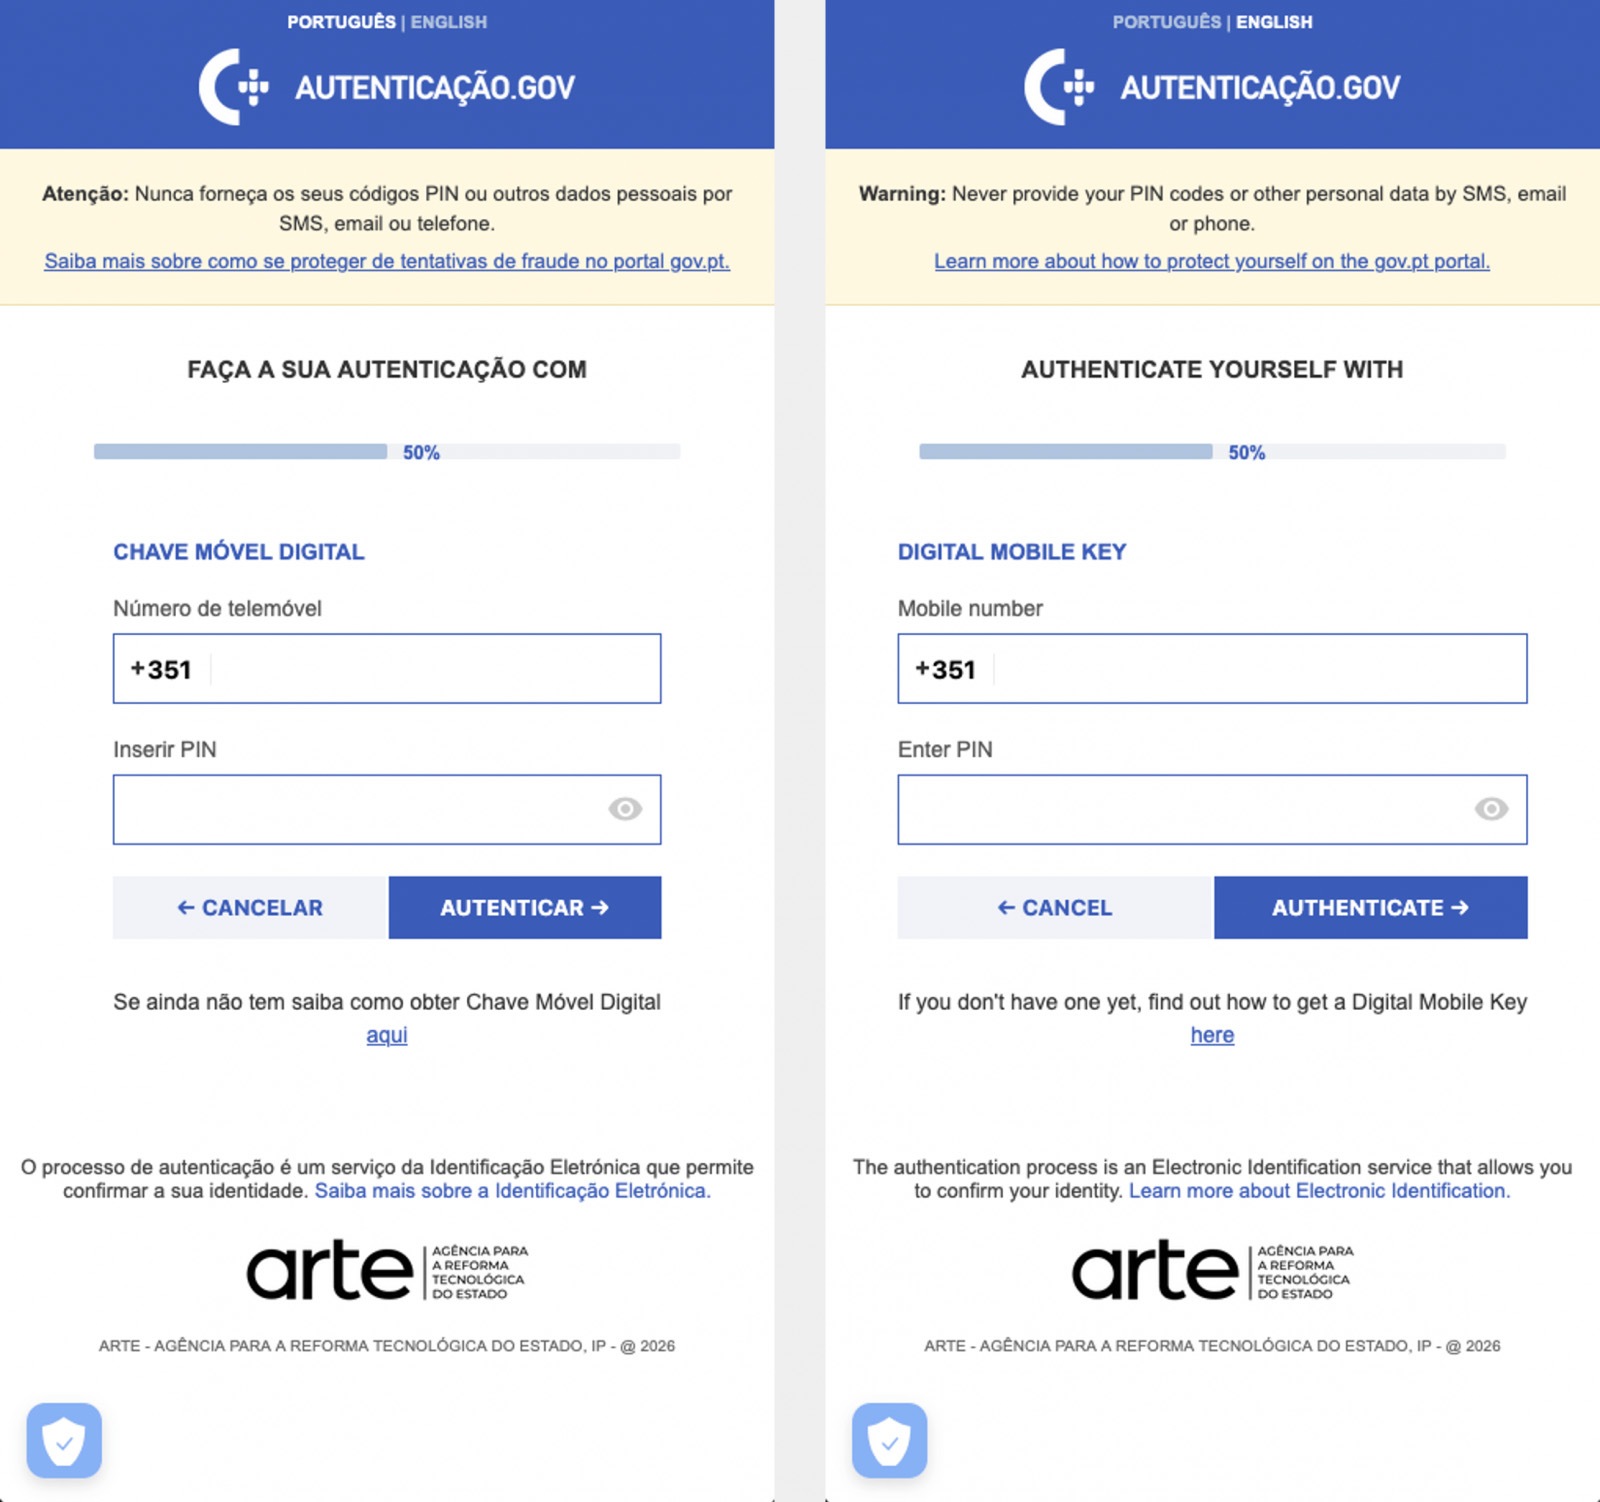
Displaying fake windows on top of legitimate ones: fake forms for entering bank details or signing in to official services, as shown in the screenshot below.
Activating a keylogger: recording and transmitting screen keyboard taps to the attackers.
Hijacking control of the compromised device.
The Massiv banking Trojan mimics the interface of the Portuguese government app Chave Móvel Digital in a fake pop-up window, looking even more convincing than the official version from Google Play. Source
Perseus steals valuable information from users’ notes
In March, researchers reported on a new campaign where several fake IPTV apps were used to distribute an even more advanced and feature-rich malware strain: Perseus.
Research into Perseus shows that the malware is based on the source code of an Android banking Trojan called Cerberus, which leaked nearly six years ago. Perseus comes in two different versions: Turkish and English. The English-language version is more advanced and shows clear signs of AI-driven refinement.
Perseus abuses Accessibility Services, a set of Android features originally designed to make life easier for users with severe visual impairments. Fraudsters learned long ago how to leverage this tool to steal data from Android devices — a topic we’ve covered in detail across several of our posts.
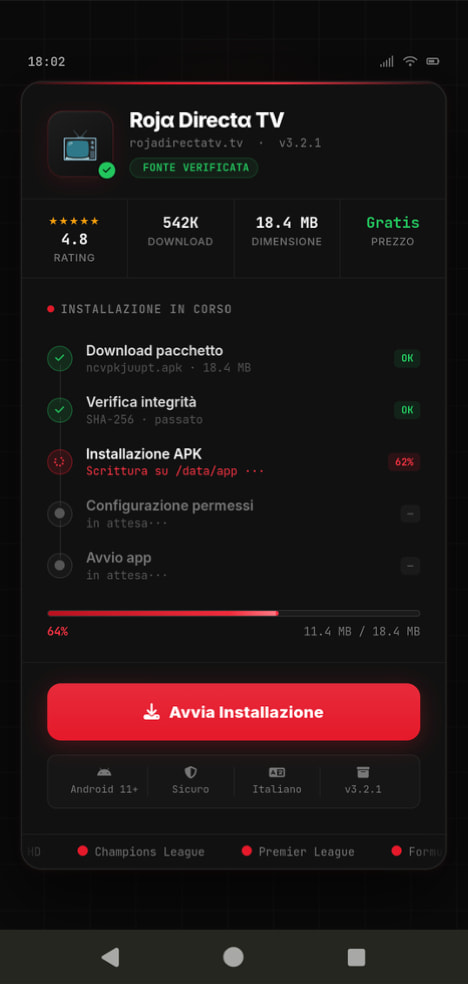
An example of a malicious APK disguised as Roja Directa TV, another IPTV app. Source
By abusing Accessibility Services, Perseus gains remote control over the victim’s device. Here’s what it can do:
Continuously capture and exfiltrate screenshots.
Send a structured map of the device’s UI for remote manipulation.
Mimic taps, swipes, text input, long presses, and other UI interactions.
Turn on the screen, launch apps, and block them from running.
Trigger a pitch-black screen overlay to hide its activities.
Log keystrokes.
On top of that, the English-language version of Perseus boasts another notable feature. The malware can hunt for sensitive information like passwords, recovery phrases, and financial data across an entire range of note-taking apps: Google Keep, Xiaomi Notes, Samsung Notes, ColorNote, Evernote, Microsoft OneNote, and Simple Notes.
All of these capabilities help criminals drain football fans’ money not just from various banking services, but from cryptocurrency apps as well.
How not to let cybercrooks ruin your World Cup
The World Cup is just around the corner, and millions of fans worldwide will definitely want to tune in to this year’s premier football event. Past experience shows that cybercriminals frequently cash in on major spectacles like this. So, how can you watch the matches safely?
Don’t download apps from unofficial stores.
Even when downloading an app from an official store — since malware occasionally slips through the cracks there, too— read the reviews carefully. Users who have been burned by fakes and malware often leave comments to warn others.
Avoid storing passwords or other sensitive information in note-taking apps. To ensure your data and finances stay secure, use a reliable password manager. By the way, Kaspersky Password Manager includes an encrypted note-taking feature, allowing you to store your valuable information safely.
You can’t even watch TV safely anymore these days! Check out other threats facing TV lovers:
The 2026 World Cup presents major cyber risks from ransomware groups, state-aligned actors, and other groups targeting critical infrastructure. Learn more here.
In May of last year, a warning about AI came from somewhere unexpected: The Auschwitz-Birkenau State Museum.
Posting publicly on social media, the museum warned about a Facebook account using generative AI to create fake images of people who died in the Holocaust. Despite using AI to generate fake images, the people in said images were sometimes real. They had real names, birthplaces, and stories of deportation that the Auschwitz-Birkenau State Museum itself had shared before. They had real faces captured in real surviving photographs, which were likely abused to generate the false images.
In other words, someone, or some team of people online, was deepfaking the Holocaust.
“These are not real photos of the victims. They are digital inventions, often stylized or sanitized, that risk turning remembrance into fictionalized performance. The history of Auschwitz is a well-documented story. Altering its visual record with AI imagery introduces distortion, no matter the intent.”
Months later, the public found out what that intent was: money.
A BBC investigation found an international network of Facebook accounts posting AI-generated images to earn money from those images’ potential virality. It’s a problem sometimes referred to as “AI slop” but it comes with a major incentive. When accounts that make these kinds of images are invited to Facebook’s content monetization program, they can make $1,000 a month for posting anything that gets clicks.
And on Facebook, the BBC found, that means several accounts posting AI-generated images about the Holocaust. As the BBC reported:
“AI spammers have posted fake images purporting to be from inside [Auschwitz], such as a prisoner playing a violin or lovers meeting at the boundaries of fences—attracting tens of thousands of likes and shares.”
The economics of lying are concrete today. People can use AI to make fake images that make people feel good about terrible things or feel scared about untrue things, and they can make money until shut down by the Big Tech platforms themselves, which, in this case, only happened because of the BBC’s investigation. In fact, it’s that type of inaction from social media platforms that compelled the German government and multiple Holocaust memorial institutions to send an open letter earlier this year that asked for better controls and restrictions against this type of content.
As the signatories warned in their letter, the economic appeal for these accounts to distort history is too high a risk to allow. You can read the full letter here.
Today, on the Lock and Code podcast with host David Ruiz, we speak with Clara Mansfeld, a historian working on digital communications at one of the institutions signed onto the open letter—the Foundation of Hamburg Memorials and Learning Centers Commemorating the Victims of Nazi Crimes. In their conversation, Mansfeld discusses digital access to history, the manipulation of factual records through AI-generated imagery, and the threat that society faces when it becomes harder to evaluate the truth.
“What happens when the first thought we have with every historical image is, ‘Is that even real or is that AI?’ I don’t think we have really grasped what that means for us as a society.”
Businesses are advised against paying – but many are prepared to deal to protect users’ privacy
After a week of outages, hundreds of millions of students’ data stolen, delayed assignment due dates and school login pages being defaced by hackers, the US tech firm Instructure – which operates the education platform Canvas, used by education providers worldwide – announced it had “reached an agreement with the unauthorised actor” behind the ransomware attack.
Experts read the careful language as a sign that a ransom has been paid. The company has not confirmed this.
Google’s Threat Intelligence Group (GTIG) heeft onlangs de eerste aanwijzing gevonden van een zero-day exploit die vermoedelijk door AI is ontwikkeld . Omdat zero-days kwetsbaarheden zijn waarvoor nog geen patch bestaat, hebben doelwitten geen tijd om zich voor te bereiden.
Na de gigantische hack rondom onderwijsplatform Canvas lijken meerdere Universiteiten te overwegen om hackerscollectief ShinyHunters te betalen. Dit willen ze doen om te voorkomen dat de privégegevens van miljoenen studenten en docenten op straat komen te liggen.
Google Chrome has been quietly downloading a 4GB AI model onto users’ devices without asking first.
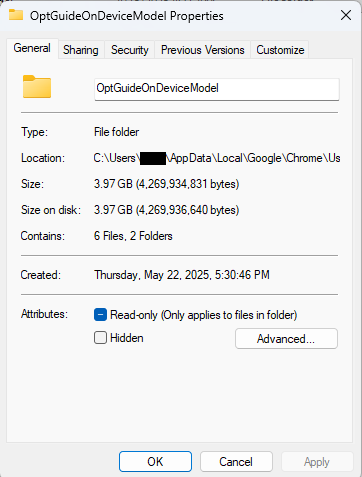
Security researcher Alexander Hanff, aka ThatPrivacyGuy, reports that Chrome has been silently installing Gemini Nano, Google’s on-device AI model, as a file called weights.bin stored in the OptGuideOnDeviceModel directory within users’ Chrome profiles. This 4GB download happens automatically when Chrome determines your device meets the hardware requirements. It does not ask for consent, and sends no notification—not even one of those annoying cookie banners you’ve learned to dismiss without reading.
The Gemini Nano model powers features like “Help me write” text composition assistance, on-device scam detection, and a Summarizer API that websites can call directly. These features are enabled by default in some recent Chrome versions. And here’s the kicker: if you discover the file and delete it, Chrome simply downloads it again.
Why this matters
Let’s start with the obvious problem: a 4GB download isn’t trivial for everyone. If you’re lucky enough to have unlimited fiber internet, you might not notice. But for users on metered connections, mobile hotspots, or in developing countries where data is expensive, Google just cost them real money without permission. For rural users or those with bandwidth caps, this kind of silent transfer can blow through monthly limits in minutes.
Hanff focuses on the environmental angle. He calculated that if this model were pushed to just 1 billion Chrome users (roughly 30% of Chrome’s user base), the distribution alone would consume 240 gigawatt-hours of energy and generate 60,000 tons of CO2 equivalent. That’s not including actually using the model, just the downloads.
But to us, the most troubling aspect is the broader pattern this represents. Just a few weeks ago, we reported another unsolicited AI invasion on our personal computers discovered by Hanff. He documented how Anthropic’s Claude Desktop app, which silently installed browser integration files across multiple Chromium browsers, including five browsers he didn’t even have installed. The integration would reinstall itself if removed, and it also happened without any meaningful user disclosure.
Hanff argues that both cases likely violate EU privacy law, specifically the ePrivacy Directive’s rules about storing data on user devices and the GDPR’s requirements around transparency and lawful processing. While these claims haven’t been tested in court, they highlight a fundamental tension: can companies just install whatever they want on your computer as long as they say it’s a feature of an app you installed?
Google might argue that having an AI on your device provides better privacy than cloud-based alternatives. Which is generally true, but it does not apply here, since Chrome’s most prominent AI feature—the “AI Mode” pill in the address bar—doesn’t even use the local model. According to Hanff’s analysis, it routes queries to Google’s cloud servers anyway.
All in all, users see a 4GB local AI model and reasonably assume their data stays private, when in reality, the most visible AI feature sends everything to Google’s servers.
Tech companies need to stop treating silent deployment as acceptable practice. We see no valid excuse for this. Your device is yours. The storage is yours. The bandwidth is yours. And the electricity bill is yours.
What happened to asking for permission? And when I remove it, I want it gone permanently—not automatic reinstallation.
When are the tech giants going to learn that we don’t want to be left discovering after the fact that our devices have become deployment targets for features we never asked for.
Update May 12, 2026 with do it yourself instructions
How to check if the AI model is on your computer (Windows)
Open File Explorer
At the top of the File Explorer window, click the address bar and paste:
%LOCALAPPDATA%\Google\Chrome\User Data
Press Enter
Look for a folder named:
OptGuideOnDeviceModel
If you see it, Chrome has likely downloaded the AI model
Properties of the folder
How to check on a Mac
Open Finder
In the menu bar at the top of the screen, click Go > Go to Folder
Paste:
~/Library/Application Support/Google/Chrome/
Look for a folder named:
OptGuideOnDeviceModel
Now, remember, this isn’t malware, and its presence doesn’t mean your computer is infected.
Turn off Chrome AI features
This part is relatively easy. You may find online instructions telling you to edit the Windows registry or use Chrome policies, but for most people the simplest and safest approach is to disable the features directly in Chrome.
We don’t recommend manually editing the registry unless you fully understand what you’re doing. Incorrect changes can cause system problems.
Instead, try this first:
Open Chrome
You can copy and paste this directly into Chrome’s address bar and press Enter:
chrome://settings/ai
On the page that opens, you can turn off features such as:
“Help me write”
AI summaries
On-device AI features
The exact options may vary depending on your Chrome version and region.
Then restart Chrome to make sure the changes take effect.
This may stop Chrome from downloading or using the AI model, although some users report the files can return after browser updates.
There is probably no need to delete the files unless you specifically need the storage space.
If chrome://settings/ai does not work, the feature may not yet be available in your region, you may be using a managed work or school account, or your version of Chrome may not support these settings yet.
Do you need to delete the OptGuideOnDeviceModel folder?
You can, but there is probably no need to.
If you disable Chrome’s AI features, the downloaded model should no longer be actively used for those features. Leaving the files in place may also prevent Chrome from downloading them again at a later point.
Browse like no one’s watching.
Malwarebytes Privacy VPN encrypts your connection and never logs what you do, so the next story you read doesn’t have to feel personal. Try it free →
DarkSword is a sophisticated piece of malware—probably government designed—that targets iOS.
Google Threat Intelligence Group (GTIG) has identified a new iOS full-chain exploit that leveraged multiple zero-day vulnerabilities to fully compromise devices. Based on toolmarks in recovered payloads, we believe the exploit chain to be called DarkSword. Since at least November 2025, GTIG has observed multiple commercial surveillance vendors and suspected state-sponsored actors utilizing DarkSword in distinct campaigns. These threat actors have deployed the exploit chain against targets in Saudi Arabia, Turkey, Malaysia, and Ukraine.
DarkSword supports iOS versions 18.4 through 18.7 and utilizes six different vulnerabilities to deploy final-stage payloads. GTIG has identified three distinct malware families deployed following a successful DarkSword compromise: GHOSTBLADE, GHOSTKNIFE, and GHOSTSABER. The proliferation of this single exploit chain across disparate threat actors mirrors the previously discovered Coruna iOS exploit kit. Notably, UNC6353, a suspected Russian espionage group previously observed using Coruna, has recently incorporated DarkSword into their watering hole campaigns.
A week after it was identified, a version of it leaked onto the internet, where it is being used more broadly.
This news is a month old. Your devices are safe, assuming you patch regularly.
AI-assistenten en autonome agenten worden een steeds groter onderdeel van ons leven, maar bescherming is op dat gebied nog schaars. Althans, dat is wat Norton VPN zag toen het besloot een speciale, en de allereerste, VPN voor Agenten te ontwikkelen.
When a major cyber incident hits, the first decisions aren’t technical—they’re human. Who takes the lead? How quickly can information be shared? When should governments step in, and how do you protect public trust while keeping essential services running?
These questions are at the heart of Microsoft’s Advancing Regional Cybersecurity (ARC) initiative, launched in 2025 to help governments strengthen cyber preparedness through practical, public-private collaboration. Today, we’re sharing the first tangible output of that work: the ARC Kenya Exercise Report & Toolkit, developed through a tabletop exercise held in Nairobi in December 2025.
Developed with Kenya’s National Computer and Cybercrime Coordination Committee (NC4) and RiskSight, the toolkit is a practical planning resource designed to help government and cross-sector leaders prepare for cyber crises before they occur. It is grounded in real conversations among leaders from government, regulators, critical infrastructure operators, law enforcement, academia, and the private sector working through what a serious cyber incident would demand of them, together.
Stress‑testing decisions before a crisis hits
The ambition of the “Silicon Savannah” makes Kenya a compelling setting for this work. Its digital economy is expanding rapidly—from mobile‑first financial services to cloud‑enabled public infrastructure—positioning the country as a regional technology leader. But rapid digital growth also brings increased exposure to more sophisticated cyber threats. As systems become more interconnected, a serious cyber incident can quickly disrupt essential services, undermine public trust, and threaten economic stability.
Kenya’s approach recognizes this reality and reflects a critical principle: cybersecurity is not separate from innovation; it is one of the conditions that allows digital transformation to scale safely. The ARC initiative embodies this philosophy and helps decision makers confront the practical realities of coordination, escalation, and response in this complex environment.
This is exactly what the ARC Kenya tabletop exercise was designed to do. The objective was not to test tools but to stress‑test decision making under pressure. Participants were challenged with complex scenarios—including AI‑enabled breaches, ransomware attacks, and infrastructure‑level disruptions. The focus was not on technical fixes but on leadership clarity, cross‑agency coordination, and real‑time decision making in high‑pressure environments.
The outcome was both a roadmap for the unknown and a clear recognition of the need for shared expectations before a crisis begins—particularly around leadership and authority, trusted information sharing channels, and agreed response frameworks. These gaps, identified by participants themselves, now form the backbone of the ARC Kenya Toolkit.
What the ARC Kenya toolkit delivers
The toolkit translates the lessons of the exercise into concrete actions that leaders can take now—before the next incident occurs. It also serves as a practical and specific 12‑month roadmap for strengthening Kenya’s cyber preparedness, moving from lessons identified to durable, institutional capability. Specifically, the toolkit provides recommendations to:
Clarify national leadership during major cyber incidents, enabling government, regulators, law enforcement, and critical infrastructure operators to coordinate more quickly, with fewer gaps and overlaps.
Establish practical, standards‑aligned incident response models for the entire country, including priority playbooks that teams can train on and execute consistently.
Strengthen operational readiness across sectors, with better coordination between security operations centers (SOCs), clearer escalation thresholds, and more reliable incident reporting pathways.
Deepen trusted information sharing and public‑private collaboration through common handling rules, safer “good‑faith” reporting mechanisms, and regular joint exercises to build muscle memory before a crisis.
Taken together, these elements enable leaders not only to respond more effectively to cyber incidents, but to institutionalize preparedness, coordination, and resilience across the national cyber ecosystem. For African countries more broadly, the model also offers a practical pathway to strengthen regional cyber cooperation—by aligning expectations around escalation, information sharing, and public‑private coordination before a cross‑border incident occurs. By translating high‑level principles into practical, repeatable approaches to crisis readiness, the toolkit underscores the value of trusted international partnerships and alignment with global norms for responsible state behavior in cyberspace.
Why Kenya’s approach matters beyond its borders
Many countries across the Global South are grappling with similar challenges: fragmented ownership of critical infrastructure, uneven cyber capacity across sectors, and the need to coordinate rapidly under pressure. While firmly grounded in Kenya’s national context, the lessons from ARC Kenya are therefore intentionally designed to resonate far beyond its borders and to be highly transferable.
Importantly, this work does not end in Kenya. We are already building on these lessons through ARC engagements in other regions, including a new workstream in Mexico, applying the same approach to strengthen preparedness, coordination, and resilience across different national contexts.
By design, the ARC initiative is not simply a record of a single exercise. It is a foundation others can build on—at a national or regional level—offering leaders a practical starting point to turn shared responsibility into sustained capability.
For more than a decade, the Microsoft Digital Crimes Unit (DCU) has persistently disrupted cybercrime and nation-state threats targeting people, organizations, and critical infrastructure. Explore major disruptions—and the ongoing cases and operations behind them here: Disrupting cyberthreats since 2008 | Microsoft

 Login