❌

Normal view

Received — 30 October 2026 ⏭ Kaspersky official blog

How to download and read ebooks safely | Kaspersky official blog

30 October 2026 at 17:02

Contrary to a common misconception, people haven’t stopped enjoying books in the digital age. The truth is that for a while now, reading on paper hasn’t been the only way to enjoy the written word.

At first glance, what cybersecurity risks could there possibly be? But then, since there are more than a billion e-book readers in the world, cybercriminals are bound to try to cash in. We spoke with Andrey Sidenko, Head of Child Online Safety at Kaspersky, to learn how criminals exploit interest in e-books, and what to look out for so you don’t become a victim yourself.

Malware instead of a book

Most often, scammers target computer and smartphone users who try to download an e-book from a pirate site. For example, our experts recently discovered a miner spreading this way: it was tapping the processing power of infected computers to generate various cryptocurrency tokens. Several of these sites let visitors read e-book excerpts for free. In reality, the attackers were stealing passwords and using a malicious script to swap links: users got an archive with malware named the same as the book they wanted. What’s more, links to these sites sat at the top of search results, so the risk of taking the bait was very high.

A year ago, we also wrote about fake e-books in Turkish or Arabic. These files were actually malicious executables disguised as ordinary PDFs. Once launched, they installed infostealers on the victim’s device: malware that sent chat-app session tokens, browser files, saved passwords, and crypto wallet data to the cybercriminals.

Traps in search results

Sites that engage in search spam pose a danger of their own. Picture this: you search for “The Lord of the Rings free download” — and land on a page that repeats your search phrase word for word and supposedly offers that very book for download. But instead of the book you were hoping for, you may be redirected to yet another sketchy site and treated to a malicious file.

By the way, this scam can work even if you search for a made-up author and a made-up book. Such sites can automatically generate plausible download pages for just about any query.

Book phishing

There are also phishing scams aimed squarely at book lovers. For example, one group of scammers sent out fake emails to users pretending to be from the popular book community Goodreads, offering various bogus (paid) services, which, alas, some recipients fell for: becoming a moderator, taking part in book events, or buying a paid promotion.

Here’s another example: ads supposedly from Orell Füssli, a well-known Swiss bookstore chain, circulated on social media. The ads offered books at hefty discounts. To place an order, users had to follow a link and enter their bank card details. Our regular readers will have no doubt guessed that the link led to a fake site, which in this case simply set up a paid subscription billed to the victim’s card.

Finally, scammers often create phishing sites that pose as pirate libraries. These libraries no longer cater only to fiction readers: readers go there for textbooks, academic papers, studies, rare editions, and other material that’s hard to find publicly. Because such libraries get blocked regularly and have to keep changing domains, it can be hard for users to tell the real site from a fake one.

Attackers take advantage of precisely this by promoting their own sites as official mirrors. These fake sites are often fully functional: you can search for and download books just like on the real thing, and the design is almost indistinguishable from the original. In 2024, for example, data on almost 10 million users of a phishing site mimicking Z-Library, a platform providing free downloads of access-restricted books and publications, was leaked online.

The leak included names, email addresses, countries of residence, password hashes, purchase details, and even crypto wallet addresses. With data this detailed, it’s easy to plan a follow-up attack: say, posing as a police officer to accuse the person of visiting an illegal site and demand money to drop the criminal case.

Can an e-reader get infected?

For attackers, e-readers aren’t the juiciest target: it’s hard to predict what device someone uses, or whether that person even has internet access. Besides, most e-readers are basic models — essentially a flash drive with a screen.

But there are more advanced devices — with internet access, browsers, and the ability to download third-party apps and use cloud storage. These are more likely targets, but let’s be honest: most of the time, it’s cybersecurity researchers who hack them — not criminals. For example, in 2025, researchers discovered a vulnerability in the Kindle that could let an attacker hijack the linked Amazon account.

Data leaks and other less obvious risks

Some e-readers let you highlight quotes, take notes on books you like, and share either with other users. Attackers can use this data for doxing, especially if a person wants to keep quiet about reading a particular book — something like, say, Fifty Shades of Grey, or anything personal that isn’t meant for the public.

In 2020, a Guardian journalist requested a copy of her personal data from Amazon, and received more than 20 000 records regarding how she’d used her e-reader. These included which books she read and when, how long she spent reading them, which passages she highlighted or copied, and which words she looked up in the dictionary.

So it’s worth treating your reading history as personal data too. If a book service leaks data, or your account gets hacked, a bad actor could learn not just your email address but far more personal details.

So how do you read e-books safely?

One of the simplest tips is to use official bookstores — and not just for copyright reasons. Since these platforms value their reputation, their content is vetted — meaning the files are more trustworthy.

Another essential tip is to update all your devices regularly — even the most basic e-reader: if it runs an operating system and any software — keep those updated. Timely updates close vulnerabilities that attackers could exploit, which lowers the risk of being hacked. The same goes for apps for reading and cataloging e-books: this year, researchers found serious vulnerabilities in both Calibre and Koodo Reader.

Note that installing unofficial firmware on your devices — for example, closed-ecosystem e-readers like Kindle — may not be the best idea. Risks include bricking the device and losing your warranty. The device may die or lock up during flashing or later on — when an automatic over-the-air update installs official firmware. The manufacturer may also block your account if it detects the modified firmware when the device goes online. And, naturally, the firmware itself may carry malware, such as stealers that siphon off your personal data and passwords. The fact that there’s no way to install an antivirus on your e-reader only exaggerates the potential problem.

It’s also a good idea to back up your digital library from time to time. Buying a book doesn’t guarantee you’ll keep access to it in your account forever. A title may become unavailable because of changes to licensing terms, platform policies, or other restrictions. What’s more, some formats can only be bought and read inside the e-reader’s closed ecosystem. So we recommend keeping a backup copy on your computer or another device, where you can get to it quickly offline. That way, you’ll keep access to your content even if something goes wrong with either the book service or your device.

Every time you download an e-book, be sure to check the file extension. A regular e-book filename should certainly not end in .exe or .bat. You can read more about the most common extensions of malicious files here.

With scammers, alas, getting better and better at disguising malware, perhaps the best all-around advice is this: don’t visit dubious websites, and don’t download unknown files. This is where Kaspersky Premium comes in: one of its main features is protection against phishing and malware. The application warns you if you try to visit an untrustworthy site, or download a potentially dangerous file. This keeps your data and money safe, and you can download and read your favorite books with peace of mind.

Love the written word? Check out our other posts about books:

Received — 19 September 2026 ⏭ Kaspersky official blog

Detection blind spots: non-standard file formats in malicious email campaigns | Kaspersky official blog

28 August 2026 at 19:12

Threat actors are constantly developing new attack schemes — from OAuth token theft to attacks on AI agents — but the classics never quite leave their playbook. On any given day, an employee may receive malware attached directly to an email, or lying in wait behind a link embedded in an email. Making these attacks succeed still requires a degree of creativity, and in recent years attackers have increasingly adopted exotic file formats. Users don’t perceive these formats as dangerous; more importantly, many EDR and email security solutions skip scanning them entirely. Yet they’ve proven highly effective for deploying malware or harvesting credentials.

Below are the file types that may be blind spots in your organization’s detection strategy — despite being observed as used in real-world attacks.

Disk images

This is the broadest and most dangerous attachment category. A disk image can contain a fully prepared, correctly structured set of files tailored to a wide range of attack scenarios. It mounts as a separate volume (standalone virtual disk), and when doing so often uses tools built into the operating system. The victim doesn’t need to extract anything or create suspicious folders on disk.

The most versatile format is ISO, which dates back to the heyday of multimedia CDs. ISO images mount natively on every major OS without additional utilities, whether through simple tools like File Explorer or via the command line interface. This is precisely why threat actors have no hesitation in sending ISO files as email attachments.

Somewhat less common are IMG containers, which also mount without additional tooling on macOS or Linux, but require installing a small, free utility such as OSFMount on Windows, or using WSL2 (Windows Subsystem for Linux), which is built into recent Windows versions. A file with identical content may also carry a DD extension.

Threat actors also make use of VHD, a virtual disk format native to Windows, which generally works on Linux machines as well (via qemu-nbd or guestmount). On macOS, an additional utility — again, qemu-nbd is a common choice — is required to mount it. Note that on unpatched Windows systems, the victim doesn’t need to take any further action after the disk mounts: CVE-2025-24993 — a vulnerability actively exploited in real-world attacks — triggers attacker code execution immediately upon mounting the image.

For completeness’ sake, VMDK, the disk image format used by VMware, is also worth detecting, though it’s largely ineffective in attacks on regular users since every popular OS requires additional software to mount it.

All of these image formats can be viewed and unpacked not only with specialized tools, but with standard archive utilities like 7-Zip or RAR. As a result, the odds that the user will fall for the bait are higher than one might hope.

In addition to not being a well-known potentially dangerous format, image files give attackers one further advantage: files extracted from disk images on Windows frequently lack the Mark of the Web flag, and therefore can be launched without triggering additional system warnings.

There’s one more reason why EPP/EDR solutions must scan virtual machines and disk images: these formats are also used during later stages of an attack. To mask active file-system activity from monitoring tools, ransomware gangs sometimes run the entire encryption process inside a virtual machine deployed on the victim’s computer. The RagnarLocker ransomware strain has used VirtualBox for this purpose, while the CRON#TRAP campaign relied on a QEMU environment.

MS Office files

No, this isn’t about macro-laced DOC files. Microsoft has grown weary enough of this classic attack vector that macros in downloaded documents are now blocked outright, and enabling them requires considerable effort from the user. But Office relies on dozens of file formats, and some of the less common ones still occasionally give attackers an edge.

Less familiar to both users and security solutions are OneNote files (.one). These are essentially simple notes, but they can carry embedded attachments, including not just images and links, but VBS/WSF/BAT scripts as well. Within the note, an attachment normally displays as an icon, but attackers overlay it with a picture showing a message with a “View” button.

Another Office format popular with attackers is the Excel add-in. These files use the .xll extension but are, in effect, full-fledged Windows dynamic-link libraries (DLLs), and therefore may have extensive functionality. Victims receive a malicious email with what looks like an invoice; the icon suggests that the file will open in Excel. Ignoring the security warning may result in an infostealer infection.

SVG “graphics”

The description of the SVG (Scalable Vector Graphics) format sounds entirely innocuous. Indeed, 99% of SVG files are logos and interface icons. But unlike PNG or JPG, SVG files are fundamentally XML documents, and beyond points, lines and fills they can contain JavaScript. In terms of malicious potential, SVG is not far behind a full web page. In real-world attacks, SVG files can redirect a user to a phishing page immediately upon opening, or render the phishing page directly by unpacking a Base64-encoded block into full HTML.

SVG files pose a distinct risk to corporate portals that accept user file uploads. If a portal’s Content Security Policy (CSP) isn’t sufficiently restrictive, and lets someone upload a malicious SVG file, the embedded JavaScript can steal cookies from the page, inject unauthorized content, and carry out similar attacks.

Polyglot files

Polyglot file formats are less exotic in and of themselves, but the files carry more than meets the eye. They’re called polyglots because attackers construct a file that can be validly interpreted in multiple ways: for example, it can be a valid ZIP archive and a valid executable at the same time. The purpose is purely to evade detection by security solutions and deceive the user. We’ve covered polyglots in detail in a separate blog post.

The clear standout in our roundup is a malicious campaign distributing the IcedID infostealer. Victims receive emails with a ZIP attachment, which unpacks into an ISO disk image. That further unpacks into a CHM file (the Windows Help format) that’s also correctly processed as an mshta (Microsoft HTML Application host) application, which then downloads the primary malware payload.

Defending against exotic files

These attacks rely on the assumption that security solutions either don’t scan unusual file formats, or scan them only superficially. Preventing the threat starts with not operating on that assumption with regard to your own infrastructure:

  • Configure EDR, web, and email filters to scan all of the file formats described above.
  • Process archives and disk images with the same rigor as you would apply to executables.
  • Detonate potentially dangerous file types in a sandbox, and configure recursive unpacking of nested formats through to the end of the chain: ZIP → ISO → CHM.
  • Where feasible, quarantine all file formats anomalous for email — disk images in particular.
  • Build detection rules for anomalous usage patterns that involve exotic files. For example, unusually small disk images are rare and are therefore worth investigating.
  • Review the technical documentation of your security solutions to confirm that complex formats are detected through deep structural parsing rather than magic-byte checks alone.
  • Deploy behavioral detection capable of flagging anomalous execution patterns and legitimate utilities launched from unexpected contexts. The usual suspects here include mshta, git, wscript, hh, and rundll32.
  • SVG files warrant a dedicated policy. Treat SVGs as active content at the email and web perimeter. On corporate portals, enforce a strict CSP, and serve user-uploaded files from a separate subdomain so that a malicious script embedded in an SVG can’t access the session on the main portal.

Received — 7 August 2026 ⏭ Kaspersky official blog

Dangerous email attachments: the files you should never open | Kaspersky official blog

7 August 2026 at 11:57

Have you ever tried to open an “encrypted” email or an urgent document, only to realize with horror that your usual DOCX attachment is actually a file with the extension .docx.exe? Or maybe you received an email supposedly with an invoice, contract, or internal memo attached — only for the file to prove something entirely different from what it claimed to be? If so, you were likely targeted in a malware infection attempt.

Cybercriminals routinely disguise malicious files as harmless documents and archives, banking on recipients blindly clicking without checking the extension. Kaspersky experts analyzed the file formats most frequently deployed in malicious email blasts to reveal what really lurks behind these extensions — and how attackers weaponize them in their campaigns.

Important note: the extensions we’ll be discussing here are routinely used for completely legitimate files. For example, Windows executables normally end in .exe. However, we’re focusing specifically on scenarios where attackers disguise or spoof a file’s extension to pass it off as a totally different type of file.

What extensions are most commonly found in malware?

Our experts analyzed malicious email blasts from the beginning of 2026 to pinpoint the 15 most common dangerous file extensions.

.exe
.js
.html
.dll
.bat
.vbs
.xls
.pdf
.jse
.au3
.docx
.htm
.wsf
.scr
.lnk

The top 15 file extensions used in malicious email blasts

Let’s take a look at what files with these extensions actually do under the hood.

Executable files

An executable file is a compiled computer program that’s ready to run. Once launched, a malicious executable can download additional payloads, alter system settings, steal user data, connect your device to external attacker-controlled servers, and much more. These are the most common executable extensions found in malicious email campaigns:

  • .exe
  • .dll
  • .com
  • .scr

.exe

The classic Windows executable extension. It powers every program you use daily, from web browsers and games to office suites and software installers.

By the way, attackers often wrap EXE malware in double extensions: invoice.docx.exe, report.pdf.exe, or even photo.jpg.exe. They take advantage of a default Windows setting: hiding extensions for known file types. Because this setting is turned on by default, users only see the first part of the file name — invoice.docx, report.pdf, or photo.jpg — and assume it’s just a normal document or image. But the second you open this trap file, the malware fires up.

.dll

Another common extension abused in malicious campaigns is .dll (dynamic-link library). These libraries hold functions that Windows programs frequently require while running, such as printing a document. This modular architecture prevents redundant code by letting multiple applications call on the exact same library for specific tasks. However, if an attacker replaces a legitimate library with an infected one, running any normal program that calls on it can trigger malicious code.

.com

While files with the .com extension have absolutely nothing to do with the web domain of the same name, cybercriminals likely count on victims mistaking these files for links in an unusual format. In reality, it’s a legacy Windows executable format.

While modern versions of Windows no longer rely on this file type, the operating system can still run and execute it, which makes opening one a very bad idea.

.scr

SCR files are screensavers — those idle Windows screen animations featuring abstract patterns, the iconic bouncing logo, or whatever else. Despite their harmless reputation, screensavers are essentially executables just like EXE files: once opened, they can install extra components or alter system settings all the same. In malicious campaigns, these files routinely masquerade as images, screenshots, or documents.

Scripts

Scripts are text files containing a sequence of commands that a computer runs automatically in order. They can download files, install and launch programs, modify security settings, and plenty more. Email attackers rely on the following script types most often:

  • .js and .jse
  • .bat
  • .cmd
  • .vbs
  • .wsf
  • .vbe
  • .au3

.js and .jse

The .js and .jse extensions are used by JavaScript files. Most users associate JavaScript strictly with websites and don’t realize these files can run locally on their computer as standalone programs.

We recently wrote about CrystalX RAT, a remote access Trojan that logs keystrokes, steals clipboard contents, and injects malicious components into web browsers upon installation. Its JS scripts monitored cryptocurrency wallet addresses and silently swapped them with the attacker’s own to hijack transactions in real time.

.cmd and .bat

BAT and CMD files are designed to automate tasks in Windows and can execute virtually any command in the operating system. Launching a file like this can infect your computer with malware.

.vbs

Visual Basic Script files with the .vbs extension are a long-time favorite among cybercriminals. Attackers frequently use double extensions to disguise .vbs files as plain text documents, such as invoices, app installation guides, or emails. For example, in the early 2000s, the iconic ILOVEYOU worm spread via a VBS script, infecting millions of computers worldwide. Victims received an email with the subject line “ILOVEYOU”, but instead of a sweet confession, the attachment contained a malicious script. At its peak, this “romantic” worm had infected up to 10% of all internet-connected computers.

Web files

This category mainly includes .html, .htm, .hta and .svg files. Often these are phishing pages in disguise, designed to mimic login forms for email, cloud services, banking apps, and other platforms. Naturally, any credentials entered on these fake pages go straight to the attackers hunting for your accounts and money. Web files can also trigger malicious scripts and download additional payloads onto your system.

Archives

Cybercriminals routinely package malicious files inside archives (most commonly having .zip, .rar, and .7z extensions). These archives are often password-protected or encrypted to hinder content scanning. Additionally, attackers sometimes create intentionally corrupted archives with damaged data structures: basic security filters often stumble over broken files and skip scanning them altogether, whereas archive managers can automatically repair and unpack the contents anyway.

That’s why we recommend using advanced security solutions that can spot phishing emails and prevent you from launching dangerous files hidden inside archives.

PDF files (.pdf)

To many, PDF feels like a completely harmless file format — after all, what could go wrong with flight tickets, documents, and slide decks? But beyond static text and images, PDFs can host clickable links, forms, and even scripts.

Malicious code in a PDF is usually tucked away behind visual elements or embedded as hidden text. What’s more, the risk comes not just from the file itself, but also from the software you use to view it: for instance, attackers spent months exploiting a vulnerability in Adobe Acrobat that allowed them to execute malicious PDF files remotely. If you regularly work on PDF documents, make sure the JavaScript feature is disabled in your Adobe Acrobat. To do this, go to Preferences → JavaScript in the menu.

By the way, heavy users of AI agents and chatbots should keep in mind that AI frequently falls for prompt injections: hidden commands buried inside images, text, and web pages that the AI interprets as legitimate instructions, and executes without your knowledge.

LNK shortcuts (.lnk)

Files with the .lnk extension are standard Windows shortcuts that we use every day for quick access to apps and folders. By themselves, shortcuts don’t contain any software — they simply tell Windows what file to open or what command to run.

However, an attacker can give a shortcut any icon and any name they want, completely hiding its real destination. The moment a victim clicks the shortcut, the infection chain kicks off. The malicious code usually executes silently in the background, leaving virtually no visual clues that anything went wrong.

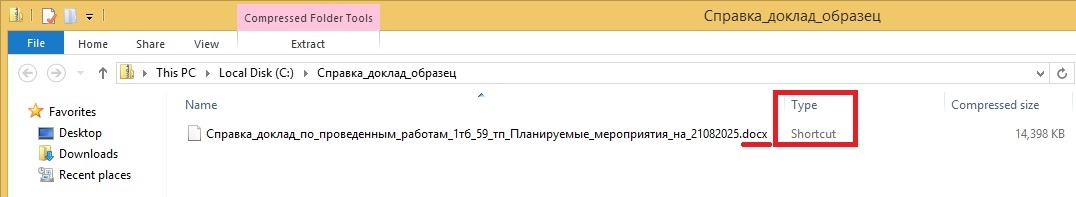
Cybercriminals also like to hide LNK files behind double extensions — betting that users won’t look close enough to see what kind of file they’re actually opening. Here’s a classic example:

Attackers use double extensions to disguise malicious LNK files

Windows File Explorer displays only the first part of the extension, .docx. The file type is clearly listed as a shortcut, but very few people notice that detail

Your best bet is to avoid clicking incoming LNK files altogether: no one in their right mind has a reason to email you a desktop shortcut.

By the way, if you haven’t updated Windows in a while, we’ve bad news for you: malicious code can automatically execute without you ever clicking the LNK — simply opening the folder where it lives is enough to trigger it. Microsoft finally released a patch for this long-abused vulnerability in December 2025. So don’t put off system updates — install them regularly to patch up the security holes attackers rely on.

Microsoft Office documents

.xls and .xlsx

The file extension .xls is used by older versions of Microsoft Excel. Millions of people use Excel spreadsheets every day, and many are still running outdated software, which makes XLS files a favorite bait for cybercriminals. Budgets, employee rosters, financial records, urgent reports, and other spreadsheets stop being harmless the moment a user clicks Enable Content, allowing the program to run macros — custom Microsoft Office scripts and commands built into the files. Once allowed, the malicious macro gets free rein to download files, launch programs, harvest system data, and alter settings.

Unlike XLS, XLSX is the modern Excel format, which doesn’t support embedded macros by default. Unfortunately, that doesn’t guarantee complete safety: the spreadsheet can still pull live data from external sources and automatically connect to web destinations in the background.

.docx

Although modern DOCX files don’t support macros by default, attackers have long figured out other ways to weaponize these documents. Typically, malicious DOCX files contain embedded links or instructions that force Word to contact external servers and pull down malicious payloads. Back in 2023, for instance, researchers uncovered a Microsoft Office vulnerability that allowed attackers to trigger built-in Windows system tools and download malware straight from the web.

To reduce your risk when working with Microsoft Office apps, we recommend turning on Protected View, blocking external connections, and disabling all macros without notification.

Macro support in modern Microsoft Office

Macros are sequences of commands that automate complex, repetitive tasks in Excel, Outlook, Word, and PowerPoint. In modern versions of Microsoft Office, documents containing embedded macros are saved in specialized file formats with extensions like .xlsm, .xltm, .xlsb, .docm, and .pptm. While Microsoft Office includes built-in security controls — such as blocking files downloaded from the web and warning you about potentially dangerous macros — if you don’t actually use macros and have no specific reason to run them, treat files with these extensions with caution.

How to check if a file is safe

  • Use a comprehensive security suite that automatically scans files for malware, prevents infections, blocks visits to suspicious sites, and completely removes malicious files from your devices. You can take advantage of a 30-day trial of Kaspersky Premium if you urgently need to disinfect your computer or scan a file for viruses.
  • Never open attachments from unknown senders. Curiosity can cost you dearly, since many malware strains specifically hunt for credit card and crypto wallet data. Let the Mail Anti-Virus feature included in our security solutions do the heavy lifting: it automatically filters out malicious or suspicious emails and protects you from phishing attacks.
  • Examine incoming emails carefully: cybercriminals have become adept at disguising malicious messages. Always verify email addresses against official ones and make sure you know the signs of phishing and spam. Attackers might try to scare you with claims of a hacked account, lure you to shady sites with “unbeatable deals”, or urge you to review a work document attached to the email. Any attempt to manipulate your emotions is a major red flag that someone is trying to trick you.
  • Never open files with double extensions. It’s almost always a trap.
  • If you run into a file with an unfamiliar extension, take a moment to look it up online. Remember: a photo or plain text document will never have an .lnk or .vbs extension.

Check out our other posts on email and file security:

Received — 18 June 2026 ⏭ Kaspersky official blog

World Cup 2026: watch out for these scams | Kaspersky official blog

The World Cup attracts a great many fans — but also a great many scammers. While millions of fans tune in to watch the matches, cybercriminals are hard at work trying to get at their money and personal data. In fact, we’ve already flagged more than 336 fake websites designed to look exactly like the official World Cup page! As the biggest sporting event of the year heats up, here are the top red flags you need to watch out for.

Totally Legit Free Streams (No Scam)

Scoring a seat at WC26 has turned into quite the mission. Soccer fans are furious over ticket prices, which have officially been dubbed the highest in World Cup history. On top of lodging and travel costs, the situation is made even worse by America’s stringent immigration policies — where referees, team staff, and even players have faced major visa and entry headaches. But fans still want to watch the games, and that’s exactly where fake streaming platforms step in to “help”.

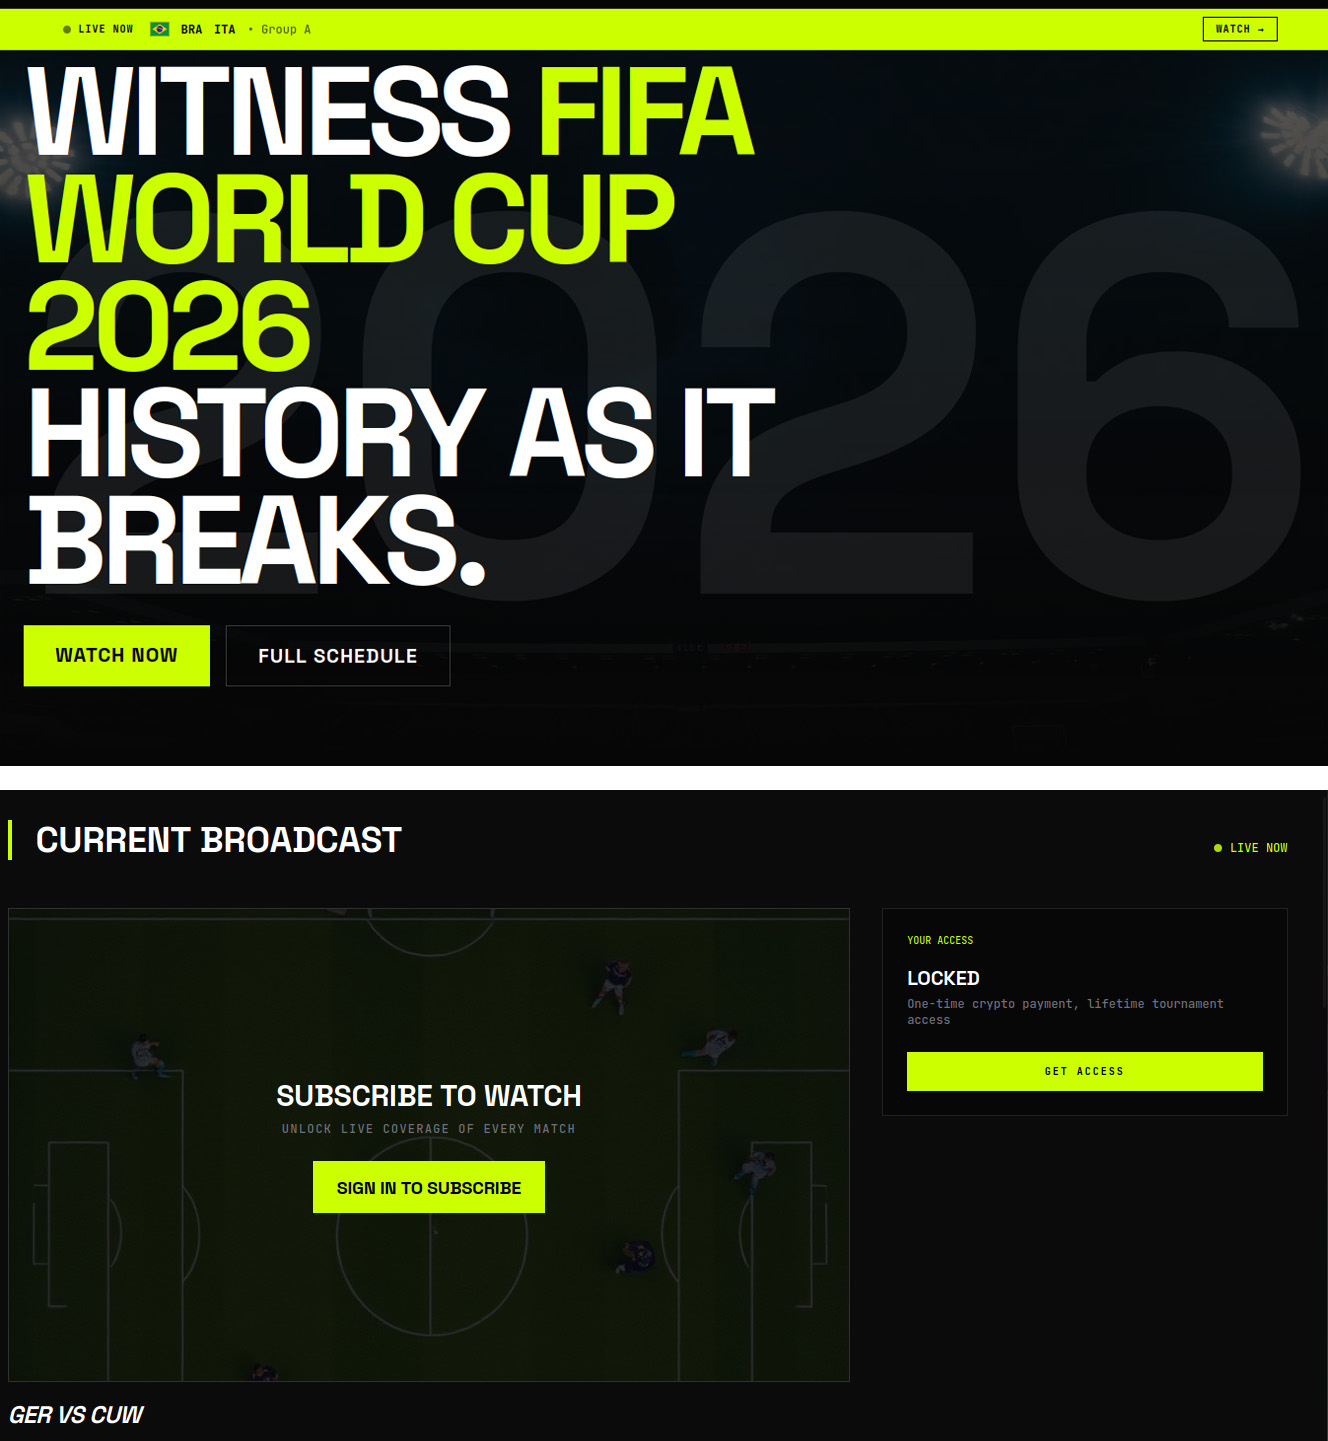
Here’s how the scam plays out: cybercriminals set up fake websites promising free access to World Cup match streams. But the moment you click Watch Now, you’re prompted to sign up and then pay for “lifetime access” to the entire tournament. In the example below, they’re asking for cryptocurrency — which is still a bit unusual, since scammers typically prefer good old-fashioned bank cards.

An example of a fake video streaming website requiring users to register and pay with cryptocurrency to watch all World Cup 2026 matches

An example of a fake video streaming website requiring users to register and pay with cryptocurrency to watch all World Cup 2026 matches

Fans who are desperate to catch their favorite teams live risk losing not just their money, but also their personal data, which hackers can later weaponize in targeted phishing attacks.

A losing bet

Match result predictions and sports betting always skyrocket in popularity during the World Cup, and scammers waste no time cashing in on the trend. And behind the flashy slogans lie classic scam tactics.

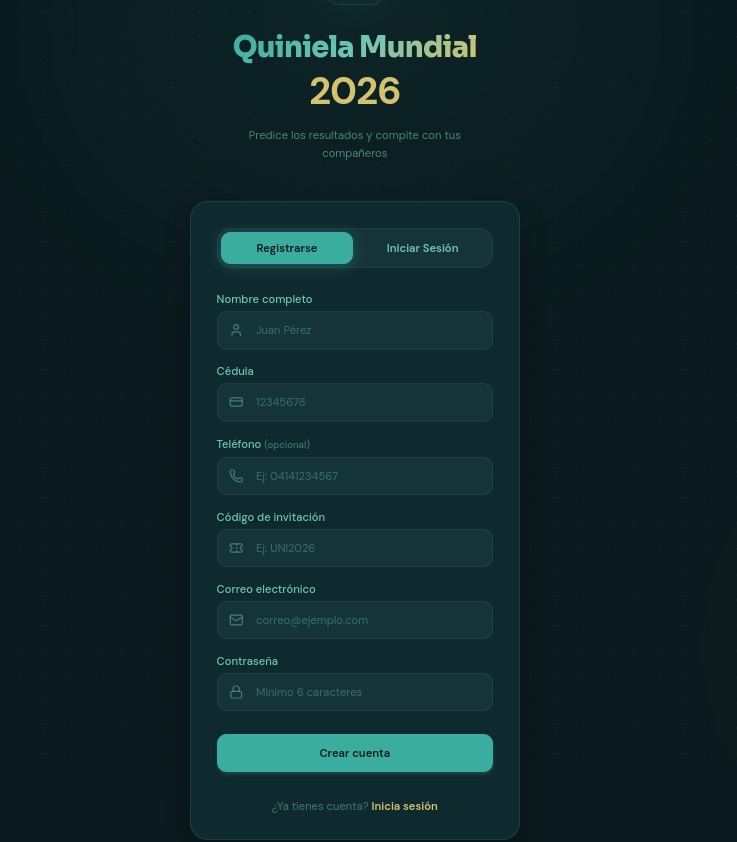
Take this beautifully designed Spanish-language website. To sign up, it demands a massive amount of personal information, including your full name, national ID number, email address, and phone number — and, of course, it asks you to create a password. If a victim uses the exact same password for multiple accounts, they’re essentially handing the keys to their digital life over to cybercriminals.

To guess match outcomes on this site, you have to hand over way too much personal info — everything short of biometrics

To guess match outcomes on this site, you have to hand over way too much personal info — everything short of biometrics

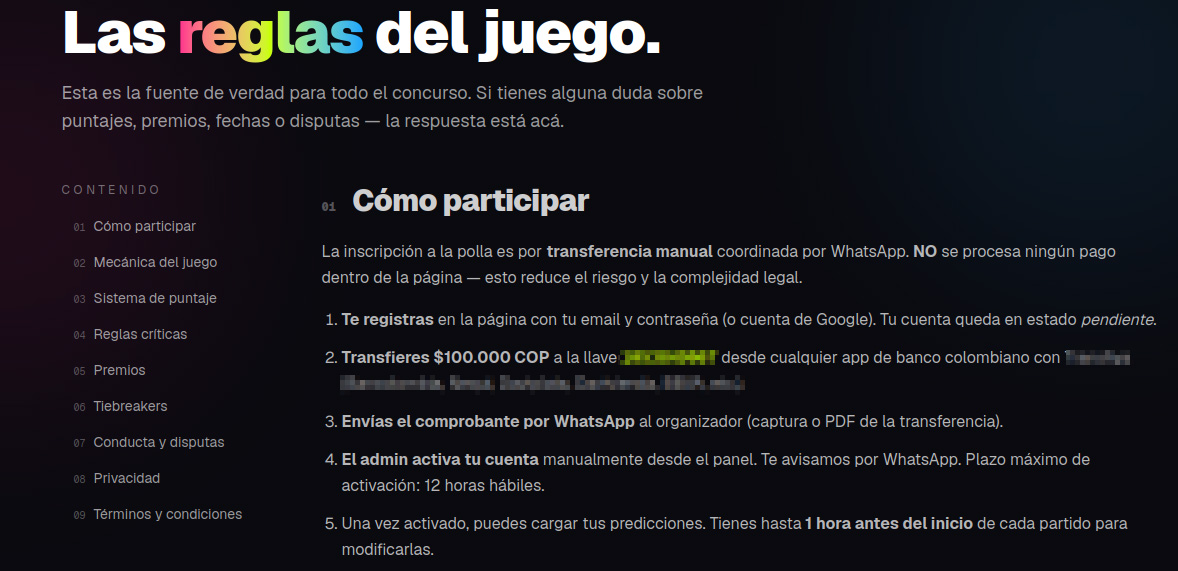
Another site, specifically targeting users in Colombia, turned the sign-up process into a paid ordeal — and it features every trick in the book.

  • To “verify” your profile, you’re forced to use WhatsApp under the guise of avoiding legal complications.
  • Before your account is activated, you must make a deposit. This means sending 100 000 Colombian pesos (about $29) to a specified account and texting the receipt to an “administrator” on WhatsApp.
  • Next, you’re told to wait 12 hours for the “administrator” to manually activate your profile.
  • Only after all of this do the scammers tell you can place unlimited bets (of course not true).
These scammers built a whole website, but they do all their business over WhatsApp. That's a red flag!

These scammers built a whole website, but they do all their business over WhatsApp. That’s a red flag!

In many countries — including Colombia — sports betting is strictly regulated. Only a handful of licensed operators are legally allowed to run these sites, and users are required by law to verify their identity. Because of this, these shady workarounds can look tempting to people who love to gamble but don’t want to — or can’t — go through the official verification process.

Unfortunately, the scammers always win in this scenario. They walk away with your initial deposit and every single bet you place on their site. At the end of the day, their only real goal is to drain their victims’ wallets for as much as they possibly can.

Discounts for collectors!

The World Cup isn’t just about the matches; it also drives record-breaking sales of collectible merchandise — stickers, scarves, team jerseys, official match balls, and more. Naturally, plenty of scammers are eager to get a piece of that action.

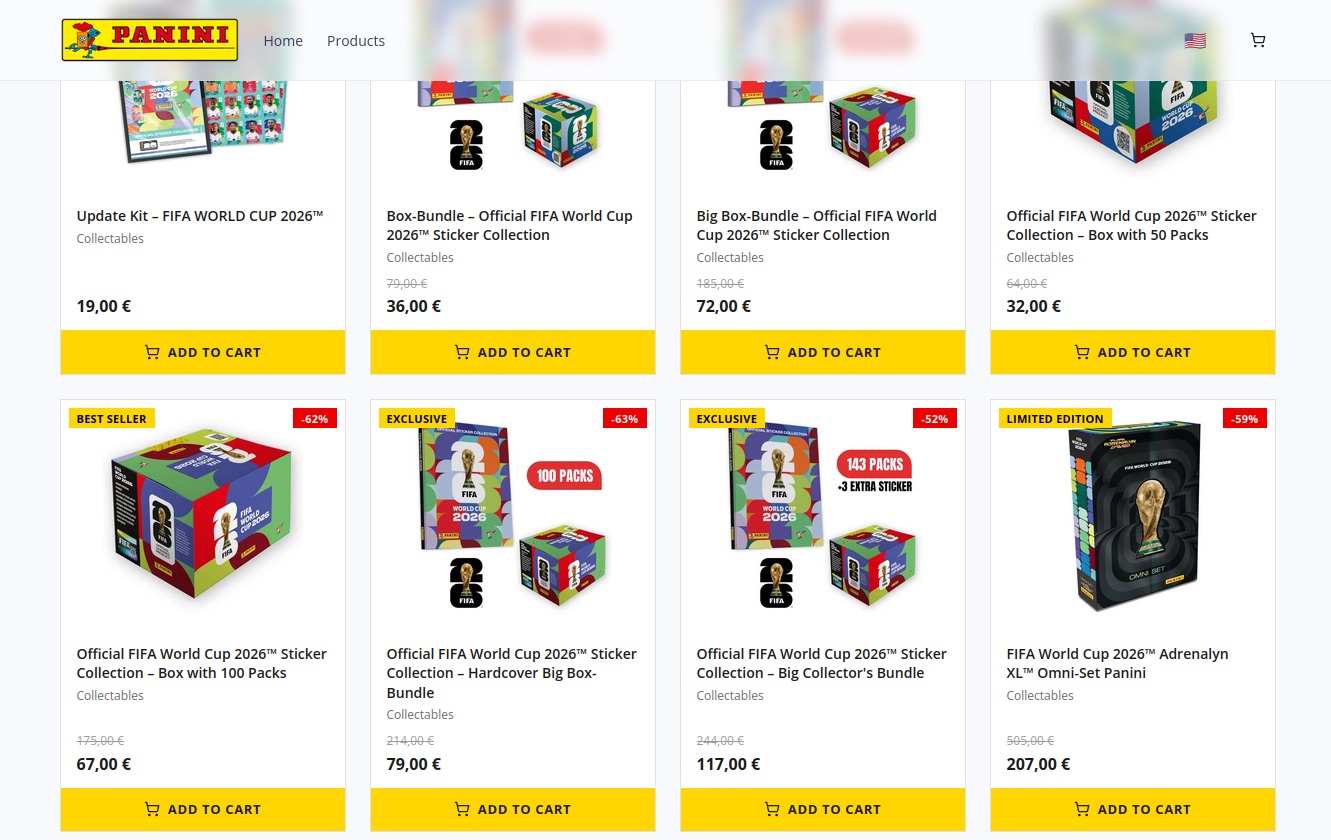
Take a look at this website offering “exclusive, limited-edition” stickers and albums. Notice anything suspicious?

Talk about a steal! Too bad the whole website is a scam

Talk about a steal! Too bad the whole website is a scam

Check out those prices: everything is heavily discounted, even though the tournament is in full swing. All it takes is a quick price check against the real deal to spot the trap. In the screenshot above, the scammers are charging 67 euros for a sticker collection. On actual online marketplaces, that exact same set goes for at least twice as much, and on the official Panini website, it’s three times the price.

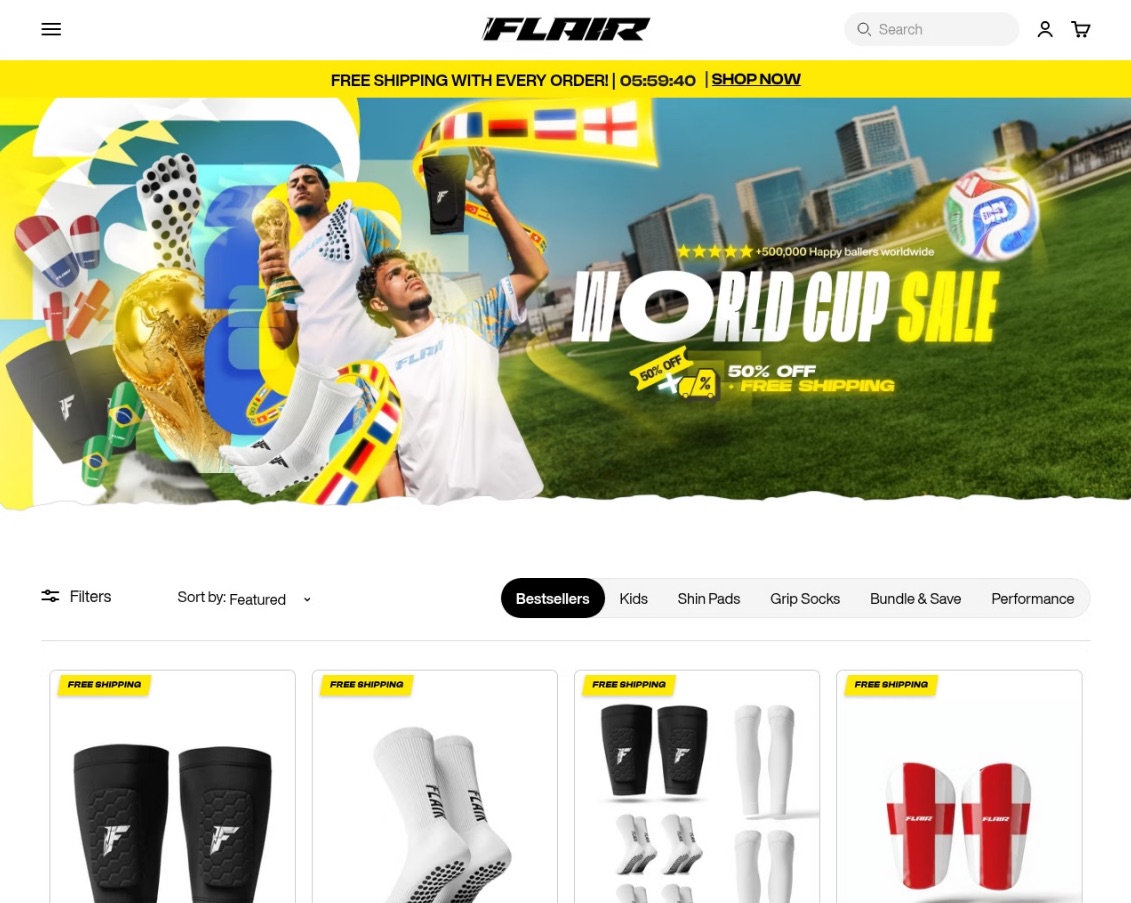
Fake websites mimicking popular sporting goods stores also offer to sell you shin guards, socks, jerseys, and any other gear. Of course, you’ll never see the merchandise, and you’ll lose both your money and your bank card details.

When they've absolutely no intention of delivering any products, they can easily offer massive discounts and free shipping

When they’ve absolutely no intention of delivering any products, they can easily offer massive discounts and free shipping

Deals that seem too good to be true are one of the biggest red flags. To make matters worse, with the help of AI, fake websites now look just as professional as the real ones, making them harder than ever to spot. That’s why we recommend installing our security suite before you start shopping online. It blocks phishing sites in real time and uses the Safe Money feature to keep your financial data secure.

Soccer by mail

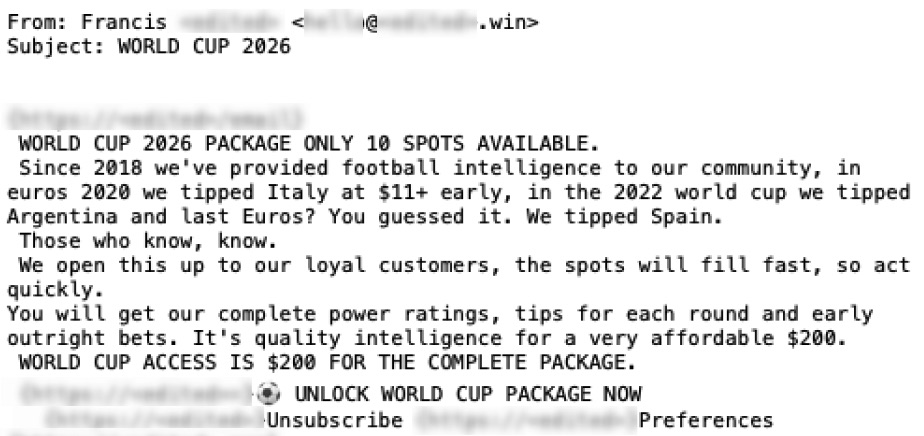
Another attack strategy involves spam campaigns centered around the World Cup. In one email, our experts uncovered an ad for a soccer analytics and betting-tips service. It uses the classic high-pressure playbook: “ONLY 10 SPOTS AVAILABLE” — so hurry up before they run out! Naturally, access comes with a price tag: AU$200.

Spammers hurrying the victim to make a decision as quickly as possible

Spammers hurrying the victim to make a decision as quickly as possible

This scheme targets fans who are into sports betting, and paying for these types of services usually ends one of two ways for them: they either lose their money with zero guarantee of getting actual predictions, or get sucked into an even deeper, multi-step financial trap.

How to avoid falling for the scams

Across all these scenarios, the World Cup is just another convenient pretext for cybercriminals. Once the tournament wraps up, they’ll most certainly pivot back to their usual tricks — like fake job offers or Telegram phishing scams — until the next Olympics or soccer tournament rolls around and they switch right back to sport.

Our research consistently shows that online fraud has evolved into a massive illegal enterprise. You aren’t just up against lone scammers anymore; you’re dealing with large criminal networks. When it comes to defense, the best approach is a proactive one. By installing Kaspersky Premium, you can safeguard all your devices from malware, phishing, spam, and malicious or lookalike websites. Plus, the included Kaspersky Password Manager will generate unique complex passwords, securely store your sensitive data — like documents and bank cards — and stop you from auto-filling your credentials on fake sites.

  • Watch the games only on legitimate streaming platforms. Don’t trust fake reviews and never enter your bank card information on unverified sites. Keep an eye out not just for sketchy streaming websites, but also for fake IPTV apps. As we’ve covered in detail before, scammers frequently use these to infect your devices with Trojans.
  • Shop smart. The best way to avoid getting ripped off is to buy merchandise exclusively through official channels (where you won’t see suspiciously deep discounts), or simply buy your gear in person at official retail locations.
  • Don’t click suspicious links. If a deal that’s too good to be true lands in your inbox — whether it’s exclusive betting tips or anything else — just ignore it and hit delete.
  • Avoid logging in through Telegram bots. At the very least, this saves you from future headaches and annoying spam. At best, it keeps your account from being hijacked and your crypto from being stolen.
  • Switch to passkeys wherever possible. Unlike traditional passwords, which are easily stolen and can be typed into any fake login page, a passkey is cryptographically tied to a specific website and won’t work on a phishing page. Kaspersky Password Manager can easily store and sync your passkeys across all your devices.

What other ruses do scammers use to make a quick buck? Check out our other posts:

Received — 8 June 2026 ⏭ Kaspersky official blog

Scams in messengers: exposing the global scam-cartels exploiting everyday messagesng-heist | Kaspersky official blog

1 June 2026 at 09:00

It starts with the familiar: a short message, a trusted name, a routine tone. Delivery updates, work pings, brand alerts hum in the background, rarely attracting scrutiny. You check, you answer… — until minutes later you’ve slipped into a trap built to lower your guard and hijack your trust.

That’s why messaging scams cut deep: they exploit everyday habits where instinct, not caution, leads. Communication once moved slowly, leaving room for doubt. Now it’s instant — and that speed is a weapon in criminal hands.

On our blog, we’ve already examined numerous scam schemes in messaging apps — from pig butchering, where the victim is groomed for a very long time, or catfishing, where the scammer creates a fake identity, to phishing via chatbots or through gift-giving campaigns in messaging apps.

Now, for the first time, Kaspersky has set out to capture the full end-to-end reality of messaging-based scams to understand how quickly harm occurs, how they impact trust and what remains after the interaction ends. What emerges is a highly organized and industrialized scam ecosystem embedded within everyday messaging channels such as SMS, WhatsApp, and email.

Kaspersky experts have prepared a report on targeted scams in messaging apps, detailing not only the financial but also the emotional damage caused by such attacks, as well as providing tips on how to protect yourself and avoid them. In this post, we explore the most interesting facts, but you can find more details in the full report.

The damage is underestimated

How much do you think a single successful attack via a messaging app costs the average victim? Ten dollars? Or maybe 50? You’re underestimating the scammers. Although more than a third (36%) of victims incur losses of less than $135, on average a victim loses… $733!

Country Average loss per victim
Senegal $392.94
Serbia $493.32
Morocco $504.28
Greece $609.32
United Kingdom $617.38
Côte d’Ivoire $654.11
Spain $672.67
United States $724.73
Portugal $868.20
Italy $896.02
France $1,193.58
Germany $1,369.35

The average amount lost by a victim in a successful attack via a messaging app

On the one hand, the financial hit doesn’t look catastrophic in isolation. These are micro-losses by design. Small enough that some never report them to the police. Small enough that banks don’t always investigate. Small enough to be dismissed as bad luck rather than organized crime.

But $733 is not nothing. It’s enough to cover a month’s worth of groceries, school or daycare fees, or utility bills. Against the backdrop of the global cost-of-living crisis, a single such loss can seriously dent a family’s budget.

In 11% of cases, losses exceed $1,350, and more than a quarter of victims (28%) report having been scammed three or more times in the past six months. Once scammers discover that a phone number responds, that contact becomes an asset, circulating from one database to another.

Now imagine the scale of the problem: if just 10% of the three billion messaging‑app users worldwide fell victim with the average loss, the total damage would amount to… nearly $220 billion! This is comparable to the GDP of Greece, and exceeds that of Morocco, Serbia, or Côte d’Ivoire.

It becomes clear that behind the daily flood of fraudulent schemes lie large scam cartels operating on an industrial scale, using AI to personalize messages that mimic those of family members, friends, and familiar brands. This, in essence, forms the basis of a full-fledged economy built on digital identity theft.

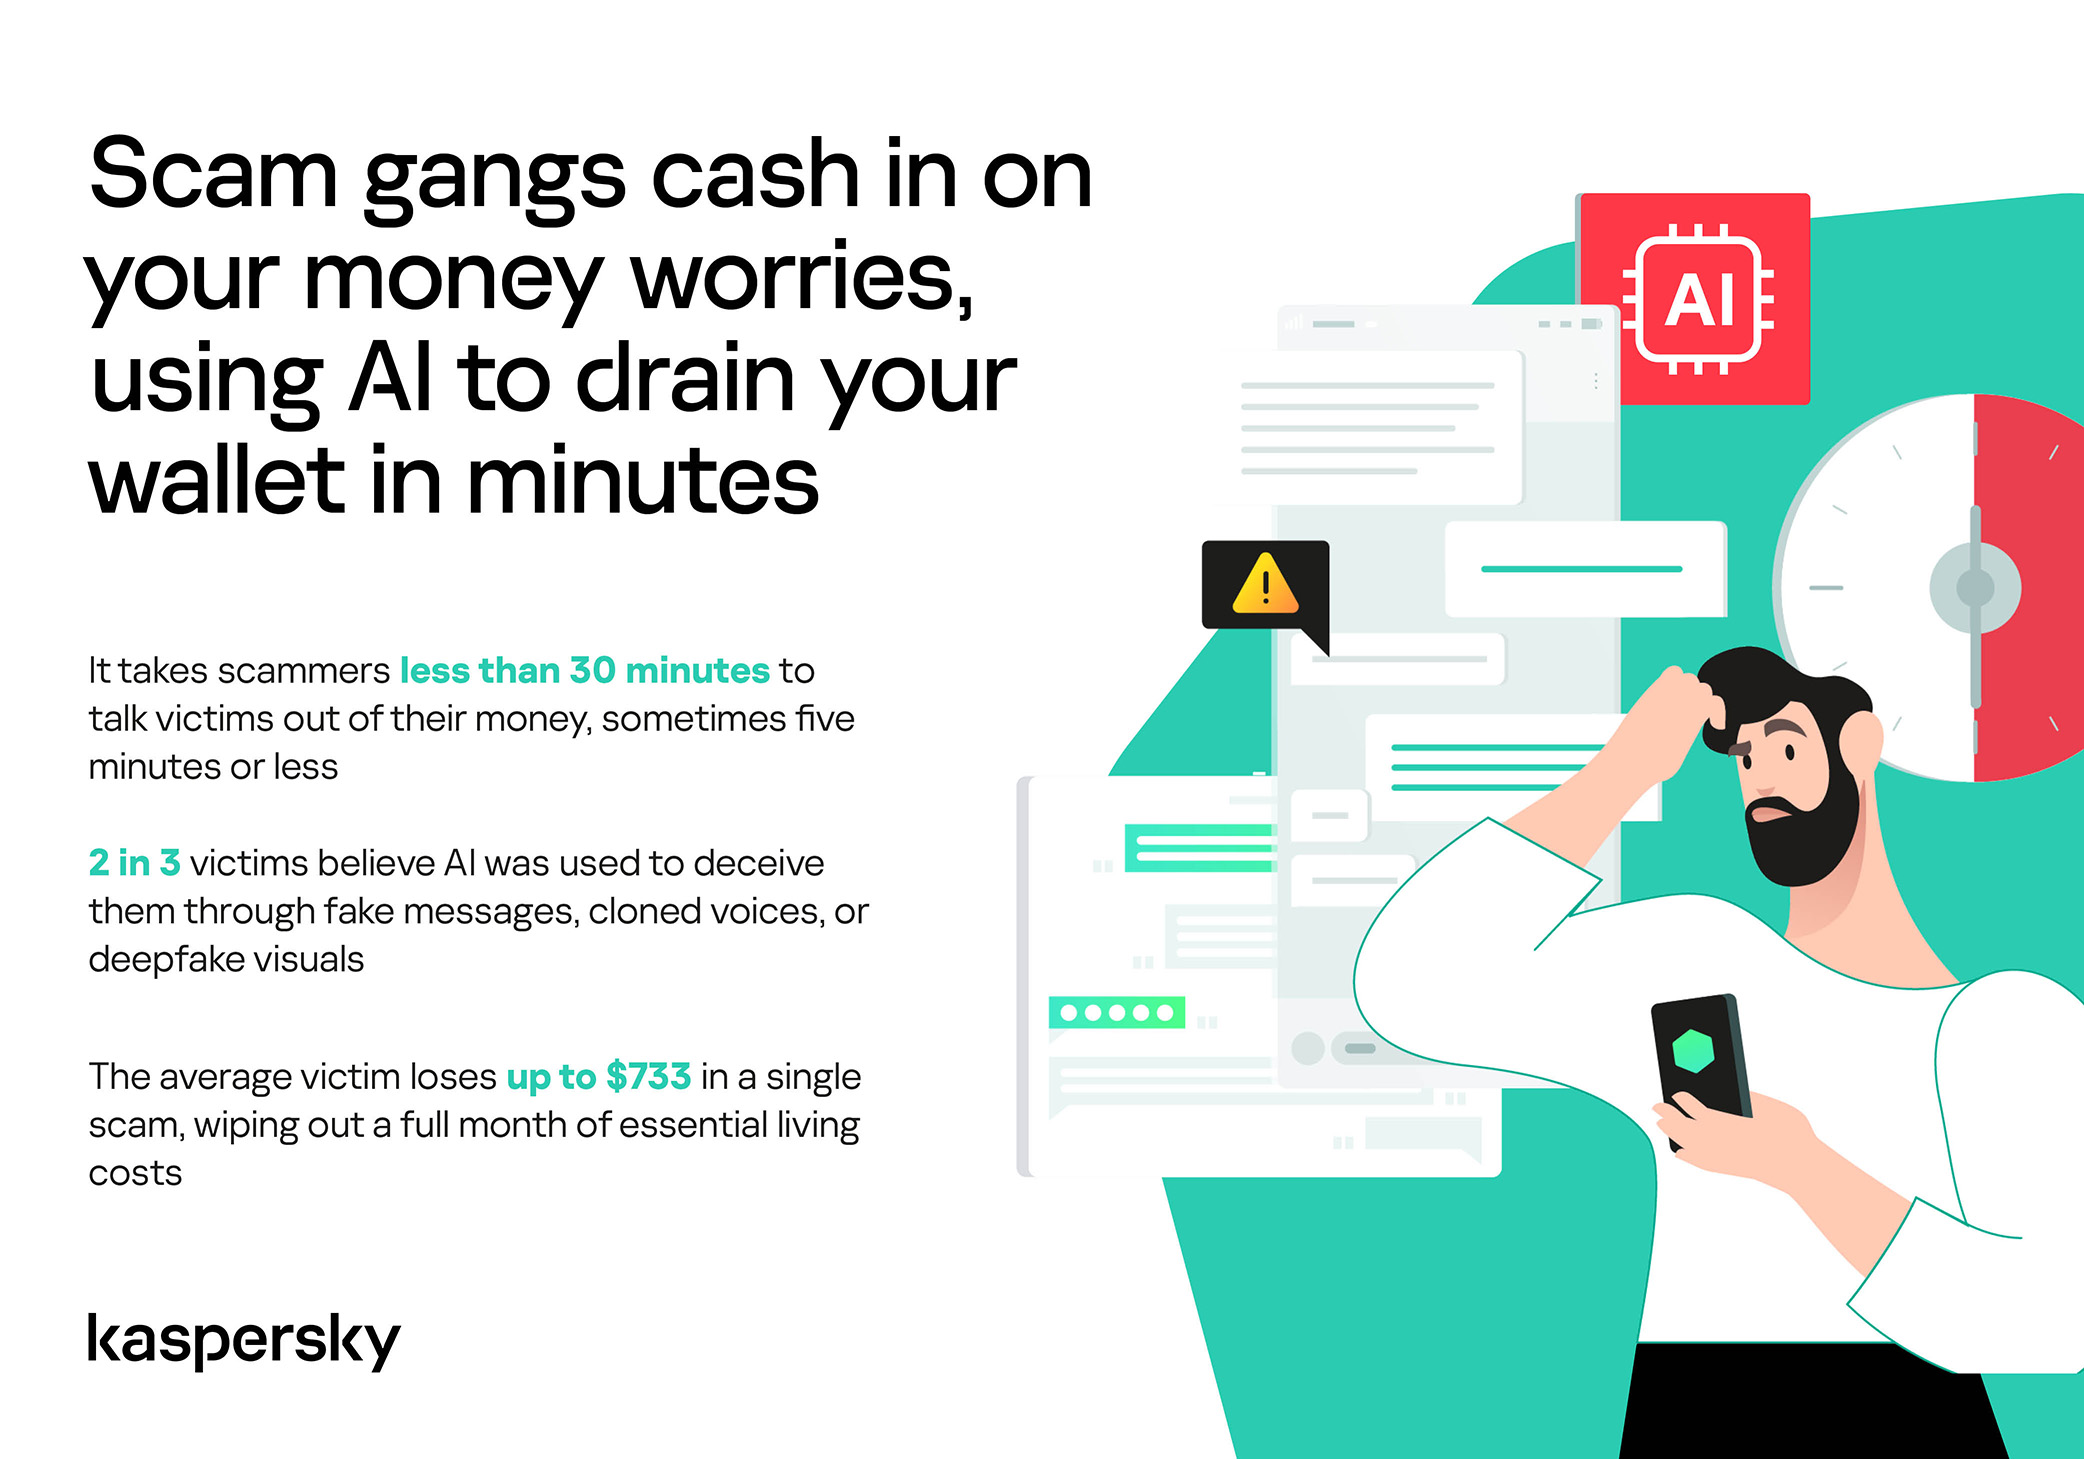
Scam gangs cash in on your money worries, using AI to drain your wallet in minutes

Speed beats scrutiny

More than half of successful messaging scams (52%) unfold in under 30 minutes — from first contact to the moment money or personal data changes hands — or even faster, before the victim begins to doubt the legitimacy of the sender. In fact, one in seven scams takes less than five minutes — quicker than boiling an egg!

The speed isn’t accidental. It’s the method. Scammers structure their schemes to deny the victim a chance to come to their senses. Every element is engineered to compress the decision-making window: the urgency of the scenario, the familiarity of the format, the plausibility of the request.

They rush you — faster, faster, don’t tell anyone, you only have a few minutes, solve the problem, don’t ask questions. Click the link, fill in the details, approve the transaction, or else… Or else what? The scammers’ imagination knows no bounds here, but if you don’t do something right now, you’ll definitely regret it.

Alas, the realization of what has happened usually comes when the damage is already irreversible. More than half of victims (51%) lose money; another 43% hand over their personal data — most commonly phone numbers, names, and email addresses — to scammers, and often the victim loses both.

Where and how attacks occur

A delivery notification, a bank alert, a message from a merchant you ordered from last week — messaging apps permeate every aspect of everyday life, making such interactions completely normal. An attack shouldn’t feel like an attack. It should feel like the same message you’ve received hundreds of times.

It’s no surprise that scammers focus their attention on this method of communication first and foremost. The most popular platforms for scams are predictable: WhatsApp (43%), SMS/iMessage (40%), Facebook (27%), Telegram (22%), and Instagram (19%) — these are the ones that people trust most.

A wide variety of schemes is used. Brand impersonation is now one of the three most common types of messaging scam worldwide — accounting for 31% of cases. Fake delivery notifications top the list at 38%, followed by investment scams at 37%.

At the same time, nearly two-thirds (63%) of fraudulent schemes span multiple platforms, moving from SMS to WhatsApp, from WhatsApp to Telegram, etc. In this way, scammers achieve two goals: they mimic organic messaging and evade moderation algorithms.

AI has taken scams to a new level

Just a couple of years ago, fraudulent messages gave themselves away with bad grammar, awkward phrasing, illogical requests, and an obsessive sense of urgency. Today, a phishing message looks, sounds, and reads just like the real thing.

Scam cartels want to catch people in motion — between meetings, on a commute, or during everyday tasks — when your attention is already fragmented. They mimic your mother’s turn of phrase. They match your bank’s tone of voice. They copy your courier’s format exactly. They mirror the rhythm, structure, and style of authentic brand communications across messaging platforms. And AI is accelerating all of it.

What this creates is overlap. Legitimate and fraudulent messages appear in the same environment, using the same formats, language, and triggers. The difference between them is no longer obvious.

The data shows that two-thirds of victims (66%) believe AI was used in the scam against them, 42% cite messages written by AI, 31% report generated or cloned voices, and 25% encountered deepfake images or videos.

That’s why mere awareness and “tech-savviness” may no longer be enough to protect oneself. From Gen Z to Gen X, messaging scams cut across every generation.

And what about the emotional toll?

But money is far from the only problem a victim is left with after an attack. After what they’ve been through, people develop distrust toward incoming messages, unfamiliar numbers, and any requests for action. As a result, 99% of fraud victims say they no longer trust incoming notifications in messaging apps.

This creates a crisis of trust in all digital channels in general. Every legitimate message can now be perceived as a scam. Brands, banks, and delivery services are forced to operate in an environment where the customer is, by default, in a state of distrust.

Dr. Elizabeth Carter, a forensic linguist and criminologist at Kingston University in London, notes that scammers use familiar contexts, common social settings and embedded linguistic norms to create the illusion for the victim that their decision-making is rational and reasonable in the moment. However, what is actually happening is that they construct false realities in which those decisions end up causing financial and psychological harm. She also notes that it is very hard to identify a false reality while you are in it.

After realizing they had been deceived, more than half of victims felt anger — the kind that comes from having trusted something and discovering it was used against you. 42% of victims report frustration, 38% — feeling upset. Moreover, several months later, these feelings haven’t gone away: nearly half of all victims (48%) are still angry, a third (33%) remain frustrated, and 30% are upset.

And nearly one in 10 victims don’t tell anyone what happened. They feel shame, a sense of having fallen for something so obvious. This leaves a significant portion of the actual damage unreported: only 24% of victims contact the police, and only 23% report it to their bank.

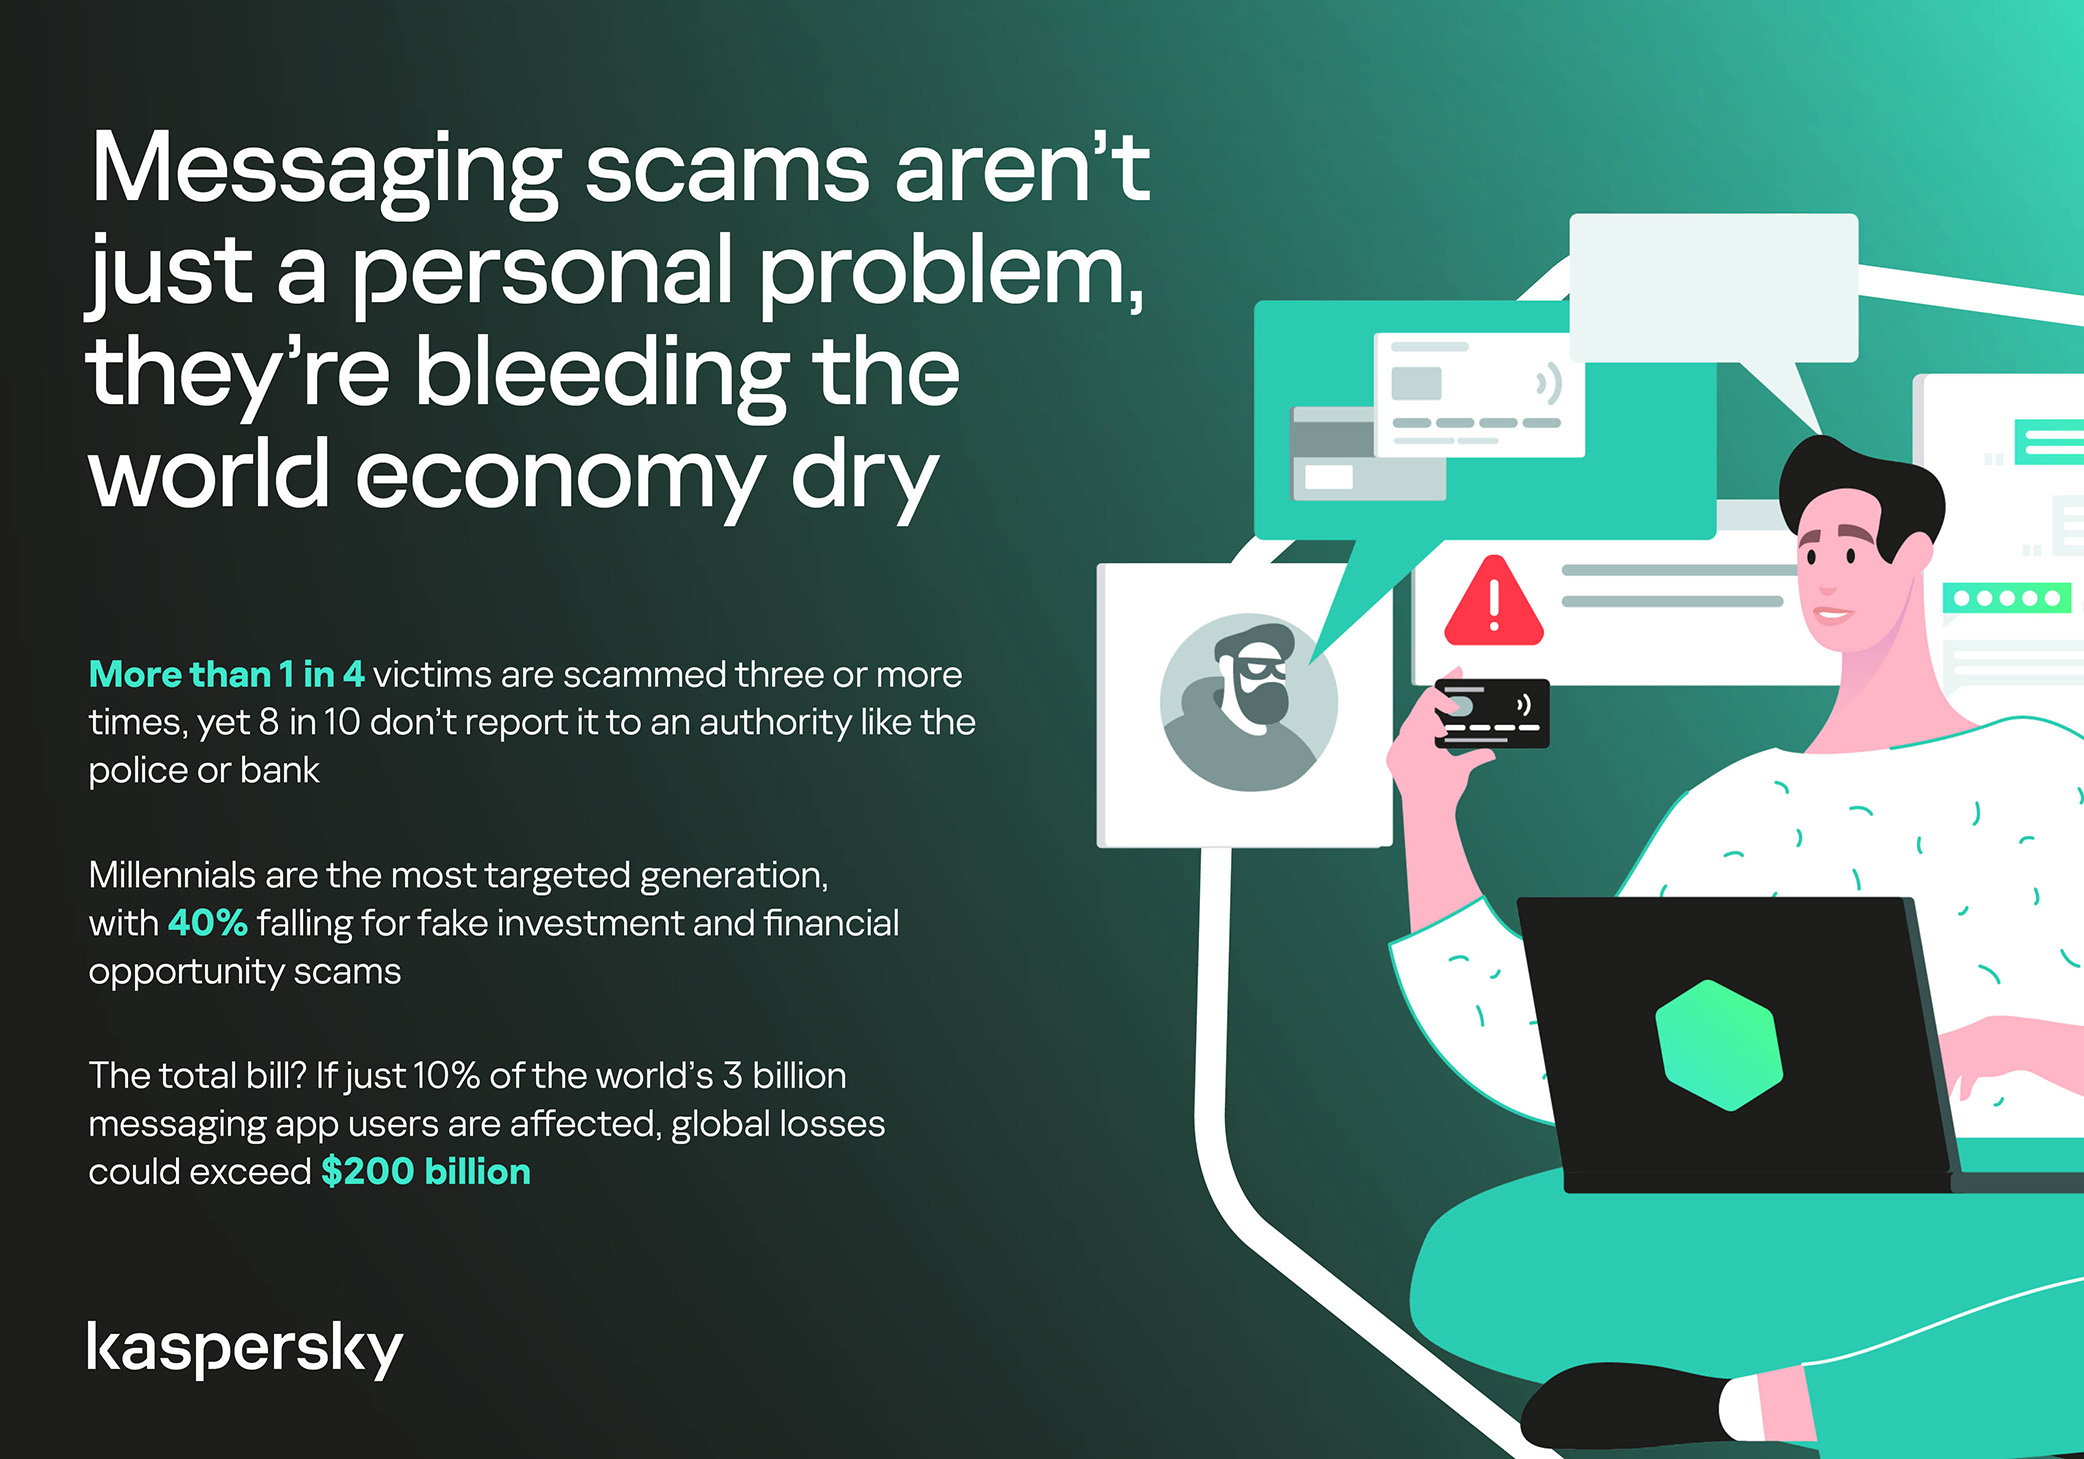
Messaging scams aren't just a personal problem, they're bleeding the world economy dry

So what can be done?

The crisis of trust — and even a touch of paranoia — that has arisen due to widespread attacks on users can linger in victims’ minds for a long time, affecting their quality of life. To prevent this, follow these guidelines:

  • Pause before you act. The sense of urgency you feel is almost always artificial. A legitimate bank, retailer, or delivery service won’t penalize you for taking 30 seconds to verify before clicking a link or confirming details. It’s precisely this instinct to resolve the situation quickly that scammers are counting on.
  • Verify through another channel. If a message appears to be from a relative, colleague, or company you trust — contact them through another channel before taking any action. Use secure verification methods, and cross-check identities when something doesn’t feel right. For families, agreeing on a “safe word” in advance can defeat even the most convincing voice clones.
  • Use a password manager. It will not only help you generate strong, unique passwords for all your accounts and store them securely, syncing them across all your devices, but also protect you from spoofed sites. Even if you click a phishing link and land on such a site, our password manager will notify you about the domain mismatch and refuse to autofill your username and password.
  • Use protection that works in real time. Modern security solutions, such as Kaspersky Premium, provide real-time protection against malicious links and phishing attempts in the apps and websites you use every day. On Android devices, a dedicated layer of anti-phishing security scans and neutralizes suspicious links as they appear, even within notifications, before you even have a chance to click them.

We’ve covered other threats in messaging apps in similar articles:

❌