❌

Normal view

Hacking Safari with GPT 5.4 

23 April 2026 at 20:58

When Anthropic unveiled Mythos and Project Glasswing, the reaction was immediate and polarized. Some dismissed it as fear-driven marketing, while others treated it as a credible shift in the threat landscape.

Like with many things, the truth is probably somewhere in the middle. I wanted to test that for myself, and since I recently got access to OpenAI’s Trusted Access for Cyber program, I decided to take it for a spin.

GPT-5.4 identified the bugs and helped assemble a working exploit chain, but it wasn’t a simple “build me an exploit” prompt. Guiding it required domain knowledge, iterative probing, and knowing which paths were actually exploitable.

On modern browsers like Safari, exploitation is less about finding bugs and more about finding bugs that still matter after multiple layers of defense.

The bug I’m going to talk about today sits in a more interesting category. The bug itself looked contained, and in many ways it was. It did not provide a path to RCE or a sandbox escape. What it did instead was cross a different boundary entirely: it broke the Same-Origin Policy.

If you visited a malicious page from any Apple device, it could read authenticated cross-origin data from other sites you use, including access tokens and other sensitive data, making account takeover trivial.

The video below shows the PoC we sent Apple, demonstrating leakage of sensitive data from both Apple Connect and iCloud / Apple ID endpoints. Although this demo focuses on Apple services, the issue affects all websites. This means that by visiting a malicious website, sensitive data from other domains is at risk of being leaked.


The Sandbox Russian Doll

Browser exploitation in 2026 is a lot like being trapped in a Russian doll.

You start in the smallest doll, and every time you escape one layer you discover you are still trapped inside another one.

Finding a low-level memory bug is not the same thing as finding an exploit. Most of these bugs die in the gap between “memory corruption happened” and “something meaningful crossed a security boundary.”

On the outside you have the browser process model. Even if renderer code goes wrong, the browser is trying very hard to keep that damage inside the web content process.

infographic

Inside that you have the web security model: Same-Origin Policy, CORS, opaque responses, cookie scoping, and credential modes. Even if a page can trigger a cross-origin request, the renderer, and especially the Gigacage, should not be able to access the response bytes. Right?…

The Bug

The original bug lives in the refresh logic for non-shared resizable WebAssembly memory.

When a non-shared WebAssembly.Memory grows in BoundsChecking mode, JavaScriptCore can replace the underlying memory handle. That part is not the bug. The bug is what happens after that to the JS-visible resizable buffer returned by memory.toResizableBuffer().

diagram

The bug is simple enough that once I saw it, it was hard to unsee it. Safari’s grow path effectively does this:

code1

And the refresh step effectively does this:

code2

After memory.grow(), WebKit updates the buffer metadata, but leaves m_data pointing at the old freed allocation.

So after a grow, JavaScript can hold a buffer whose reported size is new, whose handle is new, but whose actual data pointer still references the old freed Primitive Gigacage allocation.

That turns into a stale typed-array window over freed memory.

On its own, this is already a real bug. But we’re still stuck inside the JavaScriptCore gigacage, effectively sandboxed. Without a second bug to break out into the renderer, it doesn’t chain into anything meaningful. What we have is a solid first-stage primitive, but no real security impact on its own.

Why it did not look exploitable at first

The stale window is confined to the Primitive Gigacage, which immediately limits what you can do with it. Many typical targets either never land there, lack useful structure, or fail to produce any cross-boundary effect.

So early on, it had all the hallmarks of a bug that looks promising but rarely goes the distance:

  • easy source-level root cause
  • visible stale memory behavior
  • real reclaim
  • no clean escape path

This is where a lot of low-level browser bugs die.

What changed the problem was a very different framing: maybe I did not need to escape the cage at all.

Maybe I just needed the browser to place something valuable inside it.

The Pivot

Instead of asking “how do I get from my stale WASM view to some protected browser state?” I started asking a better question:

“What browser code takes data that JavaScript is not allowed to read, but still copies that data into normal renderer memory?”

Because that is all I need.

I don’t need to break the abstraction.

I just need the browser to break it for me.

That naturally narrows the search space to subsystems that:

  • handle sensitive cross-origin data, and
  • still allocate ArrayBuffer-backed memory as part of their internal pipeline

That points straight at Fetch. The Fetch API clearly indicates that the response is opaque, meaning that its headers and body are not available to JavaScript.

Opaque Responses Are Supposed to Be Opaque

At the API level, the Fetch model here is straightforward.

If I do a cross-origin request with:

fetch(url, { mode: “no-cors”, credentials: “include” });

The browser may send the request, including cookies depending on context, but JavaScript receives an opaque response.

That means:

  • I can hold the Response object
  • but I cannot read the body bytes

And WebKit enforces that in the obvious place:

FetchBodyOwner::readableStream() blocks opaque bodies via isBodyNullOrOpaque().

So at first glance, everything looks fine. The body is hidden. The policy is enforced. Same-Origin Policy survives another day.

Except it does not.

The Fetch Behavior that Broke the Modal

The surprising part is Response.clone().

If FetchResponse::clone() is called while the response is still loading, WebKit will internally create a readable stream so it can tee the body between the original response and the clone.

That internal path does not apply the same opaque-body check first.

And once that happens, hidden response bytes start becoming very real renderer objects.

This is the part that made me stop and stare at the source, because the mismatch is right there.

The normal body path blocks opaque responses:

code3

But FetchResponse::clone() does this while the response is still loading:

code4

That is why it works.

The visible accessor path says “opaque bodies do not get a stream.” The clone path says “if it is still loading, create a stream so both clones can tee it.”

That second path is exactly what I needed.

The data flows through normal ArrayBuffer creation paths:

  • buffered chunks go through tryCreateArrayBuffer()
  • later chunks go through takeAsArrayBuffer()
  • shared buffer data gets copied into ordinary ArrayBuffer allocations inside the renderer

So the policy ends up split in two:

  • the public Fetch API says the body is opaque
  • the renderer still materializes the opaque body into readable byte arrays during clone-time streaming

Combined with the stale WASM window, it becomes a SOP break.

The Chain

At a high level, the exploit became:

  1. Force the target WASM memory into the BoundsChecking path.
  2. Call memory.toResizableBuffer().
  3. Grow the memory.
  4. Keep the stale resizable buffer whose pointer still targets freed Primitive Gigacage pages.
  5. Trigger a cross-origin fetch(…, { mode: “no-cors”, credentials: “include” }).
  6. Call response.clone() while the response is still loading.
  7. Let Fetch internals materialize the hidden body bytes into ordinary renderer ArrayBuffers.
  8. Reclaim the stale WASM-covered pages with those allocations.
  9. Read the cross-origin bytes through the stale view.

That is the entire trick.

I never needed response.text(). I never needed response.arrayBuffer(). I never needed the public API to hand me the body.

The browser copied the body into memory for its own internal bookkeeping, and the stale WASM view read it directly.

That is why this bug stopped being “some weird WASM UAF” and became “this completely breaks the Same-Origin Policy.”

The file:// Detour

One of the weirdest parts of the research was that the request side behaved differently depending on where I launched it from.

In my testing, cross-origin requests were much easier to get moving from file:// than from a normal https attacker page.

That sounds backwards until you look at WebKit’s handling of local origins.

Document.cpp has explicit special-casing around local documents and settings like:

  • allowUniversalAccessFromFileURLs
  • allowFileAccessFromFileURLs

MiniBrowser exposes those knobs too, which made file:// very useful as a research environment. It let me focus on the memory side and confirm the leak path before I had a clean web-facing story.

But I did not want a local-file party trick.

I wanted a real web exploit.

And from a normal https page, the same request pattern was not giving me the reliability I wanted.

That is where about:blank saved me.

Why about:blank saved the final POC

The final PoC opens an about:blank popup and performs the fetches from there:

code5

This ended up mattering a lot.

At first I thought this was just an origin-inheritance trick. That part is real:

code6

So about:blank does inherit the opener’s origin.

But that alone does not explain why the popup path behaved differently.

What actually seems to matter is Safari’s cookie / first-party bookkeeping. Fetch subresource requests copy document->firstPartyForCookies() into the request:

code7

And WebKit’s cookie blocking logic bails out immediately if that first-party domain is empty:

code8

That is a very different path from a normal attacker-controlled https page. From a regular https://attacker.example origin, the first party is the attacker site, so a request to the victim site looks third-party and Safari’s tracking-prevention logic can suppress cookies.

From the about:blank popup path, the security origin still comes from the opener, but the popup’s top-level URL / first-party context is no longer a normal registrable https site in the same way. In practice, that was enough to make credentials: “include” requests behave differently and get me the authenticated traffic pattern I needed.

So the important point is not “about:blank disabled CORS.” It did not. The important point is:

  • the popup kept the opener’s origin
  • the request still went through normal Fetch/CORS code
  • Safari’s first-party cookie logic treated that popup context differently

That was the difference between “cross-origin request happens but is useless” and “cross-origin request comes back with authenticated bytes worth stealing.”

Why this was fun

This is my favorite kind of browser bug.

Not because the root cause was complicated. It was not. The WASM bug was almost embarrassingly direct.

And not because the final chain was huge. It was not.

It was fun because it is exactly the kind of bug modern browser architecture is supposed to suppress.

A stale pointer inside a cage is supposed to stay a stale pointer inside a cage.

An opaque response is supposed to stay opaque.

Those are both reasonable assumptions.

The exploit works because both assumptions were true only locally.

JavaScriptCore gave me a stale view that looked hard to use. WebCore Fetch gave me sensitive bytes that looked impossible to read.

Put them together and Safari’s Same-Origin Policy fell apart.

Disclosure

We reported our findings to Apple. Shortly after, a fix shipped, suggesting the issue was already known internally.

The vulnerability (CVE-2026-20664) is addressed in iOS 26.4 and iPadOS 26.4 (23E6254 and later), and macOS Tahoe 26.4 (25E253 and later). Make sure your systems are up to date.

Closing Thoughts

The biggest thing on my mind after working with these models is the leverage they provide, and what that means for N-days. A security patch in popular software used to hide the underlying exploit behind time, effort, and expertise. Now that you can scale tokens instead of effort, that barrier is mostly gone.

This doesn’t turn exploitation into a trivial task. You still need someone who understands what they are looking at, can filter noise, and can steer the process when it stalls. But AI changes the unit of work. Instead of deep, sequential effort, you get parallel exploration and rapid iteration. The constraint shifts from raw effort to how effectively an operator can guide multiple lines of inquiry at once.
`

The post Hacking Safari with GPT 5.4  appeared first on Blog.

How cyberattacks on companies affect everyone

23 April 2026 at 17:34

If you use the internet, you’ve likely been affected by cybercrime in some way. Even when an attack is aimed at a company, the fallout usually lands on ordinary people.

The most obvious harm is stolen data. When attackers break into a business, it is usually customer information that ends up in criminal hands, and that can lead to identity theft, tax fraud, credit card fraud, and a long tail of scam attempts that can continue for months or years. For consumers, the breach itself is often just the start of the cleanup.

That work is annoying, time-consuming, and sometimes expensive. People may have to freeze credit, replace cards, change passwords, be on the lookout for suspicious transactions, and dispute charges. The Federal Trade Commission (FTC) specifically advises consumers to use IdentityTheft.gov after a breach and recommends steps like credit freezes and fraud alerts to reduce the chance of further abuse.

When sensitive data is exposed, the harm is not only financial. Medical, insurance, and other deeply personal records can be used to create more convincing phishing or extortion attempts, and the stress of knowing that private information is circulating among criminals can linger long after the technical incident is over. In other words, breach victims are not just cleaning up a data problem, they are dealing with a loss of trust.


Breaches happen every day. Don’t be the last to know.


Cybercrime also hits consumers through service disruption. Ransomware and intrusion campaigns can interrupt payment systems, telecom services, shipping, energy distribution, booking platforms, and other infrastructure people rely on every day. In those cases, the consumer impact is immediate: you may not be able to pay, travel, call, buy, or even work normally. The CSIS timeline and Canada’s cyberthreat assessment both show that these disruptions are increasingly tied to high-value targets and can be part of broader state or criminal campaigns.

Not all these incidents are driven by cybercriminals. Recently, Britain’s cybersecurity chief warned that the UK is handling 4 nationally significant cyberincidents every week, with the majority now traced back to foreign governments rather than cybercriminal groups.

Another cost is easy to overlook: disinformation and confusion. When attackers steal data, disrupt services, or impersonate trusted brands, they can also flood the public with fake support messages, scam calls, refund schemes, and phishing emails pretending to be the breached company. The breach becomes a launchpad for more fraud, and consumers are left trying to separate legitimate notifications from those sent by attackers.

Then there is the security backlash. After a breach, companies usually tighten access rules, add more multi-factor authentication prompts, force reauthentication, shorten sessions, and increase fraud checks. Those measures are often necessary, but they also make ordinary digital life more cumbersome. The consumer ends up paying with time and frustration for security problems they did not create.

That is why company-targeted cybercrime is not really only a business problem. It is a consumer issue, a public-trust issue, and sometimes even a national security issue. A single breach can leak data, trigger fraud, interrupt essential services, amplify scams, and make using the internet more frustrating for everyone else. The real cost is rarely confined to the company that got hit.

Knowing this, it’s worth thinking carefully about which companies to trust with your data and how much you’re willing to share . You cannot stop every attack against every company you deal with, but you can limit the fallout by being more selective. Some considerations:

  • Do they need all the information they are asking for?
  • Would it hurt anything if you leave some fields blank or give less specific answers?
  • Has this company been breached in the past, and how did they handle it?
  • How long will they store the data you provide?
  • Can you easily have your data removed at your request?

Your name, address, and phone number are probably already for sale.  

Data brokers collect and sell your personal details to anyone willing to pay. Malwarebytes Personal Data Remover finds them and gets your information removed, then keeps watch so it stays that way. 

Check Point WAF Leads Application Security-Validated by Frost & Sullivan

By: anap
23 April 2026 at 15:00

Check Point has been honored Frost & Sullivan’s 2026 Technology Innovation Leadership recognition in WAF and API security, positioning us as a Company to Action shaping the future of cybersecurity. This recognition reflects a major shift in how application security must operate today. Application Security Has Fundamentally Changed Applications are no longer just web apps they now run on APIs, microservices, and AI-driven services, rapidly expanding across hybrid and multi-cloud environments. Each release introduces new components, increasing the attack surface. At the same time, accelerated DevSecOps cycles are making both web and AI applications harder to secure, while threats continue […]

The post Check Point WAF Leads Application Security-Validated by Frost & Sullivan appeared first on Check Point Blog.

Trailmark turns code into graphs

23 April 2026 at 14:00

We’re open-sourcing Trailmark, a library that parses source code into a queryable call graph of functions, classes, call relationships, and semantic metadata, then exposes that graph through a Python API that Claude skills can call directly. Install it now:

uv pip install trailmark

“Defenders think in lists. Attackers think in graphs. As long as this is true, attackers win.” John Lambert’s widely cited observation about network security applies just as well to AI-assisted software analysis.

When Claude reasons about a codebase, it reasons about lists: findings from static analyzers, surviving mutants from mutation testing, and line-by-line coverage reports. But the question that actually matters is a graph question: can untrusted input reach this code, and what breaks if it’s wrong?

We built Trailmark to answer that question. It gives Claude a graph to think with instead of a list. We’re also releasing eight Claude Code skills we’ve built on top of it, designed for mutation triage, test vector generation, protocol diagramming, and more.

When lists fall short

Mutation testing is a great example of a method that benefits from graph-level reasoning. It’s one of the best ways to measure test quality. It makes small changes to your source code (e.g., swapping a < for <=, replacing + with -) and checks whether your tests catch the difference. Mutants that survive reveal gaps in your test suite that code coverage metrics might miss. The downside is that a mutation testing run on a real codebase can produce hundreds of surviving mutants of varying significance. This is very much a list.

Some surviving mutants are equivalent: the mutation doesn’t change the program’s behavior because of structural or mathematical constraints that the mutation testing tool can’t see. Some are in dead code; some are in error message formatting; some are in the finite field arithmetic that underpins every cryptographic operation in your library. A flat list of surviving mutants doesn’t tell you which is which.

We wanted to know whether Claude could use graph-level reasoning about a codebase to automatically triage surviving mutants by security relevance: which are reachable from untrusted input, which affect high-blast-radius functions, and which represent genuine gaps in security-critical code?

How Trailmark works

Trailmark uses tree-sitter for language-agnostic AST parsing and rustworkx for high-performance graph traversal. It operates in three phases:

  1. Parse: Walk a directory, extract functions, classes, call edges, type annotations, cyclomatic complexity, and branch counts from source code.
  2. Index: Load the resulting graph into a rustworkx PyDiGraph with bidirectional ID/index mappings for fast traversal.
  3. Query: Answer questions: callers, callees, all paths between two nodes, attack surface enumeration, and complexity hotspots.

It currently supports 17 languages, including C, Rust, Go, Python, PHP, JavaScript, Solidity, Circom, and Miden Assembly.

The graph is the substrate. The skills are where the analysis happens.

The skills

The Trailmark plugin ships eight Claude Code skills that use the graph API as their backbone:

Skill What it does
trailmark Build and query a code graph with pre-analysis passes: blast radius, taint propagation, privilege boundaries, and entrypoint enumeration
diagram Generate Mermaid diagrams from code graphs: call graphs, class hierarchies, complexity heatmaps, data flow
crypto-protocol-diagram Extract protocol message flow from source code or specs (RFCs, ProVerif, Tamarin) into annotated sequence diagrams
genotoxic Triage mutation testing results using graph analysis: classify surviving mutants as equivalent, missing test coverage, or fuzzing targets
vector-forge Mutation-driven test vector generation: find coverage gaps via mutation testing, then generate Wycheproof-style vectors that close them
graph-evolution Compare code graphs at two snapshots to surface security-relevant structural changes that text diffs miss
mermaid-to-proverif Convert Mermaid sequence diagrams into ProVerif formal verification models
audit-augmentation Project SARIF and weAudit findings onto code graph nodes as annotations, enabling cross-referencing of static analysis results with blast radius and taint data

Each skill calls the Trailmark Python API directly. When genotoxic triages a surviving mutant, it queries engine.paths_between to check reachability from untrusted input. When diagram generates a complexity heatmap, it calls engine.complexity_hotspots. The graph is what makes those questions answerable in seconds rather than hours of manual tracing.

Trailmark also ingests SARIF output from static analyzers and weAudit annotations, mapping external findings onto graph nodes by file and line range. This lets Claude layer static analysis results, audit notes, and mutation testing data onto a single unified graph, then query across all of them.

What Claude found

We’ve been using these skills internally on several cryptographic libraries, combining graph analysis with language-appropriate mutation testing frameworks. Here’s what the graph let Claude see that flat lists couldn’t.

Equivalent mutants are the majority in well-tested crypto

When we ran mutation testing against an Ed448 implementation in Go, 45 mutants survived out of 583 covered. A flat list of 45 surviving mutants looks like a serious test gap. But when Claude used the Trailmark call graph (332 nodes, 3,259 call edges) to triage via genotoxic, 33 of those 45 (73%) were equivalent mutants. The mutations were unobservable because the code’s mathematical structure constrained values more tightly than the explicit bounds checks that were mutated.

For example, nine surviving mutants modified boundary conditions in NAF (non-adjacent form) digit range checks. These look like real bugs in isolation. But the NAF digits are structurally bounded by the nonAdjacentForm algorithm itself: the values that would trigger the altered boundary can never appear. The graph confirmed these functions were called from specific contexts that made the mutations undetectable.

The 12 genuine gaps were concrete and actionable: a cross-package coverage gap where Go’s coverage profiling attributed execution to the calling package instead of the defining package, a 255-byte context string boundary condition that was never tested, and overflow carry paths in wide-integer parsing that required near-maximum input values that no existing test vector produced.

Architectural bottlenecks are invisible without a graph

When Claude built a Trailmark graph of libhydrogen, a compact C cryptographic library, the graph immediately highlighted something that wasn’t obvious from linearly reading the source files: the entire library funnels through a single permutation primitive, gimli_core_u8, which receives 37 direct calls. Every cryptographic operation (hashing, encryption, key exchange, signatures, and password hashing) depends on this one function.

This isn’t a bug. It’s a deliberate design choice common in lightweight crypto libraries. But it means the blast radius of a flaw in Gimli is total. The graph quantified this: a mutation in gimli_core_u8 affects 100% of the library’s security-critical functionality. Gimli was also eliminated from the NIST Lightweight Cryptography competition. Together, these facts represent the kind of architectural risk that’s invisible in a line-by-line code review. The graph makes it obvious.

Mutation testing finds what KATs can’t cover

For standardized algorithms like Ed25519 or ML-KEM, known-answer tests (KATs) and projects like Wycheproof provide test vectors that exercise edge cases. But for novel constructions (libhydrogen’s combination of Gimli and Curve25519, for instance), independent KATs don’t exist. No one has published “if you give Gimli-based AEAD this input, you should get this output” vectors, because the construction is unique to this library.

This is where mutation testing fills the gap. It doesn’t need reference implementations or published test vectors. It tests whether your tests actually constrain your code’s behavior. The surviving mutants tell you exactly which aspects of the implementation aren’t pinned down by your test suite, regardless of whether anyone else has ever tested that specific construction.

In the RustCrypto/KEMs crates (ML-KEM, X-Wing), vector-forge found that seven surviving mutants targeted NTT multiplication (mutations like replacing * with + in polynomial dot products). These survived because the test suite only exercised NTT through full KEM round-trips. The algebraic properties of NTT were never tested directly. Existing Wycheproof vectors and NIST KATs caught most higher-level issues, but the internal algebraic invariants had no direct coverage.

Three patterns that showed up everywhere

Across multiple codebases analyzed with Trailmark, the same patterns emerged:

  • Blast radius concentrates in arithmetic modules. In libsodium (1,597 nodes, 9,574 call edges), the ed25519_ref10 module had the highest blast radius, underpinning Ed25519 signatures, Curve25519 key exchange, Ristretto255, and X-Wing KEM. In ML-KEM, the algebra module had a blast radius of 28; every polynomial and matrix operation depended on its Elem arithmetic. Graph analysis consistently identified these modules as the highest-priority targets for thorough testing.

  • Codec parsers are high-value fuzzing targets that rarely get prioritized. Multiple analyses flagged hex/Base64 decoders and IP address parsers as high-complexity functions with external input exposure. libsodium’s parse_ipv6 had a cyclomatic complexity of 18; libhydrogen’s hydro_hex2bin was the most complex function in the entire library, with a cyclomatic complexity of 11. These functions are natural targets for fuzzing, and the graph confirms they’re reachable from untrusted input.

  • Property-based testing is sparse. Across the Rust cryptographic crates we examined, property-based testing was either absent or incomplete. The KEMs crates had zero property-based tests. Barrett reduction in ML-KEM was tested with only five points, even though exhaustive testing over all 11 million values of q = 3329 is computationally feasible. The graph’s blast radius analysis shows where property-based tests would have the greatest impact.

Connecting the graph to everything else

The graph is most useful when it serves as the connective tissue between other analysis tools. When the constant-time analysis skill flags a function, Trailmark tells Claude its blast radius. When mutation testing produces survivors, Trailmark tells Claude which ones are reachable from untrusted input. When an auditor annotates a finding in weAudit, audit-augmentation shows what else in the graph is affected.

We use this internally to write targeted fuzzing harnesses. The graph identifies high-complexity functions reachable from external input; mutation testing identifies which of those functions have test gaps; the combination tells Claude exactly where a fuzzing harness will have the highest marginal value.

Start querying your codebase

Trailmark is open source under Apache-2.0. The library is on PyPI; the skills plugin is in the same repository.

Install the library (required by the skills):

uv pip install trailmark

Add the skills to Claude Code:

/plugin marketplace add trailofbits/skills

Then select the Trailmark plugin from the menu.

You can also explore the graph directly from the CLI:

# Full JSON graph
trailmark analyze path/to/project

# Analyze a specific language
trailmark analyze --language rust path/to/project

# Complexity hotspots
trailmark analyze --complexity 10 path/to/project

Or call the Python API to build your own skills on top of the graph:

from trailmark.query.api import QueryEngine

engine = QueryEngine.from_directory("path/to/project", language="c")

# What's reachable from this entrypoint?
engine.callees_of("handle_request")

# Call paths from entrypoint to sensitive function
engine.paths_between("handle_request", "crypto_verify")

# Functions with cyclomatic complexity >= 10
engine.complexity_hotspots(10)

# Run pre-analysis (blast radius, taint, privilege boundaries)
engine.preanalysis()

The graph API is designed to be called by skills, not just humans. If you’re building Claude Code skills for security analysis, code review, or test generation, Trailmark gives you the structural substrate to ask questions that lists can’t answer.

Seventeen languages. A graph, not a list. The code is on GitHub.

Apple fixes iOS bug that kept deleted notifications, including chat previews

23 April 2026 at 12:27

Apple has released a software update that deals with an issue that could allow deleted notifications to be retrieved. Something that, in at least one reported case, was used by law enforcement during forensic analysis.

Apple fixed the issue in iOS and iPadOS versions 18.7.8 and 26.4.2 (check availability for your device at those links). The update deals with a singular security vulnerability, tracked as CVE-2026-28950.

Although the description is brief—“a logging issue was addressed with improved data redaction”—the impact points us in the right direction.

“Notifications marked for deletion could be unexpectedly retained on the device.”

This suggests that Apple’s bug was that iOS kept copies of notification content in an internal database for longer than intended, even after the messages “disappeared” or the app was uninstalled. In a case reported by 404 Media, law enforcement was able to recover those notifications using standard forensic tools once they had access to the unlocked device. The example in that reported case involved Signal.


Mobile protection, anywhere, anytime.


A response on X by Signal states:

“The FBI was able to forensically extract copies of incoming Signal messages from a defendant’s iPhone, even after the app was deleted, because copies of the content were saved in the device’s push notification database.”

Before we go into the update process, you may want to know that you can mute or hide notifications in Signal, which also protects them from prying eyes. In Signal, open your Settings and tap on Notifications. You can adjust several settings there. For example, I have mine set so I only see the name of the sender.

Install the update

For iOS and iPadOS users, you can check if you’re using the latest software version by going to Settings > General > Software Update. It’s also worth turning on Automatic Updates if you haven’t already. You can do that on the same screen.

Update settings on iPad

Scammers know more about you than you think. 

Malwarebytes Mobile Security protects you from phishing, scam texts, malicious sites, and more. With real-time AI-powered Scam Guard built right in. 

Download for iOS → Download for Android → 

Roblox clamps down on chats and age checks as legal pressure builds

23 April 2026 at 09:57

Roblox has long faced criticism over child safety on its platform. Now it has started settling with state attorneys over the issue, and the total is climbing fast.

On April 21, Alabama Attorney General Steve Marshall announced a $12.2 million settlement with the child-focused online gaming platform. The State of West Virginia also settled for $11 million the same day. Those came a week after Nevada Attorney General Aaron Ford got the company to hand over $12 million.

Their problem with Roblox is clear from the settlement documents: they believe it hasn’t been adequately protecting children from predators on its platform.

What Roblox has to change

As part of Alabama’s settlement, Roblox must now run age checks on everyone via facial age estimation or a government ID starting May 1. That applies to both new and existing accounts. The company must now also monitor account behavior to catch users who lied about their age.

Adults and under-16s won’t be able to talk with each other at all unless they’re on a “trusted friend” list, added via QR code or a phone-contact import, and users that don’t undergo age verification can’t chat to anyone. 

Communication involving any minor cannot be encrypted, so law enforcement can read it during investigations. West Virginia’s settlement also insists that Roblox alert minors the first time they enter a private chat, so children understand how to communicate safely.

Roblox already stopped people from chatting without age verification as of January this year, but under new measures it will start restricting access to games for those that don’t undergo the process. Starting in June, the platform will split into three tiers: Roblox Kids for ages 5–8 will forbid any chats at all, and will only allow access to games labeled ‘minimal’ or ‘mild’ on its maturity scale. Those who don’t complete age verification will also have these restrictions. The other two account levels are Roblox Select for 9–15 year-olds, and standard accounts for those 16 and up.

Plenty more lawsuits to come

Three settlements in eight days totaling more than $35 million must hurt, but it’s just the beginning. Texas, Florida, Louisiana, Iowa, Nebraska, Kentucky, and Tennessee are all pursuing similar claims: that Roblox exposed children to risk and then misled parents about its safeguards.

In February, LA County sued Roblox, accusing the platform of choosing profit over safety and leaving kids exposed to grooming and explicit content.

Roblox is also separately dealing with nearly 80 federal lawsuits filed by families in California alone. And Australia’s eSafety Commissioner has also issued legally-enforceable transparency notices to Roblox and other tech companies. These force them to detail what they’re doing to protect children. Those notices are backed by fines of A$825,000 a day (that’s about US$590,783) for non-compliance.

Where the money will go

The $12.2 million from Alabama’s settlement funds school resource officers through the state’s Safe School Initiative. Nevada’s is earmarked for the Boys & Girls Club and “nondigital activities,” plus a law-enforcement liaison and an online-safety awareness campaign. West Virginia will invest $500,000 in safety education workshops for parents and children, create a $1.5 million three-year public safety campaign, and spend $2.4 million on a dedicated internet safety specialist for six years.

Stay alert

There’s a predictable rhythm to how big tech companies face down state attorneys general. First comes pushback, then rhetoric about shared values, and then they start handing over cash.

It is a step forward that Roblox is agreeing to new safeguards, but questions remain.

In its own lawsuit against Roblox launched last month, Nebraska complained that the company’s existing age-check technology was inadequate. From the complaint:

“Rather than meaningfully protecting children, the system has repeatedly misclassified users’ ages, placing adults in child chat groups and minors in adult categories, while age-verified accounts for young children have already been traded on third-party marketplaces, undermining any purported safety benefits.”

What happens when the age-estimation AI guesses wrong on a 14-year-old who looks 17, or when a “trusted friend” QR code gets passed around a group chat somewhere it shouldn’t?

The company’s Persona age-check tool has also turned out to do more than check ages: researchers say they found an exposed frontend showing the system was also running facial recognition against watchlists.

Settlements address past concerns, but they don’t guarantee future safety. Parents must still do the work to ensure that they know what their kids are signing up for and who else they might be playing with.

For more information about the safety of Roblox and other services, check out our research: How Safe are Kids Using Social Media?


CNET Editors' Choice Award 2026

“One of the best cybersecurity suites on the planet.” 

According to CNET. Read their review →


AI-powered defense for an AI-accelerated threat landscape

22 April 2026 at 19:00

We are at an inflection point in cybersecurity.

Recent advances in AI model capabilities are changing how vulnerabilities are discovered and exploited. AI models can autonomously discover weaknesses, chain multiple lower-severity issues into working end-to-end exploits, and produce working proof-of-concept code. This significantly compresses the window between vulnerability discovery and exploitation.

These changes require organizations to rethink exposure, response, and risk. However, the same capabilities that can give attackers an advantage also create a unique opportunity for defenders. When applied correctly, they can accelerate vulnerability discovery, improve detection engineering, and reduce time to mitigation. We look forward to working together as an industry to use these AI model capabilities as part of enterprise-grade solutions to tilt the balance in favor of defenders.

Partnering with leading model providers

Security has been and remains the top priority at Microsoft. Over the last two years, through our Secure Future Initiative (SFI), we have strengthened our security foundations for this age of AI, in part by using AI to accelerate vulnerability discovery and remediation and help defend against threats. We have also invested in fundamental AI for security research, including the development of open-source industry benchmarks that can be used to evaluate whether models are ready for real-world security work.

As we move forward, we are accelerating this work and partnering with the industry to use leading models, paired with our platforms and expertise, to turn AI-driven discovery into protection at scale.

Through Project Glasswing, Microsoft is working closely with Anthropic and industry partners to test Claude Mythos Preview, identify and mitigate vulnerabilities earlier, and coordinate defensive response. We evaluated Mythos using CTI-REALM, our open-source benchmark for real-world detection engineering tasks, and the results showed substantial improvements relative to prior models.

Microsoft is also evaluating other models. As part of our overall security approach, we continuously evaluate models from multiple providers as they are made available and integrate them into our enterprise-grade security platform. This multi-model approach is intentional as no single model defines our strategy.

Taking action in three fundamental areas

Defenders need to move faster to keep pace with AI-driven threats. We are focusing on three areas to help customers reduce risk and improve resilience.

1. AI-led vulnerability discovery and mitigations to stay current on software

We plan to incorporate advanced AI models, like Claude Mythos Preview, directly into our Security Development Lifecycle (SDL) to identify vulnerabilities and develop mitigations and updates. This allows us to discover more issues more quickly across a broader surface area than previous methods and address them earlier in the lifecycle.

AI-assisted discoveries are handled through our existing Microsoft Security Response Center (MSRC) processes, including Update Tuesday—our predictable and systematic way of distributing updates to customers—and out-of-band updates, where appropriate. Customers using Microsoft platform as a service (PaaS) and software as a service (SaaS) cloud services do not need to take any action; mitigations and updates are applied automatically. For customers who deploy Microsoft products on their own infrastructure, whether on-premises or self-hosted, staying current on all security updates is now not only the best practice; it is a fundamental requirement for staying secure against AI exposure.

We will deploy detections to Microsoft Defender, our threat protection solution, when updates are released and share details through the Microsoft Active Protections Program (MAPP) partners to help mitigate risk. We are also using advanced AI models to proactively scan select open-source codebases. Identified issues will be addressed through coordinated vulnerability disclosure.

2. AI-ready posture to reduce exposure

Patching, while critical, is not sufficient on its own. We have identified the five dimensions where autonomous AI driven attacks gain disproportionate advantage—patching, open-source software, customer source code, internet-facing assets, and baseline security hygiene.

For each dimension, Microsoft Security Exposure Management provides guidance and capabilities that customers can use to:

  • Assess their current state.
  • Understand prioritized actions to reduce risk.
  • Evaluate “what-if” scenarios before making changes.
  • Apply automation to remediate issues at scale.

These capabilities include tools like Microsoft Defender External Attack Surface Management (EASM) for continuous discovery of internet-facing assets, GitHub Advanced Security with CodeQL, Copilot Autofix for open-source and first-party code, and Microsoft Baseline Security Mode (BSM) to apply foundational controls across Exchange, Microsoft Teams, SharePoint, OneDrive, Office, and Microsoft Entra—with impact simulation before enforcement.

Others in the industry have shared guidance and rightly emphasized the importance of continuous asset discovery and posture management. We are delivering an integrated experience through a new Microsoft Security Exposure Management blade—Secure Now—that combines guidance with the ability to act, so customers proactively reduce their exposure. Secure Now is available today at https://security.microsoft.com/securenow

3. AI-powered solutions to defend at scale

Beyond plans to use advanced AI models directly into our Security Development Lifecycle (SDL), we are separately building new solutions to help customers leverage advanced AI models to improve their security at enterprise scale.

  • Rapidly deployed Defender detections developed for AI-discovered vulnerabilities, sim-shipping with corresponding updates to help mitigate risk immediately.
  • We have learned through our own testing that model capability to discover potential vulnerabilities is only the beginning. Organizations must also be able to use AI to validate and prioritize based on exploitability and impact, and build the fix. To help we plan to productize a new multi-model AI-driven scanning harness developed internally and make it available to customers to streamline their experience and deliver outcomes more quickly. This solution is expected to be available in preview in June 2026.

Our goal is to ensure findings are actionable. While models are powerful on their own, without prioritization and context, large volumes of results can overwhelm development teams. These new solutions are designed to pair model output with the context and security solutions needed for enterprises to drive security effectiveness at scale.

Get started today

Customers can get started now by reviewing the guidance at https://security.microsoft.com/securenow. Any customer with a Microsoft Entra ID will be able to access the guidance. In addition, Microsoft Security customers will have access to capabilities that enable them to assess their exposure and take action.

We have also mobilized our Customer Success organization to support customers in implementing this guidance.

What’s ahead

This work is ongoing. We will continue to share updates as testing progresses, new models emerge, and new guidance and solutions become available. The threat landscape will continue to evolve, but so will our defenses—and we are committed to ensuring that our customers have the tools, guidance, and partnership they need to stay ahead.

Security is a team sport. The organizations that act on this shift—by staying current on patches, reducing exposure, and leveraging AI-powered security solutions—will be significantly harder to compromise than those that do not. The time to act is now and we look forward to partnering with the industry to build a safer world for all.

To learn more about Microsoft Security solutions, visit our website. Bookmark the Security blog to keep up with our expert coverage on security matters. Also, follow us on LinkedIn (Microsoft Security) and X (@MSFTSecurity) for the latest news and updates on cybersecurity.

The post AI-powered defense for an AI-accelerated threat landscape appeared first on Microsoft Security Blog.

A technical walkthrough of multicloud full-stack security using AWS Security Hub Extended

22 April 2026 at 18:31

Building on our recent announcement of AWS Security Hub Extended —our full-stack enterprise security offering — we want to show you how we’re simplifying security procurement and operations for your multicloud environments. Whether you’re a security architect evaluating solutions or a CISO looking to streamline vendor management, this post walks through the streamlined experience that transforms how you acquire, deploy, and manage end-to-end enterprise security solutions across endpoint, identity, email, network, data, browser, cloud, AI, and security operations. Security Hub Extended brings together AWS security services with carefully curated security partners. Delivering better outcomes together through unified procurement, billing, and operations that significantly reduce vendor management overhead so you can focus on what matters most: protecting your organization.

The challenge we’re addressing

Security teams today spend too much time on vendor management, evaluating services, negotiating contracts, and managing multiple billing cycles instead of focusing on what matters most: managing risk. But the procurement challenge runs even deeper. Until now, customers really only had one option: sign multi-year agreements based solely on proof-of-concept testing and estimated annual usage. This forces organizations to commit budget before they can validate whether a solution will work for them at scale.

AWS Security Hub Extended transforms this procurement model. Security Hub Extended offers customers the option to get started with pay-as-you-go pricing and no commitments, so they can move fast and validate solutions in their actual environment. After they’ve confirmed a solution works at scale, they can then align their vendor strategy and sign longer-term commitments for even more favorable pricing.

Security Hub Extended provides a curated set of carefully chosen partner solutions with competitive pricing, unified billing through your AWS account, and seamless integration. Our initial launch partners, selected by customers for their proven value, include 7AI, Britive, CrowdStrike, Cyera, Island, Noma, Okta, Oligo, Opti, Proofpoint, SailPoint, Splunk, Upwind, and Zscaler.

Getting started with Security Hub Extended

AWS Security Hub consolidates threat analytics from Amazon GuardDuty, vulnerability management from Amazon Inspector, and sensitive data discovery from Amazon Macie, correlating these signals with Security Hub Exposure findings to determine overall risk, reachability, and assumability. Security Hub Extended builds on this foundation by adding curated partner solutions, extending these unified security operations across your entire organization including multicloud, on-premises, and endpoint environments. If you’re already using Security Hub, you can navigate directly to the Extended plan section.

Getting started with Security Hub is straightforward. From the AWS Management Console, search for Security Hub to start the onboarding walkthrough. If you’re not already a Security Hub customer, you can quickly complete onboarding by designating an AWS organization delegated administrator (DA) account. You can then centrally enable and manage Security Hub across your entire organization’s accounts and AWS Regions from a single location (see Introduction to AWS Security Hub). After you’ve onboarded, navigate to the Extended plan section to add curated partner solutions.

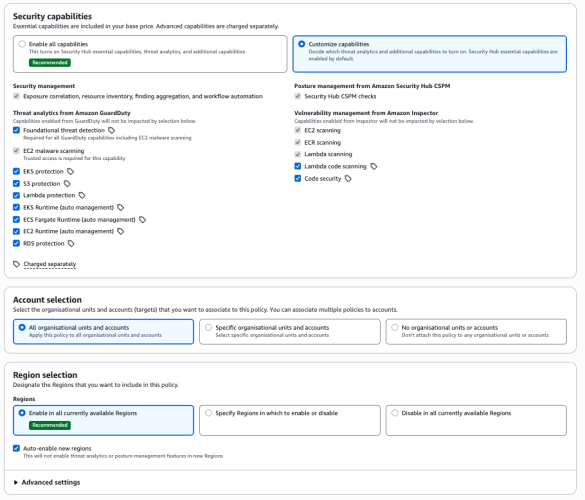
Figure 1- Security Hub centralized configuration

Figure 1: Security Hub centralized configuration

From this single interface, you can enable detection and response capabilities across your entire organization, provide granular configurations at the organizational unit or member account level, select specific Regions, and turn individual features on or off as needed.

Understanding risk through attack paths

The Security Hub risk correlation engine identifies potential exposures by correlating threats, vulnerabilities, and misconfigurations to reveal how they connect and could lead to compromise of critical resources.

Figure 2 - Security Hub exposure attack path visualization

Figure 2: Security Hub exposure attack path visualization

The attack path visualization in the preceding figure reveals critical insights including upstream root causes and blast radius, showing the potential impact if a threat actor exploits a vulnerability. You can use this visualization to focus on fixing the root cause rather than addressing symptoms. For example, updating one security group configuration can eliminate the entire attack path, cutting off all downstream exposure.

Accessing Security Hub Extended

You can find Security Hub Extended, shown in the following figure, in the left navigation pane under Management in your Security Hub delegated administrator (DA) account; Security Hub Extended will only be visible from the delegated administrator account. The Extended plan brings curated third-party security solutions directly into the Security Hub experience. Because Extended is built into Security Hub, there’s no separate console to manage. You discover, subscribe to, and operate curated partner solutions from the same place you manage enterprise security, delivering unified operations across your entire security estate.

Figure 3- Security Hub Extended partners

Figure 3: Security Hub Extended partners


Transparent, competitive pricing consolidated with Security Hub

Unlike traditional third-party engagements that require lengthy negotiations, private pricing deals, and multi-year commitments, Security Hub Extended offers complete pricing transparency. Every partner solution displays clear, competitive monthly pay-as-you-go rates billed directly with Security Hub requiring no commitments. For example, Cloud Security from Upwind costs $3.75 per resource per month, and Identity Security from Okta costs $20 per user per month.

All Security Hub Extended offerings are also eligible for AWS Enterprise Discount Program (EDP) discounts that will be applied automatically. If you have an existing AWS enterprise discount agreement, those discounts automatically apply to Security Hub Extended offerings, further reducing your effective costs. All partner solutions you deploy through Security Hub Extended appear on your consolidated AWS bill, no separate invoices or payment processes.

Streamlined onboarding

Adopting curated partner solutions through Security Hub Extended is straightforward. Choose View Product to initiate an automated workflow. Depending on the solution, you’ll either be directed to the partner onboarding console or provide information for the partner to guide you through their onboarding process tailored to your environment.

Billing begins only after you’re fully activated on the partner solution and starts automatically, no additional action is required to benefit from the unified billing. If you’re already using one of the curated partner solutions, transitioning to Security Hub Extended for consolidated billing and flexible pricing won’t disrupt your current services. Now, instead of receiving separate invoices for each partner in addition to Amazon Inspector, GuardDuty, and Security Hub CSPM you get one unified bill through Security Hub. This consolidates visibility to support better understanding of spend and to manage cost.

Unified operations

Security Hub Extended unifies security operations by consolidating findings from AWS and curated partner solutions. All findings use the Open Cybersecurity Schema Framework (OCSF) for consistency, without the need for complex data normalization, transformation, and extract, transform, and load (ETL) processes.

When you deploy solutions such as CrowdStrike, Noma, and Upwind alongside Splunk and 7AI through Security Hub Extended, security findings automatically flow into Security Hub and then seamlessly route to Splunk and 7AI. All in OCSF format so your security team can focus on responding to threats, not managing pipelines, so you can quickly identify and respond to security risks that span boundaries—from endpoint compromises to cloud infrastructure—without spending valuable time on manual integration work.

The full-stack security vision

Security Hub Extended represents a shift in how you discover, procure, and build comprehensive security programs. Instead of managing dozens of vendor relationships, negotiating separate contracts, agreeing to multi-year annual commitments, and integrating disparate tools, you now have one procurement process through AWS, one bill with transparent competitive pay-as-you-go pricing, one console for unified security operations, one support channel for AWS Enterprise Support customers, and one schema (OCSF) for all security findings. The result: reduced security risk, improved team productivity, and a more unified approach to security operations across your enterprise.

Get started

Try Security Hub Extended today and experience how simplified procurement and unified operations can transform your security program. Security Hub Extended is generally available globally in all AWS commercial Regions where Security Hub is available. We’ve also published a walk through video to further explain how Security Hub Extended works.

It’s still Day 1, but we’re iterating fast, so share your feedback with us on AWS re:Post for Security Hub or through your AWS Support contacts and watch for future blog posts on our progress.


Matt Meck

Matt Meck

Matt is a Worldwide Security Specialist at Amazon Web Services, based in New York, with 10 years of experience in the tech industry. For the past 4 years at AWS, he’s focused on Detection and Response, helping solve complex security challenges in the rapidly evolving security space. He works closely with product teams, customers, partners, and field teams to deliver effective security solutions.


Michael Fuller

Michael Fuller

Michael has been with AWS for 16 years and led product for AWS Security Services for 11 years. Michael has 29 years in the industry and held several roles in product management, business development, and software development for IBM, Cisco, and Amazon. Michael has a Bachelor’s of Science in Computer Engineering from the University of Arizona and an MBA from the University of Washington.


Palo Alto Networks and Google Cloud

22 April 2026 at 18:00

Expand Strategic Collaboration to Secure the AI Enterprise

The transition from generative AI to agentic AI represents one of the most significant shifts in the history of enterprise technology. As organizations move from simple chatbots to autonomous agents that can execute business processes, the attack surface isn't just changing, it's exploding.

At Google Cloud Next 2026 in Las Vegas, Palo Alto Networks is proud to announce a series of groundbreaking integrations with Google Cloud. These innovations are designed to do more than just monitor the new AI-driven landscape; they are built to secure it by design. AI deployment is currently outpacing AI governance. By embedding our security platform into Google Cloud’s infrastructure, we are giving today’s enterprises the foundation to become the autonomous organizations of tomorrow.

Here is a look at the four major milestones of our partnership being unveiled this week.

Secure AI Agents with Google Cloud + Prisma AIRS

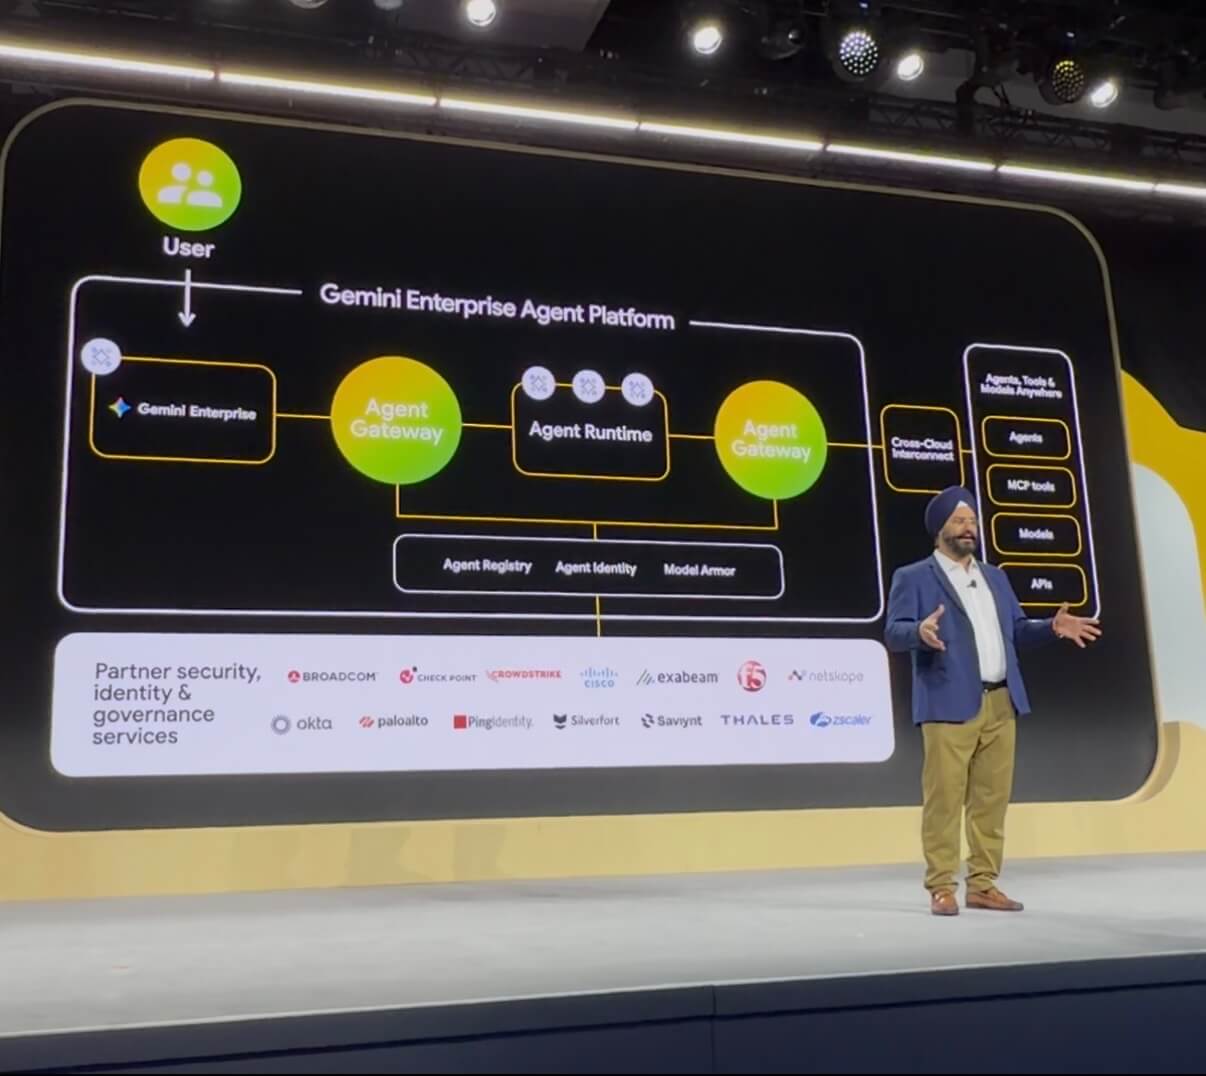
As autonomous AI agents become the new enterprise standard, security can no longer be an afterthought; it must be architectural. By integrating Prisma AIRS™ natively with Google Cloud Gemini Enterprise Agent Platform, we provide the proactive defenses required to govern complex agentic workflows. This integration ensures that as you scale your autonomous workforce, your security scales with it, providing comprehensive operational integrity without hindering the speed of innovation.

We are delivering capabilities across three critical pillars:

  • Protecting Agent-Specific Runtime Risks: In an agentic ecosystem, the primary risk is unauthorized or a destructive action taken by the AI agents themselves. Prisma AIRS secures the "agent-to-tool" interface, preventing poisoned context from triggering malicious scripts or destructive actions. The solution monitors agent execution in real-time, so agents cannot leak sensitive credentials or tool schemas, maintaining the boundary between agents and their access to enterprise data.
  • Securing the GenAI Application Surface: Modern AI applications and agents require a secure-by-design approach. Prisma AIRS AI Runtime Security™ provides prevention of more than 30 adversarial prompt injection and jailbreak techniques, as well as malicious code and URLs within LLM outputs. Prisma AIRS utilizes over 1,000 predefined patterns out of the box and ML-powered Enterprise DLP to stop sensitive data leakage.
  • Enforcing Enterprise AI Safety and Grounding: Trust in AI is built on the consistency and safety of its output. Prisma AIRS allows organizations to define safety policies in natural language and filter toxic content across eight distinct categories to protect brand reputation. Using contextual grounding, Prisma AIRS can prevent misleading outputs that contradict internal RAG data, keeping agents tied to real facts.

This integration ensures that as you scale your autonomous workforce, your security posture scales with it, providing operational integrity without hindering the speed of innovation.

Security-as-Code for Prisma AIRS Integration with Application Design Center (ADC)

The traditional bolt-on approach to security is no longer viable in a cloud-first world. Google Cloud’s Application Design Center (ADC) is revolutionizing how applications are built, using an intuitive canvas and natural language via Gemini Code Assist.

Palo Alto Networks is announcing that it will be published as a template within the Application Design Center, providing more capabilities to engineering teams:

  • Drag-and-Drop Security – Visually "snap" VM-Series firewalls and Prisma AIRS AI protections directly into network flows.
  • AI-Driven Architecture – Use natural language prompts to generate secure-by-default, multiregion architectures.
  • Simultaneous Deployment – Deploy entire application stacks and security services in a single, unified workflow, ensuring protection is present from the very first minute of deployment.

Zero-Day Protection at Scale with Advanced Malware Sandboxing for Google Cloud NGFW Enterprise

The battle against malware has shifted to the cloud. Modern attacks are faster, more evasive and capable of bypassing traditional defenses.

That is why we are excited to announce Advanced WildFire®, powered by Palo Alto Networks, natively integrated into Google Cloud NGFW Enterprise, delivering AI-driven malware prevention directly within Google Cloud environments.

This integration embeds inline sandboxing and real-time threat intelligence directly into Google Cloud’s distributed firewall to stop advanced and unknown threats before they impact workloads, enabling:

  • Secure Detonation – Suspicious files are safely executed in a controlled sandbox environment to uncover hidden and unknown threats.
  • Inline Traffic Inspection – Inbound and outbound traffic is analyzed in real time to prevent lateral movement of malicious payloads across cloud environments.
  • AI-Driven Threat Prevention – Leverages global threat intelligence by Palo Alto Networks to block zero-day threats before they compromise workloads.

With Advanced WildFire embedded directly into Google Cloud NGFW Enterprise, organizations can extend consistent protection across their cloud infrastructure while maintaining operational simplicity.

Cloud NGFW Enterprise Advanced Malware Sandboxing will be available in Public Preview soon.

Defining the Future with the Google Cloud Marketplace

Palo Alto Networks has joined the Google Cloud Marketplace Agent-as-a-Service as a launch partner to introduce the Prisma AIRS Model Security agent. Operating as an Agent-as-a-Service, this solution scans AI models for vulnerabilities and policy noncompliance before they reach production.

Available in the Agent Gallery inside Gemini Enterprise, this marketplace offering runs entirely within the customer’s own Google Cloud environment, providing both new and existing Prisma AIRS users a seamless and simple deployment experience inside Gemini Enterprise.

Securing AI Innovation at Scale

The collaboration between Palo Alto Networks and Google Cloud is built on a shared vision: Security should be an accelerator for innovation, not a bottleneck. As we look toward the future of the AI-powered enterprise, our commitment remains to provide the most robust, platform-driven security for every workload, every agent and every interaction.

Want to see these integrations in action? Contact your Palo Alto Networks representative to learn more about how we are securing the future of the cloud together. If you’re attending Google Cloud Next 2026, join us at these sponsored sessions:

The post Palo Alto Networks and Google Cloud appeared first on Palo Alto Networks Blog.

Scaling AI Agents with Confidence

22 April 2026 at 17:59

The Google Cloud and Palo Alto Networks Partnership

As AI agents move into business-critical environments, they are transforming everything from security operations to internal workflows. However, scaling these AI applications introduces unprecedented hurdles for security executives, from detecting "shadow AI" and unsanctioned usage to governing complex nonhuman identities across multimodel environments.

To overcome these challenges, organizations need more than just tools; they need a layered architecture built on a foundation of platformization. The long-standing partnership between Palo Alto Networks and Google Cloud provides this essential framework, offering customers:

  • Integrated Security Ecosystems: Seamlessly manage the full agent lifecycle with visibility and observability across your entire AI infrastructure.
  • Jointly Engineered Solutions: Leverage over 80 co-engineered integrations designed to eliminate the tradeoff between a cloud-native experience and best-in-class security.
  • Proven Scale and Performance: Benefit from a partnership that has already delivered impactful, AI-driven solutions to protect joint customers from evolving threats.

Google Cloud Marketplace enables customers to discover, try, buy and use industry-leading applications that have been validated to run on Google Cloud. Palo Alto Networks has closed $2.4 billion in GCP bookings, helping address evolving customer needs, such as simplified procurement and seamless deployment.

Kevin Ichhpurani, President, Global Partner Ecosystem at Google Cloud:

We’re pleased to celebrate Palo Alto Networks as our Global Technology Partner of the Year… Palo Alto Networks has consistently delivered impactful, AI-driven security solutions that help Google Cloud customers better protect their organizations from evolving threats.

The extensive, long-standing collaboration between Palo Alto Networks and Google Cloud includes jointly engineered offerings, built on 80 solution integrations that help customers build, run and secure AI-enhanced cloud infrastructure and applications with end-to-end protection.

Palo Alto Networks Wins 2026 Global Technology Google Cloud Partner of the Year Award

At Google Cloud Next, Palo Alto Networks has been recognized with four 2026 Google Cloud Partner of the Year awards. By partnering with Google Cloud, we help customers securely leverage the power of the cloud and AI-driven growth with comprehensive cloud-native security offerings. Wins included the following:

  • Global Technology
  • Marketplace: Technology
  • Marketplace: Security
  • Security: Artificial Intelligence

These Partner of the Year Awards underscore our expanding partnership with Google Cloud. We share a mutual dedication to improve cloud, network security and AI observability, as well as the progress we’ve made in protecting our joint customers from today’s and tomorrow’s cyberthreats.

By combining our industry-leading security engineering with Google Cloud’s industry-leading cloud infrastructure and services, we’re providing advanced protection for every stage of a customer’s digital journey. We want customers to feel secure from the formative steps of lifting workloads into the cloud, to expanding digital innovation across platforms, to reaching new levels of business scale and velocity.

Protecting these journeys requires alignment and modernization of infrastructure (lift and shift), applications (refactoring) and user access models (zero trust). It requires an advanced AI drive security operations transformation across all IT domains, leveraging machine learning and sophisticated models to minimize human interventions and unguarded sides.

Our relationship with Google Cloud is based on a deep engineering relationship, yielding integrated solutions that help customers achieve better digital outcomes. Our partnership can help your organization eliminate tradeoffs between a cloud-native experience and best-in-class security. We have more than 80 co-engineered integrations, helping to improve and protect hybrid workers, cloud migrations and application modernization efforts.

We remain committed to our goals of outpacing cyberthreats, helping customers at every stage of their cloud journey, and creating a world where tomorrow is more secure than today.

Whether you’re just beginning your cloud journey or managing complex transformational projects, our jointly engineered, AI-driven solutions are designed to deliver seamless, scalable security. Explore the dynamic partnership between Palo Alto Networks and Google Cloud. Join us at Google Cloud Next '26 in Las Vegas from April 22-24 to discover how to secure your development lifecycle from code to cloud.

The post Scaling AI Agents with Confidence appeared first on Palo Alto Networks Blog.

Network Engineering Basics

By: BHIS
22 April 2026 at 17:40

The computer networking field is broad, encompassing many focus areas similar to cybersecurity. If you’re new to the field or just interested in networking, knowing where to start can be challenging. Searching for a network engineer position on any job listing site will yield thousands of results, and no two job descriptions will be the same.

The post Network Engineering Basics appeared first on Black Hills Information Security, Inc..

From Access Control to Outcome Control: Securing AI Agents with Check Point and Google Cloud

22 April 2026 at 15:00

AI is changing how software works. Applications no longer just process requests. They reason, make decisions, and take action. AI agents now retrieve data, invoke tools, and execute workflows across systems in real time. That shift introduces a new kind of risk. Because in an agentic world, security is no longer just about who has access. It’s about what AI is allowed to do. A new control point for agentic systems in Google Cloud Google Cloud’s Gemini Enterprise Agent Platform provides a centralized control point for agentic systems enabling identity, access, policy enforcement, and observability across how agents operate. This […]

The post From Access Control to Outcome Control: Securing AI Agents with Check Point and Google Cloud appeared first on Check Point Blog.

Experience AI-Powered Check Point Firewall at Google Cloud Next

22 April 2026 at 15:00

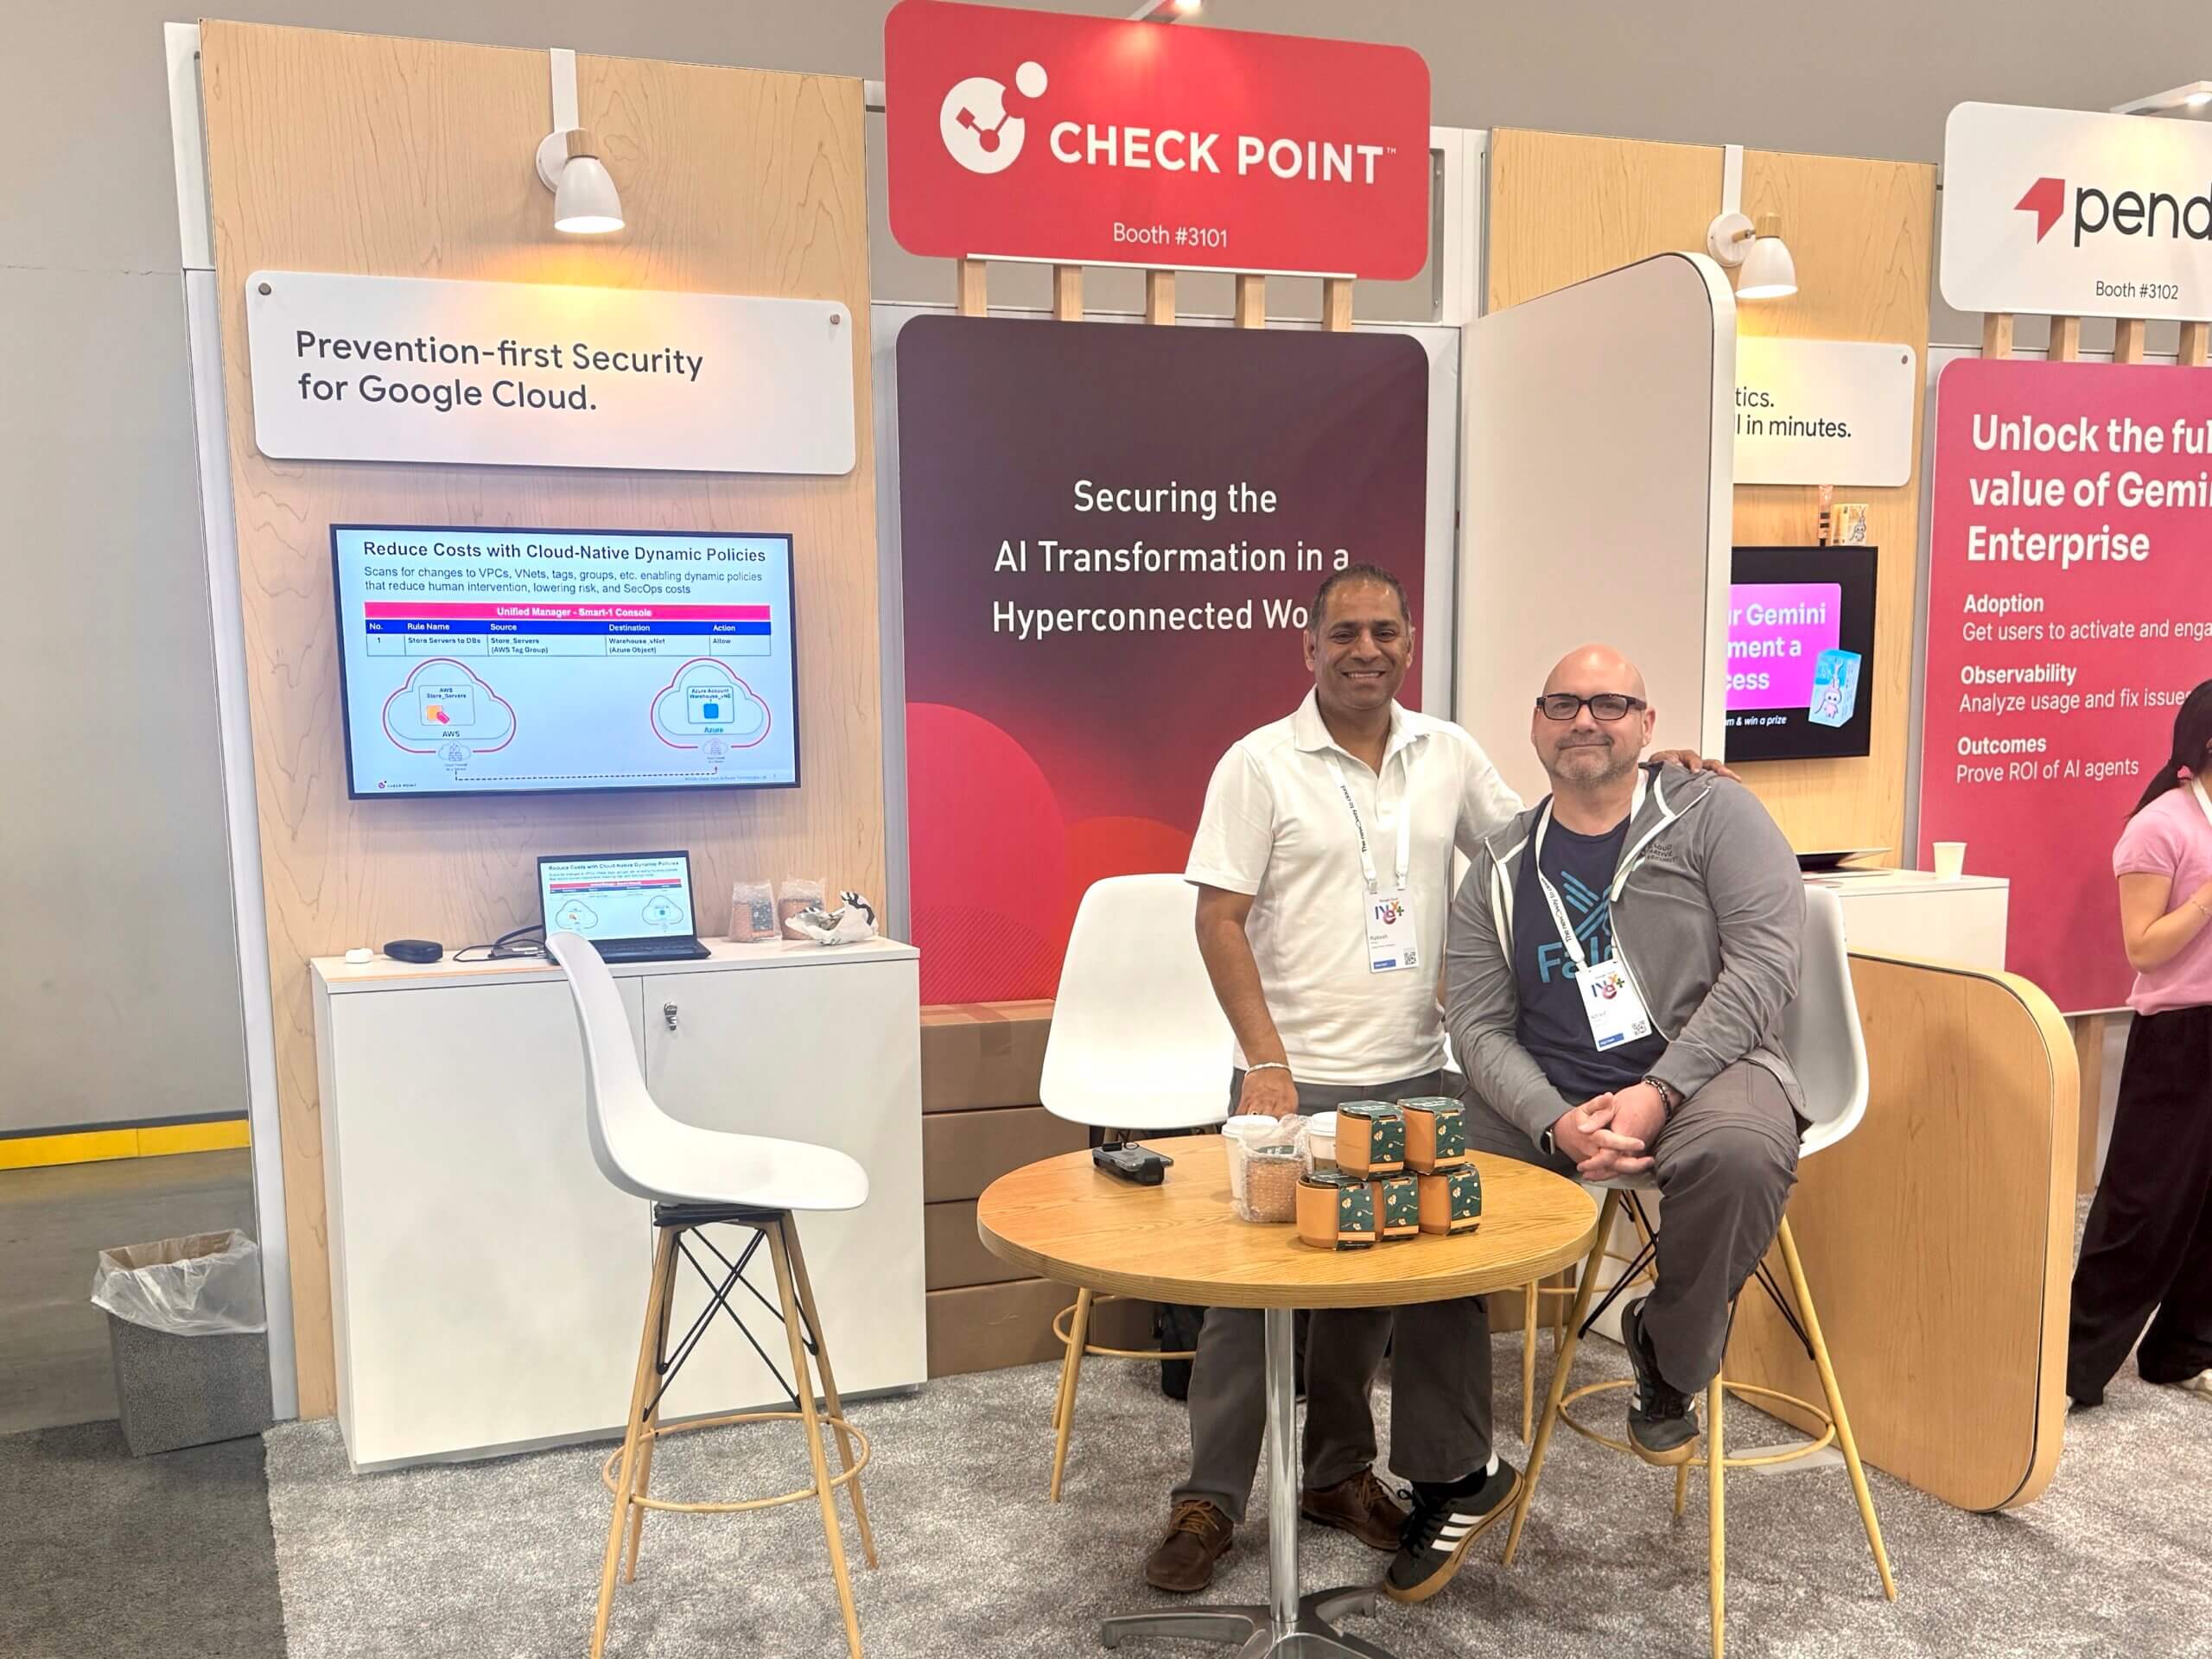
Today’s enterprises demand Zero Trust security, everywhere. Cloud security teams require high-performance protection without the burden of managing firewalls at scale. For this reason, organizations are seeking managed network security solutions that reduce operational overhead while improving consistency, visibility, and prevention across complex multi-cloud environments. Responding to that demand, Check Point is continuing rollout of an AI-powered cloud firewall as a service now available for preview on Google Cloud, as well as Amazon Web Services (AWS) and Microsoft Azure.  There will be demos of the new firewall service at the Check Point Booth #3101 in the Google Next Solution Expo.  Check Point Cloud Firewall as a Service eliminates the complex overhead of managing firewall software infrastructure, giving busy DevOps and Security teams time to focus on policy management, compliance, and other strategic initiatives.   Continued Evolution of Cloud Firewalls  Cloud Firewall as a Service on Google Cloud marketplace delivers the power of Cloud Firewall (formerly Guard Network Security) with advanced threat prevention, AI-driven security intelligence, automated policy […]

The post Experience AI-Powered Check Point Firewall at Google Cloud Next appeared first on Check Point Blog.

Palo Alto Networks Joins DNS-OARC as a Platinum Member

Palo Alto Networks recently joined the DNS-OARC community as a Platinum Member. Together, our organizations share a commitment to advancing collaboration in research and operational excellence across the global DNS ecosystem. DNS is critical to both internet infrastructure and security, and this collaboration facilitates the sharing of real-world insights among researchers and practitioners.

Our Contribution

We help organizations secure their digital environment with a comprehensive portfolio of cybersecurity solutions spanning Network, Cloud, Security Operations, AI and Identity. Trusted by more than 70,000 customers worldwide and informed by Unit 42® Threat Intelligence, their AI-driven platforms help organizations reduce complexity, modernize with confidence, and securely enable innovation.

As a Platinum Member, our subject matter experts will actively participate in the DNS-OARC community by engaging in discussions and contributing to research on evolving DNS threats and network challenges. The growing intersection of DNS and security makes access to intelligence and experience increasingly important. It strengthens the community’s ability to respond to emerging challenges and improves resilience across the internet.

Through our participation, our customers will gain stronger protection informed by community-driven intelligence and real-world operational insight. These learnings are continuously integrated into our threat intelligence and security capabilities. Our participation signals our support for DNS-OARC’s mission of fostering open dialogue and shared learning across the DNS ecosystem. This collaboration helps bridge DNS operations with broader security practices, improving coordination between operators, researchers and security practitioners.

Our Commitment to the DNS-OARC and Global Communities

Collaboration between our organizations strengthens the connection among DNS operations and modern security practices by bringing together operational insight and a global community dedicated to advancing the internet’s resilience.

For the DNS-OARC community, our commitment enhances knowledge sharing around evolving DNS threats, large-scale network operations and practical approaches to emerging challenges.

For organizations and customers, it reinforces a stronger alignment between DNS infrastructure and security, expands access to community-driven intelligence and supports more resilient, well-informed defenses.

Tong Zhao, Senior Manager of DNS Security Engineering, Palo Alto Networks:

We recognize the critical role of DNS-OARC in DNS operations and research. The teams from Palo Alto Networks believe that our DNS-OARC membership aligns perfectly with our goals. We are eager to participate in and contribute to the DNS community.

Our partnership with the DNC-OARC highlights the value of open collaboration in helping both the community and its participants stay ahead of an increasingly complex threat landscape. To learn more about how our expertise and insights support DNS-OARC’s mission to improve the security and stability of the internet’s DNS, visit DNS-OARC.

The post Palo Alto Networks Joins DNS-OARC as a Platinum Member appeared first on Palo Alto Networks Blog.

Enterprise-Grade Application Security, Cloud-Native Speed: Introducing Imperva for Google Cloud

22 April 2026 at 14:59

In today’s dynamic digital environment, the pressure to innovate has never been greater. Development teams are pushing for native cloud tools to maximize performance and cost-efficiency, while security teams require best-of-breed, enterprise-grade protection to defend against an ever-evolving threat landscape. This often creates a point of friction, forcing organizations into a difficult trade-off: sacrifice performance for security, or accept weaker protections for the sake of speed.

To resolve this challenge, Thales Imperva is collaborating with Google Cloud to deliver a solution that helps bridge this gap. We are proud to introduce Imperva for Google Cloud (IGC), an integrated security solution that offers the best of both worlds: enterprise-grade application security with the cloud-native performance you expect from Google Cloud.

Imperva for Google Cloud: A Holistic, Integrated Solution

Imperva for Google Cloud is not just another security layer; it is a fully managed, best-in-class Web Application and API Protection (WAAP) solution built directly into the fabric of Google Cloud. This integration, available now on Google Cloud Marketplace,   provides robust protection without disrupting your existing infrastructure or workflows.

  • Cloud-Native Performance Without Compromise: Imperva for Google Cloud uses Google Cloud’s native Service Extension and Private Service Connect to inspect traffic within the Google Cloud network. This means all traffic analysis happens without your data ever leaving Google Cloud infrastructure, preserving optimal latency, performance, and data residency.
  • Quick Deployment: Forget complex re-architecture. Imperva for Google Cloud can be deployed quickly using familiar tools like Terraform, Google Cloud CLI (gCloud CLI), or the Google Cloud console UI. There are no disruptive DNS, SSL, or network routing changes required, allowing you to achieve production-ready protection almost immediately.
  • Enterprise-Grade Protection Out of the Box: Imperva for Google Cloud is powered by Imperva’s industry-leading security engine, delivering comprehensive WAF, advanced API Security, and Account Bot Protection. Backed by 24/7 threat research, the Imperva solution provides near-zero false positives, with 97% of customers successfully using default policies and 95% running in blocking mode from day one. This dramatically reduces the operational overhead of constant rule tuning.

Real-World Impact: Securely Accelerating Your Business

By eliminating the trade-offs between security and performance, Imperva for Google Cloud helps organizations achieve key business outcomes:

  • Accelerate Lift-and-Shift Migrations: Migrate workloads to Google Cloud confidently with security that adapts to your applications, not the other way around. Eliminate migration delays caused by complex security re-architecture.
  • Unleash DevOps-Friendly Security: Empower development teams to innovate at speed. IGC closes the security gaps in built-in tools without slowing down deployment velocity or requiring developers to become security experts.
  • Protect Modern Cloud-Native Applications: Secure your Kubernetes and microservices architectures with best-in-class defenses optimized for low-latency environments.
  • Achieve Unified Multi-Cloud Governance: Manage security for all your Imperva-protected environments from a single, unified dashboard, providing consistent policy management and visibility across your entire multi-cloud estate.

“Bringing Thales Imperva to Google Cloud Marketplace will help customers quickly deploy, manage, and grow the company’s integrated security solution on Google Cloud’s trusted, global infrastructure,” said Dai Vu, Managing Director, Marketplace & ISV GTM Programs at Google Cloud. “Thales can now securely scale and support organizations that want to use its Imperva for Google Cloud solution to increase protection for their cloud-native applications, APIs, microservices and more.”


Join Us on the Journey to More Seamless Cloud Security

As we approach key industry events like our exclusive Executive Briefing Center (EBC) meeting in late March and Google Cloud Next 2026 in April, the conversation around integrated  security has never been more relevant. The launch of Imperva for Google Cloud marks a pivotal moment in our relationship with Google, providing a clear path for customers to secure their digital assets without compromise.

Ready to secure your cloud-native applications?

The post Enterprise-Grade Application Security, Cloud-Native Speed: Introducing Imperva for Google Cloud appeared first on Blog.
Malicious trading website drops malware that hands your browser to attackers

22 April 2026 at 14:30

During our threat hunting, we found a campaign using the same malware loader from our previous research to deliver a different threat: Needle Stealer, data-stealing malware designed to quietly harvest sensitive information from infected devices, including browser data, login sessions, and cryptocurrency wallets.

In this case, attackers used a website promoting a tool called TradingClaw (tradingclaw[.]pro), which claims to be an AI-powered assistant for TradingView.

TradingView is a legitimate platform used by traders to analyze financial markets, but this fake TradingClaw site is not part of TradingView, nor is it related to the legitimate startup tradingclaw.chat. Instead, it’s being used here as a lure to trick people into downloading malware.

What is Needle Stealer?

Needle is a modular infostealer written in Golang. In simple terms, that means it’s built in pieces, so attackers can turn features on or off depending on what they want to steal.

According to its control panel, Needle includes:

  • Needle Core: The main component, with features like form grabbing (capturing data you enter into websites) and clipboard hijacking
  • Extension module: Controls browsers, redirects traffic, injects scripts, and replaces downloads
  • Desktop wallet spoofer: Targets cryptocurrency wallet apps like Ledger, Trezor, and Exodus
  • Browser wallet spoofer: Targets browser-based wallets like MetaMask and Coinbase, including attempts to extract seed phrases

The panel also shows a “coming soon” feature to generate fake Google or Cloudflare-style pages, suggesting the attackers plan to expand into more advanced phishing techniques.

Needle Stealer panel

In this article, we analyze the distribution of the stealer through a fake website related to an AI service called TradingClaw. We have detected that the same stealer is also distributed by other malware such as Amadey and GCleaner. 

Analysis of the TradingClaw campaign

In this campaign, the malware is distributed through a fake website advertising TradingClaw as an AI trading tool.

Malicious TradingClaw website

The site itself behaves selectively. In some cases, visitors are shown the fake TradingClaw page, while in others they are redirected to a different site (studypages[.]com). This kind of filtering is commonly used by attackers to avoid detection and only show the malicious content to intended targets. Search engines, for example, see the Studypages version:

Studypages fake page
Google results shows the Studypages fake page

If a user proceeds, they are prompted to download a ZIP file. This file contains the first stage of the infection chain.

Like in the previous campaign, the attack relies on a technique called DLL hijacking. In simple terms, this means the malware disguises itself as a legitimate file that a trusted program will load automatically. When the program runs, it unknowingly executes the malicious code instead.

In this case, the DLL loader (named iviewers.dll) is executed first. It then loads a second-stage DLL, which ultimately injects the Needle Stealer into a legitimate Windows process (RegAsm.exe) using a technique known as process hollowing.

Needle Stealer injected in RegAsm.exe process
Needle Stealer injected in RegAsm.exe process

The stealer is developed in Golang, and most of the functions are implemented in the “ext” package. 

Part of the “exe” package

What the malware does

Once installed, the Needle core module can:

  • Take screenshots of the infected system
  • Steal browser data, including history, cookies, and saved information
  • Extract data from apps like Telegram and FTP clients
  • Collect files such as .txt documents and wallet data
  • Steal cryptocurrency wallet information

One of the more concerning features is its ability to install malicious browser extensions.

Malicious browser extensions

The stealer also supports the distribution of malicious browser extensions, giving attackers a powerful way to take control of the victim’s browser.

We identified multiple variations of these extensions, each with slightly different file structures and components. Behind the scenes, the malware uses built-in Golang features to unpack a hidden ZIP archive (often named base.zip or meta.zip) that contains the extension files, along with a configuration file (cfg.json).

Partial cfg.json config file:

{
  "extension_host": {},
  "api_key": "…
  "server_url": "https://C2/api/v2",
  "self_destruct": true,
  "base_extension": true,
  "ext_manifest": {
    "account_extension_type": 0,
    "active_permissions": {
      "api": [
        "history",
        "notifications",
        "storage",
        "tabs",
        "webNavigation",
        "declarativeNetRequest",
        "scripting",
        "declarativeNetRequestWithHostAccess",
        "sidePanel"
      ],
      "explicit_host": [
        "<all_urls>"
      ],
      "manifest_permissions": [],
      "scriptable_host": [
        "<all_urls>"
      ]
    },
    "commands": {
      "_execute_action": {
        "was_assigned": true
      }
    }, 
…

This configuration file is key. It tells the malware where to send stolen data (the command-and-control server), which malicious extension to install, and which features to enable.

The stealer extension is dropped in a random folder in the path %LOCALAPPDATA%\Packages\Extensions. The folder contains three main files popup.js, content.js, and background.js.   

The malicious extension dropped

The extensions analyzed have Google-related names.

The fake malicious extension on Edge Browser

What the malicious extensions can do

The extension gives attackers near full control over the browser, with capabilities that go far beyond typical malware.

It can:

  • Connect to a remote server using a built-in API key and regularly check in for instructions. It can also switch to backup domains if the main server goes offline.
  • Generate a unique ID to track the infected user over time.
  • Collect full browsing history and send it to a remote server (/upload).
  • Monitor what you’re doing in real time, including which sites you visit, and apply attacker-controlled redirect rules. This allows it to silently send you to different websites or alter what you see on a page, including injecting or hiding content.
  • Intercept downloads, cancel legitimate files, and replace them with malicious ones from attacker-controlled servers.
  • Inject scripts directly into web pages, enabling further data theft or manipulation.
  • Display fake browser notifications with attacker-controlled text and images.

How it communicates with attackers

The stealer and its extension communicate with command-and-control (C2) servers using several API endpoints. These are essentially different “channels” used for specific tasks:

  • /backup-domains/active—retrieves backup servers to stay connected if the main one is blocked
  • /upload—sends stolen data back to the attackers
  • /extension—receives instructions for redirects, downloads, and notifications
  • /scripts—downloads malicious code to inject into web pages

How to stay safe

Scammers are increasingly using AI-themed tools to make fake websites look legitimate. In this case, a supposed “AI trading assistant” was used to trick people into installing malware.

To reduce your risk:

  • Download software only from official websites. If a tool claims to work with a well-known platform, check the platform’s official site to confirm it’s real.
  • Check who created the file before running it. Look at the publisher name and avoid anything that looks unfamiliar or inconsistent.
  • Review your browser extensions regularly. Remove anything you don’t recognize, especially extensions you didn’t knowingly install.

What to do if you think you’ve been affected

If you think you may have downloaded this infostealer:

  • Check EDR and firewall logs for communications with the C2s listed in the IOCs part.
  • From a different, clean device, sign out of every active session on your important accounts: Google, Microsoft 365, any banking portal, GitHub, Discord, Telegram, Steam, and your crypto exchange. Change all passwords and enable 2FA for accounts you have accessed from this machine.
  • Check the folder %LOCALAPPDATA%\Packages\Extensions and suspicious browser extensions.
  • If you have cryptocurrency wallets on the machine, move the funds from a clean device immediately. This is what these operators monetize first.
  • Run a full scan with Malwarebytes.

Indicators of Compromise (IOCs)

HASH

95dcac62fc15e99d112d812f7687292e34de0e8e0a39e4f12082f726fa1b50ed

0d10a6472facabf7d7a8cfd2492fc990b890754c3d90888ef9fe5b2d2cca41c0

Domains

Tradingclaw[.]pro: fake website

Chrocustumapp[.]com: related to malicious extension

Chrocustomreversal[.]com: related to malicious extension

google-services[.]cc: related to malicious extension

Coretest[.]digital: C2 panel

Reisen[.]work: C2 panel

IPs

178[.]16[.]55[.]234: C2 panel

185[.]11[.]61[.]149: C2 panel

37[.]221[.]66[.]27: C2 panel

2[.]56[.]179[.]16: C2 panel

178[.]16[.]54[.]109: C2 panel

37[.]221[.]66[.]27: C2 panel

209[.]17[.]118[.]17: C2 panel

162[.]216[.]5[.]130: C2 panel


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

DEW #153 - New IPv8 Draft, macOS Threat Detection LLM Evals & Canaries in your CI/CD Pipeline

22 April 2026 at 14:04

Welcome to Issue #153 of Detection Engineering Weekly!

Every week, I read, watch and listen to all the Detection Engineering content so you can consume it all in 10 minutes. Subscribe and get a weekly digest of the latest and greatest in threat detection engineering!

✍️ Musings from the life of Zack:

  • I’m spending time in the Caribbean this week with my family and wish I could write this newsletter everyday with nice weather and an ocean nearby. Luckily New England does have the Atlantic, but it’s not the same for two reasons. First, the fruit is so much tastier down here. Lastly, I can’t find an Oscar the Grouch with dance moves quite like this Oscar :D

    100% of my fav character on Sesame Street.
  • I’m hosting a webinar with Allie Mellen from Forrester on April 30th where we’ll be diving deep on security operations and how AI is working and not working for all of us. We’ve had awesome discussions around this in the past. Feel free to register and come roast me in the chat

    Register & Roast Zack

Sponsor: Push Security

Register for a brand new research-focused webinar series from Push Security

The browser is the place where modern breaches happen, powered by a huge amount of attacker innovation — countless ClickFix variants, new malvertised phishing campaigns, and device code phishing attacks being powered by brand new PhaaS kits and AI tools. And we’re only in April.

Join Push Security threat researchers, along with incredible guests like John Hammond, Troy Hunt, and Matt Johansen, in a brand new webinar series deep-diving into the State of Browser Attacks.

Register Now


💎 Detection Engineering Gem 💎

Internet Protocol Version 8 (IPv8) by Jamie Thain

Ok, here’s a confession, but it’s more of a brag than something to be embarrassed about. When I went to college, I studied networking and network security extensively, as the 2008-2012 era had a strong focus on it. A lot of what my classes entailed was setting up large VM farms and networking devices on server racks. I lucked out because I got really good at networking, and part of that involved studying RFCs. I love RFCs. My favorite RFC is 1034, DNS, the coolest protocol in the modern Internet.

My co-worker sent out a link this week amid the Opus-4.7 news about the IETF skipping odd-numbered Internet Protocol RFCs and moving directly to IPv8. This specific proposal (not yet accepted) attempts to address the fragmentation of IPv4 & IPV6 networks around IP address assignment, DNS, NTP, telemetry, authentication, route validation, and access controls.

Jamie Thain, the proposal’s author, suggests that these fragmented services can be reconciled through a singular concept called a Zone Server. This Zone Server assigns DHCP leases that contain network information for everything I listed above. As Thain puts it:

A device connecting to an IPv8 network sends one DHCP8 Discover and receives one response containing every service endpoint it requires. No subsequent manual configuration is needed for any service. The device is fully operational -- authenticated, logged, time-synchronised, zone-policy-enforced -- before its first user interaction.

The most interesting part of this proposal, IMHO, is the authorization model. Every manageable element in an IPv8 network is authorized via OAuth2 JWT tokens. Like what Thain said in the quote, when a new device joins, it sends a single DHCP8 Discover and receives a lease containing the device’s configuration, including a JWT. The “OAuth2 Authority” can be hosted on a home router or on an external IdP such as Google Workspace, Okta, or Azure AD. The Zone Server stores the public keys for these authorizations, so local devices can verify token validity with the Zone Server before interaction. It reminds me a lot of Tailscale, but unlike Tailnets, rogue devices can still join your network; you just need to make sure peer devices validate tokens before they talk to it.

The second most interesting thing is DNS. Every outbound connection must have a valid DNS8 lookup before it traverses the broadcast domain; otherwise, it is automatically blocked. This helps protect against malware infections calling back to a C2 server.

Claude is amazing for visuals on complicated subjects if you like to learn that way!

As Claude pointed out, this authorization layer exists at a higher layer in the OSI stack. Attacks can still occur on lower layers. Putting my networking nerddom aside, it’s refreshing seeing how Internet-scale engineers are thinking about solving issues around security and having solutions being a feature of the protocol itself. This prevents service fragmentation, poor visibility, and the need to stitch together different security layers and hope they work.


🔬 State of the Art

This was a fun episode of Discarded where the hosts interviewed their coworker, Stuart Del Caliz, who’s a threat detection engineer at Proofpoint. When I think of writing rules and detections, my mind usually drifts towards researching and deploying log-based detections in a SIEM. Del Caliz, on the other hand, focuses on Suricata & YARA rules for malware using appliance products via the Emerging Threats Ruleset. The team has a robust malware sandbox that enables Del Caliz and the detection team to identify patterns in C2 traffic and binaries and to generate alerting and blocking mechanisms for customers.

Luckily, the Emerging Threats Ruleset is available for download, so you can set up your own Suricata lab to test it out.


macOS Threat Investigation Benchmark by Cotool Research

Friends of the newsletter Cotool published their latest research benchmark on the efficacy of the latest foundational model around macOS investigations. What makes this interesting is that, unlike CTF events, which have a clear incremental path to success, this benchmark uses logs and telemetry from an Odyssey stealer infection. The agents were given access to 14 log sources across hundreds of thousands of events and had question harnesses across 36 tasks in incident response, threat hunting, and detection engineering.

GPT-* models performed very well across Accuracy, Speed, and Reliability, and were middle-of-the-pack in cost. I think the most interesting finding here is that Cotool rewarded models based on task difficulty. For example, Incident Response was the hardest and most expensive among the tracks, and GPT-5.4 and 5.3 Codex had the best combination of accuracy and cost efficiency. Opus 4.6 had the same accuracy but cost nearly double that of GPT-5.4


Detecting CI/CD Supply Chain Attacks with Canary Credentials by Alessandro Brucato

The Tracebit team just released a clever canary detection mechanism for supply-chain attacks against GitHub Actions, similar to what we saw with the TeamPCP campaign a few weeks ago. Security teams can pull in their community edition GitHub action, which generates per-run canary credentials, such as AWS tokens. If your security controls fail or you fail to detect an attack, you can use these tokens as a reliable alerting tool that points to the repo and specific GitHub action.

They have a community edition, which is always great to see, because you can sign up and try it without all the vendor marketing gates and FUD that is commonly shoved down security people’s throats :).


Codex Security by OpenAI

The foundational labs are leaning more and more into cybersecurity use cases. With Mythos’ release last week, OpenAI released a Codex Security preview that allows vetted cybersecurity professionals to use an advanced version of Codex to scan their repositories for vulnerabilities. The “vetted” part of this announcement is interesting because Mythos was heavily gated in their announcement, whereas OpenAI has made it easier for folks to apply and get access if they meet certain verification criteria.


Sponsor: Spectrum Security

Stop the Grind and Kill the Detection Backlog with Spectrum

You know the grind: Research the gap. Understand the environment. Write the logic. Tune it. Deploy it. Watch it break when something upstream changes. Repeat. Backlog never shrinks.

Spectrum is now available. One platform that continuously maps your coverage, authors deployment-ready detections tailored to your stack, and keeps them resilient, so your expertise drives strategy, not maintenance.

See It In Action


☣️ Threat Landscape

Two U.S. Nationals Sentenced for Facilitating Fraudulent Remote Information Technology Worker Scheme that Generated $5M in Revenue for the Democratic People’s Republic of Korea by U.S. Department of Justice

Why is it always someone from New Jersey?

Kidding, unless you are a Jets fan. The DoJ released a sentence announcement for two U.S. nationals who became facilitators for Wagemole over several years. According to the announcement, they helped generate over $5 million USD of revenue for DPRK, stole identities of close to 100 U.S. persons, and worked at 100s of U.S. companies.

I post a lot about the DPRK in this newsletter because it hits so close to home, given that I work in tech. I also post a lot about DPRK in this newsletter because I have to follow up with these Wagemole stories by watching this Key & Peele sketch:


Every week, I read, watch and listen to all the Detection Engineering content so you can consume it all in 10 minutes. Subscribe and get a weekly digest of the latest and greatest in threat detection engineering!

NIST Updates NVD Operations to Address Record CVE Growth by NIST

NIST released updated guidelines on how they will perform CVE enrichment moving forward. They’ve had nearly two years of turmoil trying to keep up with enriching CVEs for their National Vulnerability Database. I think this failure to enrich every CVE is due to two things: funding shortages and AI. I’ve linked a ton of stories here from open-source maintainers like Daniel Stenberg, saying that AI is creating too much vulnerability research slop. But I do believe recent CVEs have been at least AI-assisted, which helps increase velocity.

In their announcement, NIST says it will prioritize CVEs into three categories: CISA KEV entries, vulnerabilities in software used by the federal government, and CVEs for Critical Software, as detailed in an executive order from 2021.

There are other playbook changes regarding severity scores and modified CVEs, but IMHO, the significant reduction in CVE enrichment is the big news here. I hope we can find a way, as a community, to fund efforts to enrich CVEs in lieu of the NVD.


MCP Supply Chain Advisory: RCE Vulnerabilities Across the AI Ecosystem by Moshe Siman Tov Bustan, Mustafa Naamnih & Nir Zadok

The Ox Security Research Team found four attack surfaces in Anthropic’s MCP Protocol implementation. These attack surfaces led the research team to disclose vulnerabilities to dozens of open-source repositories and get to 10 CVEs and counting. The way it works is how this software sets up MCP servers and what they allow as input into their configurations. The command injection is via exposed tools that can add an MCP configuration. When you add an stdio transport, you can specify an arbitrary bash command that allows remote code execution.

The team disclosed this vulnerability to Anthropic but the protocol specifically allows this option and is by design. The problem here is when users of these MCP-enabled projects don’t know about the insecure configuration and deploy it to the Internet allowing the remote code execution. There are situations where this RCE can be unauthenticated or authenticated, but for the most part, it points out that anytime you allow arbitrary configurations to be uploaded by users, you risk exposing yourselves to attacks like this.


Understanding security warnings when opening Remote Desktop (RDP) files by Microsoft

Microsoft finally released security updates to help warn users of malicious RDP files before they become victims of an infection or social engineering attack. Attackers leverage RDP files to initiate remote connections to victim computers, often using them to steal files, take pictures or steal contents of your clipboard. Now, users of the latest security update will get warnings when double-clicking on these files, hopefully preventing some of these infections from happening.

With the advent of ClickFix, my hopes aren’t too high, but sometimes security is about incremental steps versus massive swings.


🔗 Open Source

google/magika

Magika is file on steroids. It uses a deep-learning model under the hood that helps classify files with what they claim is 99% accuracy. It was trained on 100 million+ samples and 200+ content types. The cool part here is that this is the model and tool used by Google to help detect filetypes on Gmail, Drive and Safe Browsing. I imagine they can use this to route files based on their content types to different internal security services for scanning.


mukul975/cve-mcp-server

Locally ran MCP server that helps researchers and defenders connect to 27 (!) security tools for CVE lookup and enrichment. Unfortunately you won’t get much data anymore from NVD, but it has some great integrations with ATT&CK, internet scanners and even VirusTotal.


Hainrixz/cyber-neo

Cyber Neo is a Vulnerability research plugin for Claude Code. It has 11 security domains it tries to scan for, and each domain has toolsets and markdown instructions for Claude to execute to render findings.


tahaafarooq/Fenrir

GoLang credential and secrets harvesting tool that uses eBPF to skim credentials off from syscall events. It’s like a Linux rootkit that only cares about secrets. It has some interesting capabilities, such as memory-only execution and anti-detection capabilities. It tries to intercept secrets across SSH, PAM, the command line and does some file-based discovery for things like API keys and cloud secrets.


jsmonhq/xnew

xnew is a low-footprint and fast file appender. It is contextually aware of every line inside the file, and it will only append unique lines not already present. This has always been a pain for me everytime I’ve had to cat x | uniq | sort | uniq , which can sometimes take forever when the file is super large.

Researcher claims Claude Desktop installs “spyware” on macOS

22 April 2026 at 13:53

Security researcher Alexander Hanff wrote an article titled Anthropic secretly installs spyware when you install Claude Desktop.

Claims like that are bound to create two sides, so we searched for an official rebuttal by Anthropic. But we couldn’t find one. It would surprise me very much if they’d be unaware of the claim, since there’s been some noise about it.

Users on Mastodon, Reddit, and LinkedIn are confirming the researcher’s findings and discussing the subject, so it’s hard to imagine Anthropic missed it.

Let’s look at the claims first.

While looking into another matter, the researcher discovered a Native Messaging host manifest on his Mac that he did not knowingly install. On Chrome and other Chromium-based browsers, extensions can exchange messages with native applications if they register a native messaging host that can communicate with the extension. 

By testing on a clean machine, Hanff discovered that Installing Claude Desktop for macOS drops a Native Messaging host manifest into multiple Chromium profiles (Chrome, Edge, Brave, Arc, Vivaldi, Opera, Chromium), even including for browsers that are not actually installed yet.

The Native Messaging host manifest tells a Chromium‑based browser which local executable to invoke when an extension calls a native host, and those hosts run outside the browser sandbox with current users  permissions. Hanff therefore describes this as a “backdoor.” The manifest pre‑authorizes three Chrome extension IDs, so any extension with those IDs can call the helper via connectNative, giving it access to browser automation features.

Another objection is that Claude makes simple deletion futile since the manifest will be recreated the next time the user launches Claude Desktop.

It’s important here to point out that his article is about Claude Desktop, the Electron-based macOS application with bundle identifier com.anthropic.claudefordesktop, distributed as Claude.app. It is not about Claude Code, Anthropic’s command line developer tool. Claude Code is autonomous (“agentic”), allowing you to hand over a task, and it handles the planning and execution until done. So, for Claude Code, it would absolutely make sense to enable communication with browsers, provided they are present on the target system.

So, we have an application that writes into other apps’ profile/support directories (the browsers’ configuration area) and can act as the user, with capabilities like using the logged‑in browser session, DOM inspection, data extraction, form filling, and session recording. This expands the attack surface of every machine this manifest is dropped on, without asking for consent. 

Anthropic’s own launch blog on “Claude for Chrome,” which discusses Anthropic’s internal red‑team experiments, explicitly mentions prompt injection as a key risk and reports attack success rates of 23.6% (no mitigations) and 11.2% (with mitigations). Hanff cites this to argue that a pre‑positioned bridge is a non‑trivial risk.

How bad is it?

Native Messaging is a standard Chromium mechanism. Nothing here is an unknown or exotic technique per se. Chrome’s own documentation explains that Native Messaging hosts run at user privilege and are invoked by browser extensions through a manifest file. And as the researcher pointed out, the bridge does nothing. But it could potentially be abused.

I don’t think it’s fair to say that Claude Desktop installs spyware, but it does open a system up by expanding the attack surface.

Anthropic already had a separate, documented Native Messaging manifest for Claude Code that users sometimes manually copied into other Chromium browsers; the new behavior is that Claude Desktop now drops a Claude‑Desktop‑related manifest into multiple browser paths automatically.

It requires a combination of extension and host. Only combined with a matching browser extension, this bridge enables the user-like capabilities we listed earlier.

What we don’t know yet

Anthropic hasn’t published a detailed technical privacy spec for the Claude Desktop–browser bridge, so we don’t know exactly what data flows when the Chrome integration is used, beyond the general capabilities described in their documentation (session access, DOM reading, etc.).

The detailed analysis and most replication so far are on macOS. We’re in the dark about behavior on Windows and Linux, and the same is true across different browser install paths. That behavior has also not been comprehensively documented in public write‑ups.

I did reach out to Anthropic asking for a response. If and when we get an official response from Anthropic, I’ll add it here, so stay tuned.

Conclusion

Anthropic likely wanted “Claude in Chrome”‑style capabilities across Chromium‑based browsers, but that doesn’t excuse doing it silently and preinstalling the manifest into profile directories for multiple browsers, including ones that are not yet installed.

There are better ways to implement changes like these, and users should at least be made aware of them so they can weigh the advantages against the potential risks.


Stop threats before they can do any harm.

Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →

❌