❌

Normal view

Data Broker Radaris Loses Domains in Privacy Fight

16 September 2026 at 20:14

The consumer data broker Radaris.com has long had a reputation for ignoring requests to remove personal information from its vast empire of people-search services online. That reputation caught up with the company recently in a lawsuit alleging Radaris violated a New Jersey privacy law that provides for hefty fines against data brokers that publish personal information on state law enforcement officials. In the face of repeated stonewalling and prevarication by attorneys for Radaris, the judge in the case ordered that radaris.com and more than a dozen other data broker domains be transferred to the plaintiffs.

The radaris.com website, prior to the domain transfer to Atlas.

In February 2024, Radaris was sued by Atlas Data Privacy Corp, a company that has been pursuing data brokers alleged to be violating a New Jersey statute called Daniel’s Law. The statute allows state law enforcement officials, government personnel, judges and their families to have their information completely removed from commercial data brokers and people-search services, and provides for fines of $1,000 per violation against companies that ignore removal requests.

Less than a month after Atlas sued Radaris, KrebsOnSecurity published a deep dive into the Radaris co-founders — Igor and Dmitry Lubarsky (also spelled Lybarsky) — Russian-born brothers living in Massachusetts who operate a dizzying array of people-search companies as well as a number of Russian language dating services and affiliate programs.

Attorneys for the Lubarsky brothers threatened to sue for defamation if the story wasn’t removed and an apology issued. Their attorney asserted that our reporting was wildly inaccurate, and that the true owners of the company were Ukrainians living in Ukraine.

The Lubarsky brothers Dmitry or “Dan” (left) and Gary/Igor.

KrebsOnSecurity doubled down and showed how the Lubarsky brothers built and operated Radaris and other data broker companies using a fictitious CEO’s name. Our follow-up story noted that Radaris’s attorney — a lawyer with the Boston Law Group named Val Gurvits — admitted his clients had invented the CEO pseudonym “Gary Norden,” and that Radaris also had issued multiple press releases over the years that quoted the fake CEO while seeking money from potential investors.

Attorneys for Radaris waited until the last minute to appear in court and contest what was all but certain to be a default judgment in favor of the plaintiffs, and then told the court that Atlas had failed to serve the real owners and operators of Radaris and several of its sister data broker companies.

Atlas re-filed the lawsuit in June 2025, this time dramatically expanding the number of Radaris family data brokers accused of violating Daniel’s Law. Matt Adkisson, president and CEO of Atlas, said Radaris turned to a tried-and-true playbook: Delaying in court until the last possible minute, and playing shell games with Radaris’s true country of origin and the individuals listed as owners and operators of these sites.

“We refer to this period as their island-hopping phase. Privacy policies changed constantly, and new entities kept appearing from places like the Marshall Islands, the British Virgin Islands, and Seychelles,” Adkisson told KrebsOnSecurity. “Behind the scenes, it felt like a shell game. Defense lawyers told the court that certain entities merely operated the domains and were the proper parties to sue. But by the time a judgment neared, those entities would be discarded and new entities would appear. Meanwhile, the lawyers claimed the other entities that actually owned the domains should not be held responsible.”

Adkisson said when the defendants updated their terms of service to state that Radaris was suddenly managed by a company in the Marshall Islands, Atlas hired an investigator in that country and soon learned the brand new entity that Radaris claimed was managing the company didn’t even exist yet.

Mr. Gurvits stepped forward as Radaris’s attorney in a class action lawsuit the company temporarily lost in 2017 because it never contested the claim in court. When the plaintiffs told the judge they couldn’t collect on the $7.5 million default judgment, the court ordered the domain registry Verisign to transfer the radaris.com domain name to the plaintiffs.

Mr. Gurvits appealed that verdict, arguing the lawsuit hadn’t named the actual owners of the Radaris domain name — a Cyprus company called Bitseller Expert Limited — and thus taking the domain away would be a violation of their due process rights.

The judge in the 2017 case ruled in Radaris’ favor — halting the domain transfer — and told the plaintiffs they could refile their complaint. Soon after, the operator of Radaris changed from Bitseller to Andtop Company, an entity formed (PDF) in the Marshall Islands in Oct. 2020. The plaintiffs never re-filed their lawsuit.
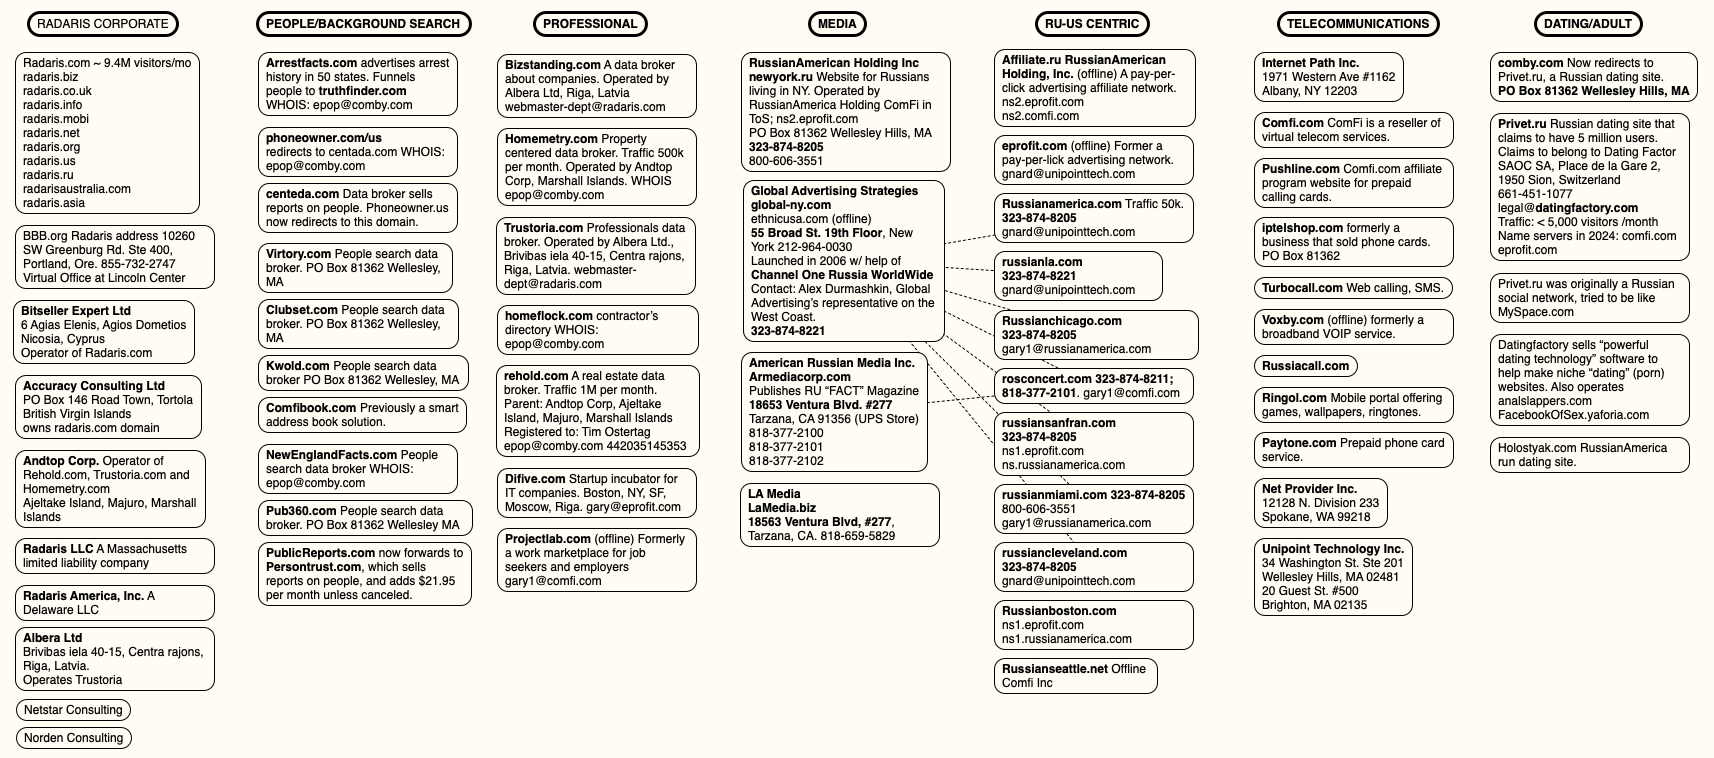
A mind map of various entities tied to Radaris and the company’s co-founders. Click to enlarge.

“That seemed to be their modus operandi,” said Raj Parikh, a partner at PEM Law in New Jersey who handles most of the Daniel’s Law litigation for Atlas. “In the past, they won by attrition. Plaintiffs’ attorneys tired of the procedural games and just gave up. That strategy worked for a decade, and it probably would have worked in this case too, since any financial recovery from foreign actors will be difficult. But we were acutely aware of the threat this website posed to law enforcement officers and other public officials in New Jersey, and decided early on to commit whatever time and resources were necessary to remove that threat.”

On August 26, the judge in the New Jersey case found the defendants were given multiple chances to appear and defend the claims against them but had failed to do so. Mr. Gurvits declined to comment on the case, saying it had been assigned to another attorney, a Mr. Victor Worms. In response to questions, Mr. Worms asserted the New Jersey court transferred Radaris.com to Atlas as part of a default judgment against Radaris.com, which is not a legal entity.

“We have made a motion to vacate that default judgment on the grounds that it is void since a non-entity has no legal capacity to sue or be sued,” Worms replied. “We also intend to pursue all appropriate appeals because we believe the transfer of Radaris.com amounts to a forfeiture in violation of various constitutional principles.”

While radaris.com still comes up prominently in results when searching online for U.S. residents by name, the domain no longer sells detailed personal dossiers on millions of Americans. Its homepage now displays a notice from Atlas, as well as links to our previous reporting on Radaris.

EMAIL CONFIRMATIONS

Atlas told KrebsOnSecurity that it has obtained more than 10,000 emails and documents in the course of litigation, and that those messages confirm our previous reporting on the owners and operators of Radaris and its myriad companies.

Atlas said the emails clearly establish that the nominal legal vehicles — Radaris America, Inc.; Bitseller Expert Limited; Digital Orbit Corp; Core Solutions Group Inc; Lucky Solutions Inc; Virtura Corp; Veripages Inc.; Nuform Solutions Inc.; Growth Data Advisors Inc.; Property Experts, Inc — are all administered by the same three or four people from the same mailboxes, share one bank or payment card set, and are all managed from one virtual office address.

“The corpus establishes, with documentary evidence generated independently by banks, payment processors, hosting providers, registrars, software-as-a-service vendors and the operators’ own systems, that radaris.com and at least twenty-five other people-search websites are one operation run by a small Boston-area group whose administrative, financial and technical functions sit on the difive.com mail domain and its successors (centerex.com, scienteco.com, eprofit.com, realmo.com, pub360.com),” reads a summary shared by Atlas.

Atlas said the emails show Radaris.com earns approximately $42,000 a month, while Veripages.com earns around $45,000 monthly via its partnership with the Lifetime Value Company, a marketing and advertising firm whose brands include PeopleLooker, PeopleSmart, NumberGuru, and Bumper, a car history site.

According to Atlas, the emails also showed the Radaris family of websites earns as much as $25,000 each month from their partnership with Onerep, a company that claims to help people remove their information from people-search sites. In March 2024, KrebsOnSecurity revealed how the Belarusian founder of Onerep had launched and operated dozens of people-search sites over the years and was continuing to operate one of them (Nuwber), effectively spreading the disease and selling the cure.

The domain radaris.com now redirects to this notice from Atlas about the court-ordered domain transfer.

The domain radaris.com now redirects to this notice from Atlas about the court-ordered domain transfer.

All told, the New Jersey court has so far transferred 14 domain names from the Radaris family of companies to Atlas. Radaris.com now redirects to a notice of the court-ordered domain transfer.

THE ROAD AHEAD

The Radaris family of companies is still potentially facing fines of $1,000 per alleged violation of Daniel’s Law. For the time being, however, Daniel’s Law is facing a constitutional challenge from virtually all of the 150 other consumer data broker firms being sued by Atlas.

The data broker industry responded by having at least 70 of the Atlas lawsuits moved to federal court, challenging the New Jersey statute as overly broad and a violation of the First Amendment. The U.S. Court of Appeals for the Third Circuit has not yet issued a decision on the constitutional challenge, but either way the case is widely expected to be appealed all the way to the U.S. Supreme Court.

Meanwhile, at least 14 other states have now passed laws modeled after the New Jersey statute, with more states considering similar measures. However, West Virginia’s Daniel’s Law was ruled facially unconstitutional under the First Amendment by a federal district court in August 2025.

Justin Sherman is a privacy expert and author of the forthcoming book “The Middlemen,” which examines how the data broker industry powers modern surveillance. Sherman said federal lawmakers have long faced intense lobbying by the technology industry against more restrictive U.S. data privacy laws, but that many powerful industries are now working against passing comprehensive data privacy legislation.

“These days at the federal level, add in the intense amount of lobbying against these laws from social media companies, big tech, cryptocurrency firms, and now AI proponents in the mix who claim that limiting their data scraping is somehow going to collapse the whole U.S. economy under Chinese rule,” he said.

Sherman said people-search companies will continue to thrive unless and until Congress enacts meaningful consumer privacy and data protection laws that are relevant to life in the 21st century. That’s because virtually all state privacy laws exempt records that might be considered “public” or “government” documents, including voting registries, property filings, marriage certificates, motor vehicle records, criminal records, court documents, death records, professional licenses, bankruptcy filings, and more.

At least 25 states have passed or implemented laws requiring age verification for residents seeking to access adult content online, but there is no federal law that limits how the companies that are scanning everyone’s drivers license can use, share or keep the data provided. Had such restrictions been enshrined in law, we may have avoided the recent breach at IDScan.net, which exposed the drivers license information on more than 153 million Americans when the records were briefly turned into a point-and-click identity theft service on the dark web.

“The average person can look at Daniel’s Law and have a perfectly normal reaction, which is that everyone should be covered, not just police and judges,” Sherman said. “But we don’t need more wake-up calls. We’ve had eight million wake-up calls already on the need for better privacy laws. The lack of comprehensive federal privacy law is not for a lack of knowledge, and anyone claiming otherwise is either not reading the news or kidding themselves.”
Don’t get fooled by TikTok resin art scams

24 July 2026 at 16:56

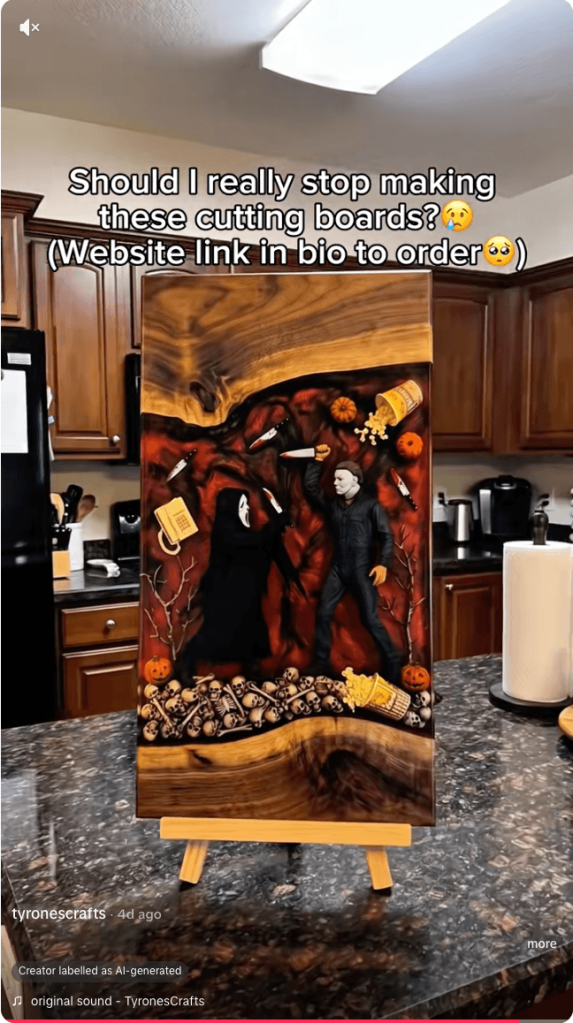
Resin art has become a popular corner of TikTok, with some videos attracting millions of views. But not every glossy, colorful post is what it claims to be. Scammers are using the look of handmade resin art to trick buyers, collectors, and even fellow artists into sending money for work that either doesn’t exist or wasn’t created by the person posting it.

There are plenty of genuine resin artists on TikTok. Unfortunately, the platform has also attracted scammers who steal videos and impersonate legitimate creators.

  • Fake resin art
  • Fake resin art
  • Fake resin art
  • Fake resin art
  • Fake resin art
  • Fake resin art

The scam is fairly straightforward. A TikTok account presents itself as a resin artist, posts satisfying videos, and invites people to “DM to order.” In some cases, the videos are stolen from other creators, the account has no real process footage, and the seller disappears after receiving payment.

One resin artist discovered that scammers were using their videos to impersonate them and scam TikTok users. They shared the following comment:

Ridiculous TikTok scammer…lol. Profile says they’re a resin artist and to DM them to order, but none of the videos are theirs. When I wrote to them asking them to take down the many videos of mine that they posted, passing them off as their own with no credit, their answer was that they aren’t a resin artist and are just sharing videos they like 🤣🤣 Literally about 1/4 of “their” videos are mine 🙄

These scams often rely on trust and urgency. The account may show polished clips of poured resin, finished coasters, trays, jewelry, or wall art, then push buyers to move the conversation into direct messages. Once the buyer moves to a different platform, the scammer typically requests a deposit, full payment, or personal details with little chance of being held accountable.

And real artists don’t just get their work ripped off. A scammer may contact a creator claiming to want to buy, feature, or license their work, but the real goal is to extract fees, banking information, or other sensitive data. Social media art scams are often repetitive because they are built from the same templates and scripts.

Script is similar across many videos in resin art scams
Different videos, same script

How to spot a TikTok resin art scam

The safest approach is the boring one: verify before you pay. If the artwork looks amazing but the seller’s identity is vague, the risk is real.

Check the TikTok account

Before ordering, look for signs that the artist is genuine:

  • The account didn’t appear overnight and has a history of original posts.
  • The same videos don’t appear under multiple creator names or belong to another artist.
  • The creator shows themselves making the artwork, with consistent process videos, a recognizable workspace, and works in progress.
  • The videos don’t contain obvious AI artifacts, such as impossible resin effects or objects moving after they’ve supposedly been sealed inside hardened resin.
  • Comments raising concerns haven’t been deleted or buried under generic praise.
  • The seller isn’t pushing you to order only through direct messages or asking for payment before you’ve verified who they are.

Check the website

If you do click through to a website, spend a few minutes checking it before you buy:

  • Look for a genuine returns and refunds policy, a physical business address, company or VAT details (where applicable), and consistent contact information.
  • Check how old the website is. Scam sites often use domains that were registered only weeks or months ago, especially when they claim to have been selling handmade products for years.
  • Search for recent independent reviews rather than relying on testimonials published on the site itself.
  • Run a reverse image search on the product photos to see whether they’ve been copied from another artist.
  • Only pay using a method that offers buyer protection, such as a credit card or PayPal. If a seller insists on a bank transfer, cryptocurrency, or another irreversible payment method, walk away.

Not every resin art account is a scam. Many belong to genuine artists, and that’s why impersonation scams can be so convincing.

If you’re unsure, paste the website address into Malwarebytes Scam Guard and ask whether it shows signs of being fraudulent. It can help identify suspiciously new domains and other common scam indicators.

Use Malwarebytes Scam Guard to check whether a social media post or website is part of a scam.

Use real-time web protection to block known fraudulent and malicious websites, like Browser Guard did for this web shop:

Browser Guard blocks the web shop due to likely fraud
Browser Guard blocks the fraudulent website

Both are free—making them much cheaper than sending money to a scammer.


Something feel off? Check it before you click.  

Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.  

Available with Malwarebytes Premium Security for all your devices, and in the Malwarebytes app for iOS and Android.  

Try it free → 

Don’t get fooled by TikTok resin art scams

24 July 2026 at 16:56

Resin art has become a popular corner of TikTok, with some videos attracting millions of views. But not every glossy, colorful post is what it claims to be. Scammers are using the look of handmade resin art to trick buyers, collectors, and even fellow artists into sending money for work that either doesn’t exist or wasn’t created by the person posting it.

There are plenty of genuine resin artists on TikTok. Unfortunately, the platform has also attracted scammers who steal videos and impersonate legitimate creators.

  • Fake resin art
  • Fake resin art
  • Fake resin art
  • Fake resin art
  • Fake resin art
  • Fake resin art

The scam is fairly straightforward. A TikTok account presents itself as a resin artist, posts satisfying videos, and invites people to “DM to order.” In some cases, the videos are stolen from other creators, the account has no real process footage, and the seller disappears after receiving payment.

One resin artist discovered that scammers were using their videos to impersonate them and scam TikTok users. They shared the following comment:

Ridiculous TikTok scammer…lol. Profile says they’re a resin artist and to DM them to order, but none of the videos are theirs. When I wrote to them asking them to take down the many videos of mine that they posted, passing them off as their own with no credit, their answer was that they aren’t a resin artist and are just sharing videos they like 🤣🤣 Literally about 1/4 of “their” videos are mine 🙄

These scams often rely on trust and urgency. The account may show polished clips of poured resin, finished coasters, trays, jewelry, or wall art, then push buyers to move the conversation into direct messages. Once the buyer moves to a different platform, the scammer typically requests a deposit, full payment, or personal details with little chance of being held accountable.

And real artists don’t just get their work ripped off. A scammer may contact a creator claiming to want to buy, feature, or license their work, but the real goal is to extract fees, banking information, or other sensitive data. Social media art scams are often repetitive because they are built from the same templates and scripts.

Script is similar across many videos in resin art scams
Different videos, same script

How to spot a TikTok resin art scam

The safest approach is the boring one: verify before you pay. If the artwork looks amazing but the seller’s identity is vague, the risk is real.

Check the TikTok account

Before ordering, look for signs that the artist is genuine:

  • The account didn’t appear overnight and has a history of original posts.
  • The same videos don’t appear under multiple creator names or belong to another artist.
  • The creator shows themselves making the artwork, with consistent process videos, a recognizable workspace, and works in progress.
  • The videos don’t contain obvious AI artifacts, such as impossible resin effects or objects moving after they’ve supposedly been sealed inside hardened resin.
  • Comments raising concerns haven’t been deleted or buried under generic praise.
  • The seller isn’t pushing you to order only through direct messages or asking for payment before you’ve verified who they are.

Check the website

If you do click through to a website, spend a few minutes checking it before you buy:

  • Look for a genuine returns and refunds policy, a physical business address, company or VAT details (where applicable), and consistent contact information.
  • Check how old the website is. Scam sites often use domains that were registered only weeks or months ago, especially when they claim to have been selling handmade products for years.
  • Search for recent independent reviews rather than relying on testimonials published on the site itself.
  • Run a reverse image search on the product photos to see whether they’ve been copied from another artist.
  • Only pay using a method that offers buyer protection, such as a credit card or PayPal. If a seller insists on a bank transfer, cryptocurrency, or another irreversible payment method, walk away.

Not every resin art account is a scam. Many belong to genuine artists, and that’s why impersonation scams can be so convincing.

If you’re unsure, paste the website address into Malwarebytes Scam Guard and ask whether it shows signs of being fraudulent. It can help identify suspiciously new domains and other common scam indicators.

Use Malwarebytes Scam Guard to check whether a social media post or website is part of a scam.

Use real-time web protection to block known fraudulent and malicious websites, like Browser Guard did for this web shop:

Browser Guard blocks the web shop due to likely fraud
Browser Guard blocks the fraudulent website

Both are free—making them much cheaper than sending money to a scammer.


Something feel off? Check it before you click.  

Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.  

Available with Malwarebytes Premium Security for all your devices, and in the Malwarebytes app for iOS and Android.  

Try it free → 

This is all it takes to stop a train (Lock and Code S07E06)

22 March 2026 at 23:02

This week on the Lock and Code podcast…

Forget the runaway train thrillingly shot in Buster Keaton’s 1926 film “The General,” and never mind the charging locomotive rescued by actors Denzel Washington and Chris Pine in the 2010 film “Unstoppable,” as there’s a far more frequent (and far less heart-pounding) railcar drama happening across California’s Bay Area: The repeated breakdown of the Bay Area Rapid Transit (BART) system, all because of a few networking errors.

Opened in 1972, BART today carries about 175,000 people every weekday on five separate lines to 50 different stations placed across dozens of cities in the Bay Area, including San Francisco, Oakland, Berkeley, Daly City, Fremont, Richmond, and more. Its tracks and railcars travel both above ground and below, and it is one of the only public transit systems in the US that goes underwater—traveling through what is called the TransBay tube. It is likely the region’s largest public project, spanning 131 miles of track, with a fleet of more than 700 cars, proving vital to workers and residents everywhere, and on May 9, 2025, it all came grinding to a halt, due to what BART officials called a “computer networking problem.”

At the Glen Park station in San Francisco, would-be travelers found yellow caution tape at the entry gates. At the El Cerrito Plaza station, BART staff and police informed visitors that the system was down. And at the Rockridge station in Oakland, a reporter for The San Francisco Chronicle witnessed a small group of people sprinting up the stairs to try and catch a train that never came.

It was the kind of meltdown for public infrastructure that puts an entire system in peril.

And it happened again just months later.

In September, a network crash brought BART to a halt, repeating almost the exact same frustrations and delays for travelers left without transportation to work.

That’s the end of it, right? Wrong. In February 2026, another computer failure caused another outage.

So, in one of the wealthiest regions in America, the subway doesn’t always run, its network is prone to crash, and any money for technology often goes elsewhere. 

Today, on the Lock and Code podcast with host David Ruiz, we speak with San Francisco Chronicle transportation report Rachel Swan about what the BART outages revealed about the state of the system’s aging technology, why public infrastructure so often struggles to modernize, and what exactly went wrong in the three prior outages.

“One piece of equipment—and again, this is old equipment—one piece breaks down and they completely lose visibility, so they don’t know where any of the trains are.”

Tune in today to listen to the full conversation.

Show notes and credits:

Intro Music: “Spellbound” by Kevin MacLeod (incompetech.com)
Licensed under Creative Commons: By Attribution 4.0 License
http://creativecommons.org/licenses/by/4.0/
Outro Music: “Good God” by Wowa (unminus.com)


Listen up—Malwarebytes doesn’t just talk cybersecurity, we provide it.

Protect yourself from online attacks that threaten your identity, your files, your system, and your financial well-being with our exclusive offer for Malwarebytes Premium Security for Lock and Code listeners.

Online shoppers at risk as Magecart skimming hits major payment networks

14 January 2026 at 13:03

Researchers have been tracking a Magecart campaign that targets several major payment providers, including American Express, Diners Club, Discover, and Mastercard.

Magecart is an umbrella term for criminal groups that specialize in stealing payment data from online checkout pages using malicious JavaScript, a technique known as web skimming.

In the early days, Magecart started as a loose coalition of threat actors targeting Magento‑based web stores. Today, the name is used more broadly to describe web-skimming operations against many e‑commerce platforms. In these attacks, criminals inject JavaScript into legitimate checkout pages to capture card data and personal details as shoppers enter them.

The campaign described by the researchers has been active since early 2022. They found a vast network of domains related to a long-running credit card skimming operation with a wide reach.

“This campaign utilizes scripts targeting at least six major payment network providers: American Express, Diners Club, Discover (a subsidiary of Capital One), JCB Co., Ltd., Mastercard, and UnionPay. Enterprise organizations that are clients of these payment providers are the most likely to be impacted.”

Attackers typically plant web skimmers on e-commerce sites by exploiting vulnerabilities in supply chains, third-party scripts, or the sites themselves. This is why web shop owners need to stay vigilant by keeping systems up to date and monitoring their content management system (CMS).

Web skimmers usually hook into the checkout flow using JavaScript. They are designed to read form fields containing card numbers, expiry dates, card verification codes (CVC), and billing or shipping details, then send that data to the attackers.

To avoid detection, the JavaScript is heavily obfuscated to and may even trigger a self‑destruct routine to remove the skimmer from the page. This can cause investigations performed through an admin session to appear unsuspicious.

Besides other methods to stay hidden, the campaign uses bulletproof hosting for a stable environment. Bulletproof hosting refers to web hosting services designed to shield cybercriminals by deliberately ignoring abuse complaints, takedown requests, and law enforcement actions.

How to stay safe

Magecart campaigns affect three groups: customers, merchants, and payment providers. Because web skimmers operate inside the browser, they can bypass many traditional server‑side fraud controls.

While shoppers cannot fix compromised checkout pages themselves, they can reduce their exposure and improve their chances of spotting fraud early.

A few things you can protect against the risk of web skimmers:

  • Use virtual or single‑use cards for online purchases so any skimmed card number has a limited lifetime and spending scope.
  • Where possible, turn on transaction alerts (SMS, email, or app push) for card activity and review statements regularly to spot unsolicited charges quickly.
  • Use strong, unique passwords on bank and card portals so attackers cannot easily pivot from stolen card data to full account takeover.
  • Use a web protection solution to avoid connecting to malicious domains.

Pro tip: Malwarebytes Browser Guard is free and blocks known malicious sites and scripts.


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

Why iPhone users should update and restart their devices now

13 January 2026 at 13:55

If you were still questioning whether iOS 26+ is for you, now is the time to make that call.

Why?

On December 12, 2025, Apple patched two WebKit zero‑day vulnerabilities linked to mercenary spyware and is now effectively pushing iPhone 11 and newer users toward iOS 26+, because that’s where the fixes and new memory protections live. These vulnerabilities were primarily used in highly targeted attacks, but such campaigns are likely to expand over time.

WebKit powers the Safari browser and many other iOS applications, so it’s a big attack surface to leave exposed and isn’t limited to “risky” behavior. These vulnerabilities allowed an attacker to execute arbitrary code on a device after exploitation via malicious web content.

Apple has confirmed that attackers are already exploiting these vulnerabilities in the wild, making installation of the update a high‑priority security task for every user. Campaigns that start with diplomats, journalists, or executives often lead to tooling and exploits leaking or being repurposed, so “I’m not a target” is not a viable safety strategy.​

Due to public resistance to new features like Liquid Glass, many iPhone users have not yet upgraded to iOS 26.2. Reports suggest adoption of iOS 26 has been unusually slow. As of January 2026, only about 4.6% of active iPhones are on iOS 26.2, and roughly 16% are on any version of iOS 26, leaving the vast majority on older releases such as iOS 18.

However, Apple only ships these fixes and newer protections, such as Memory Integrity Enforcement, on iOS 26+ for supported devices. Users on older, unsupported devices won’t be able to access these protections at all.

Another important factor in the upgrade cycle is restarting the device. What many people don’t realize is that when you restart your device, any memory-resident malware is flushed—unless it has somehow gained persistence, in which case it will return. High-end spyware tools tend to avoid leaving traces needed for persistence and often rely on users not restarting their devices.

Upgrading requires a restart, which makes this a win-win: you get the latest protections, and any memory-resident malware is flushed at the same time.

For iOS and iPadOS users, you can check if you’re using the latest software version, go to Settings > General > Software Update. It’s also worth turning on Automatic Updates if you haven’t already. You can do that on the same screen.

How to stay safe

The most important fix—however painful you may find it—is to upgrade to iOS 26.2. Not doing means missing an accumulating list of security fixes, leaving your device vulnerable to more and more newly found vulnerabilities.

 But here are some other useful tips:

  • Make it a habit to restart your device on a regular basis. The NSA recommends doing this weekly.
  • Do not open unsolicited links and attachments without verifying with the trusted sender.
  • Remember, Apple threat notifications will never ask users to click links, open files, install apps or ask for account passwords or verification code.
  • For Apple Mail users specifically, these vulnerabilities create risk when viewing HTML-formatted emails containing malicious web content.
  • Malwarebytes for iOS can help keep your device secure, with Trusted Advisor alerting you when important updates are available.
  • If you are a high-value target, or you want the extra level of security, consider using Apple’s Lockdown Mode.

We don’t just report on phone security—we provide it

Cybersecurity risks should never spread beyond a headline. Keep threats off your mobile devices by downloading Malwarebytes for iOS, and Malwarebytes for Android today.

Is Your Android TV Streaming Box Part of a Botnet?

24 November 2025 at 19:44

On the surface, the Superbox media streaming devices for sale at retailers like BestBuy and Walmart may seem like a steal: They offer unlimited access to more than 2,200 pay-per-view and streaming services like Netflix, ESPN and Hulu, all for a one-time fee of around $400. But security experts warn these TV boxes require intrusive software that forces the user’s network to relay Internet traffic for others, traffic that is often tied to cybercrime activity such as advertising fraud and account takeovers.

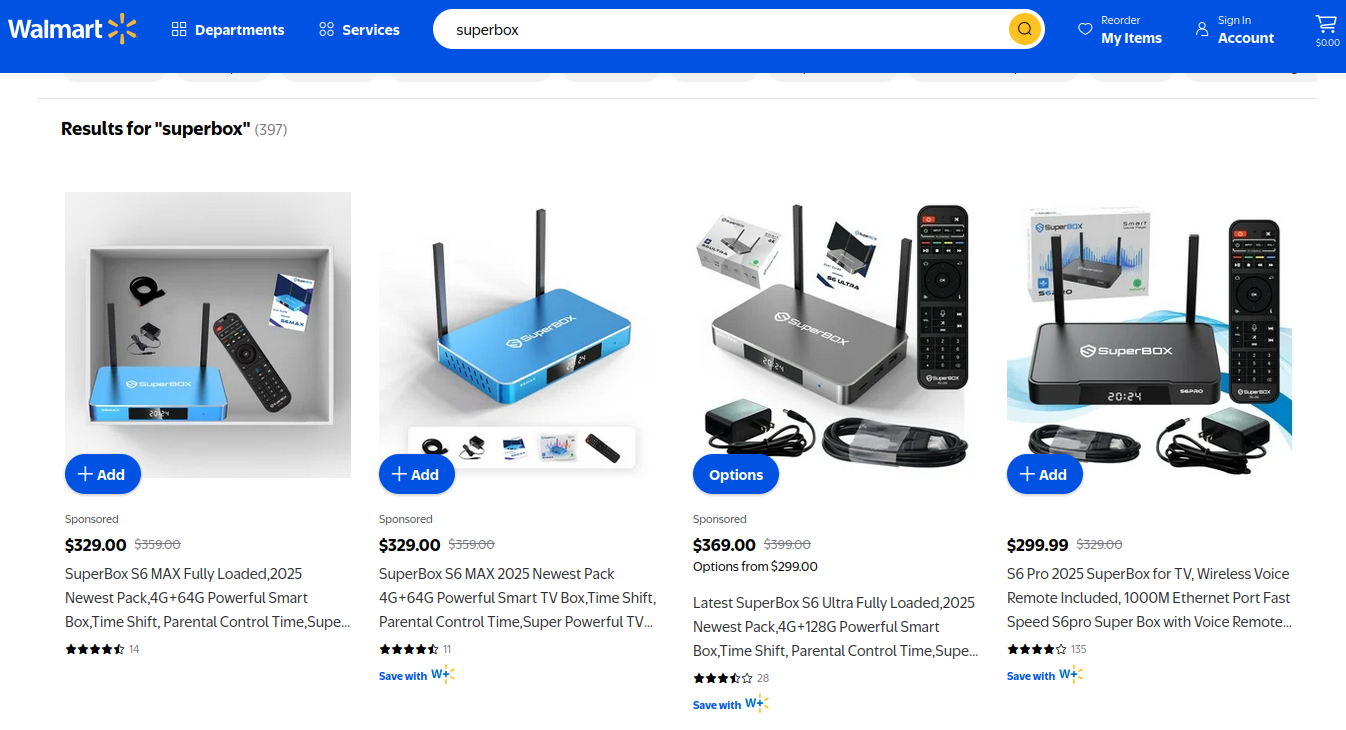
Superbox media streaming boxes for sale on Walmart.com.

Superbox bills itself as an affordable way for households to stream all of the television and movie content they could possibly want, without the hassle of monthly subscription fees — for a one-time payment of nearly $400.

“Tired of confusing cable bills and hidden fees?,” Superbox’s website asks in a recent blog post titled, “Cheap Cable TV for Low Income: Watch TV, No Monthly Bills.”

“Real cheap cable TV for low income solutions does exist,” the blog continues. “This guide breaks down the best alternatives to stop overpaying, from free over-the-air options to one-time purchase devices that eliminate monthly bills.”

Superbox claims that watching a stream of movies, TV shows, and sporting events won’t violate U.S. copyright law.

“SuperBox is just like any other Android TV box on the market, we can not control what software customers will use,” the company’s website maintains. “And you won’t encounter a law issue unless uploading, downloading, or broadcasting content to a large group.”

A blog post from the Superbox website.

There is nothing illegal about the sale or use of the Superbox itself, which can be used strictly as a way to stream content at providers where users already have a paid subscription. But that is not why people are shelling out $400 for these machines. The only way to watch those 2,200+ channels for free with a Superbox is to install several apps made for the device that enable them to stream this content.

Superbox’s homepage includes a prominent message stating the company does “not sell access to or preinstall any apps that bypass paywalls or provide access to unauthorized content.” The company explains that they merely provide the hardware, while customers choose which apps to install.

“We only sell the hardware device,” the notice states. “Customers must use official apps and licensed services; unauthorized use may violate copyright law.”

Superbox is technically correct here, except for maybe the part about how customers must use official apps and licensed services: Before the Superbox can stream those thousands of channels, users must configure the device to update itself, and the first step involves ripping out Google’s official Play store and replacing it with something called the “App Store” or “Blue TV Store.”

Superbox does this because the device does not use the official Google-certified Android TV system, and its apps will not load otherwise. Only after the Google Play store has been supplanted by this unofficial App Store do the various movie and video streaming apps that are built specifically for the Superbox appear available for download (again, outside of Google’s app ecosystem).

Experts say while these Android streaming boxes generally do what they advertise — enabling buyers to stream video content that would normally require a paid subscription — the apps that enable the streaming also ensnare the user’s Internet connection in a distributed residential proxy network that uses the devices to relay traffic from others.

Ashley is a senior solutions engineer at Censys, a cyber intelligence company that indexes Internet-connected devices, services and hosts. Ashley requested that only her first name be used in this story.

In a recent video interview, Ashley showed off several Superbox models that Censys was studying in the malware lab — including one purchased off the shelf at BestBuy.

“I’m sure a lot of people are thinking, ‘Hey, how bad could it be if it’s for sale at the big box stores?'” she said. “But the more I looked, things got weirder and weirder.”

Ashley said she found the Superbox devices immediately contacted a server at the Chinese instant messaging service Tencent QQ, as well as a residential proxy service called Grass IO.

GET GRASSED

Also known as getgrass[.]io, Grass says it is “a decentralized network that allows users to earn rewards by sharing their unused Internet bandwidth with AI labs and other companies.”

“Buyers seek unused internet bandwidth to access a more diverse range of IP addresses, which enables them to see certain websites from a retail perspective,” the Grass website explains. “By utilizing your unused internet bandwidth, they can conduct market research, or perform tasks like web scraping to train AI.” 

Reached via Twitter/X, Grass founder Andrej Radonjic told KrebsOnSecurity he’d never heard of a Superbox, and that Grass has no affiliation with the device maker.

“It looks like these boxes are distributing an unethical proxy network which people are using to try to take advantage of Grass,” Radonjic said. “The point of grass is to be an opt-in network. You download the grass app to monetize your unused bandwidth. There are tons of sketchy SDKs out there that hijack people’s bandwidth to help webscraping companies.”

Radonjic said Grass has implemented “a robust system to identify network abusers,” and that if it discovers anyone trying to misuse or circumvent its terms of service, the company takes steps to stop it and prevent those users from earning points or rewards.

Superbox’s parent company, Super Media Technology Company Ltd., lists its street address as a UPS store in Fountain Valley, Calif. The company did not respond to multiple inquiries.

According to this teardown by behindmlm.com, a blog that covers multi-level marketing (MLM) schemes, Grass’s compensation plan is built around “grass points,” which are earned through the use of the Grass app and through app usage by recruited affiliates. Affiliates can earn 5,000 grass points for clocking 100 hours usage of Grass’s app, but they must progress through ten affiliate tiers or ranks before they can redeem their grass points (presumably for some type of cryptocurrency). The 10th or “Titan” tier requires affiliates to accumulate a whopping 50 million grass points, or recruit at least 221 more affiliates.

Radonjic said Grass’s system has changed in recent months, and confirmed the company has a referral program where users can earn Grass Uptime Points by contributing their own bandwidth and/or by inviting other users to participate.

“Users are not required to participate in the referral program to earn Grass Uptime Points or to receive Grass Tokens,” Radonjic said. “Grass is in the process of phasing out the referral program and has introduced an updated Grass Points model.”

A review of the Terms and Conditions page for getgrass[.]io at the Wayback Machine shows Grass’s parent company has changed names at least five times in the course of its two-year existence. Searching the Wayback Machine on getgrass[.]io shows that in June 2023 Grass was owned by a company called Wynd Network. By March 2024, the owner was listed as Lower Tribeca Corp. in the Bahamas. By August 2024, Grass was controlled by a Half Space Labs Limited, and in November 2024 the company was owned by Grass OpCo (BVI) Ltd. Currently, the Grass website says its parent is just Grass OpCo Ltd (no BVI in the name).

Radonjic acknowledged that Grass has undergone “a handful of corporate clean-ups over the last couple of years,” but described them as administrative changes that had no operational impact. “These reflect normal early-stage restructuring as the project moved from initial development…into the current structure under the Grass Foundation,” he said.

UNBOXING

Censys’s Ashley said the phone home to China’s Tencent QQ instant messaging service was the first red flag with the Superbox devices she examined. She also discovered the streaming boxes included powerful network analysis and remote access tools, such as Tcpdump and Netcat.

“This thing DNS hijacked my router, did ARP poisoning to the point where things fall off the network so they can assume that IP, and attempted to bypass controls,” she said. “I have root on all of them now, and they actually have a folder called ‘secondstage.’ These devices also have Netcat and Tcpdump on them, and yet they are supposed to be streaming devices.”

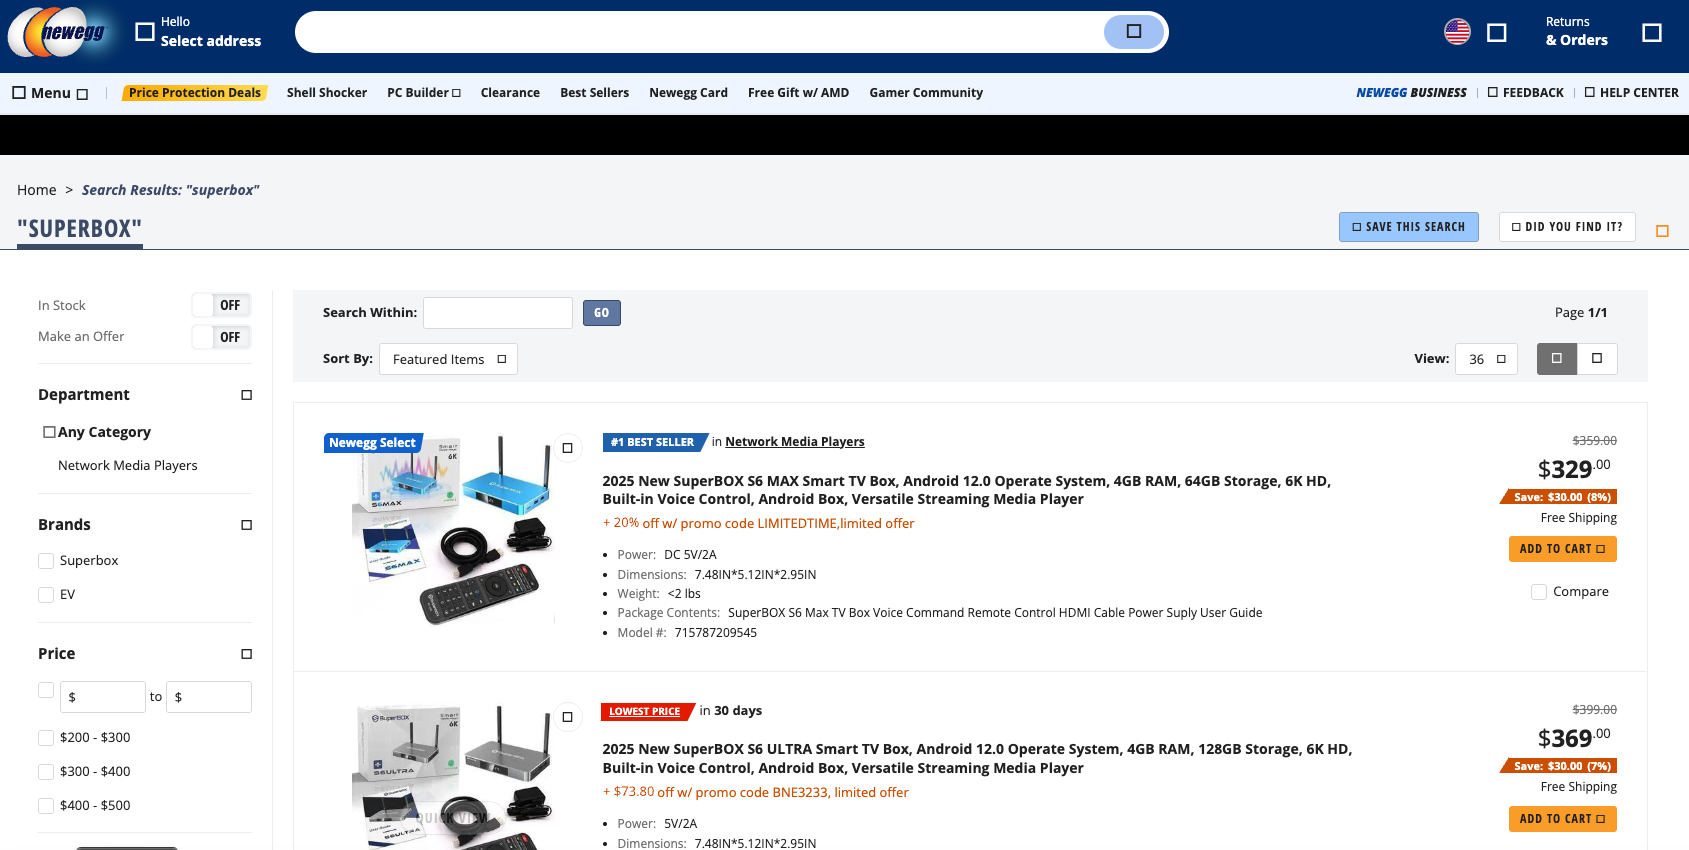
A quick online search shows various Superbox models and many similar Android streaming devices for sale at a wide range of top retail destinations, including Amazon, BestBuy, Newegg, and Walmart. Newegg.com, for example, currently lists more than three dozen Superbox models. In all cases, the products are sold by third-party merchants on these platforms, but in many instances the fulfillment comes from the e-commerce platform itself.

“Newegg is pretty bad now with these devices,” Ashley said. “Ebay is the funniest, because they have Superbox in Spanish — the SuperCaja — which is very popular.”

Superbox devices for sale via Newegg.com.

Ashley said Amazon recently cracked down on Android streaming devices branded as Superbox, but that those listings can still be found under the more generic title “modem and router combo” (which may be slightly closer to the truth about the device’s behavior).

Superbox doesn’t advertise its products in the conventional sense. Rather, it seems to rely on lesser-known influencers on places like Youtube and TikTok to promote the devices. Meanwhile, Ashley said, Superbox pays those influencers 50 percent of the value of each device they sell.

“It’s weird to me because influencer marketing usually caps compensation at 15 percent, and it means they don’t care about the money,” she said. “This is about building their network.”

A TikTok influencer casually mentions and promotes Superbox while chatting with her followers over a glass of wine.

BADBOX

As plentiful as the Superbox is on e-commerce sites, it is just one brand in an ocean of no-name Android-based TV boxes available to consumers. While these devices generally do provide buyers with “free” streaming content, they also tend to include factory-installed malware or require the installation of third-party apps that engage the user’s Internet address in advertising fraud.

In July 2025, Google filed a “John Doe” lawsuit (PDF) against 25 unidentified defendants dubbed the “BadBox 2.0 Enterprise,” which Google described as a botnet of over ten million Android streaming devices that engaged in advertising fraud. Google said the BADBOX 2.0 botnet, in addition to compromising multiple types of devices prior to purchase, can also infect devices by requiring the download of malicious apps from unofficial marketplaces.

Some of the unofficial Android devices flagged by Google as part of the Badbox 2.0 botnet are still widely for sale at major e-commerce vendors. Image: Google.

Several of the Android streaming devices flagged in Google’s lawsuit are still for sale on top U.S. retail sites. For example, searching for the “X88Pro 10” and the “T95” Android streaming boxes finds both continue to be peddled by Amazon sellers.

Google’s lawsuit came on the heels of a June 2025 advisory from the Federal Bureau of Investigation (FBI), which warned that cyber criminals were gaining unauthorized access to home networks by either configuring the products with malicious software prior to the user’s purchase, or infecting the device as it downloads required applications that contain backdoors, usually during the set-up process.

“Once these compromised IoT devices are connected to home networks, the infected devices are susceptible to becoming part of the BADBOX 2.0 botnet and residential proxy services known to be used for malicious activity,” the FBI said.

The FBI said BADBOX 2.0 was discovered after the original BADBOX campaign was disrupted in 2024. The original BADBOX was identified in 2023, and primarily consisted of Android operating system devices that were compromised with backdoor malware prior to purchase.

Riley Kilmer is founder of Spur, a company that tracks residential proxy networks. Kilmer said Badbox 2.0 was used as a distribution platform for IPidea, a China-based entity that is now the world’s largest residential proxy network.

Kilmer and others say IPidea is merely a rebrand of 911S5 Proxy, a China-based proxy provider sanctioned last year by the U.S. Department of the Treasury for operating a botnet that helped criminals steal billions of dollars from financial institutions, credit card issuers, and federal lending programs (the U.S. Department of Justice also arrested the alleged owner of 911S5).

How are most IPidea customers using the proxy service? According to the proxy detection service Synthient, six of the top ten destinations for IPidea proxies involved traffic that has been linked to either ad fraud or credential stuffing (account takeover attempts).

Kilmer said companies like Grass are probably being truthful when they say that some of their customers are companies performing web scraping to train artificial intelligence efforts, because a great deal of content scraping which ultimately benefits AI companies is now leveraging these proxy networks to further obfuscate their aggressive data-slurping activity. By routing this unwelcome traffic through residential IP addresses, Kilmer said, content scraping firms can make it far trickier to filter out.

“Web crawling and scraping has always been a thing, but AI made it like a commodity, data that had to be collected,” Kilmer told KrebsOnSecurity. “Everybody wanted to monetize their own data pots, and how they monetize that is different across the board.”

SOME FRIENDLY ADVICE

Products like Superbox are drawing increased interest from consumers as more popular network television shows and sportscasts migrate to subscription streaming services, and as people begin to realize they’re spending as much or more on streaming services than they previously paid for cable or satellite TV.

These streaming devices from no-name technology vendors are another example of the maxim, “If something is free, you are the product,” meaning the company is making money by selling access to and/or information about its users and their data.

Superbox owners might counter, “Free? I paid $400 for that device!” But remember: Just because you paid a lot for something doesn’t mean you are done paying for it, or that somehow you are the only one who might be worse off from the transaction.

It may be that many Superbox customers don’t care if someone uses their Internet connection to tunnel traffic for ad fraud and account takeovers; for them, it beats paying for multiple streaming services each month. My guess, however, is that quite a few people who buy (or are gifted) these products have little understanding of the bargain they’re making when they plug them into an Internet router.

Superbox performs some serious linguistic gymnastics to claim its products don’t violate copyright laws, and that its customers alone are responsible for understanding and observing any local laws on the matter. However, buyer beware: If you’re a resident of the United States, you should know that using these devices for unauthorized streaming violates the Digital Millennium Copyright Act (DMCA), and can incur legal action, fines, and potential warnings and/or suspension of service by your Internet service provider.

According to the FBI, there are several signs to look for that may indicate a streaming device you own is malicious, including:

-The presence of suspicious marketplaces where apps are downloaded.
-Requiring Google Play Protect settings to be disabled.
-Generic TV streaming devices advertised as unlocked or capable of accessing free content.
-IoT devices advertised from unrecognizable brands.
-Android devices that are not Play Protect certified.
-Unexplained or suspicious Internet traffic.

This explainer from the Electronic Frontier Foundation delves a bit deeper into each of the potential symptoms listed above.

How to Hack Hardware using UART

By: BHIS
3 September 2019 at 19:21

Raymond Felch // Preface: I began my exploration of reverse-engineering firmware a few weeks back (see “JTAG – Micro-Controller Debugging“), and although I made considerable progress finding and identifying the […]

The post How to Hack Hardware using UART appeared first on Black Hills Information Security, Inc..

❌