❌

Normal view

World Cup 2026: watch out for these scams | Kaspersky official blog

The World Cup attracts a great many fans — but also a great many scammers. While millions of fans tune in to watch the matches, cybercriminals are hard at work trying to get at their money and personal data. In fact, we’ve already flagged more than 336 fake websites designed to look exactly like the official World Cup page! As the biggest sporting event of the year heats up, here are the top red flags you need to watch out for.

Totally Legit Free Streams (No Scam)

Scoring a seat at WC26 has turned into quite the mission. Soccer fans are furious over ticket prices, which have officially been dubbed the highest in World Cup history. On top of lodging and travel costs, the situation is made even worse by America’s stringent immigration policies — where referees, team staff, and even players have faced major visa and entry headaches. But fans still want to watch the games, and that’s exactly where fake streaming platforms step in to “help”.

Here’s how the scam plays out: cybercriminals set up fake websites promising free access to World Cup match streams. But the moment you click Watch Now, you’re prompted to sign up and then pay for “lifetime access” to the entire tournament. In the example below, they’re asking for cryptocurrency — which is still a bit unusual, since scammers typically prefer good old-fashioned bank cards.
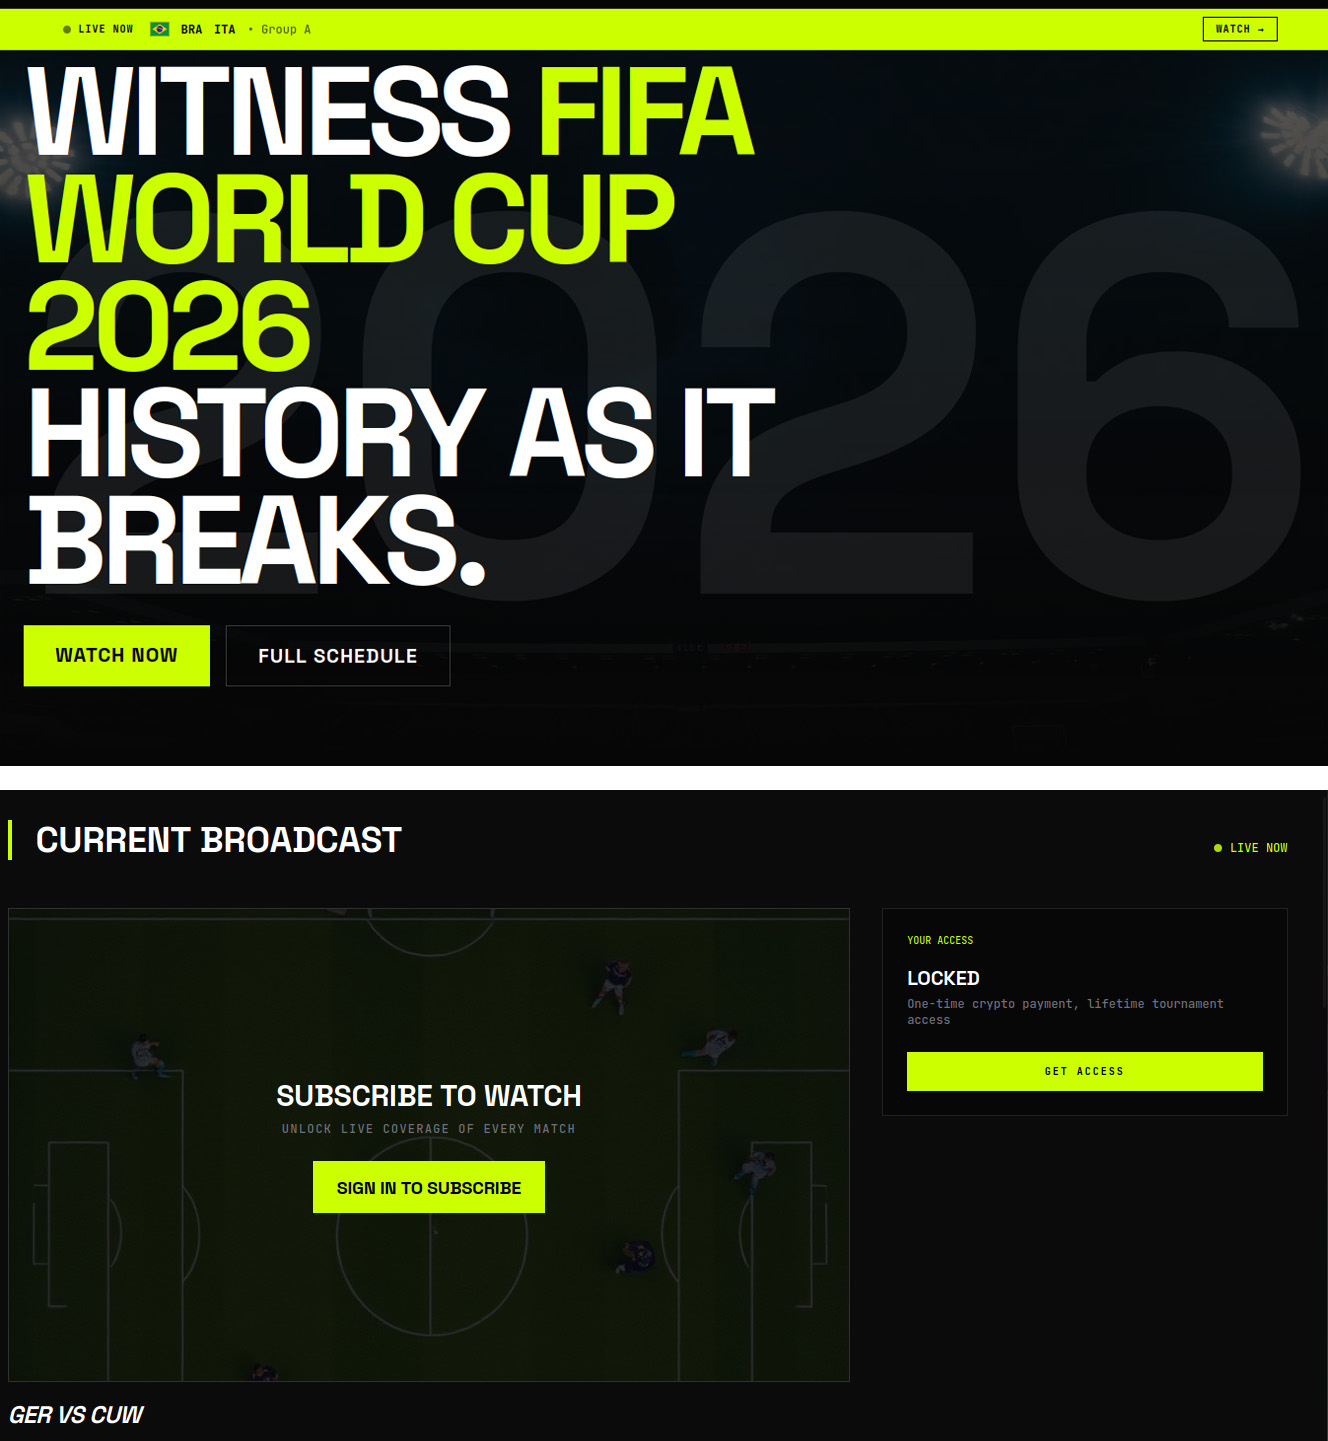
An example of a fake video streaming website requiring users to register and pay with cryptocurrency to watch all World Cup 2026 matches

An example of a fake video streaming website requiring users to register and pay with cryptocurrency to watch all World Cup 2026 matches

Fans who are desperate to catch their favorite teams live risk losing not just their money, but also their personal data, which hackers can later weaponize in targeted phishing attacks.

A losing bet

Match result predictions and sports betting always skyrocket in popularity during the World Cup, and scammers waste no time cashing in on the trend. And behind the flashy slogans lie classic scam tactics.

Take this beautifully designed Spanish-language website. To sign up, it demands a massive amount of personal information, including your full name, national ID number, email address, and phone number — and, of course, it asks you to create a password. If a victim uses the exact same password for multiple accounts, they’re essentially handing the keys to their digital life over to cybercriminals.
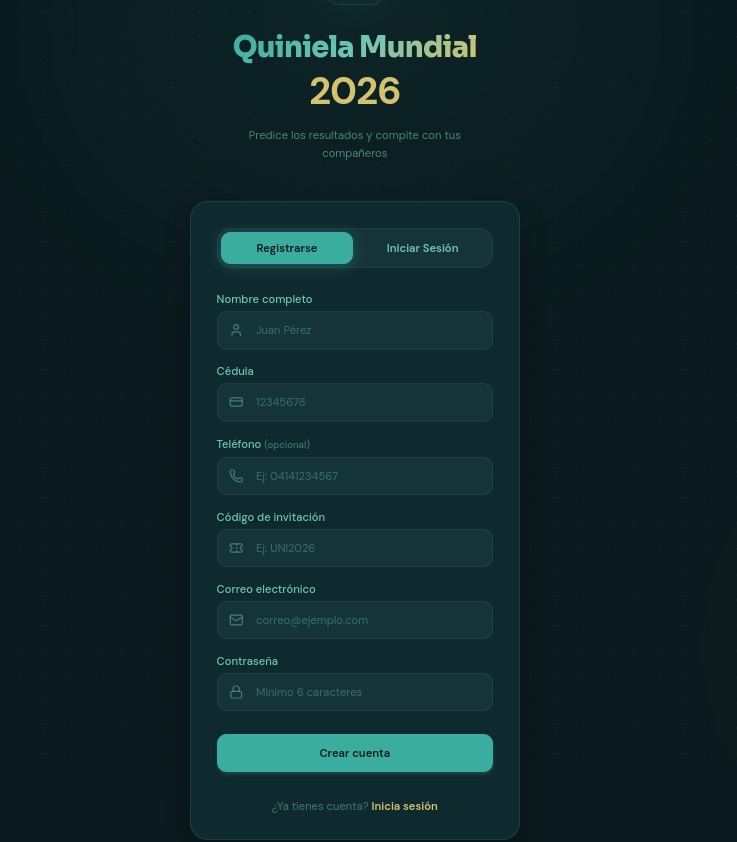
To guess match outcomes on this site, you have to hand over way too much personal info — everything short of biometrics

To guess match outcomes on this site, you have to hand over way too much personal info — everything short of biometrics

Another site, specifically targeting users in Colombia, turned the sign-up process into a paid ordeal — and it features every trick in the book.

  • To “verify” your profile, you’re forced to use WhatsApp under the guise of avoiding legal complications.
  • Before your account is activated, you must make a deposit. This means sending 100 000 Colombian pesos (about $29) to a specified account and texting the receipt to an “administrator” on WhatsApp.
  • Next, you’re told to wait 12 hours for the “administrator” to manually activate your profile.
  • Only after all of this do the scammers tell you can place unlimited bets (of course not true).
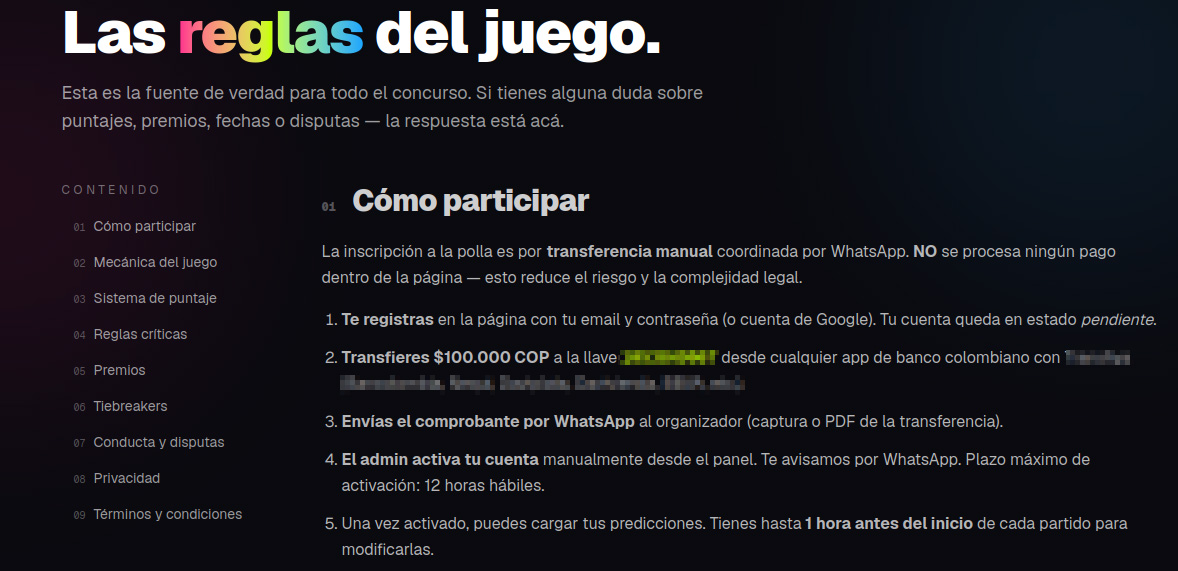
These scammers built a whole website, but they do all their business over WhatsApp. That's a red flag!

These scammers built a whole website, but they do all their business over WhatsApp. That’s a red flag!

In many countries — including Colombia — sports betting is strictly regulated. Only a handful of licensed operators are legally allowed to run these sites, and users are required by law to verify their identity. Because of this, these shady workarounds can look tempting to people who love to gamble but don’t want to — or can’t — go through the official verification process.

Unfortunately, the scammers always win in this scenario. They walk away with your initial deposit and every single bet you place on their site. At the end of the day, their only real goal is to drain their victims’ wallets for as much as they possibly can.

Discounts for collectors!

The World Cup isn’t just about the matches; it also drives record-breaking sales of collectible merchandise — stickers, scarves, team jerseys, official match balls, and more. Naturally, plenty of scammers are eager to get a piece of that action.

Take a look at this website offering “exclusive, limited-edition” stickers and albums. Notice anything suspicious?
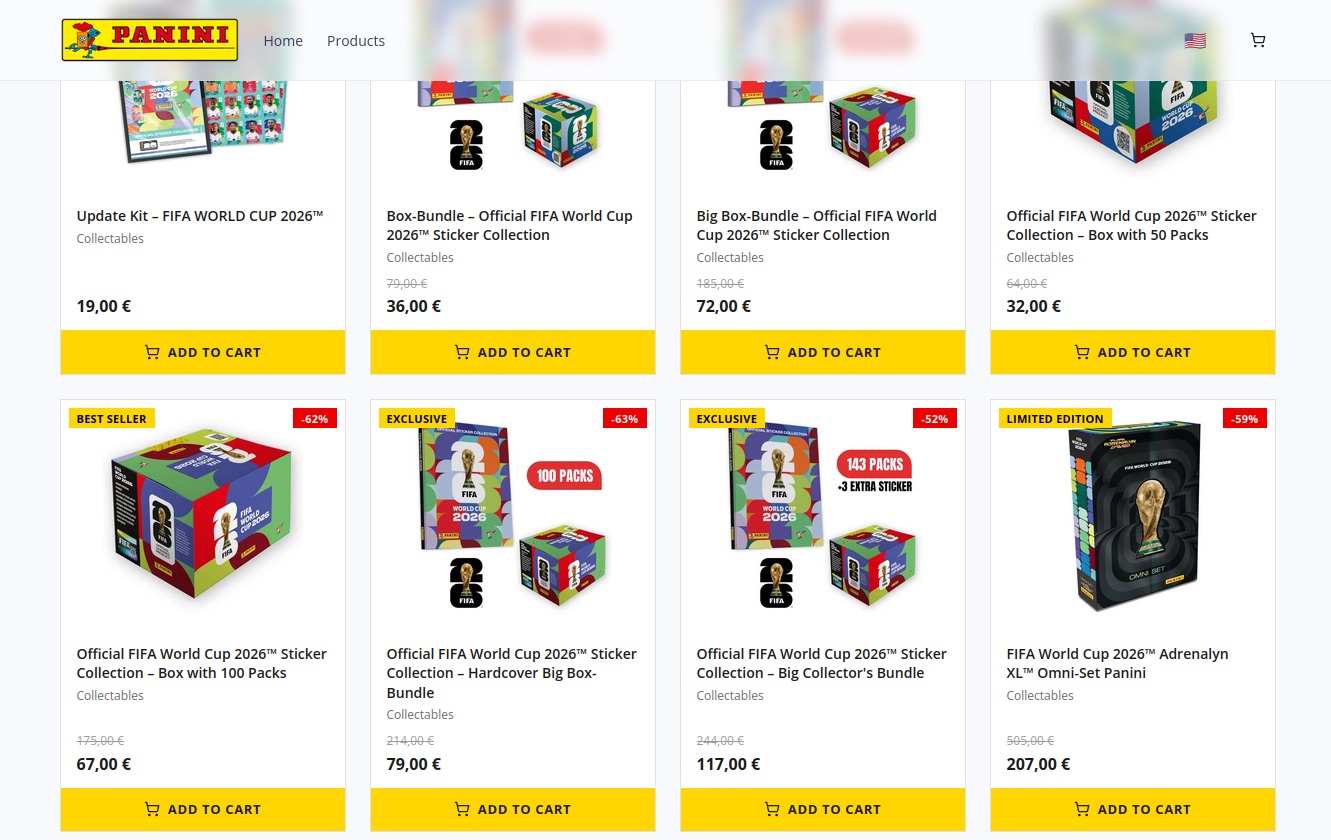
Talk about a steal! Too bad the whole website is a scam

Talk about a steal! Too bad the whole website is a scam

Check out those prices: everything is heavily discounted, even though the tournament is in full swing. All it takes is a quick price check against the real deal to spot the trap. In the screenshot above, the scammers are charging 67 euros for a sticker collection. On actual online marketplaces, that exact same set goes for at least twice as much, and on the official Panini website, it’s three times the price.

Fake websites mimicking popular sporting goods stores also offer to sell you shin guards, socks, jerseys, and any other gear. Of course, you’ll never see the merchandise, and you’ll lose both your money and your bank card details.
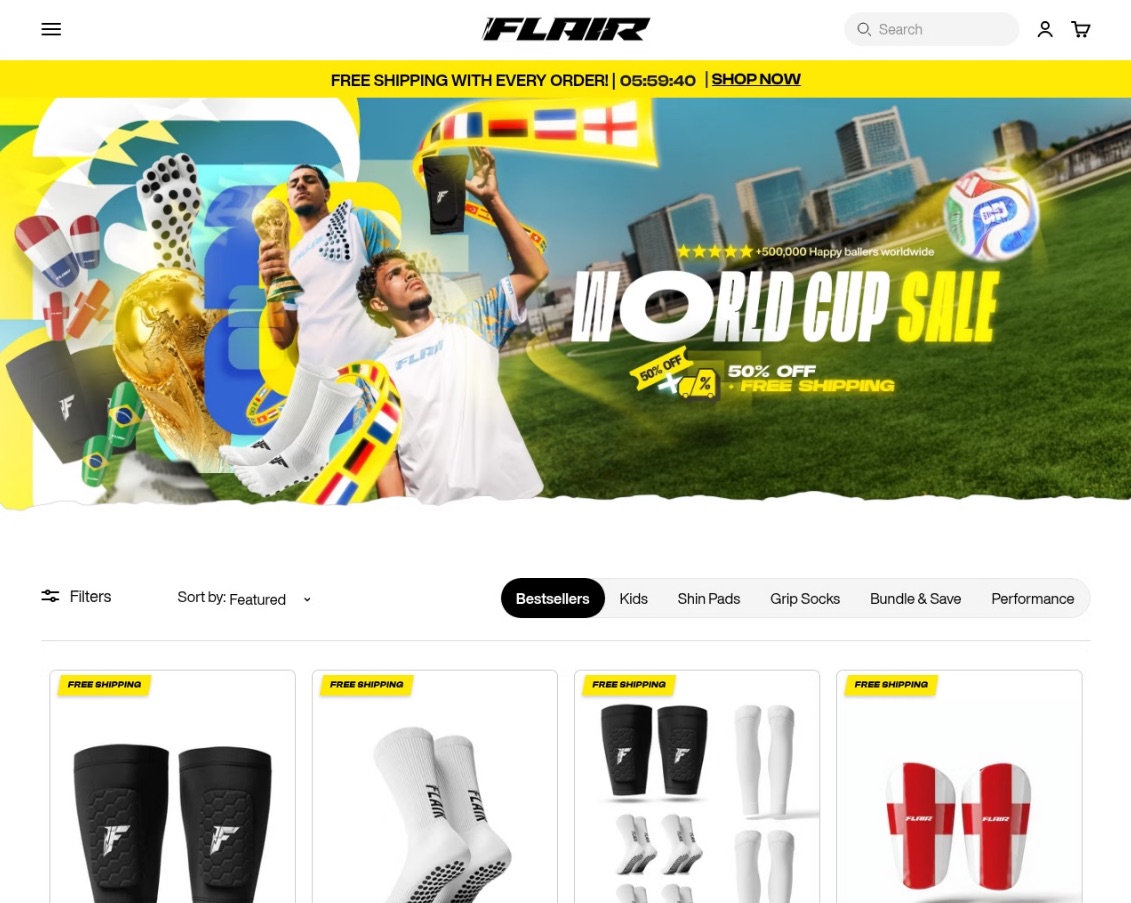
When they've absolutely no intention of delivering any products, they can easily offer massive discounts and free shipping

When they’ve absolutely no intention of delivering any products, they can easily offer massive discounts and free shipping

Deals that seem too good to be true are one of the biggest red flags. To make matters worse, with the help of AI, fake websites now look just as professional as the real ones, making them harder than ever to spot. That’s why we recommend installing our security suite before you start shopping online. It blocks phishing sites in real time and uses the Safe Money feature to keep your financial data secure.

Soccer by mail

Another attack strategy involves spam campaigns centered around the World Cup. In one email, our experts uncovered an ad for a soccer analytics and betting-tips service. It uses the classic high-pressure playbook: “ONLY 10 SPOTS AVAILABLE” — so hurry up before they run out! Naturally, access comes with a price tag: AU$200.
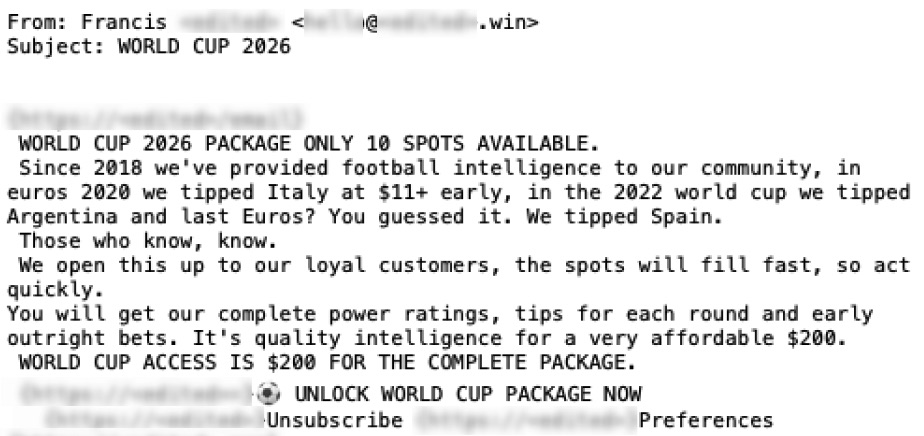
Spammers hurrying the victim to make a decision as quickly as possible

Spammers hurrying the victim to make a decision as quickly as possible

This scheme targets fans who are into sports betting, and paying for these types of services usually ends one of two ways for them: they either lose their money with zero guarantee of getting actual predictions, or get sucked into an even deeper, multi-step financial trap.

How to avoid falling for the scams

Across all these scenarios, the World Cup is just another convenient pretext for cybercriminals. Once the tournament wraps up, they’ll most certainly pivot back to their usual tricks — like fake job offers or Telegram phishing scams — until the next Olympics or soccer tournament rolls around and they switch right back to sport.

Our research consistently shows that online fraud has evolved into a massive illegal enterprise. You aren’t just up against lone scammers anymore; you’re dealing with large criminal networks. When it comes to defense, the best approach is a proactive one. By installing Kaspersky Premium, you can safeguard all your devices from malware, phishing, spam, and malicious or lookalike websites. Plus, the included Kaspersky Password Manager will generate unique complex passwords, securely store your sensitive data — like documents and bank cards — and stop you from auto-filling your credentials on fake sites.

  • Watch the games only on legitimate streaming platforms. Don’t trust fake reviews and never enter your bank card information on unverified sites. Keep an eye out not just for sketchy streaming websites, but also for fake IPTV apps. As we’ve covered in detail before, scammers frequently use these to infect your devices with Trojans.
  • Shop smart. The best way to avoid getting ripped off is to buy merchandise exclusively through official channels (where you won’t see suspiciously deep discounts), or simply buy your gear in person at official retail locations.
  • Don’t click suspicious links. If a deal that’s too good to be true lands in your inbox — whether it’s exclusive betting tips or anything else — just ignore it and hit delete.
  • Avoid logging in through Telegram bots. At the very least, this saves you from future headaches and annoying spam. At best, it keeps your account from being hijacked and your crypto from being stolen.
  • Switch to passkeys wherever possible. Unlike traditional passwords, which are easily stolen and can be typed into any fake login page, a passkey is cryptographically tied to a specific website and won’t work on a phishing page. Kaspersky Password Manager can easily store and sync your passkeys across all your devices.

What other ruses do scammers use to make a quick buck? Check out our other posts:

Americans lost nearly $900 million to AI-powered scams, FBI says

8 June 2026 at 17:02

The 2025 Federal Bureau of Investigation (FBI) Internet Crime Report shows that Americans reported $893,346,472 in AI‑related scam losses.

Those losses stem from 22,364 AI-related complaints. And these figures represent only the reported losses, which may well be the proverbial tip of the iceberg.

The main drivers behind the rise in AI-powered scams are voice cloning, deepfake images and videos, and AI‑generated scripts. These tools have supercharged classic fraud schemes such as romance scams, kidnapping and extortion calls, fake influencers, and government impersonation.

Michael Machtinger, deputy assistant director of the FBI Cyber Division, told the Wall Street Journal:

“AI-created fraudulent communications can look very official and very legitimate to even the most trained individuals.”

The FBI and financial institutions recommend verifying identities via official contact channels. One of their biggest concerns is government impersonation scams, which have evolved from crude IRS gift‑card phone calls into sophisticated, multi‑channel operations that combine spoofed caller ID, stolen agency logos, and AI‑generated audio and video of public officials.

This report, and others like it, shows how AI is being weaponized to automate research on victims, generate convincing scripts, and create highly believable deepfake personas at scale.

AI is also increasingly used in business email compromise (BEC), romance scams, and impersonation fraud. In BEC cases involving AI, losses have already reached tens of millions of dollars for businesses alone.

For a broader look at why AI is simultaneously fueling scams like these and becoming indispensable to defending against them, see my article AI: Threat, tool, or both?

It explains how both defenders and criminals use AI to find vulnerabilities, and why security vendors increasingly rely on AI to process vast amounts of telemetry, detect anomalies, and keep pace with threats that “no longer move at human speed.”

How to stay safe

Consumer protection agencies have documented a growing list of the ways scammers are using AI to try to rip people off. The main problem is that we can no longer take it at face value that the person we’re talking to is who they claim to be.

Government agencies and financial institutions recommend that you:

  • Be skeptical of urgent payment demands, especially those involving cryptocurrency or gift cards
  • Limit the amount of voice and video content you share publicly, as it can be reused by scammers
  • Report incidents quickly to your bank(s) and IC3.gov

Pro tip: Malwarebytes Scam Guard can help you determine whether a message is a scam and guide you through the next steps.


Something feel off? Check it before you click.  

Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.  

Available with Malwarebytes Premium Security for all your devices, and in the Malwarebytes app for iOS and Android.  

Try it free → 

Scams in messengers: exposing the global scam-cartels exploiting everyday messagesng-heist | Kaspersky official blog

1 June 2026 at 09:00

It starts with the familiar: a short message, a trusted name, a routine tone. Delivery updates, work pings, brand alerts hum in the background, rarely attracting scrutiny. You check, you answer… — until minutes later you’ve slipped into a trap built to lower your guard and hijack your trust.

That’s why messaging scams cut deep: they exploit everyday habits where instinct, not caution, leads. Communication once moved slowly, leaving room for doubt. Now it’s instant — and that speed is a weapon in criminal hands.

On our blog, we’ve already examined numerous scam schemes in messaging apps — from pig butchering, where the victim is groomed for a very long time, or catfishing, where the scammer creates a fake identity, to phishing via chatbots or through gift-giving campaigns in messaging apps.

Now, for the first time, Kaspersky has set out to capture the full end-to-end reality of messaging-based scams to understand how quickly harm occurs, how they impact trust and what remains after the interaction ends. What emerges is a highly organized and industrialized scam ecosystem embedded within everyday messaging channels such as SMS, WhatsApp, and email.

Kaspersky experts have prepared a report on targeted scams in messaging apps, detailing not only the financial but also the emotional damage caused by such attacks, as well as providing tips on how to protect yourself and avoid them. In this post, we explore the most interesting facts, but you can find more details in the full report.

The damage is underestimated

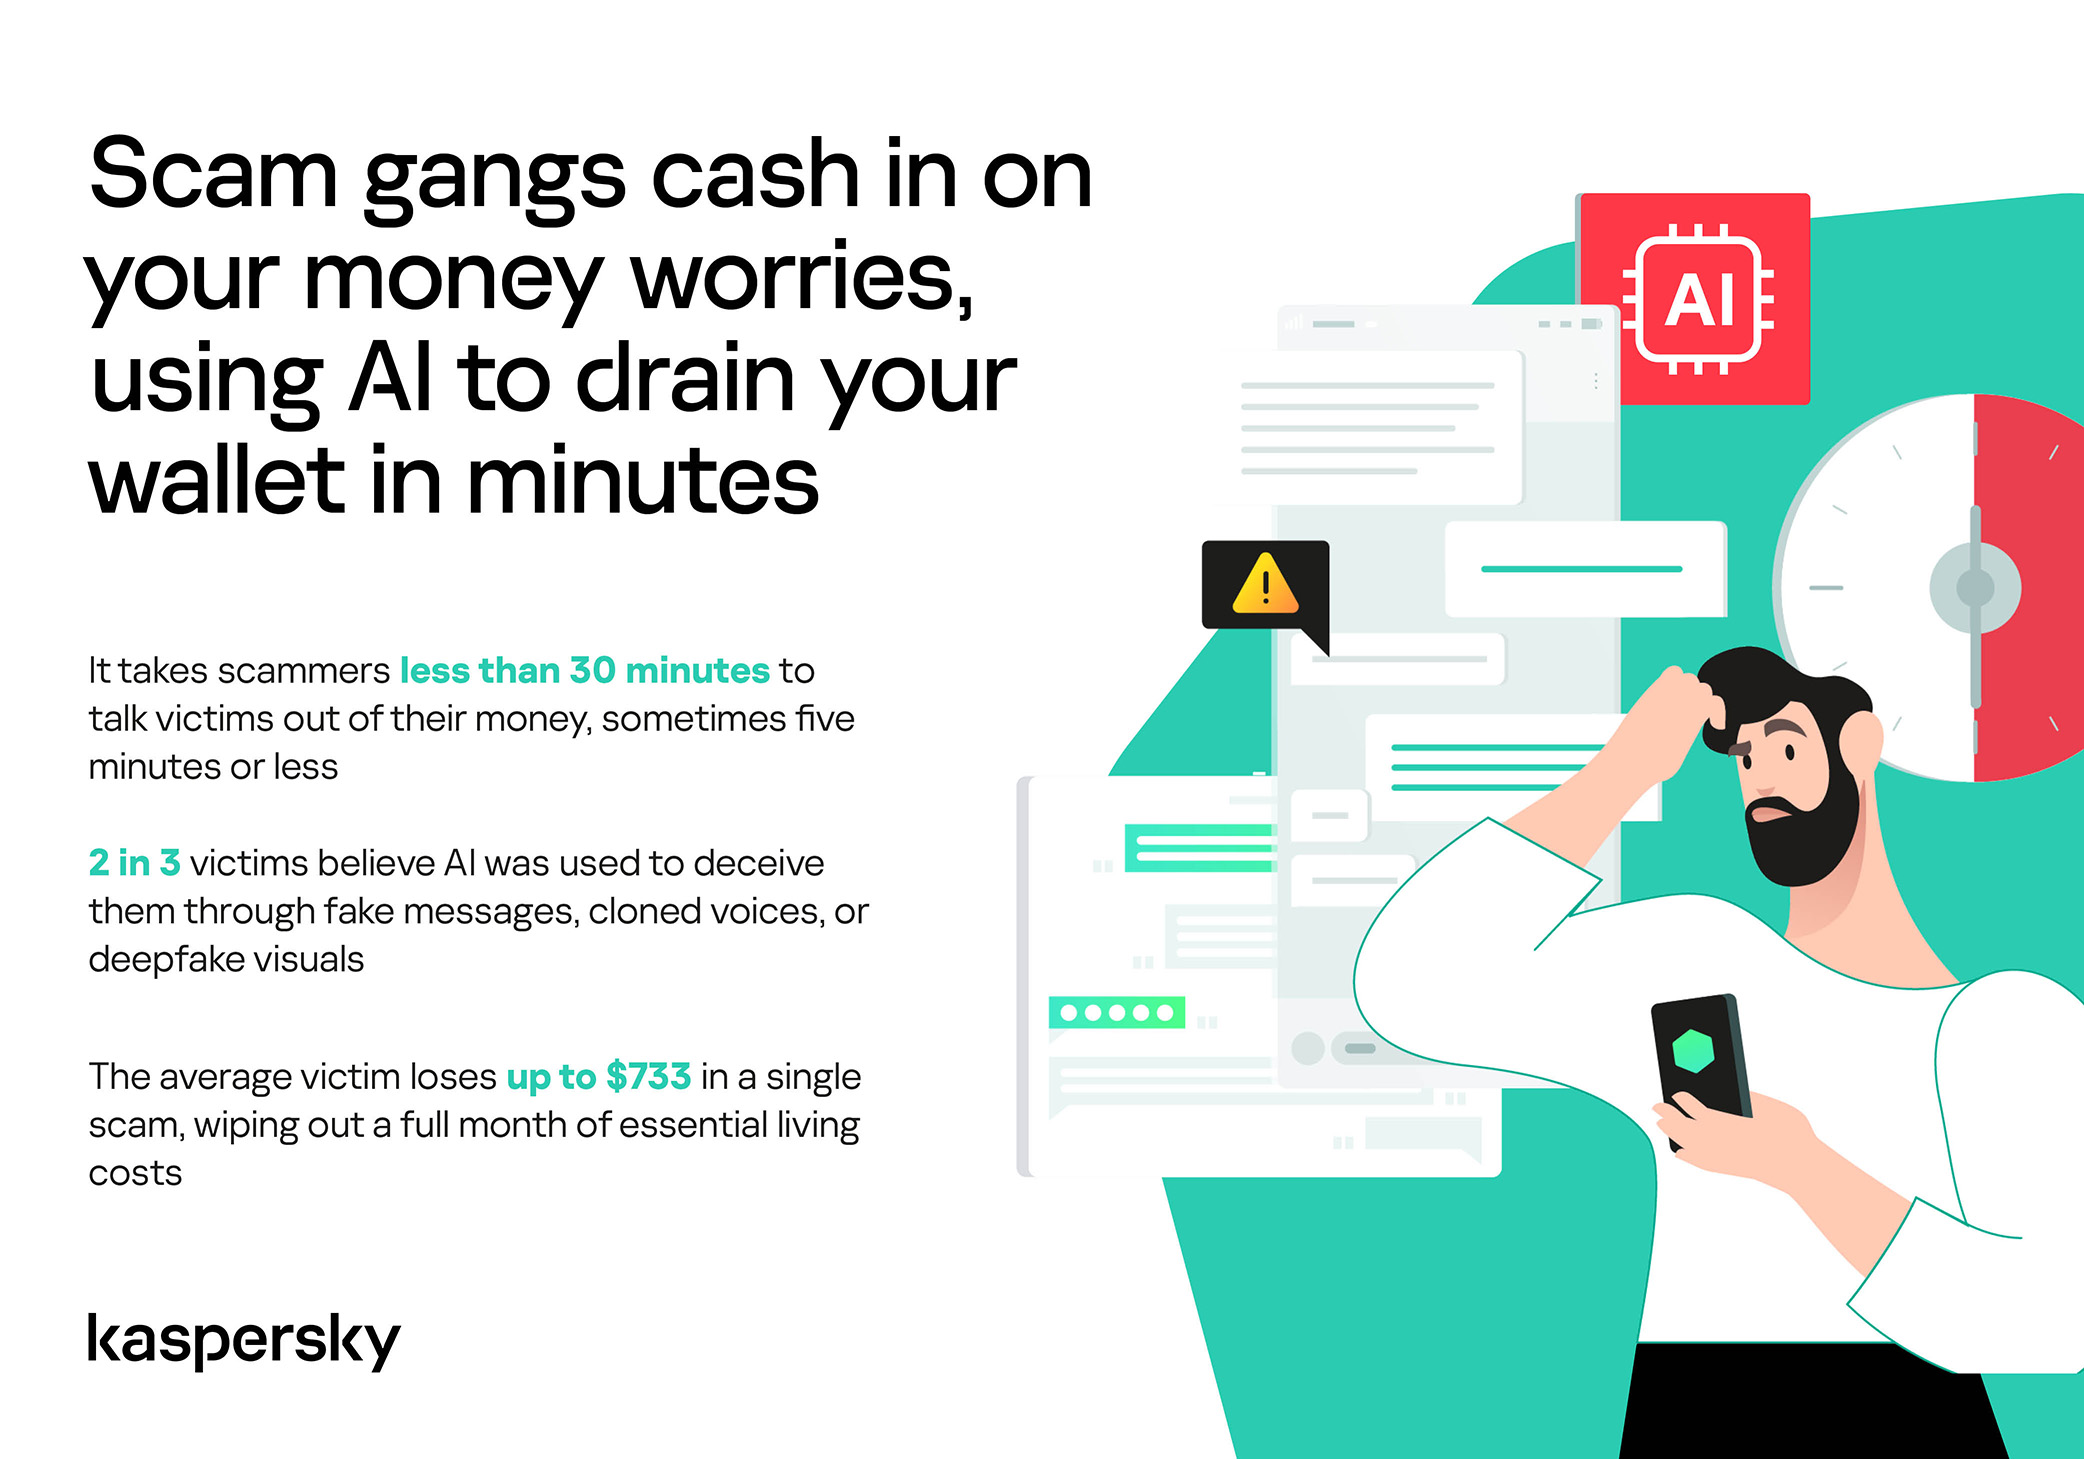
How much do you think a single successful attack via a messaging app costs the average victim? Ten dollars? Or maybe 50? You’re underestimating the scammers. Although more than a third (36%) of victims incur losses of less than $135, on average a victim loses… $733!

Country Average loss per victim
Senegal $392.94
Serbia $493.32
Morocco $504.28
Greece $609.32
United Kingdom $617.38
Côte d’Ivoire $654.11
Spain $672.67
United States $724.73
Portugal $868.20
Italy $896.02
France $1,193.58
Germany $1,369.35

The average amount lost by a victim in a successful attack via a messaging app

On the one hand, the financial hit doesn’t look catastrophic in isolation. These are micro-losses by design. Small enough that some never report them to the police. Small enough that banks don’t always investigate. Small enough to be dismissed as bad luck rather than organized crime.

But $733 is not nothing. It’s enough to cover a month’s worth of groceries, school or daycare fees, or utility bills. Against the backdrop of the global cost-of-living crisis, a single such loss can seriously dent a family’s budget.

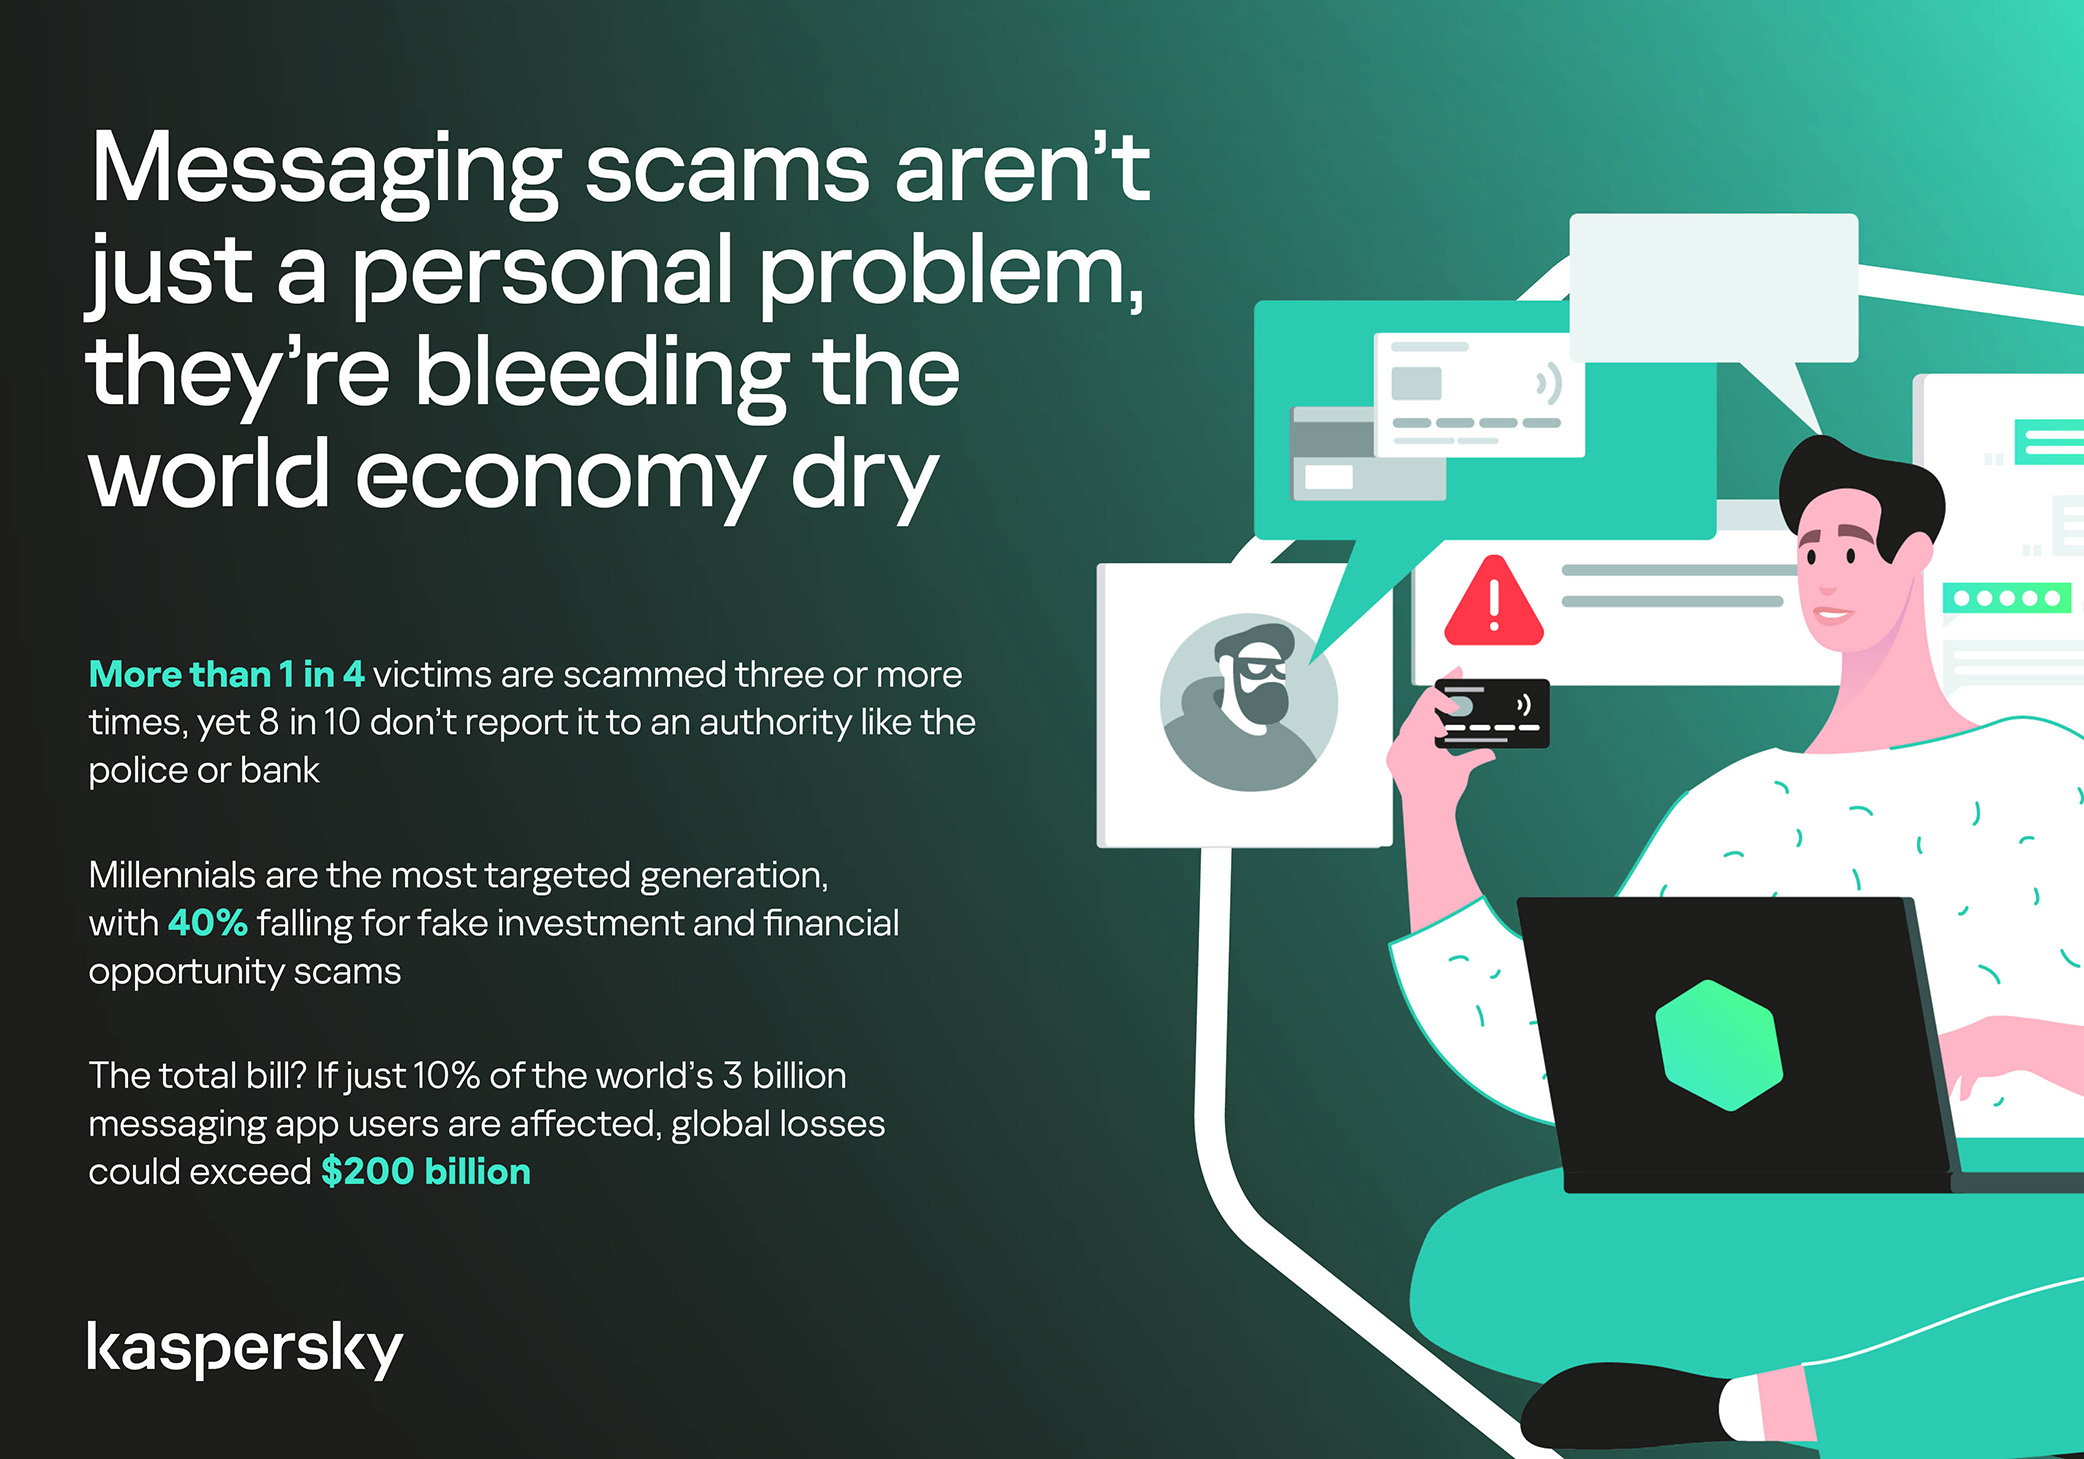
In 11% of cases, losses exceed $1,350, and more than a quarter of victims (28%) report having been scammed three or more times in the past six months. Once scammers discover that a phone number responds, that contact becomes an asset, circulating from one database to another.

Now imagine the scale of the problem: if just 10% of the three billion messaging‑app users worldwide fell victim with the average loss, the total damage would amount to… nearly $220 billion! This is comparable to the GDP of Greece, and exceeds that of Morocco, Serbia, or Côte d’Ivoire.

It becomes clear that behind the daily flood of fraudulent schemes lie large scam cartels operating on an industrial scale, using AI to personalize messages that mimic those of family members, friends, and familiar brands. This, in essence, forms the basis of a full-fledged economy built on digital identity theft.

Scam gangs cash in on your money worries, using AI to drain your wallet in minutes

Speed beats scrutiny

More than half of successful messaging scams (52%) unfold in under 30 minutes — from first contact to the moment money or personal data changes hands — or even faster, before the victim begins to doubt the legitimacy of the sender. In fact, one in seven scams takes less than five minutes — quicker than boiling an egg!

The speed isn’t accidental. It’s the method. Scammers structure their schemes to deny the victim a chance to come to their senses. Every element is engineered to compress the decision-making window: the urgency of the scenario, the familiarity of the format, the plausibility of the request.

They rush you — faster, faster, don’t tell anyone, you only have a few minutes, solve the problem, don’t ask questions. Click the link, fill in the details, approve the transaction, or else… Or else what? The scammers’ imagination knows no bounds here, but if you don’t do something right now, you’ll definitely regret it.

Alas, the realization of what has happened usually comes when the damage is already irreversible. More than half of victims (51%) lose money; another 43% hand over their personal data — most commonly phone numbers, names, and email addresses — to scammers, and often the victim loses both.

Where and how attacks occur

A delivery notification, a bank alert, a message from a merchant you ordered from last week — messaging apps permeate every aspect of everyday life, making such interactions completely normal. An attack shouldn’t feel like an attack. It should feel like the same message you’ve received hundreds of times.

It’s no surprise that scammers focus their attention on this method of communication first and foremost. The most popular platforms for scams are predictable: WhatsApp (43%), SMS/iMessage (40%), Facebook (27%), Telegram (22%), and Instagram (19%) — these are the ones that people trust most.

A wide variety of schemes is used. Brand impersonation is now one of the three most common types of messaging scam worldwide — accounting for 31% of cases. Fake delivery notifications top the list at 38%, followed by investment scams at 37%.

At the same time, nearly two-thirds (63%) of fraudulent schemes span multiple platforms, moving from SMS to WhatsApp, from WhatsApp to Telegram, etc. In this way, scammers achieve two goals: they mimic organic messaging and evade moderation algorithms.

AI has taken scams to a new level

Just a couple of years ago, fraudulent messages gave themselves away with bad grammar, awkward phrasing, illogical requests, and an obsessive sense of urgency. Today, a phishing message looks, sounds, and reads just like the real thing.

Scam cartels want to catch people in motion — between meetings, on a commute, or during everyday tasks — when your attention is already fragmented. They mimic your mother’s turn of phrase. They match your bank’s tone of voice. They copy your courier’s format exactly. They mirror the rhythm, structure, and style of authentic brand communications across messaging platforms. And AI is accelerating all of it.

What this creates is overlap. Legitimate and fraudulent messages appear in the same environment, using the same formats, language, and triggers. The difference between them is no longer obvious.

The data shows that two-thirds of victims (66%) believe AI was used in the scam against them, 42% cite messages written by AI, 31% report generated or cloned voices, and 25% encountered deepfake images or videos.

That’s why mere awareness and “tech-savviness” may no longer be enough to protect oneself. From Gen Z to Gen X, messaging scams cut across every generation.

And what about the emotional toll?

But money is far from the only problem a victim is left with after an attack. After what they’ve been through, people develop distrust toward incoming messages, unfamiliar numbers, and any requests for action. As a result, 99% of fraud victims say they no longer trust incoming notifications in messaging apps.

This creates a crisis of trust in all digital channels in general. Every legitimate message can now be perceived as a scam. Brands, banks, and delivery services are forced to operate in an environment where the customer is, by default, in a state of distrust.

Dr. Elizabeth Carter, a forensic linguist and criminologist at Kingston University in London, notes that scammers use familiar contexts, common social settings and embedded linguistic norms to create the illusion for the victim that their decision-making is rational and reasonable in the moment. However, what is actually happening is that they construct false realities in which those decisions end up causing financial and psychological harm. She also notes that it is very hard to identify a false reality while you are in it.

After realizing they had been deceived, more than half of victims felt anger — the kind that comes from having trusted something and discovering it was used against you. 42% of victims report frustration, 38% — feeling upset. Moreover, several months later, these feelings haven’t gone away: nearly half of all victims (48%) are still angry, a third (33%) remain frustrated, and 30% are upset.

And nearly one in 10 victims don’t tell anyone what happened. They feel shame, a sense of having fallen for something so obvious. This leaves a significant portion of the actual damage unreported: only 24% of victims contact the police, and only 23% report it to their bank.

Messaging scams aren't just a personal problem, they're bleeding the world economy dry

So what can be done?

The crisis of trust — and even a touch of paranoia — that has arisen due to widespread attacks on users can linger in victims’ minds for a long time, affecting their quality of life. To prevent this, follow these guidelines:

  • Pause before you act. The sense of urgency you feel is almost always artificial. A legitimate bank, retailer, or delivery service won’t penalize you for taking 30 seconds to verify before clicking a link or confirming details. It’s precisely this instinct to resolve the situation quickly that scammers are counting on.
  • Verify through another channel. If a message appears to be from a relative, colleague, or company you trust — contact them through another channel before taking any action. Use secure verification methods, and cross-check identities when something doesn’t feel right. For families, agreeing on a “safe word” in advance can defeat even the most convincing voice clones.
  • Use a password manager. It will not only help you generate strong, unique passwords for all your accounts and store them securely, syncing them across all your devices, but also protect you from spoofed sites. Even if you click a phishing link and land on such a site, our password manager will notify you about the domain mismatch and refuse to autofill your username and password.
  • Use protection that works in real time. Modern security solutions, such as Kaspersky Premium, provide real-time protection against malicious links and phishing attempts in the apps and websites you use every day. On Android devices, a dedicated layer of anti-phishing security scans and neutralizes suspicious links as they appear, even within notifications, before you even have a chance to click them.

We’ve covered other threats in messaging apps in similar articles:

How fake Android IPTV apps are stealing users’ money and data | Kaspersky official blog

Threat actors are already gearing up for this year’s biggest football (soccer) event, the World Cup 2026. With millions of fans looking for ways to stream matches online, many will turn to IPTV apps to watch live TV broadcasts over the internet. It’s no surprise, then, that cybersecurity researchers have discovered multiple campaigns over the past few months where malware was disguised as fake Android IPTV apps.

In this post, we discuss what IPTV apps are, how criminals use fake versions to spread malware, what this malware is capable of, and, most importantly, how to avoid becoming a victim.

What are IPTV apps?

IPTV stands for Internet Protocol Television. This technology delivers TV content over the internet instead of through cable, over-the-air antennas, or satellites. Naturally, the simplest and most common examples of IPTV are the official platforms of TV networks, which can include both websites and dedicated apps.

However, alongside official options, pirate IPTV services also exist. They usually lure users with free or dirt-cheap access to content that can otherwise be hard to find without expensive subscriptions — most notably broadcasts of various sporting events; football matches in particular.

As is typically the case with pirated content, these apps are blocked from official app stores, forcing users to download them from third-party sites. Consequently, the risk of using these services isn’t tied to IPTV technology itself, but rather to the fake apps and modified APK files distributed under the guise of well-known platforms — both official and pirated.

Massiv banking Trojan disguised as IPTV apps

For instance, in February researchers found the Massiv banking Trojan distributed under the guise of fake IPTV apps. Even then, experts noted that this wasn’t the only malware leveraging this tactic — several others were also spotted in the wild. The primary targets of these IPTV-mimicking malicious fakes have mostly been users in Portugal, Spain, France, and Türkiye.

In most cases, the discovered fake IPTV apps lacked the advertised functionality, so users didn’t get access to any content after installing the apps. Instead, the fake app would open the website of a legitimate IPTV service in a built-in browser to mimic normal functioning and avoid raising user suspicion.

Of course, the most interesting activity happened out of the user’s sight. These are some of the features the malware did have:

  • Displaying fake windows on top of legitimate ones: fake forms for entering bank details or signing in to official services, as shown in the screenshot below.
  • Activating a keylogger: recording and transmitting screen keyboard taps to the attackers.
  • Hijacking control of the compromised device.
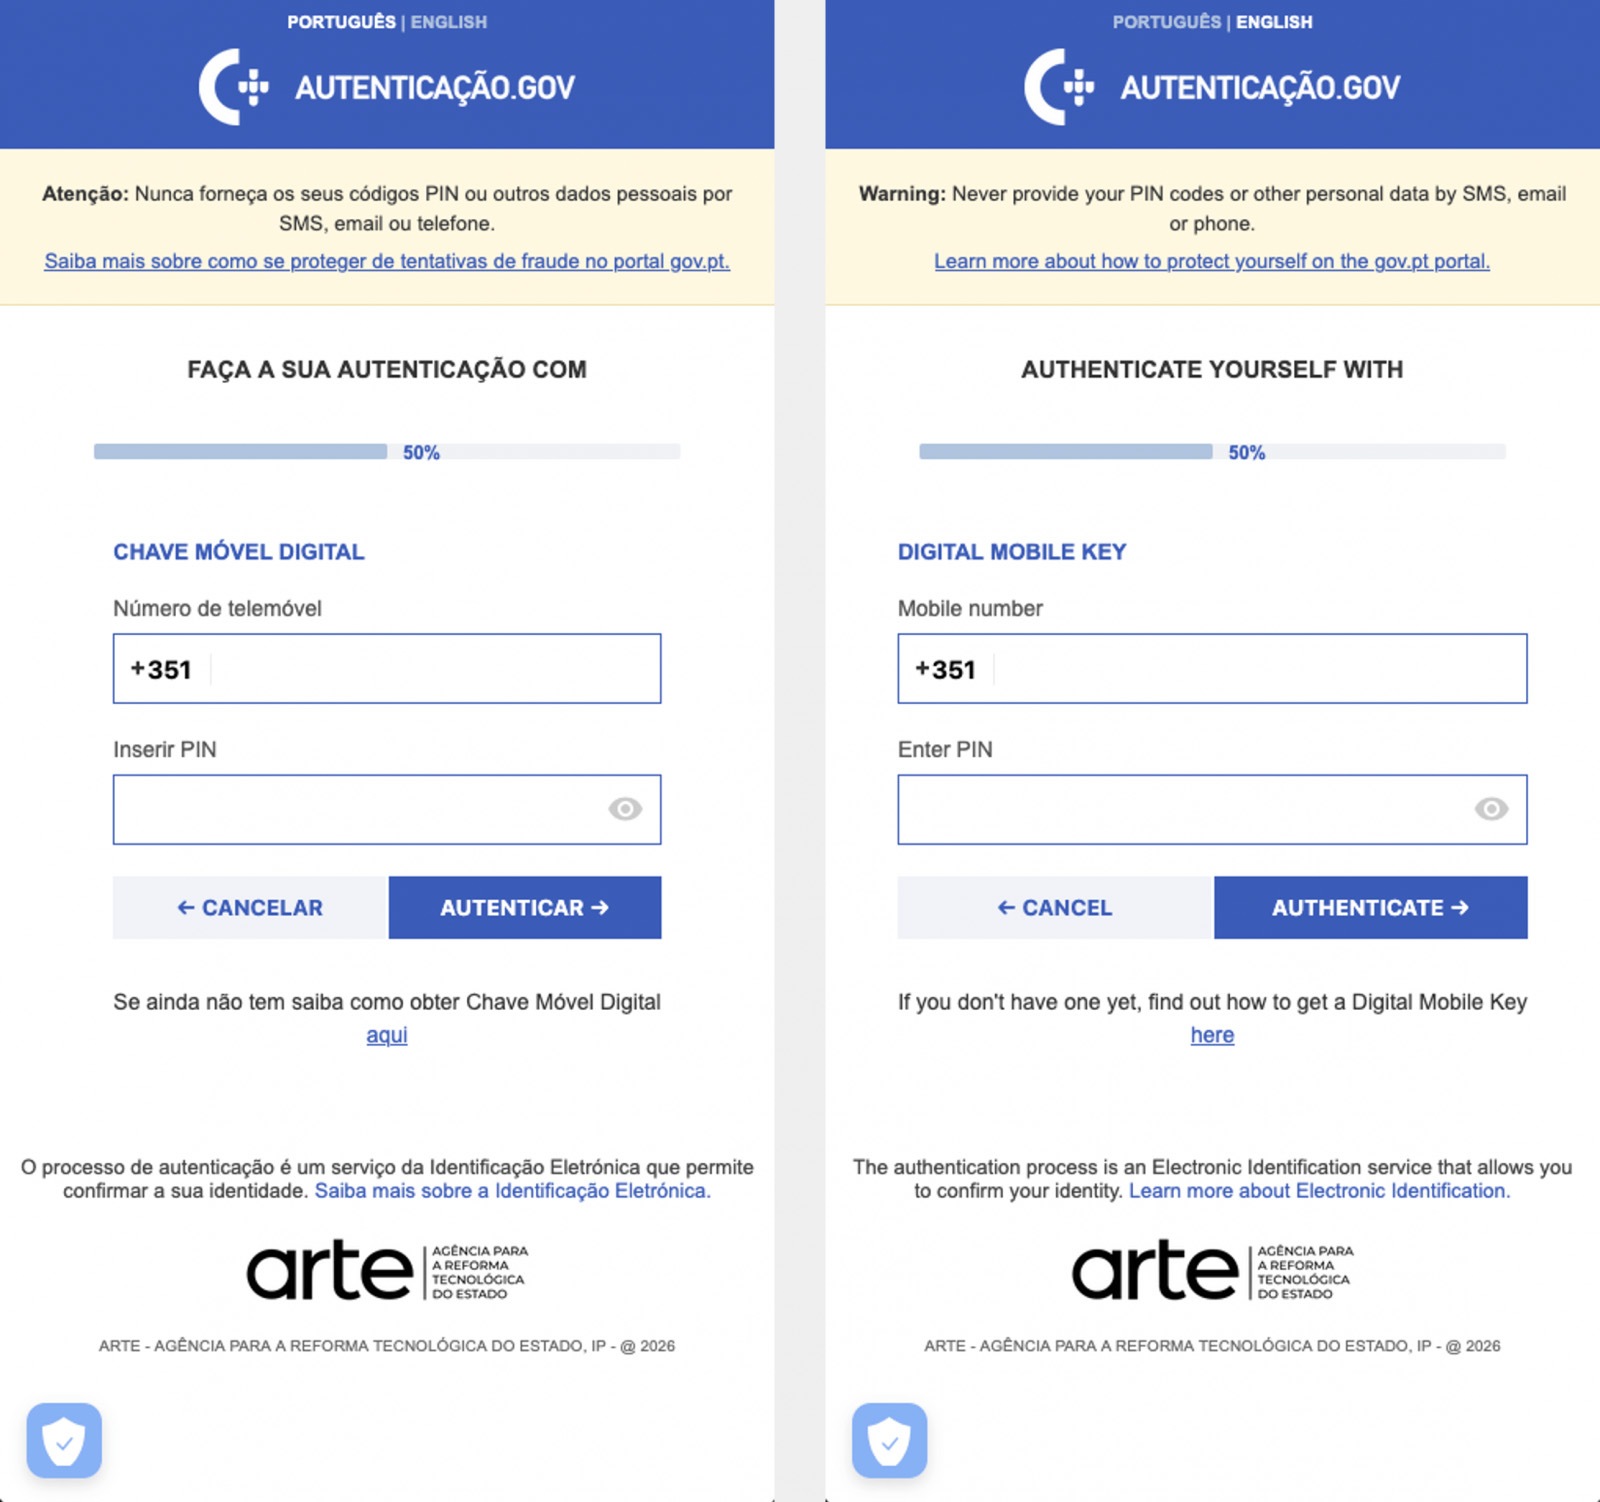
Massiv Trojan steals Chave Móvel Digital data

The Massiv banking Trojan mimics the interface of the Portuguese government app Chave Móvel Digital in a fake pop-up window, looking even more convincing than the official version from Google Play. Source

Perseus steals valuable information from users’ notes

In March, researchers reported on a new campaign where several fake IPTV apps were used to distribute an even more advanced and feature-rich malware strain: Perseus.

Research into Perseus shows that the malware is based on the source code of an Android banking Trojan called Cerberus, which leaked nearly six years ago. Perseus comes in two different versions: Turkish and English. The English-language version is more advanced and shows clear signs of AI-driven refinement.

Perseus abuses Accessibility Services, a set of Android features originally designed to make life easier for users with severe visual impairments. Fraudsters learned long ago how to leverage this tool to steal data from Android devices — a topic we’ve covered in detail across several of our posts.

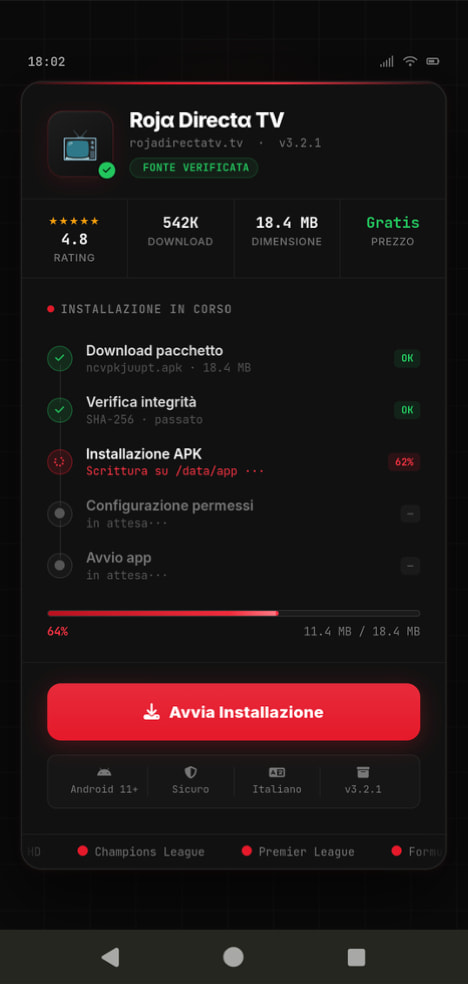
Fake IPTV app used for distributing Perseus

An example of a malicious APK disguised as Roja Directa TV, another IPTV app. Source

By abusing Accessibility Services, Perseus gains remote control over the victim’s device. Here’s what it can do:

  • Continuously capture and exfiltrate screenshots.
  • Send a structured map of the device’s UI for remote manipulation.
  • Mimic taps, swipes, text input, long presses, and other UI interactions.
  • Turn on the screen, launch apps, and block them from running.
  • Trigger a pitch-black screen overlay to hide its activities.
  • Log keystrokes.

On top of that, the English-language version of Perseus boasts another notable feature. The malware can hunt for sensitive information like passwords, recovery phrases, and financial data across an entire range of note-taking apps: Google Keep, Xiaomi Notes, Samsung Notes, ColorNote, Evernote, Microsoft OneNote, and Simple Notes.

All of these capabilities help criminals drain football fans’ money not just from various banking services, but from cryptocurrency apps as well.

How not to let cybercrooks ruin your World Cup

The World Cup is just around the corner, and millions of fans worldwide will definitely want to tune in to this year’s premier football event. Past experience shows that cybercriminals frequently cash in on major spectacles like this. So, how can you watch the  matches safely?

  • Don’t download apps from unofficial stores.
  • Even when downloading an app from an official store — since malware occasionally slips through the cracks there, too— read the reviews carefully. Users who have been burned by fakes and malware often leave comments to warn others.
  • Install a robust security app to keep all your devices safe from malware.
  • Avoid storing passwords or other sensitive information in note-taking apps. To ensure your data and finances stay secure, use a reliable password manager. By the way, Kaspersky Password Manager includes an encrypted note-taking feature, allowing you to store your valuable information safely.

You can’t even watch TV safely anymore these days! Check out other threats facing TV lovers:

Building a safer digital future, together

10 February 2026 at 06:01

As we mark Safer Internet Day 2026, we’re reflecting on a simple but enduring principle: safety must be designed into online services, not bolted on. Microsoft’s work in this space spans more than two decades—from technology solutions like PhotoDNA to our investments in responsible gaming, public-private partnerships, and empowering users through education. This foundation guides our approach as we help individuals and families navigate a rapidly evolving landscape shaped by new technologies and new risks and as we innovate with next-generation AI offerings. At a moment when 91% of people tell us they worry about harms introduced by AI, our commitment to responsible innovation has never been more important—especially for our youngest users.

Read on for more about our longstanding efforts to create a safer digital environment, plus key findings from our Global Online Safety Survey and new examples of our work to empower families and communities through tools, research, and educational resources—including the latest release in Minecraft Education’s CyberSafe series.  

Ten years of safety research 

2026 marks the tenth year of our annual Global Online Safety Survey research. For a decade, we have invested in surveying teens and adults around the world about their experiences and perceptions of life online—aiming to provide fresh insights to support our collective work. That’s 130,000+ interviews across 37 countries, with the results available on our website. Ten years later, respondents tell us that they feel more connected and more productive, but less safe online.  

This year’s Global Online Safety Survey also highlights the complexity of the digital environment young people now inhabit. Teens’ exposure to risk rose again, with hate speech (35%), scams (29%), and cyberbullying (23%) among the most commonly experienced harms. At the same time, teens demonstrated striking resilience: 72% talked to someone after experiencing a risk, and reporting behavior increased for the second consecutive year. But worries about the misuse of AI continue, underscoring again why safety-by-design for AI is essential, not optional. Find the full results and country-level summaries here. 

Year on year, the research has told a story of evolving online safety risks and of the real-world impact. In 2026, the call to action is more urgent than ever—unless industry can deliver safe and age-appropriate experiences, young people risk losing access to technology. At Microsoft, spanning across our teams from Windows to Xbox, we have sought to continuously evolve our approach and to lead industry in advancing tailored and thoughtful safety solutions.   

Evolving to meet the moment 

Looking ahead, we know we need to continue to build strong guardrails to tackle acute risks and to leverage our experience while being informed by new research, new perspectives, and new technologies. The application process closed yesterday for our first AI Futures Youth Council, to be comprised of teens from across the US and EU. We’re looking forward to bringing those teens together soon for a first meeting to get their direct feedback on the role they want emerging technology to play in their lives and how we can best support their safety.  

Microsoft has partnered with Cyberlite on a second youth-centered initiative to understand how teens aged 13–17 are engaging with AI companions. Through codesign workshops with students in India and Singapore, we’re capturing young people’s own perspectives on the benefits, risks, and emotional dimensions of AI use—insights that will directly inform educational resources for teens, parents, and educators. Early findings from the first workshop in December 2025 show that young people value AI as a judgment free space while also recognizing the tradeoffs: privacy risks, overreliance, and erosion of critical thinking loom larger for them than bad advice.  

We’re also thinking about how we define safety in the next era of Windows, leveraging the Family Safety controls that have been integrated for over a decade. As many countries have raised the local age for digital consent, more parents will have the option to enable parental controls for teens up to the age of 18—leveraging these tools as part of a holistic approach to digital parenting. And to help parents set up and understand Family Safety, we’ve developed a short new guide. 

Safety is also about transparency, empowerment, and education. At Xbox, bringing the joy of gaming to everyone means remaining transparent about the many ways we innovate so players, parents, and caregivers can feel confident that Xbox continues to be a place for positive play. You can read more about our recently published Xbox Transparency Report and the tools and resources available to players on the Xbox Wire blog.  

We’re also excited to announce the latest release in Minecraft Education’s CyberSafe series: CyberSafe: Bad Connection? This series of immersive Minecraft worlds and educational resources is free and helps translate complex risks into fun learning experiences that meet young people in their favorite blocky world. Bad Connection?—the fifth in the series—reflects our commitment to evolving to meet new and challenging risks, with a focus on tackling serious risks related to online recruitment and radicalization. Learn more about how to access this new Minecraft world here.  

The CyberSafe series has reached more than 80 million downloads since 2022 through a partnership between Minecraft Education, Xbox, and Microsoft, helping a generation of young players build the agency, resilience, and digital citizenship they need to navigate an increasingly online world. As part of our commitment to ensure people have the knowledge and skills they need to benefit from technology and stay safe, Microsoft Elevate is empowering educators and students with tools and guidance to build safer, more responsible digital habits, recognizing that AI is transforming how people learn, work, and connect. Our commitment to helping young people access technology safely is also why we’ve partnered with organizations, like the National 4-H Council to prepare young people for an AI-powered world through AI literacy and digital safety curriculum and game-based learning with Minecraft Education. 

As we look ahead, our goal is clear: build technology that is safe by design, guided by evidence, and informed through partnership. The internet has changed profoundly over the past decade, and so too have the expectations of the people who use it. Safer Internet Day is a reminder that progress requires sustained collaboration across industry, civil society, researchers, and families.

—  

Global Online Safety Survey Methodology  

Microsoft has published annual research since 2016 that surveys how people of varying ages use and view online technology. This latest consumer-based report is based on a survey of nearly 15,000 teens (13–17) and adults that was conducted this past summer in 15 countries examining people’s attitudes and perceptions about online safety tools and interactions. Responses to online safety differ depending on the country. Full results can be accessed here.  


The post Building a safer digital future, together appeared first on Microsoft On the Issues.

❌