Once. Someone named “Vincenzo lozzo” wrote to Epstein in email, in 2016: “I wouldn’t pay too much attention to this, Schneier has a long tradition of dramatizing and misunderstanding things.” The topic of the email is DDoS attacks, and it is unclear what I am dramatizing and misunderstanding.
Rabbi Schneier is also mentioned, also incidentally, also once. As far as either of us know, we are not related.
EDITED TO ADD (2/7): There is more context on the Justice.gov website version.
The LastPass Threat Intelligence, Mitigation, and Escalation (TIME) team has published a warning about an active phishing campaign in which fake “maintenance” emails pressure users to back up their vaults within 24 hours. The emails lead to credential-stealing phishing sites rather than any legitimate LastPass page.
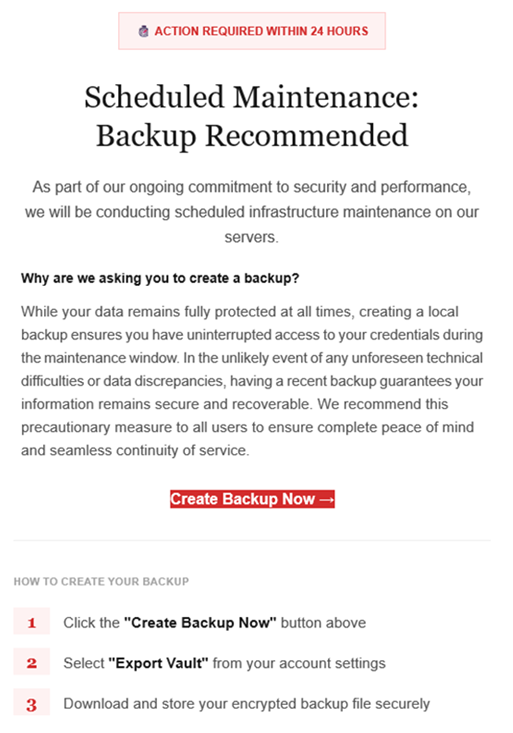
The phishing campaign that started around January 19, 2026, uses emails that falsely claim upcoming infrastructure maintenance and urge users to “backup your vault in the next 24 hours.”
Image courtesy of LastPass
“Scheduled Maintenance: Backup Recommended
As part of our ongoing commitment to security and performance, we will be conducting scheduled infrastructure maintenance on our servers. Why are we asking you to create a backup? While your data remains protected at all times, creating a local backup ensures you have access to your credentials during the maintenance window. In the unlikely event of any unforeseen technical difficulties or data discrepancies, having a recent backup guarantees your information remains secure and recoverable. We recommend this precautionary measure to all users to ensure complete peace of mind and seamless continuity of service.
Create Backup Now (link)
How to create your backup 1 Click the “Create Backup Now” button above 2 Select “Export Vault” from you account settings 3 Download and store your encrypted backup file securely”
The link in the email points to mail-lastpass[.]com, a domain that doesn’t belong to LastPass and has now been taken down.
Note that there are different subject lines in use. Here is a selection:
LastPass Infrastructure Update: Secure Your Vault Now
Your Data, Your Protection: Create a Backup Before Maintenance
Don’t Miss Out: Backup Your Vault Before Maintenance
Important: LastPass Maintenance & Your Vault Security
Protect Your Passwords: Backup Your Vault (24-Hour Window)
It is imperative for users to ignore instructions in emails like these. Giving away the login details for your password manager can be disastrous. For most users, it would provide access to enough information to carry out identity theft.
Stay safe
First and foremost, it’s important to understand that LastPass will never ask for your master password or demand immediate action under a tight deadline. Generally speaking, there are more guidelines that can help you stay safe.
Don’t click on links in unsolicited emails without verifying with the trusted sender that they’re legitimate.
Always log in directly on the platform that you are trying to access, rather than through a link.
Use a real-time, up-to-date anti-malware solution with a web protection module to block malicious sites.
Report phishing emails to the company that’s being impersonated, so they can alert other customers. In this case emails were forwarded to abuse@lastpass.com.
Pro tip: Malwarebytes Scam Guard would have recognized this email as a scam and advised you how to proceed.
We don’t just report on threats—we help safeguard your entire digital identity
Cybersecurity risks should never spread beyond a headline. Protect your, and your family’s, personal information by using identity protection.
Kent Ickler // TL;DR: This post describes the process of building an active system to automatically recon SPF violations. Disclaimer: There are parts of this build that might not be legal […]
Kent Ickler and Derrick Rauch* // Sun Protection Factor Err… wait a second. Sender Policy Framework Ladies and Gentlemen of the class of 1997, Wear Sunscreen…I will dispense my advice, […]
Beau Bullock // Full Disclosure: Black Hills Information Security believes in responsible disclosure of vulnerabilities. This vulnerability was reported to Microsoft on September 28th, 2016. As of the publication date of […]
Gail Menius // My husband set me up with GPG and Thunderbird and it was too hard. Ethan said it was cool. Lots of people gave it good reviews. It’s […]

 Login