Het lijkt wel een soap rondom de iPhone-hacksoftware Coruna. Langzamerhand komt boven water wie het inzet, bij wie het gebruikt wordt en wie de mogelijke ontwikkelaar is. En het ziet ernaar uit dat de Verenigde Staten het zichzelf erg lastig hebben gemaakt.
Cybercriminelen gebruiken momenteel een nare en doordachte truc om wachtwoorden en privégegevens te stelen. Ze doen zich voor als een officiële beveiligingscontrole van Google, maar in werkelijkheid installeren ze kwaadaardige software in je browser.
De internetcriminelen die telecomprovider Odido hebben gehackt hebben alle resterende gestolen klantgegevens openbaar gemaakt. De hackers hadden eerder nog plannen om de data in delen vrij te geven om zo de aandacht van het publiek vast te houden, maar besloten uiteindelijk om alles in één keer te publiceren.
Odido heeft geweigerd om de cybercriminele groep Shinyhunters het geëiste losgeld te betalen. De groep dreigde met een deadline die Odido heeft laten verstrijken. Om te laten zien dat het menens is, zijn nu gegevens van honderdduizenden huidige en oud-klanten op het dark web gepubliceerd.
De hackers achter de datadiefstal bij providers Odido en Ben hebben zich bekendgemaakt. Het gaat om Shinyhunters, een cybercriminele groep die momenteel druk uitoefent op Odido om meer dan een miljoen euro te verkrijgen. Zo niet? Dan lekken ze de data.
Na de recente cyberproblemen bij Odido is nu ook RTL slachtoffer geworden van een hack. Afgaand op de eerste berichten van moederbedrijf RTL Group lijkt de schade echter mee te vallen. Althans, voor het Nederlandse deel.
Google has issued a patch for a high‑severity Chrome zero‑day, tracked as CVE‑2026‑2441, a memory bug in how the browser handles certain font features that attackers are already exploiting.
CVE-2026-2441 has the questionable honor of being the first Chrome zero-day of 2026. Google considered it serious enough to issue a separate update of the stable channel for it, rather than wait for the next major release.
How to update Chrome
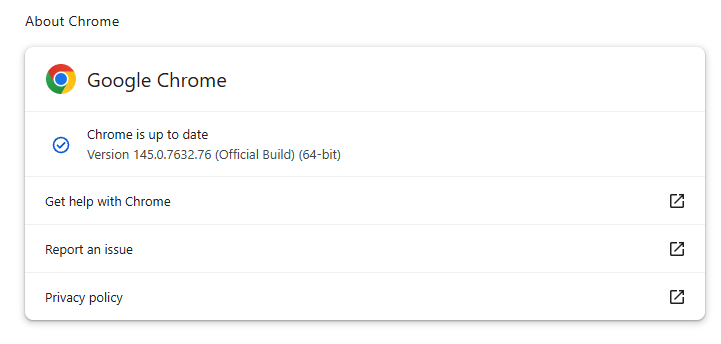
The latest version number is 145.0.7632.75/76 for Windows and macOS, and 145.0.7632.75 for Linux. So, if your Chrome is on version 145.0.7632.75 or later, it’s protected from these vulnerabilities.
The easiest way to update is to allow Chrome to update automatically. But you can end up lagging behind if you never close your browser or if something goes wrong, such as an extension preventing the update.
To update manually, click the More menu (three dots), then go to Settings > About Chrome. If an update is available, Chrome will start downloading it. Restart Chrome to complete the update, and you’ll be protected against these vulnerabilities.
Google confirms it has seen active exploitation but is not sharing who is being targeted, how often, or detailed indicators yet.
But we can derive some information from what we know.
The vulnerability is a use‑after‑free issue in Chrome’s CSS font feature handling (CSSFontFeatureValuesMap), which is part of how websites display and style text. More specifically: The root cause is an iterator invalidation bug. Chrome would loop over a set of font feature values while also changing that set, leaving the loop pointing at stale data until an attacker managed to turn that into code execution.
Use-after-free (UAF) is a type of software vulnerability where a program attempts to access a memory location after it has been freed. That can lead to crashes or, in some cases, lets an attacker run their own code.
The CVE-record says, “Use after free in CSS in Google Chrome prior to 145.0.7632.75 allowed a remote attacker to execute arbitrary code inside a sandbox via a crafted HTML page.” (Chromium security severity: High)
This means an attacker would be able to create a special website, or other HTML content that would run code inside the Chrome browser’s sandbox.
Chrome’s sandbox is like a secure box around each website tab. Even if something inside the tab goes rogue, it should be confined and not able to tamper with the rest of your system. It limits what website code can touch in terms of files, devices, and other apps, so a browser bug ideally only gives an attacker a foothold in that restricted environment, not full control of the machine.
Running arbitrary code inside the sandbox is still dangerous because the attacker effectively “becomes” that browser tab. They can see and modify anything the tab can access. Even without escaping to the operating system, this is enough to steal accounts, plant backdoors in cloud services, or reroute sensitive traffic.
If chained with a vulnerability that allows a process to escape the sandbox, an attacker can move laterally, install malware, or encrypt files, as with any other full system compromise.
How to stay safe
To protect your device against attacks exploiting this vulnerability, you’re strongly advised to update as soon as possible. Here are some more tips to avoid becoming a victim, even before a zero-day is patched:
Don’t click on unsolicited links in emails, messages, unknown websites, or on social media.
Enable automatic updates and restart regularly. Many users leave browsers open for days, which delays protection even if the update is downloaded in the background.
Use an up-to-date, real-time anti-malware solution which includes a web protection component.
Users of other Chromium-based browsers can expect to see a similar update.
We don’t just report on threats—we help safeguard your entire digital identity
Cybersecurity risks should never spread beyond a headline. Protect your, and your family’s, personal information by using identity protection.
Other noteworthy stories that might have slipped under the radar: AT&T and Verizon response to Salt Typhoon, AI agents solve security challenges, man arrested in Poland for DDos Attacks.
Criminals are using AI to clone professional websites at an industrial scale. A new report shows how one AI-powered network grew to 150+ domains by hiding behind Cloudflare and rotating IP ranges.
Google voegt ondersteuning voor slimme schakelaars en knoppen toe aan zijn Home-platform, zoals de Bilresa van IKEA. Gebruikers kunnen verschillende acties koppelen aan zo'n knop, zoals het dimmen van de lampen.
Why do successful phishing attacks target our psychology rather than just our software? Discover Unit 42’s latest insights on defeating social engineering and securing your digital life.
Russia's current isolation from the Olympics may lead to increased cyberthreats targeting the 2026 Winter Games. We discuss the potential threat picture.

 Login