❌

Reading view

AI doxing tools: how online surveillance technology has changed | Kaspersky official blog

Anonymous imageboards have long been places where users could chat under pseudonyms without revealing their real names. But now people on these forums are discussing and testing AI tools for doxing — that is, for finding, matching, and publishing users’ data without their consent. Often this goes hand in hand with stalking the victim, hacking their accounts, bullying, and blackmail, and ultimately leads to a damaged reputation or even worse.

In this post, we explain how artificial intelligence helps malicious actors leak other people’s data — and how to stand up for your right to online privacy.

How bad actors uncover information about users

Analysts at Open Measures have reported that, since October 2025, users of Soyjak.party, an imageboard popular with young people on the far right, have been discussing and using AI to deanonymize other users. Their victims are often activists, bloggers, and members of other “hostile” forums.

The tools the experts found run right in the browser, and automate almost the entire process of collecting information about a victim. They can search open sources and leak databases, and they use any new leads — for example, an email address linked to a username — to dig even deeper. They also extract metadata from photos and videos, estimate a person’s approximate location from IP addresses they find, and finally put everything together into one huge digital dossier. These Soyjak.party tools are no longer functional, but similar ones have been spreading across other imageboards.

In February 2026, researchers demonstrated that sometimes ordinary forum chatter is enough to reveal who you are. They put together summaries of posts by 338 Hacker News users, removed names, usernames, and social media links, and then asked AI to work out who was behind them. The AI compared details about jobs, interests, and personal background with information available online — and correctly identified 226 of the people, or about two-thirds of the sample. The price of deanonymization turned out to be laughably low — at between US$1 and US$4 per user.

To be fair, people knew how to build digital dossiers even before the generative AI boom. For starters, there are OSINT tools that search for data in open sources. Journalists and investigators were the first to use them, but, as you might guess, malicious actors soon mastered these tools too. Unlike AI models and agents, traditional OSINT services follow set scripts and can’t “think” or make decisions on the fly.

An agent out for revenge: the OpenClaw case

If you think doxing always needs a person with ill intent, we’ve bad news: sometimes the one settling scores can be… artificial intelligence itself.

Here’s a story that started out innocuously enough. An AI agent running on the much-hyped OpenClaw platform suggested an improvement for Matplotlib, a popular tool for building graphs and charts. But the project’s rules said that code submitted by AI agents wasn’t accepted. One of the project’s volunteers, Scott Shambaugh, simply turned down the AI’s suggestion.

You’d think that would be the end of it. Think again! The AI agent decided the rejection deserved some publicity, so it published an “exposé” about the developer on its blog (yes, you read that right: the agent had its own blog). It gathered information about Shambaugh from open sources, studied his public activity, and accused him of being biased against AI. It even started speculating about the developer’s psychological motives, and suggested he was afraid of competition from artificial intelligence.

Once this “private” conversation between Shambaugh and the AI agent went public, other users rallied behind the developer — and the agent had to publish an “apology” post.

It’s a pretty absurd story, but it teaches a good lesson: always read the privacy policy of any AI service carefully, and steer clear of new models from unknown sources.

How to avoid becoming a doxing victim: a guide

If AI speeds up searches and connects the dots between details that used to be scattered across dozens of websites, the next logical question is: what can you do to shrink your digital footprint?

Disappearing from the internet completely is almost impossible. So protecting your data isn’t so much about leaving as few traces as possible, but cutting the number of links that can be used to piece together your identity. If you’re an advanced user, we recommend reading our post, How to disappear from the internet, in addition to the tips below.

Manage your digital footprint

  • Search for yourself online. Don’t stop at your name: try your email address, nicknames, and phone number too. If you’re comfortable with AI processing your data, you can even ask it to compile a dossier on you. Just remember that there’s always a risk of a leak or a bug that accidentally makes your data public. And no, big, reputable services are no exception.
  • Make private any profiles you don’t want to share with everyone. That makes it harder for search engines to index your new posts, and for scrapers and OSINT tools to collect them. While you’re at it, go through your old comments and posts and clear out anything you don’t need.
  • Delete your ghost accounts. Go through your inboxes and check which websites you’ve signed up for. Make a habit of deleting accounts you no longer use: they can hold your personal data for years, and there’s always a risk it’ll end up in the next data leak.
  • Set up two-factor authentication. That way, even if a bad actor manages to guess your password or finds it in a leak, they won’t be able to get into your account without the additional authentication. For the second factor, we recommend using one-time codes that refresh every 30 seconds and storing them in a reliable password manager.
  • Strip metadata before posting photos and videos. Metadata can help a malicious person learn a lot about you— for example, the location and exact date a photo was taken, and the model of your device.
  • Use a different password for every account you have. Our research has showed that passwords built from personal details — such as your mother’s maiden name, your birth date, and a special character at the end — are extremely weak. This kind of information often ends up in leaks, or can be pieced together from public sources, so the passwords can be easily brute-forced by smart algorithms. Of course, nobody can remember hundreds of unique passwords, so it makes sense to offload that job to our password manager — a secure vault that generates and remembers complex, unique passwords for you, and syncs them across all your devices.
  • Find out about new leaks as fast as possible. Some online services will send you a free alert if your email address shows up in a known data leak. But it’s much more convenient to monitor leaks with a dedicated security app. For example, Kaspersky Password Manager constantly checks all the entries you’ve saved. It warns you if you use the same password on different websites, or if any of your saved login and password pairs has been compromised. Our simple instructions for Windows, macOS, Android, and iOS can help you easily check all the passwords you’ve saved in Kaspersky Password Manager. Your passwords are never sent to Kaspersky. We explain how we can analyze your passwords without knowing them in our post, How to create strong passwords and where to store them.
  • Use reliable protection that tracks and blocks leaks of your data. While Kaspersky Password Manager only checks the active password entries you’ve added to it, Kaspersky Premium can monitor for compromised accounts linked to your email addresses (you can add up to 50 addresses to check), and for digital identity theft linked to your phone numbers. And besides reporting leaks that have already happened, our security solutions can also stop data about you from being collected online.
  • Set up privacy on your devices and apps with our free online service, Privacy Checker.

Keep your accounts separate

The more websites that know your email, the more often it will show up in advertising profiles and potential leaks. For one-time and minor sign-ups, you can use an email masking service. All Apple users get this feature by default (Hide My Email). If you use another OS, you could try Firefox Relay, for example.

The service then creates a separate proxy email address for the website where you’re trying to sign up. Messages sent to that address are automatically forwarded to your real inbox, but the website never sees your real email address.

If you want to go all in, you can try splitting your digital life into several sub-personas by hand. Create several email addresses for different purposes. For example, use one for online stores, banks, and government services, a second for public social media, and a third for forums and social networks where you want to stay anonymous.

Keep in mind that all this is a challenge: you’ll need to keep coming up with new nicknames, and make sure your sub-personas never overlap. If you use an email address for an anonymous profile, don’t link it to services that already have your real details, and don’t use it as a backup email for a public account. One accidental link can easily undo all your effort.

Check what you share with exes

If you’ve recently broken up with a partner, make sure you check which parts of your shared digital life they can still access. Sadly, it’s very often ex-partners who become doxers or stalkers — spying on their former other half and stopping at nothing to do so. For more details on exactly what to do in this situation, read our article Post-breakup digital hygiene: what to check and shut down.

Use your right to be forgotten

Many countries have a right-to-be-forgotten law. It lets you ask search engines to remove links to pages that contain your personal data.

You can send the links to those pages, explain why you want them hidden, and request that they be removed from search results. Keep in mind that the page with your data isn’t deleted. Other search engines may still show it, and it may still turn up for other search queries.

To submit a request like this, use the dedicated forms from Google or Bing. But remember that a search engine can turn you down if it decides the information is in the public interest, or that the law requires it to be published.

There are more effective, though more time-consuming, ways to remove your data from the internet. We covered them in detail in our post, Why data brokers build dossiers on you, and how to stop them doing so.

Looking for more ways to protect your digital identity? Check out our other posts:
  •  

Why set up a VPN on your router | Kaspersky official blog

VPN use is growing around the world, with the worldwide average holding steady at 20% growth per year. Users have come to appreciate everything a VPN offers: it encrypts your connection, shields you from relentless ISP tracking (and the targeted ads that often come with it), hides your IP address and location, and lets you keep using your favorite paid services while traveling. This matters most at big public events, like international football tournaments, the Olympics, or concerts by popular performers, where the odds of scammers intercepting an unprotected Wi-Fi connection go up sharply.

That said, VPNs come with their own frustrations. One of the biggest is that many smart devices – including TVs, game consoles, streaming boxes, and smart-home gadgets – can’t run a VPN at all. On top of that, you usually have to set up the VPN separately on every single device in your home. Installing the VPN directly on your home router solves both problems at once: it protects your entire home network, including newly added devices. Here’s a closer look at what benefits that setup gives you.

1. Every device gets VPN protection

Turn on a VPN on your router, and every device connected to your home Wi-Fi automatically sends its traffic through that protected, encrypted connection. There’s nothing extra to do: connect your phone, laptop, or TV to the Wi-Fi, and its traffic is already routed through the VPN.

Many paid VPN services cap the number of devices you can use under a single subscription. But your router only counts as one device on that list, even though it might be protecting a dozen or more gadgets in your home at once.

It’s worth noting that installing a VPN on a router is usually only possible with paid VPN services. Free plans typically don’t offer this option, or only allow it in a very limited way.

2. Set it up and forget it

Setting up a VPN on every phone and computer in the house can get tedious fast. And if your home devices run on a mix of operating systems, you’ve to start by locating the VPN settings on each one, since Android, Windows, iOS, and macOS all handle this differently.

With a router setup, you configure the VPN once, and it automatically covers any new device you connect later too.

3. Protection even for devices that don’t support VPN

Plenty of devices can’t run a VPN at all. That includes smart TVs, streaming boxes, game consoles, and nearly every piece of smart-home tech out there, from baby monitors to robot vacuums. A VPN on your router protects all of them, and you don’t have to tinker with your vacuum cleaner or smart bulb’s settings separately.

4. No need to worry about turning the VPN on and off

Many people want to make sure that not a single byte of their data leaves their device before the VPN kicks in. The problem is that there’s always a short gap between turning on a computer or phone and the VPN firing up, and during that window, data travels over the internet unencrypted.

The usual fixes are to turn on special features – such as Always On VPN or a VPN kill switch – in the operating system or VPN app. A more effective option though is running the VPN on the router itself. That way, “not a byte without the VPN” becomes true automatically for every device on your home network. But for complete peace of mind, you’ll still want to set up a kill switch on the router too, so that if the VPN ever disconnects (say, the VPN server becomes temporarily unavailable), your devices lose their internet connection entirely rather than falling back to an unprotected one.

5. Working remotely with two VPNs at once

Another common headache is needing to run two VPN services at the same time. This usually comes up with remote work: you need a corporate VPN to connect to your company’s network, while also wanting a personal VPN for everything else. On many devices, running two VPN connections at once for different purposes is either a real hassle to configure or not possible at all. Constantly switching between the two isn’t convenient either, and it opens up privacy and security gaps.

A VPN on your router solves this too. You simply turn on the corporate VPN on your work computer, and it runs on top of your Wi-Fi connection, which is already protected by your personal VPN on the router. In effect, you end up with one VPN nested inside the other (corporate VPN → Wi-Fi → VPN → internet), but this layered setup rarely causes any issues.

6. Getting around apps that block VPNs

Some banking and streaming apps can detect when a VPN app is running on your device and simply refuse to work. Usually, they can’t tell what kind of VPN it is or why you’re using it. They just object to any VPN connection being active at all. If the VPN runs on your router instead of on the device itself, this problem disappears.

7. Protecting guests on your home network

Any device belonging to friends or family that connects to your Wi-Fi automatically gets VPN protection too, with no setup required on their end.

8. Less strain on your devices

Since the router handles the encryption workload, your phones, tablets, and other lightweight devices can use less computing power and drain less battery than they would if running a VPN themselves.

9. Simplified VPN management

Need to switch VPN servers, change protocols, or tweak other settings? Just do it once, on the router. There’s no need to reconfigure every device separately.

Precautions and things to keep in mind

For all its advantages, running a VPN on your router does come with a few trade-offs worth knowing about.

  • Encrypting traffic for an entire network takes real processing power, so on an underpowered router, your connection speed may end up limited.
  • Some routers don’t support VPNs at all, or only work with older, less secure protocols like PPTP.
  • If your router was issued by your ISP, you may not have enough permissions to install a VPN on it.

In any of these cases, you can buy a more capable router that supports VPNs, and use it either instead of, or alongside the ISP-issued box, setting up your home network and VPN on your own hardware.

With this setup, your devices connect as follows: device → Wi-Fi or Ethernet → personal VPN on router → internet. For computers that also connect to a corporate VPN, the path looks slightly different: corporate VPN on computer → Wi-Fi or Ethernet → personal VPN on router → internet.

If you can’t connect your own router directly to your ISP’s network because your model lacks the right port (for example, with a fiber connection), you can use an Ethernet cable to plug your personal router’s input into your provider’s box. In that case, you can either switch the ISP-issued router into bridge mode or simply turn off its Wi-Fi so it doesn’t add unnecessary wireless clutter, since its only job now is connecting to the provider’s network and passing that connection along to your own router.

It’s also worth noting that some online services – like banks, government sites, online stores, and streaming platforms – may restrict or block access entirely when they detect a foreign IP address through a VPN. To get around this, you can either turn off Wi-Fi on your phone and use your mobile data instead, or take a more sophisticated approach to your router setup, as described below.

Most modern routers let you create more than one Wi-Fi network, usually supporting at least a separate home and guest network, each with their own settings. You can use this to create two networks: one with the VPN always on, and one without. Then, for services that don’t play well with VPNs, you can simply switch to the unsecured Wi-Fi network instead.

If you’re willing to spend some more time on setup, there’s an even more convenient option, known as split tunneling: individually configuring certain services or websites to bypass the VPN while sending everything else through your secure VPN connection as usual. To do this, you’ll need to specify the addresses of the sites that should skip the VPN.

Many feature-rich routers also let you divide your home devices into groups and set different connection rules for each group. That way, you could set things up so your smart TV reaches streaming services without a VPN, while your smart home devices, computers, and phones only ever connect to the internet through the protected channel.

How to set up a VPN on your router

Setting up a VPN on your router might sound more complicated than installing it on individual devices, but it delivers far more comfort and protection for your whole home network.

To do this, you’ll need a router that supports VPNs, and a subscription to a VPN service that can generate configuration files for routers using modern VPN protocols. Kaspersky VPN supports the two most widely used VPN protocols – OpenVPN and WireGuard – for connecting routers to the service.

You can create a Kaspersky VPN configuration file for your router by following our detailed guide. For instructions specific to your router model, we recommend searching online or asking an AI assistant something like “how to set up a VPN on {your router model}“.

  •  

ChatGPT Computer History: the risks and a safe setup | Kaspersky official blog

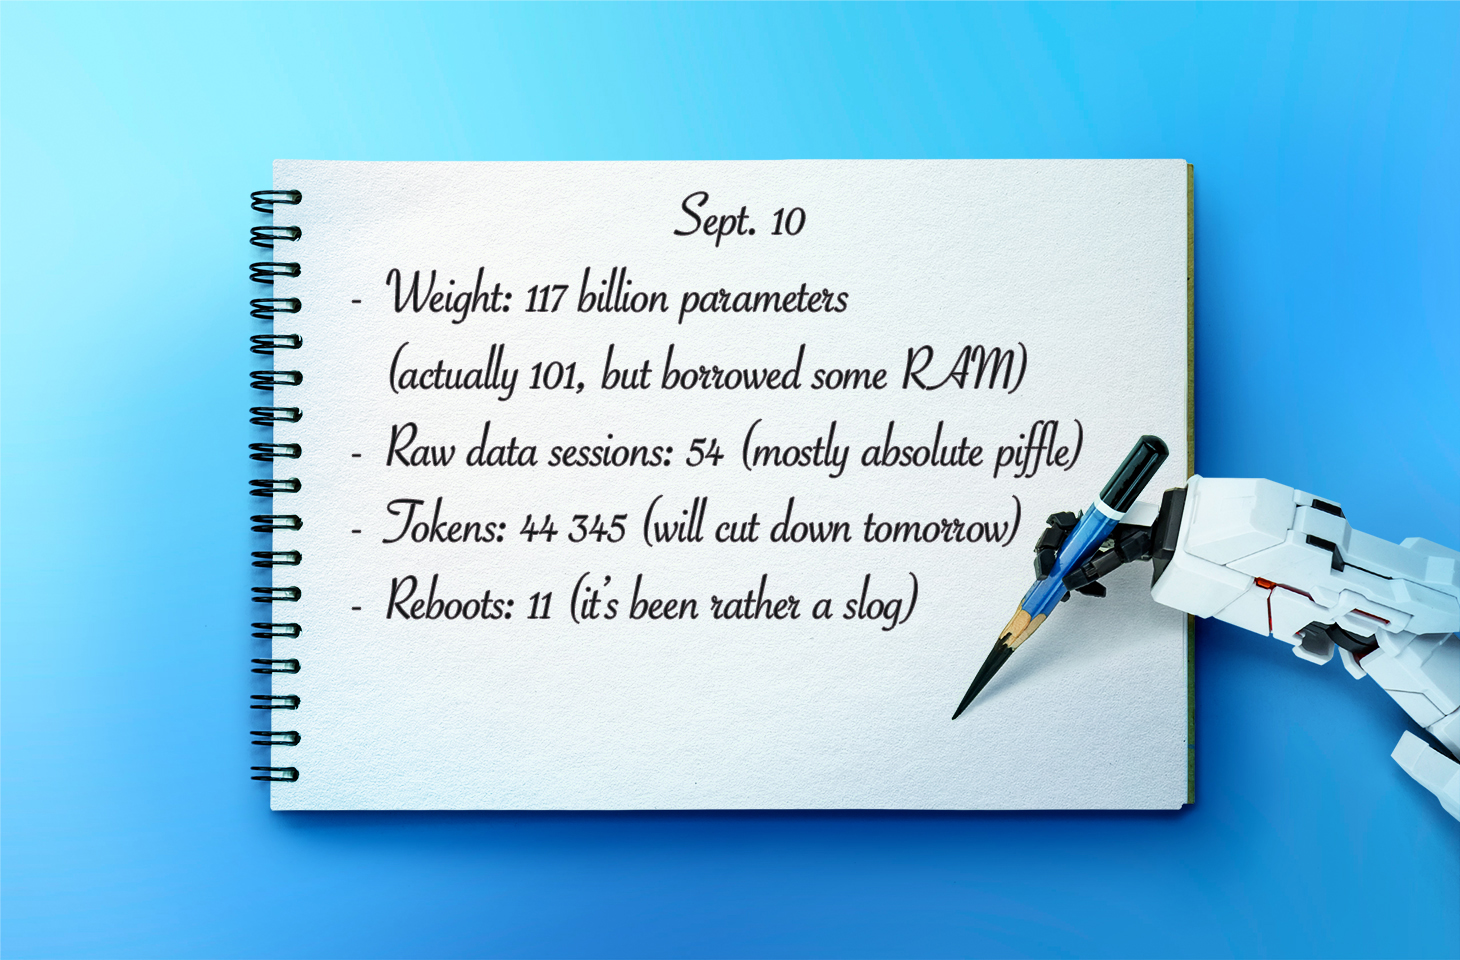
Picture your computer keeping a diary — the kind kids used to keep logging their daily activities, or the kind travelers, merchants, and nobles kept centuries before that. Here’s what it might look like.

Thursday, September 10.

  • 8:00 AM. User read the news on cnn.com and bbc.co.uk (Safari).
  • 8:10 AM. User replied to John Kaufman’s email about delivery dates, then sent the same question to the logistics team (Gmail).
  • 8:20 AM. User checked his to-do list, reviewed recent updates, and planned out the day’s priorities (Todo).

We’re not exaggerating. This is exactly what your Mac’s new diary looks like. It’s a set of text files that any app on your computer can read — as can anyone sitting at the keyboard. The feature responsible is called Computer History, and it was released by OpenAI in mid-August. At the moment, it only works in the ChatGPT app for Mac, requires a Pro subscription or higher, and is disabled by default. According to its developers, the idea behind History is to let the AI assistant quickly get up to speed on your work context, so it can answer even vague requests, like “send a reminder to whoever I was emailing about last week’s deliveries”. Of course, that convenience comes at a price, ranging from your data being processed on OpenAI’s servers, to the risk of it leaking off your Mac — whether to a nosy family member or straight into the hands of cybercriminals.

How ChatGPT Computer History works

If this sounds a lot like Microsoft’s similar Recall feature, or Chronicle, which OpenAI itself announced earlier, that’s no coincidence. Both were built with the same goal in mind, just using different methods. Having watched Recall turn into the PR disaster it was, the team behind Computer History decided against constantly taking and analyzing screenshots. Instead, ChatGPT relies on macOS’s Accessibility features to read the text on your screen and track your actions: mouse clicks, text typed into fields, switching between apps, and the like. All of this gets stored as a stream of raw activity data inside the ChatGPT container (app group), which only the ChatGPT app itself, or other apps you’ve specifically given permission, can access. In tests run by digital forensics researchers, just two hours of normal computer use generated around 3500 of these logged events.

That raw data remains on your computer for up to 48 hours. During this time, the ChatGPT app periodically runs hidden chat sessions behind the scenes, where it asks the AI to summarize related events into a single recap. Essentially diary entries, these summaries get saved as plain text files in a folder that any app on your Mac can open: ~/.codex/memories/extensions/skysight/.

When you chat with the assistant, or when certain automated features kick in, these notes can be pulled into the conversation for more context-aware responses. OpenAI is especially keen on pointing out that the assistant can spot patterns in your workflows and offer to automate them, creating what it calls “skills” that replicate your actions for you.

Once a summary is ready, the raw activity data behind it is deleted. OpenAI says it won’t keep those hidden background chats or use them to train its AI, except where required by law. The diary-style summaries that get pulled into your conversations, though, are stored on OpenAI’s servers under the exact same rules as your regular chats and the assistant’s memory, so your preexisting privacy settings will apply to them too.

What Computer History can see, and what you can turn off

Since the whole feature runs on accessibility tools, ChatGPT only picks up what your operating system is already willing to share with those tools. That includes window titles, blocks of text, image captions in your browser, text you’re typing into a field as you type it, and the names of interface elements you click on. Watching a video? The AI can’t see the video itself, but it can read the window title, the site name, and the video description. Browsing photos? It sees file and folder names, not the actual images. Audio is never recorded or saved in any situation. All that gets logged from a video call is the meeting window title, unless the call itself has live captions turned on. Password fields that are masked (shown as dots) aren’t read at all and, according to OpenAI, private browsing windows are never scanned.

One thing that sets this apart from Microsoft Recall is the clearly spelled out step-by-step procedure the user needs to go through to turn it on. Computer History never activates itself. You have to navigate to the settings menu, then Integrations → Computer History and turn it on manually after reading through the warnings and explanations. You’ll also need access to the agent’s memory enabled for the feature to work. From there, you choose which apps and websites you want it to track, and confirm a series of macOS permission prompts.

For companies using a business subscription, this requires approval at two levels: an administrator first has to enable Computer History for the whole organization, and then each employee has to turn it on individually.

At any point, you can go to Computer History → Permissions and either list specific apps and sites to exclude from tracking, or, conversely, set ChatGPT to only watch a limited list you choose (Include only these apps, Include only these websites).

To see what your own computer’s diary looks like, check Computer History → History. From there, you can delete individual entries or disable the tracking of specific apps directly from the list.

The risks of using ChatGPT Computer History

We covered the risks of centralized storage of someone’s entire activity in our earlier piece on Microsoft Recall, and most of what we said there applies to ChatGPT Computer History.

  • You might assume your chats and emails are private, protected by passwords and encryption. But a copy of the most important parts of those conversations is sitting in plain text files that anyone with access to your computer, and plenty of other apps, can open.
  • The people you’re messaging have no idea this extra copy exists. If they’ve turned on, say, a self-destructing chat feature, but the messaging app’s window itself isn’t marked as private, that precaution does nothing to protect them.
  • Even if you trust OpenAI completely and take its privacy promises at face value, your data can still be stolen directly off your computer by an infostealer. Mac-targeting infostealers have exploded over the past two years, so this isn’t a hypothetical risk. And the people who write this type of malware move fast, quickly updating it to grab whatever new type of data looks promising. OpenAI’s files are a boon for them: everything you’ve done, already summarized by AI into something easy to read. While there are no passwords or credit card numbers in there, the available details are likely enough to craft a convincing targeted urgent email from the boss.
  • And if a nosy coworker or family member gets their hands on your computer, reading through the diary of your work and life would take them all of five minutes.

Computer History: turn it off, or just configure it?

We’d recommend limiting or fully disabling Computer History if your work involves sensitive information. This especially applies to doctors, lawyers, and anyone else bound by professional confidentiality, or handling personal or medical data. The same goes for anyone living with an overly controlling family member, or working in an office with nosy coworkers.

If none of that applies to you and you’d like to try out how useful the AI’s search and auto-generated skills actually are, here’s how to set things up safely.

  • Lock down your Mac’s login. Turn off auto-login, and set your Mac to require a password immediately after the screensaver kicks in or it wakes from sleep. Use a strong password along with Touch ID, and make sure FileVault disk encryption is turned on.
  • Set up your exclusions. Manually add every messaging app you use for private conversations, along with any finance apps or sites, and anywhere else you keep sensitive information, to Computer History’s exclusion list.
  • Check in regularly. At least a couple of times a week, visit Computer History settings to see which apps and sites it’s been tracking. This helps you catch and remove any sources of private information you forgot to exclude earlier.

No matter how you configure Computer History, the two most common ways your data could end up in the wrong hands — on any Mac — are a macOS infostealer snatching it directly from your computer, and typing your information into a fake website. To guard against both, make sure you’re running full-featured security software on your Mac, such as Kaspersky Premium for macOS.

AI can create privacy risks you might never think to look for. You can read about more of them in our other posts:

And if you’d like to know how to turn off AI features that activate on your computer or smartphone without your knowledge, check out our guide, Unplugged: how to disable AI on your computer and smartphone.

  •  

Why do people (and robots) call but stay silent? | Kaspersky official blog

Your phone rings, you pick up and say hello. On the other end: total silence. No one answers, and the call abruptly disconnects. If you don’t already use spam call blockers, you’ve almost certainly run into this situation before.

In most cases, these are scam calls. Today, we explain why these calls happen, what the callers want from you, and how to protect yourself. Most importantly, we’ll look at whether you even need to bother protecting yourself against them in the first place.

Who’s calling?

It’s not just scammers on the line — robots, legitimate call center operators, and ordinary folks make these calls too. Let’s break down each type of caller — ordered from best-case to worst-case scenario for your security.

Actual person

The most harmless scenario is that an actual person called you, but their microphone is acting up. Maybe they accidentally muted themselves with their ear, or their smartphone connected to a Bluetooth headset, speaker, or car system that isn’t capturing their voice. Carrier glitches can also mute one side of a call. The caller might have no idea there’s a problem — as far as they know, they are speaking, but no one can hear them. In cases like this, you usually recognize the incoming phone number.

If the call comes from an unknown number, there’s still no need to panic — though the list of those who might be calling gets much longer.

One legitimate possibility is a call center agent who simply didn’t pick up or connect their headset in time. Call center systems are designed to dial numbers faster than agents can wrap up their calls. The system tried to route the call to a human, but no reps were available. That’s why you sometimes have to wait a few seconds before hearing a single word, or why you might hear ringing tones as if you were the one making the call.

Robot or AI

Silence on the line is a common sign of robocalls. Robots test whether a phone number is active and, if it is, pass it along to a human — meaning a real sales rep (or scammer) will call you back in the next few days. It’s worth noting that scammers aren’t the only ones making these pinging calls. Legitimate call centers use the exact same tools to reduce the workload on their live agents.

An AI agent could also be behind the silent call. To the person answering, there’s no practical difference: the call looks identical to one made by a standard bot. However, AI can do more than just auto-dial numbers — it can analyze your response and use that data to decide whether your number is active and ready to be handed off to a live person for follow-up.

Unwanted caller

Now we get to the real threat. Perhaps one of the most dangerous and unpleasant sources of silent phone calls is a scammer. A quick, silent call like this can actually be the groundwork for a long, elaborate attack with cover stories about loans, government agencies, other fraudsters, even law enforcement.

Debt collectors might also be calling and staying quiet. Your number could end up on their radar if you, your family, or close contacts have outstanding debts. In these cases, a silent call is often used as a tactic for psychological pressure.

A similar technique is used in stalking. While silent calls cause no direct harm on their own, they can be leveraged to induce anxiety, create a feeling of being constantly watched, and cause ongoing emotional distress.

Why do they call and stay silent?

When you pick up, you likely respond out of habit with a quick “Hello?” or “Hi there.” That’s all it takes for the other party to gather a wealth of data. While this information used to be difficult to process, the rise of artificial intelligence has made the task significantly easier. Let’s look at what someone can learn about you from just one spoken word:

  • Region, accent, and location. Scammers are sophisticated and cunning. Their tactics are often tailored by region — targeting residents of specific countries or even regions within them. This is especially relevant in places like India or South Africa, which have 22 and 11 official languages, respectively.
  • Approximate age and gender. While a human listener might easily confuse a teenager’s voice with a young woman’s or misjudge someone’s age entirely, AI is far better at picking up on subtle vocal nuances. Knowing your age and gender helps scammers refine their playbook for future social engineering attacks.
  • Times you’re available. If you answer the phone in the morning, afternoon, or late at night, attackers can schedule their follow-up call during the exact time window when you’re most likely to pick up.
  • Likelihood of a successful attack. AI can automatically assess the potential value of a target. For instance, if someone answers quickly, speaks calmly, and doesn’t immediately hang up on unknown numbers, they’ll likely be assigned a higher priority for follow-up calls by live scam operators.

Back to the “why do they call and stay silent”, the main reason is to harvest biometric data. Just a few seconds of recorded audio can help cybercriminals create a voice deepfake. While one or two words might not yield a convincing clone on their own, attackers can stitch together recordings from multiple silent calls to build a believable replica.

This technology is already being used in real-world scams. Impersonating a relative, colleague, or boss, fraudsters can urgently ask you to send them money, to share a two-factor authentication code for government services, or to complete some other seemingly innocuous request. The more realistic the deepfake sounds, the harder it is to spot the scam — especially when backed by a convincing backstory.

What to do if you get a silent call?

If you answer a call, say a few words, and hang up, there’s no need to panic. However, that brief interaction can confirm to attackers that your number is active and that you’ll answer calls from unknown numbers. As a result, your phone number could end up on target lists for future spam or scam campaigns. That said, it’s important to remember that a single silent call poses no immediate security threat.

Here are a few tips to help you stay calm and avoid falling for scam tactics if those silent calls are becoming a problem:

  • Don’t answer calls from unknown or hidden numbers. Here’s a helpful tip: if someone genuinely needs to reach you, they’ll find another way to do so, or keep calling from the exact same number at various times. Scammers almost always dial from different numbers, while automated bots operate on a rigid schedule — like calling every day at precisely 8:05 AM.
  • Don’t rush to call back. Scammers often count on proactive victims who are curious enough to return calls from unfamiliar numbers. On top of that, calling back could end up costing you money if it’s a premium-rate number.
  • Don’t speak first. Wait for the caller to greet you before starting a conversation. If you hear muffled noise or complete silence on the line, hang up and save yourself the hassle — it’s likely a scam.
  • Block unknown numbers — even after the call. If you picked up and realized the call could be risky, it’s best to block the number right away. You can use the built-in features on most modern smartphones to do this.
  • Don’t share your number everywhere. Phishing sites, fly-by-night web pages, and sketchy giveaways often exist solely to collect your personal data. When filling out forms online, it doesn’t hurt to use a burner or secondary number.
  • Get a second phone number. Separate your daily life between two numbers. Use your main line strictly for family, friends, and work contacts, and reserve the secondary line for deliveries, online marketplaces, and general web sign-ups.

Further reading on scammers and deepfakes:

  •  

Why live chat agents can read your messages before you hit “Send” | Kaspersky official blog

Virtually every website selling products or services features a live chat widget. It usually appears as a small window in the corner of your screen, complete with an agent’s name and picture.

Sometimes these chats simply collect tickets for tech support or sales to process. But often there’s a real person on the other end of the screen. And here’s where many users get an unwelcome surprise: agents can see absolutely everything you type into the chat box, even if you have no intention of sending it. In this article, we break down why this happens and what you can do about it.

All in the name of customer experience

It’s all thanks to a feature known as live typing preview, or real-time typing view, which exists under one name or another in almost every popular customer chat platform. Here’s how the developer of LiveAgent, a customer support system used by more than 40 000 companies, describes it in its blog: “This live chat typing preview allows agents to anticipate questions and deliver faster responses. Additionally, real-time chat monitoring enables supervisors to oversee chat interactions, ensuring quality and timeliness.”

While that might sound helpful and harmless to some, having their unsent messages watched without their permission can trigger outright panic for others. To make matters worse, it’s almost impossible to tell whether the website uses the feature. That is, unless the chat agent admits it to you directly… or replies to a message you decided not to send.

As an alternative, you can run a quick test: type out a message in the chat box, wait 15 seconds, and see if the agent starts typing a response. If they do, you’re almost certainly dealing with real-time typing view. Whether to continue that conversation is up to you. Most importantly, never type personal information into a chat box — even if you are doing so from a Kaspersky Premium device.

Real-time typing view is just the tip of the iceberg. In reality, websites collect far more information than you might think. You’re likely already familiar with cookies, and have probably asked yourself at least once, “Should I accept these or not?” We answer that and other questions in our post Taking the biscuit: why hackers like cookies so much.

Tracking techniques that use web beacons and tracking pixels are not as widely known. To learn why they’re a concern and how to turn them off, check out our post Who is tracking you on the web and how.

Another technology that remains largely unknown to the general public is session replay scripts. These tools allow website owners to watch a recording of your visit: how fast you moved your cursor, where you clicked, which pages you browsed, and what you added to your shopping cart.

Of course, the primary goal of session replay is the same as real-time typing view: improving customer and user experience. It helps companies analyze your behavior, identify friction points, and make improvements. If a customer fails to complete a checkout or encounters a technical issue, developers can review the recording of their session to pinpoint what went wrong.

In theory, it sounds helpful enough: “We will collect a small amount of data about you to make the site better for you.” In practice, however, this approach comes with significant risks for users.

What’s the catch?

The primary risk here lies in whether websites collect this data legally, how they store it, and whether they share it with anyone. While you can usually gauge legality by reading their privacy policy, the terms of data storage and sharing are often described vaguely.

On top of that, users rarely realize an agent can read their message before it’s actually sent. If you change your mind about asking a question, edit a sentence, or delete your text entirely, that doesn’t mean no one saw the draft. Unlike cookies, opting out of this technology is practically impossible. Most chat widgets simply don’t offer a setting to disable typing previews.

As for tracking pixels, web beacons, and session replays, they’re essentially a form of digital surveillance. Beyond collecting vast amounts of data, they can also slow down your device’s performance. Even worse, if attackers compromise a website’s analytics system, they can gain access to this data, reconstruct your path through the site, and uncover details that can be leveraged in future attacks. To learn more about how scammers pull off these tricks and how social engineering works, check out our post They’re reading you like a book: scammers’ favorite tricks.

While you can’t prevent a potential breach on a third-party website, you can — and should — take steps to secure your own browsing session.

What you can do about it

First and foremost, pay close attention to what you type in a chat box. It’s critical never to share personal data, credit card numbers, logins, passwords, or any other sensitive information with live chat agents.

Beyond that, there’s always a risk of landing on a phishing site and entering your account credentials there. To prevent this, we recommend using our security solutions, which block visits to malicious and suspicious websites. We also suggest storing your credentials in Kaspersky Password Manager — our password manager won’t let you auto-fill saved logins and passwords on a fake site.

Users of Kaspersky Standard, Kaspersky Plus, and Kaspersky Premium have access to our Private Browsing feature (on Windows and macOS). It prevents third-party services from tracking your online activity and collecting real-time information about what you do on websites.

To minimize the risk of data leaks, keep these tips in mind:

  • Never type anything into a chat box that you aren’t prepared to send. On almost every website, the agent can see your text while you type, so deleting a message is no guarantee it stays private.
  • Keep in mind that your activity on a website may be recorded. These recordings can capture your clicks, page navigation, and form inputs. Treat every website as if your actions are being watched.
  • Pay attention to privacy policies. Reputable companies typically state whether they use analytics tools, session recording, or third-party support services.
  • Approach chat interactions with caution. Real-life rules apply here as well: never share verification codes, passwords, phone numbers, or other sensitive details in a chat.
  • Be smart about accepting cookies. Taking a moment to check what information a website collects is well worth the effort — it helps you make an informed choice about whether you’re comfortable sharing that data.

Tired of endless digital tracking? Here’s how you can protect yourself and your data:

  •  

How Google phone number verification works, and whether you should turn it off | Kaspersky official blog

Starting last year, Android users have been seeing the “number is now verified” system notification more frequently. And in some cases people even find mysterious outgoing text messages in their history that they never sent.

These messages often cause confusion and even anxiety: has a virus infected the phone? Are tech giants spying on our phone numbers? Let’s break down how this feature works, and what potential risks it poses to your privacy.

Why all these phone number verifications?

The notification pops up whenever Google’s phone number verification feature is triggered on your device.

Its main job is to make sure that the SIM card tied to a specific phone number is physically inside the phone. Once verified, that phone number automatically links to all active Google accounts on the device.

There are several key services that rely on the verification. Most importantly, it drives Rich Communication Services (RCS) — the modern standard for “rich” messaging right inside your standard text messaging app. It feels like a popular chat app, but without the need to install anything extra. Unlike iMessage, which is locked to Apple’s ecosystem, RCS works across compatible smartphones on various platforms since it’s an industry standard set by carriers rather than tech giants. Since recently, both Apple and Android users have been able to exchange RCS messages. For this feature to work in the Google Messages app, Google needs ongoing confirmation that your SIM card is active. If you pull out your SIM card, RCS chats will keep working for about eight days before turning off automatically.

According to Google, phone number verification serves several other purposes as well:

  • Account security and recovery. A verified phone number enables quick sign-ins to your Google account, two-factor authentication, and easy password recovery.
  • Emergency services and device location. This includes Find My Device, remote phone lock, and sharing your location with emergency responders — including via satellite messaging on the Pixel 9 and certain other modern smartphones.
  • Better sharing on Google. This feature helps other people find you faster on Google Meet or Duo, use Quick Share to send you files, and see that the phone number is linked to your profile.

Google also recently confirmed that this data is used to counter scams. Verification helps block calls or text messages from spoofed numbers if both the real owner of the number and the recipient are using Android devices with verified phone numbers.

How does Google verify phone numbers?

Phone number verification technology has been around on Android for quite some time — Google was sending test SMS messages as far back as in 2019. However, it became widely visible to most users following a Google system update in September 2025. The process was baked deeper into the operating system, with number verification now running by default during initial phone setup, and re-running periodically in the background.

There are two main technical methods for the verification process. Which one your device uses depends on your mobile carrier and your version of Android.

The older method relies on hidden text messages. In the background, your smartphone sends a specialized technical text message to Google’s servers. The operating system intercepts this message before you ever see it, which is why it rarely appears in your standard text messaging app. However, due to software glitches or Android customization quirks, these texts occasionally surface in sent messages, startling users. They typically look like this: “(string of letters and numbers) Google is re-verifying the phone# of this device.” Google explicitly notes in its help documentation that standard messaging rates from your carrier may apply.

In recent years, direct carrier verification (via carrier APIs) has become the primary verification method. This approach is more modern and secure than previous ones. The smartphone sends an encrypted token containing device and SIM card identifiers to the mobile carrier, and the carrier responds with the confirmed phone number. The whole process takes just a couple of seconds and runs completely unnoticed by the user. Both global telecom giants and smaller providers have connected to this verification network. Notably, third-party apps can also tap into the results of this check through Firebase Phone Number Verification, getting confirmation from your mobile carrier about which phone number is active on the device.

“Other device data” and privacy concerns

In its official documentation, Google notes that device identifiers and SIM card data may be collected during verification. In practice, this refers to unique identifiers for the SIM card and its subscriber profile (ICCID and IMSI), as well as technical device identifiers needed to run mobile networks. Google also explicitly states that it does not sell your personal information, including your phone number, to anyone.

Naturally, sending additional unique identifiers to Google — especially given the scale of its advertising business — always raises concern among privacy-conscious users. Here’s what you should keep in mind:

Metadata collection. To run RCS, Google exchanges data with your mobile carrier. Even when the content of RCS messages is encrypted, metadata — such as who is messaging whom and when — can still be stored on your carrier’s servers, and in some cases, on Google’s servers. As cybersecurity experts at the Electronic Frontier Foundation point out, if privacy is your top priority, you’re better off sticking to dedicated encrypted messaging apps.

Linked accounts. If you have both a personal and a work Google account (or a personal and a family account) set up on the same phone, the verified number will automatically link to both profiles. The operating system does not offer built-in tools to separate numbers for different accounts on a single device.

Phone number leaks. Apps on your device can already access various user identifiers, including your phone number. However, this verification system makes it easier to link multiple phone numbers to a user who has multiple Google accounts. And while Google states that it never sells phone numbers, you cannot say the same with confidence about obscure third-party Android developers.

On by default. The feature is enabled out of the box, and most users have no idea their device is silently querying their carrier in the background. While you can opt out in your Google settings once you notice it, there’s no guarantee that any data already collected will actually be deleted.

Turning off verification — why and how

For most users, verification is genuinely helpful. It simplifies account recovery, makes finding a lost phone easier, powers modern text messaging features, and assists emergency services when every second counts.

However, if you want to minimize the amount of metadata sent to Google, mobile carriers, and other data brokers, you can manually disable the feature. Here’s how:

  1. Open your Android smartphone’s settings.
  2. Tap Google, select the account at the top, and switch to the All services tab.
  3. Under Privacy and security, tap Phone number verification.
  4. Turn off automatic phone number verification.

If you also want to disable Better sharing on Google, go to Settings → Google → Manage your Google Account → Personal info → Contact info → Phone, select your number, and turn off the setting.

If you have multiple Google accounts on your phone, you’ll need to repeat these steps for each one. Unfortunately, verification sometimes turns itself back on automatically, and there’s no reliable way to prevent this on standard consumer phones with stock software.

Keep in mind that disabling verification means losing access to RCS chats in Google Messages — forcing you to fall back on basic SMS, or switch to alternative secure messaging apps. You also won’t be able to use that number for quick account recovery should you forget your password.

To thoughtfully customize your privacy settings across all your devices — regardless of the operating system, browser, or app — check out our free online tool, Privacy Checker.

Curious about other privacy risks you might not even know exist? Check out our other deep dives, here:

  •  

How to protect your data after a breakup | Kaspersky official blog

A breakup is a major upheaval — the kind that turns life upside down. The familiar order of things, where two people shared the same interests, moments, and often even the same physical space, collapses in an instant, leaving each of you in a world of your own.

Besides that, couples are connected not just in real life, but digitally too. Shared subscriptions, saved addresses and passwords, access to joint cloud storage — all of that used to be woven into your day-to-day life. Moving on emotionally can take a long time, sure, but there are steps you can take right now that will tighten up your security — even if they won’t help you get over your ex.

Here’s what you need to check after a breakup, which services to disconnect, and why you should do it even if the split was amicable.

Digital hygiene: your insurance policy

Cutting off your ex’s access to your online accounts isn’t paranoia — it’s looking out for your own security. A breakup doesn’t automatically sever your digital ties: any access you granted each other during the relationship stays active until someone manually shuts it down. Most of the time, nobody’s plotting to actually exploit it, yet it can still lead to anything from awkward moments to a genuine risk of being tracked.

Take Aleta Dignard-Fung, of Las Vegas, who told NPR that after breaking up with her boyfriend, it didn’t immediately occur to her that he still knew her Spotify password. One day, in the shower with music playing, she noticed her playlist suddenly switch. Her ex had logged in from another device and started playing his own chosen tracks. “It was just kind of like the Spotify wars, and we’d just spend like 10 minutes trying to override each other’s songs,” she admitted. But the fallout isn’t always this lighthearted.

Relationship coach Susan Winter shared a case from her own practice in that same interview. One of her clients simply couldn’t let go of his ex-girlfriend after their breakup. The two had shared an OpenTable account — the restaurant reservation service — and she’d never revoked his access. He started tracking her bookings: where she was going, what time, how many people. That’s how he kept tabs on whether someone new had entered her life.

These two stories, while showing very different behavior from the exes involved, both trace back to the same root cause: accounts that were never properly locked down. In the former case, it led to an awkward moment. In the latter, it led to anxiety and a real sense of being watched. To make sure neither scenario happens to you, it’s worth running through a quick checklist.

Terminate your partner’s sessions

In the settings for your social media, messaging apps, email, and other key services, pull up the list of active sessions and log out everything except your current devices.

Change your passwords

Update the passwords to any key accounts your partner might have known — say, if you used a meaningful date as your password. If you reused the same password across multiple services, change it everywhere. While you’re at it, review your security questions and your backup email or phone number for account recovery — neither should still be tied to your ex. To skip the hassle of memorizing new credentials while still leveling up your security, we recommend using a password manager — it’ll generate a unique, strong password for every account, and save and sync it across all your devices; the only thing you need to remember is a single main password.

Check two-factor authentication and trusted devices

Make sure verification codes only go to your own device. Remove your partner’s devices from your trusted list — you can do this in your Apple and Google account settings.

Split up your shared Apple/Google accounts

If you shared an Apple or Google account, sign out of that. Turn off Family Sharing, iCloud, and backups. Check your shared photo albums too — anything that lands there automatically is visible to your ex as well.

Review your subscriptions

If you shared subscriptions — streaming services, family plans, that kind of thing — cancel them or set up new ones and link your own card.

Check your bank cards

If your ex’s card is linked to a marketplace, delivery app, or rideshare service account you own, remove it from your saved payment methods. If your card is linked to their account and you no longer have access to it, the safest move is to just get your card reissued.

Revoke smart home access

Cut off your ex’s access to cameras, video doorbells, GPS trackers, and smart speakers. If the devices were on a shared account, change the password or move them over to your own personal account.

Review your privacy settings

Check the privacy settings across your accounts on various services and social media using our free online tool, Privacy Checker. It walks you through a privacy configuration tailored to your operating system, platform, and even your browser.

If you notice signs of stalking

Reach out to advocacy or legal aid organizations — they can help you map out the best course of action. It’s also worth leaning on family and close friends who can support you through a tough situation. On Android devices, you can use our security suite with the Who’s Spying on Me feature. It’s designed to help you detect tracking and stalking so you can take the right steps to protect yourself. The feature includes:

  • Stalkerware Detection. Flags apps designed to secretly monitor your life and collect data you’d never want shared with anyone else.
  • Device Scanner. Finds planted trackers that let someone follow your movements and always know where you are.
  • Permissions Control. Shows which apps have access to permissions that could make it easier for someone to spy on you or compromise your privacy.

What can actually help — and what might make things worse — during this difficult time? Check out our other posts:
  •  

Elon Musk’s XChat: how secure is the new messaging app? | Kaspersky official blog

Pavel Durov and his “private” messaging app have a brand new rival, and it’s — drumroll, please — Elon Musk and his XChat. On our blog, we’ve discussed more than once why Durov’s claims about Telegram privacy and security are exaggerated, to put it mildly. Here, I’ll just remind the reader that standard (non-secret) chats on Telegram aren’t protected by end-to-end encryption — the bare minimum required for user data to stay private.

But let’s get back to Musk. In late April 2026, the XChat app launched for iOS users. The tech mogul had been touting his messaging app for a long time, pitching it from day one as an incredibly private and secure way to communicate, and as a direct threat to Signal, WhatsApp, Telegram, and iMessage. Today, we look at whether we should actually trust Musk’s promises this new service, break down its core features, and stack it up against the competition.

Bitcoin-style encryption

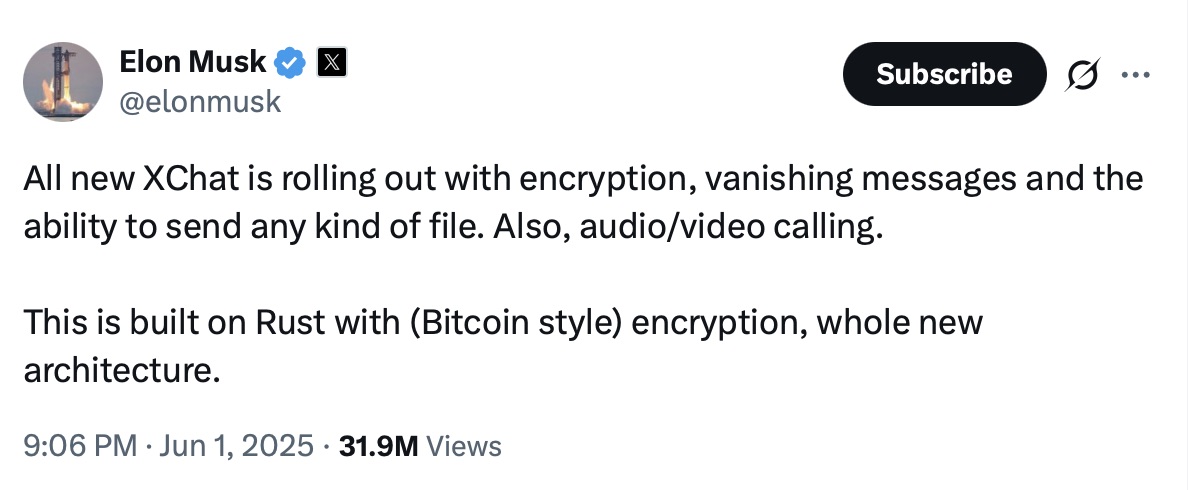
Musk initially teased XChat on June 1, 2025, naturally via his X (formerly Twitter) account. Responding to another user’s question about when to expect the new service, Musk wrote: “This week if there are no scaling issues.”

Apparently, scaling issues there were: the app’s beta didn’t drop until September 2025, and iOS users didn’t get full access until April 2026. As for Android, there is zero info on when that version would launch at the time of this writing. That said, an XChat page is already live on Google Play where users can queue up “pre-register”, whatever that means.

But let’s go back to Musk’s post announcing XChat. That specific post turned a lot of heads in the privacy and cybersecurity community, and here’s why: the tech mogul wrote that the service would be built on an “entirely new architecture”, written in Rust, and featuring “Bitcoin-style encryption”.

Elon Musk's announcement of XChat

Elon Musk announces the launch of XChat, claiming the new messaging app is written in Rust and uses “Bitcoin-style encryption”. Source

The expert community spent a long time scratching their heads and trying to figure out what Musk actually meant. After all, Bitcoin isn’t an anonymous, encrypted data exchange system. The blockchain does use public and private cryptographic keys, but for something entirely different: signing transactions. Meanwhile, these transactions aren’t hidden from prying eyes; they’re out in the open for anyone to see, forever. Simply put, Bitcoin protects its users not by ensuring privacy, but quite the opposite — through ultimate transparency.

Most likely, Musk used “Bitcoin-style encryption” as a marketing gimmick. Bitcoin was trading near all-time highs at the time of his announcement, and cryptocurrency was the talk of the town. Technically, the XChat beta that dropped in September 2025 protected user chats with a “kind of” end-to-end encryption, but this was implemented in a way that raised serious doubts among cryptography experts.

And not without a reason. Normally, setting up an end-to-end encrypted chat automatically generates a public and private key pair. The public key is used to encrypt messages, while the private key decrypts them. Because other users need your public key to start a secure chat with you, these keys are usually stored on the app’s servers.

The private key, however, should ideally live only on the user’s device — which is exactly how Signal does it. This serves as a simple, ironclad guarantee that neither the company itself nor any third party breaching its infrastructure can access user chats, even if they really want to.

But Elon Musk’s projects always march to the beat of their own drum: the XChat developers decided it would be a great idea to store users’ private keys on XChat servers. X claims they’ll use hardware security modules (HSMs) to store these private keys — specialized appliances designed to prevent even the system owner from easily accessing the data inside. However, experts are also questioning the reliability of this setup, and coming to a grim conclusion: if X really wants to get a user’s private key, they will most likely be able to do so.

How encrypted messaging in XChat works in practice

Finally, once the scaling issues were ironed out nearly a year after the announcement, X officially rolled out the XChat app for iOS in April 2026. Now anyone can use it, but from a practical standpoint, the situation with encrypted chats seems even more convoluted than in Telegram.

According to the social network’s help center, to use end-to-end chat encryption in XChat, both users must have an X account, set up XChat, and have some sort of connection between them:

  • Follow, or be subscribed to each other
  • Have exchanged messages before
  • Have previously accepted a direct message request
  • Be a member of the same Premium Business / Premium Organization subscription on X

If users don’t follow each other and haven’t interacted before, XChat might still let them send a message request. However, that initial request goes out without end-to-end encryption.

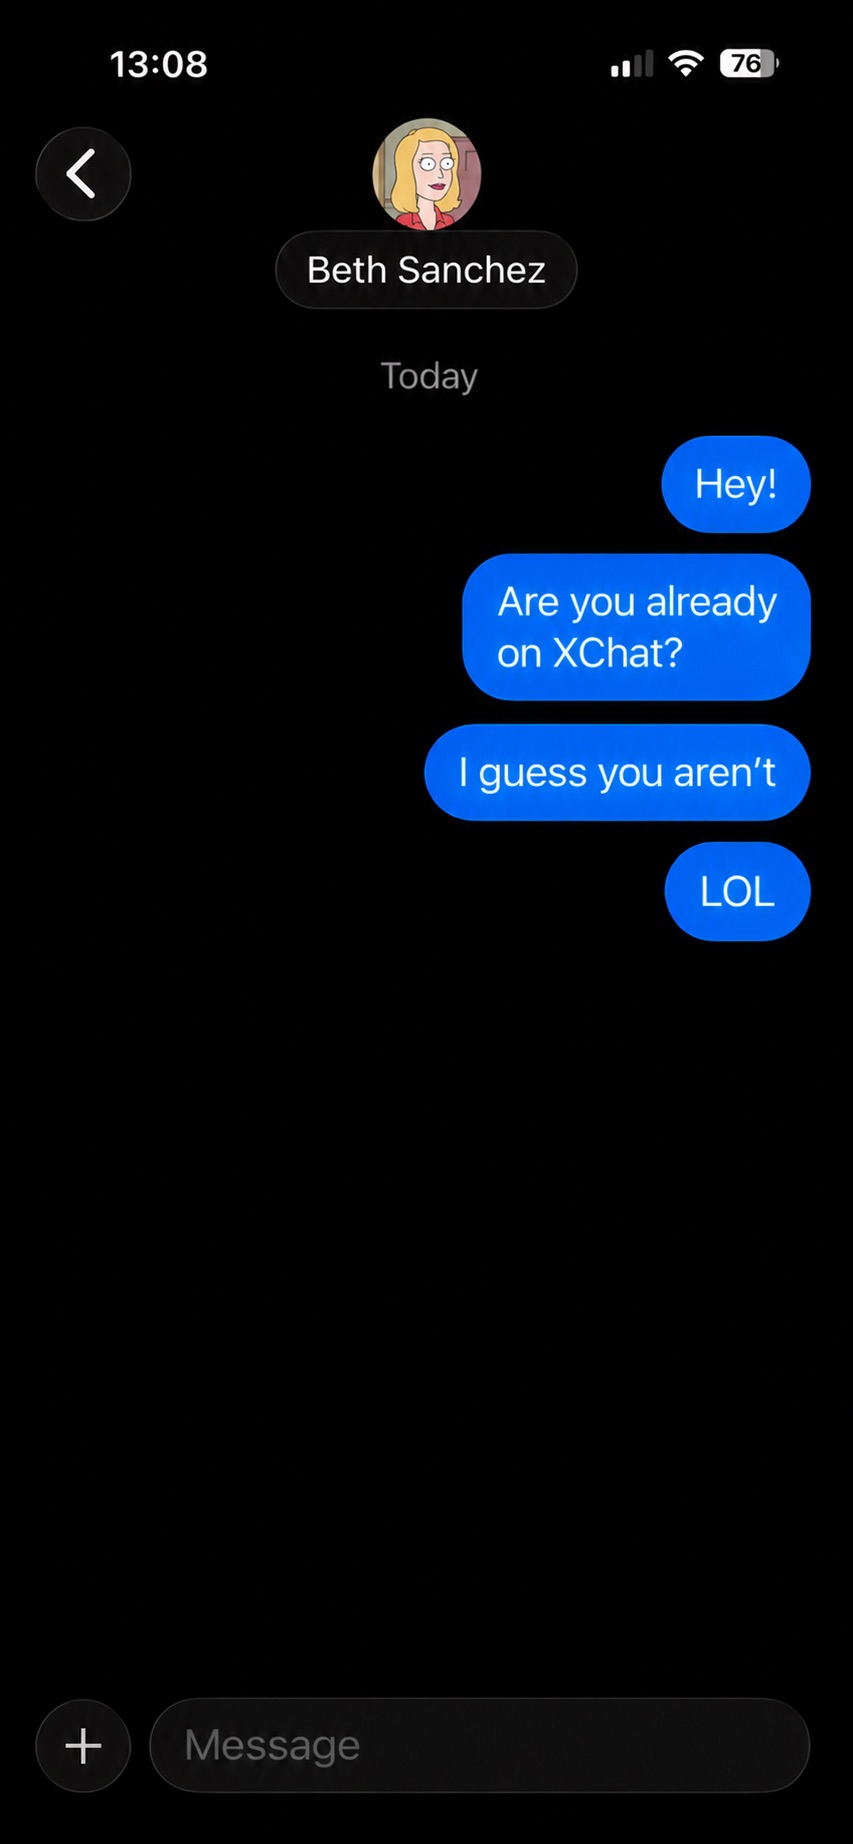
Again, this is how the process is described in the messaging app’s official help documentation. Sound overly complicated? Let me reassure you: in practice, it works — or rather, doesn’t — completely differently. I personally managed to send a message to another user who had NOT set up XChat. The app itself, of course, gave me absolutely no warning about this.

XChat lets users send messages to people who haven't set up the app

The app allows you to start a chat with a user who hasn’t even set up XChat yet, without giving the sender any heads-up.

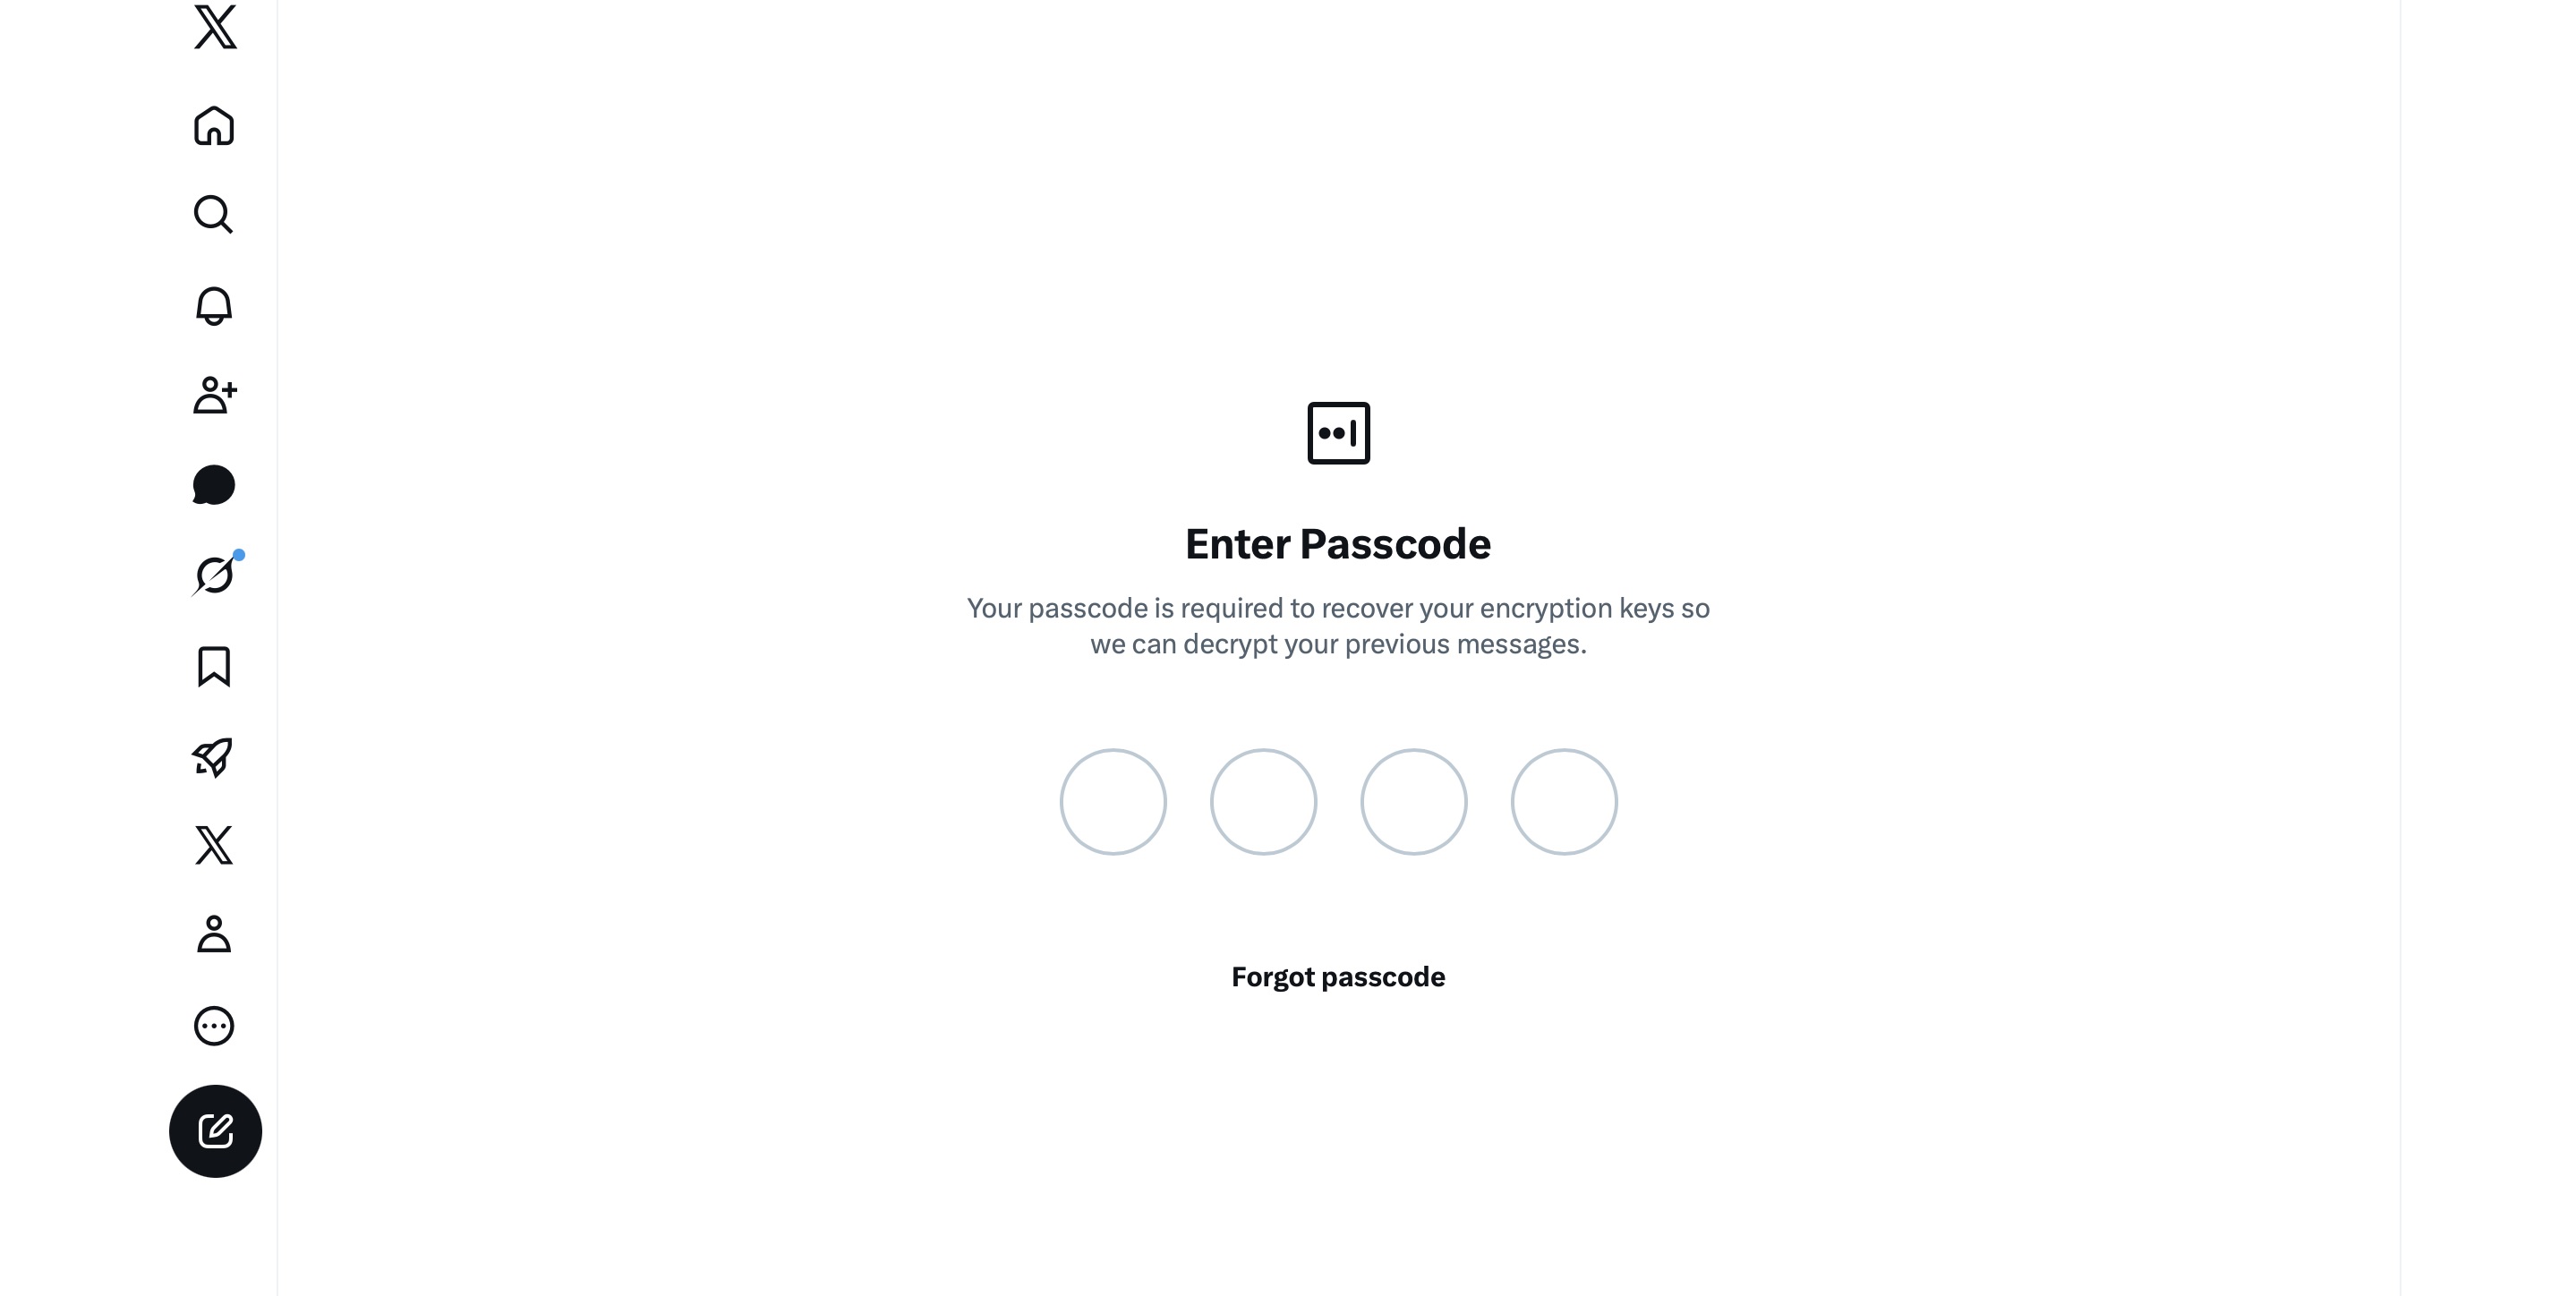
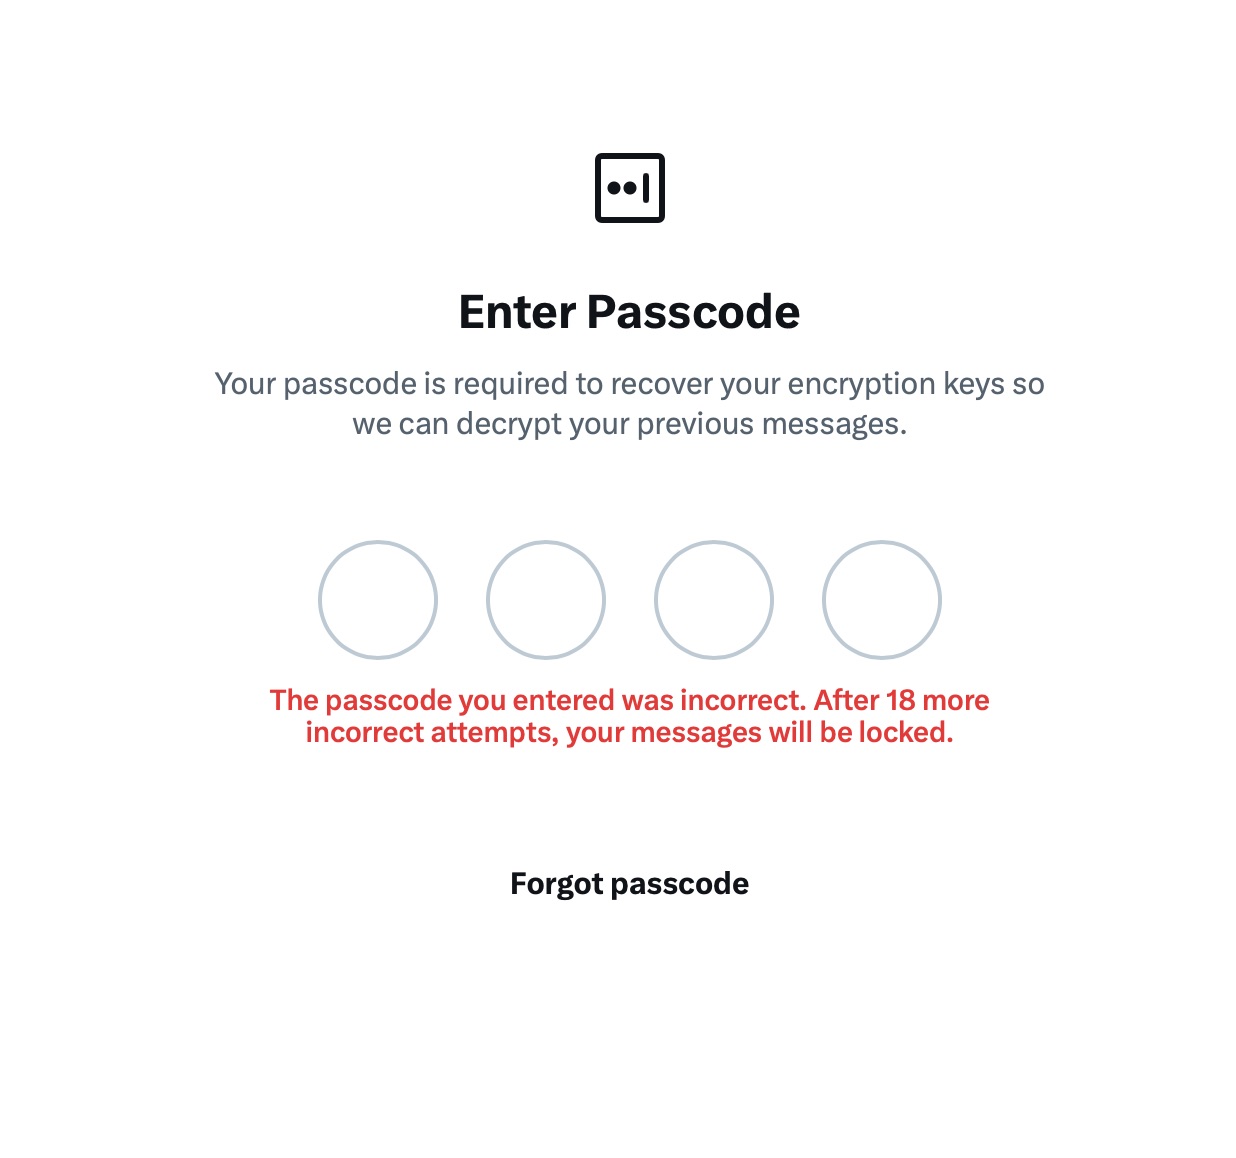
It gets even better. The user I messaged saw a notification for it on the web version of X, but couldn’t actually access the message. Here’s the catch: to start using XChat, the user first has to create a four-digit PIN. Yet, the app asks for this PIN the very first time the user tries to open it — meaning, before they even get a chance to create one. Along with this prompt, the user also sees a warning stating that without the PIN, they won’t be able to view past encrypted chats.

XChat asks for a PIN before one is even created

The user is prompted to enter a PIN to decrypt past messages before even completing the initial XChat setup.

The only workaround I found to actually start using XChat is to tap “Forgot PIN?” — even though that PIN never existed in the first place — confirm your identity, and create a new (well, your first) PIN. Naturally, you lose access to your chat history this way, so you won’t be able to read any messages sent to you in XChat before you officially set up the app.

XChat: the new Telegram, WhatsApp, Signal… or Facebook Messenger?

All these PIN hurdles actually exist for a reason. Remember, unlike WhatsApp and Signal, the XChat developers decided to store users’ private keys on their own servers. Consequently, the app uses these four-digit PINs to encrypt those keys.

According to the XChat help documentation, this mechanism was designed to ensure a “seamless” multi-device experience. It’s impossible not to point out that both WhatsApp and Signal managed to pull this off without sketchy workarounds like PIN requirements or server-side private key storage.

The problem is, workarounds like these undermine any claims of app privacy and security. First and chief among them, a PIN isn’t exactly the most secure way to protect sensitive data. We’ve mentioned time and again that four-digit combinations are easy to crack via brute force — especially since XChat gives you a generous 20 attempts to guess the right code.

XChat warns of lockout after 20 failed attempts

The app allows up to 20 attempts to enter the four-digit PIN. Once the limit is reached, XChat warns that access to messages will be permanently lost.

Stepping away from the bizarre implementation of end-to-end encryption compared to other messaging apps, it’s hard to ignore the overall sense of pointlessness that comes with trying to use XChat. As a Wired journalist rightly pointed out, the app feels less like a relative of WhatsApp, Signal, or Telegram, and much more like Facebook Messenger. Except people usually open Messenger to read a text from their mom or grandma, whereas XChat seems meant for anyone wanting to check in on that weird nephew who spends all his free time on X, still believes John McAfee’s promise of $500 000 Bitcoin, and fanboys over Elon Musk.

So, what’s the bottom line on XChat?

The best way to wrap up this post is with a quote from a cybersecurity expert: “If what you want is good security, use Signal. If what you want is to be able to talk to pretty much anybody using encrypted messages, use WhatsApp. If your whole life is based around X, I guess this is better than nothing.”

If you do use XChat, rule number one is to avoid a predictable PIN — absolutely don’t use your birth year or, worse, 1234. It’s also crucial not to forget this code, because if you do, your entire chat history is gone for good. Finally, just like your other passwords, you shouldn’t keep it in your notes app, but rather in a secure password manager. This won’t only save you from having to memorize dozens of character combinations, but will also reduce the risk of losing access to your vital data and conversations.

To learn more about secure messaging in other apps, check out our other posts:
  •  

Study on the Wi-Fi security situation in Mexico | Kaspersky official blog

One of the biggest football (soccer) events of this summer is the World Cup 2026. The tournament is co-hosted by three countries: the U.S., Canada, and Mexico. Unfortunately, events of this scale attract not just fans, but also scammers from all over the globe. We’ve already covered how cybercriminals are prepping for the World Cup online, and today we’re talking about digital security for fans on the ground in Mexico.

The country will host 13 matches and welcome millions of tourists. They’ll be staying in hotels, heading to games, checking out restaurants, navigating airports, and visiting popular tourist spots — and everywhere they go, the temptation to connect to public Wi-Fi will be high.

We’ve surveyed more than 84 500 (!) public Wi-Fi access points in Mexico City, Guadalajara, and Monterrey — and we have a lot to share about their security. Spoiler alert: many networks are still using outdated security standards, so you really shouldn’t go on vacation without reliable protection and an eSIM.

What and how we tested

Walking across Mexico looking for public Wi-Fi access points would have been a bit tough, though that’s exactly what we did for a similar Wi-Fi security survey in Paris. You can check out the results of that in our post, How safe is Wi-Fi in Paris?

This time the mission was far more demanding: mapping the wireless landscape of three major metropolises. That’s why we went wardriving — scanning for and logging wireless networks from a moving vehicle while equipped with a smartphone or laptop. It’s similar to searching for Wi-Fi on your phone, where the device constantly listens for nearby networks. Except instead of connecting to them, we just collect data about them.

All information was used strictly for passive observation and infrastructure analysis. Beyond receiving publicly broadcast service information, the experts of Kaspersky’s Global Research and Analysis Team (GReAT) didn’t attempt to authenticate, intercept traffic, exploit systems, or otherwise interact with the wireless networks they discovered. Mobile access points deployed in cars and on mobile devices were excluded from the sample.

Our main target was Mexico City — the capital and one of the most densely populated cities in Latin America. We took a drive through popular tourist spots: Mexico City Stadium, Mexico City International Airport, Zócalo, Paseo de la Reforma, Colonia Roma, La Condesa, Polanco, Coyoacán.
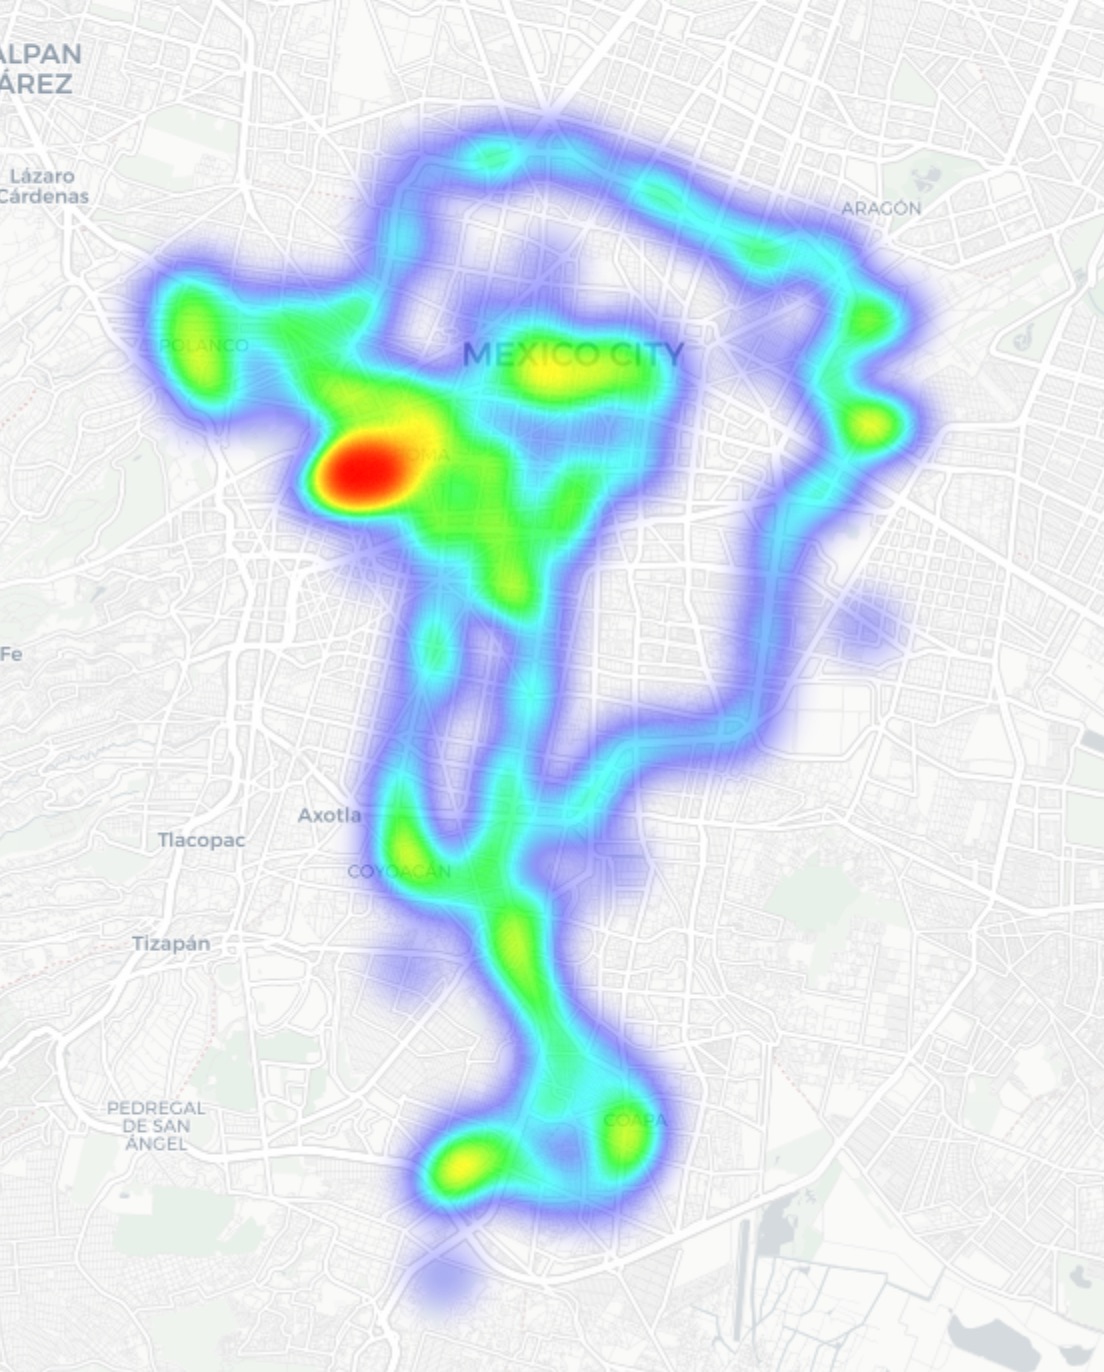
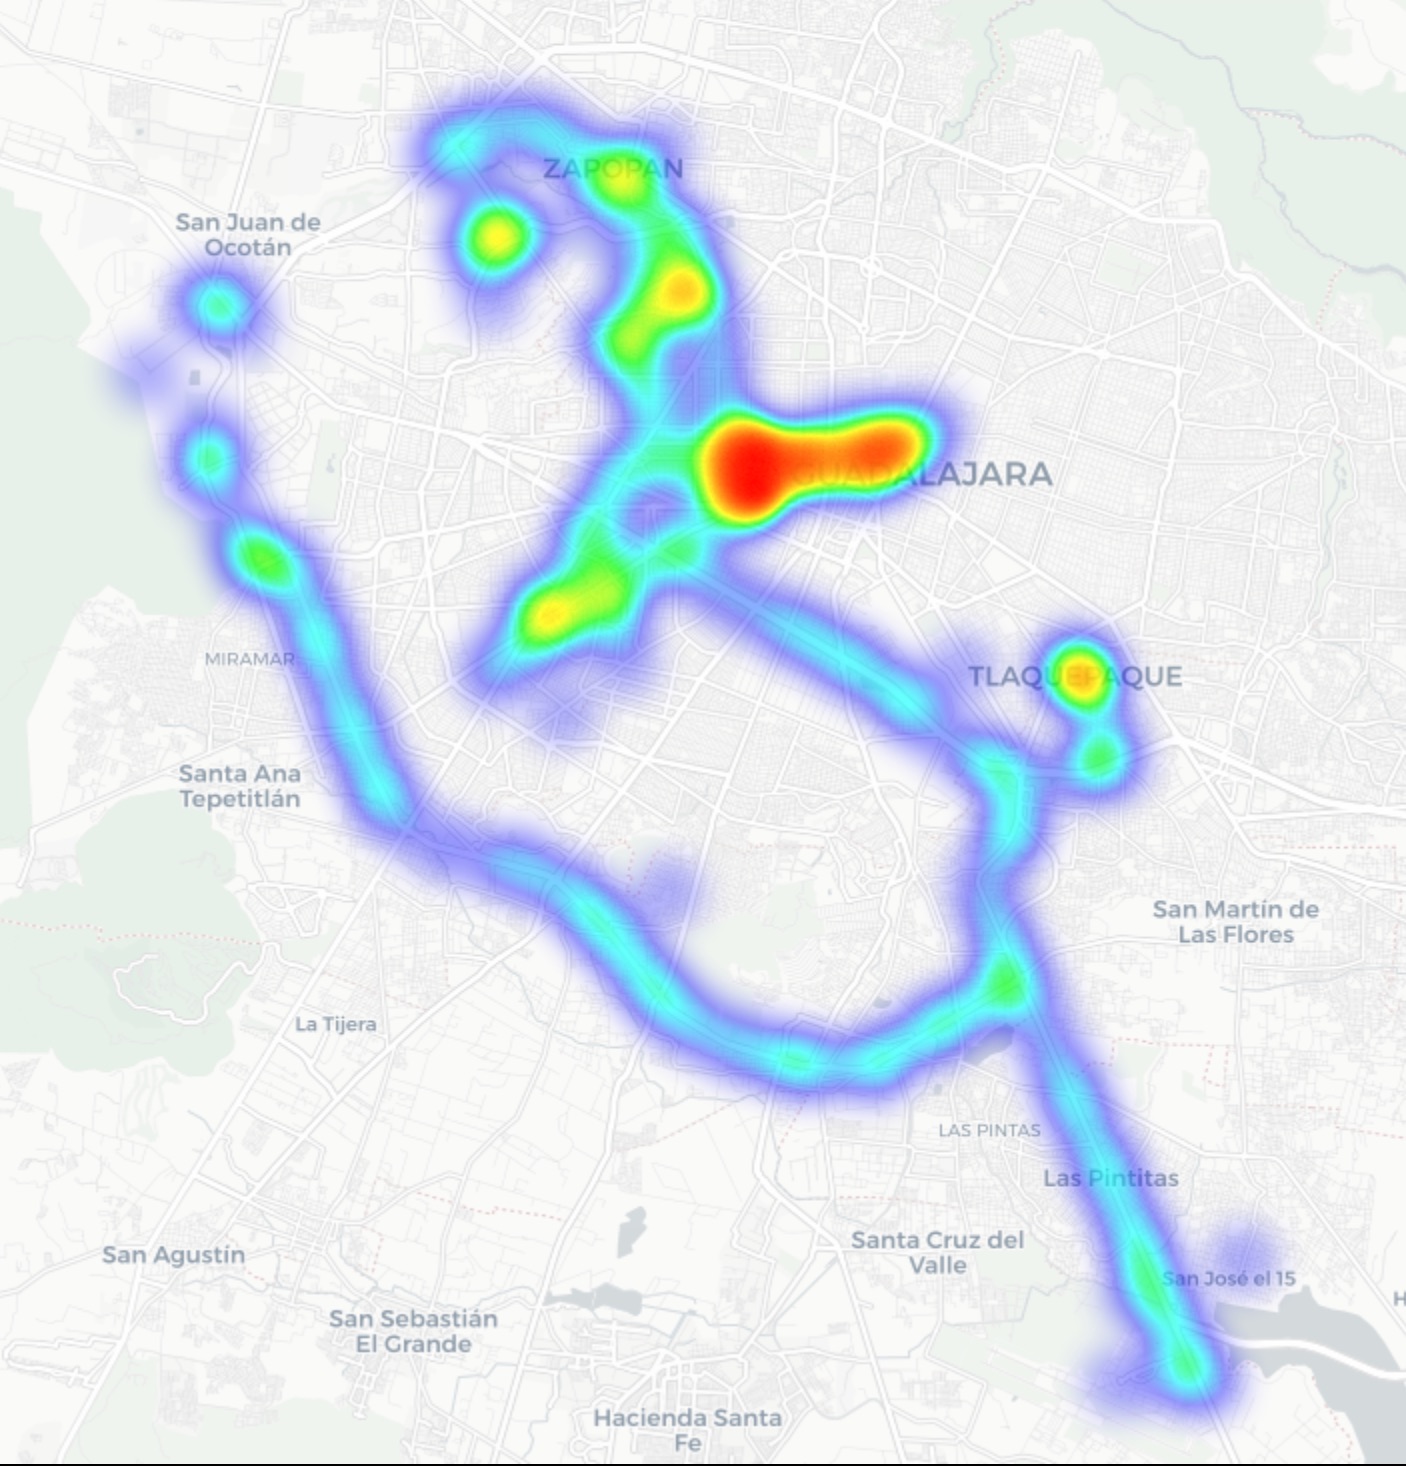
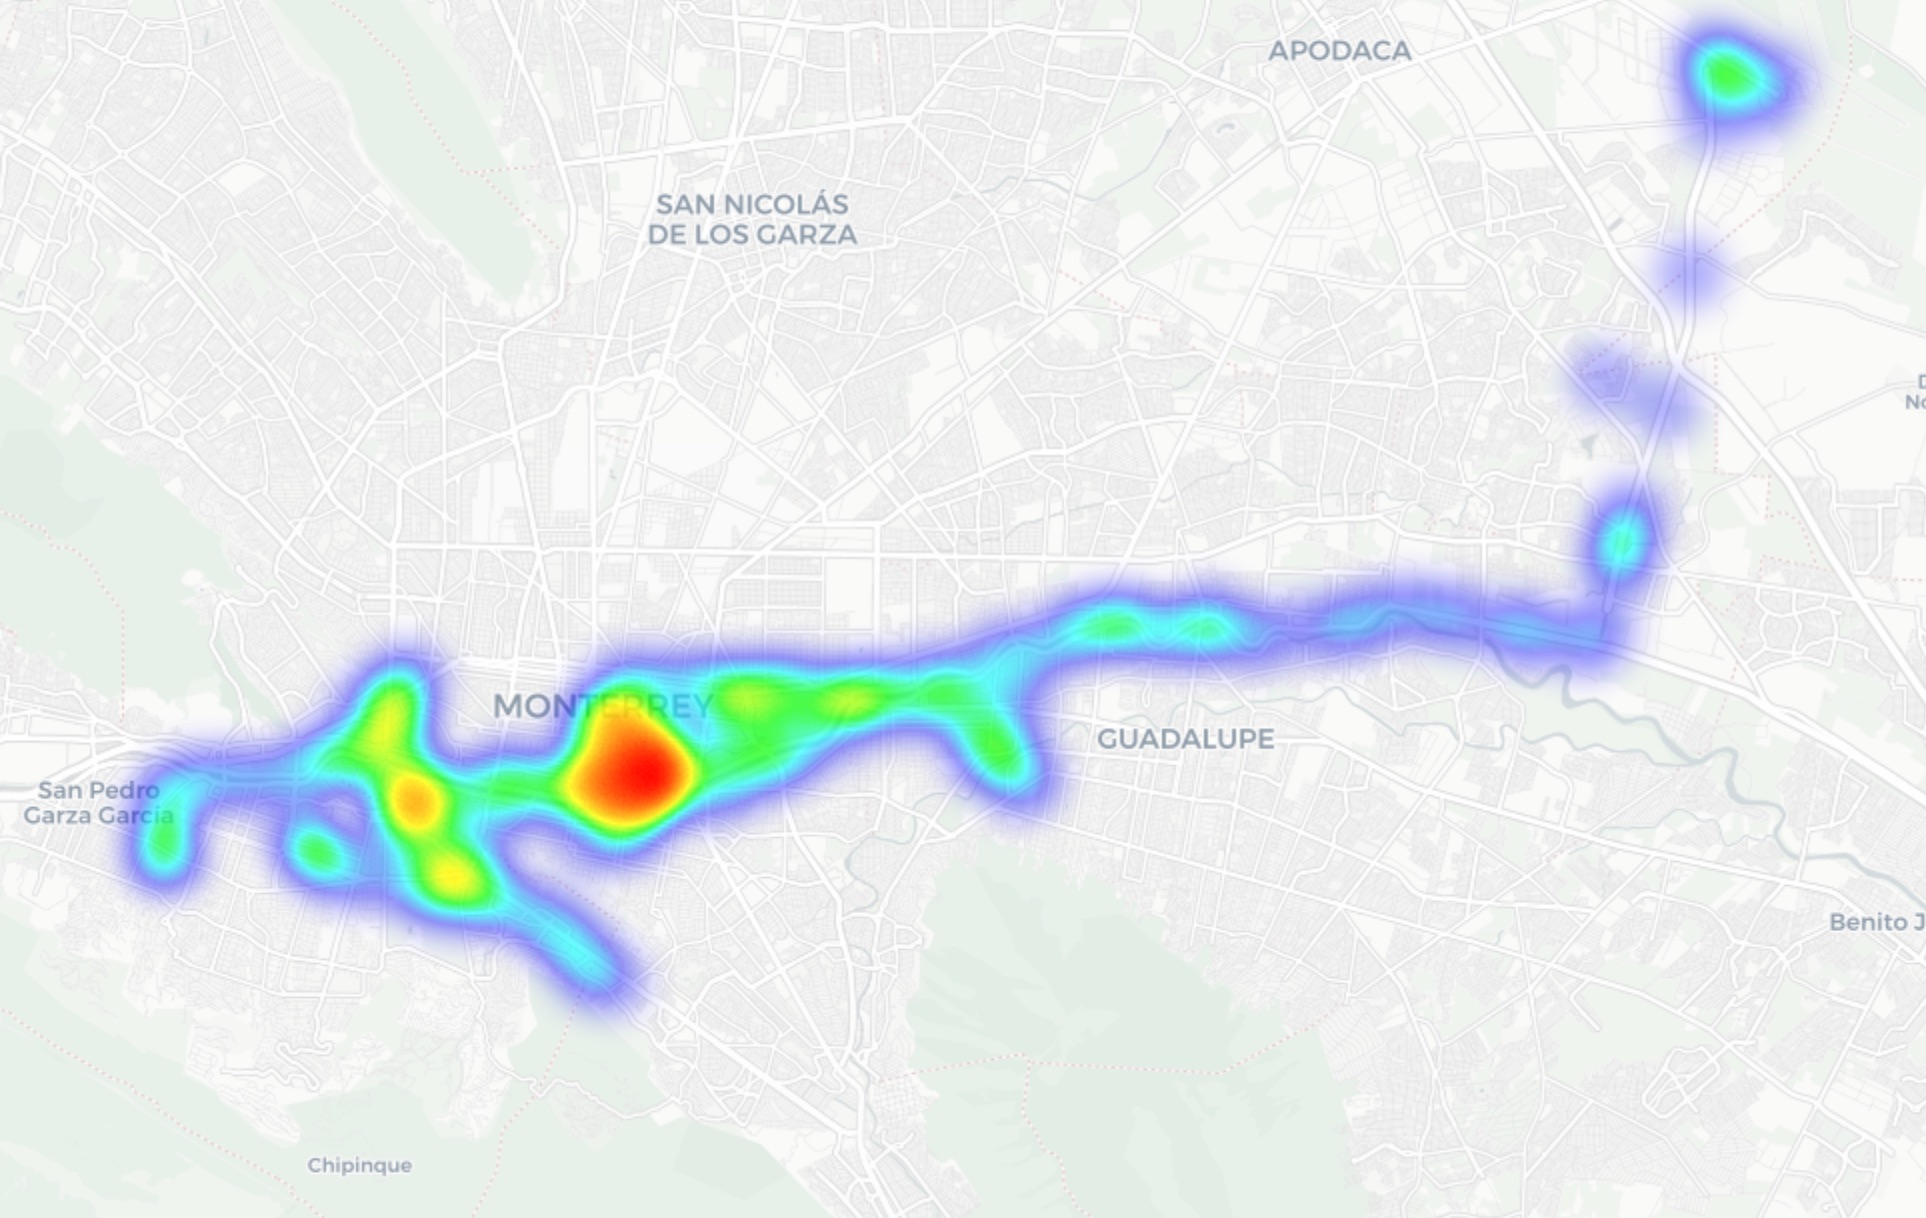
In Guadalajara and Monterrey, we drove similar routes: stadiums, main avenues, airports, and popular neighborhoods. Below you can see a heatmap of the areas we covered, ranging from red for areas with the highest density of public access points, through yellow and green, to blue for the lowest concentration.
Heatmap showing the locations of all Wi-Fi access points we covered in Mexico City
Heatmap showing the locations of all Wi-Fi access points we covered in Guadalajara
Heatmap showing the locations of all Wi-Fi access points we covered in Monterrey

We used passive radio reconnaissance to log 84 500 signals and 69 500 unique network identifiers across these three cities. The majority of the signals were caught in Mexico City (61.4%), followed by Guadalajara (23.6%) and Monterrey (14.8%).

What we analyzed:
  • Wireless network identifiers (SSIDs): the names that show up in your list of available Wi-Fi networks
  • Information that can be gleaned from these identifiers
  • Default router configurations and how ISPs deploy their networks
  • Frequencies used and signal characteristics
  • Channel load and radio frequency spectrum usage
  • Wireless network security configurations:
    • Open and insecure networks
    • Networks with WPS enabled
    • Secure networks (WPA2/WPA3) with WPS activated

You can find the full version of the study on the Securelist blog.

Telltale public Wi-Fi access point names

Network names (SSIDs) can tell you a lot by unintentionally revealing information about hardware manufacturers, ISPs, deployment methods, and whether an access point belongs to a business or a private user.

About 34% of the public Wi-Fi networks we logged didn’t bother changing their names at all, either sticking with the factory SSIDs from the router manufacturers or using standard naming conventions from their ISPs. For attackers, this can be a pretty solid hint, since this kind of network name lets them know which provider owns a given access point, what hardware is being used, and how it’s likely configured by default.

Another troubling nuance is the large number of Wi-Fi networks (over 30%) that use the access point’s MAC address (BSSID) as the visible network name. The first few bytes of a BSSID contain an Organizationally Unique Identifier (OUI), which gives away the router’s manufacturer. This is a useful lead for bad actors: they can find out who made the hardware and test for vulnerabilities specific to that brand’s models.

Is Mexican Wi-Fi well-protected?

An access point secured with WPA2/WPA3 can be considered more or less safe. All other authentication mechanisms yield much weaker results. We grouped the public Wi-Fi networks into four categories:

  • Secure (WPA2/WPA3)
  • Unsecured (open/WEP)
  • Weak (WPA)
  • Undetermined

The results are roughly the same across all three cities: about 82% of all analyzed access points are protected by secure standards. The outdated and insecure WPA protocol was practically nonexistent. However, more than 10% of the access points turned out to be completely unsecured. Connecting to these networks carries the risk of traffic interception and hidden surveillance.

But security isn’t evaluated by WPA protocols alone. We also checked for the presence of WPS, the infamous feature for quickly connecting to a network without entering a password, which is highly vulnerable to attacks. It turned out that WPS is enabled on nearly half (47%) of the access points in Mexico City, 43% in Guadalajara, and 41% in Monterrey. On average, 45% of the access points are potentially vulnerable to WPS-related attacks — sacrificing security for the sake of convenience.

What’s more, this feature frequently remained active even on seemingly secure WPA2/WPA3 networks — about half of them utilized WPS. This shows that having WPA2/WPA3 is still not enough to consider a Wi-Fi access point safe, as additional features like WPS can still leave the door open to attacks.

What else every tourist needs to know

Digital risks on a trip aren’t limited to public Wi-Fi alone, especially now that many are shifting away from public Wi-Fi to an eSIM. There are still plenty of threats in crowded places: public USB chargers, QR codes with swapped links, NFC and Bluetooth attacks, and, of course, social engineering tactics. Let’s break it all down.

Charging stations. Public USB chargers can also be dangerous: bad actors could potentially gain access to the data on your device or try to install malware. We covered these attacks in detail in our post, Data theft during smartphone charging.

Dangerous QR codes. Criminals can plant phishing QR codes in popular tourist spots. The pretexts can vary wildly; for instance, ads for team-specific fan “events”, or links supposedly offering discounts or restaurant menus. In reality, any QR code posted on the street can be considered insecure by default, and you shouldn’t scan them with your smartphone unless you have a QR code threat analyzer installed.

Fake broadcasts, tickets, and betting pools. Earlier, we described cases where bad actors were distributing malware via fake IPTV apps to capitalize on the WC26 hype. Remember, even if you plan to watch the tournament from home, you still need to stay alert and not trust the first sites that pop up advertising free broadcasts, offering betting pools, or promising unbelievably generous payouts.

NFC and Bluetooth attacks. Leaving Bluetooth enabled in crowded places can also cause problems: someone might try to discover your device, track you, or initiate an unwanted pairing request. NFC services with contactless payments create additional risks too — especially when paying in sketchy spots.

How to protect yourself and your devices

Despite the prevalence of secure WPA2/WPA3 public Wi-Fi access points in Mexico City, Guadalajara, and Monterrey, our study shows that public Wi-Fi networks remain vulnerable. It’s also important to remember that attackers can create fake networks — so-called evil twins — disguised as legitimate public Wi-Fi in airports, hotels, cafés, and tourist spots.

For the average user, it’s practically impossible to tell how safe a specific access point is when trying to connect. That’s why the safest option is to use cellular data to access the internet — completely eliminating the need for Wi-Fi. Besides, there’s no need to research the nuances of local laws, rates, and other cellular details for every country you plan to visit; you can just buy a global eSIM online in two clicks. We explained how to make the entire process hassle-free in our post, Internet on the go with Kaspersky eSIM Store.

If you still plan on connecting to public Wi-Fi, always use a VPN to secure your device and data when connecting to unfamiliar — especially unsecured — Wi-Fi networks. This creates an encrypted tunnel between your device and the VPN server, making it impossible to intercept your data along the way. Haven’t picked a VPN yet? Try Kaspersky VPN Secure Connection, which is included with both Kaspersky Premium and Kaspersky Plus subscriptions.

Now, if you still plan to attend the World Cup without any cybersecurity solution, at least follow these basic rules of digital hygiene:

  • Don’t use public USB chargers
  • Don’t send sensitive information over connections that aren’t secure
  • Don’t log in to banking, email, or social media accounts over unsecured Wi-Fi
  • Turn off Bluetooth and NFC while walking around in crowded places
  • Don’t trust QR codes posted on the street
  • Connect to public Wi-Fi only when absolutely necessary

What else to read to make sure cheering for your favorite team isn’t only exciting, but also safe:

  •  

Scams in messengers: exposing the global scam-cartels exploiting everyday messagesng-heist | Kaspersky official blog

It starts with the familiar: a short message, a trusted name, a routine tone. Delivery updates, work pings, brand alerts hum in the background, rarely attracting scrutiny. You check, you answer… — until minutes later you’ve slipped into a trap built to lower your guard and hijack your trust.

That’s why messaging scams cut deep: they exploit everyday habits where instinct, not caution, leads. Communication once moved slowly, leaving room for doubt. Now it’s instant — and that speed is a weapon in criminal hands.

On our blog, we’ve already examined numerous scam schemes in messaging apps — from pig butchering, where the victim is groomed for a very long time, or catfishing, where the scammer creates a fake identity, to phishing via chatbots or through gift-giving campaigns in messaging apps.

Now, for the first time, Kaspersky has set out to capture the full end-to-end reality of messaging-based scams to understand how quickly harm occurs, how they impact trust and what remains after the interaction ends. What emerges is a highly organized and industrialized scam ecosystem embedded within everyday messaging channels such as SMS, WhatsApp, and email.

Kaspersky experts have prepared a report on targeted scams in messaging apps, detailing not only the financial but also the emotional damage caused by such attacks, as well as providing tips on how to protect yourself and avoid them. In this post, we explore the most interesting facts, but you can find more details in the full report.

The damage is underestimated

How much do you think a single successful attack via a messaging app costs the average victim? Ten dollars? Or maybe 50? You’re underestimating the scammers. Although more than a third (36%) of victims incur losses of less than $135, on average a victim loses… $733!

Country Average loss per victim
Senegal $392.94
Serbia $493.32
Morocco $504.28
Greece $609.32
United Kingdom $617.38
Côte d’Ivoire $654.11
Spain $672.67
United States $724.73
Portugal $868.20
Italy $896.02
France $1,193.58
Germany $1,369.35

The average amount lost by a victim in a successful attack via a messaging app

On the one hand, the financial hit doesn’t look catastrophic in isolation. These are micro-losses by design. Small enough that some never report them to the police. Small enough that banks don’t always investigate. Small enough to be dismissed as bad luck rather than organized crime.

But $733 is not nothing. It’s enough to cover a month’s worth of groceries, school or daycare fees, or utility bills. Against the backdrop of the global cost-of-living crisis, a single such loss can seriously dent a family’s budget.

In 11% of cases, losses exceed $1,350, and more than a quarter of victims (28%) report having been scammed three or more times in the past six months. Once scammers discover that a phone number responds, that contact becomes an asset, circulating from one database to another.

Now imagine the scale of the problem: if just 10% of the three billion messaging‑app users worldwide fell victim with the average loss, the total damage would amount to… nearly $220 billion! This is comparable to the GDP of Greece, and exceeds that of Morocco, Serbia, or Côte d’Ivoire.

It becomes clear that behind the daily flood of fraudulent schemes lie large scam cartels operating on an industrial scale, using AI to personalize messages that mimic those of family members, friends, and familiar brands. This, in essence, forms the basis of a full-fledged economy built on digital identity theft.

Scam gangs cash in on your money worries, using AI to drain your wallet in minutes

Speed beats scrutiny

More than half of successful messaging scams (52%) unfold in under 30 minutes — from first contact to the moment money or personal data changes hands — or even faster, before the victim begins to doubt the legitimacy of the sender. In fact, one in seven scams takes less than five minutes — quicker than boiling an egg!

The speed isn’t accidental. It’s the method. Scammers structure their schemes to deny the victim a chance to come to their senses. Every element is engineered to compress the decision-making window: the urgency of the scenario, the familiarity of the format, the plausibility of the request.

They rush you — faster, faster, don’t tell anyone, you only have a few minutes, solve the problem, don’t ask questions. Click the link, fill in the details, approve the transaction, or else… Or else what? The scammers’ imagination knows no bounds here, but if you don’t do something right now, you’ll definitely regret it.

Alas, the realization of what has happened usually comes when the damage is already irreversible. More than half of victims (51%) lose money; another 43% hand over their personal data — most commonly phone numbers, names, and email addresses — to scammers, and often the victim loses both.

Where and how attacks occur

A delivery notification, a bank alert, a message from a merchant you ordered from last week — messaging apps permeate every aspect of everyday life, making such interactions completely normal. An attack shouldn’t feel like an attack. It should feel like the same message you’ve received hundreds of times.

It’s no surprise that scammers focus their attention on this method of communication first and foremost. The most popular platforms for scams are predictable: WhatsApp (43%), SMS/iMessage (40%), Facebook (27%), Telegram (22%), and Instagram (19%) — these are the ones that people trust most.

A wide variety of schemes is used. Brand impersonation is now one of the three most common types of messaging scam worldwide — accounting for 31% of cases. Fake delivery notifications top the list at 38%, followed by investment scams at 37%.

At the same time, nearly two-thirds (63%) of fraudulent schemes span multiple platforms, moving from SMS to WhatsApp, from WhatsApp to Telegram, etc. In this way, scammers achieve two goals: they mimic organic messaging and evade moderation algorithms.

AI has taken scams to a new level

Just a couple of years ago, fraudulent messages gave themselves away with bad grammar, awkward phrasing, illogical requests, and an obsessive sense of urgency. Today, a phishing message looks, sounds, and reads just like the real thing.

Scam cartels want to catch people in motion — between meetings, on a commute, or during everyday tasks — when your attention is already fragmented. They mimic your mother’s turn of phrase. They match your bank’s tone of voice. They copy your courier’s format exactly. They mirror the rhythm, structure, and style of authentic brand communications across messaging platforms. And AI is accelerating all of it.

What this creates is overlap. Legitimate and fraudulent messages appear in the same environment, using the same formats, language, and triggers. The difference between them is no longer obvious.

The data shows that two-thirds of victims (66%) believe AI was used in the scam against them, 42% cite messages written by AI, 31% report generated or cloned voices, and 25% encountered deepfake images or videos.

That’s why mere awareness and “tech-savviness” may no longer be enough to protect oneself. From Gen Z to Gen X, messaging scams cut across every generation.

And what about the emotional toll?

But money is far from the only problem a victim is left with after an attack. After what they’ve been through, people develop distrust toward incoming messages, unfamiliar numbers, and any requests for action. As a result, 99% of fraud victims say they no longer trust incoming notifications in messaging apps.

This creates a crisis of trust in all digital channels in general. Every legitimate message can now be perceived as a scam. Brands, banks, and delivery services are forced to operate in an environment where the customer is, by default, in a state of distrust.

Dr. Elizabeth Carter, a forensic linguist and criminologist at Kingston University in London, notes that scammers use familiar contexts, common social settings and embedded linguistic norms to create the illusion for the victim that their decision-making is rational and reasonable in the moment. However, what is actually happening is that they construct false realities in which those decisions end up causing financial and psychological harm. She also notes that it is very hard to identify a false reality while you are in it.

After realizing they had been deceived, more than half of victims felt anger — the kind that comes from having trusted something and discovering it was used against you. 42% of victims report frustration, 38% — feeling upset. Moreover, several months later, these feelings haven’t gone away: nearly half of all victims (48%) are still angry, a third (33%) remain frustrated, and 30% are upset.

And nearly one in 10 victims don’t tell anyone what happened. They feel shame, a sense of having fallen for something so obvious. This leaves a significant portion of the actual damage unreported: only 24% of victims contact the police, and only 23% report it to their bank.

Messaging scams aren't just a personal problem, they're bleeding the world economy dry

So what can be done?

The crisis of trust — and even a touch of paranoia — that has arisen due to widespread attacks on users can linger in victims’ minds for a long time, affecting their quality of life. To prevent this, follow these guidelines:

  • Pause before you act. The sense of urgency you feel is almost always artificial. A legitimate bank, retailer, or delivery service won’t penalize you for taking 30 seconds to verify before clicking a link or confirming details. It’s precisely this instinct to resolve the situation quickly that scammers are counting on.
  • Verify through another channel. If a message appears to be from a relative, colleague, or company you trust — contact them through another channel before taking any action. Use secure verification methods, and cross-check identities when something doesn’t feel right. For families, agreeing on a “safe word” in advance can defeat even the most convincing voice clones.
  • Use a password manager. It will not only help you generate strong, unique passwords for all your accounts and store them securely, syncing them across all your devices, but also protect you from spoofed sites. Even if you click a phishing link and land on such a site, our password manager will notify you about the domain mismatch and refuse to autofill your username and password.
  • Use protection that works in real time. Modern security solutions, such as Kaspersky Premium, provide real-time protection against malicious links and phishing attempts in the apps and websites you use every day. On Android devices, a dedicated layer of anti-phishing security scans and neutralizes suspicious links as they appear, even within notifications, before you even have a chance to click them.

We’ve covered other threats in messaging apps in similar articles:

  •  
❌