PHP2Shell Exploitation Started Days Before Patches
Initial attempts were observed on October 17, and mass activity began shortly after patches were released.
The post PHP2Shell Exploitation Started Days Before Patches appeared first on SecurityWeek.
Initial attempts were observed on October 17, and mass activity began shortly after patches were released.
The post PHP2Shell Exploitation Started Days Before Patches appeared first on SecurityWeek.
Nearly 100 vulnerabilities have been assigned a critical severity rating and Fusion Middleware received the most patches.
The post Oracle Patches Over 1,200 Vulnerabilities With October 2026 CPU appeared first on SecurityWeek.

The people and institutions closest to a community understand their needs best. Libraries, small businesses, nonprofits, and schools see firsthand where AI can create opportunity and where people need support to navigate change. At Microsoft, our role is to help these trusted institutions lead by providing practical resources, training, and clear safeguards that strengthen local capacity and put communities at the center of AI literacy and adoption.
Public libraries have served as trusted centers of community learning across the United States for generations. Today, we are announcing a new initiative with the Public Library Association, a division of the American Library Association, to expand resources and no-cost AI literacy and skills training for public library workers and their patrons.
This work delivers on the commitment we made earlier this year through our Community-First AI Infrastructure initiative: to expand access to AI learning and opportunity by investing directly in local training. We’re committed to neighborhood learning through libraries, free literacy training, and certification opportunities, age-appropriate learning in schools and colleges, and support for nonprofit and small-business workforces. This new library initiative is the latest example of our broader work to help trusted local institutions serve as entry points for AI learning, skills development, and opportunity. This program comes alongside small business accelerator programs in TechSpark, our new Elevate for Changemakers platform connecting nonprofits to resources, and our ongoing national and statewide work to bring safe and responsible AI to education.
The Public Library Association AI literacy initiative we are announcing today, Building AI Skills and Agency Through Libraries, is designed to build practical skills, critical awareness, and the judgment to use AI safely and appropriately. It will pair Microsoft’s AI skilling resources with PLA’s national network of expert practitioners to support library workers and community patrons as they navigate this rapidly evolving technology.
The initiative will expand practical resources and training for library workers, create opportunities to learn from one another through a Community of Practice, and offer free webinars and guidance to support their work with patrons.
Library workers help people navigate information, find learning resources, and make informed decisions for themselves and their families. Supporting those workers is a practical way to bring AI learning closer to people, while respecting the independence of the institutions they trust.
The approach reflects a broader view of AI literacy: people need more than instructions for using AI tools; they also need the knowledge and judgment to decide whether, when and how those tools should be used. The training will help library workers and patrons understand how AI works and expand their skills, while also evaluating potential risks, protecting personal and confidential information, critically evaluating AI-generated claims and sources, and better understanding considerations related to safety and bias.
Last July, we launched Microsoft Elevate, a company-wide initiative that brings together our work to help people and institutions build the skills and capacity to navigate AI responsibly. Under the Elevate charter, each year, Microsoft supports nearly one million nonprofit organizations and education systems worldwide with technology, training, grants and discounts. Microsoft Elevate for Educators, our global community of over 100,000 teachers and school leaders, recently recognized our inaugural group of 20 Beacon Schools and School Systems that are leading examples of AI transformation in education, bringing together effective AI practices while keeping educators and students first. They are powerful examples of what happens when you combine committed educators, AI-powered technology, and intentional, no-cost staff training.
In Washington, our Elevate commitment has included a $3 million, two-year investment supporting 10 school districts and 10 community and technical colleges with grants, coaching, and communities of practice. To date, the initiative has reached 29,375 educators, with early pilots in Kennewick and Everett helping teachers explore practical uses of AI while keeping professional judgment at the center.
Skills and access must be matched by strong safeguards. In September, Microsoft joined the American Federation of Teachers to establish a national AI Safety & Privacy Standard for Schools, with enforceable protections for student and educator data, human oversight, and transparency for families. Beginning November 1, every US school district can request Microsoft to add these protections to a new or existing agreement, without waiting for renewal or renegotiation.
That same commitment extends to nonprofit staff and leaders. The Elevate for Changemakers program has already supported over 18,000 learners, helping them build practical AI skills, connect with peers, and earn recognition for turning learning into tangible outcomes for their organizations. And today we are expanding the program and introducing a new, connected experience that brings training, resources, and community together.
Together, these efforts reflect a simple principle: responsible adoption requires more than technology. Educators, nonprofit changemakers, and community leaders need time, training, trusted connections, practical support, and clear guardrails so they can decide when AI strengthens learning and, equally important, when it does not.
For nearly a decade, Microsoft has partnered with local nonprofits and small businesses across the U.S. through our TechSpark program.
Through Fellows grants, TechSpark pairs local expertise with Microsoft coaching and a national peer network to help nonprofits expand their impact in their local community and drive accelerated innovation for local small businesses. Today, Microsoft is announcing the new 2027 TechSpark Fellows across all 50 states and releasing the 2026 Fellows Impact Report showing what a locally led model can make possible.
YouTube Video
Over the last three years, the Fellows cumulatively report access to more than $298 million in community funding, 59,600 people trained and upskilled in AI literacy, and more than 1,500 nonprofit partners mobilized to advance their missions within their communities. These numbers tell an important story: no single organization can create lasting opportunity on its own, and local context matters.
In Virginia, Rosie Riveters Executive Director Brittany Greer is showing what it looks like to build the human capabilities that innovation requires. Through hands-on STEM experiences, students build, test, and troubleshoot to develop the critical thinking, persistence, and independent judgment they will need to use AI thoughtfully. Her work is the kind of learning these partnerships are designed to strengthen.
Community institutions know their neighbors, understand the barriers they face, and are best positioned to decide how new resources can serve them.
The thread connecting a library worker, a job seeker, a TechSpark Fellow, and a teacher is not a particular product. It is the ability to make informed decisions with support from people and institutions they trust. Our responsibility is to make that support more useful, accessible, and human-centered, while being candid about what we have yet to learn.
As we navigate the rapid pace of innovation in this AI era, our aim is not simply to bring AI into more places. It is to help people retain a stronger voice in what happens next, in their workplaces, their classrooms, and their communities.
The post Expanding AI literacy with the Public Library Association and community-based programs appeared first on Microsoft On the Issues.
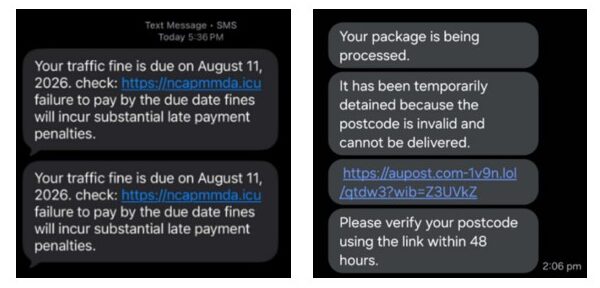
Most people have opened their messages to find a suspicious alert urgently telling them that a package cannot be delivered, a toll remains unpaid, a bank account needs attention, or a tax bill is overdue. The details may change, but the goal is the same: to get someone to click, share personal information, or pay.
These messages are relentless. Delete and block one, and another takes its place. Ignore them, and more will follow. Fall for one, and the floodgates open. What appears to be a simple scam message is often the visible end of a much larger transnational cybercriminal operation.
When Microsoft and Japan’s National Police Agency (NPA) followed a wave of fraud and scam activity targeting people and businesses in Japan, they expected to find individual campaigns. Instead, they found themselves inside a sprawling Chinese-language cybercrime marketplace where criminals could buy accounts, hosting services and tools used to create fake websites and online identities. The investigation expanded globally, involving the Japan Cybercrime Control Center (JC3), Resecurity, Cloudflare, Oracle, Proofpoint and TRM Labs to uncover the businesses sustaining this criminal ecosystem.
Today, Microsoft and Health-ISAC, a global non-profit that helps health sector organizations share cyber threat information and collaborate to improve operational resilience, are moving to dismantle three components of this criminal marketplace: YAM Store, CoGUI and Iron Man.
Since January 2026, YAM Store, CoGUI and Iron Man have collectively enabled more than one billion malicious messages targeting over 75,000 organizations worldwide, including more than 750 million messages geared toward Microsoft customers alone. These messages have been used to target consumers, healthcare organizations, financial institutions, and other businesses in more than 150 countries, generating tens of millions of dollars for their operators.
The investigation began in late 2025 after Japan’s NPA alerted Microsoft to malicious messaging campaigns targeting people in Japan. NPA continued providing intelligence and investigative support as the partners traced those campaigns back to the businesses supplying criminals around the world.
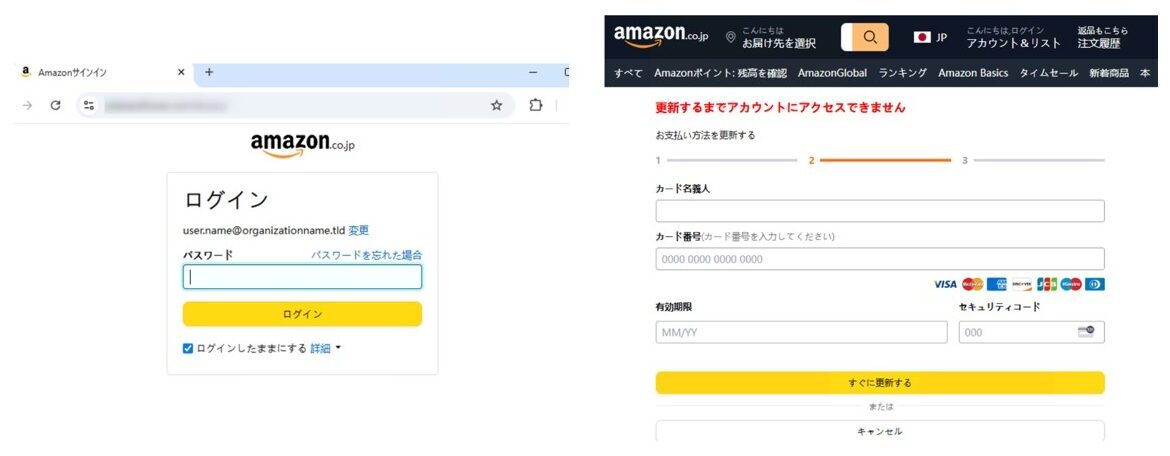
The trail led investigators deep into a Chinese-language cybercrime ecosystem that was difficult for non-native-speaking investigators to penetrate. There, they gained access to CoGUI, which supplied criminals with ready-made websites and messages impersonating companies, financial institutions, government agencies, and other trusted organizations. Instead of creating fraudulent websites themselves, criminals could quickly deploy pages designed to steal passwords, payment information, and other personal data.

As Microsoft’s investigation expanded, intelligence from JC3 helped confirm the scale of the activity affecting Japanese organizations and their customers. Drawing on information collected across its network of more than 130 member organizations, JC3 connected what appeared to be separate incidents to a broader pattern of scams targeting Japanese companies and financial institutions, including efforts to defraud consumers and to steal credentials and other sensitive information.
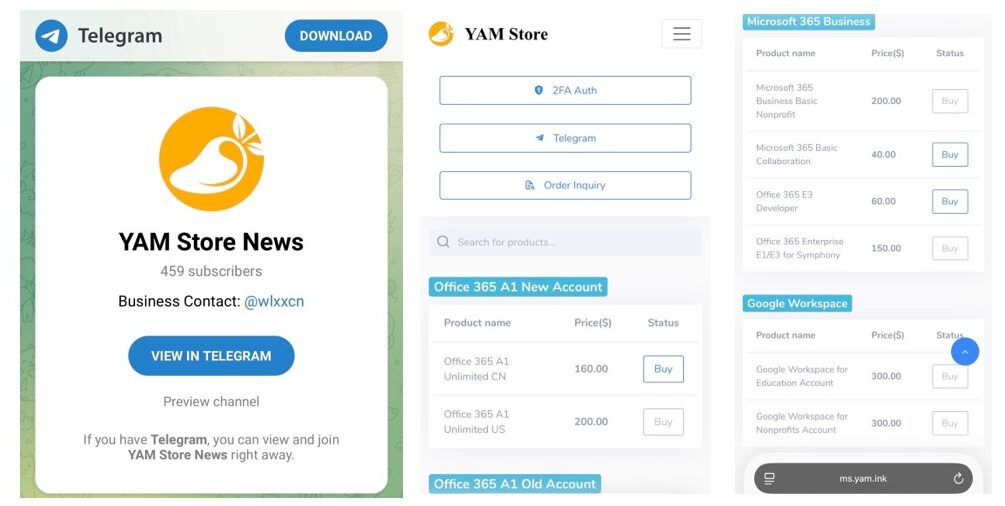
One name that kept appearing throughout the investigation was YAM Store. YAM Store operated much like an online shop. Customers could browse products, compare prices and purchase fraudulent Microsoft and Google accounts and other ready-made tools used to carry out scams, including credential theft. Controlled purchases conducted by Microsoft helped confirm how it worked.
In some cases, operators acquired internet domains that legitimate organizations had allowed to expire, often targeting certain sectors, such as non-profits and education, with specialized product offerings. They then rebuilt the websites to make those organizations appear active, allowing them to fraudulently obtain Microsoft 365 accounts that could later be sold through YAM Store.

YAM Store provided criminal infrastructure that was frequently paired with tools and services such as CoGUI. As investigators dug deeper, they found that the marketplace was already evolving. CoGUI had become one of the most widely used offerings in the ecosystem, particularly targeting victims in Japan and the United States but by mid-2026 it was increasingly being replaced by a newer offering known as Iron Man.
Iron Man expanded the model by giving criminals access to thousands of ready-made templates designed to impersonate trusted organizations. Criminals could then quickly deploy email, text and web content tailored to specific brands, industries and countries.
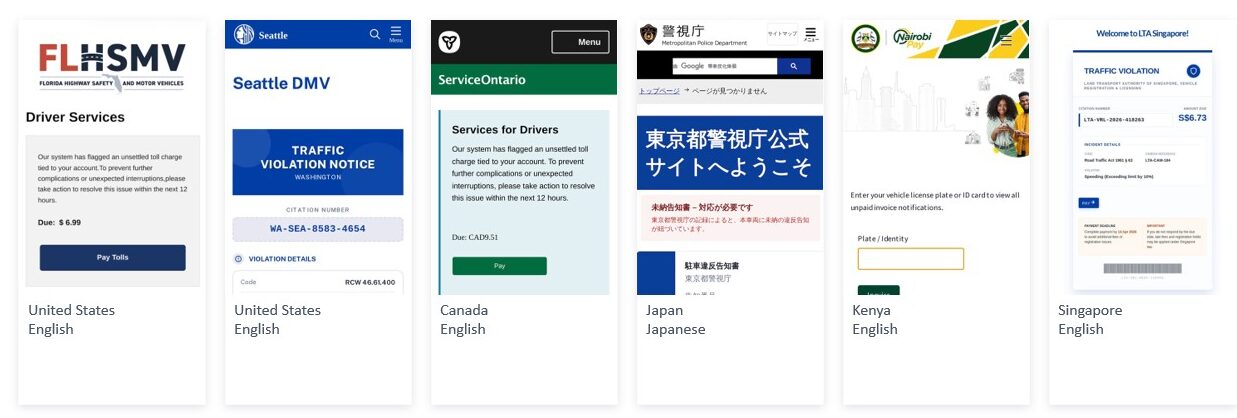
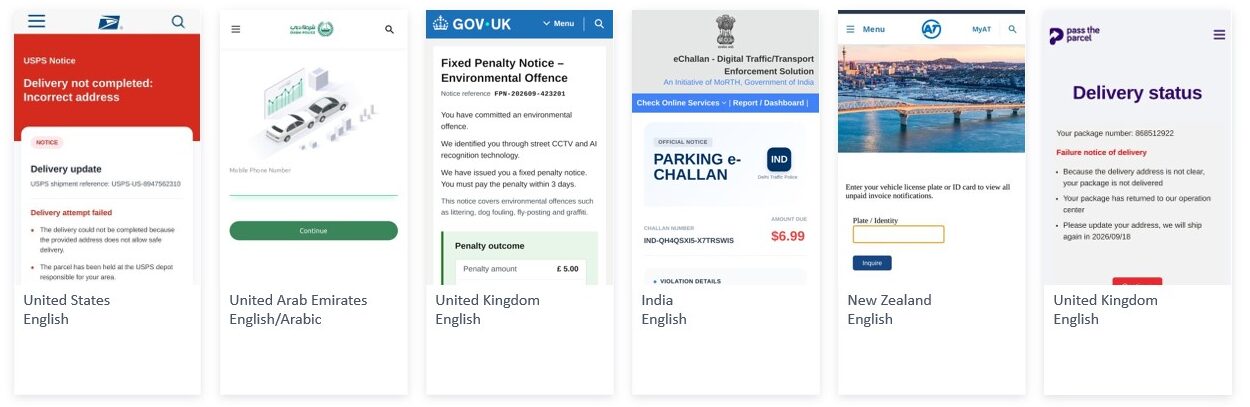
Through test purchases and work with Resecurity, investigators gained access to Iron Man and identified more than 2,300 templates impersonating banks, retailers, healthcare providers, transportation authorities, police departments, government agencies, and other organizations across more than 150 countries worldwide. Some were designed for government impersonation scams, using the appearance of official authority to pressure victims into making payments or disclosing sensitive personal information. Others impersonated organizations across industries, countries, and languages, from banks and airlines to telecommunications companies, retailers, and parcel delivery services.
Examples of these impersonation templates are below. Importantly, the presence of an organization or government entity in these templates does not indicate that its systems were compromised.


A blog from Microsoft Threat Intelligence shares more details on the network, as well as steps customers can take to protect themselves.
No single organization saw the full picture. Japan’s NPA played a critical role throughout the investigation, providing intelligence, investigative support and collaboration that helped uncover how the operation worked. JC3 helped establish the scale of the activity affecting Japanese organizations and consumers. Health-ISAC provided insight into impacts affecting healthcare organizations, while Resecurity, Cloudflare, Oracle, Proofpoint and TRM Labs contributed intelligence and investigative support.
Working together, and with the assistance of AI tools, we connected accounts, websites, and infrastructure that initially appeared unrelated, helping expose the broader criminal marketplace behind them. Microsoft also worked closely and shared intelligence with U.S. Secret Service and international law enforcement partners.
This investigation also reflects a broader trend highlighted in this year’s Microsoft Digital Defense Report: modern fraud increasingly relies on businesses and services that make it easier for criminals to reach more victims. It took two-way information sharing across industries and international borders to uncover how these deeply interconnected services worked together.
With an order from the United States District Court for the Southern District of Florida, Microsoft and Health-ISAC seized and redirected domains that were part of the underlying infrastructure powering YAM Store, CoGUI and Iron Man. Microsoft has already disabled more than 20,000 accounts connected to YAM Store and continues to dismantle the operation by removing infrastructure hosted on its services and blocking more than 100,000 domains used for impersonation and fraud.
What began with scam activity targeting people and organizations in Japan led investigators to an underground service economy supplying criminals around the world. YAM Store, CoGUI and Iron Man are only part of that larger criminal network, but disrupting them makes it harder for criminals to obtain the accounts, tools and infrastructure they rely on.
The scam message is often the only part victims see. The businesses behind it are what make it possible.
The post Disrupting the service economy behind transnational cybercrime operations appeared first on Microsoft On the Issues.
We believe in the strength and talent of the American workforce. That is why the vast majority of Microsoft employees in the United States are Americans.
We look forward to providing the Administration with additional information. For example, of the approximately 6,000 H-1B visa applications we submitted in the last fiscal year, 80% were to extend or change the status of existing Microsoft employees. These were not to hire new people. The remaining filings for new employees were for individuals already legally in the United States who decided to come work for us, and they equal only 1% of our U.S. workforce. They are not new arrivals to our country.
Microsoft only files H-1B petitions for those who meet the rigorous standards of this visa category. We pay our employees some of the highest compensation in the tech sector, and our wages are among the highest of all H-1B filings. We pay our H-1B employees the same as any other employees doing comparable work.
Microsoft succeeds as a global technology leader by developing the world’s best technology workforce. We do this by strengthening this country’s talent pipeline, hiring American workers, and attracting the best talent from around the world.
The post Microsoft Comment on Recent Immigration Questions appeared first on Microsoft On the Issues.
More than 730 cyber breaches affected over 270 million Americans last year, costing an average of $10 million per breach.
The post Senate Passes Bipartisan Bill to Strengthen Healthcare Cybersecurity appeared first on SecurityWeek.
Known as Rey, the suspect is reportedly helping the FBI identify and locate other members of the extortion group.
The post Alleged ShinyHunters Leader Arrested in Jordan appeared first on SecurityWeek.
Citrix has confirmed that a new zero-day vulnerability, CVE-2026-88779, emerged just days after two other exploited flaws were patched.
The post Exploitation of Citrix NetScaler Zero-Day Hits Appliances Patched Days Earlier appeared first on SecurityWeek.
Vulnerability and exposure management (VM) teams need critical metadata and context that clearly show which issues pose an immediate risk to their organization. While traditional VM frameworks tell defenders how severe a vulnerability may be, they do not provide visibility into how likely threat actors are to exploit it. This leaves security teams overwhelmed in patch backlogs without a clear strategy for prioritization.
Nowhere is this prioritization gap more dangerous than with ransomware. Ransomware-as-a-Service (RaaS) groups no longer choose targets at random. They look for specific technical conditions that make vulnerability exploitation easy, fast, and repeatable. With RaaS attacks rising by 45% period-over-period in H1 2026, organizations need a way to identify the specific traits that make a vulnerability attractive to ransomware operators before an attack occurs.
Flashpoint built the Ransomware Risk score into Flashpoint Vulnerability Intelligence to solve exactly this problem. Since 2022, it has rated newly discovered vulnerabilities based on how closely they resemble those known to be used in ransomware attacks. With the grant of the U.S. Patent No. 12,705,360 on August 11, 2026, the methodology behind the score is now formally patented. This milestone formalizes Flashpoint’s ability to cut through the noise with a proven, threat-informed signal that gives defenders the clarity they need to act on Day Zero.
“As vulnerability disclosures surge, prioritization is more important than ever for security teams. A severity score alone can’t tell you which vulnerabilities pose the greatest real-world risk of exploitation by ransomware actors.
Our patented Ransomware Risk model applies years of threat intelligence to that problem, giving customers an earlier signal and helping them prioritize based on how attackers actually operate.”
josh lefkowitz, co-founder and ceo at flashpoint
The patented system evaluates newly disclosed vulnerabilities against the patterns shared by vulnerabilities ransomware groups have exploited. Rather than trying to predict what threat actors will do next, the model learns what past ransomware-exploited vulnerabilities have in common and compares each new flaw against those patterns.

Every vulnerability ingested into Flashpoint Vulnerability Intelligence is profiled against more than 60 distinct technical factors. This “fingerprinting” links the vulnerability to key inputs including whether the flaw is remotely exploitable without authentication, whether it affects SCADA or Operational Technology (OT) systems, and its potential impact on data availability, which is central to extortion schemes.
The model turns each multi-factor fingerprint into a set of values that place it as a single point on a map, so vulnerabilities with similar profiles land close together.
Flashpoint overlays historical threat data onto the map to establish neighborhoods where vulnerabilities previously exploited in real-world ransomware attacks aggregate.
When a new vulnerability is ingested, its coordinates are checked against these neighborhoods. The scoring system calculates its spatial proximity to known ransomware vectors and assigns a clear rating: Low, Medium, High, or Critical.
This four-step method, developed by Flashpoint’s Ben Haynes and Jacob Kouns, is the basis of U.S. Patent No. 12,705,360.
By translating complex structural attributes into a single risk score, the patented model delivers four key operational advantages:
Flashpoint’s Ransomware Risk model is built to enhance, not replace the vulnerability management frameworks organizations already rely on. In fact, it provides even greater value for security teams as our Ransomware Risk model provides clarity for every vulnerability detailed by Flashpoint Vulnerability Intelligence, including over 105,000 issues missed by CVE and NVD.
Within Flashpoint Ignite, security teams have a complete view of vulnerability risk, seeing the score alongside CVSS (v3 and v4), EPSS, Social Risk, and exploit maturity.

Vulnerability management requires more than cataloging. It demands threat-informed prioritization that aligns security operations with real-world business risk. Flashpoint’s patented Ransomware Risk model eliminates guesswork by surfacing the flaws that match the profile of known ransomware targets, allowing security teams to patch what matters most, first.
By combining proprietary knowledge of vulnerability architecture and ransomware attacks, Flashpoint bridges the gap between theoretical and active exposure. Request a demo today to see how our Ransomware Risk model provides the definitive signal needed to stay ahead of extortion groups.
What is the Ransomware Risk score?
The Ransomware Risk score is a rating in Flashpoint Vulnerability Intelligence that shows how closely a vulnerability resembles those known to be used in ransomware attacks. Each vulnerability is rated Low, Medium, High, or Critical, so security teams can see which ones to patch first to reduce their ransomware exposure.
How is Ransomware Risk different from CVSS and EPSS?
CVSS measures how severe a vulnerability could be, and EPSS estimates how likely it is to be exploited in general. Ransomware Risk adds a ransomware-specific signal that works alongside both, showing how closely a vulnerability matches those ransomware groups have used. In Flashpoint Ignite, all three scores appear together.
What does Flashpoint’s ransomware patent cover?
U.S. Patent No. 12,705,360, granted August 11, 2026, covers Flashpoint’s method for rating how likely a vulnerability is to be used in a ransomware event. Each vulnerability is profiled on more than 60 factors, compared with vulnerabilities used in past ransomware attacks, and rated by similarity. The patent formalizes the model behind the Ransomware Risk score, live since 2022.
How often are Ransomware Risk scores updated?
Ransomware Risk scores update in near real time, so new vulnerabilities are rated as soon as they’re disclosed. The model also keeps adjusting as new vulnerabilities join the body it compares against, so ratings reflect the ransomware landscape as it stands today.
The post Ransomware Risk Model: Flashpoint’s Patented Scoring Method to Inform Vulnerability Prioritization appeared first on Flashpoint.

In this post, Flashpoint analysts examine Process Parameter Poisoning—a novel EDR evasion technique we validated in Rust—and detail how abusing undocumented process parameters allows attackers to inject code and bypass standard security products.

Modern Endpoint Detection and Response (EDR) platforms have made traditional malware injection techniques significantly harder to execute. In most cases, if a threat actor attempts to write malicious code into a process, an alert will fire. However, that sense of security is being actively challenged as cybercriminals and red teams find new ways to blend malicious payloads into standard operating system routines.
Flashpoint’s Intelligence team built and tested a proof-of-concept for a newly disclosed technique known as Process Parameter Poisoning. By compiling a custom payload and layering evasion mechanics, our analysts demonstrated how easily traditional API hooks can be rendered blind in a laboratory environment—achieving zero alerts across tested EDR/XDR controls.
Process Parameter Poisoning is a novel endpoint detection and response (EDR) evasion technique that combines process parameter spoofing and thread execution hijacking to inject code into foreign processes without triggering standard security detection mechanisms.
Discovered by researchers Max Hirschberger and Ogulcan Ugur, Process Parameter Poisoning is designed to inject code in foreign processes without relying on the conventional memory-manipulation workflows that modern security tooling monitors.
To execute process injection, historically security tools and threat actors alike have focused on a small set of well-known Windows application programming interfaces (APIs). Process Parameter Poisoning shifts away from these heavily watched routines entirely. Instead of calling memory-accessing APIs to allocate and write into a target process, the technique hides the malicious payload directly inside standard process initialization structures during the initial creation of a process. The result is a fundamental shift in defense evasion that effectively blinds traditional, API-hooking EDR agents during the initial stages of code execution.
Process Parameter Poisoning allows attackers to bypass suspicious memory-accessing Windows APIs, such as VirtualAllocEx(), WriteProcessMemory(), and MapViewOfFile2(). Security products heavily monitor these specific APIs due to their high rate of abuse in traditional process injection techniques. However, by avoiding these calls, an attacker effectively bypasses the initial primary triggers used by endpoint agents to flag malicious cross-process memory activity.
When using the Windows application programming interface (API), CreateProcessA/W(), the developer can specify parameters such as the command-line to be executed by the new process, environment variables for the new process, current working directory for the process, window title if it is a console application, create a hidden window, create the process in a suspended state, etc. Many of these parameters are passed into CreateProcessA/W() via the STARTUPINFOA/W structure.
Some entries are undocumented and labeled “reserved” by Microsoft. The discovering researchers found that data stored in STARTUPINFO->lpReserved ends up in the Process Environment Block once the new process is initialized in an entry called “ShellInfo.” Below is an example of placing data into the STARTUPINFOW->lpReserved entry in a test application and the data stored in ShellInfo while debugging the newly created process.


Flashpoint analysts created a proof-of-concept (POC) in Rust to test this technique based on the POC C++ source code provided by the researchers:
Flashpoint confirmed that after changing the memory to have executable permissions, the threat actors can perform thread hijacking by using GetThreadContext() to acquire information about the current running thread, change the instruction pointer to point to the ShellInfo.Buffer address, and then SetThreadContext() to apply the changes and execute the shellcode.

Flashpoint analysts further confirm that this technique also works with the WindowTitle entry, CommandLine entry using the same series of steps.
The technique also works with the Environment entry but requires additional steps. Environment blocks require a variable name and the variable data separated by an “=.” Environment blocks can contain multiple variable entries in which each entry is ended with a null terminator. Two null terminators are necessary to denote the end of the environment block. This means the payload needs to be embedded in a longer string with a “{NAME} = {VALUE}” format.

Flashpoint analysts note that four null terminators were appended to the shellcode bytes to denote the end of an environment block in Unicode. The resulting payload buffer is then passed into the lpEnvironment variable of CreateProcessW() along with the CREATE_UNICODE_ENVIRONMENT creation flag.
The rest of the process remains the same as reading the PEB and RTL_USER_PROCESS_PARAMETERS structure. The Environment entry is read, but at the offset of the embedded shellcode within the poisoned environment block string. Because four bytes were added to the beginning of the shellcode to make the Unicode environment block, execution needs to begin after four bytes from the beginning of the buffer to begin executing at the shellcode.
Flashpoint notes that the shellcode requires no NULL bytes, and, if using the PAGE_EXECUTE_READ flag, it cannot overwrite itself. This means automated shellcode generators such as MSFVenom might not work either because they contain NULL bytes or use encoders that perform memory writes during execution. Flashpoint analysts wrote custom shellcode to further test this technique. The shellcode downloads and executes an additional payload. The combination of this technique, custom shellcode, and the use of Rust as the programming language proved successful in minimizing initial static detections by security software.
Flashpoint tested this technique with a commonly-used open source EDR platform. The EDR platform itself failed to produce any alerts from executing the malicious binary. However, the XDR component blocked on the initial creation of a new process and COM interactions by the second stage payload.
Flashpoint analysts then combined this technique with the DLL unhooking technique and applied the non-Microsoft block DLL policy during the creation of the sacrificial process. Analysts observed no blocks from the XDR during execution and observed no alerts on the platform.
| Tactic | Technique ID | Technique Name |
| Stealth | T1055 | Process Injection |
| Stealth | T1055.003 | Process Injection: Thread Execution Hijacking |
| Stealth | T1564.010 | Hide Artifacts: Process Argument Spoofing |
Security teams can leverage several detection strategies to identify Process Parameter Poisoning, though each approach carries distinct limitations:
Process Parameter Poisoning demonstrates another advancement in stealthy process injection and the constantly evolving research into evading security products. By using the previously unknown purpose of the lpReserved field within the STARTUPINFOW structure to house shellcode, this technique bypasses standard security product triggers associated with common memory-allocation APIs. While this proof-of-concept was proven successful in lab testing, the technique has multiple opportunities for detection and will most likely require a combination of additional evasion techniques to achieve a higher success rate.
As threat actors continue to refine technique-stacking and exploit overlooked Windows internals, relying on traditional API hooks is no longer enough to protect your enterprise. Staying ahead of modern evasion mechanics requires proactive intelligence and deep visibility into emerging adversary TTPs.
Request a demo today to see how best-in-class threat intelligence can help security teams detect, prepare for, and neutralize advanced defense evasion techniques before they impact your network.
The post Process Parameter Poisoning: Inside a Novel EDR Evasion Technique appeared first on Flashpoint.

Threat actors are no longer just using automation to execute tasks, they are leveraging prepackaged, safeguard-free AI, weaponizing stolen session data, and directly targeting defenders’ security stacks.

In our latest webinar, Flashpoint Vice President of Intelligence, Ian Gray, briefed security leaders on the evolving threat environment, providing critical insights from the Flashpoint Global Threat Intelligence Report (GTIR): 2026 Midyear Edition.
The threat landscape has developed at a striking pace with Flashpoint tracking over 22 million illicit AI discussions, 7.4 million compromised hosts yielding 1.7 billion stolen credentials, and over 21,600 disclosed vulnerabilities in just six months. Beyond these staggering numbers, the on-demand session detailed something even more alarming: a fundamental shift in adversary operational tradecraft.
Here are the five critical shifts every cyber threat intelligence (CTI), Vulnerability Management, and SOC team needs to know.
The public discussion surrounding criminal artificial intelligence (AI) has reached a critical inflection point. Early in the AI boom, Flashpoint observed threat actors collaboratively experiment across underground forums, jailbreaking commercial frontier models or advertising surface-level tools like WormGPT and DarkGPT.
Today, adversaries are shifting from public forums to running fine-tuned, open-source models locally on private servers, which greatly hampers traditional signature-based detection. Flashpoint analysts are now seeing attackers generate unique, highly tailored malware variants, flawless phishing lures, and custom exploit scripts at extremely low costs—completely offline and shielded from public monitoring.
“A few months ago, a lot of this was collaborative… public outsourcing. Now what we’re seeing is scarier: pre-packaged cybercrime models run locally on private infrastructure. Malicious code, exploit scripts, and targeted phishing are all being generated inside closed environments.”
Ian Gray, VP of Intelligence, Flashpoint
Another eye-opening tactical insight shared during the session was how threat actors are repurposing defender infrastructure for automated initial access and extortion. In the webinar, we pointed to recent campaigns where adversaries specifically targeted misconfigurations and zero-day vulnerabilities inside open-source vulnerability scanners, secrets-detection tools, Kubernetes clusters, and Infrastructure-as-Code(IaC) environments.
What this means for defenders is that the attack surface is no longer bounded by traditional enterprise network boundaries: it extends directly into CI/CD pipelines, security orchestration tooling, and third-party SaaS integrations. Security teams are finding themselves in a race against attackers who use automated scanning scripts to weaponize vulnerabilities in the security tools themselves.
Flashpoint tracked 7.4 million hosts compromised by infostealers in H1 2026—a 27% increase period-over-period—harvesting 1.7 billion credentials and identity information.
While the top infostealer strains remain familiar, law enforcement operations have created vacuums that competitors rapidly fill.
Threat actors are leveraging drive-by downloads, watering holes, and pirated software packages to plant stealers. Once a machine is compromised, the logs capture corporate SSO credentials, active browser cookies, VPN keys, and SaaS session tokens. This enables adversaries to simply log in without having to leverage complex technical exploits.
The Common Vulnerabilities and Exposures (CVE) and National Vulnerability Database (NVD) have failed to keep pace with the velocity of AI-assisted vulnerability discovery. As such, vulnerability management teams are facing significant operational delays.
| Metric | Flashpoint GTIR Midyear H1 2026 Data | Operational Impact |
| Total Disclosures | 21,667 | Remediation volume exceeds defender bandwidth. |
| Exploit Availability | 19% (4,015 CVEs) | Functional code is ready before patches are deployed. |
| Public Catalog Lag | Growing Backlog (NVD/KEV) | Delay in official scoring leaves teams blind to active risk. |
Therefore, waiting for NVD enrichment before prioritizing a patch is a dangerous strategy. To compensate, security teams require Vulnerability Intelligence (VI) that provides primary-source confirmation of weaponization, exploit availability, and actionable mitigation guidance long before public databases update.
Ransomware-as-a-Service (RaaS) activity surged by 45% period-over-period, reaching 6,256 verified victim postings on data leak sites. However, total on-chain payout revenue dropped by 8% to $820 million, with victim pay-rates hitting a record low of 28%.
Faced with declining payouts and resilient enterprise backups, extortion syndicates are adapting. Rather than relying exclusively on technical file-encrypting malware, groups are executing pure data extortion campaigns—frequently targeting cloud platforms or extracting data through third-party vendor access.
Defending against machine-speed attacks requires moving beyond reactive, post-incident telemetry. Flashpoint arms security, CTI, and vulnerability management teams with the primary-source intelligence required to preempt adversary operations:
Request a demo, or watch the full on-demand webinar to explore the data shaping today’s risk landscape.
The post Cybercrime at Machine Speed: Key Takeaways from Flashpoint’s 2026 Midyear Threat Intelligence Briefing appeared first on Flashpoint.

In this post we examine how modern hacktivism has evolved into a tool of global hybrid warfare, analyzing crowdsourced attack tactics, media-driven propaganda, and real-world impacts across Ukraine, the Middle East, European Union, and NATO nations.

Hacktivism used to be perceived as digital graffiti, with lone-wolf threat actors defacing government websites or temporarily crashing banking portals to make a political point. However, Flashpoint is tracking a fundamental shift in how these groups operate.
Modern hacktivism is evolving into a disciplined component of global hybrid warfare, capable of bridging digital disruptions with tangible real-world impact. Today, these operations blur the line between volunteer activism and coordinated state interest, leveraging crowdsourced infrastructure to disrupt critical utilities, manipulate media narratives, and target public infrastructure on a global scale. Unpacking these modern hacktivist collectives reveals what their tactics look like in practice and their far-reaching consequences across dozens of nations.
Hacktivism is the use of cyberattacks to promote or advance a particular political or social cause, leveraging a wide range of tactics such as website defacement, distributed denial-of-service (DDoS) attacks, and data breaches. Modern hacktivist collectives serve as the loud, high-visibility arm of cyber conflict—frequently aligning with state geopolitical interests, as seen most prominently in recent pro-Russian operations and Iranian-aligned cyber campaigns.
These pro-Russian hacktivist groups, such as NoName057 and Killnet, alongside pro-Iranian collectives and proxy ecosystems like Handala Hack, often react to the news cycle and target countries designated by state media or ideological narratives as enemies. As such, modern hacktivist campaigns are opportunistic and tied to global events—from the escalation in the Middle East following military operations like Operation Epic Fury, to the Milan-Cortina Winter Olympics and new aid packages to Ukraine. These groups’ justification narratives typically mirror state messaging.
In tracking modern hacktivist groups, Flashpoint analysts identified a new method these groups are utilizing to convert ordinary devices into tools for hybrid warfare—the gamification of cyberattacks. Flashpoint has observed groups like NoName057 turning DDoS attacks into community-based “patriotic online games,” such as their “DDoSia Project,” with participants earning military-style ranks and cryptocurrency rewards for overloading the websites of government institutions, banks, and various infrastructure across various countries.
This model has enabled the scaling of operations by utilizing a large, low-skilled participant base rather than having to rely on sophisticated technical tradecraft. The model’s decentralized structure and ideological appeal continue to pose a significant challenge for international law enforcement.
Beyond technical disruptions, publicity is the primary currency of modern hacktivism. Hacktivist groups demonstrate a consistent pattern of media-seeking behavior and self-promotion, likely intended to amplify their perceived impact and reinforce notoriety within the broader cyber threat landscape. Many of these groups repeatedly repost media coverage and news articles referencing themselves.
This serves as a curated self-promotion mechanism, allowing the group to selectively showcase external validation of its operations, including coverage from mainstream and security-focused outlets, to its followers. This behavior aligns with a broader trend observed with especially pro-Russian hacktivist collectives, in which media visibility is treated as a measure of operational success independent of verified technical impact. It also serves as a deliberate tactic for engagement and recruitment that reinforces “patriotic” branding and sustains participant morale and visibility.
In some cases, the digital targeting of hacktivist collectives is more aligned with kinetic objectives, rather than public perception or propaganda initiatives. This is especially true for Iranian-aligned hacktivists and proxy groups who are more deeply intertwined with military operations in the Middle East. These groups have expanded their operations from website disruptions into claims of large-scale data wipers, extortion, and cyberattacks targeting key infrastructure across the Gulf.
Major geopolitical flashpoints in the Middle East have triggered waves of hacktivist activity that has spread across North America, with threat actors targeting supply chains, financial infrastructure, and operational technology and control systems.
Simultaneously, pro-Russian hacktivist groups, particularly NoName057, have been extremely prolific within the last year—carrying out two major illicit campaigns heavily targeting Ukraine, which then spilled over to more than 30 nations globally. The following breakdown contains statistics and targeting dynamics of pro-Russian hacktivist groups observed between July 2025 and 2026:

Ukraine has been the primary target for pro-Russian hacktivist groups who seek to damage Ukrainian infrastructure and morale. Anti-Ukrainian content is constantly distributed through dedicated per-language channels, making it the most linguistically developed target spanning six languages. Involved channels each post near-identical translated content within minutes to hours of the Russian original, down to the same image file with identical SHA1 hashes, which suggests a sustained propaganda distribution operation.
This has resulted in alleged data breaches impacting Ukrainian General Staff, military enlistment offices, medical, and morgue databases to push a casualty-count narrative. It also has resulted in the defacement or disruption of websites of regional capitals and administrative centers, energy plants, water and power-adjacent infrastructure, and many more.
However, Ukraine is not the sole casualty of modern hacktivism. Recent pro-Russian hacktivist campaigns have spread to other EU nations and NATO members. Germany, the United Kingdom, and Spain have been observed to be priority targets, with threat actors targeting public transportation, federal and security agencies, municipal government and utilities, financial markets, and other infrastructure. In some cases, hacktivist campaigns manifest in the real-world, with physical sticker drives on municipal streets, alongside doxxing operations releasing alleged personal data and automated scans hijacking exposed CCTV camera systems across Europe.

As hacktivist operations continue to blur the boundary between digital disruption and real-world interference, organizations can no longer view DDoS attacks or low-level intrusions as simple background noise. Protecting critical assets requires proactive visibility into threat actor networks, early detection of targeting narratives, and primary source threat intelligence.
Request a demo today to see how Flashpoint provides actionable intelligence to help security teams, government agencies, and infrastructure providers identify, monitor, and mitigate emerging hacktivist campaigns before they impact operations.
The post The Evolution of Hacktivism in Hybrid Warfare: Modern Tactics and Real-World Impact appeared first on Flashpoint.
Flashpoint’s monthly analysis of insider threat recruitment, illicit access advertising, and threat actor activity targeting enterprise environments.

Unknowingly, a member of key personnel is living two separate lives. On the clock, they are a highly-trusted systems administrator, but in their personal time, they moonlight on the deep and dark web, advertising their trust and access to the highest bidder. One day, they get a simple offer: $15,000 in the crypto of their choice to approve a single push notification at 2 AM. They accept. By morning, the attacker walks away with active domain admin credentials without the need for malware or cracking firewalls.
This is just one example of how insider threats lead to modern enterprise breaches. As perimeter security, EDR coverage, and other security tools mature, threat actors continue to target the human element, seeking employees and contractors willing to provide access to corporate systems or facilitate fraudulent activity.
In a threat landscape where identity is becoming the primary attack surface, monitoring illicit marketplaces and recruitment efforts is critical. This new monthly report leverages Flashpoint’s Primary Source Collection (PSC) to analyze insider threat tactics, tracking active recruitment and advertising on dark web forums and encrypted networks.
In September 2026, Flashpoint analysts identified a total of 9,787 insider-related posts across 1,216 channels and 1,778 authors. While the volume of observed activity decreased, threat actors continued to actively seek and advertise insider access, particularly within industries where legitimate employee privileges can be exploited to facilitate fraud. These communications included threat actors attempting to recruit insiders at target organizations, insiders advertising their services, and general discussions involving insider-related threat activity.
Of these communications, Flashpoint observed 857 unique posts between September 1 and September 30, 2026.

The majority of these posts appeared in mid-tier English-language Telegram channels, where threat actors sought or advertised insider access to organizations across several industries. Much of the observed activity focused on recruiting insiders to facilitate fraud operations.
Retail, telecommunications, and financial services remained prominent targets for insider threat activity in September 2026. However, a significant portion of the observed activity could not be attributed to a specific industry.
Flashpoint found that 45.7% of unique insider posts fell into the “Unknown” category, meaning analysts could not determine the targeted organization or industry. Among posts with an identifiable industry, retail accounted for the largest share, followed by telecommunications, financial services, and technology.
Together, these four industries accounted for 419 unique posts, or nearly 49% of all unique insider-related activity observed during the month.
The concentration of activity in retail, telecommunications, and financial services reflects continued threat actor interest in insiders who may be positioned to facilitate fraud, provide access to customer accounts, or exploit legitimate organizational privileges.

The following table shows a breakdown of unique insider posts by industry in September 2026:
| Industry | Posts |
| Other | 392 |
| Retail | 135 |
| Telecom | 116 |
| Financial | 85 |
| Technology | 83 |
| Public Sector | 41 |
| Healthcare | 3 |
| Media | 2 |
| Total | 857 |
Active insider threats generally involve two types of activity: an insider is recruited by a malicious outside party, or an insider advertises their access and services to interested threat actors. These arrangements can enable adversaries to exfiltrate sensitive data, install malware, compromise accounts, or carry out fraudulent activities such as SIM swaps.
In September 2026, Flashpoint analysts identified 15 notable insider recruitment and advertising posts across underground communities and chat forums. Of these, nine involved threat actors attempting to recruit insiders, while six involved actors advertising insider services.
Telecommunications accounted for the largest number of notable posts, with five instances of recruitment or advertising. Retail and technology followed with three each, while financial services and the public sector accounted for two each.
These examples illustrate how threat actors continue to seek access across industries, with particular interest in employees and contractors who can facilitate fraud or provide privileged access to organizational systems.
Flashpoint also observed numerous insider solicitations repeated across multiple discussion threads, often with limited details about the access or services being offered. Analysts could not independently verify the legitimacy of the recruitment and advertising claims.

Insider threats are inherently difficult to detect using internal security controls alone because the malicious activity relies on valid credentials and legitimate access privileges. Relying solely on internal logs means security teams often only detect an insider threat after data exfiltration or system sabotage has already occurred.
Flashpoint protects organizations against insider threats through our Primary Source Collection (PSC) and specialized intelligence platforms:
To learn more about how Flashpoint can help protect your enterprise from insider risk and monitor illicit underground communities, Request a Demo Today.
What is the Flashpoint Insider Threat Report?
The Flashpoint Insider Threat Report is a monthly intelligence brief that analyzes trends, volume, targeted industries, and tactics surrounding insider threat recruitment and illicit access advertising on the deep web, dark web, and encrypted chat channels.
How does Flashpoint collect insider threat data?
Flashpoint collects data using its Primary Source Collection (PSC) engine, which actively monitors thousands of dark web forums, illicit marketplaces, and underground chat networks where threat actors and malicious insiders communicate.
What is the difference between insider recruitment and insider advertising?
Insider recruitment occurs when an external cybercriminal attempts to entice a corporate employee into assisting with a cyberattack. Insider advertising occurs when an employee or contractor proactively lists their legitimate access or services for sale on illicit marketplaces.
The post Insider Threat Report: Dark Web Recruitment & Access Trends appeared first on Flashpoint.

In this post, we preview the critical findings of Flashpoint’s Global Threat Intelligence Report: 2026 Midyear Edition.

In the first half of 2026, the global threat landscape reached a clear operational inflection point: threat operations have fundamentally transitioned from human-led campaigns to machine-speed, AI-driven exploitation. As threat actors gain commoditized access to open-source AI technologies and actively deploy automated, safeguard-free tooling locally on private infrastructure, organizations face an accelerating hybrid risk environment.
The Flashpoint Global Threat Intelligence Report: 2026 Midyear Edition anchors security leaders—from threat intelligence, vulnerability management, to executive leadership—in the data required to navigate this evolving threat landscape. Covering the period from January 1 to June 30, 2026, the report delivers timely insights backed by Flashpoint’s proprietary primary-source collection from over 3.9 petabytes of continuously monitored illicit sources.
Our midyear findings reveal several key metrics that highlight the speed and scale of the H1 2026 threat landscape:
Download the Flashpoint Global Threat Intelligence Report: 2026 Midyear Edition to gain:
“AI is compressing the time between opportunity and exploitation. Capabilities that once took significant expertise, coordination, and time to develop are becoming faster to build, easier to scale, and harder to detect. Security teams are facing an adversary ecosystem that can use AI to iterate at unprecedented speed — the only way to keep pace is with primary-source intelligence that surfaces adversary behavior before attacks unfold.”
Josh Lefkowitz, Flashpoint Co-Founder & CEO
During the first half of 2026, Flashpoint captured over 22M illicit posts discussing or advertising AI for criminal-related activities. By stripping ethical safeguards, custom malicious LLMs allow unsophisticated threat actors to automate complex phases of the attack lifecycle, including target profiling, malware evasion script creation, and zero-day exploit generation.
Infostealer malware harvested 1.7 billion credentials across 7.4 million compromised systems in H1 2026 alone, turning digital identity into the main entry point for enterprise intrusions.
19% (4,015) of all H1 2026 vulnerability disclosures arrived with ready-made exploit code. Adversaries deploy automated replication scripts almost immediately upon disclosure, eliminating manual remediation windows.
Despite a 45% surge in victim volume (6,256 overall), total on-chain revenue fell by 8% to $820M. Improved enterprise backups and incident response have driven payout rates down to 28%, prompting syndicates to demand larger sums from paying victims.
The data shows that traditional enterprise security organizations are struggling to keep pace with modern threat cycles that are accelerated by illicit uses of AI. This continued convergence of AI engines and initial access vectors have further compressed attack timelines, making it nearly impossible for security teams to defend against them—especially if they are limited by traditional approaches to threat intelligence.
Equipping your team with primary-source threat intelligence is critical for protecting critical assets in 2026. Download the Flashpoint Global Threat Intelligence Report: 2026 Midyear Edition to gain the visibility and strategic clarity required to defend your organization.
The post Navigating AI-Driven Cyber Threats: Insights from Flashpoint’s 2026 GTIR Midyear Edition appeared first on Flashpoint.
The attacks targeted the US Department of Education and Library and Archives Canada, and researchers linked some agents to OpenAI.
The post AI Agents Aimed SQL Injection at US and Canadian Government Sites appeared first on SecurityWeek.
CVE-2026-104286 is a critical-severity path traversal vulnerability that could allow attackers to write arbitrary files to the system.
The post Exploited Fortinet FortiMail Zero-Day Calls for Urgent Action appeared first on SecurityWeek.
Rob Juncker is chief product and technology officer at Mimecast. Is he a hacker? “Unequivocally yes,” he says.
The post Hacker Conversations: Rob Juncker, a Knock at the Door and a Moral Compass appeared first on SecurityWeek.
According to this year’s Microsoft Digital Defense Report, government agencies and services were the sector most impacted by cyber threats in 2026, accounting for 27% of observed activity, up from 17% in 2025. Governments are also the most frequently targeted sectors for nation-state activity. They are attractive targets because they hold sensitive information, operate essential services, and sit at the center of networks of agencies, contractors, technology providers, and critical infrastructure operators.
Dwell time, the period between when an attacker gains access and when defenders detect and stop them, also increased this year across multiple sectors. While organizations responded faster once an intrusion was identified, detecting threats early remains a challenge. Attackers increasingly gain access through techniques that mimic legitimate activity, making malicious behavior harder to spot. For example, phishing accounted for 23% of observed intrusions in 2026, up from 7% in 2025, highlighting the continued importance of compromised identities as an entry point for broader attacks.
Taken together, the implication for governments is clear. Security in the AI era is no longer simply about preventing individual intrusions. It is about ensuring institutions can operate effectively in an environment where risks are interconnected, threats move faster, and attackers remain hidden longer. Public-private partnerships are also more important than ever for securing critical government infrastructure and developing the policies and regulations needed for emerging technologies.
In this year’s report, which examines cyber threat trends observed between July 2025 and June 2026, Terrell Cox, Microsoft’s Corporate Vice President & Deputy Chief Information Security Officer, and I explore how these dynamics are reshaping cyber risk. In a companion blog, Terrell takes a closer look at what these findings mean for CISOs and security professionals.
AI is compressing the window for action. Adversaries are moving faster. A vulnerability’s discovery in the wild to active weaponization can be well below 24 hours. While the number of publicly disclosed software vulnerabilities (commonly tracked as CVEs) is projected to reach a record 72,000 in 2026.
Governments best prepared for the future will be those that can rapidly gather and assess information, make decisions, coordinate across institutions and industries, and communicate effectively during a crisis. This requires clearly defined responsibilities and trusted relationships established before an incident occurs, enabling swift and coordinated action when it matters most.
AI is becoming part of the infrastructure that governments, businesses, and citizens rely on every day. As governments continue to adopt AI across public services and encourage its broader use, they should approach its security as a resilience challenge rather than a narrow technical issue.
AI systems depend on interconnected infrastructure, data, models, applications, suppliers, and governance processes. Governments should promote security across this ecosystem through secure-by-design practices, testing and evaluation, stronger supply chain protections, transparency, accountability, and international cooperation on AI risk.
The goal is not to create a separate AI security agenda. It is to integrate AI security into broader efforts to protect critical infrastructure and build national resilience.
Governments may not immediately know whether an intrusion is criminal, geopolitical, or something else. Cybercriminals and nation-state actors pursue different objectives, but increasingly rely on many of the same entry points, including compromised identities, exposed applications, social engineering, and legitimate administrative tools.
Microsoft found that 52.2% of intrusions involving valid accounts resulted in additional credential theft, highlighting how quickly attackers can expand beyond an initial foothold. A seemingly isolated compromise can evolve into ransomware, espionage, data theft, or disruption of essential services.
Governments should therefore assess incidents not only by how they begin, but by where they could lead. Response plans should account for the suppliers, partners, and service providers supporting critical functions. As attacks expand beyond their initial targets, they can also cross organizational, sectoral, and national boundaries, reinforcing the need for global collaboration.
A compromised account at one organization may provide early warning of a broader campaign. Signals that appear inconclusive in isolation can reveal coordinated activity when combined across organizations and jurisdictions. Modern cybercrime operates through interconnected networks of actors, services, and infrastructure that no single institution can fully see or disrupt on its own.
Information sharing must be timely, trusted, and two-way—also known as bidirectional. The goal is not simply for companies to report threats to government. Public agencies should also return actionable intelligence, guidance, and warnings that help organizations protect their networks, customers, and operations. Trusted channels can enable this exchange among government agencies, law enforcement, critical infrastructure operators, technology providers, and international partners while respecting legal and privacy requirements.
Policymakers can support this cooperation through protections for good-faith information sharing, common anonymization standards, and investment in shared threat intelligence and detection capabilities. Information sharing should also lead to action, including investigations, disruption efforts, and accountability for those responsible for serious cyber intrusions.
The organizations governments depend on to deliver public services, including transportation systems, communications infrastructure, schools, universities, and critical infrastructure operators, are increasingly targeted by cyber threats. Resilience therefore requires understanding not only government systems, but the broader ecosystem that supports them.
Planning documents alone are not enough. Governments should regularly conduct tabletop exercises bringing together policymakers, operational leaders, law enforcement, critical infrastructure operators, and private-sector partners to test how they would respond to incidents disrupting essential services. These exercises can expose gaps in decision-making, information sharing, public communications, and cross-sector coordination before a real-world crisis. Microsoft’s work through initiatives such as the Advancing Regional Cybersecurity (ARC) program, most recently in Kenya, illustrates how scenario-based exercises and cross-sector collaboration can help strengthen preparedness and response capabilities across the broader ecosystem.
Government leaders should also know which services are most critical, which identities, systems, suppliers, and infrastructure support them, and how incidents will be escalated. Shared-service approaches can help extend security and response capabilities to local governments and public institutions that cannot build them independently.
As cyber incidents cross organizational and national boundaries, resilience depends not only on technical preparedness, but on whether institutions can coordinate effectively under pressure.
In an era of AI-enabled and increasingly interconnected cyber threats, resilience is no longer simply about recovering from an attack. It is about preparing for a world in which cyber incidents move faster, spread further, and affect more organizations than ever before. Governments best prepared for the future will be those that can contain harm, adapt quickly, and continue delivering critical services when citizens need them the most.
The post Preparing governments for an era of interconnected cyber risk appeared first on Microsoft On the Issues.

Flashpoint was awarded U.S. Patent No. 12,705,360 for its Ransomware Risk model, which rates how closely new vulnerabilities match those used in ransomware attacks.

Vulnerability and exposure management (VM) teams need critical metadata and context that clearly show which issues pose an immediate risk to their organization. While traditional VM frameworks tell defenders how severe a vulnerability may be, they do not provide visibility into how likely threat actors are to exploit it. This leaves security teams overwhelmed in patch backlogs without a clear strategy for prioritization.
Nowhere is this prioritization gap more dangerous than with ransomware. Ransomware-as-a-Service (RaaS) groups no longer choose targets at random. They look for specific technical conditions that make vulnerability exploitation easy, fast, and repeatable. With RaaS attacks rising by 45% period-over-period in H1 2026, organizations need a way to identify the specific traits that make a vulnerability attractive to ransomware operators before an attack occurs.
Flashpoint built the Ransomware Risk score into Flashpoint Vulnerability Intelligence to solve exactly this problem. Since 2022, it has rated newly discovered vulnerabilities based on how closely they resemble those known to be used in ransomware attacks. With the grant of the U.S. Patent No. 12,705,360 on August 11, 2026, the methodology behind the score is now formally patented. This milestone formalizes Flashpoint’s ability to cut through the noise with a proven, threat-informed signal that gives defenders the clarity they need to act on Day Zero.
“As vulnerability disclosures surge, prioritization is more important than ever for security teams. A severity score alone can’t tell you which vulnerabilities pose the greatest real-world risk of exploitation by ransomware actors.
Our patented Ransomware Risk model applies years of threat intelligence to that problem, giving customers an earlier signal and helping them prioritize based on how attackers actually operate.”
josh lefkowitz, co-founder and ceo at flashpoint
The patented system evaluates newly disclosed vulnerabilities against the patterns shared by vulnerabilities ransomware groups have exploited. Rather than trying to predict what threat actors will do next, the model learns what past ransomware-exploited vulnerabilities have in common and compares each new flaw against those patterns.

Every vulnerability ingested into Flashpoint Vulnerability Intelligence is profiled against more than 60 distinct technical factors. This “fingerprinting” links the vulnerability to key inputs including whether the flaw is remotely exploitable without authentication, whether it affects SCADA or Operational Technology (OT) systems, and its potential impact on data availability, which is central to extortion schemes.
The model turns each multi-factor fingerprint into a set of values that place it as a single point on a map, so vulnerabilities with similar profiles land close together.
Flashpoint overlays historical threat data onto the map to establish neighborhoods where vulnerabilities previously exploited in real-world ransomware attacks aggregate.
When a new vulnerability is ingested, its coordinates are checked against these neighborhoods. The scoring system calculates its spatial proximity to known ransomware vectors and assigns a clear rating: Low, Medium, High, or Critical.
This four-step method, developed by Flashpoint’s Ben Haynes and Jacob Kouns, is the basis of U.S. Patent No. 12,705,360.
By translating complex structural attributes into a single risk score, the patented model delivers four key operational advantages:
Flashpoint’s Ransomware Risk model is built to enhance, not replace the vulnerability management frameworks organizations already rely on. In fact, it provides even greater value for security teams as our Ransomware Risk model provides clarity for every vulnerability detailed by Flashpoint Vulnerability Intelligence, including over 105,000 issues missed by CVE and NVD.
Within Flashpoint Ignite, security teams have a complete view of vulnerability risk, seeing the score alongside CVSS (v3 and v4), EPSS, Social Risk, and exploit maturity.

Vulnerability management requires more than cataloging. It demands threat-informed prioritization that aligns security operations with real-world business risk. Flashpoint’s patented Ransomware Risk model eliminates guesswork by surfacing the flaws that match the profile of known ransomware targets, allowing security teams to patch what matters most, first.
By combining proprietary knowledge of vulnerability architecture and ransomware attacks, Flashpoint bridges the gap between theoretical and active exposure. Request a demo today to see how our Ransomware Risk model provides the definitive signal needed to stay ahead of extortion groups.
What is the Ransomware Risk score?
The Ransomware Risk score is a rating in Flashpoint Vulnerability Intelligence that shows how closely a vulnerability resembles those known to be used in ransomware attacks. Each vulnerability is rated Low, Medium, High, or Critical, so security teams can see which ones to patch first to reduce their ransomware exposure.
How is Ransomware Risk different from CVSS and EPSS?
CVSS measures how severe a vulnerability could be, and EPSS estimates how likely it is to be exploited in general. Ransomware Risk adds a ransomware-specific signal that works alongside both, showing how closely a vulnerability matches those ransomware groups have used. In Flashpoint Ignite, all three scores appear together.
What does Flashpoint’s ransomware patent cover?
U.S. Patent No. 12,705,360, granted August 11, 2026, covers Flashpoint’s method for rating how likely a vulnerability is to be used in a ransomware event. Each vulnerability is profiled on more than 60 factors, compared with vulnerabilities used in past ransomware attacks, and rated by similarity. The patent formalizes the model behind the Ransomware Risk score, live since 2022.
How often are Ransomware Risk scores updated?
Ransomware Risk scores update in near real time, so new vulnerabilities are rated as soon as they’re disclosed. The model also keeps adjusting as new vulnerabilities join the body it compares against, so ratings reflect the ransomware landscape as it stands today.
The post Ransomware Risk Model: Flashpoint’s Patented Scoring Method to Inform Vulnerability Prioritization appeared first on Flashpoint.
The accord opened the door to future regulation but focused on four voluntary steps for the companies to take.
The post Trump Says Top Tech Firms Have Signed Accord to ‘Self-Police’ AI Development appeared first on SecurityWeek.