From August 3, 2026, Google will use IP addresses from UK, EEA and Switzerland users for ad measurement and personalization. It lands as the ICO weighs new consent rules, and years after Google itself called using such signals to identify devices "wrong." [...]
We’ve been thinking deeply about enterprise security. The operating model that served us for the past decade (collect telemetry, store it, query it, build dashboards to watch it) is no longer keeping pace. We need to shift to the new world: telemetry, context, reasoning, and actions. An approach that produces outcomes. The latest cybersecurity frontier models further made this shift urgent. Models like Claude Mythos can now find software vulnerabilities and reason through complex attack paths at machine-speed, leading to an exponentially increasing backlog of vulnerabilities.
Introducing AWS Continuum for code vulnerabilities
Today, we’re announcing AWS Continuum for code vulnerabilities, now available in gated preview. Continuum for code vulnerabilities addresses the full lifecycle of a code vulnerability at machine speed: from discovery through actions. It reasons over your environment, confirms what is real, and drives toward resolution. It’s model agnostic, using multiple frontier models where each performs best, and is built to incorporate the latest and most capable models as they emerge.
Continuum is built on lessons learned from running security across AWS and Amazon.com. Securing businesses that operate in different industries required a system that understands business context rather than applying generic rules uniformly.
How it works
Continuum for code vulnerabilities reasons over your full environment. This context includes structured data already living in Amazon Web Service (AWS) (your infrastructure, permissions, network topology, code) and the unstructured data that captures how your organization operates and your risk profile (your documents, communications, business priorities).
Continuum for code vulnerabilities operates in four continuous phases.
Discovery: Security teams tackle a backlog of vulnerabilities, and many are already using frontier models to find more. Continuum starts by ingesting that existing backlog and performing its own vulnerability scan of your environment. This creates a more comprehensive view of vulnerabilities and the associated attack paths.
Prioritization: Continuum uses context to evaluate, enrich, and prioritize every finding. Is the affected component deployed, is it reachable, is it in a production path, and what would the business impact be if exploited? The result is an evidence-backed list of priorities, allowing Continuum and your team to focus on what’s most important.
Validation: Continuum validates findings to surface false positives before they waste your team’s time. It contextualizes vulnerabilities against your environment. It then constructs working exploit examples in a sandboxed environment that provide concrete, reproducible evidence of the issue.
Mitigation and remediation: Continuum assesses existing defenses around a validated issue, including blocking and compensating controls along with detection mechanisms. It then draws on its understanding of the codebase, context, and findings to recommend mitigation or remediation of the vulnerability with a network change, policy change, or code patch. The patch recommendation is validated using the same system that confirmed the vulnerability. It also provides blast radius visibility and rollback paths where feasible.
This is just the beginning. We’re starting with code (1st and 3rd party) and then expanding to other aspects of security.
Trust is graduated
Continuum starts in learn mode with a human in the loop. Every recommendation includes the reasoning behind it. As you gain confidence, you can graduate Continuum to enforce mode, enabling remediation that can be increasingly automated based on categories and risk profiles you define.
Continuum capabilities
In addition to Continuum for code vulnerabilities, Continuum includes capabilities you might already know. The AWS Security Agent penetration testing and code scanning functionality is now part of Continuum as Continuum pen testing and Continuum code scanning (Preview). We’re also launching Continuum threat modeling in preview, which automatically generates comprehensive threat models from design documents or source code and outputs results in STRIDE format. These capabilities serve as detection and analysis sources that feed into the broader Continuum loop of discovery, prioritization, validation, and remediation.
Getting started
We’re working with customers across financial services, automotive, and technology to shape AWS Continuum. Customer feedback confirms the direction: security teams want tools that earn trust and take action.
AWS Continuum for code vulnerabilities is available in gated preview. Sign up to request access at AWS Continuum.
If you have feedback about this post, submit comments in the Comments section below.
A newly discovered data leak dubbed "FortiBleed" has exposed what appears to be a collection of Fortinet and FortiGate VPN credentials for 73,932 firewall URLs at organizations worldwide. [...]
Account takeovers are rising as attackers bypass traditional defenses through phishing, session hijacking, and MFA fatigue. Specops Software explores how device trust and continuous verification help reduce account takeover risk. [...]
India has banned Telegram until June 22 after the app was used to circulate leaked exam papers. CEO Pavel Durov accuses telecom Reliance of BGP hijacking that disrupted the app as far away as the UAE. Here's what happened, and how to get around the block with an MTProto proxy. [...]
AI security is getting attention because AI has stopped being a side experiment. It is now part of how work gets done. Employees use copilots to write, research, code, and analyze. Product teams are adding AI into customer experiences. Developers are building applications on top of foundation models. Business teams are experimenting with agents that can read email, summarize documents, query data, and trigger workflows. That is a very different world from the one many AI review processes were designed for. An AI system can pass a benchmark and still fail in production. It can behave safely in a clean test environment and then encounter real […]
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch a maximum-severity flaw in the Widget Factory Joomla Content Editor (JCE) plugin that is being actively exploited in the wild. [...]
Kodak has confirmed that it's working with external cybersecurity experts to investigate a security breach after hackers gained access to some of the company's data. [...]
Threat actors are abusing Steam Workshop, Valve's community hub for downloading game-related content, to push various malware hidden in wallpaper packages. [...]
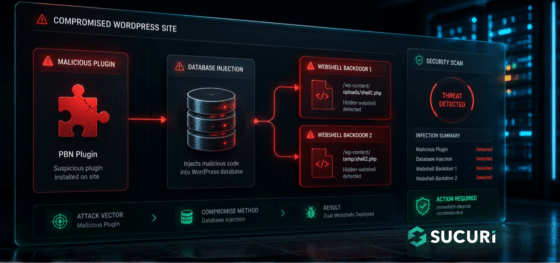
During a recent incident response engagement, our team uncovered a multi-stage WordPress infection that goes beyond the usual file-based malware. The attacker combined a fake plugin, a remote command-and-control server, and two PHP web shells stored directly inside the WordPress database.
The campaign is operated by a Turkish-speaking threat actor and is built around a classic SEO monetization scheme: hidden backlink injection for a Private Blog Network (PBN), most likely tied to the gambling and adult affiliate niche.
In this blog post you’ll learn how to detect and prevent subdomain takeover – a tactic where threat actors exploit dangling DNS records to redirect traffic to attacker-controlled resources. We’ll explain the issue, how the situation arises, and how you can use various AWS features and services to help mitigate the impact of this tactic.
Under the shared responsibility model, securing configurations in the cloud is your responsibility. AWS supports you through strong defaults, guidance in the Security Pillar of the Well-Architected Framework, and security services to help you meet that responsibility. The AWS Customer Incident Response Team (AWS CIRT) also monitors for new and trending tactics that threat actors use to exploit specific customer configurations, so that you can make informed design decisions and improve your response plans.
AWS CIRT has observed threat actors actively scanning for public DNS CNAME records that point to resources that no longer exist, looking for subdomain takeover opportunities.
Note: The subdomain takeover tactic does not leverage vulnerabilities of AWS services. It exploits a dangling DNS record to redirect traffic to an attacker-controlled resource.
Quick DNS Primer
CNAME Records: A CNAME (Canonical Name) record is a DNS entry that points one domain name to another. For example, api.example.com can be configured to point to api.example.s3-website-us-east-1.amazonaws.com. This feature of DNS enables users to configure a memorable, human-friendly domain name while the actual resource lives at a longer, machine-generated AWS hostname. A security issue emerges when the target resource is deleted but the CNAME record pointing to it remains – creating a “dangling” record.
Dangling Records: When a resource (like an S3 bucket) is deleted but the DNS record pointing to it is left behind, that DNS record becomes “dangling”, pointing to a resource that no longer exists. For resources in globally shared namespaces, threat actors can potentially reclaim the name of your deleted resource and serve malicious content through your DNS record.
What is subdomain takeover?
A subdomain is a prefix added to a domain that allows you to organize access to your resources. A subdomain takeover occurs when you delete the underlying resource and a threat actor creates a new resource with the same name to take advantage of the DNS records still pointing to it.
A subdomain takeover is possible when a CNAME record points to an AWS resource that uses a globally shared DNS namespace where the resource name can be chosen by any AWS customer. The following AWS resources meet these criteria:
Amazon S3 (global namespace): Bucket names like mybucket.s3.amazonaws.com are globally unique and can be claimed by any account if the bucket is deleted. Note: S3 buckets created with account regional namespaces (launched March 2026) are scoped to your account and are not subject to this issue.
Amazon CloudFront: Distribution domain names like d111111abcdef8.cloudfront.net are assigned by AWS and cannot be chosen by an attacker. However, if you delete a distribution and another customer creates one that happens to receive the same domain name, a dangling CNAME could resolve to their content.
AWS Elastic Beanstalk: Environment names like myapp.elasticbeanstalk.com are globally unique and can be claimed by any account if the environment is terminated.
Resources like Amazon VPC, Amazon EC2 instances, or private hosted zones are not subject to this tactic because they do not expose globally claimable DNS namespaces.
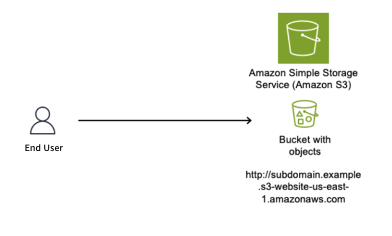
You create a DNS CNAME record pointing to your S3 website endpoint. The subdomain subdomain.example.com now resolves to subdomain.example.s3-website-us-east-1.amazonaws.com, which serves content from the S3 bucket named subdomain.example. If your team deletes the bucket and forgets to delete the DNS record, users that navigate to the site will see an error stating that the bucket doesn’t exist. However, at this point, if a threat actor sees this error and moves in to claim the bucket name, they will be able to set up their own site that users will see when they navigate to the subdomain.example.com site.
Figure 1 shows an S3 bucket named subdomain.example (a globally unique bucket name) configured to host a static website, with the S3 website endpoint subdomain.example.s3-website-us-east-1.amazonaws.com.
Figure 1: S3 bucket configured as a static website
As shown in Figure 2, we use Amazon Route 53 to create a CNAME record to resolve to our Amazon domain name; to give users a friendly name and so they do not have to remember the long S3 website name in URLs.
Figure 2: DNS Resolver configured with CNAME record pointing to origin bucket
The customer’s AWS administrator decides to stop serving content from the S3 bucket and deletes it, as shown in Figure 3.
Figure 3: Resource deleted without removing the CNAME record
With the S3 bucket deleted and the CNAME record still in place, the DNS record is now dangling. A threat actor identifies this situation and creates a new S3 bucket with the same global name subdomain.example in an AWS account that the threat actor controls, as shown in Figure 4. The threat actor can now serve content from this new bucket, including potentially malicious content. End users remain unaware of this switch and continue to access subdomain.example.com, trusting the content because it appears to originate from a URL they recognize.
Figure 4: Subdomain takeover happens
Potential impacts of a sub-domain takeover
Consider these potential impacts:
Reputation risk: There is a potential risk to your organization’s reputation, because you don’t control the content being served from the threat actor’s site that your DNS record points to.
Potential exposure to phishing campaigns: Users within your organization might have the subdomain bookmarked in their browser, not knowing the resource is no longer available, then unsuspectingly navigate to the site that now hosts malware or is used to phish user credentials.
Blocking: If the subdomain is flagged by security vendors for malicious activity, it could impact your business operations.
Financial loss: Subdomain takeover incidents can result in a financial impact due to the potential disruption to service delivery as you deal with the event.
Proactive detection
AWS Config for proactive detection
For proactive detection, you can use AWS Config to continuously monitor your Route 53 CNAME records and verify that the target resources exist in your account.
Prerequisite: This approach requires AWS Config recorder to be enabled for the resource types you want to monitor (S3 buckets, CloudFront distributions, Elastic Beanstalk environments). If Config isn’t recording a resource type, it won’t appear in the inventory check. For more information, see Setting up AWS Config with the console.
Why use AWS Config inventory instead of DNS resolution checks?
A common approach is to check whether a CNAME resolves to a valid endpoint. However, this method has a critical flaw: if an attacker has already claimed the resource, DNS resolution will succeed – to their resource, not yours. You would have no indication that you don’t own what’s responding.
By querying AWS Config’s recorded configuration items, you’re checking whether the resource exists in your account inventory, not just whether something responds at that DNS name. This approach correctly identifies dangling CNAMEs even after a takeover has occurred.
Implementation approach:
Account-level vs. organization-level scope
The reference implementation queries AWS Config inventory within a single account. This means that if a CNAME record in Account A points to a resource that legitimately exists in Account B within the same AWS organization, the rule will flag it as NON_COMPLIANT.
For organizations that share resources across accounts, you can modify the solution to use an AWS Config Aggregator, which queries resource inventory across all accounts in your organization. This is similar to how IAM Access Analyzer supports both account-level and organization-level scopes. To use this approach, you need an organization-level Config Aggregator already configured, and the Lambda function’s IAM role needs the config:SelectAggregateResourceConfig permission.
We recommend starting with account-level scope for simplicity, then expanding to organization-level if your environment includes cross-account resource sharing.
The main idea is to create a custom AWS Config rule that queries your Route 53 hosted zones for CNAME records, then parses each CNAME target to determine whether it points to a known AWS resource pattern such as S3, CloudFront, or Elastic Beanstalk. For each match, the rule cross-references the target against your AWS Config inventory to verify that the resource actually exists in your account. If the resource isn’t found, the rule marks the CNAME record as NON_COMPLIANT, surfacing it for review.
The Config rule should focus on known AWS resource patterns:
Note: CNAME records pointing to external third-party services are outside the scope of this detection mechanism, as those resources won’t appear in your AWS Config inventory.
NON_COMPLIANT findings from your Config rule can be routed to AWS Security Hub for centralized visibility, or trigger SNS notifications to alert your security team.
Figure 5: Dangling DNS Detection Solution
Reference implementation:
We’ve published a complete implementation of this detection approach as an open-source solution. The solution deploys a Lambda function that discovers CNAME records across all your Route 53 hosted zones and uses pattern matching to identify targets pointing to S3, CloudFront, and Elastic Beanstalk. It then queries your AWS Config inventory to verify whether each target resource still exists in your account. When a dangling record is detected, the solution generates a HIGH severity finding in Security Hub and can optionally send SNS notifications to alert your security team. A CloudWatch metrics dashboard is also included for ongoing compliance tracking.
Deployment:
# Clone the repository
git clone https://github.com/aws-samples/sample-dangling-dns-detection
cd sample-dangling-dns-detection

# Build the Lambda deployment package
./scripts/package.sh

# Upload to S3
aws s3 cp dist/dangling-dns-detection.zip s3://YOUR_BUCKET/

# Deploy the CloudFormation stack
aws cloudformation deploy \
  --template-file infrastructure/template.yaml \
  --stack-name dangling-dns-detection \
  --parameter-overrides \
      LambdaCodeS3Bucket=YOUR_BUCKET \
      EvaluationFrequency=TwentyFour_Hours \
  --capabilities CAPABILITY_NAMED_IAM
The stack creates an AWS Config custom rule that runs on your specified schedule (default: every 24 hours), evaluating all CNAME records and reporting compliance status.
Mitigating the effects
Mitigating subdomain takeover requires both preventive procedures and responsive capabilities.
Prevention: Standard operating procedure
The most effective mitigation is a standard operating procedure for resource deprovisioning that ensures DNS records are removed before the underlying resource:
Within your DNS zone, delete the CNAME record that points to the fully qualified domain name (FQDN) of the resource that you plan to deprovision.
Wait for the DNS TTL to expire before deleting the resource. DNS resolvers cache records for the duration of the TTL (for example, a TTL of 3600 means resolvers may serve the old record for up to one hour). If you delete the resource before the TTL expires, a threat actor could claim the resource name while cached CNAME entries are still directing traffic to it.
Deprovision the resource that you no longer want to use.
Run a DNS check of the CNAME record that you removed to verify that the resource is no longer resolving.
Key principle: Always delete DNS first, wait for the TTL to expire, then delete the resource. This order eliminates the window where a dangling record could be exploited.
Prevention: S3 account regional namespaces
As mentioned earlier, AWS introduced account regional namespaces for Amazon S3 general purpose buckets in March 2026. While this is a meaningful step toward mitigating the S3-specific takeover vector, there are important operational limitations to be aware of:
Existing buckets are unaffected. Buckets already created in the global namespace cannot be migrated to an account regional namespace. The bucket names remain globally unique and claimable by anyone if the bucket is deleted.
Global namespace is still the default. When creating a new bucket through the console, CLI, or SDK, the global namespace remains the default selection. Users who aren’t aware of the new option will continue creating globally-scoped buckets.
Existing IaC templates require updates. Existing infrastructure-as-code templates (CloudFormation, CDK, Terraform) that don’t explicitly opt in to the account regional namespace will continue provisioning buckets in the global namespace. For CloudFormation, this means setting the BucketNamespace property to account-regional. For other IaC tools, consult their documentation for the equivalent configuration. Organizations need to audit and update their templates to opt in.
For these reasons, the dangling DNS detection approach described in this post remains critical – particularly for organizations with existing S3 infrastructure, and for CloudFront, and Elastic Beanstalk resources where no equivalent namespace scoping exists.
Response: Notification and remediation
When a dangling DNS record is detected, the reference solution described in the Detection section automatically creates a HIGH severity finding in AWS Security Hub and reports the CNAME record as NON_COMPLIANT in AWS Config. If you provide an SNS topic ARN during deployment, the solution also sends notifications to alert your security or operations team via email, Slack, or other channels. For production environments, consider a human-in-the-loop workflow where these notifications are reviewed by a team member who approves the DNS record deletion before it’s executed. This prevents accidental deletion of legitimate records during transient issues.
The reference solution also includes a CloudWatch dashboard for tracking compliance status and evaluation metrics over time, giving your team ongoing visibility into DNS health across your hosted zones.
Note: Fully automated remediation (auto-deleting DNS records) carries risk – a false positive could disrupt legitimate services. We recommend starting with detection and notification, then evaluating automation based on your detection accuracy and operational maturity.
Conclusion
Subdomain takeover is a preventable misconfiguration that can have significant impact on your organization. A layered defense approach provides the best protection:
Prevention: Implement a standard operating procedure that deletes DNS records before deprovisioning the underlying resource.
Detection: Use AWS Config custom rules to proactively identify CNAME records pointing to resources that no longer exist in your account.
Response: Configure notifications through SNS or Security Hub so your team can respond quickly when dangling records are detected.
Monitoring: Maintain ongoing visibility through CloudWatch dashboards to track DNS health and compliance status.
The key insight is that good DNS hygiene – knowing when your CNAME records point to a nonexistent resource – is your first line of defense. Automated detection through AWS Config provides a safety net when operational procedures fail. And if you detect an issue, having a playbook ready to enact your response can lower the impact and your mean time to recovery.
If you have feedback about this post, submit comments in the Comments section below.
Opening a new social media account in the UK will soon mean proving you're over 16 with an ID upload or a facial age scan, under a government ban on under-16s taking effect in spring 2027. Security experts warn the age checks are easy to circumvent and create new data-breach risks. [...]
GhostTree uses recursive NTFS junctions to generate vast numbers of valid Windows file paths. Varonis explains how the technique could cause Microsoft Defender folder scans to never complete, leaving malware undetected. [...]
The U.S. Federal Trade Commission (FTC) warned that Americans lost $3.5 billion to imposter scams in 2025, with reported losses nearly tripling since 2020. [...]
Attackers can move from access to exfiltration in 72 minutes. Learn how modern SOC teams close the speed gap with Unit 42's AI-driven automation, threat hunting, MDR and Managed XSIAM.
There is a moment every security analyst knows well. It’s 2am, an alert fires, and you’re staring at a console trying to make sense of what just happened—fast. You need context, scope, and impact: What’s being targeted? Where is it coming from? Is it getting worse? What should we do next?
That moment is exactly what we built the Imperva AI Assistant to improve, starting with Cloud WAF (cWAF) investigations, where speed and clarity matter most.
Security teams are under pressure to investigate threats faster, with fewer resources
Modern application security environments generate a constant stream of signals across events, trends, attack patterns, and security posture. But turning that data into meaningful insight still takes effort. Analysts often move between dashboards, filter logs, and stitch together context across multiple tools to understand what’s happening.
At the same time, teams are expected to do more with less. A persistent skills gap and increasing alert volume mean even routine investigations can take longer than they should, slowing response times and adding pressure to already stretched teams.
The industry’s traditional response has been more dashboards, more saved reports, and more training. We think there’s a better answer: let your team ask the question in plain English and get a structured, security-relevant answer back immediately, grounded in Imperva platform data.
Introducing the AI Assistant.
What is an AI security assistant?
An AI security assistant is a natural-language tool that lets security teams investigate threats by asking questions in plain English, instead of building queries or navigating dashboards, and returns fast, ranked, security-relevant answers grounded in their own platform data. The Imperva AI Assistant brings this capability directly into the Imperva platform, starting with Cloud WAF investigations.
Protect with AI: Making security work faster, simpler, and more accessible
To address this, we’re bringing the power of AI directly into Thales’s Imperva platform.
It builds on AI ExplAIn, the one-click, plain-language explanations we introduced for Imperva Cloud WAF, extending that same clarity from individual blocked requests to full, cross-product investigations.
Our goal is simple: help security teams get answers faster, reduce manual effort, and improve day-to-day productivity.
What the AI Assistant does?
The AI Assistant is designed around three key goals:
Increase productivity
Instead of navigating dashboards or writing complex queries, users can simply ask a question and get an answer immediately.
Make AppSec more accessible
You don’t need deep expertise in Thales or Cloud WAF. The assistant uses natural language, making it easier for more team members to investigate and understand security data.
Support a wide range of use cases
Security questions don’t follow a fixed script. Our assistant can handle a variety of queries, from investigations to trend analysis, without requiring predefined workflows.
Instead of being limited to predefined dashboards or reports, teams can explore questions as they arise, using plain language to surface insights that would be impractical to design into a traditional UI. Because the assistant can draw on signals across the Imperva AppSec platform, it doesn’t just retrieve data – it connects it.
For example, an analyst might ask: “Was the IP that triggered a WAF block also behaving like automated traffic in the same session, and what changed compared to previous activity?”, and get a clear, unified answer in seconds, without having to pivot across tools or manually stitch the data together.
Security investigations, simplified with an AI security assistant
The AI Assistant is a natural-language experience built into the Imperva platform to help security teams investigate faster.
Instead of navigating dashboards or building filters, teams can simply ask:
“What are the top attack source IPs over the last 48 hours?”
“Which URLs are most targeted right now?”
“What types of attacks were blocked on site XYZ.com?”
“What changed between yesterday’s baseline and today’s spike?”
“Are these patterns concentrated in a single source or distributed across multiple locations?”
The assistant responds with a concise, ranked answer, along with a Critical Finding that highlights the security -relevant insight, not just raw data. The assistant can also access all Imperva documentation, so teams can ask “How do I configure…? Or “Where can I find…?” to easily find the information they need.
A real-world investigation, simplified.
Imagine a security analyst investigating a sudden spike in application traffic.
Today, that process often involves switching between dashboards, filtering logs, and piecing together data from multiple sources to understand what’s happening.
With the AI Assistant, the workflow is much simpler.
The analyst can ask:
“What’s driving the spike in traffic today?”
“Are these requests coming from the same source or multiple locations?”
“What has changed compared to yesterday’s baseline?”
Within seconds, the assistant provides a clear, summarized answer, highlighting key trends, identifying the most relevant signals, and surfacing a Critical Finding that explains what matters. Instead of manually connecting the dots, the analyst can quickly understand the situation, prioritize next steps, and respond faster.
Why this matters for security teams
When investigating potential threats, teams need more than confirmation that “something triggered.” They need fast, clear answers that help them understand what’s happening and what to do next.
What’s the pattern? (Is activity concentrated, distributed, or repeating?)
What’s the scope? (Which applications, URLs, geographies, or time windows are affected?)
What’s the severity? (How significant is the signal, and how quickly is it evolving?)
What’s the next best action? (Where should they focus, and what should they mitigate?)
The AI Assistant is designed to answer these questions directly, reducing investigation friction and helping teams move from data to insight, faster.
In practice, this means security teams can move from alert to understanding faster—without adding complexity or changing existing workflows.
Easy to get started
The AI Assistant is built directly into the Imperva AppSec platform, there’s nothing new to install or manage.
It’s available through the Ask AI experience and works within your existing environment, using the same data, workflows, and permissions you already rely on.
Because it’s permission-aware by design, users only see the data they’re authorized to access.
AI capabilities are always optional, customers can choose whether to enable or disable them at any time, ensuring full control over how AI is used in their environment.
Available today
The AI Assistant is currently available under controlled availability for a select group of customers. This phase allows us to refine quality, guardrails, and workflows based on real-world feedback before broader rollout.
Why it matters
AI in security has been discussed for years, often focused on detection and tuning. But the real pressure point has always been the moment of investigation, when teams need to quickly understand what’s happening and decide what to do next.
That’s where the AI Assistant is different. It focuses on turning security data into clear, actionable insight – faster. It doesn’t replace expertise, but it makes effective investigation workflows easier to access across the team.
When fewer people are bottlenecks for interpreting signals, response times improve, escalations reduce, and teams spend less time on repetitive analysis.
The impact is simple: faster decisions, fewer handoffs, and more time spent on the issues that matter most.
The bottom line
Security investigations get faster when teams can turn security data into explanations they trust. The Imperva AI Assistant is designed to shorten the path from alert to decision, starting with Cloud WAF, by helping analysts quickly pull the right data, spot what’s changed, and decide what to do next.
It starts with a question, and an answer you can defend.
Frequently asked questions about the AI security assistant
What is an AI security assistant?
An AI security assistant is a natural-language interface that lets security teams ask questions in plain English and get fast, ranked, security-relevant answers drawn from their own platform data, instead of manually building queries or pivoting across dashboards. The Imperva AI Assistant delivers this inside the Imperva platform, starting with Cloud WAF investigations.
How is the Imperva AI Assistant different from AI ExplAIn? AI ExplAIn gives one-click, plain-language explanations of individual blocked requests in Cloud WAF. The AI Assistant goes further, answering open-ended investigation and trend questions across the Imperva AppSec platform and connecting signals, such as a WAF block and automated-traffic activity, within the same session.
What questions can the AI Assistant answer?
Teams can ask investigative and trend questions such as “What are the top attack source IPs over the last 48 hours?” or “What changed between yesterday’s baseline and today’s spike?” Because it can also read the Imperva documentation, analysts can get configuration and “how do I…” answers in the same place.
Will an AI security assistant replace SOC analysts?
No. The AI Assistant is designed to speed up investigations, not replace expertise. It removes the manual work of pulling and correlating data so analysts can focus on judgment, prioritization, and response.
Is the data the AI Assistant sees kept private and under our control?
Yes. The assistant is permission-aware, so users only see data they are authorized to access, and AI capabilities are optional; customers can enable or disable them at any time.
The major enterprise WAAP solutions evaluated in this guide are Akamai, Cloudflare, F5, Fastly, Fortinet, Imperva, and Radware. In the most recent independent benchmarks, Akamai, Cloudflare, and Imperva were named Leaders in the Forrester Wave: Web Application Firewall Solutions, Q1 2025, while Akamai, Fortinet, and Imperva placed in the Leader category of the AMTSO-certified SecureIQLab Cloud WAAP v4.0 validation. The sections below compare these vendors on security efficacy, API protection, bot defense, operational efficiency, and total cost of ownership so you can match the right platform to your environment.
Web applications and APIs now sit at the center of nearly every digital business, and the threat surface has grown in step. Independent industry analysis estimates that API traffic represents more than 70% of all web traffic, that API related security incidents have climbed to roughly one third of reported data breaches, and that more than a third of recent API breaches trace back to Broken Object Level Authorization (BOLA) flaws.
At the same time, the latest AMTSO-certified SecureIQLab Cloud WAAP v4.0 validation found that average complete-security efficacy across the leading enterprise WAAP solutions declined year over year, even as operational efficiency improved slightly. The takeaway for security leaders is straightforward: WAAP capabilities are diverging across the market, and shortlist decisions made in 2022 or 2023 may no longer reflect current efficacy or operational fit.
This guide focuses on the major WAAP vendors that most frequently appear on enterprise shortlists. It draws on independent SecureIQLab testing, recent Forrester, Gartner, KuppingerCole, and IDC research, and verified peer reviews to help security and risk leaders evaluate platforms across modern, multi-cloud, API-heavy environments without reducing the decision to a generic ranked list.
1. Scope and methodology
This comparison focuses on the major WAAP vendors most commonly evaluated by enterprise buyers: Akamai, Cloudflare, F5, Fastly, Fortinet, and Radware, alongside Imperva. It uses three categories of independently sourced evidence:
Certified independent testing: the 2025 SecureIQLab Cloud WAAP v4.0 CyberRisk Validation, conducted under AMTSO Test ID AMTSO-LS1-TP097, which evaluated 11 enterprise WAAP solutions across more than 1,360 attacks aligned to the OWASP Top 10, OWASP API Security Top 10 2023, MITRE ATT&CK, and the Lockheed Martin Cyber Kill Chain.
Analyst recognition: the Forrester Wave for Web Application Firewall Solutions (Q1 2025), the Gartner Market Guide for Cloud Web Application and API Protection, the KuppingerCole 2025 Leadership Compass for WAAP, the IDC MarketScape for WAAP, and Gartner Peer Insights ratings as of the date of this article.
Verified customer reviews: Gartner Peer Insights, PeerSpot, G2, and TrustRadius user ratings, used as a sentiment signal rather than as a ranking input.
Of the seven platforms covered here, four (Akamai, Cloudflare, Fortinet, and Imperva) completed the public SecureIQLab v4.0 cycle, while three of the competitors (F5, Fastly, and Radware) are listed in the SecureIQLab comparative report as “Contact SecureIQLab” rather than appearing with published v4.0 results. For those three vendors, the profiles below rely on Forrester, Gartner, and verified customer review sources, and head-to-head efficacy comparisons should be confirmed through buyer-led testing.
Other WAAP vendors (for example hyperscaler-native services and specialized API-security vendors) may be relevant for specific buyer needs, but they fall outside the major-vendor scope used here. Buyers should treat this guide as one input among several and validate every vendor claim against their own application portfolio during a proof of value.
2. What is WAAP?
Web Application and API Protection (WAAP) is a category defined by Gartner to describe cloud-delivered services that protect web applications and APIs against runtime attacks. Core capabilities typically include a Web Application Firewall (WAF), distributed denial-of-service (DDoS) protection, advanced bot management, API security, and increasingly client-side script protection.
In practical terms, a WAAP platform sits in front of an application (or a portfolio of applications and APIs) and inspects every request, blocking exploits aligned to the OWASP Top 10 and OWASP API Security Top 10, distinguishing legitimate users from automated abuse, absorbing volumetric and Layer 7 denial-of-service traffic, and providing the visibility security teams need to investigate and tune.
For a foundational explainer, see Imperva’s What is a WAAP? Learning Center article at imperva.com/learn/application-security/web-application-and-api-protection-waap/ (set as an internal link on publish).
3. Why WAAP matters now
Three forces are reshaping WAAP buying decisions in 2026:
API growth is outpacing API security. Independent reporting indicates that API related breaches have moved from a niche concern to roughly a third of all data breaches, while only about one in five organizations rate themselves as highly capable of detecting attacks at the API layer.
Bots and AI-enabled automation are escalating. Public industry data shows AI-enabled bot activity rising sharply year over year, with credential stuffing, scraping, and inventory hoarding increasingly difficult to separate from legitimate users without sophisticated behavioral analytics.
Cloud-native deployment is the new default. As more workloads move inside hyperscale clouds, development teams increasingly prefer security that runs natively within the cloud environment rather than alongside it through external routing that can add latency and operational overhead.
Regulatory pressure is compounding. Frameworks such as PCI DSS 4.0 (client-side protection requirements), DORA, NIS2, and sector-specific rules on operational resilience are pushing application security from a best practice into a documented control requirement.
For security leaders, the business outcomes a modern WAAP must support include reduced breach risk and downtime, faster time to protection for new applications and APIs, audit and compliance readiness, and predictable cost as application portfolios scale.
4. WAAP vendor comparison at a glance
Use the table below to narrow the vendor set based on architectural focus and primary deployment use case. Then validate efficacy, API coverage, bot defense, and operational fit through your own proof of value. The order is alphabetical, not a ranking.
Vendor
Primary architectural focus
Core deployment use case
Independent 2025 recognition
Akamai
Edge-delivered WAAP on a globally distributed CDN; integrated DDoS, WAF, bot, and API security.
Large enterprises and content-heavy properties needing edge scale and integrated bot defense.
Unified WAF, Advanced Bot Protection, API Security, DDoS, Client-Side Protection, and CDN, delivered as SaaS, on-premises, or natively inside AWS, Azure, and Google Cloud.
Enterprises needing unified, multi-cloud and hybrid WAAP with deep bot, API, and DDoS coverage, including cloud-native deployment.
The Forrester Wave groups vendors into Leaders, Strong Performers, and Contenders, a single published designation that reflects the combined strength of each vendor’s current offering, strategy, and customer feedback. Rather than restate Forrester’s underlying sub-scores, the table below shows each covered vendor’s official tier, with a short note on what Forrester emphasized. This analyst recognition complements security-efficacy testing because it weighs roadmap, innovation, integrations, and customer feedback alongside current capabilities.
Vendor
Forrester tier
What Forrester emphasized
Cloudflare
Leader
Strongest current offering of any vendor evaluated; efficiency-focused features; reference customers flagged support as an area to improve.
Akamai
Leader
Strong detection and automation; broad edge and DDoS scale; noted to lag in DevOps and scanning integrations.
Imperva
Leader
Standout Layer 7 DDoS, CISA Secure by Design Pledge signatory, and a unifying platform roadmap; room to improve in DevOps and scanning integrations and UI consistency.
F5
Strong Performer
Built-in web application scanning and a strong API security story; fewer security operations integrations and a steeper learning curve.
Fastly
Strong Performer
Developer- and business-focused vision and pre-deployment rule testing; still building out API security.
Radware
Strong Performer
AI-assisted SOC tooling and tunable detection; fewer out-of-the-box integrations and less flexible reporting.
Fortinet
Contender
Strong API security capabilities and competitive pricing; roadmap less extensive than others, no rule versioning, and rule testing limited to logging mode.
Source: Forrester Wave: Web Application Firewall Solutions, Q1 2025 (published tier designations and findings). Among the seven vendors covered here, three were named Leaders, three Strong Performers, and one a Contender.
A note on tier equivalence: within Forrester’s methodology, vendors positioned in the same tier hold equivalent standing in the evaluation. The three Leaders (Cloudflare, Akamai, and Imperva) are designated by Forrester as Leaders together; vendor-specific sub-criterion scores within the tier do not change the tier-level designation.
Verified peer feedback (G2)
Independent customer ratings on G2 are a useful third complement to certified testing and analyst evaluation, because they reflect the day-to-day operational experience of paying customers. The table below shows the current G2 standing for each covered vendor’s flagship WAF product profile. Review-base sizes vary widely across vendors, so the rating is best read alongside the volume of reviews supporting it; vendors that have not actively claimed and managed their G2 product profile may show smaller review bases and older reviews.
Vendor product (G2 profile)
G2 rating (of 5)
Review base
Notes
Imperva Web Application Firewall (WAF)
4.7
41
Highest G2 rating among the flagship WAF profiles of the seven covered vendors; primarily enterprise reviewers.
F5 BIG-IP Advanced WAF
4.6
24
Strong rating with a focused enterprise review base.
Radware Cloud WAF
4.6
141
Strong rating with the second-largest review base among the seven.
Cloudflare Application Security and Performance
4.5
595
Largest review base in the category overall; review mix skews toward small business segments.
FortiAppSec Cloud
4.4
33
Solid mid-market G2 standing; reflects Fortinet’s consolidated WAAP profile launched after the Forrester Wave Q1 2025 cutoff.
Fastly Next-Gen WAF
4.2
30
Solid mid-market rating; vendor profile noted on G2 as having limited features (managed but not upgraded).
Akamai App & API Protector
4.0
2
G2 explicitly notes that there are not enough reviews to provide buying insight; the product profile is unclaimed by the vendor.
Source: G2 verified user reviews (most recent rating snapshots at time of writing). G2 product profiles do not always cover a vendor’s full WAAP suite, and review bases vary widely; the table compares each vendor’s flagship WAF product profile. See references.
Looking for the best WAAP solution?
Choosing the right WAAP platform depends on your organization’s unique security and operational needs. Contact our team to discuss your requirements and see how Imperva can help you achieve your application security goals. Get in touch with our team.
5. Key criteria to evaluate when comparing WAAP solutions
The framework below combines the SecureIQLab v4.0 evaluation model (security efficacy, operational efficiency, Secure by Design and Secure by Default ratings, false positive avoidance) with capability themes emphasized by Gartner and Forrester.
Capability
What to evaluate
Security efficacy
Independently measured coverage of OWASP Top 10 (web), OWASP API Security Top 10 2023, and advanced threats including bots and Layer 7 DDoS. Look for AMTSO-certified results.
API and microservice protection
API discovery (including shadow and undocumented endpoints), schema enforcement, BOLA and broken authentication detection, support for REST, GraphQL, SOAP, WebSockets, and gRPC.
Bot and abuse mitigation
Ability to distinguish legitimate automation from malicious bots, behavioral analytics, device and TLS fingerprinting, defenses against account takeover, scraping, and inventory hoarding.
Runtime and cloud integration
Support for major public clouds, native in-cloud deployment, Kubernetes and service-mesh ingress, edge versus centralized models, multi-cloud and hybrid coverage, CI/CD integration.
Operational efficiency and FP avoidance
Time to protection, tuning effort, automation, analytics, and false positive avoidance under real traffic. In the latest SecureIQLab v4.0 cycle, false positive avoidance ranged from near-perfect at the top of the group to noticeably weaker at the bottom.
Performance and reliability
Latency impact, scalability under load, behavior of failure modes (fail-open vs fail-closed), out-of-path versus inline architecture, published service-level commitments for availability and mitigation time.
TCO and commercial fit
Licensing model (per app, per request, per Mbps), predictability under traffic spikes, alignment with portfolio growth, marketplace availability, integration with existing security and developer toolchains.
Ecosystem and roadmap
Vendor stability, innovation pace, AI assistance, hyperscaler partnerships, SIEM and SOAR integrations, partner ecosystem, support quality reflected in verified customer reviews.
6. Five buyer questions to guide WAAP evaluation
Use these five questions as a lightweight evaluation framework. Each maps to one or more of the capability themes above.
1. How well does the platform stop the threats my applications actually face?
Look beyond generic OWASP coverage claims. Ask for AMTSO-certified third-party test results, and verify both web (OWASP Top 10) and API (OWASP API Security Top 10 2023) efficacy. In the latest SecureIQLab v4.0 testing, complete-security results spanned an extremely wide range, from near-complete coverage at the top to less than half of attacks blocked at the bottom, so the spread within a single shortlist can be very large.
2. How deep is the API protection, across all my protocols?
APIs are no longer just REST. SecureIQLab v4.0 testing measured coverage separately across REST, GraphQL, SOAP, WebSockets, and gRPC, and found that coverage varied widely by protocol even within a single vendor, with WebSockets generally the weakest area across the group. Confirm vendor coverage protocol by protocol, not just by headline API score.
3. How effective is bot defense against modern automation and AI-enabled abuse?
Ask vendors how they detect headless browsers, residential proxy traffic, and AI-driven scraping, and how those decisions are made without harming legitimate traffic. In the SecureIQLab bot suite, only a small number of the tested vendors blocked every attack type, so perfect bot defense is a genuine differentiator rather than a baseline.
4. How quickly can my team get to a tuned, low false-positive state?
Operational efficiency and false positive avoidance are tightly linked. In the latest cycle, the strongest vendors avoided essentially all false positives, while the weakest let through enough to translate into meaningfully more alerts per day and substantially more tuning effort for security operations teams. A few points of difference here can mean a very different daily workload.
5. How does the deployment and licensing model align with how my portfolio is growing?
Native in-cloud deployment, edge delivery, and traditional reverse-proxy models produce very different latency, resilience, and onboarding profiles, and per-request, per-Mbps, and per-application licensing produce very different cost curves as traffic scales. Walk through a 24 to 36 month projection with each shortlisted vendor, ideally informed by your own traffic baseline.
7. WAAP Vendor profiles
Each vendor profile below uses the same schema: a neutral summary, a list of capabilities verified from public documentation and independent sources, and a “Consider when” statement. Profiles are presented alphabetically. Capabilities should be re-validated against your specific environment during a proof of value.
Akamai — App & API Protector
Current market status: Publicly traded (NASDAQ: AKAM). Recognized as a Leader in the Forrester Wave: Web Application Firewall Solutions, Q1 2025, and placed in the Leader category of the SecureIQLab 2025 Cloud WAAP v4.0 validation.
Summary
Akamai delivers WAAP from one of the world’s largest edge networks, combining WAF, DDoS, bot management, API security, and client-side controls in its App & API Protector product. In SecureIQLab v4.0, the tested cloud-based deployment was among the strongest in the group on both complete security and operational efficiency, comfortably above the group averages, and avoided essentially all false positives. In the Forrester Wave Q1 2025, Akamai was named a Leader, strong on both current offering and strategy, with reference customers citing strong detection and automation; Forrester noted that Akamai lags in DevOps and scanning integrations and that some prospects weigh its pricing carefully.
Key capabilities
Edge-delivered WAAP integrated with Akamai’s global CDN and DDoS scrubbing capacity.
Behavioral bot detection that blocked every attack type in the SecureIQLab v4.0 bot suite.
API discovery and schema-aware protection for REST and modern protocols.
Layer 7 DDoS coverage with a perfect result in SecureIQLab v4.0 Layer 7 DoS testing.
Integration with Akamai’s broader Zero Trust and AI security portfolio.
Consider when
Consider Akamai when your organization needs edge-delivered protection at very large scale, has significant CDN and DDoS requirements alongside WAAP, and wants a vendor with an established global footprint and analyst-recognized leadership.
Current market status: Publicly traded (NYSE: NET). Recognized as a Leader in the Forrester Wave: Web Application Firewall Solutions, Q1 2025, with the strongest current-offering position of any vendor evaluated. Placed in the Visionary category of the SecureIQLab 2025 Cloud WAAP v4.0 validation; rated Secure by Default.
Summary
Cloudflare delivers WAAP from a globally distributed programmable network, with strong developer experience, rapid feature velocity, and integrated DDoS, bot management, API gateway, and Page Shield (client-side protection). In SecureIQLab v4.0, Cloudflare’s complete-security result landed around the group average, but it blocked every bot and Layer 7 DoS attack type and avoided nearly all false positives; API coverage was uneven, with strength in SOAP and gRPC and notable weakness in REST and WebSockets in the tested configuration. In the Forrester Wave Q1 2025, Cloudflare was named a Leader and posted the strongest current offering of any vendor evaluated; Forrester credited an efficiency-focused feature set and noted that reference customers flagged customer support as an area to improve.
Key capabilities
Cloud-native WAF integrated with Cloudflare’s CDN, DDoS scrubbing, and developer platform.
Programmable security policies and edge workers for custom logic.
Bot management that blocked every attack type in the SecureIQLab v4.0 bot suite.
Page Shield client-side protection aligned to PCI DSS 4.0 requirements.
Strong developer experience and rapid product release cadence.
Consider when
Consider Cloudflare when your organization values developer-led security, rapid time to deploy, and a unified edge platform across CDN, DDoS, and application protection. Plan to validate API coverage by protocol against your specific traffic mix during a proof of value.
F5 — Distributed Cloud WAAP
Current market status: Publicly traded (NASDAQ: FFIV). Named a Strong Performer in the Forrester Wave: Web Application Firewall Solutions, Q1 2025. Not part of the public 2025 SecureIQLab v4.0 published cycle (listed as Contact SecureIQLab in the comparative report).
Summary
F5 brings deep WAF heritage from BIG-IP Advanced WAF and a multi-acquisition portfolio (Volterra, Shape Security), assembled into the Distributed Cloud (XC) WAAP service. F5 is often shortlisted by organizations with significant existing F5 application delivery and security investments and a need to span data center, multi-cloud, and SaaS-delivered WAAP. In the Forrester Wave Q1 2025, F5 was named a Strong Performer, solid on both current offering and strategy; Forrester credited built-in web application scanning (via its Heyhack acquisition) and a strong API security story, while noting fewer security operations integrations and a steep learning curve cited by reference customers. Because F5 did not appear in the public SecureIQLab v4.0 dataset, comparative efficacy claims should be validated through buyer-led testing.
Key capabilities
Distributed Cloud WAAP delivered as a SaaS layer across multi-cloud and edge.
Behavioral bot defense lineage from Shape Security.
API security including discovery and schema validation.
Hybrid deployment alongside BIG-IP Advanced WAF appliances and virtual editions.
Strong fit for hybrid enterprises with existing F5 footprints.
Consider when
Consider F5 when your environment already standardizes on F5 application delivery and security infrastructure, when hybrid (data center plus SaaS) WAAP is required, and when buyer-led testing can fill the absence of comparable public SecureIQLab v4.0 data.
Fastly — Next-Gen WAF
Current market status: Publicly traded (NYSE: FSLY). Recognized as a Strong Performer in the Forrester Wave: Web Application Firewall Solutions, Q1 2025 (vision described by Forrester as developer- and business-focused). Not part of the public 2025 SecureIQLab v4.0 published cycle (listed as Contact SecureIQLab in the comparative report).
Summary
Fastly’s WAF is built on the Signal Sciences engine and is closely integrated with Fastly’s programmable edge platform. The product appeals to developer-led organizations that want deep observability into request decisions, the ability to test rules before deployment, and tight CI/CD integration. The absence of Fastly from the SecureIQLab v4.0 public cycle means head-to-head efficacy comparison against the 11 tested vendors must come from internal testing.
Key capabilities
Signal Sciences detection engine with detailed signal-based decisioning.
WAF Simulator for testing rules prior to production deployment.
Native integration with Fastly’s programmable CDN.
API security features that have continued to expand in 2024 and 2025.
Consider Fastly when application security is closely coupled to a developer-first delivery culture, when observability and pre-deployment rule testing are priorities, and when the lack of public SecureIQLab v4.0 data can be supplemented by internal validation.
Fortinet — FortiWeb
Current market status: Publicly traded (NASDAQ: FTNT). Named a Contender in the Forrester Wave: Web Application Firewall Solutions, Q1 2025, and placed in the Leader category of the SecureIQLab 2025 Cloud WAAP v4.0 validation.
Summary
FortiWeb is Fortinet’s WAAP, available as VM, AMI, container, and SaaS, and integrated with the broader Fortinet Security Fabric. The two independent sources frame Fortinet differently. In SecureIQLab v4.0, FortiWeb posted the strongest complete-security result among the tested platform vendors, with high operational efficiency and near-perfect false positive avoidance (its bot defense blocked three of the four attack types). In the Forrester Wave Q1 2025, Fortinet placed in the Contender tier, the only covered vendor below the Strong Performer band, with developing positions on both current offering and strategy. Forrester noted a roadmap less extensive than others in the evaluation, an absence of rule versioning, rule testing limited to logging mode, and limited compliance and performance reporting, while crediting strong API security capabilities and competitive pricing.
Key capabilities
WAAP available as virtual machine, AMI, container, and SaaS.
Integration with Fortinet Security Fabric (FortiGate, FortiAnalyzer, FortiSIEM).
Machine learning models for traffic profiling and threat detection.
API security capabilities including anomaly detection, PII labeling, and gRPC support (per Forrester).
April 2024 Google Cloud Technology Partner of the Year award in application security.
Strongest complete-security result among the SecureIQLab v4.0 tested platform vendors.
Consider when
Consider FortiWeb when your organization is standardized on the Fortinet Security Fabric, when integrated network and application security is a priority, and when a competitively priced option within a large security platform is the goal. Buyers prioritizing rule lifecycle management (versioning, safe rule testing outside logging mode) or breadth of strategy and roadmap should weigh the Forrester findings and validate these areas during a proof of value.
Imperva (part of Thales) — Web Application and API Protection
Current market status: Now part of Thales (acquired December 2023). Recognized as a Leader in the Forrester Wave: Web Application Firewall Solutions, Q1 2025, and the KuppingerCole 2025 Leadership Compass for WAAP. Placed in the Leader category of the SecureIQLab 2025 Cloud WAAP v4.0 validation (the fourth consecutive cycle) and awarded the Secure by Default rating.
Summary
Imperva delivers a unified WAAP combining Cloud WAF, Advanced Bot Protection, API Security, DDoS Protection, Client-Side Protection, Account Takeover Protection, and CDN under one platform, available as SaaS, on-premises, or deployed natively inside hyperscale clouds. In SecureIQLab v4.0, Imperva was among the strongest in the group on both complete security and operational efficiency, well above the group averages, and notably achieved perfect 100% results in bot defense, Layer 7 DoS, and false positive avoidance, a combination of high efficacy and full false-positive discipline that few vendors matched. In the Forrester Wave Q1 2025, Imperva was named a Leader, strong on strategy and solid on current offering. Forrester highlighted Imperva’s Layer 7 DDoS, its signing of the CISA Secure by Design Pledge, and a roadmap that integrates its application security offerings into a unified platform, while noting room to improve in out-of-the-box DevOps and scanning integrations and in some UI consistency.
Key capabilities
Unified WAAP platform across SaaS, on-premises, and cloud-native deployment.
Native in-cloud deployment for AWS, Microsoft Azure, and Google Cloud, with Imperva for Google Cloud (available on Google Cloud Marketplace) inspecting traffic inside the Google Cloud network via Service Extension and Private Service Connect, and onboarding without DNS, SSL, or routing changes.
Advanced Bot Protection with behavioral analytics and fingerprinting; blocked every bot attack type in SecureIQLab v4.0 testing.
API Security with discovery, schema-based protection, and BOLA detection; API protocol coverage well above the tested-group average.
DDoS Protection with industry SLA commitments; perfect result in SecureIQLab v4.0 Layer 7 DoS testing.
Client-Side Protection aligned to PCI DSS 4.0 magecart and script-protection requirements.
Perfect 100% results in bot defense, Layer 7 DoS, and false positive avoidance in the SecureIQLab v4.0 cycle; Secure by Default rating per CISA-aligned criteria.
Consider when
Consider Imperva when your organization needs unified WAAP across multi-cloud and hybrid environments, when deep API security and bot defense are required alongside core WAF and DDoS, when low operational burden and very high false-positive avoidance are priorities, and when cloud-native deployment inside AWS, Azure, or Google Cloud is on the roadmap.
Radware — Cloud Application Protection Service
Current market status: Publicly traded (NASDAQ: RDWR). Recognized as a Strong Performer in the Forrester Wave: Web Application Firewall Solutions, Q1 2025. Not part of the public 2025 SecureIQLab v4.0 published cycle (listed as Contact SecureIQLab in the comparative report).
Summary
Radware’s Cloud Application Protection Service combines WAF, bot management, API protection, and DDoS, with continued investment in AI-driven detection and SOC automation tooling. Radware’s heritage in DDoS protection makes it a frequent shortlist option for organizations whose risk profile is heavily weighted to availability attacks. In the Forrester Wave Q1 2025, Radware was named a Strong Performer, strong on strategy and solid on current offering; Forrester credited its AI SOC Xpert tool and tunable detection models, while noting fewer out-of-the-box integrations and reference-customer feedback that reporting could be more flexible. Comparable SecureIQLab v4.0 data is not publicly available for this cycle.
Key capabilities
Cloud Application Protection Service combining WAF, bots, API, and DDoS.
Strong DDoS protection heritage.
AI-assisted SOC tooling for application protection.
Hybrid and cloud deployment options.
Forrester recognition for detection models and pricing transparency in Q1 2025.
Consider when
Consider Radware when DDoS exposure is a primary driver, when AI-assisted SOC tooling is valued, and when the absence of public SecureIQLab v4.0 data can be addressed through internal testing.
8. Why Imperva stands out for unified, cloud-native WAAP
Imperva’s differentiation is grounded in four architectural realities that buyers can verify in their own environments and through independent testing.
Unified WAAP rather than assembled WAAP. Imperva’s Cloud WAF, Advanced Bot Protection, API Security, DDoS Protection, Client-Side Protection, Account Takeover Protection, and CDN are delivered as one platform rather than a portfolio of acquired and integrated products. The result is consistent policy, telemetry, and analytics across the entire application protection surface.
Validated efficacy with very low operational burden. In the latest AMTSO-certified SecureIQLab v4.0 cycle, Imperva paired among the strongest complete-security and operational-efficiency results in the group with perfect 100% results in false positive avoidance, bot defense, and Layer 7 DoS. Few vendors in the tested set combined top-tier efficacy with that level of false-positive discipline.
Deployment flexibility, including native cloud integration. Imperva can be deployed as SaaS, on-premises, or natively inside hyperscale clouds. Imperva for Google Cloud, available on Google Cloud Marketplace, inspects traffic inside the Google Cloud network using Service Extension and Private Service Connect, and onboards without DNS, SSL, or routing changes. This native, in-cloud direction extends across AWS, Azure, and Google Cloud, and reflects a broader roadmap of running enterprise-grade WAAP inside hyperscale infrastructure rather than alongside it through external routing.
Aligned to CISA Secure by Design. Imperva earned the SecureIQLab Secure by Default rating in the same cycle, reflecting hardened defaults and the ability to protect newly deployed applications without extensive manual tuning.
No single platform is the right answer for every environment. Buyers whose dominant requirement is a single edge platform unifying CDN, application protection, and a developer-centric workflow, or whose primary driver is the deepest possible DDoS scrubbing capacity, will want to weigh those needs explicitly. The most reliable approach is to validate any shortlist, including Imperva, against your own threat model, traffic patterns, and cloud footprint during a proof of value.
9. How to choose the right WAAP platform
Choosing a WAAP platform should start with your operating reality, not the vendor list. The matrix below maps the most common dominant security gap to the WAAP capabilities buyers should prioritize during evaluation.
If your biggest gap is…
Prioritize…
API exposure and BOLA-style abuse
API discovery (including shadow APIs), schema enforcement, behavioral analytics, BOLA detection, broad protocol coverage (REST, GraphQL, SOAP, WebSockets, gRPC).
Bot abuse and account takeover
Behavioral bot detection, device and TLS fingerprinting, real-time risk scoring, integration with fraud and identity controls.
Client-side protection that inventories scripts, detects unauthorized modification, and produces auditable evidence.
Operational overhead and tuning effort
High Secure by Default scores, high independent false positive avoidance scores, automated policy generation, and analyst-recognized ease of management.
Multi-cloud, hybrid, and cloud-native coverage
Consistent policy and telemetry across AWS, Azure, GCP, and on-premises; native in-cloud deployment options; CDN-agnostic delivery; marketplace availability.
There is no single best WAAP for every organization; the right platform depends on your threat profile, API footprint, and cloud architecture. Among the major vendors most often shortlisted by enterprises, Akamai, Cloudflare, and Imperva were named Leaders in the Forrester Wave: Web Application Firewall Solutions, Q1 2025, while Akamai, Fortinet, and Imperva placed in the Leader category of the AMTSO-certified SecureIQLab Cloud WAAP v4.0 validation. In that cycle, Imperva combined among the strongest security efficacy in the group with perfect 100% results in bot defense, Layer 7 DoS, and false positive avoidance. Validate any shortlist against your own traffic during a proof of value.
What is the difference between a WAF and a WAAP?
A Web Application Firewall (WAF) inspects and filters HTTP traffic to block common web exploits such as those in the OWASP Top 10. Web Application and API Protection (WAAP) is the broader, cloud-delivered category defined by Gartner that pairs a WAF with additional runtime defenses, typically DDoS protection, advanced bot management, API security, and client-side script protection. In other words, the WAF is one component inside a modern WAAP platform.
Which major WAAP vendors were named Leaders in the most recent Forrester Wave for WAF Solutions?
In the Forrester Wave: Web Application Firewall Solutions, Q1 2025, which evaluated 10 providers across 22 criteria, the vendors covered in this guide were placed as follows: Akamai, Cloudflare, and Imperva were named Leaders; F5, Fastly, and Radware were named Strong Performers; and Fortinet was named a Contender.
Which of the vendors covered here completed the most recent SecureIQLab Cloud WAAP testing?
Of the seven platforms covered here, four completed the public SecureIQLab v4.0 cycle: Akamai, Cloudflare, Fortinet, and Imperva. Akamai, Fortinet, and Imperva were placed in the Leader category. F5, Fastly, and Radware are listed as Contact SecureIQLab in the comparative report and did not appear with published v4.0 results.
Why does API protocol coverage matter so much in 2026?
API traffic now accounts for more than 70% of all web traffic, and independent industry reporting links roughly a third of recent data breaches to APIs, with about 35% of API breaches tied to Broken Object Level Authorization (BOLA). Modern WAAPs need to cover REST, GraphQL, SOAP, WebSockets, and gRPC; independent testing has shown wide variance across protocols even within a single vendor’s product.
What does native cloud deployment add over traditional WAAP delivery?
Native in-cloud deployment lets a WAAP inspect traffic inside the cloud provider’s own network rather than routing it externally, which can reduce latency and operational overhead and avoid changes to DNS, SSL, or routing. Imperva for Google Cloud, for example, uses Google Cloud Service Extension and Private Service Connect to operate inside the Google Cloud network, and Imperva offers native deployment across AWS, Azure, and Google Cloud.
What independent WAAP testing standards should I trust?
Look for testing conducted under the Anti-Malware Testing Standards Organization (AMTSO) framework. The SecureIQLab Cloud WAAP v4.0 methodology used in this guide is AMTSO-certified (AMTSO-LS1-TP097). Pair it with analyst evaluations (Forrester, Gartner, KuppingerCole, IDC) and verified peer reviews.
How should I treat vendor-supplied competitive content during evaluation?
Treat vendor-produced competitive comparisons as marketing inputs rather than evidence. Anchor evaluation on AMTSO-certified independent testing, recent analyst reports, and verified peer reviews, and confirm specific claims through your own proof of value.
11. Choose your next step
Strong WAAP decisions combine three things: independent testing data, analyst guidance, and a proof of value run on your own traffic. As next steps, security leaders typically benefit from running a quick application portfolio baseline (top 20 apps and APIs by risk), executing an internal red-team exercise against current controls, and shortlisting two to three vendors for parallel proof of value testing across the dimensions outlined above.
To explore Imperva’s WAAP capabilities, including native deployment for AWS, Azure, and Google Cloud, or to request a technical evaluation, contact the Imperva team.
12. References and appendix
All claims in this guide are supported by independent third-party sources or by vendor public documentation for descriptive facts. The full reference list is below.
Independent testing
[1] SecureIQLab, 2025 Cloud WAAP CyberRisk Comparative Validation Report v4.0, AMTSO Test ID AMTSO-LS1-TP097, https://www.secureiqlab.com.
[2] SecureIQLab, 2025 Cloud WAAP CyberRisk Validation Reports (individual vendor reports, including Akamai, Cloudflare, Fortinet, and Imperva).
[4] Forrester, The Forrester Wave: Web Application Firewall Solutions, Q1 2025 (Sandy Carielli, et al., March 20, 2025). Tier placements and composite scorecard scores cited here are from Figures 1 and 2 of the report.
[5] Gartner, Market Guide for Cloud Web Application and API Protection, most recent edition, https://www.gartner.com.
[6] Gartner Peer Insights, Cloud Web Application and API Protection market reviews, https://www.gartner.com/reviews/market/cloud-web-application-and-api-protection.
[7] G2, Web Application Firewall (WAF) category, verified user reviews and product ratings, https://www.g2.com/categories/web-application-firewall-waf.
[8] KuppingerCole, Leadership Compass: Web Application and API Protection (WAAP), 2025.
[9] IDC, IDC MarketScape for Web Application and API Protection (WAAP).
Industry standards and frameworks
[10] OWASP Top 10 (2021), https://owasp.org/Top10/.
[11] OWASP API Security Top 10 (2023), https://owasp.org/API-Security/.

 Login