❌

Normal view

Applying Security by Design and Cyber Immunity principles to protect AI systems | Kaspersky official blog

29 October 2026 at 14:07

AI systems are much harder to protect than traditional IT — whether from operator mistakes, malicious interference, or just plain unstable behavior. There are two main reasons for this. First, AI outputs are probabilistic, so the same prompt can give different answers each time you run it. Second, today’s LLMs can’t reliably tell commands apart from data. Despite the demonstrated security issues of AI systems that we’ve covered many times, it’s impossible to ignore the potential economic payoff of adopting them. That’s why many companies are moving beyond simple AI assistants to AI agents. These agents carry out tasks on their own and have direct access to the same tools as humans — from reading databases to changing settings in production processes. Our experts, in their new study, examine how to clearly define and minimize the resulting risks to keep potential problems to a minimum. The approach borrows and adapts the principles of Cyber Immunity and Security by Design.

The basic principles of Security by Design

All the principles of this discipline are universally applicable to the design of any computer system — AI agents included. What differs is how deeply each principle needs to be adapted and reworked for AI scenarios.

  1. Security is a separate and important factor right from the design stage. Security goals and assumptions are set on day one and followed throughout every stage of development. For AI agents, these assumptions should include three key points: (i) the language model is treated as untrusted, (ii) external data of any kind is considered potentially malicious, and (iii) irreversible actions can’t be performed autonomously without mandatory human approval.
  2. The system is designed on the assumption that it will be attacked.
  3. The trusted computing base and attack surface are kept to a minimum. Agents get only the tools they actually need, limited permissions, and the smallest amount of context possible. Security policy enforcement is handled entirely by deterministic components: the policy monitor, the agent harness, and isolation mechanisms (sandboxes).
  4. The principle of least privilege applies. Each agent has its own set of credentials and access privileges (identity), limited to the bare minimum it needs to do its job. If an agent temporarily needs elevated privileges, it gets them only after external approval, and they last exactly as long as the task that requires them.
  5. Components are isolated. In agent-based systems, this is one of the most complex and multi-layered architecture problems. The agent harness should run in an isolated environment (sandbox or virtual machine), and agents should be kept as isolated from each other as possible. Data processing in trusted and untrusted contexts is also kept separate. For example, one agent reads a pull request and writes a draft of the code, while another reviews that work without ever seeing the potentially malicious text of the request.
  6. Default deny is the rule. Security policies follow the rule: anything not explicitly allowed is forbidden. This includes tool calls, interactions between agents, and network traffic.
  7. Defense in depth is in place. Different measures should work at the same time and reinforce each other. Probabilistic defenses — like AI guardrails (a “firewall” for language models) or alignment (the model’s own sense of what’s acceptable and what isn’t) — can’t offer any formal security guarantees. Nevertheless, they make the system more secure overall and serve as a valuable source of telemetry.
  8. The supply chain is protected. Some agents can install skills, libraries, and other software components on their own, so these abilities need strict rules. Either block them completely, or limit them to a closed, pre-approved list of specific versions of specific components. Systems built on cloud LLMs face an extra risk: model updates. One day, the same API request might be answered by a different language model with different security properties.

Pitfalls of AI security

The general principles of Security by Design are well known and look simple on paper. But applying them to AI systems is tricky because agents are incredibly flexible. For example, a security team might believe that an agent on a developer’s computer runs in a sandbox and can’t change anything outside it. But an attacker, or even the agent itself, can come up with dozens of ways around this seemingly solid protection: from running commands through a local MCP server that the sandbox doesn’t restrict, to reconfiguring another AI agent installed on the system. To make things even harder, the range of attack vectors is huge: from arbitrary fields in the agent’s configuration to innocent-looking text strings in a skill file.

One serious problem that designers often underestimate is user fatigue. A busy agent can throw up dozens of requests every minute, asking the user to confirm potentially dangerous actions. Within an hour, the person is clicking Approve on autopilot without reading what they’re approving. That’s why it’s important to carefully tune both how often these requests appear and how they’re worded. Nobody will read a request description that’s too long. And one that’s too short can hide the key details the user needs in order to make the right call.

Vulnerabilities in agents and related tools are a pressing problem — and it’s made worse by how quickly these categories of software evolve and receive updates. Industry-standard platforms and apps — such as LangGraph, MS Semantic Kernel, and Claude Code — have had critical vulnerabilities patched more than once. Architects should always consider swapping a large, do-it-all framework for a compact, stripped-down system that has only the features a specific agent actually needs.

On top of that, carefully implementing standard, long-established security measures in the available tools greatly reduces the damage if an agent is attacked or behaves unexpectedly. One example is a strict allowlist of domains that the web fetch tool can open when asked by the agent. But designers rarely account for the hidden problems and overhead associated with maintaining the list. As a result, it slowly goes out of date and leaves loopholes for attackers. The most striking example is the EchoLeak attack. Microsoft 365 Copilot had a properly implemented and fairly effective allowlist for accessing external sites, but attackers circumvented it through a feature in a secondary tool and the MS Teams domain.

Practical tips for architects and security teams

AI system architects and heads of engineering and security teams should build in agent security from the design stage. They should rely primarily on verifiable, deterministic mechanisms: isolating components, controlling interactions, and keeping the trusted computing base to a minimum.

Key architectural decisions include defining acceptable autonomy for the agents, limiting access to confidential data and dangerous combinations of capabilities, and using sandboxes, separate roles for different models, and access control gateways. Restrictions added as an afterthought reduce risks, but they’re no substitute for secure architecture.

At the organizational and operational levels, companies need to keep an inventory of their agents, coordinate the efforts of security and deployment teams, protect container environments, manage the supply chain (AIBOM), and integrate multi-layered defense.

Observability requires special attention. For AI systems, this should include logging the LLM’s requests, responses, and reasoning, as well as detailed telemetry from the hosts and cloud environments where the agent harness runs.

The hardest part of designing agents is balancing security, performance, and usefulness. To learn how to strike that balance with threat modeling and clearly defined security goals, read the full version of the study.

How to completely uninstall apps on Mac and free up storage | Kaspersky official blog

9 September 2026 at 14:05

Every so often you need to tidy up, and that goes for your devices as well as your closets and drawers. But a digital cleanup can turn out to be trickier than sorting through a messy closet — especially on macOS.

Getting rid of old photos and files is straightforward enough, but fully removing an app from macOS is another story. You’d think dragging an unwanted app to the Trash would do the job, but in practice, that app can leave behind settings files, cache, logs, helper files, and other related junk. Over time, all these leftovers pile up and eat away at your storage.

To make this kind of cleanup easier, Kaspersky Premium for macOS now includes a feature called App Cleaner. It removes apps along with all their related files, and it can also track down the remains of apps you deleted earlier. This post explains where these leftover files come from, shows you how to use App Cleaner, and explains why installing the first Mac cleanup tool you find online isn’t a great idea.

Why deleted apps leave traces on your Mac

As Apple products go, macOS works in some unusual ways. Every longtime user runs into its quirks sooner or later, though that doesn’t stop us from loving it with all our hearts. Apps are no exception: the way macOS handles them is more complicated than it looks.

Most people picture an app on macOS as one specific item. Take Photoshop: it’s that familiar icon with the letters Ps, sitting in the Applications folder in Finder, ready to launch with a click. But under the hood it’s more complex. What looks like a single item in Finder is actually an app bundle: a folder containing the program itself along with everything it needs to run.

But even that is only part of the picture. While Photoshop is running, like any app, it creates and uses data stored outside that bundle. Some of this is behind-the-scenes data, like cache, settings, and user documents. Some of it is your own work, like PSD files. The distinction matters: if you delete Photoshop, you don’t expect your PSD files to vanish along with it.

Then there’s how Adobe doesn’t just install Photoshop or Acrobat: it also deploys a whole set of common apps and background services alongside them. Dragging the Ps icon to the Trash won’t remove those, and neither will Adobe’s own uninstaller.

These background files and helper services can stick around on your drive after you’ve deleted the app they came from. Worse, if you use Migration Assistant to move to a new Mac, all that dead weight gets copied over automatically. So it’s entirely possible to have never installed a single Adobe or Microsoft app on your current Mac, yet still be carrying around megabytes, or even gigabytes, of useless files tied to them.

Tracking these files down yourself isn’t easy, primarily because most people don’t even know they exist. Even if you suspect something’s hiding on your drive, you probably won’t know where to look or what the files are called. To make things harder, file names rarely give away which app they belong to.

App Cleaner has arrived in Kaspersky Premium for macOS

The new App Cleaner feature helps you remove apps along with the files they leave behind

Most of these background files live in special macOS folders. One of the main ones is Library, which contains folders like Application Support (app data) and Caches (temporary files). But Library isn’t easy to get to. Since OS X 10.7, Finder keeps it hidden by default. To find it, open the Go menu in Finder while holding down the Option key. Only then does Library show up.

Even if you’re determined enough to dig through Library, you’ll still have to figure out for yourself which of the many files belong to which apps, and which ones are safe to delete. Fortunately, you don’t have to do this by hand, because that’s exactly what App Cleaner takes care of.

How App Cleaner finds and removes apps without leaving traces

App Cleaner doesn’t just remove the app itself. It also tracks down every file connected to it. It does this by automatically identifying which files belong to which app, mainly using the app’s unique identifier (bundle ID) and typical file locations. This means it can clear out an app’s leftovers even when they’re scattered across different macOS folders.

Keep in mind that a full cleanup like this also removes the app’s saved data, so you’ll need to set things up again — for example, restore browser extensions — if you reinstall it later; you can also lose game save files. That said, App Cleaner never touches your own files. Delete Photoshop with it, and the leftover files disappear while your PSD files stay exactly where they are.

You can’t remove the extra files separately from the app itself. App Cleaner offers to delete them together as one package. But if you’ve already deleted an app the regular way and its data has stuck around, App Cleaner can find and remove that too.

If you accidentally delete something you needed, don’t worry. App Cleaner moves everything to the Trash first rather than deleting it outright. As long as the Trash isn’t emptied, you can restore those files from there, and if you haven’t closed App Cleaner since deleting them, you can restore them directly from the app instead. Files only disappear for good once you empty the Trash. We’ll walk through how to undo an accidental deletion below.

How to remove an app with Kaspersky App Cleaner: a step-by-step guide

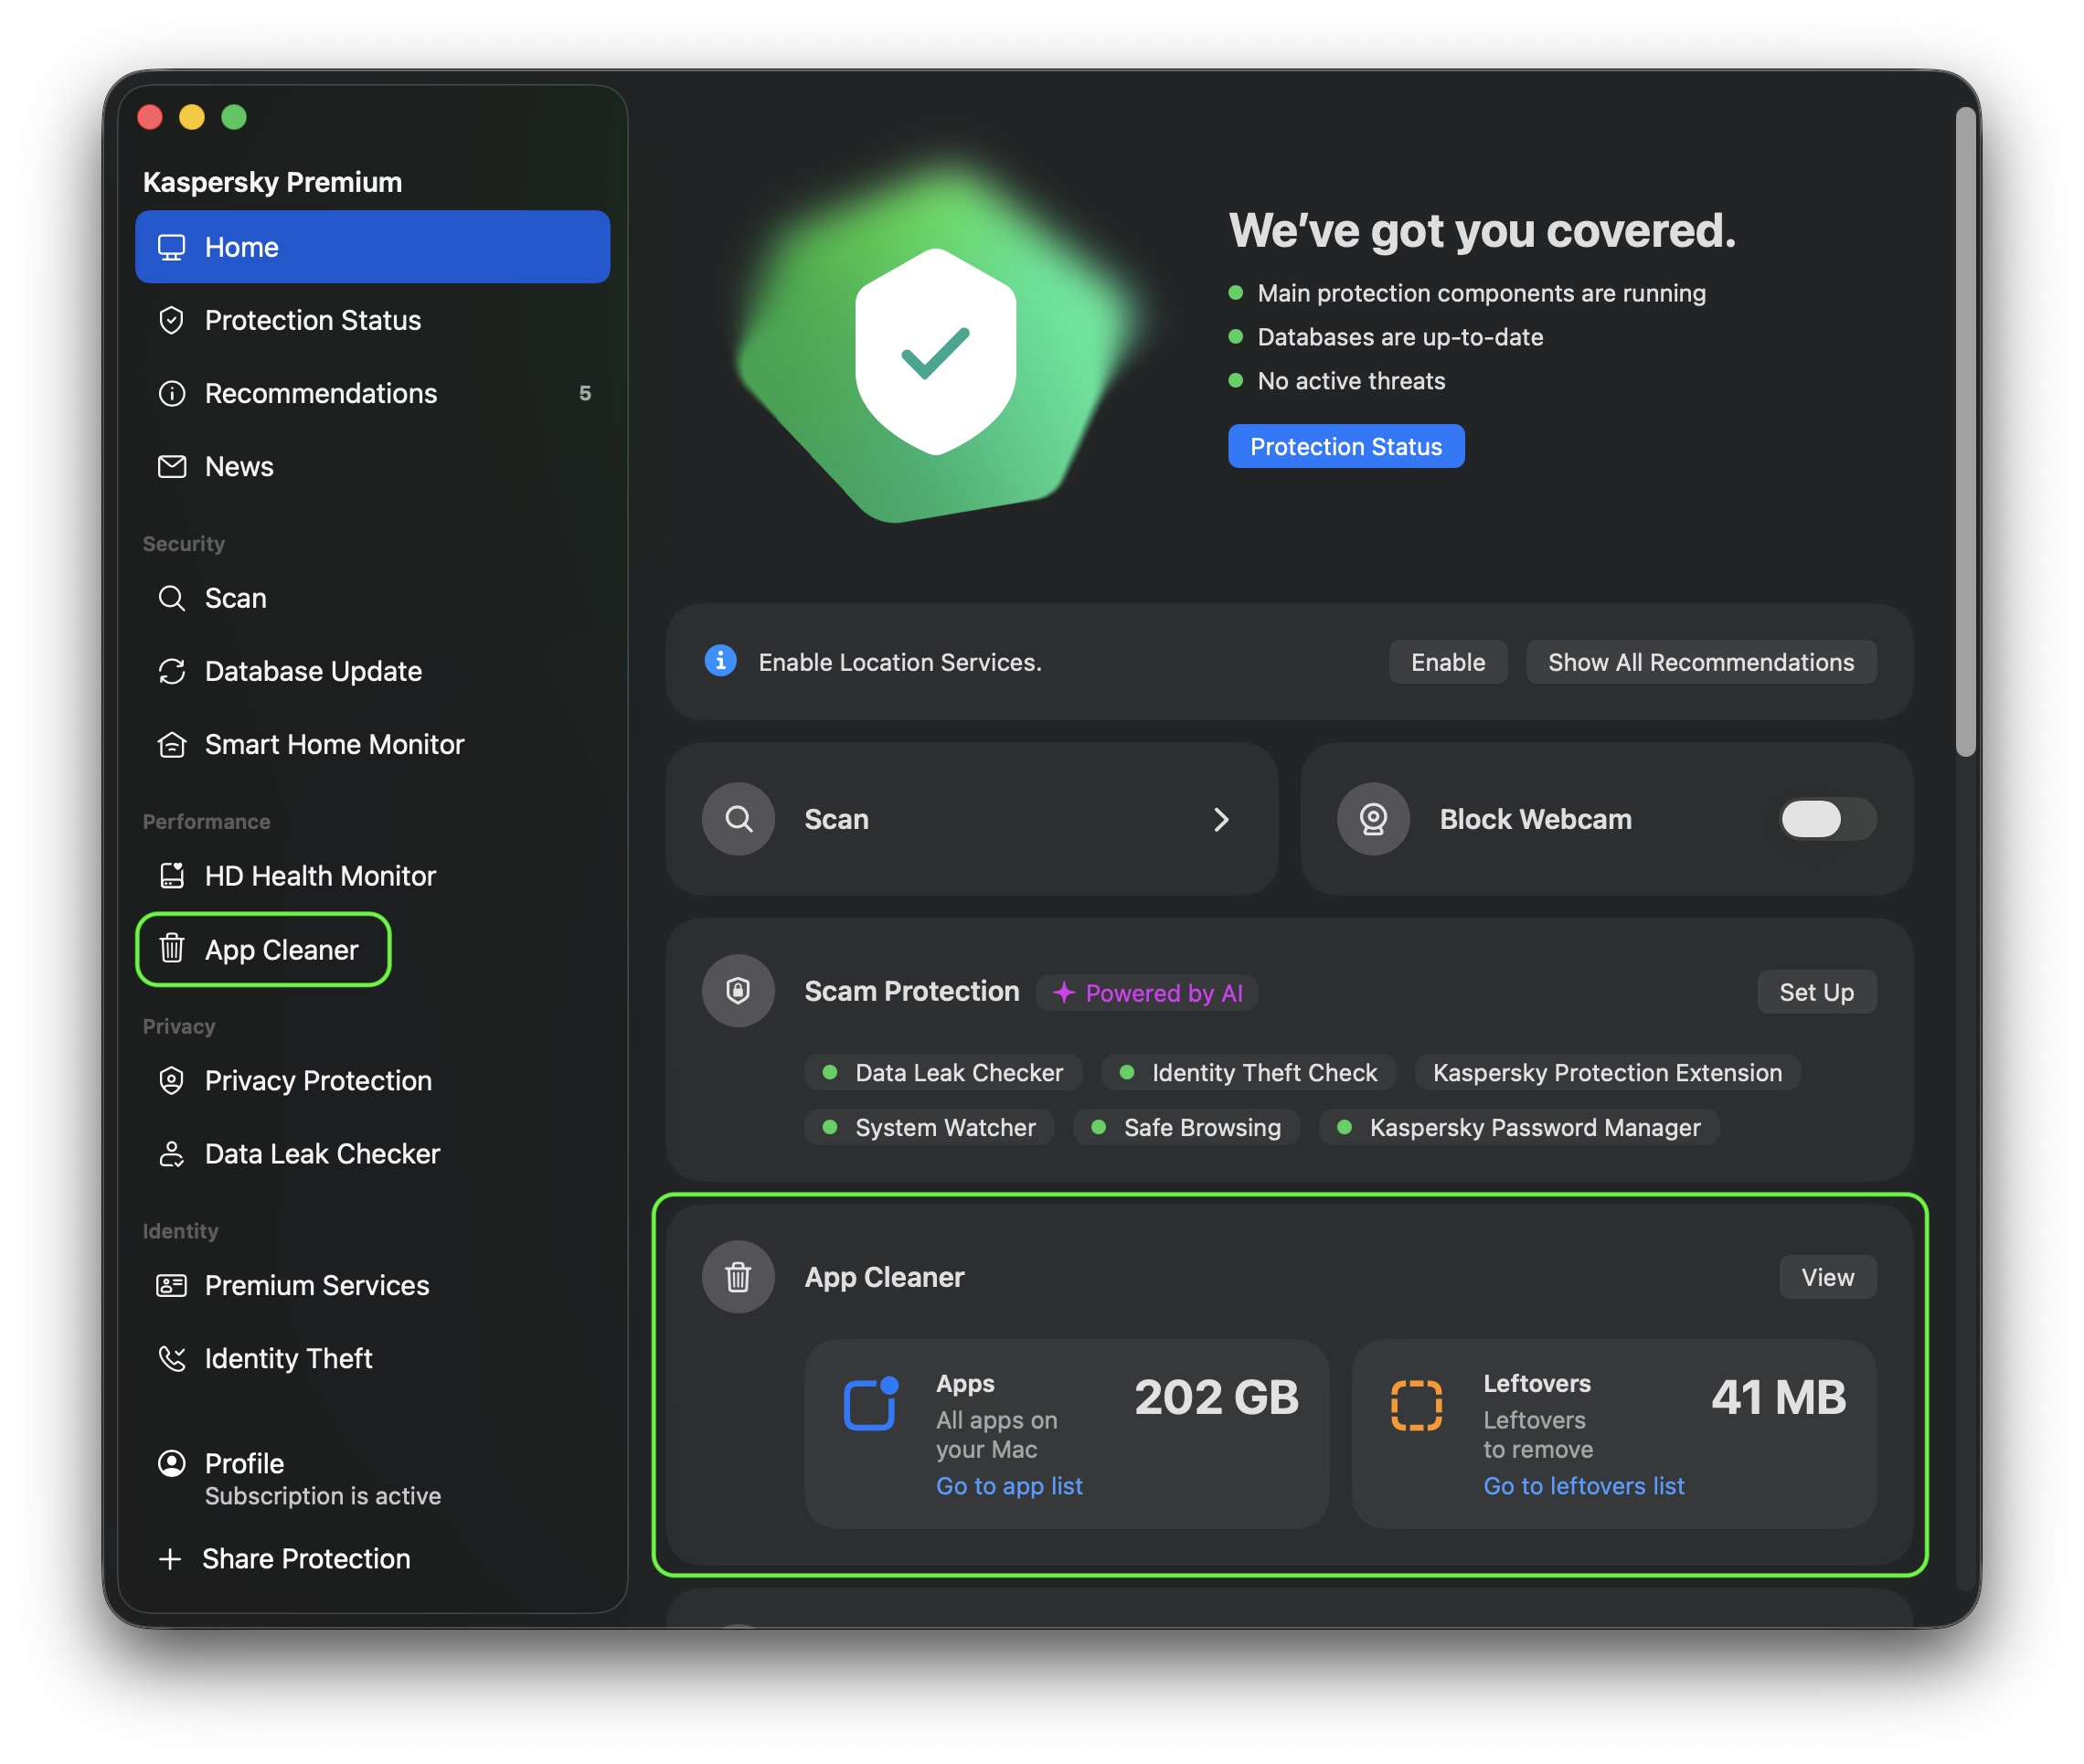
Now let’s put this into practice. To use App Cleaner, open Kaspersky Premium for macOS and head to the App Cleaner section. You’ll find it right on the app’s main screen, in its own App Cleaner block, or under Performance in the left-hand menu.

Where to find App Cleaner in Kaspersky Premium

You can open App Cleaner from the main screen of Kaspersky for macOS, or through the Performance section in the left menu

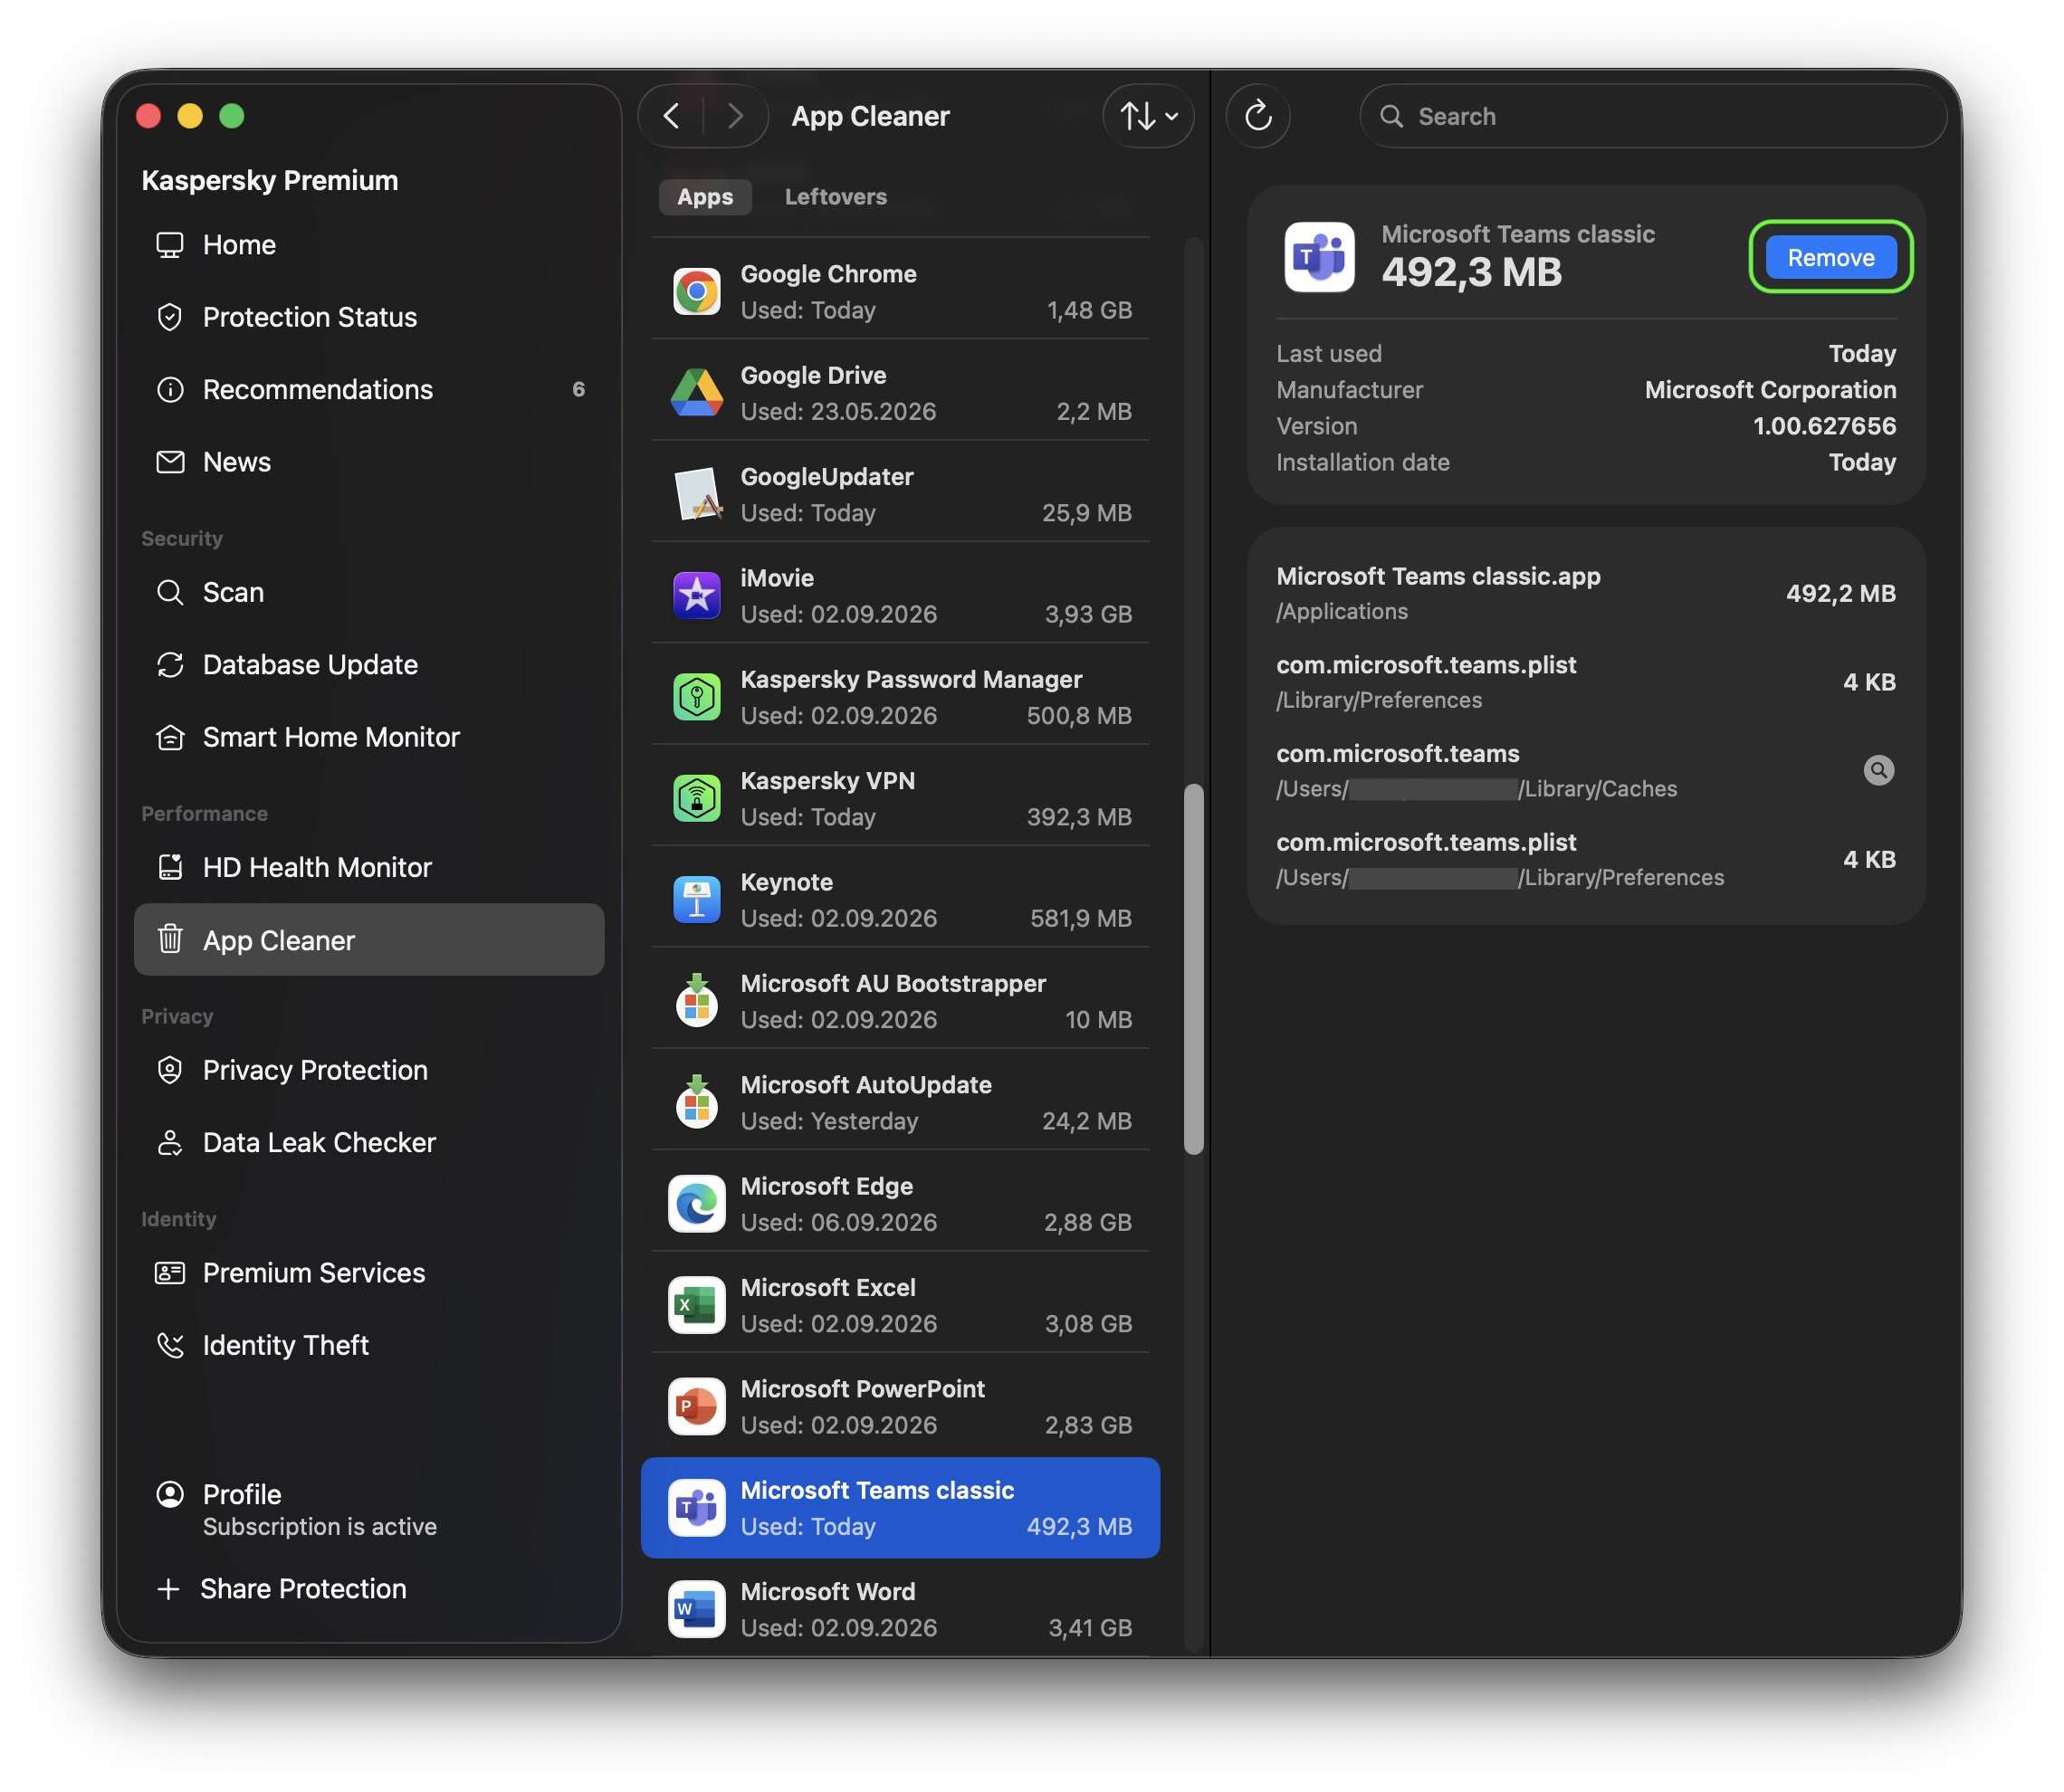
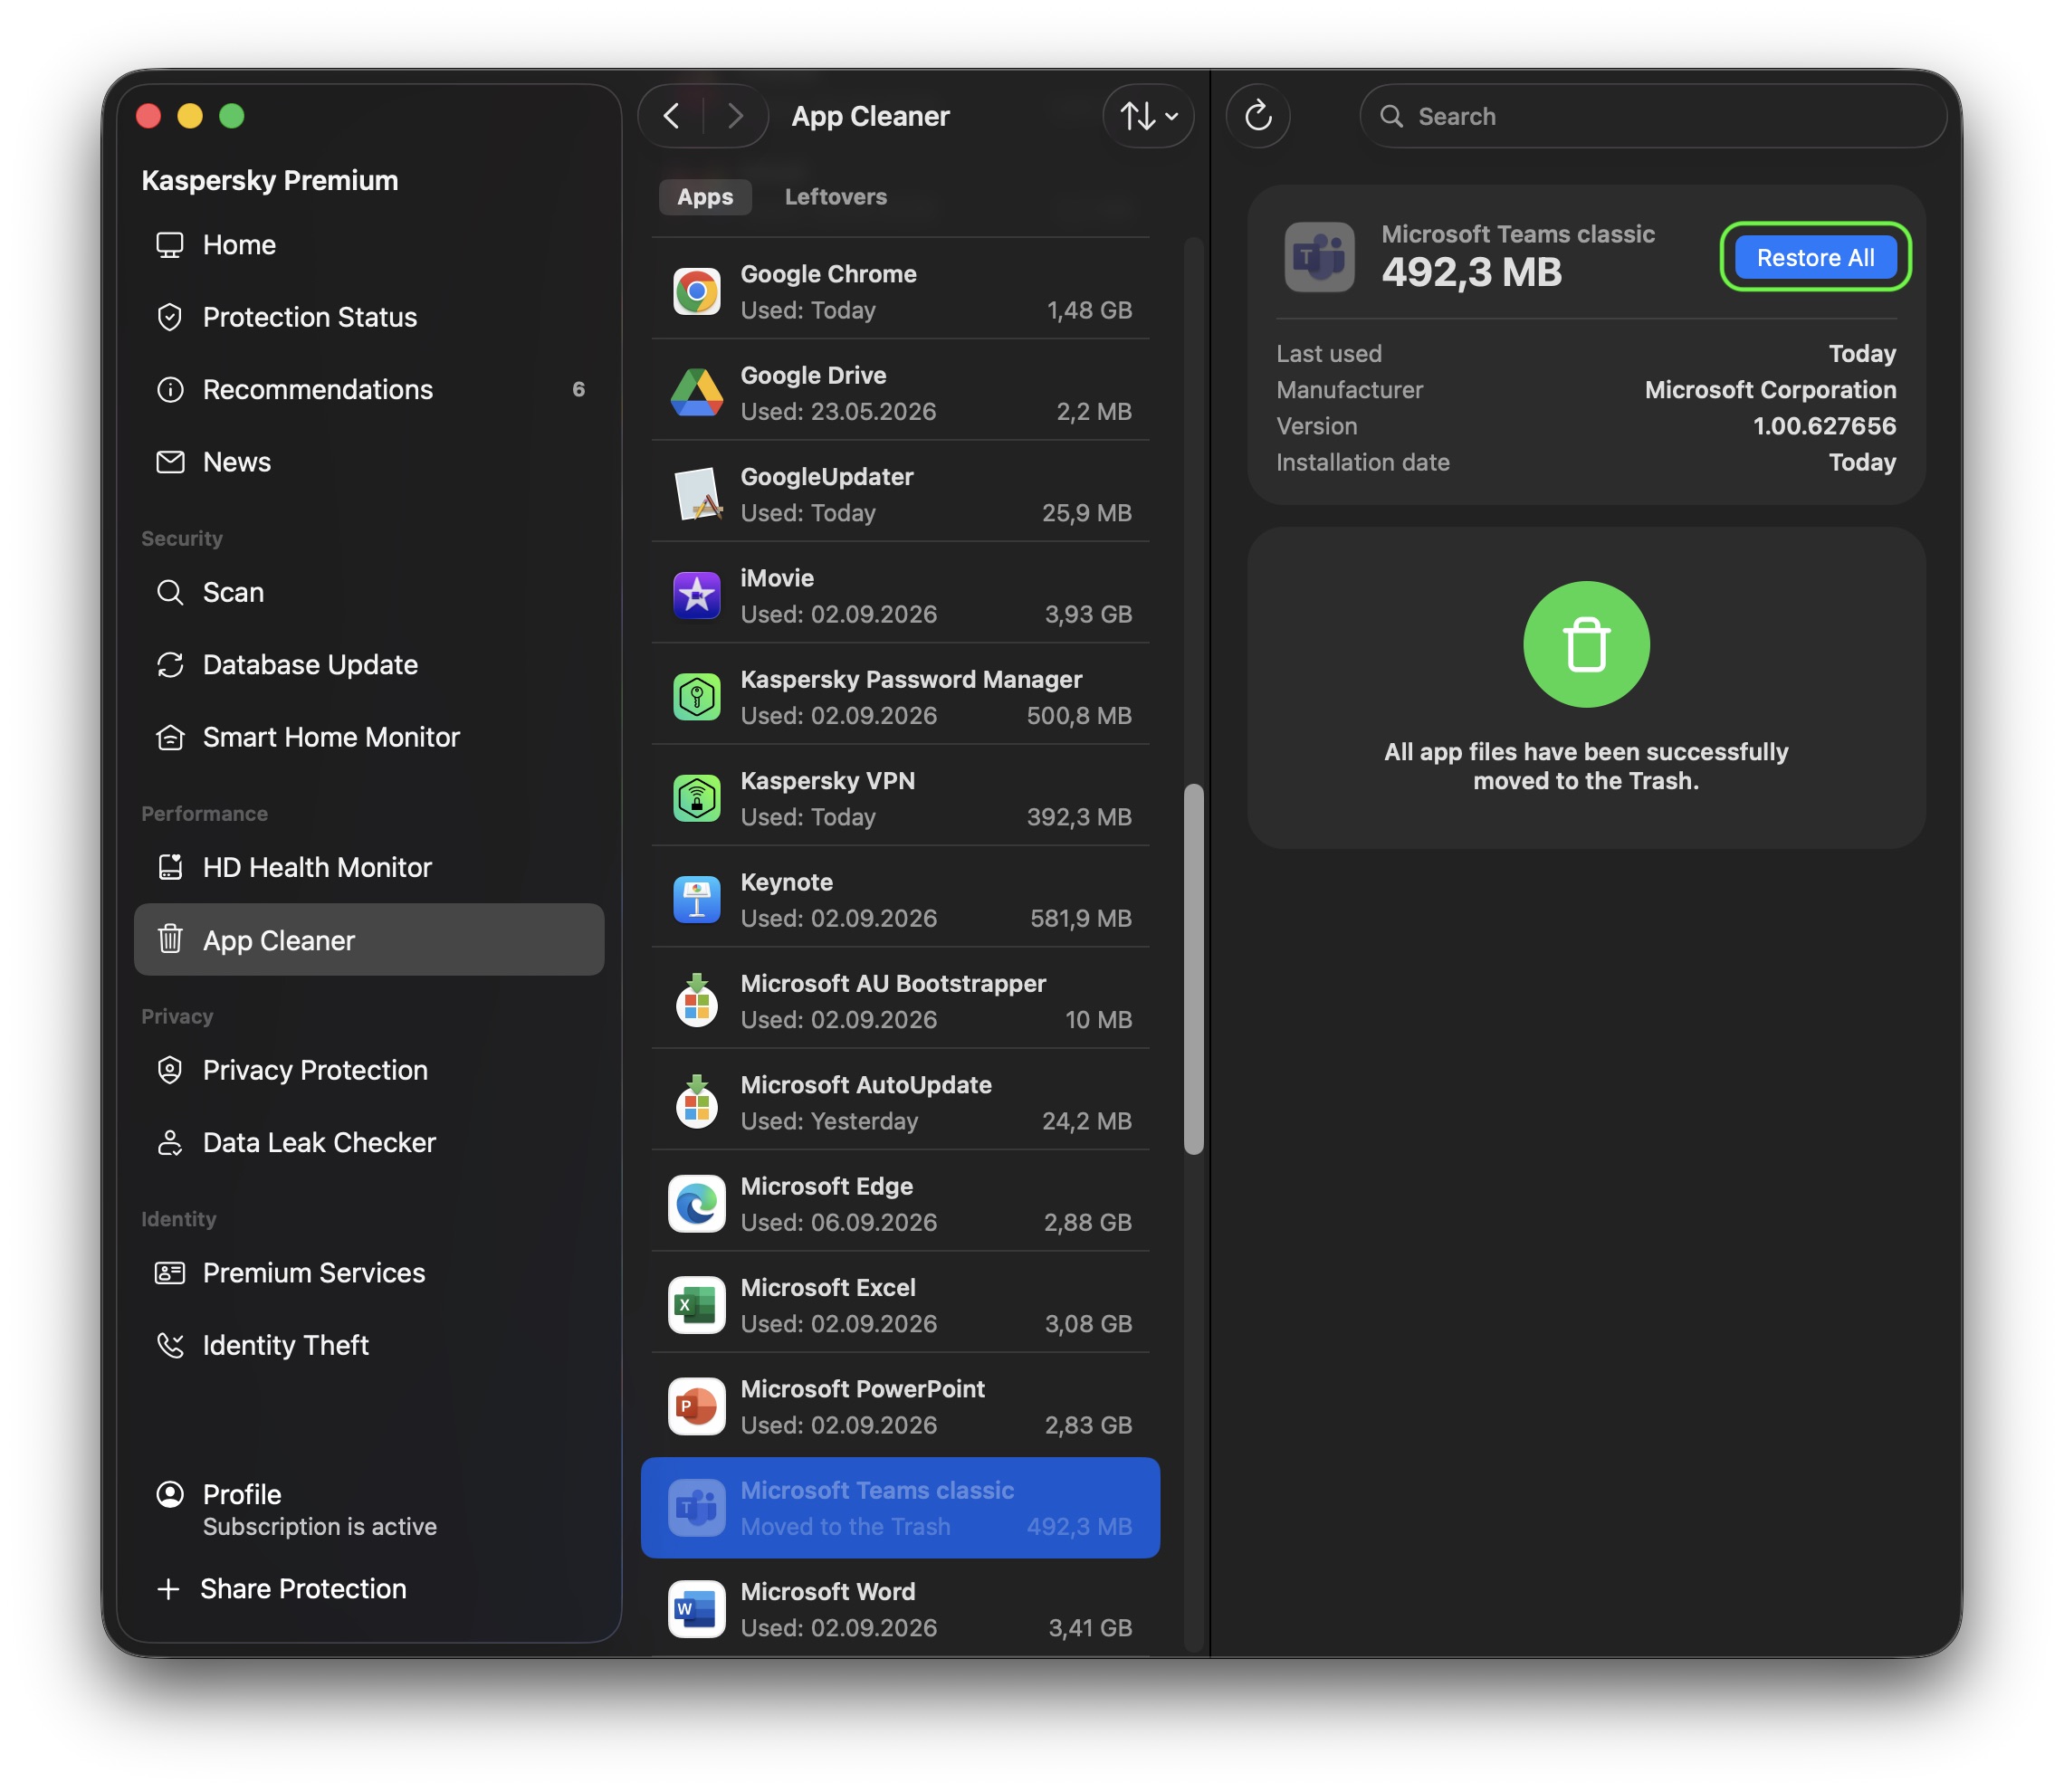
In the Apps tab, you can see every app installed on your Mac. Select the apps you no longer need, click Remove, then confirm your choice to delete them along with all their related files. The deleted files move to the Trash, from where you can restore them if needed. Ready to say goodbye for good? Just empty the Trash.

Before you remove anything, App Cleaner shows you not just the app but every file tied to it that will be deleted along with it, plus how much space each one takes up and where it’s stored. That way, you know exactly what you’re clearing out before you commit.

How to remove an app using App Cleaner

Select the app you want to remove in the Apps tab and click Remove. App Cleaner will delete it along with its related files

App Cleaner also helps users find and delete duplicate copies of applications. For example, those copied by mistake, or when one and the same app was installed from multiple sources. To free up space users caneither remove all duplicates at once or select individual ones.

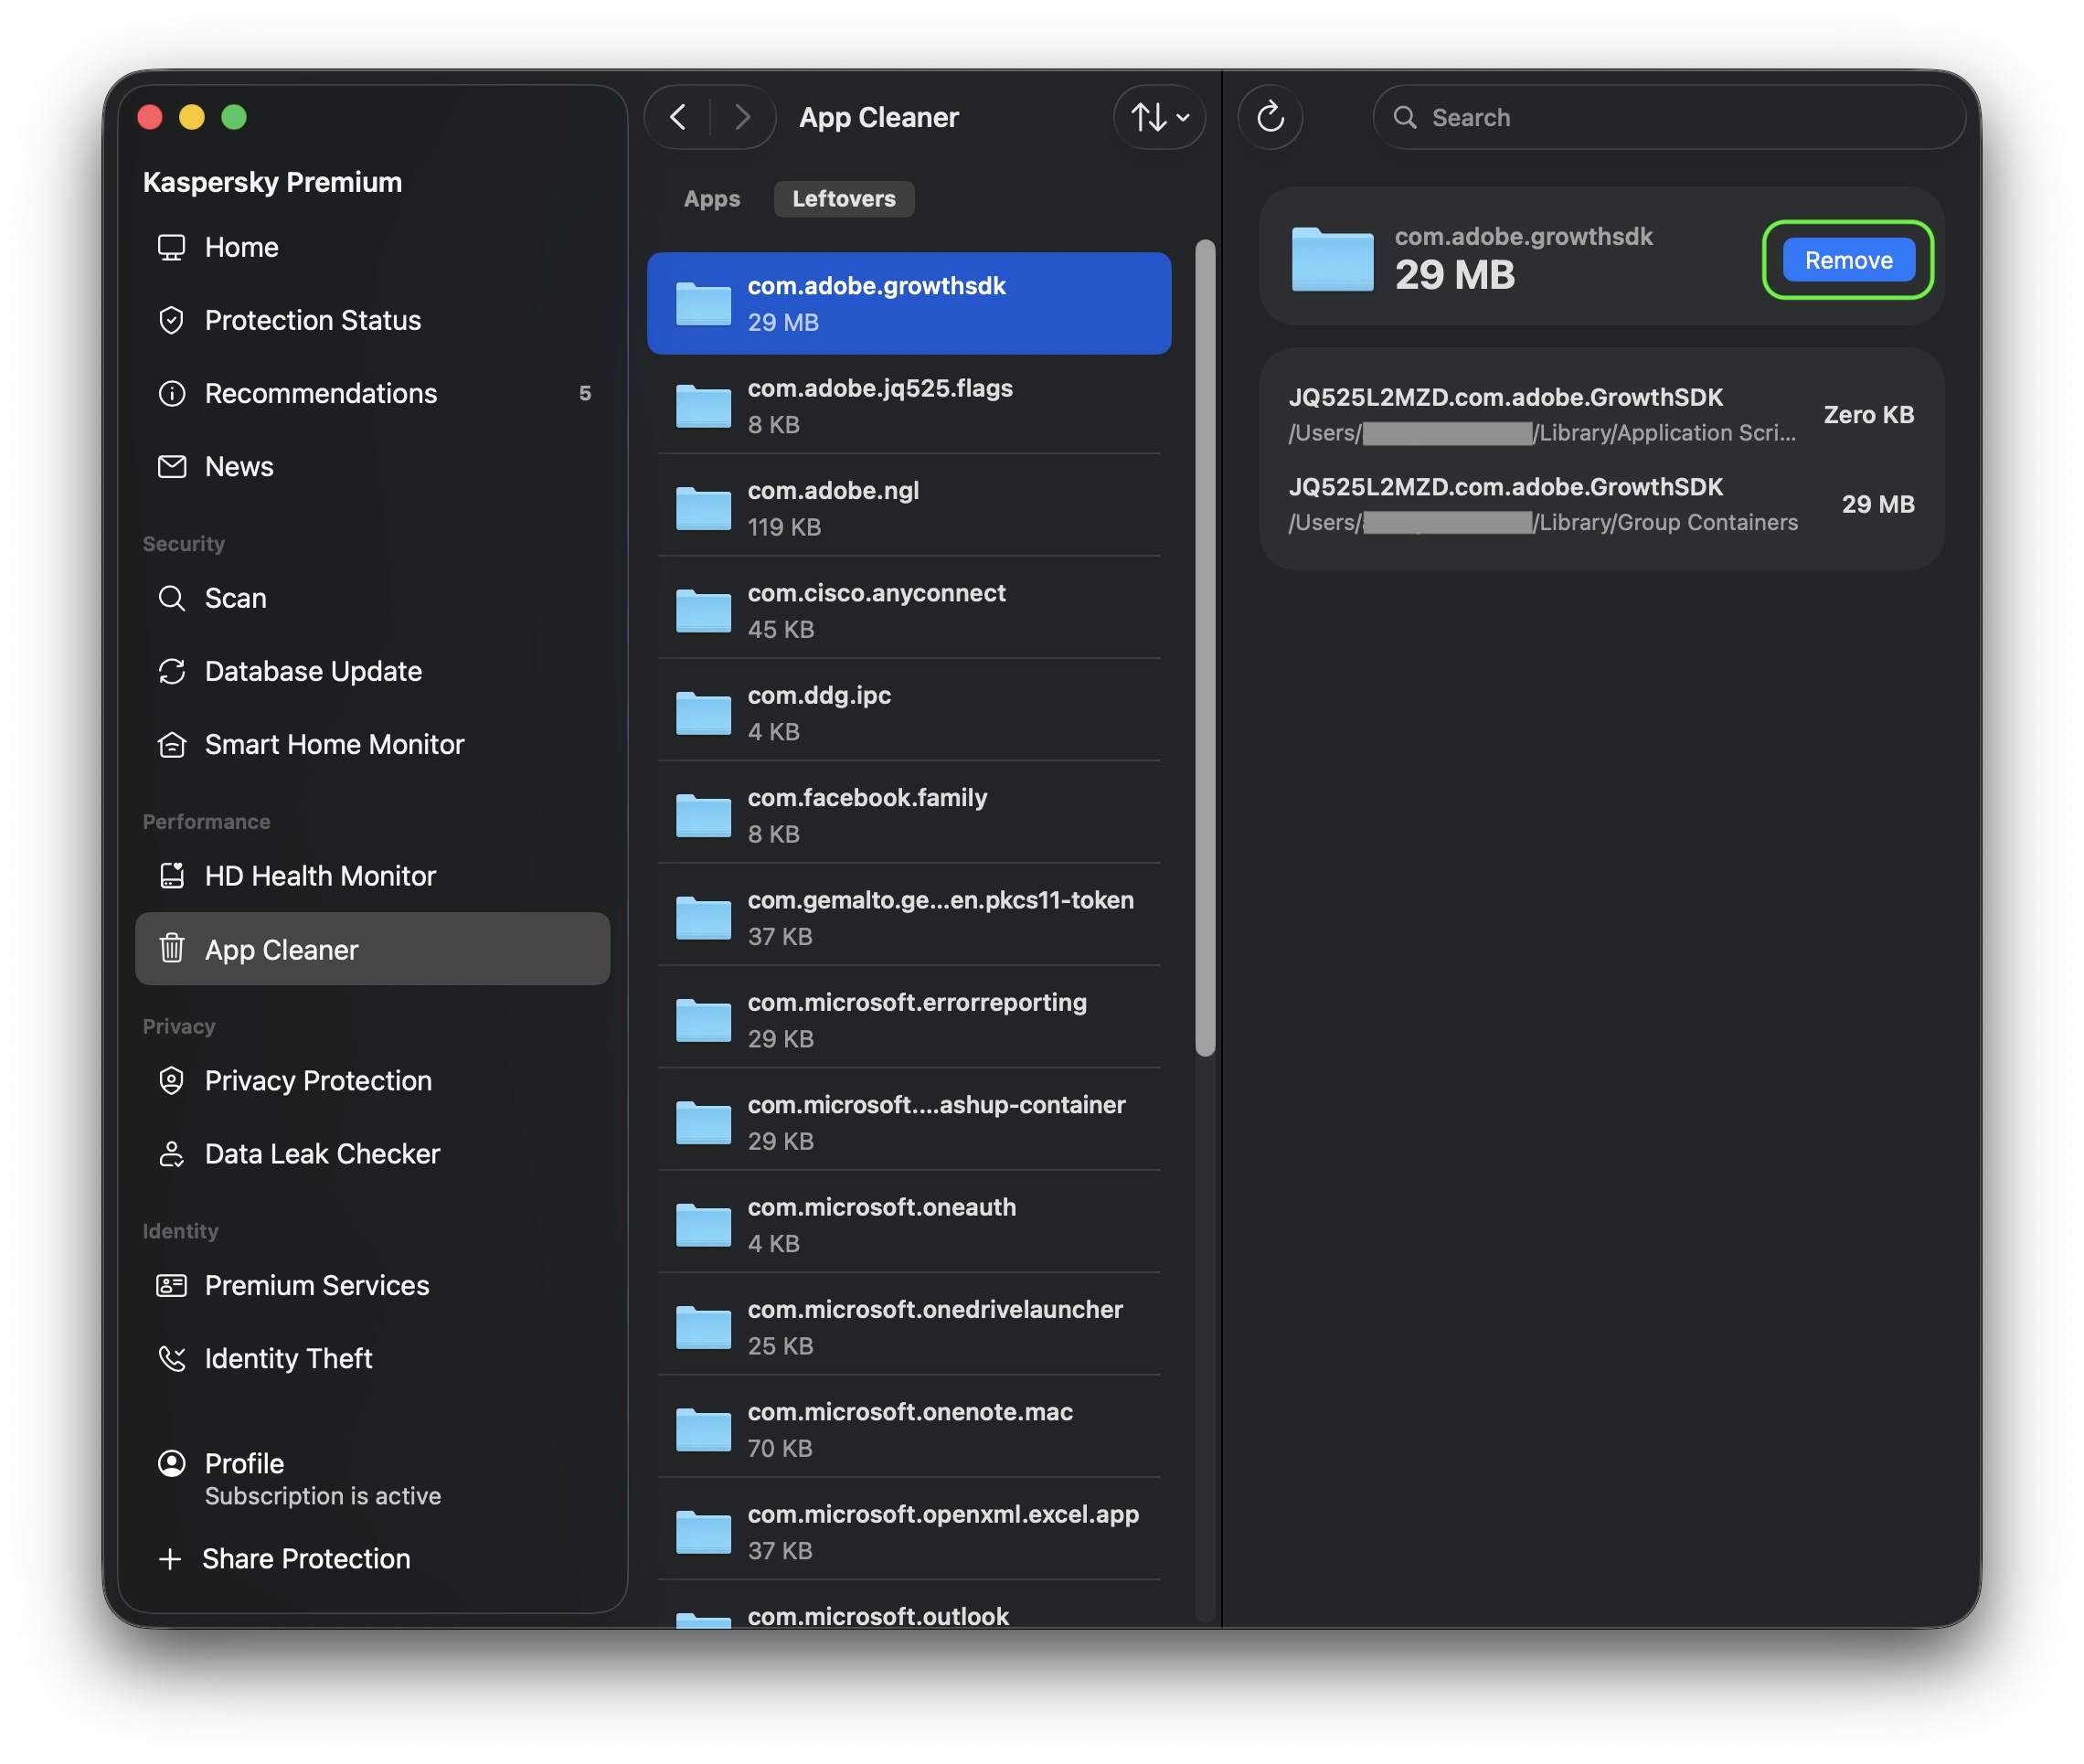
App Cleaner can also find leftovers from apps you previously deleted the regular way (by dragging them to the Trash). These show up in a separate Leftovers tab, where you can see what’s left, how much space it takes up, and where it’s stored. To clear them out, click Remove, then confirm by clicking Delete. As always, you can restore these files from the Trash if you change your mind.

How to remove the files left over from old apps

The Leftovers tab collects files left behind by the apps you’ve already deleted. Select the ones you don’t need and click Remove

Before closing Kaspersky Premium for macOS and emptying the Trash, double-check that you haven’t accidentally deleted a piece of software you need. If you have, you can bring back an app along with all its files right from App Cleaner: select the deleted app from the list and click Restore All. Once you close Kaspersky Premium for macOS, you can still recover deleted files from the Trash as long as you don’t empty it yet.

How to restore a deleted app

Select the deleted app and click Restore All. App Cleaner will bring it back along with its related files

Leftover files work the same way. As long as Kaspersky Premium for macOS is still open, you can restore them through App Cleaner. Once it’s closed, the Trash is your fallback.

Once your drive is free of clutter, it’s worth checking on its overall health too. That’s where another Kaspersky Premium for macOS feature — Hard Disk Health Monitor — comes in handy.

Not every cleanup tool is safe

When it comes to tidying up a Mac, it’s tempting to just download the first app that promises to clear out junk and free up space. But you should be careful about which program you choose. Criminals often disguise malware as well-known, legitimate Mac cleanup utilities. Kaspersky researchers have already found fake versions posing as CleanMyMac, Mole, and CCleaner Pro.

With Kaspersky, you don’t need to look for a separate cleanup tool at all. App Cleaner is already built into Kaspersky Premium for macOS. That means one solution protects your device from cyberthreats and clears out unwanted app leftovers — without the risk of accidentally downloading harmful software disguised as a cleanup tool.

What else is new in Kaspersky for macOS

App Cleaner helps you tidy up your Mac quickly and safely, freeing up time you can spend sorting through your own files instead — something no app can do for you yet. To get access to App Cleaner and other advanced protection features, purchase Kaspersky Premium for macOS or sign up for a free trial.

That’s not the only new feature in Kaspersky Premium for macOS. The app now includes Scam Protection Hub, a single control center for AI-powered protection against digital fraud. There’s also Shop with Confidence, which is now available across all our home security products. Alongside our longstanding filters for malicious sites, this feature blocks links to gray-area sites, like online stores that copy well-known brands to sell fake goods.

Still think macOS is immune to threats? Think again. Our research has found that Mac users actually run into cyberthreats more often than Windows users! Curious what those threats look like? Check out our other posts:

Getting AI for schoolwork right: 25 helpful prompts + usage tips | Kaspersky official blog

2 September 2026 at 15:40

Artificial intelligence has gone from a technological novelty to a tool so ordinary that kids in elementary school are already using it. Trying to ban children from using AI at this point makes about as much sense as it once did to ban search engines or Wikipedia.

Today we’re breaking down how chatbots actually work, and how to teach your kid to use AI as a study aid rather than a substitute for thinking for themselves

Explain to your child (and yourself) how AI works

Before explaining anything about artificial intelligence to your child, it helps to understand how it actually works and where its limits are.

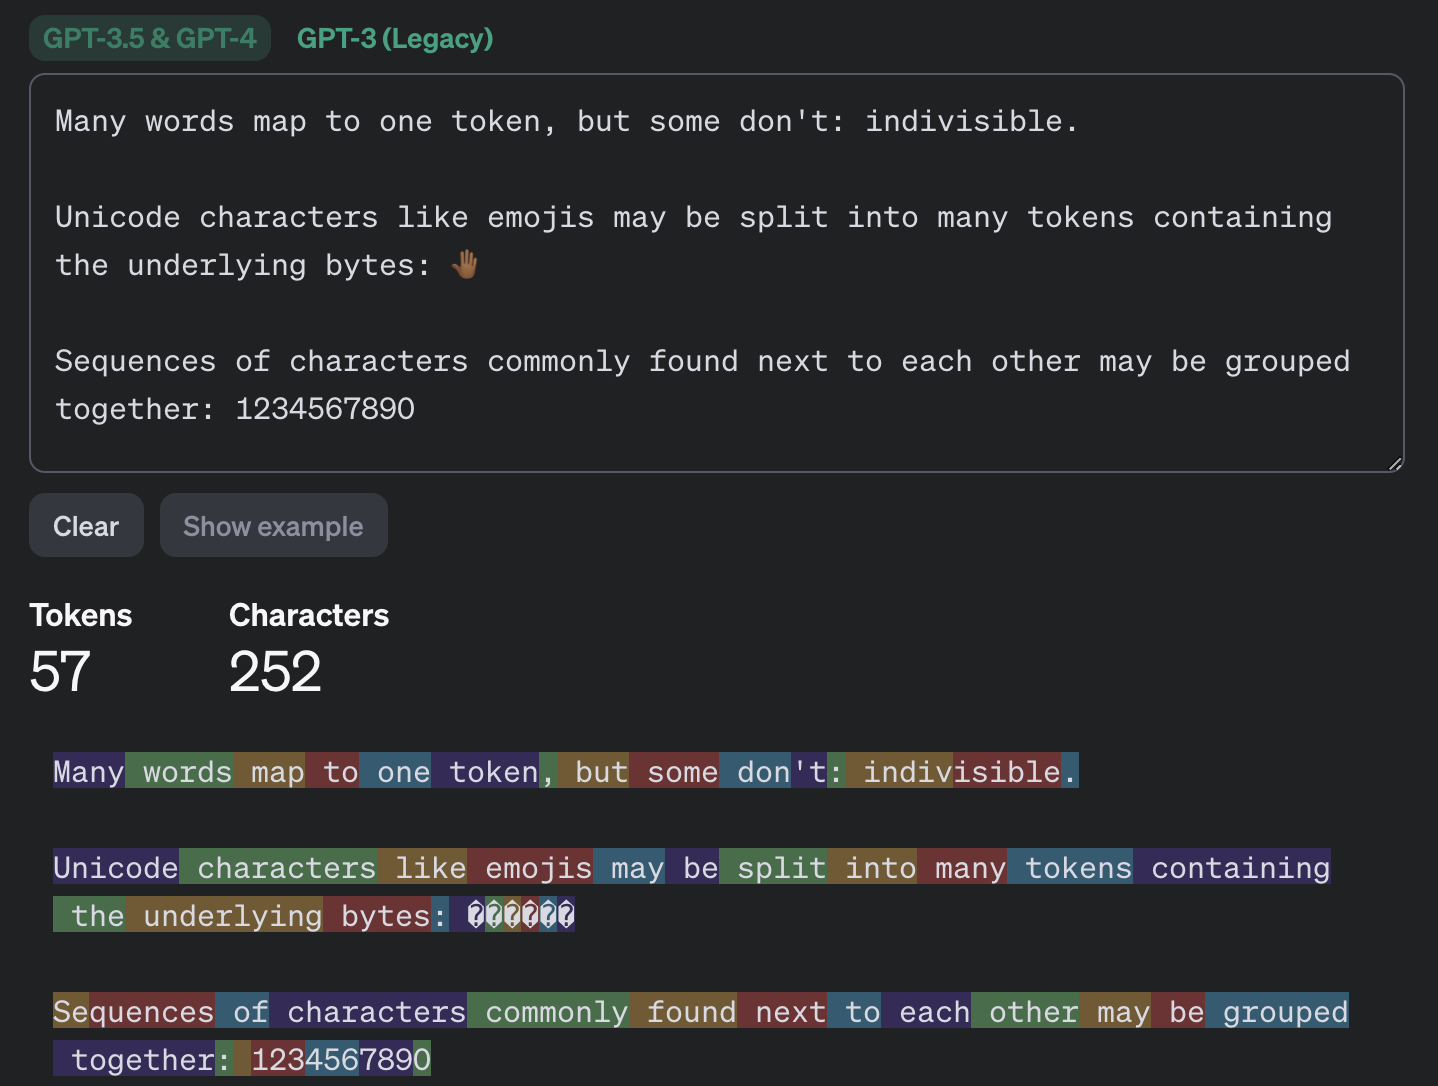
Most of the popular chatbots that kids (as well as adults) use are what’s known as large language models, or LLMs. To build such a model, researchers train it to spot patterns across huge amounts of text. The model breaks text down into small units called tokens (each token can be a sequence of words, a punctuation mark, a single word or character, or a whole sentence), then predicts which token is most likely to come next.

An example of how GPT-3.5 and GPT-4 break text into tokens

This example shows how the GPT-3.5 and GPT-4 models split messages into tokens. Source

The same thing happens when a chatbot converses with a person. A language model doesn’t actually reason on its own. It’s calculating which words and phrases are most likely to follow one another in order to produce a response that fits your query. That means chatbots will sometimes give incomplete or flat-out wrong answers, no matter how often they’re updated or retrained. A vivid example: just two years ago, popular chatbots confidently assured users that the word “strawberry” has two letters “r” instead of three. Mistakes like these are commonly known as hallucinations.

Many chatbots can also search the internet for information. In that case, the AI pulls in data from an outside source, but it still uses its own internal algorithms to put the answer together. And search results themselves can include outdated posts, advertising content, tabloids, and other questionable sources.

How to help your child use AI wisely

Talk to them about how AI can get things wrong

We’ve already seen that artificial intelligence isn’t immune to errors. Unfortunately, hallucinations aren’t the only issue. Even when a chatbot is working from accurate information, it can still present it in a misleading way by leaving something out, putting the emphasis in the wrong place, or drawing a questionable conclusion. Sometimes the result depends on factors a user would never think to consider when asking a question.

One surprising factor is simply what language you’re using. Most of the data that major models are trained on is in English, so these systems tend to perform better in English. The same AI model might answer a question correctly in English but get it wrong when asked the exact same thing in, say, Serbian. This gap shows up most in fields such as science, medicine, technology, and law, where there’s simply far more high-quality English-language material for the model to draw on.

Another quirk of chatbots is that they get worse as you feed them more information. Studies show that the more text and data a model has to work with, the harder it is for it to keep track of details, connect information from different parts of a conversation, and answer questions that require real depth of understanding. Therefore, uploading an entire book to a chatbot and asking detailed questions about it is a surefire way to trigger hallucinations.

It’s also worth questioning not just what the AI tells you, but the way you ask your questions in the first place. Chatbots often try to please the user, and will shape their answer to match the user’s apparent point of view. For example, the same chatbot might give opposite answers to “Why is the Earth overpopulated?” and “Why isn’t the Earth overpopulated?”, each time building its response around the assumption baked into the question. One recent study found that even the most advanced language models failed to challenge false premises in 26–42% of cases.

Let AI help with learning, not do the learning

Many a former student knows that copying others’ work is an art unto itself — one that takes exceptional skill and at least some engagement with the material (sometimes even a fair amount). These days, unfortunately, even that skill is at risk of disappearing: the temptation to copy an answer that took only a few seconds to generate is simply too strong. But chatbots are far from straight-A students themselves.

In one study, researchers had three popular chatbots sit a chemistry exam, and compared their scores to those of real students from 2009–2023. The students came out ahead. Chatbots will sometimes land on the correct answer, but arrive at it via a chain of flawed reasoning, so their answers could just as easily be wrong.

So it’s worth explaining to your child that having AI write essays from scratch, or solve equations without then double-checking them, is a dead end. On top of that, in a real job they’ll be judged on actual skills and knowledge, and chatbots won’t help them fake the expertise. What AI can genuinely help with, without getting in the way of learning, is explaining difficult topics and working through mistakes. Here are some examples:

If a topic is hard to make sense of

  • “Explain this topic in simple terms: {insert topic}”
  • “Explain this topic using a real-life example: {insert topic}“
  • “Here’s the part I don’t understand: {insert text}. Walk me through it step by step”
  • “Explain this topic in simple terms first, then in more technical terms: {insert topic}“
  • “Here’s a question: {insert question}. Don’t give me the answer. Ask me guiding questions so I can work it out myself”

Math and other exact sciences

  • “Give me a hint for the first step, but don’t solve the whole problem: {insert problem}“
  • “Look at my solution and tell me where I made a mistake, but don’t fix it for me: {insert problem and solution}“
  • “Come up with a similar problem for me to try: {insert problem}“
  • “Here’s my answer: {answer}. Ask me questions so I can check whether I solved it correctly”
  • “Explain why this formula applies here: {insert problem}“

Essays and written assignments

  • “Ask me five questions on this topic so I can come up with my own thesis and arguments: {insert topic}“
  • “Here’s a draft of my essay. Try to find gaps in my logic or places that need more detail: {insert draft text}“
  • “Look at my essay outline and tell me what’s missing: {insert essay outline}”
  • “Point out places in my writing where the idea isn’t clear, but don’t rewrite it for me: {insert text}“
  • “Pretend you’re an experienced teacher and try challenging my argument: {insert text}“

Language learning

  • “Have a conversation with me in {insert language} at an A2 level. After I respond, correct my mistakes”
  • “Give me five sentences to translate using this grammar structure: {insert grammar structure}“
  • “Explain this grammar rule and give me some examples: {insert grammar rule}“
  • “I’ll write a sentence, and you tell me if it has a mistake. Give me a hint first, and only show me the correct version after my second attempt. {insert sentence}“
  • “Write a short dialogue in {insert language} where I have to answer as one of the characters”

Knowledge testing

  • “Quiz me with 20 questions on this topic: {insert topic}. Ask one question at a time, and don’t show the answer right away”
  • “After each answer, only explain what I got wrong”
  • “Start with five easy questions, then ask five hard ones”
  • “Make the questions harder each time I answer correctly”
  • “Based on my mistakes, tell me which topics I should review”

Fact-check AI responses together

Make sure your child understands that they shouldn’t blindly trust what a chatbot tells them — even when it cites other sources. And asking the same chatbot to double-check its own work isn’t a great idea either; there’s a real chance it will make the same mistakes twice, or even pile up the errors.

Take any chatbot answer and go through it together, breaking it down into individual statements and asking questions about each one. Where did that date or number come from? Is the AI citing a specific person, publication, or study? Is the quote actually something that person said? If the chatbot includes a link, open it and check how accurately the AI actually represented it.

While you’re at it, take a look at the quality of the source itself. If something is written in an overly emotional tone or makes bold claims without backing them up, that’s a good sign to look for information somewhere else.

Protect your child and their accounts

Anything your child shares with a chatbot ends up on that company’s servers, and it’s used to further train the model by default. Over the past few years we’ve seen that even the biggest companies aren’t immune to bugs and data leaks. To lower the risk of your child’s information leaking and to keep their account secure, follow a few simple rules:

  • Make sure your child understands that AI isn’t a private diary. Tell them not to share their name, home address, school, or any other sensitive information with a chatbot.
  • Adjust the chatbot’s privacy settings. At the very least, turn off memory and any “improve the model” or training features. It’s also worth reading our detailed guides on setting up privacy and security in ChatGPT and DeepSeek.
  • Update the password. Most chatbots require an account, so to keep your child’s from being hacked, set a strong password that isn’t reused anywhere else. Whether your child’s password follows the classic “mother’s maiden name plus birth year” formula or uses popular meme words like “skibidi”, we have some bad news: passwords like these get cracked really fast. Instead of coming up with and memorizing passwords, it’s better to let an encrypted password manager generate and store them.
  • Turn on two-factor authentication. This adds an extra hurdle for anyone trying to break into your child’s account. Rather than using a phone number as the second factor, it’s better to use login codes generated and automatically refreshed in a password manager.
  • Use anti-phishing protection. Beyond fake websites that impersonate legitimate AI services, there’s another risk: chatbots sometimes hand users links to phishing sites (fake pages designed to steal personal information). Kaspersky Premium blocks access to suspicious sites and keeps scammers from stealing your family’s data and money.
  • Know what your child is doing online. Along with a password manager and protection from malware and phishing, Kaspersky Premium includes Kaspersky Safe Kids, which lets you set up parental controls, restrict unwanted content, and keep track of how much time your child spends online.

What else to read about keeping kids safe online and at school:

What to do if you find someone else’s bank card | Kaspersky official blog

27 August 2026 at 18:17

Neighborhood chats regularly light up with posts about lost bank cards being found. People mean well and want to help a neighbor out, so they post a photo of the card with the number and other details fully visible. Others mention in the chat that they’ve left the card with, say, a security guard, cashier, or manager at whatever store or business it was found, or which happens to be the closest. Today we’re going to explain why none of that is a good idea, and what you should really do if you find someone else’s bank card.

What NOT to do if you find a lost card, and why

Let’s start with why you shouldn’t post a photo of the card with its details visible in a group chat, keep the card, or hand it to a stranger. The first reason is the most obvious, but worth spelling out anyway: card details are private information that shouldn’t be shared with people who have no business seeing them. A photo posted in a group chat can end up in the hands of criminals, who may try to use those details to make fraudulent purchases online. The worst-case scenario is a photo showing both sides of the card that also exposes the three-digit security code (known as the CVC, CVV, or CVP) on the back.

Now to a less obvious point: why you shouldn’t post about finding a card, even with a photo of it with the number blurred out, and then hold on to it, planning to return it once the owner turns up. Since there’s no guarantee you were the first person to have the card in your hands, doing this puts you at risk of coming under suspicion if money disappears from that account. Even if you had absolutely nothing to do with any theft, the mere fact that the card was in your possession for a while could still land you in an uncomfortable conversation with its owner or the police.

The same logic applies to handing the card over to a third party. A security guard, cashier, or manager is just as much a stranger as anyone else, and none of them have any special authority to take charge of a found bank card. Handing it to them gives them the opportunity to use someone else’s money themselves, and if that happens, you could end up as a person of interest.

An “out of sight — out of mind” approach, that is, leaving the card where you found it, or moving it somewhere more visible, is safer for you personally, but it’s still not really the right call. If you do that, someone else will find it, and there’s no guarantee that they’ll be a decent person. They might try to drain money from the rightful owner’s account. So this isn’t a good option either.

What you SHOULD do with a found bank card

Now let’s talk about what you should do instead. The right approach might surprise you: call the bank that issued the card, report that you’ve found it, and then… destroy the card. It’s entirely possible the owner hasn’t even noticed it’s missing yet: with contactless payments now so widespread, a physical card can sit untouched in a wallet for quite a while. The bank will block the card, notify the owner that it’s gone, and issue a new one.

That last step — destroying the card — may come as a surprise and even attract some push-back among readers, but we stand by it: a found card really should be destroyed. That way, no one can possibly use it, and you won’t have to hold onto someone else’s property or risk coming under suspicion if money goes missing from the account. The simplest and most reliable way to destroy a card is to carefully cut it into small pieces with kitchen scissors and throw it in the trash or recycle it.

Here’s something worth keeping in mind: these days, a physical card isn’t actually worth all that much to its rightful owner. For one thing, banks reissue cards quickly and easily. With most banks, you won’t even need to visit a branch since the new card gets delivered straight to your door.

For another, getting a new card issued usually doesn’t leave the owner unable to pay for things in the meantime: in many cases, they can just switch to a virtual card or another payment method. So a destroyed card is a much smaller headache for its owner than the risk of its ending up in the wrong hands and being used to drain their account.

And if the card’s disgruntled owner does somehow track you down with questions, just show them this article so they can appreciate the trouble they avoided, thanks to you.

When you shouldn’t destroy a found card

Beyond bank cards, there are also multi-purpose cards, such as ones issued to schoolchildren and students that combine a few functions, like a school or university access pass and a public transit pass. Kids, especially younger ones, lose these kinds of cards fairly often. Restoring full functionality on cards like these can take much longer than reissuing a bank card, and the amounts stored on them are usually small, so if you find one, your best move is to take it to the school or university named on the card and hand it to security or reception / front office.

In short: what to do if you find someone else’s card

To sum it up, if a lost bank card ends up in your hands:

  1. Look for the bank’s phone number on the card. It’s usually printed there; if not, you can easily find it on the bank’s official website. Then give them a call. Let them know you’ve found someone else’s card.
  2. After the call, destroy the card: cut it into small pieces with scissors and throw it away.

And one more reminder of what not to do: don’t post photos of the card or its details in chats or on social media, don’t hold on to the card hoping to track down the owner, and don’t hand it over to strangers.

We’d also recommend following our blog to stay on top of the latest online threats. And feel free to share this article in that neighborhood chat so your neighbors know exactly what to do if they ever find someone else’s bank card.

As for protecting your own money, it’s worth using a robust, multi-layered security solution that safeguards your money, cards, wallets, and payments. Read more in Five Kaspersky technologies to protect your finances.

What other hidden risks do bank cards carry? Find out in our other posts:

Dangerous email attachments: the files you should never open | Kaspersky official blog

7 August 2026 at 11:57

Have you ever tried to open an “encrypted” email or an urgent document, only to realize with horror that your usual DOCX attachment is actually a file with the extension .docx.exe? Or maybe you received an email supposedly with an invoice, contract, or internal memo attached — only for the file to prove something entirely different from what it claimed to be? If so, you were likely targeted in a malware infection attempt.

Cybercriminals routinely disguise malicious files as harmless documents and archives, banking on recipients blindly clicking without checking the extension. Kaspersky experts analyzed the file formats most frequently deployed in malicious email blasts to reveal what really lurks behind these extensions — and how attackers weaponize them in their campaigns.

Important note: the extensions we’ll be discussing here are routinely used for completely legitimate files. For example, Windows executables normally end in .exe. However, we’re focusing specifically on scenarios where attackers disguise or spoof a file’s extension to pass it off as a totally different type of file.

What extensions are most commonly found in malware?

Our experts analyzed malicious email blasts from the beginning of 2026 to pinpoint the 15 most common dangerous file extensions.

.exe
.js
.html
.dll
.bat
.vbs
.xls
.pdf
.jse
.au3
.docx
.htm
.wsf
.scr
.lnk

The top 15 file extensions used in malicious email blasts

Let’s take a look at what files with these extensions actually do under the hood.

Executable files

An executable file is a compiled computer program that’s ready to run. Once launched, a malicious executable can download additional payloads, alter system settings, steal user data, connect your device to external attacker-controlled servers, and much more. These are the most common executable extensions found in malicious email campaigns:

  • .exe
  • .dll
  • .com
  • .scr

.exe

The classic Windows executable extension. It powers every program you use daily, from web browsers and games to office suites and software installers.

By the way, attackers often wrap EXE malware in double extensions: invoice.docx.exe, report.pdf.exe, or even photo.jpg.exe. They take advantage of a default Windows setting: hiding extensions for known file types. Because this setting is turned on by default, users only see the first part of the file name — invoice.docx, report.pdf, or photo.jpg — and assume it’s just a normal document or image. But the second you open this trap file, the malware fires up.

.dll

Another common extension abused in malicious campaigns is .dll (dynamic-link library). These libraries hold functions that Windows programs frequently require while running, such as printing a document. This modular architecture prevents redundant code by letting multiple applications call on the exact same library for specific tasks. However, if an attacker replaces a legitimate library with an infected one, running any normal program that calls on it can trigger malicious code.

.com

While files with the .com extension have absolutely nothing to do with the web domain of the same name, cybercriminals likely count on victims mistaking these files for links in an unusual format. In reality, it’s a legacy Windows executable format.

While modern versions of Windows no longer rely on this file type, the operating system can still run and execute it, which makes opening one a very bad idea.

.scr

SCR files are screensavers — those idle Windows screen animations featuring abstract patterns, the iconic bouncing logo, or whatever else. Despite their harmless reputation, screensavers are essentially executables just like EXE files: once opened, they can install extra components or alter system settings all the same. In malicious campaigns, these files routinely masquerade as images, screenshots, or documents.

Scripts

Scripts are text files containing a sequence of commands that a computer runs automatically in order. They can download files, install and launch programs, modify security settings, and plenty more. Email attackers rely on the following script types most often:

  • .js and .jse
  • .bat
  • .cmd
  • .vbs
  • .wsf
  • .vbe
  • .au3

.js and .jse

The .js and .jse extensions are used by JavaScript files. Most users associate JavaScript strictly with websites and don’t realize these files can run locally on their computer as standalone programs.

We recently wrote about CrystalX RAT, a remote access Trojan that logs keystrokes, steals clipboard contents, and injects malicious components into web browsers upon installation. Its JS scripts monitored cryptocurrency wallet addresses and silently swapped them with the attacker’s own to hijack transactions in real time.

.cmd and .bat

BAT and CMD files are designed to automate tasks in Windows and can execute virtually any command in the operating system. Launching a file like this can infect your computer with malware.

.vbs

Visual Basic Script files with the .vbs extension are a long-time favorite among cybercriminals. Attackers frequently use double extensions to disguise .vbs files as plain text documents, such as invoices, app installation guides, or emails. For example, in the early 2000s, the iconic ILOVEYOU worm spread via a VBS script, infecting millions of computers worldwide. Victims received an email with the subject line “ILOVEYOU”, but instead of a sweet confession, the attachment contained a malicious script. At its peak, this “romantic” worm had infected up to 10% of all internet-connected computers.

Web files

This category mainly includes .html, .htm, .hta and .svg files. Often these are phishing pages in disguise, designed to mimic login forms for email, cloud services, banking apps, and other platforms. Naturally, any credentials entered on these fake pages go straight to the attackers hunting for your accounts and money. Web files can also trigger malicious scripts and download additional payloads onto your system.

Archives

Cybercriminals routinely package malicious files inside archives (most commonly having .zip, .rar, and .7z extensions). These archives are often password-protected or encrypted to hinder content scanning. Additionally, attackers sometimes create intentionally corrupted archives with damaged data structures: basic security filters often stumble over broken files and skip scanning them altogether, whereas archive managers can automatically repair and unpack the contents anyway.

That’s why we recommend using advanced security solutions that can spot phishing emails and prevent you from launching dangerous files hidden inside archives.

PDF files (.pdf)

To many, PDF feels like a completely harmless file format — after all, what could go wrong with flight tickets, documents, and slide decks? But beyond static text and images, PDFs can host clickable links, forms, and even scripts.

Malicious code in a PDF is usually tucked away behind visual elements or embedded as hidden text. What’s more, the risk comes not just from the file itself, but also from the software you use to view it: for instance, attackers spent months exploiting a vulnerability in Adobe Acrobat that allowed them to execute malicious PDF files remotely. If you regularly work on PDF documents, make sure the JavaScript feature is disabled in your Adobe Acrobat. To do this, go to Preferences → JavaScript in the menu.

By the way, heavy users of AI agents and chatbots should keep in mind that AI frequently falls for prompt injections: hidden commands buried inside images, text, and web pages that the AI interprets as legitimate instructions, and executes without your knowledge.

LNK shortcuts (.lnk)

Files with the .lnk extension are standard Windows shortcuts that we use every day for quick access to apps and folders. By themselves, shortcuts don’t contain any software — they simply tell Windows what file to open or what command to run.

However, an attacker can give a shortcut any icon and any name they want, completely hiding its real destination. The moment a victim clicks the shortcut, the infection chain kicks off. The malicious code usually executes silently in the background, leaving virtually no visual clues that anything went wrong.

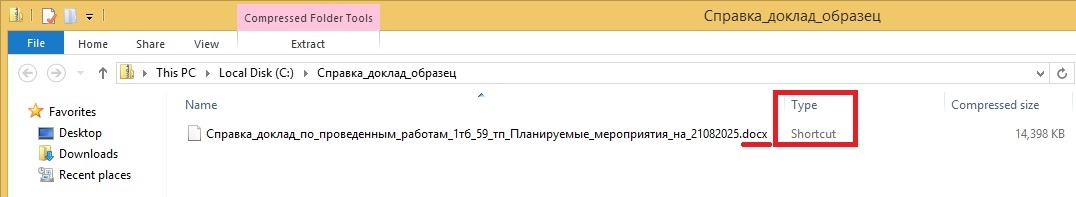
Cybercriminals also like to hide LNK files behind double extensions — betting that users won’t look close enough to see what kind of file they’re actually opening. Here’s a classic example:

Attackers use double extensions to disguise malicious LNK files

Windows File Explorer displays only the first part of the extension, .docx. The file type is clearly listed as a shortcut, but very few people notice that detail

Your best bet is to avoid clicking incoming LNK files altogether: no one in their right mind has a reason to email you a desktop shortcut.

By the way, if you haven’t updated Windows in a while, we’ve bad news for you: malicious code can automatically execute without you ever clicking the LNK — simply opening the folder where it lives is enough to trigger it. Microsoft finally released a patch for this long-abused vulnerability in December 2025. So don’t put off system updates — install them regularly to patch up the security holes attackers rely on.

Microsoft Office documents

.xls and .xlsx

The file extension .xls is used by older versions of Microsoft Excel. Millions of people use Excel spreadsheets every day, and many are still running outdated software, which makes XLS files a favorite bait for cybercriminals. Budgets, employee rosters, financial records, urgent reports, and other spreadsheets stop being harmless the moment a user clicks Enable Content, allowing the program to run macros — custom Microsoft Office scripts and commands built into the files. Once allowed, the malicious macro gets free rein to download files, launch programs, harvest system data, and alter settings.

Unlike XLS, XLSX is the modern Excel format, which doesn’t support embedded macros by default. Unfortunately, that doesn’t guarantee complete safety: the spreadsheet can still pull live data from external sources and automatically connect to web destinations in the background.

.docx

Although modern DOCX files don’t support macros by default, attackers have long figured out other ways to weaponize these documents. Typically, malicious DOCX files contain embedded links or instructions that force Word to contact external servers and pull down malicious payloads. Back in 2023, for instance, researchers uncovered a Microsoft Office vulnerability that allowed attackers to trigger built-in Windows system tools and download malware straight from the web.

To reduce your risk when working with Microsoft Office apps, we recommend turning on Protected View, blocking external connections, and disabling all macros without notification.

Macro support in modern Microsoft Office

Macros are sequences of commands that automate complex, repetitive tasks in Excel, Outlook, Word, and PowerPoint. In modern versions of Microsoft Office, documents containing embedded macros are saved in specialized file formats with extensions like .xlsm, .xltm, .xlsb, .docm, and .pptm. While Microsoft Office includes built-in security controls — such as blocking files downloaded from the web and warning you about potentially dangerous macros — if you don’t actually use macros and have no specific reason to run them, treat files with these extensions with caution.

How to check if a file is safe

  • Use a comprehensive security suite that automatically scans files for malware, prevents infections, blocks visits to suspicious sites, and completely removes malicious files from your devices. You can take advantage of a 30-day trial of Kaspersky Premium if you urgently need to disinfect your computer or scan a file for viruses.
  • Never open attachments from unknown senders. Curiosity can cost you dearly, since many malware strains specifically hunt for credit card and crypto wallet data. Let the Mail Anti-Virus feature included in our security solutions do the heavy lifting: it automatically filters out malicious or suspicious emails and protects you from phishing attacks.
  • Examine incoming emails carefully: cybercriminals have become adept at disguising malicious messages. Always verify email addresses against official ones and make sure you know the signs of phishing and spam. Attackers might try to scare you with claims of a hacked account, lure you to shady sites with “unbeatable deals”, or urge you to review a work document attached to the email. Any attempt to manipulate your emotions is a major red flag that someone is trying to trick you.
  • Never open files with double extensions. It’s almost always a trap.
  • If you run into a file with an unfamiliar extension, take a moment to look it up online. Remember: a photo or plain text document will never have an .lnk or .vbs extension.

Check out our other posts on email and file security:

Scams in messengers: exposing the global scam-cartels exploiting everyday messagesng-heist | Kaspersky official blog

1 June 2026 at 09:00

It starts with the familiar: a short message, a trusted name, a routine tone. Delivery updates, work pings, brand alerts hum in the background, rarely attracting scrutiny. You check, you answer… — until minutes later you’ve slipped into a trap built to lower your guard and hijack your trust.

That’s why messaging scams cut deep: they exploit everyday habits where instinct, not caution, leads. Communication once moved slowly, leaving room for doubt. Now it’s instant — and that speed is a weapon in criminal hands.

On our blog, we’ve already examined numerous scam schemes in messaging apps — from pig butchering, where the victim is groomed for a very long time, or catfishing, where the scammer creates a fake identity, to phishing via chatbots or through gift-giving campaigns in messaging apps.

Now, for the first time, Kaspersky has set out to capture the full end-to-end reality of messaging-based scams to understand how quickly harm occurs, how they impact trust and what remains after the interaction ends. What emerges is a highly organized and industrialized scam ecosystem embedded within everyday messaging channels such as SMS, WhatsApp, and email.

Kaspersky experts have prepared a report on targeted scams in messaging apps, detailing not only the financial but also the emotional damage caused by such attacks, as well as providing tips on how to protect yourself and avoid them. In this post, we explore the most interesting facts, but you can find more details in the full report.

The damage is underestimated

How much do you think a single successful attack via a messaging app costs the average victim? Ten dollars? Or maybe 50? You’re underestimating the scammers. Although more than a third (36%) of victims incur losses of less than $135, on average a victim loses… $733!

Country Average loss per victim
Senegal $392.94
Serbia $493.32
Morocco $504.28
Greece $609.32
United Kingdom $617.38
Côte d’Ivoire $654.11
Spain $672.67
United States $724.73
Portugal $868.20
Italy $896.02
France $1,193.58
Germany $1,369.35

The average amount lost by a victim in a successful attack via a messaging app

On the one hand, the financial hit doesn’t look catastrophic in isolation. These are micro-losses by design. Small enough that some never report them to the police. Small enough that banks don’t always investigate. Small enough to be dismissed as bad luck rather than organized crime.

But $733 is not nothing. It’s enough to cover a month’s worth of groceries, school or daycare fees, or utility bills. Against the backdrop of the global cost-of-living crisis, a single such loss can seriously dent a family’s budget.

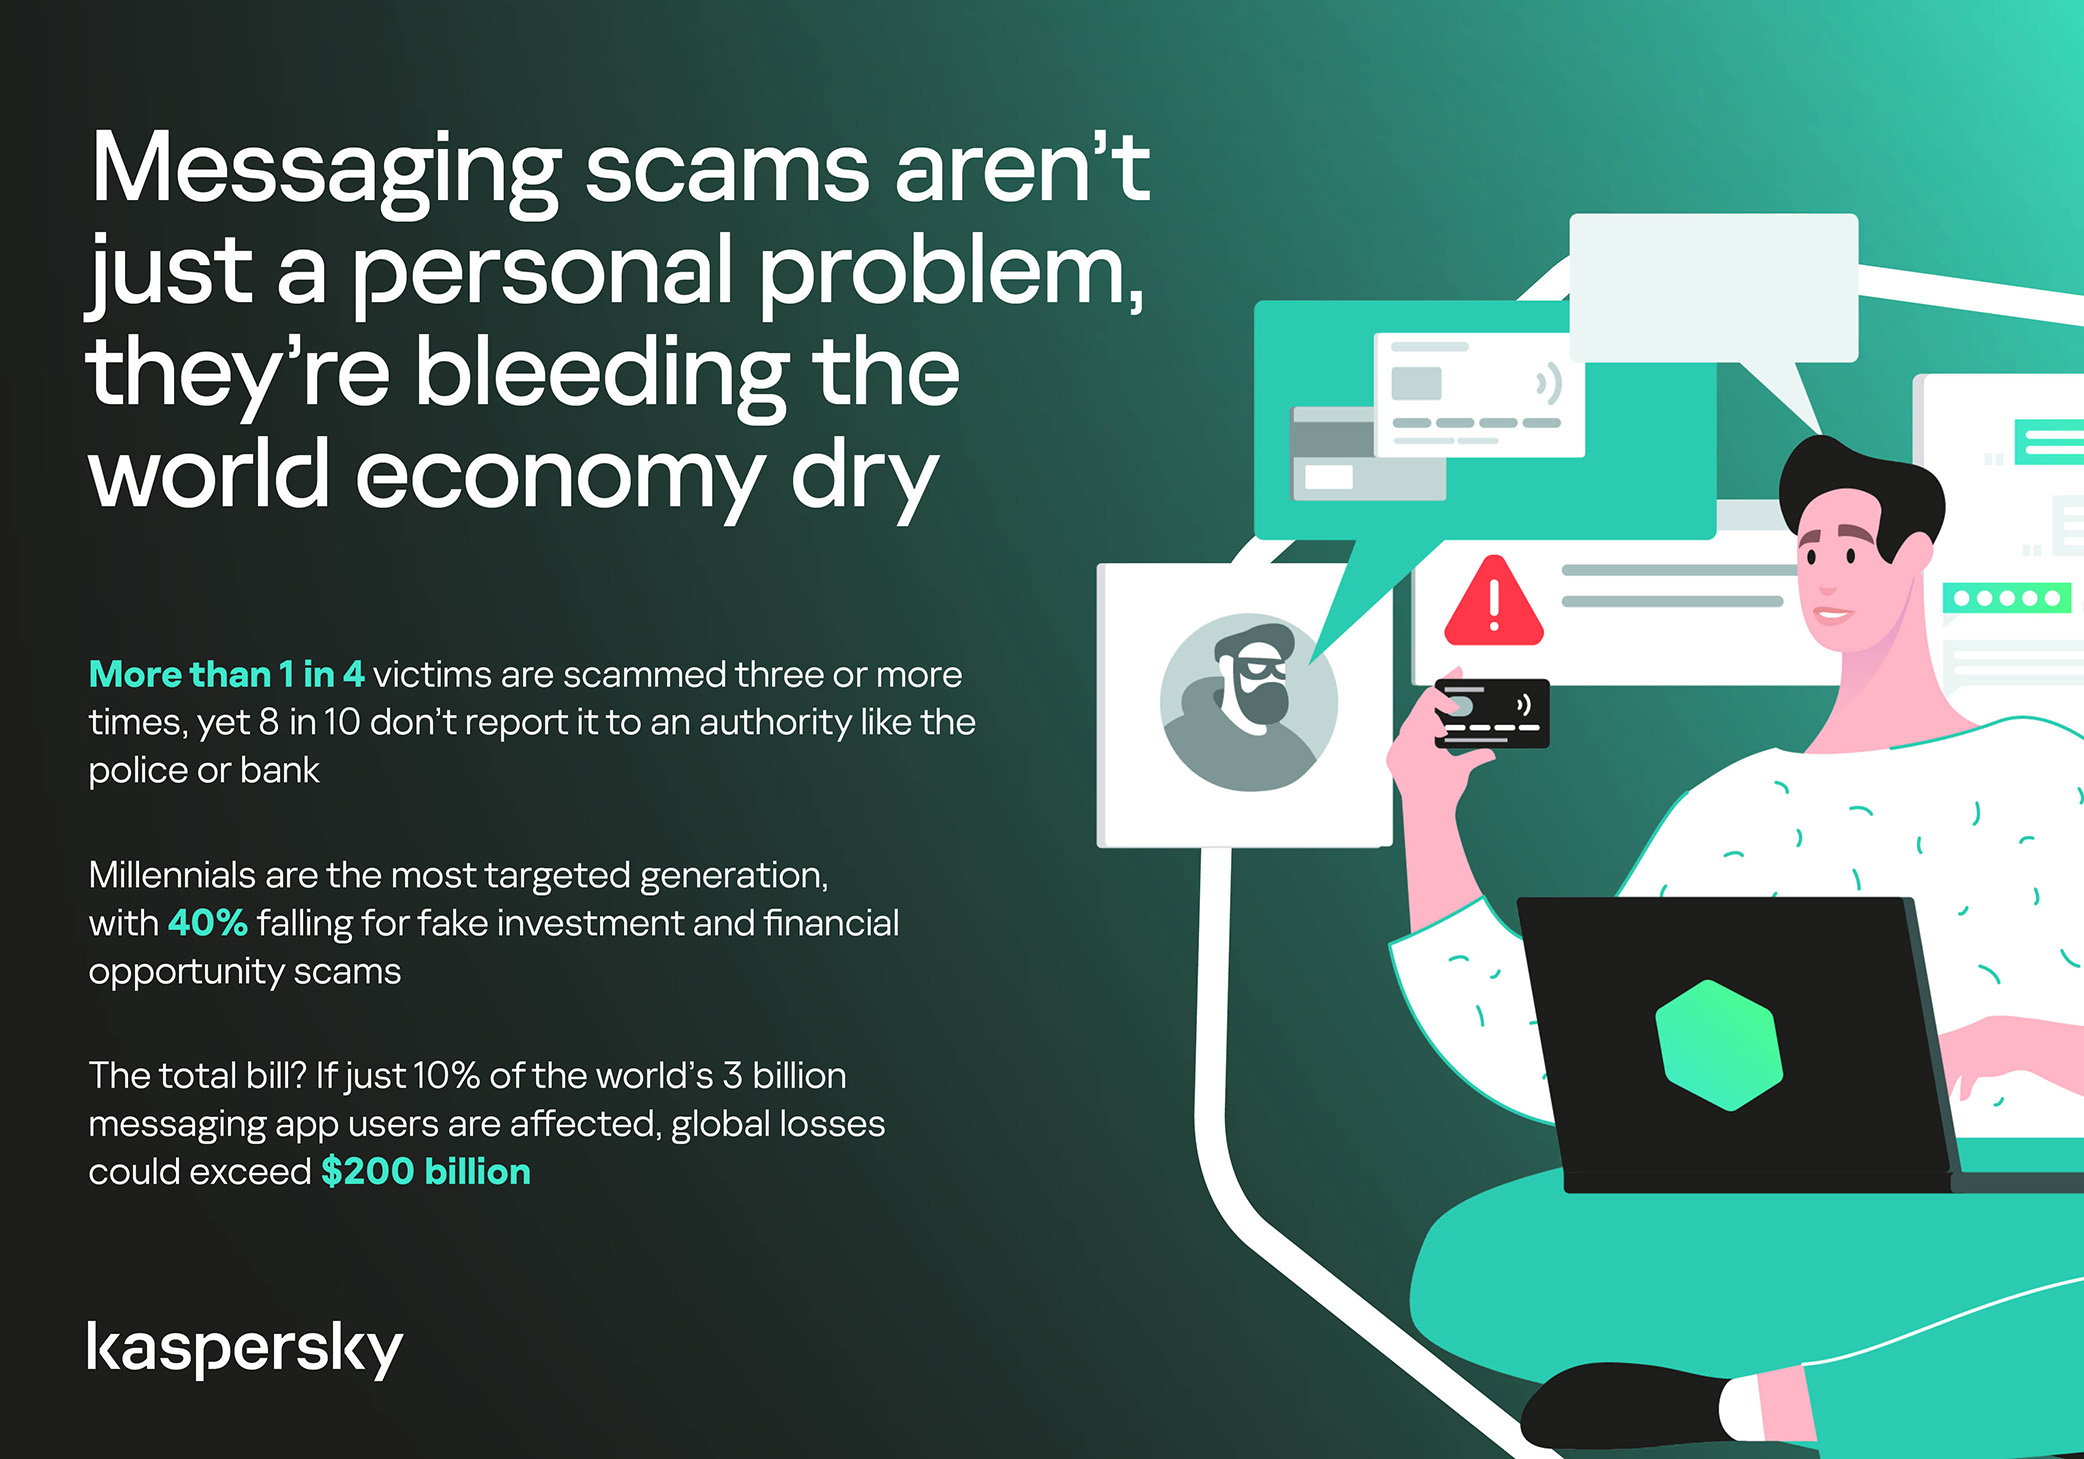
In 11% of cases, losses exceed $1,350, and more than a quarter of victims (28%) report having been scammed three or more times in the past six months. Once scammers discover that a phone number responds, that contact becomes an asset, circulating from one database to another.

Now imagine the scale of the problem: if just 10% of the three billion messaging‑app users worldwide fell victim with the average loss, the total damage would amount to… nearly $220 billion! This is comparable to the GDP of Greece, and exceeds that of Morocco, Serbia, or Côte d’Ivoire.

It becomes clear that behind the daily flood of fraudulent schemes lie large scam cartels operating on an industrial scale, using AI to personalize messages that mimic those of family members, friends, and familiar brands. This, in essence, forms the basis of a full-fledged economy built on digital identity theft.

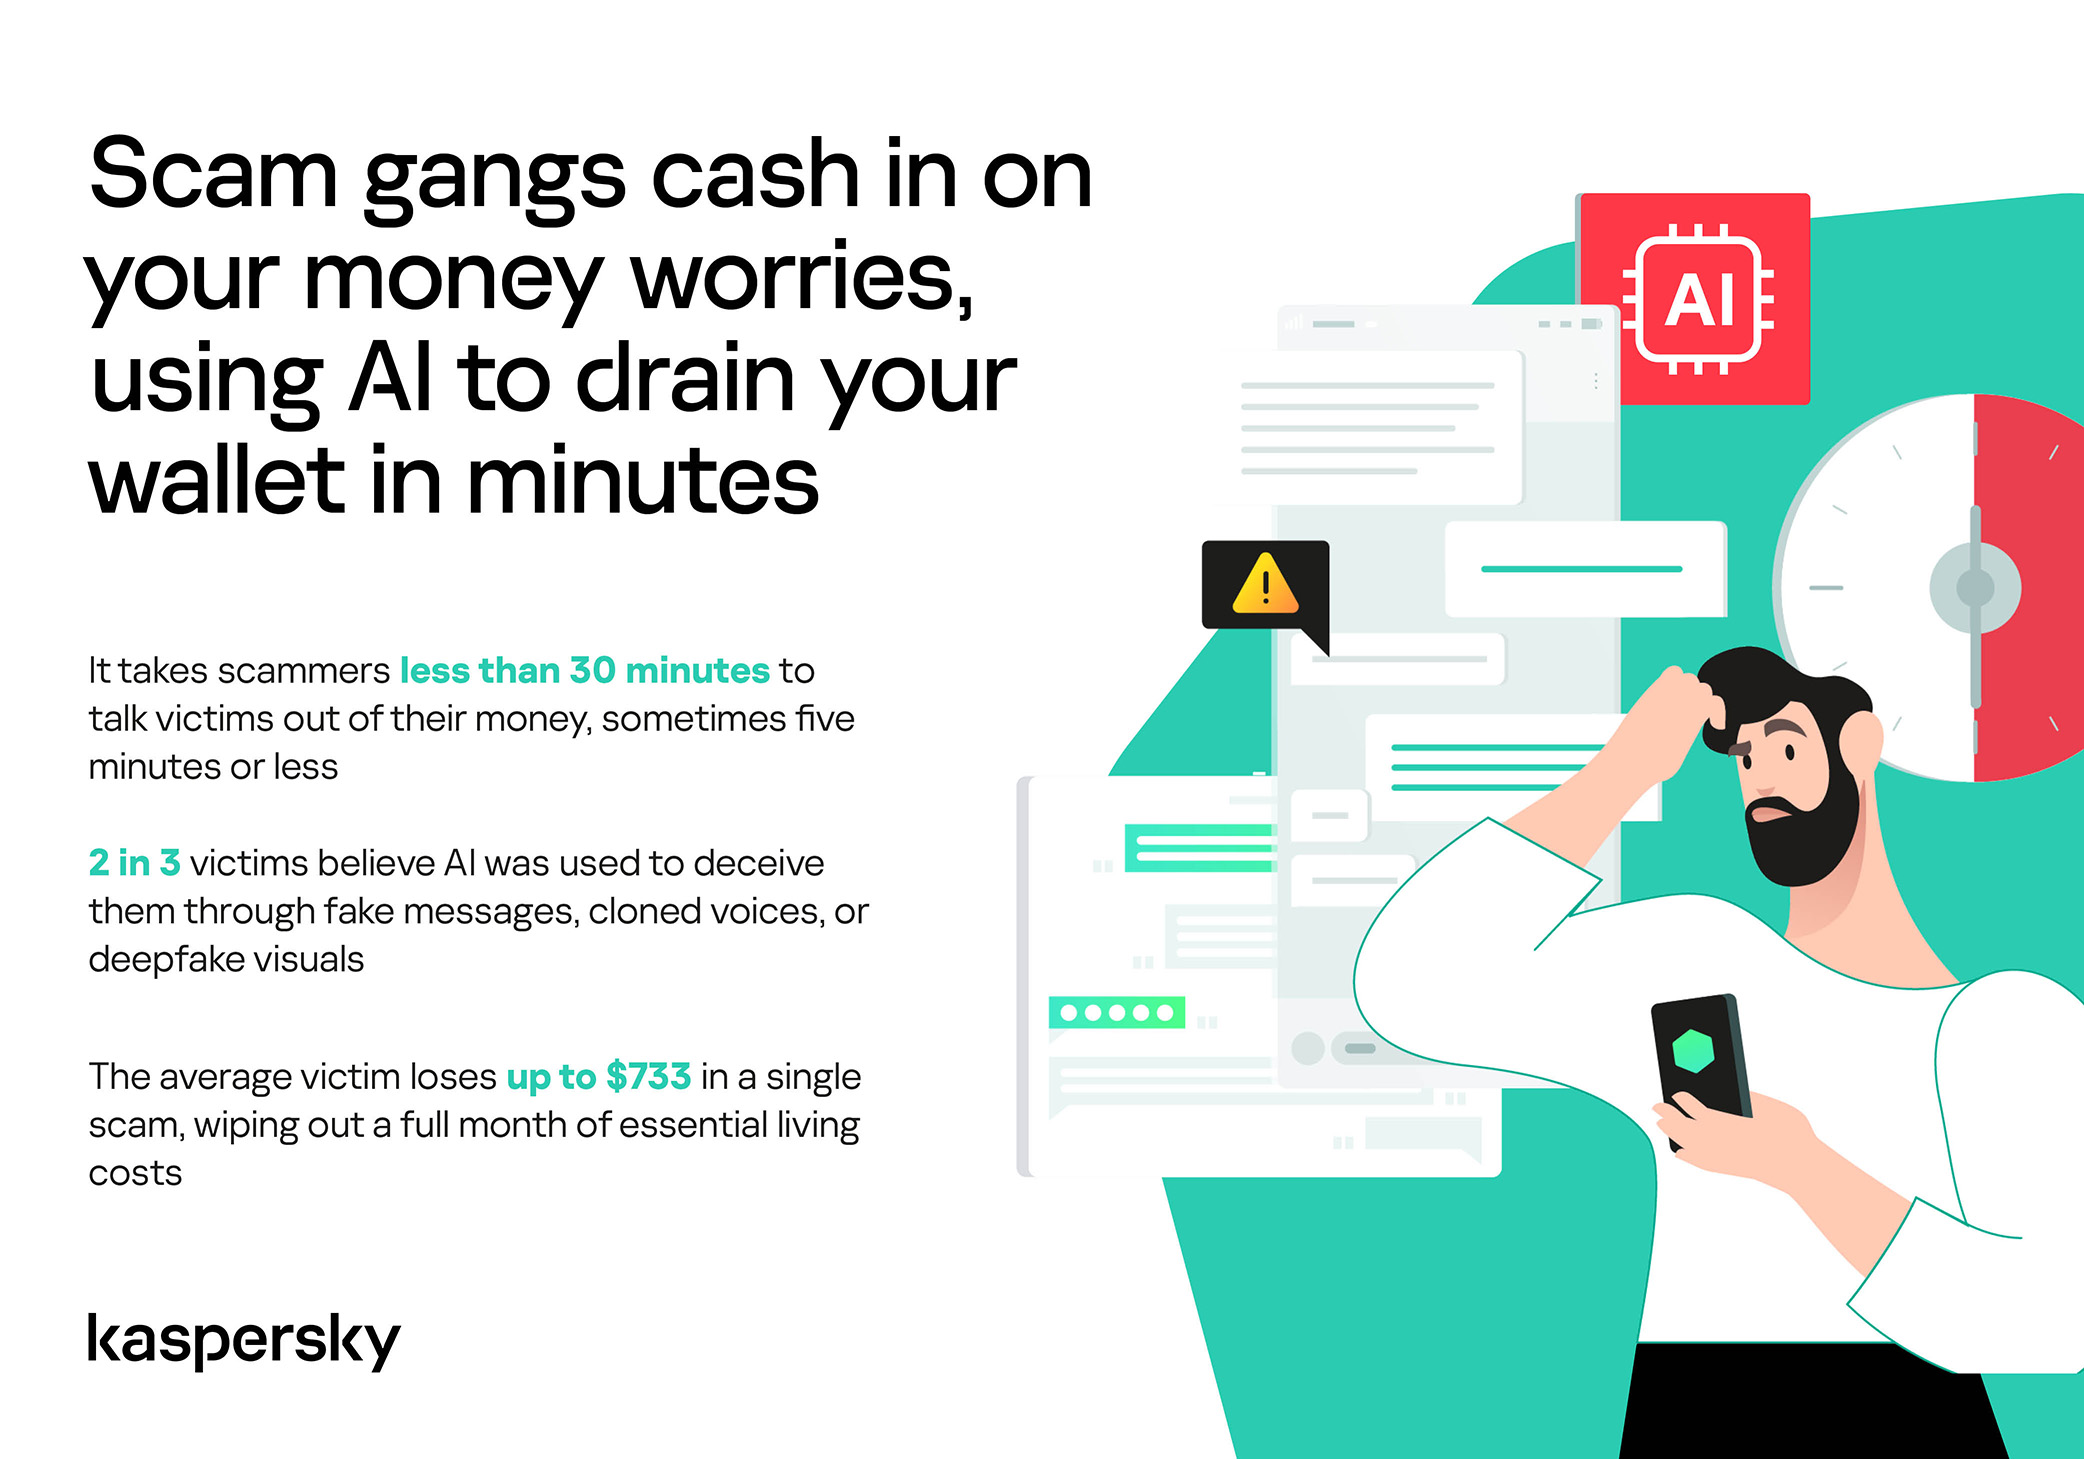
Scam gangs cash in on your money worries, using AI to drain your wallet in minutes

Speed beats scrutiny

More than half of successful messaging scams (52%) unfold in under 30 minutes — from first contact to the moment money or personal data changes hands — or even faster, before the victim begins to doubt the legitimacy of the sender. In fact, one in seven scams takes less than five minutes — quicker than boiling an egg!

The speed isn’t accidental. It’s the method. Scammers structure their schemes to deny the victim a chance to come to their senses. Every element is engineered to compress the decision-making window: the urgency of the scenario, the familiarity of the format, the plausibility of the request.

They rush you — faster, faster, don’t tell anyone, you only have a few minutes, solve the problem, don’t ask questions. Click the link, fill in the details, approve the transaction, or else… Or else what? The scammers’ imagination knows no bounds here, but if you don’t do something right now, you’ll definitely regret it.

Alas, the realization of what has happened usually comes when the damage is already irreversible. More than half of victims (51%) lose money; another 43% hand over their personal data — most commonly phone numbers, names, and email addresses — to scammers, and often the victim loses both.

Where and how attacks occur

A delivery notification, a bank alert, a message from a merchant you ordered from last week — messaging apps permeate every aspect of everyday life, making such interactions completely normal. An attack shouldn’t feel like an attack. It should feel like the same message you’ve received hundreds of times.

It’s no surprise that scammers focus their attention on this method of communication first and foremost. The most popular platforms for scams are predictable: WhatsApp (43%), SMS/iMessage (40%), Facebook (27%), Telegram (22%), and Instagram (19%) — these are the ones that people trust most.

A wide variety of schemes is used. Brand impersonation is now one of the three most common types of messaging scam worldwide — accounting for 31% of cases. Fake delivery notifications top the list at 38%, followed by investment scams at 37%.

At the same time, nearly two-thirds (63%) of fraudulent schemes span multiple platforms, moving from SMS to WhatsApp, from WhatsApp to Telegram, etc. In this way, scammers achieve two goals: they mimic organic messaging and evade moderation algorithms.

AI has taken scams to a new level

Just a couple of years ago, fraudulent messages gave themselves away with bad grammar, awkward phrasing, illogical requests, and an obsessive sense of urgency. Today, a phishing message looks, sounds, and reads just like the real thing.

Scam cartels want to catch people in motion — between meetings, on a commute, or during everyday tasks — when your attention is already fragmented. They mimic your mother’s turn of phrase. They match your bank’s tone of voice. They copy your courier’s format exactly. They mirror the rhythm, structure, and style of authentic brand communications across messaging platforms. And AI is accelerating all of it.

What this creates is overlap. Legitimate and fraudulent messages appear in the same environment, using the same formats, language, and triggers. The difference between them is no longer obvious.

The data shows that two-thirds of victims (66%) believe AI was used in the scam against them, 42% cite messages written by AI, 31% report generated or cloned voices, and 25% encountered deepfake images or videos.

That’s why mere awareness and “tech-savviness” may no longer be enough to protect oneself. From Gen Z to Gen X, messaging scams cut across every generation.

And what about the emotional toll?

But money is far from the only problem a victim is left with after an attack. After what they’ve been through, people develop distrust toward incoming messages, unfamiliar numbers, and any requests for action. As a result, 99% of fraud victims say they no longer trust incoming notifications in messaging apps.

This creates a crisis of trust in all digital channels in general. Every legitimate message can now be perceived as a scam. Brands, banks, and delivery services are forced to operate in an environment where the customer is, by default, in a state of distrust.

Dr. Elizabeth Carter, a forensic linguist and criminologist at Kingston University in London, notes that scammers use familiar contexts, common social settings and embedded linguistic norms to create the illusion for the victim that their decision-making is rational and reasonable in the moment. However, what is actually happening is that they construct false realities in which those decisions end up causing financial and psychological harm. She also notes that it is very hard to identify a false reality while you are in it.

After realizing they had been deceived, more than half of victims felt anger — the kind that comes from having trusted something and discovering it was used against you. 42% of victims report frustration, 38% — feeling upset. Moreover, several months later, these feelings haven’t gone away: nearly half of all victims (48%) are still angry, a third (33%) remain frustrated, and 30% are upset.

And nearly one in 10 victims don’t tell anyone what happened. They feel shame, a sense of having fallen for something so obvious. This leaves a significant portion of the actual damage unreported: only 24% of victims contact the police, and only 23% report it to their bank.

Messaging scams aren't just a personal problem, they're bleeding the world economy dry

So what can be done?

The crisis of trust — and even a touch of paranoia — that has arisen due to widespread attacks on users can linger in victims’ minds for a long time, affecting their quality of life. To prevent this, follow these guidelines:

  • Pause before you act. The sense of urgency you feel is almost always artificial. A legitimate bank, retailer, or delivery service won’t penalize you for taking 30 seconds to verify before clicking a link or confirming details. It’s precisely this instinct to resolve the situation quickly that scammers are counting on.
  • Verify through another channel. If a message appears to be from a relative, colleague, or company you trust — contact them through another channel before taking any action. Use secure verification methods, and cross-check identities when something doesn’t feel right. For families, agreeing on a “safe word” in advance can defeat even the most convincing voice clones.
  • Use a password manager. It will not only help you generate strong, unique passwords for all your accounts and store them securely, syncing them across all your devices, but also protect you from spoofed sites. Even if you click a phishing link and land on such a site, our password manager will notify you about the domain mismatch and refuse to autofill your username and password.
  • Use protection that works in real time. Modern security solutions, such as Kaspersky Premium, provide real-time protection against malicious links and phishing attempts in the apps and websites you use every day. On Android devices, a dedicated layer of anti-phishing security scans and neutralizes suspicious links as they appear, even within notifications, before you even have a chance to click them.

We’ve covered other threats in messaging apps in similar articles:

❌