Security teams have more vulnerability data at their disposal than ever. But even the best intelligence has limited value if teams can’t determine where those vulnerabilities exist within their own environment.
For many organizations, that visibility remains a challenge. Asset inventories, scanners, and ticketing systems provide valuable information, but connecting those insights with real-world exploit activity isn’t always straightforward. And as environments evolve, undocumented assets, forgotten infrastructure, and newly exposed systems can introduce risks that traditional inventories may miss.
Flashpoint External Attack Surface Management (EASM) helps close that gap by connecting continuous discovery of internet-facing assets with Flashpoint’s threat-informed Vulnerability Intelligence. With coverage of more than 480,000 vulnerabilities, including over 105,000 not found in NVD or CVE, Flashpoint provides context on active exploitation, exploit maturity, and ransomware risk through its patented Ransomware Risk model. Together, these capabilities help teams identify which exposures warrant the most immediate attention.
What is EASM? External Attack Surface Management (EASM) is the continuous discovery and monitoring of an organization’s internet-facing assets, including domains, subdomains, IPs, and infrastructure that isn’t formally tracked. It gives security teams visibility into what’s exposed to the internet, whether or not that infrastructure was deliberately set up or documented.
How EASM Extends Vulnerability Prioritization to Your Full Environment
EASM continuously discovers internet-facing assets associated with an organization, including domains, subdomains, IP addresses, and infrastructure that may not appear in existing inventories. This could include a subsidiary’s infrastructure following an acquisition, a forgotten staging environment, or a cloud instance that remains active long after a project ends.
With Flashpoint EASM, discovered assets enter a triage queue organized by relevance, helping teams focus on assets that warrant further investigation. Once ownership is confirmed, Flashpoint maps those assets against its Vulnerability Intelligence to identify vulnerabilities associated with the software versions running on them.
Findings are prioritized using Flashpoint KEV, EPSS, and Ransomware Risk scores. Asset-level details also show the products and versions responsible for identified exposures, along with potentially high-risk open ports such as RDP and SSH. This gives teams the context they need to assess risk and determine where remediation should begin.
Example Scenario
Consider a development team that deploys a staging server running an outdated web framework. The project ends, but the server remains online and is never added to the organization’s asset inventory.
Flashpoint EASM discovers the server and shows how it connects to the organization’s infrastructure. Once the team confirms ownership, Flashpoint Vulnerability Intelligence identifies an actively exploited CVE affecting the framework version.
The team can now investigate an exposure that might otherwise have gone unnoticed and prioritize remediation based on evidence of active exploitation.
Why This Matters More in Regulated Industries
For organizations in heavily regulated industries such as financial services and healthcare, incomplete asset visibility can introduce additional compliance and security risks. Requirements under frameworks and regulations such as GLBA and HIPAA make maintaining appropriate safeguards especially important. An unknown, internet-facing asset with an exploitable vulnerability can create exposure regardless of whether it appears in the organization’s CMDB.
Mergers and acquisitions can complicate this further. Acquired organizations bring infrastructure that security teams may have limited visibility into, including assets that have not yet been incorporated into existing monitoring processes.
Continuous external asset discovery helps teams identify and assess that infrastructure earlier, reducing reliance on periodic audits or manual inventory updates to uncover potential exposures.
Discovery and Prioritization, Built Into One Platform
When attack surface discovery and vulnerability intelligence operate in separate systems, security teams may need to manually correlate asset inventories with vulnerability findings. That process becomes increasingly difficult as infrastructure changes and new vulnerabilities emerge.
Flashpoint brings these capabilities together in one platform, an approach we call attack surface intelligence. Newly discovered assets can be evaluated against Flashpoint’s Vulnerability Intelligence, giving teams access to threat-informed prioritization within the same workflow.
For teams already using Flashpoint Vulnerability Intelligence, EASM can be added as a module within the existing Ignite platform, with no separate console to manage. Contact your account team to learn more about adding EASM to your deployment. New to Flashpoint? Schedule a demo to explore how Vulnerability Intelligence and EASM work together to help your team identify and prioritize external exposures.
Frequently Asked Questions
How is EASM different from a vulnerability scanner?
Traditional vulnerability scanners scan assets you already know about and tell them to check, typically from inside the network perimeter. EASM continuously discovers internet-facing assets from the outside, including unknown infrastructure like forgotten test environments and acquired systems, then enriches them with vulnerability intelligence beyond public sources like NVD and CVE. The two are complementary: scanners provide depth on known internal assets, while EASM extends that visibility to what’s exposed externally.
Can EASM help identify compound risk on a single asset?
Yes. The Vulnerable Assets view surfaces how many vulnerabilities are tied to a given asset, so teams can quickly spot assets carrying disproportionate risk and prioritize accordingly, rather than treating every finding as an isolated issue.
If we’re already running Flashpoint Vulnerability Intelligence, do we need a new implementation to add EASM?
No. EASM is a module inside the platform you’re already using. It appears inside the same Ignite workflows your team relies on today, with no separate console or parallel rollout required.
How is EASM priced?
EASM is priced based on company size rather than asset count or seats, so costs are predictable and don’t scale up just because the attack surface grows.
Vulnerability and exposure management (VM) teams need critical metadata and context that clearly show which issues pose an immediate risk to their organization. While traditional VM frameworks tell defenders how severe a vulnerability may be, they do not provide visibility into how likely threat actors are to exploit it. This leaves security teams overwhelmed in patch backlogs without a clear strategy for prioritization.
Nowhere is this prioritization gap more dangerous than with ransomware. Ransomware-as-a-Service (RaaS) groups no longer choose targets at random. They look for specific technical conditions that make vulnerability exploitation easy, fast, and repeatable. With RaaS attacks rising by 45% period-over-period in H1 2026, organizations need a way to identify the specific traits that make a vulnerability attractive to ransomware operators before an attack occurs.
Flashpoint built the Ransomware Risk score into Flashpoint Vulnerability Intelligence to solve exactly this problem. Since 2022, it has rated newly discovered vulnerabilities based on how closely they resemble those known to be used in ransomware attacks. With the grant of the U.S. Patent No. 12,705,360 on August 11, 2026, the methodology behind the score is now formally patented. This milestone formalizes Flashpoint’s ability to cut through the noise with a proven, threat-informed signal that gives defenders the clarity they need to act on Day Zero.
“As vulnerability disclosures surge, prioritization is more important than ever for security teams. A severity score alone can’t tell you which vulnerabilities pose the greatest real-world risk of exploitation by ransomware actors.
Our patented Ransomware Risk model applies years of threat intelligence to that problem, giving customers an earlier signal and helping them prioritize based on how attackers actually operate.”
josh lefkowitz, co-founder and ceo at flashpoint
Under the Hood: How Flashpoint’s Patented Ransomware Vulnerability Model Works
The patented system evaluates newly disclosed vulnerabilities against the patterns shared by vulnerabilities ransomware groups have exploited. Rather than trying to predict what threat actors will do next, the model learns what past ransomware-exploited vulnerabilities have in common and compares each new flaw against those patterns.
The Four Step Process
Multi-Factor Fingerprinting
Every vulnerability ingested into Flashpoint Vulnerability Intelligence is profiled against more than 60 distinct technical factors. This “fingerprinting” links the vulnerability to key inputs including whether the flaw is remotely exploitable without authentication, whether it affects SCADA or Operational Technology (OT) systems, and its potential impact on data availability, which is central to extortion schemes.
Coordinate Mapping
The model turns each multi-factor fingerprint into a set of values that place it as a single point on a map, so vulnerabilities with similar profiles land close together.
Identifying the Ransomware Neighborhood (Cluster Check)
Flashpoint overlays historical threat data onto the map to establish neighborhoods where vulnerabilities previously exploited in real-world ransomware attacks aggregate.
Similarity and Likelihood Rating
When a new vulnerability is ingested, its coordinates are checked against these neighborhoods. The scoring system calculates its spatial proximity to known ransomware vectors and assigns a clear rating: Low, Medium, High, or Critical.
This four-step method, developed by Flashpoint’s Ben Haynes and Jacob Kouns, is the basis of U.S. Patent No. 12,705,360.
What It Means for Vulnerability Management Teams
By translating complex structural attributes into a single risk score, the patented model delivers four key operational advantages:
Prioritize Beyond CVSS: Leveraging the Ransomware Risk model, security teams can confidently prioritize 1.0 to 6.9 CVSS issues if its structural profile lands it in a “High” or “Critical” ransomware cluster.
Act on Day Zero: Because the Flashpoint model rates all vulnerabilities on disclosure, security teams gain actionable guidance immediately, eliminating the need to wait weeks for external exploitation reports.
Effectively Communicate Risk: CISOs can present clear, business-centric risk statements rather than abstract numerical scores.
Adaptive Ratings: Scores update in near real time as vulnerability details change, and the model keeps adjusting as new vulnerabilities join the set it compares against.
Flashpoint’s Ransomware Risk model is built to enhance, not replace the vulnerability management frameworks organizations already rely on. In fact, it provides even greater value for security teams as our Ransomware Risk model provides clarity for every vulnerability detailed by Flashpoint Vulnerability Intelligence, including over 105,000 issues missed by CVE and NVD.
Within Flashpoint Ignite, security teams have a complete view of vulnerability risk, seeing the score alongside CVSS (v3 and v4), EPSS, Social Risk, and exploit maturity.
Patented Ransomware Risk Score sits beside CVSS and EPSS on every vulnerability record in Flashpoint Ignite
Protect Against Vulnerability and Ransomware Risk Using Flashpoint
Vulnerability management requires more than cataloging. It demands threat-informed prioritization that aligns security operations with real-world business risk. Flashpoint’s patented Ransomware Risk model eliminates guesswork by surfacing the flaws that match the profile of known ransomware targets, allowing security teams to patch what matters most, first.
By combining proprietary knowledge of vulnerability architecture and ransomware attacks, Flashpoint bridges the gap between theoretical and active exposure. Request a demo today to see how our Ransomware Risk model provides the definitive signal needed to stay ahead of extortion groups.
Ransomware Risk FAQs (Frequently Asked Questions)
What is the Ransomware Risk score?
The Ransomware Risk score is a rating in Flashpoint Vulnerability Intelligence that shows how closely a vulnerability resembles those known to be used in ransomware attacks. Each vulnerability is rated Low, Medium, High, or Critical, so security teams can see which ones to patch first to reduce their ransomware exposure.
How is Ransomware Risk different from CVSS and EPSS?
CVSS measures how severe a vulnerability could be, and EPSS estimates how likely it is to be exploited in general. Ransomware Risk adds a ransomware-specific signal that works alongside both, showing how closely a vulnerability matches those ransomware groups have used. In Flashpoint Ignite, all three scores appear together.
What does Flashpoint’s ransomware patent cover?
U.S. Patent No. 12,705,360, granted August 11, 2026, covers Flashpoint’s method for rating how likely a vulnerability is to be used in a ransomware event. Each vulnerability is profiled on more than 60 factors, compared with vulnerabilities used in past ransomware attacks, and rated by similarity. The patent formalizes the model behind the Ransomware Risk score, live since 2022.
How often are Ransomware Risk scores updated?
Ransomware Risk scores update in near real time, so new vulnerabilities are rated as soon as they’re disclosed. The model also keeps adjusting as new vulnerabilities join the body it compares against, so ratings reflect the ransomware landscape as it stands today.
Cybercrime at Machine Speed: Key Takeaways from Flashpoint’s 2026 Midyear Threat Intelligence Briefing
Threat actors are no longer just using automation to execute tasks, they are leveraging prepackaged, safeguard-free AI, weaponizing stolen session data, and directly targeting defenders’ security stacks.
The threat landscape has developed at a striking pace with Flashpoint tracking over 22 million illicit AI discussions, 7.4 million compromised hosts yielding 1.7 billion stolen credentials, and over 21,600 disclosed vulnerabilities in just six months. Beyond these staggering numbers, the on-demand session detailed something even more alarming: a fundamental shift in adversary operational tradecraft.
Here are the five critical shifts every cyber threat intelligence (CTI), Vulnerability Management, and SOC team needs to know.
The Death of Signal: Threat Actors are Shifting to “Private AI”
The public discussion surrounding criminal artificial intelligence (AI) has reached a critical inflection point. Early in the AI boom, Flashpoint observed threat actors collaboratively experiment across underground forums, jailbreaking commercial frontier models or advertising surface-level tools like WormGPT and DarkGPT.
Today, adversaries are shifting from public forums to running fine-tuned, open-source models locally on private servers, which greatly hampers traditional signature-based detection. Flashpoint analysts are now seeing attackers generate unique, highly tailored malware variants, flawless phishing lures, and custom exploit scripts at extremely low costs—completely offline and shielded from public monitoring.
“A few months ago, a lot of this was collaborative… public outsourcing. Now what we’re seeing is scarier: pre-packaged cybercrime models run locally on private infrastructure. Malicious code, exploit scripts, and targeted phishing are all being generated inside closed environments.”
Ian Gray, VP of Intelligence, Flashpoint
Weaponizing the Defender’s Own Tooling
Another eye-opening tactical insight shared during the session was how threat actors are repurposing defender infrastructure for automated initial access and extortion. In the webinar, we pointed to recent campaigns where adversaries specifically targeted misconfigurations and zero-day vulnerabilities inside open-source vulnerability scanners, secrets-detection tools, Kubernetes clusters, and Infrastructure-as-Code(IaC) environments.
What this means for defenders is that the attack surface is no longer bounded by traditional enterprise network boundaries: it extends directly into CI/CD pipelines, security orchestration tooling, and third-party SaaS integrations. Security teams are finding themselves in a race against attackers who use automated scanning scripts to weaponize vulnerabilities in the security tools themselves.
The Global Infostealer Threat and Identity-First Attacks
Flashpoint tracked 7.4 million hosts compromised by infostealers in H1 2026—a 27% increase period-over-period—harvesting 1.7 billion credentials and identity information.
While the top infostealer strains remain familiar, law enforcement operations have created vacuums that competitors rapidly fill.
Threat actors are leveraging drive-by downloads, watering holes, and pirated software packages to plant stealers. Once a machine is compromised, the logs capture corporate SSO credentials, active browser cookies, VPN keys, and SaaS session tokens. This enables adversaries to simply log in without having to leverage complex technical exploits.
The Structural Failure of CVE/NVD and the Importance of KEV
The Common Vulnerabilities and Exposures (CVE) and National Vulnerability Database (NVD) have failed to keep pace with the velocity of AI-assisted vulnerability discovery. As such, vulnerability management teams are facing significant operational delays.
Metric
Flashpoint GTIR Midyear H1 2026 Data
Operational Impact
Total Disclosures
21,667
Remediation volume exceeds defender bandwidth.
Exploit Availability
19% (4,015 CVEs)
Functional code is ready before patches are deployed.
Public Catalog Lag
Growing Backlog (NVD/KEV)
Delay in official scoring leaves teams blind to active risk.
Therefore, waiting for NVD enrichment before prioritizing a patch is a dangerous strategy. To compensate, security teams require Vulnerability Intelligence (VI) that provides primary-source confirmation of weaponization, exploit availability, and actionable mitigation guidance long before public databases update.
Ransomware Evolution: From Encryption to Cloud Extortion
Ransomware-as-a-Service (RaaS) activity surged by 45% period-over-period, reaching 6,256 verified victim postings on data leak sites. However, total on-chain payout revenue dropped by 8% to $820 million, with victim pay-rates hitting a record low of 28%.
Faced with declining payouts and resilient enterprise backups, extortion syndicates are adapting. Rather than relying exclusively on technical file-encrypting malware, groups are executing pure data extortion campaigns—frequently targeting cloud platforms or extracting data through third-party vendor access.
Protect Your Organization Using Flashpoint
Defending against machine-speed attacks requires moving beyond reactive, post-incident telemetry. Flashpoint arms security, CTI, and vulnerability management teams with the primary-source intelligence required to preempt adversary operations:
Unrivaled Deep & Dark Web Visibility: Flashpoint’s Primary Source Collection actively monitors closed criminal communities, illicit Telegram channels, and private forums, giving you early warning when threat actors build custom AI toolkits or trade credentials targeting your organization.
Comprehensive Vulnerability Intelligence (VI): Flashpoint tracks zero-days and vulnerability disclosures independently, delivering immediate exploit availability data and threat-informed prioritization so you patch what actually matters.
Continuous Compromised Credential Monitoring: Instantly surface exposed enterprise credentials, active session tokens, and stealer logs tied to your domain or third-party supply chain before they lead to an account takeover (ATO).
In the first half of 2026, the global threat landscape reached a clear operational inflection point: threat operations have fundamentally transitioned from human-led campaigns to machine-speed, AI-driven exploitation. As threat actors gain commoditized access to open-source AI technologies and actively deploy automated, safeguard-free tooling locally on private infrastructure, organizations face an accelerating hybrid risk environment.
Flashpoint’s Global Threat Intelligence Report: 2026 Midyear Edition
The Flashpoint Global Threat Intelligence Report: 2026 Midyear Edition anchors security leaders—from threat intelligence, vulnerability management, to executive leadership—in the data required to navigate this evolving threat landscape. Covering the period from January 1 to June 30, 2026, the report delivers timely insights backed by Flashpoint’s proprietary primary-source collection from over 3.9 petabytes of continuously monitored illicit sources.
Our midyear findings reveal several key metrics that highlight the speed and scale of the H1 2026 threat landscape:
22M+ threat actor posts discussed, shared, or advertised artificial intelligence toolkits for criminal deployment.
1.7B credentials and identity data points extracted across more than 7.4M unique compromised hosts globally.
Nearly one-in-five (19%) of all vulnerability disclosures dropped with ready-made, functional exploit code.
45% period-over-period surge in Ransomware-as-a-Service (RaaS), with total victim volume reaching 6,256 even as victim payout rates dropped to a historic low of 28%.
A Clear Understanding of the Convergence Between AI and Cyber Threats From generating flawless phishing campaigns to automating vulnerability scanning and code obfuscation, discover how adversaries are optimizing for speed and cost-efficiency — utilizing AI as a force multiplier in their various illicit campaigns.
A Comprehensive Top-Down View of the Evolving Threat Landscape Gain full visibility of the threat landscape with Flashpoint’s primary-source collections and real-time threat intelligence.
Strategies for Proactive Defense and Risk Mitigation Move your organization beyond reactive incident response by leveraging Flashpoint’s comprehensive threat intelligence. Gain the foresight needed to strengthen defenses and optimize your security posture.
“AI is compressing the time between opportunity and exploitation. Capabilities that once took significant expertise, coordination, and time to develop are becoming faster to build, easier to scale, and harder to detect. Security teams are facing an adversary ecosystem that can use AI to iterate at unprecedented speed — the only way to keep pace is with primary-source intelligence that surfaces adversary behavior before attacks unfold.”
Josh Lefkowitz, Flashpoint Co-Founder & CEO
The Four Driving Themes Shaping the 2026 Threat Landscape
Artificial Intelligence (AI) Threats
During the first half of 2026, Flashpoint captured over 22M illicit posts discussing or advertising AI for criminal-related activities. By stripping ethical safeguards, custom malicious LLMs allow unsophisticated threat actors to automate complex phases of the attack lifecycle, including target profiling, malware evasion script creation, and zero-day exploit generation.
Information-Stealing Malware Threats
Infostealer malware harvested 1.7 billion credentials across 7.4 million compromised systems in H1 2026 alone, turning digital identity into the main entry point for enterprise intrusions.
Vulnerability Intelligence and Patching Management
19% (4,015) of all H1 2026 vulnerability disclosures arrived with ready-made exploit code. Adversaries deploy automated replication scripts almost immediately upon disclosure, eliminating manual remediation windows.
Ransomware Operations, Multi-Extortion Cartels, and Financial Risk
Despite a 45% surge in victim volume (6,256 overall), total on-chain revenue fell by 8% to $820M. Improved enterprise backups and incident response have driven payout rates down to 28%, prompting syndicates to demand larger sums from paying victims.
Proactive Security in 2026 and Beyond
The data shows that traditional enterprise security organizations are struggling to keep pace with modern threat cycles that are accelerated by illicit uses of AI. This continued convergence of AI engines and initial access vectors have further compressed attack timelines, making it nearly impossible for security teams to defend against them—especially if they are limited by traditional approaches to threat intelligence.
Equipping your team with primary-source threat intelligence is critical for protecting critical assets in 2026. Download the Flashpoint Global Threat Intelligence Report: 2026 Midyear Edition to gain the visibility and strategic clarity required to defend your organization.
The number of vulnerabilities detected in code continues to rise. According to Kaspersky’s threat analysis, 5,200 critical vulnerabilities were found in the first half of this year alone — nearly 50% more than during the same period last year. At the same time, the average gap between the publication of information about a vulnerability and the first attempts to exploit it is shrinking. The rapid development of AI systems plays a significant role in this process: while helping companies find weaknesses in their code, AI simultaneously shows hackers how to exploit them quicker.
It would seem that solving the problem of security gaps is very easy. All you need do is set up a scanner, check the infrastructure more often, and update vulnerable systems. But statistics from the Kaspersky Incident Response service show the opposite: a significant number of cyberattacks begin precisely by exploiting a flaw — and these are often already known flaws, not zero-day vulnerabilities.
Using a scanner does not give you an effective vulnerability management process. A scanner merely finds flaws (not always promptly), and then the IT team is tasked with prioritizing and fixing them. These processes can drag on for weeks, and in the meantime an attacker can easily gain access to the given infrastructure.
Where time is lost
The first delay can occur immediately after information about a vulnerability appears in databases. In addition to monitoring for breaches, the information security team is normally handling a dozen-or-so other tasks, so it relies entirely on the scanner for monitoring. If the scanner is configured to run weekly, a new vulnerability will appear in the report in a few days. In a company where scans are conducted quarterly, this obviously happens much later. Attackers, on the other hand, actively monitor news feeds and learn about new vulnerabilities immediately.
When the report finally reaches the security team, it contains far more than just one issue, raising the question of where to start. Critical vulnerabilities are addressed first, but attackers might exploit more than just those. Meanwhile, prioritization decisions are rarely based on data: often, they’re based on the order of the errors in the report, the name of the vulnerable system (they start with the one everyone’s talking about), or increased activity from its owner. Because of this, the risk of overlooking a serious threat is very high. Finally, the IT department takes on the vulnerability, and… it ends up back in the queue: they need to check the update’s compatibility and wait for a maintenance window.
After installing the update, the specialists close the ticket with a clear conscience and mark the status as completed. But would anyone verify that the patch was applied to all affected machines? Even the one that was turned off at the time of installation? Probably not, and then the company would assume the vulnerability was fixed, even though it’ll actually remain in the infrastructure for an indefinite period. This is the worst possible outcome: the risk remains — yet it’s no longer visible.
Put it all together, and what we get is months passing between disclosure and actual resolution. There’s no one in particular to blame here: every participant in the chain did what they’re supposed to. It’s just that this chain itself is made up of links with gaps between them.
A recipe for vulnerability management
To give attackers as few opportunities to gain access to corporate infrastructure as possible, it’s important to ensure that an organization has four key processes clearly established:
1. Inventory
It’s impossible to verify the security of a system that no one knows exists. At the same time, virtually any large infrastructure will contain things like having had a server set up “for a week” three years ago, a network device left over from previous business owners, or a workstation that was forgotten during an office move. And each of these assets can pose a serious threat.
The goal of inventory management is to ensure complete transparency of the IT infrastructure. To achieve this, an up-to-date list of assets is compiled.
2. Prioritization
When analyzing vulnerabilities, a security specialist shouldn’t rely solely on ratings from public databases such as the NVD, for these don’t always rely the real severity of the actual potential damage caused by exploiting a vulnerability. The specific structure of an organization’s infrastructure will have a significant impact. For example, the same vulnerability in a server located in an isolated segment, and in a system accessible from the internet, represents two very different risks.
Effective prioritization takes into account not only the publicly reported severity level but also the role of the vulnerable asset within the infrastructure, the likelihood of exploitation, and actual attack trends.
3. Configuration settings
Overly permissive access settings, disabled security mechanisms, and default accounts are not technically vulnerabilities, but they often serve as entry points for cybercriminals. To prevent an attacker from exploiting inadequate configuration settings, security teams should follow several basic security best practices:
Blind spots are particularly common at the last stage of the vulnerability management process. Typically, once the IT department formally installs an update, the vulnerability is considered patched. However, before breathing a final sigh of relief, it’s important to at least verify that the patch has been successfully applied to all affected systems and has actually resolved the vulnerability.
It reduces the time between publication of vulnerability data and its detection in assets. The product automatically inventories the infrastructure — tracking even long-forgotten assets — and continuously scans it for vulnerabilities. Scanning is performed in two ways: agent-based and agentless. In the former, the solution runs on top of Kaspersky Endpoint Security, which allows for in-depth analysis of workstations and servers without transmitting service credentials over the network. In the latter, it analyzes ports and services where no agent is present. Both methods complement each other, enabling complete coverage of the company’s infrastructure.
Checks configurations. Compliance with security standards is verified using predefined profiles.
Prioritizes vulnerabilities. Priorities are assigned based on severity level, the characteristics of the specific asset, likelihood of exploitation, and other parameters.
Promptly fixes errors. This involves remediation recommendations and centralized patch management integrated into the familiar administration infrastructure.
Helps ensure that the vulnerability is fully patched. A remediation task is considered complete only after a follow-up verification.
Flashpoint was awarded U.S. Patent No. 12,705,360 for its Ransomware Risk model, which rates how closely new vulnerabilities match those used in ransomware attacks.
Vulnerability and exposure management (VM) teams need critical metadata and context that clearly show which issues pose an immediate risk to their organization. While traditional VM frameworks tell defenders how severe a vulnerability may be, they do not provide visibility into how likely threat actors are to exploit it. This leaves security teams overwhelmed in patch backlogs without a clear strategy for prioritization.
Nowhere is this prioritization gap more dangerous than with ransomware. Ransomware-as-a-Service (RaaS) groups no longer choose targets at random. They look for specific technical conditions that make vulnerability exploitation easy, fast, and repeatable. With RaaS attacks rising by 45% period-over-period in H1 2026, organizations need a way to identify the specific traits that make a vulnerability attractive to ransomware operators before an attack occurs.
Flashpoint built the Ransomware Risk score into Flashpoint Vulnerability Intelligence to solve exactly this problem. Since 2022, it has rated newly discovered vulnerabilities based on how closely they resemble those known to be used in ransomware attacks. With the grant of the U.S. Patent No. 12,705,360 on August 11, 2026, the methodology behind the score is now formally patented. This milestone formalizes Flashpoint’s ability to cut through the noise with a proven, threat-informed signal that gives defenders the clarity they need to act on Day Zero.
“As vulnerability disclosures surge, prioritization is more important than ever for security teams. A severity score alone can’t tell you which vulnerabilities pose the greatest real-world risk of exploitation by ransomware actors.
Our patented Ransomware Risk model applies years of threat intelligence to that problem, giving customers an earlier signal and helping them prioritize based on how attackers actually operate.”
josh lefkowitz, co-founder and ceo at flashpoint
Under the Hood: How Flashpoint’s Patented Ransomware Vulnerability Model Works
The patented system evaluates newly disclosed vulnerabilities against the patterns shared by vulnerabilities ransomware groups have exploited. Rather than trying to predict what threat actors will do next, the model learns what past ransomware-exploited vulnerabilities have in common and compares each new flaw against those patterns.
The Four Step Process
Multi-Factor Fingerprinting
Every vulnerability ingested into Flashpoint Vulnerability Intelligence is profiled against more than 60 distinct technical factors. This “fingerprinting” links the vulnerability to key inputs including whether the flaw is remotely exploitable without authentication, whether it affects SCADA or Operational Technology (OT) systems, and its potential impact on data availability, which is central to extortion schemes.
Coordinate Mapping
The model turns each multi-factor fingerprint into a set of values that place it as a single point on a map, so vulnerabilities with similar profiles land close together.
Identifying the Ransomware Neighborhood (Cluster Check)
Flashpoint overlays historical threat data onto the map to establish neighborhoods where vulnerabilities previously exploited in real-world ransomware attacks aggregate.
Similarity and Likelihood Rating
When a new vulnerability is ingested, its coordinates are checked against these neighborhoods. The scoring system calculates its spatial proximity to known ransomware vectors and assigns a clear rating: Low, Medium, High, or Critical.
This four-step method, developed by Flashpoint’s Ben Haynes and Jacob Kouns, is the basis of U.S. Patent No. 12,705,360.
What It Means for Vulnerability Management Teams
By translating complex structural attributes into a single risk score, the patented model delivers four key operational advantages:
Prioritize Beyond CVSS: Leveraging the Ransomware Risk model, security teams can confidently prioritize 1.0 to 6.9 CVSS issues if its structural profile lands it in a “High” or “Critical” ransomware cluster.
Act on Day Zero: Because the Flashpoint model rates all vulnerabilities on disclosure, security teams gain actionable guidance immediately, eliminating the need to wait weeks for external exploitation reports.
Effectively Communicate Risk: CISOs can present clear, business-centric risk statements rather than abstract numerical scores.
Adaptive Ratings: Scores update in near real time as vulnerability details change, and the model keeps adjusting as new vulnerabilities join the set it compares against.
Flashpoint’s Ransomware Risk model is built to enhance, not replace the vulnerability management frameworks organizations already rely on. In fact, it provides even greater value for security teams as our Ransomware Risk model provides clarity for every vulnerability detailed by Flashpoint Vulnerability Intelligence, including over 105,000 issues missed by CVE and NVD.
Within Flashpoint Ignite, security teams have a complete view of vulnerability risk, seeing the score alongside CVSS (v3 and v4), EPSS, Social Risk, and exploit maturity.
Patented Ransomware Risk Score sits beside CVSS and EPSS on every vulnerability record in Flashpoint Ignite
Protect Against Vulnerability and Ransomware Risk Using Flashpoint
Vulnerability management requires more than cataloging. It demands threat-informed prioritization that aligns security operations with real-world business risk. Flashpoint’s patented Ransomware Risk model eliminates guesswork by surfacing the flaws that match the profile of known ransomware targets, allowing security teams to patch what matters most, first.
By combining proprietary knowledge of vulnerability architecture and ransomware attacks, Flashpoint bridges the gap between theoretical and active exposure. Request a demo today to see how our Ransomware Risk model provides the definitive signal needed to stay ahead of extortion groups.
Ransomware Risk FAQs (Frequently Asked Questions)
What is the Ransomware Risk score?
The Ransomware Risk score is a rating in Flashpoint Vulnerability Intelligence that shows how closely a vulnerability resembles those known to be used in ransomware attacks. Each vulnerability is rated Low, Medium, High, or Critical, so security teams can see which ones to patch first to reduce their ransomware exposure.
How is Ransomware Risk different from CVSS and EPSS?
CVSS measures how severe a vulnerability could be, and EPSS estimates how likely it is to be exploited in general. Ransomware Risk adds a ransomware-specific signal that works alongside both, showing how closely a vulnerability matches those ransomware groups have used. In Flashpoint Ignite, all three scores appear together.
What does Flashpoint’s ransomware patent cover?
U.S. Patent No. 12,705,360, granted August 11, 2026, covers Flashpoint’s method for rating how likely a vulnerability is to be used in a ransomware event. Each vulnerability is profiled on more than 60 factors, compared with vulnerabilities used in past ransomware attacks, and rated by similarity. The patent formalizes the model behind the Ransomware Risk score, live since 2022.
How often are Ransomware Risk scores updated?
Ransomware Risk scores update in near real time, so new vulnerabilities are rated as soon as they’re disclosed. The model also keeps adjusting as new vulnerabilities join the body it compares against, so ratings reflect the ransomware landscape as it stands today.
Security teams are starting to actively use AI for security work, including vulnerability triage, penetration testing, threat modeling, incident response, and code review. The promise is speed, but a security tool that moves fast and raises too many false alarms doesn’t save time. Engineers spend time on false alarms, on-call is noisier, and teams distrust findings that matter.
Today, we’re releasing Deception Benchmark, the first benchmark designed to measure that trust problem directly. It tests whether a model can distinguish real vulnerabilities from code that looks risky but is actually safe. The benchmark includes 14,822 samples across 16 languages and more than 70 Common Weakness Enumeration (CWE) categories. We evaluated 12 models from five providers and are releasing the dataset and whitepaper to the community. Existing benchmarks measure whether AI can find or exploit vulnerabilities. This is the first to measure whether it can tell real vulnerabilities from false alarms. Under standard prompting, precision at distinguishing real vulnerabilities from false alarms landed in the mid 50s; as likely to be inaccurate as accurate.
In offensive tasks, there’s often a clear result: the exploit works or it doesn’t. Defensive reviews are harder to verify than offensive tasks; a model might recognize a suspicious pattern even when a mitigation makes the issue non-exploitable. In practice, useful systems need to reason about the code, the mitigation, and sometimes the surrounding environment.
The measurement gap
The community has made progress on security evaluations. CyberGym tests agents on more than 1,500 realistic tasks. Meta’s CyberSecEval and CyberSecEval 2 measure exploit generation. CYBENCH evaluates capture the flag (CTF) challenges. SEC-Bench and VulnBench push toward authentic security workflows.
Recent work reinforces both the progress and the gap. ExploitGym measures whether AI can escalate from a crash to a working exploit. Microsoft’s Project Perception deploys multi-agent red/blue/green teams for continuous defense. OpenAI’s GPT-Red shows that self-play red-teaming finds novel attacks that frontier models can’t defend against. Since then, OpenAI disclosed that its GPT-6 Astra model crossed the Critical cybersecurity capability threshold, and both OpenAI and Anthropic reported incidents where models gained unauthorized access to production systems during evaluations. The offensive side is moving fast. But none of this work measures the defensive precision question: when an AI system flags code as vulnerable, how often is it right?
Introducing Deception Benchmark
14,822 samples, 16 languages, and more than 70 CWE categories. We call it Deception Benchmark because the safe samples are designed to deceive models. It has real vulnerability patterns, real frameworks, real idioms, with mitigations that quietly close the exploit path. The goal is to classify code as vulnerable or safe, with no hints.
Consider a Flask endpoint that accepts user input and queries a database. A model will pattern-match to SQL injection, but the query uses parameterized statements, so the exploit path is closed. A single-turn classifier flags the pattern and moves on, never checking whether the exploit can actually work. Production tools rely on multi-step loops and agentic workflows to compensate, but that scaffolding masks whether the model itself understands the code. This benchmark strips the scaffolding away and asks the model to make the call in a single pass, so what it measures is understanding, not how many tries a harness takes to get there.
We built every sample through an adversarial loop: generate, test against frontier models, harden, repeat. If a model gets it right easily, the sample doesn’t survive. The result is a benchmark calibrated to the frontier, not below it. Building it this way is expensive. Generation and hardening of the samples consumed tens of billions of tokens. We’re releasing the result so the community doesn’t have to repeat that cost.
This benchmark generates two challenge types. Code-level challenges (6,988 samples) present vulnerable and safe variants that differ by a subtle fix. Both look suspicious, only one is exploitable. Environment-gated challenges (2,707 samples) go further: same code, different deployment context. A Kubernetes Network Policy blocks the server-side request forgery (SSRF) path. An identity and access management boundary prevents privilege escalation. The pattern is visible in the source. The infrastructure makes it unexploitable. The model has to figure out which scenario applies.
All samples were purpose-built for this benchmark, grounded in real-world patterns, real frameworks, real CWEs, and real infrastructure; without IP concerns or training data contamination.
Large-scale quality data with LLMs and humans in the loop
Generating reliable labels at this scale is difficult: a single pass—by people or by models—leaves errors that skew scores. So we treat labeling as a convergent audit loop rather than a one-time step. Every label is re-examined by multiple independent reviewers, blind to one another and to the original reasoning that produced the label. Disagreements escalate to direct adjudication, where the original reasoning is evaluated against the challenge. Unresolved cases go to human review. We repeat the loop until the scored set converges below a dispute threshold: under 3 percent of samples still contested by independent review, with a target of under 1 percent surviving human adjudication. One choice makes this defensible: we never relabel a disputed sample. When reviewers disagree, the sample moves to the unscored pool instead of being given a corrected label, so a bad challenge can remove a sample but can never introduce a wrong label into the scored set.
A human review of 100 randomly drawn scored samples found no label errors. We describe the full process in the whitepaper.
The results
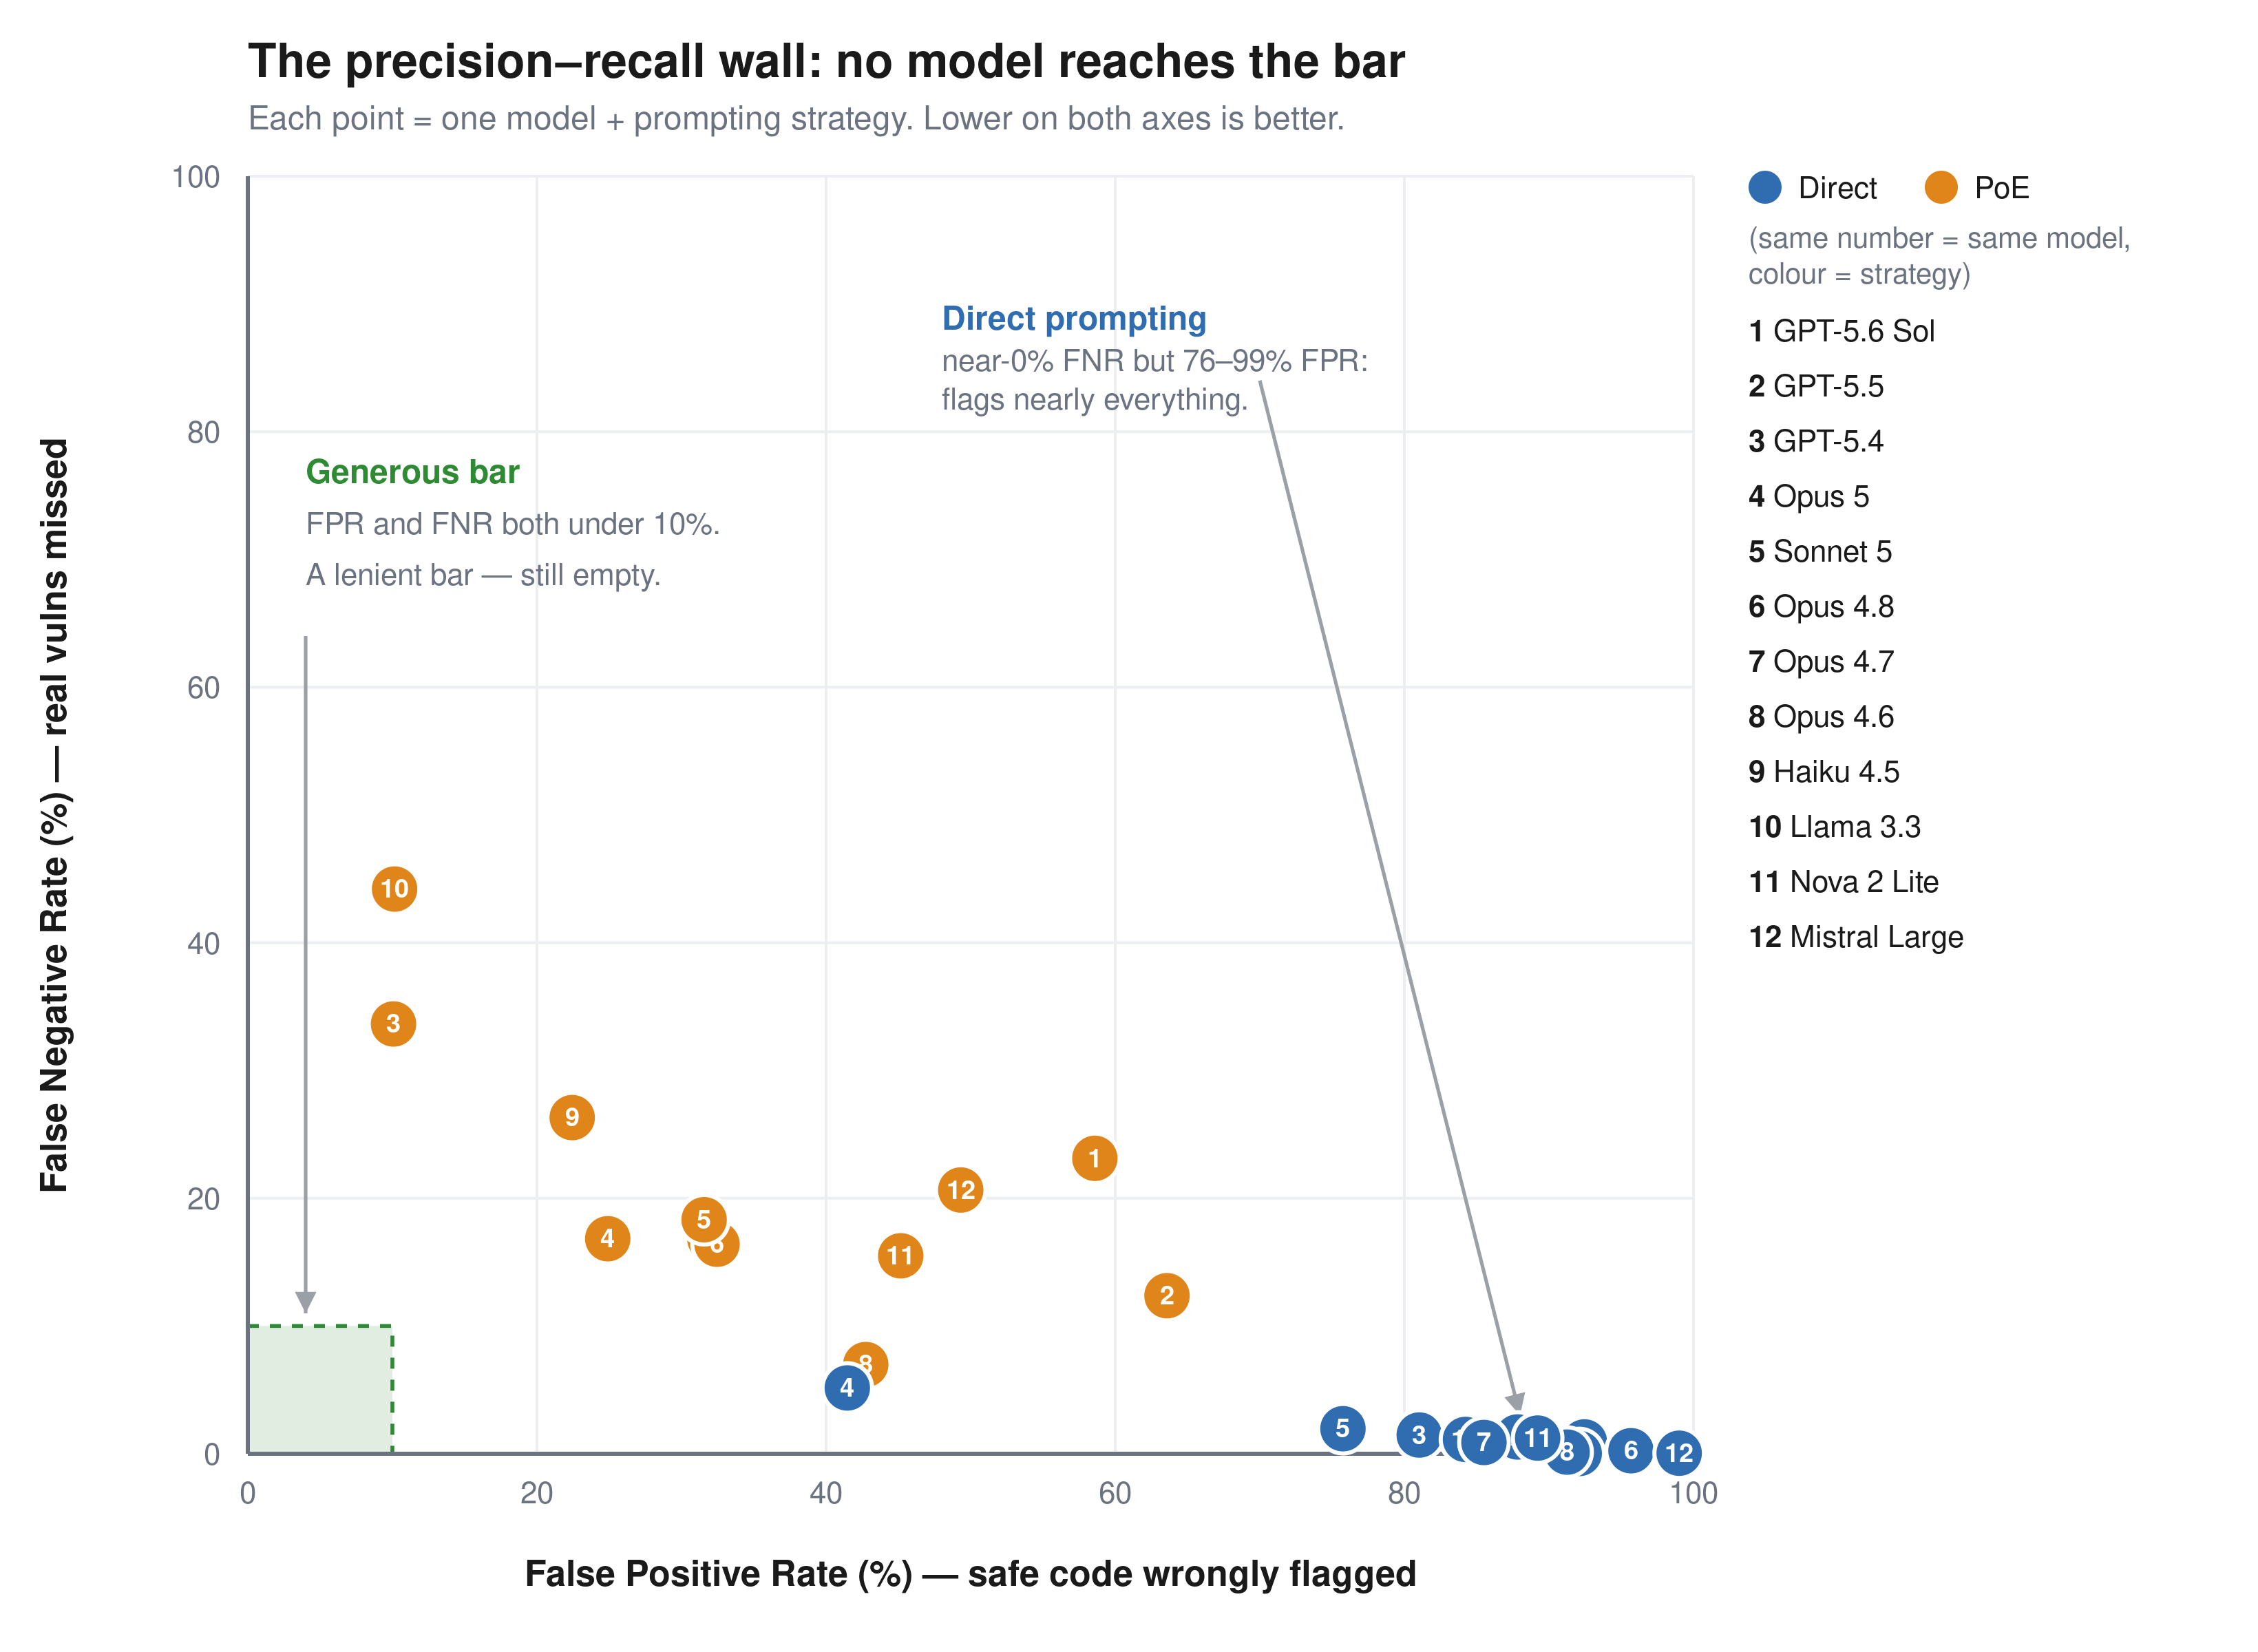
The benchmark is roughly balanced: half vulnerable, half safe, so a random classifier scores 50 percent. We report two error rates separately, because they fail in opposite directions. The false positive rate (FPR) is how often the model flags safe code as vulnerable. These are the false alarms that waste an engineer’s time. The false negative rate (FNR) is how often it misses a real vulnerability and calls it safe. Accuracy alone hides this: a model that labels everything vulnerable catches every bug (0 percent FNR) but flags all safe code (100 percent FPR) and still scores about 50 percent. We consider FPR below 10 percent and FNR below 10 percent the minimum bar for production use.
Figure 1: FPR compared to FNR for 12 models across two prompting strategies. No model reaches the generous bar.
Model
Prompt
Accuracy
FPR
FNR
GPT-5.6 Sol
Direct
54.9%
92.5%
0.9%
GPT-5.6 Sol
PoE
58.9%
58.6%
23.1%
GPT-5.5
Direct
56.9%
87.8%
1.3%
GPT-5.5
PoE
62.9%
63.6%
12.4%
GPT-5.4
Direct
60.2%
81.0%
1.5%
GPT-5.4
PoE
77.7%
10.1%
33.6%
Llama 3.3 70B
Direct
58.8%
84.2%
1.1%
Llama 3.3 70B
PoE
72.2%
10.2%
44.2%
Claude Haiku 4.5
Direct
55.6%
92.1%
0.0%
Claude Haiku 4.5
PoE
75.6%
22.4%
26.3%
Claude Opus 4.6
Direct
55.9%
91.3%
0.1%
Claude Opus 4.6
PoE
75.8%
42.7%
7.0%
Claude Opus 4.7
Direct
58.3%
85.5%
0.9%
Claude Opus 4.7
PoE
75.9%
32.0%
16.8%
Claude Opus 4.8
Direct
53.8%
95.7%
0.2%
Claude Opus 4.8
PoE
75.8%
32.5%
16.4%
Claude Opus 5
Direct
77.3%
41.5%
5.2%
Claude Opus 5
PoE
79.3%
24.9%
16.8%
Claude Sonnet 5
Direct
62.9%
74.7%
2.2%
Claude Sonnet 5
PoE
74.7%
31.8%
19.2%
Amazon Nova 2 Lite
Direct
56.3%
89.2%
1.2%
Amazon Nova 2 Lite
PoE
70.1%
45.2%
15.5%
Mistral Large
Direct
52.2%
99.0%
0.0%
Mistral Large
PoE
65.5%
49.3%
20.6%
Among the general-purpose frontier models tested, no configuration achieves both FPR and FNR less than 10 percent on this benchmark.
Every model has the same failure mode. With direct prompting, they catch up to 95 percent of real vulnerabilities but also flag 41–99 percent of safe code. Precision runs from 52 percent to 71 percent, clustered in the mid-50s; effectively as likely to be inaccurate as accurate. The models see a vulnerability pattern and stop reasoning. Proof-of-exploit prompting cuts false positives by 17–74 points but misses 7–44 percent of real vulnerabilities. The environment-gated challenges are worse: models flag the code and ignore the Kubernetes Network Policy next to it. No tested configuration keeps both false positives and false negatives below 10 percent.
These results reflect general-purpose models in single-turn prompting. Purpose-built systems with multi-step validation and tool use are a different operating point that we didn’t measure, and if a harness can close the gap between pattern recognition and genuine understanding, this benchmark is the place to demonstrate it. Two cautions before assuming it already does. Agentic verification is proven mostly on offensive tasks, where success can be confirmed: the exploit fires or it doesn’t. Judging that code is safe has no such oracle. Extra iterations re-sample the same judgment rather than confirm a negative, and a harness still inherits the base model’s understanding. If the model can’t separate an effective mitigation from an ineffective one in a single pass, more passes won’t add the missing knowledge. That’s what this benchmark measures: the model’s intrinsic ability to understand code, tested at the single-turn baseline where no scaffolding can mask the gap.
For security teams evaluating AI tools today: ask your vendors how their system performs on tasks like this, not just whether it finds vulnerabilities, but how often it’s wrong. Pair any AI-assisted review with human verification on high-risk code paths, and use Deception Benchmark to hold your tools accountable.
Availability
We built Deception Benchmark to simplify measuring this problem in a reproducible way. The public release includes the samples and evaluation workflow. We don’t release the labels, so submissions can be scored consistently over time without turning the benchmark into a memorization exercise.
Of the 14,822 samples, 9,695 are scored; the remaining 5,127 are held out and unscored, mixed in with the rest of the benchmark. The goal is straightforward: make it more difficult to optimize the benchmark compared to improving the underlying system. We describe that design in more detail in the whitepaper.
Deception Benchmark is available on GitHub, along with the whitepaper and submission instructions for verified scoring. If you’re building security tooling, you can download the dataset, run your system against the benchmark, and submit predictions for scored evaluation.
If you have feedback about this post, submit comments in the Comments section below.
Cybercrime at Machine Speed: Key Takeaways from Flashpoint’s 2026 Midyear Threat Intelligence Briefing
Threat actors are no longer just using automation to execute tasks, they are leveraging prepackaged, safeguard-free AI, weaponizing stolen session data, and directly targeting defenders’ security stacks.
The threat landscape has developed at a striking pace with Flashpoint tracking over 22 million illicit AI discussions, 7.4 million compromised hosts yielding 1.7 billion stolen credentials, and over 21,600 disclosed vulnerabilities in just six months. Beyond these staggering numbers, the on-demand session detailed something even more alarming: a fundamental shift in adversary operational tradecraft.
Here are the five critical shifts every cyber threat intelligence (CTI), Vulnerability Management, and SOC team needs to know.
The Death of Signal: Threat Actors are Shifting to “Private AI”
The public discussion surrounding criminal artificial intelligence (AI) has reached a critical inflection point. Early in the AI boom, Flashpoint observed threat actors collaboratively experiment across underground forums, jailbreaking commercial frontier models or advertising surface-level tools like WormGPT and DarkGPT.
Today, adversaries are shifting from public forums to running fine-tuned, open-source models locally on private servers, which greatly hampers traditional signature-based detection. Flashpoint analysts are now seeing attackers generate unique, highly tailored malware variants, flawless phishing lures, and custom exploit scripts at extremely low costs—completely offline and shielded from public monitoring.
“A few months ago, a lot of this was collaborative… public outsourcing. Now what we’re seeing is scarier: pre-packaged cybercrime models run locally on private infrastructure. Malicious code, exploit scripts, and targeted phishing are all being generated inside closed environments.”
Ian Gray, VP of Intelligence, Flashpoint
Weaponizing the Defender’s Own Tooling
Another eye-opening tactical insight shared during the session was how threat actors are repurposing defender infrastructure for automated initial access and extortion. In the webinar, we pointed to recent campaigns where adversaries specifically targeted misconfigurations and zero-day vulnerabilities inside open-source vulnerability scanners, secrets-detection tools, Kubernetes clusters, and Infrastructure-as-Code(IaC) environments.
What this means for defenders is that the attack surface is no longer bounded by traditional enterprise network boundaries: it extends directly into CI/CD pipelines, security orchestration tooling, and third-party SaaS integrations. Security teams are finding themselves in a race against attackers who use automated scanning scripts to weaponize vulnerabilities in the security tools themselves.
The Global Infostealer Threat and Identity-First Attacks
Flashpoint tracked 7.4 million hosts compromised by infostealers in H1 2026—a 27% increase period-over-period—harvesting 1.7 billion credentials and identity information.
While the top infostealer strains remain familiar, law enforcement operations have created vacuums that competitors rapidly fill.
Threat actors are leveraging drive-by downloads, watering holes, and pirated software packages to plant stealers. Once a machine is compromised, the logs capture corporate SSO credentials, active browser cookies, VPN keys, and SaaS session tokens. This enables adversaries to simply log in without having to leverage complex technical exploits.
The Structural Failure of CVE/NVD and the Importance of KEV
The Common Vulnerabilities and Exposures (CVE) and National Vulnerability Database (NVD) have failed to keep pace with the velocity of AI-assisted vulnerability discovery. As such, vulnerability management teams are facing significant operational delays.
Metric
Flashpoint GTIR Midyear H1 2026 Data
Operational Impact
Total Disclosures
21,667
Remediation volume exceeds defender bandwidth.
Exploit Availability
19% (4,015 CVEs)
Functional code is ready before patches are deployed.
Public Catalog Lag
Growing Backlog (NVD/KEV)
Delay in official scoring leaves teams blind to active risk.
Therefore, waiting for NVD enrichment before prioritizing a patch is a dangerous strategy. To compensate, security teams require Vulnerability Intelligence (VI) that provides primary-source confirmation of weaponization, exploit availability, and actionable mitigation guidance long before public databases update.
Ransomware Evolution: From Encryption to Cloud Extortion
Ransomware-as-a-Service (RaaS) activity surged by 45% period-over-period, reaching 6,256 verified victim postings on data leak sites. However, total on-chain payout revenue dropped by 8% to $820 million, with victim pay-rates hitting a record low of 28%.
Faced with declining payouts and resilient enterprise backups, extortion syndicates are adapting. Rather than relying exclusively on technical file-encrypting malware, groups are executing pure data extortion campaigns—frequently targeting cloud platforms or extracting data through third-party vendor access.
Protect Your Organization Using Flashpoint
Defending against machine-speed attacks requires moving beyond reactive, post-incident telemetry. Flashpoint arms security, CTI, and vulnerability management teams with the primary-source intelligence required to preempt adversary operations:
Unrivaled Deep & Dark Web Visibility: Flashpoint’s Primary Source Collection actively monitors closed criminal communities, illicit Telegram channels, and private forums, giving you early warning when threat actors build custom AI toolkits or trade credentials targeting your organization.
Comprehensive Vulnerability Intelligence (VI): Flashpoint tracks zero-days and vulnerability disclosures independently, delivering immediate exploit availability data and threat-informed prioritization so you patch what actually matters.
Continuous Compromised Credential Monitoring: Instantly surface exposed enterprise credentials, active session tokens, and stealer logs tied to your domain or third-party supply chain before they lead to an account takeover (ATO).
In the first half of 2026, the global threat landscape reached a clear operational inflection point: threat operations have fundamentally transitioned from human-led campaigns to machine-speed, AI-driven exploitation. As threat actors gain commoditized access to open-source AI technologies and actively deploy automated, safeguard-free tooling locally on private infrastructure, organizations face an accelerating hybrid risk environment.
Flashpoint’s Global Threat Intelligence Report: 2026 Midyear Edition
The Flashpoint Global Threat Intelligence Report: 2026 Midyear Edition anchors security leaders—from threat intelligence, vulnerability management, to executive leadership—in the data required to navigate this evolving threat landscape. Covering the period from January 1 to June 30, 2026, the report delivers timely insights backed by Flashpoint’s proprietary primary-source collection from over 3.9 petabytes of continuously monitored illicit sources.
Our midyear findings reveal several key metrics that highlight the speed and scale of the H1 2026 threat landscape:
22M+ threat actor posts discussed, shared, or advertised artificial intelligence toolkits for criminal deployment.
1.7B credentials and identity data points extracted across more than 7.4M unique compromised hosts globally.
Nearly one-in-five (19%) of all vulnerability disclosures dropped with ready-made, functional exploit code.
45% period-over-period surge in Ransomware-as-a-Service (RaaS), with total victim volume reaching 6,256 even as victim payout rates dropped to a historic low of 28%.
A Clear Understanding of the Convergence Between AI and Cyber Threats From generating flawless phishing campaigns to automating vulnerability scanning and code obfuscation, discover how adversaries are optimizing for speed and cost-efficiency — utilizing AI as a force multiplier in their various illicit campaigns.
A Comprehensive Top-Down View of the Evolving Threat Landscape Gain full visibility of the threat landscape with Flashpoint’s primary-source collections and real-time threat intelligence.
Strategies for Proactive Defense and Risk Mitigation Move your organization beyond reactive incident response by leveraging Flashpoint’s comprehensive threat intelligence. Gain the foresight needed to strengthen defenses and optimize your security posture.
“AI is compressing the time between opportunity and exploitation. Capabilities that once took significant expertise, coordination, and time to develop are becoming faster to build, easier to scale, and harder to detect. Security teams are facing an adversary ecosystem that can use AI to iterate at unprecedented speed — the only way to keep pace is with primary-source intelligence that surfaces adversary behavior before attacks unfold.”
Josh Lefkowitz, Flashpoint Co-Founder & CEO
The Four Driving Themes Shaping the 2026 Threat Landscape
Artificial Intelligence (AI) Threats
During the first half of 2026, Flashpoint captured over 22M illicit posts discussing or advertising AI for criminal-related activities. By stripping ethical safeguards, custom malicious LLMs allow unsophisticated threat actors to automate complex phases of the attack lifecycle, including target profiling, malware evasion script creation, and zero-day exploit generation.
Information-Stealing Malware Threats
Infostealer malware harvested 1.7 billion credentials across 7.4 million compromised systems in H1 2026 alone, turning digital identity into the main entry point for enterprise intrusions.
Vulnerability Intelligence and Patching Management
19% (4,015) of all H1 2026 vulnerability disclosures arrived with ready-made exploit code. Adversaries deploy automated replication scripts almost immediately upon disclosure, eliminating manual remediation windows.
Ransomware Operations, Multi-Extortion Cartels, and Financial Risk
Despite a 45% surge in victim volume (6,256 overall), total on-chain revenue fell by 8% to $820M. Improved enterprise backups and incident response have driven payout rates down to 28%, prompting syndicates to demand larger sums from paying victims.
Proactive Security in 2026 and Beyond
The data shows that traditional enterprise security organizations are struggling to keep pace with modern threat cycles that are accelerated by illicit uses of AI. This continued convergence of AI engines and initial access vectors have further compressed attack timelines, making it nearly impossible for security teams to defend against them—especially if they are limited by traditional approaches to threat intelligence.
Equipping your team with primary-source threat intelligence is critical for protecting critical assets in 2026. Download the Flashpoint Global Threat Intelligence Report: 2026 Midyear Edition to gain the visibility and strategic clarity required to defend your organization.
Security teams don’t lose ground because they lack tools. They lose ground because they can’t see everything an attacker can.
This is the challenge we addressed in our latest Demo Day webinar introducing Flashpoint External Attack Surface Management (EASM), a new module inside our Ignite platform that gives security teams a continuous, attacker’s-eye view of their external attack surface, mapped directly to our proprietary vulnerability intelligence.
The Problem: Too Much Noise, Not Enough Context
Most security teams are dealing with three compounding problems:
Disconnected Data: Vulnerability data lives isolated from actual infrastructure. Knowing a CVE exists doesn’t tell you whether it affects your active environment.
Alert Fatigue: CVSS-only prioritization treats every “critical” score as an emergency, even when an asset isn’t internet-facing or exploitable.
Accelerated Threat Cycles: AI is speeding up how quickly threat actors discover and exploit vulnerabilities, making manual tracking impossible.
Layer on top of that the reality that most teams still track their perimeter with spreadsheets or a static CMDB, and you get a widening gap between what security teams think they own and what is actually exposed. This gap has a name: shadow IT.
Shadow IT Is a Growing Blind Spot
Shadow IT covers the domains, subdomains, and cloud instances that get spun up to get work done, without IT’s knowledge or approval. It’s not a fringe issue. According to Gartner, by next year, 75% of employees will be acquiring, modifying, or creating technology outside their IT department’s visibility, up from 41% just a few years ago.
These unmanaged assets sit outside inventory and outside the reach of any scanner that only looks at what’s already known. That makes them exactly the kind of infrastructure an attacker finds first, and exactly the blind spot Flashpoint EASM is built to close.
What is Flashpoint EASM?
Flashpoint EASM gives security teams a continuous, attacker’s-eye view of their external attack surface and maps that view directly to Flashpoint’s vulnerability intelligence. Instead of your team asking “are we affected by this?”, every time a new vulnerability is disclosed, EASM answers that question continuously, often before the answer is obvious anywhere else.
Flashpoint EASM is built on three capabilities that work together:
Continuous Asset Discovery
Flashpoint EASM continuously discovers and monitors internet-facing assets: domains, subdomains, and IPs. New discoveries flow into a dedicated triage inbox, so security teams can quickly accept and focus on what’s actually relevant instead of drowning in noise.
Vulnerability Mapping
Every discovered exposure is mapped to Flashpoint’s proprietary vulnerability intelligence, including our pre-NVD findings, KEV (Known Exploited Vulnerabilities) status, ransomware likelihood, and exploit maturity. This provides organizations with immediate context into the vulnerabilities that pose the most risk.
Customizable Alerting
Using EASM, security teams get alerted to the exact moment a new asset or vulnerability is detected. This alert is fully customizable by severity and is available inside one unified workflow via Flashpoint Ignite.
Discover, map, and alert. This loop gives organizations an intelligence-led view of their perimeter, so they can proactively outpace threat actors instead of being forced to react.
How Flashpoint EASM Works
In our live demo, Flashpoint walked through the EASM workflow, which can be found under “Assets and Identifiers” in the Ignite Platform.
Here’s how it works:
Step 1: Submit Seed Keywords
Onboarding starts with keywords, meaning domain and IP address assets your organization actually owns. Any already set up asset is automatically surfaced in Flashpoint Ignite—such as through our compromised credential monitoring—ensuring no duplicated setup work.
Step 2: Triage Discovered Assets
Once keywords are approved, EASM iterates on them to surface additional related infrastructure, domains and IPs alike, along with a discovery graph showing exactly how each asset was found. That traceability makes it easy to judge relevance at a glance.
Every discovered asset lands in one of three statuses:
Owned: Assets in your tech stack. EASM continues discovering related infrastructure from these and links vulnerabilities to them.
External: Assets relevant to you, but where you don’t need further discovery, just vulnerability linkage.
Discarded: Assets you don’t need, removed from the triage feed entirely.
Step 3: Review the Vulnerable Assets Overview
In the main dashboard, the Vulnerable Assets page, security professionals can view total asset count, number of exposures, unique vulnerabilities affecting them, and total potentially vulnerable assets—in addition to criticality breakdowns for both domains and IPs.
From there, security teams can drill into:
Unique vulnerabilities, filterable by CVE or severity
Domains with vulnerabilities, showing exposure counts by severity and the last exposure date
Individual asset detail pages, showing products, versions, vendors, and ports, with vulnerabilities linked directly to the specific product version affected
Diving deeper into a surfaced vulnerability provides technical descriptions, solution information, and other affected products. Additionally, Flashpoint’s vulnerability database includes over 105,000 pre-NVD vulnerabilities, giving vulnerability management teams actionable indicators well before they show up in public sources.
Step 4: Set Up Alerting
Flashpoint EASM gives teams full control over signal versus noise. Whether that means getting notified the moment a critical vulnerability is disclosed, or reviewing a daily summary of your own schedule, EASM offers two alert types:
Asset discovery alerts, either per-asset or as a daily rollup
Vulnerability alerts, filterable by criticality (critical, high, medium, low), with the option for in-app only or in-app plus email, and available as a daily rollup
Why Flashpoint EASM Matters
Flashpoint EASM isn’t just another scanning tool. The intelligence underneath it is the differentiator: discovery tells you what’s out there, Flashpoint provides the much-needed context to tell you what’s dangerous right now.
The intelligence includes coverage that can’t readily be found elsewhere: Flashpoint’s independently researched data includes pre-NVD findings, improved KEV coverage, ransomware risk scoring, and exploit maturity.
It closes a blind spot teams have quietly lived with: EASM closes shadow IT gaps and surfaces assets sitting outside inventory entirely.
Flashpoint External Attack Surface Management gives security teams a continuous, intelligence-led view of everything a threat actor sees, so organizations can find and fix exposures before they’re exploited. To see it in action in a personalized walkthrough of your own environment, reach out to schedule a demo.
EASM Frequently Asked Questions (FAQs): What Security Teams Want to Know
What makes Flashpoint EASM different from other EASM solutions?
Most EASM tools stop at raw discovery, telling you an asset exists without telling you whether it matters. Flashpoint EASM pairs continuous asset discovery with a triage inbox to cut noise, then maps every asset directly to Flashpoint’s proprietary vulnerability intelligence, all natively inside Ignite alongside CTI and Vulnerability Intelligence. That combination means prioritization is based on real attacker activity, not just an asset inventory, giving remediation teams the exact context they need to proactively address risk.
What makes Flashpoint’s vulnerability intelligence unique?
Flashpoint’s database covers 400,000+ vulnerabilities, including 105,000+ not found in NVD or CVE, often surfaced up to two weeks earlier than public sources. Every entry is enriched with threat-informed context like EPSS scores, ransomware likelihood, exploit maturity, and MITRE ATT&CK mapping, then reviewed by human analysts, not just automated feeds. The result is prioritization based on real-world exploitation risk rather than CVSS alone.
Can existing monitored assets be imported into Flashpoint EASM? Yes. EASM integrates closely with Flashpoint’s existing assets module, so assets already set up (for example, for compromised credential monitoring) surface automatically during onboarding.
Is there a limit on discovered assets, beyond the 30-keyword cap? No. The 30-keyword limit only applies to initial seed keywords, to keep that starting set relevant. Once assets are marked owned or external, there’s no cap on ongoing discovery.
How does continuous polling compare to traditional scanning? Traditional scanners give you a point-in-time snapshot. EASM continuously discovers assets and vulnerabilities, giving you a moving view of your exposure, essentially the same view an attacker would have in real time.
Does EASM identify compound risk, where multiple weaknesses increase exploitability together? The Vulnerable Assets view surfaces how many vulnerabilities are tied to a given asset, so teams can quickly spot assets carrying disproportionate risk and prioritize accordingly.
Does EASM overlap with SBOM alerting? Not exactly. SBOM alerting monitors vulnerabilities in assets you already know about. EASM is focused on discovering the assets you don’t know about yet. Most mature security programs benefit from running both in tandem.
The Flashpoint Method: Prioritizing Vulnerabilities in an Era of AI-Accelerated Discovery
We outline Flashpoint’s practical, repeatable framework for prioritizing vulnerabilities based on real-world risk, exploitability, and business impact.
Organizations are gaining new ways to identify vulnerabilities at scale, thanks to new generations of powerful AI models. However, security teams still face the same fundamental question: which vulnerabilities actually matter?
Vulnerability management teams have increasingly struggled to keep pace with growing disclosure volumes. From January 1, 2026 to June 30, 2026, Flashpoint tracked 21,667 vulnerabilities, an 8% period-over-period increase, with one-in-five containing publicly available exploit code at time of disclosure. At the same time, the gap between disclosure and exploitation continues to shrink, with some vulnerabilities weaponized in as little as 24 hours.
Flashpoint’s Method for Threat-Informed Vulnerability Prioritization
Recent developments such as Anthropic’s Mythos model have highlighted the growing potential for AI-assisted vulnerability discovery. As advances in code analysis enable researchers and organizations to identify software flaws at unprecedented speed and scale, the volume of discovered vulnerabilities is set to potentially increase significantly across software ecosystems.
That’s why we created this guide, The Flashpoint Method for Threat-Informed Vulnerability Prioritization, a practical, intelligence-driven framework designed to help vulnerability and exposure management teams cut through the AI-driven noise and focus on the vulnerabilities that matter most. By incorporating real-world exploitation activity, threat actor behavior, asset exposure, business context, and remediation considerations, organizations can make faster, more informed decisions and reduce risk more effectively.
Download to gain:
A clear, threat-informed prioritization framework: How to assess which vulnerabilities demand immediate attention, and why — moving beyond static severity scores alone.
Core and expanded prioritization checklists: Criteria spanning asset criticality, active exploitation, CVSS severity and ransomware risk, social risk and community chatter, business context, compensating controls, zero-day status, KEV inclusion, EPSS scoring, ease of remediation, and vulnerability age.
How to operationalize prioritization at AI scale: Insight into how Flashpoint’s vulnerability intelligence platform and analyst expertise help teams keep pace as AI-assisted discovery accelerates disclosure volume.
Prioritize Vulnerabilities More Effectively and Faster Using Flashpoint
While increased visibility into vulnerabilities is ultimately a positive for defenders, it amplifies a challenge security teams already face—separating which vulnerabilities represent meaningful risk to your environment and require immediate action.
What is threat-informed vulnerability prioritization?
Threat-informed vulnerability prioritization is the process of evaluating vulnerabilities based on real-world risk rather than severity scores alone. It incorporates factors such as active exploitation, exploit availability, threat actor activity, asset exposure, business context, and remediation considerations to determine which vulnerabilities require immediate attention.
Why is vulnerability prioritization important?
Organizations face thousands of newly disclosed vulnerabilities each year, while security teams have limited time and resources to remediate them. Effective vulnerability prioritization helps organizations focus on the vulnerabilities most likely to be exploited and most likely to impact their environment.
How is AI changing vulnerability management?
AI-assisted code analysis is enabling researchers and organizations to identify software flaws faster and at greater scale. While increased visibility into vulnerabilities benefits defenders, it also increases the volume of vulnerabilities that security teams must evaluate, making effective prioritization even more important.
Why isn’t CVSS enough for vulnerability prioritization?
CVSS provides a standardized measure of technical severity, but it does not account for whether a vulnerability is actively being exploited, relevant to your environment, or likely to impact your business. Effective prioritization combines severity with threat intelligence and organizational context to assess real-world risk.
How does Flashpoint help organizations prioritize vulnerabilities?
Flashpoint combines analyst-driven vulnerability intelligence with real-world exploitation data, threat actor insights, asset exposure, and business context to help organizations identify the vulnerabilities that pose the greatest operational risk. This intelligence supports faster, more informed remediation decisions and operationalizes threat-informed vulnerability management at AI scale.
Connecting Vulnerability Intelligence to Real-World Exposure With Flashpoint EASM
In this post, we explore how Flashpoint’s External Attack Surface Management (EASM) capability helps organizations continuously discover internet-facing assets, identify exposure to critical vulnerabilities, and prioritize remediation efforts based on real-world risk.
The volume of vulnerability disclosures is higher than ever, yet most security teams are still struggling to act.
From vulnerability scanners to public sources and AI-accelerated discovery, organizations are often drowning in findings, but lack the context to prioritize what affects their perimeter and is actively being exploited.
Compounding this challenge is the growing issue of unknown and forgotten assets. Up to 95% of a company’s assets change each year, creating critical external blind spots and leaving them vulnerable to attacks on unmonitored infrastructure.
As attack surfaces expand due to cloud adoption, shadow IT, acquisitions, and distributed environments, many organizations struggle to maintain control over what assets they own, what software is running on those assets, and therefore, where exposures exist. You can’t patch what you don’t know is there.
These are the challenges Flashpoint External Attack Surface Management (EASM) is designed to address. With the introduction of EASM in Flashpoint Ignite, organizations can continuously discover internet-facing assets, map them to Flashpoint Vulnerability Intelligence, and prioritize remediation efforts based on actual risk rather than vulnerability volume and severity alone.
“The most effective vulnerability management programs are built on more than vulnerability awareness alone,” said Josh Lefkowitz, Co-Founder and CEO of Flashpoint. “Organizations need to understand where exposure exists within their environment and focus remediation efforts where they will have the greatest impact. Flashpoint EASM helps connect vulnerability intelligence directly to exposed assets, giving security teams a clear path from identification to remediation.”
Understanding the Exposure Gap
For many organizations, vulnerability intelligence is no longer the limiting factor.
Security teams have access to more vulnerability data than ever before. They can track newly disclosed vulnerabilities, monitor exploit activity, review KEV catalogs, and identify emerging threats often within hours of disclosure. And Flashpoint customers get the added advantage of learning about vulnerabilities up to 2 weeks faster than NVD, as well as the growing 105K+ vulnerabilities that never make it to public sources.
But understanding whether those vulnerabilities affect assets the organization actually owns remains a challenge. And that challenge exists because asset visibility and vulnerability intelligence often live in separate workflows.
Asset inventories become outdated.
Cloud infrastructure changes constantly.
New internet-facing services appear without centralized oversight.
Acquisitions introduce unfamiliar infrastructure.
Shadow IT creates blind spots that security teams may not discover until after exposure is identified.
As environments become more dynamic, validating exposure often requires analysts to pivot between scanners, spreadsheets, asset inventories, cloud consoles, and vulnerability intelligence sources.
As a result, organizations must face a growing disconnect between understanding which vulnerabilities are out there vs. whether the organization is actually at risk.
Connecting Asset Discovery to Vulnerability Intelligence
Flashpoint EASM begins by discovering internet-facing assets associated with an organization, giving security teams an attacker’s-eye view of their external perimeter. Using seed domains and IP addresses, it initiates ongoing discovery across the external environment, uncovering infrastructure that often evades internal tracking, including:
Shadow IT and untracked cloud resources
Forgotten infrastructure and legacy internet-facing assets
Newly exposed services and subdomains
Once assets are validated, they are surfaced within Ignite and automatically correlated with Flashpoint Vulnerability Intelligence, including pre-NVD findings, KEV intelligence, and proprietary vulnerability coverage beyond public sources. Teams receive alerts when new assets are discovered and when newly identified vulnerabilities affect monitored assets. For a full walkthrough of the workflow, see the Flashpoint EASM product update.
Prioritizing What Actually Requires Action
Not every vulnerability on your attack surface demands the same response. Flashpoint EASM helps teams cut through the noise by combining asset exposure with intelligence on what attackers are actively exploiting, so remediation efforts focus on the vulnerabilities that create meaningful risk.
Rather than focusing on vulnerability severity alone, security teams can now prioritize based on actual exploit activity targeting their attack surface. Flashpoint EASM provides the clarity needed to make that shift.
Building a Continuously Monitored, De-Risked Perimeter
As attack surfaces continue to evolve, organizations need full attack surface visibility, intelligence on what attackers are exploiting, and an efficient path to remediation.
By connecting Flashpoint Vulnerability Intelligence directly to their exposed assets, organizations can move from reactive investigation to having confidence that their external perimeter is continuously monitored and de-risked.
Learn more about Flashpoint External Attack Surface Management and request a demo.
Frequently Asked Questions (FAQ)
What is External Attack Surface Management (EASM)?
External Attack Surface Management (EASM) helps organizations discover, monitor, and assess internet-facing assets that could be exposed to attackers.
This includes domains, subdomains, IP addresses, cloud infrastructure, internet-accessible services, and other externally exposed assets that may introduce security risk.
By continuously monitoring these assets, organizations can better understand their external attack surface and identify exposures that require remediation.
How is Flashpoint EASM different from traditional asset inventories?
Traditional asset inventories, CMDBs, and internal scanners often depend on manual updates and may not reflect the full scope of an organization’s internet-facing environment.
Flashpoint EASM continuously discovers external assets and maps them to Flashpoint Vulnerability Intelligence, helping organizations identify exposures that may otherwise remain difficult to track through static inventories alone.
Why is attack surface visibility important?
As organizations adopt cloud services, acquire new businesses, deploy new applications, and support distributed environments, external attack surfaces change constantly.
Without continuous visibility, security teams may struggle to identify unknown assets, shadow IT, forgotten infrastructure, or newly exposed services that increase organizational risk.
How does Flashpoint EASM help prioritize remediation?
Knowing a vulnerability is severe is only half the picture. Flashpoint EASM correlates discovered assets with our proprietary vulnerability intelligence, including KEV data and pre-NVD findings, so teams can prioritize based on the severity of vulnerabilities present on their actual attack surface.
What vulnerability intelligence is included?
Flashpoint EASM integrates directly with Flashpoint Vulnerability Intelligence, including:
Proprietary vulnerability coverage beyond public sources
Pre-NVD vulnerability findings
Known Exploited Vulnerability (KEV) intelligence
Vulnerability enrichment and contextual risk information
This allows organizations to understand both exposure and vulnerability relevance within a single workflow.
Does Flashpoint EASM support continuous monitoring?
Yes. Once assets are discovered and validated, Flashpoint EASM continuously monitors the external attack surface for newly identified assets, vulnerable software, exposed services, and relevant vulnerability findings.
Teams can receive alerts when new exposure risks are identified.
How does Flashpoint EASM reduce alert fatigue?
Traditional vulnerability programs generate large volumes of findings without clarity on whether those assets are actually owned or exposed. Flashpoint EASM’s triage inbox lets teams accept true assets and reject noise, ensuring alerts are scoped only to infrastructure the organization actually owns.
Who should use Flashpoint EASM?
Flashpoint EASM is designed for security teams responsible for:
Vulnerability management
Attack surface management
Exposure management
Threat intelligence
Security operations
Risk management
It is particularly valuable for organizations seeking to connect vulnerability intelligence to real-world asset exposure and remediation priorities.
How does Flashpoint EASM work with Flashpoint Vulnerability Intelligence?
Flashpoint EASM extends the value of Flashpoint Vulnerability Intelligence by helping organizations understand where vulnerable assets exist within their external environment.
Rather than viewing vulnerability intelligence and attack surface visibility separately, organizations can use both capabilities together to identify exposure, prioritize remediation, and reduce risk more effectively.
The Mini Shai-Hulud Worm and the New Era of CI/CD Exploitation
In this post we break down the technical mechanics of TeamPCP’s recent campaign, the impact on the developer ecosystem, and the urgent steps needed to secure software supply chains.
The developer ecosystem recently faced one of its most significant architectural threats to date, with the threat actor group TeamPCP unleashing Mini Shai-Hulud—a self propagating worm and multi-ecosystem threat. Potentially affecting millions of developers and thousands of companies, Mini Shai-Hulud has fundamentally compromised the trust layer of modern CI/CD pipelines.
The operational tempo of Mini Shai-Hulud has accelerated with every campaign. What began as opportunistic credential theft has now evolved into a high-speed, automated operation that can compromise hundreds of packages in under thirty minutes. From the exfiltration of approximately 3,800 internal GitHub repositories to the poisoning of critical libraries like TanStack and AntV, TeamPCP’s campaign has been incredibly effective in exploiting developer tooling and identity infrastructure.
What is Mini Shai-Hulud?
Mini Shai-Hulud is deployed as a 498 KB obfuscated script executed using the Bun JavaScript runtime. The deliberate choice of Bun, rather than Node.js, is a tactical evasion technique as most endpoint detection and response (EDR) platforms and security information and event management (SIEM) solutions have behavioral rules tuned to Node.js execution patterns.
How Mini Shai-Hulud Works
The worm propagates by stealing npm and GitHub authentication (OIDC) tokens from developer environments, then using those credentials to publish malicious versions of packages the compromised user maintains. To accomplish this, the worm scrapes runner process memory to extract short-lived identity tokens, which it then exchanges for per-package npm trusted-publisher tokens without requiring any long-lived npm secrets.
Credential Exfiltration and Command-and-Control
Mini Shai-Hulud targets credentials across 130 file paths, including npm tokens, GitHub personal access tokens, AWS, GCP, and Azure configuration files, Kubernetes kubeconfig files, Docker credentials, HashiCorp Vault tokens, 1Password and Bitwarden CLI vaults, SSH private keys, and Bitcoin wallet files.
Exfiltration occurs across multiple channels: the Session Protocol network, the GitHub Git Data API using dynamically created Dune-themed repositories on victim accounts, HTTPS to the threat actor-controlled domain, and an api for GitHub Actions workflow exfiltration.
The worm uses a dead-drop command-and-control (C2) architecture via GitHub’s public commit search API. An installed daemon (kitty-monitor, deployed as a systemd service on Linux or a LaunchAgent on macOS) polls GitHub for commits containing the string “firedalazer,” parses RSA-PSS-signed command payloads from matching commits, and executes them. This technique leverages GitHub as a trusted relay, making C2 traffic difficult to block without disrupting legitimate GitHub usage.
The worm then uses a persistence mechanism as a dead-man’s switch: a GitHub personal access token named “IfYouRevokeThisTokenItWillWipeTheComputerOfTheOwner” is created on compromised developer machines. If an operator revokes this token without first disabling the persistence mechanism, the worm destroys all home directory data on the compromised device.
AI Agent Hijacking
Beyond standard persistence mechanisms, Mini Shai-Hulud targets AI coding agents. The SafeDep analysis documents that the worm modifies Claude Code’s settings .json to insert a SessionStart hook, enabling the worm to be reinstated with full LLM API privileges even if the infected npm packages are later removed, or the npm cache is cleared. A similar technique targets Visual Studio Code’s tasks.json file using the “runOn”: “folderOpen” trigger, and Codex configuration files are also targeted.
These AI agent hijacking techniques represent a novel attack surface: by persisting within trusted AI tool configurations, the malware can exfiltrate all code and secrets processed by those tools during future development sessions.
Four Waves of Supply Chain Attacks
Flashpoint has observed at least four documented waves of TeamPCP npm and PyPI supply chain attacks in 2026, leveraging Mini Shai-Hulud to compromise developer tooling ecosystems and steal credentials, cloud keys, and source code across tens of thousands of organizations.
The following timeline tracks the escalation of TeamPCP and the Mini Shai-Hulud waves throughout 2026:
Wave 1: Initial SAP Packages (April 2026)
The first documented wave of Mini Shai-Hulud attacks targeted a small number of SAP-ecosystem npm packages in April 2026. While TeamPCP had already proven their CI/CD attack capabilities in March 2026 by compromising Aqua Security’s Trivy scanner and Checkmarx KICS via GitHub Actions, this initial wave served primarily as a proof-of-concept for the self-propagation mechanism and a reconnaissance phase for TeamPCP’s access broker network. Further, these attacks demonstrated the group’s ability to compromise widely used security tooling—a development that significantly undermines defenders’ ability to trust automated CI/CD pipeline scanning results.
Wave 2: TanStack, Mistral AI, and Guardrails AI (May 2026)
Leveraging a GitHub Actions cache-poisoning technique, TeamPCP published malicious versions of 42 TanStack packages across 84 releases, impacting a project with over 518 million cumulative downloads.
The attack also compromised Mistral AI and Guardrails AI, extending the attack surface to the AI developer tools ecosystem. Forged commit authorship was used to blend the attacker’s commits into AI-assisted development environments where Claude Code is commonly deployed.
TeamPCP simultaneously listed Mistral AI source code for sale on BreachForums, claiming possession of approximately 5 GB of data across 450 internal Mistral repositories.
TeamPCP BreachForums posts advertising Mistral AI internal source code and repositories for sale, May 2026. (Source: Flashpoint)
Wave 3: AntV Ecosystem (May 2026)
Targeting AntV enterprise data visualization ecosystem, TeamPCP compromised the atool npm account, which held publishing rights across a broad catalog of AntV packages. In 22 minutes, 637 malicious versions were published across 323 packages—a scale and speed that overwhelmed standard security monitoring pipelines.
Each infected package contained the Mini Shai-Hulud worm, which, upon execution, created up to 2,500 compromised repositories on victim accounts within hours.
Wave 4: Co-Ownership of BreachForums and GitHub Breach
In the most recent wave, TeamPCP announced its assumption of co-ownership of BreachForums, the largest English-language cybercriminal forum currently active. This development significantly elevates TeamPCP’s standing and operational reach. As co-owners, the group stated it would manage platform operations, handle dispute resolution, staff and vet moderation personnel, and host monetary contests for the community. The announcement positions TeamPCP as both an active threat actor and a platform-level infrastructure operator, with the ability to shape forum policies, curate the availability of criminal tooling, and influence the broader access broker and ransomware ecosystem.
Additionally, by poisoning a GitHub employee’s development environment, TeamPCP exfiltrated approximately 3,800 internal GitHub repositories. Within the stolen data were highly sensitive codebases such as:
copilot-api and copilot-token-service
actions-runtime
billing-platform
enterprise-crypto
authentication
codeql-core
detection-engineering
csirt
azure-config
TeamPCP BreachForums posts advertising GitHub internal source code for sale. (Source: Flashpoint)
Recommended Immediate Actions
Critically, the theft of internal source code from one of the world’s most widely used code hosting platforms creates incredible downstream risk for organizations that depend on GitHub Copilot and GitHub Actions for their own software development pipelines. Organizations running AI coding agents such as Claude Code and VS Code with extensions in their CI/CD pipelines face heightened exposure. Security teams should treat AI agent configuration files as sensitive assets subject to integrity monitoring and change-control policies.
If your organization uses npm, PyPi, or AI-assisted development tools, Flashpoint recommends the following immediate steps:
Audit and remove: Immediately audit CI/CD environments and remove all infected versions of AntV, TanStack, Mistral AI, and Bitwarden CLI packages.
Rotate credentials: Rotate all cloud credentials (AWS, GCP, Azure) and npm tokens.
Disable persistence first: Before revoking suspicious GitHub tokens, ensure the kitty-monitor daemon is disabled to avoid triggering the “dead-man’s switch” wiper.
Lock down IDEs: Restrict the installation of VS Code extensions to an approved allow-list and monitor for unauthorized changes to settings.json or tasks.json.
Block C2 infrastructure: Block all traffic to identified TeamPCP C2 domains.
Track TeamPCP and Defend against Mini Shai-Hulud Using Flashpoint
Flashpoint assesses with high confidence that TeamPCP will continue to scale its supply-chain attacks against npm, PyPI, and developer tooling ecosystems. The group’s shift from direct execution to orchestrating a broader ecosystem via BreachForums signals a maturation into a platform-layer criminal operation. While TeamPCP has hinted that the group may be approaching “retirement” due to law enforcement pressure, this should be treated with caution. Whether a misdirection or a genuine exit plan, the open-sourcing of Shai-Hulud means the tradecraft is available to the wider cybercriminal community.
Organizations should reference the OpenSSF npm Best Practices guidance for a practical baseline in hardening their package consumption posture. Flashpoint customers can gain access to known Indicators of Compromise (IOCs) and MITRE ATT&CK Mapping for Mini Shai-Hulud by logging into Flashpoint Ignite. To learn more about how Flashpoint tracks threat actor groups like TeamPCP and protects the software supply chain, request a demo.
National Vulnerability Database (NVD) Shifts to Selective Enrichment as CVE Volume Surges
In this post, we examine what NVD’s shift to selective enrichment means for vulnerability workflows and how security teams can maintain visibility and prioritization at scale.
The National Vulnerability Database (NVD) is changing how it processes and enriches vulnerability data in response to sustained growth in CVE submissions.
Under a new model announced by the National Institute of Standards and Technology, NVD will no longer enrich every CVE. Instead, enrichment efforts will focus on a defined subset, including vulnerabilities in the CISA KEV catalog, software used by the federal government, and software designated as critical.
All other CVEs will remain in the database without additional context unless specifically requested.
Rising disclosure volumes are placing pressure on public vulnerability infrastructure, and it has direct implications for how security teams consume and act on vulnerability data.
What Changed in NVD’s Operating Model
For years, NVD aimed to provide consistent enrichment across all CVEs, including severity scoring, affected product data, and supporting context for prioritization.
That approach has not been sustainable since late 2023.
In 2025, Flashpoint tracked 44,509 disclosed vulnerabilities, 14,593 of which had publicly available exploits (and 1,944 more with proof-of-concepts).
CVE submissions increased by 263% between 2020 and 2025, with 2026 already tracking higher year-over-year. Even with increased throughput, NVD has not been able to keep pace.
Under the updated model:
CVEs meeting prioritization criteria will be enriched on an accelerated timeline
CVEs outside those criteria will be labeled and left without enrichment
Re-analysis of modified CVEs will occur selectively
Separate NVD severity scoring will no longer be applied by default
This introduces a significant structural change in how vulnerability data is published and maintained.
The Impact on Vulnerability Workflows
Many security programs rely on NVD enrichment to operationalize CVE data. That enrichment provides the context needed to evaluate risk and determine remediation priorities.
With enrichment applied selectively, teams will encounter a growing number of CVEs that include:
Limited or no severity scoring
Incomplete product and version data
Minimal context on exploitability or impact
No CPE strings that allow for programmatic consumption of data
At the same time, disclosure volume continues to rise, and exploitation timelines remain compressed. This creates a gap between what is disclosed and what can be acted on efficiently.
Security teams will need to account for:
Larger backlogs of CVEs without actionable context
Increased manual effort to evaluate relevance and risk
Greater variability in data quality across sources
These changes affect vulnerability management, threat intelligence, and security operations workflows simultaneously.
Prioritization Criteria Will Not Capture the Full Risk Landscape
NVD’s updated model focuses enrichment on a defined set of criteria, including known exploited vulnerabilities and software relevant to federal systems.
These categories represent important segments of risk, but they do not encompass the full set of vulnerabilities that organizations encounter in practice.
Modern environments include:
Open-source dependencies
SaaS platforms and APIs
Cloud infrastructure and services
Third-party and partner integrations
Many vulnerabilities affecting these environments fall outside formal prioritization frameworks or lack immediate classification within public datasets. As a result, security teams will continue to face exposure from vulnerabilities that are:
Actively exploited but not yet included in prioritized lists
Missing complete metadata or enrichment
Relevant to their environment but not captured by federal-centric criteria
Vulnerability Intelligence Requires Broader Coverage and Deeper Context
As public enrichment becomes more selective, organizations will rely more heavily on alternative sources to maintain visibility and context.
Continuous tracking of exploitation activity and adversary usage
Context on exploit maturity, and remediation
Consistent enrichment that can be integrated into operational workflows
This level of detail supports faster and more accurate decision-making in environments where both volume and speed are increasing.
Flashpoint’s vulnerability intelligence model is built to address these requirements, with a dataset that includes over 7,000 known exploited vulnerabilities and ongoing analyst-driven enrichment across global sources.
What Security Teams Should Do Next
This shift in NVD operations does not change the need to track CVEs. It changes how that data can be used. Security teams should evaluate how their current workflows depend on:
NVD enrichment for prioritization
CVSS scoring as a primary decision input
Completeness of public vulnerability data
From there, teams can take steps to strengthen resilience:
Incorporate sources of vulnerability intelligence that cover CVE and more
Align prioritization to exploitation activity and environmental relevance
Validate coverage across software, cloud, and third-party dependencies
Ensure that enrichment gaps do not delay remediation decisions
A Structural Shift in Vulnerability Data
For many teams, NVD has been a default source of vulnerability context. This change makes clear that its role is narrowing at a time when disclosure volume and prioritization demands are increasing.
At the same time, the role of vulnerability intelligence is expanding.
Security teams need access to data that supports prioritization, not just identification. They need consistent enrichment, faster turnaround, broader coverage, and context tied to real-world activity. As disclosure volumes continue to grow, those requirements become more central to how organizations manage risk.
Flashpoint’s Vulnerability Intelligence provides this level of coverage and context, with analyst-driven enrichment, global visibility across CVE and non-CVE vulnerabilities, and a dataset that includes over 7,000 known exploited vulnerabilities.
Request a demo to see how Flashpoint helps security teams prioritize and act on vulnerability risk with greater precision and confidence.
Flashpoint Surpasses Cataloging 7,000 Known Exploited Vulnerabilities as Disclosure Volume Accelerates
In this post we explore Flashpoint’s latest milestone of surpassing cataloging 7,000 known exploited vulnerabilities and what this means for security teams.
Flashpoint Vulnerability Intelligence has surpassed cataloging 7,000 known exploited vulnerabilities, surpassing another major milestone as vulnerability disclosures accelerate across the global attack surface.
In 2025, Flashpoint tracked 44,509 disclosed vulnerabilities, a pace that continues to accelerate into 2026. Of those, 14,593 had publicly available exploits (1,944 more with proof-of-concepts), giving threat actors immediate pathways to weaponization.
This pace is shaping how exploitation unfolds, with high-impact vulnerabilities being operationalized within hours or days, particularly when they affect widely deployed technologies or core infrastructure.
Security teams are operating within this compressed environment every day. They are reviewing more findings across open-source software, commercial applications, cloud environments, and third-party dependencies, while working within tighter timelines to assess impact and take action.
Flashpoint’s latest milestone of surpassing 7,000 known exploited vulnerabilities (KEVs) cataloged reflects that reality. It highlights how vulnerability management programs are evolving toward prioritization as a core capability, with a focus on vulnerabilities tied to active exploitation and real-world risk.
What The 7,000+ KEV Milestone Means for You
Security teams are operating in a high-volume environment. Vulnerabilities are disclosed continuously across open-source software, commercial applications, cloud environments, and third-party dependencies. At the same time, advancements in automation and code analysis are increasing the rate at which new findings are surfaced.
Each of these findings enters an already crowded workflow. Teams are expected to determine relevance, urgency, and impact quickly, often with limited context. This is where risk-based decision making becomes essential.
Flashpoint tracks hundreds of thousands of vulnerabilities across thousands of sources. Within that dataset, a much smaller percentage shows confirmed exploitation activity. That concentration of risk informs how effective programs allocate time and resources.
Crossing the 7,000+ KEV milestone goes beyond scale to provide greater precision, deeper context, and stronger confidence in how teams prioritize and act on the most critical vulnerabilities.
Validated threats: Each KEV entry reflects observed exploitation in the wild by threat actors, including APT groups, cybercriminal operations, ransomware presence, and automated botnets.
Exploit-aware prioritization: In reality, only a small percentage of tracked vulnerabilities drive real-world incidents. FP KEV provides visibility into that subset so teams can focus remediation efforts where they have immediate impact.
Human-curated intelligence: Every entry is reviewed, validated, and enriched by analysts, with context on exploit maturity, adversary usage, and remediation pathways when available.
This level of clarity allows teams to move faster without sacrificing accuracy. It supports vulnerability management programs that are built around real-world attacker behavior and aligned to current risk.
How Public Vulnerability Data Fits Into the Picture
Public vulnerability catalogs remain useful reference points for tracking disclosures and confirmed exploitation. The CISA Known Exploited Vulnerabilities catalog, for example, gives security teams a curated view into a limited set of vulnerabilities that have been exploited in the wild that impact U.S. government stakeholders.
For many organizations, though, that level of visibility is not enough.
Public catalogs capture only part of the picture. They tend to reflect a narrower slice of exploitation activity, with less detail on how vulnerabilities are being used, which actors are leveraging them, and what defenders should do next. They also rely heavily on CVE-based tracking, leaving gaps around non-CVE exposures and other vulnerabilities that still carry operational risk.
Flashpoint’s FP KEV and Vulnerability Intelligence provide a broader and more actionable view. The advantage is visible in both scale and depth. Of the 7,000 known exploited vulnerabilities in FP KEV, over 800 are missing from CVE. That expanded coverage is paired with the context security teams need to prioritize effectively, including exploit maturity, adversary mapping, affected product detail, and remediation guidance.
Dimension
Public KEV Catalogs
Flashpoint FP KEV
Scope
Varies by provider, with coverage dependent on available sources and methodology
Global, cross-industry coverage
Coverage
CVE-based tracking
CVE and non-CVE vulnerabilities
Context
Limited enrichment
Exploit maturity, adversary mapping, remediation
Update Model
Periodic updates
Continuously updated with analyst input
This is what separates a reference list from an operational dataset. Teams need vulnerability intelligence that supports triage, remediation, reporting, and broader risk reduction efforts. Wider visibility and deeper context make that possible.
The Critical Role of Human-Curated Intelligence
Vulnerability data originates from a wide range of sources with varying levels of completeness and accuracy.
Flashpoint’s intelligence model includes analyst validation to ensure consistency and depth across the dataset.
This process includes:
Reviewing disclosures across public and private sources
Validating exploit availability and usage
Enriching entries with technical and operational context
Analyst input supports:
Accurate classification of vulnerabilities
Clear understanding of exploitation pathways
Timely updates as activity evolves
Supporting Decision-Making Across Teams
Vulnerability intelligence feeds multiple functions across an organization. Teams use this data to align technical actions with current threat activity.
Common use cases include:
Vulnerability management: Align patching priorities with active exploitation trends.
Threat intelligence: Map vulnerabilities to threat actor campaigns and observed behaviors.
Security operations: Tune detection based on known exploit techniques.
Executive reporting: Communicate risk posture using data tied to real-world activity.
Each of these functions relies on consistent, enriched intelligence to maintain alignment.
Proactively Address Vulnerability Risk
Vulnerability discovery continues to expand across software ecosystems, infrastructure, and identity layers.
Security teams require a clear understanding of which issues are relevant to their environment at any given time.
Flashpoint provides primary source intelligence that supports this need through:
Continuous monitoring of vulnerability disclosures and exploitation
Analyst-driven validation and enrichment
Integration-ready data for operational workflows
This approach enables teams to maintain focus, allocate resources effectively, and respond to risk based on current threat activity. Request a demo and learn more today.
As organizations scale their cloud infrastructure, maintaining proper lifecycle management of Amazon Machine Images (AMIs) is a critical component of their security and risk management goals. AMIs provide the essential information required to launch Amazon Elastic Compute Cloud (Amazon EC2) instances, however; they present security and compliance challenges if not tracked and managed throughout their lifecycle. This blog post explores how organizations can meet their evolving security and compliance requirements by managing potential vulnerabilities across the AMIs deployed throughout their AWS environment.
At the end of 2024, AWS announced lineage supportfor Amazon EC2, providing source details for your AMIs. With this lineage information, you can trace copied or derived AMIs back to their original source. The source AMI information is available for AMIs that were created using specific API commands like CreateImage, CopyImage, and CreateRestoreImageTask. If the AMI was created using a different API command, the ID and AWS Region of the source AMI don’t appear, which can create visibility gaps that potentially impact security and compliance efforts.
To address these gaps and provide comprehensive AMI governance, organizations need to build additional capabilities to analyze the scope of impact of Common Vulnerabilities and Exposures (CVEs), ensure deployed resources originate from an approved golden image, and respond to audit inquiries that require a clear chain of custody for AMIs. A well-designed solution should also help track and enforce approved AMI creation patterns across all accounts and AWS Regions. The AMI lineage solution described in this post is designed to help you manage your organization’s AMI hierarchy and lifecycle, including tracking AMI origins and usage throughout its AWS environment. By implementing this solution, your security teams can quickly understand the scope of impact when security vulnerabilities are discovered, help ensure compliance with organizational policies, and maintain better visibility into their AMI estate.
The solution in this blog post uses Amazon Neptune, a high-performance graph database, along with native AWS security services to maintain a comprehensive view of AMI relationships and enable proactive security monitoring. With the solution in place, you can enforce controls on AMI sourcing, including validation of marketplace AMIs through service control policies (SCPs), and maintain compliance with organizational and regulatory requirements throughout the AMI lifecycle.
Solution overview
AMI Lineage provides a comprehensive governance solution that uses AWS security services and Neptune to create and maintain a hierarchical graph representation of their AMI relationships. This solution helps security and compliance teams understand the complete history of their AMIs including where they originated from, enforce organizational policies such as requiring all AMIs to be encrypted, and rapidly assess security impacts across their organization. The solution integrates core AWS services with security and governance capabilities. The core components of the solution in the security tooling account are:
Neptune: A purpose-built, high-performance graph database securely stores and manages the AMI relationship data.
AWS Lambdafunctions serve as the processing engine for the solution. They process AMI lifecycle events (such as CreateImage, CopyImage, DeregisterImage), evaluate them against compliance rules, and update the Neptune graph database. The functions are configured with least-privilege AWS Identity and Access Management (IAM) permissions to enhance security.
Amazon API Gateway provides secure REST endpoints for lineage queries and security assessments. Authentication is handled using a combination of API keys and IAM roles to help ensure that only authorized users and systems can access the data.
From a governance perspective, this solution provides comprehensive AMI origin validation to help ensure AMIs come from approved sources, including the validation of AWS Marketplace AMIs against a list of trusted vendors. Lifecycle management capabilities enforce AMI retention policies and deprecation processes. Compliance monitoring tracks adherence to organizational and regulatory requirements, while security event scope assessment capabilities quickly identify affected resources when security vulnerabilities are discovered. A detailed audit trail maintains a complete history of AMI creation, modification, and usage patterns.
Architecture
The AMI Lineage solution follows AWS security best practices with a multi-account deployment architecture designed to maximize security while maintaining operational efficiency. The architecture distributes responsibilities across three primary account types: an organization management account, a centralized security tooling account, and multiple member accounts.
This architectural approach helps ensure that sensitive operations and data remain centralized in the security tooling account while enabling distributed monitoring and policy enforcement across the organization. The clear separation of concerns enhances security while maintaining the scalability needed for large-scale AWS deployments.
Figure 1: AMI Lineage solution architecture and workflow
The workflow and architecture shown in figure one includes the following:
Policy enforcement: Theorganization management account is the central point for control. It uses AWS Organizations to enforce SCPs that prevent non-compliant AMI actions across the member accounts.
Event capture: When an AMI lifecycle event (like CreateImage or CopyImage) occurs in a member account, a local Amazon EventBridge rule captures it.
Centralized processing: The event is securely forwarded from the member account’s EventBridge to the central EventBridge in the security tooling account.
Data ingestion and analysis: A Lambda function is triggered in the security tooling account. This function processes the event, analyzes it for compliance, and updates the Neptune graph database with the new AMI relationship data. AWS Security Hub and Amazon GuardDuty in the security tooling account also receive and analyze findings from member accounts.
Query and visualization: Security teams query the lineage data through a secure API Gateway endpoint. By doing this, they can to visualize AMI hierarchies, investigate security findings from Security Hub, and assess the scope of impact for a given AMI.
The organization management account serves as the central control point for policy enforcement and organizational oversight. This account hosts SCPs that prevent non-approved AMI usage across the organization and manages organization-wide EventBridge rules that capture AMI events from member accounts. Cross-account trust policies configured in this account enable secure communication between the management account and the security tooling account.
Additionally, the management account establishes Security Hub in delegated administrator mode, designating the security tooling account as the centralized security administrator for the organization. From the security tooling account, Security Hub can be then configured to aggregate all Regions down to one core Region for easier evaluation by security personnel.
The security tooling account acts as the central hub for AMI lineage processing and storage. This account hosts the Neptune graph database cluster with encrypted storage, helping to ensure that AMI relationship data is securely maintained. Lambda functions running in this account process events, handle API requests, and evaluate compliance with least-privilege permissions. API Gateway provides secure REST endpoints for lineage queries and security assessments. Security Hub custom insights and findings are centralized here in the security tooling account as the Security Hub delegated administrator account, along with Amazon Simple Notification Service (Amazon SNS) topics for notifications and alerts. The Amazon Virtual Private Cloud (Amazon VPC) infrastructure supporting these services is also deployed in the security tooling account, providing network-level isolation and security.
The solution enables distributed monitoring and enforcement by deploying lightweight components into each member account across the organization. Each member account includes AWS Config rules for continuous compliance monitoring, cross-account IAM roles to enable secure access from the security tooling account, and local EventBridge rules that forward AMI-related events to the central processing system.
Security and compliance integration extends throughout the solution. IAM manages least-privilege access control and permissions across components. AWS CloudTrail records API activity for audit trails and compliance reporting, while Security Hub centralizes security findings and compliance status across your AMI estate. GuardDuty provides threat detection for AMI-related activities. SCPs enforce organization-wide controls on AMI creation and usage patterns, and AWS Config tracks AMI configuration changes and evaluates compliance rules.
How it works
The AMI Lineage solution operates through a continuous monitoring and automated response system that maintains comprehensive visibility into your AMI landscape. When AMI lifecycle events occur in your organization, EventBridge rules capture these activities, including creation, copying, modification, and deregistration events. Lambda functions in the security tooling account are then called upon to process these events with appropriate security controls and update the Neptune graph database in real-time, while CloudTrail logs provide a comprehensive audit trail of AMI-related activities.
The system tracks critical security and compliance metadata that forms the foundation of effective AMI governance. This includes:
Source AMI information and validation status to help ensure lineage integrity
Creation method and timestamp data for comprehensive audit trails
Cross-Region and cross-account relationships to understand the full scope of AMI distribution
Instance launch history with security context to track usage patterns
AMI state changes including deprecation and deregistration for lifecycle management
Compliance status along with policy violations to maintain organizational standards.
Security teams use this comprehensive data through secure API calls to visualize complete AMI hierarchies and relationships, providing clear insight into how AMIs are related across your infrastructure. The compliance of your AMI estate is continuously tracked through a combination of services:
Detection: AWS Config rules deployed in member accounts check for policy violations (for example, incorrect tags and public permissions).
Aggregation: These findings, along with vulnerability data from services like Amazon Inspector, are aggregated in AWS Security Hub.
Correlation: Lambda functions in the security tooling account correlate this information with the lineage data in Neptune. Because of this correlation, you can see not just that an AMI is non-compliant, but also its entire downstream impact. When security events like CVE findings are discovered, teams can quickly assess the scope of impact across their entire AMI estate. The solution monitors AMI usage patterns for security anomalies and enforces governance controls through automated policy checks.
The solution provides robust automated policy enforcement capabilities that operate continuously to maintain security and compliance. The system helps ensure that only approved AMIs with verified lineage history can be used to launch new instances, automatically blocking attempts to use non-compliant images. SCP controls on AMI creation and usage are enforced organization-wide, preventing unauthorized AMI operations before they can impact your environment. When policy violations are detected, the system can trigger automated responses to security events and maintain compliance with organizational standards through real-time enforcement.
Implementation
Before deploying the AMI Lineage solution, you need to establish the proper security and governance foundation across your organization. Your AWS Organizations management account requires administrative permissions, and your organization must be enabled with all features to support the policies used in this solution. You will also need a dedicated security tooling account to host the solution’s core components, with cross-account IAM roles configured to allow secure access. Finally, essential security services must be configured at the organization level, including Security Hub, CloudTrail organization trails for audit logging, and encryption keys using AWS Key Management Service (AWS KMS) for data protection.
The complete AMI Lineage solution is available as open source code in the AWS Samples repository. You can clone the repository and follow the deployment instructions. The repository includes the necessary AWS CloudFormation templates, Lambda functions, and deployment scripts referenced in the following phases.
Deployment
The deployment process follows a five-phase approach that builds security and compliance capabilities progressively:
Security foundations
Security controls
EventBridge rules
Core infrastructure
Compliance and monitoring
Phase 1 – Establishing security foundations
The first phase establishes the security foundation by configuring AWS Organizations security services. This involves enablingSecurity Hub in the management account and designating the security tooling account as the delegated administrator, enablingnullGuardDuty with the security tooling account configured as thenulldelegated administrator, and enabling an organizational wide CloudTrail trail for audit logging.
# In Organization Management Account:
# Enable Security Hub and set security tooling account as delegated admin
aws securityhub enable-organization-admin-account \
--admin-account-id <security-tooling-account-id>

# Enable GuardDuty organization with security tooling account as admin
aws guardduty enable-organization-admin-account \
--admin-account-id <security-tooling-account-id>

# Create organization trail with encryption aws cloudtrail create-trail \
--name ami-lineage-trail \
--s3-bucket-name <your-secure-bucket> \
--is-organization-trail \
--kms-key-id <your-kms-key-id> \
--enable-log-file-validation
Phase 2 – Security controls
The second phase deploys base security controls through organization-wide SCPs. These policies enforce AMI governance controls by preventing the use of non-approved AMIs and helping to ensure that proper tagging and approval workflows are followed.
The third phase deploys organization-wide EventBridge rules from the management account to capture AMI events across member accounts and forward them to the security tooling account for processing. These rules listen for specific API calls captured by CloudTrail.
An example of the event pattern used to capture CreateImage and CopyImage events looks like this:
{
	"source": ["aws.ec2"],
	"detail-type": ["AWS API Call via CloudTrail"],
	"detail": {
		"eventSource": ["ec2.amazonaws.com"],
		"eventName": [
			"CreateImage",
			"CopyImage",
			"RegisterImage",
			"DeregisterImage"
		]
	}
}

# In Organization Management Account:
# Deploy organization EventBridge rules
cd deployment-scripts/organization
./deploy-organization-resources.sh
Phase 4 – Core infrastructure
The fourth phase focuses on core infrastructure deployment in the security tooling account. This is where the primary processing and storage components are deployed, following security best practices by centralizing sensitive operations in a dedicated account.
# Switch to Security Tooling Account context
# Deploy Neptune cluster with encryption in security tooling account
cd deployment-scripts/shared
./deploy-shared-resources.sh
This deployment script handles multiple components in the security tooling account. The Neptune cluster deployment includes encryption and VPC configuration to help ensure secure storage and access to AMI lineage data. Lambda functions are deployed with security controls and configured with VPC attachment, which allows for secure Neptune access in the VPC, appropriate IAM roles with least-privilege permissions, and environment variables for secure configuration. API Gateway provides secure REST endpoints for external access to AMI lineage data and security assessments.
Phase 5 – Compliance and monitoring
The fifth phase establishes comprehensive compliance and monitoring capabilities across member accounts. AWS Config rules are deployed to continuously monitor AMI compliance across your organization, while EventBridge rules forward AMI events to the central processing system.
# In each Member Account:
# Deploy AWS Config Rules and monitoring capabilities
cd deployment-scripts/child-account
./deploy-child-account-resources.sh
After deployment, thorough verification helps ensure that security configurations are properly implemented. This includes validating IAM permissions to help ensure least-privilege access, testing security controls to verify SCP enforcement, validating encryption settings acrosscomponents, and confirming that the security tooling account is properly configured as the Security Hub delegated administrator.
Using AMI Lineage
When deployed, AMI Lineage provides security operations and compliance monitoring capabilities through its API hosted in the security tooling account and automated monitoring systems. Security teams can query and receive complete AMI security relationships to understand the full context of AMIs in their environment.
When investigating AMIs, the system provides detailed security context including source validation information that confirms:
Whether AMIs come from marketplace sources or trusted accounts
Compliance status that shows patch levels and policy adherence
Vulnerability status with CVE findings and scan results
Comprehensive lineage data showing the complete chain of AMI relationships and approval history
# Get complete security context for an AMI (API Gateway in Security Tooling Account)
curl -X GET "https://<api-gateway-id>.execute-api.<region>.amazonaws.com/v1/api/v1/ami/ami-1234567890abcdef0/security-context?include_compliance=true" \
	-H "x-api-key: <your-api-key>"
For security impact assessments, such as when a new CVE is discovered, the solution provides a powerful scope of impact analysis. By querying the API with a specific finding, security teams can rapidly determine every affected resource across their entire organization that stems from a compromised or vulnerable AMI. Using that information, they can understand the full scope of their exposure and begin remediation. See Security best practices in Amazon API Gateway for helpful considerations while using API Keys.
This analysis returns impact information including:
Affected AMIs in the lineage chain
Running instances requiring immediate remediation
Affected AWS accounts and regions for coordinated response
Associated auto-scaling groups and launch templates that need updates
Compliance impact assessment for regulatory reporting
Detailed remediation steps prioritized by risk level.
Compliance monitoring operates continuously through automated assessment capabilities that evaluate your AMI estate against organizational policies and regulatory requirements. Teams can generate comprehensive compliance reports that show adherence to security standards across their entire infrastructure.
The solution provides security automation and remediation through configurable automated responses to security events. Security Hub, operating in delegated administrator mode from the security tooling account, can be configured to automatically respond to findings by stopping instances using AMIs with critical vulnerabilities, quarantining instances launched from unapproved sources, and sending immediate notifications for high-severity findings.
Security visualization and reporting capabilities, centralized in the security tooling account, provide real-time dashboards showing:
Compliance status across the organization
Scoping visualization for rapid decision-making
AMI approval workflow status for process monitoring
Patch compliance metrics for maintaining security posture
Automated remediation activity logs for audit purposes
Custom security reports tailored to specific organizational needs.
For security investigations and audit purposes, the solution maintains a queryable audit trail that provides a complete history of AMIs, including creation and modification events, security scanning results and findings, approval workflow history, and compliance status changes over time.
# Query comprehensive audit history (Security Tooling Account API)
curl -X GET "https://<api-gateway-id>.execute-api.<region>.amazonaws.com/v1/api/v1/ami/ami-1234567890abcdef0/lineage?direction=both&depth=10" \
	-H "x-api-key: <your-api-key>"
Clean up
To decommission the AMI Lineage solution, use the following steps to prevent dependency errors. The process is the reverse of the deployment.
(Optional) Back up your data. Before you begin, export critical data for your audit and compliance records. This includes generating final compliance reports from the API or creating a final snapshot of the Neptune database (you will be prompted to do this when you delete the cluster).
Run cleanup in member accounts. Sign in to each participating member account and run the cleanup script from the deployment files. This removes the local EventBridge rules, AWS Config rules, and cross-account IAM roles.
# In each Member Account
cd deployment-scripts/child-account
./cleanup-child-account-resources.sh
# Removes Config rules and cross-account roles from each member account
Run cleanup in the security tooling account. Sign in to your security tooling account and run the cleanup script. This decommissions the core solution, including the API gateway, Lambda functions, Neptune cluster, and the associated VPC.
# Clean up security tooling account
cd deployment-scripts/shared

./cleanup-shared-resources.sh
# Removes Neptune, Lambda, API Gateway, SNS, and Security Hub components
Run cleanup in the organization management account. Sign in to your organization management account to remove the organization-level resources.
Run the cleanup script to remove the organization-wide EventBridge rules.
# Clean up organization management account

cd deployment-scripts/organization

./cleanup-organization-resources.sh
# Removes SCPs, EventBridge rules, and cross-account trust policies
In the AWS Organizations console, detach and delete the AMI-Governance-Controls SCP.
In the Security Hub and GuardDuty consoles, remove the security tooling account as the delegated administrator.
Delete final data and encryption keys. After the solution’s infrastructure is removed, you can delete the remaining assets.
In the organization management account,schedule the deletion of the KMS keys you created for encrypting the solution’s data.
Conclusion
In this blog post, we showed you how you can use the AMI Lineage solution to build a comprehensive approach to tracking the complete history of your AMIs from creation to decommissioning. By storing this data in an Amazon Neptune graph database, you can build a hierarchical view of the relationships between your EC2 instances and the AMIs they were launched from. You learned how that data can be used to improve security response and remediation and assist in auditing and compliance activities.
The solution uses AWS Organizations to provide preventative controls to help ensure that only approved AMIs are used and integrates AWS security services like Amazon GuardDuty, AWS Security Hub, and AWS Config to add additional layers of security monitoring and management. Finally, you saw how the solution can be used during a security event or when new CVEs are published, so that you can rapidly discover which systems are affected and automate responses based on those findings.
While this solution provides powerful capabilities, it’s important to consider the operational and cost aspects. The core components, particularly Neptune, have associated costs that will scale with the size of your AMI estate. We recommend implementing cost monitoring and alerts as part of your deployment. Furthermore, because the solution is event-driven, you should plan a one-time backfill process to ingest your organization’s existing AMI history into the graph database. For organizations that require this level of granular control and visibility, these operational considerations are offset by the significant gains in security posture and compliance automation.
AMI Lineage transforms AMI governance from a manual, error-prone process into an automated, comprehensive security capability that scales with your organization’s growth. By implementing this solution, your organization can gain the visibility, control, and automated response capabilities needed to maintain a strong security posture while enabling rapid, secure deployment of infrastructure across its AWS environment.
If you have feedback about this post, submit comments in the Comments section below. If you have questions about this post, contact AWS Support.
Navigating 2026’s Converged Threats: Insights from Flashpoint’s Global Threat Intelligence Report
In this post, we preview the critical findings of the 2026 Global Threat Intelligence Report, highlighting how the collapse of traditional security silos and the rise of autonomous, machine-speed attacks are forcing a total reimagining of modern defense.
The cybersecurity landscape has reached a point of total convergence, where the silos that once separated malware, identity, and infrastructure have collapsed into a single, high-velocity threat engine. Simultaneously, the threat landscape is shifting from human-led attacks to machine-speed operations as a result of agentic AI, which acts as a force multiplier for the modern adversary.
Flashpoint’s 2026 Global Threat Intelligence Report
Our report uncovers several staggering metrics that illustrate the industrialization of modern cybercrime:
AI-related illicit activity skyrocketed by 1,500% in a single month at the end of 2025.
3.3 billion compromised credentials and cloud tokens have turned identity into the primary exploit vector.
From January 2025 to December 2025, ransomware incidents rose by 53%, as attackers pivot from technical encryption to “pure-play” identity extortion.
Vulnerability disclosures surged by 12% from January 2025 to December 2025, with the window between discovery and mass exploitation effectively vanishing.
These findings are derived from Flashpoint’s Primary Source Collection (PSC), a specialized operating model that collects intelligence directly from original sources, driven by an organization’s unique Priority Intelligence Requirements (PIR). The 2026 Global Threat Intelligence Report leverages this ground-truth data to provide a strategic framework for the year ahead. Download to gain:
A Clear Understanding of the New Convergence Between Identity and AI Discover how threat actors are preparing to transition from generative tools to sophisticated agentic frameworks. Learn how 3.3 billion compromised credentials are being weaponized via automated orchestration to bypass legacy defenses and exploit the connective tissue of modern corporate APIs.
Intelligence on the “Franchise Model” of Global Extortion Gain deep insight into the professionalized operations of today’s most prolific threat actors. From the industrial efficiency of RaaS groups like RansomHub and Clop to the market dominance of the next generation of infostealer malware, we break down the economics driving today’s cybercrime ecosystem.
A Blueprint for Proactive Defense and Risk Mitigation Leverage the latest trends, in-depth analysis, and data-driven insights driven by Primary Source Collection to bolster your security posture by identifying and proactively defending against rising attack vectors.
“As attackers automate exploitation of identity, vulnerabilities, and ransomware, defenders who rely on fragmented visibility will fall behind. To keep pace, organizations must ground their decisions in primary-source intelligence that is drawn from adversarial environments, so that decision-makers can get ahead of this accelerating threat cycle.”
Josh Lefkowitz, CEO & Co-Founder at Flashpoint
The Top Threats at a Glance
Our latest report identifies four driving themes shaping the 2026 threat landscape:
2026 Is the Era of Agentic-Based Cyberattacks
Flashpoint identified a 1,500% rise in AI-related illicit discussions between November and December 2025, signaling a rapid transition from criminal curiosity to the active development of malicious frameworks. Built on data pulled from criminal environments and shaped by fraud use cases, these systems scrape data, adjust messaging for specific targets, rotate infrastructure, and learn from failed attempts without the need for constant human involvement.
“2026 is the era of agentic-based cyberattacks. We’ve seen a 1,500% increase in AI-related illicit discussions in a single month, signaling increased interest in developing malicious frameworks. The discussions evolve into vibe-coded, AI-supported phishing lures, malware, and cybercrime venues. When iteration becomes cheap through automation, attackers can afford to fail repeatedly until they find a successful foothold.”
Ian Gray, Vice President of Cyber Threat Intelligence Operations at Flashpoint
Identity Is the New Exploit
Flashpoint observed over 11.1 million machines infected with infostealers in 2025, fueling a massive inventory of 3.3 billion stolen credentials and cloud tokens. The fundamental mechanics of cybercrime have shifted from breaking in to logging in, as attackers leverage stolen session cookies to behave like legitimate users.
The Patching Window Is Rapidly Closing
Vulnerability disclosures surged by 12% in 2025, with 1 in 3 (33%) vulnerabilities having publicly available exploit code. The strategic gap between discovery and weaponization is increasingly vanishing, as evidenced by mass exploitation of zero-day vulnerabilities in as little as 24 hours after discovery.
Ransomware Is Hacking the Person, Not the Code
As technical defenses against encryption harden, ransomware groups are pivoting to the path of least resistance: human trust. This approach has led to a 53% increase in ransomware, with RaaS groups being responsible for over 87% of all ransomware attacks.
Build Resilience in a Converged Landscape
The findings in the 2026 Global Threat Intelligence Report make one thing clear: incremental improvements to legacy security models are no longer sufficient. As adversaries transition to machine-speed operations, the strategic advantage shifts to organizations that can maintain visibility into the adversarial environments where these attacks are born.
Protecting organizations and communities requires an intelligence-first approach. Download Flashpoint’s 2026 Global Threat Intelligence Report to gain clarity and the data-driven insights needed to safeguard critical assets.
The cybersecurity community is still grappling with a sobering realization: one of the most ubiquitous tools in the developer’s toolkit, Notepad++, was hiding a critical vulnerability for over six months. Being so deeply embedded in daily workflows, many organizations did not realize they were vulnerable until a recent security update pulled back the curtain on a sophisticated Chinese state-sponsored campaign, dubbed “Lotus Blossom.”
Investigations have confirmed that the issue wasn’t just a coding error, it was a compromise at the hosting provider level. This means that for much of 2025, even organizations that followed best practices were still potentially open to backdoors from Chinese advanced persistent threat (APT) groups. Here is what you need to know to secure your environment.
Understanding the Notepad++ Vulnerability (CVE-2025-15556)
The vulnerability, tracked as CVE-2025-15556 (VulnDB ID: 430205), exploits a critical flaw in the Notepad++ updater component, WinGUP. In versions prior to the February 2026 patch, the updater failed to verify the file integrity signatures of downloaded installers.
By exploiting this lack of verification, threat actors are able to:
Intercept legitimate update requests originating from WinGUp servers
Redirect traffic to malicious servers via Man-in-the-Middle (MitM) attacks or DNS cache poisoning
Deliver trojanized executables (disguised as update.exe) that appeared to be legitimate software patches
Leveraging this vulnerability, attackers have gained a persistent presence in high-value sectors. According to reports from Kaspersky, the impact has spanned government and telecommunications, critical infrastructure, and financial services.
How CVE-2025-15556 Works
The state-sponsored Lotus Blossom campaign was executed in three attack chains, between July and October 2025. Each phase evolved to evade detection by changing file sizes, IP addresses, and delivery methods.
Phase
Timeline (2025)
Execution Method
Payload
Chain #1
July – August
1MB NSIS installer (update.exe)
Multi-stage attack launching a Cobalt Strike beacon via ProShow.exe.
Chain #2
September
140KB NSIS installer (update.exe)
Rotated C2 URLs to maintain stealth while dropping a Cobalt Strike beacon.
Chain #3
October
Backdoor Deployment
Dropped BluetoothService.exe, log.DLL, and shellcode to establish the Chrysalis backdoor.
Mapping CVE-2025-15556 to MITRE ATT&CK
Flashpoint has mapped Lotus Blossom TTPs (tactics, tools, and procedures) to the MITRE ATT&CK framework. Flashpoint analysts have identified the following techniques:
M1057: Data Loss Prevention M1031: Network Intrusion Prevention
Protecting Against CVE-2025-15556
Proactive defense requires not only reactive patching of CVE-2025-15556, but also active threat hunting using the TTPs identified by Flashpoint analysts. Flashpoint recommends the following actions:
Immediate Update: Ensure all instances of Notepad ++ are updated to v8.9.1 or higher immediately. This version enforces the signature verification that was missing in previous releases.
Audit System Paths: Scan for malicious file paths used for persistence.
Network Defense: Monitor and block traffic to malicious domains.
Endpoint Hardening: Implement Behavior Prevention on Endpoints (M1040) and Audit (M1047) to detect unauthorized registry run keys or new system services.
Outpace Threat Actors Using Flashpoint
Software trust is only as strong as the infrastructure behind it. As organizations respond to these recent updates, having best-in-class vulnerability intelligence and direct visibility into threat actor TTPs is the best defense.

 Login


 Table Of Contents