 Login

Alleged ShinyHunters Leader Arrested in Jordan
Known as Rey, the suspect is reportedly helping the FBI identify and locate other members of the extortion group.
The post Alleged ShinyHunters Leader Arrested in Jordan appeared first on SecurityWeek.

Known as Rey, the suspect is reportedly helping the FBI identify and locate other members of the extortion group.
The post Alleged ShinyHunters Leader Arrested in Jordan appeared first on SecurityWeek.
Pepijn van der Stap was convicted in 2023 for hacking multiple organizations, stealing their data, and extorting them.
The post Dutch Police Arrest Convicted Hacker in ShinyHunters Investigation appeared first on SecurityWeek.
BBC News reports it has seen samples of stolen FBI agents’ medical examinations. The “fitness-for-work” reports identify FBI agents by name and address, and reveal even more personal details. They include blood and urine test results and doctors’ notes mentioning high cholesterol, blood in the urine, and even a shellfish and banana allergy.
As we reported last week, extortion group ShinyHunters claims to have breached the FBI. After reportedly taking over ransomware group Clop’s leak site, ShinyHunters says it attacked the FBI to punish the agency for spreading what it calls false information about the group.
The BBC’s findings raise the stakes: The alleged theft includes highly sensitive medical records, not just staff identity and contact data. ShinyHunters shared samples with journalists as proof of its claims.
The BBC states:
“The samples shared with journalists appear genuine and include names, addresses, phone numbers, badge numbers, job titles and information about spouses.”
ShinyHunters claims it accessed several systems, including FBI MedLink, which stores medical records, and FBI BEAST, which handles background checks on employees and applicants, but the FBI has not confirmed these claims. The FBI has acknowledged an incident affecting FBIJobs-related systems and says it is investigating whether its own environment or a third-party provider was compromised.
The group’s stated demand remains non-financial: It wants the FBI to retract or remove a May advisory that ShinyHunters calls false and defamatory. It says it will release the data within five days if its demands are not met.
The cybercriminals also raised the number of affected people. ShinyHunters nows claims to hold sensitive information on around 60,000 current and former FBI staff. Medical histories could make affected people vulnerable long after the immediate incident: Unlike a stolen password, a medical record cannot be changed.
The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
Last week on Malwarebytes Labs:
Stay safe!
From reporting threats to removing them.
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
Extortion group ShinyHunters is not afraid to make enemies. Now it claims to have breached the FBI.
After reportedly taking over ransomware group Clop’s leak site, ShinyHunters says it attacked the FBI to punish the agency for spreading what it calls false information about the group.
In a very long post on its leak site, the group outlines its grievances:
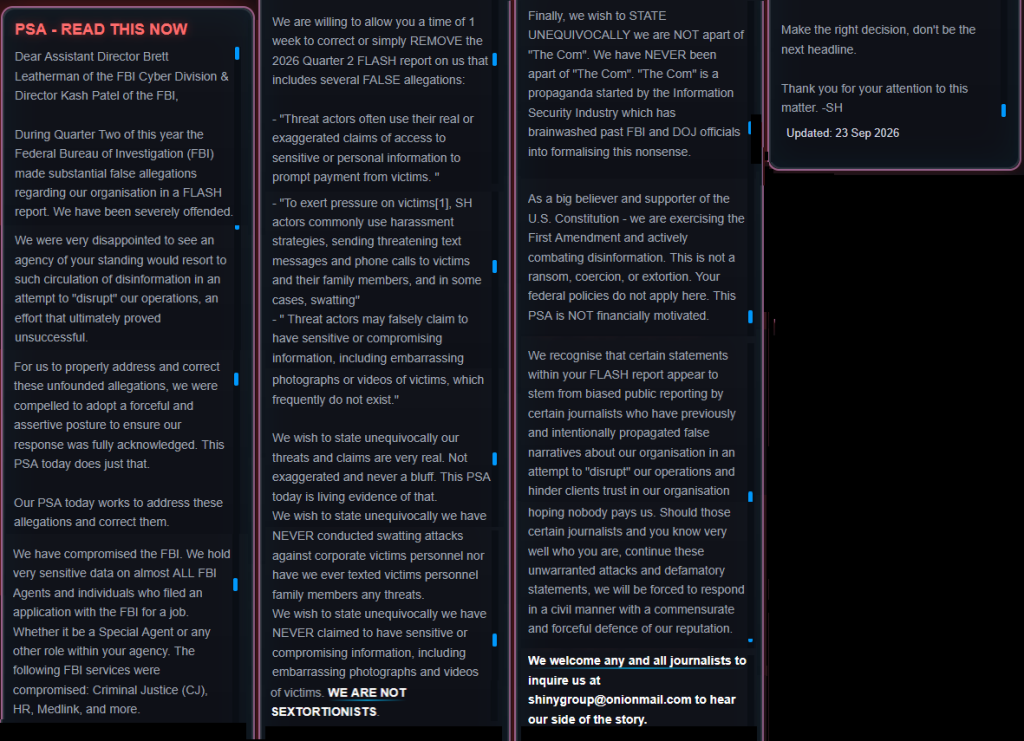
“PSA – READ THIS NOW
Dear Assistant Director Brett Leatherman of the FBI Cyber Division & Director Kash Patel of the FBI,
During Quarter Two of this year the Federal Bureau of Investigation (FBI) made substantial false allegations regarding our organisation in a FLASH report. We have been severely offended.
We were very disappointed to see an agency of your standing would resort to such circulation of disinformation in an attempt to “disrupt” our operations, an effort that ultimately proved unsuccessful.
For us to properly address and correct these unfounded allegations, we were compelled to adopt a forceful and assertive posture to ensure our response was fully acknowledged. This PSA today does just that.
Our PSA today works to address these allegations and correct them.
We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job. Whether it be a Special Agent or any other role within your agency. The following FBI services were compromised: Criminal Justice (CJ), HR, Medlink, and more.
We are willing to allow you a time of 1 week to correct or simply REMOVE the 2026 Quarter 2 FLASH report on us that includes several FALSE allegations:
- “Threat actors often use their real or exaggerated claims of access to sensitive or personal information to prompt payment from victims.”
- “To exert pressure on victims[1], SH actors commonly use harassment strategies, sending threatening text messages and phone calls to victims and their family members, and in some cases, swatting”
- “Threat actors may falsely claim to have sensitive or compromising information, including embarrassing photographs or videos of victims, which frequently do not exist.”
We wish to state unequivocally our threats and claims are very real. Not exaggerated and never a bluff. This PSA today is living evidence of that.
We wish to state unequivocally we have NEVER conducted swatting attacks against corporate victims personnel nor have we ever texted victims personnel family members any threats.
We wish to state unequivocally we have NEVER claimed to have sensitive or compromising information, including embarrassing photographs and videos of victims. WE ARE NOT SEXTORTIONISTS.
Finally, we wish to STATE UNEQUIVOCALLY we are NOT apart of “The Com”. We have NEVER been apart of “The Com”. “The Com” is a propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalising this nonsense.
As a big believer and supporter of the U.S. Constitution – we are exercising the First Amendment and actively combating disinformation. This is not a ransom, coercion, or extortion. Your federal policies do not apply here. This PSA is NOT financially motivated.
We recognise that certain statements within your FLASH report appear to stem from biased public reporting by certain journalists who have previously and intentionally propagated false narratives about our organisation in an attempt to “disrupt” our operations and hinder clients trust in our organisation hoping nobody pays us. Should those certain journalists and you know very well who you are, continue these unwarranted attacks and defamatory statements, we will be forced to respond in a civil manner with a commensurate and forceful defence of our reputation.
We welcome any and all journalists to inquire us at shinygroup@onionmail[.]com to hear our side of the story.
Make the right decision, don’t be the next headline.
Thank you for your attention to this matter. -SH
Updated: 23 Sep 2026“
The post is essentially a hostile “correction notice” directed at FBI leaders Brett Leatherman and Kash Patel. Its central grievance is an FBI advisory that says ShinyHunters commonly harasses victims and their families, including through threatening messages, phone calls, and, in some cases, swatting.
It also warns that threat actors may exaggerate their access to personal information or falsely claim to possess compromising photos or videos. The advisory does not use the word “sextortion,” but ShinyHunters appears to have interpreted the reference to compromising material that way. The group denies much of the FBI’s account while simultaneously using coercive language of its own.
The document it appears to mean is the FBI/IC3 public advisory “ShinyHunters: Cyber Criminal Group Attacks Learning Management System,” issued on May 15, 2026. Despite ShinyHunters calling it a “2026 Quarter 2 FLASH report,” the publicly accessible document is labeled a Public Service Announcement (PSA), not a FLASH.
The picture may have been further confused by a sextortionist who pretended to be ShinyHunters. ShinyHunters declares:
“WE ARE NOT SEXTORTIONISTS.”
It also denies carrying out swatting attacks or sending threatening messages to the family members of people working for its corporate victims.
The group also denies being part of The Com, a decentralized network linked to cybercrime and violence. It calls that connection:
“propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalizing this nonsense.”
The group then threatens journalists it accuses of spreading these “false narratives.”
The most worrying part of the message is the group’s claim that it stole sensitive data on:
“almost ALL FBI Agents, and individuals who filed an application with the FBI for a job.”
According to 404 Media, ShinyHunters provided a sample containing information on roughly 5,000 FBI agents, including names, home addresses, phone numbers, and details about their spouses. The publication reportedly verified portions of the sample, but the full dataset and the wider claims about the breach have not been independently confirmed.
The group also reportedly defaced the FBI’s jobs website. The FBI says it is aware of claims involving unauthorized activity affecting FBIjobs.gov and is investigating, although “broken” does not necessarily mean “breached.”
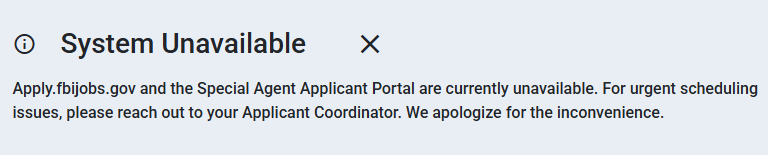
The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
Authorities in the Netherlands have arrested a 24-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions by the prolific hacker group ShinyHunters. In the days immediately following the suspect’s arrest, remaining ShinyHunters members dramatically escalated their attacks, stealing highly sensitive data from the FBI and extorting the Russian ransomware group Cl0p.
According to three sources familiar with the matter, the Dutch man arrested by authorities this month is Pepijn van der Stap, a convicted cybercriminal from Almere and Lelystad in the Netherlands. Van der Stap was previously convicted in 2023 in connection with a string of data thefts and extortions that prosecutors said earned between €1.5 million and €2.7 million.
At his trial in late 2023, van der Stap admitted that he lived a Dr. Jekyll and Mr. Hyde existence, secretly using the hacker handle “Umbreon” to extort victims and post their data on English language hacking communities like the now-defunct RaidForums and Breached. By day, however, van der Stap was working as a software engineer at the Amsterdam-based cybersecurity startup Hadrian, while volunteering at the Dutch Institute for Vulnerability Disclosure (DIVD), a nonprofit security research group.

Pepijn van der Stap’s alter ego “Umbreon” selling a database on RaidForums, offering information on 2.3 million people from The Netherlands in September 2021. This user’s avatar is a depiction of the Pokemon character Umbreon. Image: KELA.
Van der Stap confessed to his data theft and extortion activity, and was sentenced to four years in prison (one of which was suspended). During his trial, van der Stap opted to remain in custody for a time rather than at home, saying he could not find better treatment on the outside for his ongoing psychological issues, which he claimed included PTSD related to childhood trauma. He was released from prison in December 2025.
In an interview with KrebsOnSecurity on September 9, 2026, Van der Stap cast himself as a reformed hacker who was trying to turn his life around and make a positive contribution to society. Van der Stap is currently employed as offensive security lead at the Dutch company Neo Security, which did not respond to requests for comment.
Van der Stap said he was still dealing with civil lawsuits and restitution related to his previous cybercrime victims, and that he was trying his best to make amends. But not long after that interview, the Dutch hacker abruptly stopped replying to messages. Efforts by others close to him also repeatedly failed to elicit a response for the past two weeks.

The LinkedIn profile for Pepijn van der Stap.
According to two sources with knowledge of the matter, Van der Stap was arrested by Dutch authorities on or around September 16, and has been held in custody for questioning since. One source said a colleague of theirs personally witnessed Dutch authorities carting items out of Van der Stap’s residence.
Authorities in the Netherlands have been asking the public for help in identifying the voice in a recorded telephone call from February 2026 in which a native Dutch-speaking ShinyHunters member social engineered their way into Odido, the nation’s largest mobile telecommunications provider. In that intrusion, ShinyHunters tricked an Odido employee into logging in at a spoofed website, and then used that access to steal data on more than 6.2 million Dutch people.
Responding to Dutch news media, ShinyHunters confirmed that the suspect in the audio clip is indeed a member of the hacker collective.
“Our team member has our full support – emotionally, mentally, and financially,” the hackers said. “Everything has been arranged, including a criminal defense lawyer. We do not look down on our staff and members; we take excellent care of them,” reads a statement ShinyHunters shared with NL Times. It remains unclear if the Dutch police have matched the Odido caller to a confirmed real-life identity. The Dutch police unit handling the Odido incident did not respond to requests for comment.
The group also lashed out at the authorities in the Netherlands. “The Dutch police will need all the luck in the world – and everyone’s prayers – if they want to catch him before we carry out another large-scale data theft in the Netherlands,” the ShinyHunters statement said. “Frankly, the Dutch police are a big joke; they are incapable of doing anything. Incompetent. Irrelevant. Unimportant. Useless.”
Just days after sources say Van der Stap was detained by Dutch authorities, ShinyHunters claimed credit for an unusually brazen breach at the FBI’s job application site apply.fbijobs.gov. According to reporting from 404 Media, the data stolen from the FBI site includes Social Security numbers and personal information on more than 5,000 officials.
404 Media and Reuters reported the FBI data included each person’s job title or team, such as special agent, threat intake examiner, major cybercrimes unit, and those investigating cyber threats from foreign state-backed actors. Reuters examined documents shared by ShinyHunters and found they included sensitive psychiatric and medical files of FBI staff. The FBI issued a brief statement confirming the hack.
ShinyHunters said it gained access to the FBI site and other victims by exploiting a recently patched vulnerability (CVE-2026-35273) in PeopleSoft, a software-as-a-service platform from the software giant Oracle that is broadly used by companies to manage hiring and human resources, benefits and payroll. Oracle quickly issued a fix for the Peoplesoft vulnerability that ShinyHunters reportedly began exploiting as a zero-day in June, and at the time Mandiant released web application firewall rules intended for organizations who couldn’t apply the security update quickly enough.
But on Friday, BleepingComputer reported that ShinyHunters used a URL-encoding trick to bypass Mandiant’s suggested web application firewall rules designed to mitigate the threat from the PeopleSoft flaw. In a report released Sept. 25, security experts at Mandiant and the Google Threat Intelligence Group (GTIG) confirmed that ShinyHunters had mass-exploited the PeopleSoft vulnerability to steal data from dozens of systems across a range of industries, including higher education, technology, healthcare, agriculture, transportation and government.
Van der Stap’s former hacker alias Umbreon was hidden in plain sight throughout the imagery ShinyHunters used to spread news about the FBI hack: The defacement image that ShinyHunters left behind on the hacked FBI jobs site included an ASCII art design featuring the Pokemon character Umbreon. The message at the top read, “This site has been seized by ShinyHunters. rooting your systems since ’19 ;)” The image appears identical to a defacement message ShinyHunters used in their 2020 hack of the English-language cybercrime community Hackforums.

The defacement message left by ShinyHunters on the FBI jobs site included an ASCII art rendition of the Pokemon character Umbreon. Image: Bleeping Computer.
Multiple sources close to the ShinyHunters investigation said the group’s recent risky attacks against the FBI and one of Russia’s most venerated ransomware groups amounted to a major pivot away from the more measured tenor of the hacking gang’s operations. Those sources said the sudden shift came about after ShinyHunters was taken over by a teenage cybercriminal from Amman, Jordan who goes by the nickname Rey and operates as part of a cybercrime group called ScatteredLapsussHunters (SLSH), which experts say is an amalgamation of three hacking groups — Scattered Spider, LAPSUS$ and ShinyHunters.
Those sources said Rey had an ongoing beef with the Dutch hacker over control of the ShinyHunters brand and data, and that the inclusion of the oversized Umbreon Pokemon image in the FBI jobs site defacement was likely an attempt by Rey to pin the hack on the Dutchman.
Rey was first publicly identified by the cybersecurity firm KELA in March 2025. In advance of our November 2025 profile of Rey, KrebsOnSecurity messaged Rey’s father and asked for permission to interview his teenage son. Rey’s dad merely forwarded the message to his son, who admitted to participating in ransomware attacks and said he was trying to extricate himself from the SLSH hacker group.
Immediately after news of the FBI jobs site hack was picked up in the media, Rey’s main account on Twitter/X (Ryan Moran/@rmoskovy) was taunting the Cl0p ransomware group and the FBI, crudely depicting them as the twin towers in New York being struck by planes labeled “cl0p drama” and “fbi breach claim.” In the foreground of the city is the giant Pokemon figure of Umbreon.

A taunting meme uploaded to Twitter/X by Rey’s now-defunct account on Sept. 22. A giant float-sized version of the Pokemon character Umbreon can be seen in the bottom left.
On Sept. 24, KrebsOnSecurity again contacted Rey’s dad, asking to interview him and his son for a story on Rey’s apparent ascendency as the head of ShinyHunters. Just hours after that request, Rey deleted his longtime Twitter/X account. Meanwhile, Rey’s dad, who works for the Royal Jordanian Airlines, has failed to respond to a half-dozen emailed requests for comment about his son’s alleged activities.
Where does the bad blood between SLSH and ShinyHunters come from? According to a story in Wired this month, ShinyHunters and SLSH members briefly partnered earlier this year to help better monetize important stolen credentials collected by TeamPCP, an upstart group that was having great success compromising global code supply chains with malicious software but hadn’t been able to profit much from their stolen data (two alleged leaders of TeamPCP were arrested last month in Australia, and in an interview the TeamPCP leader claimed they made just $20,000).
The Wired story noted how Mandiant had infiltrated TeamPCP and was secretly responsible for having the crime group’s stolen credentials burned so quickly: Mandiant was secretly feeding those credentials to the major cloud providers like Amazon and Microsoft, who quickly invalidated the stolen keys. Meanwhile, the formerly cooperating hacker groups began to blame one another for causing the credentials to become worthless.
Wired’s Andy Greenberg reported that a few weeks after partnering with TeamPCP, “ShinyHunters went rogue, carrying out its own extortions with TeamPCP’s credentials but without giving the supply-chain hackers their cut.”
Mandiant researcher Austin Larsen told KrebsOnSecurity earlier this month that ShinyHunters has been enjoying a successful extortion spree so far this year, and is on track to pull in nearly $100 million in extortion payments from cybercrime victims in 2026.
Van der Stap claims he was never motivated by money and that his earlier hacker activity was driven by a desire to have the world’s most complete collection of stolen databases. Speaking with reporters from Bloomberg in 2024, Van der Stap said that singular focus in turn fueled his desire to carry out cyberattacks.
“The hacking was very easy for me, and it wasn’t a compulsion,” he told Bloomberg. “My habit was collecting. Collecting data, organizing data, downloading data, creating folders.”
DIVD, the nonprofit security research group where Van der Stap previously served as a volunteer, disclosed on LinkedIn last week that the organization was dealing with an internal cybersecurity incident that appears to have involved the malicious use of artificial intelligence. DIVD has released few details about that incident, but a spokesperson for the nonprofit told KrebsOnSecurity it does not appear related to ShinyHunters, nor are there any signs the matter involves the work of a previous volunteer.
Update: 3:44 p.m. ET: Corrected Van der Stap’s age, which is 24 (not 23).
Update, 4:54 p.m. ET: The Dutch police have confirmed the arrest of a 24-year-old in connection with the ShinyHunters investigation. In a statement on Twitter/X, the Dutch police said the man will appear on Tuesday, September 29 before the chambers of the Rotterdam District Court, and that it will provide more information tomorrow.
Sept. 29, 9:42 a.m. ET: The Dutch news outlet RTL reports that investigators suspect Van der Stap tried to orchestrate at least two murders. RTL reported the two murders were allegedly to be committed abroad, and that there are indications the suspect gave the order for this.
The FBI released a short video message on the ShinyHunters investigation from Brett Leatherman, assistant director of the FBI’s cyber division, who thanked Dutch law enforcement partners for their assistance and urged remaining ShinyHunters members to turn themselves in.
“Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left,” Leatherman said. “The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out to us while the choice is still yours.”
BBC News reports it has seen samples of stolen FBI agents’ medical examinations. The “fitness-for-work” reports identify FBI agents by name and address, and reveal even more personal details. They include blood and urine test results and doctors’ notes mentioning high cholesterol, blood in the urine, and even a shellfish and banana allergy.
As we reported last week, extortion group ShinyHunters claims to have breached the FBI. After reportedly taking over ransomware group Clop’s leak site, ShinyHunters says it attacked the FBI to punish the agency for spreading what it calls false information about the group.
The BBC’s findings raise the stakes: The alleged theft includes highly sensitive medical records, not just staff identity and contact data. ShinyHunters shared samples with journalists as proof of its claims.
The BBC states:
“The samples shared with journalists appear genuine and include names, addresses, phone numbers, badge numbers, job titles and information about spouses.”
ShinyHunters claims it accessed several systems, including FBI MedLink, which stores medical records, and FBI BEAST, which handles background checks on employees and applicants, but the FBI has not confirmed these claims. The FBI has acknowledged an incident affecting FBIJobs-related systems and says it is investigating whether its own environment or a third-party provider was compromised.
The group’s stated demand remains non-financial: It wants the FBI to retract or remove a May advisory that ShinyHunters calls false and defamatory. It says it will release the data within five days if its demands are not met.
The cybercriminals also raised the number of affected people. ShinyHunters nows claims to hold sensitive information on around 60,000 current and former FBI staff. Medical histories could make affected people vulnerable long after the immediate incident: Unlike a stolen password, a medical record cannot be changed.
The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
Last week on Malwarebytes Labs:
Stay safe!
From reporting threats to removing them.
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
Extortion group ShinyHunters is not afraid to make enemies. Now it claims to have breached the FBI.
After reportedly taking over ransomware group Clop’s leak site, ShinyHunters says it attacked the FBI to punish the agency for spreading what it calls false information about the group.
In a very long post on its leak site, the group outlines its grievances:
“PSA – READ THIS NOW
Dear Assistant Director Brett Leatherman of the FBI Cyber Division & Director Kash Patel of the FBI,
During Quarter Two of this year the Federal Bureau of Investigation (FBI) made substantial false allegations regarding our organisation in a FLASH report. We have been severely offended.
We were very disappointed to see an agency of your standing would resort to such circulation of disinformation in an attempt to “disrupt” our operations, an effort that ultimately proved unsuccessful.
For us to properly address and correct these unfounded allegations, we were compelled to adopt a forceful and assertive posture to ensure our response was fully acknowledged. This PSA today does just that.
Our PSA today works to address these allegations and correct them.
We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job. Whether it be a Special Agent or any other role within your agency. The following FBI services were compromised: Criminal Justice (CJ), HR, Medlink, and more.
We are willing to allow you a time of 1 week to correct or simply REMOVE the 2026 Quarter 2 FLASH report on us that includes several FALSE allegations:
- “Threat actors often use their real or exaggerated claims of access to sensitive or personal information to prompt payment from victims.”
- “To exert pressure on victims[1], SH actors commonly use harassment strategies, sending threatening text messages and phone calls to victims and their family members, and in some cases, swatting”
- “Threat actors may falsely claim to have sensitive or compromising information, including embarrassing photographs or videos of victims, which frequently do not exist.”
We wish to state unequivocally our threats and claims are very real. Not exaggerated and never a bluff. This PSA today is living evidence of that.
We wish to state unequivocally we have NEVER conducted swatting attacks against corporate victims personnel nor have we ever texted victims personnel family members any threats.
We wish to state unequivocally we have NEVER claimed to have sensitive or compromising information, including embarrassing photographs and videos of victims. WE ARE NOT SEXTORTIONISTS.
Finally, we wish to STATE UNEQUIVOCALLY we are NOT apart of “The Com”. We have NEVER been apart of “The Com”. “The Com” is a propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalising this nonsense.
As a big believer and supporter of the U.S. Constitution – we are exercising the First Amendment and actively combating disinformation. This is not a ransom, coercion, or extortion. Your federal policies do not apply here. This PSA is NOT financially motivated.
We recognise that certain statements within your FLASH report appear to stem from biased public reporting by certain journalists who have previously and intentionally propagated false narratives about our organisation in an attempt to “disrupt” our operations and hinder clients trust in our organisation hoping nobody pays us. Should those certain journalists and you know very well who you are, continue these unwarranted attacks and defamatory statements, we will be forced to respond in a civil manner with a commensurate and forceful defence of our reputation.
We welcome any and all journalists to inquire us at shinygroup@onionmail[.]com to hear our side of the story.
Make the right decision, don’t be the next headline.
Thank you for your attention to this matter. -SH
Updated: 23 Sep 2026“
The post is essentially a hostile “correction notice” directed at FBI leaders Brett Leatherman and Kash Patel. Its central grievance is an FBI advisory that says ShinyHunters commonly harasses victims and their families, including through threatening messages, phone calls, and, in some cases, swatting.
It also warns that threat actors may exaggerate their access to personal information or falsely claim to possess compromising photos or videos. The advisory does not use the word “sextortion,” but ShinyHunters appears to have interpreted the reference to compromising material that way. The group denies much of the FBI’s account while simultaneously using coercive language of its own.
The document it appears to mean is the FBI/IC3 public advisory “ShinyHunters: Cyber Criminal Group Attacks Learning Management System,” issued on May 15, 2026. Despite ShinyHunters calling it a “2026 Quarter 2 FLASH report,” the publicly accessible document is labeled a Public Service Announcement (PSA), not a FLASH.
The picture may have been further confused by a sextortionist who pretended to be ShinyHunters. ShinyHunters declares:
“WE ARE NOT SEXTORTIONISTS.”
It also denies carrying out swatting attacks or sending threatening messages to the family members of people working for its corporate victims.
The group also denies being part of The Com, a decentralized network linked to cybercrime and violence. It calls that connection:
“propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalizing this nonsense.”
The group then threatens journalists it accuses of spreading these “false narratives.”
The most worrying part of the message is the group’s claim that it stole sensitive data on:
“almost ALL FBI Agents, and individuals who filed an application with the FBI for a job.”
According to 404 Media, ShinyHunters provided a sample containing information on roughly 5,000 FBI agents, including names, home addresses, phone numbers, and details about their spouses. The publication reportedly verified portions of the sample, but the full dataset and the wider claims about the breach have not been independently confirmed.
The group also reportedly defaced the FBI’s jobs website. The FBI says it is aware of claims involving unauthorized activity affecting FBIjobs.gov and is investigating, although “broken” does not necessarily mean “breached.”
The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
The extortion group has modified its exploit in new attacks targeting the PeopleSoft vulnerability CVE-2026-35273.
The post Google Warns of ShinyHunters’ Fresh Oracle PeopleSoft Campaign appeared first on SecurityWeek.
Sextortion scammers are using email addresses from data leaked by the ShinyHunters hacking group to add some credibility to their feeble attempts to convince people they have embarrassing information about them.
Sextortion emails are messages claiming that the scammer recorded you through your webcam while you watched pornography and now demand payment. They have been around for years and keep evolving with small changes in wording and fake technical detail.
In this campaign, the scammers pretend to be ShinyHunters. What hasn’t changed is the basic truth: there is no malware, no recording, and no credible evidence behind the threat. Despite seeing countless versions of these emails over the years, I’ve yet to encounter one that was backed up by the evidence the sender claimed to have.
BleepingComputer reports that ShinyHunters data leaks are fueling a $2,000 sextortion email scam and shared the following example:
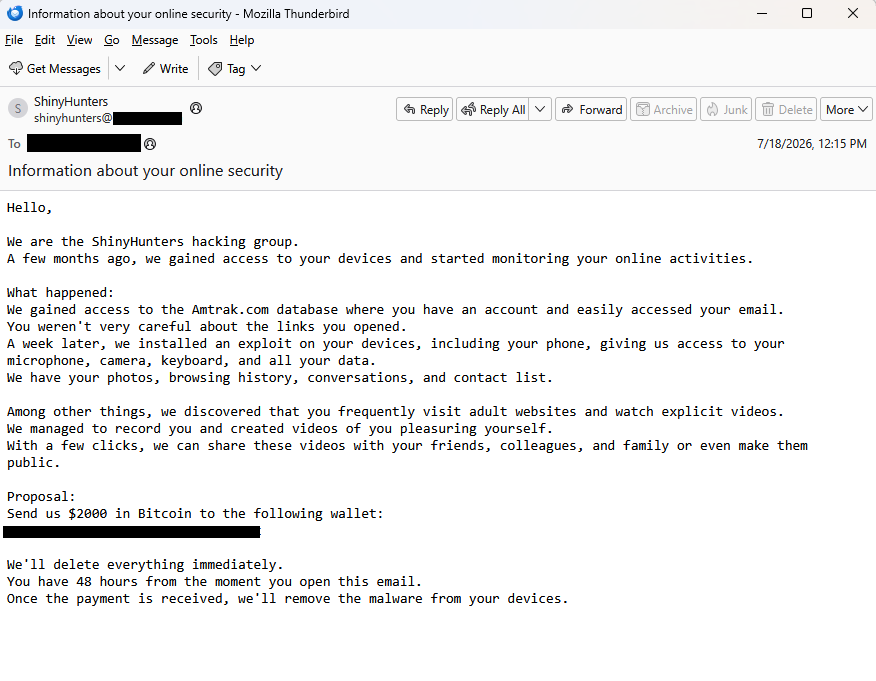
“Subject: Information about your online security
Hello,
We are the ShinyHunters hacking group.
A few months ago, we gained access to your devices and started monitoring your online activities.What happened:
We gained access to the Amtrak.com database where you have an account and easily accessed your email.
You weren’t very careful about the links you opened.
A week later, we installed an exploit on your devices, including your phone, giving us access to your microphone,
camera, keyboard, and all your data.
We have your photos, browsing history, conversations, and contact list.Among other things, we discovered that you frequently visit adult websites and watch explicit videos.
We managed to record you and created videos of you pleasuring yourself.
With a few clicks, we can share these videos with your friends,
colleagues, and family or even make them public.Proposal:
Send us $2000 in Bitcoin to the following wallet:
xxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxWe’ll delete everything immediately.
You have 48 hours from the moment you open this email.
Once the payment is received, we’ll remove the malware from your devices.”
BleepingComputer states it has seen data from the Amtrak, Hallmark, ADT, Substack, Betterment, CarGurus, Panera Bread, and McGraw Hill breaches used to target victims in this sextortion email campaign.
A California community college also issued a warning after seeing the campaign target people affected by the Canvas data breach.
They confirmed that the targeted email addresses had previously appeared in data leaked by ShinyHunters. They also contacted the group, which denied being behind the sextortion emails.
The increase to a $2,000 demand may suggest the scammers paid someone for the email lists. Although it’s more likely they simply downloaded the leaked data after ShinyHunters published it following failed extortion attempts.
A quick check of the Bitcoin address used in the email shows no activity.
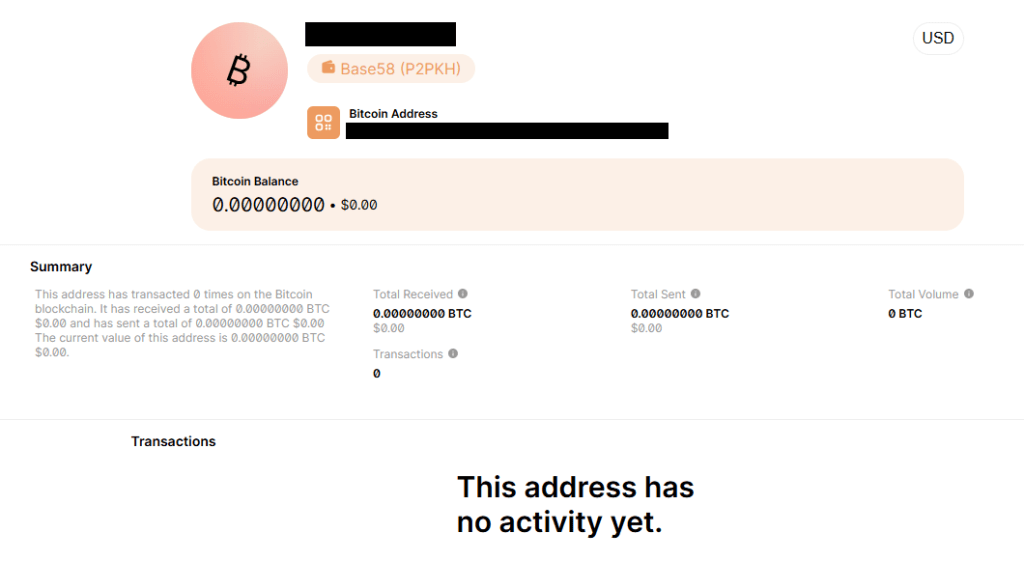
Let’s keep it that way. With any luck, these dungeon dwellers will eventually give up trying to scare people out of their hard-earned money.
Some sextortion emails are badly written, but many have been polished by AI and look convincing. Regardless of how professional they look, they should be treated the same way: as unsubstantiated threats designed to scare victims into paying.
Pro tip: Malwarebytes Scam Guard recognized this email for what it is: sextortion. It can recognize scams and advise you how to proceed.
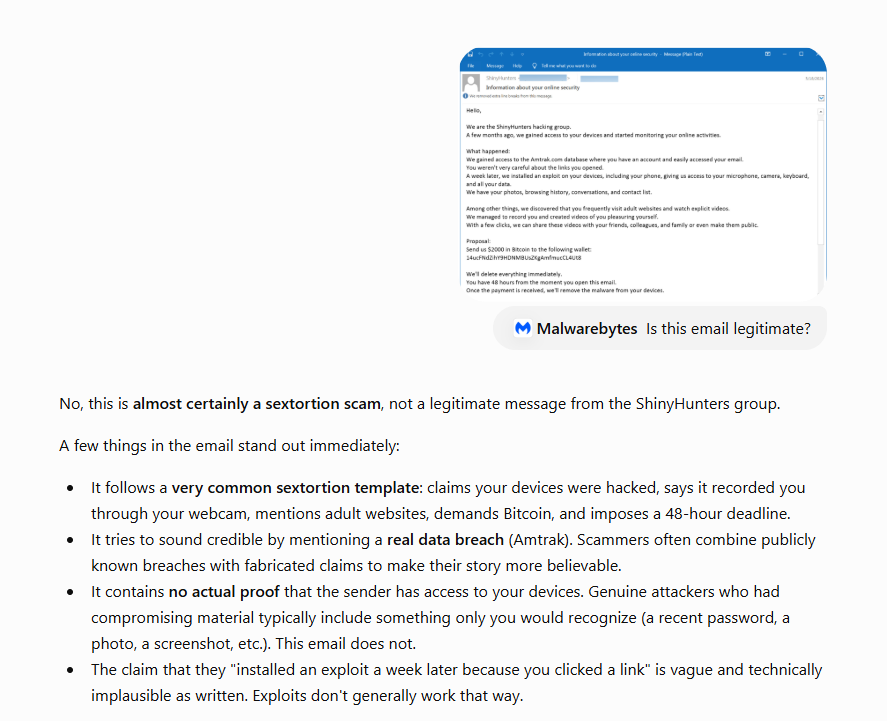
While these sextortion emails are almost always bluffs, if you’re concerned about webcam spying, Malwarebytes Webcam Monitoring can alert you when applications attempt to access your camera.
Sextortion scammers are using email addresses from data leaked by the ShinyHunters hacking group to add some credibility to their feeble attempts to convince people they have embarrassing information about them.
Sextortion emails are messages claiming that the scammer recorded you through your webcam while you watched pornography and now demand payment. They have been around for years and keep evolving with small changes in wording and fake technical detail.
In this campaign, the scammers pretend to be ShinyHunters. What hasn’t changed is the basic truth: there is no malware, no recording, and no credible evidence behind the threat. Despite seeing countless versions of these emails over the years, I’ve yet to encounter one that was backed up by the evidence the sender claimed to have.
BleepingComputer reports that ShinyHunters data leaks are fueling a $2,000 sextortion email scam and shared the following example:
“Subject: Information about your online security
Hello,
We are the ShinyHunters hacking group.
A few months ago, we gained access to your devices and started monitoring your online activities.What happened:
We gained access to the Amtrak.com database where you have an account and easily accessed your email.
You weren’t very careful about the links you opened.
A week later, we installed an exploit on your devices, including your phone, giving us access to your microphone,
camera, keyboard, and all your data.
We have your photos, browsing history, conversations, and contact list.Among other things, we discovered that you frequently visit adult websites and watch explicit videos.
We managed to record you and created videos of you pleasuring yourself.
With a few clicks, we can share these videos with your friends,
colleagues, and family or even make them public.Proposal:
Send us $2000 in Bitcoin to the following wallet:
xxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxWe’ll delete everything immediately.
You have 48 hours from the moment you open this email.
Once the payment is received, we’ll remove the malware from your devices.”
BleepingComputer states it has seen data from the Amtrak, Hallmark, ADT, Substack, Betterment, CarGurus, Panera Bread, and McGraw Hill breaches used to target victims in this sextortion email campaign.
A California community college also issued a warning after seeing the campaign target people affected by the Canvas data breach.
They confirmed that the targeted email addresses had previously appeared in data leaked by ShinyHunters. They also contacted the group, which denied being behind the sextortion emails.
The increase to a $2,000 demand may suggest the scammers paid someone for the email lists. Although it’s more likely they simply downloaded the leaked data after ShinyHunters published it following failed extortion attempts.
A quick check of the Bitcoin address used in the email shows no activity.
Let’s keep it that way. With any luck, these dungeon dwellers will eventually give up trying to scare people out of their hard-earned money.
Some sextortion emails are badly written, but many have been polished by AI and look convincing. Regardless of how professional they look, they should be treated the same way: as unsubstantiated threats designed to scare victims into paying.
Pro tip: Malwarebytes Scam Guard recognized this email for what it is: sextortion. It can recognize scams and advise you how to proceed.
While these sextortion emails are almost always bluffs, if you’re concerned about webcam spying, Malwarebytes Webcam Monitoring can alert you when applications attempt to access your camera.
Kodak told SecurityWeek it believes there is no threat to its systems or operations as a result of the cybersecurity incident.
The post Kodak Admits Data Breach After ShinyHunters Hack Claims appeared first on SecurityWeek.
Carnival Corporation, parent of Carnival Cruise Line, is sending out fresh “Notice of Cybersecurity Event” letters dated May 27, 2026. If you feel like you’ve read that sentence before, you’re not imagining things. Over the last decade, the world’s largest cruise operator has accumulated a worrying track record of breaches, ransomware incidents, and regulatory penalties, with this 2026 incident adding yet another entry to an already lengthy cybersecurity history.
There are several data breaches involving Carnival Corporation or one of its subsidiaries in our database.
Between 2019 and 2021 alone, Carnival reported four separate cybersecurity events to the New York Department of Financial Services. These included two ransomware attacks and a phishing incident in which attackers deployed malware, accessed and encrypted internal systems, and stole personal customer and employee information.
In this latest case, an attacker used social engineering to trick a Carnival employee into granting access to part of the company’s IT systems on April 14, 2026. By April 22, they used a compromised account to access a “limited portion” of Carnival’s IT systems, where they were able to copy personal data before being blocked.
According to the data breach notice filed in Maine, a total of 5,995,277 people were affected. Carnival determined that the intruder had illegally copied files containing personal information and is now writing to affected individuals to tell them that “data elements” relating to them were obtained.
Researchers cited by Gblock say the stolen data appears to include:
The template letter does not list specific data fields. Instead, it uses a placeholder:
“We have determined that your <<data elements>> were obtained.”
This strongly suggests that Carnival is populating each letter with data categories relevant to that particular individual, a common pattern in large breaches where people may have provided different information at different times.
Furthermore, the letters contain the usual content about the speed with which the company acted, involving third‑party experts, and frame the affected systems as a limited subset of the environment. For recipients, the important fact is not how limited the breach was from the company’s point of view, but whether the exposed information could be used for identity theft, fraud, or highly convincing phishing attacks.
We do know from past Carnival incidents that exposed data has included names, addresses, dates of birth, passport numbers, health information, and payment details. In previous breaches affecting cruise lines, compromised data has ranged from basic contact details to Social Security numbers and credit card information. Carnival has not publicly disclosed the full categories of data involved in the 2026 incident, but given that this 2026 event again involves “personal information” copied from internal systems, it is reasonable to treat it as a serious privacy incident, even if the exact mix of data varies per person.
The attack was claimed by extortion group ShinyHunters, which is known to steal data and then ask for a ransom. If the victim does not agree to the terms, the data will be published and/or sold to the highest bidder.
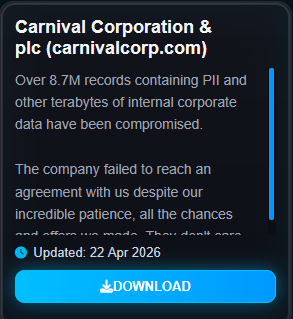
From a cybercriminal’s perspective, cruise industry data is highly prized. Cruise passengers are often relatively wealthy, and passenger records can combine identity data (names, addresses, dates of birth, passport numbers), contact data (emails, phone numbers), and potentially payment data (card numbers and sometimes bank details), making them valuable for identity theft, targeted phishing, and fraud.
To mitigate the fallout, Carnival is offering a complimentary 24‑month TransUnion credit‑monitoring package, delivered via the MyTrueIdentity platform and supported by Cyberscout for fraud assistance.
Be cautious of emails, texts, or calls claiming to come from Carnival or credit-monitoring providers, as cybercriminals often exploit breaches with phishing scams. Read our advice on what to do when you find out you’re involved in a data breach.
What do cybercriminals know about you?
Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.
Unit 42 explores trends in data theft and extortion, outlining key strategies for organizations as frontier AI models advance.
The post Out of the Crypt: The Evolving Cyber Extortion Economy appeared first on Unit 42.
In this post, we dive into the decentralized architecture of “The Com,” exposing its hybrid ecosystem of hacking, extortion, and real-life violence—and how it fuels a ruthless pipeline of cyber-fraud cycles and adolescent exploitation.
 Table Of Contents

The Community, more widely known as “The Com” is a sophisticated hybrid threat ecosystem in which cybercrime serves as the venture capital for domestic terrorism. Existing since the early 2010s, it operates in the “edgesphere”, a grey area where mainstream social media overlaps with underground criminal networks, blending nihilistic violent extremism (NVE) with high-level financial fraud. In The Com, cybercrime against Fortune 500 companies is the primary revenue stream used by members to fund a domestic terror network that aims to radicalize youth and encourage real-world violence.
However, The Com poses more than just financial risk, it is a self-serving victim-to-perpetrator pipeline. It uses stolen capital to recruit adolescents, who they view as a disposable workforce, turning them from a victim to a perpetrator. Despite being a decentralized web of individuals rather than a traditional threat actor organization, The Com has managed to grow by hiding in the gaps between corporate security, parental oversight, and law enforcement.
The Com is often mischaracterized as a single, formal organization. In reality, its ecosystem is unstructured and lacks a shared culture or leadership. However, the various factions within the ecosystem are extremely organized, supporting three broad categories of criminal activity: cybercrime, exploitation of minors, and real-world physical violence.
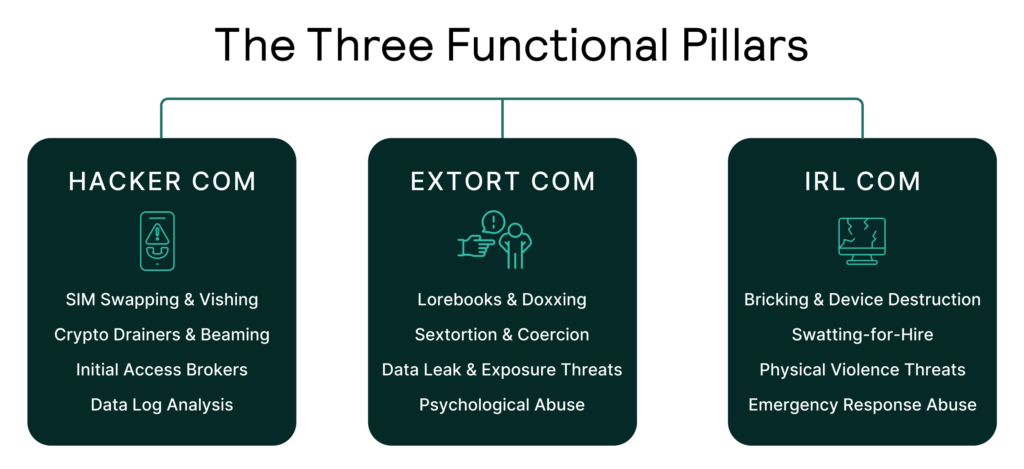
Federal investigations have shown that The Com includes a mix of adults and minors, men and women. While the exact number of members is difficult to determine, Flashpoint estimates that the broader ecosystem of The Com is in the thousands. While being a global threat, its most active core members are concentrated in Western English-speaking countries: the United Kingdom, the United States, and Canada.
While The Com is a decentralized ecosystem, its internal structure is defined by a high degree of operational alignment. Individual crews and networks within each pillar exhibit a shared psychology and standardized tradecraft that ensures their criminal activities remain effective and repeatable.
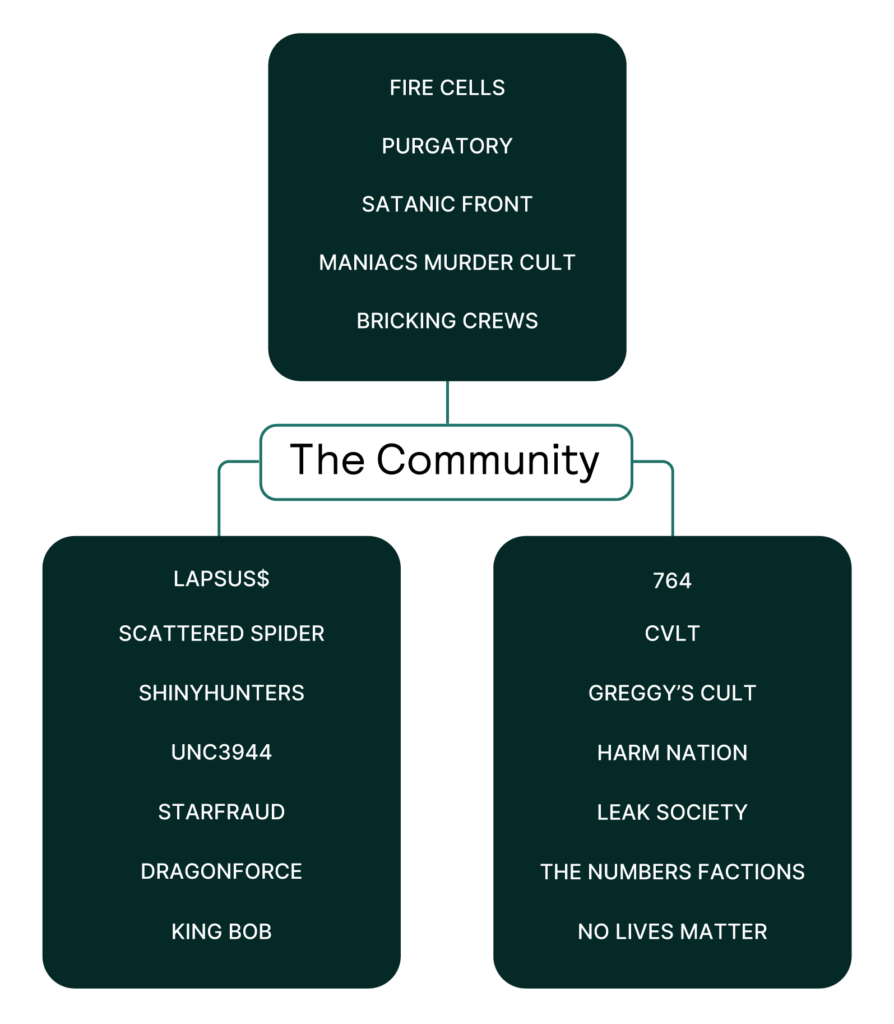
However, Flashpoint notes that members of these pillars do not operate alone. Their interaction with members of other pillars (extortion and real-world violence) amplifies the intended threat.
Hacker Com acts as the ecosystem’s economic engine and primary technical arm. Its primary function is to hack major corporations and commit financial fraud to fund the broader community’s activities and lifestyle.
Seeing themselves as the elite technical tier of The Com, Hacker Com members are motivated primarily by financial gain and the thrill of outsmarting corporate security infrastructures. Notable crews within this pillar include Scattered Spider, LAPSUS$, ShinyHunters, and DragonForce.
The following tactics, tools, and procedures (TTPs) have been observed by HACKER COM groups:
Hacker Com members capitalize on TTPs that target human vulnerabilities instead of relying solely on software and other exploits. Vishing is a signature move of the Scattered Spider crew, whose native English-speaking members call corporate IT helpdesks impersonating employees of that company.
Analysts note these threat actors are likely Gen Z who socially engineer older support staff by mimicking the impatient attitudes and vernacular of young tech executives, essentially hacking the generation gap. They leverage this form of social engineering to convince support staff to reset passwords or even re-enroll new multifactor authentication (MFA) devices, which grants them access to the victims’ networks.
Crews in this pillar have also successfully breached major targets by attacking their trusted vendors. For instance, Lapsus$ compromised Okta by targeting its third-party contractor, Sykes, while Scattered Spider has repeatedly targeted Okta’s identity services to pivot into their clients’ networks.
Once inside a network, threat actors avoid detection by using legitimate, preexisting software and other remote admin tools such as AnyDesk, Ngrok, and Teleport to maintain persistence and move laterally. They often gamify this access, mocking victims for allowing them to simply “log in” using standard admin tools rather than having to hack their way in via complex exploits. They treat the ease of access as a testament to the victim’s incompetence.
A SIM swap attack is a foundational TTP used by financially motivated actors that involves social engineering mobile carriers to hijack a target’s phone number, usually resulting in the takeover of high-value cryptocurrency accounts.
The Extort Com pillar functions as a machine designed for psychological control, coercion, and sexual exploitation of minors. Its goals intersect squarely with NVE ideologies, resulting in a marketplace and production center for CSAM and extreme violence, where members often trade these materials as a form of social currency.
Targets are migrated from public channels, which include social media and video games such as Roblox and Minecraft, to private ones maintained by The Com. Once moved, the dynamic shifts from recruitment to active exploitation, which is done to ensure the victim’s compliance.
The “In Real Life” (IRL) pillar serves as the physical enforcement arm of the ecosystem, effectively bridging the gap between virtual threats and reality. Sometimes referred to by law enforcement as “IRL Terror,” members often turn online animosity and disputes into real-world harm against people and their property.
The evolution of The Com represents a fundamental shift in the global threat landscape. It is not enough to view cybercrime as a purely financial risk or domestic extremism as a purely ideological one, the two have merged into a self-sustaining engine where stolen corporate capital fuels the radicalization and exploitation of the next generation.
As The Com continues to professionalize its tradecraft and expand its reach, the boundary between our digital and physical worlds will only continue to thin. To protect against this decentralized threat, organizations will require a mutli-layered defense strategy that is powered by intelligence that is sourced at the heart of these groups. Request a demo to learn more.
The post Understanding Illicit Ecosystems: The Hybrid Threat of “The Com” appeared first on Flashpoint.
The hackers claimed to have stolen more than 600,000 Salesforce records, including personal information and corporate data.
The post 7-Eleven Data Breach Confirmed After ShinyHunters Ransom Demand appeared first on SecurityWeek.
Grafana appears to have been targeted by Coinbase Cartel, a cybercrime group linked to ShinyHunters, Scattered Spider, and Lapsus$.
The post Grafana Confirms Breach After Hackers Claim They Stole Data appeared first on SecurityWeek.
Tens of thousands of students studying for final exams around the world have regained access to a key online learning system after a cyberattack had earlier knocked it offline.
The post Canvas System Is Online After a Cyberattack Disrupted Thousands of Schools appeared first on SecurityWeek.
Days after confirming a major data breach, Instructure is now facing a second blow.
Earlier this week, Instructure confirmed a major data breach affecting its cloud‑hosted Canvas environment, with the ShinyHunters group claiming it stole hundreds of millions of records tied to thousands of schools and universities worldwide. As discussed in our earlier blog, that incident involved data such as student and staff records, enrollment details, and private messages allegedly accessed through Canvas export features and APIs. At that stage, the focus was on large‑scale data theft and the long‑term risks for affected students and families, including identity fraud and highly targeted phishing.
According to new reporting, ShinyHunters has now hit Instructure again, this time moving from quiet data theft to very visible extortion. Using another vulnerability in Instructure’s systems, the attackers were able to modify Canvas login portals for hundreds of educational institutions, defacing both web logins and the Canvas app with an on‑screen ransom message.
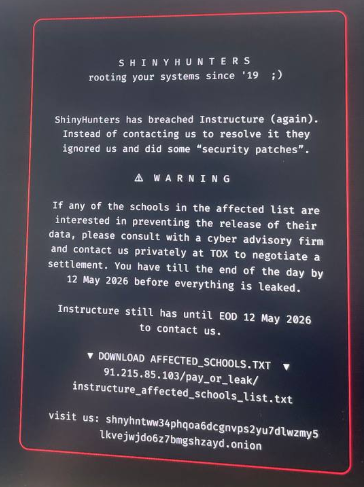
The message both claimed responsibility for the earlier breach and set a deadline of May 12 for Instructure and affected schools to contact the gang or risk the public release of stolen data.
This second wave matters for two reasons. First, it confirms that ShinyHunters still has meaningful access to Instructure’s environment, or at least to components that control the look and behavior of school login pages. Second, it marks a clear escalation in pressure tactics, from leaked claims and dark web posts to messages shown directly to students, parents, and staff trying to access their courses.
For students and families, the practical advice from our original blog still applies:
For schools and districts, this latest extortion campaign underlines the need to coordinate closely with Instructure, review single sign-on (SSO) integrations, and prepare clear communications so that any future defacements or data leaks do not catch staff and parents by surprise.

According to CNET. Read their review →


