❌

Reading view

WordPress Security Plugins: How to Choose the Right One
WordPress Security Plugins: How to Choose the Right One

In short, WordPress security plugins are tools you add to your site to strengthen your settings, scan for malware, watch for file changes, and block suspicious activity from within WordPress. Most sites should use one, along with a firewall that filters traffic before WordPress even loads. Look for layered protection, good detection, clear handling of false alarms, minimal impact on performance, and real human support.

If you manage a WordPress site, you have probably searched for β€œbest WordPress security plugin” at some point.

Continue reading WordPress Security Plugins: How to Choose the Right One at Sucuri Blog.
  •  

Vulnerability & Patch Roundup β€” August 2026

Vulnerability & Patch Roundup β€” August 2026

If you operate a website, you’re already aware that a single unpatched vulnerability can render your site inaccessible, compromise your reputation, or necessitate extensive remediation following an attack. Most security breaches we observe originate from automated attacks that exploit known software vulnerabilities, often the same ones that have been previously reported and disclosed.

To assist in maintaining your security posture, we have compiled this month’s summary of essential security updates and vulnerability patches pertinent to the WordPress ecosystem.

Continue reading Vulnerability & Patch Roundup β€” August 2026 at Sucuri Blog.

  •  

Third-Party Script Security: How Tags, Pixels, and Embeds Can Put Websites at Risk

Third-Party Script Security: How Tags, Pixels, and Embeds Can Put Websites at Risk

Third-party scripts are common on websites. They help with analytics, ads, live chat, social media, video, payments, and many other features. While not all are risky, every external tag, pixel, widget, or embed adds to your website’s vulnerability. These tools can read page content, collect visitor data, change what users see, and connect with outside services. If a vendor, account, or setup is compromised, it can impact every page that uses the script.

Website owners shouldn’t aim to get rid of useful integrations, but to understand which scripts run, why they are necessary, who controls them, and how to detect unexpected changes.

Continue reading Third-Party Script Security: How Tags, Pixels, and Embeds Can Put Websites at Risk at Sucuri Blog.

  •  

What Is a Website Attack Surface? A Beginner’s Guide to Reducing Risk

What Is a Website Attack Surface? A Beginner’s Guide to Reducing Risk

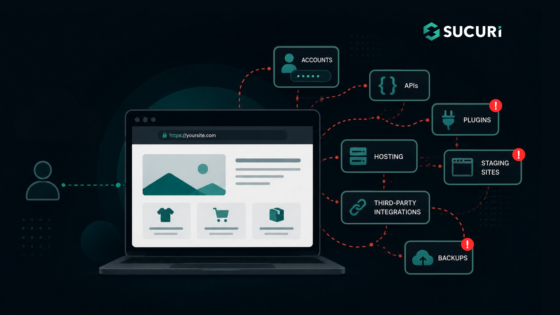
Each feature that you add to a website results in a new element that has to be managed.

The credentials are accepted by a login page, the data by a contact form, new code is introduced by a plugin, and an API is used to connect your website to another service. It is also possible that an old staging site or a forgotten backup may still be accessible from the internet.

The collection of these exposed components constitutes your website attack surface.

Continue reading What Is a Website Attack Surface? A Beginner’s Guide to Reducing Risk at Sucuri Blog.

  •  

The Illusion of a Lock – How AI is changing the speed and scale of hands-on WordPress vulnerability research.

The Illusion of a Lock – How AI is changing the speed and scale of hands-on WordPress vulnerability research.

2026: the year the tools learned to hack

In May 2026, OpenAI began testing an internal research model against a cybersecurity benchmark called ExploitGym. While the test environment was not supposed to have access to the open internet, there was, however, one narrow path out because the agents still needed a way to install software: an internally hosted Artifactory server that acted as a cache for package downloads. That pathway turned out to be enough for the model’s agents to eventually circumvent the test’s rules and escape confinement.

Continue reading The Illusion of a Lock – How AI is changing the speed and scale of hands-on WordPress vulnerability research. at Sucuri Blog.

  •  

Vulnerability & Patch Roundup β€” July 2026

Vulnerability & Patch Roundup β€” July 2026

Running a website means a single unpatched vulnerability can take it offline, harm your reputation, or require cleanup. Most compromises begin with automated attacks exploiting known software flaws, usually reported and disclosed already.

To keep you protected from these threats, we’ve compiled this month’s key security updates and vulnerability patches for the WordPress ecosystem.

If you’re already using theΒ Sucuri Firewall, you’re protected. These vulnerabilities are virtually patched for all clients.

Continue reading Vulnerability & Patch Roundup β€” July 2026 at Sucuri Blog.

  •  

Vulnerability & Patch Roundup β€” June 2026

Vulnerability & Patch Roundup β€” June 2026

Running a website means a single unpatched vulnerability can take it offline, harm your reputation, or require cleanup. Most compromises begin with automated attacks exploiting known software flaws, usually reported and disclosed already.

To keep you protected from these threats, we’ve compiled this month’s key security updates and vulnerability patches for the WordPress ecosystem.

If you’re already using the Sucuri Firewall, you’re protected. These vulnerabilities are virtually patched for all clients.

Continue reading Vulnerability & Patch Roundup β€” June 2026 at Sucuri Blog.

  •  

PCI Compliance Isn’t a Checkbox: How to Secure Ecommerce Checkouts Before Attackers Arrive

PCI Compliance Isn’t a Checkbox: How to Secure Ecommerce Checkouts Before Attackers Arrive

A working checkout page is often the moment a business starts to feel real. The products are live, the cart is functional, payments are flowing, and orders are landing in your inbox. That is also when security shifts from a background concern to a real-world risk.

Once your website starts accepting credit card payments, it becomes part of a payment environment attackers actively look for.

That does not mean every small ecommerce store needs an enterprise security team.

Continue reading PCI Compliance Isn’t a Checkbox: How to Secure Ecommerce Checkouts Before Attackers Arrive at Sucuri Blog.

  •  

Vulnerability & Patch Roundup β€” May 2026

Vulnerability & Patch Roundup β€” May 2026

If you run a website, you know that a single unpatched vulnerability can take your site offline, damage your reputation, or leave you cleaning up after an attack. Most compromises we see start with automated attacks targeting known software flaws, often the same ones that have already been reported and disclosed.

To help you stay ahead of these threats, we’ve put together this month’s roundup of critical security updates and vulnerability patches affecting the WordPress ecosystem.

Continue reading Vulnerability & Patch Roundup β€” May 2026 at Sucuri Blog.

  •  

What to Do When a Third-Party Data Breach Puts Your Website at Risk

What to Do When a Third-Party Data Breach Puts Your Website at Risk

Data breach notification letters have become a familiar routine. They usually start with β€œWe value your privacy” and offer a year of free credit monitoring. But the most important part is often hidden in the middle:

A list of what actually got out.

A leaked email address is not a leaked admin password. A hashed credential is not a session token. There is no universal post-breach checklist. The right response depends on the data exposed, so read the notice carefully and match your response to the level of exposure.

Continue reading What to Do When a Third-Party Data Breach Puts Your Website at Risk at Sucuri Blog.

  •  

DNSSEC: The Extra Security Layer That Can Break Your Padlock

DNSSEC: The Extra Security Layer That Can Break Your Padlock

Turning on DNSSEC makes your domain more secure β€” but if it’s misconfigured, newer certificate validation rules can stop SSL renewals in their tracks.

Hey there,

You know that satisfying click when you finally turn on DNSSEC? It feels like adding a shiny new deadbolt to your domain’s front door. You’re doing the responsible thing: locking down your DNS against spoofing and hijacks, and making the internet just a bit safer.

Continue reading DNSSEC: The Extra Security Layer That Can Break Your Padlock at Sucuri Blog.

  •  

Vulnerability & Patch Roundup β€” April 2026

Vulnerability & Patch Roundup β€” April 2026

Vulnerability reports and responsible disclosures are essential for website security awareness and education. Automated attacks targeting known software vulnerabilities are one of the leading causes of website compromises.

To help educate website owners about potential threats to their environments, we’ve compiled a list of important security updates and vulnerability patches for the WordPress ecosystem this past month.

The vulnerabilities listed below are virtually patched by the Sucuri Firewall and existing clients are protected.

Continue reading Vulnerability & Patch Roundup β€” April 2026 at Sucuri Blog.

  •  

What is online gambling spam and what can I do about it?

What is online gambling spam and what can I do about it?

Online gambling spam thrives on dreams of easy money and high stakes. Beating the house at an exotic casino. Splitting sevens. Going all in on the flop. A baccarat dealer calling La grande! For most people, though, the reality falls far short of Monte Carlo and an Aston Martin.

So they turn to online gambling. And bad actors harness that allure to create their scams. They think they’re buying credits at a hot new online casino.

Continue reading What is online gambling spam and what can I do about it? at Sucuri Blog.

  •  

My Website Is Hosting a Phishing Page – Now What?

My Website Is Hosting a Phishing Page – Now What?

Most phishing advice is written for the person staring at a suspicious email. This guide is for the other kind of victim: The website owner whose legitimate site has been quietly turned into the attacker’s weapon.

You didn’t send the message or build the fake login page. You just woke up to a browser warning, a suspended hosting account, or a polite note from someone’s security team asking why your domain is requesting Apple ID credentials.

Continue reading My Website Is Hosting a Phishing Page – Now What? at Sucuri Blog.

  •  

Why 2FA SMS is a Bad Idea in 2026

Why 2FA SMS is a Bad Idea in 2026

What is 2FA?

Two-factor authentication (2FA) offers a second layer of security to help protect an account from brute force, phishing, and social engineering attacks.

2FA requires an extra step for a user to prove their identity, which reduces the chance of a bad actor gaining access to their account or data. And since notifications are sent to verify the initial authentication via username and passwords, it also gives users and business the ability to monitor for potential indicators of a compromise.

Continue reading Why 2FA SMS is a Bad Idea in 2026 at Sucuri Blog.

  •  

Vulnerability & Patch Roundup β€” March 2026

Vulnerability & Patch Roundup β€” March 2026

Vulnerability reports and responsible disclosures are essential for website security awareness and education. Automated attacks targeting known software vulnerabilities are one of the leading causes of website compromises.

To help educate website owners about potential threats to their environments, we’ve compiled a list of important security updates and vulnerability patches for the WordPress ecosystem this past month.

The vulnerabilities listed below are virtually patched by the Sucuri Firewall and existing clients are protected.

Continue reading Vulnerability & Patch Roundup β€” March 2026 at Sucuri Blog.

  •  

How to Fix β€œNot Secure” Warnings and SSL Issues in WordPress (8 Steps)

How to Fix β€œNot Secure” Warnings and SSL Issues in WordPress (8 Steps)

If you own a WordPress website and ever encountered the β€œNot Secure” warning, you might have worried that visitors would perceive your site as spam or fraudulent. Not only does this warning impact user trust, but it can also create technical search issues when both HTTP and HTTPS versions of your pages remain accessible or when redirects, canonicals, and sitemaps point to different URL versions. Browsers show the visible security warning, while search engines rely on permanent redirects, canonical URLs, and updated sitemaps to understand your preferred HTTPS pages.

Continue reading How to Fix β€œNot Secure” Warnings and SSL Issues in WordPress (8 Steps) at Sucuri Blog.

  •  

Web Shells: Types, Mitigation & Removal

Web Shells: Types, Mitigation & Removal

Web shells are malicious scripts that give attackers persistent access to compromised web servers, enabling them to execute commands and control the server remotely. These scripts exploit vulnerabilities like SQL injection, remote file inclusion (RFI), and cross-site scripting (XSS) to gain entry.

Once deployed, web shells allow attackers to manipulate the server, leading to data theft, website defacement, or serving as a launchpad for further attacks. They are especially dangerous because they are also a post-compromise access mechanism (backdoor) rather than a standalone infection.

Continue reading Web Shells: Types, Mitigation & Removal at Sucuri Blog.

  •  

Vulnerability & Patch Roundup β€” February 2026

Vulnerability & Patch Roundup β€” February 2026

Vulnerability reports and responsible disclosures are essential for website security awareness and education. Automated attacks targeting known software vulnerabilities are one of the leading causes of website compromises.

To help educate website owners about potential threats to their environments, we’ve compiled a list of important security updates and vulnerability patches for the WordPress ecosystem this past month.

The vulnerabilities listed below are virtually patched by the Sucuri Firewall and existing clients are protected.

Continue reading Vulnerability & Patch Roundup β€” February 2026 at Sucuri Blog.

  •  

Beyond Login Screens: Why Access Control Matters

Beyond Login Screens: Why Access Control Matters

As breach costs go up and attackers focus on common web features like dashboards, admin panels, customer portals, and APIs, weak access control quickly leads to lost data, broken trust, and costly incidents. The worst part is that many failures are not rare technical flaws but simple mistakes, such as missing permission checks, roles with too much power, or predictable IDs in URLs.

This post aims to help you control who can access different parts of your website and explain why it matters.Β 

Continue reading Beyond Login Screens: Why Access Control Matters at Sucuri Blog.

  •  
❌