
 Login

Reading view
Monnai Raises $12 Million for Identity and Risk Data Infrastructure
The company will use the investment to accelerate the adoption of its solution among financial institutions and digital businesses.
The post Monnai Raises $12 Million for Identity and Risk Data Infrastructure appeared first on SecurityWeek.
Cybersecurity Firms React to China’s Reported Software Ban
China has more than 5,000 cybersecurity companies and all the top 20 firms are working with the government.
The post Cybersecurity Firms React to China’s Reported Software Ban appeared first on SecurityWeek.
Cyber Insights 2026: External Attack Surface Management
AI will assist companies in finding their external attack surface, but it will also assist bad actors in locating and attacking the weak points.
The post Cyber Insights 2026: External Attack Surface Management appeared first on SecurityWeek.
Why Effective CTEM Must be an Intelligence-Led Program
Blog
Why Effective CTEM Must be an Intelligence-Led Program
Continuous Threat Exposure Management (CTEM) is a continuous program and operational framework, not a single pre-boxed platform. Flashpoint believes that effective CTEM must be intelligence-led, using curated threat intelligence as the operational core to prioritize risk and turn exposure data into defensible decisions.

 Table Of Contents

Table of Contents
More
subscribe to our newsletter
Continuous Threat Exposure Management (CTEM) is Not a Product
Since Gartner’s introduction of CTEM as a framework in 2022, cybersecurity vendors have engaged in a rapid “productization” race. This has led to inconsistent market definitions, with a variety of vendors from vulnerability scanners to Attack Surface Management (ASM) providers now claiming to be an “exposure management” solution.
The current approach to productizing CTEM is flawed. There is no such thing as a single “exposure management platform.” The enterprise reality is that most enterprises buy three or more products just to approximate what CTEM promises in theory. Even with these technologies, organizations still require heavy lifting with people, process, and custom integrations to actually make it work.
The Exposure Stack: When One Platform Becomes Three (or More)
A functional CTEM approach typically requires multiple platforms or tools, including:
- Continuous Penetration/Exploitation Testing & Attack Path Analysis for continuous pentesting, attack path validation, and hands-on exposure validation.
- Vulnerability and Exposure Management for vulnerability scanning, exposure scoring, and asset risk views.
- Intelligence for deep, curated vulnerability, compromised credentials, card fraud, and other forms of intelligence that goes far beyond the scope of technology-based “management platforms”.
In some cases, organizations may also use an ASM vendor for shadow IT discovery, a CMDB for asset context, and ticketing integrations to drive remediation. This multi-platform model is the rule, not the exception. And that raises a hard truth: if you need three or more products, plus a dedicated team to implement CTEM, you need an intelligence-led CTEM program.
CTEM is an Operational Discipline, Not a Single Product
The narrative that CTEM can be packaged into a single product breaks down for three critical reasons:
1. CTEM is a Program, Not a Platform
You cannot buy a capability that requires full-stack asset visibility, contextualized threat actor data, real-world validation, and remediation orchestration from one tool. Each component spans a different domain of expertise and data. A vulnerability scanner, alone, cannot validate exploitability, a pentest service has a tough time scaling to daily monitoring, and generic threat intelligence feeds cannot provide critical business context.
However, CTEM requires orchestration of all these components in one operational loop. No single product delivers this comprehensively out of the box; this is why CTEM must be viewed as a continuous program, not a one-size-fits-all product.
2. Human Expertise is Irreplaceable
Vendors often advertise automation, however, key intelligence functions are still powered by and reliant on human analysis. Even with best-in-class AI tools in place, security teams are depending on human insights for:
- Triaging noisy CVE lists
- Cross-referencing exposure data with asset inventories
- Manually validating if risks are real
- Prioritizing based on threat intelligence and internal context
- Writing custom logic and integrations to bridge platforms together
In other words, exposure management today still relies on human insights and expertise. So while vendors advertise “automation and intelligence,” what they’re really delivering is a starting point. Ultimately, AI is a force multiplier for threat analysts, not a replacement.
3. Risk Without Intelligence Is Just Data
Most platforms treat exposure like a math problem. But real risk isn’t just CVSS (Common Vulnerability Scoring System) scores or asset counts, it requires answering critical, intelligence-based questions:
- How likely is this vulnerability to be exploited, and what’s the impact if it is?
- How likely is this misconfiguration to be exploited, and what is its impact?
- How likely is this compromised credential to be used by a threat actor, and what is the potential impact?
These answers require intelligence, not just data. Best-in-class intelligence provides security teams with confirmed exploit activity in the wild, context around attacker usage in APT (Advanced Persistent Threat) campaigns, and detailed metadata for prioritization where CVSS fails. That is why Flashpoint intelligence is leveraged by over 800 organizations as the operational core of exposure management, turning exposure data into defensible decisions.
CTEM Productization vs. CTEM Reality
If your risk strategy requires continuous penetration and exploit testing, vulnerability management, threat intelligence, and manual prioritization and validation, you’re not buying CTEM; you’re building it. At Flashpoint, we’re helping organizations build CTEM the right way: driven by intelligence, and powered by integrations and AI.
The Intelligence-Led Future of Exposure Management
Flashpoint treats CTEM for what it really is, as a program that must be constructed intelligently, iteratively, and contextually.
That means:
- Using threat and vulnerability intelligence to drive what actually gets prioritized
- Treating scanners, ASM platforms, and pentesting as inputs, not outcomes
- Building processes where intelligence, context, and validation inform exposure decisions, not just ticket creation
- Investing in platform interconnectivity, not just feature checklists
Using Flashpoint’s intelligence collections, organizations can achieve intelligence-led exposure management, with threat and vulnerability intelligence working together to provide context and actionable insights in a continuous, prioritized loop. This empowers security teams to build and scale their own CTEM programs, which is the only realistic approach in a cybersecurity landscape where no single platform can do it all.
Achieve Elite Operation Control Over Your CTEM Program Using Flashpoint
If you’re evaluating exposure management tools, ask yourself:
- What happens when we find a critical vulnerability and how do we know it matters?
- Can this platform correlate attacker behavior with our asset landscape?
- Does it validate risk or just report it?
- How many other tools will we need to buy just to complete the picture?
The answers may surprise you. At Flashpoint, we’re helping organizations build CTEM the right way, driven by intelligence, powered by integration, and grounded in reality. Request a demo today and see how best-in-class intelligence is the key to achieving an effective CTEM program.
Request a demo today.
The post Why Effective CTEM Must be an Intelligence-Led Program appeared first on Flashpoint.
Flashpoint Weekly Vulnerability Insights and Prioritization Report
Blog
Flashpoint Weekly Vulnerability Insights and Prioritization Report
Week of December 20 – December 26, 2025
Anticipate, contextualize, and prioritize vulnerabilities to effectively address threats to your organization.
 Table Of Contents
Table of Contents
More
Your Guide to
Proactive Vulnerability
Management
Flashpoint’s VulnDB documents over 400,000 vulnerabilities and has over 6,000 entries in Flashpoint’s KEV database, making it a critical resource as vulnerability exploitation rises. However, if your organization is relying solely on CVE data, you may be missing critical vulnerability metadata and insights that hinder timely remediation. That’s why we created this weekly series—where we surface and analyze the most high priority vulnerabilities security teams need to know about.
Key Vulnerabilities:
Week of December 20 – December 26, 2025
Foundational Prioritization
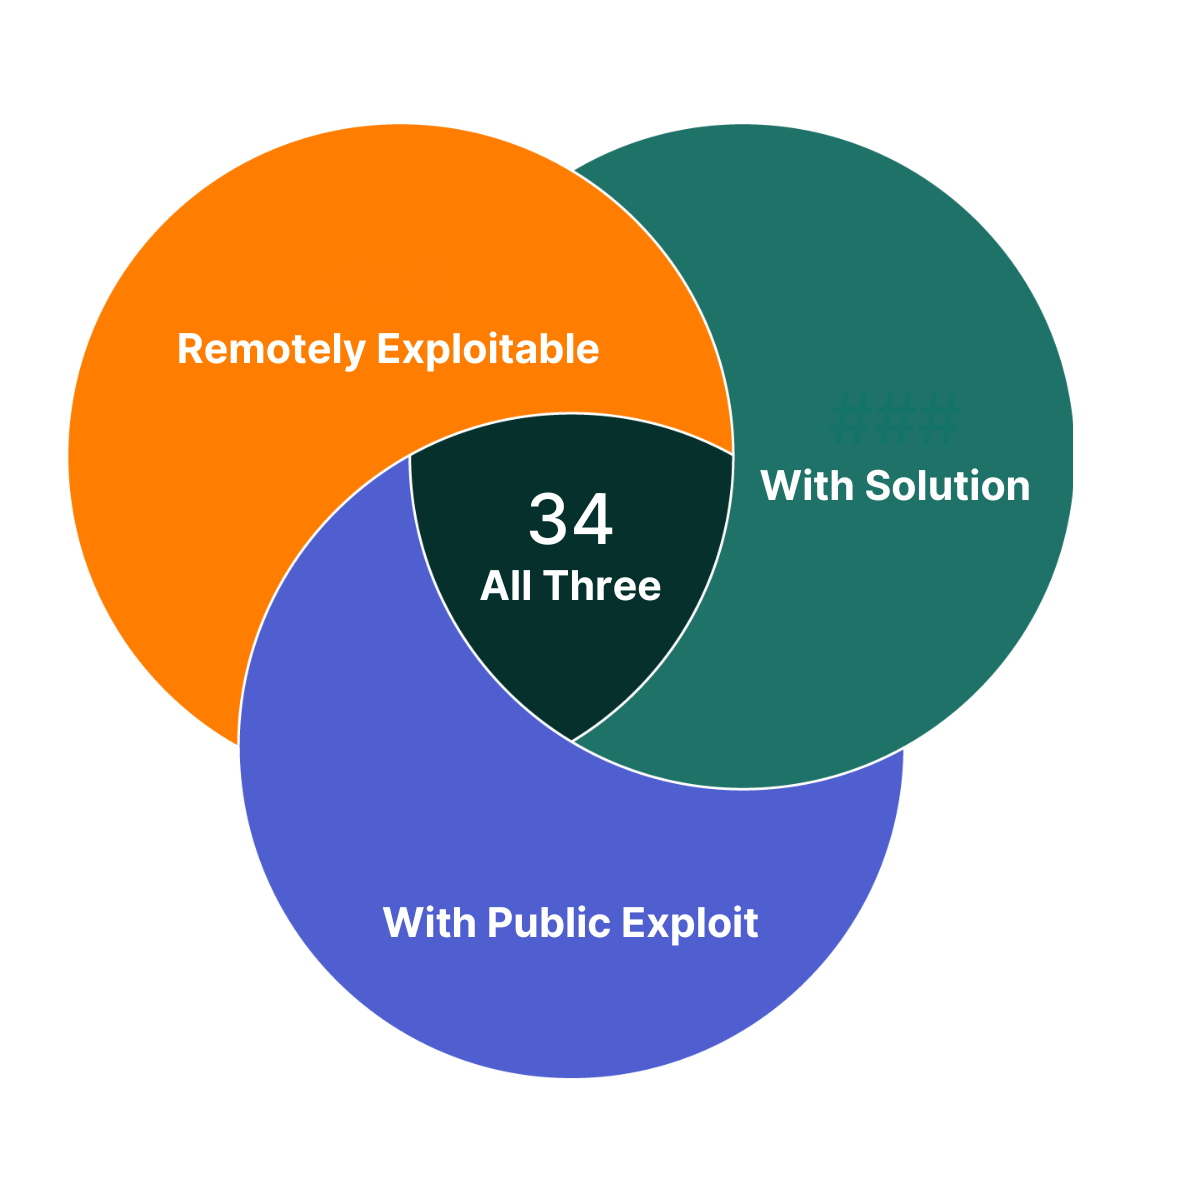
Of the vulnerabilities Flashpoint published this week, there are 34 that you can take immediate action on. They each have a solution, a public exploit exists, and are remotely exploitable. As such, these vulnerabilities are a great place to begin your prioritization efforts.
Diving Deeper – Urgent Vulnerabilities
Of the vulnerabilities Flashpoint published last week, four are highlighted in this week’s Vulnerability Insights and Prioritization Report because they contain one or more of the following criteria:
- Are in widely used products and are potentially enterprise-affecting
- Are exploited in the wild or have exploits available
- Allow full system compromise
- Can be exploited via the network alone or in combination with other vulnerabilities
- Have a solution to take action on
In addition, all of these vulnerabilities are easily discoverable and therefore should be investigated and fixed immediately.
To proactively address these vulnerabilities and ensure comprehensive coverage beyond publicly available sources on an ongoing basis, organizations can leverage Flashpoint Vulnerability Intelligence. Flashpoint provides comprehensive coverage encompassing IT, OT, IoT, CoTs, and open-source libraries and dependencies. It catalogs over 100,000 vulnerabilities that are not included in the NVD or lack a CVE ID, ensuring thorough coverage beyond publicly available sources. The vulnerabilities that are not covered by the NVD do not yet have CVE ID assigned and will be noted with a VulnDB ID.
| CVE ID | Title | CVSS Scores (v2, v3, v4) | Exploit Status | Exploit Consequence | Ransomware Likelihood Score | Social Risk Score | Solution Availability |
| CVE-2025-33222 | NVIDIA Isaac Launchable Unspecified Hardcoded Credentials | 5.0 9.8 9.3 | Private | Credential Disclosure | High | Low | Yes |
| CVE-2025-33223 | NVIDIA Isaac Launchable Unspecified Improper Execution Privileges Remote Code Execution | 10.0 9.8 9.3 | Private | Remote Code Execution | High | Low | Yes |
| CVE-2025-68613 | n8n Package for Node.js packages/workflow/src/expression-evaluator-proxy.ts Workflow Expression Evaluation Remote Code Execution | 9.0 9.9 9.4 | Public | Remote Code Execution | High | High | Yes |
| CVE-2025-14847 | MongoDB transport/message_compressor_zlib.cpp ZlibMessageCompressor::decompressData() Function Zlib Compressed Protocol Header Handling Remote Uninitialized Memory Disclosure (Mongobleed) | 10.0 9.8 9.3 | Public | Uninitialized Memory Disclosure | High | High | Yes |
NOTES: The severity of a given vulnerability score can change whenever new information becomes available. Flashpoint maintains its vulnerability database with the most recent and relevant information available. Login to view more vulnerability metadata and for the most up-to-date information.
CVSS scores: Our analysts calculate, and if needed, adjust NVD’s original CVSS scores based on new information being available.
Social Risk Score: Flashpoint estimates how much attention a vulnerability receives on social media. Increased mentions and discussions elevate the Social Risk Score, indicating a higher likelihood of exploitation. The score considers factors like post volume and authors, and decreases as the vulnerability’s relevance diminishes.
Ransomware Likelihood: This score is a rating that estimates the similarity between a vulnerability and those known to be used in ransomware attacks. As we learn more information about a vulnerability (e.g. exploitation method, technology affected) and uncover additional vulnerabilities used in ransomware attacks, this rating can change.
Flashpoint Ignite lays all of these components out. Below is an example of what this vulnerability record for CVE-2025-33223 looks like.
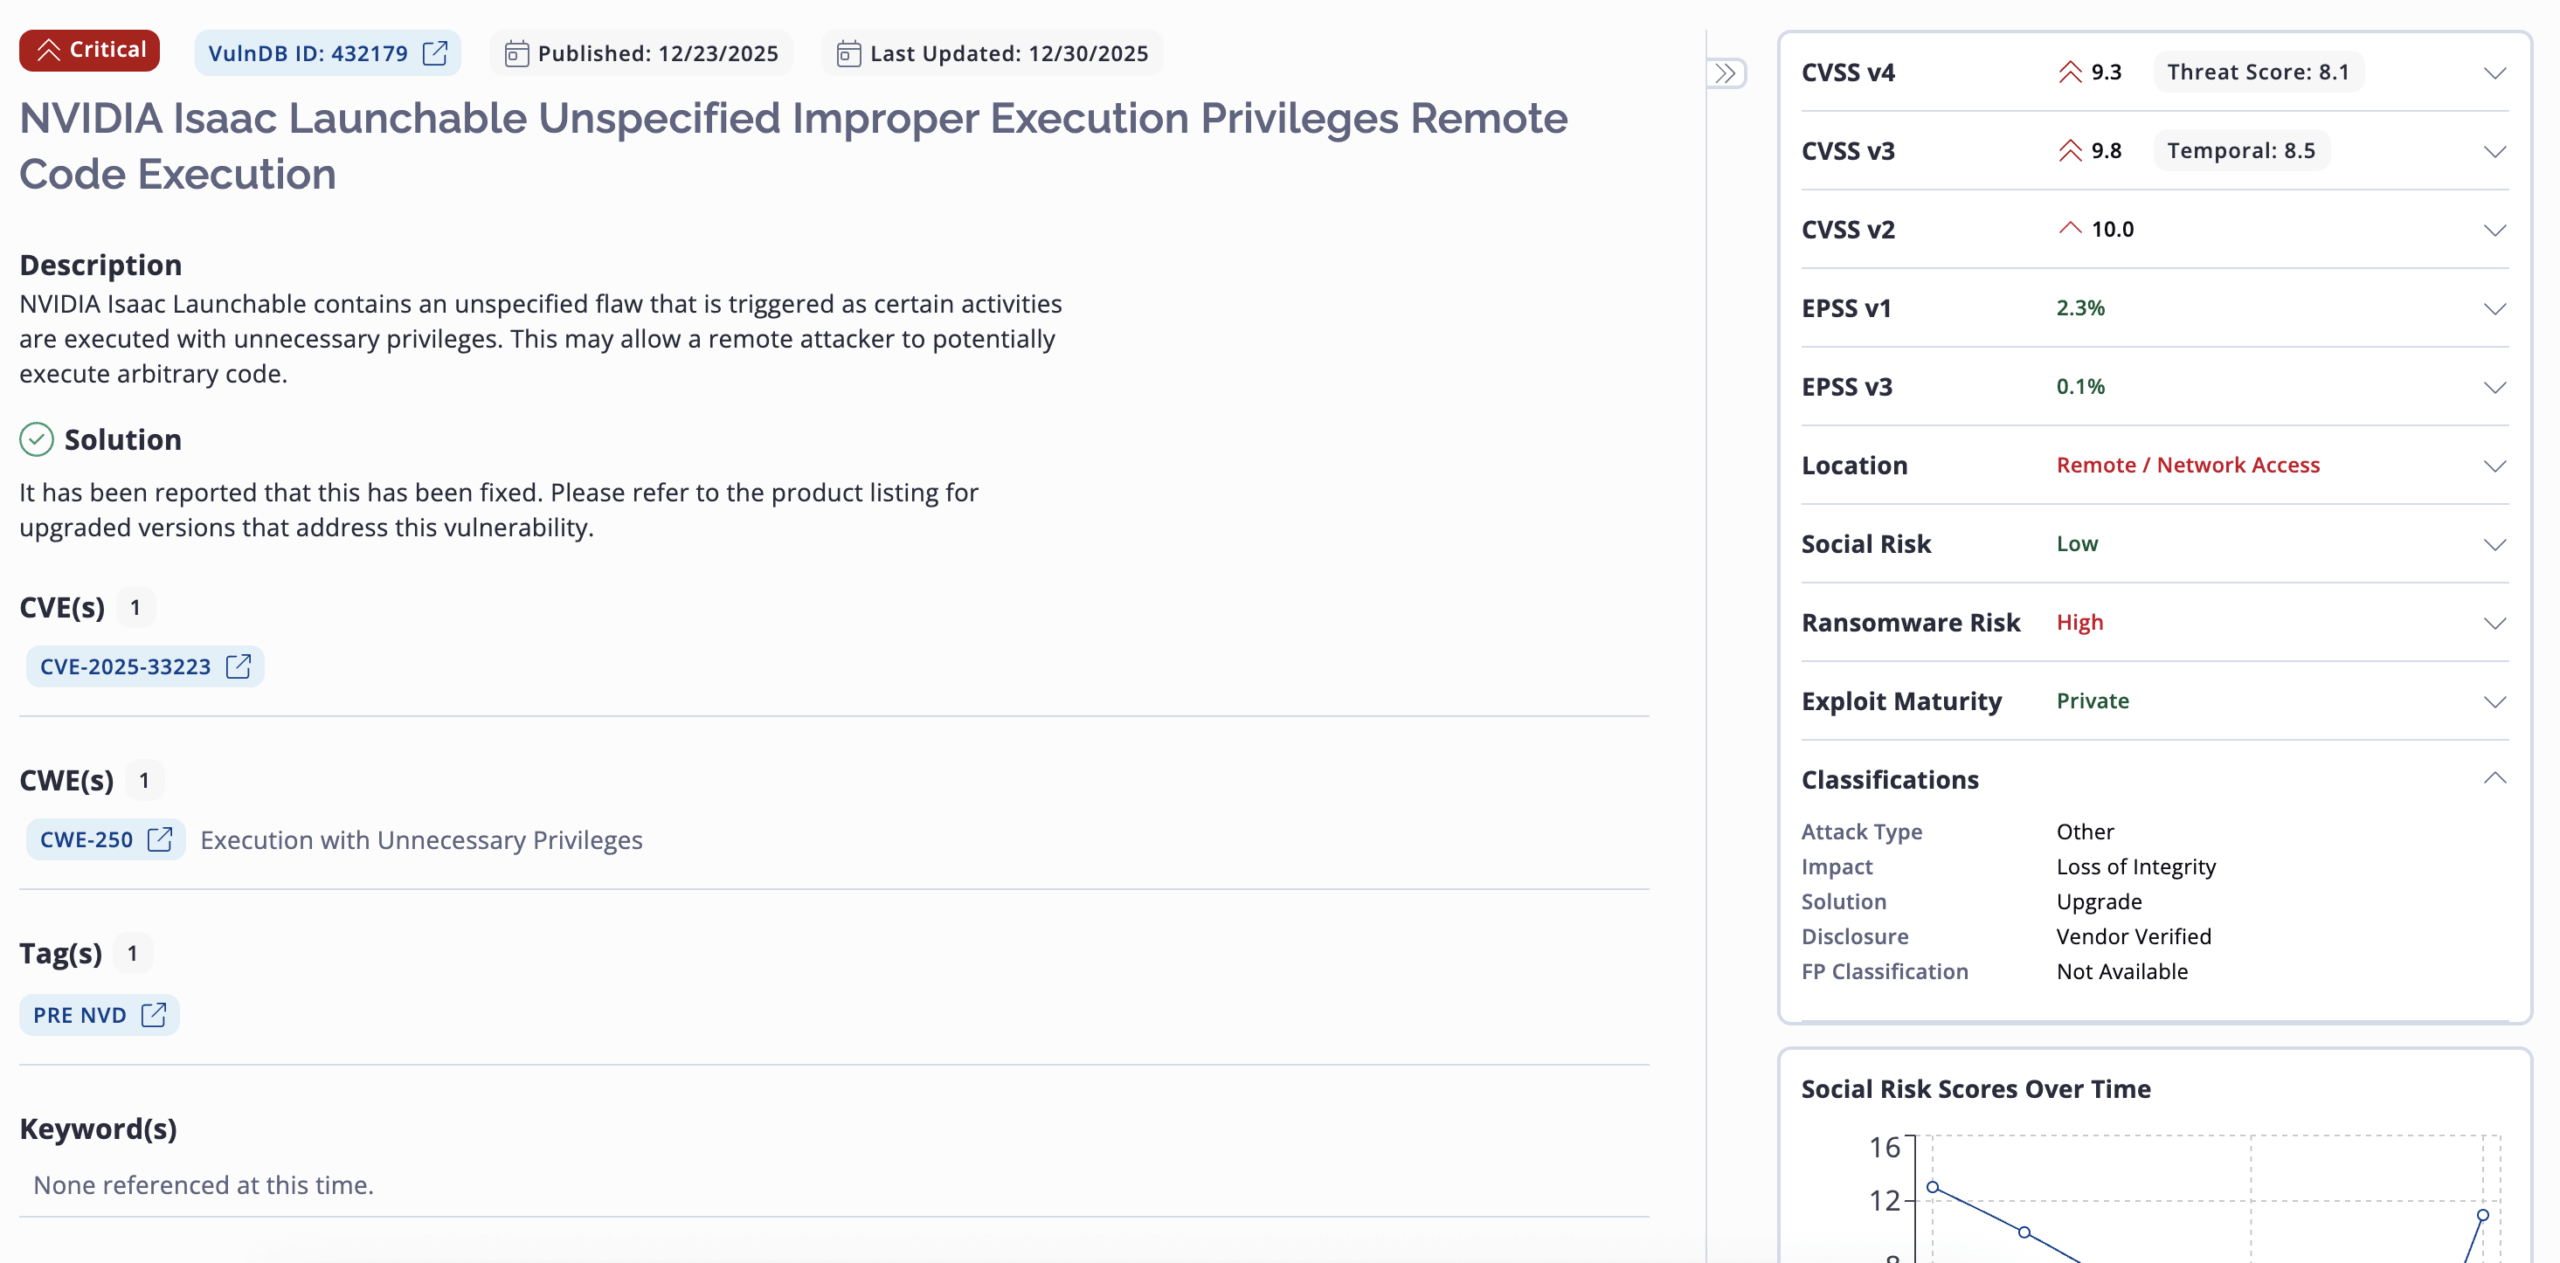
This record provides additional metadata like affected product versions, MITRE ATT&CK mapping, analyst notes, solution description, classifications, vulnerability timeline and exposure metrics, exploit references and more.
Analyst Comments on the Notable Vulnerabilities
Below, Flashpoint analysts describe the five vulnerabilities highlighted above as vulnerabilities that should be of focus for remediation if your organization is exposed.
CVE-2025-33222
NVIDIA Isaac Launchable contains a flaw that is triggered by the use of unspecified hardcoded credentials. This may allow a remote attacker to trivially gain privileged access to the program.
CVE-2025-33223
NVIDIA Isaac Launchable contains an unspecified flaw that is triggered as certain activities are executed with unnecessary privileges. This may allow a remote attacker to potentially execute arbitrary code.
CVE-2025-68613
n8n Package for Node.js contains a flaw in packages/workflow/src/expression-evaluator-proxy.ts that is triggered as workflow expressions are evaluated in an improperly isolated execution context. This may allow an authenticated, remote attacker to execute arbitrary code with the privileges of the n8n process.
CVE-2025-14847
MongoDB contains a flaw in the ZlibMessageCompressor::decompressData() function in mongo/transport/message_compressor_zlib.cpp that is triggered when handling mismatched length fields in Zlib compressed protocol headers. This may allow a remote attacker to disclose uninitialized memory contents on the heap.
Previously Highlighted Vulnerabilities
| CVE/VulnDB ID | Flashpoint Published Date |
| CVE-2025-21218 | Week of January 15, 2025 |
| CVE-2024-57811 | Week of January 15, 2025 |
| CVE-2024-55591 | Week of January 15, 2025 |
| CVE-2025-23006 | Week of January 22, 2025 |
| CVE-2025-20156 | Week of January 22, 2025 |
| CVE-2024-50664 | Week of January 22, 2025 |
| CVE-2025-24085 | Week of January 29, 2025 |
| CVE-2024-40890 | Week of January 29, 2025 |
| CVE-2024-40891 | Week of January 29, 2025 |
| VulnDB ID: 389414 | Week of January 29, 2025 |
| CVE-2025-25181 | Week of February 5, 2025 |
| CVE-2024-40890 | Week of February 5, 2025 |
| CVE-2024-40891 | Week of February 5, 2025 |
| CVE-2024-8266 | Week of February 12, 2025 |
| CVE-2025-0108 | Week of February 12, 2025 |
| CVE-2025-24472 | Week of February 12, 2025 |
| CVE-2025-21355 | Week of February 24, 2025 |
| CVE-2025-26613 | Week of February 24, 2025 |
| CVE-2024-13789 | Week of February 24, 2025 |
| CVE-2025-1539 | Week of February 24, 2025 |
| CVE-2025-27364 | Week of March 3, 2025 |
| CVE-2025-27140 | Week of March 3, 2025 |
| CVE-2025-27135 | Week of March 3, 2025 |
| CVE-2024-8420 | Week of March 3, 2025 |
| CVE-2024-56196 | Week of March 10, 2025 |
| CVE-2025-27554 | Week of March 10, 2025 |
| CVE-2025-22224 | Week of March 10, 2025 |
| CVE-2025-1393 | Week of March 10, 2025 |
| CVE-2025-24201 | Week of March 17, 2025 |
| CVE-2025-27363 | Week of March 17, 2025 |
| CVE-2025-2000 | Week of March 17, 2025 |
| CVE-2025-27636 CVE-2025-29891 | Week of March 17, 2025 |
| CVE-2025-1496 | Week of March 24, 2025 |
| CVE-2025-27781 | Week of March 24, 2025 |
| CVE-2025-29913 | Week of March 24, 2025 |
| CVE-2025-2746 | Week of March 24, 2025 |
| CVE-2025-29927 | Week of March 24, 2025 |
| CVE-2025-1974 CVE-2025-2787 | Week of March 31, 2025 |
| CVE-2025-30259 | Week of March 31, 2025 |
| CVE-2025-2783 | Week of March 31, 2025 |
| CVE-2025-30216 | Week of March 31, 2025 |
| CVE-2025-22457 | Week of April 2, 2025 |
| CVE-2025-2071 | Week of April 2, 2025 |
| CVE-2025-30356 | Week of April 2, 2025 |
| CVE-2025-3015 | Week of April 2, 2025 |
| CVE-2025-31129 | Week of April 2, 2025 |
| CVE-2025-3248 | Week of April 7, 2025 |
| CVE-2025-27797 | Week of April 7, 2025 |
| CVE-2025-27690 | Week of April 7, 2025 |
| CVE-2025-32375 | Week of April 7, 2025 |
| VulnDB ID: 398725 | Week of April 7, 2025 |
| CVE-2025-32433 | Week of April 12, 2025 |
| CVE-2025-1980 | Week of April 12, 2025 |
| CVE-2025-32068 | Week of April 12, 2025 |
| CVE-2025-31201 | Week of April 12, 2025 |
| CVE-2025-3495 | Week of April 12, 2025 |
| CVE-2025-31324 | Week of April 17, 2025 |
| CVE-2025-42599 | Week of April 17, 2025 |
| CVE-2025-32445 | Week of April 17, 2025 |
| VulnDB ID: 400516 | Week of April 17, 2025 |
| CVE-2025-22372 | Week of April 17, 2025 |
| CVE-2025-32432 | Week of April 29, 2025 |
| CVE-2025-24522 | Week of April 29, 2025 |
| CVE-2025-46348 | Week of April 29, 2025 |
| CVE-2025-43858 | Week of April 29, 2025 |
| CVE-2025-32444 | Week of April 29, 2025 |
| CVE-2025-20188 | Week of May 3, 2025 |
| CVE-2025-29972 | Week of May 3, 2025 |
| CVE-2025-32819 | Week of May 3, 2025 |
| CVE-2025-27007 | Week of May 3, 2025 |
| VulnDB ID: 402907 | Week of May 3, 2025 |
| VulnDB ID: 405228 | Week of May 17, 2025 |
| CVE-2025-47277 | Week of May 17, 2025 |
| CVE-2025-34027 | Week of May 17, 2025 |
| CVE-2025-47646 | Week of May 17, 2025 |
| VulnDB ID: 405269 | Week of May 17, 2025 |
| VulnDB ID: 406046 | Week of May 19, 2025 |
| CVE-2025-48926 | Week of May 19, 2025 |
| CVE-2025-47282 | Week of May 19, 2025 |
| CVE-2025-48054 | Week of May 19, 2025 |
| CVE-2025-41651 | Week of May 19, 2025 |
| CVE-2025-20289 | Week of June 3, 2025 |
| CVE-2025-5597 | Week of June 3, 2025 |
| CVE-2025-20674 | Week of June 3, 2025 |
| CVE-2025-5622 | Week of June 3, 2025 |
| CVE-2025-5419 | Week of June 3, 2025 |
| CVE-2025-33053 | Week of June 7, 2025 |
| CVE-2025-5353 | Week of June 7, 2025 |
| CVE-2025-22455 | Week of June 7, 2025 |
| CVE-2025-43200 | Week of June 7, 2025 |
| CVE-2025-27819 | Week of June 7, 2025 |
| CVE-2025-49132 | Week of June 13, 2025 |
| CVE-2025-49136 | Week of June 13, 2025 |
| CVE-2025-50201 | Week of June 13, 2025 |
| CVE-2025-49125 | Week of June 13, 2025 |
| CVE-2025-24288 | Week of June 13, 2025 |
| CVE-2025-6543 | Week of June 21, 2025 |
| CVE-2025-3699 | Week of June 21, 2025 |
| CVE-2025-34046 | Week of June 21, 2025 |
| CVE-2025-34036 | Week of June 21, 2025 |
| CVE-2025-34044 | Week of June 21, 2025 |
| CVE-2025-7503 | Week of July 12, 2025 |
| CVE-2025-6558 | Week of July 12, 2025 |
| VulnDB ID: 411705 | Week of July 12, 2025 |
| VulnDB ID: 411704 | Week of July 12, 2025 |
| CVE-2025-6222 | Week of July 12, 2025 |
| CVE-2025-54309 | Week of July 18, 2025 |
| CVE-2025-53771 | Week of July 18, 2025 |
| CVE-2025-53770 | Week of July 18, 2025 |
| CVE-2025-54122 | Week of July 18, 2025 |
| CVE-2025-52166 | Week of July 18, 2025 |
| CVE-2025-53942 | Week of July 25, 2025 |
| CVE-2025-46811 | Week of July 25, 2025 |
| CVE-2025-52452 | Week of July 25, 2025 |
| CVE-2025-41680 | Week of July 25, 2025 |
| CVE-2025-34143 | Week of July 25, 2025 |
| CVE-2025-50454 | Week of August 1, 2025 |
| CVE-2025-8875 | Week of August 1, 2025 |
| CVE-2025-8876 | Week of August 1, 2025 |
| CVE-2025-55150 | Week of August 1, 2025 |
| CVE-2025-25256 | Week of August 1, 2025 |
| CVE-2025-43300 | Week of August 16, 2025 |
| CVE-2025-34153 | Week of August 16, 2025 |
| CVE-2025-48148 | Week of August 16, 2025 |
| VulnDB ID: 416058 | Week of August 16, 2025 |
| CVE-2025-32992 | Week of August 16, 2025 |
| CVE-2025-7775 | Week of August 24, 2025 |
| CVE-2025-8424 | Week of August 24, 2025 |
| CVE-2025-34159 | Week of August 24, 2025 |
| CVE-2025-57819 | Week of August 24, 2025 |
| CVE-2025-7426 | Week of August 24, 2025 |
| CVE-2025-58367 | Week of September 1, 2025 |
| CVE-2025-58159 | Week of September 1, 2025 |
| CVE-2025-58048 | Week of September 1, 2025 |
| CVE-2025-39247 | Week of September 1, 2025 |
| CVE-2025-8857 | Week of September 1, 2025 |
| CVE-2025-58321 | Week of September 8, 2025 |
| CVE-2025-58366 | Week of September 8, 2025 |
| CVE-2025-58371 | Week of September 8, 2025 |
| CVE-2025-55728 | Week of September 8, 2025 |
| CVE-2025-55190 | Week of September 8, 2025 |
| VulnDB ID: 419253 | Week of September 13, 2025 |
| CVE-2025-10035 | Week of September 13, 2025 |
| CVE-2025-59346 | Week of September 13, 2025 |
| CVE-2025-55727 | Week of September 13, 2025 |
| CVE-2025-10159 | Week of September 13, 2025 |
| CVE-2025-20363 | Week of September 20, 2025 |
| CVE-2025-20333 | Week of September 20, 2025 |
| CVE-2022-4980 | Week of September 20, 2025 |
| VulnDB ID: 420451 | Week of September 20, 2025 |
| CVE-2025-9900 | Week of September 20, 2025 |
| CVE-2025-52906 | Week of September 27, 2025 |
| CVE-2025-51495 | Week of September 27, 2025 |
| CVE-2025-27224 | Week of September 27, 2025 |
| CVE-2025-27223 | Week of September 27, 2025 |
| CVE-2025-54875 | Week of September 27, 2025 |
| CVE-2025-41244 | Week of September 27, 2025 |
| CVE-2025-61928 | Week of October 6, 2025 |
| CVE-2025-61882 | Week of October 6, 2025 |
| CVE-2025-49844 | Week of October 6 2025 |
| CVE-2025-57870 | Week of October 6, 2025 |
| CVE-2025-34224 | Week of October 6, 2025 |
| CVE-2025-34222 | Week of October 6, 2025 |
| CVE-2025-40765 | Week of October 11, 2025 |
| CVE-2025-59230 | Week of October 11, 2025 |
| CVE-2025-24990 | Week of October 11, 2025 |
| CVE-2025-61884 | Week of October 11, 2025 |
| CVE-2025-41430 | Week of October 11, 2025 |
| VulnDB ID: 424051 | Week of October 18, 2025 |
| CVE-2025-62645 | Week of October 18, 2025 |
| CVE-2025-61932 | Week of October 18, 2025 |
| CVE-2025-59503 | Week of October 18, 2025 |
| CVE-2025-43995 | Week of October 18, 2025 |
| CVE-2025-62168 | Week of October 18, 2025 |
| VulnDB ID: 425182 | Week of October 25, 2025 |
| CVE-2025-62713 | Week of October 25, 2025 |
| CVE-2025-54964 | Week of October 25, 2025 |
| CVE-2024-58274 | Week of October 25, 2025 |
| CVE-2025-41723 | Week of October 25, 2025 |
| CVE-2025-20354 | Week of November 1, 2025 |
| CVE-2025-11953 | Week of November 1, 2025 |
| CVE-2025-60854 | Week of November 1, 2025 |
| CVE-2025-64095 | Week of November 1, 2025 |
| CVE-2025-11833 | Week of November 1, 2025 |
| CVE-2025-64446 | Week of November 8, 2025 |
| CVE-2025-36250 | Week of November 8, 2025 |
| CVE-2025-64400 | Week of November 8, 2025 |
| CVE-2025-12686 | Week of November 8, 2025 |
| CVE-2025-59118 | Week of November 8, 2025 |
| VulnDB ID: 426231 | Week of November 8, 2025 |
| VulnDB ID: 427979 | Week of November 22, 2025 |
| CVE-2025-55796 | Week of November 22, 2025 |
| CVE-2025-64428 | Week of November 22, 2025 |
| CVE-2025-62703 | Week of November 22, 2025 |
| VulnDB ID: 428193 | Week of November 22, 2025 |
| CVE-2025-65018 | Week of November 22, 2025 |
| CVE-2025-54347 | Week of November 22, 2025 |
| CVE-2025-55182 | Week of November 29, 2025 |
| CVE-2024-14007 | Week of November 29, 2025 |
| CVE-2025-66399 | Week of November 29, 2025 |
| CVE-2022-35420 | Week of November 29, 2025 |
| CVE-2025-66516 | Week of November 29, 2025 |
| CVE-2025-59366 | Week of November 29, 2025 |
| CVE-2025-14174 | Week of December 6, 2026 |
| CVE-2025-43529 | Week of December 6, 2026 |
| CVE-2025-8110 | Week of December 6, 2026 |
| CVE-2025-59719 | Week of December 6, 2026 |
| CVE-2025-59718 | Week of December 6, 2026 |
| CVE-2025-14087 | Week of December 6, 2026 |
| CVE-2025-62221 | Week of December 6, 2026 |
Transform Vulnerability Management with Flashpoint
Request a demo today to see how Flashpoint can transform your vulnerability intelligence, vulnerability management, and exposure identification program.
Request a demo today.
Digital Supply Chain Risk: Critical Vulnerability Affecting React Allows for Unauthorized Remote Code Execution
Blog
Digital Supply Chain Risk: Critical Vulnerability Affecting React Allows for Unauthorized Remote Code Execution
CVE-2025-55182 (VulnDB ID: 428930), is a severe, unauthenticated RCE impacting a major component of React and its ecosystem, putting global applications at immediate, high-fidelity risk.
 Table Of Contents
The React team disclosed a critical vulnerability impacting three products in the React Server Components (RSC) that allows for unauthenticated remote code execution.
Flashpoint’s vulnerability research team assesses significant enterprise and supply chain risk given React’s ubiquity: the impacted JavaScript library underpins modern UIs, with 168,640 dependents and more than 51 million weekly downloads.
How CVE-2025-55182 Works
CVE-2025-55182 (VulnDB ID: 428930) impacts all React versions since 19.0.0, meaning that this issue has been potentially exploitable since November 14, 2024. This vulnerability stems from how React handles payloads sent to React Server Function endpoints and deserializes them.
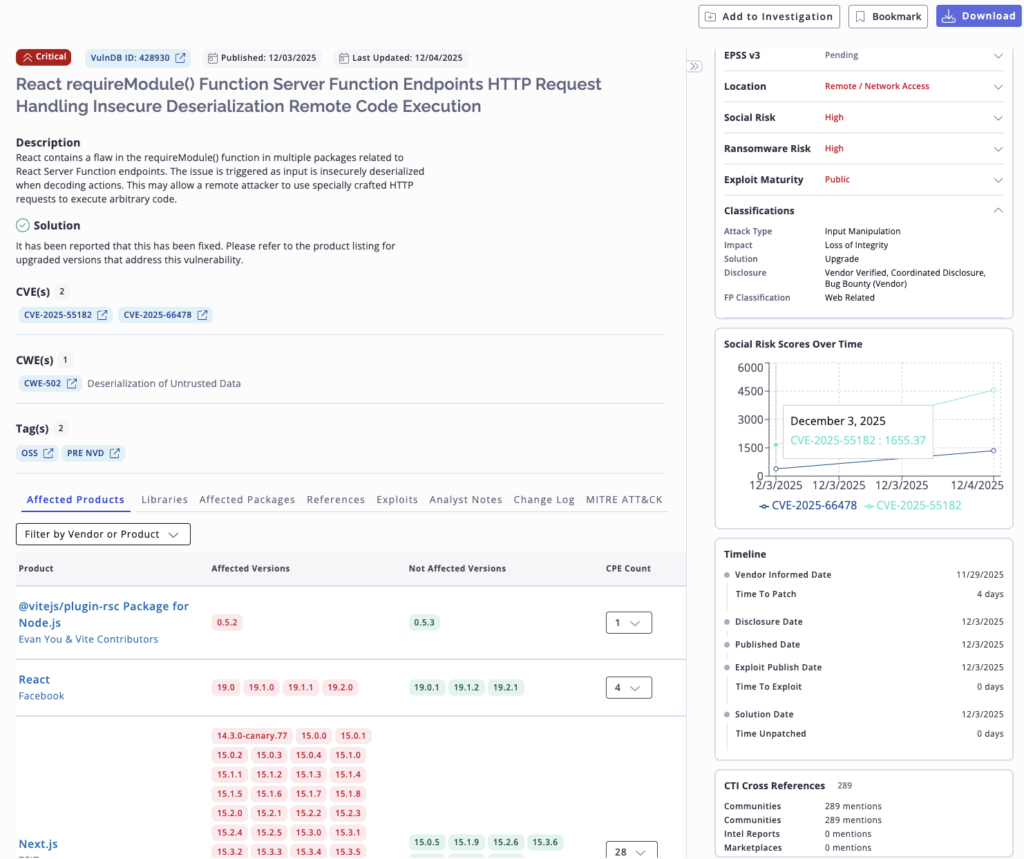
Depending on the implementation of this library, a remote, unauthenticated threat actor could send a crafted payload that would be deserialized in a way that causes remote code execution. This would lead to a total compromise of the system hosting the application, allowing for malware such as infostealers, ransomware, or cryptojackers (cryptocurrency mining) to be downloaded.
A working exploit for CVE-2025-55182 has already been published that is effective against some installations. In addition, Amazon has reported that two threat actors, attributed to Chinese Advanced Persistent Threat Groups (APTs), have begun to exploit this vulnerability. Those groups are:
- Earth Lamia (STAC6451, REF0657, CL-STA-0048)
- Jackpot Panda (iSoon, DRAGNET PANDA, Anxun Information, deepclif, Poison Carp, Houndstooth Typhoon)
Understanding the Impact and Scope of CVE-2025-55182
It is critical that security teams fully understand the potential downstream scope and impact so that they can fully focus on mitigation, rather than time-consuming research. While the vendor has provided a full disclosure, there are several important caveats to understand about CVE-2025-55182:
- Applications not implementing any React Server Function endpoints may still be vulnerable as long as it supports React Server Components.
- If an application’s React code does not use a server, it is not affected by this vulnerability.
- Applications that do not use a framework, bundler, or bundler plugins that support React Server Components are unaffected by this vulnerability.
Additionally, several React frameworks and bundlers have been discovered to leverage vulnerable React packages in various ways. The following frameworks and bundlers are known to be affected:
- next
- react-router
- waku
- @parcel/rsc
- @vitejs/plugin-rsc
- rwsdk
NPMJS.com currently shows that the react-dom package, which is effectively part of React, has 168,640 dependents. This means that an incredible number of enterprise applications are likely to be affected. Nearly every commercial application is built on hundreds, sometimes thousands of components and dependencies. Furthermore, applications coded via Vibe and similar technology are also likely to leverage React: potentially amplifying the downstream risk this vulnerability poses.
How to Mitigate CVE-2025-55182
For mitigation, the React library has released versions 19.0.1, 19.1.2, and 19.2.1 that resolve the issue. Flashpoint advises organizations to upgrade their respective libraries urgently. Security teams leveraging dynamic SBOMs (Software Bill of Materials) can drastically increase risk mapping and triage for deployed React versions.
CloudFlare has upgraded their web-application firewall (WAF) to protect against CVE-2025-55182. It is available for both free and paid plans but requires that React application traffic is proxied through the CloudFlare WAF.
To avoid confusion, security teams should ignore CVE-2025-66478. It has been rejected for being a duplicate of the preferred CVE-2025-55182.
Mitigate Critical Vulnerabilities Using Flashpoint
Flashpoint strongly recommends security teams treat this vulnerability with utmost urgency. Our vulnerability research team will continue to monitor this vulnerability and its downstream impacts. All updates will be provided via Flashpoint’s VulnDB.
Request a demo today and gain access to quality vulnerability intelligence that helps address critical threats in a timely manner.
Request a demo today.
The post Digital Supply Chain Risk: Critical Vulnerability Affecting React Allows for Unauthorized Remote Code Execution appeared first on Flashpoint.
