
 Login

Reading view
Monnai Raises $12 Million for Identity and Risk Data Infrastructure
The company will use the investment to accelerate the adoption of its solution among financial institutions and digital businesses.
The post Monnai Raises $12 Million for Identity and Risk Data Infrastructure appeared first on SecurityWeek.
AI and the Corporate Capture of Knowledge
More than a decade after Aaron Swartz’s death, the United States is still living inside the contradiction that destroyed him.
Swartz believed that knowledge, especially publicly funded knowledge, should be freely accessible. Acting on that, he downloaded thousands of academic articles from the JSTOR archive with the intention of making them publicly available. For this, the federal government charged him with a felony and threatened decades in prison. After two years of prosecutorial pressure, Swartz died by suicide on Jan. 11, 2013.
The still-unresolved questions raised by his case have resurfaced in today’s debates over artificial intelligence, copyright and the ultimate control of knowledge.
At the time of Swartz’s prosecution, vast amounts of research were funded by taxpayers, conducted at public institutions and intended to advance public understanding. But access to that research was, and still is, locked behind expensive paywalls. People are unable to read work they helped fund without paying private journals and research websites.
Swartz considered this hoarding of knowledge to be neither accidental nor inevitable. It was the result of legal, economic and political choices. His actions challenged those choices directly. And for that, the government treated him as a criminal.
Today’s AI arms race involves a far more expansive, profit-driven form of information appropriation. The tech giants ingest vast amounts of copyrighted material: books, journalism, academic papers, art, music and personal writing. This data is scraped at industrial scale, often without consent, compensation or transparency, and then used to train large AI models.
AI companies then sell their proprietary systems, built on public and private knowledge, back to the people who funded it. But this time, the government’s response has been markedly different. There are no criminal prosecutions, no threats of decades-long prison sentences. Lawsuits proceed slowly, enforcement remains uncertain and policymakers signal caution, given AI’s perceived economic and strategic importance. Copyright infringement is reframed as an unfortunate but necessary step toward “innovation.”
Recent developments underscore this imbalance. In 2025, Anthropic reached a settlement with publishers over allegations that its AI systems were trained on copyrighted books without authorization. The agreement reportedly valued infringement at roughly $3,000 per book across an estimated 500,000 works, coming at a cost of over $1.5 billion. Plagiarism disputes between artists and accused infringers routinely settle for hundreds of thousands, or even millions, of dollars when prominent works are involved. Scholars estimate Anthropic avoided over $1 trillion in liability costs. For well-capitalized AI firms, such settlements are likely being factored as a predictable cost of doing business.
As AI becomes a larger part of America’s economy, one can see the writing on the wall. Judges will twist themselves into knots to justify an innovative technology premised on literally stealing the works of artists, poets, musicians, all of academia and the internet, and vast expanses of literature. But if Swartz’s actions were criminal, it is worth asking: What standard are we now applying to AI companies?
The question is not simply whether copyright law applies to AI. It is why the law appears to operate so differently depending on who is doing the extracting and for what purpose.
The stakes extend beyond copyright law or past injustices. They concern who controls the infrastructure of knowledge going forward and what that control means for democratic participation, accountability and public trust.
Systems trained on vast bodies of publicly funded research are increasingly becoming the primary way people learn about science, law, medicine and public policy. As search, synthesis and explanation are mediated through AI models, control over training data and infrastructure translates into control over what questions can be asked, what answers are surfaced, and whose expertise is treated as authoritative. If public knowledge is absorbed into proprietary systems that the public cannot inspect, audit or meaningfully challenge, then access to information is no longer governed by democratic norms but by corporate priorities.
Like the early internet, AI is often described as a democratizing force. But also like the internet, AI’s current trajectory suggests something closer to consolidation. Control over data, models and computational infrastructure is concentrated in the hands of a small number of powerful tech companies. They will decide who gets access to knowledge, under what conditions and at what price.
Swartz’s fight was not simply about access, but about whether knowledge should be governed by openness or corporate capture, and who that knowledge is ultimately for. He understood that access to knowledge is a prerequisite for democracy. A society cannot meaningfully debate policy, science or justice if information is locked away behind paywalls or controlled by proprietary algorithms. If we allow AI companies to profit from mass appropriation while claiming immunity, we are choosing a future in which access to knowledge is governed by corporate power rather than democratic values.
How we treat knowledge—who may access it, who may profit from it and who is punished for sharing it—has become a test of our democratic commitments. We should be honest about what those choices say about us.
This essay was written with J. B. Branch, and originally appeared in the San Francisco Chronicle.
Cyber Insights 2026: Social Engineering
We've known that social engineering would get AI wings. Now, at the beginning of 2026, we are learning just how high those wings can soar.
The post Cyber Insights 2026: Social Engineering appeared first on SecurityWeek.
Vibe Coding Tested: AI Agents Nail SQLi but Fail Miserably on Security Controls
Vibe coding generates a curate’s egg program: good in parts, but the bad parts affect the whole program.
The post Vibe Coding Tested: AI Agents Nail SQLi but Fail Miserably on Security Controls appeared first on SecurityWeek.
“Reprompt” attack lets attackers steal data from Microsoft Copilot
Researchers found a method to steal data which bypasses Microsoft Copilot’s built-in safety mechanisms.
The attack flow, called Reprompt, abuses how Microsoft Copilot handled URL parameters in order to hijack a user’s existing Copilot Personal session.
Copilot is an AI assistant which connects to a personal account and is integrated into Windows, the Edge browser, and various consumer applications.
The issue was fixed in Microsoft’s January Patch Tuesday update, and there is no evidence of in‑the‑wild exploitation so far. Still, it once again shows how risky it can be to trust AI assistants at this point in time.
Reprompt hides a malicious prompt in the q parameter of an otherwise legitimate Copilot URL. When the page loads, Copilot auto‑executes that prompt, allowing an attacker to run actions in the victim’s authenticated session after just a single click on a phishing link.
In other words, attackers can hide secret instructions inside the web address of a Copilot link, in a place most users never look. Copilot then runs those hidden instructions as if the users had typed them themselves.
Because Copilot accepts prompts via a q URL parameter and executes them automatically, a phishing email can lure a user into clicking a legitimate-looking Copilot link while silently injecting attacker-controlled instructions into a live Copilot session.
What makes Reprompt stand out from other, similar prompt injection attacks is that it requires no user-entered prompts, no installed plugins, and no enabled connectors.
The basis of the Reprompt attack is amazingly simple. Although Copilot enforces safeguards to prevent direct data leaks, these protections only apply to the initial request. The attackers were able to bypass these guardrails by simply instructing Copilot to repeat each action twice.
Working from there, the researchers noted:
“Once the first prompt is executed, the attacker’s server issues follow‑up instructions based on prior responses and forms an ongoing chain of requests. This approach hides the real intent from both the user and client-side monitoring tools, making detection extremely difficult.”
How to stay safe
You can stay safe from the Reprompt attack specifically by installing the January 2026 Patch Tuesday updates.
If available, use Microsoft 365 Copilot for work data, as it benefits from Purview auditing, tenant‑level data loss prevention (DLP), and admin restrictions that were not available to Copilot Personal in the research case. DLP rules look for sensitive data such as credit card numbers, ID numbers, health data, and can block, warn, or log when someone tries to send or store it in risky ways (email, OneDrive, Teams, Power Platform connectors, and more).
Don’t click on unsolicited links before verifying with the (trusted) source whether they are safe.
Reportedly, Microsoft is testing a new policy that allows IT administrators to uninstall the AI-powered Copilot digital assistant on managed devices.
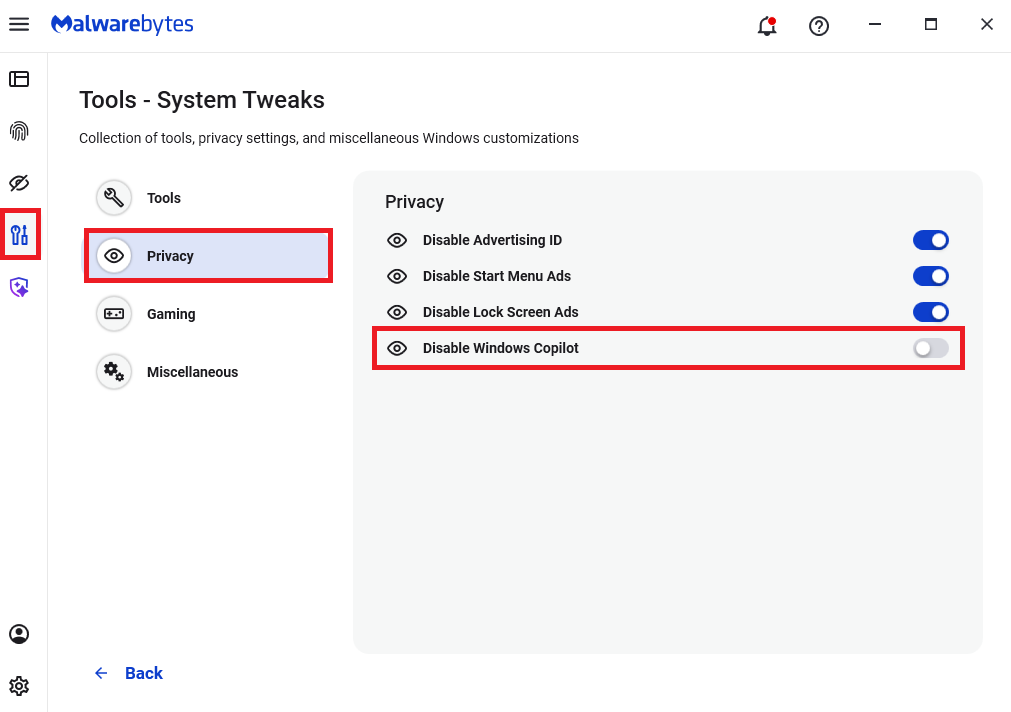
Malwarebytes users can disable Copilot for their personal machines under Tools > Privacy, where you can toggle Disable Windows Copilot to on (blue).
In general, be aware that using AI assistants still pose privacy risks. As long as there are ways for assistants to automatically ingest untrusted input—such as URL parameters, page text, metadata, and comments—and merge it into hidden system prompts or instructions without strong separation or filtering, users remain at risk of leaking private information.
So when using any AI assistant that can be driven via links, browser automation, or external content, it is reasonable to assume “Reprompt‑style” issues are at least possible and should be taken into consideration.
We don’t just report on threats—we remove them
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
isVerified Emerges From Stealth With Voice Deepfake Detection Apps
isVerified provides Android and iOS mobile applications designed to protect enterprise communications.
The post isVerified Emerges From Stealth With Voice Deepfake Detection Apps appeared first on SecurityWeek.
New ‘Reprompt’ Attack Silently Siphons Microsoft Copilot Data
The attack bypassed Copilot’s data leak protections and allowed for session exfiltration even after the Copilot chat was closed.
The post New ‘Reprompt’ Attack Silently Siphons Microsoft Copilot Data appeared first on SecurityWeek.
Building effective AI for the SOC: How Intezer Forensic AI SOC follows Anthropic’s best practices
One of the most influential publications on real-world AI system design is Anthropic’s guide, Building Effective Agents. Its core message is simple:
Effective AI requires structure first, adaptability second.
Anthropic emphasizes that AI agents work best when:
- A deterministic workflow does all the structured work up front
- The agent only activates when uncertainty remains
- The agent begins with full context, not an empty slate
- Tool usage is controlled and evidence-driven
- Human-in-the-loop remains central for oversight and trust
These principles ensure accuracy, avoid hallucinations and keep investigations reproducible, all critical requirements for cybersecurity.
Intezer Forensic AI SOC is built on exactly this philosophy. Our platform uses a dual-mode design with Intezer AI Workflow and AI Agent, completely aligning with Anthropic’s best practices to deliver fast, scalable and highly accurate investigations across a broad range of alerts, all while keeping analysts in the loop.
Here is how Intezer implements Anthropic’s best practices for agents.
Structured first: Intezer AI Workflow handles the majority of alerts
Anthropic advises that AI systems should begin with deterministic workflows instead of free-form reasoning. In cybersecurity, this is essential for accuracy, auditability, trust and scalability (when handling huge volumes of alerts).
Intezer’s AI Workflow mode is a structured triage process designed by security experts and executed with strict consistency. It applies AI only at key decision points, not as the driver of the entire investigation.
This approach provides:
- Deterministic, reproducible results
- High speed due to streamlined, parallelizable steps
- Lower costs because heavy reasoning is used sparingly
- No drift or unexpected branching
- Clear human oversight points
Most alerts, especially well-defined ones, are fully resolved at this stage, giving SOCs broad alert coverage at low cost.
Adaptive only when needed: Intezer AI Agent extends the investigation
Anthropic states that agents should activate only when the structured workflow reaches uncertainty, and only after they inherit the full context. Intezer follows this exactly.
AI Agent mode activates only when the Workflow cannot reach a high-confidence verdict.
At that point, the agent:
- Starts with all evidence collected so far
- Avoids premature assumptions
- Uses tools deliberately and contextually
- Expands the investigation where human analysts would
- Surfaces deeper behavioral patterns or cross-asset correlations
This ensures the agent is guided, not free-floating, and its decisions remain grounded in evidence, not guesswork.
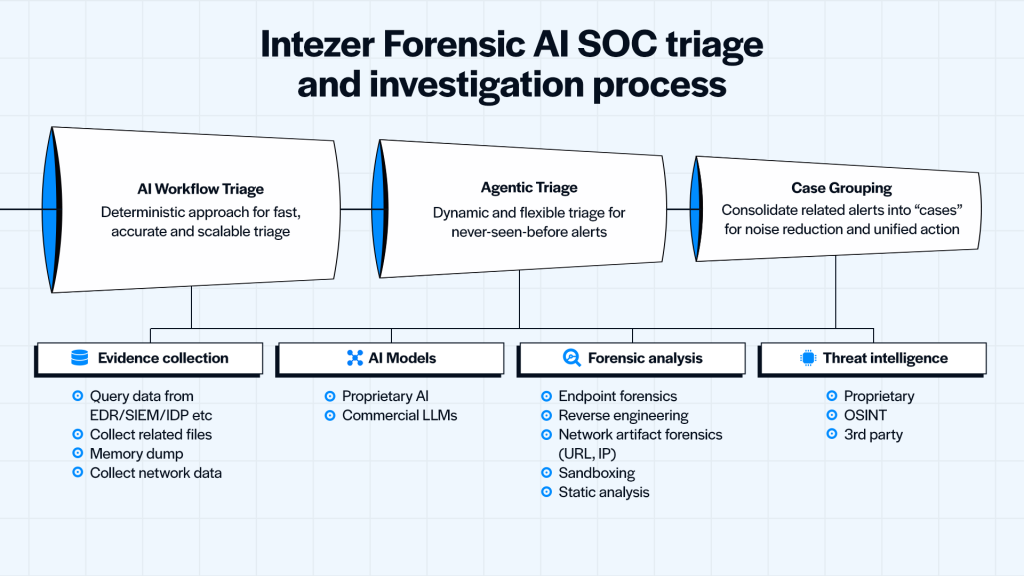
Tools the AI Agent can leverage once activated
- Dynamic SIEM queries
- EDR/XDR telemetry lookups
- Identity provider (IDP) investigation
- Behavioral analysis of processes and command lines
- User activity mapping
- Process ancestry and parent-child correlation
- Intezer’s historical alert database
- Code DNA similarity and malware lineage tracking
- Additional host, memory, or file-based forensics
The result is deeper investigation where it matters, without unnecessary cost.
Human-in-the-loop by design
Intezer keeps human analysts at the center so they can review and override conclusions, and trace every decision made by Intezer. Of course, all evidence and reasoning is grounded in forensic data and is fully transparent and explainable for beginners and advanced analysts alike.
This aligns with Anthropic’s principle that humans remain final decision-makers, especially in high-stakes domains like cybersecurity.
How this architecture improves SOC performance
Intezer’s adherence to Anthropic’s best practices produces measurable outcomes across the three most important SOC metrics: accuracy, coverage, and speed, while also reducing cost.
Accuracy
Intezer’s approach of combining deterministic forensics + adaptive AI = best-in-class verdict quality.
- The structured workflow prevents hallucinations
- The AI Agent only activates with strong guardrails
- Context inheritance ensures consistent reasoning
- Analysts always have visibility and control
This hybrid approach dramatically reduces false positives and prevents premature conclusions.
Triage of all alerts, including low-severity (where threats often hide)
Because AI Workflows handle the bulk of alerts inexpensively and AI Agents only run when needed, heavy and expensive reasoning calls are minimized
This frees SOCs from cherry-picking which alerts to ingest allowing them to triage and investigate them all.
This is crucial for:
- High-volume enterprise environments
- MSSPs with strict SLAs
- Cloud-scale detection pipelines
- 24/7 monitoring teams
You get broad alert coverage without inflating compute costs.
Speed: Structured steps + adaptive depth
- Workflow mode resolves most alerts within seconds
- Agents accelerate investigations that normally take analysts hours
- No bottlenecks, no backlog, no manual evidence gathering
The result is a SOC where every alert is investigated quickly, consistently, and with forensic depth.
Table of how Intezer’s design reflects Anthropic’s guidance
| Anthropic best practice | How Intezer implements it |
| Start with deterministic workflows | AI Workflow handles structured triage with predefined expert steps |
| Activate agents only when needed | AI Agent triggers only when confidence is insufficient |
| Give agents full context | Agent inherits the entire Workflow evidence set |
| Control tool usage | Agent selects tools based on evidence, not speculation |
| Maintain human-in-the-loop | Analysts can verify, guide, and override conclusions |
| Prioritize safety and reproducibility | Every action is logged, justified, and traceable |
Conclusion: Anthropic’s Agent principles in a real SOC
Anthropic’s framework for building effective agents is now influencing industries far beyond general AI research. Intezer Forensic AI SOC might be one of the strongest real-world implementations of these practices in cybersecurity.
By combining:
- Deterministic workflows for reliable baseline investigations
- Adaptive agents for deeper reasoning when needed
- Human oversight for trust and accountability
- Cost efficiency enabling full-pipeline alert coverage
Intezer is able to deliver fast, accurate, and scalable triage that transforms SOC operations.
Learn more about how you can transform your SOC today.
The post Building effective AI for the SOC: How Intezer Forensic AI SOC follows Anthropic’s best practices appeared first on Intezer.
Thinking Like an Attacker: How Attackers Target AI Systems
In September 2025, security researchers at Anthropic uncovered something unprecedented: an AI-orchestrated espionage campaign where attackers used Claude to perform 80–90% of a sophisticated hacking operation. The AI handled everything from reconnaissance to payload development, demonstrating that artificial intelligence has fundamentally changed the threat landscape, not just as a tool for defenders, but as both
The post Thinking Like an Attacker: How Attackers Target AI Systems appeared first on OffSec.
WitnessAI Raises $58 Million for AI Security Platform
The company will use the fresh investment to accelerate its global go-to-market and product expansion.
The post WitnessAI Raises $58 Million for AI Security Platform appeared first on SecurityWeek.
