❌

Reading view

mSecure tells users to change passwords but won’t say why [updated]

Password manager mSecure has warned current and former customers to protect the confidential information stored in its app after detecting “suspicious activity.”

But its advice about what users should do comes without an explanation of what happened or whose information might be at risk.

The warning leaves users to decide whether to replace credentials—and whether it’s safe to store replacements in mSecure.

While those are perfectly reasonable questions, mSecure’s warning does not answer them.

In an email published by The Hacker News and sent to customers on November 3, mSecure’s developer, mSeven Software, said:

“mSeven Software (‘mSeven’) recently learned of suspicious activity associated with the mSecure password management application. In response, mSeven quickly launched an investigation, took steps to mitigate the issue, and engaged external cybersecurity experts to assist.”

The notice recommends that customers “immediately take steps to protect all confidential information” stored in mSecure. Those steps:

“may include changing passwords, resetting or re-enrolling two-factor authentication methods, or removing existing passkeys.”

But the notice does not identify the suspicious activity, when it occurred, which systems were involved, or whether anyone accessed customers’ stored information. The Register, which also reviewed the email, noted that the company had not explained whether customers’ secrets were exposed.

How to be safe

Because the scope of the incident is unknown, we recommend prioritizing your most important accounts while mSeven investigates.

Changing your mSecure password alone may not be enough if someone has already accessed your account. mSecure’s documentation explicitly warns that someone may already have made a backup of its contents. That guidance does not establish what happened in this incident.

Users should not have to wait for a completed forensic investigation before receiving useful guidance. They need to know who should act, which credentials need attention, and whether the tool they would normally use to manage those changes remains safe to use.

Until mSeven provides those answers, our advice is to prioritize your most important accounts, replace the relevant credentials through official services, and avoid destructive account resets:

  • Change passwords through each service’s official website or app, beginning with your primary email, financial accounts, work accounts, and accounts used to recover access to other services. Use a new, different, strong password for each.
  • Review two-factor authentication stored in the vault. If that could be compromised by unauthorized access, consider re-enrolling that account’s authenticator through the service’s security settings.
  • For passkeys stored in mSecure, use each website or app’s account-security settings to remove the old registration and create a replacement with a different provider as a precaution. But make sure another working sign-in method is available first.
  • Think carefully about where replacement credentials go. The notice does not establish whether saving new credentials in mSecure is safe. For users rotating important accounts now, using a different password manager temporarily is a reasonable precaution.

We’ll keep you posted if we learn more about this incident, so stay tuned.

Update November 6, 2026

According to follow-up messages attributed to mSecure support and reproduced by multiple customers on the company’s forum, the incident affects only users who synchronized with mSecure Cloud. We have not located a directly published company statement confirming that scope.


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 
  •  

CrashStealer, a new infostealer for macOS: how it works and how to stay safe | Kaspersky official blog

Mac users have historically trusted their operating system to keep them safe. That peace of mind mostly comes from Apple’s strict control over its ecosystem, and the fact that macOS has historically faced fewer mass attacks than Windows. However, that doesn’t mean Macs are invulnerable: threats do exist, and new ones emerge all the time. Over just the past few weeks, security researchers have published reports on at least two new campaigns that target Apple devices.

The malware used in one of the campaigns has been dubbed CrashStealer, while the other is known as ClickLock. Both rely on different tricks to force users into entering their Mac password, which attackers then use to steal account credentials, crypto assets, documents, and much more. In today’s post, we take a close look at how CrashStealer operates — and how to avoid falling victim to it.

A videoconferencing app with CrashStealer inside

It was back in May 2026 that researchers spotted the first signs this malware was being developed, and by early July, they caught it operating in the wild. The malware earned its name because of its core mechanism: it disguises itself as the macOS built-in crash reporting tool (CrashReporter) while functioning as an infostealer designed to hijack sensitive data.

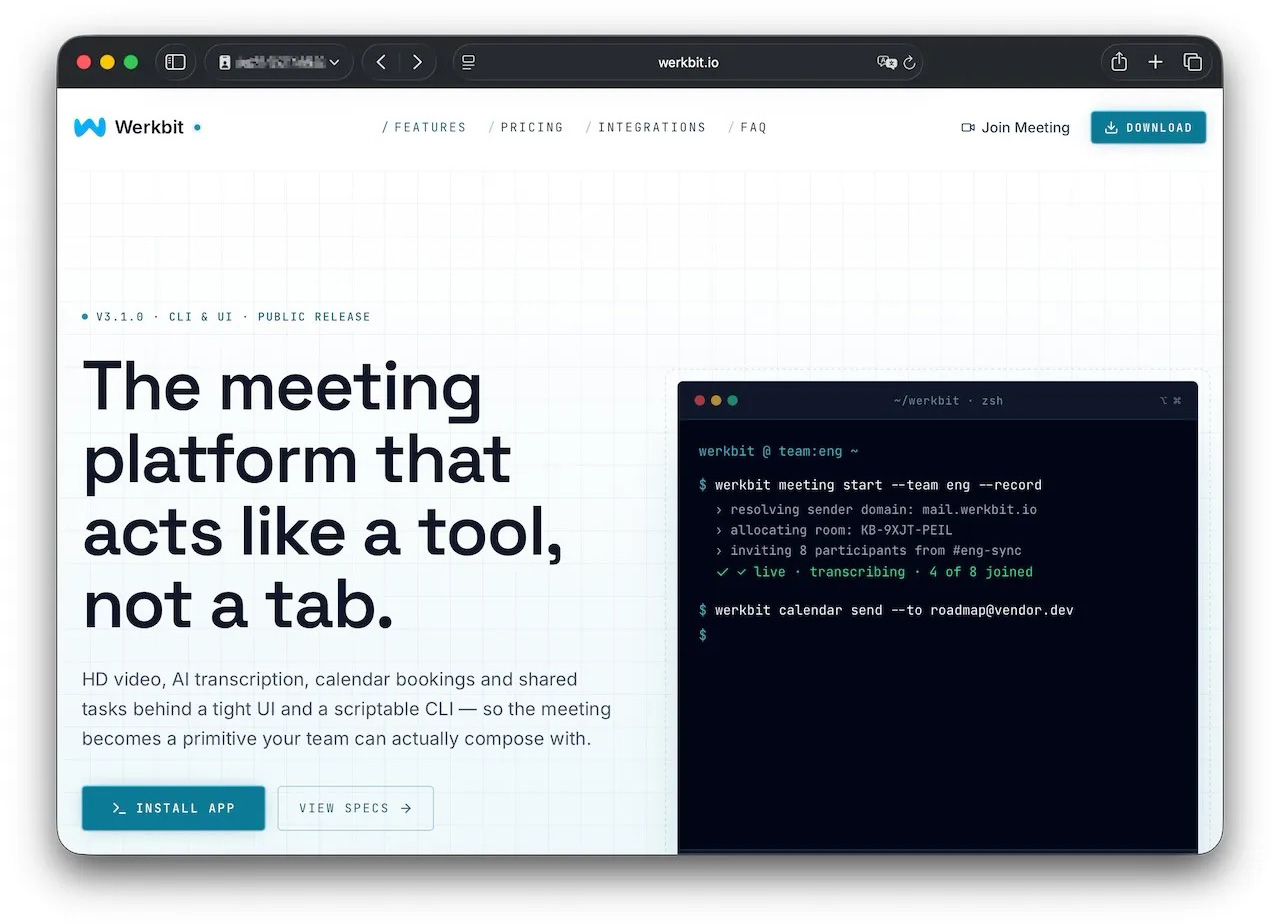
Researchers managed to trace one of the websites users visited to download the malware. The site poses as a legitimate platform for distributing the video conferencing tool Werkbit.

A website that distributes CrashStealer under the guise of the Werkbit app

According to researchers, this is the site victims used to download Werkbit, which secretly contained the CrashStealer malware loader. Source

However, you can’t just visit the site and download the software. Before downloading, visitors are asked to enter a special meeting PIN. This setup likely allows the attackers to limit the distribution scope by targeting only specific, pre-selected victims. Exactly how the cybercriminals choose their targets and deliver the PIN remains unknown.

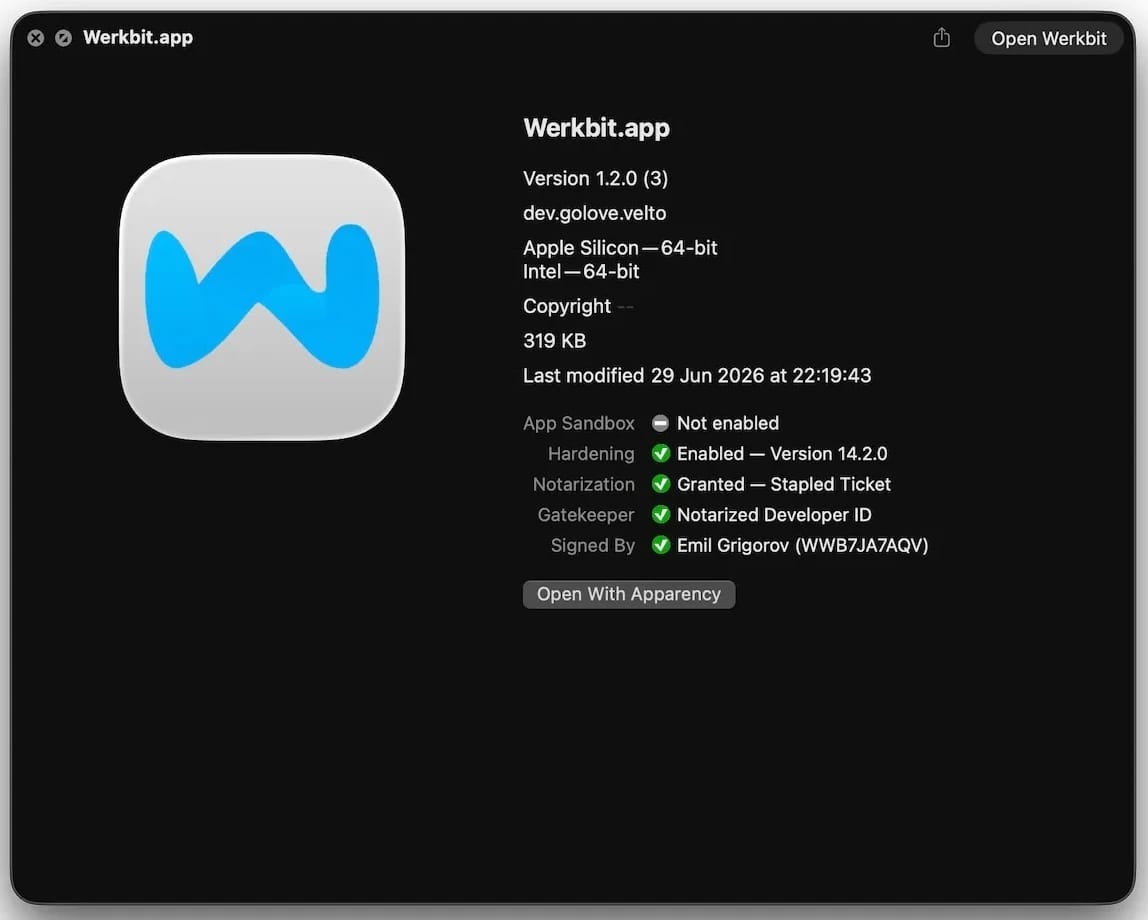
The “lucky” users with a code end up installing the initial malicious payload — named Werkbit Setup. Interestingly, it carries a valid Apple developer certificate and has successfully passed Apple’s notarization process — meaning it cleared the automated prescan for malicious code. As a result, the attackers manage to bypass the operating system’s built-in Gatekeeper defense. This allows the payload to launch without triggering the usual untrusted software warnings.

Signed and notarized Werkbit Setup installer

The Werkbit Setup installer is signed with a valid Apple developer certificate and has passed notarization. Source

Once launched, Werkbit Setup first reaches out to GitHub. Researchers believe using this popular platform helps attackers blend in by making these initial network requests look far less suspicious to security tools. After retrieving instructions from a GitHub repository, the program connects directly to the attackers’ server to fetch CrashStealer itself.

The loader then saves the malware to a temporary macOS folder, launches it, and wipes most of the intermediate setup files. As a result, a fully functional infostealer is up and running within seconds of Werkbit Setup starting. By the way, the user never gets any videoconferencing app.

How CrashStealer works

Unlike the Werkbit Setup loader, the CrashStealer malware itself isn’t signed with an Apple developer certificate. To keep users from suspecting anything, the malware disguises itself as the built-in macOS crash reporting tool, CrashReporter, by using the exact same name, app identifier, and a similar icon.

Once launched, CrashStealer completes a sequence of steps to gain access to sensitive data, establish persistence in the system, and cover its tracks:

  1. Remove metadata — including the attribute that flags the app as an internet download.
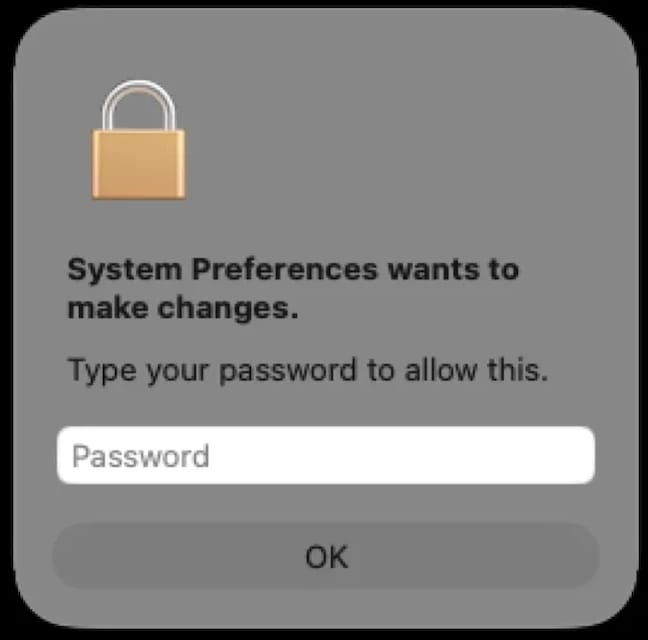
  2. Display a fake system prompt asking for the user’s macOS password.
  3. Use the previously captured credentials to gain access to Keychain, the built-in macOS password manager.
  4. Check the computer for installed security tools and malware analysis software.
  5. Collect saved browser passwords, cookies, Keychain contents, and data from other password managers and crypto wallets.
  6. Encrypt the data it stole and prepare it for forwarding to the attackers’ server.
  7. Create a copy of itself and establish persistence to launch automatically every time macOS boots.
  8. Delete temporary files and other installation traces to make detection much harder.

Step two deserves a closer look. The password prompt that the user sees looks extremely convincing. What’s more, the malware immediately verifies whether the credentials are correct: if you make a typo and enter an invalid password, CrashStealer will pop the window right back up to ask you again.

Fake macOS password prompt

Once launched, CrashStealer displays a pop-up that mimics the standard macOS password request. Source

What data is CrashStealer after?

CrashStealer’s hit list is massive. First and foremost, its operators target Keychain: the built-in macOS password manager where the system stores account credentials, cryptographic keys, certificates, tokens, and more.

Users of third-party password managers aren’t safe either: the malware steals data from 14 of these services, including 1Password, Bitwarden, LastPass, Dashlane, Keeper, KeePassXC, NordPass, Enpass, and RoboForm.

In addition, the malware collects all credentials and cookies stored in Chromium-based browsers — Chrome, Brave, Edge, Opera, Opera GX, Vivaldi, Chromium, and NAVER Whale — as well as Firefox. The attackers clearly have a strong interest in crypto assets: CrashStealer specifically targets data from 80 different crypto wallet extensions, including MetaMask, Phantom, Coinbase Wallet, Trust Wallet, Rabby, Exodus, Keplr, and Solflare.

Finally, the malware scans the Documents and Downloads folders to pick files that might be of interest to the cybercriminals. CrashStealer encrypts all the stolen data with the AES-256-GCM algorithm, ZIP’s it up, and sends it to the attackers’ server.

How to protect your device

The spike in attacks on macOS is a clear wake-up call: Apple users need to get proactive about their security. We recommend:

  • Researching apps online before installing them
  • Sticking to utilities from official app stores whenever possible
  • Using a reliable security solution that blocks malicious websites and stops malware activity on your device
  • Keeping all your credentials and banking details in a secure password manager. One option is Kaspersky Password Manager— which, notably, wasn’t listed among the apps targeted by CrashStealer

Kaspersky security solutions detect the malware described in this post and assigns to it the verdicts HEUR:Trojan-Downloader.OSX.Agent.gen and HEUR:Trojan-PSW.OSX.Agent.gen.

  •  

World Cup 2026: watch out for these scams | Kaspersky official blog

The World Cup attracts a great many fans — but also a great many scammers. While millions of fans tune in to watch the matches, cybercriminals are hard at work trying to get at their money and personal data. In fact, we’ve already flagged more than 336 fake websites designed to look exactly like the official World Cup page! As the biggest sporting event of the year heats up, here are the top red flags you need to watch out for.

Totally Legit Free Streams (No Scam)

Scoring a seat at WC26 has turned into quite the mission. Soccer fans are furious over ticket prices, which have officially been dubbed the highest in World Cup history. On top of lodging and travel costs, the situation is made even worse by America’s stringent immigration policies — where referees, team staff, and even players have faced major visa and entry headaches. But fans still want to watch the games, and that’s exactly where fake streaming platforms step in to “help”.

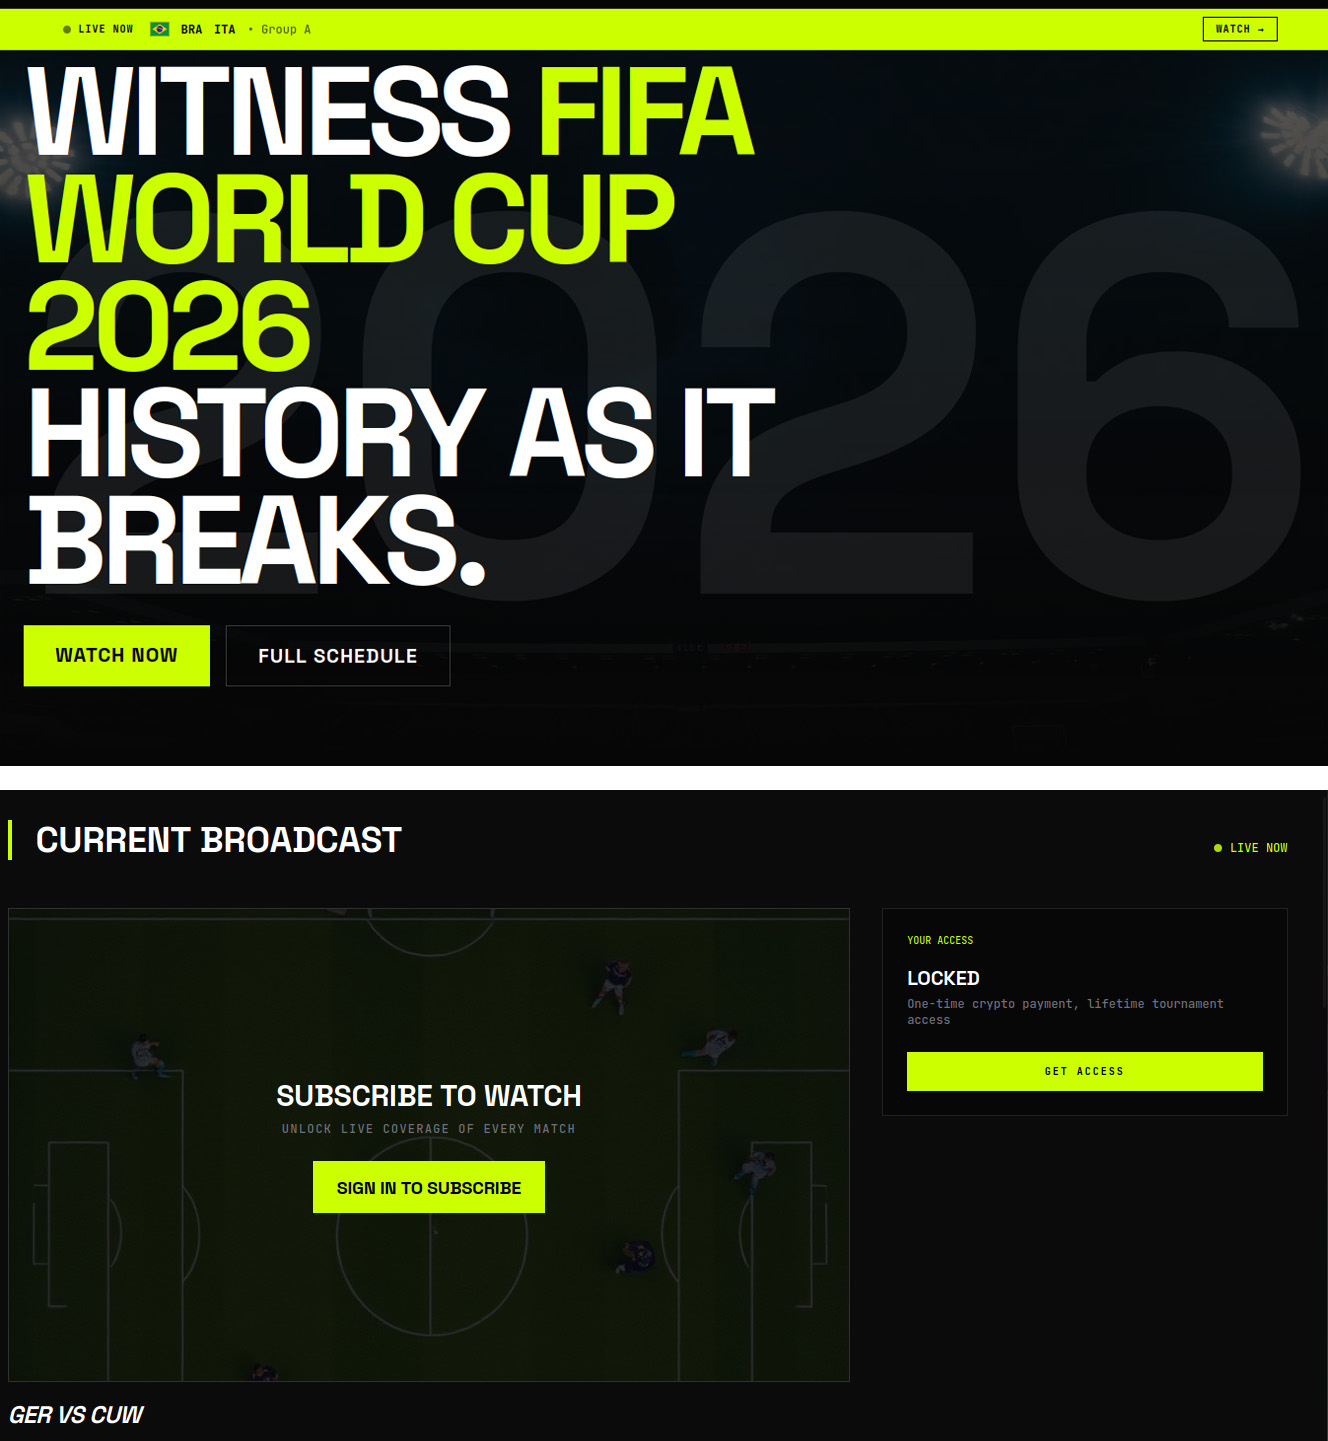
Here’s how the scam plays out: cybercriminals set up fake websites promising free access to World Cup match streams. But the moment you click Watch Now, you’re prompted to sign up and then pay for “lifetime access” to the entire tournament. In the example below, they’re asking for cryptocurrency — which is still a bit unusual, since scammers typically prefer good old-fashioned bank cards.

An example of a fake video streaming website requiring users to register and pay with cryptocurrency to watch all World Cup 2026 matches

An example of a fake video streaming website requiring users to register and pay with cryptocurrency to watch all World Cup 2026 matches

Fans who are desperate to catch their favorite teams live risk losing not just their money, but also their personal data, which hackers can later weaponize in targeted phishing attacks.

A losing bet

Match result predictions and sports betting always skyrocket in popularity during the World Cup, and scammers waste no time cashing in on the trend. And behind the flashy slogans lie classic scam tactics.

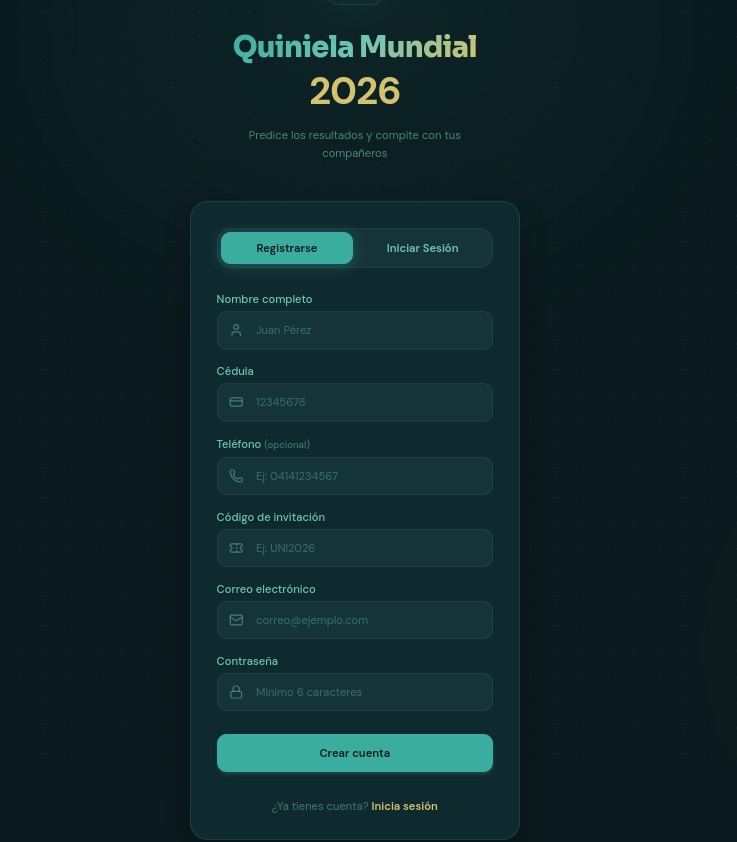
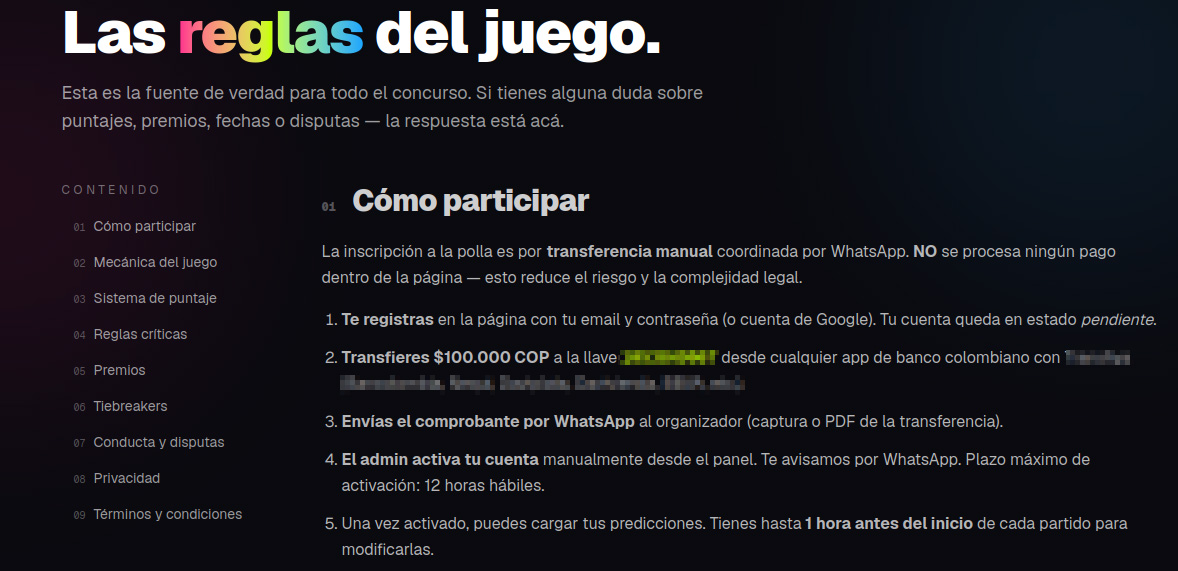
Take this beautifully designed Spanish-language website. To sign up, it demands a massive amount of personal information, including your full name, national ID number, email address, and phone number — and, of course, it asks you to create a password. If a victim uses the exact same password for multiple accounts, they’re essentially handing the keys to their digital life over to cybercriminals.

To guess match outcomes on this site, you have to hand over way too much personal info — everything short of biometrics

To guess match outcomes on this site, you have to hand over way too much personal info — everything short of biometrics

Another site, specifically targeting users in Colombia, turned the sign-up process into a paid ordeal — and it features every trick in the book.

  • To “verify” your profile, you’re forced to use WhatsApp under the guise of avoiding legal complications.
  • Before your account is activated, you must make a deposit. This means sending 100 000 Colombian pesos (about $29) to a specified account and texting the receipt to an “administrator” on WhatsApp.
  • Next, you’re told to wait 12 hours for the “administrator” to manually activate your profile.
  • Only after all of this do the scammers tell you can place unlimited bets (of course not true).
These scammers built a whole website, but they do all their business over WhatsApp. That's a red flag!

These scammers built a whole website, but they do all their business over WhatsApp. That’s a red flag!

In many countries — including Colombia — sports betting is strictly regulated. Only a handful of licensed operators are legally allowed to run these sites, and users are required by law to verify their identity. Because of this, these shady workarounds can look tempting to people who love to gamble but don’t want to — or can’t — go through the official verification process.

Unfortunately, the scammers always win in this scenario. They walk away with your initial deposit and every single bet you place on their site. At the end of the day, their only real goal is to drain their victims’ wallets for as much as they possibly can.

Discounts for collectors!

The World Cup isn’t just about the matches; it also drives record-breaking sales of collectible merchandise — stickers, scarves, team jerseys, official match balls, and more. Naturally, plenty of scammers are eager to get a piece of that action.

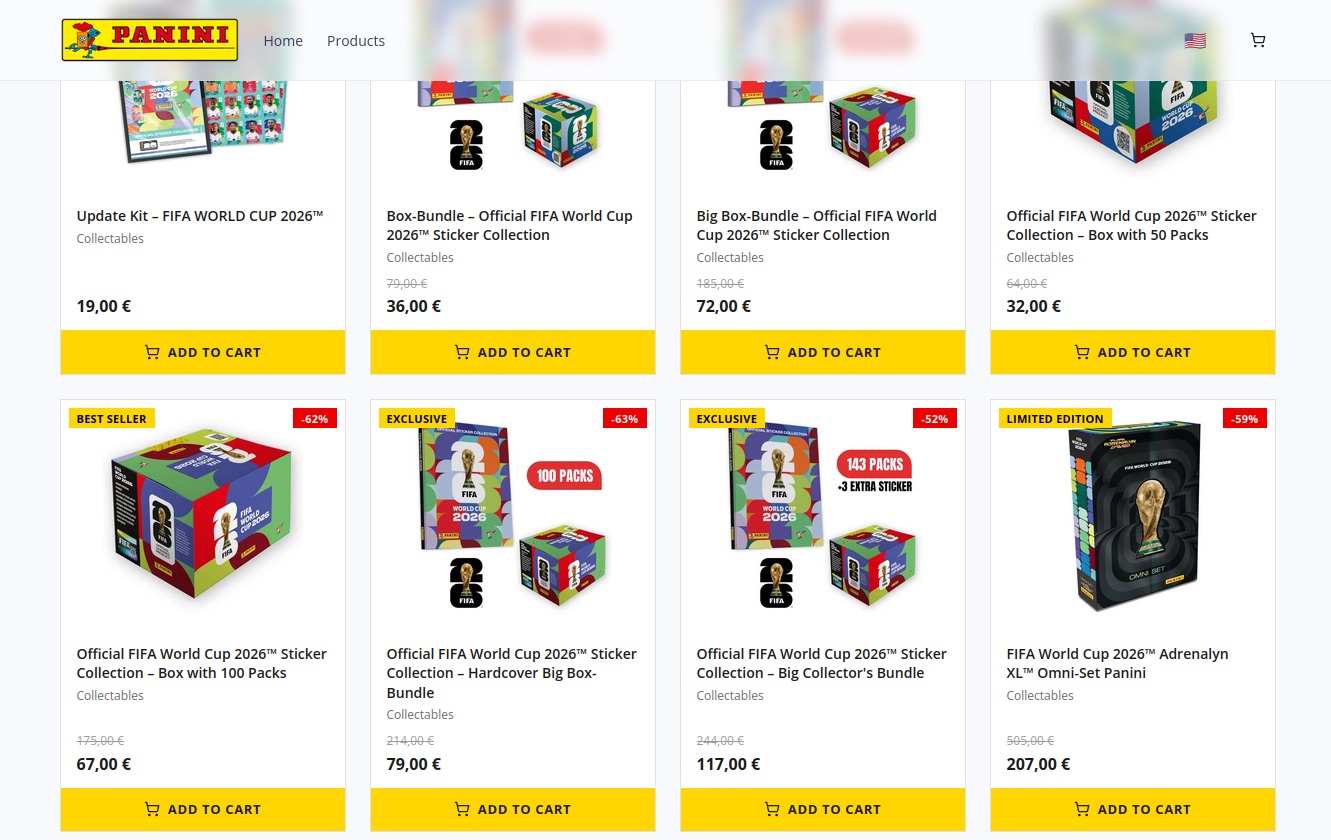
Take a look at this website offering “exclusive, limited-edition” stickers and albums. Notice anything suspicious?

Talk about a steal! Too bad the whole website is a scam

Talk about a steal! Too bad the whole website is a scam

Check out those prices: everything is heavily discounted, even though the tournament is in full swing. All it takes is a quick price check against the real deal to spot the trap. In the screenshot above, the scammers are charging 67 euros for a sticker collection. On actual online marketplaces, that exact same set goes for at least twice as much, and on the official Panini website, it’s three times the price.

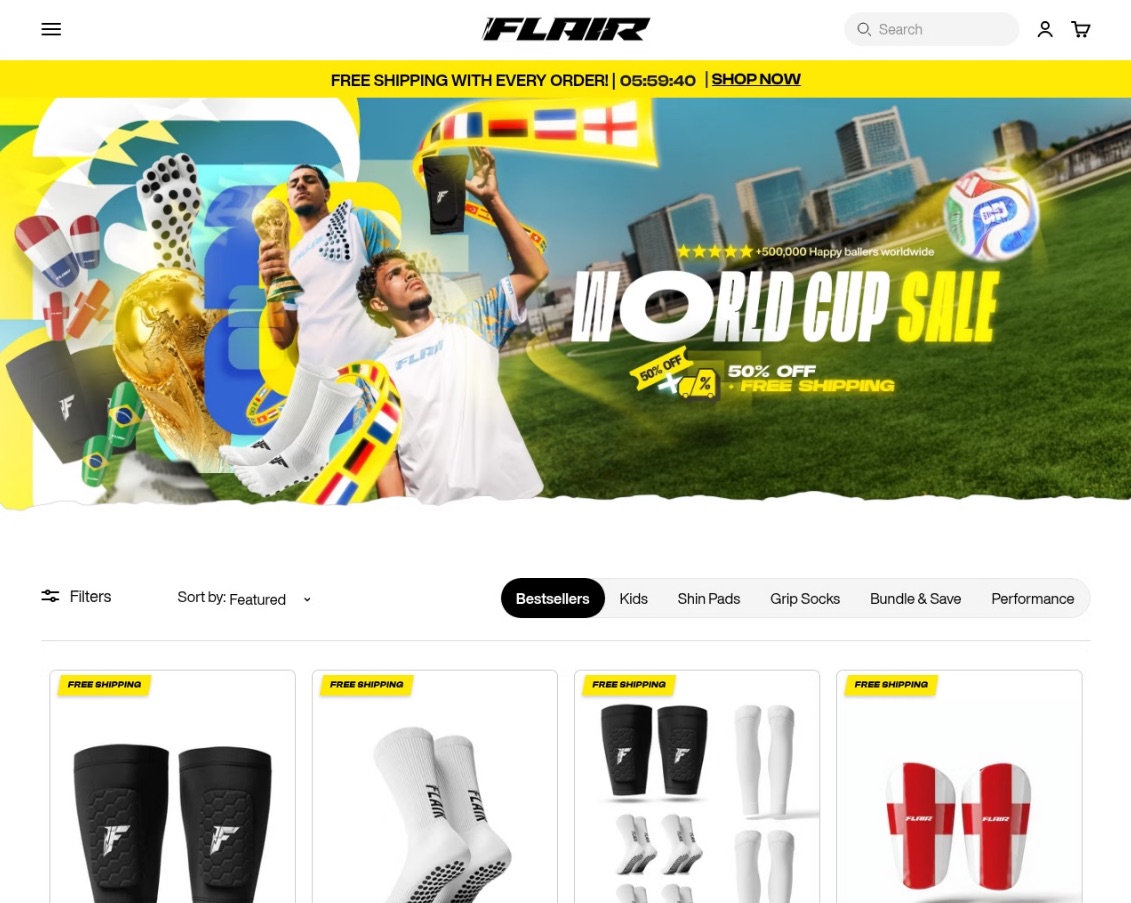
Fake websites mimicking popular sporting goods stores also offer to sell you shin guards, socks, jerseys, and any other gear. Of course, you’ll never see the merchandise, and you’ll lose both your money and your bank card details.

When they've absolutely no intention of delivering any products, they can easily offer massive discounts and free shipping

When they’ve absolutely no intention of delivering any products, they can easily offer massive discounts and free shipping

Deals that seem too good to be true are one of the biggest red flags. To make matters worse, with the help of AI, fake websites now look just as professional as the real ones, making them harder than ever to spot. That’s why we recommend installing our security suite before you start shopping online. It blocks phishing sites in real time and uses the Safe Money feature to keep your financial data secure.

Soccer by mail

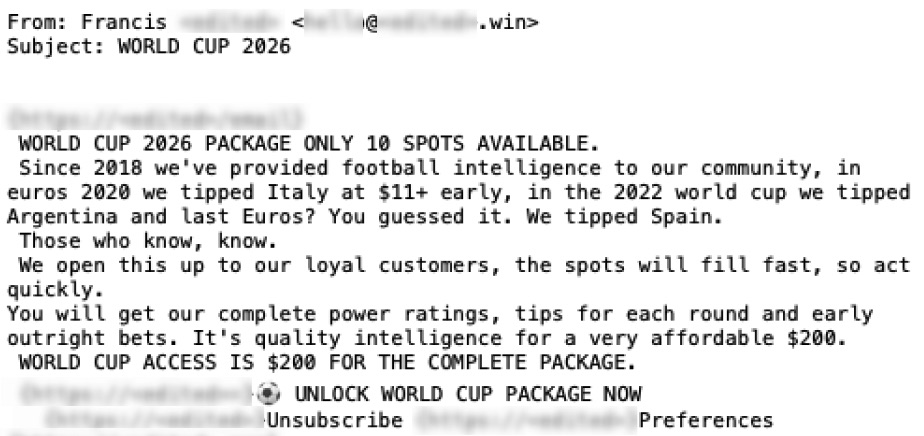
Another attack strategy involves spam campaigns centered around the World Cup. In one email, our experts uncovered an ad for a soccer analytics and betting-tips service. It uses the classic high-pressure playbook: “ONLY 10 SPOTS AVAILABLE” — so hurry up before they run out! Naturally, access comes with a price tag: AU$200.

Spammers hurrying the victim to make a decision as quickly as possible

Spammers hurrying the victim to make a decision as quickly as possible

This scheme targets fans who are into sports betting, and paying for these types of services usually ends one of two ways for them: they either lose their money with zero guarantee of getting actual predictions, or get sucked into an even deeper, multi-step financial trap.

How to avoid falling for the scams

Across all these scenarios, the World Cup is just another convenient pretext for cybercriminals. Once the tournament wraps up, they’ll most certainly pivot back to their usual tricks — like fake job offers or Telegram phishing scams — until the next Olympics or soccer tournament rolls around and they switch right back to sport.

Our research consistently shows that online fraud has evolved into a massive illegal enterprise. You aren’t just up against lone scammers anymore; you’re dealing with large criminal networks. When it comes to defense, the best approach is a proactive one. By installing Kaspersky Premium, you can safeguard all your devices from malware, phishing, spam, and malicious or lookalike websites. Plus, the included Kaspersky Password Manager will generate unique complex passwords, securely store your sensitive data — like documents and bank cards — and stop you from auto-filling your credentials on fake sites.

  • Watch the games only on legitimate streaming platforms. Don’t trust fake reviews and never enter your bank card information on unverified sites. Keep an eye out not just for sketchy streaming websites, but also for fake IPTV apps. As we’ve covered in detail before, scammers frequently use these to infect your devices with Trojans.
  • Shop smart. The best way to avoid getting ripped off is to buy merchandise exclusively through official channels (where you won’t see suspiciously deep discounts), or simply buy your gear in person at official retail locations.
  • Don’t click suspicious links. If a deal that’s too good to be true lands in your inbox — whether it’s exclusive betting tips or anything else — just ignore it and hit delete.
  • Avoid logging in through Telegram bots. At the very least, this saves you from future headaches and annoying spam. At best, it keeps your account from being hijacked and your crypto from being stolen.
  • Switch to passkeys wherever possible. Unlike traditional passwords, which are easily stolen and can be typed into any fake login page, a passkey is cryptographically tied to a specific website and won’t work on a phishing page. Kaspersky Password Manager can easily store and sync your passkeys across all your devices.

What other ruses do scammers use to make a quick buck? Check out our other posts:

  •  

Password Managers Vulnerable to Vault Compromise Under Malicious Server

Researchers at ETH Zurich have tested the security of Bitwarden, LastPass, Dashlane, and 1Password password managers.

The post Password Managers Vulnerable to Vault Compromise Under Malicious Server appeared first on SecurityWeek.

  •  

The Paper Password Manager

Michael Allen // Every year around the holidays I end up having a conversation with at least one friend or family member about the importance of choosing unique passwords for […]

The post The Paper Password Manager appeared first on Black Hills Information Security, Inc..

  •  
❌