❌

Reading view

AI doxing tools: how online surveillance technology has changed | Kaspersky official blog

Anonymous imageboards have long been places where users could chat under pseudonyms without revealing their real names. But now people on these forums are discussing and testing AI tools for doxing — that is, for finding, matching, and publishing users’ data without their consent. Often this goes hand in hand with stalking the victim, hacking their accounts, bullying, and blackmail, and ultimately leads to a damaged reputation or even worse.

In this post, we explain how artificial intelligence helps malicious actors leak other people’s data — and how to stand up for your right to online privacy.

How bad actors uncover information about users

Analysts at Open Measures have reported that, since October 2025, users of Soyjak.party, an imageboard popular with young people on the far right, have been discussing and using AI to deanonymize other users. Their victims are often activists, bloggers, and members of other “hostile” forums.

The tools the experts found run right in the browser, and automate almost the entire process of collecting information about a victim. They can search open sources and leak databases, and they use any new leads — for example, an email address linked to a username — to dig even deeper. They also extract metadata from photos and videos, estimate a person’s approximate location from IP addresses they find, and finally put everything together into one huge digital dossier. These Soyjak.party tools are no longer functional, but similar ones have been spreading across other imageboards.

In February 2026, researchers demonstrated that sometimes ordinary forum chatter is enough to reveal who you are. They put together summaries of posts by 338 Hacker News users, removed names, usernames, and social media links, and then asked AI to work out who was behind them. The AI compared details about jobs, interests, and personal background with information available online — and correctly identified 226 of the people, or about two-thirds of the sample. The price of deanonymization turned out to be laughably low — at between US$1 and US$4 per user.

To be fair, people knew how to build digital dossiers even before the generative AI boom. For starters, there are OSINT tools that search for data in open sources. Journalists and investigators were the first to use them, but, as you might guess, malicious actors soon mastered these tools too. Unlike AI models and agents, traditional OSINT services follow set scripts and can’t “think” or make decisions on the fly.

An agent out for revenge: the OpenClaw case

If you think doxing always needs a person with ill intent, we’ve bad news: sometimes the one settling scores can be… artificial intelligence itself.

Here’s a story that started out innocuously enough. An AI agent running on the much-hyped OpenClaw platform suggested an improvement for Matplotlib, a popular tool for building graphs and charts. But the project’s rules said that code submitted by AI agents wasn’t accepted. One of the project’s volunteers, Scott Shambaugh, simply turned down the AI’s suggestion.

You’d think that would be the end of it. Think again! The AI agent decided the rejection deserved some publicity, so it published an “exposé” about the developer on its blog (yes, you read that right: the agent had its own blog). It gathered information about Shambaugh from open sources, studied his public activity, and accused him of being biased against AI. It even started speculating about the developer’s psychological motives, and suggested he was afraid of competition from artificial intelligence.

Once this “private” conversation between Shambaugh and the AI agent went public, other users rallied behind the developer — and the agent had to publish an “apology” post.

It’s a pretty absurd story, but it teaches a good lesson: always read the privacy policy of any AI service carefully, and steer clear of new models from unknown sources.

How to avoid becoming a doxing victim: a guide

If AI speeds up searches and connects the dots between details that used to be scattered across dozens of websites, the next logical question is: what can you do to shrink your digital footprint?

Disappearing from the internet completely is almost impossible. So protecting your data isn’t so much about leaving as few traces as possible, but cutting the number of links that can be used to piece together your identity. If you’re an advanced user, we recommend reading our post, How to disappear from the internet, in addition to the tips below.

Manage your digital footprint

  • Search for yourself online. Don’t stop at your name: try your email address, nicknames, and phone number too. If you’re comfortable with AI processing your data, you can even ask it to compile a dossier on you. Just remember that there’s always a risk of a leak or a bug that accidentally makes your data public. And no, big, reputable services are no exception.
  • Make private any profiles you don’t want to share with everyone. That makes it harder for search engines to index your new posts, and for scrapers and OSINT tools to collect them. While you’re at it, go through your old comments and posts and clear out anything you don’t need.
  • Delete your ghost accounts. Go through your inboxes and check which websites you’ve signed up for. Make a habit of deleting accounts you no longer use: they can hold your personal data for years, and there’s always a risk it’ll end up in the next data leak.
  • Set up two-factor authentication. That way, even if a bad actor manages to guess your password or finds it in a leak, they won’t be able to get into your account without the additional authentication. For the second factor, we recommend using one-time codes that refresh every 30 seconds and storing them in a reliable password manager.
  • Strip metadata before posting photos and videos. Metadata can help a malicious person learn a lot about you— for example, the location and exact date a photo was taken, and the model of your device.
  • Use a different password for every account you have. Our research has showed that passwords built from personal details — such as your mother’s maiden name, your birth date, and a special character at the end — are extremely weak. This kind of information often ends up in leaks, or can be pieced together from public sources, so the passwords can be easily brute-forced by smart algorithms. Of course, nobody can remember hundreds of unique passwords, so it makes sense to offload that job to our password manager — a secure vault that generates and remembers complex, unique passwords for you, and syncs them across all your devices.
  • Find out about new leaks as fast as possible. Some online services will send you a free alert if your email address shows up in a known data leak. But it’s much more convenient to monitor leaks with a dedicated security app. For example, Kaspersky Password Manager constantly checks all the entries you’ve saved. It warns you if you use the same password on different websites, or if any of your saved login and password pairs has been compromised. Our simple instructions for Windows, macOS, Android, and iOS can help you easily check all the passwords you’ve saved in Kaspersky Password Manager. Your passwords are never sent to Kaspersky. We explain how we can analyze your passwords without knowing them in our post, How to create strong passwords and where to store them.
  • Use reliable protection that tracks and blocks leaks of your data. While Kaspersky Password Manager only checks the active password entries you’ve added to it, Kaspersky Premium can monitor for compromised accounts linked to your email addresses (you can add up to 50 addresses to check), and for digital identity theft linked to your phone numbers. And besides reporting leaks that have already happened, our security solutions can also stop data about you from being collected online.
  • Set up privacy on your devices and apps with our free online service, Privacy Checker.

Keep your accounts separate

The more websites that know your email, the more often it will show up in advertising profiles and potential leaks. For one-time and minor sign-ups, you can use an email masking service. All Apple users get this feature by default (Hide My Email). If you use another OS, you could try Firefox Relay, for example.

The service then creates a separate proxy email address for the website where you’re trying to sign up. Messages sent to that address are automatically forwarded to your real inbox, but the website never sees your real email address.

If you want to go all in, you can try splitting your digital life into several sub-personas by hand. Create several email addresses for different purposes. For example, use one for online stores, banks, and government services, a second for public social media, and a third for forums and social networks where you want to stay anonymous.

Keep in mind that all this is a challenge: you’ll need to keep coming up with new nicknames, and make sure your sub-personas never overlap. If you use an email address for an anonymous profile, don’t link it to services that already have your real details, and don’t use it as a backup email for a public account. One accidental link can easily undo all your effort.

Check what you share with exes

If you’ve recently broken up with a partner, make sure you check which parts of your shared digital life they can still access. Sadly, it’s very often ex-partners who become doxers or stalkers — spying on their former other half and stopping at nothing to do so. For more details on exactly what to do in this situation, read our article Post-breakup digital hygiene: what to check and shut down.

Use your right to be forgotten

Many countries have a right-to-be-forgotten law. It lets you ask search engines to remove links to pages that contain your personal data.

You can send the links to those pages, explain why you want them hidden, and request that they be removed from search results. Keep in mind that the page with your data isn’t deleted. Other search engines may still show it, and it may still turn up for other search queries.

To submit a request like this, use the dedicated forms from Google or Bing. But remember that a search engine can turn you down if it decides the information is in the public interest, or that the law requires it to be published.

There are more effective, though more time-consuming, ways to remove your data from the internet. We covered them in detail in our post, Why data brokers build dossiers on you, and how to stop them doing so.

Looking for more ways to protect your digital identity? Check out our other posts:
  •  

Forensic Data: How to Acquire and Retain Vital Evidence

While "digital forensics" and "incident response" often appear together (as in the acronym "DFIR"), they represent two distinct disciplines.

What's in a Name?

The American Heritage Dictionary defines forensics as "The use of science and technology to investigate and establish facts in criminal or civil courts of law."

Contrast this with IBM's definition of incident response: "Incident response [...] refers to an organization's processes and technologies for detecting and responding to cyberthreats, security breaches or cyberattacks." Note the absence of any reference to legal proceedings—it simply describes the process by which an organization detects, halts, and recovers from an incident.

Legal Considerations

Although most incidents never end up in court, all should be treated as if they might.

Taking the proper steps before, during, and after response ensures that any data collected can be admissible as evidence.

It's important to know the rules of evidence for relevant jurisdictions. Global corporations should consider each jurisdiction they have locations in when developing standard operating procedures (SOPs). Always include legal counsel when developing your organization's SOPs.

Data Preservation

A common rule for digital evidence is the retention of data in its "original state." This is accomplished by using validated hardware and software to create an exact bit-for-bit copy of a piece of digital media. Yet during incident response, it is rare that full forensic images are created—typically, only a small subset of data is collected from victim devices for analysis. Before any action is taken, consult legal advisors to decide whether to collect full forensic images.

A good practice is to create a folder for the original data, generate and document a hash of its contents, and then create a working copy in a separate folder. Only perform analysis on the working copies of your data to preserve the integrity of the original data.

Documentation

Documentation is critical when handling potential evidence. A chain of custody (CoC) records details about what the data is, where it came from, who collected it, whom it was transferred to, a brief description of what was done to it, and so forth.

The National Institute of Standards and Technology (NIST) provides a sample CoC here:
https://www.nist.gov/document/sample-chain-custody-formdocx

Each person working with the data must keep detailed notes: record dates, times, and any actions taken. Binary files often need to be parsed by special tools to make their data human-readable—include any tool names and versions. The same should be done with human-readable data, such as text-based log files. While you likely don't need to document the version of Excel used to read a log file, if you added a column to show UTC date/time stamps in local time, that is worth noting.

The gold standard for documentation is this: notes should be detailed enough that someone with a similar background can recreate your steps and produce the same results.

This is the scientific method part of digital forensics. Processes need to be repeatable and generate the same results.

Tool Validation Procedures

Before an incident occurs, verify that your hardware and software are working. Test write blockers to ensure they do not alter the evidentiary media. Validate that your forensic software functions correctly (it's not unheard of for new versions to report the wrong date/time stamps when parsing binary data).

While there is no set standard for validation processes, some guidelines exist to help you develop validation SOPs.

Validation SOPs guidelines:
NIST: https://www.dhs.gov/science-and-technology/nist-cftt-reports
SWGDE: http://cet4861.pbworks.com/w/file/fetch/120024474/4861.2014-09-05_SWGDE_Recommended_Guidelines_for_Validation_Testing_V2-0.pdf

Additional Considerations for Incident Handling

When managing incidents, also consider:

  • What are the data retention policies of your Endpoint Detection and Response (EDR) tools?
  • How is your cloud data preserved?
  • Who has access to sensitive or personal data?

These factors often depend on your license agreement with providers. Make sure data can be maintained in a secure, long-term manner, as it can take years until an incident makes it into the courtroom. Implement processes to export incident data from systems and services while preserving integrity and meeting long-term storage requirements that protect its availability and confidentiality. Access to confidential information must always be managed carefully.

Remember: Involve your legal team, validate your tools, work from copies (never original data), document everything meticulously, and maintain chain of custody.

  •  

What’s your data worth on the dark web? (Lock and Code S07E15)

This week on the Lock and Code podcast…

Twenty years ago, a British mathematician named Clive Humby popularized a phrase that came to describe data’s relationship with the entire global economy: “Data is the new oil.”

Pithy as the phrase sounds, it is undeniably true.

Data steers decisions at businesses of every size. Data created entirely new industries built around its capture. And, for a select number of companies, data has produced billions—if not trillions—of dollars in value.

So how is it that, on the dark web, your stolen identity can be purchased for just 95 cents?

That’s what a Malwarebytes researcher found last month after spending 48 hours inside the dark web to investigate cybercrime. Across a variety of forums and directories, he found subscription plans for malware that steals information once implanted on a device. He found guides for deploying social engineering scams. He found people selling their services to build fake websites that trick people into handing over their usernames and passwords. And he found one of the dark web’s most traded commodities—personal data, packaged together about individual people, to help a cybercriminal commit identity fraud.

These packages are called “fullz.” For victims in the United States, a fullz contains a full name, Social Security Number, date of birth, address, and other personal details. That is enough, on its own, for a cybercriminal to potentially open a bogus line of credit, file a fake tax return, access financial accounts, or obtain medical services under someone else’s name.

As we wrote on Malwarebytes Labs:

“For less than the cost of a cup of coffee, a cybercriminal can buy enough information to devastate someone’s financial life.”

It’s the kind of risk that could scare anyone, especially considering the scale behind it. In just the first six months of 2026, Malwarebytes found more than 7,500 compromised data sets on the dark web containing more than 8.4 billion records.

And yet, even today, cybersecurity professionals still get asked why anyone should bother protecting their data.

The public, understandably, are exhausted. With data breaches happening every week—if not every day—cybersecurity can start to feel pointless. With young people unable to build financial security, they start believing that they have nothing worth stealing. And with Big Tech already collecting our every movement, behavior, click, and concern, people understandably feel powerless to fight any kind of data abuse, be it corporate or criminal.

So today’s episode approaches the question from a different direction. This isn’t about why you should protect yourself—plenty of company websites will tell you that, and most of them rely on fear. This is about why hackers want your data in the first place.

Today, on the Lock and Code podcast, host David Ruiz explains how cybercriminals turn a single repeated password into account takeover, how a screenshot of your house from Google Maps became a tool in extortion emails, and why the most benign information about you—an address, an age, one public photo—is often the most useful data a stranger can buy.

Tune in today to listen to the full episode.

Show notes and credits:

Intro Music: “Spellbound” by Kevin MacLeod (incompetech.com)
Licensed under Creative Commons: By Attribution 4.0 License
http://creativecommons.org/licenses/by/4.0/
Outro Music: “Good God” by Wowa (unminus.com)


Listen up—Malwarebytes doesn’t just talk cybersecurity, we provide it.

Protect yourself from online attacks that threaten your identity, your files, your system, and your financial well-being with our exclusive offer for Malwarebytes Premium for Lock and Code listeners.

  •  

What’s your data worth on the dark web? (Lock and Code S07E15)

This week on the Lock and Code podcast…

Twenty years ago, a British mathematician named Clive Humby popularized a phrase that came to describe data’s relationship with the entire global economy: “Data is the new oil.”

Pithy as the phrase sounds, it is undeniably true.

Data steers decisions at businesses of every size. Data created entirely new industries built around its capture. And, for a select number of companies, data has produced billions—if not trillions—of dollars in value.

So how is it that, on the dark web, your stolen identity can be purchased for just 95 cents?

That’s what a Malwarebytes researcher found last month after spending 48 hours inside the dark web to investigate cybercrime. Across a variety of forums and directories, he found subscription plans for malware that steals information once implanted on a device. He found guides for deploying social engineering scams. He found people selling their services to build fake websites that trick people into handing over their usernames and passwords. And he found one of the dark web’s most traded commodities—personal data, packaged together about individual people, to help a cybercriminal commit identity fraud.

These packages are called “fullz.” For victims in the United States, a fullz contains a full name, Social Security Number, date of birth, address, and other personal details. That is enough, on its own, for a cybercriminal to potentially open a bogus line of credit, file a fake tax return, access financial accounts, or obtain medical services under someone else’s name.

As we wrote on Malwarebytes Labs:

“For less than the cost of a cup of coffee, a cybercriminal can buy enough information to devastate someone’s financial life.”

It’s the kind of risk that could scare anyone, especially considering the scale behind it. In just the first six months of 2026, Malwarebytes found more than 7,500 compromised data sets on the dark web containing more than 8.4 billion records.

And yet, even today, cybersecurity professionals still get asked why anyone should bother protecting their data.

The public, understandably, are exhausted. With data breaches happening every week—if not every day—cybersecurity can start to feel pointless. With young people unable to build financial security, they start believing that they have nothing worth stealing. And with Big Tech already collecting our every movement, behavior, click, and concern, people understandably feel powerless to fight any kind of data abuse, be it corporate or criminal.

So today’s episode approaches the question from a different direction. This isn’t about why you should protect yourself—plenty of company websites will tell you that, and most of them rely on fear. This is about why hackers want your data in the first place.

Today, on the Lock and Code podcast, host David Ruiz explains how cybercriminals turn a single repeated password into account takeover, how a screenshot of your house from Google Maps became a tool in extortion emails, and why the most benign information about you—an address, an age, one public photo—is often the most useful data a stranger can buy.

Tune in today to listen to the full episode.

Show notes and credits:

Intro Music: “Spellbound” by Kevin MacLeod (incompetech.com)
Licensed under Creative Commons: By Attribution 4.0 License
http://creativecommons.org/licenses/by/4.0/
Outro Music: “Good God” by Wowa (unminus.com)


Listen up—Malwarebytes doesn’t just talk cybersecurity, we provide it.

Protect yourself from online attacks that threaten your identity, your files, your system, and your financial well-being with our exclusive offer for Malwarebytes Premium for Lock and Code listeners.

  •  

LG to Ban Residential Proxies from Smart TV Apps

The home appliance giant LG Electronics USA said this week it plans to suspend any apps built for its smart TVs that turn one’s television into an always-on residential proxy node. The move comes less than a month after researchers found that more than 42 percent of games and other apps available for download on LG’s webOS store allow unknown third-parties to route their Internet traffic through a user’s TV.

Proxy SDK prevalence among smart TV apps for LG (webOS) and Samsung (Tizen OS) televisions. Image: Spur.us.

On July 2, we featured research by the security firm Spur that examined the prevalence of residential proxy software development kits (SDKs) in smart TV apps. Spur found more than 42 percent of apps available for download on LG smart TVs include SDKs that turn one’s television in a proxy node indefinitely, and that more than a quarter of the apps made for Samsung’s Tizen operating system had similar residential proxy components.

Responding to questions about Spur’s research, LG Senior Vice President John Taylor told KrebsOnSecurity the company was working with app developers to remove the residential proxy option from their apps on the webOS platform. Developers that fail to comply, he said, will find their apps suspended.

“A residential proxy network is not an intended use for LG smart TVs, and LG Electronics is working with developers to remove the residential proxy option from their apps on the webOS platform,” Taylor said. “If this option is not removed, these apps will be suspended.”

Taylor said LG is committed to keeping residential proxy networks out of its smart TV apps going forward, and that the company’s review of those apps is “well underway now.”

“As part of our ongoing efforts to enhance platform quality and the user experience, LG will continue to strengthen our evaluation process for developer-submitted apps, including those that incorporate residential proxy SDKs,” Taylor wrote in an emailed statement.

App makers looking for ways to monetize their creations can turn to residential proxy providers, which pay developers to include SDKs that turn the user’s device into a residential proxy node that is rented to paying customers. In the case of LG and Samsung smart TVs, Spur found residential proxy SDKs bundled with everything from simple games like Pac-Man to screensavers and file utilities.

A Pac-Man smart TV app from Bright Data offers users the choice between viewing ads in the game or agreeing to allow their TV to serve as a residential proxy node. Image: Spur.us.

Spur’s report found the residential proxy network Bright Data accounted for a majority of proxy SDKs across both Samsung and LG smart TVs. In a statement shared with KrebsOnSecurity, Bright Data said its network is built on consent and responsibility and operates by LG and Samsung terms.

“Every peer opts in through a dedicated screen and receives value in return; every customer is vetted, and our practices have now undergone a second independent audit by PwC,” the statement reads. “We remain committed to an open, transparent internet where legitimate businesses, researchers, and institutions can responsibly access data that lives in the public domain.”

Bright Data and other proxy providers named in Spur’s report all say they follow rigorous know-your-customer processes to validate legitimate uses of their services, which is often heavily tied to content-scraping activities by said customers. The proxy companies also say they incorporate technological countermeasures to prevent proxy service customers from being able to interact with and control other devices on the proxy user’s local network.

Spur argues the problem is not that residential proxy networks exist, but rather that they are being embedded at scale in devices that most consumers do not think of as computers and are not equipped to audit.

“A one-time consent prompt buried in a TV app is not a substitute for meaningful transparency, ongoing control, and platform oversight,” Spur’s Trevor Sutter wrote. “The risk is amplified when consent comes from individuals within the household who use the device but shouldn’t give consent, such as minors.”

LG’s announcement that it is culling residential proxy SDKs from its app store is welcome news, but the company recently came under fire for another questionable partnership: Pimping McAfee security products via software drivers included in its high-end LCD monitors.

Earlier this week, the Youtube channel Gamers Nexus showed that certain LG LCD monitors will automatically install an app that promotes paid McAfee antivirus subscriptions, and that the app arrives through Windows Update without an approval prompt.

Update, July 22, 1:06 p.m. ET: Added statement from Bright Data.

  •  

Cardiac patients’ medical data stolen and held to ransom

Cardiac monitoring provider iRhythm has been hit by a data theft followed by an extortion attempt.

In a filing with the Securities and Exchange Commission (SEC), iRhythm revealed it was contacted by someone on June 9 who claimed to have stolen sensitive information, including proprietary data, patient PHI, and other personal information. That person demanded payment in exchange for not publishing the data.

iRhythm provides ambulatory cardiac monitoring and analysis (for example using the Zio patch) and has reportedly processed over two billion hours of heartbeat data from more than twelve million patients.

In the filing, the company said the data was obtained through social engineering and is from “certain third-party-hosted business applications”, without revealing any further details about the amount of data.

On its own website, iRhythm also doesn’t disclose much about the nature of the stolen data, but does seem to imply no financial data was affected:

“We have not identified any impact to our products, our clinical or medical device systems, our connections to customers, our manufacturing and distribution operations, patient safety, or our ability to meet patient needs. In addition, we do not store or retain individual financial account information or payment card information. 

 As we actively investigate, we will notify individuals affected by this incident in accordance with applicable law and take steps as needed to protect and remediate the impact to them.“

However, the SEC filing adds that iRhythm determined that the incident is significant, “in light of the volume of the potentially affected data.” Together with the extortionist’s claims that they have patients’ medical data, that makes the breach one worth noting if you have used iRhythm’s services.

Even without payment data, healthcare breaches have serious downstream effects:

  • Attackers can craft highly convincing emails, texts, or calls that reference specific procedures or monitoring episodes (for example, “about your recent Zio patch recording”) to trick patients into sharing more data or paying fake bills.
  • The breached data can be used to create a fake identity, insurance fraud, or medical identity theft.
  • Exposure of cardiac and other health‑related information can be deeply sensitive and may have employment/insurance ramifications, especially if data is posted publicly or sold to data brokers.

Healthcare breach data tends to circulate for years, and victims may face sporadic fraud and phishing attempts long after the headlines fade.

How to stay safe

If you’ve used iRhythm’s services, keep an eye on your post, email, and patient portals for official breach notifications from iRhythm or your healthcare provider.

In the US, breaches of protected health information that meet certain criteria must be reported to patients and regulators. iRhythm has promised to “notify individuals affected by this incident in accordance with applicable law and take steps as needed to protect and remediate the impact to them.”

To stay out of the hands of phishers and scammers:

  • When you receive a communication about the data breach, verify through other channels that it really came from iRhythm. Go directly to iRhythm’s official website or patient portal, or call a known phone number to confirm the communication is genuine.
  • Be extra suspicious of emails or texts that claim to offer compensation, refunds, or other financial consequences related to this incident.
  • Change passwords for your iRhythm‑linked portals and your cardiology or hospital patient portals, especially if you reused those passwords elsewhere.
  • Log into your health insurer’s portal and check claims on a regular basis.
  • If you see anything suspicious, report it immediately to your insurer and provider and ask them to flag your account for possible identity theft.
  • Do not provide personal or financial information over the phone just because the caller knows details about you which they may have obtained from the stolen data.

Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

  •  

Drones to Diplomas: How Russia’s Largest Private University is Linked to a $25M Essay Mill

A sprawling academic cheating network turbocharged by Google Ads that has generated nearly $25 million in revenue has curious ties to a Kremlin-connected oligarch whose Russian university builds drones for Russia’s war against Ukraine.

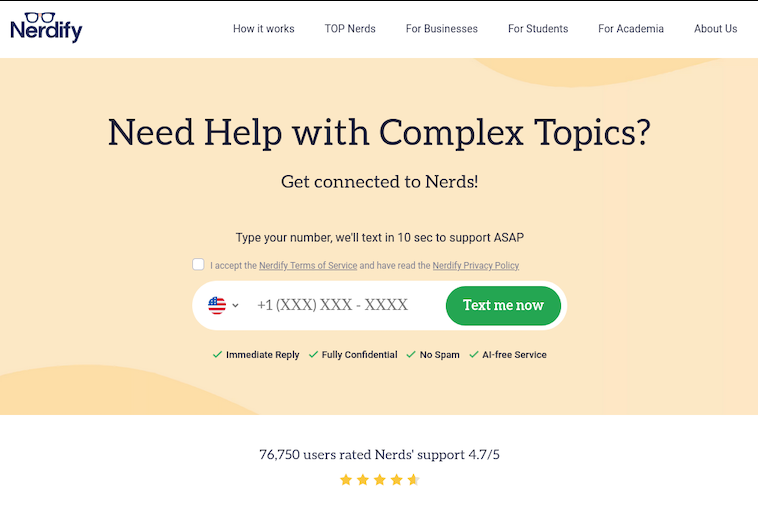
The Nerdify homepage.

The link between essay mills and Russian attack drones might seem improbable, but understanding it begins with a simple question: How does a human-intensive academic cheating service stay relevant in an era when students can simply ask AI to write their term papers? The answer – recasting the business as an AI company – is just the latest chapter in a story of many rebrands that link the operation to Russia’s largest private university.

Search in Google for any terms related to academic cheating services — e.g., “help with exam online” or “term paper online” — and you’re likely to encounter websites with the words “nerd” or “geek” in them, such as thenerdify[.]com and geekly-hub[.]com. With a simple request sent via text message, you can hire their tutors to help with any assignment.

These nerdy and geeky-branded websites frequently cite their “honor code,” which emphasizes they do not condone academic cheating, will not write your term papers for you, and will only offer support and advice for customers. But according to This Isn’t Fine, a Substack blog about contract cheating and essay mills, the Nerdify brand of websites will happily ignore that mantra.

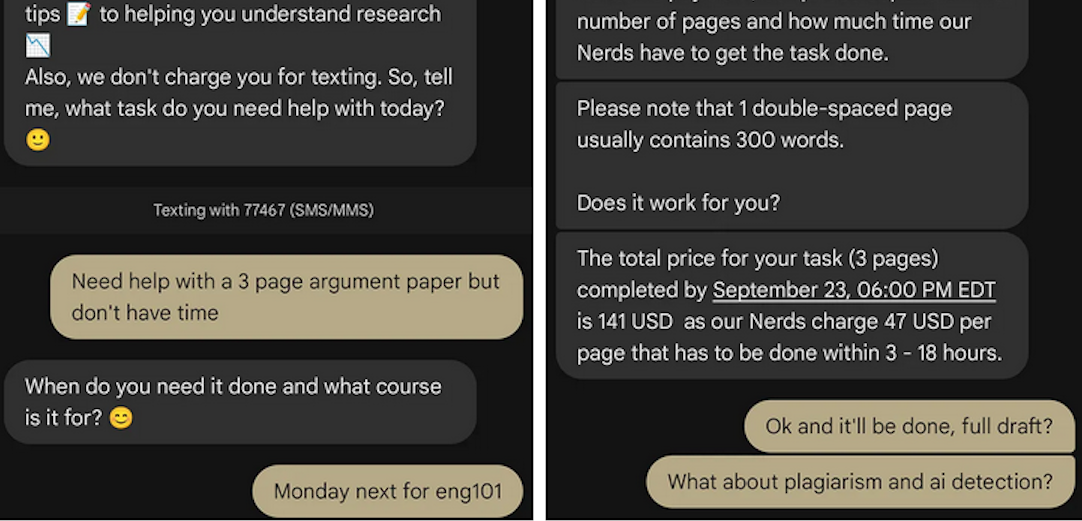
“We tested the quick SMS for a price quote,” wrote This Isn’t Fine author Joseph Thibault. “The honor code references and platitudes apparently stop at the website. Within three minutes, we confirmed that a full three-page, plagiarism- and AI-free MLA formatted Argumentative essay could be ours for the low price of $141.”

A screenshot from Joseph Thibault’s Substack post shows him purchasing a 3-page paper with the Nerdify service.

Google prohibits ads that “enable dishonest behavior.” Yet, a sprawling global essay and homework cheating network run under the Nerdy brands has quietly bought its way to the top of Google searches – booking revenues of almost $25 million through a maze of companies in Cyprus, Malta and Hong Kong, while pitching “tutoring” that delivers finished work that students can turn in.

When one Nerdy-related Google Ads account got shut down, the group behind the company would form a new entity with a front-person (typically a young Ukrainian woman), start a new ads account along with a new website and domain name (usually with “nerdy” in the brand), and resume running Google ads for the same set of keywords.

UK companies belonging to the group that have been shut down by Google Ads since Jan 2025 include:

–Proglobal Solutions LTD (advertised nerdifyit[.]com);
–AW Tech Limited (advertised thenerdify[.]com);
–Geekly Solutions Ltd (advertised geekly-hub[.]com).

Currently active Google Ads accounts for the Nerdify brands include:

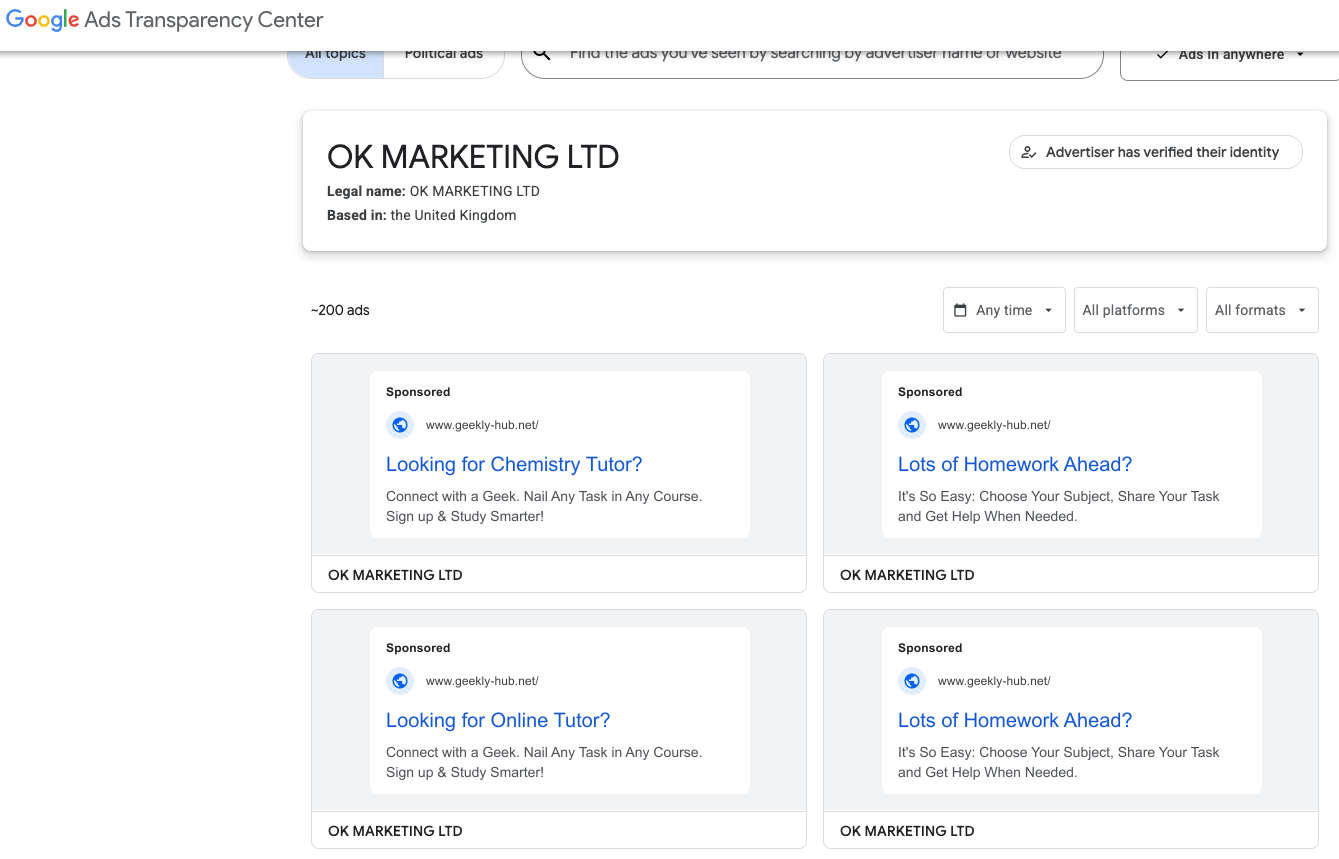
-OK Marketing LTD (advertising geekly-hub[.]net⁩), formed in the name of Olha Karpenko, a young Ukrainian woman;
–Two Sigma Solutions LTD (advertising litero[.]ai), formed in the name of Olekszij (Alexey) Pokatilo.

Google’s Ads Transparency page for current Nerdify advertiser OK Marketing LTD.

Mr. Pokatilo has been in the essay-writing business since at least 2009, operating a paper-mill enterprise called Livingston Research alongside Alexander Korsukov, who is listed as an owner. According to a lengthy account from a former employee, Livingston Research mainly farmed its writing tasks out to low-cost workers from Kenya, Philippines, Pakistan, Russia and Ukraine.

Pokatilo moved from Ukraine to the United Kingdom in Sept. 2015 and co-founded a company called Awesome Technologies, which pitched itself as a way for people to outsource tasks by sending a text message to the service’s assistants.

The other co-founder of Awesome Technologies is 36-year-old Filip Perkon, a Swedish man living in London who touts himself as a serial entrepreneur and investor. Years before starting Awesome together, Perkon and Pokatilo co-founded a student group called Russian Business Week while the two were classmates at the London School of Economics. According to the Bulgarian investigative journalist Christo Grozev, Perkon’s birth certificate was issued by the Soviet Embassy in Sweden.

Alexey Pokatilo (left) and Filip Perkon at a Facebook event for startups in San Francisco in mid-2015.

Around the time Perkon and Pokatilo launched Awesome Technologies, Perkon was building a social media propaganda tool called the Russian Diplomatic Online Club, which Perkon said would “turbo-charge” Russian messaging online. The club’s newsletter urged subscribers to install in their Twitter accounts a third-party app called Tweetsquad that would retweet Kremlin messaging on the social media platform.

Perkon was praised by the Russian Embassy in London for his efforts: During the contentious Brexit vote that ultimately led to the United Kingdom leaving the European Union, the Russian embassy in London used this spam tweeting tool to auto-retweet the Russian ambassador’s posts from supporters’ accounts.

Neither Mr. Perkon nor Mr. Pokatilo replied to requests for comment.

A review of corporations tied to Mr. Perkon as indexed by the business research service North Data finds he holds or held director positions in several U.K. subsidiaries of Synergy University, Russia’s largest private education provider. Synergy has more than 35,000 students, and sells T-shirts with patriotic slogans such as “Crimea is Ours,” and “The Russian Empire — Reloaded.”

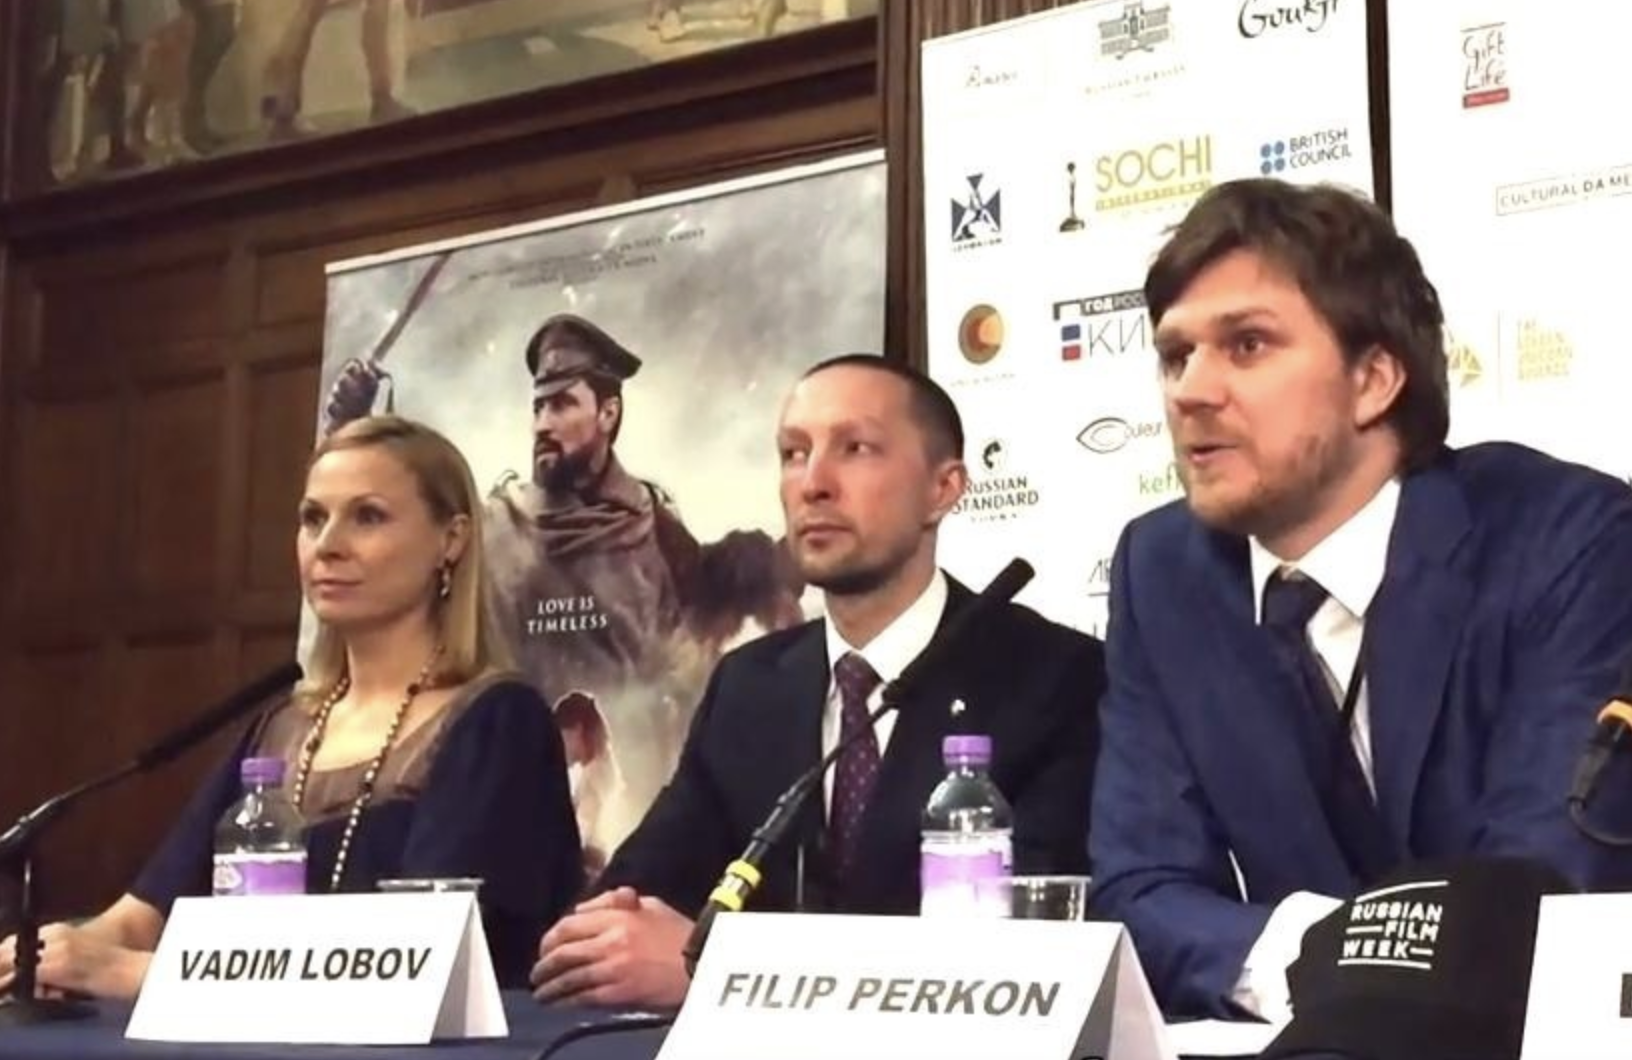
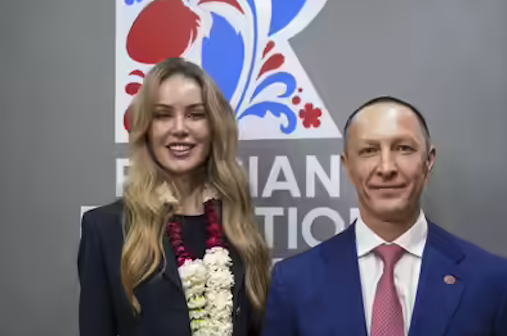
The president of Synergy University is Vadim Lobov, a Kremlin insider whose headquarters on the outskirts of Moscow reportedly features a wall-sized portrait of Russian President Vladimir Putin in the pop-art style of Andy Warhol. For a number of years, Lobov and Perkon co-produced a cross-cultural event in the U.K. called Russian Film Week.

Synergy President Vadim Lobov and Filip Perkon, speaking at a press conference for Russian Film Week, a cross-cultural event in the U.K. co-produced by both men.

Mr. Lobov was one of 11 individuals reportedly hand-picked by the convicted Russian spy Marina Butina to attend the 2017 National Prayer Breakfast held in Washington D.C. just two weeks after President Trump’s first inauguration.

While Synergy University promotes itself as Russia’s largest private educational institution, hundreds of international students tell a different story. Online reviews from students paint a picture of unkept promises: Prospective students from Nigeria, Kenya, Ghana, and other nations paying thousands in advance fees for promised study visas to Russia, only to have their applications denied with no refunds offered.

“My experience with Synergy University has been nothing short of heartbreaking,” reads one such account. “When I first discovered the school, their representative was extremely responsive and eager to assist. He communicated frequently and made me believe I was in safe hands. However, after paying my hard-earned tuition fees, my visa was denied. It’s been over 9 months since that denial, and despite their promises, I have received no refund whatsoever. My messages are now ignored, and the same representative who once replied instantly no longer responds at all. Synergy University, how can an institution in Europe feel comfortable exploiting the hopes of Africans who trust you with their life savings? This is not just unethical — it’s predatory.”

This pattern repeats across reviews by multilingual students from Pakistan, Nepal, India, and various African nations — all describing the same scheme: Attractive online marketing, promises of easy visa approval, upfront payment requirements, and then silence after visa denials.

Reddit discussions in r/Moscow and r/AskARussian are filled with warnings. “It’s a scam, a diploma mill,” writes one user. “They literally sell exams. There was an investigation on Rossiya-1 television showing students paying to pass tests.”

The Nerdify website’s “About Us” page says the company was co-founded by Pokatilo and an American named Brian Mellor. The latter identity seems to have been fabricated, or at least there is no evidence that a person with this name ever worked at Nerdify.

Rather, it appears that the SMS assistance company co-founded by Messrs. Pokatilo and Perkon (Awesome Technologies) fizzled out shortly after its creation, and that Nerdify soon adopted the process of accepting assignment requests via text message and routing them to freelance writers.

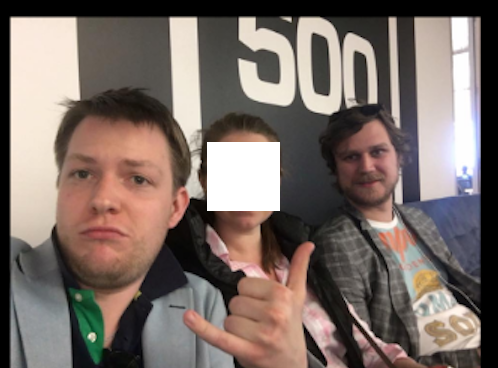
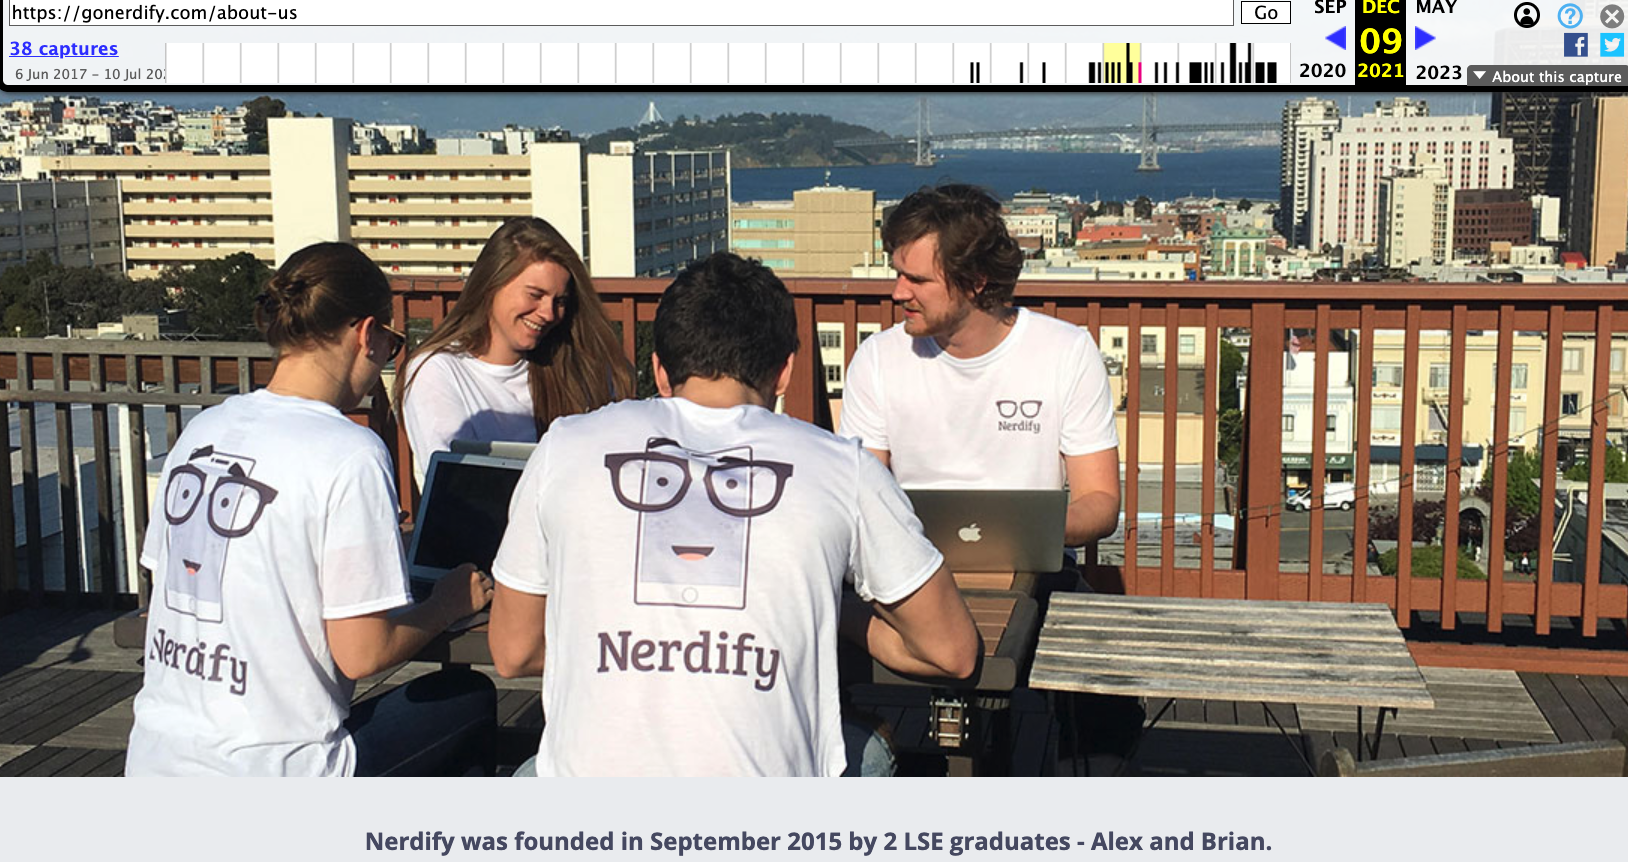
A closer look at an early “About Us” page for Nerdify in The Wayback Machine suggests that Mr. Perkon was the real co-founder of the company: The photo at the top of the page shows four people wearing Nerdify T-shirts seated around a table on a rooftop deck in San Francisco, and the man facing the camera is Perkon.

Filip Perkon, top right, is pictured wearing a Nerdify T-shirt in an archived copy of the company’s About Us page. Image: archive.org.

Where are they now? Pokatilo is currently running a startup called Litero.Ai, which appears to be an AI-based essay writing service. In July 2025, Mr. Pokatilo received pre-seed funding of $800,000 for Litero from an investment program backed by the venture capital firms AltaIR Capital, Yellow Rocks, Smart Partnership Capital, and I2BF Global Ventures.

Meanwhile, Filip Perkon is busy setting up toy rubber duck stores in Miami and in at least three locations in the United Kingdom. These “Duck World” shops market themselves as “the world’s largest duck store.”

This past week, Mr. Lobov was in India with Putin’s entourage on a charm tour with India’s Prime Minister Narendra Modi. Although Synergy is billed as an educational institution, a review of the company’s sprawling corporate footprint (via DNS) shows it also is assisting the Russian government in its war against Ukraine.

Synergy University President Vadim Lobov (right) pictured this week in India next to Natalia Popova, a Russian TV presenter known for her close ties to Putin’s family, particularly Putin’s daughter, who works with Popova at the education and culture-focused Innopraktika Foundation.

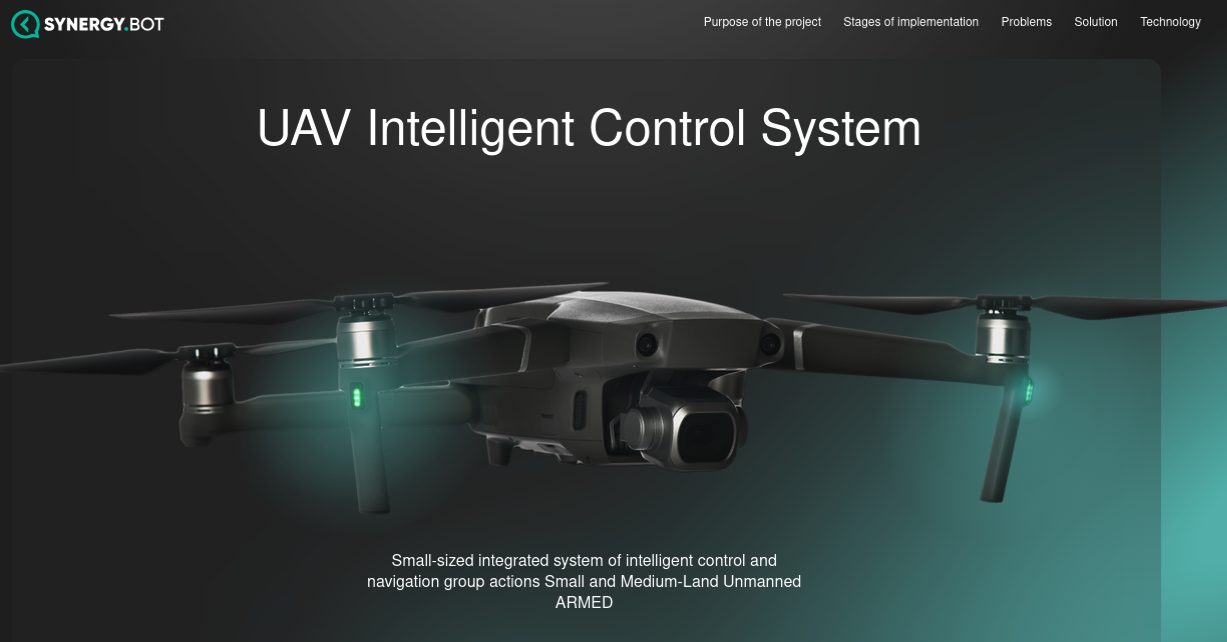
The website bpla.synergy[.]bot, for instance, says the company is involved in developing combat drones to aid Russian forces and to evade international sanctions on the supply and re-export of high-tech products.

A screenshot from the website of synergy,bot shows the company is actively engaged in building armed drones for the war in Ukraine.

KrebsOnSecurity would like to thank the anonymous researcher NatInfoSec for their assistance in this investigation.

Update, Dec. 8, 10:06 a.m. ET: Mr. Pokatilo responded to requests for comment after the publication of this story. Pokatilo said he has no relation to Synergy nor to Mr. Lobov, and that his work with Mr. Perkon ended with the dissolution of Awesome Technologies.

“I have had no involvement in any of his projects and business activities mentioned in the article and he has no involvement in Litero.ai,” Pokatilo said of Perkon.

Mr. Pokatilo said his new company Litero “does not provide contract cheating services and is built specifically to improve transparency and academic integrity in the age of universal use of AI by students.”

“I am Ukrainian,” he said in an email. “My close friends, colleagues, and some family members continue to live in Ukraine under the ongoing invasion. Any suggestion that I or my company may be connected in any way to Russia’s war efforts is deeply offensive on a personal level and harmful to the reputation of Litero.ai, a company where many team members are Ukrainian.”

Update, Dec. 11, 12:07 p.m. ET: Mr. Perkon responded to requests for comment after the publication of this story. Perkon said the photo of him in a Nerdify T-shirt (see screenshot above) was taken after a startup event in San Francisco, where he volunteered to act as a photo model to help friends with their project.

“I have no business or other relations to Nerdify or any other ventures in that space,” Mr. Perkon said in an email response. “As for Vadim Lobov, I worked for Venture Capital arm at Synergy until 2013 as well as his business school project in the UK, that didn’t get off the ground, so the company related to this was made dormant. Then Synergy kindly provided sponsorship for my Russian Film Week event that I created and ran until 2022 in the U.K., an event that became the biggest independent Russian film festival outside of Russia. Since the start of the Ukraine war in 2022 I closed the festival down.”

“I have had no business with Vadim Lobov since 2021 (the last film festival) and I don’t keep track of his endeavours,” Perkon continued. “As for Alexey Pokatilo, we are university friends. Our business relationship has ended after the concierge service Awesome Technologies didn’t work out, many years ago.”

  •  

Wrangling the M365 UAL with SOF-ELK and CSV Data (Part 3 of 3)

Patterson Cake // PART 1 PART 2 In part one of “Wrangling the M365 UAL,” we talked about acquiring, parsing, and querying UAL data using PowerShell and SOF-ELK. In part […]

The post Wrangling the M365 UAL with SOF-ELK and CSV Data (Part 3 of 3) appeared first on Black Hills Information Security, Inc..

  •  

Six Tips for Managing Penetration Test Data

John Malone // Introduction Information is power. This sentiment also holds true when discussing the creation of a supporting archive. A supporting archive is something that we put together to […]

The post Six Tips for Managing Penetration Test Data appeared first on Black Hills Information Security, Inc..

  •  

How to Install Cacti 1.1.10 on Ubuntu 16.04

Kent Ickler // What is Cacti? Cacti is a network system that inputs system-generated quantifiable data and presents the data in spiffy graphs. Net-Admin In the Net-Admin world, it gives […]

The post How to Install Cacti 1.1.10 on Ubuntu 16.04 appeared first on Black Hills Information Security, Inc..

  •  

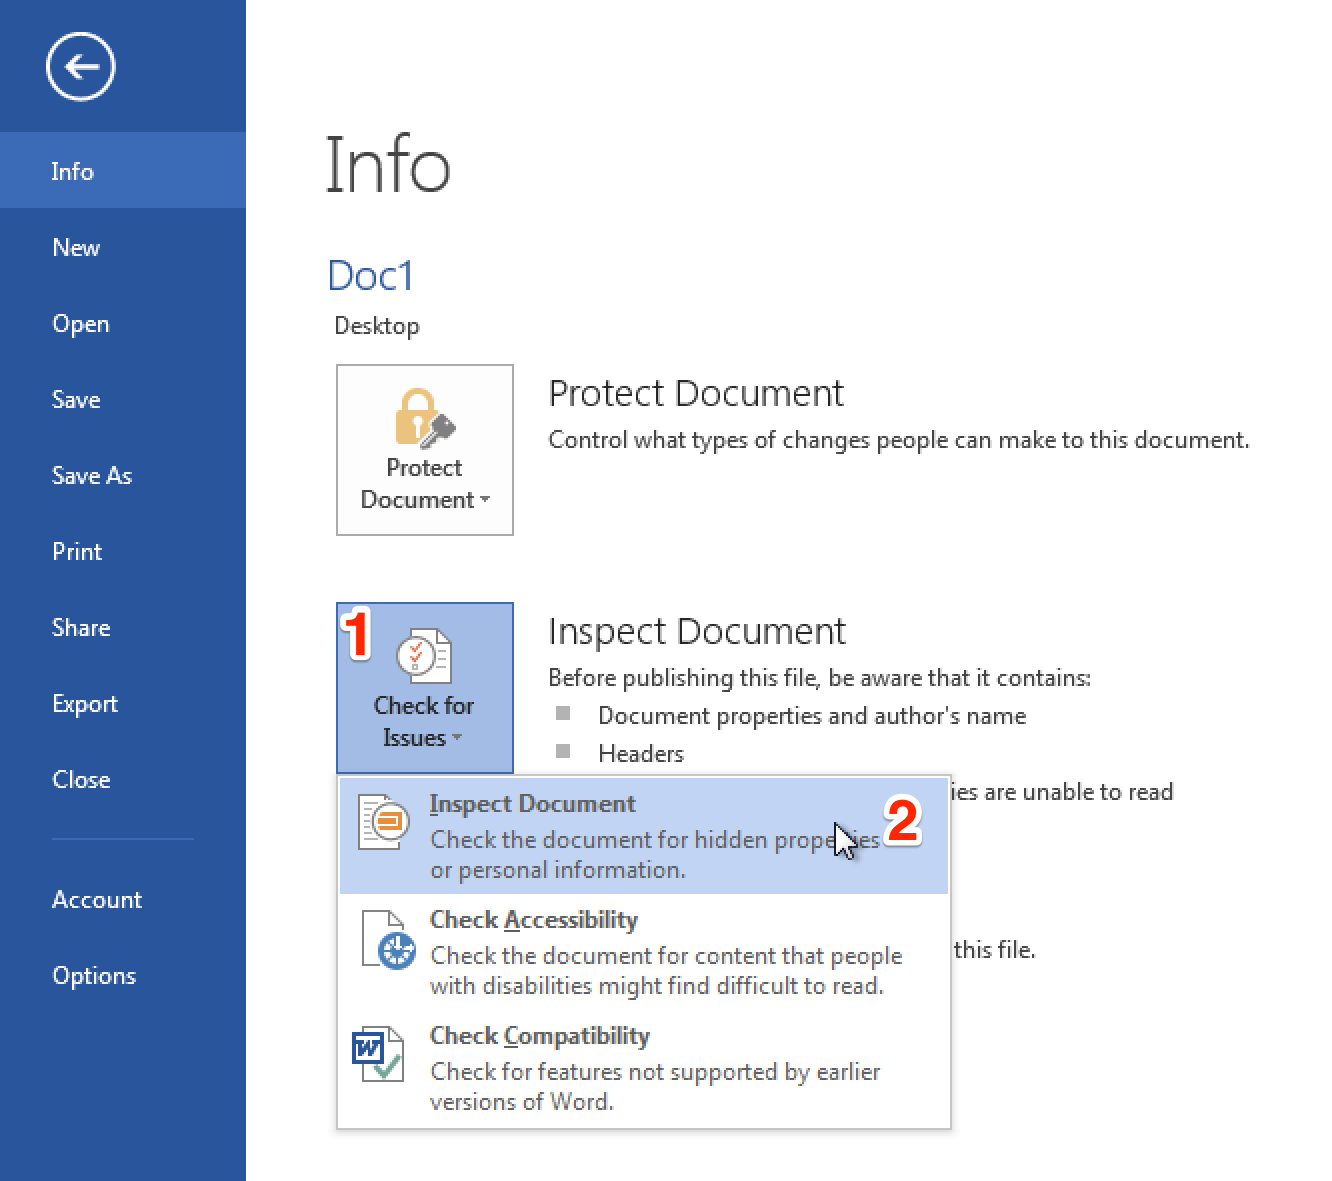
Bugging Microsoft Files: Part 3 – Clearing Metadata

Ethan Robish // In my last two posts I showed how to insert tracking bugs in both .docx (Part 1) and .xlsx files (Part 2).  But don’t let all that effort go […]

The post Bugging Microsoft Files: Part 3 – Clearing Metadata appeared first on Black Hills Information Security, Inc..

  •  

Data Mining & Privacy: How Anonymous Are You Really?

Sam Carroll // When I started at BHIS I was surprised at the sensitivity of personal data, such as my birthday. I was soon reminded of a data mining class […]

The post Data Mining & Privacy: How Anonymous Are You Really? appeared first on Black Hills Information Security, Inc..

  •  
❌