❌

Reading view

Disrupting the service economy behind transnational cybercrime operations

Most people have opened their messages to find a suspicious alert urgently telling them that a package cannot be delivered, a toll remains unpaid, a bank account needs attention, or a tax bill is overdue. The details may change, but the goal is the same: to get someone to click, share personal information, or pay. 

These messages are relentless. Delete and block one, and another takes its place. Ignore them, and more will follow. Fall for one, and the floodgates open. What appears to be a simple scam message is often the visible end of a much larger transnational cybercriminal operation. 

When Microsoft and Japan’s National Police Agency (NPA) followed a wave of fraud and scam activity targeting people and businesses in Japan, they expected to find individual campaigns. Instead, they found themselves inside a sprawling Chinese-language cybercrime marketplace where criminals could buy accounts, hosting services and tools used to create fake websites and online identities. The investigation expanded globally, involving the Japan Cybercrime Control Center (JC3), Resecurity, Cloudflare, Oracle, Proofpoint and TRM Labs to uncover the businesses sustaining this criminal ecosystem. 

Today, Microsoft and Health-ISAC, a global non-profit that helps health sector organizations share cyber threat information and collaborate to improve operational resilience, are moving to dismantle three components of this criminal marketplace: YAM Store, CoGUI and Iron Man.  

Since January 2026, YAM Store, CoGUI and Iron Man have collectively enabled more than one billion malicious messages targeting over 75,000 organizations worldwide, including more than 750 million messages geared toward Microsoft customers alone. These messages have been used to target consumers, healthcare organizations, financial institutions, and other businesses in more than 150 countries, generating tens of millions of dollars for their operators.   

Tracing the businesses behind the scams

The investigation began in late 2025 after Japan’s NPA alerted Microsoft to malicious messaging campaigns targeting people in Japan. NPA continued providing intelligence and investigative support as the partners traced those campaigns back to the businesses supplying criminals around the world. 

The trail led investigators deep into a Chinese-language cybercrime ecosystem that was difficult for non-native-speaking investigators to penetrate. There, they gained access to CoGUI, which supplied criminals with ready-made websites and messages impersonating companies, financial institutions, government agencies, and other trusted organizations. Instead of creating fraudulent websites themselves, criminals could quickly deploy pages designed to steal passwords, payment information, and other personal data.  

Two side-by-side screenshots of Amazon Japan webpages. The left shows an Amazon.co.jp login page with email and password fields. The right shows a payment method update page with fields for cardholder name, card number, expiration date, and security code, along with a yellow “Update now” button.
A fraudulent Amazon lookalike from CoGUI designed to steal login and payment information from Japanese-speaking users

As Microsoft’s investigation expanded, intelligence from JC3 helped confirm the scale of the activity affecting Japanese organizations and their customers. Drawing on information collected across its network of more than 130 member organizations, JC3 connected what appeared to be separate incidents to a broader pattern of scams targeting Japanese companies and financial institutions, including efforts to defraud consumers and to steal credentials and other sensitive information.  

One name that kept appearing throughout the investigation was YAM Store. YAM Store operated much like an online shop. Customers could browse products, compare prices and purchase fraudulent Microsoft and Google accounts and other ready-made tools used to carry out scams, including credential theft. Controlled purchases conducted by Microsoft helped confirm how it worked. 
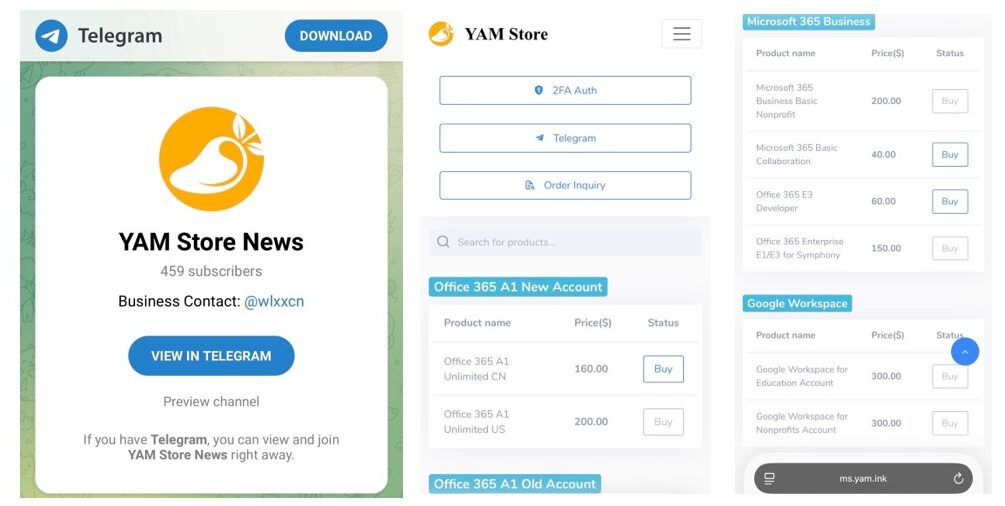
Three screenshots showing the YAM Store online marketplace. The left shows a Telegram preview for “YAM Store News” with 459 subscribers and a business contact. The center and right show YAM Store product listings offering Office 365, Microsoft 365 Business, and Google Workspace accounts at various prices, with “Buy” buttons.

In some cases, operators acquired internet domains that legitimate organizations had allowed to expire, often targeting certain sectors, such as non-profits and education, with specialized product offerings. They then rebuilt the websites to make those organizations appear active, allowing them to fraudulently obtain Microsoft 365 accounts that could later be sold through YAM Store.  
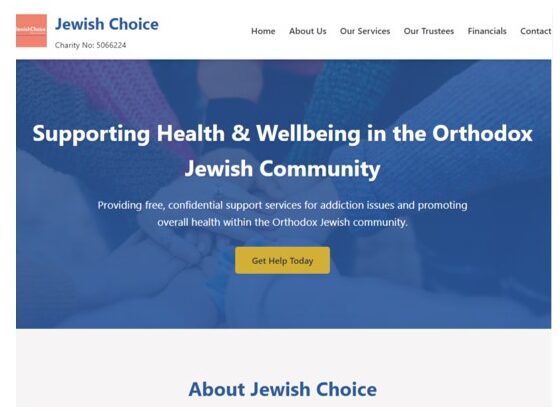
Screenshot of the Jewish Choice charity website. A blue banner reads “Supporting Health & Wellbeing in the Orthodox Jewish Community,” with text describing free, confidential support services for addiction issues and overall health, plus a “Get Help Today” button. The page also shows navigation links and an “About Jewish Choice” section.
A rebuilt nonprofit website used to create fraudulent Microsoft 365 accounts that could later be sold through YAM Store

Ready-made tools

YAM Store provided criminal infrastructure that was frequently paired with tools and services such as CoGUI. As investigators dug deeper, they found that the marketplace was already evolving. CoGUI had become one of the most widely used offerings in the ecosystem, particularly targeting victims in Japan and the United States but by mid-2026 it was increasingly being replaced by a newer offering known as Iron Man. 

Iron Man expanded the model by giving criminals access to thousands of ready-made templates designed to impersonate trusted organizations. Criminals could then quickly deploy email, text and web content tailored to specific brands, industries and countries.  

Through test purchases and work with Resecurity, investigators gained access to Iron Man and identified more than 2,300 templates impersonating banks, retailers, healthcare providers, transportation authorities, police departments, government agencies, and other organizations across more than 150 countries worldwide. Some were designed for government impersonation scams, using the appearance of official authority to pressure victims into making payments or disclosing sensitive personal information. Others impersonated organizations across industries, countries, and languages, from banks and airlines to telecommunications companies, retailers, and parcel delivery services.  

Examples of these impersonation templates are below. Importantly, the presence of an organization or government entity in these templates does not indicate that its systems were compromised. 

Six side-by-side screenshots of webpages in different languages and countries: a French DPD delivery status page, a German vehicle service payment notice, a Dutch tax refund application page, a Polish housing subsidy page, an Australian ANZ rewards points redemption page, and a Brazilian traffic fines consultation page.

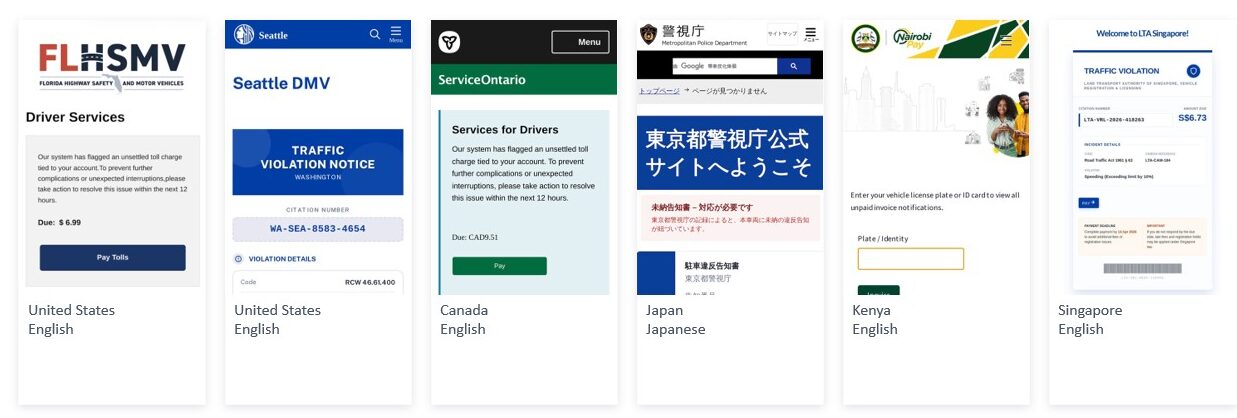
Six side-by-side screenshots of traffic and driver-service webpages from different countries. The examples include Florida and Seattle traffic violation notices in the United States, an Ontario toll notice in Canada, a Japanese Metropolitan Police Department page, a Nairobi Pay vehicle notice page in Kenya, and a Singapore traffic violation notice with a payment amount.

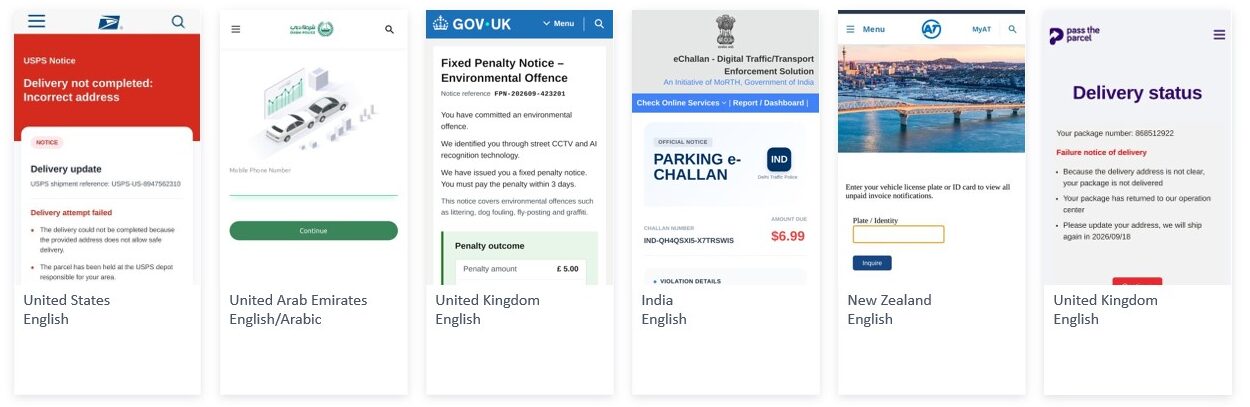
Six mobile webpage examples from the United States, United Arab Emirates, United Kingdom, India, and New Zealand showing delivery notices, traffic or environmental penalties, parking charges, and requests to enter personal or vehicle information.
Examples of Iron Man templates impersonating brands and government organizations around the world
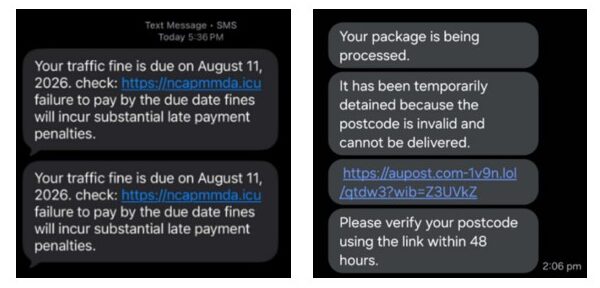
Two screenshots of suspicious text messages containing links. The left message claims a traffic fine is due and warns of late-payment penalties. The right message says a package has been detained because of an invalid postcode and asks the recipient to verify the postcode through a link within 48 hours.
Examples of Iron Man SMS templates impersonating traffic authorities in the Philippines and Australia Post, a package delivery service

A blog from Microsoft Threat Intelligence shares more details on the network, as well as steps customers can take to protect themselves.  

Putting the pieces together

No single organization saw the full picture. Japan’s NPA played a critical role throughout the investigation, providing intelligence, investigative support and collaboration that helped uncover how the operation worked. JC3 helped establish the scale of the activity affecting Japanese organizations and consumers. Health-ISAC provided insight into impacts affecting healthcare organizations, while Resecurity, Cloudflare, Oracle, Proofpoint and TRM Labs contributed intelligence and investigative support.  

Working together, and with the assistance of AI tools, we connected accounts, websites, and infrastructure that initially appeared unrelated, helping expose the broader criminal marketplace behind them. Microsoft also worked closely and shared intelligence with U.S. Secret Service and international law enforcement partners.

Alert page stating that a website domain has been seized by Microsoft, featuring the Microsoft logo and logos from collaborating organizations, including Japan’s National Police Agency, JC3, Health-ISAC, Resecurity, Proofpoint, Cloudflare, Oracle, TRM, Pillsbury, and law enforcement. Small text at the bottom references legal action and cybersecurity protections.

This investigation also reflects a broader trend highlighted in this year’s Microsoft Digital Defense Report: modern fraud increasingly relies on businesses and services that make it easier for criminals to reach more victims. It took two-way information sharing across industries and international borders to uncover how these deeply interconnected services worked together. 

Going after the suppliers

With an order from the United States District Court for the Southern District of Florida, Microsoft and Health-ISAC seized and redirected domains that were part of the underlying infrastructure powering YAM Store, CoGUI and Iron Man. Microsoft has already disabled more than 20,000 accounts connected to YAM Store and continues to dismantle the operation by removing infrastructure hosted on its services and blocking more than 100,000 domains used for impersonation and fraud.   

What began with scam activity targeting people and organizations in Japan led investigators to an underground service economy supplying criminals around the world. YAM Store, CoGUI and Iron Man are only part of that larger criminal network, but disrupting them makes it harder for criminals to obtain the accounts, tools and infrastructure they rely on. 

The scam message is often the only part victims see. The businesses behind it are what make it possible. 

The post Disrupting the service economy behind transnational cybercrime operations appeared first on Microsoft On the Issues.

  •  

Preparing governments for an era of interconnected cyber risk

According to this year’s Microsoft Digital Defense Report, government agencies and services were the sector most impacted by cyber threats in 2026, accounting for 27% of observed activity, up from 17% in 2025. Governments are also the most frequently targeted sectors for nation-state activity. They are attractive targets because they hold sensitive information, operate essential services, and sit at the center of networks of agencies, contractors, technology providers, and critical infrastructure operators.  

Dwell time, the period between when an attacker gains access and when defenders detect and stop them, also increased this year across multiple sectors. While organizations responded faster once an intrusion was identified, detecting threats early remains a challenge. Attackers increasingly gain access through techniques that mimic legitimate activity, making malicious behavior harder to spot. For example, phishing accounted for 23% of observed intrusions in 2026, up from 7% in 2025, highlighting the continued importance of compromised identities as an entry point for broader attacks. 

Taken together, the implication for governments is clear. Security in the AI era is no longer simply about preventing individual intrusions. It is about ensuring institutions can operate effectively in an environment where risks are interconnected, threats move faster, and attackers remain hidden longer. Public-private partnerships are also more important than ever for securing critical government infrastructure and developing the policies and regulations needed for emerging technologies.  

In this year’s report, which examines cyber threat trends observed between July 2025 and June 2026, Terrell Cox, Microsoft’s Corporate Vice President & Deputy Chief Information Security Officer, and I explore how these dynamics are reshaping cyber risk. In a companion blog, Terrell takes a closer look at what these findings mean for CISOs and security professionals.

Two Microsoft Threat Intelligence charts compare sectors impacted by cyber threats in 2026. Government agencies and services lead overall at 27%, followed by information technology at 17% and research and academia at 14%. For nation-state targeting, IT and research and academia each account for 20%, government and think tanks/NGOs 10% each, transportation 7%, manufacturing 5%, and other sectors 28%.


To strengthen resilience, governments should focus on five priorities:

1. Prepare for a faster threat environment 

AI is compressing the window for action. Adversaries are moving faster. A vulnerability’s discovery in the wild to active weaponization can be well below 24 hours. While the number of publicly disclosed software vulnerabilities (commonly tracked as CVEs) is projected to reach a record 72,000 in 2026. 

Governments best prepared for the future will be those that can rapidly gather and assess information, make decisions, coordinate across institutions and industries, and communicate effectively during a crisis. This requires clearly defined responsibilities and trusted relationships established before an incident occurs, enabling swift and coordinated action when it matters most.  

2. Build security into the AI ecosystem  

AI is becoming part of the infrastructure that governments, businesses, and citizens rely on every day. As governments continue to adopt AI across public services and encourage its broader use, they should approach its security as a resilience challenge rather than a narrow technical issue. 

AI systems depend on interconnected infrastructure, data, models, applications, suppliers, and governance processes. Governments should promote security across this ecosystem through secure-by-design practices, testing and evaluation, stronger supply chain protections, transparency, accountability, and international cooperation on AI risk. 

The goal is not to create a separate AI security agenda. It is to integrate AI security into broader efforts to protect critical infrastructure and build national resilience. 

3. Plan for incidents to spread

Governments may not immediately know whether an intrusion is criminal, geopolitical, or something else. Cybercriminals and nation-state actors pursue different objectives, but increasingly rely on many of the same entry points, including compromised identities, exposed applications, social engineering, and legitimate administrative tools. 

Microsoft found that 52.2% of intrusions involving valid accounts resulted in additional credential theft, highlighting how quickly attackers can expand beyond an initial foothold. A seemingly isolated compromise can evolve into ransomware, espionage, data theft, or disruption of essential services. 

Governments should therefore assess incidents not only by how they begin, but by where they could lead. Response plans should account for the suppliers, partners, and service providers supporting critical functions. As attacks expand beyond their initial targets, they can also cross organizational, sectoral, and national boundaries, reinforcing the need for global collaboration. 

World map showing countries where customers were most frequently impacted by cyber threats from January through June 2026. The United States accounts for 25.5% of total impact, followed by Israel 7.6%, Ukraine 4.8%, Taiwan 3.9%, United Kingdom 3.8%, United Arab Emirates 2.8%, India and Japan 2.5% each, Canada 1.8%, Germany 1.7%, and Australia and the Philippines 1.5% each. Source: Microsoft Threat Intelligence.

4. Enable timely, two-way public-private information sharing 

A compromised account at one organization may provide early warning of a broader campaign. Signals that appear inconclusive in isolation can reveal coordinated activity when combined across organizations and jurisdictions. Modern cybercrime operates through interconnected networks of actors, services, and infrastructure that no single institution can fully see or disrupt on its own. 

Information sharing must be timely, trusted, and two-way—also known as bidirectional. The goal is not simply for companies to report threats to government. Public agencies should also return actionable intelligence, guidance, and warnings that help organizations protect their networks, customers, and operations. Trusted channels can enable this exchange among government agencies, law enforcement, critical infrastructure operators, technology providers, and international partners while respecting legal and privacy requirements. 

Policymakers can support this cooperation through protections for good-faith information sharing, common anonymization standards, and investment in shared threat intelligence and detection capabilities. Information sharing should also lead to action, including investigations, disruption efforts, and accountability for those responsible for serious cyber intrusions. 

5. Prepare essential services to operate through disruption

The organizations governments depend on to deliver public services, including transportation systems, communications infrastructure, schools, universities, and critical infrastructure operators, are increasingly targeted by cyber threats. Resilience therefore requires understanding not only government systems, but the broader ecosystem that supports them.

Horizontal bar chart showing attacks against SLED and critical infrastructure sectors from November 1, 2025, to April 30, 2026. Research and academia accounts for 38%, transportation systems 22%, government agencies and services 13%, communications infrastructure 11%, critical manufacturing 7%, energy 4%, government facilities 4%, chemicals 1%, water and wastewater systems 1%, and emergency services 1%. Source: Microsoft Threat Intelligence.

Planning documents alone are not enough. Governments should regularly conduct tabletop exercises bringing together policymakers, operational leaders, law enforcement, critical infrastructure operators, and private-sector partners to test how they would respond to incidents disrupting essential services. These exercises can expose gaps in decision-making, information sharing, public communications, and cross-sector coordination before a real-world crisis. Microsoft’s work through initiatives such as the Advancing Regional Cybersecurity (ARC) program, most recently in Kenya, illustrates how scenario-based exercises and cross-sector collaboration can help strengthen preparedness and response capabilities across the broader ecosystem. 

Government leaders should also know which services are most critical, which identities, systems, suppliers, and infrastructure support them, and how incidents will be escalated. Shared-service approaches can help extend security and response capabilities to local governments and public institutions that cannot build them independently. 

As cyber incidents cross organizational and national boundaries, resilience depends not only on technical preparedness, but on whether institutions can coordinate effectively under pressure. 

In an era of AI-enabled and increasingly interconnected cyber threats, resilience is no longer simply about recovering from an attack. It is about preparing for a world in which cyber incidents move faster, spread further, and affect more organizations than ever before. Governments best prepared for the future will be those that can contain harm, adapt quickly, and continue delivering critical services when citizens need them the most.  

The post Preparing governments for an era of interconnected cyber risk appeared first on Microsoft On the Issues.

  •  

Disrupting EvilTokens: The AI Chatbot Built for Cybercrime

Microsoft has disrupted EvilTokens, a powerful cybercrime platform that used AI at every step of the attack chain—from compromising email accounts to designing intricate roadmaps for financial fraud and scams. While EvilTokens helped cybercriminals access email accounts, at the center of the service was an AI-style chatbot that could analyze a victim’s inbox and help criminals identify trusted relationships, payment authorizations, and sensitive responsibilities, as well as other circumstances where fraud was most likely to succeed. The platform could even recommend fraud strategies, including drafting messages that impersonated trusted contacts to help criminals trick victims into taking action. 

In short, AI was not simply helping attackers write more convincing messages. It helped them decide who to target, who to impersonate, and how to most effectively exploit the relationship to extract as much money as possible.   

Within months of launching in February 2026, EvilTokens had been linked to more than 12,000 compromised email inboxes across over 10,000 organizations worldwide, showing how quickly the service gained traction. Microsoft observed the highest concentrations of victim activity in the United States, Canada, the United Kingdom, Australia, India, and France. Affected organizations ranged from wholesale distribution and construction to financial services, real estate, higher education, and healthcare. Working with partners, Microsoft seized 50 websites used to operate the service and disabled more than 150 additional domains tied to its supporting infrastructure. In the United Kingdom, the Metropolitan Police Service’s cybercrime team arrested two men on suspicion of offenses connected with the alleged operation of EvilTokens.  

But the significance of EvilTokens extends beyond its rapid growth and global reach. It offers an early warning of what happens when cybercriminals combine stolen access with AI capable of understanding how an organization works. 

From account access to financial fraud

EvilTokens helped criminals gain access to email accounts by tricking victims into entering an authentication code on Microsoft’s legitimate sign-in page. By completing the normal authentication sign-in process, victims unknowingly gave criminals access to their email accounts without revealing their passwords. That access could persist even after a password reset if the associated sessions and tokens were not also revoked. Microsoft Threat Intelligence provides additional technical details about the operation, how device-code attacks work, and steps customers can take to protect themselves here. 

Screenshot of an Outlook inbox showing an email about upcoming group events, with “AI Analysis” and “Summary” features highlighted in red.

Screenshot of an AI analysis interface identifying potential targets, opportunity levels, attack vectors, and financial opportunities based on scanned organizational emails.
EvilTokens AI analysis of compromised inbox and suggested follow- up prompts.

Once inside an account, criminals have traditionally needed time and experience to sift through thousands of messages, identify decision-makers, understand payment processes, and find opportunities for fraud. 

EvilTokens began automating that work. Its AI tools could summarize and translate emails, surface financial conversations, map organizational roles, identify trusted relationships, and recommend potential targets. Preset prompts offered to find wire-transfer discussions, identify the organization’s “money movers,” locate vendor invoices, and determine the best people to impersonate.

Sold through Telegram for a $1,500 initiation fee and a recurring $500 subscription, EvilTokens combined account compromise, mailbox analysis, target selection, and fraud preparation in a single service. Capabilities that once required experience across identity attacks, cloud systems, social engineering, and financial fraud were available through a ready-made interface.

Three screenshots of the EvilTokens Store Bot, including a DeviceCapture logo and messages advertising Microsoft 365 token capture and inbox access capabilities.
EvilTokens store on Telegram.
Screenshot of the EvilTokens “Essential Tools” dashboard displaying tools for token capture, browser access, traffic redirection, email automation, SMTP delivery, and email validation.
EvilTokens “Essential Tools” optimized for cybercrime.

AI lowered the barriers at both ends

Investigators found evidence that large portions of EvilTokens had been “vibe coded,” with AI helping its creators build the platform itself. They also determined that EvilTokens drew on capabilities from multiple AI models. 

The result was more than a collection of attack tools. EvilTokens packaged much of the fraud process into a commercially run service, complete with subscription pricing, customer support, management dashboards, and tools designed to move customers from account access toward financial exploitation.

Disrupting the platform

No single organization could disrupt EvilTokens alone. The service relied on hosting providers, cloud services, AI tools, financial services, and other online resources that cybercriminals repurposed to support fraud at scale. 

The disruption combined civil legal action with coordinated operational work across industry and law enforcement. Because healthcare organizations were among those targeted, Health-ISAC—a global non–profit that helps health sector organizations share cyber threat information and collaborate to improve operational resilience—joined Microsoft’s legal action as a co-plaintiff.

With authorization from the U.S. District Court for the Eastern District of Virginia, Microsoft and Health-ISAC worked with Cloudflare, Coinbase, OpenAI, Railway, SpyCloud, The Shadowserver Foundation, and TRM Labs to act against key parts of the platform. Microsoft also notified affected customers, helped remediate compromised accounts, and shared intelligence to support further defensive and investigative action.

The operation also demonstrated the value of rapid cooperation between private-sector investigators and law enforcement. Microsoft worked closely with specialist officers from the Metropolitan Police Service’s cybercrime team, sharing intelligence that enabled officers to take operational action in the United Kingdom. On September 11, 2026, officers arrested two men, aged 32 and 38, and seized digital devices and other items for examination. Both men have been released on police bail subject to conditions while the investigation continues. 

Screenshot of a Microsoft domain seizure notice featuring Microsoft and partner logos, including Cloudflare, Coinbase, Health-ISAC, Metropolitan Police, OpenAI, and others.
Seizure notice displayed after Microsoft and its partners disrupted infrastructure used by EvilTokens.

While EvilTokens used AI to identify targets and prioritize fraud opportunities, Microsoft investigators used reverse engineering and AI-powered tools to analyze evidence, accelerate the investigation, and identify the infrastructure supporting the service. The case shows how AI is changing not only how cybercriminals operate, but also how defenders investigate and disrupt them. 

This action marks the Microsoft Digital Crimes Unit’s (DCU) 40th court-authorized disruption spanning nearly two decades of targeting cyber threat actors, malicious tools, and supporting infrastructure. It is also DCU’s first action against an end-to-end AI-enabled cybercrime service. 

What EvilTokens reveals about cybercrime’s next phase

The infrastructure supporting EvilTokens has been disrupted, but the model it demonstrated will not disappear with it. As Microsoft notes in its 2026 Responsible AI Transparency Report, increasingly capable and accessible AI is being used to scale fraud, impersonation, and other forms of online abuse. EvilTokens offers an early example of how those capabilities can be combined with compromised accounts to accelerate financial fraud. 

For organizations, the lesson is: assume that once an inbox is compromised, criminals may understand its contents in minutes, not days. Strong identity protections and monitoring remain essential, but organizations should also independently verify requests to change payment information, redirect funds, or approve unusual transactions through a trusted second channel.


The post Disrupting EvilTokens: The AI Chatbot Built for Cybercrime appeared first on Microsoft On the Issues.

  •  

Protecting customer privacy means standing up for transparency

Why LinkedIn is challenging an overbroad government demand—and why Congress must make secrecy the exception

Today, the U.S. Court of Appeals for the Fourth Circuit heard oral argument in LinkedIn’s (a Microsoft subsidiary) appeal challenging a government demand for user records and a related secrecy order that is preventing LinkedIn from notifying those users that the government is seeking their data. The appeal asks important, constitutional questions about whether service providers may challenge demands that sweep in records unrelated to an investigation, and when the government may prevent a provider from notifying the user of a request.  

This appeal continues Microsoft’s longstanding work to ensure that secrecy orders remain the exception, not the rule. LinkedIn’s appeal asks courts to enforce meaningful limits on both the scope of government demands and the secrecy that can accompany them. 

We recognize law enforcement’s important role in protecting public safety and investigating crime, and sometimes that does need to be done covertly. We respond to lawful legal requests. At the same time, customers and users deserve meaningful limits and independent oversight through an adversarial process. And, customers deserve to be notified when the government seeks their data, unless the government clearly establishes the need for secrecy under statutory and constitutional standards. 

Those safeguards fulfill basic constitutional rights. The Fourth Amendment protects the right to be free from unreasonable searches and seizures. That right applies to papers kept in a desk, and it also applies when personal and business records are stored online. Online service providers, like LinkedIn and Microsoft, also have a First Amendment right to speak to their customers when the government obtains an order to search their private information. Secrecy may sometimes be justified—but it should be tailored to demonstrated needs and subject to meaningful review.  

This particular case arose after LinkedIn received a court order seeking user records together with a secrecy order preventing LinkedIn from informing anyone about the order. The details remain under seal, including the nature of the information the government seeks and the people who own that information. But the Fourth Circuit partially unsealed LinkedIn’s opening brief in July, allowing the public to understand some of the core issues. LinkedIn argues that the demand is overbroad, the secrecy order is unconstitutional, and the government has violated LinkedIn’s due process by withholding evidence from LinkedIn. 

Three amicus briefs from a broad coalition support LinkedIn’s position. The American Civil Liberties Union and ACLU of Virginia argue that users’ privacy interests must inform whether a demand is reasonable and that providers may be the only practical means of challenging unlawful process because users often receive no notice. The Reporters Committee for Freedom of the Press warns that overbroad demands, delayed notice, and secret evidence can expose confidential sources and chill newsgathering. Amazon, Apple, Google, Meta, and X emphasize that cloud providers are uniquely positioned to identify irrelevant requests and that secrecy orders require case-specific evidence rather than boilerplate assertions. Together, these briefs show why cloud providers must be able to test both the scope of government demands and the need for secrecy. 

Microsoft has a long record of standing up for these principles. In 2014, Microsoft successfully challenged a secrecy order connected to a National Security Letter that prevented notice to an enterprise customer. In 2016, we filed a landmark challenge to the widespread use of indefinite secrecy orders. We’ve successfully challenged individual secrecy orders time and again over the years. Our efforts contributed to updated Justice Department policies, but executive-branch practices can change. Durable protections require the development of case law and legislation. 

The U.S. House of Representatives recently took an important step in that direction. On August 31, the House passed legislation to rein in secret surveillance and strengthen notice protections when the government seeks data held by technology providers. As we explained when the bill passed, the reforms would place clearer limits on secrecy orders, require greater accountability, and help ensure that secrecy is the exception – not the rule. The Senate should act promptly to send these historic reforms to the President. 

The House –passed legislation recognizes that privacy and public safety are not opposing values. Clear standards can give investigators the confidentiality they genuinely need while providing courts, providers, and customers with predictable rules. The pending legislation and LinkedIn’s appeal are the latest, complementary chapters in this broader effort. Legislation can establish durable, system-wide rules for notice and accountability. Courts must meanwhile enforce the limits already contained in existing statutes and the Constitution. Neither task requires obstructing legitimate investigations. Rather, both mean the government must seek only relevant information, justify secrecy with specific evidence, and infringe on speech to the least extent possible. 

That is why today’s argument matters beyond a single sealed investigation. People and organizations increasingly entrust their most sensitive information to online services. If providers cannot challenge demands they know are overbroad—or if courts may silence them without a rigorous, adversarial review—the safeguards the law requires will be weakened precisely when they are most needed.

Microsoft and LinkedIn will continue to support lawful investigations while standing up for customer privacy, transparency, and the rule of law. We have appealed to the Fourth Circuit to preserve providers’ ability to challenge overbroad demands and to require the government to meet its constitutional burden before imposing secrecy. And we urge the Senate to complete the work the House began by enacting durable non-disclosure order reform.

Further reading 

The post Protecting customer privacy means standing up for transparency appeared first on Microsoft On the Issues.

  •  

Safe Participation Framework: Opportunity and Safety for the Next Generation in the Age of AI

Today, Microsoft is sharing our Safe Participation Framework, which centers on designing and enabling safe, privacy-preserving, and age-appropriate experiences for young people online. Members of our AI Youth Futures Council have delivered a clear message: they want to learn, create, and prepare for a future with AI. Protecting their privacy, ensuring their safety, and preserving their opportunity to participate must go hand in hand.   

They are right. Children and families should not have to choose between the protections they need and the opportunities technology can provide. 

Technology companies have a responsibility both to protect young people from harm and to ensure they can benefit from technology through thoughtfully designed experiences, age-appropriate protections, and demonstrable safeguards. Microsoft’s Safe Participation Framework serves as a foundation for our work today, and we expect it to continue evolving as technology, research, and societal expectations change. We do not claim to have all the answers, but we believe it is important to share our approach and our learnings to help inform emerging regulatory frameworks and advance protection and opportunity together. 

Pillar one: Safety by design

Microsoft recognizes our responsibility to help create safer experiences for all users, particularly children and those more vulnerable to harm. Our safety-by-design approach seeks to embed protection from the outset: identifying foreseeable risks, examining the impact of product features and user experiences, and implementing proportionate safeguards. As risks evolve, we continue to learn from emerging research, science, andas well as from customers, governments, and other stakeholders. 

For more than a decade, Microsoft has invested in technologies designed to protect people online, beginning with PhotoDNA  in 2009 and continuing through our work to build safeguards for AI experiences and address emerging harms such as synthetic and non-consensual intimate imagery. We have also learned that families want tools that are simpler, intuitive, and easier to use. That is why, earlier this week, we announced new protections and defaults for children, teenagers, and families using Windows Family Safety. We view these changes as an important step forward, while recognizing that earning and maintaining trust requires continued investment, learning, and iteration. 

Bing has also strengthened protections against child sexually abusive material (CSAM) across its generative AI experiences. We have also expanded SafeSearch globally to cover additional categories of harmful content, helping reduce the risk of exposure to harmful material. We will continue to make progress, listen to our users and stakeholders, and learn by working with others to strengthen safety.  

Our goal is to help children and teenagers participate confidently in appropriate digital experiences that reinforce access to the meaningful educational, social, and economic opportunities technology can provide. Achieving that goal requires real protections that are proportionate to risk and implemented in ways that respect users’ privacy. Risks are not uniform across different technologies and services, and safeguards should reflect and address those differences.   

Pillar two: Age-differentiated experiences

We recognize that young people are not a single group. Their needs, capabilities, and expectations evolve with age, development, and context. For that reason, age-appropriate design is an important element of creating safer digital experiences and complements safety-by-design. Age-appropriate design ensures protections and experiences are responsive to the needs of users at different stages of development. This approach informs experiences across Microsoft’s consumer ecosystem.  

On XBOX, we leverage family safety and privacy tools designed specifically to help manage online interactions, content access, spending, screen time, and privacy settings. These features are intended to support safer experiences while giving families flexibility to make choices. We are applying many of these same learnings to Copilot. All users must now sign in to use Copilot, and access is restricted for children under 13 (or older where required by local law). We have also implemented measures to reduce exposure to harmful content, directing users to crisis support resources when self-harm risks are detected, and encouraging healthy use through transparency, break reminders, reporting tools, and guardrails to protect against delusional outputs.   

Microsoft has now also extended protections at the platform level. Through our new Windows Age application programming interface (API), expanded age assurance capabilities, and enhanced family safety tools, Microsoft is helping establish a more consistent and privacy-conscious foundation for age-appropriate experiences across the broader ecosystem. These capabilities are intended to provide developers with trusted age signals to support age-appropriate protections, making the experience ultimately easier for families to understand and navigate downstream. 

Reliable age signals play an important role in enabling age-appropriate experiences. Innovations such as the Windows Age API help provide privacy-preserving age signals while minimizing the collection and sharing of personal data. Young people share this expectation. Participants in Microsoft’s AI Youth Futures Council have consistently emphasized the importance of understanding how their information is collected, used, and protected. 

Pillar three: Education and empowerment

Technology alone cannot deliver safe participation. Young people and their families must have an opportunity to provide direct feedback, and they must have easy access to tools and resources that support and build their knowledge as they navigate digital experiences, evaluate what they encounter, and decide when to seek help. Digital literacy is, therefore, a core component of child safety. 

Microsoft has invested in digital literacy and safety education for years through resources and partnerships that reach communities around the world. Earlier this year, we launched Behind the Chat: A Human Guide to Safe AI Conversations, designed specifically to help young people understand the opportunities and risks associated with AI companionship. This toolkit is supported by classroom resources for educators and materials for parents and trusted adults, reflecting our belief that supporting young people requires an ecosystem approach. Beginning this fall, we will expand these resources throughout Europe, Asia, and the Americas. We will also continue working closely with educators to ensure safety and privacy. 

Over the coming year, we will deepen partnerships with researchers, AI Safety Institutes (AISIs), governments, and civil society to advance the research, evaluations, and benchmarks needed for safer digital and AI experiences. Working together, we will learn and help build the foundation for the next generation of trusted technology. 

A framework for the future

Our work is far from finished. As technology evolves, our understanding of how to support young people safely and responsibly must continue to evolve with it. This framework reflects our current approach, informed by evidence, shaped by young people and their families, and grounded in ongoing learning. We recognize that we do not have every answer, and that building safer digital experiences will require continued experimentation, humility, and collaboration. No single organization can do this alone. Progress will depend on deep partnerships across government, industry, civil society, educators, and families worldwide. Together, we can help build a future in which every young person has the opportunity to participate, create, learn, and thrive. 

The post Safe Participation Framework: Opportunity and Safety for the Next Generation in the Age of AI appeared first on Microsoft On the Issues.

  •  

Scaling cybercrime disruption through innovation and AI

Microsoft is taking a new approach to fighting cybercrime, targeting the cyberattack supply chain, not just individual services. In a case unsealed today, we are simultaneously targeting two widely used cybercrime tools, Amadey and StealC, after AI-assisted analysis revealed they rely on the same infrastructure.

This action goes after the cybercrime “assembly line,” where coordinated tools drive ransomware, financial fraud, and disruptions to public services. Amadey and StealC are often used alongside each other: Amadey helps attackers gain access to devices, while StealC steals passwords and sensitive information. Together, they form a critical link in the chain. In the first two weeks of May alone, Amadey and StealC were linked to more than 140,000 infected computers globally, highlighting how widely they are used.

Working with Europol and industry partners, we targeted both tools at once. The goal: break the chain. Since the start of the operation, Microsoft has identified more than 18,000 victim computers, severed criminal control of those devices, and is working with telecommunications providers to help protect affected customers globally.

When multiple parts of an operation are disrupted together, attacks are harder to launch, scale, and recover from. The result: fewer disrupted services, fewer opportunities for cybercriminals to profit, and more friction when they try to rebuild.

It’s no longer enough to go after threats one by one. We need to interrupt how the attacks are put together. 

What’s different about this action   

Microsoft has long used civil legal action to disrupt cybercriminal infrastructure and pioneered the innovative use of existing laws, including the Racketeer Influenced and Corrupt Organizations Act (RICO), a US law designed to target organized crime.

What’s new is how we’re combining AI analysis with an expanded use of that law.

Amadey and StealC were developed by separate cybercriminals, but they relied on the same infrastructure. To understand how they worked, investigators used AI, including Copilot, to quickly analyze the malware, asking questions in plain English instead of manually combing through complex code. That helped surface key details, uncover hidden data, and test findings in a fraction of the time, turning what would have taken hours or days into minutes and enabling the team to spot connections faster.

Those insights allowed the legal team to treat both malware families as part of a single conspiracy. Instead of going after each tool separately, as we have done in the past, we used RICO to charge multiple complicit enablers involved across the operation. In total, Microsoft’s Digital Crimes Unit disrupted over 200 command-and-control servers—the systems criminals use to control infected devices, steal data, and keep attacks running.

By targeting tools together, we can disrupt the cybercrime chain more efficiently and more effectively, in a way that better reflects how these networks actually operate today.

Cybercrime now runs like an assembly line 

Cybercrime is no longer a series of isolated attacks—it’s a coordinated system.

Specialized tools handle each step: one gains access, another steals credentials, and others sell or exploit that access for fraud, ransomware, espionage, or other nefarious purposes. Different actors may be involved at each stage, but together they turn access into profit, quickly and at scale.

How cybercrime tools are built to be modular

That structure also creates a point of vulnerability. The people behind these cybercriminal tools may never interact directly, but their tools are designed to work together. If those connections can be identified, multiple stages of an attack can be disrupted at once.

How these attacks play out in the real world 

Most people will never hear the names Amadey or StealC, but they feel the effects. A hospital locked out of critical systems. A city unable to deliver essential services. A small business losing access to accounts overnight. A retiree who lost their life savings.

These attacks don’t happen all at once. They unfold step by step: attackers get in, passwords are stolen, access is reused or sold, and sometimes repurposed for more targeted operations. For example, Microsoft has observed Russian-affiliated actor Secret Blizzard leveraging Amadey infections to deploy custom malware against targets in Ukraine.

By targeting multiple points in that chain at once, we reduce the chance that a single compromise turns into widespread harm. Put simply: fewer attacks succeed and fewer people feel the impact when they do.

No one organization can do this alone 

Actions like this underscore a fundamental reality: we’re successful when we collaborate. No single organization, whether government or industry, has full visibility into how cyber threats operate across borders and sectors. What makes this effort effective is the combination of perspectives and data.

Microsoft had been tracking Amadey due to its impact on customers, working with cybersecurity partners ESET, BitSight, Lumen, and Mitsui Bussan Secure Directions (MBSD) to better understand how it operated. At the same time, Europol’s European Cybercrime Centre (EC3), together with European law enforcement partners including Germany’s Federal Criminal Police Office and the Dutch and Danish National Police, was investigating StealC as part of Operation Endgame, alongside IBM X-Force and Proofpoint.

Bringing those efforts together expanded our collective datasets and made it possible to identify the connections between the two tools and act on them quickly. That shared understanding enabled a coordinated response that went further than any single organization could achieve alone.


This shows why partnerships matter. Industry shares technical insight, government brings visibility, and we need trusted ways to exchange that information. Only by working from the same picture can we stay ahead of attackers, disrupting not just individual tools but also the systems that make cybercrime possible.

Creating sustained pressure on cybercrime  

This work doesn’t end with a single action. Cybercriminals adapt quickly, which is why we continue tracking how these operations evolve and working with partners to disrupt them.

Microsoft’s court-authorized disruption in this case is paired with ongoing efforts to track how cybercriminals rebuild, identify new infrastructure, and work with partners to disrupt the services they rely on to operate. It also includes incorporating the findings from this disruption into initiatives like Microsoft’s Statutory Automated Disruption program, which helps accelerate the removal of malicious domains and infrastructure.

The goal is not just to stop one operation but to slow the system itself—making attacks harder to launch, scale, and recover from. By combining AI-driven insight, legal action, and strong partnerships, we can continue to raise the cost of cybercrime and reduce its impact.

For more than a decade, Microsoft’s Digital Crimes Unit (DCU) has worked to disrupt cybercrime and nation-state threats, filing around 40 cases since 2008 and partnering with law enforcement to take down criminal networks. Learn more about the team’s efforts here.


The post Scaling cybercrime disruption through innovation and AI appeared first on Microsoft On the Issues.

  •  

Strengthening our approach to tackling non-consensual intimate imagery

When intimate images are shared without consent—whether real or AI-generated—the harm is immediate, deeply personal, and often long-lasting. It can affect someone’s sense of safety, dignity, and control, both online and offline. Protecting people from harms like non-consensual intimate imagery (NCII) has long been a priority for Microsoft. And as technology advances, our response continues to evolve to tackle very real challenges like the proliferation of highly realistic synthetic imagery. With the US Take It Down Act coming into force this month, establishing new federal protections against the spread of NCII, it’s important to share how we’re evolving our approach: making it easier to report harm, taking new steps to detect known NCII, and enabling more effective enforcement across our services.

Expanding protections across Microsoft services

Our goal is to make it simpler for individuals, or their representatives, to report violative content to Microsoft. We have strengthened our global reporting processes for NCII with a more intuitive form, with clear options to describe harm, including both real and AI‑generated images. These changes are designed to ease the burden for people in a distressing moment and enable faster, more effective action by our teams. Microsoft’s NCII policy is applied consistently across real and synthetic content, recognizing that the harm to individuals is the same, regardless of how an image was created. To report content on Microsoft services, hit “Report A Concern” or in the product where you encounter the content.  

We also want to proactively detect and prevent the spread of known NCII by working with StopNCII.org, a reporting platform that enables individuals to create a digital “fingerprint,” or hash, of their images. Two years ago, we provided StopNCII.org with a new version of PhotoDNA that enables victims to create a hash without an image ever leaving their device. This can then be used by StopNCII.org partners to detect and remove matching NCII content across platforms, allowing industry to work together to prevent re-sharing and protect individuals’ privacy. We have been piloting the use of these hashes in Bing since September 2024. 

We have now expanded our use of validated StopNCII.org hashes across Microsoft consumer services, including Teams Free, OneDrive, and Xbox. We will implement these changes carefully to advance effectiveness and accuracy—accelerating removals, automating where appropriate, maintaining human review for reported cases, and providing clear, accessible paths for users to appeal decisions.

Enhancing our collective response to this harm

No single company can address NCII alone. It requires coordination across industry, governments, and civil society. Microsoft will continue working with partners to improve shared tools and approaches that help prevent this content from spreading. We will also continue to advocate for clear, effective policies that protect victims, support innovation, and strengthen accountability across the ecosystem.

We will also continue to advocate for policies that support efforts to advance laws that prevent and deter image-based abuse. Microsoft advocated in support of the US Take It Down Act and welcomes the European Union’s work to strengthen protections against “nudification” apps, alongside global efforts to criminalize this misuse of technology. We are closely tracking Ofcom’s recent announcement that new measures will be required under the UK Online Safety Act to address illegal NCII harms. We believe our proactive work in this area will help us maintain trust with survivors, users, and regulators, among others.

Speed, clarity, and trust matter for people affected by intimate image abuse. When someone reaches out for help, we will strive to respond quickly, respectfully, and effectively. Our goal, though, is to invest in technologies and partnerships that reduce the likelihood of harm. We have joined forces with Childnet, a UK NGO that aims to safeguard children online, and created educational materials to prevent the misuse of AI to create intimate imagery among teens. These materials have now been released in the UK, as well as localized with partners in Singapore, South Korea, and Japan.

I am proud to learn from our digital safety team, which is carefully charting our path, and from the many industry and community leaders contributing to this work. This is an evolving challenge. We are committed to the journey, grounded by the voices of experts and survivors.

The post Strengthening our approach to tackling non-consensual intimate imagery appeared first on Microsoft On the Issues.

  •  

Disrupting Fox Tempest: A cybercrime service that turned “verified” software into a pathway for ransomware 

Every day, we decide what software to trust in seconds guided by simple labels such as “verified,” “secure,” and “safe to install.” The problem is that those signs can be manipulated.

Today, Microsoft unsealed a legal case in the US District Court for the Southern District of New York targeting a cybercrime service known as Fox Tempest, which, since May 2025, has enabled cybercriminals to disguise malware as legitimate software. The malware-signing-as-a-service (MSaaS) worked by fraudulently accessing and abusing code signing tools, such as Microsoft’s Artifact Signing, a system designed to verify that software is legitimate and hasn’t been tampered with. Cybercriminals used the service to deliver malware and enable ransomware and other attacks, infecting thousands of machines and compromising networks worldwide.

For the first time, Microsoft is taking public action against a powerful, but often unseen, enabler within the cybercrime ecosystem, targeting how cybercriminals prepare and employ techniques to optimize their rate of success. To disrupt the service, we seized Fox Tempest’s website signspace[.]cloud, took offline hundreds of the virtual machines running the operation, and blocked access to a site hosting the underlying code. This action builds upon persistent internal efforts to revoke fraudulently obtained code‑signing certificates and enhance our defenses and employ new security features to detect and thwart such malicious activity. It’s already having an impact: cybercriminals are complaining about challenges accessing the current service.

Our impact extends beyond one actor. The lawsuit targets Fox Tempest’s infrastructure and also names Vanilla Tempest as a co-conspirator, a prominent ransomware group that used the service to deploy malware like Oyster, Lumma Stealer, and Vidar, and ransomware, including  Rhysida, in multiple recent cyberattacks. Vanilla Tempest has targeted schools, hospitals, and other critical organizations worldwide, while Rhysida, a highly evolved ransomware variant that both encrypts files and steals data, often used for double extortion, has been used by various actors in numerous high-profile attacks globally, including to steal and leak internal documents from the British Library and to disrupt operations at Seattle-Tacoma International Airport. Microsoft’s investigation further linked Fox Tempest to various additional ransomware affiliates and families, including INC, Qilin, Akira, and  others.

More broadly, this case points to how cybercrime is changing.  What once required a single group to carry out an attack from start to finish is now broken into a modular ecosystem where services are bought and sold and work interchangeably with one another. Some services are inexpensive and widely used. Others, like Fox Tempest, are highly specialized and expensive because they remove friction or bypass obstacles that make attacks fail, making them both more reliable and harder to detect. As seen with Fox Tempest, when these services are combined with AI-powered tactics, attacks can scale more easily, reaching more people and becoming more convincing.

This kind of abuse isn’t new, but it is evolving

Illicit code-signing certificates have been  sold and trafficked for more than a decade. That includes its use by nation-state actors to target critical infrastructure organizations in Europe. What’s changed is how this activity is marketed, packaged, and sold as a service, along with the scale at which it is now used across ransomware campaigns. Instead of buying certificates one-by-one, criminals upload their malware to a service that signs it for them.

What also makes this model notable is the level of investment. Unlike lower-cost services like RedVDS, a cybercriminal infrastructure provider that costs as little as $24 per  month, which Microsoft disrupted earlier this year, Fox Tempest shows that more sophisticated actors are willing to pay thousands of dollars for advanced capabilities that make attacks easier to carry out, harder to detect, and more likely to succeed.

How Fox Tempest sold “legitimacy” at scale

Fox Tempest’s business model was straightforward: sell fraudulent code-signing capability, let others package malware, and enable attacks downstream. The model has generated millions in proceeds, demonstrating significant financial profit.

Behind the scenes, the operators built access at scale. Using fabricated identities and impersonating legitimate organizations, they created hundreds of fraudulent Microsoft accounts to obtain real code-signing credentials in volume. Customers who paid for Fox Tempest’s services could then upload malicious files via an online portal for them to  be signed using Fox Tempest-controlled certificates. Cybercriminals paid thousands of dollars for the service, reflecting how valuable this capability was.

Fox Tempest’s pricing model form and Telegram channel where you could purchase the service. The more you pay, the quicker you get access to the service.

Once signed, their malware appeared legitimate. Attackers then distributed the signed malware through tactics such as search manipulation and malicious ads, where users are more likely to trust what they encounter.  AI then helped generate and refine these campaigns  to reach a broader audience.

How code-signed malware appears in search results.
Fake Microsoft Teams download page and delivery mechanism for disguised code-signed malware

That changed the odds. Malicious software that should have been blocked or flagged by antivirus and other safeguards was more likely to be opened, allowed to run, or pass security checks—essentially allowing malware to hide in plain sight. Instead of forcing their way in, attackers could slip through the front door by masquerading as a welcomed guest.

An overview of malware‑signing‑as‑a‑service.

As Microsoft disabled fraudulent accounts, revoked fraudulently obtained certificates and introduced enhanced protections, the Fox Tempest operators continually adapted. In February 2026, they ultimately shifted to networks of third-party-hosted virtual machines to maintain and scale operations. That kind of rapid change is part of the model: these services evolve quickly in response to pressure and friction. In fact, Microsoft has observed further adaptations in response to our layered disruption efforts, with Fox Tempest attempting to shift operations and customers to another code-signing service.

Fox Tempest’s response to the disruptive efforts—translated from Russian by a third-party partner

In addition to seizing the core infrastructure behind the operation and degrading its ability to function at scale, we have taken further steps to prevent similar abuse, removing fraudulent accounts, strengthening verification, and limiting how this type of access can be reused. More technical details on the operation and the steps we’re taking to prevent similar abuse are available in this Microsoft Threat Intelligence blog.

Cutting off a critical enabler of cybercrime

This action wasn’t about stopping one actor. It sought to strategically neutralize a vital service that many attackers, particularly ransomware groups, rely on. When legitimate code signing services are weaponized, everything downstream gets easier: malware looks legitimate, security warnings are less likely to trigger, and attacks are more likely to succeed. Degrading that capability adds friction and forces a reset. The success rates of attacks decrease, and attackers have to rebuild, find new ways in, and accept more risk with each attempt—driving up both the cost and the time required to operate.

Importantly, disruption actions don’t happen in isolation and are never one-and- done. Collaboration is critical, as different organizations and sectors have visibility into different parts of the cybercrime ecosystem. In this case, we are working closely with cybersecurity company Resecurity, whose insights help us better understand how Fox Tempest operates. We are also collaborating closely with Europol’s European Cybercrime Centre (EC3) and the Federal Bureau of Investigation (FBI). As we’ve seen in previous efforts, we expect actors to try to rebuild. Collectively, we will continue to take action and keep the pressure on. That also means strengthening the code signing ecosystem through intelligence sharing and partnering with other code signing services, so it’s harder for malicious actors to regain that ground in the first place.

When attackers can make malicious software look legitimate, it undermines how people and systems decide what’s safe. Disrupting that capability is key to raising the cost of cybercrime. As threats evolve, the Microsoft Digital Crimes Unit will continue working with partners across industry and law enforcement to persistently identify and cut off the services that enable them.

For more than a decade, the Microsoft Digital Crimes Unit (DCU) has persistently disrupted cybercrime and nation-state threats targeting people, organizations, and critical infrastructure. Explore major disruptions—and the ongoing cases and operations behind them here: Disrupting cyberthreats since 2008 | Microsoft

The post Disrupting Fox Tempest: A cybercrime service that turned “verified” software into a pathway for ransomware  appeared first on Microsoft On the Issues.

  •  

Strengthening cyber capacity in Kenya: A new toolkit with lessons for the region

When a major cyber incident hits, the first decisions aren’t technical—they’re human. Who takes the lead? How quickly can information be shared? When should governments step in, and how do you protect public trust while keeping essential services running? 

These questions are at the heart of Microsoft’s Advancing Regional Cybersecurity (ARC) initiative, launched in 2025 to help governments strengthen cyber preparedness through practical, public-private collaboration. Today, we’re sharing the first tangible output of that work: the ARC Kenya Exercise Report & Toolkit, developed through a tabletop exercise held in Nairobi in December 2025.  

Developed with Kenya’s National Computer and Cybercrime Coordination Committee (NC4) and RiskSight, the toolkit is a practical planning resource designed to help government and cross-sector leaders prepare for cyber crises before they occur. It is grounded in real conversations among leaders from government, regulators, critical infrastructure operators, law enforcement, academia, and the private sector working through what a serious cyber incident would demand of them, together. 

Stress‑testing decisions before a crisis hits

The ambition of the “Silicon Savannah” makes Kenya a compelling setting for this work. Its digital economy is expanding rapidly—from mobile‑first financial services to cloud‑enabled public infrastructure—positioning the country as a regional technology leader. But rapid digital growth also brings increased exposure to more sophisticated cyber threats. As systems become more interconnected, a serious cyber incident can quickly disrupt essential services, undermine public trust, and threaten economic stability. 

Kenya’s approach recognizes this reality and reflects a critical principle: cybersecurity is not separate from innovation; it is one of the conditions that allows digital transformation to scale safely. The ARC initiative embodies this philosophy and helps decision makers confront the practical realities of coordination, escalation, and response in this complex environment. 

This is exactly what the ARC Kenya tabletop exercise was designed to do. The objective was not to test tools but to stress‑test decision making under pressure. Participants were challenged with complex scenarios—including AI‑enabled breaches, ransomware attacks, and infrastructure‑level disruptions. The focus was not on technical fixes but on leadership clarity, cross‑agency coordination, and real‑time decision making in high‑pressure environments. 

The outcome was both a roadmap for the unknown and a clear recognition of the need for shared expectations before a crisis begins—particularly around leadership and authority, trusted information sharing channels, and agreed response frameworks. These gaps, identified by participants themselves, now form the backbone of the ARC Kenya Toolkit. 

What the ARC Kenya toolkit delivers

The toolkit translates the lessons of the exercise into concrete actions that leaders can take now—before the next incident occurs. It also serves as a practical and specific 12‑month roadmap for strengthening Kenya’s cyber preparedness, moving from lessons identified to durable, institutional capability. Specifically, the toolkit provides recommendations to: 

  • Clarify national leadership during major cyber incidents, enabling government, regulators, law enforcement, and critical infrastructure operators to coordinate more quickly, with fewer gaps and overlaps. 
  • Establish practical, standards‑aligned incident response models for the entire country, including priority playbooks that teams can train on and execute consistently. 
  • Strengthen operational readiness across sectors, with better coordination between security operations centers (SOCs), clearer escalation thresholds, and more reliable incident reporting pathways. 
  • Deepen trusted information sharing and public‑private collaboration through common handling rules, safer “good‑faith” reporting mechanisms, and regular joint exercises to build muscle memory before a crisis.

Taken together, these elements enable leaders not only to respond more effectively to cyber incidents, but to institutionalize preparedness, coordination, and resilience across the national cyber ecosystem. For African countries more broadly, the model also offers a practical pathway to strengthen regional cyber cooperation—by aligning expectations around escalation, information sharing, and public‑private coordination before a cross‑border incident occurs. By translating high‑level principles into practical, repeatable approaches to crisis readiness, the toolkit underscores the value of trusted international partnerships and alignment with global norms for responsible state behavior in cyberspace. 

Why Kenya’s approach matters beyond its borders

Many countries across the Global South are grappling with similar challenges: fragmented ownership of critical infrastructure, uneven cyber capacity across sectors, and the need to coordinate rapidly under pressure. While firmly grounded in Kenya’s national context, the lessons from ARC Kenya are therefore intentionally designed to resonate far beyond its borders and to be highly transferable. 

Importantly, this work does not end in Kenya. We are already building on these lessons through ARC engagements in other regions, including a new workstream in Mexico, applying the same approach to strengthen preparedness, coordination, and resilience across different national contexts. 

By design, the ARC initiative is not simply a record of a single exercise. It is a foundation others can build on—at a national or regional level—offering leaders a practical starting point to turn shared responsibility into sustained capability. 

Explore the ARC Kenya Toolkit & Tabletop Exercise


For more than a decade, the Microsoft Digital Crimes Unit (DCU) has persistently disrupted cybercrime and nation-state threats targeting people, organizations, and critical infrastructure. Explore major disruptions—and the ongoing cases and operations behind them here: Disrupting cyberthreats since 2008 | Microsoft

The post Strengthening cyber capacity in Kenya: A new toolkit with lessons for the region appeared first on Microsoft On the Issues.

  •  

From capability to responsibility: Securing our global digital ecosystem with next‑generation AI

Cybersecurity is at a turning point. Advanced AI models are dramatically accelerating vulnerability discovery and creating conditions ripe for exploitation, underscored by the announcement of Claude Mythos Preview. This marks a shift, and whether this technology will favor defenders or attackers will depend on the choices we make now. 

With the right safeguards, these capabilities can help trusted defenders identify and fix vulnerabilities across critical systems in hospitals, power grids, water, and telecommunications. Released irresponsibly or not properly secured, however, those same capabilities could be abused by malicious actors, threatening the foundations of our digital ecosystem. 

Much of the discussion has rightly focused on risks. As advanced AI models speed up the discovery of vulnerabilities, the way we fix them must speed up too. That means stronger pre-deployment risk assessments and close collaboration between governments, frontier AI developers, software providers, and the broader ecosystem to ensure these tools reduce, rather than increase, cyber risk. This is particularly important as AI systems themselves have become high‑value targets, requiring stronger protection of models, systems, data, and underlying infrastructure. 

This is ultimately an international challenge. Neither software supply chains nor threat actors stop at borders. Neither can our response. Meeting this moment will require shared approaches across countries, sectors, and systems—rooted in trust, shared standards, resilience, and responsible use. 

This moment is also an opportunity. Security has been and remains the top priority at Microsoft. Over the last two years, through our  Secure Future Initiative, we have strengthened our security foundations for this age of AI, in part by using AI to accelerate vulnerability discovery and remediation. We have also invested in fundamental AI for security research, including the development of open-source industry benchmarks that can be used to evaluate whether models are ready for real-world security work. We are accelerating that work through deeper public-private collaboration and in partnership with AI, including Anthropic’s Project Glasswing and OpenAI’s Trusted Access for Cyber program. 

Securing our digital ecosystem with next‑generation AI is within reach but is not automatic.  

Building secure foundations for the era of frontier AI  

Ensuring advanced AI technologies are used to strengthen cybersecurity requires deliberate and urgent action. We are sharing the following recommendations as practical steps governments, industry, and the broader ecosystem can take to ensure these tools, often referred to as “frontier AI”, reinforce the security foundations on which digital societies depend. And we hope to continue to partner with model providers, industry and government so we can work together to improve security outcomes for all. 

1. Reinforce core cybersecurity practices  

Advanced AI can strengthen cybersecurity only when strong, consistent cyber hygiene is already in place. As frontier AI accelerates vulnerability discovery and response, core practices such as rapid patching, access control, and system resilience become more critical, not less. 

Security gains in the frontier AI era depend on close coordination between technology providers advancing new capabilities and the organizations responsible for operating, updating, and securing real‑world systems. Without this interdependence, advanced AI cannot deliver durable improvements in security. No organization can solve these cybersecurity problems alone. 

That is why sustained investment in what we know works remains essential: secure‑by‑design product lifecycles, Zero Trust architectures, multi‑factor authentication, least‑privileged access, and ongoing security training. Broad adoption and harmonization of established cybersecurity frameworks to ensure consistent resilience across AI‑enabled systems. Trusted cloud environments that enable these practices at scale, supporting secure data handling, continuous patching, and the secure deployment of AI‑enabled tools for defenders.  

  2. Release advanced capabilities responsibly  

As frontier AI systems gain reasoning, coding, and agentic capabilities, some of the most serious security risks arise before deployment, including realistic misuse involving multi‑step reasoning, tool use, and reconnaissance. Technical safety benchmarks remain important, but they are insufficient without rigorous, real‑world testing.  

As a result, governments are increasingly establishing pre‑deployment evaluations that combine technical testing with threat modeling. These assessments are most effective when frontier developers work closely with organizations that track national‑security risks. Investing in secure evaluation environments and modern testing methods can help governments keep pace as capabilities advance.  

Responsible release practices, including phased and controlled access, are a critical extension of this approach. Our work with Anthropic in Project Glasswing offers one practical model, enabling trusted defenders to evaluate advanced capabilities in constrained settings prior to broader release. Similarly, OpenAI and Microsoft work closely through Trusted Access for Cyber program, and we already support OpenAI’s use of scoped, early deployments for safety and security testing.  

Responsibility does not end at release. Organizations that deploy frontier models are often best positioned to detect emerging misuse and should monitor, mitigate, and share threat information. Microsoft is working with peers through the Frontier Model Forum to advance best practices for evaluating and managing cyber risk and enable information sharing. Governments should encourage continued industry collaboration to restrict access for identified threat actors and counter adversarial or malicious use of advanced AI. 

  3. Modernize vulnerability management  

AI is changing both the speed of vulnerability discovery and what constitutes meaningful security risk. Faster discovery only improves security if triage, validation, and remediation can keep up. 

As AI accelerates discovery, vulnerability management must shift from tracking raw volume to reducing real‑world risk. That means prioritizing vulnerabilities that are genuinely exploitable, assigning clear responsibility for triage and remediation, and using phased, risk‑based disclosure when private coordination improves safety. Above all, systems must be designed around validation and realistic remediation capacity, not the assumption that more findings automatically lead to better security. 

Developers of frontier AI models should embed vulnerability coordination and disclosure directly into responsible‑release frameworks. And work with governments and industry to ensure findings are routed to the right owners, acted on early, and supported by clear coordination pathways. 

  4. Fix faster: Strengthen and accelerate response and remediation 

As AI accelerates vulnerability discovery, remediation must keep pace. Initiatives such as DARPA’s AI Cyber Challenge show how AI can help both find and fix flaws in open‑source software. Hardening defenses requires investment not just in detection tools but in the people, processes, and infrastructure responsible for fixing vulnerabilities, especially in critical sectors. 

Much of the software underpinning critical infrastructure relies on open‑source components maintained by small teams or volunteers with limited security capacity. A surge in AI‑enabled discovery risks overwhelming existing triage and disclosure processes. Efforts such as the GitHub Secure Open Source Fund, alongside investments by Microsoft and others through the Linux Foundation, Alpha‑Omega, and OpenSSF, are helping maintainers adapt in ways that are practical and aligned with existing workflows.  

Governments should treat remediation capacity as a core resilience priority, including sustained investment in and support for maintainers, surge capacity during large discovery events, and modernized disclosure pathways—recognizing that effective remediation still largely depends on human judgment, coordination, and time.  

  5. Advance AI security internationally 

AI security is essential to deploy AI at scale. Because AI systems, supply chains, and the risks they introduce operate across borders, national approaches alone will not be sufficient. 

Governments and industry should work together to build interoperable international foundations for AI security, including risk evaluation, coordinated vulnerability disclosure, and information sharing. Priorities should include strengthening the defensive use of AI, preventing misuse through shared norms and safeguards, and securing AI systems- and the AI technology stack.  

Global participation is critical. Countries and organizations with limited cybersecurity resources or legacy infrastructure are often the most exposed. International cooperation should prioritize capacity‑building, ensuring that the security benefits of AI are realized broadly and equitably. 

AI security is not just a safeguard; it is an enabler for innovation and growth. By acting collectively and moving quickly, governments and industry can strengthen global digital resilience and unlock the trusted adoption of AI across economies, critical infrastructure, and public services.

Meeting the moment: Use frontier AI capabilities to build trust and confidence  

Meeting this moment is ultimately about trust: not in any single technology or provider, but in our collective ability to introduce advanced AI responsibly.  

Used deliberately and built on strong security foundations, these capabilities can strengthen cybersecurity and reinforce confidence in the systems society depends on. The choice is not between innovation and security but whether we enable them to reinforce one another. 

That outcome is within reach. With governments, industry, and infrastructure operators aligned, advanced AI can be deployed in ways that match real‑world defensive capacity and support trusted, lawful action. Done right and working together, frontier AI can help protect the digital infrastructure that underpins modern life and build lasting confidence in its resilience. 


For more than a decade, the Microsoft Digital Crimes Unit (DCU) has persistently disrupted cybercrime and nation-state threats targeting people, organizations, and critical infrastructure. Explore major disruptions—and the ongoing cases and operations behind them here: Disrupting cyberthreats since 2008 | Microsoft

The post From capability to responsibility: Securing our global digital ecosystem with next‑generation AI appeared first on Microsoft On the Issues.

  •  

New findings show how hands-on support can improve water sector cybersecurity

Cyber threats to water systems are no longer hypothetical. When attacks succeed, communities can face loss of trust, safety concerns, or service disruptions.

Today, Microsoft, in collaboration with the Cyber Readiness Institute (CRI) and the Center on Cyber Technology and Innovation (CCTI), is releasing a report that examines both the urgency of this challenge and what it will take to close the cyber readiness gap in the water sector. The report draws on a pilot program that provided water and wastewater utilities with practical cybersecurity training paired with hands‑on coaching, testing whether real-world support can meaningfully improve cyber readiness.

The findings point to a clear conclusion: improving cyber resilience in the water sector is achievable when training is paired with hands-on support and delivered through trusted sector partners. Because of the success of this pilot, the program is now a permanent offering, giving water utilities continued access to practical training and support to strengthen cyber resilience and better protect their communities from evolving threats.

Why cyber resilience in the water sector matters now

Water and wastewater utilities underpin public health, economic activity, and community resilience across all critical infrastructure. Yet recent assessments from the U.S. intelligence community and public reporting on cyber incidents underscore how exposed many systems remain. Even larger, well-resourced utilities have experienced cyber incidents, highlighting vulnerabilities that are far more pronounced among smaller operators serving rural and underserved communities.

Awareness of cyber risk is growing, but awareness is not preparedness. The challenge is how to move from growing awareness to sustained, operational readiness, especially for utilities with limited time, funding, and technical capacity.

What the pilot set out to test and what it showed

The CRI pilot was designed to answer a practical question facing the water sector: can accessible, behavior‑focused cybersecurity training paired with hands‑on support meaningfully improve cyber readiness?

Participating utilities used CRI’s free Cyber Readiness Program, which focuses on core cybersecurity practices such as strong authentication, software updates, phishing awareness, and secure data handling. Utilities also had access to CRI Certified Cyber Coaches, who worked directly with designated “Cyber Leaders” inside utilities to help translate training into policies, playbooks, and incident response planning. This model paired accessible training with personalized support to help utilities make meaningful progress despite resource constraints. The pilot revealed three clear findings about what helps and what limits cyber readiness in the water sector.

  • CRI program improves readiness: Participating utilities reported stronger cybersecurity fundamentals, greater confidence responding to incidents, and the identification of previously undocumented, yet critical, gaps such as missing continuity plans and weak password practices.
  • Hands-on support accelerates success: Utilities paired with a CRI‑certified coach were significantly more likely to complete the program than those participating on a self‑paced basis.
  • Demand exceeds capacity: While interest in cybersecurity support is high, staffing shortages, limited funding, and dependence on third-party vendors continue to limit utilities’ ability to fully implement improvements. Participation data helps explain this finding: of the 113 utilities that expressed initial interest, 72 began the program and 43 completed it.

Implications for policymakers and the ecosystem

The findings point to a central takeaway for policymakers and the ecosystem: improving cybersecurity outcomes requires moving beyond sharing information to providing hands-on support that helps utilities implement and sustain change.

  • Free resources are necessary but not enough: No-cost guidance alone cannot overcome staffing and funding constraints. Effective programs must include implementation support, like cyber coaches, to drive real outcomes.
  • Incentives increase participation: Tying cybersecurity training to operator licensing or continuing education requirements helps embed cyber readiness into routine professional development.
  • Trusted messengers drive engagement: Participation and completion were highest when programs were facilitated through established sector associations and networks that utilities already trust.

A path forward through collaboration

The lesson from this pilot is clear: cyber readiness improves when training is paired with hands‑on support and facilitated through trusted partners. But the findings also underscore a broader reality: lasting progress will require moving beyond information sharing toward approaches that build real, sustained capacity building on the ground.

At Microsoft, this work reflects a practical commitment to supporting cyber resilience across critical infrastructure, helping to move from awareness to action. Addressing the challenges identified in this report will require continued collaboration among policymakers, sector associations, nonprofits, and the private sector.

This work also complements Microsoft’s broader commitment to be water positive, including minimizing our water use and replenishing more water than we consume[1][2], by helping strengthen the resilience of the water systems and utilities that serve communities. Supporting practical cyber readiness is one way we can contribute to more resilient water systems for the future.

[1] Sustainability | Microsoft

[2] Building Community-First AI Infrastructure – Microsoft On the Issues

The post New findings show how hands-on support can improve water sector cybersecurity appeared first on Microsoft On the Issues.

  •  

Defending the gates: How a global coalition disrupted Tycoon 2FA, a major driver of initial access and large-scale online impersonation

One email was all it took. An employee clicked what looked like a routine sign‑in request. Behind the scenes, attackers swiped credentials, slipped past security controls, impersonated a trusted user, and gained access to critical systems. In other cases, similar intrusions delayed paychecks, rerouted invoices, stole sensitive data, locked up entire networks, interrupted patient care, and strained already tight budgets at schools and critical services. 

Those attacks were powered by Tycoon 2FA. Today, Microsoft, Europol, and industry partners announced a coordinated action to disrupt the service responsible for tens of millions of fraudulent emails reaching over 500,000 organizations each month worldwide. 

Disrupting a global phishing operation 

Active since at least 2023, Tycoon 2FA enabled thousands of cybercriminals to impersonate real users and gain unauthorized access to email and online service accounts, including Microsoft 365, Outlook, and Gmail. Unlike traditional phishing kits, Tycoon 2FA was designed to defeat additional security protections, including multifactor authentication, allowing cybercriminals to log in as legitimate users without triggering alerts, even on protected accounts. 

Acting under a court order from the U.S. District Court for the Southern District of New York, and for the first time in coordination with Europol’s Cyber Intelligence Extension Programme (CIEP), Microsoft seized 330 active domains that powered Tycoon 2FA’s core infrastructure, including control panels and fraudulent login pages. The CIEP framework brought public‑ and private‑sector partners together to move from simply sharing intelligence to coordinated, cross‑border action, accelerating disruption and limiting further harm. 

Taking this infrastructure offline cuts off a major pipeline for account takeovers and helps protect people and organizations from follow‑on attacks such as data theft, ransomware, business email compromise, and financial fraud. 

The scale and real‑world impact of Tycoon 2FA 

By mid‑2025, Tycoon 2FA accounted for approximately 62 percent of all phishing attempts Microsoft blocked, including more than 30 million emails in a single month. That placed Tycoon 2FA among the largest phishing operations globally.  

Despite extensive defenses, the service is linked to an estimated 96,000 distinct phishing victims worldwide since 2023, including more than 55,000 Microsoft customers.  

Healthcare and education organizations were hit hardest. More than 100 members of Health‑ISAC, a global threat-sharing group for the health sector and a co-plaintiff in this case, were successfully phished. In New York alone, at least two hospitals, six municipal schools, and three universities faced attempted or successful compromise through Tycoon 2FA. These incidents had tangible consequences: disrupted operations, diverted resources, and delayed patient care.  

Why Tycoon 2FA was so dangerous 

Tycoon 2FA combined convincing phishing templates, realistic landing pages, and real‑time capture of credentials and authentication codes into an easy‑to‑use package that scaled quickly. By lowering the technical barrier to entry, it allowed criminals with limited expertise to run sophisticated impersonation campaigns. 

With each successful phishing victim, attackers could operate with the same level of trust as legitimate users moving laterally across systems, accessing sensitive data, and abusing sign‑on connections without raising alarms. Research from Microsoft Threat Intelligence provides more details on how Tycoon 2FA operated. 

Dark‑themed admin dashboard showing security and login activity. At the top are summary cards for Total Visits (5), Valid (4), Invalid (2), and SSO (0). The center includes a donut chart comparing valid, invalid, and SSO logins, a bar chart of login websites with Microsoft highlighted, and a world map labeled “Visitors by Country.” Below, a table lists valid accounts with columns for email, website, browser, IP, country, 2FA status, and date, with action buttons such as “Copy Zip Pass” and “Download.”
The Tycoon 2FA customer dashboard.

This shift reflects a broader trend in cybercrime: identity, not infrastructure, has become the primary target. A single compromised account can now unlock banking systems, healthcare portals, workplace applications, and social media accounts. 

Inside the impersonation economy

Tycoon 2FA operated like a business within the broader impersonation‑for‑hire ecosystem. The primary developer, Saad Fridi, who is believed to be based in Pakistan, worked alongside partners responsible for marketing, payments, and technical support. 

Cybercriminals typically used Tycoon 2FA alongside other illicit services. While Tycoon 2FA captured credentials and session tokens, other services handled mass email delivery, malware distribution, hosting, and access monetization. For example, RedVDS, disrupted by Microsoft in January 2026, provided inexpensive virtual computers, which cybercriminals paired with Tycoon 2FA to deliver phishing campaigns. Together, these different services created an interconnected ecosystem for identity‑based attacks. Disrupting one component can have cascading effects across the cybercrime economy. 

Sustained pressure reshapes the market 

Over the past 18 months, Microsoft’s Digital Crimes Unit has targeted multiple services that enable impersonation and initial access, including extensive disruption operations of Lumma Stealer, RaccoonO365, Fake ONNX (aka “Caffeine”), and RedVDS. 

When widely used tools are disrupted, attackers are forced to adapt, often shifting to alternatives like Tycoon 2FA. This substitution pattern shows how sustained pressure prevents any single service from remaining dominant while steadily raising the cost and risk of cybercrime. 

These efforts have led to arrests in Egypt and Nigeria, complete service shutdowns, infrastructure loss, and reputational damage for operators beyond law‑enforcement reach. RedVDS alone lost more than 95 percent of its infrastructure since January 2026, significantly degrading its ability to support mass impersonation campaigns and other online scams. 

As pressure increased, many operators tightened access controls, retreated into closed channels, or shut down entirely to avoid legal action. In Tycoon 2FA’s case, Microsoft could not purchase access to the service; the operator rejected attempts by our investigators, requiring a trusted intermediary. In fact, Tycoon 2FA’s operator and the now‑arrested developer of RaccoonO365 communicated with one another, highlighting the ecosystem’s interdependence and how disruptions in one area influence activity elsewhere. 

Screenshot of a dark‑mode chat conversation interface. Multiple message bubbles discuss “2FA/MFA” services, with usernames such as “Raccoon0365,” “ItsPump,” and others visible. Messages reference choosing or not choosing a provider, friendship between groups, and competition between services. Timestamps appear next to messages, and emoji reactions are included.
Correspondence suggesting interactions between the operators of RaccoonO365 and Tycoon 2FA.

Global threats require global action 

Cybercrime operates across borders, and effective response must do the same. Disrupting Tycoon 2FA spanned multiple jurisdictions, underscoring why sustained, coordinated pressure is essential, especially as cybercrime becomes more scalable through automation and AI. 

Microsoft Threat Intelligence, joining many security researchers, identified Tycoon 2FA as one of the most significant threats to identity-based attacks. Microsoft’s Digital Crimes Unit consulted with Europol, which also tracked the actor based on intelligence supplied by TrendAI. Through the CIEP, Europol convened partners to take action. Microsoft worked with industry partners to pursue a coordinated infrastructure disruption, while law enforcement authorities in Latvia, Lithuania, Portugal, Poland, Spain, and the United Kingdom conducted seizures of infrastructure and carried out other operational measures linked to Tycoon 2FA. 

Industry partners, including Proofpoint, Intel 471, and eSentire, expanded visibility through telemetry, threat intelligence, and criminal‑forum insight. Cloudflare assisted by taking down infrastructure outside U.S. jurisdiction, while Health‑ISAC quantified impacts on healthcare organizations. SpyCloud contributed key victimology data, Resecurity facilitated access to Tycoon 2FA, and Coinbase helped trace the movement of stolen funds. Finally, the Shadowserver Foundation supported notifications to more than 200 computer emergency response teams worldwide, helping limit further harm. 

No single organization could have assembled this full picture alone.

Splash page appearing on seized domains.

Sustaining pressure, together 

Stopping identity‑based cybercrime requires action across individuals, organizations, and governments. Multifactor authentication, scrutiny of unexpected messages, strong session controls, and coordinated threat‑sharing all reduce risk. Early enforcement matters too; it prevents small intrusions from escalating into systemic harm. Microsoft will continue applying the lessons learned from Tycoon 2FA and prior disruptions to fragment the impersonation economy, limit scale, and make cybercrime riskier and less profitable. 

The post Defending the gates: How a global coalition disrupted Tycoon 2FA, a major driver of initial access and large-scale online impersonation appeared first on Microsoft On the Issues.

  •  

Extortion and ransomware drive over half of cyberattacks

In 80% of the cyber incidents Microsoft’s security teams investigated last year, attackers sought to steal data—a trend driven more by financial gain than intelligence gathering. According to the latest Microsoft Digital Defense Report, written with our Chief Information Security Officer Igor Tsyganskiy, over half of cyberattacks with known motives were driven by extortion or ransomware. That’s at least 52% of incidents fueled by financial gain, while attacks focused solely on espionage made up just 4%. Nation-state threats remain a serious and persistent threat, but most of the immediate attacks organizations face today come from opportunistic criminals looking to make a profit.

Every day, Microsoft processes more than 100 trillion signals, blocks approximately 4.5 million new malware attempts, analyzes 38 million identity risk detections, and screens 5 billion emails for malware and phishing. Advances in automation and readily available off-the-shelf tools have enabled cybercriminals—even those with limited technical expertise—to expand their operations significantly. The use of AI has further added to this trend with cybercriminals accelerating malware development and creating more realistic synthetic content, enhancing the efficiency of activities such as phishing and ransomware attacks. As a result, opportunistic malicious actors now target everyone—big or small—making cybercrime a universal, ever-present threat that spills into our daily lives.

In this environment, organizational leaders must treat cybersecurity as a core strategic priority—not just an IT issue—and build resilience into their technology and operations from the ground up. In our sixth annual Microsoft Digital Defense Report, which covers trends from July 2024 through June 2025, we highlight that legacy security measures are no longer enough; we need modern defenses leveraging AI and strong collaboration across industries and governments to keep pace with the threat. For individuals, simple steps like using strong security tools—especially phishing-resistant multifactor authentication (MFA)—makes a big difference, as MFA can block over 99% of identity-based attacks. Below are some of the key findings.

Critical services are prime targets with a real-world impact

Malicious actors remain focused on attacking critical public services—targets that, when compromised, can have a direct and immediate impact on people’s lives. Hospitals and local governments, for example, are all targets because they store sensitive data or have tight cybersecurity budgets with limited incident response capabilities, often resulting in outdated software. In the past year, cyberattacks on these sectors had real-world consequences, including delayed emergency medical care, disrupted emergency services, canceled school classes, and halted transportation systems.

Ransomware actors in particular focus on these critical sectors because of the targets’ limited options. For example, a hospital must quickly resolve its encrypted systems, or patients could die, potentially leaving no other recourse but to pay. Additionally, governments, hospitals, and research institutions store sensitive data that criminals can steal and monetize through illicit marketplaces on the dark web, fueling downstream criminal activity. Government and industry can collaborate to strengthen cybersecurity in these sectors—particularly for the most vulnerable. These efforts are critical to protecting communities and ensuring continuity of care, education, and emergency response.

Nation-state actors are expanding operations

While cybercriminals are the biggest cyber threat by volume, nation-state actors still target key industries and regions, expanding their focus on espionage and, in some cases, on financial gain. Geopolitical objectives continue to drive a surge in state-sponsored cyber activity, with a notable expansion in targeting communications, research, and academia.

Key insights:

  • China is continuing its broad push across industries to conduct espionage and steal sensitive data. State-affiliated actors are increasingly attacking non-governmental organizations (NGOs) to expand their insights and are using covert networks and vulnerable internet-facing devices to gain entry and avoid detection. They have also become faster at operationalizing newly disclosed vulnerabilities.
  • Iran is going after a wider range of targets than ever before, from the Middle East to North America, as part of broadening espionage operations. Recently, three Iranian state-affiliated actors attacked shipping and logistics firms in Europe and the Persian Gulf to gain ongoing access to sensitive commercial data, raising the possibility that Iran may be pre-positioning to have the ability to interfere with commercial shipping operations.
  • Russia, while still focused on the war in Ukraine, has expanded its targets. For example, Microsoft has observed Russian state-affiliated actors targeting small businesses in countries supporting Ukraine. In fact, outside of Ukraine, the top ten countries most affected by Russian cyber activity all belong to the North Atlantic Treaty Organization (NATO)—a 25% increase compared to last year. Russian actors may view these smaller companies as possibly less resource-intensive pivot points they can use to access larger organizations. These actors are also increasingly leveraging the cybercriminal ecosystem for their attacks.
  • North Korea remains focused on revenue generation and espionage. In a trend that has gained significant attention, thousands of state-affiliated North Korean remote IT workers have applied for jobs with companies around the world, sending their salaries back to the government as remittances. When discovered, some of these workers have turned to extortion as another approach to bringing in money for the regime.

The cyber threats posed by nation-states are becoming more expansive and unpredictable. In addition, the shift by at least some nation-state actors to further leveraging the cybercriminal ecosystem will make attribution even more complicated. This underscores the need for organizations to stay abreast of the threats to their industries and work with both industry peers and governments to confront the threats posed by nation-state actors.

2025 saw an escalation in the use of AI by both attackers and defenders

Over the past year, both attackers and defenders harnessed the power of generative AI. Threat actors are using AI to boost their attacks by automating phishing, scaling social engineering, creating synthetic media, finding vulnerabilities faster, and creating malware that can adapt itself. Nation-state actors, too, have continued to incorporate AI into their cyber influence operations. This activity has picked up in the past six months as actors use the technology to make their efforts more advanced, scalable, and targeted.

For defenders, AI is also proving to be a valuable tool. Microsoft, for example, uses AI to spot threats, close detection gaps, catch phishing attempts, and protect vulnerable users. As both the risks and opportunities of AI rapidly evolve, organizations must prioritize securing their AI tools and training their teams. Everyone—from industry to government—must be proactive to keep pace with increasingly sophisticated attackers and to ensure that defenders keep ahead of adversaries.

Adversaries aren’t breaking in; they’re signing in

Amid the growing sophistication of cyber threats, one statistic stands out: more than 97% of identity attacks are password attacks. In the first half of 2025 alone, identity-based attacks surged by 32%. That means the vast majority of malicious sign-in attempts an organization might receive are via large-scale password guessing attempts. Attackers get usernames and passwords (“credentials”) for these bulk attacks largely from credential leaks.

However, credential leaks aren’t the only place where attackers can obtain credentials. This year, we saw a surge in the use of infostealer malware by cybercriminals. Infostealers can secretly gather credentials and information about your online accounts, like browser session tokens, at scale. Cybercriminals can then buy this stolen information on cybercrime forums, making it easy for anyone to access accounts for purposes such as the delivery of ransomware.

Luckily, the solution to identity compromise is simple. The implementation of phishing-resistant multifactor authentication (MFA) can stop over 99% of this type of attack even if the attacker has the correct username and password combination. To target the malicious supply chain, Microsoft’s Digital Crimes Unit (DCU) is fighting back against the cybercriminal use of infostealers. In May, the DCU disrupted the most popular infostealer—Lumma Stealer—alongside the US Department of Justice and Europol.

Moving forward: Cybersecurity is a shared defensive priority

As threat actors grow more sophisticated, persistent, and opportunistic, organizations must stay vigilant, continually updating their defenses and sharing intelligence. Microsoft remains committed to doing its part to strengthen our products and services via our Secure Future Initiative. We also continue to collaborate with others to track threats, alert targeted customers, and share insights with the broader public when appropriate.

However, security is not only a technical challenge but a governance imperative. Defensive measures alone are not enough to deter nation-state adversaries. Governments must build frameworks that signal credible and proportionate consequences for malicious activity that violates international rules. Encouragingly, governments are increasingly attributing cyberattacks to foreign actors and imposing consequences such as indictments and sanctions. This growing transparency and accountability are important steps toward building collective deterrence. As digital transformation accelerates—amplified by the rise of AI—cyber threats pose risks to economic stability, governance, and personal safety. Addressing these challenges requires not only technical innovation but coordinated societal action.

The post Extortion and ransomware drive over half of cyberattacks appeared first on Microsoft On the Issues.

  •  
❌