❌

Reading view

Popcorn Time’s forgotten updater left millions of devices exposed to hijacking

You may have forgotten about Popcorn Time. Unfortunately, its updater didn’t forget about your device.

Security researchers have intervened to disable an abandoned update mechanism in Time4Popcorn, a version of the once-popular streaming app. If left running in the background, the updater could have allowed attackers to take control of Windows and Mac computers, even if their owners hadn’t opened the app in years.

Eye Security estimates that the vulnerable updater was present on millions of devices worldwide, including 2.5–3 million Windows computers and around 250,000–350,000 Macs.

Popcorn Time made watching movies and TV shows through BitTorrent look more like browsing Netflix. Rather than making users find torrent files and open them in a separate client, it wrapped the process in a familiar streaming-style interface.

Amid concerns about copyright infringement and its possible consequences, the original developers abandoned it shortly after its launch in 2014. But because its source code was publicly available, other developers could pick it up and create their own versions, known as forks.

One of those was Time4Popcorn, which was also distributed under the name “Popcorn Time.” That shared branding matters because people may have installed the affected software without ever seeing the Time4Popcorn name.

The problem at hand

Time4Popcorn was eventually abandoned too. But its update infrastructure was left behind, and at some point the domains associated with the software became available for others to register.

In other words, the people maintaining the software had gone away. The software’s ability to accept instructions had not. Time4Popcorn’s updater used unencrypted HTTP connections and accepted executable updates without checking digital signatures to verify their authenticity. So, someone who controlled an update domain or was able to tamper with the unencrypted traffic could supply their own program instead.

That combination created a remote code execution vulnerability, tracked as CVE-2026-30612, which could let an attacker run malicious software on a device. An attacker wouldn’t need to persuade someone to watch a movie or click a suspicious attachment. The forgotten updater could do the work for them.

Although Android was affected too, users had an extra layer of protection. Its updater checked for updates when the application was opened, but installing an attacker-supplied APK required the user to approve the installation. It was not the same silent, background takeover route researchers found on Windows and macOS.

What the researchers did

Eye Security registered an abandoned update domain and used the vulnerable mechanism to distribute an update that disabled the updater itself. On Windows, it stopped and disabled the service; on macOS, it prevented the update process from starting. The researchers say their intervention did not delete users’ files or collect host data.

By March 2026, Eye Security reported more than two million downloads of its updater-disabling fix, and update requests to its domains had fallen by 98%. Later that month, it transferred the 15 domains it controlled to the nonprofit Shadowserver Foundation.

Researchers could not remotely disable the Android updater in the same way. And the desktop application still contained other weaknesses, including an obsolete Chrome engine dating from 2014 and disabled sandbox protections, which normally help contain malicious code.

What users should do

If you used Popcorn Time years ago, check the devices on which you installed it. Don’t assume that no longer using an application means its background components have stopped running.

  • Check your list of installed applications for Popcorn Time or Time4Popcorn. Pay particular attention to older Windows PCs, Macs, and Android devices where you may have forgotten about installing it. The affected fork was distributed under both names.
  • Remove the old application. There is no vendor security update for the abandoned Time4Popcorn software. Disabling the updater addresses one vulnerability, not the application’s other security weaknesses.
  • On Windows and macOS, check that the background updater is no longer running. Eye Security identifies the Windows component as Updater.exe, normally inside a Popcorn Time folder under Program Files or Program Files (x86), running through a service called Update Service. On macOS, the component is /Library/PrivilegedHelperTools/PT.updd, with a launch daemon at /Library/LaunchDaemons/PT.updd.plist. Its advisory provides instructions for disabling these components if needed.
  • On Android, uninstall the affected app rather than accepting an update prompt from it. The updater is part of the main application and cannot easily be disabled separately.
  • Use an up-to-date, real-time anti-malware solution to detect and block any attempts to install malware on your devices.

As we saw recently, cybercriminals can use software updates to distribute malware. Remove abandoned apps and check for any background updaters they leave behind.


From reporting threats to removing them.

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
  •  

March 2026 Patch Tuesday fixes two zero-day vulnerabilities

Microsoft releases important security updates on the second Tuesday of every month, known as Patch Tuesday. This month’s update fixes 79 Microsoft CVEs including two zero-day vulnerabilities.

Microsoft defines a zero-day as “a flaw in software for which no official patch or security update is available yet.” So, since the patch is now available, those two are no longer zero-days. There is also no reason to believe they were ever actively exploited.

But let’s have a look at the possible consequences if you don’t install the update.

The vulnerability tracked as CVE-2026-21262 (CVSS score 8.8 out of 10) is a bug in Microsoft SQL Server that lets a logged-in user quietly climb the privilege ladder and potentially become a full database administrator (sysadmin). With that level of control, they can read, change, or delete data, create new accounts, and tamper with database configurations or jobs. Where SQL Server is supposed to check what each user is allowed to do, in this case it can be tricked into granting more power than intended.

There is no user interaction required once the attacker has that foothold: exploitation can happen over the network using crafted SQL requests that abuse the flawed permission checks. In a typical real‑world scenario, this bug would be the second act in an attack chain: first get in with low privileges, then use CVE-2026-21262 to quietly promote yourself to database king and start rewriting the script.

CVE-2026-26127 (CVSS score 7.5 out of 10) is a bug in Microsoft’s .NET platform that lets an attacker remotely crash .NET applications, effectively taking them offline for a while. The flaw lives in Microsoft .NET 9.0 and 10.0, across Windows, macOS, and Linux, in the .NET runtime or libraries, not in a specific app. In other words, it’s a bug in the engine that runs .NET code, so any app created with affected .NET versions could be at risk until patched.

The main outcome is denial of service: an attacker can cause targeted .NET processes to crash or become unstable, leading to downtime or degraded performance. For a public‑facing web API, a payment service, or any line‑of‑business app built on .NET, this can mean real‑world outages and angry users while services are repeatedly knocked over.

Vulnerabilities affecting Microsoft Office users are two remote code execution flaws in Microsoft Office (CVE-2026-26110 and CVE-2026-26113) which can both be exploited via the preview pane, and a Microsoft Excel information disclosure flaw (CVE-2026-26144), which could be used to exfiltrate data via Microsoft Copilot. Office vulnerabilities appear regularly in Patch Tuesday releases, and in this case none have been reported as actively exploited.

How to apply fixes and check if you’re protected

These updates fix security problems and keep your Windows PC protected. Here’s how to make sure you’re up to date:

1. Open Settings

  • Click the Start button (the Windows logo at the bottom left of your screen).
  • Click on Settings (it looks like a little gear).

2. Go to Windows Update

  • In the Settings window, select Windows Update (usually at the bottom of the menu on the left).

3. Check for updates

  • Click the button that says Check for updates.
  • Windows will search for the latest Patch Tuesday updates.
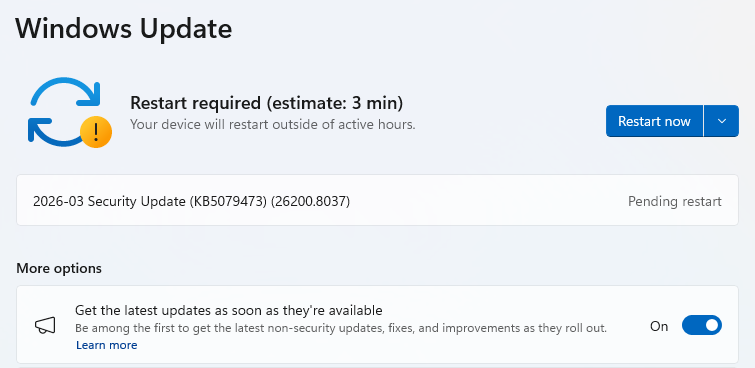
  • If you have selected to get the latest updates as soon as they’re available, you may see this under More options.
  • In which case you may see a Restart required message. Restart your system and the update will complete.
    Restart now to apply patches
  • If not, continue with the steps below.

4. Download and Install

  • If updates are found, they’ll start downloading right away. Once complete, you’ll see a button that says Install or Restart now.
  • Click Install if needed and follow any prompts. Your computer will usually need a restart to finish the update. If it does, click Restart now.
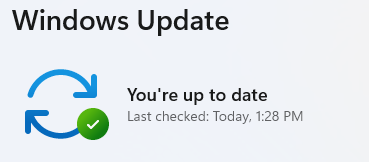
    Windows up to date

5. Double-check you’re up to date

  • After restarting, go back to Windows Update and check again. If it says You’re up to date, you’re all set!

We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
  •  

Why iPhone users should update and restart their devices now

If you were still questioning whether iOS 26+ is for you, now is the time to make that call.

Why?

On December 12, 2025, Apple patched two WebKit zero‑day vulnerabilities linked to mercenary spyware and is now effectively pushing iPhone 11 and newer users toward iOS 26+, because that’s where the fixes and new memory protections live. These vulnerabilities were primarily used in highly targeted attacks, but such campaigns are likely to expand over time.

WebKit powers the Safari browser and many other iOS applications, so it’s a big attack surface to leave exposed and isn’t limited to “risky” behavior. These vulnerabilities allowed an attacker to execute arbitrary code on a device after exploitation via malicious web content.

Apple has confirmed that attackers are already exploiting these vulnerabilities in the wild, making installation of the update a high‑priority security task for every user. Campaigns that start with diplomats, journalists, or executives often lead to tooling and exploits leaking or being repurposed, so “I’m not a target” is not a viable safety strategy.​

Due to public resistance to new features like Liquid Glass, many iPhone users have not yet upgraded to iOS 26.2. Reports suggest adoption of iOS 26 has been unusually slow. As of January 2026, only about 4.6% of active iPhones are on iOS 26.2, and roughly 16% are on any version of iOS 26, leaving the vast majority on older releases such as iOS 18.

However, Apple only ships these fixes and newer protections, such as Memory Integrity Enforcement, on iOS 26+ for supported devices. Users on older, unsupported devices won’t be able to access these protections at all.

Another important factor in the upgrade cycle is restarting the device. What many people don’t realize is that when you restart your device, any memory-resident malware is flushed—unless it has somehow gained persistence, in which case it will return. High-end spyware tools tend to avoid leaving traces needed for persistence and often rely on users not restarting their devices.

Upgrading requires a restart, which makes this a win-win: you get the latest protections, and any memory-resident malware is flushed at the same time.

For iOS and iPadOS users, you can check if you’re using the latest software version, go to Settings > General > Software Update. It’s also worth turning on Automatic Updates if you haven’t already. You can do that on the same screen.

How to stay safe

The most important fix—however painful you may find it—is to upgrade to iOS 26.2. Not doing means missing an accumulating list of security fixes, leaving your device vulnerable to more and more newly found vulnerabilities.

 But here are some other useful tips:

  • Make it a habit to restart your device on a regular basis. The NSA recommends doing this weekly.
  • Do not open unsolicited links and attachments without verifying with the trusted sender.
  • Remember, Apple threat notifications will never ask users to click links, open files, install apps or ask for account passwords or verification code.
  • For Apple Mail users specifically, these vulnerabilities create risk when viewing HTML-formatted emails containing malicious web content.
  • Malwarebytes for iOS can help keep your device secure, with Trusted Advisor alerting you when important updates are available.
  • If you are a high-value target, or you want the extra level of security, consider using Apple’s Lockdown Mode.

We don’t just report on phone security—we provide it

Cybersecurity risks should never spread beyond a headline. Keep threats off your mobile devices by downloading Malwarebytes for iOS, and Malwarebytes for Android today.

  •  
❌