❌

Normal view

Update your iPhone, iPad, or Mac: Flaw could run attackers’ code

29 September 2026 at 12:35

Apple has released updates for iPhones, iPads, and Macs to fix a flaw that could let an attacker run code when a device processes a malicious file. Apple says it may have been used in highly targeted attacks against iPhone users running versions of iOS before iOS 27.

The fix is in iOS and iPadOS 26.7.1, as well as macOS Sequoia 15.8.1 and macOS Tahoe 26.7.1. Check Software Update on each of your Apple devices and install the latest version offered.

Updates for your particular device

The table below shows which relevant updates are available and links to Apple’s security information for each one.

UpdateAvailable for
iOS 26.7.1 and iPadOS 26.7.1iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
macOS Tahoe 26.7.1macOS Tahoe
macOS Sequoia 15.8.1macOS Sequoia

How to update your Apple devices

How to update your iPhone or iPad

To check if you’re using the latest software version, go to Settings > General > Software Update. You’ll see if an update is available and be guided through installing it.

Turn on Automatic Updates if you haven’t already—you’ll find it on the same screen.

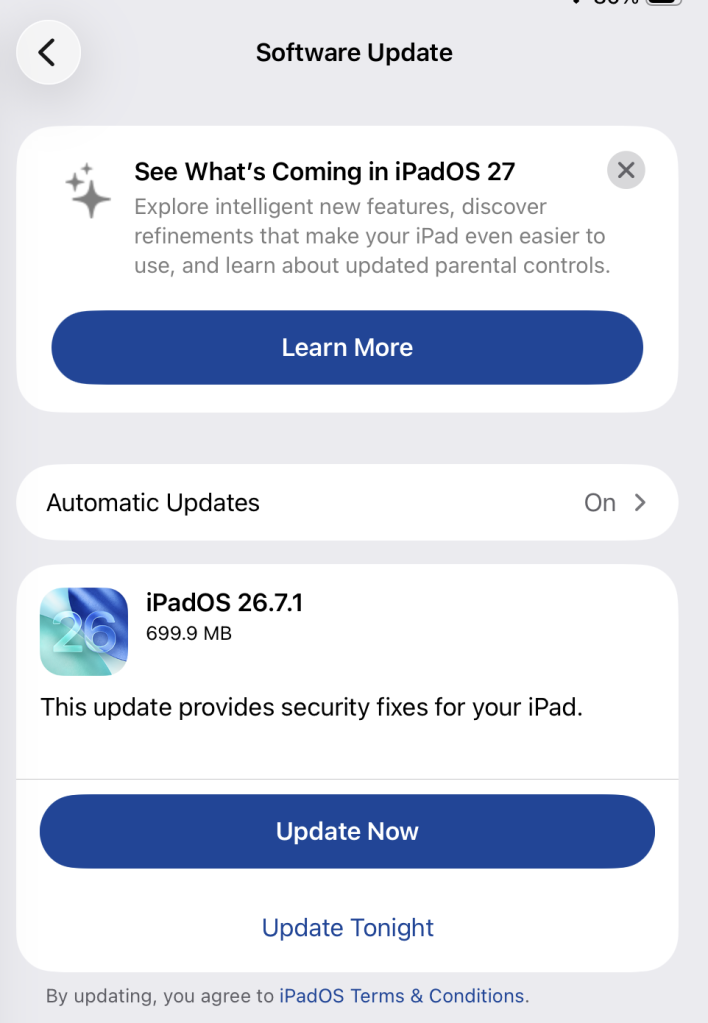
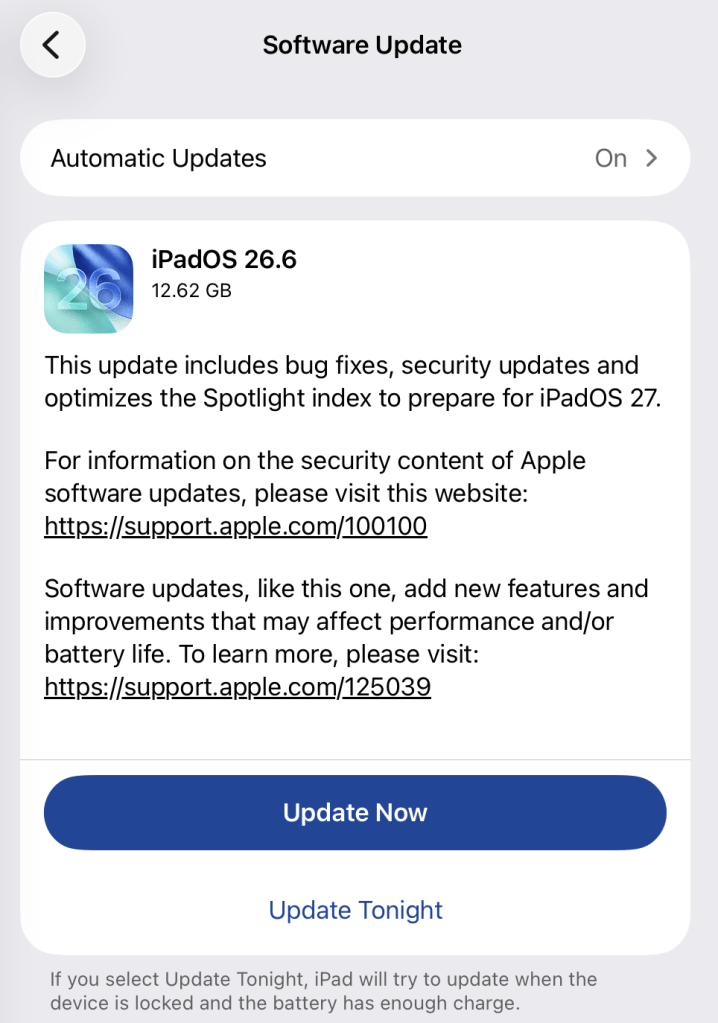
Available update options on iPad

How to update macOS on any version

To update macOS on any supported Mac, use Software Update:

  • Click the Apple menu in the upper-left corner of your screen.
  • Choose System Settings (or System Preferences on older versions).
  • Select General in the sidebar, then click Software Update on the right. On older macOS, look for Software Update directly.
  • Your Mac will check for updates automatically. If updates are available, click Update Now (or Upgrade Now for major new versions) and follow the on-screen instructions. Before you upgrade to macOS Tahoe 26, read Apple’s instructions.
  • Enter your administrator password if prompted, then let your Mac finish the update. It may need to restart.
  • Make sure your Mac stays plugged in and connected to the internet until the update is done.

Technical details

The bug, CVE-2026-86950, affects CoreGraphics, an Apple framework used throughout its operating systems and apps to display and process visual content such as images and PDFs.

It’s an out-of-bounds write issue, which Apple addressed with improved bounds checking. This type of bug happens when software writes data beyond the limits of its allocated area of memory. It can overwrite other data in memory, interfere with the normal operation of the program, cause a crash, or even let an attacker take control of the affected process. In this case, processing a maliciously crafted file may lead to an attacker running their own code.

Apple says it is aware of a report that the issue may have been exploited in an “extremely sophisticated attack” against specific people using versions of iOS before iOS 27. Although the reported attack was highly targeted, other attackers could try to exploit the flaw now that it has been disclosed. 


Scammers know more about you than you think. 

Malwarebytes Mobile Security protects you from phishing, scam texts, malicious sites, and more. With real-time AI-powered Scam Guard built right in. 

.wp-block-kadence-advancedbtn.kb-btns97520_6de029-2f{gap:var(--global-kb-gap-xs, 0.5rem );justify-content:flex-start;align-items:center;}.kt-btns97520_6de029-2f .kt-button{font-weight:normal;font-style:normal;}.kt-btns97520_6de029-2f .kt-btn-wrap-0{margin-right:5px;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button{color:#555555;border-color:#555555;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:hover, .wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:focus{color:#ffffff;border-color:#444444;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button::before{display:none;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:hover, .wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:focus{background:#444444;}
ul.menu .wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button{width:initial;}.wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button{color:var(--color-neutral-10);background:var(--color-brand-blue-60);border-top-left-radius:40px;border-top-right-radius:40px;border-bottom-right-radius:40px;border-bottom-left-radius:40px;box-shadow:1px 1px 2px 0px rgba(0, 0, 0, 0.2);}.wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button:hover, .wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button:focus{box-shadow:0px 4px 0px 0px var(--color-brand-blue-90);}Try it now

Update your iPhone, iPad, or Mac: Flaw could run attackers’ code

29 September 2026 at 12:35

Apple has released updates for iPhones, iPads, and Macs to fix a flaw that could let an attacker run code when a device processes a malicious file. Apple says it may have been used in highly targeted attacks against iPhone users running versions of iOS before iOS 27.

The fix is in iOS and iPadOS 26.7.1, as well as macOS Sequoia 15.8.1 and macOS Tahoe 26.7.1. Check Software Update on each of your Apple devices and install the latest version offered.

Updates for your particular device

The table below shows which relevant updates are available and links to Apple’s security information for each one.

UpdateAvailable for
iOS 26.7.1 and iPadOS 26.7.1iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
macOS Tahoe 26.7.1macOS Tahoe
macOS Sequoia 15.8.1macOS Sequoia

How to update your Apple devices

How to update your iPhone or iPad

To check if you’re using the latest software version, go to Settings > General > Software Update. You’ll see if an update is available and be guided through installing it.

Turn on Automatic Updates if you haven’t already—you’ll find it on the same screen.

Available update options on iPad

How to update macOS on any version

To update macOS on any supported Mac, use Software Update:

  • Click the Apple menu in the upper-left corner of your screen.
  • Choose System Settings (or System Preferences on older versions).
  • Select General in the sidebar, then click Software Update on the right. On older macOS, look for Software Update directly.
  • Your Mac will check for updates automatically. If updates are available, click Update Now (or Upgrade Now for major new versions) and follow the on-screen instructions. Before you upgrade to macOS Tahoe 26, read Apple’s instructions.
  • Enter your administrator password if prompted, then let your Mac finish the update. It may need to restart.
  • Make sure your Mac stays plugged in and connected to the internet until the update is done.

Technical details

The bug, CVE-2026-86950, affects CoreGraphics, an Apple framework used throughout its operating systems and apps to display and process visual content such as images and PDFs.

It’s an out-of-bounds write issue, which Apple addressed with improved bounds checking. This type of bug happens when software writes data beyond the limits of its allocated area of memory. It can overwrite other data in memory, interfere with the normal operation of the program, cause a crash, or even let an attacker take control of the affected process. In this case, processing a maliciously crafted file may lead to an attacker running their own code.

Apple says it is aware of a report that the issue may have been exploited in an “extremely sophisticated attack” against specific people using versions of iOS before iOS 27. Although the reported attack was highly targeted, other attackers could try to exploit the flaw now that it has been disclosed. 


Scammers know more about you than you think. 

Malwarebytes Mobile Security protects you from phishing, scam texts, malicious sites, and more. With real-time AI-powered Scam Guard built right in. 

.wp-block-kadence-advancedbtn.kb-btns97520_6de029-2f{gap:var(--global-kb-gap-xs, 0.5rem );justify-content:flex-start;align-items:center;}.kt-btns97520_6de029-2f .kt-button{font-weight:normal;font-style:normal;}.kt-btns97520_6de029-2f .kt-btn-wrap-0{margin-right:5px;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button{color:#555555;border-color:#555555;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:hover, .wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:focus{color:#ffffff;border-color:#444444;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button::before{display:none;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:hover, .wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:focus{background:#444444;}
ul.menu .wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button{width:initial;}.wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button{color:var(--color-neutral-10);background:var(--color-brand-blue-60);border-top-left-radius:40px;border-top-right-radius:40px;border-bottom-right-radius:40px;border-bottom-left-radius:40px;box-shadow:1px 1px 2px 0px rgba(0, 0, 0, 0.2);}.wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button:hover, .wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button:focus{box-shadow:0px 4px 0px 0px var(--color-brand-blue-90);}Try it now

Update Chrome: 108 security fixes for desktop, new release for Android

24 September 2026 at 13:06

Over the last few days, Google issued several different Chrome updates.

On September 22, Google released a Stable Channel Update for Desktop. This is the most important one for desktop users. It brings Chrome to version 154.0.8037.57 for Linux and versions 154.0.8037.57/.58 for Windows and Mac. The update includes 108 security fixes including 11 rated Critical.

It will roll out over the coming days and weeks.

One day later, Google released Chrome 155 for Android, version 155.0.8059.16, to a small percentage of users. It may not be available on Google Play for everyone yet, but keep an eye out for it. Google says it includes stability and performance improvements.

On top of these, Chrome 155 is also available in the Beta channel. The Android release is an Early Stable rollout, meaning Google sends it to a small share of users first, to spot unexpected compatibility or reliability issues before expanding it to everyone. Beta is a separate prerelease version for people who want to try upcoming features roughly four to six weeks before Stable. It is relatively polished but can still contain bugs, so it is best suited to testing rather than everyday use.

How to update Chrome

The easiest option is to allow Chrome to update automatically. But you can end up lagging behind on updates if you never close your browser or if something goes wrong, such as an extension preventing the update.

If you don’t want to wait for the rollout to reach you, manually updating is easy. open About Google Chrome from Chrome’s settings or Help menu. Chrome will check for updates. If one is available, click Relaunch to apply it.

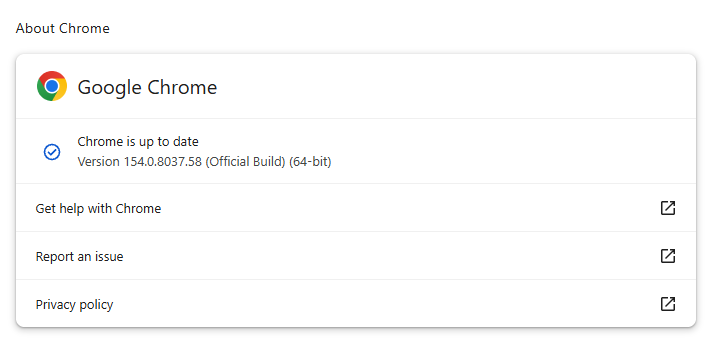
Chrome 154.0.8037.58 is up to date

You can find an explanation of the version numbering system and step-by-step instructions in our guide: How to update Chrome on every operating system.

Technical details

Some of the desktop security fixes deserve a closer look.

Let’s start with CVE-2026-95350, a buffer overflow flaw in ANGLE, Chrome’s graphics-translation layer.

A buffer overflow is a bug in code that allows an attack to happen when a program puts more data into an area of memory than it can hold. Essentially, the attacker writes garbage data that fills up the memory, then writes code that overwrites existing code in adjoining memory, which later gets executed by the vulnerable process.

A crafted webpage could potentially trigger the flaw, which could lead to memory safety bugs, including browser crashes or possible code execution.

Another Critical buffer overflow bug in ANGLE is tracked as CVE-2026-95281. A malicious webpage could potentially reach vulnerable graphics-processing code, so the bug may enable serious impacts such as browser compromise, but Google has not provided exploitation details.

And then there is CVE-2026-95357, an out-of-bounds write in Chrome’s GPU component. This means a program could write data outside its intended area of memory.

The GPU component is the part of Chrome that handles how graphics work with your computer’s graphics processor.


Stop threats before they can do any harm.

Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →

Some cheap smart glasses are a security disaster

22 September 2026 at 17:04

Apart from the privacy concerns around smart glasses, researchers have found that some cheap brands come with barely any security at all.

ABC Australia reports that researchers from NSB Cyber and Abstract Shield tested two inexpensive pairs, costing A$60 and A$110 (around US$42 and US$78), and found more than a dozen flaws across the smart glasses themselves, their app, and an associated website.

The main problem they uncovered was insecure Bluetooth pairing: If the glasses were powered on and not connected to their owner’s phone, an attacker could connect first, with no password or meaningful pairing confirmation.

After connecting, an attacker could reportedly control the glasses to capture photos or recordings, copy existing media, and intercept data moving between the glasses and the phone. An attacker could also make another device appear to be the victim’s glasses, allowing it to connect to the owner’s mobile app.

The testing also found that a Bluetooth-visible device identifier could allegedly be used with a weakness in the app’s website to retrieve a user’s email address and date of birth.

The research uncovered another privacy issue. ABC reports that voice or text submitted to the built-in AI, along with images sent to it, was first transmitted to a server in Shenzhen and could be forwarded elsewhere, depending on the function. The tests did not establish how the data was subsequently used.

The server locations, combined with some of the AI’s answers to specific questions, led researchers to conclude that the chatbot companion relied at least in part on Chinese sovereign AI models. Professor Kimberlee Weatherall, a technology regulation expert involved in the testing, said the failure to identify China in the privacy policy appeared to violate the Australian Privacy Principles,

The timing of the testing is also relevant because Australia’s smart-device security standards apply to most consumer smart devices manufactured on or after March 4, 2026. They require, among other measures, no universal default passwords, a way to report vulnerabilities, and information about the minimum security-update period. Devices made before that date are outside the requirements.

Experts quoted by ABC said the devices violated Australia’s privacy laws and were also likely to breach several sections of the Cyber Security Act. However, whether the new smart-device standards apply would depend partly on when the glasses were manufactured, and the rules have not yet been tested in a known enforcement action.

Professor Weatherall said:

“The rules say that the password must be unique. It doesn’t even seem like they were applying a password, which might mean that their standards are so low they don’t even technically breach that rule, which I find amazing.”

What to do

We’re not fans of smart glasses, expensive or cheap. But if you own a pair:

  • Avoid pairing or using inexpensive camera glasses that lack a clear physical pairing step, account authentication, a published security-contact process, and a stated update-support period.
  • Stop using their AI or cloud features for sensitive material, remove unnecessary permissions from the companion app, check for firmware and app updates, and consider returning the product if the vendor cannot document a fix.
  • Ask permission before recording people, and check your local laws to understand what is and isn’t allowed.

From reporting threats to removing them.

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

Meta’s Muse AI assistant has a zero-day that can turn it into a Mac backdoor

22 September 2026 at 12:53

Mac security researcher Patrick Wardle says it’s trivial to turn Muse into “the ultimate backdoor.”

Increasingly, AI assistants are changing from tools that simply answer questions into agents that can plan tasks, use connected services, and take actions for us. These actions might include booking appointments, filling out forms, creating documents, making purchases, or interacting with email and calendars.

To do that, they need more permissions, account connections, and sensitive data. So, when Meta promised that “Muse is built from the ground up for privacy and security,” we did not expect an AI agent that can easily be manipulated into handing all that access to an attacker.

Meta says Muse can handle appointments, forms, customer-service interactions, purchases, document creation, and connections to services such as WhatsApp, email, calendars, and social platforms. It may also receive macOS permissions to access protected resources, including files, the microphone, camera, location, and calendars.

According to Ars Technica, Wardle found that a locally running application or terminal command could alter an undocumented Muse configuration setting that controls the server used for dictation transcription. By redirecting dictation traffic to an attacker-controlled server, an attacker could capture voice prompts and obtain the authentication token for the victim’s Muse account.

This is not a remote-code-execution vulnerability that can compromise an otherwise clean Mac. The attacker first needs a way to run code locally, such as through malware, a malicious application, or social engineering.

But as we have seen with infostealer malware finding its way onto Macs, that initial access is far from impossible.


Someone’s watching your accounts. Make sure it’s us.


Traditional infostealer malware must independently locate browser data, credentials, documents, chat histories, and other valuable material. A compromised AI agent could lower that barrier by bundling access to multiple services and operating-system permissions behind one already authenticated interface.

Ultimately, this is not just about one unsafe configuration setting. It shows why AI agents need a higher security standard than ordinary apps.

How to stay safe

Wardle’s advice about Muse is simple: “Please don’t install.”

The same caution should apply to other AI agents.

The Open Worldwide Application Security Project (OWASP), a nonprofit foundation that provides free application-security guidance, lists prompt injection, tool abuse, privilege escalation, data exfiltration, excessive autonomy, memory poisoning, and sensitive-data exposure among the major security risks posed by AI agents.

A useful rule is that an AI agent should not have more access than it needs, and it should not be able to turn untrusted instructions into sensitive actions without meaningful checks. In practice, this means:

  • Avoid giving a new agent broad access to email, chat apps, calendars, cloud storage, payment methods, and device permissions all at once.
  • Regularly review and remove connections the agent does not genuinely need.
  • Be aware of prompt injection. Do not assume that an AI agent will recognize malicious instructions embedded in a webpage, document, email, or other external content.
  • Watch for unusual agent behavior, such as unexpected requests for new permissions, account reauthentication, external file sharing, or actions you did not initiate.

You should also protect your device against malware:

  • Keep your software updated so attackers can’t use known vulnerabilities against you.
  • Use an up-to-date, real-time anti-malware solution on all your devices.
  • To protect against ClickFix attacks, don’t follow instructions you find on websites and in unsolicited messages that tell you to run commands.

From reporting threats to removing them.

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

Update Chrome: 108 security fixes for desktop, new release for Android

24 September 2026 at 13:06

Over the last few days, Google issued several different Chrome updates.

On September 22, Google released a Stable Channel Update for Desktop. This is the most important one for desktop users. It brings Chrome to version 154.0.8037.57 for Linux and versions 154.0.8037.57/.58 for Windows and Mac. The update includes 108 security fixes including 11 rated Critical.

It will roll out over the coming days and weeks.

One day later, Google released Chrome 155 for Android, version 155.0.8059.16, to a small percentage of users. It may not be available on Google Play for everyone yet, but keep an eye out for it. Google says it includes stability and performance improvements.

On top of these, Chrome 155 is also available in the Beta channel. The Android release is an Early Stable rollout, meaning Google sends it to a small share of users first, to spot unexpected compatibility or reliability issues before expanding it to everyone. Beta is a separate prerelease version for people who want to try upcoming features roughly four to six weeks before Stable. It is relatively polished but can still contain bugs, so it is best suited to testing rather than everyday use.

How to update Chrome

The easiest option is to allow Chrome to update automatically. But you can end up lagging behind on updates if you never close your browser or if something goes wrong, such as an extension preventing the update.

If you don’t want to wait for the rollout to reach you, manually updating is easy. open About Google Chrome from Chrome’s settings or Help menu. Chrome will check for updates. If one is available, click Relaunch to apply it.

Chrome 154.0.8037.58 is up to date

You can find an explanation of the version numbering system and step-by-step instructions in our guide: How to update Chrome on every operating system.

Technical details

Some of the desktop security fixes deserve a closer look.

Let’s start with CVE-2026-95350, a buffer overflow flaw in ANGLE, Chrome’s graphics-translation layer.

A buffer overflow is a bug in code that allows an attack to happen when a program puts more data into an area of memory than it can hold. Essentially, the attacker writes garbage data that fills up the memory, then writes code that overwrites existing code in adjoining memory, which later gets executed by the vulnerable process.

A crafted webpage could potentially trigger the flaw, which could lead to memory safety bugs, including browser crashes or possible code execution.

Another Critical buffer overflow bug in ANGLE is tracked as CVE-2026-95281. A malicious webpage could potentially reach vulnerable graphics-processing code, so the bug may enable serious impacts such as browser compromise, but Google has not provided exploitation details.

And then there is CVE-2026-95357, an out-of-bounds write in Chrome’s GPU component. This means a program could write data outside its intended area of memory.

The GPU component is the part of Chrome that handles how graphics work with your computer’s graphics processor.


Stop threats before they can do any harm.

Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →

Some cheap smart glasses are a security disaster

22 September 2026 at 17:04

Apart from the privacy concerns around smart glasses, researchers have found that some cheap brands come with barely any security at all.

ABC Australia reports that researchers from NSB Cyber and Abstract Shield tested two inexpensive pairs, costing A$60 and A$110 (around US$42 and US$78), and found more than a dozen flaws across the smart glasses themselves, their app, and an associated website.

The main problem they uncovered was insecure Bluetooth pairing: If the glasses were powered on and not connected to their owner’s phone, an attacker could connect first, with no password or meaningful pairing confirmation.

After connecting, an attacker could reportedly control the glasses to capture photos or recordings, copy existing media, and intercept data moving between the glasses and the phone. An attacker could also make another device appear to be the victim’s glasses, allowing it to connect to the owner’s mobile app.

The testing also found that a Bluetooth-visible device identifier could allegedly be used with a weakness in the app’s website to retrieve a user’s email address and date of birth.

The research uncovered another privacy issue. ABC reports that voice or text submitted to the built-in AI, along with images sent to it, was first transmitted to a server in Shenzhen and could be forwarded elsewhere, depending on the function. The tests did not establish how the data was subsequently used.

The server locations, combined with some of the AI’s answers to specific questions, led researchers to conclude that the chatbot companion relied at least in part on Chinese sovereign AI models. Professor Kimberlee Weatherall, a technology regulation expert involved in the testing, said the failure to identify China in the privacy policy appeared to violate the Australian Privacy Principles,

The timing of the testing is also relevant because Australia’s smart-device security standards apply to most consumer smart devices manufactured on or after March 4, 2026. They require, among other measures, no universal default passwords, a way to report vulnerabilities, and information about the minimum security-update period. Devices made before that date are outside the requirements.

Experts quoted by ABC said the devices violated Australia’s privacy laws and were also likely to breach several sections of the Cyber Security Act. However, whether the new smart-device standards apply would depend partly on when the glasses were manufactured, and the rules have not yet been tested in a known enforcement action.

Professor Weatherall said:

“The rules say that the password must be unique. It doesn’t even seem like they were applying a password, which might mean that their standards are so low they don’t even technically breach that rule, which I find amazing.”

What to do

We’re not fans of smart glasses, expensive or cheap. But if you own a pair:

  • Avoid pairing or using inexpensive camera glasses that lack a clear physical pairing step, account authentication, a published security-contact process, and a stated update-support period.
  • Stop using their AI or cloud features for sensitive material, remove unnecessary permissions from the companion app, check for firmware and app updates, and consider returning the product if the vendor cannot document a fix.
  • Ask permission before recording people, and check your local laws to understand what is and isn’t allowed.

From reporting threats to removing them.

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

Meta’s Muse AI assistant has a zero-day that can turn it into a Mac backdoor

22 September 2026 at 12:53

Mac security researcher Patrick Wardle says it’s trivial to turn Muse into “the ultimate backdoor.”

Increasingly, AI assistants are changing from tools that simply answer questions into agents that can plan tasks, use connected services, and take actions for us. These actions might include booking appointments, filling out forms, creating documents, making purchases, or interacting with email and calendars.

To do that, they need more permissions, account connections, and sensitive data. So, when Meta promised that “Muse is built from the ground up for privacy and security,” we did not expect an AI agent that can easily be manipulated into handing all that access to an attacker.

Meta says Muse can handle appointments, forms, customer-service interactions, purchases, document creation, and connections to services such as WhatsApp, email, calendars, and social platforms. It may also receive macOS permissions to access protected resources, including files, the microphone, camera, location, and calendars.

According to Ars Technica, Wardle found that a locally running application or terminal command could alter an undocumented Muse configuration setting that controls the server used for dictation transcription. By redirecting dictation traffic to an attacker-controlled server, an attacker could capture voice prompts and obtain the authentication token for the victim’s Muse account.

This is not a remote-code-execution vulnerability that can compromise an otherwise clean Mac. The attacker first needs a way to run code locally, such as through malware, a malicious application, or social engineering.

But as we have seen with infostealer malware finding its way onto Macs, that initial access is far from impossible.


Someone’s watching your accounts. Make sure it’s us.


Traditional infostealer malware must independently locate browser data, credentials, documents, chat histories, and other valuable material. A compromised AI agent could lower that barrier by bundling access to multiple services and operating-system permissions behind one already authenticated interface.

Ultimately, this is not just about one unsafe configuration setting. It shows why AI agents need a higher security standard than ordinary apps.

How to stay safe

Wardle’s advice about Muse is simple: “Please don’t install.”

The same caution should apply to other AI agents.

The Open Worldwide Application Security Project (OWASP), a nonprofit foundation that provides free application-security guidance, lists prompt injection, tool abuse, privilege escalation, data exfiltration, excessive autonomy, memory poisoning, and sensitive-data exposure among the major security risks posed by AI agents.

A useful rule is that an AI agent should not have more access than it needs, and it should not be able to turn untrusted instructions into sensitive actions without meaningful checks. In practice, this means:

  • Avoid giving a new agent broad access to email, chat apps, calendars, cloud storage, payment methods, and device permissions all at once.
  • Regularly review and remove connections the agent does not genuinely need.
  • Be aware of prompt injection. Do not assume that an AI agent will recognize malicious instructions embedded in a webpage, document, email, or other external content.
  • Watch for unusual agent behavior, such as unexpected requests for new permissions, account reauthentication, external file sharing, or actions you did not initiate.

You should also protect your device against malware:

  • Keep your software updated so attackers can’t use known vulnerabilities against you.
  • Use an up-to-date, real-time anti-malware solution on all your devices.
  • To protect against ClickFix attacks, don’t follow instructions you find on websites and in unsolicited messages that tell you to run commands.

From reporting threats to removing them.

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

Google Pixel owners urged to patch actively exploited modem flaw

16 September 2026 at 12:39

Google has released its September 2026 Pixel Update Bulletin, fixing 110 vulnerabilities, including one that it says “may be under limited, targeted exploitation.”

The bug is not described as a simple remote takeover, but as a vulnerability that could give an attacker who already has a foothold on a phone more power than they should have.

Although Pixel devices also run Android, they receive separate security updates and bug fixes from the standard monthly patches distributed to Android manufacturers because of the unique hardware platform Google controls directly and its exclusive features and capabilities.

To apply this month’s security updates, Pixel users should go to Settings > Security & privacy > System & updates > Security update, tap Install, and restart their device to complete the update process.

A supported device with the 2026-09-05 patch level is up to date. After updating, check that the Android security update level shows September 5, 2026, or later.

Technical details

Google says it there are indications that the vulnerability, tracked as CVE-2026-58704, may be under limited, targeted exploitation. Found in the cellular modem, it is a possible permission bypass caused by a logic error in the code. This could lead to remote escalation of privilege (EoP) with no additional execution privileges or user interaction needed.

The vulnerability affects the modem component of Pixel devices and is rated high severity. The modem is the part of a smartphone that handles communication with mobile networks. It allows a phone to connect for calls, texts, and mobile data. Because it is such an important component, a flaw affecting it deserves attention, even if the conditions needed to exploit it limit the number of potential victims.

The vulnerability does not mean every unpatched Pixel can be hacked from anywhere on the internet, nor has Google said that simply being within wireless range of a phone is enough. The available information indicates that an attacker needs access to an adjacent network and basic privileges on the targeted device, but it does not explain how those privileges are obtained.

Attackers commonly need more than one step to compromise a well-protected device. One weakness may give them a limited foothold, while another lets them escape restrictions and gain access to more sensitive functions or data.

This is why bugs like this can be especially useful in targeted operations. An attacker may combine the modem vulnerability with another exploit, a malicious app, stolen credentials, or physical access to the device. Each part of the chain brings the attacker one step closer to compromising the device: getting in, gaining more privileges, and accessing the information or functions they’re after.

While Android users should always install the latest update offered by their device manufacturer, this particular zero-day appears in the Pixel-specific bulletin. Google’s Pixel phones use hardware and software components that other Android manufacturers do not necessarily share, including the affected modem component. If you have another Android brand, you won’t receive this specific Pixel fix, but you should still check for your manufacturer’s latest monthly security update.


Scammers know more about you than you think. 

Malwarebytes Mobile Security protects you from phishing, scam texts, malicious sites, and more. With real-time AI-powered Scam Guard built right in. 

Download for iOS → Download for Android → 

Google Pixel owners urged to patch actively exploited modem flaw

16 September 2026 at 12:39

Google has released its September 2026 Pixel Update Bulletin, fixing 110 vulnerabilities, including one that it says “may be under limited, targeted exploitation.”

The bug is not described as a simple remote takeover, but as a vulnerability that could give an attacker who already has a foothold on a phone more power than they should have.

Although Pixel devices also run Android, they receive separate security updates and bug fixes from the standard monthly patches distributed to Android manufacturers because of the unique hardware platform Google controls directly and its exclusive features and capabilities.

To apply this month’s security updates, Pixel users should go to Settings > Security & privacy > System & updates > Security update, tap Install, and restart their device to complete the update process.

A supported device with the 2026-09-05 patch level is up to date. After updating, check that the Android security update level shows September 5, 2026, or later.

Technical details

Google says it there are indications that the vulnerability, tracked as CVE-2026-58704, may be under limited, targeted exploitation. Found in the cellular modem, it is a possible permission bypass caused by a logic error in the code. This could lead to remote escalation of privilege (EoP) with no additional execution privileges or user interaction needed.

The vulnerability affects the modem component of Pixel devices and is rated high severity. The modem is the part of a smartphone that handles communication with mobile networks. It allows a phone to connect for calls, texts, and mobile data. Because it is such an important component, a flaw affecting it deserves attention, even if the conditions needed to exploit it limit the number of potential victims.

The vulnerability does not mean every unpatched Pixel can be hacked from anywhere on the internet, nor has Google said that simply being within wireless range of a phone is enough. The available information indicates that an attacker needs access to an adjacent network and basic privileges on the targeted device, but it does not explain how those privileges are obtained.

Attackers commonly need more than one step to compromise a well-protected device. One weakness may give them a limited foothold, while another lets them escape restrictions and gain access to more sensitive functions or data.

This is why bugs like this can be especially useful in targeted operations. An attacker may combine the modem vulnerability with another exploit, a malicious app, stolen credentials, or physical access to the device. Each part of the chain brings the attacker one step closer to compromising the device: getting in, gaining more privileges, and accessing the information or functions they’re after.

While Android users should always install the latest update offered by their device manufacturer, this particular zero-day appears in the Pixel-specific bulletin. Google’s Pixel phones use hardware and software components that other Android manufacturers do not necessarily share, including the affected modem component. If you have another Android brand, you won’t receive this specific Pixel fix, but you should still check for your manufacturer’s latest monthly security update.


Scammers know more about you than you think. 

Malwarebytes Mobile Security protects you from phishing, scam texts, malicious sites, and more. With real-time AI-powered Scam Guard built right in. 

Download for iOS → Download for Android → 

BlueMoon exploit kit turns Chrome and Windows flaws into attacks

10 September 2026 at 17:49

BlueMoon, a shared Chrome and Windows exploit kit, shows why “patch later” is becoming a dangerous gamble.

Security updates are easy to put off. The browser still opens, Windows still works, and choosing to relaunch your browser or restart your computer later can feel harmless.

But a newly documented exploit kit called “BlueMoon” shows how quickly patching delays can become dangerous. Proofpoint Researchers found four espionage groups using the same exploit chain against Chrome browsers running on Windows within days of one another.

The campaign is a timely reminder that once a security flaw, or even its fix, becomes public, attackers may move faster than many users expect.

The attacks began with phishing emails. A victim who clicked a malicious link could be sent to a web page designed to exploit two vulnerabilities in Chrome’s V8 JavaScript engine, followed by a Windows vulnerability to break out of the browser’s protections and gain higher privileges on the computer.

The Chrome vulnerabilities used by BlueMoon were patched in the Stable channel on September 3 and September 8, 2026. The first was already actively exploited when Google released its update. Microsoft addressed the Windows vulnerability in its September Patch Tuesday updates, by which point it was also being exploited.

CISA has since added all three flaws to its Known Exploited Vulnerabilities (KEV) catalog, which lists vulnerabilities known to have been exploited in real-world attacks.

The notable part is not just that BlueMoon exploited the flaws, but how quickly the capability appears to have spread. Publicly visible upstream fixes can give attackers clues before downstream browser updates reach users, allowing a weaponized chain to be developed and adopted by multiple groups very quickly.

Does that mean that patches can no longer be tested before they are released to the public? No, but we may need to rethink how they are tested and deployed, because it appears some cybercriminals are effectively beta-testing the patches themselves.

The researchers also found clues, but no conclusive evidence, that the exploit kit was developed with AI assistance. The broader concern is credible: AI tools can help attackers interpret source-code changes, write and modify code, document test results, and learn from failed attempts.

In practical terms, the gap between “a flaw is fixed upstream” and “most people are protected” may be increasingly valuable to attackers. We should try to minimize that gap.

How to stay safe

Not every security update needs to be installed the moment it appears. In organizations especially, updates may need testing, staged deployment, and contingency plans. But vulnerabilities known to be actively exploited deserve greater priority. That is precisely why CISA’s KEV catalog is so important: It helps organizations identify the vulnerabilities they should address first.

For home users:

  • Install browser and operating-system updates promptly. Use the few minutes they take to grab a drink rather than repeatedly postponing them.
  • Don’t click links in unsolicited emails.
  • Use up-to-date, real-time anti-malware protection to help catch the malware that exploit kits attempt to deliver.

Stop threats before they can do any harm.

Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →

BlueMoon exploit kit turns Chrome and Windows flaws into attacks

10 September 2026 at 17:49

BlueMoon, a shared Chrome and Windows exploit kit, shows why “patch later” is becoming a dangerous gamble.

Security updates are easy to put off. The browser still opens, Windows still works, and choosing to relaunch your browser or restart your computer later can feel harmless.

But a newly documented exploit kit called “BlueMoon” shows how quickly patching delays can become dangerous. Proofpoint Researchers found four espionage groups using the same exploit chain against Chrome browsers running on Windows within days of one another.

The campaign is a timely reminder that once a security flaw, or even its fix, becomes public, attackers may move faster than many users expect.

The attacks began with phishing emails. A victim who clicked a malicious link could be sent to a web page designed to exploit two vulnerabilities in Chrome’s V8 JavaScript engine, followed by a Windows vulnerability to break out of the browser’s protections and gain higher privileges on the computer.

The Chrome vulnerabilities used by BlueMoon were patched in the Stable channel on September 3 and September 8, 2026. The first was already actively exploited when Google released its update. Microsoft addressed the Windows vulnerability in its September Patch Tuesday updates, by which point it was also being exploited.

CISA has since added all three flaws to its Known Exploited Vulnerabilities (KEV) catalog, which lists vulnerabilities known to have been exploited in real-world attacks.

The notable part is not just that BlueMoon exploited the flaws, but how quickly the capability appears to have spread. Publicly visible upstream fixes can give attackers clues before downstream browser updates reach users, allowing a weaponized chain to be developed and adopted by multiple groups very quickly.

Does that mean that patches can no longer be tested before they are released to the public? No, but we may need to rethink how they are tested and deployed, because it appears some cybercriminals are effectively beta-testing the patches themselves.

The researchers also found clues, but no conclusive evidence, that the exploit kit was developed with AI assistance. The broader concern is credible: AI tools can help attackers interpret source-code changes, write and modify code, document test results, and learn from failed attempts.

In practical terms, the gap between “a flaw is fixed upstream” and “most people are protected” may be increasingly valuable to attackers. We should try to minimize that gap.

How to stay safe

Not every security update needs to be installed the moment it appears. In organizations especially, updates may need testing, staged deployment, and contingency plans. But vulnerabilities known to be actively exploited deserve greater priority. That is precisely why CISA’s KEV catalog is so important: It helps organizations identify the vulnerabilities they should address first.

For home users:

  • Install browser and operating-system updates promptly. Use the few minutes they take to grab a drink rather than repeatedly postponing them.
  • Don’t click links in unsolicited emails.
  • Use up-to-date, real-time anti-malware protection to help catch the malware that exploit kits attempt to deliver.

Stop threats before they can do any harm.

Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →

Update your iPhone, iPad and Mac to fix Apple security holes

28 July 2026 at 13:35

Apple has shipped a hefty round of July security patches, headlined by iOS/iPadOS 26.6, macOS Tahoe 26.6, and Safari 26.6, with dozens of vulnerabilities squashed across kernel, WebKit, media frameworks, and core apps. These updates are primarily about improving security rather than adding new features, and users should install them as soon as possible.

Updates for your particular device

The table below shows which updates are available and points you to the relevant security content for that subject.

iOS 26.6 and iPadOS 26.6iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
macOS Tahoe 26.6macOS Tahoe
macOS Sequoia 15.7.8macOS Sequoia
macOS Sonoma 14.8.8macOS Sonoma
tvOS 26.6Apple TV HD and Apple TV 4K (all models)
watchOS 26.6Apple Watch Series 6 and later
visionOS 26.6Apple Vision Pro (all models)
Safari 26.6macOS Sonoma and macOS Sequoia

How to update your Apple devices

How to update your iPhone or iPad

For iOS and iPadOS users, here’s how to check if you’re using the latest software version:

Go to Settings > General > Software Update. You will see if there are updates available and be guided through installing them.

Turn on Automatic Updates if you haven’t already—you’ll find it on the same screen.

iPadOS update options

How to update macOS on any version

To update macOS on any supported Mac, use the Software Update feature, which Apple designed to work consistently across all recent versions. Here are the steps:

  • Click the Apple menu in the upper-left corner of your screen.
  • Choose System Settings (or System Preferences on older versions).
  • Select General in the sidebar, then click Software Update on the right. On older macOS, just look for Software Update directly.
  • Your Mac will check for updates automatically. If updates are available, click Update Now (or Upgrade Now for major new versions) and follow the on-screen instructions. Before you upgrade to macOS Tahoe 26, please read these instructions.
  • Enter your administrator password if prompted, then let your Mac finish the update (it might need to restart during this process).
  • Make sure your Mac stays plugged in and connected to the internet until the update is done.

How to update your Safari browser

Safari updates are included with macOS updates, so installing the latest version of macOS will also update Safari. To check manually:

  • Open the Apple menu > System Settings > General > Software Update.
  • If you see a Safari update listed separately, click Update Now to install it.
  • Restart your device when prompted.

If you’re on an older macOS version that’s still supported (like Sonoma or Sequoia), Apple may offer Safari updates independently through Software Update.

Technical details

Among the more interesting vulnerabilities patched in this update are CVE-2026-43818 in ImageIO,  CVE-2026-43776 in AppleDouble, and CVE-2026-64763 to 64766 in SceneKit.

Although found in different applications, these vulnerabilities have one thing in common. Their descriptions say:

“Processing a maliciously crafted file may lead to unexpected app termination or arbitrary code execution.”

The identical “processing a maliciously crafted file may lead to unexpected app termination or arbitrary code execution” language is not a coincidence. It’s Apple’s standard impact boilerplate for file‑parsing bugs across multiple frameworks, including ImageIO, AppleDouble, and SceneKit. The similarities reflect shared exploitation patterns (untrusted file input hitting native parsers), while the differences lie in what each framework does and which file types/contexts are affected.

ImageIO is the system framework responsible for reading and displaying image formats such as JPEG, PNG, TIFF, RAW, GIF, and other formats. It’s used throughout iOS and macOS by apps including Photos, Safari, Messages, Mail, and Preview.

SceneKit is a 3D graphics and scene graph framework used for rendering models, animations, and complex 3D scenes in apps and games on Apple platforms. It parses scene description files and 3D assets and turns them into renderable content.

AppleDouble is something macOS uses behind the scenes to keep extra file information like icons and other Finder details in cases where your files live on certain types of disks or servers. When Apple mentions “AppleDouble” in security notes, it’s talking about the code that reads and writes that hidden metadata, particularly when files are stored on network drives or shared with non‑Apple systems.

Apple’s advisories reuse a standard warning for any memory‑corruption bug in a file parser: the best‑case outcome is just a crash, the worst case is someone running their malicious code on your device. ImageIO, AppleDouble, and SceneKit all sit in that same danger zone. Although the file types are different, they all present the same underlying risk.

Until you’ve installed this update, it’s an even worse idea than usual to open unsolicited messages and emails with images in them.


Scammers know more about you than you think. 

Malwarebytes Mobile Security protects you from phishing, scam texts, malicious sites, and more. With real-time AI-powered Scam Guard built right in. 

Download for iOS → Download for Android → 

Update your iPhone, iPad and Mac to fix Apple security holes

28 July 2026 at 13:35

Apple has shipped a hefty round of July security patches, headlined by iOS/iPadOS 26.6, macOS Tahoe 26.6, and Safari 26.6, with dozens of vulnerabilities squashed across kernel, WebKit, media frameworks, and core apps. These updates are primarily about improving security rather than adding new features, and users should install them as soon as possible.

Updates for your particular device

The table below shows which updates are available and points you to the relevant security content for that subject.

iOS 26.6 and iPadOS 26.6iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later
macOS Tahoe 26.6macOS Tahoe
macOS Sequoia 15.7.8macOS Sequoia
macOS Sonoma 14.8.8macOS Sonoma
tvOS 26.6Apple TV HD and Apple TV 4K (all models)
watchOS 26.6Apple Watch Series 6 and later
visionOS 26.6Apple Vision Pro (all models)
Safari 26.6macOS Sonoma and macOS Sequoia

How to update your Apple devices

How to update your iPhone or iPad

For iOS and iPadOS users, here’s how to check if you’re using the latest software version:

Go to Settings > General > Software Update. You will see if there are updates available and be guided through installing them.

Turn on Automatic Updates if you haven’t already—you’ll find it on the same screen.

iPadOS update options

How to update macOS on any version

To update macOS on any supported Mac, use the Software Update feature, which Apple designed to work consistently across all recent versions. Here are the steps:

  • Click the Apple menu in the upper-left corner of your screen.
  • Choose System Settings (or System Preferences on older versions).
  • Select General in the sidebar, then click Software Update on the right. On older macOS, just look for Software Update directly.
  • Your Mac will check for updates automatically. If updates are available, click Update Now (or Upgrade Now for major new versions) and follow the on-screen instructions. Before you upgrade to macOS Tahoe 26, please read these instructions.
  • Enter your administrator password if prompted, then let your Mac finish the update (it might need to restart during this process).
  • Make sure your Mac stays plugged in and connected to the internet until the update is done.

How to update your Safari browser

Safari updates are included with macOS updates, so installing the latest version of macOS will also update Safari. To check manually:

  • Open the Apple menu > System Settings > General > Software Update.
  • If you see a Safari update listed separately, click Update Now to install it.
  • Restart your device when prompted.

If you’re on an older macOS version that’s still supported (like Sonoma or Sequoia), Apple may offer Safari updates independently through Software Update.

Technical details

Among the more interesting vulnerabilities patched in this update are CVE-2026-43818 in ImageIO,  CVE-2026-43776 in AppleDouble, and CVE-2026-64763 to 64766 in SceneKit.

Although found in different applications, these vulnerabilities have one thing in common. Their descriptions say:

“Processing a maliciously crafted file may lead to unexpected app termination or arbitrary code execution.”

The identical “processing a maliciously crafted file may lead to unexpected app termination or arbitrary code execution” language is not a coincidence. It’s Apple’s standard impact boilerplate for file‑parsing bugs across multiple frameworks, including ImageIO, AppleDouble, and SceneKit. The similarities reflect shared exploitation patterns (untrusted file input hitting native parsers), while the differences lie in what each framework does and which file types/contexts are affected.

ImageIO is the system framework responsible for reading and displaying image formats such as JPEG, PNG, TIFF, RAW, GIF, and other formats. It’s used throughout iOS and macOS by apps including Photos, Safari, Messages, Mail, and Preview.

SceneKit is a 3D graphics and scene graph framework used for rendering models, animations, and complex 3D scenes in apps and games on Apple platforms. It parses scene description files and 3D assets and turns them into renderable content.

AppleDouble is something macOS uses behind the scenes to keep extra file information like icons and other Finder details in cases where your files live on certain types of disks or servers. When Apple mentions “AppleDouble” in security notes, it’s talking about the code that reads and writes that hidden metadata, particularly when files are stored on network drives or shared with non‑Apple systems.

Apple’s advisories reuse a standard warning for any memory‑corruption bug in a file parser: the best‑case outcome is just a crash, the worst case is someone running their malicious code on your device. ImageIO, AppleDouble, and SceneKit all sit in that same danger zone. Although the file types are different, they all present the same underlying risk.

Until you’ve installed this update, it’s an even worse idea than usual to open unsolicited messages and emails with images in them.


Scammers know more about you than you think. 

Malwarebytes Mobile Security protects you from phishing, scam texts, malicious sites, and more. With real-time AI-powered Scam Guard built right in. 

Download for iOS → Download for Android → 

Claude Fable 5 and Mythos 5 “abruptly disabled” after US gov. ban

15 June 2026 at 16:32

Anthropic has been ordered by the US government to cut off its newest Claude Fable 5 and Mythos 5 models for fear of abuse by adversaries.

Reuters reports that Anthropic said it will “abruptly ​disable” its most advanced AI models for all users after the US government ordered it to suspend access to the models for foreign nationals, citing national security ‌concerns.

Officials reportedly believe a jailbreak could turn Fable 5 and Mythos 5 into vulnerability-discovery tools for adversaries, so Anthropic says it is disabling them worldwide rather than try to nationality‑filter access, since it is virtually impossible to verify every user’s nationality.

In a statement on its website, Anthropic says:

“The letter did not provide specific details of its national security concern. Our understanding is that the government believes it has become aware of a method of bypassing, or “jailbreaking” Fable 5. We reviewed a demonstration of this specific technique being used to identify a small number of previously known, minor vulnerabilities. These vulnerabilities all appear relatively simple, and we have found that other publicly-available models are able to discover them as well without requiring a bypass.”

Mythos 5 is the non-public full version, which is currently used only by government agencies and selected corporate partners to harden their systems. Fable 5 is a Mythos-class model that should supposedly be safe for general use.

It makes sense to me that if Fable 5 is easy to jailbreak, that it should fall under the same restrictions as Mythos 5. However, Anthropic maintains that it has built-in safeguards that mean queries on some topics will instead receive a response from the next-most-capable model, Claude Opus 4.8. 

The relationship between the US government and Anthropic had shown signs of easing in parts of the US government after tensions over military use, surveillance, and autonomous weapons. In March, defense Secretary Pete Hegseth designated the San Francisco-based company a “supply-chain risk to national security.”

To understand the nature of the argument, it is necessary to understand that Mythos 5 is described in multiple reports as particularly effective at identifying software vulnerabilities, including long‑standing bugs in complex, legacy systems such as those in banking and other critical infrastructure. Many view this as dual‑use: great for defense hardening, but catastrophic in the wrong hands.

In recent updates from major software vendors like Microsoft and Google, we’ve seen a growth in numbers of patched vulnerabilities after the vendors began using AI-guided search for new vulnerabilities in their own software. We also know that Mozilla found over 270 Firefox vulnerabilities with the aid of Anthropic’s new Claude Mythos model. 

What this means

In the wrong hands these vulnerabilities could definitely do a lot of harm. So, it looks like it will take some time before regular consumers and developers will gain access to Fable 5 and Mythos 5 entirely. However, existing Anthropic models (older Claude variants) remain available.

For home users who were simply chatting with Claude or using it to help with basic scripting, the change will mostly show up as “this specific version is unavailable” rather than a broader AI blackout.

Removing a high‑end vulnerability‑finding model from broad circulation increases the effort required for less‑resourced cybercriminals to automate discovery of complex bugs in consumer‑facing software and services only by so much. There are other models available on the black market that might be just as effective. And for most cybercriminals, turning a vulnerability into a method they can utilize in an exploit is much more relevant.


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

Microsoft’s biggest-ever Patch Tuesday fixes 206 bugs, including 3 zero-days

10 June 2026 at 14:43

This month’s Patch Tuesday fixes 206 security flaws in Microsoft software, making it the biggest Patch Tuesday release ever.

The update includes 32 critical vulnerabilities, as well as three publicly disclosed zero-days. Microsoft classifies these as zero-days because information about the vulnerabilities became public before patches were available. None are known to have been actively exploited by attackers.

The huge number of fixed vulnerabilities makes this the largest Patch Tuesday since Microsoft launched the program in October 2003. The company introduced the monthly update schedule after the Blaster worm caused disruption in the early days of Windows.

How to apply patches and check if you’re protected

These updates fix security problems and keep your Windows PC protected. Here’s how to make sure you’re up to date:

1. Open Settings

  • Click the Start button (the Windows logo at the bottom left of your screen).
  • Click on Settings (it looks like a little gear).

2. Go to Windows Update

  • In the Settings window, select Windows Update (usually at the bottom of the menu on the left).

3. Check for updates

  • Click the button that says Check for updates.
  • Windows will search for the latest Patch Tuesday updates.
  • If you have selected to get the latest updates as soon as they’re available, you may see this under More options.
    In which case you may see a Restart required message. Restart your system and the update will complete.
    restart required
  • If not, continue with the steps below.

4. Download and install

  • If updates are found, they’ll start downloading automatically. Once complete, you’ll see a button that says Install or Restart now.
  • Click Install if needed and follow any prompts. Your computer will usually need a restart to finish the update. If it does, click Restart now.

5. Double-check you’re up to date

  • After restarting, go back to Windows Update and check again. If it says You’re up to date, you’re all set!
Windows up to date

Technical details

One publicly disclosed vulnerability is important to mention. This flaw in Windows BitLocker is tracked as CVE-2026-50507 (CVSS score: 6.8 out of 10) and its description states:

“a protection mechanism failure in Windows BitLocker allows an unauthorized attacker to bypass a security feature with a physical attack.”

BitLocker is a built-in Windows security feature that encrypts your entire hard drive, securing your data from unauthorized access if your device is lost or stolen. However, this vulnerability could allow an attacker with physical access to bypass BitLocker Device Encryption and gain access to encrypted data.

Another is CVE-2026-49160 (CVSS score: 7.5 out of 10) in HTTP.sys. This vulnerability can be exploited to launch a remote denial-of-service attack against major web servers using a technique called HTTP/2 Bomb.

The third to discuss is CVE-2026-45586 (CVSS score: 7.8 out of 10) in the Windows Collaborative Translation Framework (CTFMON). An attacker who successfully exploited this vulnerability could gain SYSTEM privileges. These elevation of privilege (EoP) vulnerabilities are especially valuable to attackers because they can be combined with other flaws to gain full control of a compromised system.


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

Firefox 151 packs big privacy upgrades into a small update

20 May 2026 at 13:46

Mozilla has published release notes for Firefox browser version 151.0, and this update includes several genuinely meaningful privacy and security improvements.

Three changes stand out in particular:

  • Stronger anti‑fingerprinting
  • Broader protection for local network access
  • More control over private sessions and permissions

Note that Mozilla says several Firefox 151 features are “part of a progressive roll out,” meaning they will appear for some users first and be expanded over time. So, you may not see all of them immediately.

Privacy

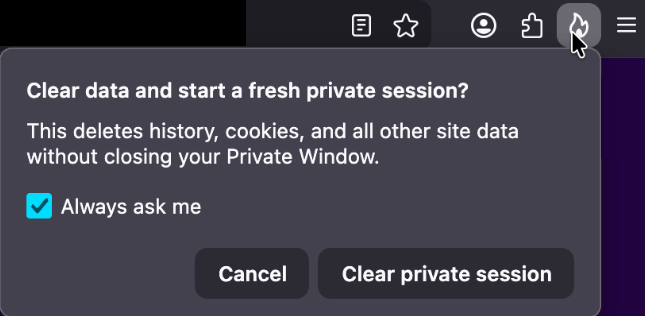
One of the more visible additions is a new “end private session” control in Private Browsing Mode. Instead of closing every private window to clear your traces, you now get a dedicated fire‑icon button next to the address bar that wipes the current private session’s data and immediately starts a fresh one.

End private session button

Under the hood, this clears the usual private browsing artifacts for that session, including history, cookies, cached files, and other site data that would normally disappear only when the last private window closes.

For people who routinely mix normal and private windows, this is safer and less error‑prone than hunting down every private tab before you walk away from the machine.

Firefox 151 also tightens its defenses against browser fingerprinting in the default “Standard” Enhanced Tracking Protection (ETP) mode. Mozilla says Firefox now limits the amount of device and browser information exposed to websites in a way that reduces the number of uniquely identifiable users by about 14% overall, and by roughly 49% on macOS.

This makes it harder for trackers to pick you out of the crowd, especially on platforms with fewer users to begin with (like certain macOS configurations). This reduces the privacy risk surface by default, which makes it harder for phishing and landing pages that redirect visitors to “categorize” you.

Another important change is Firefox’s “local network access restrictions,” which are now rolling out to all users, not just those who turned Enhanced Tracking Protection to Strict.

This means that when a website wants to communicate with devices on your local network, or with apps and services running on your machine, Firefox now asks for permission first. Chrome and Edge have been rolling out similar permission prompts.

Security

Firefox 151 also quietly fixes several security vulnerabilities.

The most notable example is CVE‑2026‑8953, a sandbox escape due to a use‑after‑free in the Disability Access APIs component. While there are currently no reports of in‑the‑wild exploitation for this specific bug at the time of writing, this is the kind of bug cybercriminals love.

A use-after-free (UAF) is a software memory vulnerability where a program attempts to access a memory location after it has been freed. If the program fails to clear the pointer to that freed memory, attackers can manipulate the error to crash the system or execute arbitrary code. A memory corruption leading to a sandbox escape is exactly the kind of link attackers want to complete a browser exploit chain.

How to update

If you’re running Firefox in a home or small‑office environment, we recommend updating to Firefox 151 as soon as possible to get the fingerprinting protections, local network access prompts, and security patches.

To update Firefox:

  • Open Firefox
  • Click the menu (three stacked lines) in the upper-right corner
  • Go to Help > About Firefox
  • Firefox will automatically check for updates and begin downloading them
  • Restart the browser when prompted to complete the update

Once your Firefox browser has been updated, it will show a green checkmark along with the message: “Firefox is up to date.”

Firefox is up to date

Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

May 2026 Patch Tuesday: no zero-days but plenty to fix

13 May 2026 at 13:00

This month’s Patch Tuesday remedies 137 security vulnerabilities, including 31 marked critical by Microsoft, with no zero-days actively exploited in the wild.

Microsoft defines a zero-day as “a flaw in software for which no official patch or security update is available yet.” This month, Microsoft has not observed any included vulnerability being exploited in production environments.

Still, this release is far from low-risk. A large chunk of the critical bugs allow remote code execution (RCE) across Windows services, Office, Azure, SharePoint, and graphics components. That means attackers who trick a user into opening a malicious document or lure them into connecting to a malicious service could gain full control of a system.

Two vulnerabilities to prioritize

From that list, we selected two that look like they could cause some trouble.

First is CVE-2026-40361, which has a CVSS score of 8.4 out of 10. It’s described as a critical use-after-free vulnerability in Microsoft Word that could allow an attacker to execute code locally on the affected system.

Use-after-free is a class of vulnerability caused by incorrect use of dynamic memory during a program’s operation. If, after freeing a memory location, a program does not clear the pointer to that memory, an attacker may be able to use the error to manipulate the program.

So, if an attacker convinces a user to open a malicious Word document, or even previews the file, they could execute arbitrary code with the privileges of the current user. That’s often enough to install malware, steal credentials, or move laterally through a network.

Second is CVE-2026-35421 (CVSS score 7.8 out of 10). This is a critical heap-based buffer overflow in Windows Graphics Device Interface (GDI). A buffer overflow occurs when an area of memory within a software application reaches its address boundary and writes into an adjacent memory region. Microsoft notes:

“For this vulnerability to be exploited, a user would need to open or otherwise process a specially crafted Enhanced Metafile (EMF) file using Microsoft Paint. This action is necessary to trigger the affected graphics functionality in the Windows component.”


Real-time protection. Zero effort. 


How to apply fixes and check if you’re protected

These updates fix security problems and keep your Windows PC protected. Here’s how to make sure you’re up to date:

1. Open Settings

  • Click the Start button (the Windows logo at the bottom left of your screen).
  • Click on Settings (it looks like a little gear).

2. Go to Windows Update

  • In the Settings window, select Windows Update (usually at the bottom of the menu on the left).

3. Check for updates

  • Click the button that says Check for updates.
  • Windows will search for the latest Patch Tuesday updates.
  • If you have selected to get the latest updates as soon as they’re available, you may see this under More options.
  • In which case you may see a Restart required message. Restart your system and the update will complete.
    May restart required
  • If not, continue with the steps below.

4. Download and Install If updates are found, they’ll start downloading automatically. Once complete, you’ll see a button that says Install or Restart now.

  • Click Install if needed and follow any prompts. Your computer will usually need a restart to finish the update. If it does, click Restart now.

5. Double-check you’re up to date

  • After restarting, go back to Windows Update and check again. If it says You’re up to date, you’re all set!
Windows is up to date

We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

Update WhatsApp now: Two new flaws could expose you to malicious files

5 May 2026 at 13:39

Meta has published a new security advisory for messaging app WhatsApp, announcing patches for two vulnerabilities.

WhatsApp has fixed two security flaws that could be abused to interfere with how media and attachments are handled on your device. There is no evidence that either bug has been exploited in the wild.

These bugs don’t automatically infect devices, but they lower the barrier for social engineering and could be chained with other vulnerabilities for more serious attacks.

Malicious messages

The first issue, tracked as CVE‑2026‑23866, affects how WhatsApp processes AI‑generated “rich response messages” that embed Instagram Reels. On affected iOS and Android versions, incomplete validation means a specially crafted message could cause the app to load media from an attacker‑controlled URL. In some cases, this could trigger operating system‑level custom URL scheme handlers.

In other words: a booby‑trapped message could prompt your device to open content from an untrusted source.

How to update WhatsApp for Android

You can easily update WhatsApp from the Google Play Store.

  1. Open the Google Play Store
  2. Search for WhatsApp Messenger
  3. Tap Update

Note: Updates may not be available immediately in all regions.

How to update WhatsApp on iOS

To update WhatsApp on iOS:

  • Open the App Store
  • Tap your profile icon
  • Scroll to find WhatsApp and tap Update

If it’s not listed, search for WhatsApp to check if an “Update” button is available.

Misleading filenames

The second bug, CVE‑2026‑23863, affects WhatsApp for Windows before version 2.3000.1032164386.258709.

In this case, WhatsApp did not correctly handle filenames containing embedded NUL bytes. This could allow a file to appear as a harmless type in the interface while actually being treated as an executable when opened. That’s a classic recipe for social engineering: “click the PDF,” but get an .exe file.

How to update WhatsApp for Windows

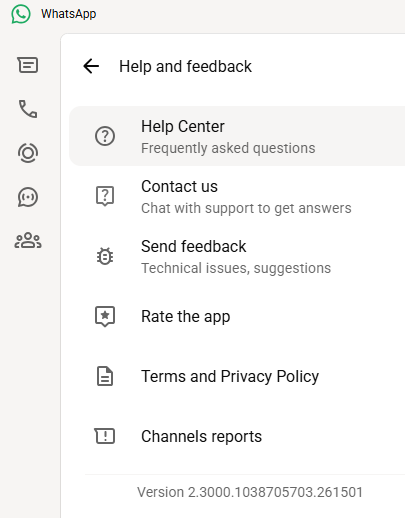
You can find your WhatsApp for Windows version number by clicking on your profile picture and selecting Help and feedback.

Version 2.3000.1038705703.261501

If your version number is earlier than 2.3000.1032164386.258709, update via the Microsoft Store:

  1. Click the Start menu and search for Microsoft Store to open it
  2. Click Library located at the bottom-left corner
  3. Find WhatsApp Desktop
  4. Click Get Updates or Update

Once installed, restart the app to apply the changes.

Automatic updates on Windows

My WhatsApp was already up to date because I have automatic updates turned on. Here’s how to turn it on:

  1. Click the Start menu and search for Microsoft Store to open it
  2. Select Profile (your account picture) > Settings
  3. Make sure App updates is toggled to On
Auto updates on Windows

Scammers don’t need to hack you. They just need you to click once. 

Malwarebytes Identity Theft Protection catches suspicious activity before it becomes a problem.

Actively exploited cPanel bug exposes millions of websites to takeover

1 May 2026 at 12:48

Security researchers are warning about a newly discovered vulnerability in the widely used web server management software cPanel and WebHost Manager (WHM). 

This is a critical, actively exploited authentication-bypass bug in cPanel/WHM that lets attackers gain administrative access to the interface without credentials, potentially take over servers and all hosted sites.

The vulnerability, tracked as CVE-2026-41940, has been added to the Known Exploited Vulnerabilities catalog by the Cybersecurity and Infrastructure Security Agency (CISA), meaning there is evidence it is being used in real-world attacks.

Because cPanel/WHM is used by over a million sites worldwide, including banks and health organizations, the potential impact is huge. In simple terms, the bug can act like a front‑door key to a big chunk of the web’s hosting infrastructure.

cPanel released patches on April 28, 2026, and urged all customers and hosts to update. It said all supported versions after 11.40 are affected, including DNSOnly and WP Squared.

Hosting providers including Namecheap, HostGator, and KnownHost temporarily blocked access to cPanel interfaces while patching, treating this as a critical authentication bypass and reporting exploit attempts going back to late February 2026.

How to stay safe

While it’s up to the hosting companies and website owners to patch as quickly as possible, there are ways to reduce your risk if a site you use is compromised.

As always, limit the data you share with websites to what’s absolutely necessary. Data they don’t have can’t be stolen.

When ordering from an online retailer, don’t tick the box to save your card details for future purchases as they will be stored on the server.

If there’s an option to check out as a guest, use it. It reduces the amount of personal data tied to an account.

Don’t reuse passwords. When one site is compromised, having the same credentials in several places turns it into a multi‑account takeover problem. A password manager can help you create complex unique passphrases, and remember them for you.

Where possible, pay by credit card. In many regions, this gives you stronger fraud protection.


Personal Data Remover

Your details are probably already for sale. 


When a site you trust gets hacked

If you think you’ve been affected by a data breach, take the following steps:

  • Check the company’s advice. Every breach is different, so check with the company to find out what’s happened and follow any specific advice it offers.
  • Change your password. You can make a stolen password useless to thieves by changing it. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
  • Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
  • Watch out for impersonators. The thieves may contact you posing as the breached platform. Check the official website to see if it’s contacting victims and verify the identity of anyone who contacts you using a different communication channel.
  • Take your time. Phishing attacks often impersonate people or brands you know, and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
  • Consider not storing your card details. It’s definitely more convenient to let sites remember your card details, but it increases risk if a retailer suffers a breach.
  • Set up identity monitoring, which alerts you if your personal information is found being traded illegally online and helps you recover after.

What do cybercriminals know about you?

Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.

❌