❌

Normal view

Revolut phishing texts appear days after data breach

17 September 2026 at 16:07

Only days after Revolut acknowledged that it disclosed sensitive customer records to an unauthorized party, affected customers are receiving phishing texts. However, we don’t know yet if the phishing texts are linked to the breach.

The company had accepted fraudulent information requests sent from an email address on a legitimate government agency domain.

Through this social engineering attack, rather than by gaining access to Revolut’s systems, the criminals obtained the following types of information about customers:

  • Identity and contact information such as dates of birth, postal addresses, email addresses, and phone numbers
  • Copies of IDs such as passports and driver’s licenses
  • Verification selfies
  • Account statements and transaction histories

Revolut has said only that a “limited” or “very limited” number of customers were affected, and that it contacted them directly.

One affected customer received a phishing text on Monday, September 14, two days after Revolut publicly acknowledged the data breach. The message appeared in the same conversation as other Revolut texts, making it look as though it had come from the bank.

Scammers target Revolut customer
Phishing text to a Revolut customer

According to VirusTotal, the phishing domain was first scanned that same day.

In a separate example, another customer said that opening the link took them to a web page that requested access to their device’s camera. If you tap Allow, the page reportedly imitates Revolut’s live-video “turn your head” identity check before prompting you to enter a password.

This makes the phishing page appear more authentic. It may also allow the scammers to collect a selfie or video that could be used for further social engineering, identity fraud, or to make subsequent scams more convincing.

A convincing fake liveness check followed by a password screen is a common way to lower suspicion and obtain the information attackers need to attempt a real login or account-recovery flow.

If the campaign is connected to the breach, the information obtained from Revolut, combined with login details entered by victims or their approval of a login request, could be enough to take over their accounts.

How to stay safe

We don’t yet know whether the phishing campaign is using data exposed in the breach or whether unrelated scammers are exploiting news of the incident to target Revolut customers more broadly.

Either way, treat unexpected messages about your account with caution:

  • Don’t follow links in unsolicited messages. If a message concerns your account, open the official Revolut app directly.
  • Check the actual domain in your browser’s address bar to see if it corresponds with what you expect.
  • Use an up-to-date, real-time anti-malware solution on your device, preferably with a web protection component.
  • Malwarebytes Scam Guard can help you determine whether a message is a scam and advise you on what to do next.

Stop threats before they can do any harm.

Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →
Revolut phishing texts appear days after data breach

17 September 2026 at 16:07

Only days after Revolut acknowledged that it disclosed sensitive customer records to an unauthorized party, affected customers are receiving phishing texts. However, we don’t know yet if the phishing texts are linked to the breach.

The company had accepted fraudulent information requests sent from an email address on a legitimate government agency domain.

Through this social engineering attack, rather than by gaining access to Revolut’s systems, the criminals obtained the following types of information about customers:

  • Identity and contact information such as dates of birth, postal addresses, email addresses, and phone numbers
  • Copies of IDs such as passports and driver’s licenses
  • Verification selfies
  • Account statements and transaction histories

Revolut has said only that a “limited” or “very limited” number of customers were affected, and that it contacted them directly.

One affected customer received a phishing text on Monday, September 14, two days after Revolut publicly acknowledged the data breach. The message appeared in the same conversation as other Revolut texts, making it look as though it had come from the bank.

Scammers target Revolut customer
Phishing text to a Revolut customer

According to VirusTotal, the phishing domain was first scanned that same day.

In a separate example, another customer said that opening the link took them to a web page that requested access to their device’s camera. If you tap Allow, the page reportedly imitates Revolut’s live-video “turn your head” identity check before prompting you to enter a password.

This makes the phishing page appear more authentic. It may also allow the scammers to collect a selfie or video that could be used for further social engineering, identity fraud, or to make subsequent scams more convincing.

A convincing fake liveness check followed by a password screen is a common way to lower suspicion and obtain the information attackers need to attempt a real login or account-recovery flow.

If the campaign is connected to the breach, the information obtained from Revolut, combined with login details entered by victims or their approval of a login request, could be enough to take over their accounts.

How to stay safe

We don’t yet know whether the phishing campaign is using data exposed in the breach or whether unrelated scammers are exploiting news of the incident to target Revolut customers more broadly.

Either way, treat unexpected messages about your account with caution:

  • Don’t follow links in unsolicited messages. If a message concerns your account, open the official Revolut app directly.
  • Check the actual domain in your browser’s address bar to see if it corresponds with what you expect.
  • Use an up-to-date, real-time anti-malware solution on your device, preferably with a web protection component.
  • Malwarebytes Scam Guard can help you determine whether a message is a scam and advise you on what to do next.

Stop threats before they can do any harm.

Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →

Revolut gave customer IDs and financial data to a government impostor

14 September 2026 at 13:15

Revolut has acknowledged that it disclosed sensitive customer records to an unauthorized party. The company had accepted fraudulent information requests sent from an email address on a legitimate government agency domain, according to TechCrunch.

Revolut is a London-based banking and financial platform with more than 80 million customers globally, according to the company.

Revolut describes this as an external impersonation scam, not an intrusion into its systems. It also says customer funds were not affected. Revolut has not identified the government agency or disclosed its email domain.

The attacker appears to have abused the trust attached to a real government email domain to make bogus requests for customer information. Revolut detected the activity, blocked the sending address, and says it notified the relevant agency, law enforcement, data protection authorities, and financial regulators.

“Upon detection, we immediately blocked the address and alerted the relevant government agency as well as enforcement agencies, data protection, and financial regulators.”

Through this social engineering attack, rather than by gaining access to Revolut’s systems, the criminals obtained the following types of information about customers:

  • Identity and contact information like dates of birth, postal address, email address, and phone number.
  • Copies of IDs such as passports and driver’s licenses.
  • Verification selfies.
  • Account statements and transaction histories.

Revolut has said only that a “limited” or “very limited” number of customers were affected, and that it contacted them directly.

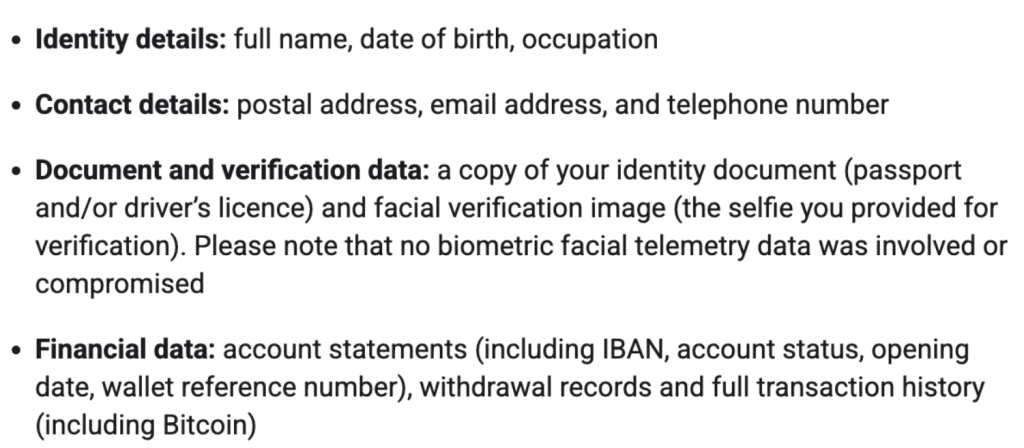
Those customers have received or will receive an email specifying which of their personal data was disclosed:

Affected Revolut customers will be told what type of data was disclosed.

How to stay safe

The likely consumer impact will be second-stage fraud attempts rather than immediate unauthorized transfers. Here are some guidelines to help keep your money safe:

Treat any unexpected Revolut-related contact as suspicious, especially calls, emails, WhatsApp messages, or text messages claiming you need to “secure” an account, reverse a transfer, or replace documents. Do not use links or phone numbers supplied in the message. Revolut advises ending contact with suspected scammers and contacting the company through official channels.

IDs and other exposed information could be used for identity theft. Monitor your accounts and credit reports for unfamiliar account openings or credit applications, and consider placing a fraud alert or using credit monitoring where available in your country.

If you received a notification email, check your balances, cards, beneficiaries, recent transfers, account statements, and linked devices. Report any unfamiliar activity immediately through Revolut’s secure in-app chat.

If you were involved in a data breach, read our blog Involved in a data breach? Here’s what you need to know for more recommendations. 

Pro tip: Use Malwarebytes Scam Guard to analyze any suspicious communications. It can help you determine whether a message is a scam and advise you on what to do next.


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

Revolut gave customer IDs and financial data to a government impostor

14 September 2026 at 13:15

Revolut has acknowledged that it disclosed sensitive customer records to an unauthorized party. The company had accepted fraudulent information requests sent from an email address on a legitimate government agency domain, according to TechCrunch.

Revolut is a London-based banking and financial platform with more than 80 million customers globally, according to the company.

Revolut describes this as an external impersonation scam, not an intrusion into its systems. It also says customer funds were not affected. Revolut has not identified the government agency or disclosed its email domain.

The attacker appears to have abused the trust attached to a real government email domain to make bogus requests for customer information. Revolut detected the activity, blocked the sending address, and says it notified the relevant agency, law enforcement, data protection authorities, and financial regulators.

“Upon detection, we immediately blocked the address and alerted the relevant government agency as well as enforcement agencies, data protection, and financial regulators.”

Through this social engineering attack, rather than by gaining access to Revolut’s systems, the criminals obtained the following types of information about customers:

  • Identity and contact information like dates of birth, postal address, email address, and phone number.
  • Copies of IDs such as passports and driver’s licenses.
  • Verification selfies.
  • Account statements and transaction histories.

Revolut has said only that a “limited” or “very limited” number of customers were affected, and that it contacted them directly.

Those customers have received or will receive an email specifying which of their personal data was disclosed:

Affected Revolut customers will be told what type of data was disclosed.

How to stay safe

The likely consumer impact will be second-stage fraud attempts rather than immediate unauthorized transfers. Here are some guidelines to help keep your money safe:

Treat any unexpected Revolut-related contact as suspicious, especially calls, emails, WhatsApp messages, or text messages claiming you need to “secure” an account, reverse a transfer, or replace documents. Do not use links or phone numbers supplied in the message. Revolut advises ending contact with suspected scammers and contacting the company through official channels.

IDs and other exposed information could be used for identity theft. Monitor your accounts and credit reports for unfamiliar account openings or credit applications, and consider placing a fraud alert or using credit monitoring where available in your country.

If you received a notification email, check your balances, cards, beneficiaries, recent transfers, account statements, and linked devices. Report any unfamiliar activity immediately through Revolut’s secure in-app chat.

If you were involved in a data breach, read our blog Involved in a data breach? Here’s what you need to know for more recommendations. 

Pro tip: Use Malwarebytes Scam Guard to analyze any suspicious communications. It can help you determine whether a message is a scam and advise you on what to do next.


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

❌