Login

Apple Patches iOS Flaw Allowing Recovery of Deleted Chats
Apple rolled out the security patches for dozens of iPhone and iPad models and generations.
The post Apple Patches iOS Flaw Allowing Recovery of Deleted Chats appeared first on SecurityWeek.

Apple rolled out the security patches for dozens of iPhone and iPad models and generations.
The post Apple Patches iOS Flaw Allowing Recovery of Deleted Chats appeared first on SecurityWeek.
The flaw allows attackers to access the SAM database, extract NTLM hashes, and gain System privileges.
The post Recent Microsoft Defender Vulnerability Exploited as Zero-Day appeared first on SecurityWeek.
In this post, we examine what NVD’s shift to selective enrichment means for vulnerability workflows and how security teams can maintain visibility and prioritization at scale.
 Table Of Contents

The National Vulnerability Database (NVD) is changing how it processes and enriches vulnerability data in response to sustained growth in CVE submissions.
Under a new model announced by the National Institute of Standards and Technology, NVD will no longer enrich every CVE. Instead, enrichment efforts will focus on a defined subset, including vulnerabilities in the CISA KEV catalog, software used by the federal government, and software designated as critical.
All other CVEs will remain in the database without additional context unless specifically requested.
Rising disclosure volumes are placing pressure on public vulnerability infrastructure, and it has direct implications for how security teams consume and act on vulnerability data.
For years, NVD aimed to provide consistent enrichment across all CVEs, including severity scoring, affected product data, and supporting context for prioritization.
That approach has not been sustainable since late 2023.
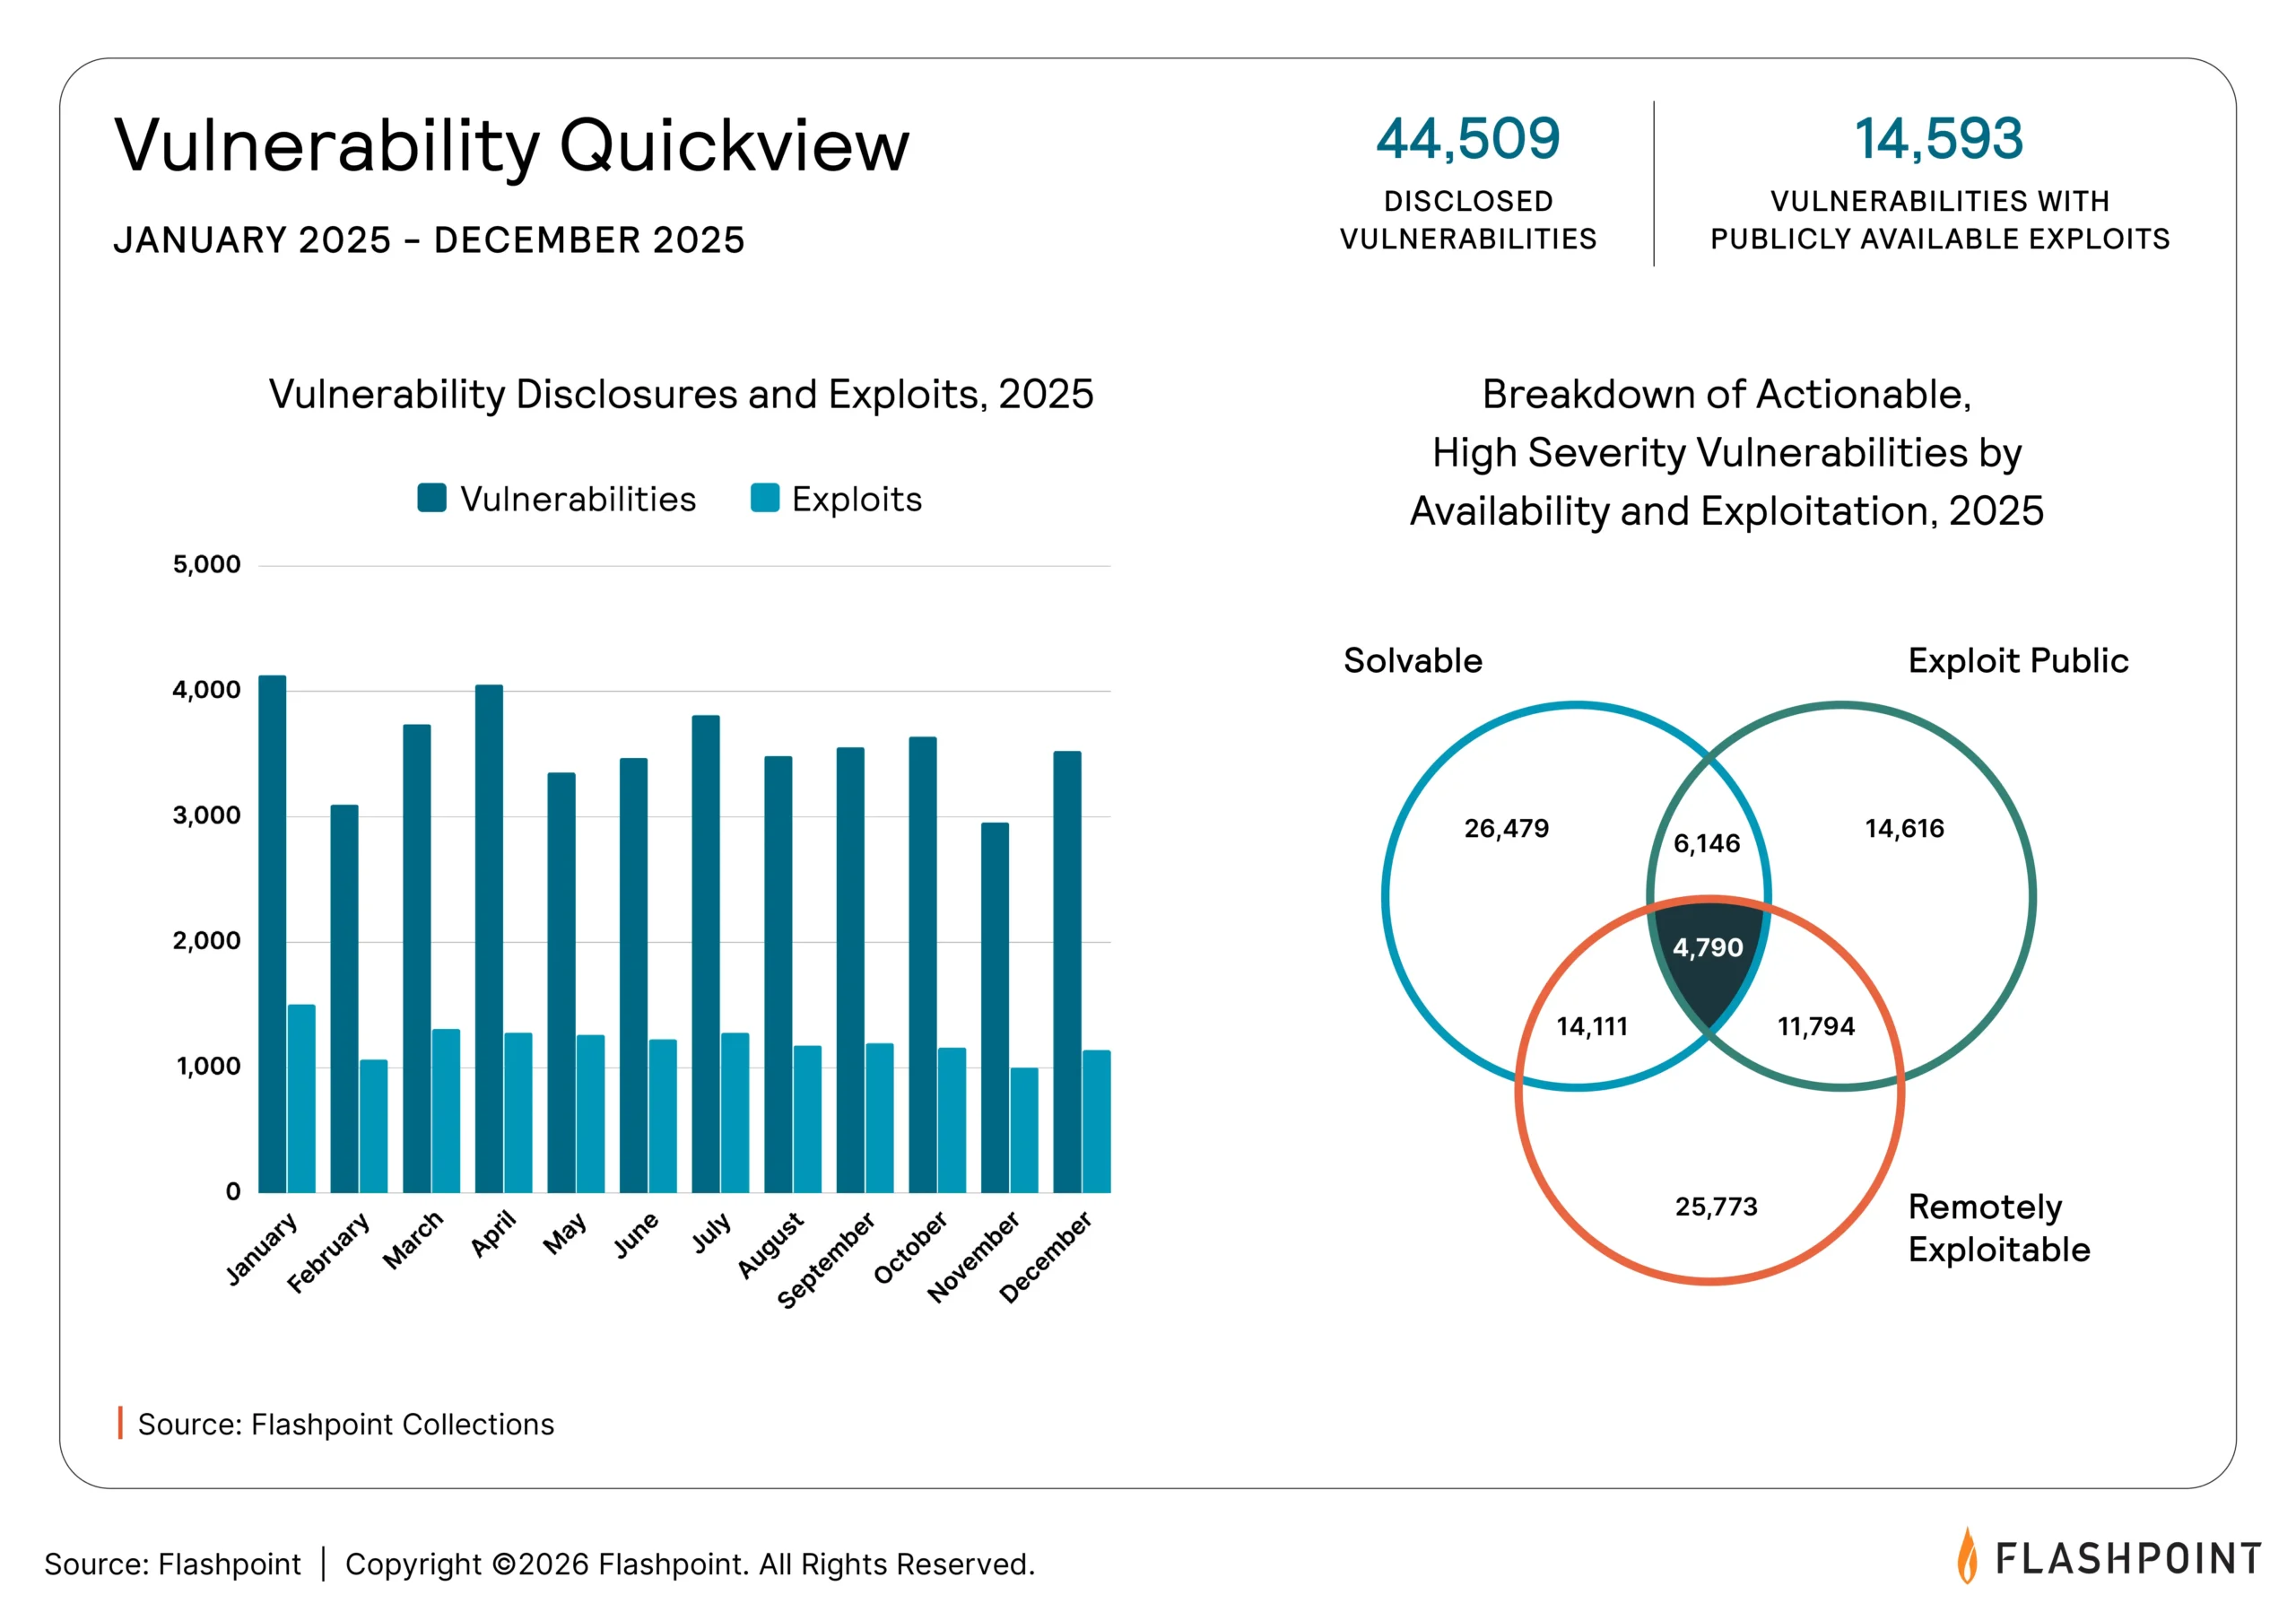
In 2025, Flashpoint tracked 44,509 disclosed vulnerabilities, 14,593 of which had publicly available exploits (and 1,944 more with proof-of-concepts).
CVE submissions increased by 263% between 2020 and 2025, with 2026 already tracking higher year-over-year. Even with increased throughput, NVD has not been able to keep pace.
Under the updated model:
This introduces a significant structural change in how vulnerability data is published and maintained.
Many security programs rely on NVD enrichment to operationalize CVE data. That enrichment provides the context needed to evaluate risk and determine remediation priorities.
With enrichment applied selectively, teams will encounter a growing number of CVEs that include:
At the same time, disclosure volume continues to rise, and exploitation timelines remain compressed. This creates a gap between what is disclosed and what can be acted on efficiently.
Security teams will need to account for:
These changes affect vulnerability management, threat intelligence, and security operations workflows simultaneously.
NVD’s updated model focuses enrichment on a defined set of criteria, including known exploited vulnerabilities and software relevant to federal systems.
These categories represent important segments of risk, but they do not encompass the full set of vulnerabilities that organizations encounter in practice.
Modern environments include:
Many vulnerabilities affecting these environments fall outside formal prioritization frameworks or lack immediate classification within public datasets. As a result, security teams will continue to face exposure from vulnerabilities that are:
As public enrichment becomes more selective, organizations will rely more heavily on alternative sources to maintain visibility and context.
Effective vulnerability intelligence requires:
This level of detail supports faster and more accurate decision-making in environments where both volume and speed are increasing.
Flashpoint’s vulnerability intelligence model is built to address these requirements, with a dataset that includes over 7,000 known exploited vulnerabilities and ongoing analyst-driven enrichment across global sources.
This shift in NVD operations does not change the need to track CVEs. It changes how that data can be used. Security teams should evaluate how their current workflows depend on:
From there, teams can take steps to strengthen resilience:
For many teams, NVD has been a default source of vulnerability context. This change makes clear that its role is narrowing at a time when disclosure volume and prioritization demands are increasing.
At the same time, the role of vulnerability intelligence is expanding.
Security teams need access to data that supports prioritization, not just identification. They need consistent enrichment, faster turnaround, broader coverage, and context tied to real-world activity. As disclosure volumes continue to grow, those requirements become more central to how organizations manage risk.
Flashpoint’s Vulnerability Intelligence provides this level of coverage and context, with analyst-driven enrichment, global visibility across CVE and non-CVE vulnerabilities, and a dataset that includes over 7,000 known exploited vulnerabilities.
Request a demo to see how Flashpoint helps security teams prioritize and act on vulnerability risk with greater precision and confidence.
The post National Vulnerability Database (NVD) Shifts to Selective Enrichment as CVE Volume Surges appeared first on Flashpoint.
Last week, Anthropic pulled back the curtain on Claude Mythos Preview, an AI model so capable at finding and exploiting software vulnerabilities that the company decided it was too dangerous to release to the public. Instead, access has been restricted to roughly 50 organizations—Microsoft, Apple, Amazon Web Services, CrowdStrike and other vendors of critical infrastructure—under an initiative called Project Glasswing.
The announcement was accompanied by a barrage of hair-raising anecdotes: thousands of vulnerabilities uncovered across every major operating system and browser, including a 27-year-old bug in OpenBSD, a 16-year-old flaw in FFmpeg. Mythos was able to weaponize a set of vulnerabilities it found in the Firefox browser into 181 usable attacks; Anthropic’s previous flagship model could only achieve two.
This is, in many respects, exactly the kind of responsible disclosure that security researchers have long urged. And yet the public has been given remarkably little with which to evaluate Anthropic’s decision. We have been shown a highlight reel of spectacular successes. However, we can’t tell if we have a blockbuster until they let us see the whole movie.
For example, we don’t know how many times Mythos mistakenly flagged code as vulnerable. Anthropic said security contractors agreed with the AI’s severity rating 198 times, with an 89 per cent severity agreement. That’s impressive, but incomplete. Independent researchers examining similar models have found that AI that detects nearly every real bug also hallucinates plausible-sounding vulnerabilities in patched, correct code.
This matters. A model that autonomously finds and exploits hundreds of vulnerabilities with inhuman precision is a game changer, but a model that generates thousands of false alarms and non-working attacks still needs skilled and knowledgeable humans. Without knowing the rate of false alarms in Mythos’s unfiltered output, we cannot tell whether the examples showcased are representative.
There is a second, subtler problem. Large language models, including Mythos, perform best on inputs that resemble what they were trained on: widely used open-source projects, major browsers, the Linux kernel and popular web frameworks. Concentrating early access among the largest vendors of precisely this software is sensible; it lets them patch first, before adversaries catch up.
But the inverse is also true. Software outside the training distribution—industrial control systems, medical device firmware, bespoke financial infrastructure, regional banking software, older embedded systems—is exactly where out-of-the-box Mythos is likely least able to find or exploit bugs.
However, a sufficiently motivated attacker with domain expertise in one of these fields could nevertheless wield Mythos’s advanced reasoning capabilities as a force multiplier, probing systems that Anthropic’s own engineers lack the specialized knowledge to audit. The danger is not that Mythos fails in those domains; it is that Mythos may succeed for whoever brings the expertise.
Broader, structured access for academic researchers and domain specialists—cardiologists’ partners in medical device security, control-systems engineers, researchers in less prominent languages and ecosystems—would meaningfully reduce this asymmetry. Fifty companies, however well chosen, cannot substitute for the distributed expertise of the entire research community.
None of this is an indictment of Anthropic. By all appearances the company is trying to act responsibly, and its decision to hold the model back is evidence of seriousness.
But Anthropic is a private company and, in some ways, still a start-up. Yet it is making unilateral decisions about which pieces of our critical global infrastructure get defended first, and which must wait their turn.
It has finite staff, finite budget and finite expertise. It will miss things, and when the thing missed is in the software running a hospital or a power grid, the cost will be borne by people who never had a say.
The security problem is far greater than one company and one model. There’s no reason to believe that Mythos Preview is unique. (Not to be outdone, OpenAI announced that its new GPT-5.4-Cyber is so dangerous that the model also will not be released to the general public.) And it’s unclear how much of an advance these new models represent. The security company Aisle was able to replicate many of Anthropic’s published anecdotes using smaller, cheaper, public AI models.
Any decisions we make about whether and how to release these powerful models are more than one company’s responsibility. Ultimately, this will probably lead to regulation. That will be hard to get right and requires a long process of consultation and feedback.
In the short term, we need something simpler: greater transparency and information sharing with the broader community. This doesn’t necessarily mean making powerful models like Claude Mythos widely available. Rather, it means sharing as much data and information as possible, so that we can collectively make informed decisions.
We need globally co-ordinated frameworks for independent auditing, mandatory disclosure of aggregate performance metrics and funded access for academic and civil-society researchers.
This has implications for national security, personal safety and corporate competitiveness. Any technology that can find thousands of exploitable flaws in the systems we all depend on should not be governed solely by the internal judgment of its creators, however well intentioned.
Until that changes, each Mythos-class release will put the world at the edge of another precipice, without any visibility into whether there is a landing out of view just below, or whether this time the drop will be fatal. That is not a choice a for-profit corporation should be allowed to make in a democratic society. Nor should such a company be able to restrict the ability of society to make choices about its own security.
This essay was written with David Lie, and originally appeared in The Globe and Mail.
CVE-2023-33538 allows for command injection in TP-Link routers. We discuss exploitation attempts with payloads characteristic of Mirai botnet malware.
The post A Deep Dive Into Attempted Exploitation of CVE-2023-33538 appeared first on Unit 42.
In this post we explore Flashpoint’s latest milestone of surpassing cataloging 7,000 known exploited vulnerabilities and what this means for security teams.
 Table Of Contents
Flashpoint Vulnerability Intelligence has surpassed cataloging 7,000 known exploited vulnerabilities, surpassing another major milestone as vulnerability disclosures accelerate across the global attack surface.
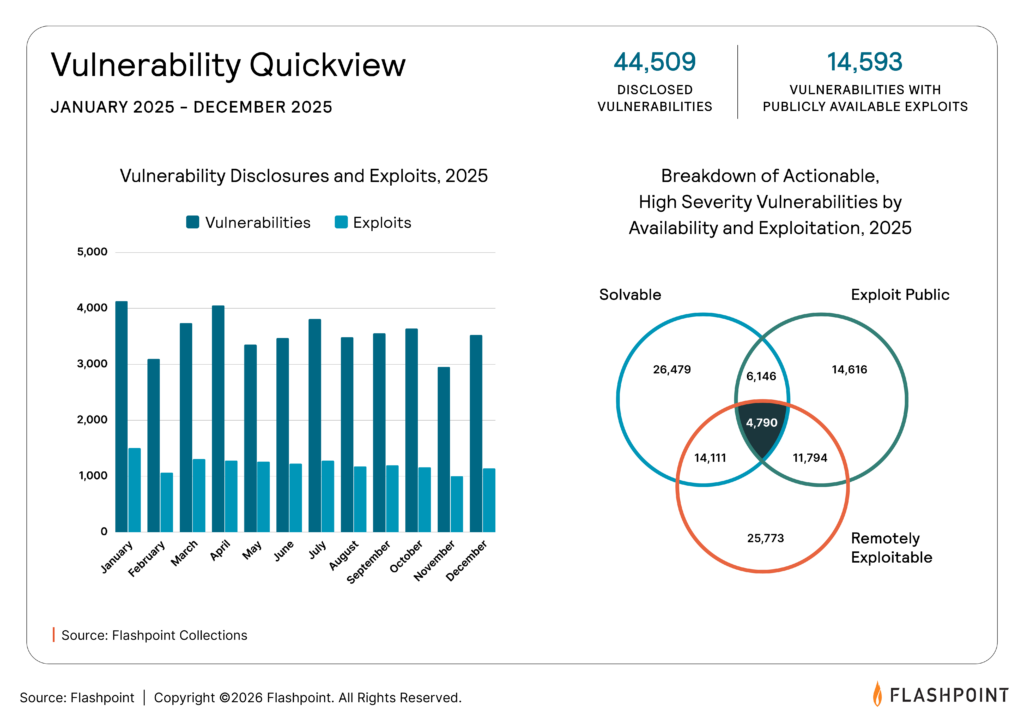
In 2025, Flashpoint tracked 44,509 disclosed vulnerabilities, a pace that continues to accelerate into 2026. Of those, 14,593 had publicly available exploits (1,944 more with proof-of-concepts), giving threat actors immediate pathways to weaponization.
This pace is shaping how exploitation unfolds, with high-impact vulnerabilities being operationalized within hours or days, particularly when they affect widely deployed technologies or core infrastructure.
Security teams are operating within this compressed environment every day. They are reviewing more findings across open-source software, commercial applications, cloud environments, and third-party dependencies, while working within tighter timelines to assess impact and take action.
Flashpoint’s latest milestone of surpassing 7,000 known exploited vulnerabilities (KEVs) cataloged reflects that reality. It highlights how vulnerability management programs are evolving toward prioritization as a core capability, with a focus on vulnerabilities tied to active exploitation and real-world risk.
Security teams are operating in a high-volume environment. Vulnerabilities are disclosed continuously across open-source software, commercial applications, cloud environments, and third-party dependencies. At the same time, advancements in automation and code analysis are increasing the rate at which new findings are surfaced.
Each of these findings enters an already crowded workflow. Teams are expected to determine relevance, urgency, and impact quickly, often with limited context. This is where risk-based decision making becomes essential.
Flashpoint tracks hundreds of thousands of vulnerabilities across thousands of sources. Within that dataset, a much smaller percentage shows confirmed exploitation activity. That concentration of risk informs how effective programs allocate time and resources.
Crossing the 7,000+ KEV milestone goes beyond scale to provide greater precision, deeper context, and stronger confidence in how teams prioritize and act on the most critical vulnerabilities.
This level of clarity allows teams to move faster without sacrificing accuracy. It supports vulnerability management programs that are built around real-world attacker behavior and aligned to current risk.
Public vulnerability catalogs remain useful reference points for tracking disclosures and confirmed exploitation. The CISA Known Exploited Vulnerabilities catalog, for example, gives security teams a curated view into a limited set of vulnerabilities that have been exploited in the wild that impact U.S. government stakeholders.
For many organizations, though, that level of visibility is not enough.
Public catalogs capture only part of the picture. They tend to reflect a narrower slice of exploitation activity, with less detail on how vulnerabilities are being used, which actors are leveraging them, and what defenders should do next. They also rely heavily on CVE-based tracking, leaving gaps around non-CVE exposures and other vulnerabilities that still carry operational risk.
Flashpoint’s FP KEV and Vulnerability Intelligence provide a broader and more actionable view. The advantage is visible in both scale and depth. Of the 7,000 known exploited vulnerabilities in FP KEV, over 800 are missing from CVE. That expanded coverage is paired with the context security teams need to prioritize effectively, including exploit maturity, adversary mapping, affected product detail, and remediation guidance.
| Dimension | Public KEV Catalogs | Flashpoint FP KEV |
| Scope | Varies by provider, with coverage dependent on available sources and methodology | Global, cross-industry coverage |
| Coverage | CVE-based tracking | CVE and non-CVE vulnerabilities |
| Context | Limited enrichment | Exploit maturity, adversary mapping, remediation |
| Update Model | Periodic updates | Continuously updated with analyst input |
This is what separates a reference list from an operational dataset. Teams need vulnerability intelligence that supports triage, remediation, reporting, and broader risk reduction efforts. Wider visibility and deeper context make that possible.
Vulnerability data originates from a wide range of sources with varying levels of completeness and accuracy.
Flashpoint’s intelligence model includes analyst validation to ensure consistency and depth across the dataset.
This process includes:
Analyst input supports:
Vulnerability intelligence feeds multiple functions across an organization. Teams use this data to align technical actions with current threat activity.
Common use cases include:
Each of these functions relies on consistent, enriched intelligence to maintain alignment.
Vulnerability discovery continues to expand across software ecosystems, infrastructure, and identity layers.
Security teams require a clear understanding of which issues are relevant to their environment at any given time.
Flashpoint provides primary source intelligence that supports this need through:
This approach enables teams to maintain focus, allocate resources effectively, and respond to risk based on current threat activity. Request a demo and learn more today.
The post Flashpoint Surpasses Cataloging 7,000 Known Exploited Vulnerabilities as Disclosure Volume Accelerates appeared first on Flashpoint.
On March 4, 2026, Google and iVerify published reports about a highly sophisticated exploit kit targeting Apple iPhone devices. According to Google, the exploit kit was first discovered in targeted attacks conducted by a customer of an unnamed surveillance vendor. It was later used by other attackers in watering-hole attacks in Ukraine and in financially motivated attacks in China. Additionally, researchers discovered an instance with the debug version of the exploit kit, which revealed the internal names of the exploits and the framework name used by its developers — Coruna. Analysis of the kit showed that it relies on the exploitation of many previously patched vulnerabilities and also includes exploits for CVE-2023-32434 and CVE-2023-38606. These two vulnerabilities particularly caught our attention because they had been first discovered as zero-days used in Operation Triangulation.
Operation Triangulation is a complex mobile APT campaign targeting iOS devices. We discovered it while monitoring the network traffic of our own corporate Wi-Fi network. We noticed suspicious activity that originated from several iOS-based phones. Following the investigation, we learned that this campaign employed a sophisticated spyware implant and multiple zero-day exploits. The investigation lasted for over six months, during which we disclosed our findings in connection to the attack. Kaspersky GReAT experts also presented these findings at the 37th Chaos Communication Congress (37C3).
Although all the details of both CVE-2023-32434 and CVE-2023-38606 have long been publicly available, and other researchers have developed their own exploits without ever seeing the Triangulation code, we decided to closely investigate the exploits used in Coruna. Some of the exploit kit distribution links provided by Google remained active at the time the report was published, which allowed us to collect, decrypt, and analyze all components of Coruna.
During our analysis, we discovered that the kernel exploit for CVE-2023-32434 and CVE-2023-38606 vulnerabilities used in Coruna, in fact, is an updated version of the same exploit that had been used in Operation Triangulation. The images below illustrate a high-level overview of the two attack chains. The exploit in question is highlighted with a red rectangle.
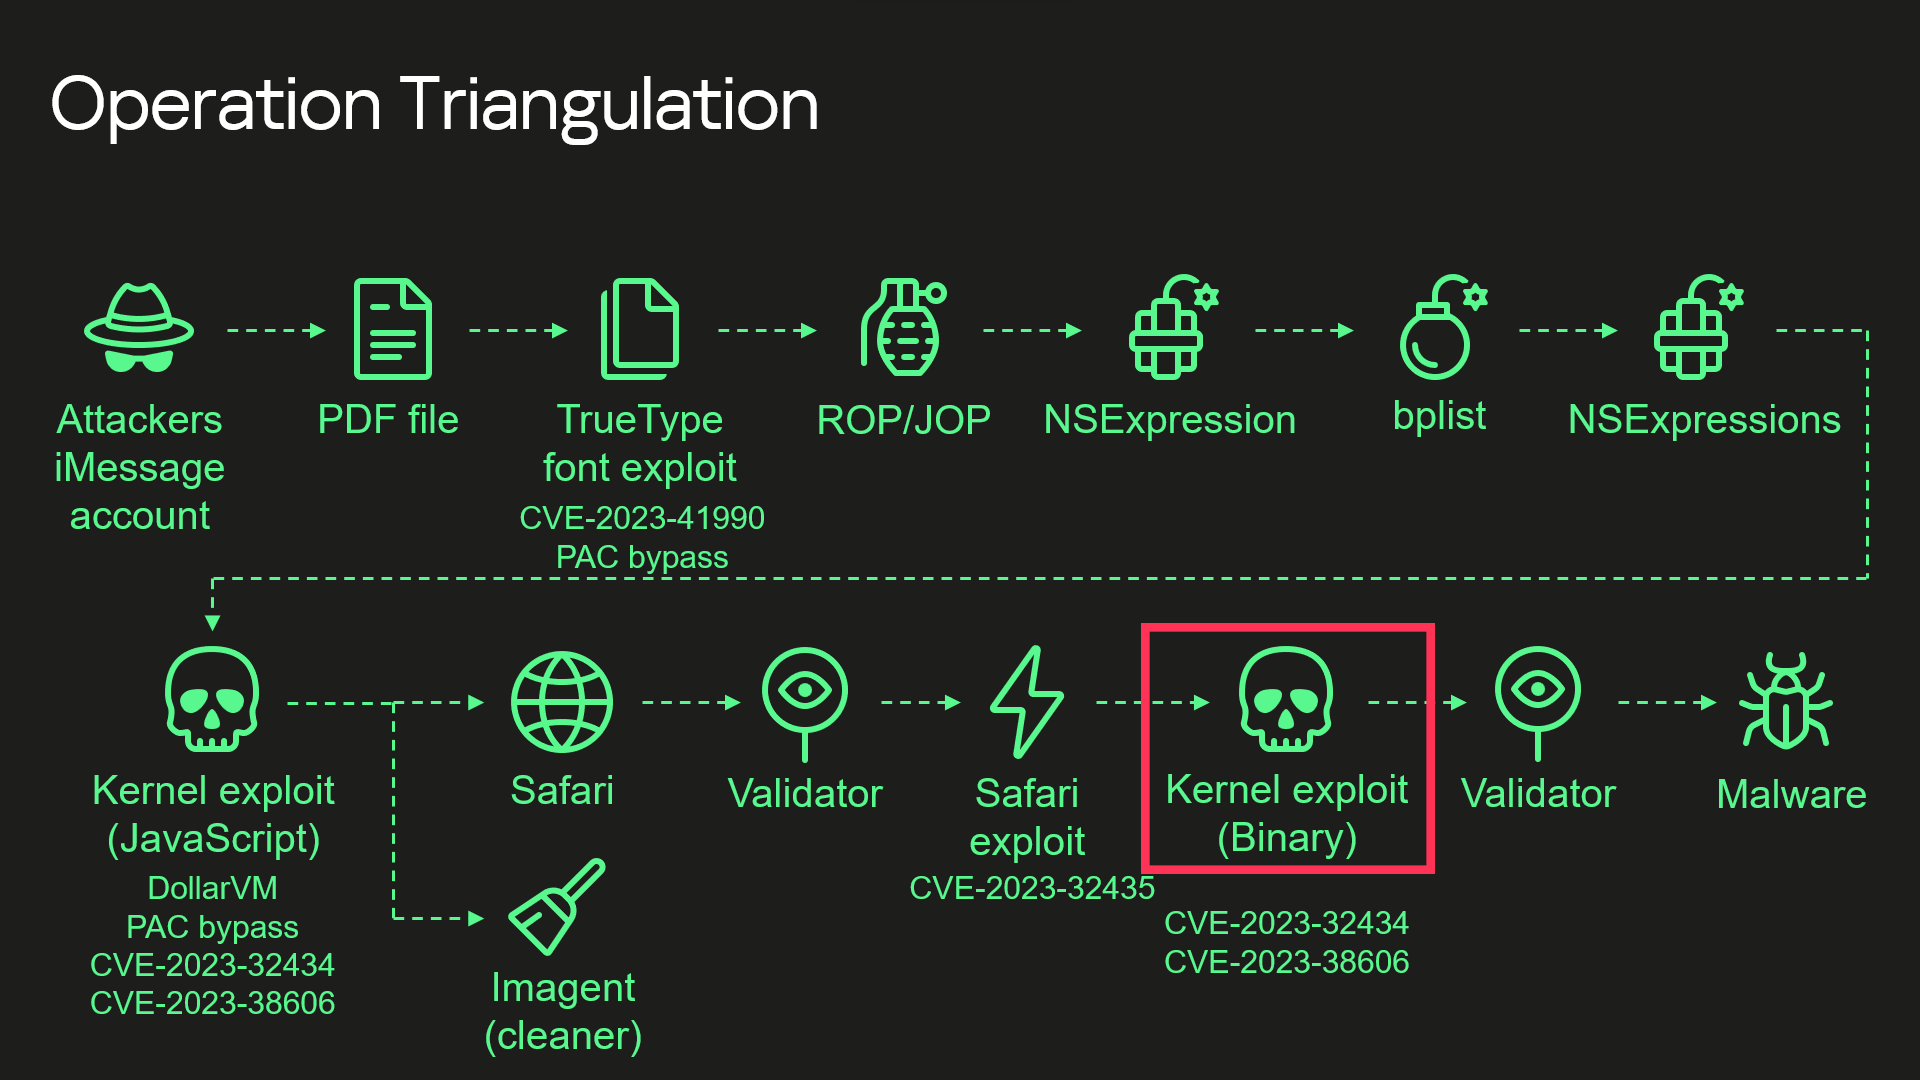
Attack chain of Operation Triangulation (simplified)
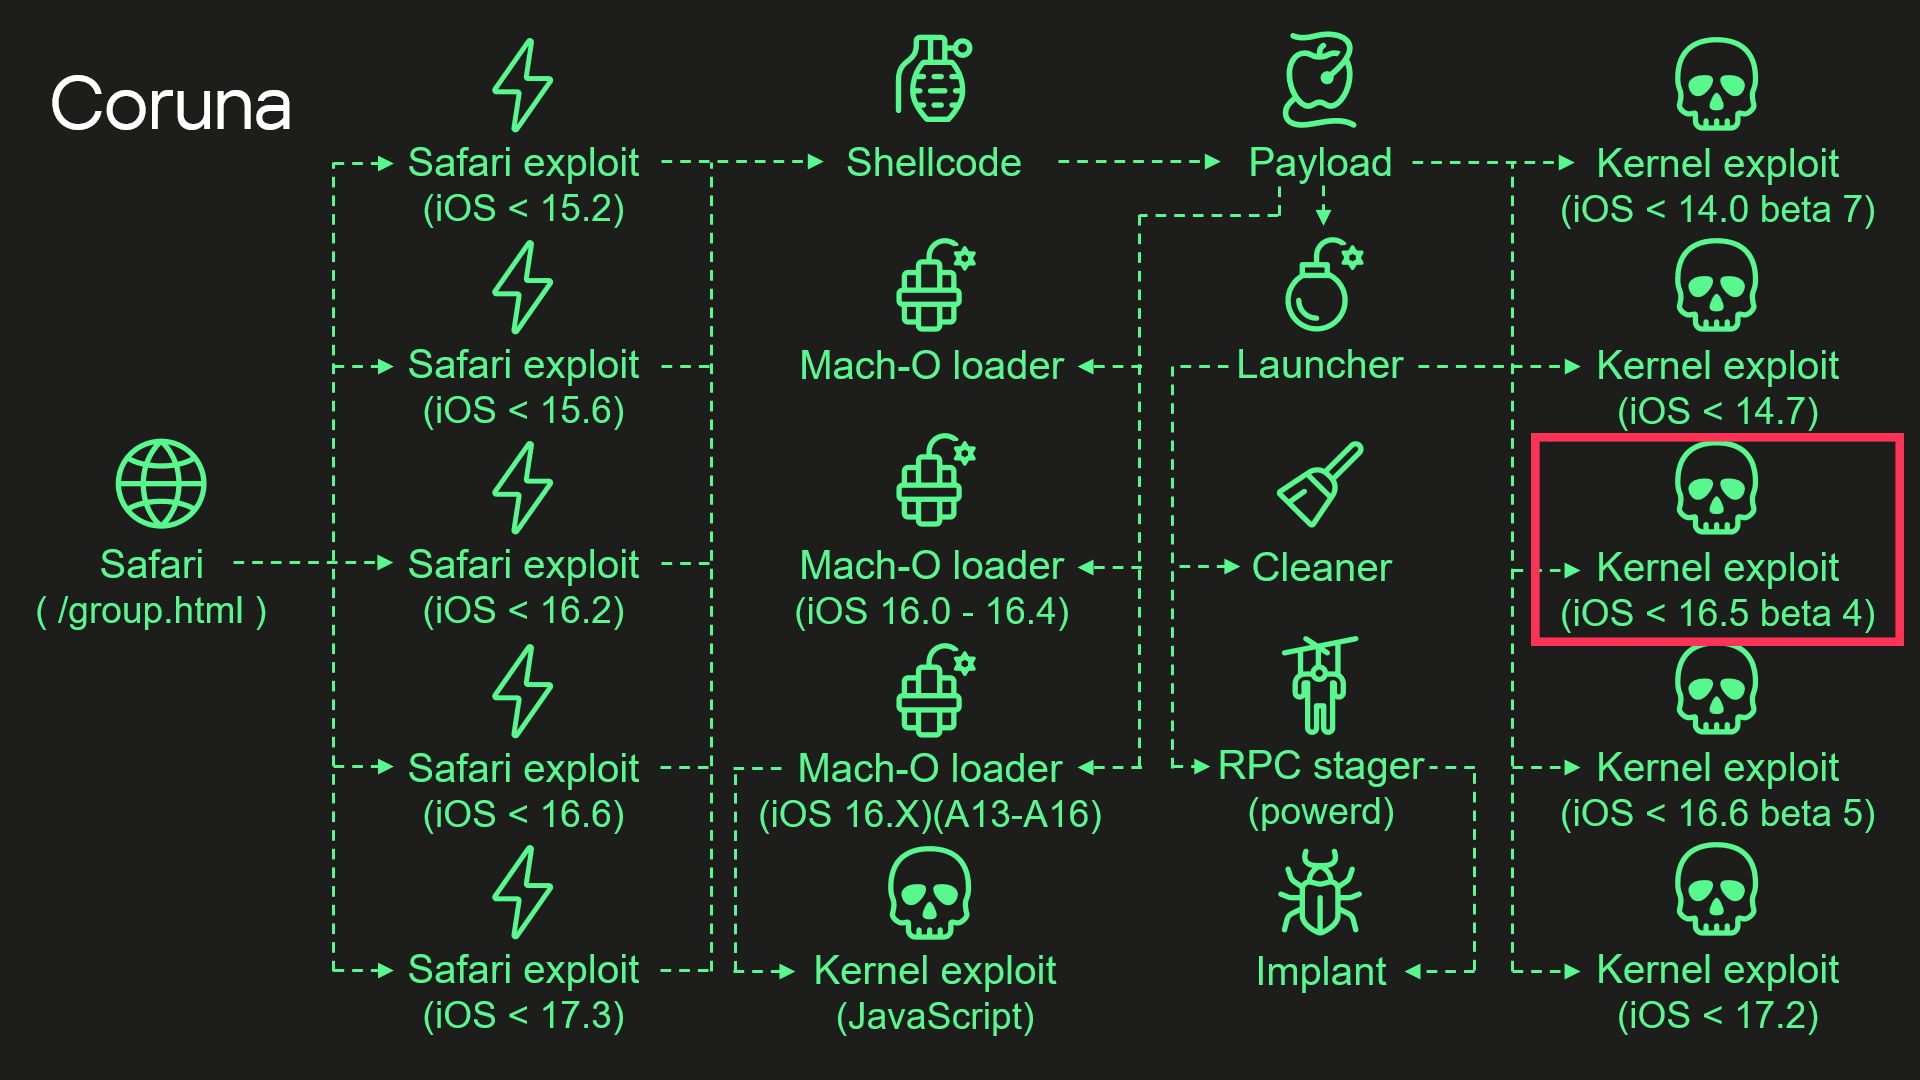
Attack chain of Coruna (simplified)
Moreover, we discovered that Coruna includes four additional kernel exploits that we had not seen used in Operation Triangulation, two of which were developed after the discovery of Operation Triangulation. All of these exploits are built on the same kernel exploitation framework and share common code. Code similarities from kernel exploits can also be found in other components of Coruna. These findings led us to conclude that this exploit kit was not patchworked but rather designed with a unified approach. We assume that it’s an updated version of the same exploitation framework that was used — at least to some extent — in Operation Triangulation.
While we continue to investigate all exploits and vulnerabilities used by Coruna, this post provides a high-level overview of the exploit kit and attack chain.
Exploitation begins with a stager that fingerprints the browser and selects and executes appropriate remote code execution (RCE) and pointer authentication code (PAC) exploits depending on the browser version. It also contains a URL to an encrypted file with information about all available packages containing exploits and other components. The stager also includes a 256-bit key used to decrypt it. The URL and decryption key are passed to a payload embedded in PAC exploits.
The payload is responsible for initiating the exploitation of the kernel. After initialization, the payload first downloads a file with information about other available components. To extract it, the payload performs several steps processing multiple file formats.
First, the downloaded file is decrypted using the ChaCha20 stream cipher. Decryption yields a container with the magic number 0xBEDF00D, which stores LZMA-compressed data.
The file format used by the exploit kit to store compressed data
| Offset | Field |
| 0x00 | Magic number (0xBEDF00D) |
| 0x04 | Decompressed data size |
| 0x08 | LZMA-compressed data |
The decompressed data presents another container with the magic number 0xF00DBEEF. This file format is used in the exploit kit to store and retrieve files by their IDs.
The file format used by the exploit kit to store files
| Offset | Field |
| 0x00 | Magic number (0xF00DBEEF) |
| 0x04 | Number of entries |
| 0x08 | Entry[0].File ID |
| 0x0C | Entry[0].Status |
| 0x10 | Entry[0].File offset |
| 0x14 | Entry[0].File size |
We provide a description of all possible File ID values below. At this stage, when the payload gathers information about all available file packages, this container holds only one file, and its File ID is 0x70000.
Finally, we get to the file with information about all available file packages. It starts with the magic value 0x12345678. The exploit kit uses this file format to obtain URLs and decryption keys for additional components that need to be downloaded.
The file format used by the exploit kit to store information about file packages
| Offset | Field |
| 0x00 | Magic number (0x12345678) |
| 0x04 | Flags |
| 0x08 | Directory path |
| 0x108 | Number of entries |
| 0x10C | Entry[0].Package ID |
| 0x110 | Entry[0].ChaCha20 key |
| 0x130 | Entry[0].File name |
The components required for exploiting a targeted device are selected using the Package ID. Its high byte specifies the package type and required hardware. We’ve seen the following package types:
The payload code also supports additional package types, such as 0xF1, an exploit for older ARM devices that do not support 64-bit architecture. Interestingly, however, the files for such exploits are missing.
Other bytes of the Package ID define the supported firmware version and CPU generation.
Some of the observed Package IDs (those with unique content)
| Package ID | Description |
| 0xF3300000 | Kernel exploit (iOS < 14.0 beta 7) and other components |
| 0xF3400000 | Kernel exploit (iOS < 14.7) and other components |
| 0xF3700000 | Kernel exploit (iOS < 16.5 beta 4) and other components |
| 0xF3800000 | Kernel exploit (iOS < 16.6 beta 5) and other components |
| 0xF3900000 | Kernel exploit (iOS < 17.2) and other components |
| 0xA3030000 | Mach-O loader (iOS 16.X) (A13 – A16) |
| 0xA3050000 | Mach-O loader (iOS 16.0 – 16.4) |
The files inside these packages are also stored in encrypted and compressed 0xF00DBEEF containers, but this time compression is optional and is determined by the second bit in the Flags field. Different packages contain different sets of files. A description of all possible File IDs is given in the table below.
Observed File IDs
| File ID | Description |
| 0x10000 | Implant |
| 0x50000 | Mach-O loader (default) |
| 0x70000 | List of additional components |
| 0x70005 | Launcher config |
| 0x80000 | Launcher in 0xF2/0xF3 packages, or Mach-O loader in 0xA2/0xA3 |
| 0x90000 | Kernel exploit |
| 0x90001 | Kernel exploit (for Mach-O loader) |
| 0xA0000 | Logs cleaner |
| 0xA0001 | Mach-O loader component |
| 0xA0002 | Mach-O loader component |
| 0xF0000 | RPC stager |
After downloading the necessary components, the payload begins executing kernel exploits, Mach-O loaders, and the malware launcher. The payload selects an appropriate Mach-O loader based on the firmware version, CPU, and presence of the iokit-open-service permission.
We analyzed all five kernel exploits from the kit and discovered that one of them is an updated version of the same exploit we discovered in Operation Triangulation. There are many small changes, but the most noticeable are as follows:
Why does the exploit need to check for iOS 17.2 and newer CPUs if the targeted vulnerabilities were fixed in iOS 16.5 beta 4? The answer can be found by examining other exploits: they are all based on the same source code. The only difference is in the vulnerabilities they exploit, so these checks were added to support the newer exploits and appeared in the older version after recompilation.
The launcher is responsible for orchestrating the post-exploitation activities. It also uses the kernel exploit and the interface it provides. However, since the exploit creates special kernel objects during its execution that provide the ability to read and write to kernel memory, the launcher simply reuses these objects without the need to trigger vulnerabilities and go through the entire exploitation path again. The launcher cleans up exploitation artifacts, retrieves the process name for injection from a config with the 0xDEADD00F magic number, injects a stager into the target process, uses it to execute itself, and launches the implant.
This case demonstrates once again the dangers associated with such malicious tools that lie in their potential wide usage. Originally developed for cyber-espionage purposes, this framework is now being used by cybercriminals of a broader kind, placing millions of users with unpatched devices at risk. Given its modular design and ease of reuse, we expect that other threat actors will begin incorporating it into their attacks. We strongly recommend that users install the latest security updates as soon as possible, if they have not already done so.
On March 4, 2026, Google and iVerify published reports about a highly sophisticated exploit kit targeting Apple iPhone devices. According to Google, the exploit kit was first discovered in targeted attacks conducted by a customer of an unnamed surveillance vendor. It was later used by other attackers in watering-hole attacks in Ukraine and in financially motivated attacks in China. Additionally, researchers discovered an instance with the debug version of the exploit kit, which revealed the internal names of the exploits and the framework name used by its developers — Coruna. Analysis of the kit showed that it relies on the exploitation of many previously patched vulnerabilities and also includes exploits for CVE-2023-32434 and CVE-2023-38606. These two vulnerabilities particularly caught our attention because they had been first discovered as zero-days used in Operation Triangulation.
Operation Triangulation is a complex mobile APT campaign targeting iOS devices. We discovered it while monitoring the network traffic of our own corporate Wi-Fi network. We noticed suspicious activity that originated from several iOS-based phones. Following the investigation, we learned that this campaign employed a sophisticated spyware implant and multiple zero-day exploits. The investigation lasted for over six months, during which we disclosed our findings in connection to the attack. Kaspersky GReAT experts also presented these findings at the 37th Chaos Communication Congress (37C3).
Although all the details of both CVE-2023-32434 and CVE-2023-38606 have long been publicly available, and other researchers have developed their own exploits without ever seeing the Triangulation code, we decided to closely investigate the exploits used in Coruna. Some of the exploit kit distribution links provided by Google remained active at the time the report was published, which allowed us to collect, decrypt, and analyze all components of Coruna.
During our analysis, we discovered that the kernel exploit for CVE-2023-32434 and CVE-2023-38606 vulnerabilities used in Coruna, in fact, is an updated version of the same exploit that had been used in Operation Triangulation. The images below illustrate a high-level overview of the two attack chains. The exploit in question is highlighted with a red rectangle.
Attack chain of Operation Triangulation (simplified)
Attack chain of Coruna (simplified)
Moreover, we discovered that Coruna includes four additional kernel exploits that we had not seen used in Operation Triangulation, two of which were developed after the discovery of Operation Triangulation. All of these exploits are built on the same kernel exploitation framework and share common code. Code similarities from kernel exploits can also be found in other components of Coruna. These findings led us to conclude that this exploit kit was not patchworked but rather designed with a unified approach. We assume that it’s an updated version of the same exploitation framework that was used — at least to some extent — in Operation Triangulation.
While we continue to investigate all exploits and vulnerabilities used by Coruna, this post provides a high-level overview of the exploit kit and attack chain.
Exploitation begins with a stager that fingerprints the browser and selects and executes appropriate remote code execution (RCE) and pointer authentication code (PAC) exploits depending on the browser version. It also contains a URL to an encrypted file with information about all available packages containing exploits and other components. The stager also includes a 256-bit key used to decrypt it. The URL and decryption key are passed to a payload embedded in PAC exploits.
The payload is responsible for initiating the exploitation of the kernel. After initialization, the payload first downloads a file with information about other available components. To extract it, the payload performs several steps processing multiple file formats.
First, the downloaded file is decrypted using the ChaCha20 stream cipher. Decryption yields a container with the magic number 0xBEDF00D, which stores LZMA-compressed data.
The file format used by the exploit kit to store compressed data
| Offset | Field |
| 0x00 | Magic number (0xBEDF00D) |
| 0x04 | Decompressed data size |
| 0x08 | LZMA-compressed data |
The decompressed data presents another container with the magic number 0xF00DBEEF. This file format is used in the exploit kit to store and retrieve files by their IDs.
The file format used by the exploit kit to store files
| Offset | Field |
| 0x00 | Magic number (0xF00DBEEF) |
| 0x04 | Number of entries |
| 0x08 | Entry[0].File ID |
| 0x0C | Entry[0].Status |
| 0x10 | Entry[0].File offset |
| 0x14 | Entry[0].File size |
We provide a description of all possible File ID values below. At this stage, when the payload gathers information about all available file packages, this container holds only one file, and its File ID is 0x70000.
Finally, we get to the file with information about all available file packages. It starts with the magic value 0x12345678. The exploit kit uses this file format to obtain URLs and decryption keys for additional components that need to be downloaded.
The file format used by the exploit kit to store information about file packages
| Offset | Field |
| 0x00 | Magic number (0x12345678) |
| 0x04 | Flags |
| 0x08 | Directory path |
| 0x108 | Number of entries |
| 0x10C | Entry[0].Package ID |
| 0x110 | Entry[0].ChaCha20 key |
| 0x130 | Entry[0].File name |
The components required for exploiting a targeted device are selected using the Package ID. Its high byte specifies the package type and required hardware. We’ve seen the following package types:
The payload code also supports additional package types, such as 0xF1, an exploit for older ARM devices that do not support 64-bit architecture. Interestingly, however, the files for such exploits are missing.
Other bytes of the Package ID define the supported firmware version and CPU generation.
Some of the observed Package IDs (those with unique content)
| Package ID | Description |
| 0xF3300000 | Kernel exploit (iOS < 14.0 beta 7) and other components |
| 0xF3400000 | Kernel exploit (iOS < 14.7) and other components |
| 0xF3700000 | Kernel exploit (iOS < 16.5 beta 4) and other components |
| 0xF3800000 | Kernel exploit (iOS < 16.6 beta 5) and other components |
| 0xF3900000 | Kernel exploit (iOS < 17.2) and other components |
| 0xA3030000 | Mach-O loader (iOS 16.X) (A13 – A16) |
| 0xA3050000 | Mach-O loader (iOS 16.0 – 16.4) |
The files inside these packages are also stored in encrypted and compressed 0xF00DBEEF containers, but this time compression is optional and is determined by the second bit in the Flags field. Different packages contain different sets of files. A description of all possible File IDs is given in the table below.
Observed File IDs
| File ID | Description |
| 0x10000 | Implant |
| 0x50000 | Mach-O loader (default) |
| 0x70000 | List of additional components |
| 0x70005 | Launcher config |
| 0x80000 | Launcher in 0xF2/0xF3 packages, or Mach-O loader in 0xA2/0xA3 |
| 0x90000 | Kernel exploit |
| 0x90001 | Kernel exploit (for Mach-O loader) |
| 0xA0000 | Logs cleaner |
| 0xA0001 | Mach-O loader component |
| 0xA0002 | Mach-O loader component |
| 0xF0000 | RPC stager |
After downloading the necessary components, the payload begins executing kernel exploits, Mach-O loaders, and the malware launcher. The payload selects an appropriate Mach-O loader based on the firmware version, CPU, and presence of the iokit-open-service permission.
We analyzed all five kernel exploits from the kit and discovered that one of them is an updated version of the same exploit we discovered in Operation Triangulation. There are many small changes, but the most noticeable are as follows:
Why does the exploit need to check for iOS 17.2 and newer CPUs if the targeted vulnerabilities were fixed in iOS 16.5 beta 4? The answer can be found by examining other exploits: they are all based on the same source code. The only difference is in the vulnerabilities they exploit, so these checks were added to support the newer exploits and appeared in the older version after recompilation.
The launcher is responsible for orchestrating the post-exploitation activities. It also uses the kernel exploit and the interface it provides. However, since the exploit creates special kernel objects during its execution that provide the ability to read and write to kernel memory, the launcher simply reuses these objects without the need to trigger vulnerabilities and go through the entire exploitation path again. The launcher cleans up exploitation artifacts, retrieves the process name for injection from a config with the 0xDEADD00F magic number, injects a stager into the target process, uses it to execute itself, and launches the implant.
This case demonstrates once again the dangers associated with such malicious tools that lie in their potential wide usage. Originally developed for cyber-espionage purposes, this framework is now being used by cybercriminals of a broader kind, placing millions of users with unpatched devices at risk. Given its modular design and ease of reuse, we expect that other threat actors will begin incorporating it into their attacks. We strongly recommend that users install the latest security updates as soon as possible, if they have not already done so.
The vulnerability can be exploited remotely, without authentication, to circumvent existing authentication controls.
The post Critical HPE AOS-CX Vulnerability Allows Admin Password Resets appeared first on SecurityWeek.
In this post, we preview the critical findings of the 2026 Global Threat Intelligence Report, highlighting how the collapse of traditional security silos and the rise of autonomous, machine-speed attacks are forcing a total reimagining of modern defense.
 Table Of Contents

The cybersecurity landscape has reached a point of total convergence, where the silos that once separated malware, identity, and infrastructure have collapsed into a single, high-velocity threat engine. Simultaneously, the threat landscape is shifting from human-led attacks to machine-speed operations as a result of agentic AI, which acts as a force multiplier for the modern adversary.
Flashpoint’s 2026 Global Threat Intelligence Report (GTIR) was developed to anchor security leaders — from threat intelligence and vulnerability management teams to physical security professionals and the CISO’s office — with the data required to navigate this year’s greatest threats, rife with infostealers, vulnerabilities, ransomware, and malicious insiders.
Our report uncovers several staggering metrics that illustrate the industrialization of modern cybercrime:
These findings are derived from Flashpoint’s Primary Source Collection (PSC), a specialized operating model that collects intelligence directly from original sources, driven by an organization’s unique Priority Intelligence Requirements (PIR). The 2026 Global Threat Intelligence Report leverages this ground-truth data to provide a strategic framework for the year ahead. Download to gain:
“As attackers automate exploitation of identity, vulnerabilities, and ransomware, defenders who rely on fragmented visibility will fall behind. To keep pace, organizations must ground their decisions in primary-source intelligence that is drawn from adversarial environments, so that decision-makers can get ahead of this accelerating threat cycle.”
Josh Lefkowitz, CEO & Co-Founder at Flashpoint
Our latest report identifies four driving themes shaping the 2026 threat landscape:

Flashpoint identified a 1,500% rise in AI-related illicit discussions between November and December 2025, signaling a rapid transition from criminal curiosity to the active development of malicious frameworks. Built on data pulled from criminal environments and shaped by fraud use cases, these systems scrape data, adjust messaging for specific targets, rotate infrastructure, and learn from failed attempts without the need for constant human involvement.
“2026 is the era of agentic-based cyberattacks. We’ve seen a 1,500% increase in AI-related illicit discussions in a single month, signaling increased interest in developing malicious frameworks. The discussions evolve into vibe-coded, AI-supported phishing lures, malware, and cybercrime venues. When iteration becomes cheap through automation, attackers can afford to fail repeatedly until they find a successful foothold.”
Ian Gray, Vice President of Cyber Threat Intelligence Operations at Flashpoint
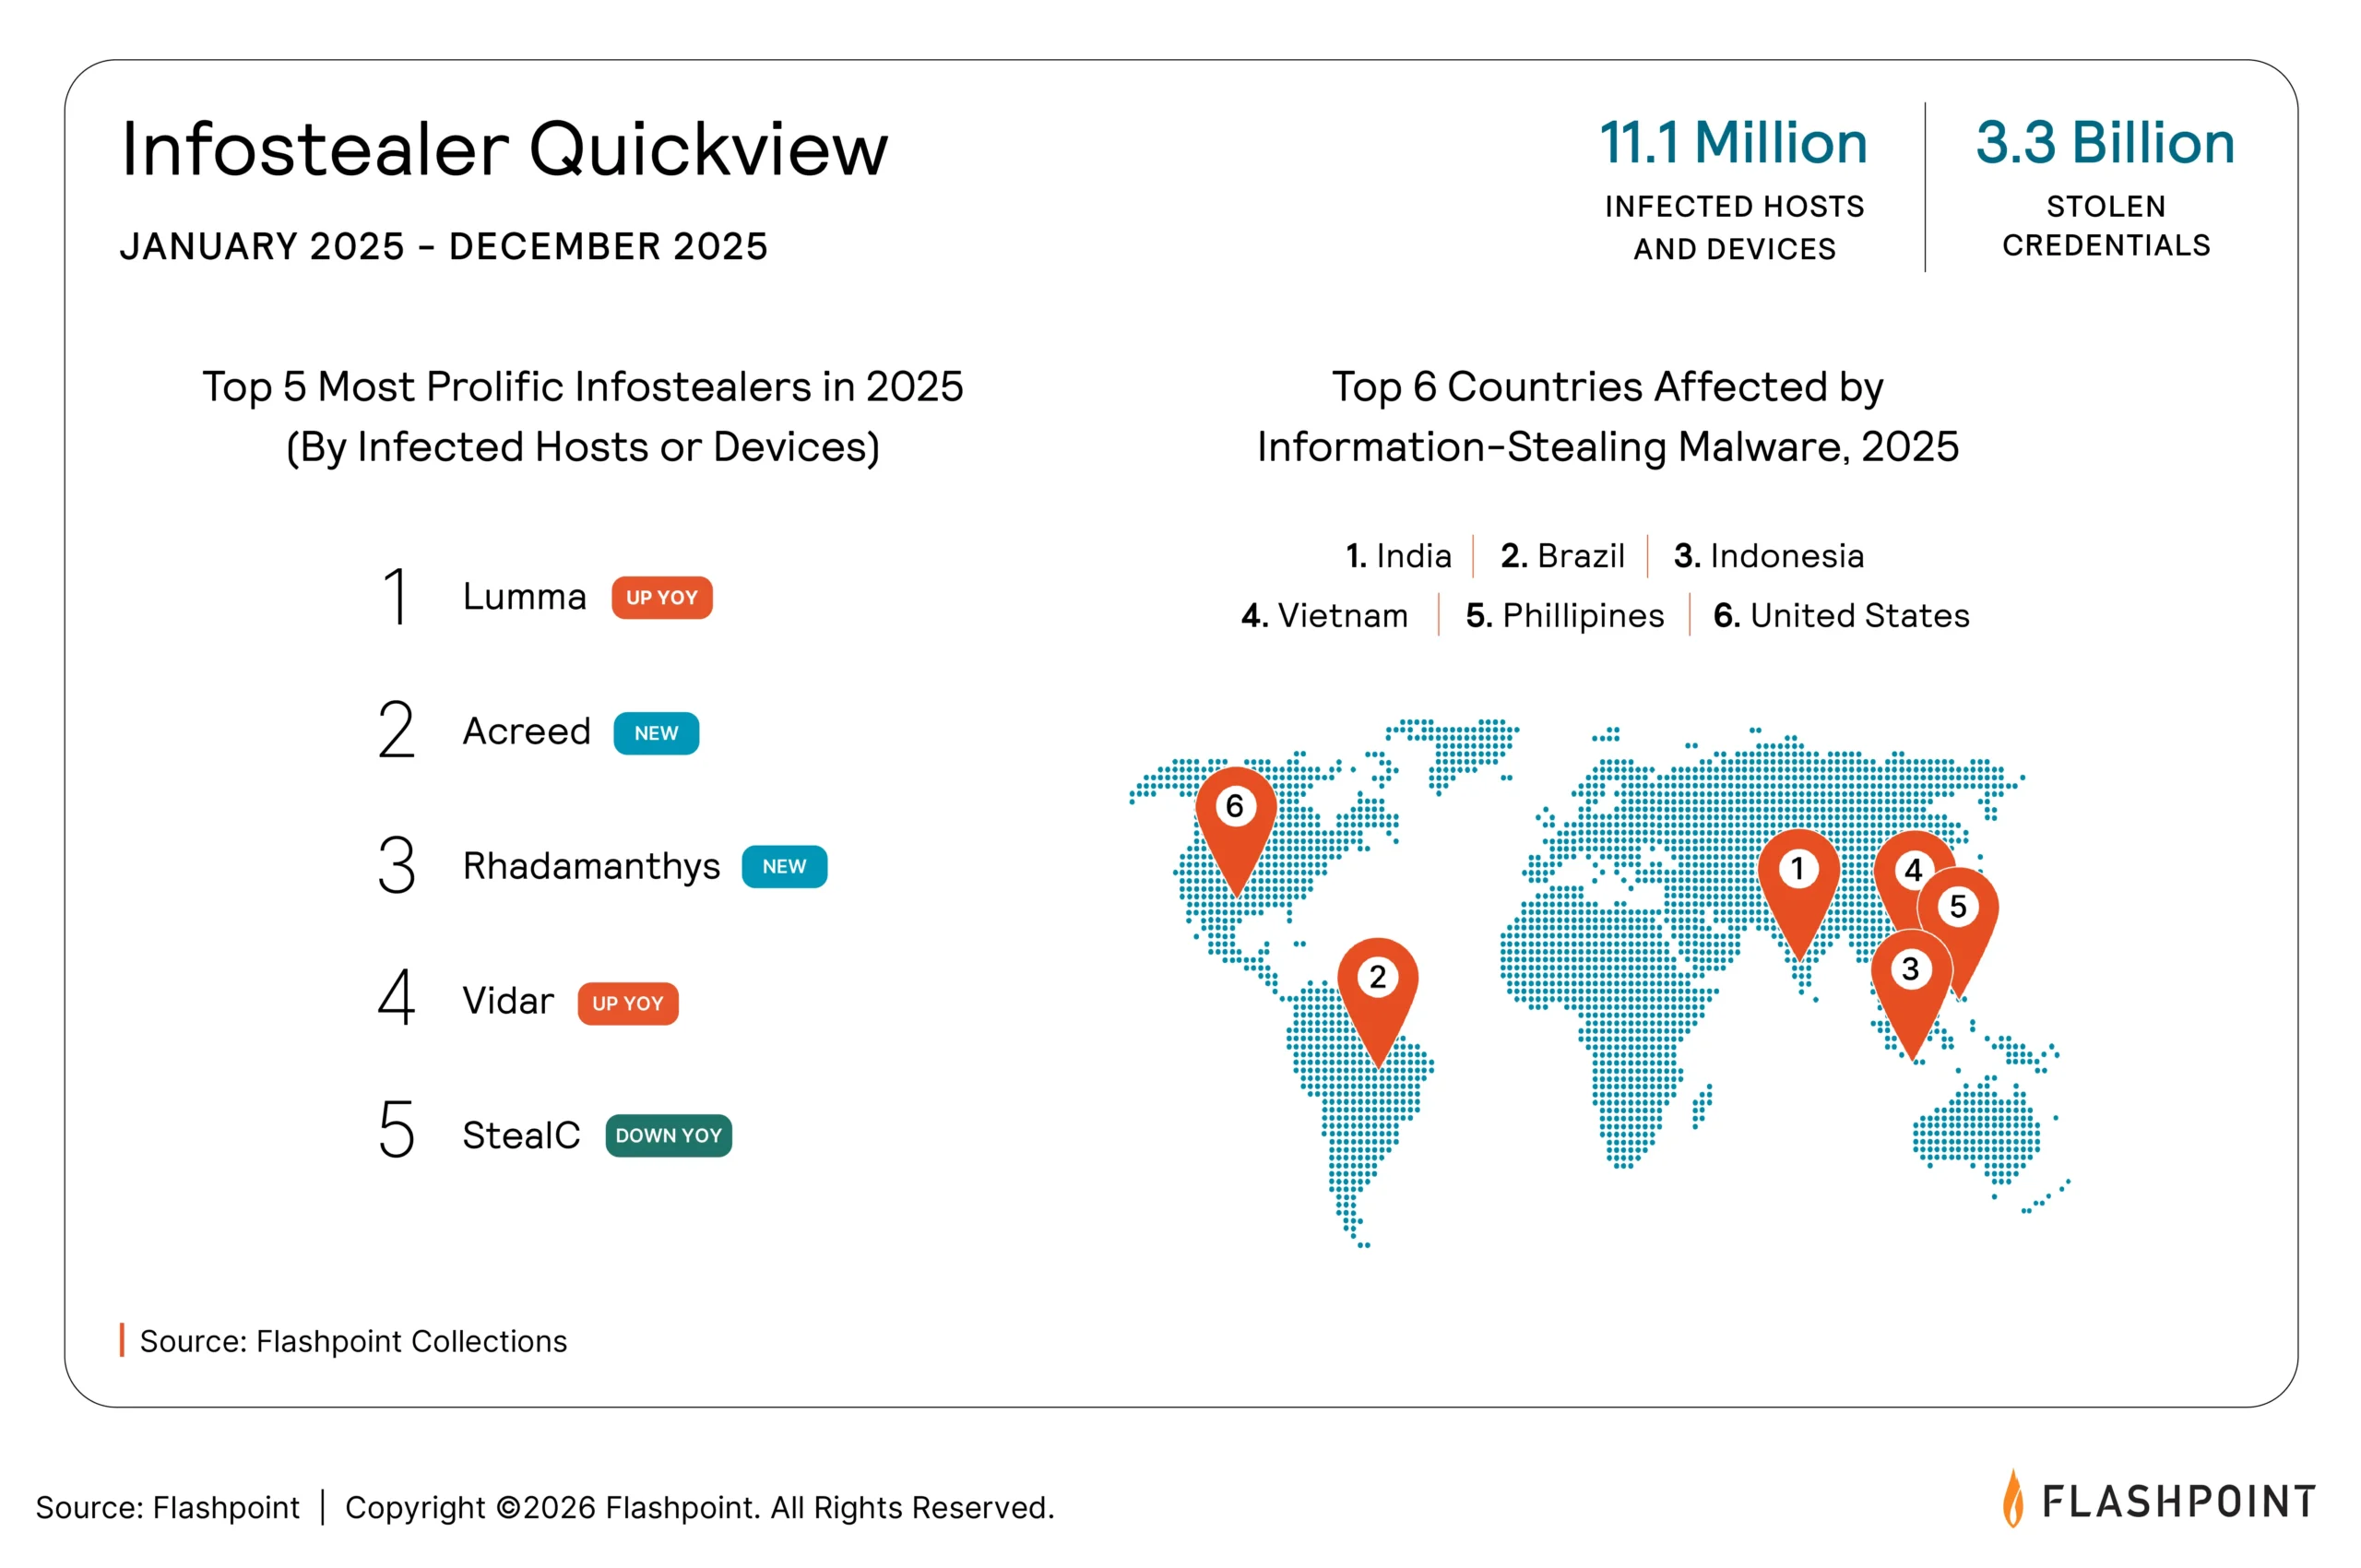
Flashpoint observed over 11.1 million machines infected with infostealers in 2025, fueling a massive inventory of 3.3 billion stolen credentials and cloud tokens. The fundamental mechanics of cybercrime have shifted from breaking in to logging in, as attackers leverage stolen session cookies to behave like legitimate users.
Vulnerability disclosures surged by 12% in 2025, with 1 in 3 (33%) vulnerabilities having publicly available exploit code. The strategic gap between discovery and weaponization is increasingly vanishing, as evidenced by mass exploitation of zero-day vulnerabilities in as little as 24 hours after discovery.
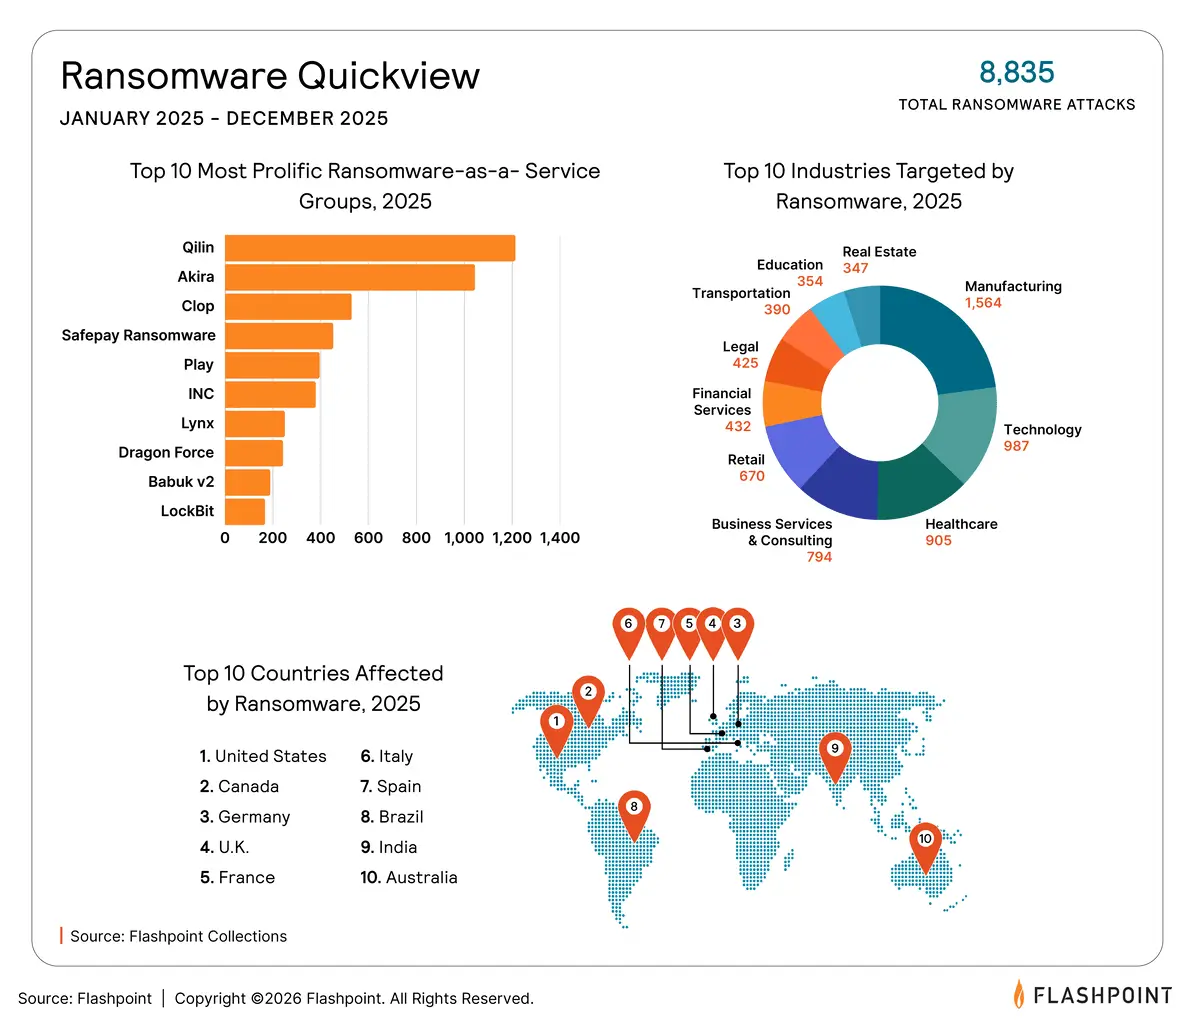
As technical defenses against encryption harden, ransomware groups are pivoting to the path of least resistance: human trust. This approach has led to a 53% increase in ransomware, with RaaS groups being responsible for over 87% of all ransomware attacks.
The findings in the 2026 Global Threat Intelligence Report make one thing clear: incremental improvements to legacy security models are no longer sufficient. As adversaries transition to machine-speed operations, the strategic advantage shifts to organizations that can maintain visibility into the adversarial environments where these attacks are born.
Protecting organizations and communities requires an intelligence-first approach. Download Flashpoint’s 2026 Global Threat Intelligence Report to gain clarity and the data-driven insights needed to safeguard critical assets.
The post Navigating 2026’s Converged Threats: Insights from Flashpoint’s Global Threat Intelligence Report appeared first on Flashpoint.
In this post we examine the mechanics of the CVE-2025-15556 supply-chain attack and provide actionable steps to secure your environment.
 Table Of Contents
The cybersecurity community is still grappling with a sobering realization: one of the most ubiquitous tools in the developer’s toolkit, Notepad++, was hiding a critical vulnerability for over six months. Being so deeply embedded in daily workflows, many organizations did not realize they were vulnerable until a recent security update pulled back the curtain on a sophisticated Chinese state-sponsored campaign, dubbed “Lotus Blossom.”
Investigations have confirmed that the issue wasn’t just a coding error, it was a compromise at the hosting provider level. This means that for much of 2025, even organizations that followed best practices were still potentially open to backdoors from Chinese advanced persistent threat (APT) groups. Here is what you need to know to secure your environment.
The vulnerability, tracked as CVE-2025-15556 (VulnDB ID: 430205), exploits a critical flaw in the Notepad++ updater component, WinGUP. In versions prior to the February 2026 patch, the updater failed to verify the file integrity signatures of downloaded installers.
By exploiting this lack of verification, threat actors are able to:
Leveraging this vulnerability, attackers have gained a persistent presence in high-value sectors. According to reports from Kaspersky, the impact has spanned government and telecommunications, critical infrastructure, and financial services.
The state-sponsored Lotus Blossom campaign was executed in three attack chains, between July and October 2025. Each phase evolved to evade detection by changing file sizes, IP addresses, and delivery methods.
| Phase | Timeline (2025) | Execution Method | Payload |
|---|---|---|---|
| Chain #1 | July – August | 1MB NSIS installer (update.exe) | Multi-stage attack launching a Cobalt Strike beacon via ProShow.exe. |
| Chain #2 | September | 140KB NSIS installer (update.exe) | Rotated C2 URLs to maintain stealth while dropping a Cobalt Strike beacon. |
| Chain #3 | October | Backdoor Deployment | Dropped BluetoothService.exe, log.DLL, and shellcode to establish the Chrysalis backdoor. |
Flashpoint has mapped Lotus Blossom TTPs (tactics, tools, and procedures) to the MITRE ATT&CK framework. Flashpoint analysts have identified the following techniques:
Execution
| Technique Title | ID | Recommendations |
|---|---|---|
| User Execution: Malicious File | T1204.002 | M1040: Behavior Prevention on Endpoint M1038: Execution Prevention M1017: User Training |
| Native API | T1106 | M1040: Behavior Prevention on Endpoint M1038: Execution Prevention |
| Command and Scripting Interpreter: Windows Command Shell | T1059.003 | M1038: Execution Prevention |
Persistence
| Technique Title | ID | Recommendations |
|---|---|---|
| Hijack Execution Flow: DLL | T1574.002 | M1013: Application Developer Guidance M1047: Audit M1038: Execution Prevention M1044: Restrict Library Loading M1051: Update Software |
| Boot or Logon Autostart Execution: Registry Run Keys / Startup Folder | T1547.001 | *MITRE currently does not list any mitigation guidance to combat this attack technique. |
| Create or Modify System Process: Windows Service | T1543.003 | M1047: Audit M1040: Behavior Prevention on Endpoint M1045: Code Signing M1028: Operating System Configuration M1018: User Account Management |
Defense Evasion
| Technique Title | ID | Recommendations |
|---|---|---|
| Masquerading | T1036 | M1049: Antivirus/Antimalware M1047: Audit M1040: Behavior Prevention on Endpoint M1045: Code Signing M1038: Execution Prevention M1022: Restrict File and Directory Permissions M1018: User Account Management M1017: User Training |
| Obfuscated Files or Information | T1027 | M1049: Antivirus/Antimalware M1047: Audit M1040: Behavior Prevention on Endpoint M1017: User Training |
| Obfuscated Files or Information: Dynamic API Resolution | T1027.007 | *MITRE currently does not list any mitigation guidance to combat this attack technique. |
| Deobfuscate/Decode Files or Information | T1140 | *MITRE currently does not list any mitigation guidance to combat this attack technique. |
| Process Injection | T1055 | M1040: Behavior Prevention on Endpoint M1026: Privileged Account Management |
| Reflective Code Loading | T1620 | *MITRE currently does not list any mitigation guidance to combat this attack technique. |
| Execution Guardrails: Mutual Exclusion | T1480.002 | M1055: Do Not Mitigate |
| Indicator Removal: File Deletion | T1070.004 | *MITRE currently does not list any mitigation guidance to combat this attack technique. |
Discovery
| Technique Title | ID | Recommendations |
|---|---|---|
| File and Directory Discovery | T1083 | *MITRE currently does not list any mitigation guidance to combat this attack technique. |
| Ingress Tool Transfer | T1105 | M1031: Network Intrusion Prevention |
Collection
Command and Control
| Technique Title | ID | Recommendations |
|---|---|---|
| Application Layer Protocol: Web Protocols | T1071.001 | M1031: Network Intrusion Prevention |
| Encrypted Channel | T1573 | M1031: Network Intrusion Prevention M1020: SSL/TLS Inspection |
Exfiltration
| Technique Title | ID | Recommendations |
|---|---|---|
| Exfiltration Over C2 Channel | T1041 | M1057: Data Loss Prevention M1031: Network Intrusion Prevention |
Proactive defense requires not only reactive patching of CVE-2025-15556, but also active threat hunting using the TTPs identified by Flashpoint analysts. Flashpoint recommends the following actions:
Software trust is only as strong as the infrastructure behind it. As organizations respond to these recent updates, having best-in-class vulnerability intelligence and direct visibility into threat actor TTPs is the best defense.
Leveraging Flashpoint vulnerability intelligence, organizations can move beyond CVE and NVD, by gaining deeper technical analysis and MITRE ATT&CK mapping to defend against sophisticated threat actors. Request a demo to learn more.
The post What to Know About the Notepad++ Supply-Chain Attack appeared first on Flashpoint.
CVE-2026-1731 is an RCE vulnerability in identity platform BeyondTrust. This flaw allows attackers control of systems without login credentials.
The post VShell and SparkRAT Observed in Exploitation of BeyondTrust Critical Vulnerability (CVE-2026-1731) appeared first on Unit 42.
The bugs could lead to arbitrary code execution, privilege escalation, or authentication rate-limit bypass.
The post Fortinet, Ivanti, Intel Patch High-Severity Vulnerabilities appeared first on SecurityWeek.
The fourth quarter of 2025 went down as one of the most intense periods on record for high-profile, critical vulnerability disclosures, hitting popular libraries and mainstream applications. Several of these vulnerabilities were picked up by attackers and exploited in the wild almost immediately.
In this report, we dive into the statistics on published vulnerabilities and exploits, as well as the known vulnerabilities leveraged with popular C2 frameworks throughout Q4 2025.
This section contains statistics on registered vulnerabilities. The data is taken from cve.org.
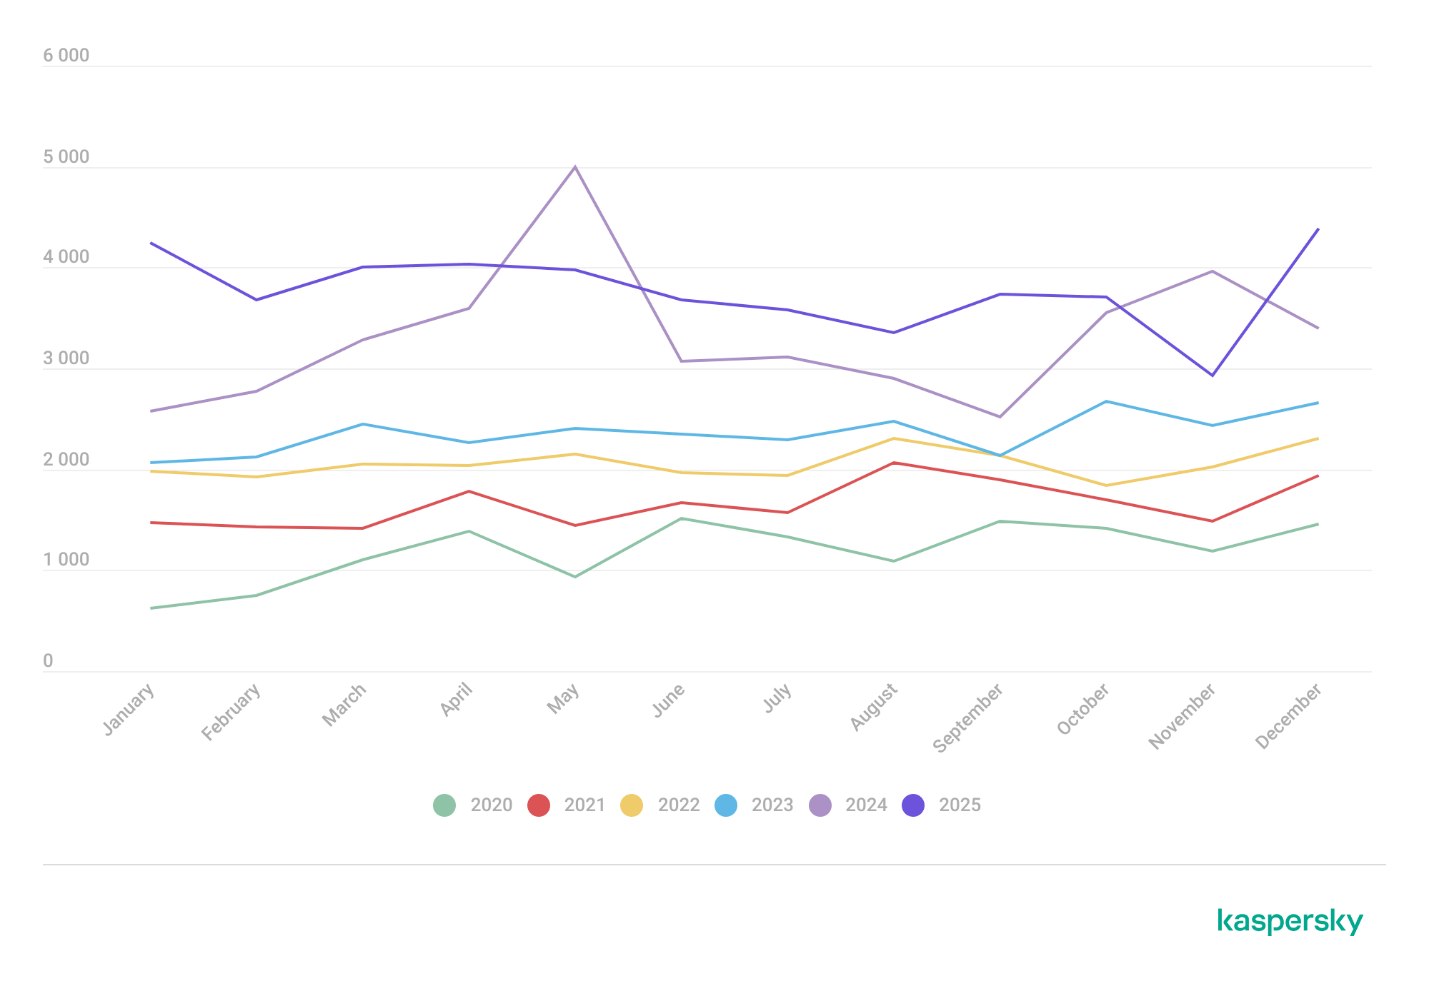
Let’s take a look at the number of registered CVEs for each month over the last five years, up to and including the end of 2025. As predicted in our last report, Q4 saw a higher number of registered vulnerabilities than the same period in 2024, and the year-end totals also cleared the bar set the previous year.
Total published vulnerabilities by month from 2021 through 2025 (download)
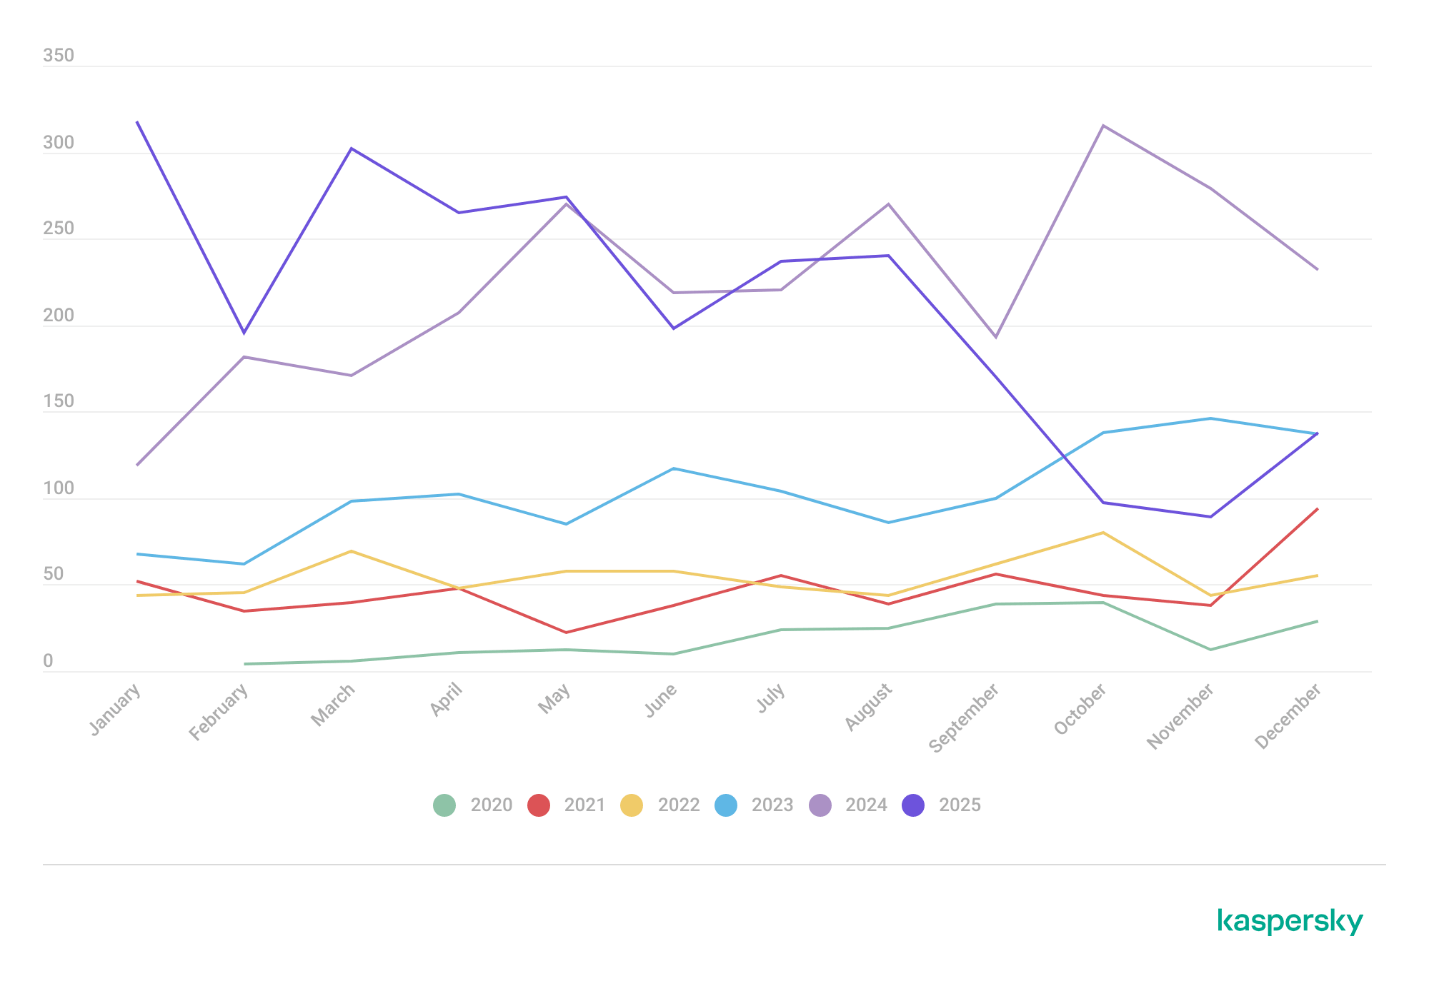
Now, let’s look at the number of new critical vulnerabilities (CVSS > 8.9) for that same period.
Total number of published critical vulnerabilities by month from 2021 to 2025< (download)
The graph shows that the volume of critical vulnerabilities remains quite substantial; however, in the second half of the year, we saw those numbers dip back down to levels seen in 2023. This was due to vulnerability churn: a handful of published security issues were revoked. The widespread adoption of secure development practices and the move toward safer languages also pushed those numbers down, though even that couldn’t stop the overall flood of vulnerabilities.
This section contains statistics on the use of exploits in Q4 2025. The data is based on open sources and our telemetry.
In Q4 2025, the most prevalent exploits targeted the exact same vulnerabilities that dominated the threat landscape throughout the rest of the year. These were exploits targeting Microsoft Office products with unpatched security flaws.
Kaspersky solutions detected the most exploits on the Windows platform for the following vulnerabilities:
The list has remained unchanged for years.
We also see that attackers continue to adapt exploits for directory traversal vulnerabilities (CWE-35) when unpacking archives in WinRAR. They are being heavily leveraged to gain initial access via malicious archives on the Windows operating system:
As in the previous quarter, we see a rise in the use of archiver exploits, with fresh vulnerabilities increasingly appearing in attacks.
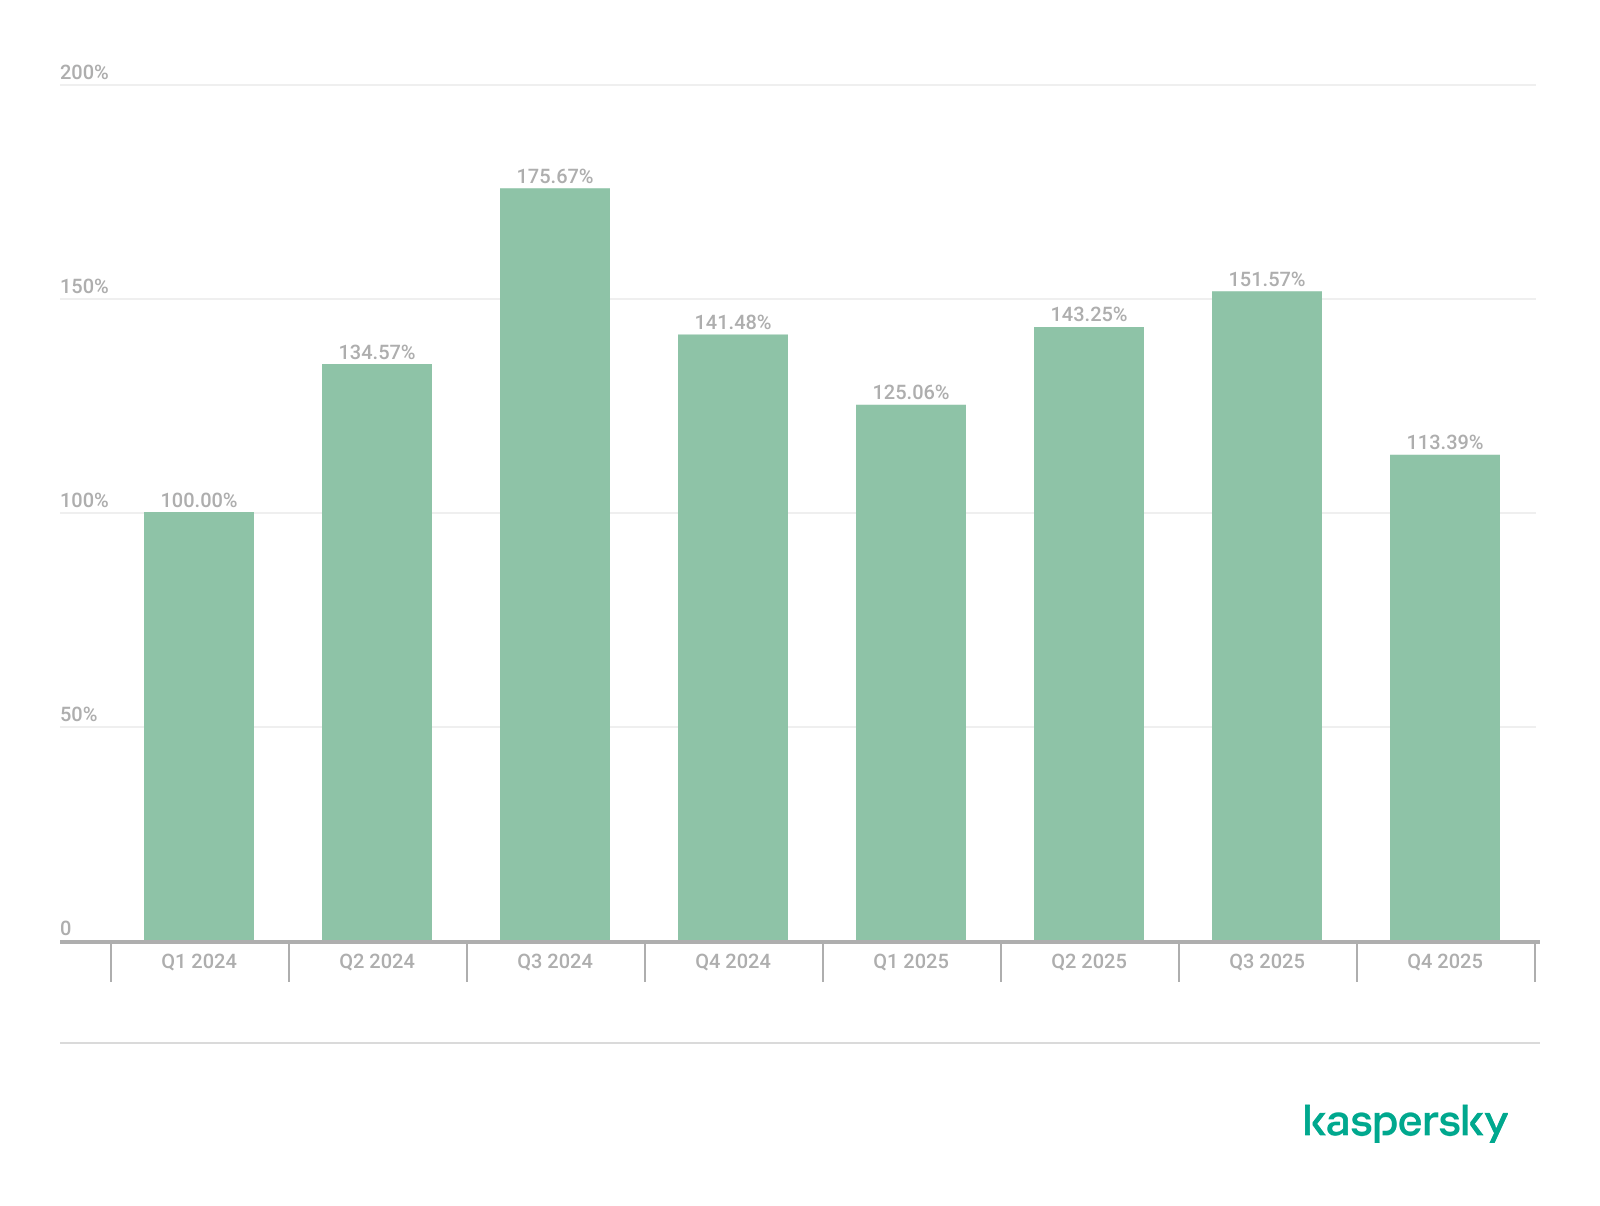
Below are the exploit detection trends for Windows users over the last two years.
Dynamics of the number of Windows users encountering exploits, Q1 2024 – Q4 2025. The number of users who encountered exploits in Q1 2024 is taken as 100% (download)
The vulnerabilities listed here can be used to gain initial access to a vulnerable system. This highlights the critical importance of timely security updates for all affected software.
On Linux-based devices, the most frequently detected exploits targeted the following vulnerabilities:
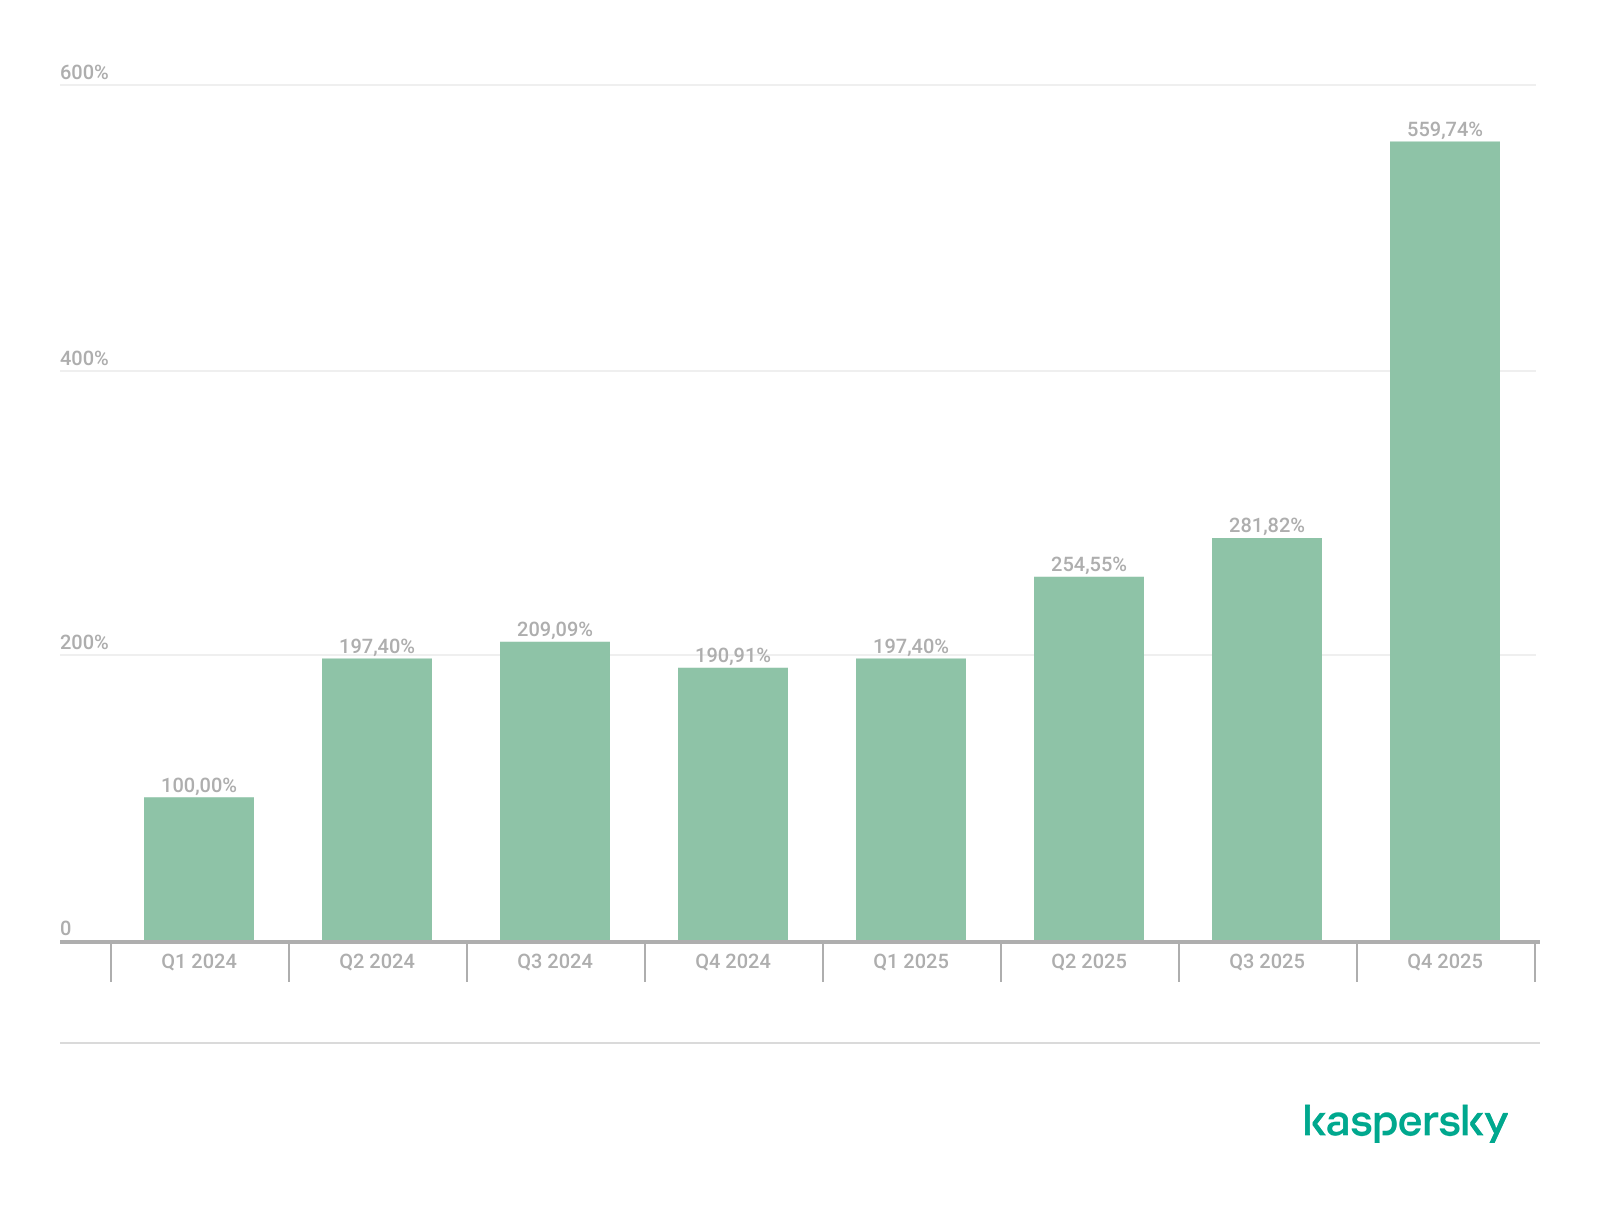
Dynamics of the number of Linux users encountering exploits, Q1 2024 – Q4 2025. The number of users who encountered exploits in Q1 2024 is taken as 100% (download)
We are seeing a massive surge in Linux-based exploit attempts: in Q4, the number of affected users doubled compared to Q3. Our statistics show that the final quarter of the year accounted for more than half of all Linux exploit attacks recorded for the entire year. This surge is primarily driven by the rapidly growing number of Linux-based consumer devices. This trend naturally attracts the attention of threat actors, making the installation of security patches critically important.
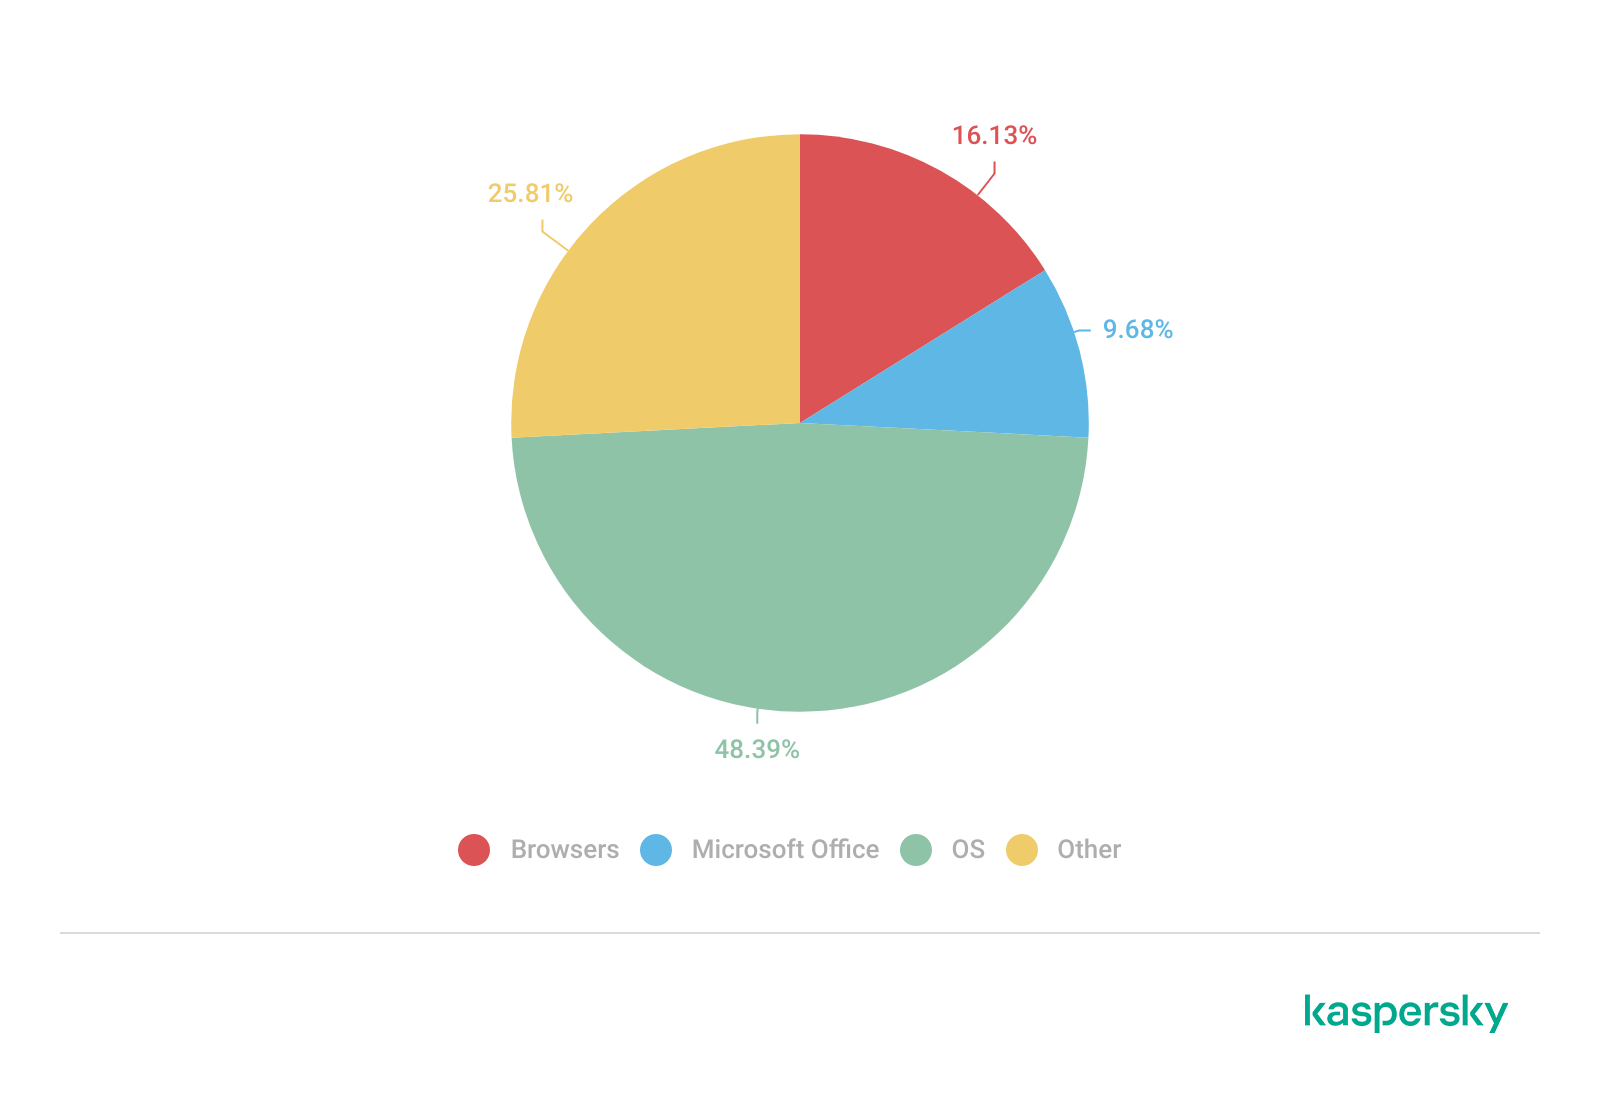
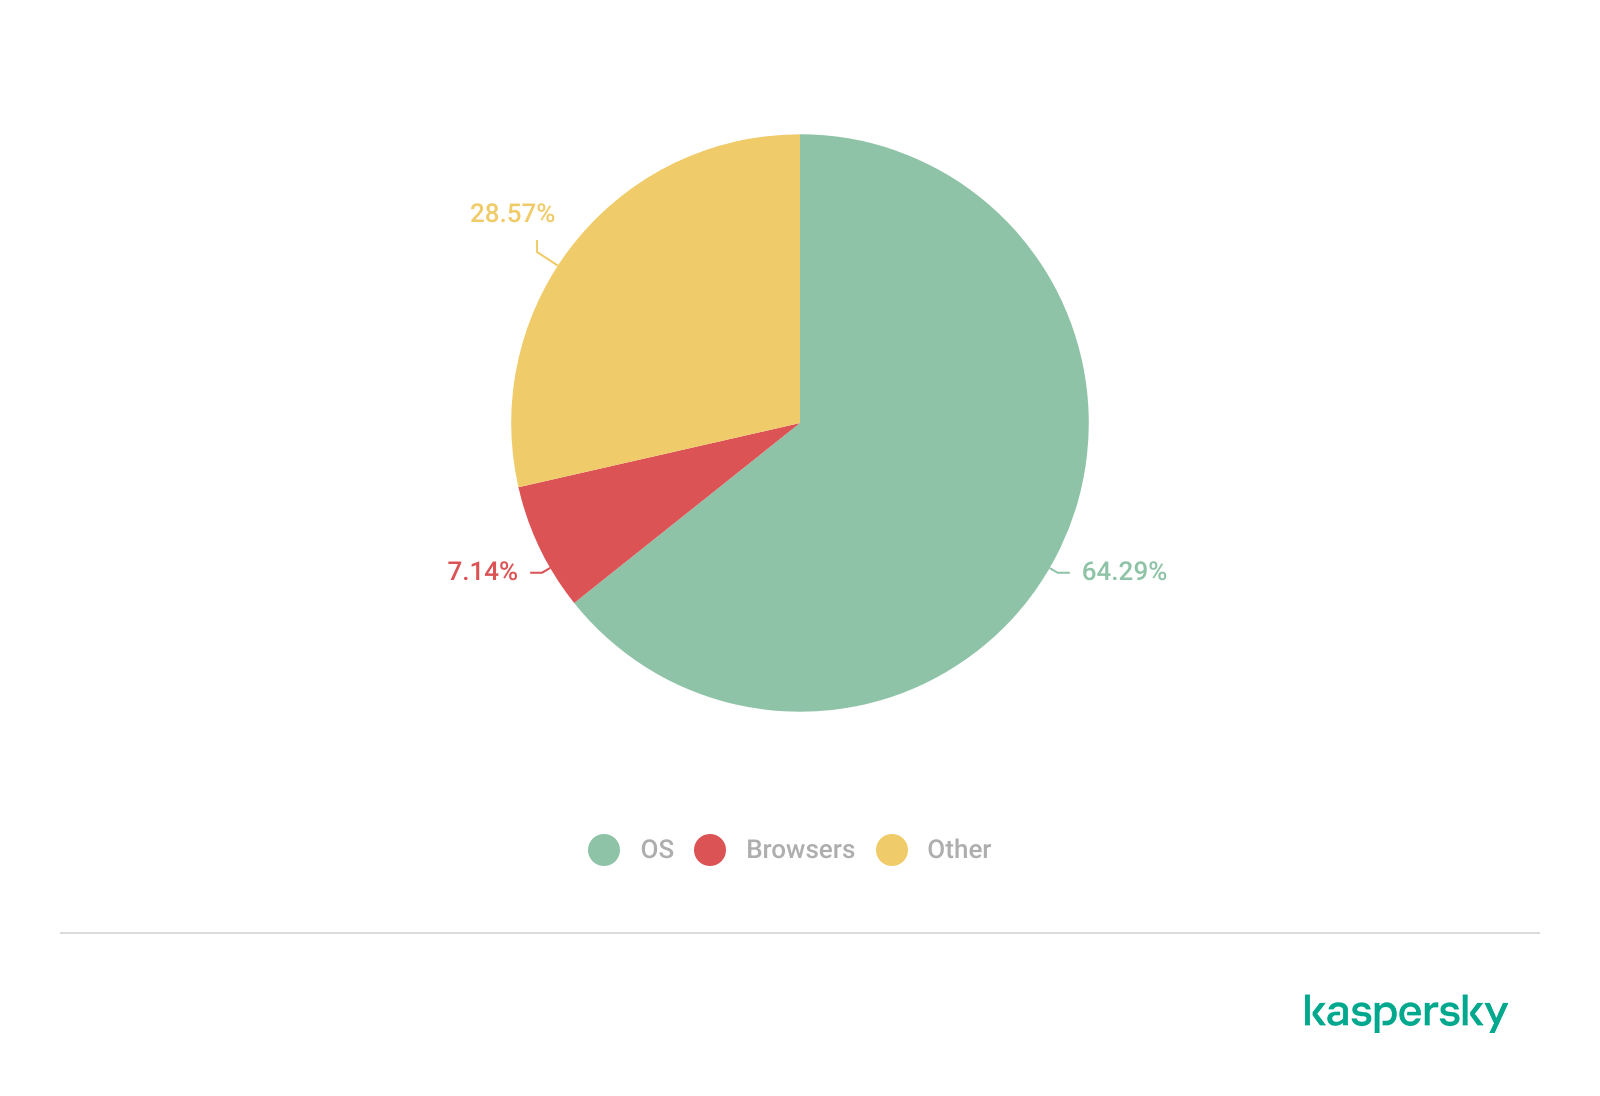
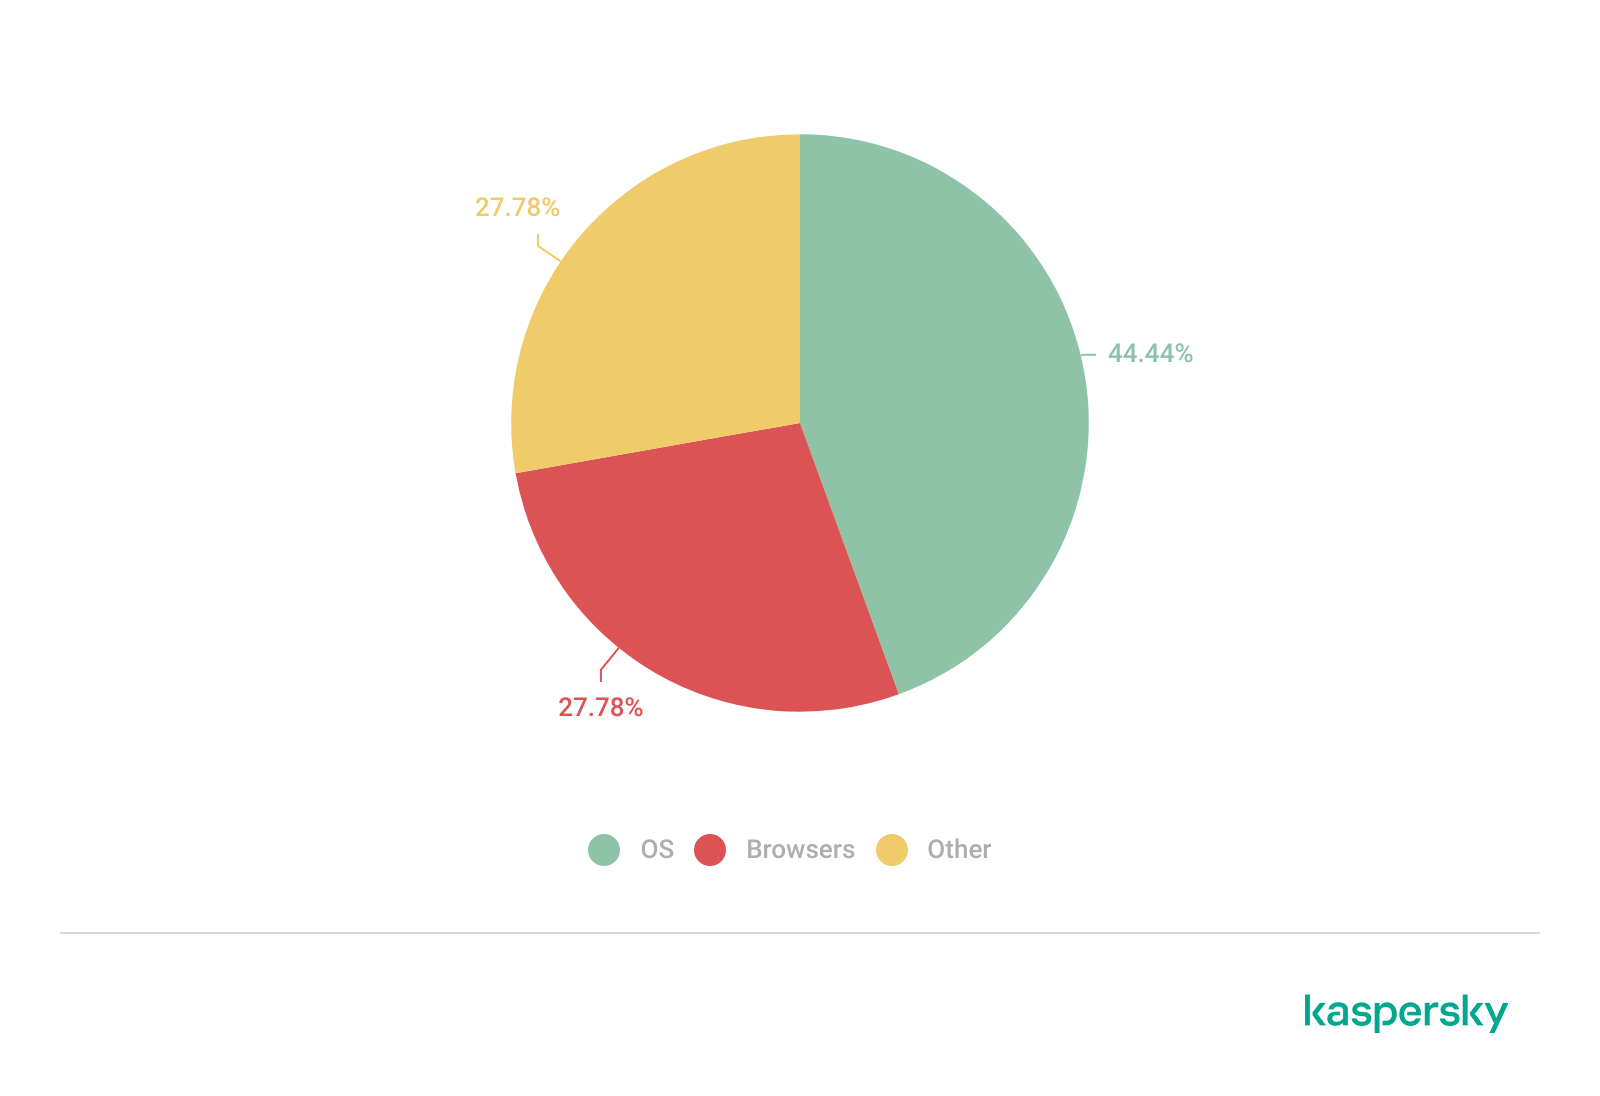
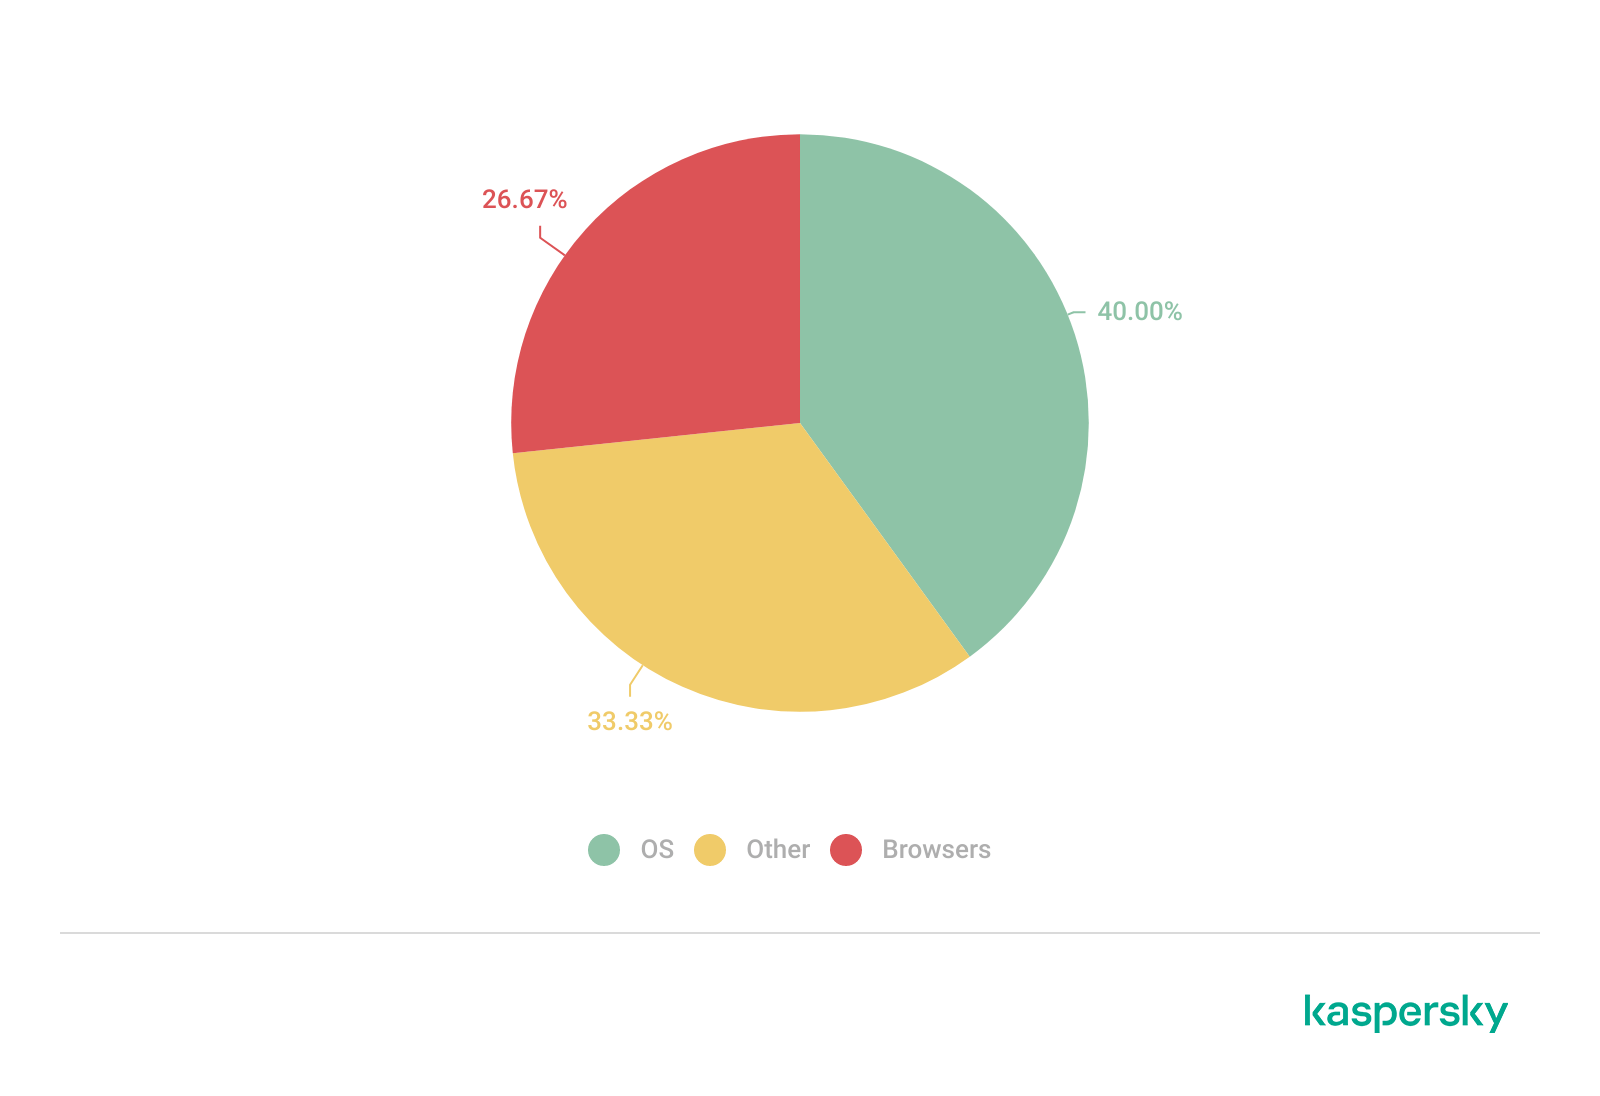
The distribution of published exploits by software type in Q4 2025 largely mirrors the patterns observed in the previous quarter. The majority of exploits we investigate through our monitoring of public research, news, and PoCs continue to target vulnerabilities within operating systems.
Distribution of published exploits by platform, Q1 2025 (download)
Distribution of published exploits by platform, Q2 2025 (download)
Distribution of published exploits by platform, Q3 2025 (download)
Distribution of published exploits by platform, Q4 2025 (download)
In Q4 2025, no public exploits for Microsoft Office products emerged; the bulk of the vulnerabilities were issues discovered in system components. When calculating our statistics, we placed these in the OS category.
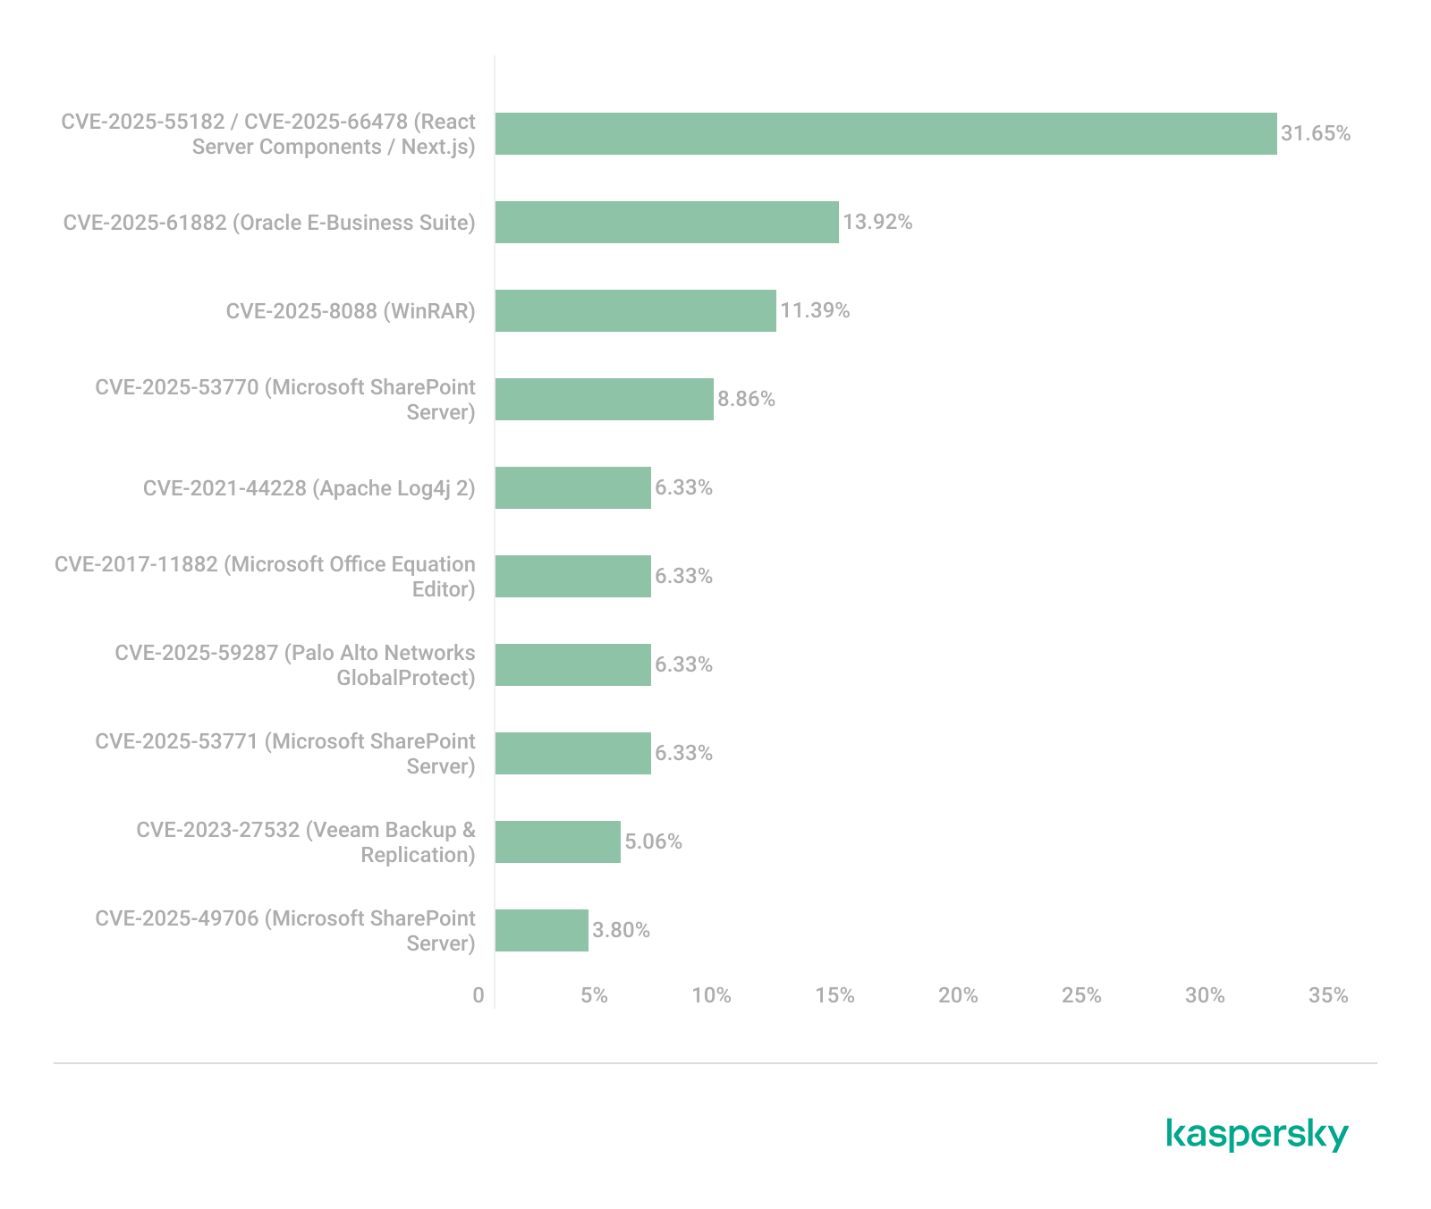
We analyzed which vulnerabilities were utilized in APT attacks during Q4 2025. The following rankings draw on our telemetry, research, and open-source data.
TOP 10 vulnerabilities exploited in APT attacks, Q4 2025 (download)
In Q4 2025, APT attacks most frequently exploited fresh vulnerabilities published within the last six months. We believe that these CVEs will remain favorites among attackers for a long time, as fixing them may require significant structural changes to the vulnerable applications or the user’s system. Often, replacing or updating the affected components requires a significant amount of resources. Consequently, the probability of an attack through such vulnerabilities may persist. Some of these new vulnerabilities are likely to become frequent tools for lateral movement within user infrastructure, as the corresponding security flaws have been discovered in network services that are accessible without authentication. This heavy exploitation of very recently registered vulnerabilities highlights the ability of threat actors to rapidly implement new techniques and adapt old ones for their attacks. Therefore, we strongly recommend applying the security patches provided by vendors.
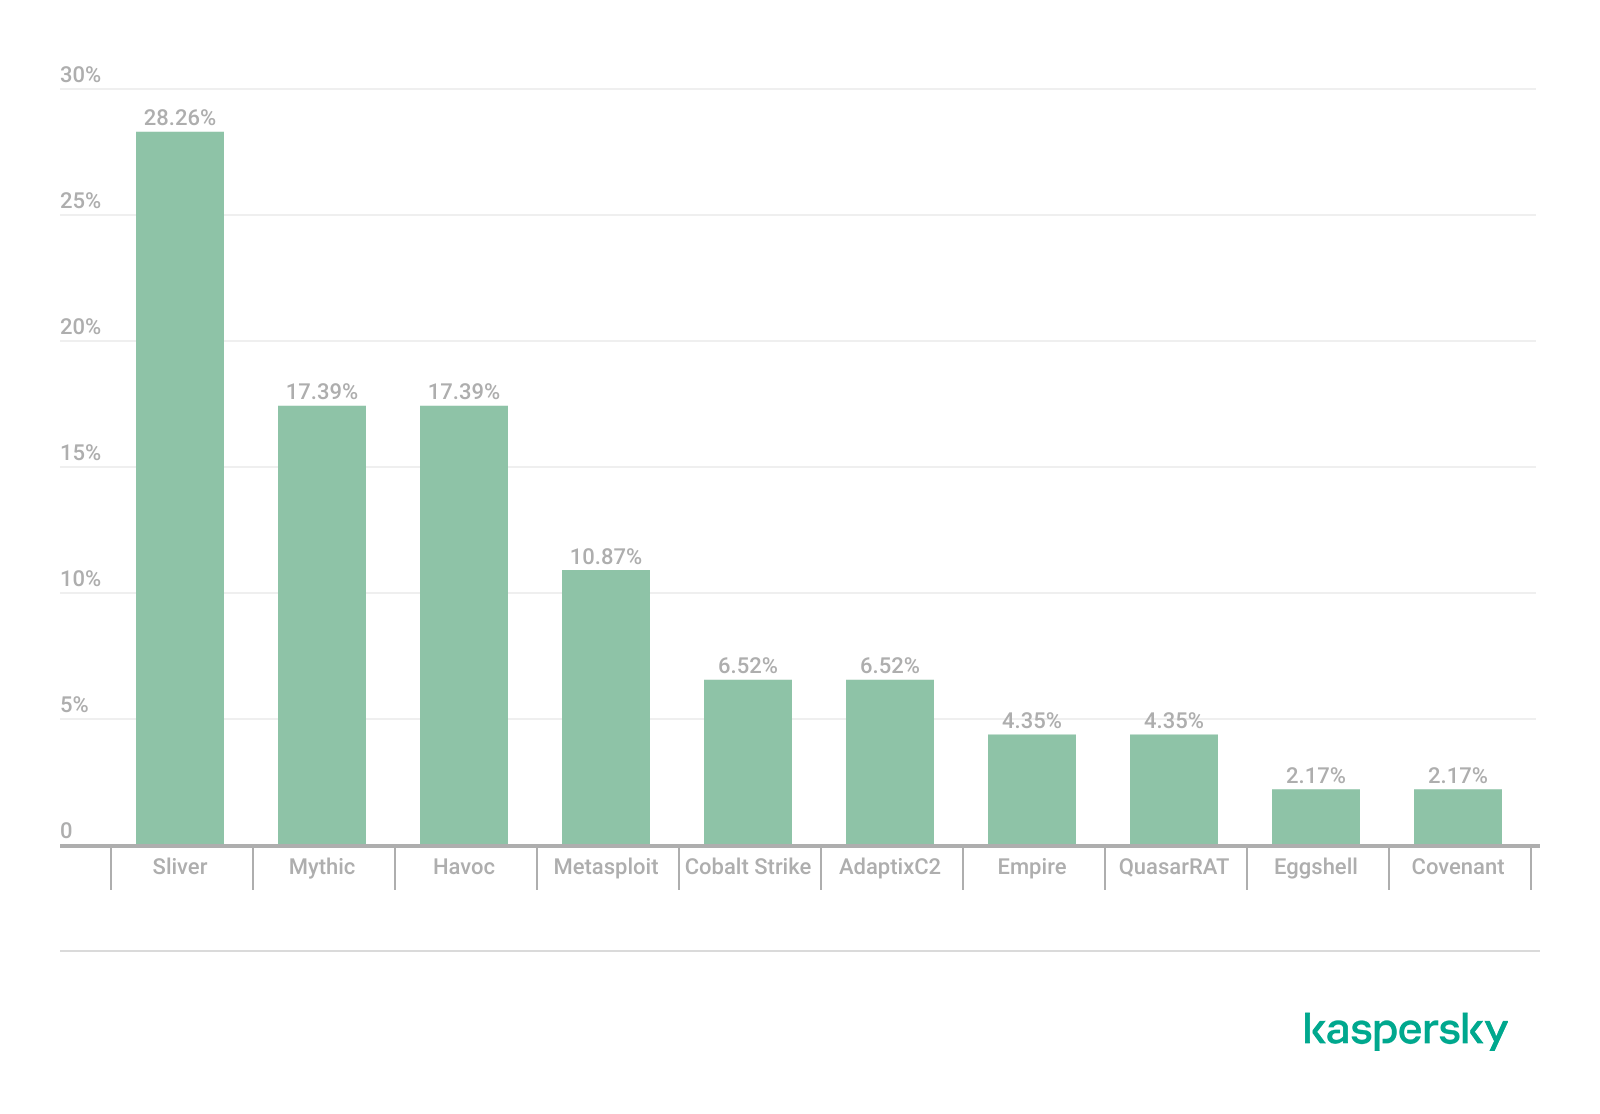
In this section, we will look at the most popular C2 frameworks used by threat actors and analyze the vulnerabilities whose exploits interacted with C2 agents in APT attacks.
The chart below shows the frequency of known C2 framework usage in attacks against users during Q4 2025, according to open sources.
TOP 10 C2 frameworks used by APTs to compromise user systems in Q4 2025 (download)
Despite the significant footprints it can leave when used in its default configuration, Sliver continues to hold the top spot among the most common C2 frameworks in our Q4 2025 analysis. Mythic and Havoc were second and third, respectively. After reviewing open sources and analyzing malicious C2 agent samples that contained exploits, we found that the following vulnerabilities were used in APT attacks involving the C2 frameworks mentioned above:
The set of vulnerabilities described above suggests that attackers have been using them for initial access and early-stage maneuvers in vulnerable systems to create a springboard for deploying a C2 agent. The list of vulnerabilities includes both zero-days and well-known, established security issues.
This section highlights the most noteworthy vulnerabilities that were publicly disclosed in Q4 2025 and have a publicly available description.
We typically describe vulnerabilities affecting a specific application. CVE-2025-55182 stood out as an exception, as it was discovered in React, a library primarily used for building web applications. This means that exploiting the vulnerability could potentially disrupt a vast number of applications that rely on the library. The vulnerability itself lies in the interaction mechanism between the client and server components, which is built on sending serialized objects. If an attacker sends serialized data containing malicious functionality, they can execute JavaScript commands directly on the server, bypassing all client-side request validation. Technical details about this vulnerability and an example of how Kaspersky solutions detect it can be found in our article.
This vulnerability represents a data-handling flaw that occurs when retrieving information from a remote server: when executing the curl or Invoke-WebRequest command, Windows launches Internet Explorer in the background. This can lead to a cross-site scripting (XSS) attack.
This vulnerability reinforces the trend of exploiting security flaws found in file archivers. The core of CVE-2025-11001 lies in the incorrect handling of symbolic links. An attacker can craft an archive so that when it is extracted into an arbitrary directory, its contents end up in the location pointed to by a symbolic link. The likelihood of exploiting this vulnerability is significantly reduced because utilizing such functionality requires the user opening the archive to possess system administrator privileges.
This vulnerability was associated with a wave of misleading news reports claiming it was being used in real-world attacks against end users. This misconception stemmed from an error in the security bulletin.
The year 2025 saw a surge in high-profile vulnerabilities, several of which were significant enough to earn a unique nickname. This was the case with CVE-2025-49844, also known as RediShell, which was unveiled during a hacking competition. This vulnerability is a use-after-free issue related to how the load command functions within Lua interpreter scripts. To execute the attack, an attacker needs to prepare a malicious script and load it into the interpreter.
As with any named vulnerability, RediShell was immediately weaponized by threat actors and spammers, albeit in a somewhat unconventional manner. Because technical details were initially scarce following its disclosure, the internet was flooded with fake PoC exploits and scanners claiming to test for the vulnerability. In the best-case scenario, these tools were non-functional; in the worst, they infected the system. Notably, these fraudulent projects were frequently generated using LLMs. They followed a standardized template and often cross-referenced source code from other identical fake repositories.
Driver vulnerabilities are often discovered in legitimate third-party applications that have been part of the official OS distribution for a long time. Thus, CVE-2025-24990 has existed within code shipped by Microsoft throughout nearly the entire history of Windows. The vulnerable driver has been shipped since at least Windows 7 as a third-party driver for Agere Modem. According to Microsoft, this driver is no longer supported and, following the discovery of the flaw, was removed from the OS distribution entirely.
The vulnerability itself is straightforward: insecure handling of IOCTL codes leading to a null pointer dereference. Successful exploitation can lead to arbitrary command execution or a system crash resulting in a blue screen of death (BSOD) on modern systems.
CVE-2025-59287 represents a textbook case of insecure deserialization. Exploitation is possible without any form of authentication; due to its ease of use, this vulnerability rapidly gained traction among threat actors. Technical details and detection methodologies for our product suite have been covered in our previous advisories.
In Q4 2025, the rate of vulnerability registration has shown no signs of slowing down. Consequently, consistent monitoring and the timely application of security patches have become more critical than ever. To ensure resilient defense, it is vital to regularly assess and remediate known vulnerabilities while implementing technology designed to mitigate the impact of potential exploits.
Continuous monitoring of infrastructure, including the network perimeter, allows for the timely identification of threats and prevents them from escalating. Effective security also demands tracking the current threat landscape and applying preventative measures to minimize risks associated with system flaws. Kaspersky Next serves as a reliable partner in this process, providing real-time identification and detailed mapping of vulnerabilities within the environment.
Securing the workplace remains a top priority. Protecting corporate devices requires the adoption of solutions capable of blocking malware and preventing it from spreading. Beyond basic measures, organizations should implement adaptive systems that allow for the rapid deployment of security updates and the automation of patch management workflows.
The fourth quarter of 2025 went down as one of the most intense periods on record for high-profile, critical vulnerability disclosures, hitting popular libraries and mainstream applications. Several of these vulnerabilities were picked up by attackers and exploited in the wild almost immediately.
In this report, we dive into the statistics on published vulnerabilities and exploits, as well as the known vulnerabilities leveraged with popular C2 frameworks throughout Q4 2025.
This section contains statistics on registered vulnerabilities. The data is taken from cve.org.
Let’s take a look at the number of registered CVEs for each month over the last five years, up to and including the end of 2025. As predicted in our last report, Q4 saw a higher number of registered vulnerabilities than the same period in 2024, and the year-end totals also cleared the bar set the previous year.
Total published vulnerabilities by month from 2021 through 2025 (download)
Now, let’s look at the number of new critical vulnerabilities (CVSS > 8.9) for that same period.
Total number of published critical vulnerabilities by month from 2021 to 2025< (download)
The graph shows that the volume of critical vulnerabilities remains quite substantial; however, in the second half of the year, we saw those numbers dip back down to levels seen in 2023. This was due to vulnerability churn: a handful of published security issues were revoked. The widespread adoption of secure development practices and the move toward safer languages also pushed those numbers down, though even that couldn’t stop the overall flood of vulnerabilities.
This section contains statistics on the use of exploits in Q4 2025. The data is based on open sources and our telemetry.
In Q4 2025, the most prevalent exploits targeted the exact same vulnerabilities that dominated the threat landscape throughout the rest of the year. These were exploits targeting Microsoft Office products with unpatched security flaws.
Kaspersky solutions detected the most exploits on the Windows platform for the following vulnerabilities:
The list has remained unchanged for years.
We also see that attackers continue to adapt exploits for directory traversal vulnerabilities (CWE-35) when unpacking archives in WinRAR. They are being heavily leveraged to gain initial access via malicious archives on the Windows operating system:
As in the previous quarter, we see a rise in the use of archiver exploits, with fresh vulnerabilities increasingly appearing in attacks.
Below are the exploit detection trends for Windows users over the last two years.
Dynamics of the number of Windows users encountering exploits, Q1 2024 – Q4 2025. The number of users who encountered exploits in Q1 2024 is taken as 100% (download)
The vulnerabilities listed here can be used to gain initial access to a vulnerable system. This highlights the critical importance of timely security updates for all affected software.
On Linux-based devices, the most frequently detected exploits targeted the following vulnerabilities:
Dynamics of the number of Linux users encountering exploits, Q1 2024 – Q4 2025. The number of users who encountered exploits in Q1 2024 is taken as 100% (download)
We are seeing a massive surge in Linux-based exploit attempts: in Q4, the number of affected users doubled compared to Q3. Our statistics show that the final quarter of the year accounted for more than half of all Linux exploit attacks recorded for the entire year. This surge is primarily driven by the rapidly growing number of Linux-based consumer devices. This trend naturally attracts the attention of threat actors, making the installation of security patches critically important.
The distribution of published exploits by software type in Q4 2025 largely mirrors the patterns observed in the previous quarter. The majority of exploits we investigate through our monitoring of public research, news, and PoCs continue to target vulnerabilities within operating systems.
Distribution of published exploits by platform, Q1 2025 (download)
Distribution of published exploits by platform, Q2 2025 (download)
Distribution of published exploits by platform, Q3 2025 (download)
Distribution of published exploits by platform, Q4 2025 (download)
In Q4 2025, no public exploits for Microsoft Office products emerged; the bulk of the vulnerabilities were issues discovered in system components. When calculating our statistics, we placed these in the OS category.
We analyzed which vulnerabilities were utilized in APT attacks during Q4 2025. The following rankings draw on our telemetry, research, and open-source data.
TOP 10 vulnerabilities exploited in APT attacks, Q4 2025 (download)
In Q4 2025, APT attacks most frequently exploited fresh vulnerabilities published within the last six months. We believe that these CVEs will remain favorites among attackers for a long time, as fixing them may require significant structural changes to the vulnerable applications or the user’s system. Often, replacing or updating the affected components requires a significant amount of resources. Consequently, the probability of an attack through such vulnerabilities may persist. Some of these new vulnerabilities are likely to become frequent tools for lateral movement within user infrastructure, as the corresponding security flaws have been discovered in network services that are accessible without authentication. This heavy exploitation of very recently registered vulnerabilities highlights the ability of threat actors to rapidly implement new techniques and adapt old ones for their attacks. Therefore, we strongly recommend applying the security patches provided by vendors.
In this section, we will look at the most popular C2 frameworks used by threat actors and analyze the vulnerabilities whose exploits interacted with C2 agents in APT attacks.
The chart below shows the frequency of known C2 framework usage in attacks against users during Q4 2025, according to open sources.
TOP 10 C2 frameworks used by APTs to compromise user systems in Q4 2025 (download)
Despite the significant footprints it can leave when used in its default configuration, Sliver continues to hold the top spot among the most common C2 frameworks in our Q4 2025 analysis. Mythic and Havoc were second and third, respectively. After reviewing open sources and analyzing malicious C2 agent samples that contained exploits, we found that the following vulnerabilities were used in APT attacks involving the C2 frameworks mentioned above:
The set of vulnerabilities described above suggests that attackers have been using them for initial access and early-stage maneuvers in vulnerable systems to create a springboard for deploying a C2 agent. The list of vulnerabilities includes both zero-days and well-known, established security issues.
This section highlights the most noteworthy vulnerabilities that were publicly disclosed in Q4 2025 and have a publicly available description.
We typically describe vulnerabilities affecting a specific application. CVE-2025-55182 stood out as an exception, as it was discovered in React, a library primarily used for building web applications. This means that exploiting the vulnerability could potentially disrupt a vast number of applications that rely on the library. The vulnerability itself lies in the interaction mechanism between the client and server components, which is built on sending serialized objects. If an attacker sends serialized data containing malicious functionality, they can execute JavaScript commands directly on the server, bypassing all client-side request validation. Technical details about this vulnerability and an example of how Kaspersky solutions detect it can be found in our article.
This vulnerability represents a data-handling flaw that occurs when retrieving information from a remote server: when executing the curl or Invoke-WebRequest command, Windows launches Internet Explorer in the background. This can lead to a cross-site scripting (XSS) attack.
This vulnerability reinforces the trend of exploiting security flaws found in file archivers. The core of CVE-2025-11001 lies in the incorrect handling of symbolic links. An attacker can craft an archive so that when it is extracted into an arbitrary directory, its contents end up in the location pointed to by a symbolic link. The likelihood of exploiting this vulnerability is significantly reduced because utilizing such functionality requires the user opening the archive to possess system administrator privileges.
This vulnerability was associated with a wave of misleading news reports claiming it was being used in real-world attacks against end users. This misconception stemmed from an error in the security bulletin.
The year 2025 saw a surge in high-profile vulnerabilities, several of which were significant enough to earn a unique nickname. This was the case with CVE-2025-49844, also known as RediShell, which was unveiled during a hacking competition. This vulnerability is a use-after-free issue related to how the load command functions within Lua interpreter scripts. To execute the attack, an attacker needs to prepare a malicious script and load it into the interpreter.
As with any named vulnerability, RediShell was immediately weaponized by threat actors and spammers, albeit in a somewhat unconventional manner. Because technical details were initially scarce following its disclosure, the internet was flooded with fake PoC exploits and scanners claiming to test for the vulnerability. In the best-case scenario, these tools were non-functional; in the worst, they infected the system. Notably, these fraudulent projects were frequently generated using LLMs. They followed a standardized template and often cross-referenced source code from other identical fake repositories.
Driver vulnerabilities are often discovered in legitimate third-party applications that have been part of the official OS distribution for a long time. Thus, CVE-2025-24990 has existed within code shipped by Microsoft throughout nearly the entire history of Windows. The vulnerable driver has been shipped since at least Windows 7 as a third-party driver for Agere Modem. According to Microsoft, this driver is no longer supported and, following the discovery of the flaw, was removed from the OS distribution entirely.
The vulnerability itself is straightforward: insecure handling of IOCTL codes leading to a null pointer dereference. Successful exploitation can lead to arbitrary command execution or a system crash resulting in a blue screen of death (BSOD) on modern systems.
CVE-2025-59287 represents a textbook case of insecure deserialization. Exploitation is possible without any form of authentication; due to its ease of use, this vulnerability rapidly gained traction among threat actors. Technical details and detection methodologies for our product suite have been covered in our previous advisories.
In Q4 2025, the rate of vulnerability registration has shown no signs of slowing down. Consequently, consistent monitoring and the timely application of security patches have become more critical than ever. To ensure resilient defense, it is vital to regularly assess and remediate known vulnerabilities while implementing technology designed to mitigate the impact of potential exploits.
Continuous monitoring of infrastructure, including the network perimeter, allows for the timely identification of threats and prevents them from escalating. Effective security also demands tracking the current threat landscape and applying preventative measures to minimize risks associated with system flaws. Kaspersky Next serves as a reliable partner in this process, providing real-time identification and detailed mapping of vulnerabilities within the environment.
Securing the workplace remains a top priority. Protecting corporate devices requires the adoption of solutions capable of blocking malware and preventing it from spreading. Beyond basic measures, organizations should implement adaptive systems that allow for the rapid deployment of security updates and the automation of patch management workflows.
Security researchers have seen the vulnerabilities being exploited to deliver shells, conduct reconnaissance, and download malware.
The post Ivanti Exploitation Surges as Zero-Day Attacks Traced Back to July 2025 appeared first on SecurityWeek.
Novee researchers discovered 16 vulnerabilities in Foxit and Apryse PDF tools that could have been exploited via malicious documents or URLs.
The post Vulnerabilities in Popular PDF Platforms Allowed Account Takeover, Data Exfiltration appeared first on SecurityWeek.
The title of the post is”What AI Security Research Looks Like When It Works,” and I agree:
In the latest OpenSSL security release> on January 27, 2026, twelve new zero-day vulnerabilities (meaning unknown to the maintainers at time of disclosure) were announced. Our AI system is responsible for the original discovery of all twelve, each found and responsibly disclosed to the OpenSSL team during the fall and winter of 2025. Of those, 10 were assigned CVE-2025 identifiers and 2 received CVE-2026 identifiers. Adding the 10 to the three we already found in the Fall 2025 release, AISLE is credited for surfacing 13 of 14 OpenSSL CVEs assigned in 2025, and 15 total across both releases. This is a historically unusual concentration for any single research team, let alone an AI-driven one.
These weren’t trivial findings either. They included CVE-2025-15467, a stack buffer overflow in CMS message parsing that’s potentially remotely exploitable without valid key material, and exploits for which have been quickly developed online. OpenSSL rated it HIGH severity; NIST‘s CVSS v3 score is 9.8 out of 10 (CRITICAL, an extremely rare severity rating for such projects). Three of the bugs had been present since 1998-2000, for over a quarter century having been missed by intense machine and human effort alike. One predated OpenSSL itself, inherited from Eric Young’s original SSLeay implementation in the 1990s. All of this in a codebase that has been fuzzed for millions of CPU-hours and audited extensively for over two decades by teams including Google’s.
In five of the twelve cases, our AI system directly proposed the patches that were accepted into the official release.
AI vulnerability finding is changing cybersecurity, faster than expected. This capability will be used by both offense and defense.
More.
The vulnerability added to CISA’s KEV catalog affects ThreatSonar Anti-Ransomware and it was patched in 2024.
The post CISA: Hackers Exploiting Vulnerability in Product of Taiwan Security Firm TeamT5 appeared first on SecurityWeek.
GTIG and Mandiant said the zero-day tracked as CVE-2026-22769 has been exploited by UNC6201 since at least 2024.
The post Dell RecoverPoint Zero-Day Exploited by Chinese Cyberespionage Group appeared first on SecurityWeek.