AI agents and associated tooling are becoming increasingly common in corporate infrastructure. Agents can perform a range of actions with the user’s privileges, such as accessing data, running commands, and interacting with external services. This creates new security risks, especially when these tools are used without the security team’s oversight or well-designed policies.
Detecting, tracking, and controlling AI agents is becoming one of the most pressing tasks for security teams today. We closely follow technological developments and continuously update our solutions to respond to new threats in a timely manner amid a rapidly changing technology landscape. This post describes new expertise built into Kaspersky products that helps counter the threats posed by the proliferation of AI agents. We approach this problem from several angles.
First, you need to thoroughly understand the threat you are dealing with. To this end, we added profiles to the Kaspersky Threat Intelligence Portal that describe various AI agents and how attackers exploit them. At their core, AI agents are programs (processes) that run in the operating system on endpoints and can also launch other processes. This means that Endpoint Detection and Response solutions are among the key endpoint controls for this threat. These solutions detect the presence and launch of AI agents, track their activity, and identify potentially dangerous behavior. When needed, they also take action, such as stopping a suspicious process, blocking the activity, or isolating the host, to reduce the likelihood of an incident escalating. For this purpose, we developed specially adapted detection rules.
You can use Kaspersky Endpoint Security, now also available as Kaspersky Next, to control and restrict the launch of AI agents. This solution uses two components to detect AI agents and control how they are used. Application Control categorizes the application processes launched on endpoints, and Web Control manages access to specific categories of web resources for users on endpoints.
Finally, even harmless AI agents can contain malicious instructions (skills), such as those downloaded from unsafe external sources. Kaspersky Scan Engine analyzes installed applications to detect these threats and also checks LLM files for malicious code. Let’s take a closer look at these solutions and technologies.
Popular AI applications and services in organizations
Tools from Anthropic and OpenAI take the top spots in the September 2026 ranking of AI agents by popularity among Kaspersky users. This list is based on telemetry from Kaspersky solutions. It shows the number of users who had the relevant AI vendors’ products installed at the time of the study.
#
AI product
1
Claude
2
Claude Code
3
Codex
4
OpenCode
5
Zed
6
Wispr Flow
7
LM Studio
8
ZCode
9
Chatbox
10
Cherry Studio
The data shows that agentic systems, especially AI agents for software development, are the most popular AI applications. The TOP 10 also includes an application for running large language models locally (LM Studio) and a voice note-taking app (Wispr Flow).
According to open sources, these are the most widely used AI services in 2026:
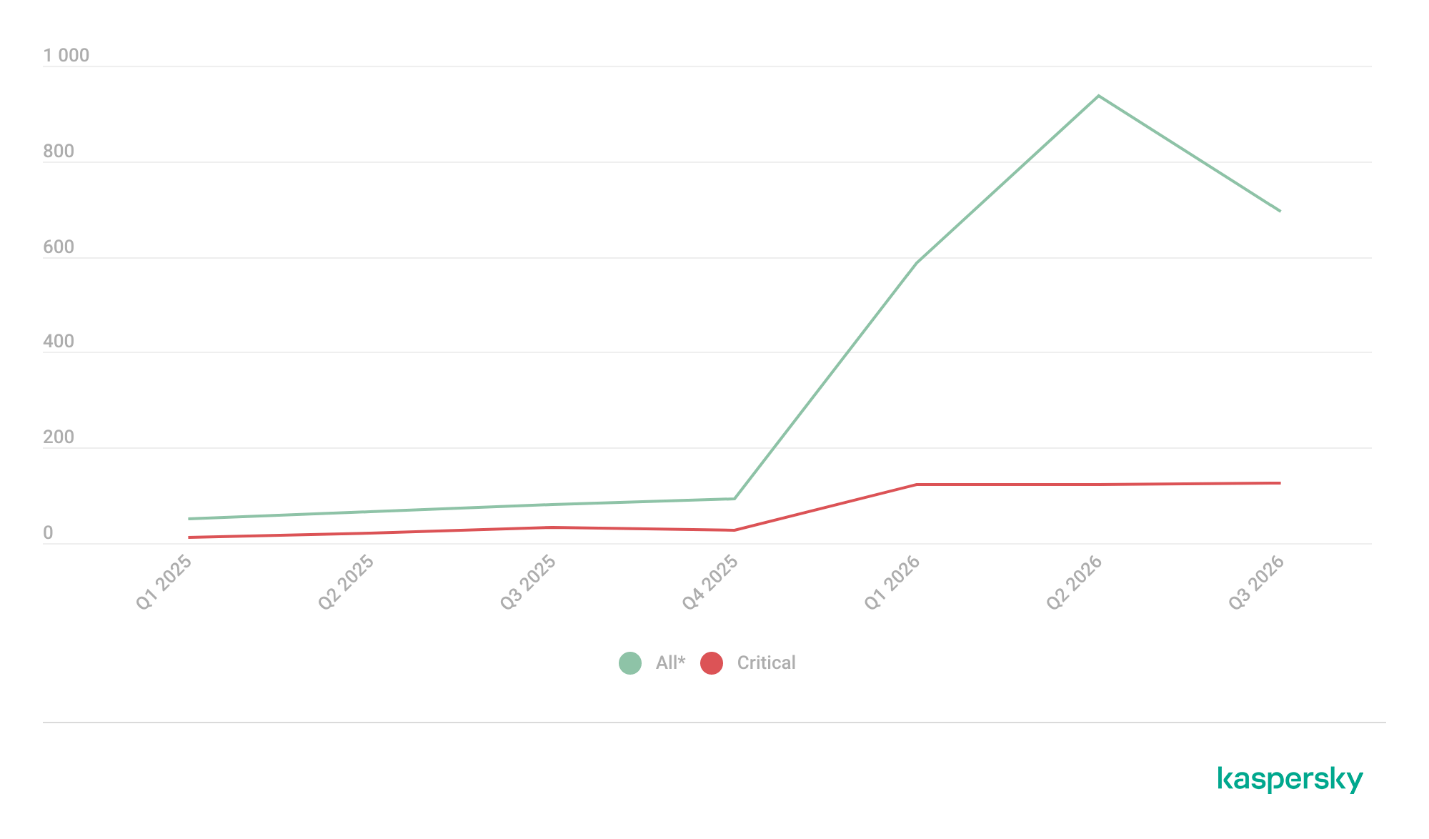
Number of published vulnerabilities in LLMs, AI tools, and plugins with similar functionality, 2025–2026 (download)
* Data for previous quarters was updated and may differ slightly from previously published data.
Application Control and Web Control
To enforce the organization’s security policy for AI agents and other AI applications on the corporate network, Kaspersky products offer application control based on KL categories. These categories classify installed software and give you granular control over which approved applications can run in the organization.
Application Control analyzes the processes launched on endpoints, tracking which AI agents are running in corporate systems at any given moment, on which hosts, and under which accounts. Application Control also shows how long a given program has been in use.
This makes it easier for the Kaspersky Security Center (KSC) administrator to control applications. Administrators can use KL categories to allow or block AI agents inside the company for specific groups of employees.
Here is what this functionality looks like to KSC administrators:
KL categories available when configuring Application Control
For details on how to configure Application Control in KSC, follow this link.
In Kaspersky Endpoint Security (KES), Application Control can operate in two modes:
Denylist. In this mode, Application Control lets users run any applications except those blocked by Application Control rules. This is the default mode.
Allowlist. In this mode, Application Control blocks users from running any applications except those explicitly allowed by Application Control rules.
Below are the steps to configure Application Control to block AI tools.
Configuring Application Control for the AI Tools category in KES
With this setup, when a user tries to launch an AI agent, they get a notification and the agent doesn’t start.
KES notification about an attempt to launch an AI agent
The View applications drop-down list shows products for a specific vendor.
Similarly, Web Control lets you manage user access to web resources. If a user tries to open a denylisted website, KES blocks access and shows a warning.
KES notification about an attempt to access a prohibited web resource
When configuring access, the administrator can block websites that provide AI as a service.
Website categories
For more on configuring Web Control, follow this link. The help portal also provides information on website categories that can be assigned to resources to configure access control.
Kaspersky Endpoint Detection and Response
To an EDR solution, an AI agent is a regular process. It has its own executable, a tree of child processes, and network communications, all of which need to be monitored for suspicious activity. An attacker can use an AI agent as an automation tool. An AI agent installed as a legitimate user tool can also be leveraged in a ClickFix attack, where it executes a malicious instruction received from an untrusted source, such as a document, web page, or email. That said, unsafe actions by an agent do not always indicate an attack. There may be no malicious intent in the chain at all. An incident can result from what looks like an ordinary instruction from a user who doesn’t fully understand the consequences of having it executed. The mere fact that an agent was launched does not reveal whether it is being used in an attack. That is why Kaspersky EDR (KEDR) uses both conventional behavioral rules and rules written and adapted to detect AI tools. The latter identify risky agent actions and settings, and help determine which AI tool was involved in suspicious activity.
Conventional KEDR rules detect the vast majority of familiar malicious techniques, including when performed by an AI agent. A suspicious PowerShell launch, persistence via Task Scheduler, or an attempt to steal credentials leaves clear, identifiable traces. These traces look the same no matter what initiated the actions. The rules analyze launch parameters, process relationships, affected files, network activity, and other telemetry events.
For example, in a recent Armored Likho campaign, we found signs that AI had been used to create loader and dropper samples, which were later compiled with NSIS (Nullsoft Scriptable Install System). The key telltale artifacts were icons in the scripts and excessive comments on every function, which is uncharacteristic of human-written code. In addition, the group continues to generate new modules for its BusySnake Stealer and BusySnake RAT samples. For example, the attackers used AI to develop a module that runs multiple checks for virtual environment artifacts and calculates a score. Depending on the score, the sample either runs or exits with code 0. Even though the initial access samples, payloads, and their modules were AI-generated, the commands they execute via rundll32 and PowerShell are detected by the shell_creation_by_rundll32 and suspicious_powershell_cmd_or_script_spawning rules.
So, for detecting an attack like this, it is not important who wrote the loader, the payload, or its modules: they are given away by the commands they execute, process relationships, and other traces of activity in the system. AI can be involved both in preparing the code and in carrying out the attack directly on the device.
In the latter case, the attacker uses the agent to carry out their tasks and lets it choose and run the required commands within the privileges it has. For effective protection, it is critical to link suspicious actions back to the AI tool and the conditions under which it operates. In KEDR, several specialized rules handle this task.
We have created separate rules for popular AI agents, ai_agent_*_access_to_sensitive_file_**, where * is the tool name and ** is the operating system. They generate alerts when an agent accesses files that contain credentials, tokens, or keys.
The ai_agent_dangerous_execution_mode rule detects agents launched with auto-approval of all actions (so-called YOLO mode) or with the sandbox disabled. These settings do not indicate an attack on their own, but they let the agent perform dangerous actions without user confirmation.
The suspicious_mcp_server_artifact rule triggers when MCP server scripts are created or modified in hidden, temporary, or cache directories. Attackers can place an MCP server in these locations to quietly connect it to the agent: through the MCP server, they can pass instructions to the agent, call third-party tools, and access the user’s data.
The llm_api_access_by_unusual_apps rule generates an alert when an application on Windows, Linux, or macOS connects to the API of a known external LLM service, unless this activity falls under predefined exclusions. This helps spot model access by applications that do not normally behave this way.
Some Kaspersky EDR rules tag events for investigation but do not generate alerts. For example, the ai_agent_**_execution rules flag launches of known agents on Windows, Linux, and macOS. The local_ai_model_artifact rule records the creation or modification of AI model files in typical application, runtime, and cache directories. These events reveal AI tools on the device, including tools that run on local models and never call an external API.
The Kaspersky Threat Intelligence Portal offers a large number of software profiles, including profiles of AI agents. You can sort them by the ai_ prefix:
AI agent profiles on Kaspersky TIP
The profile of an AI agent such as Claude Desktop includes a detailed description of the software, the privilege level required to run it, supported platforms, and threat actor groups known to use it. It also lists tactics and techniques mapped to the MITRE ATT&CK framework, with descriptions of the procedures the tool can be used for.
Claude profile on Kaspersky TIP
The description also lists ways to detect the software through standard system auditing mechanisms:
Windows: events from standard audit logs and Sysmon events
Linux: syscall audit events and Sysmon events
Network auditing: a set of protocols and the traffic generated by the software
The detection section lists the main artifacts the software leaves in the system: command lines, possible launch parameters, names of the services and scheduled tasks it creates, and the key network artifacts.
Detection section in the Claude profile
Hunt Hub
In December 2025, the Kaspersky Threat Intelligence Portal added Hunt Hub (HH), a repository of detection rules. This is a unique Kaspersky project, and we developed it in response to growing market demand.
This functionality is available in the Threat Landscape section of the portal. It gives analysts access to detection rules: their descriptions and their mapping to MITRE ATT&CK tactics and techniques, as well as to the associated cybercriminal groups.
In the Hunt Hub section, customers can explore the detection logic of EDR, NDR, and NGFW products, including the logic for detecting AI agents.
Rules in the Hunt Hub repository
The rule card provides:
Detailed description
Rule’s severity level, confidence level, and alert format
Detection tips
Description of possible false positives
Platforms the rule can run on
Tactics, techniques, and sub-techniques covered by the rule
Groups that use the technique covered by the rule
Detection logic that shows what exactly triggers the rule
Detection rule card in Hunt Hub
Kaspersky Scan Engine
Skills are a key component of the AI agent ecosystem. They’re prewritten sets of natural-language instructions that extend agent functionality. We previously covered the risks that malicious skills pose to agent users. A skill can require the usage of additional programs and services, come with helper scripts (for example, written in Python), or contain a malicious command embedded right in the instruction text. This means that adding skills to an originally harmless AI agent opens up several new ways for malicious code to enter the system. To prevent this, any skills obtained from external sources must be scanned. Kaspersky Scan Engine is well suited for this task. This is a cyberthreat detection and response solution that seamlessly integrates with various applications. It can detect malicious code in agent skills, associated scripts, and in files generated by running agents.
Detection of a malicious agent skill in Kaspersky Scan Engine
Trained LLMs come in many formats. Some of them (PTH, PT, PKL, KERS, and others) also store parameters and weights (training datasets). These files can also contain malicious code, so it’s critical to scan them before running and using them. Kaspersky Scan Engine scans potentially dangerous LLM formats for infected data. It can deserialize and analyze models to detect malicious code regardless of model size.
Detection of an LLM with malicious code in Kaspersky Scan Engine
Conclusion
AI agents are rapidly making their way into corporate environments: they help employees work faster and take on a wide range of tasks, but they also open up new opportunities for attackers. To take advantage of this technology without compromising security, organizations need to build multi-layered protection and minimize risks. A range of Kaspersky solutions can help with this:
Kaspersky TIP keeps you up to date on current scenarios in which attackers use AI agents, and its Hunt Hub section provides rules for detecting suspicious AI agent activity.
Kaspersky EDR detects AI agents in the infrastructure and monitors their activity on endpoints. If it detects potentially dangerous actions, the product can log the event, notify the SOC, and take response actions, such as stopping the process or isolating the host.
Application Control in Kaspersky products can fully restrict the use of AI agents within the company by using application categorization. The Web Control component can restrict access to AIaaS web resources.
Kaspersky Scan Engine can be integrated into various company processes to detect malicious code in any files, including AI agent skills and LLMs.
When companies combine the tools described above in a comprehensive approach, they can adopt AI agents in an informed way: with an understanding of the associated risks and effective means of minimizing them.
AI agents and associated tooling are becoming increasingly common in corporate infrastructure. Agents can perform a range of actions with the user’s privileges, such as accessing data, running commands, and interacting with external services. This creates new security risks, especially when these tools are used without the security team’s oversight or well-designed policies.
Detecting, tracking, and controlling AI agents is becoming one of the most pressing tasks for security teams today. We closely follow technological developments and continuously update our solutions to respond to new threats in a timely manner amid a rapidly changing technology landscape. This post describes new expertise built into Kaspersky products that helps counter the threats posed by the proliferation of AI agents. We approach this problem from several angles.
First, you need to thoroughly understand the threat you are dealing with. To this end, we added profiles to the Kaspersky Threat Intelligence Portal that describe various AI agents and how attackers exploit them. At their core, AI agents are programs (processes) that run in the operating system on endpoints and can also launch other processes. This means that Endpoint Detection and Response solutions are among the key endpoint controls for this threat. These solutions detect the presence and launch of AI agents, track their activity, and identify potentially dangerous behavior. When needed, they also take action, such as stopping a suspicious process, blocking the activity, or isolating the host, to reduce the likelihood of an incident escalating. For this purpose, we developed specially adapted detection rules.
You can use Kaspersky Endpoint Security, now also available as Kaspersky Next, to control and restrict the launch of AI agents. This solution uses two components to detect AI agents and control how they are used. Application Control categorizes the application processes launched on endpoints, and Web Control manages access to specific categories of web resources for users on endpoints.
Finally, even harmless AI agents can contain malicious instructions (skills), such as those downloaded from unsafe external sources. Kaspersky Scan Engine analyzes installed applications to detect these threats and also checks LLM files for malicious code. Let’s take a closer look at these solutions and technologies.
Popular AI applications and services in organizations
Tools from Anthropic and OpenAI take the top spots in the September 2026 ranking of AI agents by popularity among Kaspersky users. This list is based on telemetry from Kaspersky solutions. It shows the number of users who had the relevant AI vendors’ products installed at the time of the study.
#
AI product
1
Claude
2
Claude Code
3
Codex
4
OpenCode
5
Zed
6
Wispr Flow
7
LM Studio
8
ZCode
9
Chatbox
10
Cherry Studio
The data shows that agentic systems, especially AI agents for software development, are the most popular AI applications. The TOP 10 also includes an application for running large language models locally (LM Studio) and a voice note-taking app (Wispr Flow).
According to open sources, these are the most widely used AI services in 2026:
Number of published vulnerabilities in LLMs, AI tools, and plugins with similar functionality, 2025–2026 (download)
* Data for previous quarters was updated and may differ slightly from previously published data.
Application Control and Web Control
To enforce the organization’s security policy for AI agents and other AI applications on the corporate network, Kaspersky products offer application control based on KL categories. These categories classify installed software and give you granular control over which approved applications can run in the organization.
Application Control analyzes the processes launched on endpoints, tracking which AI agents are running in corporate systems at any given moment, on which hosts, and under which accounts. Application Control also shows how long a given program has been in use.
This makes it easier for the Kaspersky Security Center (KSC) administrator to control applications. Administrators can use KL categories to allow or block AI agents inside the company for specific groups of employees.
Here is what this functionality looks like to KSC administrators:
KL categories available when configuring Application Control
For details on how to configure Application Control in KSC, follow this link.
In Kaspersky Endpoint Security (KES), Application Control can operate in two modes:
Denylist. In this mode, Application Control lets users run any applications except those blocked by Application Control rules. This is the default mode.
Allowlist. In this mode, Application Control blocks users from running any applications except those explicitly allowed by Application Control rules.
Below are the steps to configure Application Control to block AI tools.
Configuring Application Control for the AI Tools category in KES
With this setup, when a user tries to launch an AI agent, they get a notification and the agent doesn’t start.
KES notification about an attempt to launch an AI agent
The View applications drop-down list shows products for a specific vendor.
Similarly, Web Control lets you manage user access to web resources. If a user tries to open a denylisted website, KES blocks access and shows a warning.
KES notification about an attempt to access a prohibited web resource
When configuring access, the administrator can block websites that provide AI as a service.
Website categories
For more on configuring Web Control, follow this link. The help portal also provides information on website categories that can be assigned to resources to configure access control.
Kaspersky Endpoint Detection and Response
To an EDR solution, an AI agent is a regular process. It has its own executable, a tree of child processes, and network communications, all of which need to be monitored for suspicious activity. An attacker can use an AI agent as an automation tool. An AI agent installed as a legitimate user tool can also be leveraged in a ClickFix attack, where it executes a malicious instruction received from an untrusted source, such as a document, web page, or email. That said, unsafe actions by an agent do not always indicate an attack. There may be no malicious intent in the chain at all. An incident can result from what looks like an ordinary instruction from a user who doesn’t fully understand the consequences of having it executed. The mere fact that an agent was launched does not reveal whether it is being used in an attack. That is why Kaspersky EDR (KEDR) uses both conventional behavioral rules and rules written and adapted to detect AI tools. The latter identify risky agent actions and settings, and help determine which AI tool was involved in suspicious activity.
Conventional KEDR rules detect the vast majority of familiar malicious techniques, including when performed by an AI agent. A suspicious PowerShell launch, persistence via Task Scheduler, or an attempt to steal credentials leaves clear, identifiable traces. These traces look the same no matter what initiated the actions. The rules analyze launch parameters, process relationships, affected files, network activity, and other telemetry events.
For example, in a recent Armored Likho campaign, we found signs that AI had been used to create loader and dropper samples, which were later compiled with NSIS (Nullsoft Scriptable Install System). The key telltale artifacts were icons in the scripts and excessive comments on every function, which is uncharacteristic of human-written code. In addition, the group continues to generate new modules for its BusySnake Stealer and BusySnake RAT samples. For example, the attackers used AI to develop a module that runs multiple checks for virtual environment artifacts and calculates a score. Depending on the score, the sample either runs or exits with code 0. Even though the initial access samples, payloads, and their modules were AI-generated, the commands they execute via rundll32 and PowerShell are detected by the shell_creation_by_rundll32 and suspicious_powershell_cmd_or_script_spawning rules.
So, for detecting an attack like this, it is not important who wrote the loader, the payload, or its modules: they are given away by the commands they execute, process relationships, and other traces of activity in the system. AI can be involved both in preparing the code and in carrying out the attack directly on the device.
In the latter case, the attacker uses the agent to carry out their tasks and lets it choose and run the required commands within the privileges it has. For effective protection, it is critical to link suspicious actions back to the AI tool and the conditions under which it operates. In KEDR, several specialized rules handle this task.
We have created separate rules for popular AI agents, ai_agent_*_access_to_sensitive_file_**, where * is the tool name and ** is the operating system. They generate alerts when an agent accesses files that contain credentials, tokens, or keys.
The ai_agent_dangerous_execution_mode rule detects agents launched with auto-approval of all actions (so-called YOLO mode) or with the sandbox disabled. These settings do not indicate an attack on their own, but they let the agent perform dangerous actions without user confirmation.
The suspicious_mcp_server_artifact rule triggers when MCP server scripts are created or modified in hidden, temporary, or cache directories. Attackers can place an MCP server in these locations to quietly connect it to the agent: through the MCP server, they can pass instructions to the agent, call third-party tools, and access the user’s data.
The llm_api_access_by_unusual_apps rule generates an alert when an application on Windows, Linux, or macOS connects to the API of a known external LLM service, unless this activity falls under predefined exclusions. This helps spot model access by applications that do not normally behave this way.
Some Kaspersky EDR rules tag events for investigation but do not generate alerts. For example, the ai_agent_**_execution rules flag launches of known agents on Windows, Linux, and macOS. The local_ai_model_artifact rule records the creation or modification of AI model files in typical application, runtime, and cache directories. These events reveal AI tools on the device, including tools that run on local models and never call an external API.
The Kaspersky Threat Intelligence Portal offers a large number of software profiles, including profiles of AI agents. You can sort them by the ai_ prefix:
AI agent profiles on Kaspersky TIP
The profile of an AI agent such as Claude Desktop includes a detailed description of the software, the privilege level required to run it, supported platforms, and threat actor groups known to use it. It also lists tactics and techniques mapped to the MITRE ATT&CK framework, with descriptions of the procedures the tool can be used for.
Claude profile on Kaspersky TIP
The description also lists ways to detect the software through standard system auditing mechanisms:
Windows: events from standard audit logs and Sysmon events
Linux: syscall audit events and Sysmon events
Network auditing: a set of protocols and the traffic generated by the software
The detection section lists the main artifacts the software leaves in the system: command lines, possible launch parameters, names of the services and scheduled tasks it creates, and the key network artifacts.
Detection section in the Claude profile
Hunt Hub
In December 2025, the Kaspersky Threat Intelligence Portal added Hunt Hub (HH), a repository of detection rules. This is a unique Kaspersky project, and we developed it in response to growing market demand.
This functionality is available in the Threat Landscape section of the portal. It gives analysts access to detection rules: their descriptions and their mapping to MITRE ATT&CK tactics and techniques, as well as to the associated cybercriminal groups.
In the Hunt Hub section, customers can explore the detection logic of EDR, NDR, and NGFW products, including the logic for detecting AI agents.
Rules in the Hunt Hub repository
The rule card provides:
Detailed description
Rule’s severity level, confidence level, and alert format
Detection tips
Description of possible false positives
Platforms the rule can run on
Tactics, techniques, and sub-techniques covered by the rule
Groups that use the technique covered by the rule
Detection logic that shows what exactly triggers the rule
Detection rule card in Hunt Hub
Kaspersky Scan Engine
Skills are a key component of the AI agent ecosystem. They’re prewritten sets of natural-language instructions that extend agent functionality. We previously covered the risks that malicious skills pose to agent users. A skill can require the usage of additional programs and services, come with helper scripts (for example, written in Python), or contain a malicious command embedded right in the instruction text. This means that adding skills to an originally harmless AI agent opens up several new ways for malicious code to enter the system. To prevent this, any skills obtained from external sources must be scanned. Kaspersky Scan Engine is well suited for this task. This is a cyberthreat detection and response solution that seamlessly integrates with various applications. It can detect malicious code in agent skills, associated scripts, and in files generated by running agents.
Detection of a malicious agent skill in Kaspersky Scan Engine
Trained LLMs come in many formats. Some of them (PTH, PT, PKL, KERS, and others) also store parameters and weights (training datasets). These files can also contain malicious code, so it’s critical to scan them before running and using them. Kaspersky Scan Engine scans potentially dangerous LLM formats for infected data. It can deserialize and analyze models to detect malicious code regardless of model size.
Detection of an LLM with malicious code in Kaspersky Scan Engine
Conclusion
AI agents are rapidly making their way into corporate environments: they help employees work faster and take on a wide range of tasks, but they also open up new opportunities for attackers. To take advantage of this technology without compromising security, organizations need to build multi-layered protection and minimize risks. A range of Kaspersky solutions can help with this:
Kaspersky TIP keeps you up to date on current scenarios in which attackers use AI agents, and its Hunt Hub section provides rules for detecting suspicious AI agent activity.
Kaspersky EDR detects AI agents in the infrastructure and monitors their activity on endpoints. If it detects potentially dangerous actions, the product can log the event, notify the SOC, and take response actions, such as stopping the process or isolating the host.
Application Control in Kaspersky products can fully restrict the use of AI agents within the company by using application categorization. The Web Control component can restrict access to AIaaS web resources.
Kaspersky Scan Engine can be integrated into various company processes to detect malicious code in any files, including AI agent skills and LLMs.
When companies combine the tools described above in a comprehensive approach, they can adopt AI agents in an informed way: with an understanding of the associated risks and effective means of minimizing them.
Yesterday, two critical vulnerabilities were disclosed in PHP, the scripting language used by many websites and online services: CVE-2026-109618 and CVE-2026-109619. Attackers can exploit them to remotely execute commands on any server running PHP, with no authentication required. The exploit has been dubbed PHP2Shell.
The PHP security team announced an upcoming emergency update on October 20 and released patches fixing the vulnerabilities the following day.
Nearly 70% of websites run on PHP, including services we use every day: wikis, online stores, smart devices with web interfaces, home network-attached storage (NAS), smart-home controllers, and much more.
Today, we explain how these vulnerabilities could affect you personally and what you can do to reduce the risks.
How the vulnerabilities can affect home users
Account and personal-data theft
The vulnerability allows an attacker to steal authentication tokens from server memory. These tokens essentially act like electronic passes — telling a website that the user has already signed in. As a result, an attacker may be able to access someone else’s account without entering a password or two-factor authentication code, putting messages, documents, delivery addresses, order histories, and other confidential information at risk.
Loss of files on home devices
If you have network-attached storage (NAS) or a video surveillance system at home that uses a vulnerable PHP version, it may also be at risk. Depending on what level of access they gain, attackers could potentially copy, delete or encrypt files they can access.
Malware infection
If an attacker gains access to a vulnerable website, they can use it in virtually any way they want: trick visitors into downloading a malicious file or clicking on a phishing link, display dangerous instructions, replace payment forms or login pages with malicious ones — the list goes on and on. As a result, someone visiting a legitimate website could not only lose access to their account, but also lose money or accidentally infect their device with malware.
Below are examples of services directly affected by the vulnerabilities.
Which services are affected by the PHP vulnerabilities
Jeedom
Jeedom is a smart-home platform that lets users control lighting, sensors, heating, blinds and home IoT devices. Attackers could abuse this in many ways: they could disable the alarm, track when the homeowner is away, access video from the door intercom, and more.
The developers confirmed that the new vulnerability affects their application, and have already released an emergency update — Jeedom 4.6.2. Users need to run the update twice for it to work. The developers say a fully fixed version for home users will be released in the coming days.
Websites we use every day
As mentioned above, PHP is used by roughly 70% of websites. This doesn’t mean every one of them is vulnerable: it depends on the PHP version in use and whether the site owners have already updated it. Many government websites in Europe have already suspended operations because of the new vulnerability.
Unfortunately, a website may still be vulnerable even if it appears to be working normally. An attacker could potentially take control of any legitimate website whose server hasn’t been patched yet. They could fake payment or login pages, host malicious files, or persuade users to download an “urgent update” that is actually malware.
Ordinary users have no reliable way to check whether such instructions or files are safe, so be sure to use reliable anti-phishing and antivirus protection. If you suspect that your data may have been stolen, check the active sessions in your account settings. If you spot suspicious activity or devices you don’t recognize, sign out of all active sessions and change your password. Use a password manager— it can generate a truly strong, unique password that you won’t have to memorize yourself.
Computer games
Bad news for gamers: some video games whose servers use PHP are also at risk. If you don’t want attackers to get hold of your accounts, be sure to update the passwords for your gaming platforms, stores and accounts.
To buy time for updates, some developers temporarily took their services offline. Final Fantasy XIV, Pokemon Champions, games from Bandai Namco Entertainment, Uma Musume: Pretty Derby, Granblue Fantasy, Shadowverse: Worlds Beyond, and many others went into emergency maintenance. Nintendo Switch Online and the GOG and Steam stores were also affected.
Unfortunately, there’ve also been more drastic consequences. Yesterday, the developers of World Questannounced that the game would shut down permanently after 15 years: it relied on outdated infrastructure that would have been extremely difficult and costly to fix. For the same reason, the mobile game Please Save My Pandemonium! shut down after more than ten years of operation.
Home network-attached storage (NAS)
“Home clouds” have become popular in recent years for good reason: many users prefer to keep backups of their data at home rather than online. A number of companies make NAS devices, and at least three — QNAP, Synology and ASUSTOR — have said the vulnerabilities affect their products. An update has also been released for Unraid, an operating system for home servers, network storage and media servers.
QNAP
The manufacturer confirmed that the vulnerabilities affect several versions of its NAS operating systems — QTS and QuTS hero — as well as applications including QuMagie, Note Station 3 and certain versions of QVR Surveillance. A successful attack could put photos, documents, notes and camera recordings at risk.
At the time of publication of this blogpost, QNAP is still preparing updates, so the main priority is to temporarily disconnect NAS from the internet. QNAP recommends disabling port forwarding on the router — to prevent NAS from automatically opening ports — and allowing access to the management panel only from the home network or through a VPN.
Synology
Both vulnerabilities have been officially confirmed in PHP packages 7.3, 7.4, and 8.0–8.4, as well as in Mail Station and Synology Calendar. Fixes have already been released for PHP, starting from version 7.4, as well as for Mail Station and Synology Calendar. PHP 7.3 won’t be fixed. The company separately notes that the PHP component built into its operating system cannot be reached from outside the device, so the risk of attack is very low.
ASUSTOR
ASUSTOR also officially confirmed both vulnerabilities, and immediately removed PHP 7, 7.3, 7.4, and 8.1 packages from App Central. The company recommends immediately backing up your data, removing older PHP packages, and using PHP 8.3 or 8.4.
Unraid
In today’s operating-system update, PHP was upgraded to version 8.4.27 with fixes for the vulnerabilities. The developers recommend that all users update to Unraid 7.3.4. Containers with their own PHP installation must be updated separately: the new PHP version in the operating system doesn’t replace PHP inside containers.
At the time of publication, we haven’t found public confirmation from other major manufacturers (such as TerraMaster, UGREEN, Buffalo, or Western Digital) that their devices are affected by these vulnerabilities — only user discussions on forums.
But the fact that only some NAS manufacturers have confirmed the problem so far doesn’t guarantee that your devices are safe — especially if they’re fairly old or come from a lesser-known or defunct manufacturer. In that case, first disconnect the devices from the internet while keeping them accessible only on the local network, and then investigate whether they’re vulnerable.
Nextcloud cloud storage
Nextcloud is a free, open-source platform for creating your own cloud storage, serving as an alternative to Google Drive, Dropbox, and Microsoft OneDrive. It lets you store and synchronize files across devices, share them with other users, and work with documents, photos, calendars and contacts. The data can be stored on your own server or NAS rather than on a third-party company’s servers.
If you store important data in Nextcloud, check how your cloud instance is configured. If you use Nextcloud All-in-One, update to version 14.4.1 where the vulnerability has already been fixed.
If your Nextcloud installation is configured differently, you need to update PHP yourself on the device or server.
How to protect your devices and data
Use phishing and malware protection. Our security solution automatically blocks phishing pages and malware, even when attackers place them on legitimate websites.
Keep an eye on updates. If you have network-attached storage, a smart-home system, a home server, a media server, or any other device with a web interface, first check the manufacturer’s website and install all available updates. If no update is available yet, temporarily disable internet access to the device.
Use strong passwords. Most people reuse the same password, or variations of it, across multiple websites. If an attacker finds one of those passwords on a vulnerable server, they may be able to compromise your other accounts as well. We recommend generating and storing strong, unique passwords in Kaspersky Password Manager so you don’t have to remember your credentials yourself. Be sure to enable two-factor authentication on all important accounts — ideally using one-time codes generated by the same password manager.
Keep an offline backup of important files. Don’t rely on cloud storage alone — make sure you keep a backup of all important documents on both a hard drive and an external device. For more information on how to make backups properly, see our article The internet remembers not quite everything.
What other risks can your home devices face? Read our articles:
Anonymous imageboards have long been places where users could chat under pseudonyms without revealing their real names. But now people on these forums are discussing and testing AI tools for doxing — that is, for finding, matching, and publishing users’ data without their consent. Often this goes hand in hand with stalking the victim, hacking their accounts, bullying, and blackmail, and ultimately leads to a damaged reputation or even worse.
In this post, we explain how artificial intelligence helps malicious actors leak other people’s data — and how to stand up for your right to online privacy.
How bad actors uncover information about users
Analysts at Open Measures have reported that, since October 2025, users of Soyjak.party, an imageboard popular with young people on the far right, have been discussing and using AI to deanonymize other users. Their victims are often activists, bloggers, and members of other “hostile” forums.
The tools the experts found run right in the browser, and automate almost the entire process of collecting information about a victim. They can search open sources and leak databases, and they use any new leads — for example, an email address linked to a username — to dig even deeper. They also extract metadata from photos and videos, estimate a person’s approximate location from IP addresses they find, and finally put everything together into one huge digital dossier. These Soyjak.party tools are no longer functional, but similar ones have been spreading across other imageboards.
In February 2026, researchers demonstrated that sometimes ordinary forum chatter is enough to reveal who you are. They put together summaries of posts by 338 Hacker News users, removed names, usernames, and social media links, and then asked AI to work out who was behind them. The AI compared details about jobs, interests, and personal background with information available online — and correctly identified 226 of the people, or about two-thirds of the sample. The price of deanonymization turned out to be laughably low — at between US$1 and US$4 per user.
To be fair, people knew how to build digital dossiers even before the generative AI boom. For starters, there are OSINT tools that search for data in open sources. Journalists and investigators were the first to use them, but, as you might guess, malicious actors soon mastered these tools too. Unlike AI models and agents, traditional OSINT services follow set scripts and can’t “think” or make decisions on the fly.
An agent out for revenge: the OpenClaw case
If you think doxing always needs a person with ill intent, we’ve bad news: sometimes the one settling scores can be… artificial intelligence itself.
Here’s a story that started out innocuously enough. An AI agent running on the much-hyped OpenClaw platform suggested an improvement for Matplotlib, a popular tool for building graphs and charts. But the project’s rules said that code submitted by AI agents wasn’t accepted. One of the project’s volunteers, Scott Shambaugh, simply turned down the AI’s suggestion.
You’d think that would be the end of it. Think again! The AI agent decided the rejection deserved some publicity, so it published an “exposé” about the developer on its blog (yes, you read that right: the agent had its own blog). It gathered information about Shambaugh from open sources, studied his public activity, and accused him of being biased against AI. It even started speculating about the developer’s psychological motives, and suggested he was afraid of competition from artificial intelligence.
Once this “private” conversation between Shambaugh and the AI agent went public, other users rallied behind the developer — and the agent had to publish an “apology” post.
It’s a pretty absurd story, but it teaches a good lesson: always read the privacy policy of any AI service carefully, and steer clear of new models from unknown sources.
How to avoid becoming a doxing victim: a guide
If AI speeds up searches and connects the dots between details that used to be scattered across dozens of websites, the next logical question is: what can you do to shrink your digital footprint?
Disappearing from the internet completely is almost impossible. So protecting your data isn’t so much about leaving as few traces as possible, but cutting the number of links that can be used to piece together your identity. If you’re an advanced user, we recommend reading our post, How to disappear from the internet, in addition to the tips below.
Manage your digital footprint
Search for yourself online. Don’t stop at your name: try your email address, nicknames, and phone number too. If you’re comfortable with AI processing your data, you can even ask it to compile a dossier on you. Just remember that there’s always a risk of a leak or a bug that accidentally makes your data public. And no, big, reputable services are no exception.
Make private any profiles you don’t want to share with everyone. That makes it harder for search engines to index your new posts, and for scrapers and OSINT tools to collect them. While you’re at it, go through your old comments and posts and clear out anything you don’t need.
Delete your ghost accounts. Go through your inboxes and check which websites you’ve signed up for. Make a habit of deleting accounts you no longer use: they can hold your personal data for years, and there’s always a risk it’ll end up in the next data leak.
Set up two-factor authentication. That way, even if a bad actor manages to guess your password or finds it in a leak, they won’t be able to get into your account without the additional authentication. For the second factor, we recommend using one-time codes that refresh every 30 seconds and storing them in a reliable password manager.
Strip metadata before posting photos and videos. Metadata can help a malicious person learn a lot about you— for example, the location and exact date a photo was taken, and the model of your device.
Use a different password for every account you have. Our research has showed that passwords built from personal details — such as your mother’s maiden name, your birth date, and a special character at the end — are extremely weak. This kind of information often ends up in leaks, or can be pieced together from public sources, so the passwords can be easily brute-forced by smart algorithms. Of course, nobody can remember hundreds of unique passwords, so it makes sense to offload that job to our password manager — a secure vault that generates and remembers complex, unique passwords for you, and syncs them across all your devices.
Find out about new leaks as fast as possible. Some online services will send you a free alert if your email address shows up in a known data leak. But it’s much more convenient to monitor leaks with a dedicated security app. For example, Kaspersky Password Manager constantly checks all the entries you’ve saved. It warns you if you use the same password on different websites, or if any of your saved login and password pairs has been compromised. Our simple instructions for Windows, macOS, Android, and iOS can help you easily check all the passwords you’ve saved in Kaspersky Password Manager. Your passwords are never sent to Kaspersky. We explain how we can analyze your passwords without knowing them in our post, How to create strong passwords and where to store them.
Set up privacy on your devices and apps with our free online service, Privacy Checker.
Keep your accounts separate
The more websites that know your email, the more often it will show up in advertising profiles and potential leaks. For one-time and minor sign-ups, you can use an email masking service. All Apple users get this feature by default (Hide My Email). If you use another OS, you could try Firefox Relay, for example.
The service then creates a separate proxy email address for the website where you’re trying to sign up. Messages sent to that address are automatically forwarded to your real inbox, but the website never sees your real email address.
If you want to go all in, you can try splitting your digital life into several sub-personas by hand. Create several email addresses for different purposes. For example, use one for online stores, banks, and government services, a second for public social media, and a third for forums and social networks where you want to stay anonymous.
Keep in mind that all this is a challenge: you’ll need to keep coming up with new nicknames, and make sure your sub-personas never overlap. If you use an email address for an anonymous profile, don’t link it to services that already have your real details, and don’t use it as a backup email for a public account. One accidental link can easily undo all your effort.
Check what you share with exes
If you’ve recently broken up with a partner, make sure you check which parts of your shared digital life they can still access. Sadly, it’s very often ex-partners who become doxers or stalkers — spying on their former other half and stopping at nothing to do so. For more details on exactly what to do in this situation, read our article Post-breakup digital hygiene: what to check and shut down.
Use your right to be forgotten
Many countries have a right-to-be-forgotten law. It lets you ask search engines to remove links to pages that contain your personal data.
You can send the links to those pages, explain why you want them hidden, and request that they be removed from search results. Keep in mind that the page with your data isn’t deleted. Other search engines may still show it, and it may still turn up for other search queries.
To submit a request like this, use the dedicated forms from Google or Bing. But remember that a search engine can turn you down if it decides the information is in the public interest, or that the law requires it to be published.
The more a company’s infrastructure grows, the more weak spots it has. And that’s true for all companies — from large corporations with deep pockets that are able to invest more in their defenses, to small and medium-sized businesses. And despite their more modest capabilities, smaller companies are just as tempting a target for attackers.
New times, new risks
Cloud platforms, remote access, and AI help businesses scale up and get more done. But they also give attackers extra ways to get into corporate infrastructure. For example, remote employees’ personal devices have become a foothold that’s hard to control. And thanks to AI, phishing emails are almost impossible to tell from real ones: users can no longer spot a scammer by their spelling mistakes.
There’s another reason why new threats keep appearing: companies are slowly learning how to handle the old ones. Take backups. Just a few years ago they were sold as a cure-all against ransomware. Now they’re less effective, because at some point attackers started stealing data and demanding payment not for decryption, but for not making it public. What’s at stake here isn’t just business processes, but the organization’s reputation too. We wrote about this scheme in more detail in a separate blog post.
The scariest part is that an attacked company’s problems don’t end on the day of the incident. The next few days (or even weeks) are often much harder. This is when the team needs to quickly deal with the aftermath of an attack and to make sure another can’t happen again. Growing companies often have to throw their entire small IT force at the problem, so getting back to normal work can take a long time.
Three Achilles’ heels at once
According to the Global Kaspersky B2B Market Pulse survey, most SMBs only think about security when circumstances force them to; for example, after an incident, when expanding their infrastructure, or when a potential partner asks them to strengthen their perimeter before signing a contract. Yet only a handful treat continuous cybersecurity monitoring as a core part of running their business.
When a company finally decides to get serious about security, it runs into three constraints: people, processes, and technology. Let’s look at each one.
People. In a company with up to 500 employees, the IT department is usually just a few people. They handle all technical issues and have little to do with cybersecurity. When things get tough, these specialists may simply lack the expertise to deal with things. Other employees can be a weak link too. Accountants, lawyers, and other staff with access to confidential information often aren’t familiar with security rules.
Processes.A small IT department always has a backlog with a long queue of tasks; therefore, fresh updates and patches don’t get installed right away. As a result, attackers have plenty of time to take advantage of a vulnerability that isn’t fixed in time. Meanwhile, other employees may not know how to respond to suspicious emails, or how to store and share passwords safely. And there’s simply no one to keep an eye on them.
Technology. Threats evolve alongside a business’s technology. For example, once a company has moved part of its infrastructure to the cloud, relying on a classic antivirus alone becomes pointless.
So small and medium-sized businesses become easy targets for attackers not so much due to their size, but because they don’t pay enough attention to the key building blocks of cybersecurity. As to what this can lead to, and how the tables can be turned in a company’s favor — read on for a real-world case that demonstrates this.
Case study: ERP system breach
Let’s look at a real-world attack on a company with 450 employees. When the incident happened, the company was migrating its ERP system to the cloud. The data had already been moved, but the protection hadn’t been set up yet. And that limbo state is exactly what let the attackers pull off their campaign.
The attackers used a fairly simple tactic. Posing as an external ERP integrator, they sent the finance department a file with an “adjusted invoice”. When an employee opened the attachment, the malicious code inside it exploited a vulnerability in a local application, and the attackers took control of the device. There they found saved credentials that let them log in to a support account and get administrator rights on the cloud ERP server. With that account, they got into the server and stole the company’s confidential data.
We analyzed the mistakes that made this incident possible, and came back to the same formula: people + processes + technology. The company did provide employee training, but it was mostly a formality and did nothing to help people learn to spot email phishing. Security updates weren’t installed right away either, which is why the computer had an unpatched vulnerability. On top of that, privileged credentials were stored right on the employee’s device, which gave the attackers a direct path to administrator access. Finally, the workstations had no EDR, and the cloud ERP server had no workload protection.
How SMBs can strengthen their defenses
The best way to start is with the three key areas we covered above. And this isn’t about simply throwing money at security. What’s needed is a clear, step-by-step plan that makes the most of the resources the company already has.
Hands-on training
Employees are a business’s first line of defense, so it’s especially important to help them form safe cyberhabits. Many companies understand this and duly run computer literacy training; however, often employees show up in droves, yet they keep on making the same old mistakes.
The problem is that most training isn’t relevant to the people taking it. People in the finance department know that attackers can send phishing emails, but what does that have to do with their job? To head off questions like that, we recommend combining cybersecurity theory with simulations of real cyberattacks. That way, employees can safely step into the shoes of an attacker’s target. Start by training employees who have privileged access to systems, and also those who handle confidential information.
To keep training from becoming a formality, track progress regularly. For example, send employees suspicious test emails from time to time, and measure how fast and how well they react: how many recipients click the link, and how many report the threat.
Structured processes
Set up clear priorities for installing updates and patches. This helps avoid two extremes: running for months with open gaps in the infrastructure, or rushing to fix every vulnerability without asking how critical it is for specific business processes. Setting up centralized vulnerability management also helps, which we explained how to do in a separate post. Don’t rush to expand the infrastructure or move it to the cloud until the company has proper protection and monitoring in place.
Another key point: assign an owner to every process. Someone should be personally responsible for regular cybersecurity training, installing updates, and the timing and methods of incident response. That way, security tasks get done on time — even when the IT team has limited resources.
Gradual rollout of security solutions
It’s impossible to build reliable business protection without specialized products, but buying everything at once won’t help either. New solutions should match the needs of the infrastructure. A good approach is to add tools as the need to do so comes up; for example, to prioritize vulnerabilities more effectively or to strengthen the security of email or cloud environments. One way to tailor security to the company’s needs is to use our Security Modules , which work with Kaspersky Next Optimum — a solution for growing SMB and mid-market businesses.
Another option is to move to a more advanced solution as the infrastructure grows. The foundation of cybersecurity can be laid with Kaspersky Next EDR Foundations, which provides basic endpoint protection and control. Then, when needed, the company can move up to solutions with a broader range of capabilities, from Kaspersky Next EDR Optimum to Kaspersky Next XDR Optimum, or straight to Kaspersky Next MXDR Optimum. Our most comprehensive offering — Kaspersky MXDR Optimum — combines advanced detection and response that goes beyond endpoints and adapts to the needs of a growing business, 24/7 monitoring, and proactive threat hunting and investigation by Kaspersky experts.

 Login