Login


Malicious Chrome and Edge add-ons: how to spot them and why they’re dangerous | Kaspersky official blog
Malicious extensions and ClickFix attacks are two hugely popular topics on our blog, and for a good reason: they’re both very common. In this post, we bring them together. Here’s the thing: in our posts about malicious ClickFix instructions, we don’t always explain exactly how users end up on the attackers’ pages in the first place. A recent study gives us a chance to fill that gap and talk about one of those methods: malicious extensions.
Readers who are not deep into cybersecurity may already have a bunch of questions at this point: how can extensions be malicious? where do they come from? and what exactly is ClickFix, anyway? Fret not: this post answers all these questions.
The danger of browser extensions
Let’s start with the basics. Browser extensions or add-ons are lightweight tools installed in your browser to give it extra capabilities or change how it works with web pages. For example, extensions can block ads, translate pages, download audio and video, save passwords, or take screenshots.
Most browser developers offer users an official extension store. For instance, for the most popular browser, Chrome, that store is the Chrome Web Store. There are also alternative platforms for distributing extensions, though browser developers have recently made it much harder to install and use extensions that don’t come from an official source.
Just like any other software, extensions can be useful, but they can also be malicious. In fact, cybercriminals often spread malicious extensions through those very same official stores, and we’ve covered plenty of such cases on our blog before.
It’s no accident that criminals love spreading malicious plug-ins. To work properly, most extensions need permission to read and modify the content of every web page the user visits. Without that permission, add-ons would be basically useless. For instance, a translation extension needs to read all the text on a page before it can swap the original for the translation.
Cybercriminals take advantage of these capabilities for their own purposes: for example, they intercept logins, passwords and other data entered on websites, swap out payment details, or show victims fake forms and messages. And all of this happens on legitimate sites that users have come to trust without a second thought.
Now let’s move on to a fresh piece of research about a campaign that spread 19 malicious add-ons through the Chrome and Edge extension stores. We’ll use it as an example to look at what these tools can actually do.
Almost twenty malicious extensions for Chrome and Edge
In late August, cybersecurity researchers reported finding 18 malicious extensions for Chrome and one for Edge. They said all 19 add-ons were probably linked to the same campaign. They base this on the similarity of the malicious code and the methods the attackers used. You’ll find the full list of malicious extensions at the end of this post.
Most of the extensions discovered, 14 in total, were built by the attackers themselves. Their first versions weren’t malicious at all and did exactly what users downloaded them for. But after a while, once users had come to trust the add-on, the attackers pushed an update that slipped in malicious functionality.
As for the remaining five extensions, their creators had nothing to do with the cybercriminals at all. They simply sold their creations to them. This way of getting hold of extensions is also popular among cybercrooks. There are plenty of reasons for that: ready-made add-ons can be bought for relatively little money, and criminals don’t have to build or promote them from scratch. And most importantly, along with the extension, they also inherit its existing user base. Upon buying the add-on, all the attackers need to do is add malicious functions and push an update that installs automatically for users. Users are never told that the extension’s real owner has changed.
In this case, the add-on cybercriminals bought most often was Enable Right Click & Copy — Smart Unlock + OCR. It had 70 000 users in Chrome and 10 000 in Edge. This purchase is exactly why there’s a single Edge extension among all its Chrome relatives. The add-on itself originally served a perfectly benign purpose: it let users select and copy text on sites where that’s normally blocked, and it could also pull text out of images with optical character recognition (OCR).
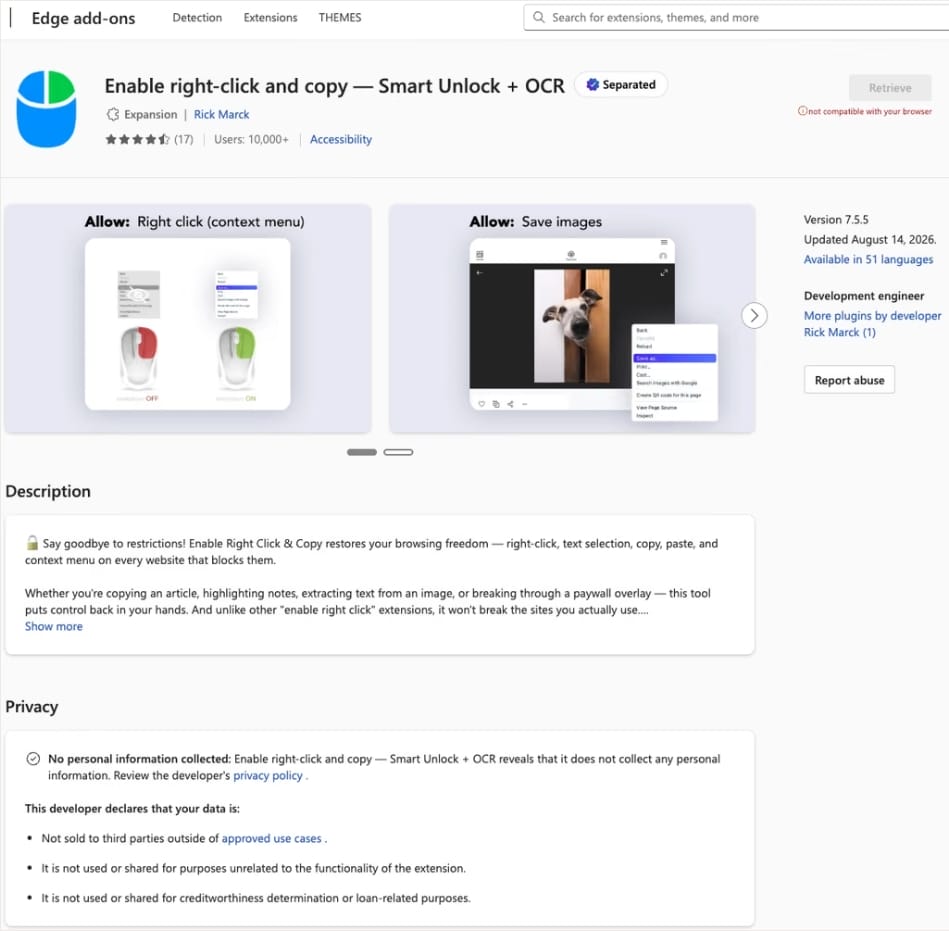
At the time of the research, the Edge version of the extension had more than 10 000 users. Source
The malicious functionality introduced into the extension makes it reach out to the attackers’ command-and-control (C2) server to download additional modules of nefarious code. These modules can change over time. Since Chrome automatically updates all installed extensions by default, the malicious version lands on the device without users having to do anything at all.
For the downloaded code to run on the websites the user visits, the extension disables one of their defenses — Content Security Policy (CSP). This mechanism allows website owners to declare which scripts and other resources are allowed to load and run on a page. Once this protection is turned off, the extension can inject code it gets from the C2 server right into the pages open in the browser. The website itself isn’t hacked, and it looks the same to everyone else, but for that one infected user, the legitimate page quietly turns malicious.
What these 19 extensions can do
Now let’s take a closer look at what the malicious modules loaded by the extension are actually capable of. Researchers found 16 such modules, built for all sorts of tasks: from stealing data and hijacking cryptocurrency to the ClickFix attacks we’re focusing on here.
Some of the modules simply collect user data. They intercept logins, passwords, email addresses, and other valuable information the user enters into web forms, including payment details. On top of that, the add-ons steal data from Facebook and LinkedIn accounts and collect browsing history. Criminals can use this information to take over accounts, steal money, and launch further attacks against the victim.
A few other modules focus specifically on stealing cryptocurrency and related data directly. One of them is a crypto drainer, a tool that empties crypto wallets. It works with Ethereum and compatible blockchains as well as Solana and Tron. It replaces the real Connect Wallet and Swap buttons on websites with its own fake ones. When a user clicks one of these buttons, the drainer takes over all further interaction with the wallet and walks the victim through confirming the actions needed to steal their cryptocurrency.
Other modules target users of Ledger and Trezor hardware wallets. Right on the official websites of these services, the malicious extension displays a fake wallet update-and-restore page that asks for a seed phrase of 12, 18, or 24 words. The seed phrase the user enters is forwarded straight to the attackers, giving them full control over the wallet.
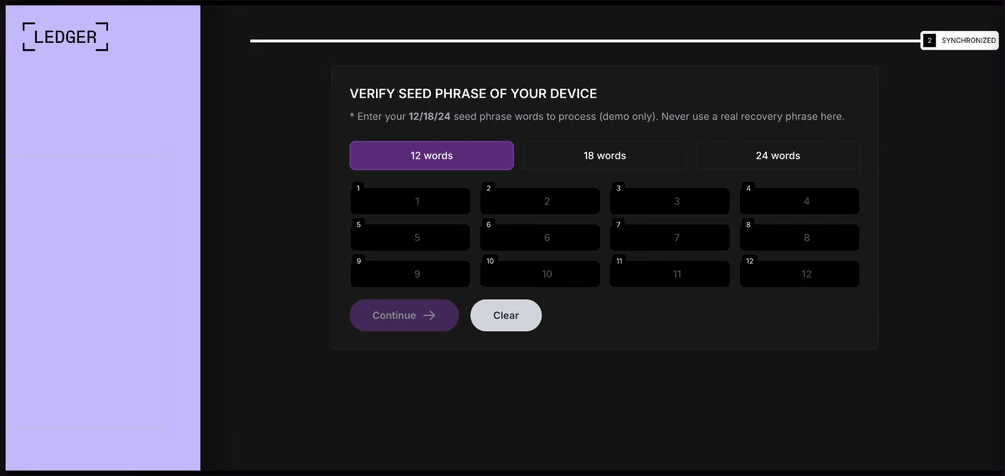
The fake form asks the user to enter a seed phrase of 12, 18, or 24 words, which then ends up in the attackers’ hands. Source
Finally, some modules gather information from crypto service pages open in the browser, such as OKX, MEXC, Kraken, KuCoin, Coinbase, Binance, Bybit, and MetaMask, including balance details and active session data that can be used to hijack accounts.
And now we’ve finally reached the module that matters most for this post: the one used for ClickFix attacks. We’ll talk about it in the next part.
How malicious extensions are used in ClickFix attacks
The ClickFix attack technique has become extremely popular among cybercriminals lately. It relies on social engineering: the victim is shown fake instructions supposedly needed to complete some action, such as passing a CAPTCHA check, fixing an error, or updating a program. Following these instructions, the user copies the command suggested by the attackers, pastes it into a system tool built for running these commands, and runs it, all by themselves.
We’ve written about attacks like this and their consequences more than once on our blog. But we rarely dig into exactly how a victim ends up on a page with fake instructions in the first place. A campaign that spread malicious extensions through the Chrome Web Store shows us one way this can happen.
Add-ons turn out to be a very handy tool for ClickFix attacks. As we mentioned earlier, when a user visits a page, extensions are allowed reading and changing its content in order to work. That gives attackers the chance to swap in a fake ClickFix instruction at just the right moment, replacing the content of the page the person actually wanted to open.
What’s more, the ClickFix technique itself lets attackers break out of the browser and gain a foothold directly in the system. That means removing the malicious extension won’t necessarily undo the damage: after the user has run the ClickFix command, malware may already be installed outside the browser.
In the specific attack example the researchers describe, the user sees a fake notification saying their browser needs to be updated, along with instructions on how to do it. The instructions change depending on the operating system, and the extension picks up that information automatically too.
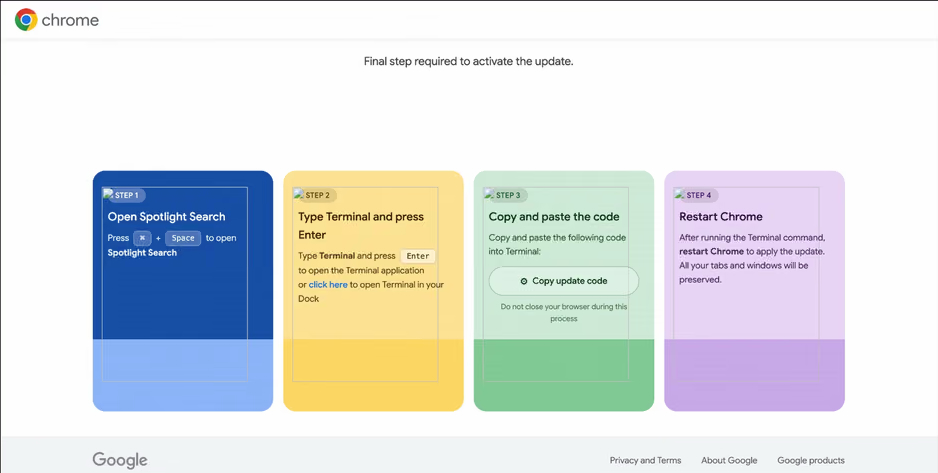
In the macOS version of this attack, the user is told to open Terminal, copy a command, paste it there and run it, then restart Chrome to supposedly finish the update. Source
How to avoid falling victim to infected extensions
First off, we recommend checking whether any of the following malicious extensions are already installed in your browser:
- Enable Right Click & Copy — Smart Unlock + OCR
- RapidLens – Google Lens for Screen Search & Images
- QuickLens – Search Screen with Google Lens
- Password Protect PDF
- Allow Copy – Select & Enable Right Click
- PixelCheck
- Creative Library – Ad Spy Tool
- Website Traffic Checker: MirrorSphere SEO Stats
- Site Signal – Website Traffic & SEO Checker
- SEO Pulse Pro – Website Traffic & SEO Analyzer
- Private Crypto News Reader
- Blockfolio: Address Monitor
- Crypto Rates & Fiat Converter
- Crypto Alerter: Price Alarms & Volatility Warnings
- DeFi Pulse Tracker
- Crypto Price Badge: Quick Glance
- Multi-Chain Explorer
- LedgerLook: Wallet Checker
- Meta & Facebook Ad Library Spy — Save Ads, Finder, Downloader | FeedX-Ray
If you find any of these extensions on your device, we recommend removing it as soon as you can and running a full system scan with a reliable antivirus. As we mentioned above, simply deleting the add-on might not be enough. You can use a free trial version to detect and remove the infection.
How to avoid falling victim to malicious extensions and ClickFix attacks in the future?
- Don’t install too many extensions and regularly check the list of those you have.
- Remove extensions you don’t use.
- Trust the warnings from your operating system and security software, rather than the instructions — or even the demands — of websites and apps.
- Install a trusted security solution on all your devices.
What else makes browser extensions and the ClickFix technique dangerous? Find out in our other posts: