Cybersecurity is in the middle of a generational shift. AI has disrupted a 30-year balance of power between defenders and adversaries.
Armed with agentic AI tools and open-weight models stripped of safety guardrails, threat actors are discovering, validating, and chaining exposures at machine speed. In a recent Unit 42 investigation, the attacker used more than 50 MITRE ATT&CK techniques to reduce weeks of methodical intrusion tradecraft into less than 10 hours—97% faster than a skilled red team could have done. Time-to-exfiltration has compressed to under an hour in real-world attacks. And when new CVEs are publicly disclosed, automated adversary scanners are weaponizing them within 15 minutes.
Defending at human speed is no longer viable. Organizations must close years of accumulated exposure while securing the AI they are rapidly adopting. That demands action on five fronts: continuously find and fix vulnerabilities, reduce exposure, secure AI infrastructure, unify attack prevention, and automate detection and response at machine speed.
Today, we are announcing Unit 42 Continuous Frontier AI Defense to put the first two priorities into practice. Powered by Anthropic's Mythos models and OpenAI's latest GPT cyber models, this always-on, agentic service combines our offensive security experts with proprietary multi-model harnesses to discover vulnerabilities, validate real-world exploitability, and accelerate remediation across applications, identities, cloud infrastructure, and network assets.
Led by our offensive security experts, this service discovers, validates and remediates exposures before they can be exploited. We use proprietary AI harnesses and gated capability models—powerful models restricted from public use—to discover vulnerabilities, prove real-world exploitability, and accelerate remediation across applications, identities, cloud infrastructure, and network assets as an organization’s environment changes.
Continuous Frontier AI Defense builds on Unit 42’s Frontier AI Defense, which launched in April and introduced Frontier AI Exposure Analysis, a point-in-time exposure analysis, and a security blueprint that benchmarks current capabilities to help organizations modernize their cybersecurity systems. In August, Unit 42 expanded the list of frontier AI models to include OpenAI’s GPT-5.6-Cyber and Anthropic's Claude Mythos 5, giving organizations access to additional AI capabilities.
A Single AI Model Is Not a Security Strategy
Frontier models are powerful, but no single AI model is a cybersecurity silver bullet and the models require equally powerful AI scanning harnesses.
Unit 42 research evaluation of model performance across enterprise codebases and live environments revealed two stark operational realities:
Coverage caps: No single AI model catches more than 40% of vulnerabilities in a complex environment.
Visibility: Leading cyber models such as Anthropic Claude Mythos 5 and OpenAI GPT-5.6-Cyber have less than 10% overlap in the exposures they identify.
To solve the single model gaps, Continuous Frontier AI Defense runs on proprietary multi-model harnesses. These harnesses act as an intelligent orchestration layer, routing specific offensive testing tasks to the model best suited for the job. This approach aligns model strengths, eliminates individual gaps, and keeps compute spend economical.
We combine these frontier models with Unit 42 threat intelligence, and frontline security expertise to turn raw vulnerability data into verified, actionable protection. Zero Data Retention (ZDR) architectures protect enterprise source code and telemetry, so customer data is never retained or used to train public models.
What Happens When AI Meets Real Enterprise Architecture
We did not build this service on theoretical assumptions. We built and validated it internally across Palo Alto Networks and across more than 100 customer engagements.
During our internal deployment, continuous Mythos-based scanning achieved over a year’s worth of traditional penetration testing results in just three weeks. The harness identified 3.2 times more high and critical vulnerabilities per product than legacy testing methods, and helped engineering teams cut mean time to remediate by 51%.
When we executed the service across customer environments, the frontline data delivered a clear warning:
Hidden exposures: In third-party applications, two out of three validated exposures had no known CVE. Vulnerability-only scanners will never see them.
High severity: 37% of identified exposures rated high or critical in severity.
Chained attack paths: Flaws rarely existed in isolation. In one financial sector engagement, our harness identified a sequence of individually minor flaws: an application payment link that failed to re-verify identity, a skipped one-time password check, and a session routing flaw. Chained together, an attacker could achieve complete account takeover and payment fraud without any victim action.
Moving from Discovery to Validated Protection
Finding weaknesses without fixing them only creates noise. And, security teams do not lack findings; they already have more alerts than they can act on. The bigger challenge is knowing which weaknesses an attacker can actually exploit and chain into a viable path to compromise, and then remediating them.
Unit 42 Continuous Frontier AI Defense translates findings directly into risk reduction:
Continuous Testing Engine: Provides a full-estate baseline scan followed by always-on testing as an organization’s environment changes.
Multi-Model AI Harness: Unit 42 deploys proprietary multi-model harnesses, the software architecture to route work to the model best suited for the task, improving efficacy and coverage while managing the cost of frontier AI at scale.
Leading Cyber Models: The harnesses are built around gated capability models, including Anthropic Claude Mythos 5 and OpenAI GPT-5.6-Cyber, as well as open weight models.
Advanced Adversary Simulation: Proves real-world exploitability by validating end-to-end attack paths across first- and third-party web apps, APIs, cloud infrastructure, source code repositories, and network assets.
Accelerated Remediation: Delivers actionable and prioritized fixes, code-level guidance, and virtual patch recommendations. To implement virtual patches before vulnerabilities are publicly disclosed or official patches exist, organizations can pair this with Frontier Virtual Patching.
Unit 42 Continuous Frontier AI Defense is available worldwide today on an annual subscription basis. Register for our upcoming virtual Threat Briefing to see how we apply Frontier AI, our proprietary multi-model harness, and offensive security expertise to protect Palo Alto Networks and our customers.
The vulnerability landscape shifted significantly in Q2 2026. First, the number of registered CVEs reached an unprecedented level. This is driven primarily by the widespread adoption of AI, both for application development and search for security flaws. This resulted in entire new classes of vulnerabilities emerging, particularly in the Linux networking subsystem.
Second, security researchers have been publishing exploits for unpatched vulnerabilities more frequently. Publications like these can generate significant fallout, since they potentially open the door for attackers to target unprotected systems.
Statistics on registered vulnerabilities
This section provides statistical data on registered vulnerabilities. The data comes from Kaspersky’s vulnerability knowledge base, which draws on the CVE database as well as the Russian BDU database and GitHub Advisory (GHSA). As a result, the figures for previous reporting periods may differ from those published in earlier reports.
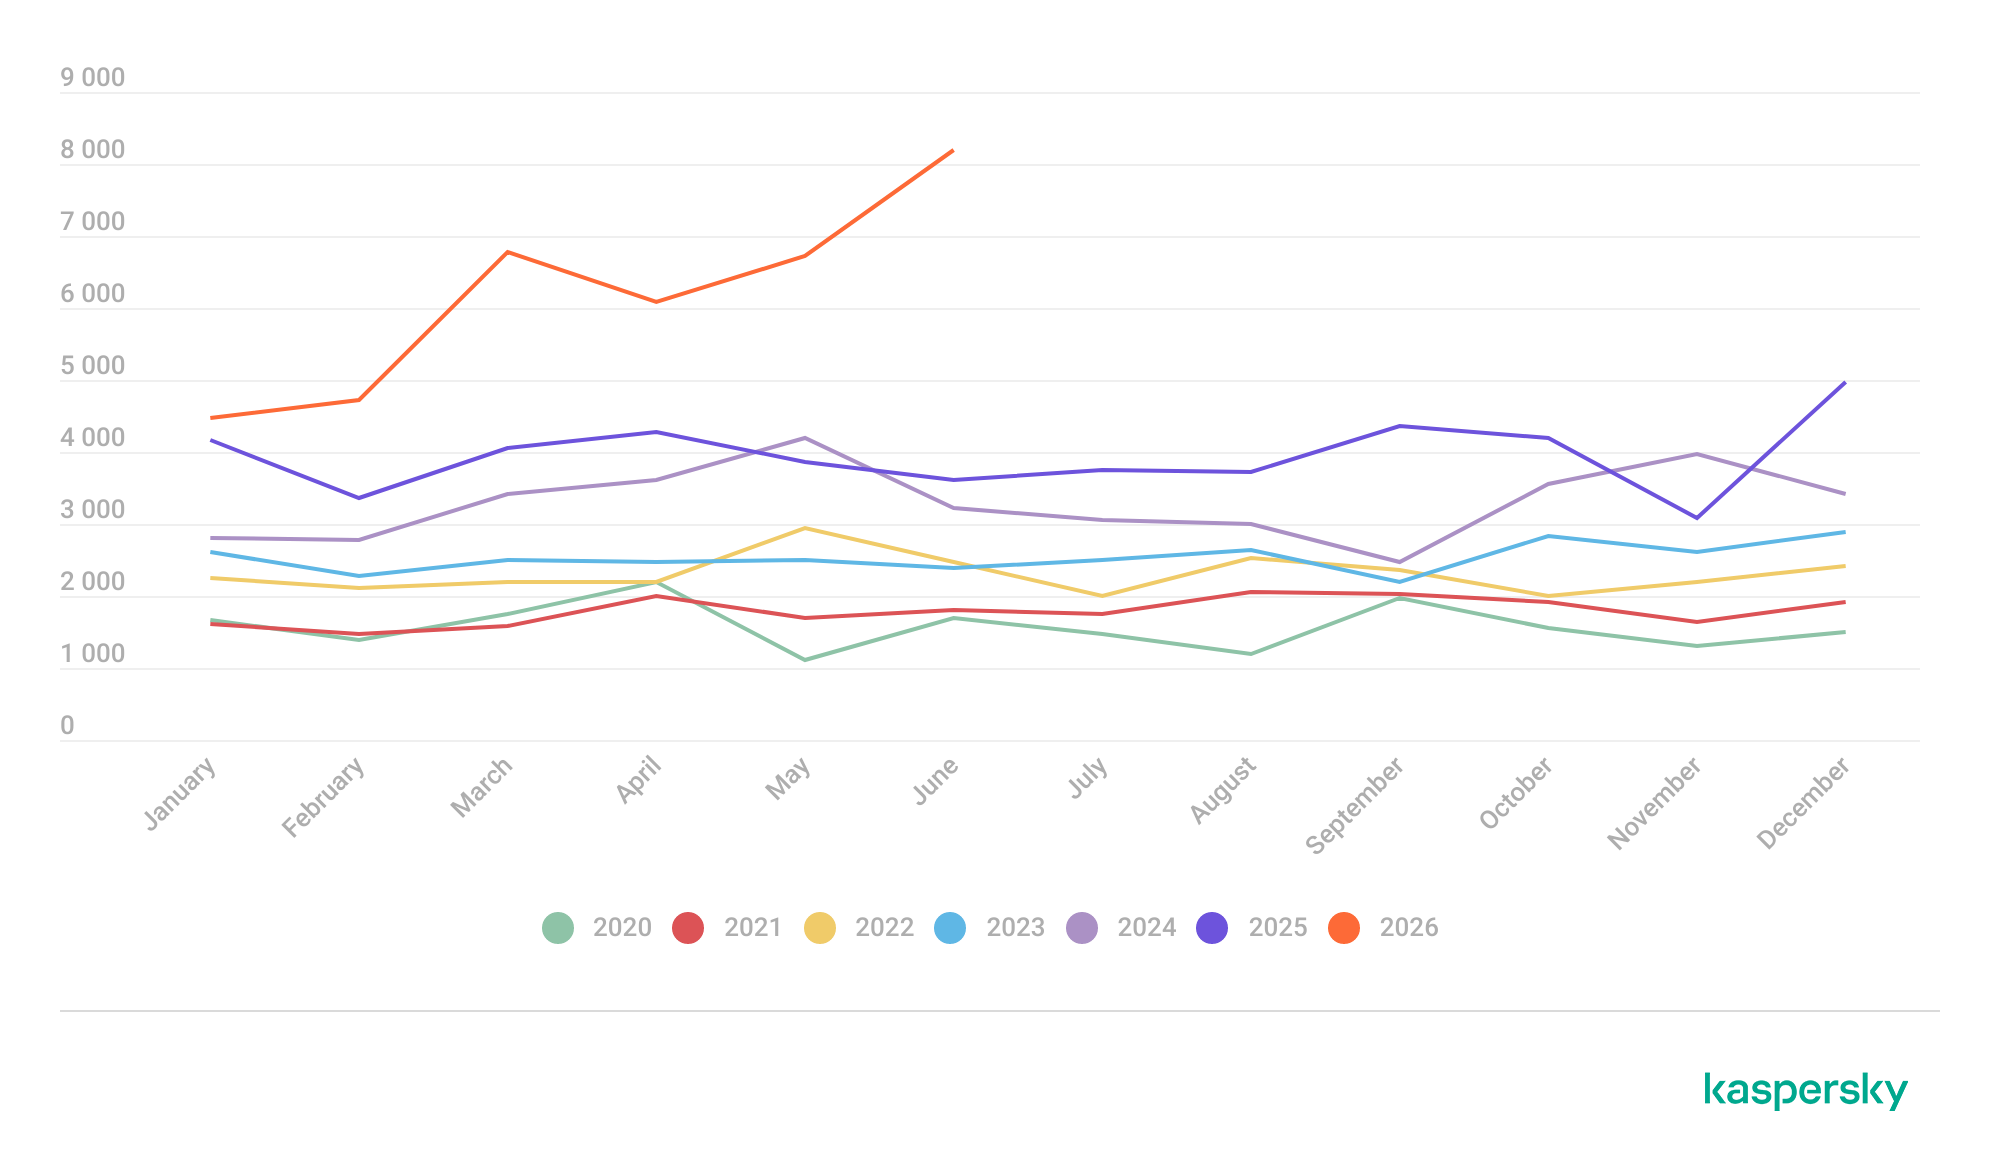
We examine the number of registered vulnerabilities for each month over the last five years. As the chart below shows, this number continues to surge, a trend reflected across all the databases we track. It’s driven primarily by the widespread adoption of AI tools: as we predicted in our previous report, these tools have played a major role in the discovery of vulnerabilities in third-party software. Meanwhile, these tools often contain security issues of their own. For example, OpenClaw, a popular AI project, ranked 12th among those with the highest number of vulnerabilities discovered and published in Q2, with over 200 CVEs registered during the reporting period. Finally, AI development tools are also contributing to the vulnerability landscape, since the quality of the code they produce can vary widely. Therefore, the rate at which new vulnerabilities are discovered will inevitably keep growing.
Total published vulnerabilities per month from 2022 through 2026 (download)
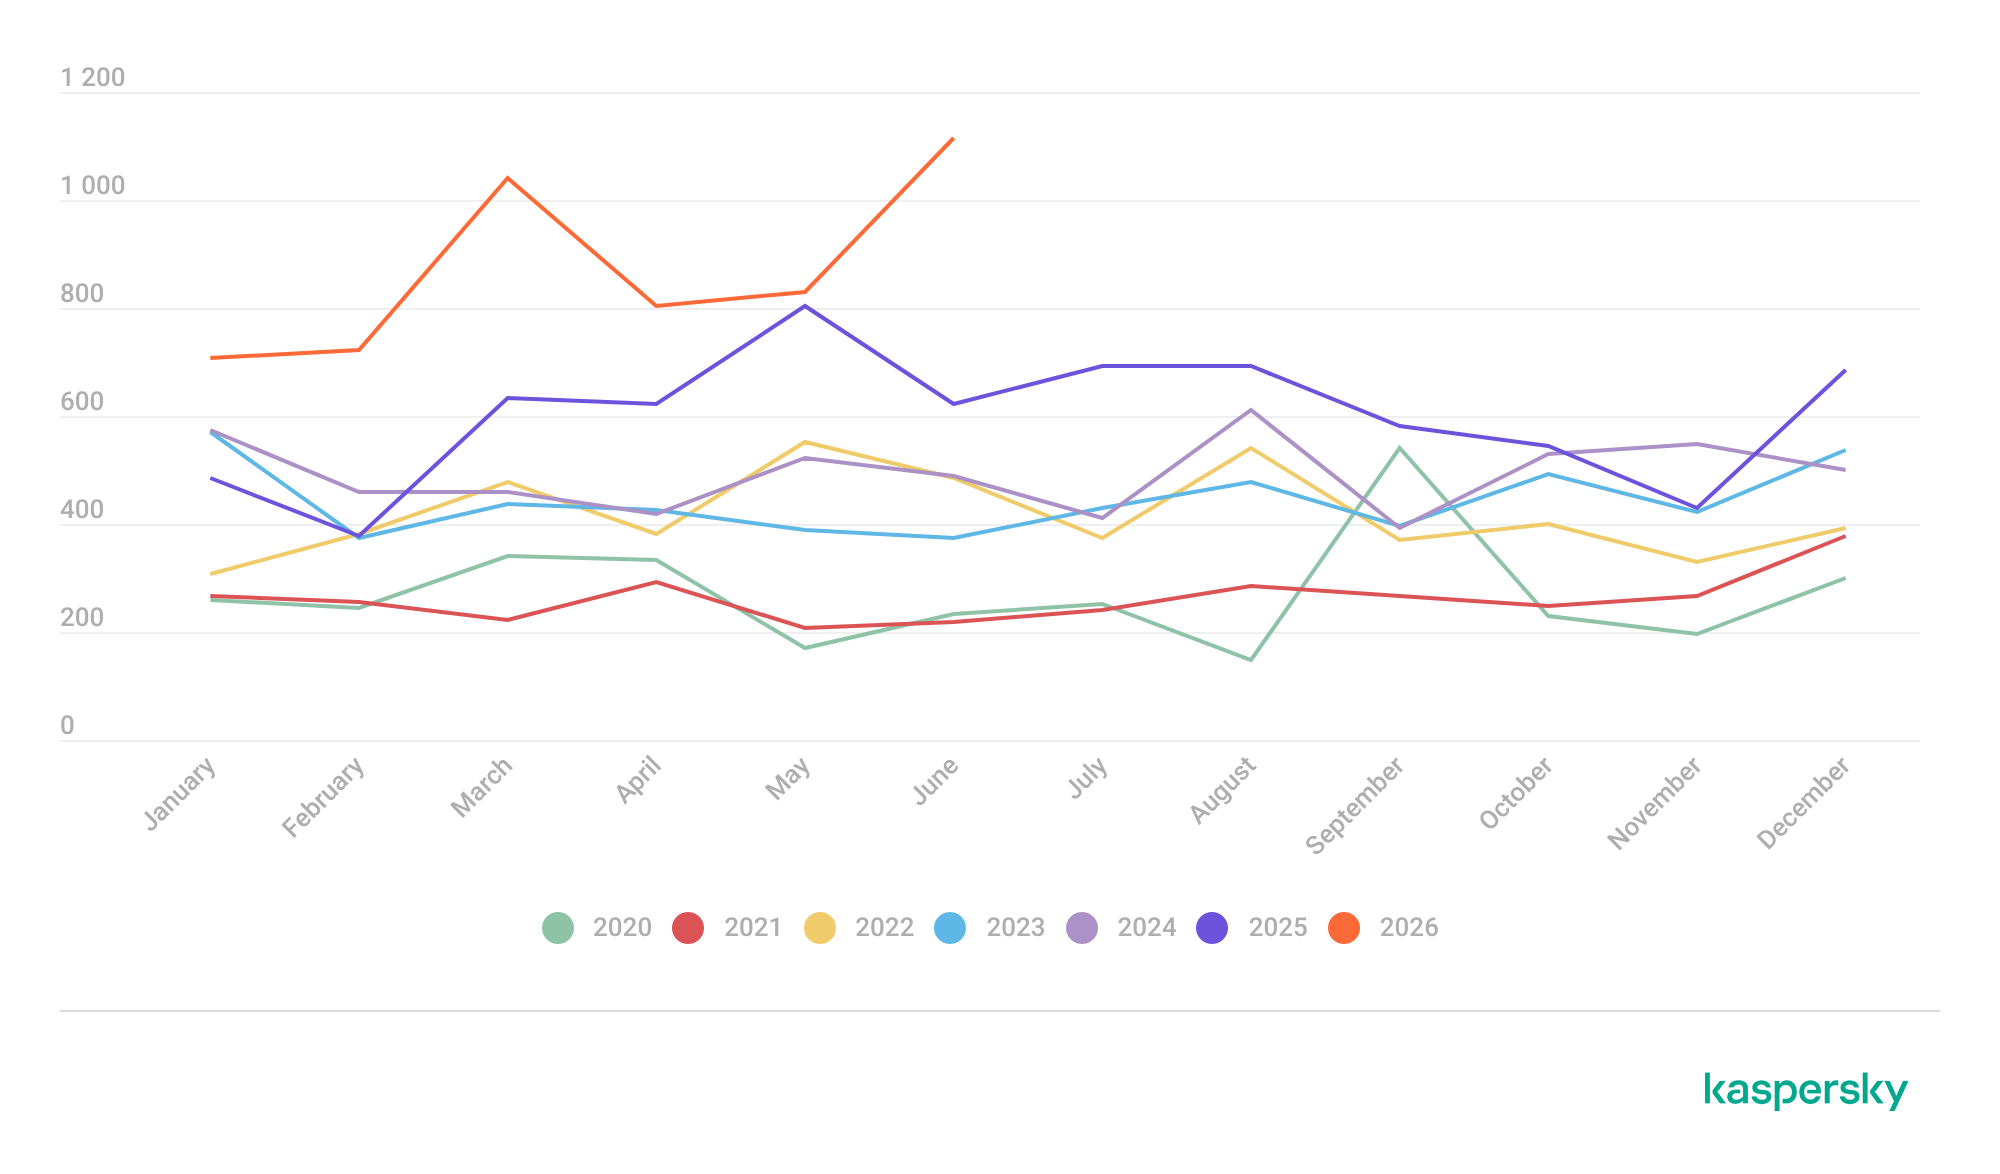
Next, we analyze the number of new critical vulnerabilities (CVSS > 9.0) over the same period.
Total critical vulnerabilities published per month from 2022 through 2026 (download)
As the chart shows, the number of published critical vulnerabilities jumped sharply in Q2. This is because using AI for vulnerability research makes it possible to analyze massive amounts of previously unexamined code, uncover new attack surfaces, and identify entire classes of vulnerabilities that have gone unnoticed for decades. In particular, AI was used to find a series of Dirty Frag vulnerabilities in the Linux kernel.
Exploitation statistics
This section presents statistics on vulnerability exploitation for Q2 2026. The data draws on open sources and our telemetry.
Windows and Linux vulnerability exploitation
Q2 2026 saw a new precedent in the publication of vulnerabilities in Windows components and exploits for these: researchers no longer waiting for CVE registration, let alone patches. A case in point: a researcher who goes by Nightmare Eclipse (also known as Chaotic Eclipse) published a list of new “named” vulnerabilities across various Windows subsystems. At the time the technical details were published, none of the vulnerabilities had been assigned a CVE identifier:
BlueHammer: a local privilege escalation vulnerability in Windows Defender. During signature database updates, a time-of-check to time-of-use (TOCTOU) race condition occurs, allowing an attacker to substitute the directory where temporary update files are written. The researcher published a fully functional exploit for the vulnerability.
RedSun: another logical vulnerability in Windows Defender with a working exploit. Suspicious and malicious files marked as “cloud” can be overwritten or restored to their original directory with elevated privileges. The exploit incorporates fragments of algorithms that make it possible to leverage various logical vulnerabilities in Windows, effectively combining a large number of popular exploitation techniques.
YellowKey: a vulnerability that lets the user bypass BitLocker full-disk encryption and access system data through the Windows Recovery Environment (WinRE). A fully functional exploit was also published.
GreenPlasma: a vulnerability that enables system object injection via the CTF loader for the Collaborative Translation Framework (CTFMON) service in Windows. The original publication included an exploit with limited functionality.
RoguePlanet: yet another Windows Defender vulnerability that, like BlueHammer, stems from a TOCTOU issue, this time in the engine responsible for real-time system scanning. The published exploit uses the vulnerability to overwrite the system file wermgr.exe with a malicious one.
UnDefend: another vulnerability in the Windows Defender service. This time, the exploit causes a denial of service and blocks updates.
Even though such cases remain isolated for now, we believe they’ll grow into a full-fledged trend. Early publication of exploits gives attackers an advantage over software developers, who are left with no time to fix the issues.
Veteran vulnerabilities in Windows software also remain relevant. These are the ones our solutions most frequently detect exploits for:
CVE-2018-0802: a remote code execution (RCE) vulnerability in the Equation Editor component
CVE-2017-11882: another RCE vulnerability also affecting Equation Editor
CVE-2017-0199: a vulnerability in Microsoft Office and WordPad that allows an attacker to gain control over the system
CVE-2023-38831: a vulnerability in WinRAR that involves improper handling of objects within an archive
CVE-2025-6218 (formerly ZDI-CAN-27198): another WinRAR vulnerability allowing the specification of relative paths to extract files into arbitrary directories, potentially leading to malicious command execution
CVE-2025-8088: a vulnerability similar in exploitation method to CVE-2025-6218. The attackers used NTFS Streams to circumvent controls on the directory into which files are being unpacked
The vulnerabilities listed here can be leveraged to gain initial access to a vulnerable system and for privilege escalation. This underscores the critical importance of timely software updates.
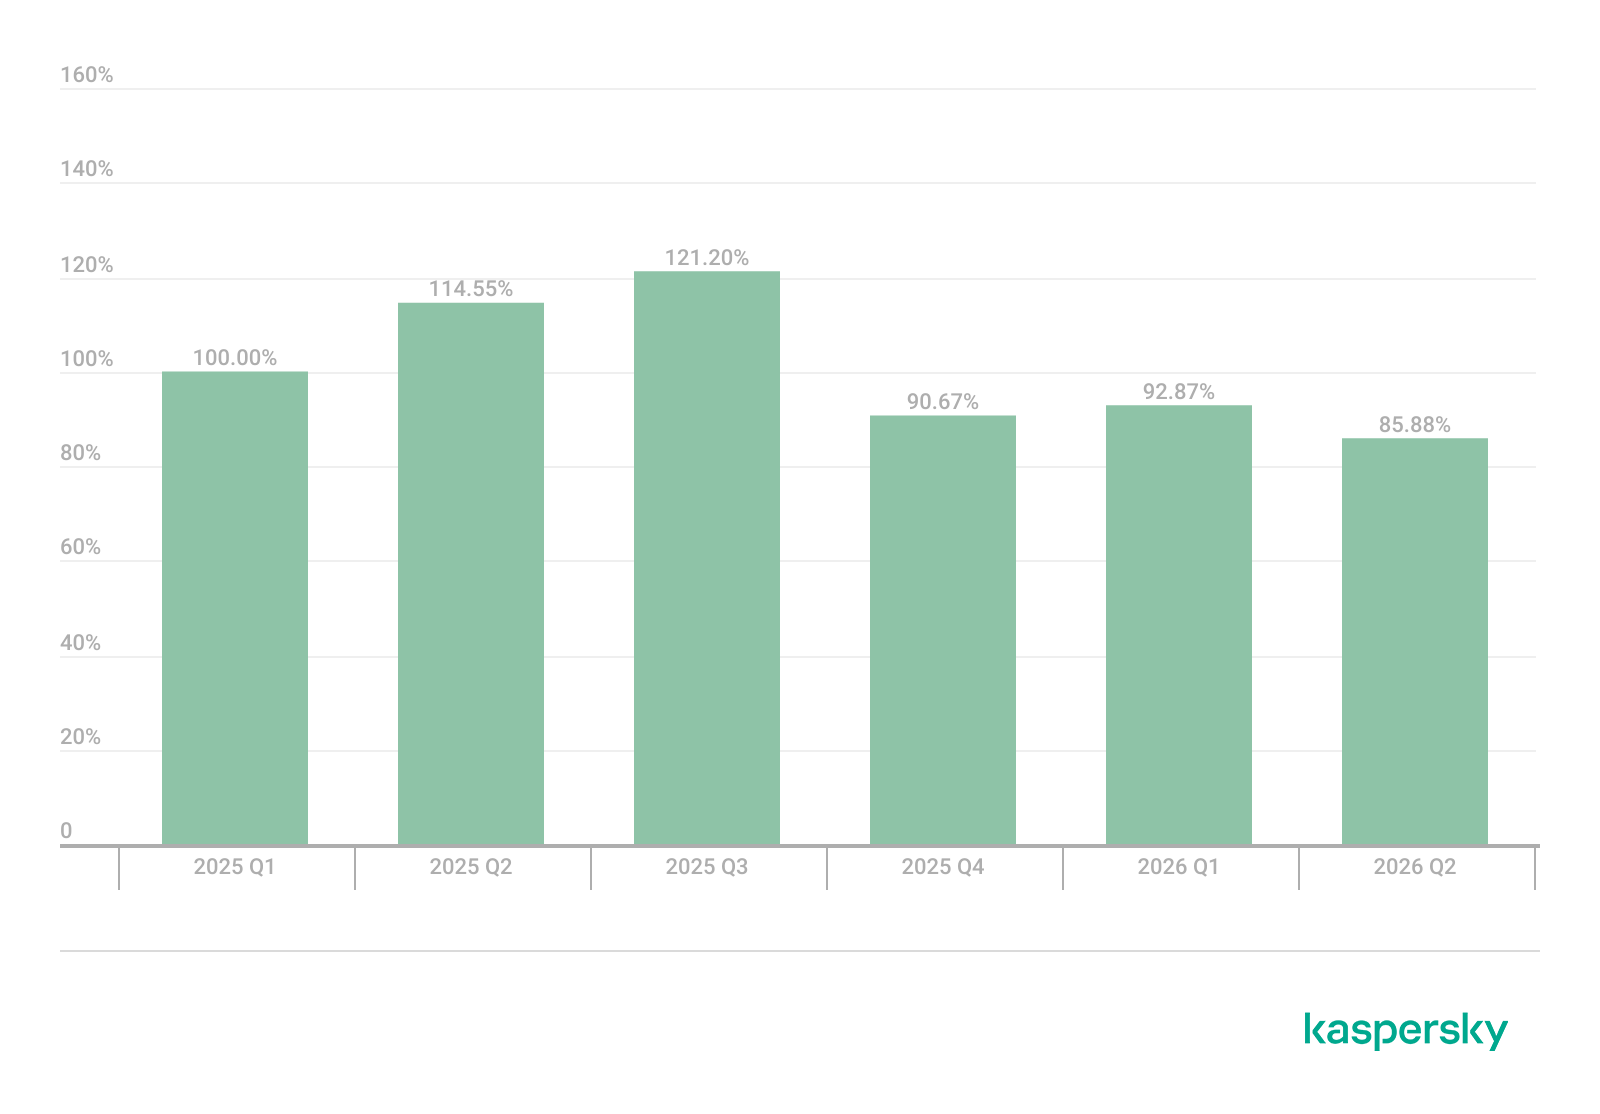
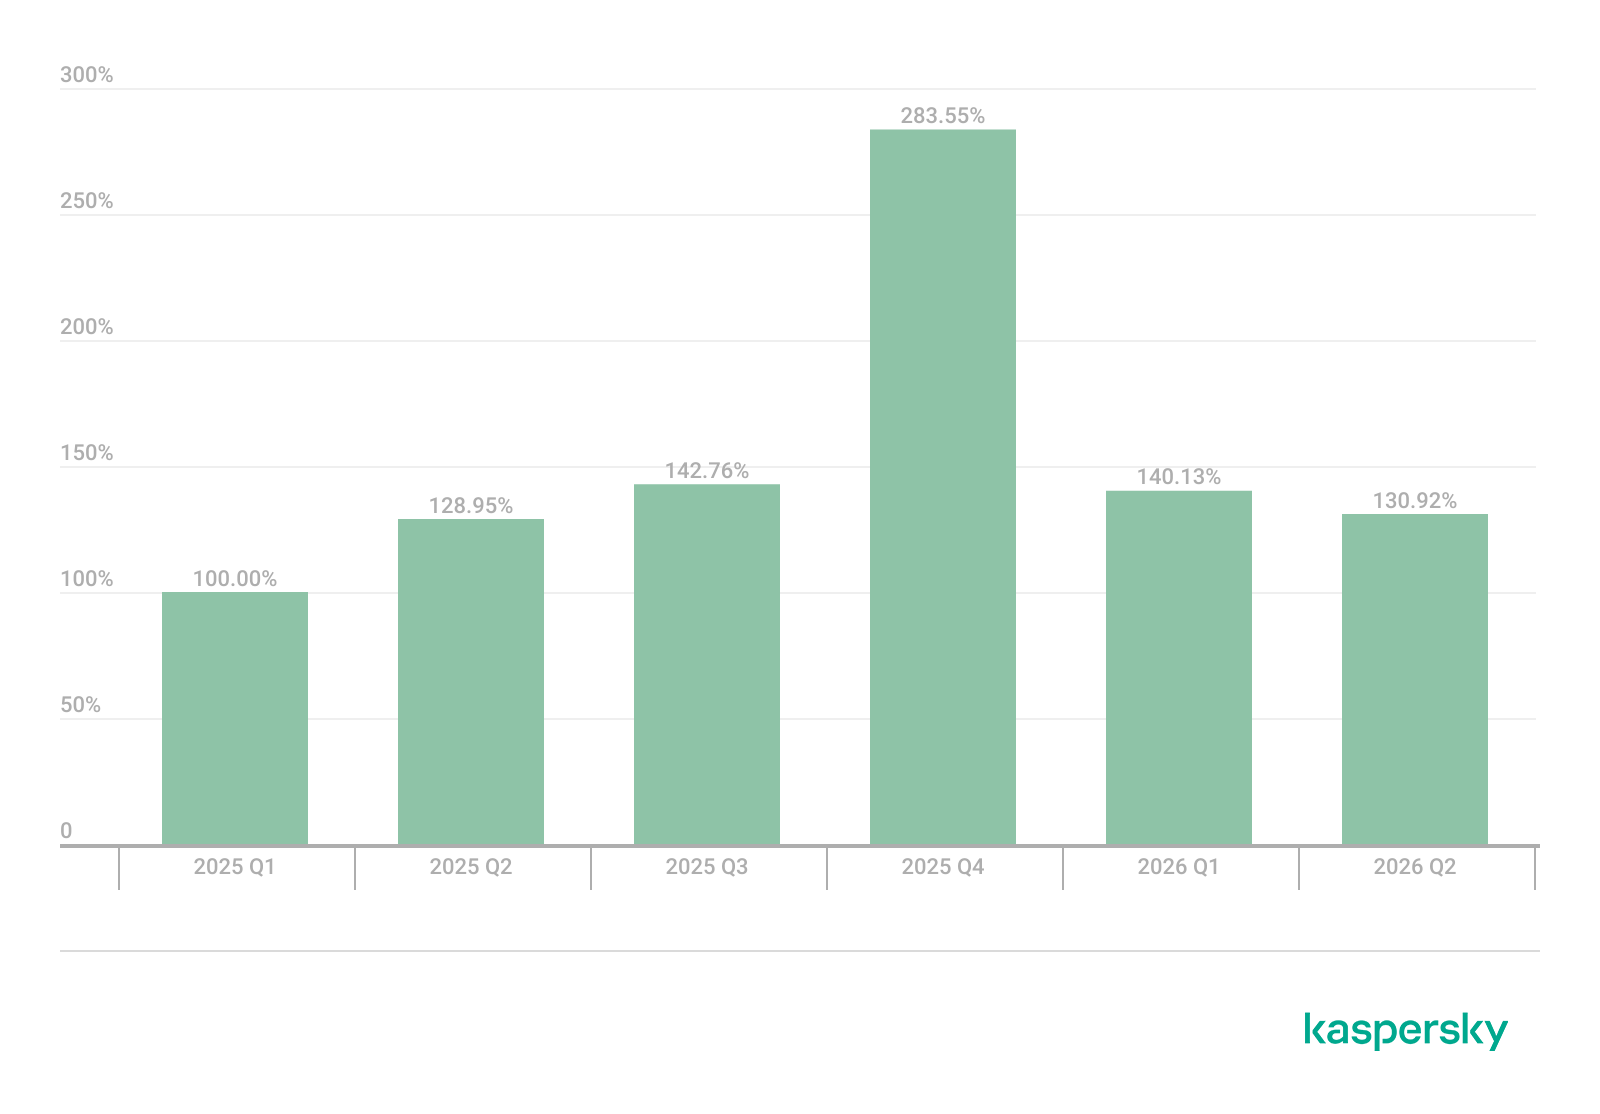
That said, the number of Windows users who encountered exploits declined slightly in Q2, hitting an 18-month low.
Dynamics of the number of Windows users encountering exploits, Q1 2025 – Q2 2026. The number of users who encountered exploits in Q1 2025 is taken as 100% (download)
Linux also hit a rough patch in Q2 2026. Specifically, the period saw the disclosure of the Dirty Frag family of vulnerabilities, which lets an attacker reliably escalate privileges within the operating system.
All the vulnerabilities published in Q2 2026 were, in one way or another, related to the Linux caching subsystem. Here are the ones being most actively exploited:
CVE-2026-31431 (Copy Fail): a local privilege escalation vulnerability in the Linux kernel that lets an unprivileged user modify the page cache and gain root privileges. Especially dangerous for cloud and containerized environments
CVE-2026-43284, CVE-2026-43500 (Dirty Frag): a family of vulnerabilities in the Linux networking subsystem (IPsec ESP and RxRPC) that lets a local user overwrite the page cache and escalate privileges to root
CVE-2026-46300 (Fragnesia): a local privilege escalation vulnerability in the Linux kernel related to packet fragment handling and the page cache mechanism. It lets an unprivileged user gain root privileges and is also classified as part of the Dirty Frag family
CVE-2026-31635 (DirtyDecrypt): a Linux kernel vulnerability that lets a local attacker escalate privileges due to improper handling of decryption operations and page cache data modification
CVE-2026-43494 (PinTheft): a Linux kernel vulnerability that lets a local user gain elevated privileges due to errors in the memory page pinning mechanism
CVE-2026-46331 (pedit COW): a vulnerability in the Linux kernel’s traffic control subsystem (tc-pedit) that exploits a flaw in copy-on-write to modify the page cache and subsequently escalate privileges to root
The vulnerabilities described above were quickly embraced by attackers. At the same time, our solutions continue to detect exploitation attempts targeting older vulnerabilities as well:
CVE-2022-0847: a vulnerability known as Dirty Pipe, which enables privilege escalation and the hijacking of running applications
CVE-2019-13272: a vulnerability caused by improper handling of privilege inheritance, which can be exploited to achieve privilege escalation
CVE-2021-22555: a heap out-of-bounds write vulnerability in the Netfilter kernel subsystem
CVE-2023-32233: another Netfilter subsystem vulnerability that allows for Use-After-Free conditions and privilege escalation through improper processing of network requests
Dynamics of the number of Linux users encountering exploits, Q1 2025 – Q2 2026. The number of users who encountered exploits in Q1 2025 is taken as 100% (download)
In Q2 2026, the number of Linux users who encountered exploits declined slightly compared to Q1. Given that a significant share of new vulnerabilities are tied to the operating system’s caching subsystem, we recommend installing patches as quickly as possible, or disabling vulnerable kernel modules if patching isn’t an option.
Most common published exploits
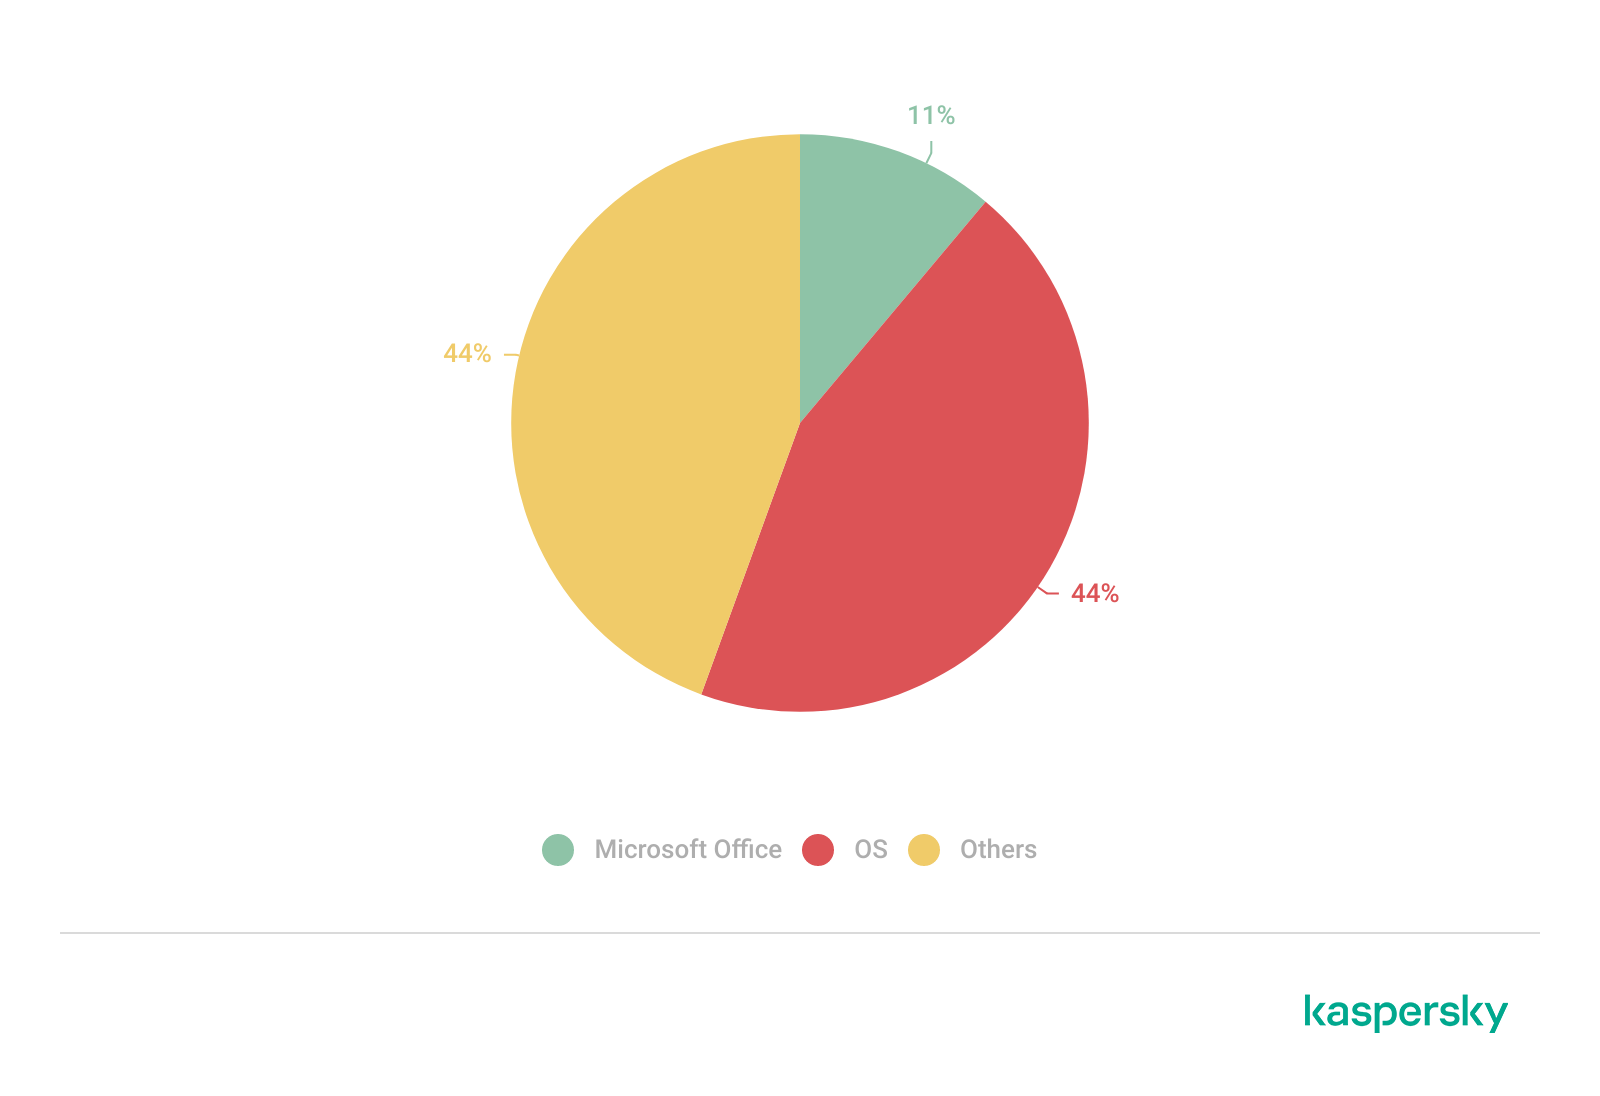
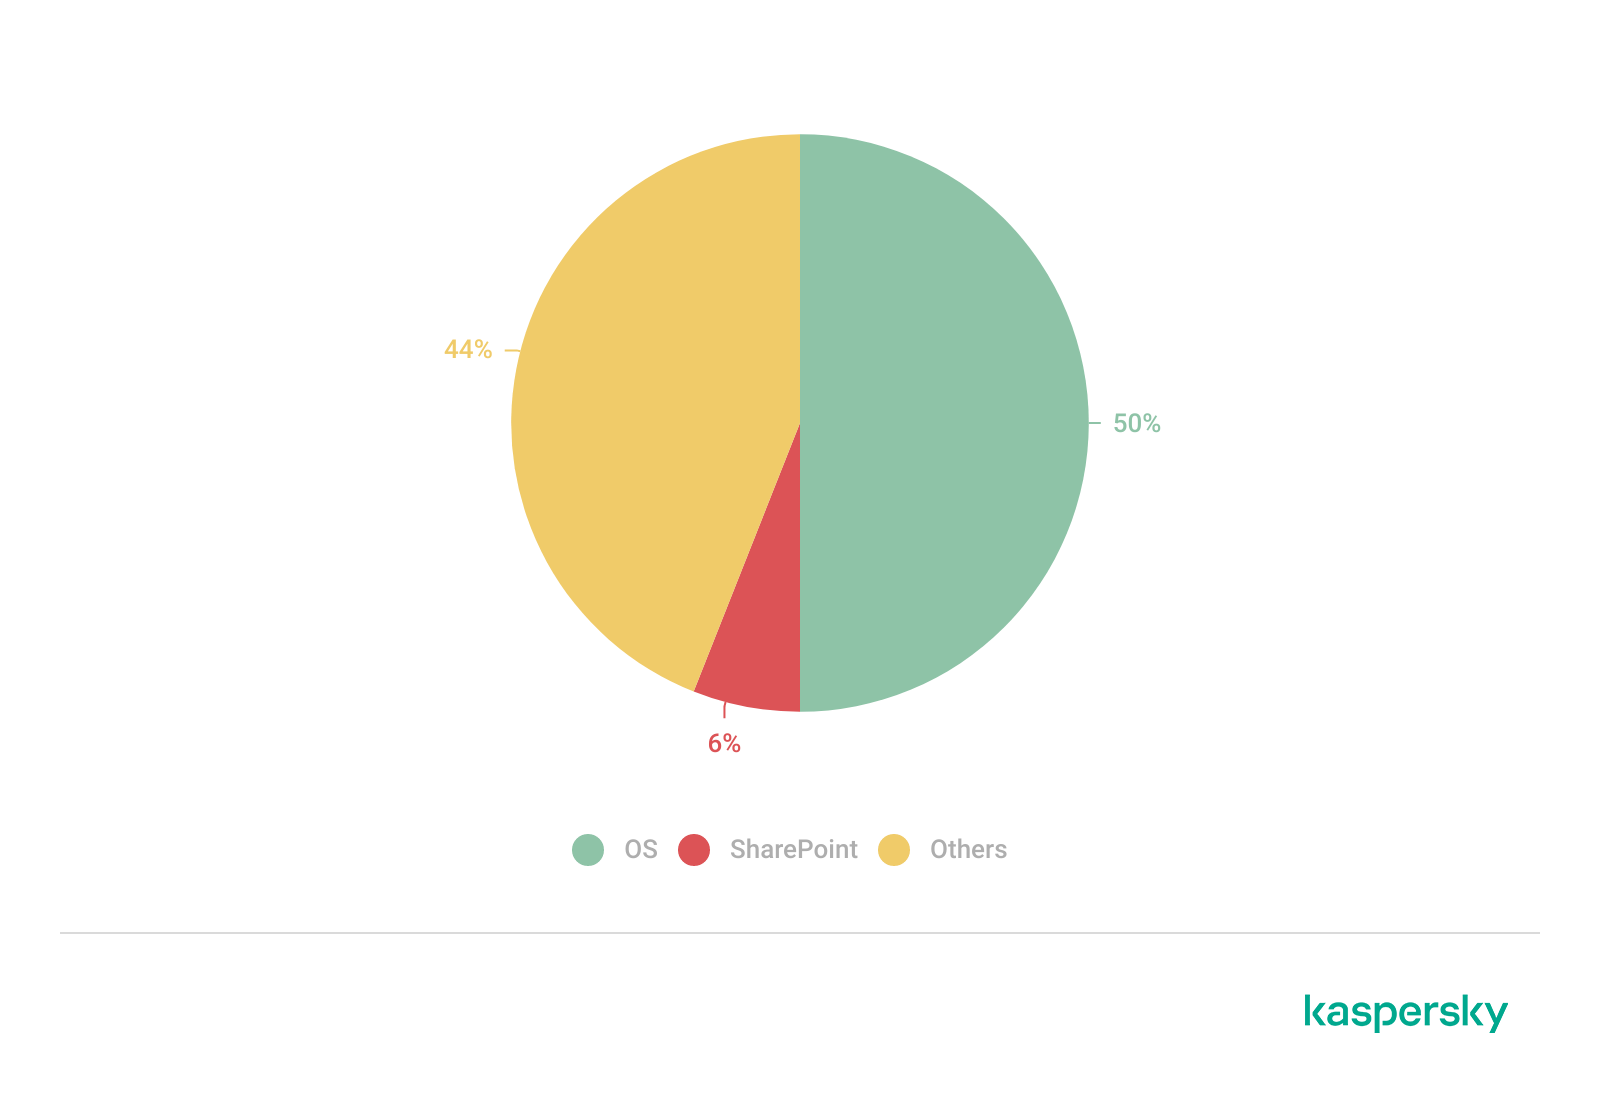
The distribution of published exploits by software type in Q2 2026 includes categories that haven’t appeared in the sample for a long time. For instance, we’re once again seeing exploits targeting SharePoint. It’s worth noting that while several vulnerability write-ups for Exchange and SharePoint were published during the quarter, most turned out to be fake, AI-generated research. While the articles and exploit source code themselves look fairly polished, they describe nonexistent problems in the software or its components — often close to genuinely vulnerable mechanisms — in order to mislead researchers. This type of attack is aimed at increasing the time it takes to detect real vulnerabilities. In some cases, the description of a nonexistent vulnerability came bundled with completely unrelated malware.
Distribution of published exploits by platform, Q1 2026 (download)
Distribution of published exploits by platform, Q2 2026 (download)
Vulnerability exploitation in APT attacks
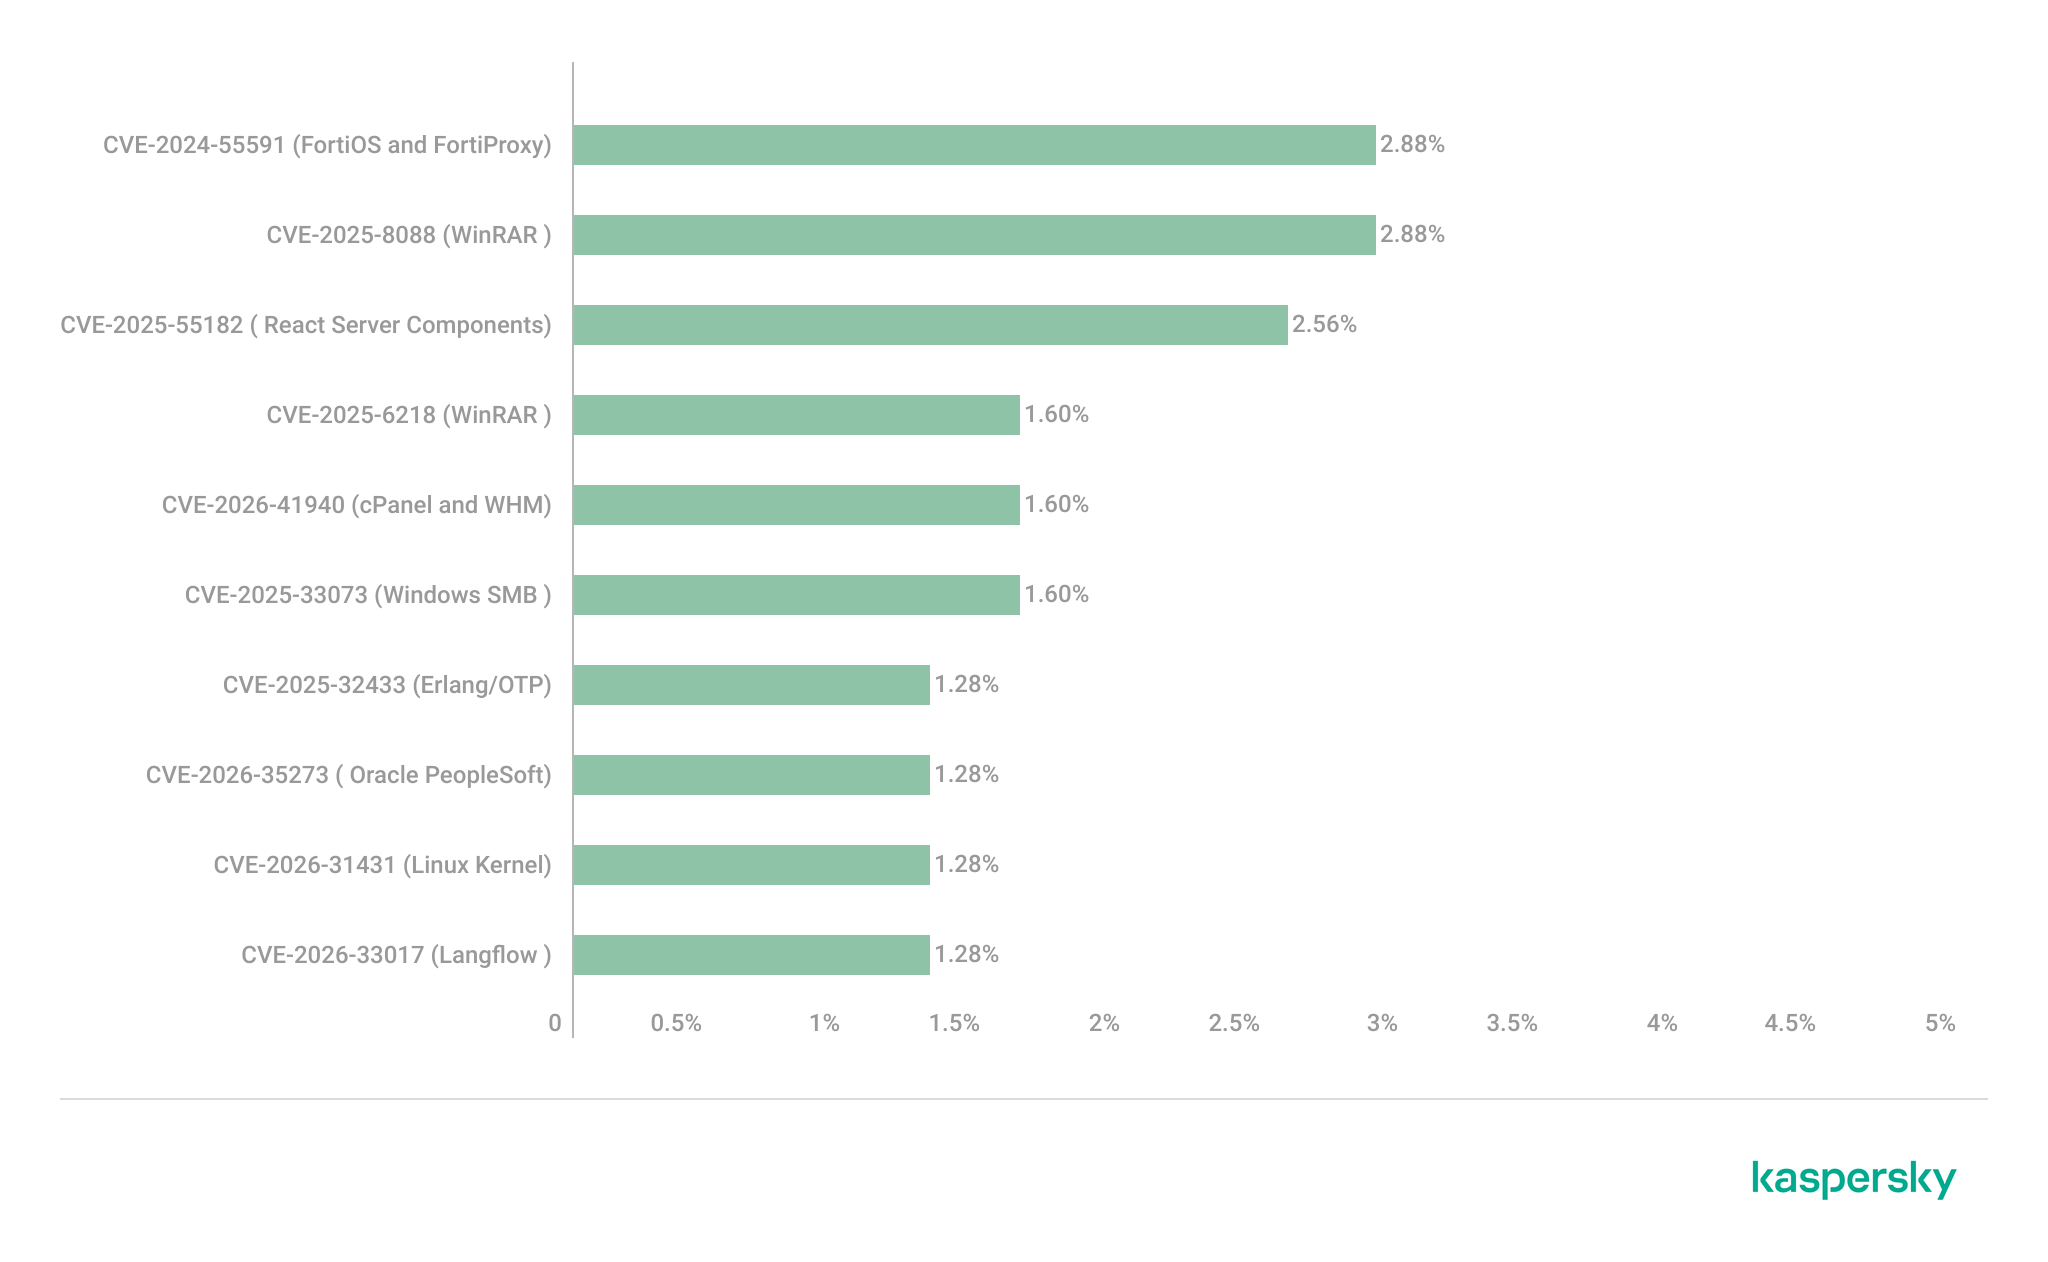
We analyzed which vulnerabilities were exploited in APT attacks during Q2 2026. The rankings provided below include data based on our telemetry, research, and open sources.
TOP 10 vulnerabilities exploited in APT attacks, Q2 2026 (download)
In Q2 2026, a trend emerged in APT attacks toward exploiting new vulnerabilities right from the moment they’re published. As before, we’re also seeing a large number of zero-day vulnerabilities. The Langflow vulnerability deserves particular attention: it’s one of the first cases of an APT group exploiting AI technology, which many organizations are only just beginning to integrate. Because most of this tech is proprietary, it has a considerable number of security blind spots. Therefore, given the growing number of AI-based automation tools, we strongly recommend going beyond the usual patching and developing secure procedures for credential use and sensitive data handling in systems that rely on agents and LLMs.
C2 frameworks
In this section, we examine the most popular C2 frameworks used by APT groups and analyze the vulnerabilities targeted by the exploits that interacted with C2 agents in APT attacks.
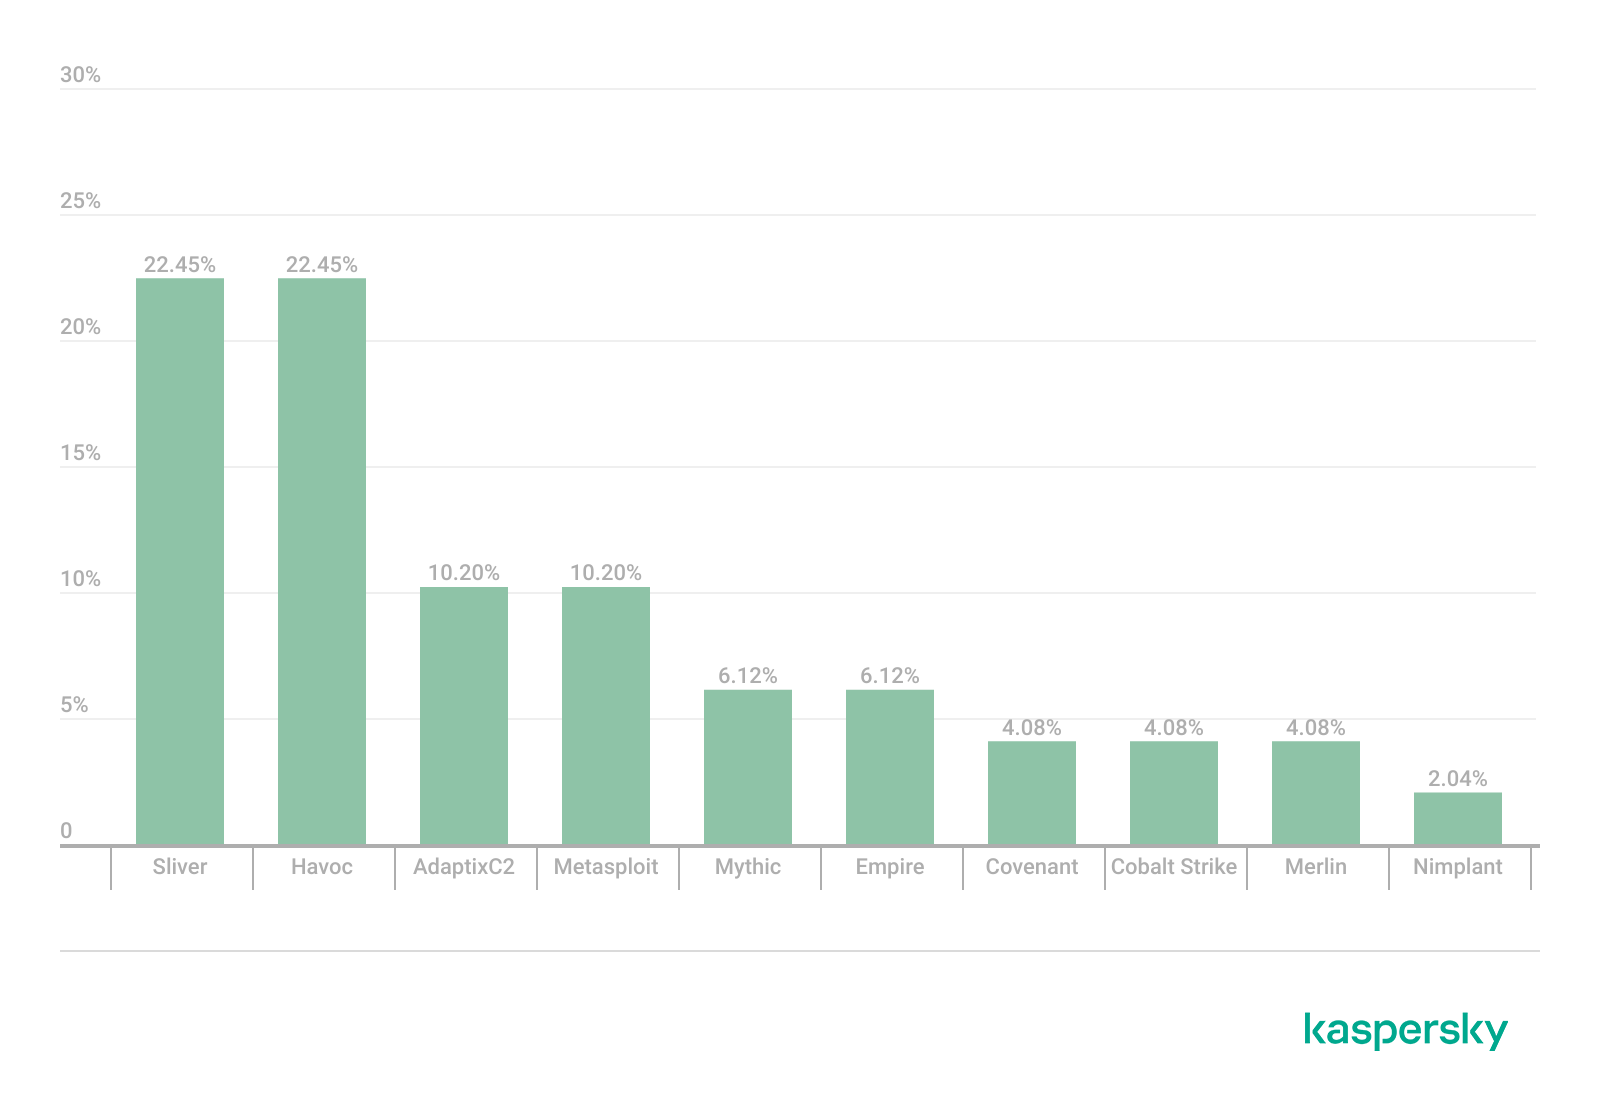
The chart below shows the frequency of known C2 framework usage in attacks during Q2 2026, according to open sources.
TOP 10 C2 frameworks used by APTs to compromise user systems, Q2 2026 (download)
Sliver, Havoc, AdaptixC2, and Metasploit remain the most widely used C2 frameworks. After studying open sources and analyzing samples of malicious C2 agents that contained exploits, we determined that the following vulnerabilities were utilized in APT attacks involving the C2 frameworks mentioned above:
CVE-2026-35273: a vulnerability in Oracle PeopleSoft PeopleTools that security vendors classify as server-side request forgery (SSRF). The details of the vulnerability have never been disclosed, although some research covers the post-exploitation steps
CVE-2023-46604: an insecure deserialization vulnerability in Apache ActiveMQ that allows arbitrary code execution in the context of the service process
CVE-2024-12356 and CVE-2026-1731: command injection vulnerabilities in BeyondTrust software that allow an attacker to send malicious commands even without system authentication
CVE-2023-36884: a vulnerability in the Windows Search component that allows commands to be run on the system, bypassing the mark-of-the-web (MoTW) mechanism
CVE-2025-53770: an insecure deserialization vulnerability in Microsoft SharePoint that allows for unauthenticated command execution on the server
CVE-2025-8088 and CVE-2025-6218: similar directory traversal vulnerabilities in WinRAR that allow files to be extracted from an archive to a predetermined path, potentially without the archiving utility displaying any alerts to the user
These vulnerabilities show that attackers used them for initial access and privilege escalation on vulnerable systems, setting the stage for launching a C2 agent. They include both zero-day vulnerabilities and fairly well-known security issues.
LLM/AI tool vulnerabilities
This section analyzes data published in Kaspersky’s vulnerability knowledge base. We reviewed the Q2 2026 version of the knowledge base.
As mentioned above, AI tools, plugins, and technologies have proven fairly effective at automating the search for problematic code and anomalous behavior. The high speed at which new vulnerabilities are being discovered has naturally created a need to fix them just as quickly. AI is often used for this too, which increases the volume of code being generated. However, neither code written without human involvement nor AI-generated advice is always correct.
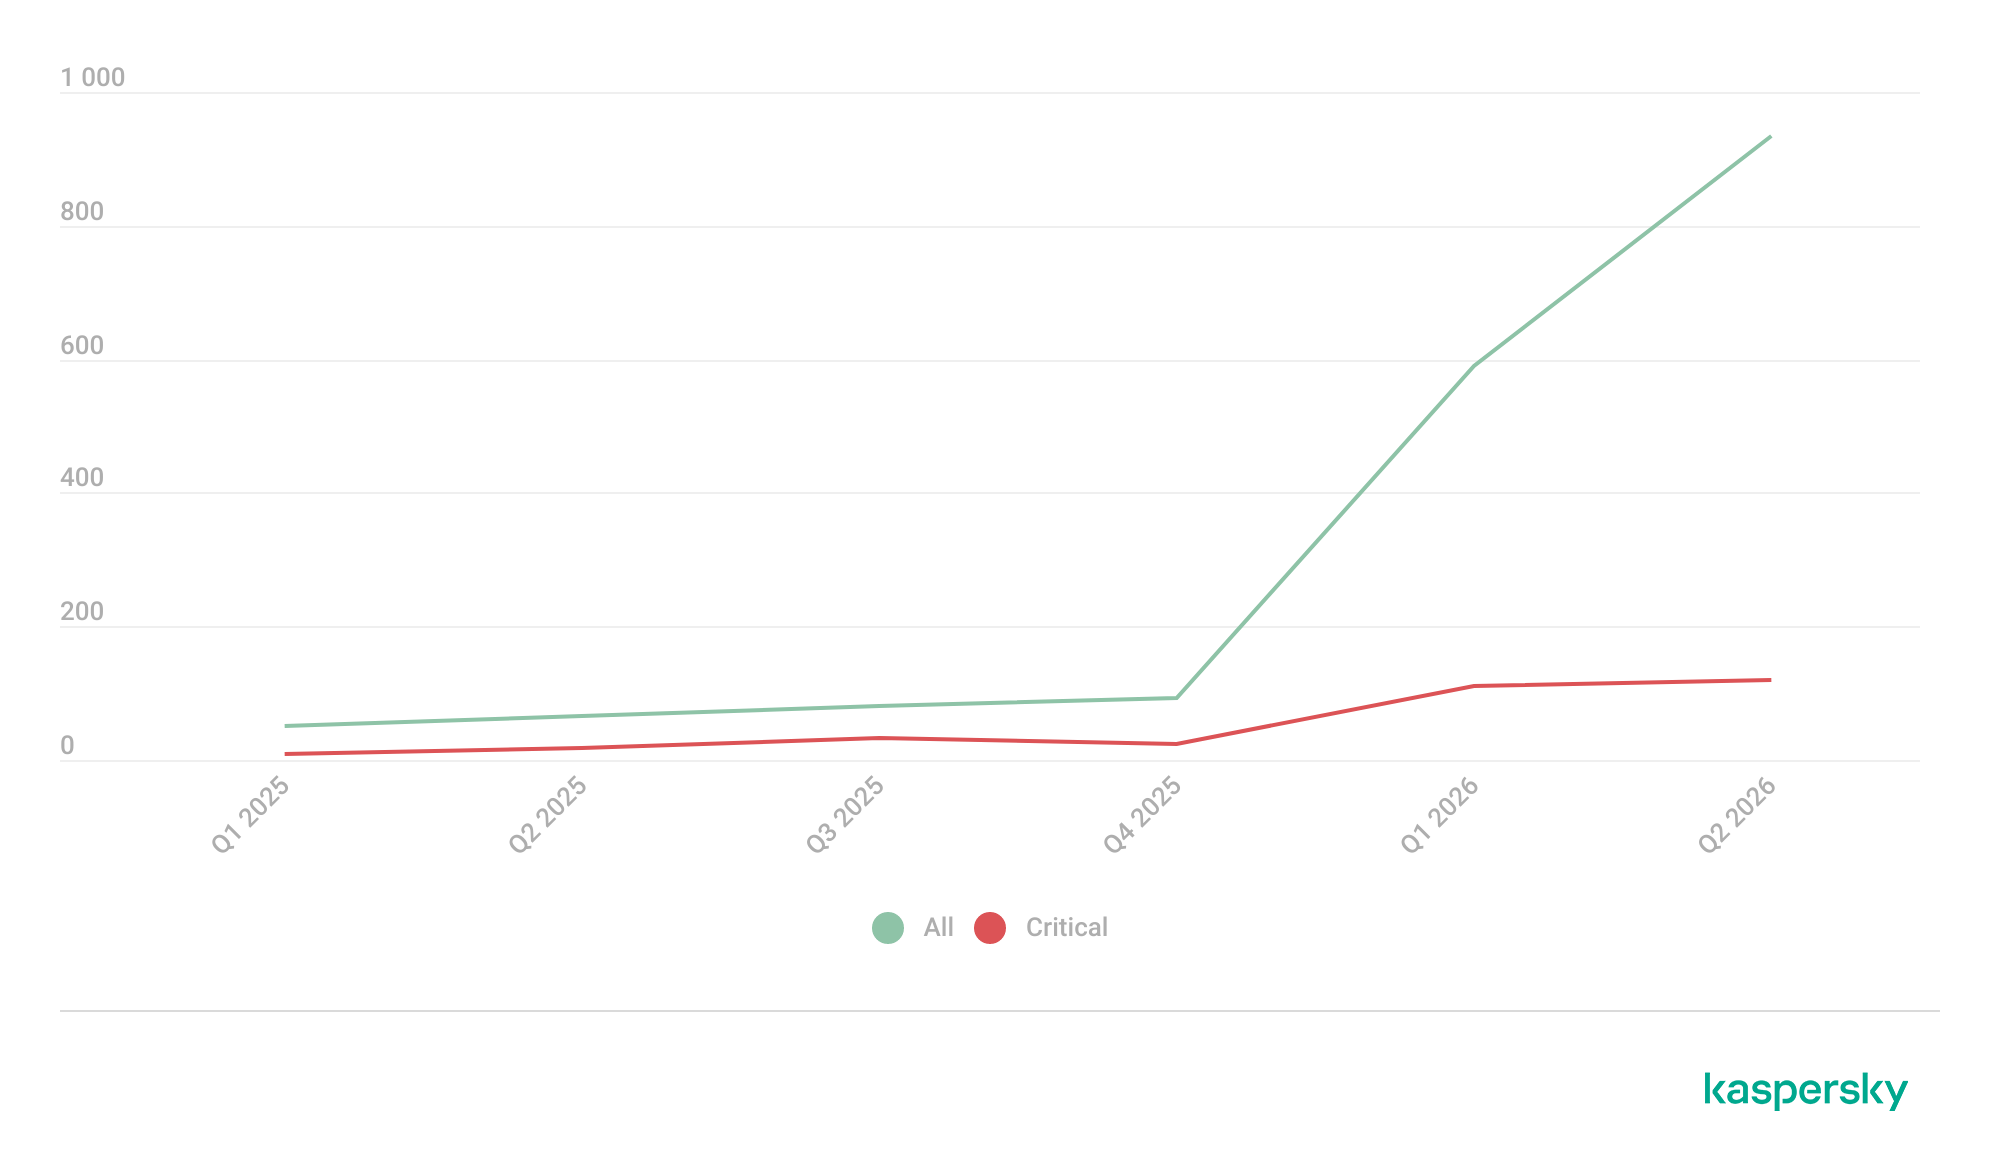
The chart below covers registered vulnerabilities in AI tools for 2025–2026.
Number of published vulnerabilities in LLMs, AI tools, and plugins with similar functionality, 2025–2026 (download)
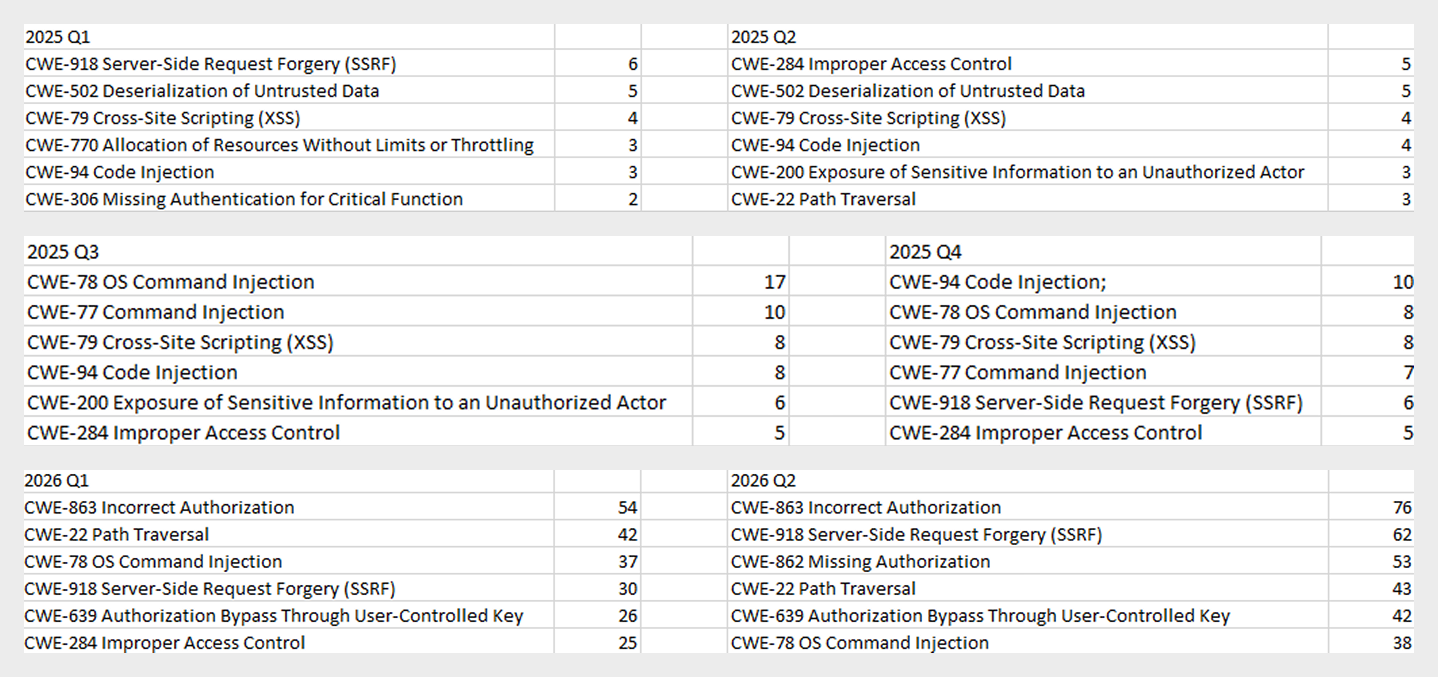
As the charts show, AI tools are racking up a substantial number of registered vulnerabilities, and that number keeps growing quarter over quarter. It’s also worth looking at how AI tool vulnerabilities break down by type, according to the CWE system:
TOP 6 vulnerability types in products that implement or use AI/LLM logic, 2025–2026
Interestingly, vulnerabilities of an undetermined type have ranked first in every quarter since the start of 2025. Traditionally-made software has the same issue, and it doesn’t look like the growing number of AI tools will fix it. It’s also notable that the list includes classes CWE developers themselves don’t recommend using for vulnerability classification, since they lump together a whole range of more specific types. CWE-284 is an example of this.
Looking at the most common classes, the key issues found in AI-related software can be summed up as follows:
Inadequate access control over critical system objects
Improper implementation of authentication and authorization mechanisms
Injections
It’s worth noting that injection-related vulnerabilities were relatively rare before AI agents took off (previously, they mostly affected web apps). Recently, though, these security issues have become relevant again.
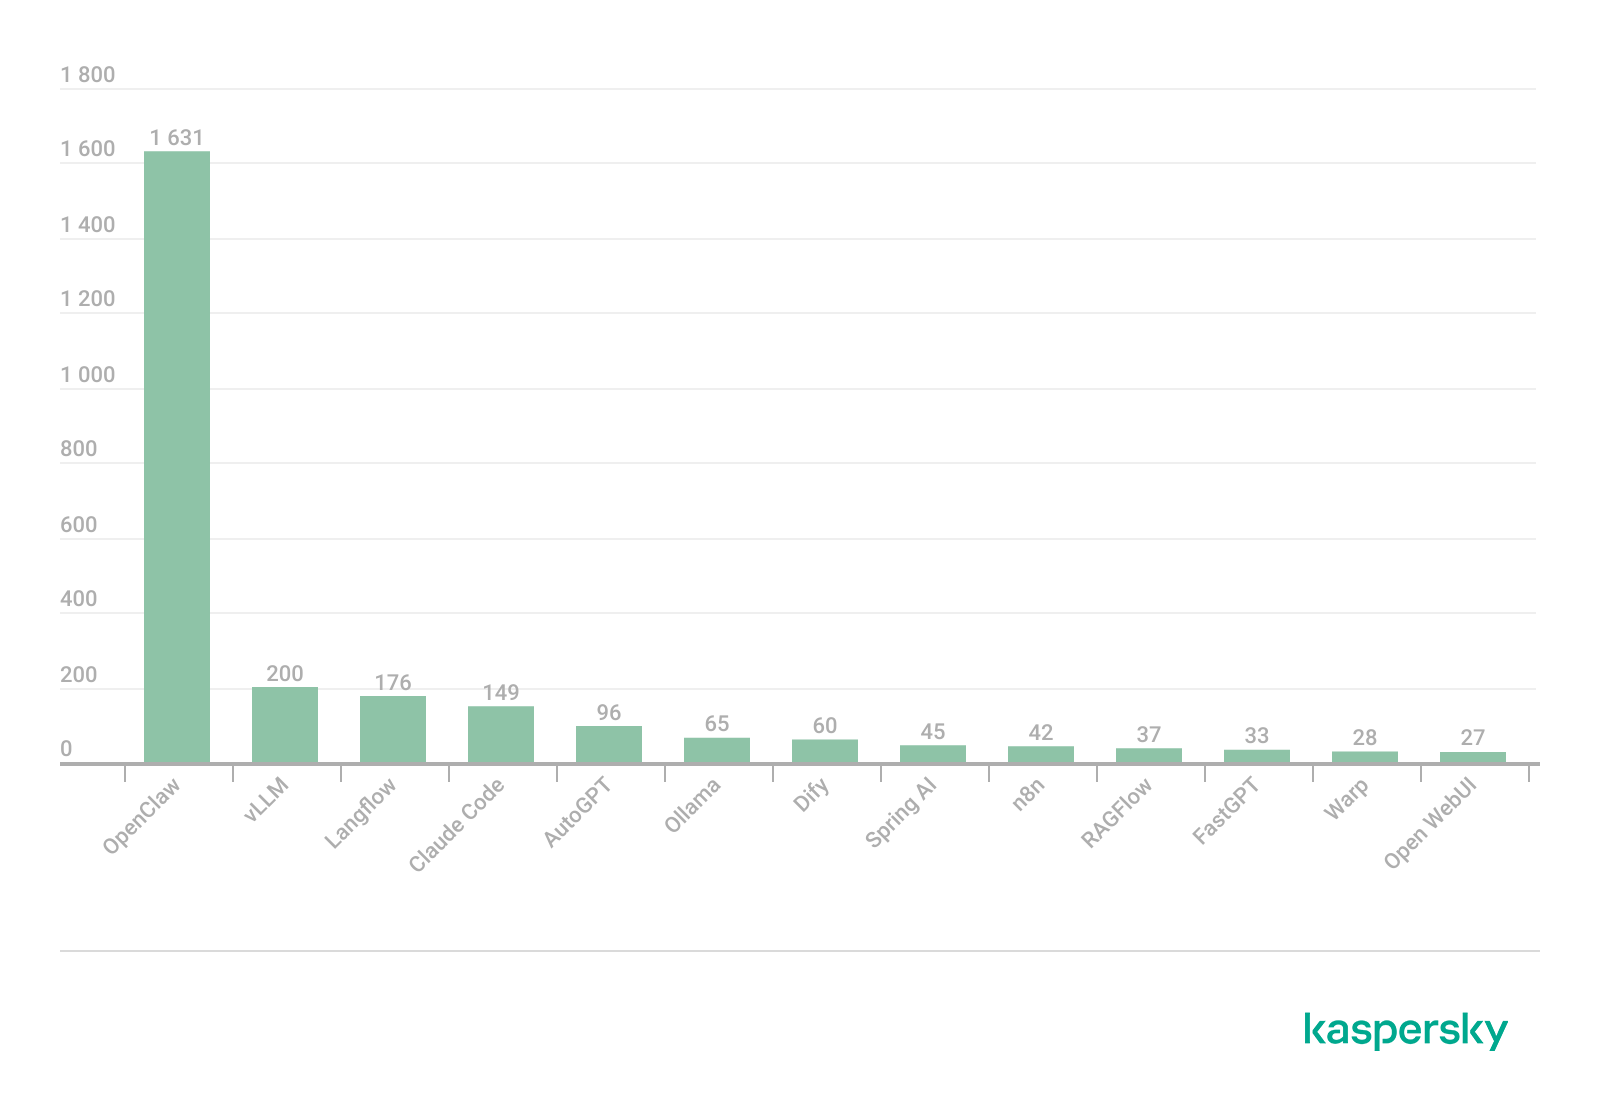
Looking back at a year and a half of the AI boom, one conclusion stands out regarding registered vulnerabilities: AI tool developers are more focused on expanding functionality than on security. This is worth keeping in mind when using these tools. Let’s look at the projects and applications that either integrated AI tools or offered them as the core product. Below is a list of the those with the highest number of registered vulnerabilities for 2025–2026.
TOP AI/LLM-related projects by number of published vulnerabilities, 2025–2026 (download)
Notable vulnerabilities
This section highlights the most significant vulnerabilities published in Q2 2026 that have publicly available descriptions. Since the above already covers several significant vulnerabilities published during the reporting period, this section consists mainly of LLM/AI tool vulnerabilities.
CVE-2026-25253: a gatewayUrl vulnerability in OpenClaw
The issue stems from the fact that the OpenClaw user interface trusts the value of the gatewayUrl parameter passed in the URL and automatically establishes a WebSocket connection to the specified address. During this connection process, it sends an authentication token without any additional user confirmation.
The attack algorithm exploiting this vulnerability works as follows:
The application obtains a critical connection address from an external source (the gatewayUrl URL parameter), which is controlled by the attacker.
There is no validation before use.
The client automatically initiates a connection to the address specified in the parameter, which belongs to the attacker.
While connected, the application sends credentials (an access token) to the specified address.
If the attacker obtains a valid token, the consequences depend on that token’s level of access within the system. In general, this could lead to:
User session compromise
Execution of operations on the user’s behalf
Modification of the AI agent configuration
Unauthorized access to tools and resources connected to the agent
Under certain OpenClaw configurations, further compromise of the host running the agent
It’s worth noting that the risk of exploitation arises from a combination of several factors: the automatic connection and token transmission, the lack of address trust verification, and the high privileges granted to the local AI agent.
CVE-2026-41948: a path traversal vulnerability in the Dify AI platform
The vulnerability lets an authenticated user craft a request that enables the application to escape its permitted tenant and gain access to internal REST APIs that weren’t meant for that user. The root cause is insufficient normalization and validation of the URL path before it’s passed to the internal service.
Depending on the Dify configuration, the consequences can include:
Unauthorized access to internal service interfaces
Breach of isolation between workspaces
Exposure of internal service information
Conditions favorable to further attacks when combined with other vulnerabilities
The use of Dify in enterprise AI platforms is particularly risky, since internal services there tend to hold elevated privileges.
CVE-2026-45386: an improper access control vulnerability in Open WebUI
In Open WebUI, pin/unpin operations on messages are write operations, since they modify that message’s metadata (is_pinned, pinned_by, pinned_at). In vulnerable versions, however, before performing these actions, the API only checked for read access to the channel (a chat between a user or group and the AI) containing the message, not permission to modify its content. As a result, a user with a role limited to viewing messages could still change a message’s pinned status.
The vulnerability’s mechanism works as follows:
The user initiates an action that changes the state of an object.
The application treats this action as a regular read request.
Only channel view permission is checked.
The application performs a write without verifying the required user authorization.
This violates one of the fundamental principles of access control models — namely, that any operation that changes the state of data must be checked for the appropriate write or moderation permissions, regardless of whether the object itself is readable.
Although the vulnerability doesn’t lead to arbitrary code execution or compromise of sensitive data, it can affect data integrity and collaborative workflows. Potential consequences of exploitation include unauthorized pinning or unpinning of messages, disruption of channel moderators’ and administrators’ activities, changes to the display order of important information, and even the potential spread of false or misleading information by altering the channel containing a pinned message.
Open WebUI is widely used as an interface for interacting with local and enterprise LLMs. In these systems, pinned messages often contain important instructions, announcements, or tips for users. The ability to modify them with minimal privileges can disrupt collaborative workflows, cause confusion, and undermine trust in information published by administrators and moderators.
CVE-2026-45501: a vulnerability in Microsoft Exchange
The vulnerability stems from improper neutralization of user input when generating Exchange web pages. As a result, the browser may interpret specially crafted data as active content instead of plain text.
Although Microsoft categorizes the potential impact of exploiting this vulnerability as spoofing, flaws like this can lead to alteration of displayed content, imitation of trusted interfaces, actions on behalf of the user within an active session, and abuse of user trust.
It’s worth noting that issues like this are still relevant in modern software, given that mechanisms like Content Security Policy and various parsers were specifically created to help developers neutralize dangerous parts of user page content.
Conclusion and advice
Q2 brought the first significant results of AI automation adoption in software development and vulnerability hunting tools. This research shows that beyond traditional patch management, organizations now need real-time monitoring of systems and access controls, since infrastructure and everyday applications now contain far more AI functionality that could lead to compromise.
Accordingly, besides quickly detecting infrastructure vulnerabilities and managing security patches, modern enterprise-grade security solutions need to provide a broad range of preventive measures for tracking the overall health of systems and workstations. Kaspersky Next meets these requirements by combining proactive mechanisms with the ability to respond promptly to emerging threats.
The vulnerability landscape shifted significantly in Q2 2026. First, the number of registered CVEs reached an unprecedented level. This is driven primarily by the widespread adoption of AI, both for application development and search for security flaws. This resulted in entire new classes of vulnerabilities emerging, particularly in the Linux networking subsystem.
Second, security researchers have been publishing exploits for unpatched vulnerabilities more frequently. Publications like these can generate significant fallout, since they potentially open the door for attackers to target unprotected systems.
Statistics on registered vulnerabilities
This section provides statistical data on registered vulnerabilities. The data comes from Kaspersky’s vulnerability knowledge base, which draws on the CVE database as well as the Russian BDU database and GitHub Advisory (GHSA). As a result, the figures for previous reporting periods may differ from those published in earlier reports.
We examine the number of registered vulnerabilities for each month over the last five years. As the chart below shows, this number continues to surge, a trend reflected across all the databases we track. It’s driven primarily by the widespread adoption of AI tools: as we predicted in our previous report, these tools have played a major role in the discovery of vulnerabilities in third-party software. Meanwhile, these tools often contain security issues of their own. For example, OpenClaw, a popular AI project, ranked 12th among those with the highest number of vulnerabilities discovered and published in Q2, with over 200 CVEs registered during the reporting period. Finally, AI development tools are also contributing to the vulnerability landscape, since the quality of the code they produce can vary widely. Therefore, the rate at which new vulnerabilities are discovered will inevitably keep growing.
Total published vulnerabilities per month from 2022 through 2026 (download)
Next, we analyze the number of new critical vulnerabilities (CVSS > 9.0) over the same period.
Total critical vulnerabilities published per month from 2022 through 2026 (download)
As the chart shows, the number of published critical vulnerabilities jumped sharply in Q2. This is because using AI for vulnerability research makes it possible to analyze massive amounts of previously unexamined code, uncover new attack surfaces, and identify entire classes of vulnerabilities that have gone unnoticed for decades. In particular, AI was used to find a series of Dirty Frag vulnerabilities in the Linux kernel.
Exploitation statistics
This section presents statistics on vulnerability exploitation for Q2 2026. The data draws on open sources and our telemetry.
Windows and Linux vulnerability exploitation
Q2 2026 saw a new precedent in the publication of vulnerabilities in Windows components and exploits for these: researchers no longer waiting for CVE registration, let alone patches. A case in point: a researcher who goes by Nightmare Eclipse (also known as Chaotic Eclipse) published a list of new “named” vulnerabilities across various Windows subsystems. At the time the technical details were published, none of the vulnerabilities had been assigned a CVE identifier:
BlueHammer: a local privilege escalation vulnerability in Windows Defender. During signature database updates, a time-of-check to time-of-use (TOCTOU) race condition occurs, allowing an attacker to substitute the directory where temporary update files are written. The researcher published a fully functional exploit for the vulnerability.
RedSun: another logical vulnerability in Windows Defender with a working exploit. Suspicious and malicious files marked as “cloud” can be overwritten or restored to their original directory with elevated privileges. The exploit incorporates fragments of algorithms that make it possible to leverage various logical vulnerabilities in Windows, effectively combining a large number of popular exploitation techniques.
YellowKey: a vulnerability that lets the user bypass BitLocker full-disk encryption and access system data through the Windows Recovery Environment (WinRE). A fully functional exploit was also published.
GreenPlasma: a vulnerability that enables system object injection via the CTF loader for the Collaborative Translation Framework (CTFMON) service in Windows. The original publication included an exploit with limited functionality.
RoguePlanet: yet another Windows Defender vulnerability that, like BlueHammer, stems from a TOCTOU issue, this time in the engine responsible for real-time system scanning. The published exploit uses the vulnerability to overwrite the system file wermgr.exe with a malicious one.
UnDefend: another vulnerability in the Windows Defender service. This time, the exploit causes a denial of service and blocks updates.
Even though such cases remain isolated for now, we believe they’ll grow into a full-fledged trend. Early publication of exploits gives attackers an advantage over software developers, who are left with no time to fix the issues.
Veteran vulnerabilities in Windows software also remain relevant. These are the ones our solutions most frequently detect exploits for:
CVE-2018-0802: a remote code execution (RCE) vulnerability in the Equation Editor component
CVE-2017-11882: another RCE vulnerability also affecting Equation Editor
CVE-2017-0199: a vulnerability in Microsoft Office and WordPad that allows an attacker to gain control over the system
CVE-2023-38831: a vulnerability in WinRAR that involves improper handling of objects within an archive
CVE-2025-6218 (formerly ZDI-CAN-27198): another WinRAR vulnerability allowing the specification of relative paths to extract files into arbitrary directories, potentially leading to malicious command execution
CVE-2025-8088: a vulnerability similar in exploitation method to CVE-2025-6218. The attackers used NTFS Streams to circumvent controls on the directory into which files are being unpacked
The vulnerabilities listed here can be leveraged to gain initial access to a vulnerable system and for privilege escalation. This underscores the critical importance of timely software updates.
That said, the number of Windows users who encountered exploits declined slightly in Q2, hitting an 18-month low.
Dynamics of the number of Windows users encountering exploits, Q1 2025 – Q2 2026. The number of users who encountered exploits in Q1 2025 is taken as 100% (download)
Linux also hit a rough patch in Q2 2026. Specifically, the period saw the disclosure of the Dirty Frag family of vulnerabilities, which lets an attacker reliably escalate privileges within the operating system.
All the vulnerabilities published in Q2 2026 were, in one way or another, related to the Linux caching subsystem. Here are the ones being most actively exploited:
CVE-2026-31431 (Copy Fail): a local privilege escalation vulnerability in the Linux kernel that lets an unprivileged user modify the page cache and gain root privileges. Especially dangerous for cloud and containerized environments
CVE-2026-43284, CVE-2026-43500 (Dirty Frag): a family of vulnerabilities in the Linux networking subsystem (IPsec ESP and RxRPC) that lets a local user overwrite the page cache and escalate privileges to root
CVE-2026-46300 (Fragnesia): a local privilege escalation vulnerability in the Linux kernel related to packet fragment handling and the page cache mechanism. It lets an unprivileged user gain root privileges and is also classified as part of the Dirty Frag family
CVE-2026-31635 (DirtyDecrypt): a Linux kernel vulnerability that lets a local attacker escalate privileges due to improper handling of decryption operations and page cache data modification
CVE-2026-43494 (PinTheft): a Linux kernel vulnerability that lets a local user gain elevated privileges due to errors in the memory page pinning mechanism
CVE-2026-46331 (pedit COW): a vulnerability in the Linux kernel’s traffic control subsystem (tc-pedit) that exploits a flaw in copy-on-write to modify the page cache and subsequently escalate privileges to root
The vulnerabilities described above were quickly embraced by attackers. At the same time, our solutions continue to detect exploitation attempts targeting older vulnerabilities as well:
CVE-2022-0847: a vulnerability known as Dirty Pipe, which enables privilege escalation and the hijacking of running applications
CVE-2019-13272: a vulnerability caused by improper handling of privilege inheritance, which can be exploited to achieve privilege escalation
CVE-2021-22555: a heap out-of-bounds write vulnerability in the Netfilter kernel subsystem
CVE-2023-32233: another Netfilter subsystem vulnerability that allows for Use-After-Free conditions and privilege escalation through improper processing of network requests
Dynamics of the number of Linux users encountering exploits, Q1 2025 – Q2 2026. The number of users who encountered exploits in Q1 2025 is taken as 100% (download)
In Q2 2026, the number of Linux users who encountered exploits declined slightly compared to Q1. Given that a significant share of new vulnerabilities are tied to the operating system’s caching subsystem, we recommend installing patches as quickly as possible, or disabling vulnerable kernel modules if patching isn’t an option.
Most common published exploits
The distribution of published exploits by software type in Q2 2026 includes categories that haven’t appeared in the sample for a long time. For instance, we’re once again seeing exploits targeting SharePoint. It’s worth noting that while several vulnerability write-ups for Exchange and SharePoint were published during the quarter, most turned out to be fake, AI-generated research. While the articles and exploit source code themselves look fairly polished, they describe nonexistent problems in the software or its components — often close to genuinely vulnerable mechanisms — in order to mislead researchers. This type of attack is aimed at increasing the time it takes to detect real vulnerabilities. In some cases, the description of a nonexistent vulnerability came bundled with completely unrelated malware.
Distribution of published exploits by platform, Q1 2026 (download)
Distribution of published exploits by platform, Q2 2026 (download)
Vulnerability exploitation in APT attacks
We analyzed which vulnerabilities were exploited in APT attacks during Q2 2026. The rankings provided below include data based on our telemetry, research, and open sources.
TOP 10 vulnerabilities exploited in APT attacks, Q2 2026 (download)
In Q2 2026, a trend emerged in APT attacks toward exploiting new vulnerabilities right from the moment they’re published. As before, we’re also seeing a large number of zero-day vulnerabilities. The Langflow vulnerability deserves particular attention: it’s one of the first cases of an APT group exploiting AI technology, which many organizations are only just beginning to integrate. Because most of this tech is proprietary, it has a considerable number of security blind spots. Therefore, given the growing number of AI-based automation tools, we strongly recommend going beyond the usual patching and developing secure procedures for credential use and sensitive data handling in systems that rely on agents and LLMs.
C2 frameworks
In this section, we examine the most popular C2 frameworks used by APT groups and analyze the vulnerabilities targeted by the exploits that interacted with C2 agents in APT attacks.
The chart below shows the frequency of known C2 framework usage in attacks during Q2 2026, according to open sources.
TOP 10 C2 frameworks used by APTs to compromise user systems, Q2 2026 (download)
Sliver, Havoc, AdaptixC2, and Metasploit remain the most widely used C2 frameworks. After studying open sources and analyzing samples of malicious C2 agents that contained exploits, we determined that the following vulnerabilities were utilized in APT attacks involving the C2 frameworks mentioned above:
CVE-2026-35273: a vulnerability in Oracle PeopleSoft PeopleTools that security vendors classify as server-side request forgery (SSRF). The details of the vulnerability have never been disclosed, although some research covers the post-exploitation steps
CVE-2023-46604: an insecure deserialization vulnerability in Apache ActiveMQ that allows arbitrary code execution in the context of the service process
CVE-2024-12356 and CVE-2026-1731: command injection vulnerabilities in BeyondTrust software that allow an attacker to send malicious commands even without system authentication
CVE-2023-36884: a vulnerability in the Windows Search component that allows commands to be run on the system, bypassing the mark-of-the-web (MoTW) mechanism
CVE-2025-53770: an insecure deserialization vulnerability in Microsoft SharePoint that allows for unauthenticated command execution on the server
CVE-2025-8088 and CVE-2025-6218: similar directory traversal vulnerabilities in WinRAR that allow files to be extracted from an archive to a predetermined path, potentially without the archiving utility displaying any alerts to the user
These vulnerabilities show that attackers used them for initial access and privilege escalation on vulnerable systems, setting the stage for launching a C2 agent. They include both zero-day vulnerabilities and fairly well-known security issues.
LLM/AI tool vulnerabilities
This section analyzes data published in Kaspersky’s vulnerability knowledge base. We reviewed the Q2 2026 version of the knowledge base.
As mentioned above, AI tools, plugins, and technologies have proven fairly effective at automating the search for problematic code and anomalous behavior. The high speed at which new vulnerabilities are being discovered has naturally created a need to fix them just as quickly. AI is often used for this too, which increases the volume of code being generated. However, neither code written without human involvement nor AI-generated advice is always correct.
The chart below covers registered vulnerabilities in AI tools for 2025–2026.
Number of published vulnerabilities in LLMs, AI tools, and plugins with similar functionality, 2025–2026 (download)
As the charts show, AI tools are racking up a substantial number of registered vulnerabilities, and that number keeps growing quarter over quarter. It’s also worth looking at how AI tool vulnerabilities break down by type, according to the CWE system:
TOP 6 vulnerability types in products that implement or use AI/LLM logic, 2025–2026
Interestingly, vulnerabilities of an undetermined type have ranked first in every quarter since the start of 2025. Traditionally-made software has the same issue, and it doesn’t look like the growing number of AI tools will fix it. It’s also notable that the list includes classes CWE developers themselves don’t recommend using for vulnerability classification, since they lump together a whole range of more specific types. CWE-284 is an example of this.
Looking at the most common classes, the key issues found in AI-related software can be summed up as follows:
Inadequate access control over critical system objects
Improper implementation of authentication and authorization mechanisms
Injections
It’s worth noting that injection-related vulnerabilities were relatively rare before AI agents took off (previously, they mostly affected web apps). Recently, though, these security issues have become relevant again.
Looking back at a year and a half of the AI boom, one conclusion stands out regarding registered vulnerabilities: AI tool developers are more focused on expanding functionality than on security. This is worth keeping in mind when using these tools. Let’s look at the projects and applications that either integrated AI tools or offered them as the core product. Below is a list of the those with the highest number of registered vulnerabilities for 2025–2026.
TOP AI/LLM-related projects by number of published vulnerabilities, 2025–2026 (download)
Notable vulnerabilities
This section highlights the most significant vulnerabilities published in Q2 2026 that have publicly available descriptions. Since the above already covers several significant vulnerabilities published during the reporting period, this section consists mainly of LLM/AI tool vulnerabilities.
CVE-2026-25253: a gatewayUrl vulnerability in OpenClaw
The issue stems from the fact that the OpenClaw user interface trusts the value of the gatewayUrl parameter passed in the URL and automatically establishes a WebSocket connection to the specified address. During this connection process, it sends an authentication token without any additional user confirmation.
The attack algorithm exploiting this vulnerability works as follows:
The application obtains a critical connection address from an external source (the gatewayUrl URL parameter), which is controlled by the attacker.
There is no validation before use.
The client automatically initiates a connection to the address specified in the parameter, which belongs to the attacker.
While connected, the application sends credentials (an access token) to the specified address.
If the attacker obtains a valid token, the consequences depend on that token’s level of access within the system. In general, this could lead to:
User session compromise
Execution of operations on the user’s behalf
Modification of the AI agent configuration
Unauthorized access to tools and resources connected to the agent
Under certain OpenClaw configurations, further compromise of the host running the agent
It’s worth noting that the risk of exploitation arises from a combination of several factors: the automatic connection and token transmission, the lack of address trust verification, and the high privileges granted to the local AI agent.
CVE-2026-41948: a path traversal vulnerability in the Dify AI platform
The vulnerability lets an authenticated user craft a request that enables the application to escape its permitted tenant and gain access to internal REST APIs that weren’t meant for that user. The root cause is insufficient normalization and validation of the URL path before it’s passed to the internal service.
Depending on the Dify configuration, the consequences can include:
Unauthorized access to internal service interfaces
Breach of isolation between workspaces
Exposure of internal service information
Conditions favorable to further attacks when combined with other vulnerabilities
The use of Dify in enterprise AI platforms is particularly risky, since internal services there tend to hold elevated privileges.
CVE-2026-45386: an improper access control vulnerability in Open WebUI
In Open WebUI, pin/unpin operations on messages are write operations, since they modify that message’s metadata (is_pinned, pinned_by, pinned_at). In vulnerable versions, however, before performing these actions, the API only checked for read access to the channel (a chat between a user or group and the AI) containing the message, not permission to modify its content. As a result, a user with a role limited to viewing messages could still change a message’s pinned status.
The vulnerability’s mechanism works as follows:
The user initiates an action that changes the state of an object.
The application treats this action as a regular read request.
Only channel view permission is checked.
The application performs a write without verifying the required user authorization.
This violates one of the fundamental principles of access control models — namely, that any operation that changes the state of data must be checked for the appropriate write or moderation permissions, regardless of whether the object itself is readable.
Although the vulnerability doesn’t lead to arbitrary code execution or compromise of sensitive data, it can affect data integrity and collaborative workflows. Potential consequences of exploitation include unauthorized pinning or unpinning of messages, disruption of channel moderators’ and administrators’ activities, changes to the display order of important information, and even the potential spread of false or misleading information by altering the channel containing a pinned message.
Open WebUI is widely used as an interface for interacting with local and enterprise LLMs. In these systems, pinned messages often contain important instructions, announcements, or tips for users. The ability to modify them with minimal privileges can disrupt collaborative workflows, cause confusion, and undermine trust in information published by administrators and moderators.
CVE-2026-45501: a vulnerability in Microsoft Exchange
The vulnerability stems from improper neutralization of user input when generating Exchange web pages. As a result, the browser may interpret specially crafted data as active content instead of plain text.
Although Microsoft categorizes the potential impact of exploiting this vulnerability as spoofing, flaws like this can lead to alteration of displayed content, imitation of trusted interfaces, actions on behalf of the user within an active session, and abuse of user trust.
It’s worth noting that issues like this are still relevant in modern software, given that mechanisms like Content Security Policy and various parsers were specifically created to help developers neutralize dangerous parts of user page content.
Conclusion and advice
Q2 brought the first significant results of AI automation adoption in software development and vulnerability hunting tools. This research shows that beyond traditional patch management, organizations now need real-time monitoring of systems and access controls, since infrastructure and everyday applications now contain far more AI functionality that could lead to compromise.
Accordingly, besides quickly detecting infrastructure vulnerabilities and managing security patches, modern enterprise-grade security solutions need to provide a broad range of preventive measures for tracking the overall health of systems and workstations. Kaspersky Next meets these requirements by combining proactive mechanisms with the ability to respond promptly to emerging threats.
Frontier AI has compressed attack timelines from weeks to minutes.
For defenders to gain the upper hand, they need to fight back at machine speed. That’s why Palo Alto Networks Unit 42 launched Frontier AI Defense, our comprehensive service that pairs advanced frontier AI models with leading threat intelligence to uncover hidden risks, validate real attack paths, and accelerate remediation before adversaries strike.
Today, in a major milestone for organizations to defend themselves against AI-powered attacks, Unit 42 is expanding its Frontier AI Exposure Analysis capabilities with Anthropic’s Claude Mythos 5, giving organizations access to its advanced cyber capabilities.
Unlocking High-Fidelity Security with the Right Models, Harness and Expertise
While incredibly powerful, achieving high-fidelity results with frontier AI requires three things: the right models, an advanced harness, and the expertise to run it. With Unit 42 Frontier AI Exposure Analysis, guided and reviewed by Unit 42 experts, Claude Mythos 5 goes beyond identifying exposures. It tests whether those exposures can actually be exploited, connects weaknesses into attack paths, and helps prioritize the most urgently needed fixes. That answers the questions conventional scanners alone cannot: Is this exploitable? What can an attacker reach from here? And what should we fix first?
Further,our research shows models have different strengths. Unit 42’s multi-model approach applies the model best suited for the task, improving coverage and results while allowing us to continuously incorporate the strongest new capabilities as models advance.
Human expertise remains at the center. Unit 42 combines these models with our offensive security experts, global Palo Alto Networks telemetry, and Unit 42 Threat Intelligence to turn model output into validated attack paths, prioritized remediation, and clear defensive action.
How It Works
Our Frontier AI Defense service uses the most advanced AI models to discover exposures, test whether they are exploitable, validate attack paths and help customers prioritize what to fix first, including:
Leading Cyber Models: Advanced AI applied to discovery, testing, and validation.
Multi-Model Harness: Dynamic routing for stronger results, wider coverage, and managed costs.
Exposure Discovery: Identification of vulnerabilities, misconfigurations, exposed credentials, and unmanaged attack surfaces across apps and networks.
Advanced Adversary Simulation: Live exploitability testing and end-to-end attack path validation.
Custom Remediation Plans: Prioritized fixes delivered directly into existing IT, development, and security workflows.
Security teams do not need more findings. They need to know which weaknesses lead to a viable attack path. Attackers do not think about applications, identity, cloud, and infrastructure in isolation. They look for ways to move across them to reach their objective.
By putting frontier models to work with Unit 42 experts, we can identify and validate those attack paths before attackers do, and help organizations close them first.
Unit 42 is putting the latest frontier cyber models to work across customer environments to find, validate and help remediate the attack paths that matter most.
In May, we introduced Frontier AI Defense with a warning: the window to get ahead of AI-enabled attacks was shorter than most people realized. Since then, we have briefed more than 1,000 security teams around the world and introduced our Frontier AI Defense service to hundreds of customers.
Today, through our partnership with OpenAI, we are expanding Unit 42 Frontier AI Exposure Analysis to put advanced frontier cyber models directly to work in customer environments. Under Unit 42 direction, these models can find exposures, test whether they are exploitable, validate attack paths and help customers prioritize what to fix first.
Our early work shows why this approach matters: 36% of the exposures we identified map to no known CVE, often because they involve multiple gaps that have to be discovered, chained and tested together.
Bringing the Latest Frontier Cyber Capabilities to Defenders
Palo Alto Networks has been among a limited group of organizations with early access to advanced cyber capabilities from the leading frontier AI labs. Through our partnership with OpenAI, Unit 42 can now bring its latest advanced cyber capabilities, including GPT-5.6 Daybreak, to security testing and validation for our customers. Until now, GPT-5.6 Daybreak has not been available for commercial use.
Frontier models have helped inform the work of our experts. Now they can increasingly perform complex offensive security tasks directly, at machine speed and under Unit 42 direction. That allows us to go deeper than traditional vulnerability discovery by testing exploitability, reasoning across multiple weaknesses and determining how an attacker could use them to achieve an objective.
There is no single best model for every cyber task. Our research has shown that different models have different strengths and find vulnerabilities others miss. A multi-model harness routes work to the model best suited for the task, improving efficacy and coverage while managing the cost of frontier AI at scale. As stronger models emerge, we can incorporate them without rebuilding the offering around a single model or provider.
Unit 42 experts remain central to the process. We combine frontier models with our offensive security expertise, Palo Alto Networks telemetry and Unit 42 Threat Intelligence to validate findings, connect exposures into attack paths and understand what an attacker could ultimately achieve.
Built to Find What Attackers Can Exploit
The expanded service brings five capabilities together:
Leading cyber models: Apply the latest advanced cyber models to improve exposure discovery, testing and validation.
Multi-model harness: Use the right model for the right task to improve efficacy, expand coverage and optimize cost.
Exposure discovery: Find vulnerabilities, misconfigurations, leaked credentials, unmanaged attack surface and other posture gaps across applications and network assets.
Advanced adversary simulation: Actively test exploitability and validate end-to-end attack paths to understand how an attacker could compromise the environment.
Custom remediation plan: Prioritize the fixes that break the most important attack paths and feed those findings into existing IT, development and security workflows.
Most security teams already have more findings than they can act on. The harder problem is knowing which ones create a real path to compromise. Attackers look across applications, infrastructure, identity and cloud for weaknesses they can combine to achieve an objective. Frontier AI Exposure Analysis applies that same adversarial perspective, helping defenders understand which paths matter and what to fix first.
The Asymmetry Runs Both Ways Now
For the past several months, frontier AI has been a story about what is coming for defenders: vulnerability discovery at scale, exploit chaining that sees full-stack logic no scanner catches, and attack cycles compressed to seconds from initial access to exfiltration.
All of that is still true. Our answer has been to put everything we learn testing these frontier models into the hands of defenders. Today, that gets more direct: not just what frontier models have taught us, but the models themselves, working in your environment for your defenders before those same capabilities are working for the attacker.
The window is still closing. We intend to spend it building on the side of the defenders.
Microsoft today released updates to remedy at least 398 security vulnerabilities in its Windows operating systems and supported software, including one weakness that is already being actively exploited and two others that were publicly detailed prior to today.
Image: Shutterstock, Mallika Home Studio.
August’s overstuffed bundle of patch joy from Microsoft did not eclipse its recording breaking release of more than 570 security updates last month, but it is double June’s then-record batch of nearly 200 fixes. Microsoft has attributed the recent patch deluge to vulnerability discoveries aided by artificial intelligence, and experts roundly agree that Windows users should get used to the idea of Patch Tuesdays (the second Tuesday of each month) covering hundreds of newly discovered security flaws.
Fully 42 of the 398 flaws that Microsoft patched today earned Redmond’s most-dire “critical” rating, meaning they are severe enough that malware or malcontents could exploit them to gain remote control over a Windows computer with little to no help from the user.
The sole known “zero day” bug fixed by Microsoft this month is CVE-2026-68820, a privilege escalation weakness in a core Windows component called afd.sys, which the security firm Automox describes as “the driver behind Windows socket connections on effectively every endpoint.”
“This isn’t a front-door bug,” Automox’s Landon Mileswrote in a Patch Tuesday blog post. “It’s step two in a chain: an attacker phishes their way into a low-privilege foothold, then uses the driver flaw to take the box. The 7.0 score reflects the high attack complexity, because race conditions are fiddly. The exploit has to be thrown over and over until the timing lands. Someone is clearly landing it anyway.”
CVE-2026-62832 is another privilege escalation flaw that Microsoft has labeled likely to be exploited; this flaw, in the Windows User Profile Service, may be related to the recent “LegacyHive” public disclosure from the prolific bug hunter known as Nightmare Eclipse. The other publicly disclosed flaw is CVE-2026-72971, a low-impact local tampering vulnerability that Microsoft reckons is unlikely to be exploited.
Other major software makers are likewise increasing their patch volumes and cadence thanks to AI, including Adobe which last month moved to twice-monthly security bulletins published on the 2nd and 4th Tuesday of each month. Cisco, Google, Mozilla and Oracle also are shipping updates far more frequently and abundantly.
By all accounts, AI is quite good at finding security holes in software. But for now at least, patching the resulting bugpocalypse remains a heavily human-centric endeavor, and the jury is still out on whether AI technologies will turn out to be as good at fixing vulnerabilities as they are at finding and exploiting them. This is an important question when one considers that these same AI technologies also are suggesting fixes for the vulnerabilities they find.
Researchers at 1Password recently examined what happens when different large language models (LLMs) generate vulnerability patches for newly disclosed, complex vulnerabilities. They found the LLMs produced patches that failed to fix the flaw or added a new weakness in the process (or both) more than half the time.
Ed Skoudis, president of the SANS Technology Institute, said his team has seen excellent results using AI to generate patches, provided there are humans in the loop to test the suggested fixes and push for iterative improvements.
“AI is rapidly becoming astonishingly good at finding vulnerabilities, but this research shows that fixing them is a very different problem,” Skoudis wrote in a SANS newsletter today. “Don’t expect one-shot AI patching to work reliably. Instead, iterate, test, challenge, improve, and verify. AI can be an extraordinary patching partner, but today it still needs a skilled human at the keyboard.”
Tyler Reguly at Fortra says while reports of Microsoft patching hundreds of vulnerabilities in one go have prompted some organizations to try to patch faster, it’s important to bear in mind that only one of the almost 400 bugs addressed today is known to be actively exploited. Reguly suggested security leaders check in with their teams to see how they’re handling the increasing workloads, which often involve testing fixes before deploying them in production environments.
“If you’re a chief security officer talk to your teams about how they are shifting or modifying their workflows to better accommodate the patching shift that we’re seeing and support them across various organizational units by enabling the changes they want to see made,” Reguly said. “There’s no need to rush these updates, no matter what various vendors and organizations try to tell you. You need to make sure that you are rolling out safe updates that will not negatively impact your systems.”
Speaking of the humans behind the keyboards, don’t neglect to backup your system and/or data before applying this month’s monster patch load. The day after each month’s Patch Tuesday is sometimes derisively referred to as Reboot Wednesday, but it generally doesn’t hurt to wait a few days to apply these huge update bundles because it sometimes takes a couple of days for the occasional misbehaving patch to get ironed out properly by Microsoft.
For a clickable, per-patch breakdown by severity and urgency, check out this roundup from the SANS Internet Storm Center.
Government entities and critical infrastructure were targeted for espionage in SE Asia by attackers using a hybrid toolkit, including custom TinyRCT backdoor.
A cybersecurity startup dangling millions of dollars to acquire zero-day security vulnerabilities in popular software is run by a pair of far-right conspiracy theorists and convicted felons whose most recent ventures included fake intelligence companies and a now-defunct AI-based lobbying platform they operated under assumed names.
The X/Twitter account IRIS C2 (@C2IRIS) has gained more than 4,000 followers since its creation in January 2025, posting frequently about security vulnerabilities, AI and software exploits. IRIS C2 says it is a company in McLean, Va. that sells offensive cybersecurity capabilities.
The IRIS C2 website dangles the possibility of million-dollar payouts for exploits to attract talent.
“Our business model is this,” reads a pinned post on top of the IRIS C2 account on X. “Attract the very best vulnerability researchers and exploit developers in the world to join our company. This mostly revolves around junior engineers with raw talent/extremely high IQ. We don’t care if they have a college degree/industry experience.”
The website linked in that profile — irisc2[.]com — says the company is hiring for a number of open positions, and a recent post on its LinkedIn page enthuses about an overwhelming number of applications from potential employees. The website claims IRIS C2 is in the business of acquiring “zero-day exploits, individual primitives, partial chains, and full capabilities across all major platforms. Payouts range from $10,000 to $7 million depending on target, reliability, and operational value.”
The government contracting portal g2exchange.comreports that irisc2[.]com is operated by a business based in Virginia called Calvexa Group LLC. The “contact” link on the website for Calvexa Group — calvexagroup[.]com — forwards visitors to irisc2[.]com. G2Exchange shows that while Calvexa Group LLC is registered as a federal contractor, it does not appear to be working on any direct government contracts.
A search on the Arlington, Va. address listed in the incorporation records for Calvexa Group LLC finds the property is occupied by Jack Burkman, the 60-year-old founder and managing partner of the lobbying firm Burkman & Associates. When approached with questions about IRIS C2, Burkman referred further inquiries to his longtime associate, 28-year-old Jacob Wohl.
Jack Burkman (left) and Jacob Wohl, at a press conference in August 2020. Image: Wikipedia.
Burkman and Wohl have a storied history of creating fake intelligence companies and using them to spread false claims about and frame public figures, including fabricated sexual assault claims against then FBI director Robert Mueller, and Pete Buttigieg, then mayor of South Bend, Indiana and a Democratic candidate for the presidency. In 2019, Burkman and Wohl held press conferences falsely alleging extramarital affairs by Sen. Elizabeth Warren (D-Mass.) and then-2020 presidential candidate Kamala Harris.
In the wake of the 2020 presidential election, Wohl and Burkman were prosecuted by multiple U.S. states for making thousands of robocalls to residents of battleground states and disseminating false claims about mail-in ballots. They were indicted in Cleveland on 15 felony counts of orchestrating a robocall scheme aimed at suppressing the black vote in Detroit, and were sentenced in late 2025 to probation after their appeals to dismiss the charges were rejected.
In 2022, Wohl and Burkman both pleaded guilty to a single felony charge of telecommunications fraud in Ohio, and sentenced to a fine, probation, and community service. In March 2023, a judge in a New York civil case ruled that Wohl and Burkman had violated federal and state civil rights laws, and the two agreed to pay a $1 million settlement.
In June 2023, the Federal Communications Commission (FCC) imposed a $5.1 million fine against Wohl and Burkman for their robocall campaigns, at the time the largest fine ever sought by the FCC under the Telephone Consumer Protection Act.
Jacob “Jay” Wohl’s GitHub account.
By the age of 17, Wohl had started multiple investment firms, and cultivated the nickname “Wohl of Wall Street” after appearing on Fox News in 2015 to discuss his new hedge funds. In 2017, the Arizona Corporation Commission charged Wohl and his investment funds with 14 counts of securities fraud, and ordered him to pay $35,000 in restitution. In 2019, Wohl pleaded guilty in California to four felony counts of selling unregistered securities and was sentenced to two years of probation.
The market for previously unknown security vulnerabilities has always been populated by a colorful mix of researchers, academics, charlatans, clout-chasers and people actively involved in cybercrime communities. But the market for selling offensive security services to the U.S. government tends to be far more circumspect. Plenty of government contractors recruit vulnerability researchers and pay for the exclusive rights to novel software exploits, yet none of them do so quite as brazenly and openly as IRIS C2.
Recent posts from the Twitter/X account IRISC2 (@c2iris).
Indeed, KrebsOnSecurity was unaware of IRIS C2 until last month, when an attendee at a regional cybersecurity conference shared that Wohl and Calvexa Group were pestering people at the conference about selling their vulnerability research.
In an interview with KrebsOnSecurity, Wohl said Mr. Burkman was not involved in the day-to-day operations of IRIS C2. Wohl shared that IRIS C2 originally began as a penetration testing company, but shifted its focus recently to selling phone-hacking services to the government. Several times throughout the interview, Mr. Wohl mentioned working on federal government contracts, but when pressed for specifics said he was not at liberty to speak publicly about them.
Mr. Wohl said he does not have any formal education or training in computer science or information security, and that most of his knowledge on the matter is self-taught.
“I know more about tech than anyone,” Wohl bragged. “My background has always been extremely technical, and I’ve always been deeply into tech. People know me as someone who is able to create spectacularly exquisite capabilities that would make your head spin.”
Wohl said security researchers bring the company unique vulnerability findings “on a regular basis,” but that in many cases those findings are preliminary and not fully fleshed-out.
“Let’s say someone finds a flaw in a media decoder on a phone,” Wohl said. “A lot of times what we receive is an exploit primitive, where the idea is there but the [execution] needs work. You need that exploit to be stable and reliable, and that’s what we do.”
Wohl claims IRIS C2 has approximately 40 employees, although he said none of them are allowed to list their employment on LinkedIn for operational security reasons. In May, the author of the IRIS C2 account on X said that his girlfriend had no idea what he did for a living. But if IRIS C2 has any other employees, they may be similarly unaware of Mr. Wohl’s history of outright fabrications — or even his real name.
In September 2024, Politicoreported that Burkman and Wohl were bragging about big companies supposedly buying services from their now-defunct company LobbyMatic, which claimed to use artificial intelligence to assist in political lobbying efforts. However, Politico found the pair were running the company using pseudonyms, with Wohl reportedly adopting the name “Jay Klein” and Burkman using the moniker “Bill Sanders.” Politico reported that two of the former LobbyMatic employees resigned after learning of their true identities, while other employees only learned after they had left the company.
Update, July 9, 9:44 a.m. ET: Several readers pointed our attention to a March 31 publication from journalist Molly White, which reported that Burkman and Wohl were paid a $300,000 retainer by a Canadian cryptocurrency fraudster wanted by the United States and several other countries for allegedly stealing $65 million from the crypto platforms KyberSwap and Indexed Finance. According to that report, the two were hired to pursue a “presidential pardon to avert a miscarriage of justice” on behalf of the accused hacker, who has not yet been convicted.
Insufficient egress filtering is a commonly identified vulnerability found during BHIS penetration tests. The insufficient egress filtering finding indicates that network traffic leaving the organization’s environment is not properly restricted.
The Future of Threat Defense Resides at the IP Layer
For years, network security operated on a relatively predictable premise: inspect traffic, identify malicious content, and block it. Because deep content inspection created a seemingly robust defense in depth, relatively static legacy approaches—like reliance on threat intelligence feeds—were allowed to simply persist in the background.
The weaponization of agentic AI and highly evasive techniques has fundamentally shattered that model. Attackers are no longer just iterating on old threats. They are launching attacks at staggering velocity, completely outpacing threat feeds, and employing evasion tactics that actively starve legacy prevention solutions of the content they rely on to inspect.
Our new research report from Unit 42, Attackers Are Evading Threat Prevention at the Internet Edge, reveals how adversaries are actively exploiting the contextual vacuum at the IP layer to bypass standard security controls. For security leaders, understanding this shift is no longer optional. As the nature of the threat fundamentally changes, our strategic approach to network security must definitively change with it.
The AI-Accelerated, Evasive Attack Lifecycle
To understand why legacy defenses are failing, we must look at how adversaries are accelerating and obfuscating every stage of the attack lifecycle. As these threats progress, the commonly used network indicators we have long relied upon are vanishing, collapsing traditional defenses and leaving defenders with little to act on.
Powered by frontier AI, adversaries now automate reconnaissance and exploitation at huge scale and speed, while using anonymizers to mask their intent. Once an intrusion is launched, orchestration shifts to highly evasive command and control (C2). Attackers hide communications using advanced encryption and AI-built malware-less techniques. They’re also bypassing traditional web and DNS inspection entirely by routing traffic directly to IP addresses—a tactic Unit 42 found in 23% of modern malware
Ultimately, the takeaway is clear: network threat prevention can no longer rely solely on detecting malicious payloads. As AI-driven attacks continue to minimize their footprint, security strategies must augment content inspection with real-time IP layer monitoring to left-shift threat detection and counter these rapid, machine-speed threats at the network foundation.
Existing Approaches Aren’t Working
Where content-based detection falls short, many security vendors and organizations still rely on IP threat intelligence feeds to pick up the slack in an attempt to filter out malicious connections on the network layer. However, after years of operating under this model, the results are in—the traditional feed is showing its age.
Attackers have long relied on proxies, anonymizers, residential routers and public cloud providers as a tactic to evade detection. However, agentic AI morphs this process, enabling rapid infrastructure rotation and stealth at an unprecedented scale. As this autonomous evasion accelerates, experienced network defenders continue to run into the well-known limitations of classic IP blocklists:
Too slow to keep pace: Unit 42 found an average 20-day lag time before new threats hit popular feeds. Because agentic AI enables adversaries to autonomously rotate proxy IPs in hours, these lists are obsolete at the moment of delivery.
Fundamentally incomplete: IP feeds are unable to see a massive portion of the modern attack surface. Unit 42 research indicates that 52% of malicious IPs used for direct-to-IP connections are completely absent from these lists.
Unactionable on shared infrastructure: Even known threats are often impossible to block. The Unit 42 team reports that 37% of direct-to-IP traffic uses reputable CDNs and cloud providers. IP feeds cannot distinguish malicious connections from legitimate ones, making blocking too risky for business continuity.
A management nightmare: Among the security teams that Unit 42 polled, 30% indicate resource-intensive vetting and false-positive triage as their top pain point. To avoid breaking legitimate traffic, feeds are frequently relegated to an alert-only mode, defeating the entire purpose of prevention.
If modern and agentic AI-enabled attacks can outrun traditional network payload-based detections, we need a new weapon in the network defender’s arsenal. We can no longer depend on yesterday’s IP feeds to secure such an extremely agile threat environment.
The Blueprint for Modernizing the Internet Edge
To outpace the impact of agentic AI and advanced evasion on network threat prevention, security leaders must redefine their defense strategy and shift-left to track the attacker infrastructure itself—monitoring the exact IP layer locations where adversaries build and control their campaigns. Deep content inspection remains essential, but securing the modern edge requires establishing the context and intent of a connection before a session is established.
To achieve this goal, organizations must move beyond the limitations of static defense and adopt a modern security blueprint:
Proactive protection against attacker infrastructure: While high-quality threat feeds remain essential for SOC investigations and incident response, relying on them for frontline, real-time prevention creates major blind spots. Instead, security teams must use real-world, global telemetry to proactively identify and block connections to attacker-controlled hosts before requesting a URL or file.
Zero trust principles applied to the network layer: An IP address without a negative reputation does not equal a safe connection. Continuous verification requires extending zero trust down to the network foundation. It validates the real-time behavior and intent of every single session to ensure attackers cannot hide in the contextual vacuum of the IP layer.
Reducing the attack surface with rich contextual attributes: Traditional IP blocking is like a blunt instrument that creates unacceptable false positives and alert fatigue. To modernize the edge, security teams need deep, attribute-based visibility across the entire Internet address space to reduce noise and replace legacy IP feeds entirely.
By moving away from point-in-time assumptions and embracing real-time, inline protection, security leaders can reclaim the advantage at the network foundation.
To see how these evasion tactics operate in the wild, read the latest Unit 42 report, Attackers Are Evading Threat Prevention at the Internet Edge. You’ll find this report valuable in understanding the systemic gaps in legacy risk models and learning why continuous verification must be our new mandate.
For the last several months, we have had early, unbounded access to the latest frontier AI models. What we’ve seen from that vantage point has made it clear that the window for organizations to get ahead of what’s coming is shorter than most leaders realize.
We have moved past the era of incremental AI improvements into a threat landscape shift. Our testing has revealed a step-change in capability that demonstrates an intuitive understanding of software vulnerabilities. This is more than faster code generation, it is a shift from AI as an assistant to AI as an autonomous agent capable of discovering and chaining flaws at a scale that most defenders aren’t prepared for.
These capabilities will not stay confined to controlled environments for long. When Mythos first launched, we predicted a six-month window before attackers gained access. We now believe that timeline has accelerated significantly.
To meet this inflection point, defense must operate at the speed of the adversary. That is why Palo Alto Networks has introduced Frontier AI Defense. This initiative unites our AI-native security platforms with Unit 42® consulting and threat expertise with strategic partners to deliver continuous protection, prioritized risk mitigation and autonomous remediation.
What the Threat Looks Like Now
The latest frontier models, including OpenAI’s GPT-5.5-Cyber, Anthropic’s Mythos and Claude Opus 4.7, and the specialized variants emerging across major labs, represent roughly a 50% improvement in coding efficiency over their predecessors. That number sounds incremental, but in practice, it’s the threshold at which AI crosses from a helpful assistant into an autonomous operator.
Based on our testing and review, we found four key developments that, taken together, redefine the modern threat landscape:
Vulnerability Discovery at Scale: Frontier AI is exceptionally effective at identifying vulnerabilities across massive, complex codebases. In our testing, three weeks of model-assisted analysis matched a full year of manual penetration testing, with broader coverage.
Exploit Chaining & Synthesis: What is more consequential than individual discovery is the models’ ability to think like an attacker. They link multiple lower-severity issues into single, critical exploit paths, seeing full-stack logic, including SaaS and public-facing surfaces, in ways traditional scanners cannot.
Attack Cycle Compression: In AI-assisted scenarios, the time from initial access to exfiltration has collapsed to as little as 25 minutes. Detection and response measured in hours is no longer a viable standard; single-digit MTTR (Mean Time to Respond) is the new floor.
The Unsupervised Attack Surface: Rapid AI development and decentralized innovation are creating a massive, unsupervised attack surface in real-time. As local AI agents become commonplace, every desktop is now effectively a server, yet most organizations lack visibility into the code their own employees are generating and deploying.
Our Approach
These emerging threats form the foundation of how we have architected our platform response for the agentic era – Frontier AI Defense. Our approach moves beyond traditional, reactive defense to provide a comprehensive framework built to outpace frontier-AI-enabled attackers. This initiative is defined by:
Advanced Access: We leverage early access to frontier AI models to harden defenses and simulate attacks before they reach the mainstream.
Intelligence-Led Resilience: Unit 42 experts leverage frontier AI to fast-track discovery and remediation of exposures at machine speed through our Unit 42 Frontier AI Defense service.
Unified Global Ecosystem: We provide the scale required for global protection through our Frontier AI Alliance of elite partners, including Accenture, Armadin, Deloitte, IBM, NTT DATA, and PwC.
Machine Speed Security: By natively integrating Frontier AI across our platforms, we deliver the automated, real-time defense necessary to counter autonomous threats.
The Window Is Open. It Won’t Be for Long.
The capabilities we tested under early-access conditions are expected to become widely available over the next several months. Success in this new environment requires adapting your cybersecurity stack before these tools are in the hands of every adversary.
The threat has never been more sophisticated. The window to prepare for this shift is closing. And we're here to help secure your future at the edge of the frontier.
This article shows you how to identify and secure open proxies in your AWS environment to prevent abuse, protect your IP address reputation, and control costs.
An open proxy is a server that forwards traffic on behalf of internet users without requiring authentication. While proxies can support legitimate use cases such as load balancing or caching, open proxies allow unrestricted access that threat actors can use to hide harmful activity. In Amazon Web Services (AWS) environments, open proxies often result from misconfigured Amazon Elastic Compute Cloud (Amazon EC2) instances, containers, or compute resources such as AWS Lambda functions. These resources expose proxy functionality without access controls.
Open proxies come in several forms. Common open proxies can include:
HTTP proxies: HTTP proxies forward HTTP requests to web servers, making them useful for web traffic management. These proxies can create potential issues when they’re unsecured.
SOCKS proxies: SOCKS proxies support a wider range of traffic types and provide more flexibility. These proxies create a broader potential for misuse.
Transparent proxies: Transparent proxies intercept traffic without the client’s knowledge and are often used to filter content. These proxies can become security liabilities when misconfigured.
Reverse proxies: Reverse proxies help with internal routing. Unauthorized users can misuse these proxies if they’re exposed.
Knowing these risks can help you better protect your AWS environment.
Security risks
Because of the unrestricted configuration of open proxy servers, threat actors target them to conduct denial of service (DoS) events, intrusion attempts, distribute spam, and other forms of unauthorized activity. These open proxy servers allow threat actors to hide their actual IP address and other forms of identification from the intended targets.
When your AWS infrastructure hosts an open proxy, several risks emerge that can affect both your operations and customers:
Threat actors can misuse your resources, which can result in your IP address being added to security service and reputation system block lists. This can affect your legitimate business operations and customer access. When external parties use your infrastructure for harmful activities, the reputation damage extends beyond immediate technical concerns to affect your ability to reach customers and partners.
Unexpected costs from resource consumption occur when threat actors use your bandwidth and compute capacity. The traffic patterns that proxy abuse generate can also alert AWS security monitoring systems and create additional operational overhead as you investigate and respond to these alerts.
Service disruptions might affect your legitimate workloads because unauthorized traffic competes for resources with your business-critical applications. This competition for resources can potentially degrade performance or cause availability issues for your customers.
Implementing security measures
To prevent the risks associated with open proxies, it’s essential to implement proper security controls for proxy services in AWS environments. The following guidance is a comprehensive approach that you can follow to secure your proxy infrastructure.
Access control implementation
An important security step is to use passwords and authentication mechanisms to restrict access to proxy services. Configure your proxies to accept connections only from known, trusted IP address ranges. For Elastic Load Balancing (ELB), limit access based on source IP addresses and add authentication to proxies behind the load balancers. When you create new instances in Amazon Elastic Kubernetes Service (Amazon EKS), limit access to your balancer in each instance. If instances don’t have public IP addresses, then you can limit access to the balancer instead. If instances have public IP addresses, then you must limit access to those IP addresses.
When possible, use AWS PrivateLink virtual private cloud (VPC) endpoints to provide private connectivity to AWS services without exposing them to the internet. Deploy proxy services in private subnets with controlled outbound access through NAT gateways or other controlled channels. For Amazon EC2 and Amazon Lightsail resources, update the attached security group to prevent public internet access. To secure the proxy, you must either limit access to specific IP addresses or implement authentication on the endpoint.
Authentication and authorization
Turn on authentication for the proxy software and use strong credentials, certificates, or integration with AWS Identity and Access Management (IAM) and AWS Directory Service. Apply IAM policies with the principle of least privilege to limit access to only what users need to perform their tasks. This approach reduces the potential effects of credential compromise and helps maintain clear accountability for resource access.
Monitoring and detection
To detect unusual proxy activity, configure Amazon Virtual Private Cloud (Amazon VPC) Flow Logs, AWS CloudTrail, and Amazon GuardDuty. Use Amazon CloudWatch alarms to notify you of abnormal traffic patterns that might indicate unauthorized use of your proxy services. These monitoring capabilities provide visibility into your network traffic patterns and help you identify both legitimate usage and potential security concerns.
Deployment best practices
Use HTTPS for ELB traffic to protect data in transit, and restrict security groups to necessary ports to minimize the surface area for potential misuse. Integrate AWS WAF with balancers to filter web traffic based on rules that you define. You can also use AWS Network Firewall for advanced traffic filtering capabilities. For APIs, deploy Amazon API Gateway with authentication and authorization controls to manage access to your backend services. This layered approach to security helps protect your infrastructure at multiple points in the traffic flow.
Regular security assessments
Run Amazon Inspector to scan for misconfigurations in your infrastructure, and use AWS Security Hub to centralize security findings across your AWS environment. Conduct penetration tests in accordance with AWS policy to identify potential security issues before they can result in unintended access.
Incident response planning
Automate remediation with AWS Config rules and Automation, a capability of AWS Systems Manager, to respond rapidly to security events. Maintain incident response runbooks that outline clear steps for addressing proxy-related security incidents, and decommission unused resources that could become security liabilities.
Documented procedures and automated responses reduce the time between detection and remediation and minimizes the potential effects of security incidents on your operations.
Benefits of proper proxy security
When you implement these security measures, you gain the following advantages for your AWS environment:
Protection of your IP address reputation helps maintain customer trust and prevents security services from blocking your legitimate traffic. When your infrastructure maintains a positive reputation, your business communications reach their intended recipients without interference.
Cost control prevents unauthorized users from consuming your AWS resources and generating unexpected charges on your account. When you restrict access to legitimate users and use cases, you maintain predictable costs that align with your business needs.
Operational stability reduces the risk of service disruptions that abuse of your proxy infrastructure can cause. When you dedicate your resources to serving your customers rather than supporting unauthorized activity, you can deliver consistent performance and availability.
Enhanced visibility into your network traffic patterns helps you identify both legitimate usage and potential security concerns. This awareness allows you to make informed decisions about capacity planning, security improvements, and operational optimizations.
Conclusion
Open proxies present a serious risk in AWS environments, but you can effectively secure proxies with the right measures. By implementing strict access controls and additional security practices such as authentication, monitoring, and regular assessments, you can prevent misuse, protect your infrastructure, and maintain your IP address reputation.
Taking proactive steps strengthens your own environment and supports the broader security of the internet ecosystem. Under the AWS shared responsibility model, you’re responsible for the configuration and maintenance of these security controls, while AWS provides the underlying secure infrastructure. By following the guidance in this article, you can build a robust security posture that protects your proxy infrastructure while supporting your legitimate business needs.
If you have feedback about this post, submit comments in the Comments section below.
Frontier AI is changing what is possible for attackers. To meet this escalating threat, Palo Alto Networks is teaming up with Armadin, the new offensive security company founded by Kevin Mandia. This partnership expands our newly introduced Unit 42 Frontier AI Defense service, scaling our ability to identify and remediate AI-driven exposures, and accelerating protection across the enterprise.
Over the past few weeks, we’ve spoken with hundreds of CISOs who universally feel the urgency on the frontlines. Security leaders need to know exactly where they stand against the AI-driven attacks happening right now, and the ones coming in the next six months.
Expanding Frontier AI Defense — The External AI Hyperattack Assessment
For organizations seeking to actively pressure-test their perimeter, this partnership introduces an autonomous, AI-driven offensive assessment of your external attack surface.
This added layer identifies real attack paths and proves exploitability across internet-facing assets. The platform begins with passive discovery, validating publicly exposed assets, cloud resources and secrets. Next, Armadin deploys a coordinated swarm of autonomous AI attack agents, operating at machine speed across your external footprint.
These agents execute active reconnaissance, launch attacks and exploit vulnerabilities in parallel, using over 50,000 templates. Upon initial access, the swarm simulates post-exploitation behavior to demonstrate impact, logging every attack chain as decision-grade evidence of exploitable risk.
Decision-Grade Proof of Exploitable Risk
With this added layer of autonomous simulation, Unit 42 Frontier AI Defense provides an even more rigorous, pressure-tested view of an organization's external attack surface. This allows our experts to accurately simulate the tradecraft of the most capable, AI-equipped threat actors, compressing complex attack lifecycles from days into minutes.
AI may change what is possible for attackers, but in the hands of defenders, it becomes a decisive advantage. This partnership is another important step in making sure that advantage stays with the defenders.
A member of Project Glasswing and OpenAI’s Trusted Access for Cyber (TAC) program, Palo Alto Networks remains the only company equipped to deliver this strategic level of partnership through Unit 42 Frontier AI Defense and the Frontier AI Alliance, driven to integrate cutting-edge technologies into our products and services.
Frontier AI models have given the security industry a preview of what comes next. As they become weaponized, attackers will automate the discovery and chaining of vulnerabilities in near real-time – compressing timelines, increasing scale and outpacing human-led defense.
Until now, defenders have had time to detect activity, investigate signals and contain threats before exposures were chained into full attacks. AI is quickly closing this window.
Defending against AI-driven threats means engineering a resilient architecture that limits how easily attackers can exploit discovered weaknesses, that contains the blast radius when they do, and enables faster response at scale. It also means using AI to accelerate the security program itself, from vulnerability discovery and code review to triage, remediation and incident response.
The transition should cover three areas. First, discover and remediate your current exposure before attackers do. Second, strengthen controls that reduce exposure and contain impact. Third, modernize operations so teams can detect and respond in real-time.
Powered by the latest AI models, Unit 42 Frontier AI Defense helps organizations answer a critical question: Are your defenses ready for AI-powered attacks?
Unit 42 Frontier AI Defense combines three core components delivered by expert consultants, coupled with 6 months of complimentary access to Cortex® XDR, Cortex Xpanse® and Koi Agentic Security.
Frontier AI Exposure Analysis: Identify and validate the exposures most likely to be chained into real attacks before attackers weaponize them.
Actions
Use the latest frontier models, Unit 42 offensive security expertise, threat telemetry and Unit 42 Threat Intelligence to assess your environment.
Identify the vulnerabilities, misconfigurations and posture gaps most likely to be exploited across infrastructure, applications, code, identity and cloud.
Validate the attack paths most likely to matter in real-world attacks.
Outputs
A prioritized view of vulnerabilities and attack paths that matter most
Clear actions to fix the exposures that matter first
Autonomous Security Blueprint: Benchmark current capabilities and define the changes required for machine-speed defense.
Actions
Assess current-state capabilities across attack surface, identity, software supply chain, zero trust containment, as well as real-time detection and response.
Identify where AI-powered threats create the greatest exposure and where current controls are most likely to fail.
Define the technical and operational changes required to close those gaps.
Outputs
A clear blueprint for immediate action
A prioritized roadmap to reduce exposure, strengthen containment and modernize security for the AI era
Agentic Defense Transformation: Implement the prioritized architecture, control and operating changes needed to modernize defenses for AI-driven threats.
Actions
Implement the architectural, operational and control changes required to defend against AI-driven threats.
Modernize exposure management, harden the software supply chain, and advance zero trust architecture.
Build response capabilities that can keep pace with autonomous attacks.
Outputs
Accelerated implementation of the changes that matter most
A more modern security architecture, built to reduce exposure and improve containment
The Window Is Still Open, for Now
AI is the biggest security inflection point since enterprises moved to the cloud. Organizations that act now will be the ones that are ready. Those that wait will be forced to respond under maximum pressure on the worst possible day.
Frontier AI is changing what is possible for attackers. In the hands of defenders, it can become a decisive advantage.
An offensive security perspective on Microsoft Edge WebView2 Runtime, including architectural weaknesses, existing vulnerabilities, and exploitation methods.

 Login