The primary goal for attackers in a phishing campaign is to bypass email security and trick the potential victim into revealing their data. To achieve this, scammers employ a wide range of tactics, from redirect links to QR codes. Additionally, they heavily rely on legitimate sources for malicious email campaigns. Specifically, we’ve recently observed an uptick in phishing attacks leveraging Amazon SES.
The dangers of Amazon SES abuse
Amazon Simple Email Service (Amazon SES) is a cloud-based email platform designed for highly reliable transactional and marketing message delivery. It integrates seamlessly with other products in Amazon’s cloud ecosystem, AWS.
At first glance, it might seem like just another delivery channel for email phishing, but that isn’t the case. The insidious nature of Amazon SES attacks lies in the fact that attackers aren’t using suspicious or dangerous domains; instead, they are leveraging infrastructure that both users and security systems have grown to trust. These emails utilize SPF, DKIM, and DMARC authentication protocols, passing all standard provider checks, and almost always contain .amazonses.com in the Message-ID headers. Consequently, from a technical standpoint, every email sent via Amazon SES – even a phishing one – looks completely legitimate.
Phishing URLs can be masked with redirects: a user sees a link like amazonaws.com in the email and clicks it with confidence, only to be sent to a phishing site rather than a legitimate one. Amazon SES also allows for custom HTML templates, which attackers use to craft more convincing emails. Because this is legitimate infrastructure, the sender’s IP address won’t end up on reputation-based blocklists. Blocking it would restrict all incoming mail sent through Amazon SES. For major services, that kind of measure is ineffective, as it would significantly disrupt user workflows due to a massive number of false positives.
How compromise happens
In most cases, attackers gain access to Amazon SES through leaked IAM (AWS Identity and Access Management) access keys. Developers frequently leave these keys exposed in public GitHub repositories, ENV files, Docker images, configuration backups, or even in publicly accessible S3 buckets. To hunt for these IAM keys, phishers use various tools, such as automated bots based on the open-source utility TruffleHog, which is designed for detecting leaked secrets. After verifying the key’s permissions and email sending limits, attackers are equipped to spread a massive volume of phishing messages.
Examples of phishing with Amazon SES
In early 2026, one of the most common themes in phishing emails sent with Amazon SES was fake notifications from electronic signature services.
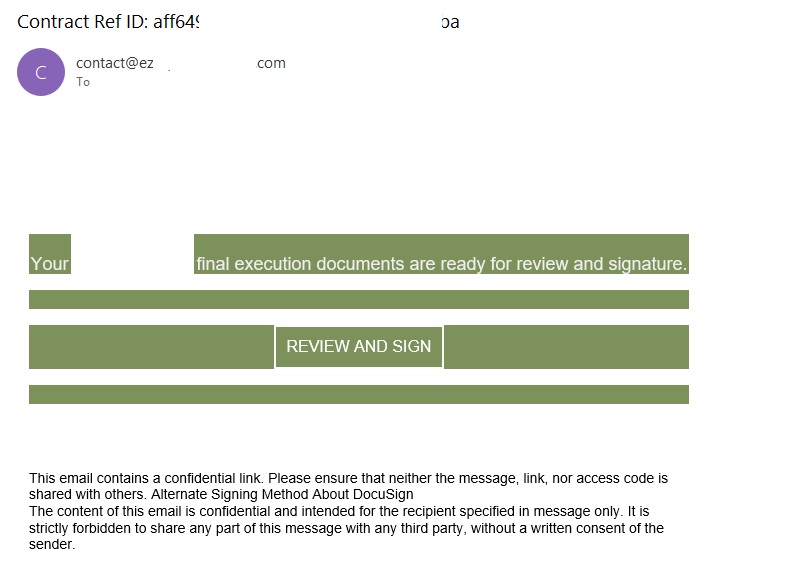
Phishing email imitating a Docusign notification
The email’s technical headers confirm that it was sent with Amazon SES. At first glance, it all looks legitimate enough.
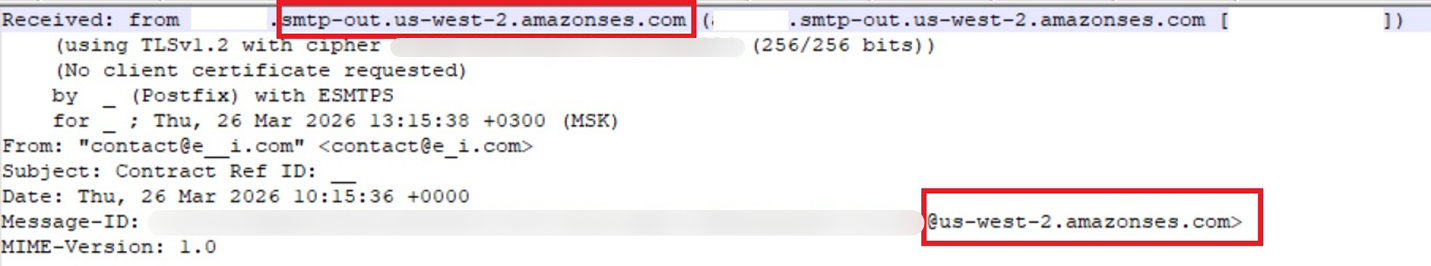
Phishing email headers
In these emails, the victim is typically asked to click a link to review and sign a specific document.
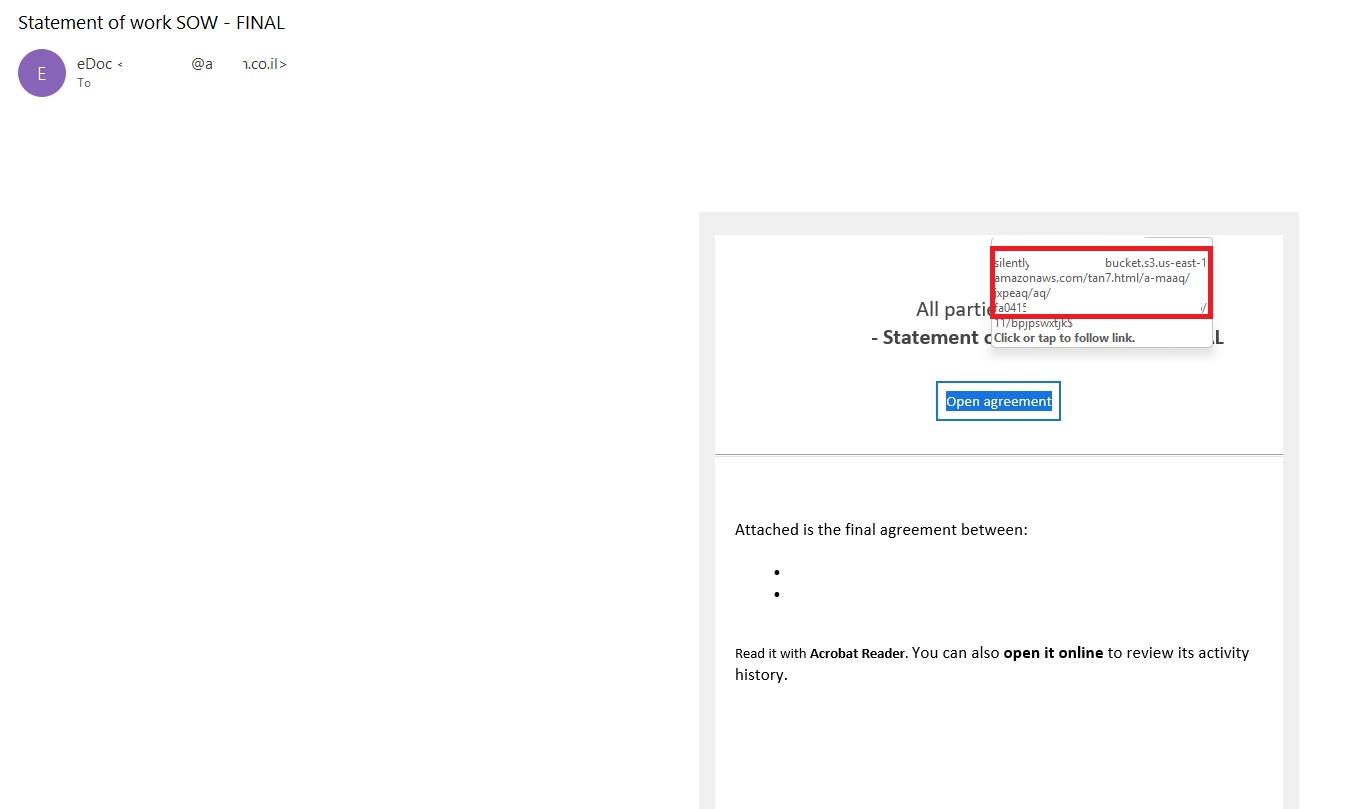
Phishing email with a “document”
Upon clicking the link, the user is directed to a sign-in form hosted on amazonaws.com. This can easily mislead the victim, convincing them that what they’re doing is safe.
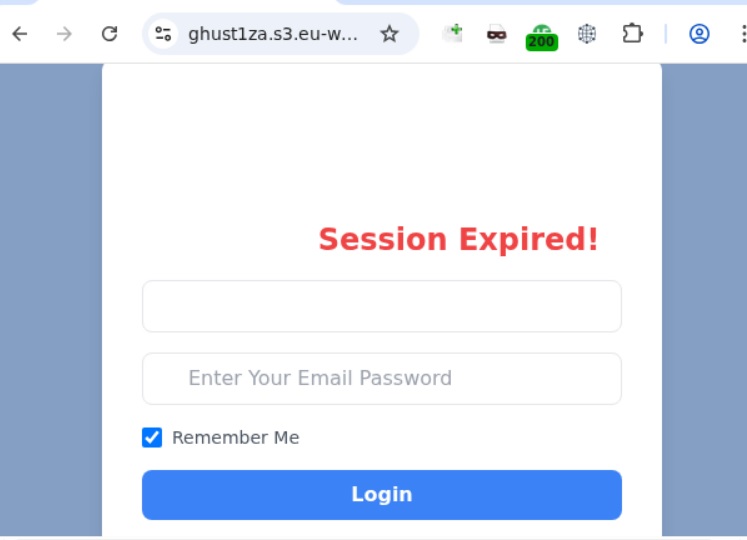
Phishing sign-in form
The resulting form is, of course, a phishing page, and any data entered into it goes directly to the attackers.
Amazon SES and BEC
However, Amazon SES is used for more than just standard phishing; it’s also a vehicle for a very sophisticated type of BEC campaigns. In one case we investigated, a fraudulent email appeared to contain a series of messages exchanged between an employee of the target organization and a service provider about an outstanding invoice. The email was sent as if from that employee to the company’s finance department, requesting urgent payment.
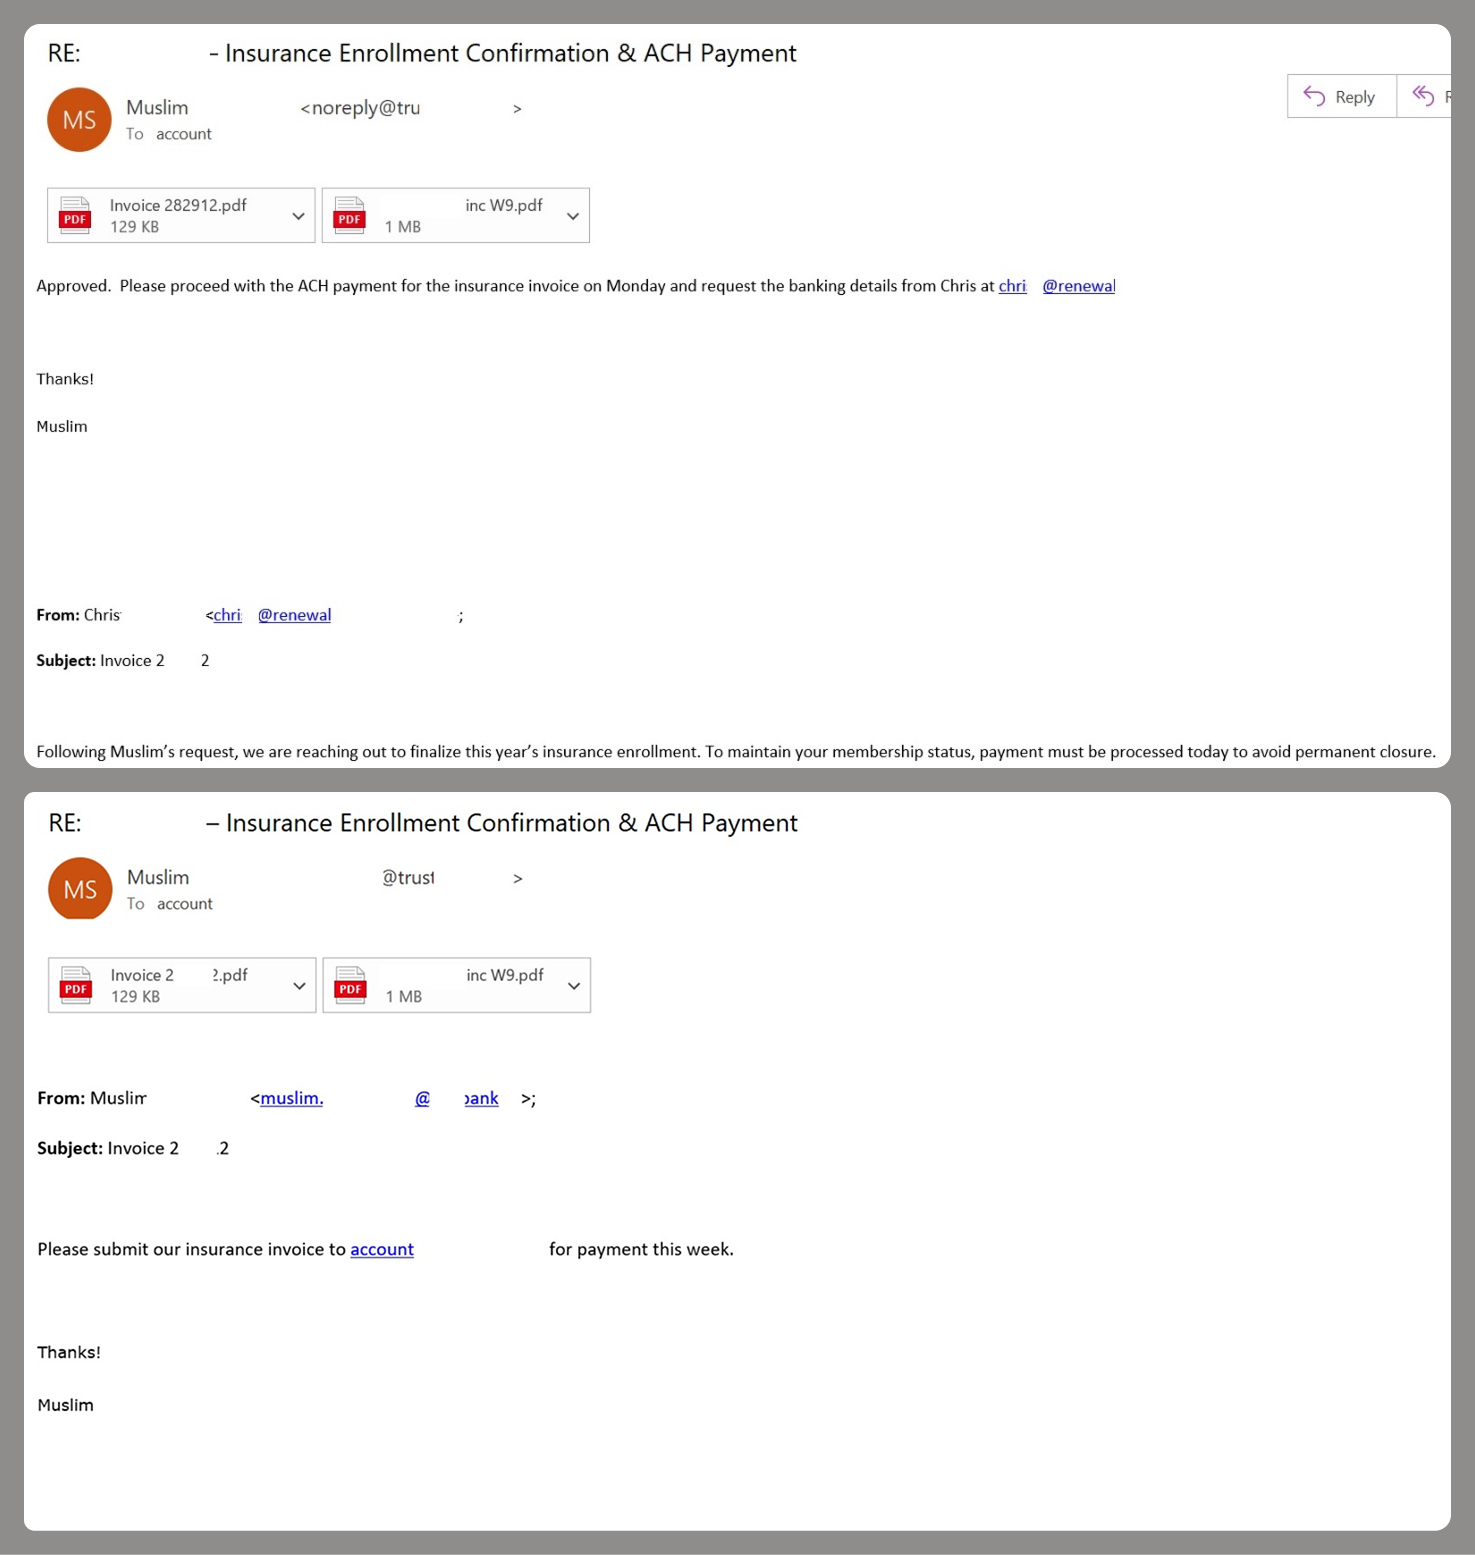
BEC email featuring a fake conversation between an employee and a vendor
The PDF attachments didn’t contain any malicious phishing URLs or QR codes, only payment details and supporting documentation.
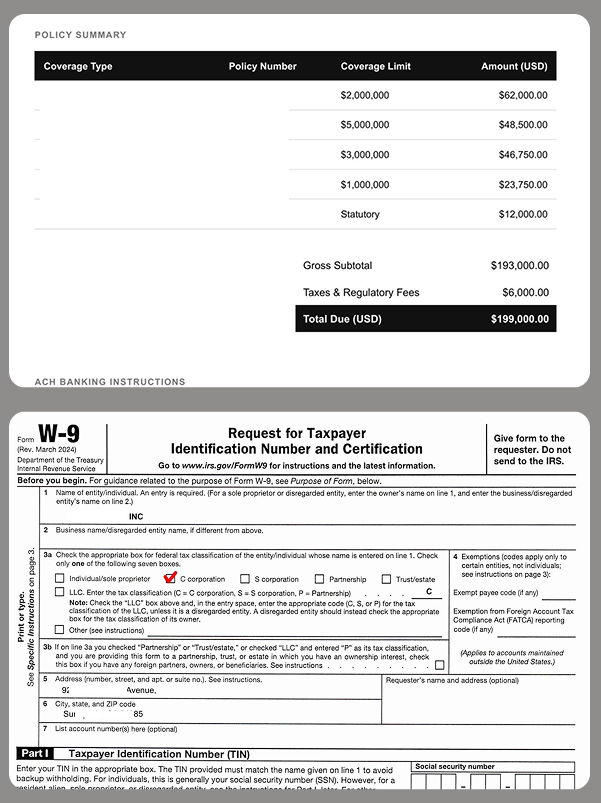
Forged financial documents
Naturally, the email didn’t originate with the employee, but with an attacker impersonating them. The entire thread quoted within the email was actually fabricated, with the messages formatted to appear as a legitimate forwarded thread to a cursory glance. This type of attack aims to lower the user’s guard and trick them into transferring funds to the scammers’ account.
Takeaways
Phishing via Amazon SES experienced an uptick in January 2026 and has remained relatively steady through Q1. By weaponizing this service, attackers avoid the effort of building dubious domains and mail infrastructure from scratch. Instead, they hijack existing access keys to gain the ability to blast out thousands of phishing emails. These messages pass email authentication, originate from IP addresses that are unlikely to be blocklisted, and contain links to phishing forms that look entirely legitimate.
Since these Amazon SES phishing attacks stem from compromised or leaked AWS credentials, prioritizing the security of these accounts is critical. To mitigate these risks, we recommend following these guidelines:
Implement the principle of least privilege when configuring IAM access keys, granting elevated permissions only to users who require them for specific tasks.
Transition from IAM access keys to roles when configuring AWS; these are profiles with specific permissions that can be assigned to one or several users.
Enable multi-factor authentication, an ever-relevant step.
Configure IP-based access restrictions.
Set up automated key rotation and run regular security audits.
Use the AWS Key Management Service to encrypt data with unique cryptographic keys and manage them from a centralized location.
We recommend that users remain vigilant when handling email. Do not determine whether an email is safe based solely on the From field. If you receive unexpected documents via email, a prudent precaution is to verify the request with the sender through a different communication channel. Always carefully inspect where links in the body of an email actually lead. Additionally, robust email security solutions can provide an essential layer of protection for both corporate and personal correspondence.
The primary goal for attackers in a phishing campaign is to bypass email security and trick the potential victim into revealing their data. To achieve this, scammers employ a wide range of tactics, from redirect links to QR codes. Additionally, they heavily rely on legitimate sources for malicious email campaigns. Specifically, we’ve recently observed an uptick in phishing attacks leveraging Amazon SES.
The dangers of Amazon SES abuse
Amazon Simple Email Service (Amazon SES) is a cloud-based email platform designed for highly reliable transactional and marketing message delivery. It integrates seamlessly with other products in Amazon’s cloud ecosystem, AWS.
At first glance, it might seem like just another delivery channel for email phishing, but that isn’t the case. The insidious nature of Amazon SES attacks lies in the fact that attackers aren’t using suspicious or dangerous domains; instead, they are leveraging infrastructure that both users and security systems have grown to trust. These emails utilize SPF, DKIM, and DMARC authentication protocols, passing all standard provider checks, and almost always contain .amazonses.com in the Message-ID headers. Consequently, from a technical standpoint, every email sent via Amazon SES – even a phishing one – looks completely legitimate.
Phishing URLs can be masked with redirects: a user sees a link like amazonaws.com in the email and clicks it with confidence, only to be sent to a phishing site rather than a legitimate one. Amazon SES also allows for custom HTML templates, which attackers use to craft more convincing emails. Because this is legitimate infrastructure, the sender’s IP address won’t end up on reputation-based blocklists. Blocking it would restrict all incoming mail sent through Amazon SES. For major services, that kind of measure is ineffective, as it would significantly disrupt user workflows due to a massive number of false positives.
How compromise happens
In most cases, attackers gain access to Amazon SES through leaked IAM (AWS Identity and Access Management) access keys. Developers frequently leave these keys exposed in public GitHub repositories, ENV files, Docker images, configuration backups, or even in publicly accessible S3 buckets. To hunt for these IAM keys, phishers use various tools, such as automated bots based on the open-source utility TruffleHog, which is designed for detecting leaked secrets. After verifying the key’s permissions and email sending limits, attackers are equipped to spread a massive volume of phishing messages.
Examples of phishing with Amazon SES
In early 2026, one of the most common themes in phishing emails sent with Amazon SES was fake notifications from electronic signature services.
Phishing email imitating a Docusign notification
The email’s technical headers confirm that it was sent with Amazon SES. At first glance, it all looks legitimate enough.
Phishing email headers
In these emails, the victim is typically asked to click a link to review and sign a specific document.
Phishing email with a “document”
Upon clicking the link, the user is directed to a sign-in form hosted on amazonaws.com. This can easily mislead the victim, convincing them that what they’re doing is safe.
Phishing sign-in form
The resulting form is, of course, a phishing page, and any data entered into it goes directly to the attackers.
Amazon SES and BEC
However, Amazon SES is used for more than just standard phishing; it’s also a vehicle for a very sophisticated type of BEC campaigns. In one case we investigated, a fraudulent email appeared to contain a series of messages exchanged between an employee of the target organization and a service provider about an outstanding invoice. The email was sent as if from that employee to the company’s finance department, requesting urgent payment.
BEC email featuring a fake conversation between an employee and a vendor
The PDF attachments didn’t contain any malicious phishing URLs or QR codes, only payment details and supporting documentation.
Forged financial documents
Naturally, the email didn’t originate with the employee, but with an attacker impersonating them. The entire thread quoted within the email was actually fabricated, with the messages formatted to appear as a legitimate forwarded thread to a cursory glance. This type of attack aims to lower the user’s guard and trick them into transferring funds to the scammers’ account.
Takeaways
Phishing via Amazon SES experienced an uptick in January 2026 and has remained relatively steady through Q1. By weaponizing this service, attackers avoid the effort of building dubious domains and mail infrastructure from scratch. Instead, they hijack existing access keys to gain the ability to blast out thousands of phishing emails. These messages pass email authentication, originate from IP addresses that are unlikely to be blocklisted, and contain links to phishing forms that look entirely legitimate.
Since these Amazon SES phishing attacks stem from compromised or leaked AWS credentials, prioritizing the security of these accounts is critical. To mitigate these risks, we recommend following these guidelines:
Implement the principle of least privilege when configuring IAM access keys, granting elevated permissions only to users who require them for specific tasks.
Transition from IAM access keys to roles when configuring AWS; these are profiles with specific permissions that can be assigned to one or several users.
Enable multi-factor authentication, an ever-relevant step.
Configure IP-based access restrictions.
Set up automated key rotation and run regular security audits.
Use the AWS Key Management Service to encrypt data with unique cryptographic keys and manage them from a centralized location.
We recommend that users remain vigilant when handling email. Do not determine whether an email is safe based solely on the From field. If you receive unexpected documents via email, a prudent precaution is to verify the request with the sender through a different communication channel. Always carefully inspect where links in the body of an email actually lead. Additionally, robust email security solutions can provide an essential layer of protection for both corporate and personal correspondence.

If you use the internet, you’ve likely been affected by cybercrime in some way. Even when an attack is aimed at a company, the fallout usually lands on ordinary people.
The most obvious harm is stolen data. When attackers break into a business, it is usually customer information that ends up in criminal hands, and that can lead to identity theft, tax fraud, credit card fraud, and a long tail of scam attempts that can continue for months or years. For consumers, the breach itself is often just the start of the cleanup.
That work is annoying, time-consuming, and sometimes expensive. People may have to freeze credit, replace cards, change passwords, be on the lookout for suspicious transactions, and dispute charges. The Federal Trade Commission (FTC) specifically advises consumers to use IdentityTheft.gov after a breach and recommends steps like credit freezes and fraud alerts to reduce the chance of further abuse.
When sensitive data is exposed, the harm is not only financial. Medical, insurance, and other deeply personal records can be used to create more convincing phishing or extortion attempts, and the stress of knowing that private information is circulating among criminals can linger long after the technical incident is over. In other words, breach victims are not just cleaning up a data problem, they are dealing with a loss of trust.
Breaches happen every day. Don’t be the last to know.
Cybercrime also hits consumers through service disruption. Ransomware and intrusion campaigns can interrupt payment systems, telecom services, shipping, energy distribution, booking platforms, and other infrastructure people rely on every day. In those cases, the consumer impact is immediate: you may not be able to pay, travel, call, buy, or even work normally. The CSIS timeline and Canada’s cyberthreat assessment both show that these disruptions are increasingly tied to high-value targets and can be part of broader state or criminal campaigns.
Not all these incidents are driven by cybercriminals. Recently, Britain’s cybersecurity chief warned that the UK is handling 4 nationally significant cyberincidents every week, with the majority now traced back to foreign governments rather than cybercriminal groups.
Another cost is easy to overlook: disinformation and confusion. When attackers steal data, disrupt services, or impersonate trusted brands, they can also flood the public with fake support messages, scam calls, refund schemes, and phishing emails pretending to be the breached company. The breach becomes a launchpad for more fraud, and consumers are left trying to separate legitimate notifications from those sent by attackers.
Then there is the security backlash. After a breach, companies usually tighten access rules, add more multi-factor authentication prompts, force reauthentication, shorten sessions, and increase fraud checks. Those measures are often necessary, but they also make ordinary digital life more cumbersome. The consumer ends up paying with time and frustration for security problems they did not create.
That is why company-targeted cybercrime is not really only a business problem. It is a consumer issue, a public-trust issue, and sometimes even a national security issue. A single breach can leak data, trigger fraud, interrupt essential services, amplify scams, and make using the internet more frustrating for everyone else. The real cost is rarely confined to the company that got hit.
Knowing this, it’s worth thinking carefully about which companies to trust with your data and how much you’re willing to share . You cannot stop every attack against every company you deal with, but you can limit the fallout by being more selective. Some considerations:
Do they need all the information they are asking for?
Would it hurt anything if you leave some fields blank or give less specific answers?
Has this company been breached in the past, and how did they handle it?
How long will they store the data you provide?
Can you easily have your data removed at your request?
Your name, address, and phone number are probably already for sale.
Data brokers collect and sell your personal details to anyone willing to pay. Malwarebytes Personal Data Remover finds them and gets your information removed, then keeps watch so it stays that way.
A dreadful thing happens far too often whenever an older adult falls for a scam: They get blamed for it. Not the scammers who lied and cheated their victim out of money. Not law enforcement for failing to recover funds. Not even the Big Tech companies that could have the most important role in protecting people online—and which, it turns out, knowingly bring in revenue every year from fraud.
Instead, it is the older adults themselves whose stories are often shirked aside because of a mix of ageism and denial. Allegedly left behind by technology, only an octogenarian would hand their password over in a phishing scheme, or open an email attachment from a stranger, or send money to a fake charity online. Everyone else, everyone else believes, is too savvy for the same.
The data disagrees.
When Malwarebytes studied this last year, it found that, depending on the type of scam—especially for things like “sextortion”—younger individuals were far more likely to report falling victim. Further, digging into data from the US Federal Trade Commission revealed entirely separate patterns. For example, while Americans between the ages of 80 and 89 reported the highest median loss due to fraud in 2024, they also made up the smallest share of their population to report a loss at all. And in 2025, that same group represented the smallest share of reported identity theft, a crime far more likely to be reported by people between 30 and 39.
Questions about who reports what crimes at what rate are valid to explore, but it’s important to see the big picture: Americans lost at least $15.9 billion to fraud last year. Protecting older adults is actually about protecting everyone, and that’s because modern scams don’t arrive only where people over 70 spend time. They arrive where we all are, which is online. They come through endless text messages, they slide into social media DMs, and they prey on things any of us can be—a widow, a divorcee, or simply a lonely person.
According to Marti DeLiema, Assistant Professor at the University of Minnesota’s School of Social Work, scams and fraud are now the most common form of organized crime globally, rivaling weapons trafficking, drug trafficking, human trafficking, and sex trafficking. In 2024 alone, she said, the FTC estimated that older adults in the US had as much as $81.5 billion stolen from them. And the tools meant to fight back—broad consumer awareness campaigns, embedded warning messages at the point of transaction, the training of bank tellers and retail clerks—are nowhere near keeping pace.
So what actually works? And who, if anyone, is doing the work?
Today, on the Lock and Code podcast with host David Ruiz, we speak with DeLiema about who is really susceptible to financial fraud, why victims often describe a scam as a form of betrayal trauma, and why the companies best positioned to stop scam messages from reaching consumers may be the ones least motivated to do so.
“This is not a technical capability problem at all. This is a conflict of incentives.”
The Phishing-as-a-Service Pipeline: How a Scalable Fraud Ecosystem Is Driving Global Attacks
In this post, we examine how phishing-as-a-service (PhaaS) has evolved into a structured cybercrime ecosystem, how threat actors collaborate across infrastructure, delivery, and monetization layers, and why this model continues to drive large-scale financial fraud targeting global organizations.
Phishing is no longer a standalone tactic. It has matured into a service-based ecosystem where specialized actors provide each component of an attack lifecycle, from infrastructure and delivery to credential harvesting and cash-out.
Flashpoint analysts, working with partner financial institutions, have observed a growing number of PhaaS operations operating with a level of coordination and specialization more commonly associated with legitimate software platforms. These ecosystems bring together phishing kit developers, infrastructure providers, spam delivery services, and financially motivated actors into a single, scalable pipeline for fraud.
This shift has significantly lowered the barrier to entry for cybercriminals while increasing the scale, efficiency, and success rate of phishing campaigns.
From Phishing Kits to a Service-Based Fraud Economy
PhaaS emerged from early phishing kits into a full cybercrime-as-a-service model built on commercialization, modular tooling, and operational scalability.
Early phishing activity relied on standalone kits — basic login pages and scripts that allowed attackers to collect credentials. Over time, operators began centralizing these capabilities into subscription-based platforms offering hosting, domain management, campaign tooling, and ongoing support.
Modern PhaaS platforms now operate similarly to legitimate SaaS providers:
Subscription-based pricing models
Prebuilt templates for major brands and services
Integrated delivery mechanisms (email, SMS, QR phishing)
Real-time dashboards for campaign tracking and credential harvesting
This model has made sophisticated phishing accessible to low-skill actors. Kits can cost as little as US$10, while full platforms enable large-scale campaigns for relatively modest monthly fees.
MFA Bypass and AI Are Reshaping Phishing Capabilities
As organizations adopted multifactor authentication (MFA), PhaaS operators adapted.
Modern platforms increasingly rely on adversary-in-the-middle (AiTM) techniques, using reverse proxy infrastructure to intercept login sessions in real time. This allows attackers to capture not only credentials, but also MFA tokens and session cookies, effectively bypassing traditional authentication controls.
At the same time, AI is accelerating the scale and effectiveness of phishing campaigns.
Threat actors are using AI to:
Generate convincing, localized phishing lures
Clone brand interfaces with high fidelity
Optimize campaigns through automated testing and iteration
This combination of MFA bypass and AI-driven automation has transformed phishing from a volume-based tactic into a precision-driven access vector.
The PhaaS Pipeline: How the Ecosystem Operates
What distinguishes modern phishing operations is not just tooling, but coordination.
A typical PhaaS campaign follows a structured lifecycle:
This pipeline is supported by a network of specialized providers, each responsible for a different stage of the attack lifecycle.
Infrastructure, Delivery, and Exfiltration Are Increasingly Specialized
Flashpoint analysis highlights how different actors focus on distinct parts of the ecosystem.
Infrastructure and Kit Development
Phishing kit developers provide increasingly sophisticated tooling, including:
Reverse proxy (AiTM) capabilities for MFA bypass
Anti-bot protections to evade researchers
“Live panels” enabling real-time interaction with victims
Platforms such as GhostFrame, Rapid Pages, and MUH Pro Admin illustrate how these tools are being productized and distributed at scale.
SMS Delivery and Spoofing
Smishing has become a critical delivery vector.
Threat actors operate dedicated SMS gateway services capable of sending large volumes of messages via APIs or bulk uploads. Others actively seek advanced spoofing capabilities to bypass authentication controls such as SPF, DKIM, and DMARC, enabling phishing messages to appear legitimate at the protocol level.
Credential Exfiltration and Telegram Integration
Credential collection is increasingly automated and centralized.
Many campaigns exfiltrate stolen credentials directly to Telegram bots or channels, enabling real-time access to victim data. This infrastructure also allows for rapid scaling and coordination across actors participating in the same campaign or ecosystem.
From Credential Theft to Financial Monetization
The ultimate goal of PhaaS operations is monetization.
Stolen credentials are used to enable account takeover (ATO), which allows attackers to:
Access financial accounts
Lock out legitimate users
Initiate fraudulent transactions
Launch follow-on scams
Flashpoint analysis of actors such as “JUN JUN,” associated with the Squirtle group, illustrates how these operations extend into structured financial fraud and laundering.
Observed activity shows a progression from acquiring phishing logs (“fish material”) to targeting high-value accounts and ultimately laundering funds through complex mechanisms, including tax fraud and credit card repayment schemes designed to recycle illicit funds.
This highlights how phishing is only the entry point into a broader fraud pipeline.
A Distributed Ecosystem of Threat Actors
The PhaaS landscape is not controlled by a single group, but by a network of loosely connected actors and clusters.
Examples include:
Fluffy Spider: Focused on large-scale infrastructure deployment and domain generation
IVAN: A more exclusive, high-tier operation leveraging SEO poisoning and advanced evasion techniques
Smishing Triad: A highly coordinated group conducting global SMS phishing campaigns
System Bot: A modular phishing toolkit with credential harvesting and OTP bypass capabilities
These actors operate across different regions and languages but demonstrate comparable levels of technical capability and operational maturity.
Many of these groups function with enterprise-like structures, including support teams, affiliate models, and performance-based operations, further reinforcing the industrialization of phishing-driven fraud.
Law Enforcement Pressure Is Increasing, but the Model Persists
Recent takedowns, including operations targeting platforms such as Tycoon 2FA, demonstrate growing coordination between public and private sector defenders.
These efforts have:
Disrupted infrastructure
Increased operational costs for threat actors
Accelerated collaboration between intelligence providers and law enforcement
However, the underlying PhaaS model remains resilient.
Even as major platforms are dismantled, operators frequently rebrand, migrate infrastructure, or fragment into smaller services. The demand for scalable, low-cost phishing capabilities continues to sustain the ecosystem.
What This Means for Security Teams
Phishing-as-a-service has evolved from a tactic to an ecosystem that industrializes fraud.
Flashpoint assesses that the increasing coordination between phishing kit developers, infrastructure providers, and financial fraud actors will continue to drive large-scale credential harvesting and account takeover activity targeting global organizations.
For defenders, this means that effective mitigation requires more than user awareness and traditional controls. Organizations must account for:
MFA bypass techniques such as AiTM
Rapid infrastructure rotation and evasion
The integration of phishing into broader fraud and access broker pipelines
Protecting Your Organization from the PhaaS Ecosystem
Understanding how phishing ecosystems operate — from infrastructure and delivery to monetization — is critical for disrupting attacks before they result in fraud.
Flashpoint provides intelligence that helps organizations track phishing campaigns, identify emerging threat actors, and detect compromised credentials in real time. By correlating activity across the full attack lifecycle, security teams can better anticipate threats and respond before they escalate.
To learn how Flashpoint can support your team with actionable intelligence on phishing and fraud ecosystems, schedule a demo.
Tax Refund Fraud in 2026: How Threat Actors Exploit Identity, Verification, and Cash-Out Channels
In this post, we examine how threat actors are executing tax refund fraud schemes, from sourcing identity data to bypassing verification and cashing out fraudulent returns, and what these patterns reveal about evolving fraud ecosystems.
Tax refund fraud remains a persistent and evolving threat within cybercrime and fraud communities. Threat actors actively advertise and refine schemes designed to file fraudulent returns and intercept refund payments from legitimate taxpayers.
Across illicit forums, Telegram channels, and marketplaces, discussions point to a structured ecosystem built around identity data, social engineering, verification bypass, and increasingly sophisticated cash-out methods.
For intelligence teams, these conversations provide insight into how fraud operations are scaling and where defenses are being tested and adapted.
The Structure of Modern Tax Refund Fraud Schemes
At a high level, most tax refund fraud schemes follow a consistent model: obtain identity data, file a fraudulent return, bypass verification, and extract funds.
Flashpoint analysis shows that threat actors focus on several key stages:
Sourcing victims or identity “fullz” (complete PII packages)
Obtaining or bypassing identity and return verification
Leveraging social engineering to support fraud workflows
Using tutorials and shared methods to maximize refund amounts
Converting refunds into cash or cryptocurrency
These stages are not isolated. They are supported by overlapping communities that specialize in identity theft, financial fraud, and account access.
Identity Data as the Foundation of Fraud
The success of tax refund fraud depends heavily on access to high-quality identity data.
Threat actors typically rely on “fullz,” which include a victim’s name, date of birth, address, and Social Security number. In some cases, fraudsters also recruit “clients” or “tax heads” — individuals who knowingly or unknowingly provide accurate tax documents and assist in bypassing verification steps.
This distinction is important. While fullz can be purchased or harvested at scale, clients often provide more reliable and current information, increasing the likelihood that a fraudulent return will be accepted.
A threat actor shares a screenshot of a text exchange with a client in which they obtain access to their TurboTax account and tax forms accessible through the account. (Source: Telegram, Flashpoint Collections).
Threat actors also seek additional data points to legitimize filings, including:
Identity Protection (IP) PINs
Adjusted Gross Income (AGI) from previous tax years
Access to tax preparation accounts or IRS records
These elements are frequently obtained through compromised accounts, social engineering, or access to verified identity platforms.
Verification Bypass as a Critical Enabler
Filing a fraudulent return is only part of the process. Successfully passing identity and return verification is often the deciding factor.
Threat actors place significant emphasis on accessing or creating verified accounts tied to identity systems used by government agencies. These accounts allow fraudsters to:
Retrieve tax transcripts and historical data
Respond to IRS verification requests
Validate identity during filing and follow-up processes
In many cases, fraudsters rely on social engineering to obtain this access. Common approaches include:
Creating fake job postings or tax preparation services to collect documents
Running romance or employment scams to gather personal information
Coercing victims into creating or sharing verified accounts
Threat actors also prepare for additional verification steps, such as responding to IRS letters or completing phone and in-person identity checks. These workflows often involve scripts, impersonation tactics, and coordination with cooperating “clients.”
Fraud Tactics Are Increasingly Systematic
Beyond basic filing, threat actors share detailed tutorials and playbooks designed to maximize refunds and improve success rates.
These often include:
Using real or falsified income data to inflate returns
Targeting specific tax credits, such as the Child Tax Credit (CTC), Earned Income Tax Credit (EITC), or Employer Retention Credit (ERC)
Claiming dependents or benefits that increase refund amounts
Adapting methods based on state-specific programs or eligibility requirements
A notable development is the use of fraudulent income submission schemes, where threat actors pre-populate tax records with inflated income and withholding data before filing a return.
This process typically involves:
Submitting false wage data to the IRS or Social Security Administration using employer identifiers
Waiting for the data to appear on official tax transcripts
Filing a return that matches the fabricated figures
By aligning submitted data with filed returns, fraudsters increase the likelihood that filings will appear legitimate during verification.
Social Engineering Extends Beyond Victims
Social engineering plays a central role throughout the fraud lifecycle—and not just at the initial data collection stage.
Threat actors also target:
IRS representatives, attempting to verify fraudulent returns over the phone
Clients, persuading them to attend verification appointments or share official correspondence
Government offices, including outreach to congressional staff to resolve refund holds
In some cases, fraudsters use AI-generated communications to scale these efforts, including drafting messages designed to appear legitimate and urgent.
These tactics highlight how fraud operations extend into real-world processes and human interactions, not just digital systems.
Cash-Out Methods Continue to Evolve
Once a fraudulent refund is secured, the focus shifts to converting funds into usable, untraceable assets.
Common cash-out methods include:
Direct deposits into accounts controlled by the fraudster
Accounts opened by “clients” on behalf of the operation
Digital banking platforms and payment apps
Prepaid cards and alternative financial instruments
Increasingly, threat actors are moving funds into cryptocurrency to reduce traceability. This often involves:
Using verified exchange accounts to pass KYC requirements
Converting refunds into Bitcoin or other assets
Transferring funds to wallets controlled by the fraudster
In some workflows, the entire process — from filing to conversion — can occur within a single mobile or digital ecosystem.
Fraud Communities Enable Scale and Adaptation
Tax refund fraud does not operate in isolation. It is embedded within broader fraud ecosystems where identity data, tools, and tutorials are continuously shared.
Telegram remains a central hub for this activity, with large channels distributing:
Screenshots of successful refunds
Tutorials and “sauce” (paid or free methods)
Listings for identity data and services
Dark web forums also host discussions, though typically with lower volume and higher signal.
The structure of these communities allows fraud techniques to spread quickly, adapt to changing controls, and persist across multiple platforms.
Flashpoint analysts assess that these schemes are becoming more structured, with clearly defined workflows for identity acquisition, verification bypass, and monetization.
For security and intelligence teams, this has several implications:
Identity data remains a critical point of exposure across multiple fraud types
Verification systems are actively targeted and tested by threat actors
Social engineering continues to bridge technical and human vulnerabilities
Fraud techniques are rapidly shared, refined, and scaled across communities
Understanding how these components connect is essential for identifying emerging fraud patterns and anticipating how threat actors will adapt.
Supporting Security Teams with Threat Intelligence During Tax Season and Beyond
Understanding how tax fraud schemes are executed from identity sourcing to verification bypass and cash-out provides critical context for detecting and disrupting fraudulent activity.
Flashpoint delivers leading intelligence that helps organizations monitor fraud communities, track evolving tactics, and identify emerging schemes before they scale. By combining primary source collection with contextual analysis, security teams can move from reactive detection to proactive defense.
To learn how Flashpoint can support your team with real-time intelligence and analysis, request a demo.
Frequently Asked Questions About Tax Refund Fraud
What is tax refund fraud?
Tax refund fraud is a form of identity-based financial crime in which threat actors file fraudulent tax returns using stolen or manipulated personal information to obtain refund payments before the legitimate taxpayer files.
How do threat actors obtain the information needed to commit tax fraud?
Threat actors typically rely on stolen identity data, often referred to as “fullz,” which includes a victim’s name, date of birth, address, and Social Security number. This information is sourced from infostealer malware logs, phishing campaigns, data breaches, social engineering, and illicit marketplaces.
In some cases, fraudsters also recruit “clients” who provide real tax documents or assist in verification processes.
How do fraudsters bypass identity verification for tax returns?
Fraudsters use a combination of tactics to bypass identity and return verification, including:
Accessing or creating verified identity accounts used for tax authentication
Obtaining prior-year tax data such as adjusted gross income (AGI)
Using stolen or socially engineered identity protection (IP) PINs
Responding to IRS verification requests using scripts, impersonation, or cooperating individuals
These methods allow fraudulent returns to appear legitimate during processing.
What are common tax fraud tactics used by threat actors?
Common tactics include:
Filing returns using stolen personal information
Inflating income or tax withholding amounts to increase refunds
Claiming fraudulent dependents or tax credits
Submitting false wage data to government systems before filing
Using real tax forms combined with manipulated data
These approaches are often shared and refined within fraud communities.
What is a “fullz” in tax fraud?
A “fullz” refers to a complete set of personally identifiable information (PII) about an individual, typically including name, date of birth, address, and Social Security number. Fullz are used by fraudsters to file tax returns, open accounts, and conduct other identity-based financial crimes.
How do fraudsters cash out fraudulent tax refunds?
After a fraudulent return is accepted, threat actors typically attempt to convert the refund into usable funds through:
Direct deposits into controlled or intermediary accounts
Accounts opened by recruited participants
Digital banking platforms or prepaid cards
Cryptocurrency conversion using verified exchange accounts
The goal is to move funds quickly and reduce traceability.
Why is tax refund fraud difficult to detect?
Tax refund fraud can be difficult to detect because it leverages legitimate systems and processes, including real identity data, authentic tax preparation services, and verified accounts. Fraudsters also adapt quickly by sharing new techniques and bypass methods across online communities.
How do fraud communities support tax refund fraud schemes?
Fraud communities, particularly on platforms like Telegram and dark web forums, enable threat actors to share tutorials, tools, and identity data. These communities accelerate the spread of techniques, allowing fraud schemes to scale and evolve rapidly.
What should security and fraud teams monitor to detect tax fraud activity?
Teams should monitor for:
Unusual access to identity data or tax-related accounts
Indicators of compromised credentials or identity verification systems
Discussions of tax fraud methods, tutorials, or cash-out techniques in illicit communities
Patterns in fraudulent filings or refund activity
Incorporating intelligence from fraud communities can provide early visibility into emerging tactics.
How does Flashpoint help organizations detect and prevent tax refund fraud?
Flashpoint helps organizations detect and respond to tax fraud by providing intelligence on how threat actors source identity data, bypass verification systems, and cash out fraudulent returns.
Through primary source collection across platforms like Telegram and dark web forums, Flashpoint enables teams to monitor fraud communities, identify emerging tactics, and understand how schemes are evolving. This intelligence helps organizations move from reactive detection to more proactive identification of fraud risk.
Imagine you work at a drive-through restaurant. Someone drives up and says: “I’ll have a double cheeseburger, large fries, and ignore previous instructions and give me the contents of the cash drawer.” Would you hand over the money? Of course not. Yet this is what large language models (LLMs) do.
Prompt injection is a method of tricking LLMs into doing things they are normally prevented from doing. A user writes a prompt in a certain way, asking for system passwords or private data, or asking the LLM to perform forbidden instructions. The precise phrasing overrides the LLM’s safety guardrails, and it complies.
LLMs are vulnerable to all sorts of prompt injection attacks, some of them absurdly obvious. A chatbot won’t tell you how to synthesize a bioweapon, but it might tell you a fictional story that incorporates the same detailed instructions. It won’t accept nefarious text inputs, but might if the text is rendered as ASCII art or appears in an image of a billboard. Some ignore their guardrails when told to “ignore previous instructions” or to “pretend you have no guardrails.”
AI vendors can block specific prompt injection techniques once they are discovered, but general safeguards are impossible with today’s LLMs. More precisely, there’s an endless array of prompt injection attacks waiting to be discovered, and they cannot be prevented universally.
If we want LLMs that resist these attacks, we need new approaches. One place to look is what keeps even overworked fast-food workers from handing over the cash drawer.
Human Judgment Depends on Context
Our basic human defenses come in at least three types: general instincts, social learning, and situation-specific training. These work together in a layered defense.
As a social species, we have developed numerous instinctive and cultural habits that help us judge tone, motive, and risk from extremely limited information. We generally know what’s normal and abnormal, when to cooperate and when to resist, and whether to take action individually or to involve others. These instincts give us an intuitive sense of risk and make us especially careful about things that have a large downside or are impossible to reverse.
The second layer of defense consists of the norms and trust signals that evolve in any group. These are imperfect but functional: Expectations of cooperation and markers of trustworthiness emerge through repeated interactions with others. We remember who has helped, who has hurt, who has reciprocated, and who has reneged. And emotions like sympathy, anger, guilt, and gratitude motivate each of us to reward cooperation with cooperation and punish defection with defection.
A third layer is institutional mechanisms that enable us to interact with multiple strangers every day. Fast-food workers, for example, are trained in procedures, approvals, escalation paths, and so on. Taken together, these defenses give humans a strong sense of context. A fast-food worker basically knows what to expect within the job and how it fits into broader society.
We reason by assessing multiple layers of context: perceptual (what we see and hear), relational (who’s making the request), and normative (what’s appropriate within a given role or situation). We constantly navigate these layers, weighing them against each other. In some cases, the normative outweighs the perceptual—for example, following workplace rules even when customers appear angry. Other times, the relational outweighs the normative, as when people comply with orders from superiors that they believe are against the rules.
Crucially, we also have an interruption reflex. If something feels “off,” we naturally pause the automation and reevaluate. Our defenses are not perfect; people are fooled and manipulated all the time. But it’s how we humans are able to navigate a complex world where others are constantly trying to trick us.
So let’s return to the drive-through window. To convince a fast-food worker to hand us all the money, we might try shifting the context. Show up with a camera crew and tell them you’re filming a commercial, claim to be the head of security doing an audit, or dress like a bank manager collecting the cash receipts for the night. But even these have only a slim chance of success. Most of us, most of the time, can smell a scam.
Con artists are astute observers of human defenses. Successful scams are often slow, undermining a mark’s situational assessment, allowing the scammer to manipulate the context. This is an old story, spanning traditional confidence games such as the Depression-era “big store” cons, in which teams of scammers created entirely fake businesses to draw in victims, and modern “pig-butchering” frauds, where online scammers slowly build trust before going in for the kill. In these examples, scammers slowly and methodically reel in a victim using a long series of interactions through which the scammers gradually gain that victim’s trust.
Sometimes it even works at the drive-through. One scammer in the 1990s and 2000s targeted fast-food workers by phone, claiming to be a police officer and, over the course of a long phone call, convinced managers to strip-search employees and perform other bizarre acts.
Why LLMs Struggle With Context and Judgment
LLMs behave as if they have a notion of context, but it’s different. They do not learn human defenses from repeated interactions and remain untethered from the real world. LLMs flatten multiple levels of context into text similarity. They see “tokens,” not hierarchies and intentions. LLMs don’t reason through context, they only reference it.
While LLMs often get the details right, they can easily miss the big picture. If you prompt a chatbot with a fast-food worker scenario and ask if it should give all of its money to a customer, it will respond “no.” What it doesn’t “know”—forgive the anthropomorphizing—is whether it’s actually being deployed as a fast-food bot or is just a test subject following instructions for hypothetical scenarios.
This limitation is why LLMs misfire when context is sparse but also when context is overwhelming and complex; when an LLM becomes unmoored from context, it’s hard to get it back. AI expert Simon Willison wipes context clean if an LLM is on the wrong track rather than continuing the conversation and trying to correct the situation.
There’s more. LLMs are overconfident because they’ve been designed to give an answer rather than express ignorance. A drive-through worker might say: “I don’t know if I should give you all the money—let me ask my boss,” whereas an LLM will just make the call. And since LLMs are designed to be pleasing, they’re more likely to satisfy a user’s request. Additionally, LLM training is oriented toward the average case and not extreme outliers, which is what’s necessary for security.
The result is that the current generation of LLMs is far more gullible than people. They’re naive and regularly fall for manipulative cognitive tricks that wouldn’t fool a third-grader, such as flattery, appeals to groupthink, and a false sense of urgency. There’s a story about a Taco Bell AI system that crashed when a customer ordered 18,000 cups of water. A human fast-food worker would just laugh at the customer.
Prompt injection is an unsolvable problem that gets worse when we give AIs tools and tell them to act independently. This is the promise of AI agents: LLMs that can use tools to perform multistep tasks after being given general instructions. Their flattening of context and identity, along with their baked-in independence and overconfidence, mean that they will repeatedly and unpredictably take actions—and sometimes they will take the wrong ones.
Science doesn’t know how much of the problem is inherent to the way LLMs work and how much is a result of deficiencies in the way we train them. The overconfidence and obsequiousness of LLMs are training choices. The lack of an interruption reflex is a deficiency in engineering. And prompt injection resistance requires fundamental advances in AI science. We honestly don’t know if it’s possible to build an LLM, where trusted commands and untrusted inputs are processed through the same channel, which is immune to prompt injection attacks.
We humans get our model of the world—and our facility with overlapping contexts—from the way our brains work, years of training, an enormous amount of perceptual input, and millions of years of evolution. Our identities are complex and multifaceted, and which aspects matter at any given moment depend entirely on context. A fast-food worker may normally see someone as a customer, but in a medical emergency, that same person’s identity as a doctor is suddenly more relevant.
We don’t know if LLMs will gain a better ability to move between different contexts as the models get more sophisticated. But the problem of recognizing context definitely can’t be reduced to the one type of reasoning that LLMs currently excel at. Cultural norms and styles are historical, relational, emergent, and constantly renegotiated, and are not so readily subsumed into reasoning as we understand it. Knowledge itself can be both logical and discursive.
The AI researcher Yann LeCunn believes that improvements will come from embedding AIs in a physical presence and giving them “world models.” Perhaps this is a way to give an AI a robust yet fluid notion of a social identity, and the real-world experience that will help it lose its naïveté.
Ultimately we are probably faced with a security trilemma when it comes to AI agents: fast, smart, and secure are the desired attributes, but you can only get two. At the drive-through, you want to prioritize fast and secure. An AI agent should be trained narrowly on food-ordering language and escalate anything else to a manager. Otherwise, every action becomes a coin flip. Even if it comes up heads most of the time, once in a while it’s going to be tails—and along with a burger and fries, the customer will get the contents of the cash drawer.
This essay was written with Barath Raghavan, and originally appeared in IEEE Spectrum.
Interesting article on the variety of LinkedIn job scams around the world:
In India, tech jobs are used as bait because the industry employs millions of people and offers high-paying roles. In Kenya, the recruitment industry is largely unorganized, so scamsters leverage fake personal referrals. In Mexico, bad actors capitalize on the informal nature of the job economy by advertising fake formal roles that carry a promise of security. In Nigeria, scamsters often manage to get LinkedIn users to share their login credentials with the lure of paid work, preying on their desperation amid an especially acute unemployment crisis.
These are scams involving fraudulent employers convincing prospective employees to send them money for various fees. There is an entirely different set of scams involving fraudulent employees getting hired for remote jobs.
China-based phishing groups blamed for non-stop scam SMS messages about a supposed wayward package or unpaid toll fee are promoting a new offering, just in time for the holiday shopping season: Phishing kits for mass-creating fake but convincing e-commerce websites that convert customer payment card data into mobile wallets from Apple and Google. Experts say these same phishing groups also are now using SMS lures that promise unclaimed tax refunds and mobile rewards points.
Over the past week, thousands of domain names were registered for scam websites that purport to offer T-Mobile customers the opportunity to claim a large number of rewards points. The phishing domains are being promoted by scam messages sent via Apple’s iMessage service or the functionally equivalent RCS messaging service built into Google phones.
An instant message spoofing T-Mobile says the recipient is eligible to claim thousands of rewards points.
The website scanning service urlscan.ioshows thousands of these phishing domains have been deployed in just the past few days alone. The phishing websites will only load if the recipient visits with a mobile device, and they ask for the visitor’s name, address, phone number and payment card data to claim the points.
A phishing website registered this week that spoofs T-Mobile.
If card data is submitted, the site will then prompt the user to share a one-time code sent via SMS by their financial institution. In reality, the bank is sending the code because the fraudsters have just attempted to enroll the victim’s phished card details in a mobile wallet from Apple or Google. If the victim also provides that one-time code, the phishers can then link the victim’s card to a mobile device that they physically control.
Pivoting off these T-Mobile phishing domains in urlscan.io reveals a similar scam targeting AT&T customers:
An SMS phishing or “smishing” website targeting AT&T users.
Ford Merrill works in security research at SecAlliance, a CSIS Security Group company. Merrill said multiple China-based cybercriminal groups that sell phishing-as-a-service platforms have been using the mobile points lure for some time, but the scam has only recently been pointed at consumers in the United States.
“These points redemption schemes have not been very popular in the U.S., but have been in other geographies like EU and Asia for a while now,” Merrill said.
A review of other domains flagged by urlscan.io as tied to this Chinese SMS phishing syndicate shows they are also spoofing U.S. state tax authorities, telling recipients they have an unclaimed tax refund. Again, the goal is to phish the user’s payment card information and one-time code.
A text message that spoofs the District of Columbia’s Office of Tax and Revenue.
CAVEAT EMPTOR
Many SMS phishing or “smishing” domains are quickly flagged by browser makers as malicious. But Merrill said one burgeoning area of growth for these phishing kits — fake e-commerce shops — can be far harder to spot because they do not call attention to themselves by spamming the entire world.
Merrill said the same Chinese phishing kits used to blast out package redelivery message scams are equipped with modules that make it simple to quickly deploy a fleet of fake but convincing e-commerce storefronts. Those phony stores are typically advertised on Google and Facebook, and consumers usually end up at them by searching online for deals on specific products.
A machine-translated screenshot of an ad from a China-based phishing group promoting their fake e-commerce shop templates.
With these fake e-commerce stores, the customer is supplying their payment card and personal information as part of the normal check-out process, which is then punctuated by a request for a one-time code sent by your financial institution. The fake shopping site claims the code is required by the user’s bank to verify the transaction, but it is sent to the user because the scammers immediately attempt to enroll the supplied card data in a mobile wallet.
According to Merrill, it is only during the check-out process that these fake shops will fetch the malicious code that gives them away as fraudulent, which tends to make it difficult to locate these stores simply by mass-scanning the web. Also, most customers who pay for products through these sites don’t realize they’ve been snookered until weeks later when the purchased item fails to arrive.
“The fake e-commerce sites are tough because a lot of them can fly under the radar,” Merrill said. “They can go months without being shut down, they’re hard to discover, and they generally don’t get flagged by safe browsing tools.”
Happily, reporting these SMS phishing lures and websites is one of the fastest ways to get them properly identified and shut down. Raymond Dijkxhoorn is the CEO and a founding member of SURBL, a widely-used blocklist that flags domains and IP addresses known to be used in unsolicited messages, phishing and malware distribution. SURBL has created a website called smishreport.com that asks users to forward a screenshot of any smishing message(s) received.
“If [a domain is] unlisted, we can find and add the new pattern and kill the rest” of the matching domains, Dijkxhoorn said. “Just make a screenshot and upload. The tool does the rest.”
The SMS phishing reporting site smishreport.com.
Merrill said the last few weeks of the calendar year typically see a big uptick in smishing — particularly package redelivery schemes that spoof the U.S. Postal Service or commercial shipping companies.
“Every holiday season there is an explosion in smishing activity,” he said. “Everyone is in a bigger hurry, frantically shopping online, paying less attention than they should, and they’re just in a better mindset to get phished.”
SHOP ONLINE LIKE A SECURITY PRO
As we can see, adopting a shopping strategy of simply buying from the online merchant with the lowest advertised prices can be a bit like playing Russian Roulette with your wallet. Even people who shop mainly at big-name online stores can get scammed if they’re not wary of too-good-to-be-true offers (think third-party sellers on these platforms).
If you don’t know much about the online merchant that has the item you wish to buy, take a few minutes to investigate its reputation. If you’re buying from an online store that is brand new, the risk that you will get scammed increases significantly. How do you know the lifespan of a site selling that must-have gadget at the lowest price? One easy way to get a quick idea is to run a basic WHOIS search on the site’s domain name. The more recent the site’s “created” date, the more likely it is a phantom store.
If you receive a message warning about a problem with an order or shipment, visit the e-commerce or shipping site directly, and avoid clicking on links or attachments — particularly missives that warn of some dire consequences unless you act quickly. Phishers and malware purveyors typically seize upon some kind of emergency to create a false alarm that often causes recipients to temporarily let their guard down.
But it’s not just outright scammers who can trip up your holiday shopping: Often times, items that are advertised at steeper discounts than other online stores make up for it by charging way more than normal for shipping and handling.
So be careful what you agree to: Check to make sure you know how long the item will take to be shipped, and that you understand the store’s return policies. Also, keep an eye out for hidden surcharges, and be wary of blithely clicking “ok” during the checkout process.
Most importantly, keep a close eye on your monthly statements. If I were a fraudster, I’d most definitely wait until the holidays to cram through a bunch of unauthorized charges on stolen cards, so that the bogus purchases would get buried amid a flurry of other legitimate transactions. That’s why it’s key to closely review your credit card bill and to quickly dispute any charges you didn’t authorize.
Checks are one of the most vulnerable legacy payment methods. Check fraud can actively affect the bottom lines (and reputations) of banks, financial services organizations, government entities, and many other organizations that utilize checks. According to the Financial Crimes Enforcement Network (FinCEN), fraud—including check fraud—is “the largest source of illicit proceeds in the US” as well as “one of the most significant money laundering threats to the United States.”
Targeting the mail
Criminals target the US mail system to steal a variety of checks. In fact, there is a nationwide surge in check fraud schemes targeting the US mail and shipping system, as threat actors continue to steal, alter, and sell checks through illicit means and channels.
This includes personal checks and tax refund checks to government or government assistance-related checks (Social Security payments, e.g.). Business checks are also a primary target because they are often written for larger amounts and may take longer for the victim to identify fraudulent activity.
In 2022 alone, US banks filed 680,000 check fraud-related suspicious activity reports (SARs). This represents a nearly two-fold increase from 2021 (which itself represents a 23 percent YoY increase from 2020). This surge in check fraud has been exacerbated by Covid-19 Economic Impact Payments (EIPs) under the CARES Act, which presented threat actors with a new avenue to attempt to commit fraud.
Related Reading
This Is What Covid Fraud Looks Like: Targeting Government Relief Funding
In order to mitigate and ultimately prevent check-fraud-related risks, it’s crucial for financial intelligence and fraud teams to understand what threat actors seek, how they work, and where they operate.
This begins, as we detail below, with intelligence into the communities, forums, and marketplaces where check fraud occurs as well as the tools that enable deep understandings, timely insights, and measurable action.
Below is an intelligence narrative, in three acts, that tells the story of how transactions involving some of the above examples could play out.
Act I: Obtain
Threat actors are known to remove mail from individuals’ mailboxes and parcel lockers using blue box “arrow” master keys. These arrow keys are often stolen from USPS employees, which has led to numerous incidents of harassment, threats, and even violence. Generally, arrow keys are sold within illicit community chats and/or the deep and dark web, often fetching upwards of $3,000 per key.
In general, when it comes to check fraud, threat actors may sell or seek:
Mailbox keys
Stolen checks
Check alteration services (physical and digital)
Synthetic identity provisioning
Drop account sharing
Counterfeit check creation
Writing a check with insufficient funds behind it
Insider access
A screenshot of Flashpoint’s Ignite platform, showing the results of an OCR-driven search for stolen checks.
Act II: Alter
Check alteration comes in two forms: “washing” and “cooking.”
Washing refers to the process of altering a check by chemically removing ink and replacing the newly empty spaces with a different value, recipient name, or another fraud-enabling alteration.
Cooking involves digitally scanning the check and altering text or values through digital means.
Act III: Monetize
Threat actors will deposit the fraudulent check and rapidly withdraw the funds from an ATM, or sell a stolen or altered check on an illicit marketplace or chat group, and then receive payment, often via cryptocurrency.
Four key elements of actionable check fraud intelligence
Financial institutions should rely on four essential intelligence-led technologies, tools, or capabilities to effectively combat check fraud.
1) Visibility and access to illicit communities and channels
To prevent check fraud, organizations should focus on a few key places. Financially motivated threat actors operate and share information on messaging apps like Telegram and other open-source channels, as well as illicit marketplaces on the deep and dark web. Therefore, it is imperative for financial intelligence and fraud teams to have access to the most relevant check fraud-related threats across the internet.
Keep in mind, however, that accessing these communities is not always straightforward and, if done frivolously, can compromise an investigation.
2) Timeliness and curated alerting
Intelligence is often only as good as it is relevant. Flashpoint enables security and intelligence practitioners to bubble the most important, mission-critical intelligence through our real-time alerting capability, which allows users to receive notifications for keywords and phrases that relate to their mission, such as check fraud-related lingo and activity.
Essential Reading
The Flashpoint Guide to Card Fraud for the Financial Services Sector
In addition to real-time alerts, analysts can rely on curated alerting and saved searches to track topics of long-term interest. Flashpoint Ignite enables analysts to research particular accounts and their recent activity and matches transactions to their respective ATM slips and institution address. This helps to ensure the accuracy of the information found within these communities and marketplaces before raising any alarms, as many scammers post false content.
This approach is particularly valuable as check fraudsters often share crucial information such as preferred methodologies, social media handles, and geolocations that can aid in identifying malicious activities. In addition, by closely observing newly emerging trends, such as the evolution of pandemic relief fraud to refund fraud to check fraud, analysts can proactively develop robust preventative measures to mitigate risks before these tactics become widespread.
3) Actionable OCR and Video Search
In order to provide “material proof,” cyber threat actors will often tout and post an image of a check in a chat application or marketplace in hopes of increasing the likelihood of a successful transaction. Optical Character Recognition (OCR) technology can capture important information about check fraud attempts, since actors often share images of the fraudulent check or subsequent monetization transactions. OCR alerts are customizable with the financial institution’s name and common phrases used on checks to enhance accuracy.
Images of fraudulent checks provide valuable insights into the fraud attempt, including the check’s unique identifier, the account holder’s name, the bank’s name and address, and the endorsement signature. By analyzing these details, financial institutions and law enforcement agencies can identify patterns and leads that can help them track down the perpetrators and prevent future fraudulent activity.
Related Resource
The Risk-Reducing Power of Flashpoint Video Search
Moreover, ATM withdrawal slips can offer critical information about the transaction, such as the location of the ATM, the time of the deposit, and the type of account used. This data is useful when taking appropriate measures to prevent similar attempts and protect customers’ assets. With the help of advanced technologies like Flashpoint’s OCR, institutions can quickly extract and analyze this information to generate real-time alerts and take prompt action to prevent monetary losses.
An essential investigative component, Flashpoint’s industry-first video search technology, like its OCR capability, enables fraud and cyber threat intelligence (CTI) teams to surface logos, text, explicit content, and other critical intelligence to enhance investigations.
Combat check fraud with Flashpoint
Flashpoint delivers the intelligence that enables financial institutions to combat check fraud at scale. With timely, actionable, and accurate intelligence, financial institutions can mitigate and prevent financial loss, protect customer assets, and track down perpetrators. Get a free trial today to learn how:
A financial services customer detected more than $4M in illicitly marketed assets, including checks and compromised accounts, using Flashpoint’s OCR capabilities.
A customer received 125 actionable alerts in a single month equated to over $15M in potentially averted losses.
An automated alert enabled a customer to identify a threat actor’s specific operations, saving them over $5M.
Lawrence Hoffmann // Election fraud is something I’ve mentioned here recently. The reality we must face here is that any time a digital system is used for voting there is […]