Login
Palo Alto Crosswalk Signals Had Default Passwords
9 January 2026 at 13:06
Palo Alto’s crosswalk signals were hacked last year. Turns out the city never changed the default passwords.

Palo Alto’s crosswalk signals were hacked last year. Turns out the city never changed the default passwords.

Why are companies still recommending an 8-character password minimum? Passwords are some of the easiest targets for attackers, yet companies still allow weak passwords in their environment. Multiple service providers recommend […]
The post Podcast: Passwords: You Are the Weakest Link appeared first on Black Hills Information Security, Inc..
Michael Allen // Every year around the holidays I end up having a conversation with at least one friend or family member about the importance of choosing unique passwords for […]
The post The Paper Password Manager appeared first on Black Hills Information Security, Inc..
Why are companies still recommending an 8-character password minimum? Passwords are some of the easiest targets for attackers, yet companies still allow weak passwords in their environment. Multiple service providers recommend […]
The post Webcast: Passwords: You Are the Weakest Link appeared first on Black Hills Information Security, Inc..
Darin Roberts // “Why do you recommend a 15-character password policy when (name your favorite policy here) recommends only 8-character minimum passwords?” I have had this question posed to me […]
The post Passwords: Our First Line of Defense appeared first on Black Hills Information Security, Inc..
David Fletcher// The weak password policy finding is typically an indicator of one of two conditions during a test: A password could be easily guessed using standard authentication mechanisms. A […]
The post Finding: Weak Password Policy appeared first on Black Hills Information Security, Inc..


Kelsey Bellew // Dear Big All-Powerful Company, Your idea of a ‘strong password’ is flawed. When I first saw the following message, I laughed. I said out loud, “No, you […]
The post An Open Letter about Big All-Powerful Company’s Password Policy appeared first on Black Hills Information Security, Inc..
Sally Vandeven // Back in November Beau Bullock wrote a blog post describing how his awesome PowerShell tool MailSniper can sometimes bypass OWA portals to get mail via EWS if […]
The post How to Bypass Two-Factor Authentication – One Step at a Time appeared first on Black Hills Information Security, Inc..
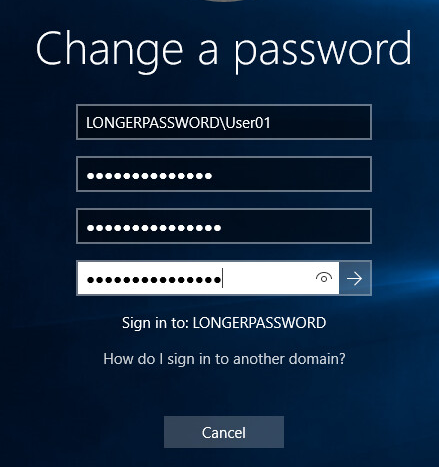
Kent Ickler // As a start to a series on Windows Administration in the eyes of a security-conscious “Windows Guy” I invite you on configuring AD DS PSOs (Password Security […]
The post How to Increase the Minimum Character Password Length (15+) Policies in Active Directory appeared first on Black Hills Information Security, Inc..
Lawrence Hoffman // The list this week is a little shorter, I didn’t include a tool or POC link as I usually do. No particular reason, just didn’t run across […]
The post Lawrence’s List 072216 appeared first on Black Hills Information Security, Inc..
Carrie Roberts // Answer: Enough to make it worth it! Penetration testers love to perform password spraying attacks against publicly available email portals as described here in this great post by Beau Bullock. […]
The post Question: What Can I Learn from Password Spraying a 2FA Microsoft Web App Portal? appeared first on Black Hills Information Security, Inc..
Lawrence Hoffman // It’s been one of those crazy busy weeks. I always feel like I didn’t get enough time to read articles, surf Reddit, and attempt to keep up […]
The post Lawrence’s List 061016 appeared first on Black Hills Information Security, Inc..
Joff Thyer // Recently I have been thinking about online challenges I encounter in daily life. As I thought about it, I realized that many of these items I […]
The post 10 Ways to Protect Your Online Digital Life appeared first on Black Hills Information Security, Inc..
Rick Wisser & Gail Menius // Frequently we get asked about where to store passwords. Should they be stored in a word/excel /txt file on your computer? Maybe, written down […]
The post Herding Those Pesky Passwords appeared first on Black Hills Information Security, Inc..
Gail Menius // Once upon a time, in a land not too far away (about two miles from where I’m sitting now) I used to be an elementary school librarian. […]
The post Passphrases for Tiny People appeared first on Black Hills Information Security, Inc..
Brian King // There’s a one-liner password spray script that a lot of folks use to see if anyone on a domain is using a bad password like LetMeIn! or […]
The post Check\ Your\ Tools appeared first on Black Hills Information Security, Inc..
Beau Bullock // This is part two of a series of posts (See part 1 here) where I am detailing multiple ways to gain access to domain user credentials without ever being […]
The post Password Spraying Outlook Web Access – How to Gain Access to Domain Credentials Without Being on a Target’s Network: Part 2 appeared first on Black Hills Information Security, Inc..
Beau Bullock // In this series of posts I am going to detail multiple ways to gain access to domain user credentials without ever being on a target organization’s network. […]
The post Exploiting Password Reuse on Personal Accounts: How to Gain Access to Domain Credentials Without Being on a Target’s Network: Part 1 appeared first on Black Hills Information Security, Inc..
Sally Vandeven // As pentesters we LOVE passwords – they come in all shapes and sizes. A good password has 16+ characters and a mix of case, digits and special […]
The post Your Password Is… wait for it… NOT Always Encrypted appeared first on Black Hills Information Security, Inc..