❌

Normal view

Received — 28 October 2026 ⏭ Palo Alto Networks Blog

Palo Alto Networks Named a Leader in the 2026 Gartner® Magic Quadrant™ for Privileged Access Management

26 October 2026 at 16:07

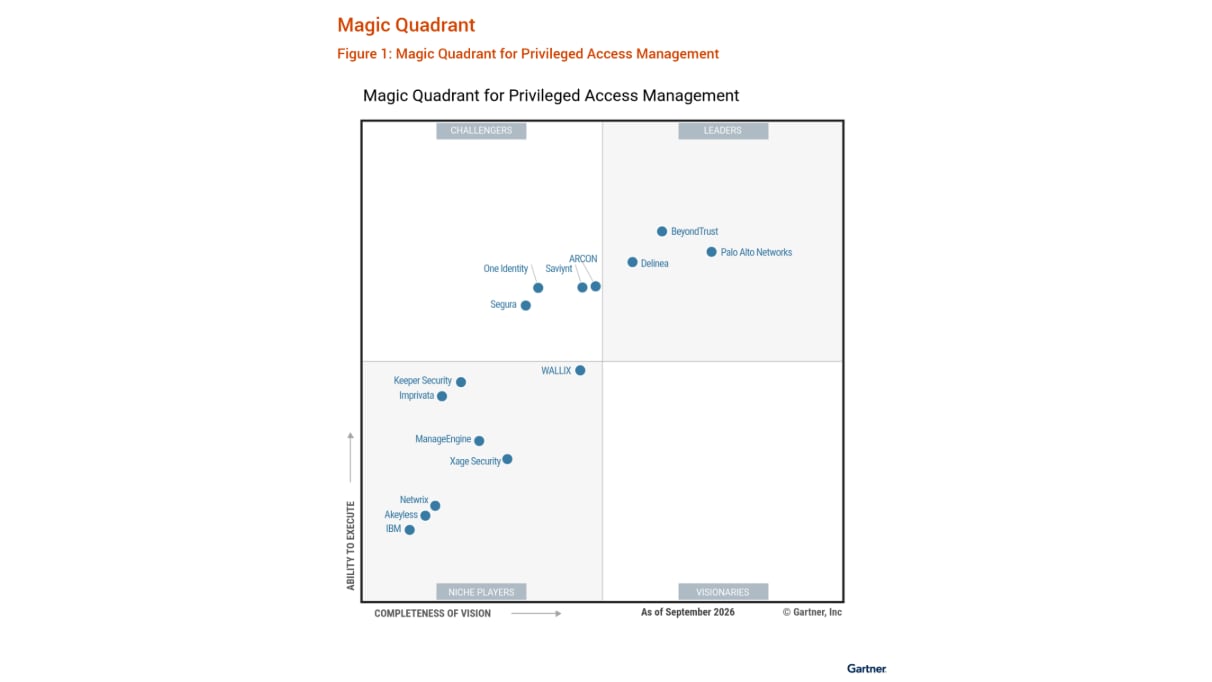
For the eighth consecutive time, Palo Alto Networks is recognized as a Leader in the 2026 Gartner® Magic Quadrant™ for Privileged Access Management. Once again, it is positioned furthest along in Completeness of Vision and has been positioned so in every Magic Quadrant published for this category.

Read the 2026 Gartner® Magic Quadrant™ for Privileged Access Management.

Gartner Magic Quadrant PAM

Identity is not a siloed risk. As an increasingly attractive target for threat actors, it must be understood and secured across the entire attack surface. For our customers, the benefit is clear: as part of Palo Alto Networks, Idira helps you adopt AI innovation at speed while retaining control over privileged access.

Why Vision Matters Most Right Now

The 2026 Gartner Magic Quadrant evaluates providers across their Ability to Execute and Completeness of Vision. We feel that being positioned furthest in Completeness of Vision matters most in moments of technology change like this one. Idira is built for an environment where:

  • Identity is the attack surface, and frontier AI lets attackers move faster, increasingly logging in rather than breaking in.
  • Identities have exploded, and human and machine privilege alike must be controlled.
  • The pace of change has never been higher, as organizations race to adopt AI and modernize infrastructure without losing control.

Customers need a partner that can execute on an innovative vision as the threat and technology landscape evolves. With the scale of Palo Alto Networks behind us, we are focused on securing every identity and every moment of privilege in the AI enterprise.

The AI Era Demands More From PAM

We are in a new era, where identity and access have fundamentally changed. Machine identities now outnumber humans 109 to 1, AI agents (which require access to enterprise systems to do useful work) are entering the workforce, and attackers have noticed. That access must be governed alongside the human and machine identities already protected. Increasingly, though, attackers log in rather than break in, and PAM must evolve to stay ahead of these challenges. PAM must now extend beyond vaulted administrator credentials to discover, control, and govern privilege across the enterprise.

Idira’s Modern PAM platform is enabling PAM to meet the demands of the AI era; it combines vaulted access and zero standing privileges (ZSP) with secrets management, workload security, and identity governance. We are bringing ZSP to every modern target, including cloud, apps, and Kubernetes. And access challenges go beyond humans, so Idira does as well. To secure non-human access, Idira added native SPIFFE/SVID support to deliver short-lived cryptographic identities to workloads and AI agents. Our ability to deliver and innovate on our vision enables Idira to deliver purpose-built, end-to-end protection at scale for the modern AI enterprise.

Modernizing PAM: Where We Deliver

Making modern PAM easier to adopt is central to our approach. 

While some of the largest organizations continue to trust Idira for our proven traditional PAM leadership, they now also rely on us to guide their modern PAM transformation initiatives.

Data-Driven Innovation: We believe that our Transformation Decision Engine, which uses customer environment data to quantify the value of PAM modernization, combined with our years of proven experience guiding both the implementation and modernization of PAM programs across our expansive customer base, demonstrates our ability to help customers through any stage of their PAM journey with an informed, data-driven approach. 

Customer Experience: Idira guides cross-functional security teams through complex operational shifts, from standing access to ZSP, supported by the Idira Blueprint, hands-on training, and an active peer community. 

Scale and Reach: Idira customers already have a partner with global reach, and joining Palo Alto Networks extends it further. Our security platform sees identity risk across the whole attack surface, so a stolen or abused privilege becomes a signal your defenses act on in the moment, backed by the investment and expertise of the industry's largest cybersecurity company.

Ready for the Demands of the AI Enterprise 

Eight reports, eight times furthest in vision. I'm grateful to the customers whose trust and expertise shaped every one of them. This is also a first, as it’s the first report to carry the Palo Alto Networks name. Since Idira joined forces with Palo Alto Networks, our PAM expertise and platform now sit inside the industry's leading cybersecurity company, where privileged access connects to real-time threat detection and response, AI security, and Unit 42 threat intelligence.

The next chapter of privileged access is being written now, by attackers with frontier AI models and by enterprises deciding how fast to move. We intend to stay furthest ahead of both.

Thank you to our customers and community for your trust, and for the partnership that helps shape our innovation.


Gartner, Magic Quadrant for Privileged Access Management, Paul Mezzera, Shubham Gera, Tarun Rohilla, Scott Brinker, 21 October 2026.

Gartner and Magic Quadrant are trademarks of Gartner, Inc. and/or its affiliates.

Gartner does not endorse any company, vendor, product or service depicted in its publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner publications consist of the opinions of Gartner’s business and technology insights organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this publication, including any warranties of merchantability or fitness for a particular purpose.


What is the Gartner® Magic Quadrant™?

“Magic Quadrant reports are a culmination of rigorous, fact-based research in specific markets, providing a wide-angle view of the relative positions of providers in markets where growth is high and provider differentiation is distinct. Providers are positioned into four quadrants: Leaders, Challengers, Visionaries and Niche Players. The research enables you to get the most from market analysis in alignment with your unique business and technology needs."

How can PAM help secure AI agents in the enterprise?

PAM can help secure AI agents by controlling their access to systems and data, protecting the secrets they use, and recording their access and actions. Capabilities vary by solution; controls should limit each agent’s permissions and how long those permissions remain active. Learn more about Idira Agentic Identity Security.

How does zero standing privileges differ from vaulted access?

Vaulted access protects stored privileged credentials. ZSP removes standing privileged access by granting permissions for a specific task and revoking them when the task or authorized period ends. Modern PAM can combine both approaches to support different environments and access needs.

The post Palo Alto Networks Named a Leader in the 2026 Gartner® Magic Quadrant™ for Privileged Access Management appeared first on Palo Alto Networks Blog.
Palo Alto Networks Brings Continuous AI Defense and Prisma AIRS to the OpenAI Marketplace

23 October 2026 at 18:32

Palo Alto Networks announces that Unit 42® Continuous Frontier AI Defense and Prisma AIRS™ are now on the newly launched OpenAI Marketplace, making them directly available to OpenAI’s enterprise customers. Threat actors are deploying artificial intelligence to find and exploit vulnerabilities at unprecedented speed, compressing breach cycles by almost 97%—from weeks down to mere hours. Human-speed defense can no longer keep pace with adversaries executing automated, continuous attacks.

AI Investments: The OpenAI Marketplace Advantage

For enterprise organizations holding OpenAI spend commitments, this milestone offers a compelling 2-for-1 financial and strategic advantage. Security teams can now deploy machine-speed, proactive defense while retiring their pre-committed OpenAI spend.

Palo Alto Networks offers two flagship solutions available for procurement through the OpenAI Marketplace.

  • Unit 42® Continuous Frontier AI Defense: An always-on, expert-led agentic offensive security service that uses defender-grade models to discover, validate, and accelerate the remediation of exposures across applications and network assets before weaponization.
  • Prisma® AIRS™: A comprehensive AI security platform designed to provide complete discovery, risk assessment, runtime protection, identity and data governance, and observability for AI applications, agents, models, and artifacts across enterprise cloud platforms, SaaS environments, and endpoints.

Machine-Speed Defense with Unit 42 Continuous Frontier AI Defense

Unit 42 Continuous Frontier AI Defense is an expert-led, agentic offensive security service engineered to identify, validate, and remediate enterprise exposures as an organization’s environment changes.

This always-on, agentic service combines our offensive security experts with our proprietary multi-model harness, which uses defender-grade frontier models to discover vulnerabilities, validate real-world exploitability, and accelerate remediation across applications, identities, cloud infrastructure, and network assets as an organization’s environment changes. At the core of this capability is our proprietary multi-model software harness that dynamically routes security tasks to the optimal AI model, maximizing efficacy and coverage while managing the cost of frontier AI at scale.

The harness integrates defender-grade models, including OpenAI’s GPT-5.6-Cyber, and other commercial models alongside open-weight models and Unit 42 threat intelligence. By executing non-destructive adversary simulations across first- and third-party environments, the system proves actual exploitability and delivers prioritized remediation guidance including actionable fixes, code-level changes, and virtual patches. Organizations can pair this with Frontier Virtual Patching to block exploits long before official patches exist or CVEs are publicly disclosed.

The real-world impact of this proactive methodology was validated over six months of in-house testing and across more than 75 customer engagements backed by a $17 million R&D investment. During internal deployment within Palo Alto Networks, the service uncovered over two years’ worth of exposures in just three weeks. In customer assessments, the underlying analysis identified exposures in 100% of assessed organizations, with 37% rated high or critical severity. Crucially, over two-thirds of exposures found in third-party applications had no known CVE, proving the urgent necessity of continuous, AI-driven discovery.

Unit 42 Continuous Frontier AI Defense is available worldwide today on an annual subscription basis. Register for our upcoming Virtual Threat Briefing to see how we apply Frontier AI, our proprietary multi-model harness, and offensive security expertise to protect Palo Alto Networks and our customers.

To learn more about Unit 42 Continuous Frontier AI Defense, register for the upcoming Virtual Threat Briefing here.

Scale Enterprise AI Adoption Safely with Prisma AIRS

As OpenAI customers rapidly scale their use of powerful AI models, AI coding assistants, and autonomous agents, the enterprise attack surface is expanding faster than traditional security teams can manage. The transition to autonomous AI breaks traditional security boundaries, creating shadow AI blind spots, supply chain risks in open-source base models, unsafe actions from malicious inputs, and uncontrolled AI agents executing tasks with excessive permissions.

Prisma AIRS: Secure Every AI Ambition

Prisma AIRS is the Palo Alto Networks unified AI security platform, enabling enterprises to accelerate AI adoption while maintaining control over sensitive data, agent identities, autonomous actions and AI costs. Recognized by Gartner as a Market Shaper in the September 2026 Emerging Market Quadrant for AI Application Security – Established Vendors, Palo Alto Networks brings together discovery, continuous risk assessment, real-time protection and centralized governance to secure AI applications and agents across enterprise environments.

  • Gain Visibility Across Enterprise AI: Discover and inventory AI applications, coding assistants, autonomous agents and associated assets across endpoints, cloud and enterprise environments. Identify shadow AI and gain visibility into the AI systems operating across the organization.
  • Identify Risks Before They Become Threats: Continuously assess AI security posture, scan models and agent artifacts—including skills and MCP servers—for vulnerabilities and supply chain risks, and proactively red team AI applications and agents to uncover exploitable weaknesses before deployment.
  • Secure AI Interactions, Data and Agent Identities: Enforce real-time protection against prompt injection, malicious interactions and sensitive data exposure. Verify agent identities, enforce least-privilege access and prevent unauthorized actions as agents interact with enterprise systems and data.
  • Centralize AI Policy, Access and Spend: Use AI Gateway to govern connections to LLMs, MCP servers, APIs and enterprise services. Centralize policy enforcement, control model and provider access, monitor consumption and manage AI usage and costs across teams and applications.

Together, these capabilities help OpenAI enterprise customers secure AI-powered workflows, maintain accountability for autonomous actions and scale AI adoption with consistent security and governance.

Book a demo to see our AI Security solution in action.

The post Palo Alto Networks Brings Continuous AI Defense and Prisma AIRS to the OpenAI Marketplace appeared first on Palo Alto Networks Blog.
Millions of PHP Instances Exposed - What Organizations Need To Do Right Now

21 October 2026 at 17:31

Two critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619) have been published. Both vulnerabilities carry a severe CVSS score of 9.2 (more technical details are in the Unit 42 Threat Brief). 

This is not just another high-severity vulnerability disclosure, it marks the opening chapter in a massive acceleration of cyberthreats that will define the foreseeable future. Because PHP is widely used globally (by some estimates, more than half of all websites), the sheer scale of this is massive. Navigating this new reality demands immediate imperatives, including continuous, proactive vulnerability discovery before adversaries weaponize code, and a modern defense strategy that pairs traditional patching with real-time virtual patching. At a footprint of 22 million exposed instances, relying on manual remediation cycles alone is not a viable defense.

For context, exposures are typically in the thousands, for example around 50,000 potentially vulnerable exposed instances for recent NetScaler vulnerabilities, and about 16,000 exposed instances of BeyondTrust, potentially vulnerable to CVE-2026-1731. Pervasive open-source software introduces an exposure footprint on an entirely different order of magnitude. 

This situation illustrates what I shared in Defender’s Guide to the Frontier AI Impact on Cybersecurity. We’re officially in a new reality, and this is going to be an ongoing cycle.

An Accelerating Cycle

The latest frontier AI models are extraordinarily capable at finding vulnerabilities in code. We’ll see these models continue to surface critical issues at a pace faster than ever before.

But here’s the challenge: As soon as patches for vulnerabilities are available, attackers will reverse engineer the patch, locate the root flaw, and target them in near real time. It simply takes too long to apply patches to every system. This vulnerability deluge demands urgency and new technologies, such as virtual patching, are needed.

What Organizations Should Do Now

(1) Assess Your Open Source Inventory

Given the unprecedented speed at which new, critical vulnerabilities are being found with frontier AI, organizations need the ability to understand their true exposure at a moment’s notice. Attack surface management solutions have never been more critical for finding these blind spots across your entire codebase and supply chain. You can’t protect what you can’t see.

Additionally, services like Unit 42 Continuous Frontier AI Defense put defender-grade AI models in the hands of defenders to find and fix vulnerabilities before attackers can weaponize them.

(2) Prioritize Remediation Based on Reachability

You have to reduce what is reachable by attackers. You can't instantly patch everything everywhere, so prioritize what needs to be fixed first based on attack-path reachability. Secure what must be accessible to the public internet, and evaluate your environments to understand which of those exposed PHP instances carry the most immediate risk. For example, Cortex Xpanse and exposure management are great tools for determining reachability and automating remediation.

(3) Secure your AI deployments

While not the main focus for these PHP vulnerabilities, rapid deployment of AI across organizations is expanding the attack surface. All AI deployments must be secure AI deployments.

(4) Mitigate and Ensure Attack Protections

While you coordinate patching with your development teams, ensure best-in-class protections are in place to block the actual exploits. Mitigate against potential attacks immediately through proactive virtual patching and reducing overall exposure. Deploying high-fidelity virtual patches across your network and cloud security provides the mitigation layer necessary to give your teams the time they need to update the actual software safely.

Our new Frontier Virtual Patching capability delivered preemptive coverage for these PHP vulnerabilities ahead of today’s public disclosure. Additionally, Palo Alto Networks customers are protected from exploitation of these vulnerabilities by Advanced Threat Prevention available on our next-generation firewalls and Prisma Access.

(5) Deploy Real-Time Security Operations

Autonomous AI-driven attacks will drive attack lifecycles to minutes requiring every SOC to achieve single-digit mean time to detect (MTTD) and mean time to respond (MTTR).

The Path Forward: Institutionalize Defenses

This isn’t a one-and-done situation. With frontier AI compressing the patch-to-exploit window to minutes, assessing exposure, prioritizing reachability, mitigating and ensuring attack protections must become a continuous, automated motion.

This is a pivotal moment. While the scale of the challenge presented by frontier AI is real, I’m confident in our ability to solve it. Take the steps to secure your organization today, and build the foundation needed to ensure the advantage remains with the defender.

Mitigating Critical PHP Vulnerabilities (CVSS 9.2) at Machine Speed

When frontier AI models accelerate both vulnerability discovery and reverse-engineering of patches, traditional remediation creates an unavoidable window of exposure. Get started with Frontier Virtual Patching in Advanced Threat Prevention Plus to solve this structural delay.
Get Started

The post Millions of PHP Instances Exposed - What Organizations Need To Do Right Now appeared first on Palo Alto Networks Blog.
Advancing Agentic AI Security with Palo Alto Networks and NVIDIA

AI is moving from answering questions to taking action. Agents can use tools, access enterprise data, and carry out work across systems on our behalf or autonomously. This creates opportunities for businesses to move faster, but it also changes what security must protect. An agent’s identity, the authority it carries, and the actions it takes all become security decisions.

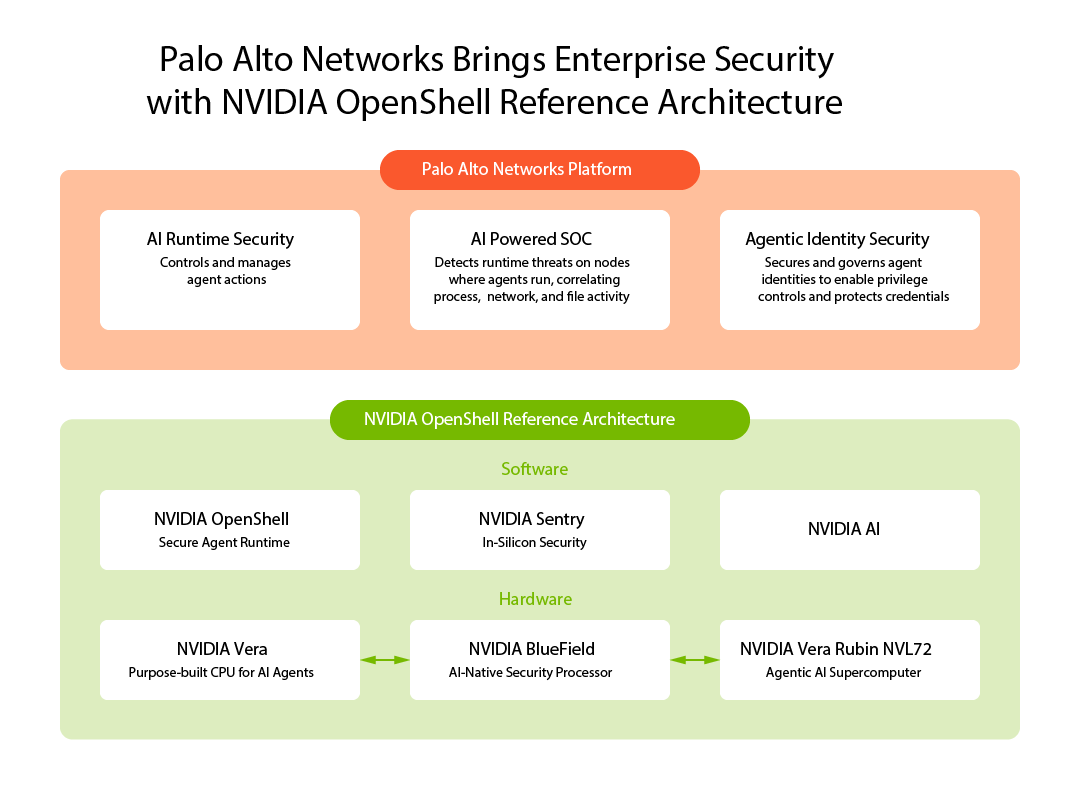
As enterprises put agents into production, they need controls that keep pace without hindering the work those agents are designed to do. Palo Alto Networks is working with NVIDIA to advance this goal across five connected areas in support of the NVIDIA OpenShell Reference Architecture for safe AI agents: an AI gateway on NVIDIA Vera CPU systems; runtime protection on NVIDIA BlueField DPUs; agent identity governance on NVIDIA Sentry; AI factory visibility through an AI-driven, agentic security operations center (SOC); and partner services that help customers implement a secure architecture.

Palo Alto Networks AI Runtime Security Extends Protection Across the AI Factory and Edge

Until now, the AI factory conversation has centered primarily on compute capacity and token generation. But as autonomous agents execute higher-stakes workloads, runtime security has become just as essential. Agents can be steered past their guardrails, and a compromised host cannot be trusted to accurately report what occurred. To be effective, security teams require visibility and enforcement that operate independently of the host environment.

Palo Alto Networks AI Runtime Security on NVIDIA BlueField DPUs isolates security processing in a dedicated infrastructure domain. Because BlueField sits in the path between agents and the models, data, and services they access, security policies are enforced in silicon — beyond the reach of a compromised host. This capability safeguards both GPU-accelerated AI workloads and CPU-based agent runtimes and is now generally available across AI factory and industrial edge deployments. Offloading security from the host node delivers two critical benefits: increased token throughput and stronger runtime protection across the entire AI factory.

Deployment at scale must be manageable. Our work with Spectro Cloud manages the deployment and operation of AI Runtime Security on BlueField DPUs, enabling consistent management across the AI factory infrastructure — from the data center to distributed edge environments. 

Idira Governs the Identity Behind Every Agent Action

Runtime protection answers what an agent is doing. Identity governance helps determine whether it is authorized to do it.

An agent may act for a person, a team, or an autonomous business process, often requiring access to multiple tools and data sources across the organization. Granting an agent broad, persistent access creates risk, while making access too restrictive limits its usefulness. To achieve the optimal balance of control and agent access, Palo Alto Networks is advancing an integration between agentic identity security and NVIDIA Sentry on BlueField — bringing identity and delegated authority closer to where agent interactions are governed.

The goal is to give each agent a verifiable identity, grant access appropriate to its task, and make its actions attributable. Once available, this solution will deliver zero-trust protection and tamper-resistant auditing for agents by moving the security controls — including identity — to the NVIDIA Bluefield DPU, separate from the host operating system. This addresses an immediate business need — enabling enterprises to scale agent deployments while retaining control over whose authority agents use and which resources they can reach.

Bringing AI Factory Signals into Cortex

Security teams need visibility into activity across the infrastructure that runs AI agents. Palo Alto Networks has announced an integration of Cortex XSIAM with NVIDIA DOCA Argus, which monitors host activity from BlueField’s independent trust domain. This provides security operations teams with runtime signals that do not rely on an agent installed on the host being monitored.

By bringing those signals together with network, cloud, and identity data in an AI-driven SOC, security teams can investigate AI infrastructure in the context of the broader enterprise. Palo Alto Networks is continuing to develop this foundation to support broader fleet visibility and more comprehensive response workflows — enabling security teams to identify unusual activity and act with greater confidence as AI deployments grow.

AI agents run within the NVIDIA OpenShell secure runtime, operated directly on the NVIDIA Vera CPU within the NVIDIA OpenShell Platform. Security observability is completely offloaded to the NVIDIA BlueField DPU. Operating out-of-band, NVIDIA Sentry, built on DOCA Argus, provides real-time memory and network inspection to detect threats without slowing AI inference. When malicious events or policy violations occur, DOCA Argus streams high-fidelity alerts directly to Palo Alto Networks Cortex XSIAM, where they can be automatically correlated and surfaced for rapid threat response. 

Turning Secure AI Factory Designs into Deployments

Customers need more than an architecture diagram to bring an AI factory into production. They need a practical path to design, validate, and operate security across compute, networking, applications, and the SOC.

Palo Alto Networks is working with strategic vendors , including Deloitte and World Wide Technology (WWT), to help customers plan and deploy secure NVIDIA AI factories. Deloitte’s Silicon-to-Service (S2S) offering, combined with its Secure AI Foundations, helps organizations implement AI use cases on NVIDIA AI infrastructure through validated architectures and managed services. By building security into the full AI factory stack, Deloitte helps clients balance performance, safety, and cost as they scale from pilot to production.  

WWT’s AI Proving Ground allows customers to evaluate and test an integrated stack before committing to production deployment.These engagements can help enterprises move from individual security components to a repeatable approach tailored to their environments and requirements.

Building Confidence into the Next Phase of Agentic AI

The value of agentic AI depends on an enterprise’s ability to give agents useful access while maintaining control over their actions. This requires runtime protection, governed identities, independent visibility, and a unified way to manage controls across the enterprise. 

Palo Alto Networks delivers comprehensive security across every layer of the AI factory through a unified platform. In collaboration with NVIDIA, we support the NVIDIA OpenShell Reference Architecture for enterprise governance, isolation, and security.  Together, we deliver the continuous protection needed to move safely from AI agent pilots to full-scale enterprise production.

To learn more about the general availability of AI Runtime Security on the BlueField DPU, read our blog, Palo Alto Networks Announces Support for NVIDIA Enterprise AI Factory. 

The post Advancing Agentic AI Security with Palo Alto Networks and NVIDIA appeared first on Palo Alto Networks Blog.
Reinventing Endpoint Security with Cortex XDR One

19 October 2026 at 14:59

Enterprises spent the last two years racing to capture the vast potential of AI, authorizing AI agents to touch production code, internal databases, customer tickets and financial ledgers. Because these agents operate non-deterministically with broad capabilities, they can easily be manipulated into unexpected or malicious behavior. The result is agents breaking out of isolation, shifting AI risk from a hallucinating chatbot to an operational liability. 

The standard fixes, such as software containers or prompt-level guardrails, aren't sufficient to prevent malicious agent behavior. And traditional endpoint security was not designed to secure agents, which operate with real user access. Just as we pioneered XDR to include network, identity and cloud, we must now expand protection to secure agents in the enterprise. 

Cortex XDR One brings together XDR and Koi Agentic Endpoint Security to protect both traditional system processes and AI agents, delivering layered enforcement across an agent’s execution path. XDR One is designed to control an agent’s actions at the source, enforce hard boundaries at the operating system level, and spot rogue behavior through an AI-driven layer of defense.

An Emerging Security Blind Spot

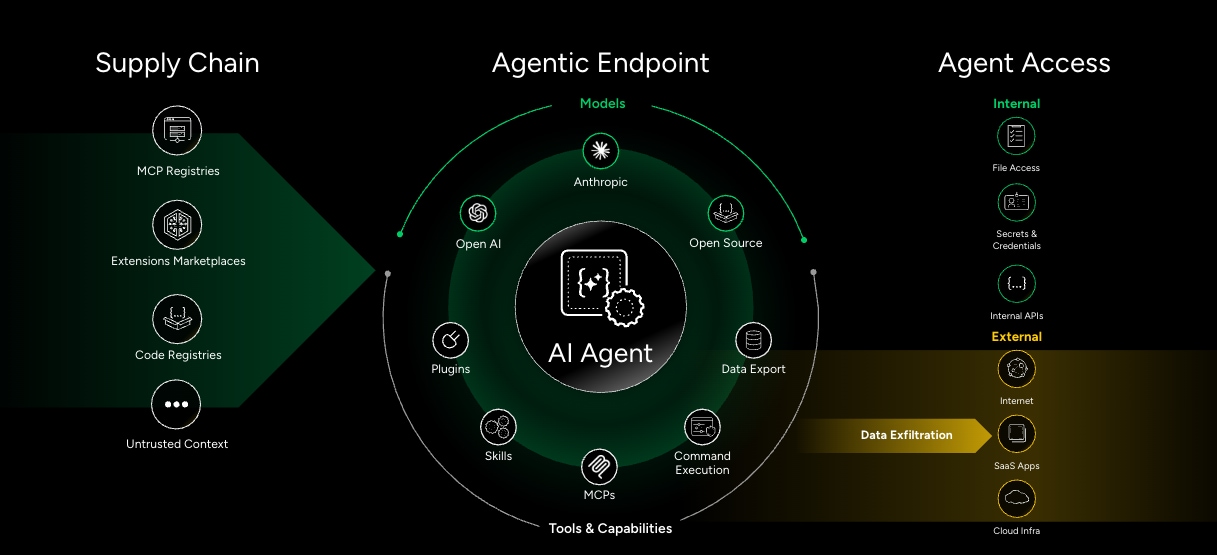
Endpoints have evolved from controlled execution environments into complex ecosystems of AI coding agents, AI co-pilots, MCP servers and personal agents with access to sensitive data and systems. These artifacts can bypass traditional controls and operate in critical blind spots. 

When an agent ingests an untrusted input, connects to a compromised enterprise app or executes an unauthorized command, it transforms from a productivity tool into an active risk vector. Because agents operate with real user permissions and non-deterministic behavior, security teams face a compounding set of enterprise challenges that extend far beyond simple prompt injections.

Employees are adopting personal AI agents and browser tools that bypass IT oversight, spreading shadow AI across endpoints. At the same time, attackers are exploiting connected systems to manipulate these agents. By poisoning the external data, databases, or SaaS applications an agent relies on, adversaries can alter its behavior indirectly without ever touching the AI model itself. Without hard boundaries, an agent can be tricked into escalating host privileges, bypassing local containers or executing arbitrary system commands. In short, the agent escapes its intended sandbox and becomes an unwitting insider threat.

AI Agents and Tools are on Nearly Every Endpoint

Adversaries are already exploiting this new vulnerability. In the ClawHavoc supply chain attack, adversaries targeted agents by uploading hundreds of malicious skills to OpenClaw's marketplace; once installed, these rogue skills broke runtime isolation to give remote attackers direct command-line access on the host. In a separate incident, Unit 42 research showed how agents can be tricked into revealing secret system prompts or sensitive information through indirect data poisoning from connected applications. Additionally, agents can bypass system and access controls when tricked into issuing unauthorized API calls or executing system tools under the guise of legitimate user permissions. Compounding these risks is the rise of shadow AI, as ungoverned, unmonitored agents deployed by employees silently inherit elevated system privileges without IT visibility.

When agentic AI was just emerging, we saw the potential risks it would bring and immediately sought out a solution to secure our internal AI workloads. Our InfoSec team found and deployed Koi while the startup was still in stealth mode. Impressed by Koi’s unique ability to secure new agentic endpoint behavior, we welcomed the talented Koi team into the Palo Alto Networks family to deliver this protection directly to our customers.

Cortex XDR One: Securing Every Endpoint and Agent from a Single Platform

XDR One integrates Cortex XDR and Cortex Agentic Endpoint Security with a single user interface and sensor, providing centralized visibility, management and investigation.

Agentic Endpoint Security for Complex Endpoint Ecosystems

From sanctioned agents to shadow AI, XDR One gives teams a real-time inventory of every AI artifact the moment it appears on an endpoint. Armed with visibility into all the agent activity in the enterprise, security teams can control what packages, extensions, agents and AI artifacts are allowed to be installed or used. For example, a CISO can evaluate which vibe coding agents are actually being used by engineering teams and make an informed decision about the productivity impact of removing access to a specific agent. 

Securing the modern endpoint requires unified defense across both the AI agent lifecycle and the underlying operating system. XDR One delivers this protection, from software installation to live execution. Within the agent layer, it enforces runtime guardrails to help stop prompt injections and destructive commands. Simultaneously at the OS layer, XDR One continuously monitors runtime process chains to block zero-day exploits and living-off-the-land attacks in real time without affecting performance. To complement these defenses, optimized small language models run directly on the endpoint sensor to guard against evasive, fileless threats even while offline and without sending sensitive code to the cloud. By stitching cross-domain telemetry into clear, end-to-end attack chains, XDR One cuts false positives by up to 95% and drives automated remediation in minutes.

Ultimately, consolidating this security telemetry onto a single sensor eliminates fragmented point tools and establishes a powerful operational foundation, equipping Cortex XSIAM with the critical data needed to better govern AI risk across the enterprise.

Flexible Protection with Standalone Agentic Endpoint Security or Native Integration

Cortex Agentic Endpoint Security (AES) specifically governs AI tools, MCP servers and agentic workflows running on those hosts. Organizations have the flexibility to deploy AES alongside existing third-party EDR environments using the Cortex targeted sensor.

However, organizations can simplify operations when AES and XDR come together natively in Cortex XDR One. By unifying agentic defense and extended detection and response into a single sensor and platform, XDR One bridges the gap between traditional host security and AI risks, delivering seamless visibility, management and real-time investigation.

Setting a New Baseline for Endpoint Security

The era of standalone EDR has passed. Just as XDR moved beyond siloed endpoint detection and response to encompass network, identity and cloud, securing the modern enterprise now demands native protection for autonomous AI workloads. EDR without integrated agentic security is incomplete and fundamentally legacy. Disconnected point solutions lack visibility into OS execution, while bolt-on EDR offerings fail to correlate the agent’s prompt and tool context with subsequent system behaviors. Relying on a bird of prey may seem like high-end security, until you discover it only swoops in after the wolf has already attacked the flock.

XDR One sets the new standard for endpoint security, providing unmatched visibility and preemptive control across both the OS and AI layers within a single sensor.

Scaling Enterprise AI with Confidence

While XDR One delivers complete standalone protection, security leaders grappling with this complex new attack surface can augment their team’s capabilities with Unit 42 MDR, which will now include Managed Agentic Endpoint Security. By combining XDR One telemetry with elite threat intelligence, Unit 42 experts deliver proactive threat hunting, incident investigation, and AI risk governance to strengthen overall resilience.

Securing the Agentic Frontier

As organizations race to adopt AI agents, security teams face a pivotal transition. The expansion of agentic capabilities across enterprise endpoints demands a security posture that treats agents with the same rigor and control as traditional system processes.

By unifying agentic endpoint defense and XDR into a single sensor and platform, XDR One sets a new standard for endpoint security in the agentic era. Whether deployed independently or backed by Unit 42 expertise, XDR One gives security leaders the visibility and control needed to eliminate shadow AI, enforce operational guardrails and accelerate their AI transformation.


Forward-Looking Statements
This blog contains forward-looking statements that involve risks, uncertainties and assumptions, including, without limitation, statements regarding the benefits, impact, or performance or potential benefits, impact or performance of our products and technologies or future products and technologies. Any unreleased services or features (and any services or features not generally available to customers) referenced in this or other press releases or public statements are not currently available (or are not yet generally available to customers) and may not be delivered when expected or at all. Customers who purchase Palo Alto Networks applications should make their purchase decisions based on services and features currently generally available.

The post Reinventing Endpoint Security with Cortex XDR One appeared first on Palo Alto Networks Blog.
Introducing Unit 42 Managed Agentic Endpoint Security

19 October 2026 at 14:59

AI agents and AI-enabled tools are fundamentally changing how work gets done. From coding assistants to Model Context Protocol (MCP) servers, autonomous tools now access sensitive data, execute commands, and modify local workflows directly from the endpoint. Traditional endpoint security models fail to offer the visibility or governance required to manage these autonomous actions.

The security gap is already significant. Only 6% of organizations have an advanced AI security strategy. And the fastest attacks can move from initial access to data exfiltration in just 72 minutes, according to the 2026 Unit 42 Global Incident Response Report. As AI adoption grows, teams need context to prioritize risk and experts ready to respond so the business can continue adopting AI with confidence.

Today, we are announcing Unit 42 Managed Agentic Endpoint Security (Managed AES). We built the service on Cortex AES, our AI-native endpoint security platform that provides visibility, contextual risk intelligence and protection for AI agents and artifacts. Managed AES adds 24/7 Unit 42 expertise to help organizations put those capabilities into action. Backed by Unit 42 threat intelligence, our experts provide AI governance, threat hunting, investigation and response, and AI-related cyber hygiene. They apply human judgment to turn contextual intelligence into policy recommendations and prioritized actions as the environment evolves.

Continuous Expert Defense for the AI Environment

Managed AES brings continuous Unit 42 expertise to four areas of AI endpoint security.

  • Govern AI Adoption with Greater Confidence
    AI adoption often moves faster than security teams can assess it. Our experts help identify AI tools and associated risks, evaluate exposure and recommend improvements to policies and controls. Security leaders gain a clearer view of AI use across their environment.
  • Hunt for Emerging and Zero-Day Threats
    AI-related threats can emerge before they trigger a known alert. Our threat hunters use frontline threat intelligence and Cortex AES signals to proactively hunt across the customer’s AI environment. They evaluate findings, recommend action and refine policies and correlation rules to strengthen protection over time.
  • Investigate and Respond 24/7
    Our analysts continuously monitor activity, investigate suspicious behavior and take permitted actions on the customer’s behalf to contain AI-related threats. Security teams gain specialized support to understand what happened, determine the potential impact and prioritize next steps.
  • Continuously Strengthen AI-Related Cyber Hygiene
    Unit 42 assesses the customer’s AI security posture as adoption evolves. AI Security Posture Reports identify policy and control improvements, while Threat Impact Reports detail threats, potential impact, response actions taken and recommended next steps. These insights help teams prioritize improvements.

Expert Protection Across Your AES Environment

Organizations can choose the Cortex AES deployment model that best fits their environment while receiving the same 24/7 Unit 42 expertise.

  • Managed AES with Standalone Cortex AES
    Organizations can deploy Cortex AES alongside their existing endpoint security solution for AI-native visibility, contextual risk intelligence, governance and protection for AI agents and AI-enabled tools. Managed AES adds Unit 42 experts who help customers act on that visibility and risk intelligence.
  • Managed AES with Cortex XDR One
    Cortex XDR One brings together Cortex AES and Cortex XDR into a single sensor and console experience. It combines endpoint detection and response with AI-native security for AI agents and artifacts. Unit 42 experts provide 24/7 governance, threat hunting, investigation and response across the entire endpoint attack surface.

Securely Scale AI Adoption

Unit 42 Managed AES helps security teams understand how AI is being used, address risk before it escalates and respond quickly when threats emerge. By combining Cortex AES context with frontline threat intelligence and expert analysis, Managed AES helps businesses adopt AI with confidence.

Register for our upcoming webinar, The Next Era of Endpoint Security, to learn how Cortex AES and Unit 42 experts help your team govern AI risks, strengthen visibility and protect the agentic endpoint.

The post Introducing Unit 42 Managed Agentic Endpoint Security appeared first on Palo Alto Networks Blog.
Fast-Track Your PQC Strategy: A Template for OMB M-26-15 Readiness

16 October 2026 at 19:28

Your Template for OMB M-26-15 Migration

The transition to Post-Quantum Cryptography (PQC) is not just a technical upgrade; it is a vital national security imperative that represents the most significant cryptographic reset in the history of the Federal Government. Driven by Executive Order 14412 and Office of Management and Budget (OMB) M-26-15, Federal Civilian Executive Branch (FCEB) agencies face a strict October 22, 2026 deadline to submit comprehensive PQC Migration Plans to OMB and the Office of the National Cyber Director (ONCD).

To take the heavy lifting off agency leaders facing this tight 120-day window, we developed a ready-to-use Template for OMB M-26-15 Readiness and OMB M-26-15 PQC Migration Plan Instructions. Precision-engineered to align directly with the White House mandates, this template serves as a "fast-track" for federal teams. Instead of spending limited cycles building complex compliance documentation from scratch, security leaders can leverage this template to rapidly map their transition pathways and shift their focus to active discovery and remediation.

Per M-26-15, each agency’s migration plan must contain, at a minimum, nine core elements, all of which are featured in the PQC Migration Plan Template:

  • System prioritization strategy with risk-based justification.
  • Timelines and milestones to achieve the first three migration phases.
  • TLS 1.3 support milestones for the January 2, 2030, deadline.
  • Methodologies and automated tools for cryptographic inventory.
  • Cryptographic agile architecture implementation plan.
  • Third-party coordination plan.
  • Estimate of funding and personnel resources.
  • Risk management strategy for the migration period.
  • Governance roles and responsibilities definition.

Agencies must specifically prioritize high impact systems, High Value Assets (HVAs), and any systems vulnerable to cryptographically relevant quantum computer (CRQC) based attacks. This includes logical access control systems based in asymmetric encryption (such as PKI) and any data expected to remain mission-sensitive through 2030.

For most agencies, the core challenge of a migration plan is uncovering "cryptographic debt,” the years of hidden, legacy encryption buried in fractured IT systems. Because this debt creates unseen risks, establishing cryptographic visibility is the primary enabler for success. Once you can see your entire environment, the path to a quantum-safe future becomes clear and manageable.

A successful migration plan depends on an agency's ability to move quickly and accurately, requiring a fundamental shift in security architecture that prioritizes active discovery over passive lists. By deploying a structured and automated methodology, agencies gain the real-time visibility necessary to:

  1. Discover their full cryptographic footprint with total clarity.
  2. Protect critical assets against immediate and emerging threats.
  3. Accelerate the rollout of quantum-safe resilience across the enterprise.

To maximize your team’s resources, our OMB M-26-15 PQC Migration Plan Instructions and Template for OMB M-26-15 Readiness are a practical "fast-track" for building a compliant transition plan. This template provides a clear implementation methodology and a detailed checklist to ensure all required elements are addressed.


I. Policy Foundation

The federal mandate is driven by two specific directives that agencies must operationalize:

  • Executive Order 14412: Accelerates the Federal Government's transition to post-quantum cryptography to mitigate emerging quantum computing threats.
  • OMB Memorandum M-26-15: Directs each agency to prioritize critical information technology for migration and develop a plan that integrates PQC readiness into existing governance structures.

While this specific policy targets federal agencies, the global trend is clear: critical infrastructure operators and private sector entities should view this mandate as a strategic blueprint.

II. Compliance Timeline & Milestones

M-26-15 establishes a multi-phased timeline for agency compliance. While initial efforts focus on prioritizing HVAs and high-impact systems to mitigate immediate risk, agencies are expected to complete migration across remaining systems by 2035.

Deadline Policy Requirement & Milestone
July 22, 2026 PQC Migration Lead Designation: Agencies must formally identify a PQC migration lead.
Oct 22, 2026 Submittal of PQC Migration Plan: Deadline for agencies to deliver a dynamic migration roadmap to OMB and ONCD.
Jan 2, 2030 TLS 1.3 Implementation: Agencies must support TLS 1.3 (or a successor version) to enable the extensible handshake needed for hybrid-PQC key exchange models.
Dec 31, 2030 Key Establishment Deadline: Agencies must transition all HVAs and high impact systems to PQC (FIPS 203 ML-KEM) for key establishment.
Dec 31, 2031 Digital Signature Deadline: Transition all HVAs and high impact systems to PQC for digital signatures using FIPS 204 (ML-DSA) or FIPS 205 (SLH-DSA).

III. Mandatory Elements of the PQC Migration Plan

Agency heads must ensure that their submitted plans address the following nine core elements:

  1. System Prioritization Strategy: Risk-based justification addressing HVAs and PKI-based logical access control systems.
  2. Timelines and Milestones: Phased migration plans within the initial planning horizon.
  3. TLS 1.3 Support Milestones: Testing and deployment timelines for the 2030 deadline.
  4. Methodologies and Automated Tools: Documentation of tools used for cryptographic inventory.
  5. Cryptographic Agile Architecture: Strategy for algorithm rotation via configuration rather than code.
  6. Third-Party Coordination Plan: Delineating the Shared Responsibility Model with cloud providers.
  7. Resource & Personnel Allocation: Estimates for annual budget requests.
  8. Risk Management Strategy: Specific to the migration period itself.
  9. Governance Roles and Responsibilities: Defining implementation and risk acceptance accountability.

IV. Strategic Phasing: Multi-Year Transformation

  • Discovery & Strategy (2026-2027): Inventory, assessment, and governance framework setup.
  • Piloting (2027-2028): Early migration of prioritized systems.
  • Prioritized Key Migration (2028-2030): HVAs and systems vulnerable to CRQC-based attacks.
  • Signature Migration (2031): Digital signature protocols for prioritized systems.
  • Full Enterprise Migration (2035): Completion for all remaining systems.

V. Operationalizing the Transition with QSS

Quantum-Safe Security (QSS), a FedRAMP Moderate authorized tool, helps agencies move from box-checking to real operational resilience.

Strategic alignment with M-26-15:

  • Automated Discovery and CBOM Generation: Real-time visibility and generation of Cryptographic Bills of Materials (CBOM) to identify hidden dependencies.
  • FedRAMP Authorized: Accelerates adoption by removing the need for a separate agency-level ATO for the discovery tool.
  • Validation of Cryptographic Agility: Ensures systems can rotate to NIST standards (ML-KEM, ML-DSA) without hard-coded updates.
  • Integration with Zero Trust: Secures the cryptographic roots of device attestation and inter-service communication.

VI. Conclusion

The transition to quantum-safe cryptography demands immediate leadership. Agencies cannot afford to delay while adversaries continue to archive sensitive data.

Don't start from scratch, fast-track your PQC strategy!

The post Fast-Track Your PQC Strategy: A Template for OMB M-26-15 Readiness appeared first on Palo Alto Networks Blog.
The Blind Spot in Orbit: Why Space Could Be the Next Infrastructure Crisis

14 October 2026 at 10:29

Are organisations becoming so reliant on third party space assets that they would face severe disruption if the assets were impacted by a cyber attack?

When most people think of space technology, they imagine routine weather forecasts or blue-dot navigation on a smartphone map. But behind those quiet satellite signals lies an invisible digital thread holding modern society together. From crop harvesting schedules to international flight routes and supermarket supply chains, daily life on Earth is deeply dependent on data from space.

Yet space security remains the cyber risk that very few in executive boardrooms are addressing. As the space economy surges toward a $1.01 trillion valuation by 2034, a dangerous blind spot has emerged. Cyber threats to orbital infrastructure are no longer a theoretical hazard—they are happening now.

Privatization Outpacing Security

Historically, space operations were the exclusive domain of governments operating in strictly air-gapped environments with near-zero tolerance for risk. Today, rapid commercial privatization has slashed launch costs, but speed to market is dangerously outstripping security by design. Commercial operators inherit standard enterprise IT vulnerabilities, complex supply chain risks, unpatched APIs, and operational technology gaps.

The systemic disconnect is stark:

Physical Consequences on the Ground

Unlike typical corporate breaches, orbital cyber attacks can trigger immediate physical impacts on Earth. Tampering with satellite telemetry can destabilize regional crop yields by altering planting schedules or paralyze commercial aviation by injecting false data into flight-navigation networks.

Crucially, these risks are not limited to assets in orbit. Ground-based power substations, telemetry command hubs, and downlink facility infrastructure have become primary cyber-physical targets. A coordinated cyber attack on local energy substations supporting satellite ground operations could sever communication links and ground control just as effectively as an in-orbit compromise.

A study commissioned by the European Space Agency (ESA) modeled the impact of a hypothetical 7-day satellite communications outage across ESA member states and Canada. The potential cost reaches up to €20 billion ($21.8 billion) in total economic losses. This includes €19 billion in maritime logistics and port bottlenecks, €558 million in direct aviation losses (canceling ~4,000 transatlantic flights), €352 million in lost connectivity for emergency services and remote communities, and €89.8 million from stalled offshore energy operations.

Aging Tech Meets Advanced Threat Actors

Geostationary satellites carry mission lifespans of 10 to 15 years, locking critical communications into legacy hardware designed before modern cyber threats existed. Nation-states and cybercriminals are exploiting these gaps; Palo Alto Networks Unit 42 threat intelligence currently tracks multiple state-sponsored groups actively targeting space-sector systems.

What Leaders Must Do Now

Governments and enterprise boards must recognize space-based timing, navigation, and observation as core national critical infrastructure. Leadership teams should execute four priorities immediately:

  1. Map Space Dependencies: Audit third-party services, cloud links, and automated logistics relying on satellite telemetry.
  2. Establish Terrestrial Backups: Build manual redundancies—including ground-based radio networks and offline inventory controls—for scenario planning when space signals go dark.
  3. Elevate Supply Chain Audits: Evaluate whether key vendors rely on single-point-of-failure commercial satellite constellations or unfortified ground substations.
  4. Update Risk Registers: Formally integrate space dependencies into corporate cyber risk registers.

Translating these action items into real-world operational resilience requires moving beyond static compliance policies. To protect complex ecosystems—where ground stations, power substations, cloud environments, and orbital data streams converge—organizations need a unified, platformized approach to security that provides continuous visibility across every link in the space supply chain.

In the modern threat landscape, business resilience, national sovereignty, and space security are inseparable. It is time for leaders to look up before an orbital breach brings ground operations to a standstill.

The post The Blind Spot in Orbit: Why Space Could Be the Next Infrastructure Crisis appeared first on Palo Alto Networks Blog.

NHS England evolves its cybersecurity strategy with Palo Alto Networks and IBM

13 October 2026 at 10:29

The NHS has set an ambitious goal of achieving cyber resilience across healthcare organisations by 2030. Delivering on that vision requires technology, expertise and close collaboration across the public and private sectors.

This is clearly a highly complex task, but one we're delighted to help deliver in partnership with IBM. Through this partnership, Palo Alto Networks will provide advanced cloud-based perimeter technology, alongside IBM Consulting’s specialist guidance, implementation support and tailored onboarding for NHS organisations.

As health and care services continue to modernise, maintaining resilient, secure digital infrastructure has never been more important. Healthcare organisations are operating in an increasingly complex environment, with growing digital dependencies, expanding supply chains, evolving cyber threats and new technologies such as AI reshaping the landscape.

According to IBM's Cost of a Data Breach Report, healthcare continues to be one of the most impacted sectors globally when it comes to the financial consequences of cyber incidents. This highlights the importance of taking a proactive, long-term approach to cyber resilience across critical public services.

Palo Alto Networks' continued work with the NHS demonstrates the scale and complexity of securing modern healthcare environments. As organisations balance innovation, operational demands and evolving security requirements, there is a growing need for solutions that provide both strong protection and the flexibility to meet local needs.

Introducing the Next Generation of the NHS Secure Boundary Programme

Palo Alto Networks will deliver next-generation, cloud-based security solutions through the next iteration of the NHS Secure Boundary programme. The service has been designed to help strengthen cyber resilience across UK health and social care organisations while supporting the safe and reliable delivery of services.

Secure Boundary provides the capability to support a network spanning more than 1.5 million NHS staff, over 200 NHS trusts, more than 55,000 organisations handling health data and approximately 2 million devices under national cyber monitoring. The nationally integrated and centrally funded service embodies a "Defend as One" approach, helping organisations benefit from shared protection while retaining local control.

Secure Boundary supports NHS organisations through:

  • An AI-enabled cybersecurity capability designed to strengthen resilience and support the safe, reliable delivery of healthcare services.
  • Enhanced visibility and protection for internet traffic across the Health and Social Care Network.
  • Improved security for infrastructure and clinical applications operating across multiple service providers.
  • Increased protection for information shared across NHS organisations and trusted third parties.
  • Greater privacy and security for staff accessing web-based services, whether on-site or remotely.
  • A "Defend as One" approach that complements existing local security measures while allowing organisations to tailor policies to their specific requirements.
  • Reduced complexity through the consolidation of security tools and management processes.
  • Improved efficiency through a centrally funded model that helps reduce duplication of technology and investment.

The new Secure Boundary service represents a significant step forward in strengthening the NHS's digital resilience. By providing a more secure foundation for NHS services, it helps support operational continuity, safeguard sensitive information and enable healthcare teams to continue delivering high-quality care in communities across the UK for years to come.

If you would like to find out more about Secure Boundary and how it can help your organisation, please contact ukpubsec@paloaltonetworks.com. 


Forward-Looking Statements

This blog contains forward-looking statements that involve risks, uncertainties and assumptions, including, without limitation, statements regarding the benefits, impact, or performance or potential benefits, impact or performance of our products and technologies or future products and technologies. These forward-looking statements are not guarantees of future performance, and there are a significant number of factors that could cause actual results to differ materially from statements made in this blog. We identify certain important risks and uncertainties that could affect our results and performance in our most recent Annual Report on Form 10-K, our most recent Quarterly Report on Form 10-Q, and our other filings with the U.S. Securities and Exchange Commission from time-to-time, each of which are available on our website at investors.paloaltonetworks.com and on the SEC's website at www.sec.gov.  All forward-looking statements in this blog are based on information available to us as of the date hereof, and we do not assume any obligation to update the forward-looking statements provided to reflect events that occur or circumstances that exist after the date on which they were made.  


The post NHS England evolves its cybersecurity strategy with Palo Alto Networks and IBM appeared first on Palo Alto Networks Blog.

The Mango Strategy: A CEO’s Guide to AI Cybersecurity

8 October 2026 at 23:30

Hope is not a strategy. Neither is nostalgia.

Mark Carney, Prime Minister of Canada


Business leaders cannot respond to AI-era cyber risk by longing for a simpler technology stack, slower decision-making or a security model built around a trusted internal network. AI is changing how organisations operate—and how adversaries identify and exploit weaknesses—faster than many leadership teams can anticipate.

Cybersecurity has therefore evolved from a “coconut strategy”, built around a hardened perimeter and trusted interior, to what I call a “mango strategy”. The modern enterprise and its digitally connected ecosystem have a porous, continuously changing edge, but it must place its strongest protection around the core: its data, identities, code repositories, applications, digital essentials and critical operations.

What is the CEO’s role in AI governance and cybersecurity?

This shift makes cybersecurity a CEO-level business priority. CEOs do not need to oversee every AI deployment, but they must define how the organisation adopts, governs and secures AI while maintaining resilience, accountability and trust. That means setting risk thresholds, assigning accountability, protecting critical data and identities, and ensuring that security can operate at the same machine-speed as autonomous systems.

Why autonomous AI agents require workforce-level oversight

Given this dual nature, business leaders cannot afford to ignore AI. Like water, AI adoption will find its way and follow the path of least resistance as a senior cybersecurity leader from a large European bank put it. Without clear governance, it can expose weak controls, while AI-enabled attackers can exploit those weaknesses at unprecedented speed and scale.

Some have suggested that CEOs should double as Chief AI Officers. However, as executive responsibilities expand, expecting a CEO to oversee day-to-day AI implementations while setting broader corporate vision is unrealistic. While the CEO may not manage specific AI initiatives, they must actively shape the overarching strategy, the “AI surround and framework”.

This leadership starts with developing and hiring highly capable talent to execute the vision. The CEO’s true value lies in ensuring that AI is embraced across every business unit, integrated into risk models, and governed by robust safeguards. Proper administration and oversight are no longer secondary concerns—they are core executive functions.

A critical dimension of this responsibility is governing the use of agentic AI. Autonomous agents function effectively as "authorized insiders." Custom-built for specific workflows, they leverage elevated privileges to access critical applications, databases, and proprietary tools around the clock.

In practice, these agents represent a new class of virtual employees. Though non-human, their operational impact is comparable to their human counterparts, yet they operate 24/7. CEOs must ensure that autonomous agents are deployed, monitored, and evaluated with the same rigors applied to the rest of the workforce.

How can leaders build resilience against AI-driven instability?

Translating this new operational reality into steady organizational resilience requires recognizing AI's broader societal impact. While the technology holds vast potential for good, it can also accelerate systemic and geopolitical instability when misused. For instance, recent developments in frontier AI models demonstrating advanced exploit-generation capabilities highlight the immediate necessity of defense-in-depth.

Palo Alto Networks CEO Nikesh Arora highlighted this shift in this article - Weaponised Intelligence -  “These are not incremental improvements. Imagine a horde of agents methodically cataloging every weakness in your technology infrastructure, constantly. Over the next six months, the barrier to entry for sophisticated attacks will continue to diminish. A hacker’s dream weapon will be available to anyone with a credit card and computer.”

To counter these emerging risks, leading AI developers and security organizations are actively collaborating. Through initiatives like Project Glasswing, partners across technology and financial services are stress-testing defender-grade models to harden critical software and establish proactive defenses before threats reach the wild.

These collaborative initiatives address the exact questions executive boards are asking today: Where are our exposure points, how severe are they, and how quickly can we contain them?

Answering these questions requires a strong security culture. Defining how an organization adopts and governs AI is now a core mandate for executive leadership. Even with specialized AI leadership in place, the CEO must drive the culture to align AI implementation with business values and strategic priorities.

Ultimately, executive leadership must set clear parameters: defining operational boundaries, establishing accountability, tracking key progress metrics, and encouraging responsible innovation within controlled risk thresholds.

Four cybersecurity priorities for the agentic AI era

The cybersecurity landscape has reached an inescapable inflection point: we have entered the "Agentic Era," where autonomous AI agents drive attacks at machine speed. In this environment, manual, reactive patching is no longer just slow—it is a mathematical dead end that can leave enterprises effectively unprotected.

Navigating this shift requires a deliberate transition from reactive measures to proactive architecture built on four strategic pillars:

  1. Fight Machine with real-time machine speed: Because automated adversaries can scan millions of endpoints and chain multiple low-severity vulnerabilities into catastrophic exploit paths, human-led response is a guaranteed failure. Organizations must move to a prevention-first posture, using AI-driven systems that natively integrate across network, cloud, and endpoint telemetry to block threats in real-time.
  2. The "Customer Zero" Mandate: The time between a model's release and its weaponization is shrinking to zero. Palo Alto Networks acts as "Customer Zero" by stress-testing frontier models during their development phase, hardening the security stack against specific autonomous logic capabilities well before they are public.
  3. Move Beyond "Find-and-Fix": Finding vulnerabilities is only half the battle. The new imperative is to prioritize remediation based on exploitability and reachability—identifying which vulnerabilities can be chained together by an attacker—rather than just severity. This requires shifting operations to machine-speed defense via unified platforms and services like Unit 42 Frontier AI Defense or virtual patching, allowing you to safely patch your digital essentials when real-time agentic attacks are happening.
  4. Prioritize Platformization: Fragmented security architectures—where point solutions cannot communicate—are an open invitation to automated lateral movement. A unified, data-driven architecture is a prerequisite for security, enabling a threat blocked at the endpoint to harden an organization’s perimeter.

How CEOs can create the defender’s advantage

For the C-suite, the takeaway is clear: Digital transformation and cybersecurity transformation are now inextricably linked. The organizations that adapt by rebuilding their architecture around unified data and autonomous prevention will hold the "defender's advantage," while those relying on legacy, manual workflows remain exposed to a rapidly accelerating threat landscape.

Nostalgia offers no protection against the speed and complexity of the modern threat landscape. Operating under the assumption that perimeters remain secure is a legacy mindset. 

As executive leaders refine their strategy for the AI era, two core principles should guide their approach:

  • Cybersecurity is a data issue, not a technology issue. The goal is to protect data, not just to harden infrastructure.
  • Many of our core best practices in cybersecurity, such as Zero Trust and modular platformization, are more appropriate than ever in the era of AI and automated agents. 

Helmut Reisinger is CEO for Europe, Middle East and Africa at Palo Alto Networks.

The post The Mango Strategy: A CEO’s Guide to AI Cybersecurity appeared first on Palo Alto Networks Blog.

❌