❌

Normal view

Received — 3 October 2026 ⏭ Palo Alto Networks Blog

“SASE Gateway” provided by KDDI : How SP Interconnect Simplifies Closed Network Zero Trust

30 September 2026 at 04:12

We are thrilled to announce that KDDI Corporation, a long-standing NextWave partner of Palo Alto Networks and a Managed Security Service Provider (MSSP) with whom we have built a strong partnership, has launched an innovative new service, "SASE Gateway powered by Palo Alto Networks," equipped with our latest "SP Interconnect (SPI)" architecture. 

As the implementation of AI in business operations and the shift to the cloud accelerate, and enterprise data becomes more distributed than ever, cyberattacks are also leveraging AI to become more advanced and sophisticated. In such an environment, enterprise security must completely transition from traditional perimeter defense to a Zero Trust architecture that continuously verifies all traffic. Our Prisma SASE is the industry's premier platform built to defend, scale, and secure your enterprise at the speed of AI. Powered by Precision AI®, it enforces dynamic Zero Trust guardrails to proactively defend against frontier AI attacks and secures the adoption of GenAI and autonomous agents across the enterprise.

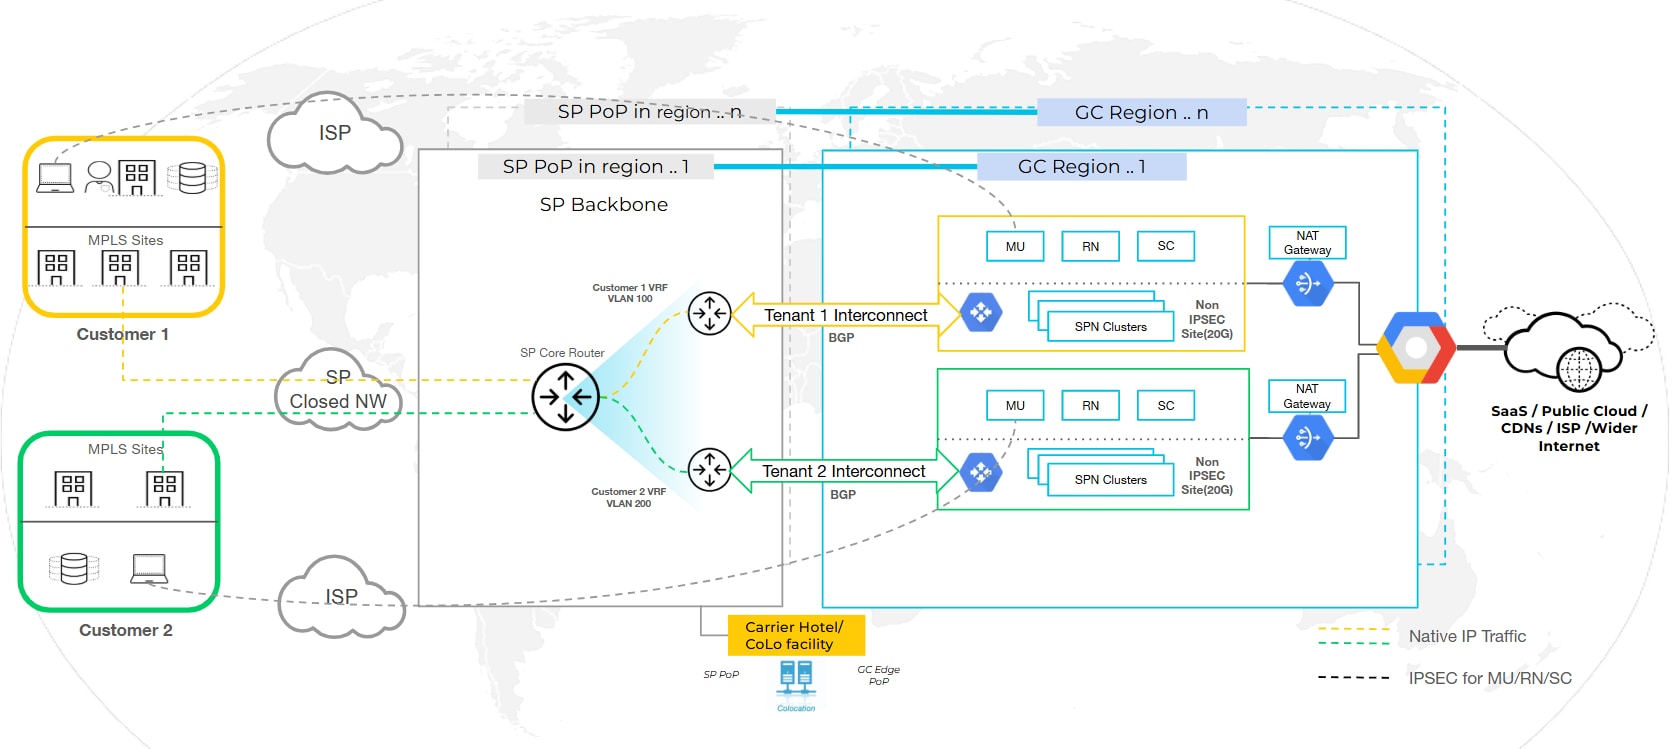
The "SP Interconnect (SPI)" adopted by KDDI this time is a next-generation architecture that directly interconnects telecommunications carriers' high-quality networks with our Prisma SASE. This integration makes it possible to directly connect traffic from closed networks (KDDI Wide Area Virtual Switch 2: WVS2)—which remain highly demanded among Japanese enterprises—to SASE, in addition to internet connections. In particular, the latest SPI achieves the flexibility and performance required to meet the strict requirements of the Japanese market, including the elimination of IPsec connection overhead . As a result, an ideal infrastructure foundation has been completed that uncompromisingly balances the communication quality of the carrier backbone and the latest security of Palo Alto Networks, allowing unified management under a single policy engine.

Executive Perspective: KDDI Leadership on Next-Gen Security

Regarding this release, Junji Hori, General Manager of Product Management at KDDI Corporation, stated:


"With the launch of Prisma SASE with SP Interconnect, the convergence of closed networks and the internet has accelerated. This service serves as the core first-phase solution in the Security-as-a-Service domain under KDDI’s 'AccelWaves Vision,' and we position it as a major milestone toward realizing 'KDDI AccelWaves Network,' an autonomous network service for enterprises scheduled for release in 2028.

By simply unifying the individual design and management of security across both closed networks and the internet, this newly announced service reduces the operational burden on security and networking while contributing to rapid response in the event of an incident. This is an advanced initiative made possible by combining the long-standing partnership and expertise cultivated between both companies.

Equipped with AI security capabilities, we are confident this service will deliver new value not only to existing WVS2 customers, but also to customers aiming to centralize security operations and optimize their networks.

KDDI will continue to further strengthen its partnership with Palo Alto Networks and strive to deliver innovative services that accelerate our customers' AI implementation."
 

Key Architectural Advantages of SP Interconnect 

The SP Interconnect that underpins the "SASE Gateway" offers the following outstanding benefits to customers: 

  • Direct Connection to KDDI's Closed Network and Ensuring Reliability: Achieves a low-latency and stable communication environment through the high SLA and cloud scale of Prisma SASE, and closed connection with KDDI's high-quality, wide-band backbone.
  • Realization of Comprehensive ZTNA: Consistently applies best-in-class Zero Trust security to access SaaS and private applications, regardless of the line type (closed network, Internet, etc.).
  • Securing the AI-Driven Enterprise: By routing high-speed closed network traffic through Prisma SASE, organizations can safely adopt GenAI and agentic AI tools. SP Interconnect enables  this traffic to benefit from machine-speed inline inspection, stopping automated, frontier AI attacks (like machine-scale vulnerability scanning and prompt injections) while enforcing complete visibility, identity control, and advanced data loss prevention (DLP).
  • Proactive IT Operations Powered by AI: Accelerate time-to-value by transforming reactive IT support into proactive, self-healing operations. It leverages AIOps and ADEM (Autonomous Digital Experience Management) to comprehensively visualize and manage transport networks across branches, clouds, and data centers, predicting and resolving network issues before users even notice them.
Figure: Interconnection with KDDI Backbone via the Latest SP Interconnect

Furthermore, to realize a platform-based approach to security, KDDI offers the "SASE Gateway" service alongside the extensibility to introduce advanced security solutions such as our "Cortex XDR" and "Prisma Browser" (a secure enterprise browser). Additionally, to provide end-to-end support for customers' security operations and management, this offering can be combined with SOC and IR (Incident Response) services provided by LAC Co., Ltd. 

Palo Alto Networks is confident that this "SASE Gateway" will become an essential business foundation supporting secure DX (Digital Transformation) for many Japanese enterprises advancing AI adoption, hybrid work and cloud migration. Through our strong alliance with KDDI, we look forward to further deepening our technical collaboration and greatly expect them to powerfully lead the expansion of sales and adoption among enterprise companies as a strong core solution for KDDI's "AccelWaves Vision".

KDDI’s SASE Gateway with Palo Alto Networks is now available as part of the companies’ joint integrated security portfolio.

Modernize Your Closed Network Security Today

Ready to simplify your hybrid network management and protect your organization against AI-driven threats? Contact us to schedule a custom architecture review or explore how KDDI SASE Gateway can fit into your cloud strategy.

The post “SASE Gateway” provided by KDDI : How SP Interconnect Simplifies Closed Network Zero Trust appeared first on Palo Alto Networks Blog.
Received — 3 August 2026 ⏭ Palo Alto Networks Blog

Palo Alto Networks and AT&T - Delivering Quantum-Resilient SASE Fabric

16 July 2026 at 16:00

By Yogesh Ranade from Palo Alto Networks, and Senthil Ramakrishnan from AT&T

The digital world is currently navigating a dual-speed revolution. Acceleration of AI and hyperconnectivity is unlocking unprecedented economic value. The silent but rapid progress of quantum computing is fundamentally threatening the cryptographic foundation upon which that value is built.

As leaders in global networking and cybersecurity, Palo Alto Networks and AT&T Business launched Secure Connectivity solutions for Business Customers. We recognize that quantum-readiness is no longer a distant milestone; it is now a strategic imperative. With threatening data longevity and Trust Now, Forge Later targeting digital identities, the risks are already looming. 

By integrating Prisma SD-WAN’s cryptographic innovation with AT&T’s global network, Palo Alto Networks and AT&T Business are proud to deliver the Quantum-Resilient SASE Fabric.

The Quantum Shift Towards Building Resilience for Tomorrow’s Reality

For over 30 years, the difficulty of mathematics has been our primary defense. Classical algorithms, like RSA and Diffie-Hellman, provided the shield for our global economy because they were computationally impossible for classical machines to solve. However, quantum computing fundamentally changes this landscape by providing an exponential speed-up. By leveraging Shor’s Algorithm, quantum computers can break these classical cryptographic foundations, turning a decryption process that would take a classic supercomputer millennia into a task of mere hours.

Neutralizing the Quantum Crisis

Palo Alto Networks is embedding Post-Quantum Cryptography (PQC) as a native pillar of the Prisma SASE fabric. We are moving beyond the forklift-upgrade model to a software-defined, standards-based foundation, which is built on strict separation of management and data plane components:

  • Universal Control Plane Hardening (TLS 1.3): We have transitioned all control plane traffic to TLS 1.3 (Transport Layer Security 1.3), the global gold standard for Internet encryption. This secures the "brain" of the network (where routing configurations and security policies are managed), making it immune to quantum-enabled impersonation and credential theft.
  • PQC-Hardened Data Plane (IETF Standards): We are operationalizing PQC across the entire fabric by adopting official standards published by the Internet Engineering Task Force (IETF), specifically RFC 9370, 9242, and 8784. In plain terms, these standards allow us to use "hybrid key exchanges." This means we wrap your data in two layers of protection at once: a classical mathematical shield for immediate compatibility, and a quantum-resistant shield to protect against future decryption threats, all without causing packet fragmentation or network slowdowns.
  • Logs and Telemetry Plane: All network telemetry and metadata (the automated operational logs and traffic pattern data generated by the network, rather than the actual content of your business files) are encrypted in transit via TLS 1.3. This architecture guarantees that even this secondary network metadata is geofenced to your chosen region with no cross-region aggregation, satisfying the most stringent data residency mandates.
  • Crypto-Agility as a Standard: "Crypto-agility" is natively built into our systems, which means the software is designed to adopt new mathematical algorithms. As the National Institute of Standards and Technology (NIST) refines its guidelines, our systems can be upgraded seamlessly via simple, automated cloud updates without requiring expensive hardware replacements to ensure our customers’ security posture.
  • Secure Boot Support: Palo Alto Networks Prisma SD-WAN ION hardware supports Secure Boot to ensure that only cryptographically signed bootloaders, kernels, and trusted applications are executed during the boot process. This establishes a chain of trust from the BIOS firmware to the operating system, preventing the execution of unauthorized or tampered software. ION hardware appliances ship with an integrated, dedicated Trusted Platform Module (TPM), which provides hardware-level root-of-trust by securely storing cryptographic keys, certificates, and sensitive data to prevent unauthorized physical tampering and ensure secure device authentication. The OS/software layers use PQC algorithms to negotiate and secure the management, control plane and data plane tunnels. This ensures quantum readiness without requiring an immediate, widespread rip-and-replace of physical branch hardware.

The AT&T Perspective Views Security at Global Scale

From the perspective of a global leader like AT&T, PQC is an operational mandate. Providing connectivity to the world’s most regulated industries means that security cannot be bolted on. Security must be an inherent property of the transport layer and the connectivity infrastructure itself.

Turning Complexity into a Strategic Advantage

Managing a global footprint that spans across 5G, fiber, and legacy underlays requires an institutional expertise that few can match. For AT&T, the move to a more secure quantum-ready fabric with Dynamic Defense is about providing security where it matters most: the network. Our customers shouldn't have to worry about whether their data is traveling over an MPLS circuit or the public internet.

Through this collaboration, AT&T expands the delivery of Dynamic Defense:

  • Cross-Underlay Consistency: We enable PQC protection to be applied uniformly across all transport mediums, eliminating the "weak links" that often exist in hybrid environments where data moves between private and public circuits.
  • Automated PQC Policy Orchestration: New branch locations are seamlessly integrated into the quantum-ready fabric through automated policy distribution. The moment a device is activated via zero touch provisioning, the branch is enabled to be protected against HNDL threats from the first packet without requiring manual site-by-site intervention.
  • Compliance: With mandates like NIS2/DORA in Europe and NORA/CNSA 2.0 in the U.S., our clients face a closing window for compliance. AT&T provides the verifiable chain of trust required to prove "Quantum Readiness" across the entire circuit path, ensuring your fabric is audit-ready and compliant with global standards.

The Power of the Post-Quantum Secure Fabric

The true value of this relationship lies in the synergy between the network and the security stack. By combining our strengths, we have built a solution that is significantly more resilient than the sum of its parts.

The SPI Advantage Is Performance Without Compromise

Through Service Provider Interconnect (SPI), Palo Alto Networks' security platforms natively integrate with AT&T’s private network core to deliver a seamless quantum-safe on-ramp. This means business traffic can connect directly to a secure AT&T network without having to build slow, complex software tunnels over the public internet, preserving high performance while delivering next-generation encryption. Historically, high-level encryption meant a "performance tax" on latency and throughput. Our combined architecture allows quantum-safe traffic to flow over AT&T’s network backbone, enabling organizations to modernize their security without sacrificing the user experience.

Securing the Decentralized Perimeter (The Branch as the Edge)

In today’s highly distributed business landscape, the traditional corporate "headquarters" is no longer the center of gravity. The network perimeter has shifted to the branch (decentralized edge locations like retail storefronts, remote clinics, regional bank offices, and warehouse hubs) and the individual 5G-connected devices employees use. Securing these remote, local edge points is critical because they represent the primary gateway where sensitive company data first enters the network. 

By utilizing AT&T’s leadership in WAN, 5G and cellular technologies, we leverage Hybrid Public Key Infrastructure (PKI) to secure these edge locations. Hybrid PKI is a digital identity framework that issues dual security credentials to every device: one "classical" identity to ensure compatibility with existing networks today, and one "quantum-resistant" identity. This double-verification guarantees that a cellular-connected remote branch or a mobile site is just as immune to quantum decryption or identity spoofing as a fortified corporate data center.

The Path Forward Is a Vision for Long-Term Trust

The transition to a quantum-ready future is a marathon, not a sprint, and the first steps must be taken now. Palo Alto Networks and AT&T Business are offering a clear, practical path to quantum resilience.

We are delivering more than a simple software update as we prepare customers for the next generation of digital commerce. Together, we are designing our network to help ensure the data of today remains protected against the threats of tomorrow, securing the digital integrity of every enterprise we serve.

As we redefine the boundaries of security in connectivity, we invite you to join us in helping secure your organization’s digital future. Contact your or Palo Alto Networks account representative today to begin a strategic Quantum-Readiness Assessment and experience the power of the Quantum-Resilient SASE Fabric.

The post Palo Alto Networks and AT&T - Delivering Quantum-Resilient SASE Fabric appeared first on Palo Alto Networks Blog.

Received — 12 March 2026 ⏭ Palo Alto Networks Blog

A Joint Vision for Simplified SASE Management at Scale

Palo Alto Networks, ServiceNow, and Bell Canada have come together in a strategic collaboration to build an innovative ServiceNow application that creates an automated bridge between world-class security operations and industry-leading service management.

Large enterprises need robust security at cloud speed, but operational complexity keeps getting in the way. ​​Here’s what that looks like in practice:

  • Operations teams juggle multiple dashboards. When an issue surfaces, they are bouncing between the Prisma® SASE (secure access service edge) console to identify the incident, ServiceNow to log the case, and a customer support portal to escalate the issue. Every handoff inflates MTTR (mean time to resolution) and introduces room for error.
  • Customers are stuck in a deployment purgatory. Manual infrastructure configuration, connector setup, and mobile user onboarding can stretch on for weeks or months. Every day spent wrestling with configuration files is a day that value isn’t delivered.
  • Multi-tenant management doesn’t scale. If operational overhead grows linearly with each new tenant, the business model ultimately caps itself.

Bell Canada, through its innovative and security-first approach in the Canadian market, is a lighthouse partner that helped pioneer this innovation through its deep engagement with ServiceNow and a strategic partnership with Palo Alto Networks. With a strong focus on delivering exceptional customer value, Bell helped drive the vision for a simplified, scalable approach to SASE management.

Driven by their commitment to service excellence and customer outcomes, Bell worked closely with Palo Alto Networks and ServiceNow on this solution, accelerating customer time to value and simplifying operational complexity. Bell was among the first to champion this vision, acting as a market thought leader and helping shape a new standard for integrated SASE and service management outcomes in Canada.

Large Enterprises and Managed Service Providers can accelerate time to value by automating the entire lifecycle of Prisma SASE, from deployment to ongoing incident response through a newly launched Prisma SASE app on the ServiceNow store. The Prisma SASE app can accelerate MSP service delivery and management, significantly shrinking time to value and thereby positively impacting both top-line revenue and bottom-line EBITDA.

The Prisma SASE Platform Is Accelerating Value through Unified Automation and Platformization

Time to value (TTV) is one of the most critical metrics for IT teams helping customers move forward. With the Prisma SASE app, customers can go from implementation to go-live in just hours. There’s no need to build custom API integrations or take on technical debt for Day 0 to Day N operations. The app automates infrastructure setup, including ZTNA connectors and mobile user workflows, so providers can get their SASE offerings to market faster.

Comparing ServiceNow with and without Prisma SASE App.
Optimizing Service Delivery through Unified Incident Lifecycle Management.

The joint solution eliminates swivel chair operations. Security and network administrators no longer need to toggle between the Prisma SASE console, ServiceNow and support portals. Incident ingestion and management now happen in one place. Incidents stay in sync, manual overhead drops, and mean time to resolution improves. For MSPs, there’s the added benefit: they can create Palo Alto Networks CSP (Customer Support Portal) tickets directly from the ServiceNow SASE app, making incident correlation and troubleshooting straightforward.

Drive Scalable Growth by Automating Cross-Instance Support with Service Exchange

ServiceNow’s Service Bridge is a major unlock for Managed Service Providers scaling their SASE offerings. It automates cross-instance support so critical security incidents and status updates flow between the MSP’s ServiceNow instance and the customer’s ServiceNow instance without manual sync work. This creates operational transparency and a better service experience for customers while MSPs can deliver faster without adding headcount or complexity.

Key Takeaways:

  • Rapid Time to Value: Shift from months of manual configuration to hours of automated deployment by leveraging out-of-the-box integrations that eliminate custom R&D and technical debt.
  • Unified Operational Excellence: Eliminate "swivel chair" management by unifying incident ingestion, ticket syncing and support portal escalation into a single ServiceNow interface, significantly reducing MTTR.
  • SASE at Scale: The Prisma SASE app provides a unified architecture that scales across tenants automatically, ensuring security keeps pace with business growth.

Take the Next Step

As you adopt SASE, take out the complexity of implementation with the Prisma SASE app.

  • Download the App: Visit the ServiceNow Store today and download the Prisma SASE app to start automating your deployment.
  • Meet Us at MWC: Are you heading to Barcelona for Mobile World Congress (MWC)? Come see these integrations in action. Stop by the Palo Alto Networks booth (Hall 4, Stand D55) for a live demo and to chat with our experts about simplifying your SASE implementation.
  • Contact our sales team for any additional questions.

The post A Joint Vision for Simplified SASE Management at Scale appeared first on Palo Alto Networks Blog.

❌