โŒ

Normal view

Received โ€” 28 October 2026 โญ Palo Alto Networks Blog

NHS England evolves its cybersecurity strategy with Palo Alto Networks and IBM

13 October 2026 at 10:29

The NHS has set an ambitious goal of achieving cyber resilience across healthcare organisations by 2030. Delivering on that vision requires technology, expertise and close collaboration across the public and private sectors.

This is clearly a highly complex task, but one we're delighted to help deliver in partnership with IBM. Through this partnership, Palo Alto Networks will provide advanced cloud-based perimeter technology, alongside IBM Consultingโ€™s specialist guidance, implementation support and tailored onboarding for NHS organisations.

As health and care services continue to modernise, maintaining resilient, secure digital infrastructure has never been more important. Healthcare organisations are operating in an increasingly complex environment, with growing digital dependencies, expanding supply chains, evolving cyber threats and new technologies such as AI reshaping the landscape.

According to IBM's Cost of a Data Breach Report, healthcare continues to be one of the most impacted sectors globally when it comes to the financial consequences of cyber incidents. This highlights the importance of taking a proactive, long-term approach to cyber resilience across critical public services.

Palo Alto Networks' continued work with the NHS demonstrates the scale and complexity of securing modern healthcare environments. As organisations balance innovation, operational demands and evolving security requirements, there is a growing need for solutions that provide both strong protection and the flexibility to meet local needs.

Introducing the Next Generation of the NHS Secure Boundary Programme

Palo Alto Networks will deliver next-generation, cloud-based security solutions through the next iteration of the NHS Secure Boundary programme. The service has been designed to help strengthen cyber resilience across UK health and social care organisations while supporting the safe and reliable delivery of services.

Secure Boundary provides the capability to support a network spanning more than 1.5 million NHS staff, over 200 NHS trusts, more than 55,000 organisations handling health data and approximately 2 million devices under national cyber monitoring. The nationally integrated and centrally funded service embodies a "Defend as One" approach, helping organisations benefit from shared protection while retaining local control.

Secure Boundary supports NHS organisations through:

  • An AI-enabled cybersecurity capability designed to strengthen resilience and support the safe, reliable delivery of healthcare services.
  • Enhanced visibility and protection for internet traffic across the Health and Social Care Network.
  • Improved security for infrastructure and clinical applications operating across multiple service providers.
  • Increased protection for information shared across NHS organisations and trusted third parties.
  • Greater privacy and security for staff accessing web-based services, whether on-site or remotely.
  • A "Defend as One" approach that complements existing local security measures while allowing organisations to tailor policies to their specific requirements.
  • Reduced complexity through the consolidation of security tools and management processes.
  • Improved efficiency through a centrally funded model that helps reduce duplication of technology and investment.

The new Secure Boundary service represents a significant step forward in strengthening the NHS's digital resilience. By providing a more secure foundation for NHS services, it helps support operational continuity, safeguard sensitive information and enable healthcare teams to continue delivering high-quality care in communities across the UK for years to come.

If you would like to find out more about Secure Boundary and how it can help your organisation, please contact ukpubsec@paloaltonetworks.com.ย 


ย 

Forward-Looking Statements

This blog contains forward-looking statements that involve risks, uncertainties and assumptions, including, without limitation, statements regarding the benefits, impact, or performance or potential benefits, impact or performance of our products and technologies or future products and technologies. These forward-looking statements are not guarantees of future performance, and there are a significant number of factors that could cause actual results to differ materially from statements made in this blog. We identify certain important risks and uncertainties that could affect our results and performance in our most recent Annual Report on Form 10-K, our most recent Quarterly Report on Form 10-Q, and our other filings with the U.S. Securities and Exchange Commission from time-to-time, each of which are available on our website at investors.paloaltonetworks.com and on the SEC's website at www.sec.gov.ย  All forward-looking statements in this blog are based on information available to us as of the date hereof, and we do not assume any obligation to update the forward-looking statements provided to reflect events that occur or circumstances that exist after the date on which they were made.ย ย 

ย 

The post NHS England evolves its cybersecurity strategy with Palo Alto Networks and IBM appeared first on Palo Alto Networks Blog.

Received โ€” 3 October 2026 โญ Palo Alto Networks Blog

โ€œSASE Gatewayโ€ provided by KDDI : How SP Interconnect Simplifies Closed Network Zero Trust

30 September 2026 at 04:12

We are thrilled to announce that KDDI Corporation, a long-standing NextWave partner of Palo Alto Networks and a Managed Security Service Provider (MSSP) with whom we have built a strong partnership, has launched an innovative new service, "SASE Gateway powered by Palo Alto Networks," equipped with our latest "SP Interconnect (SPI)" architecture.ย 

As the implementation of AI in business operations and the shift to the cloud accelerate, and enterprise data becomes more distributed than ever, cyberattacks are also leveraging AI to become more advanced and sophisticated. In such an environment, enterprise security must completely transition from traditional perimeter defense to a Zero Trust architecture that continuously verifies all traffic. Our Prisma SASE is the industry's premier platform built to defend, scale, and secure your enterprise at the speed of AI. Powered by Precision AIยฎ, it enforces dynamic Zero Trust guardrails to proactively defend against frontier AI attacks and secures the adoption of GenAI and autonomous agents across the enterprise.

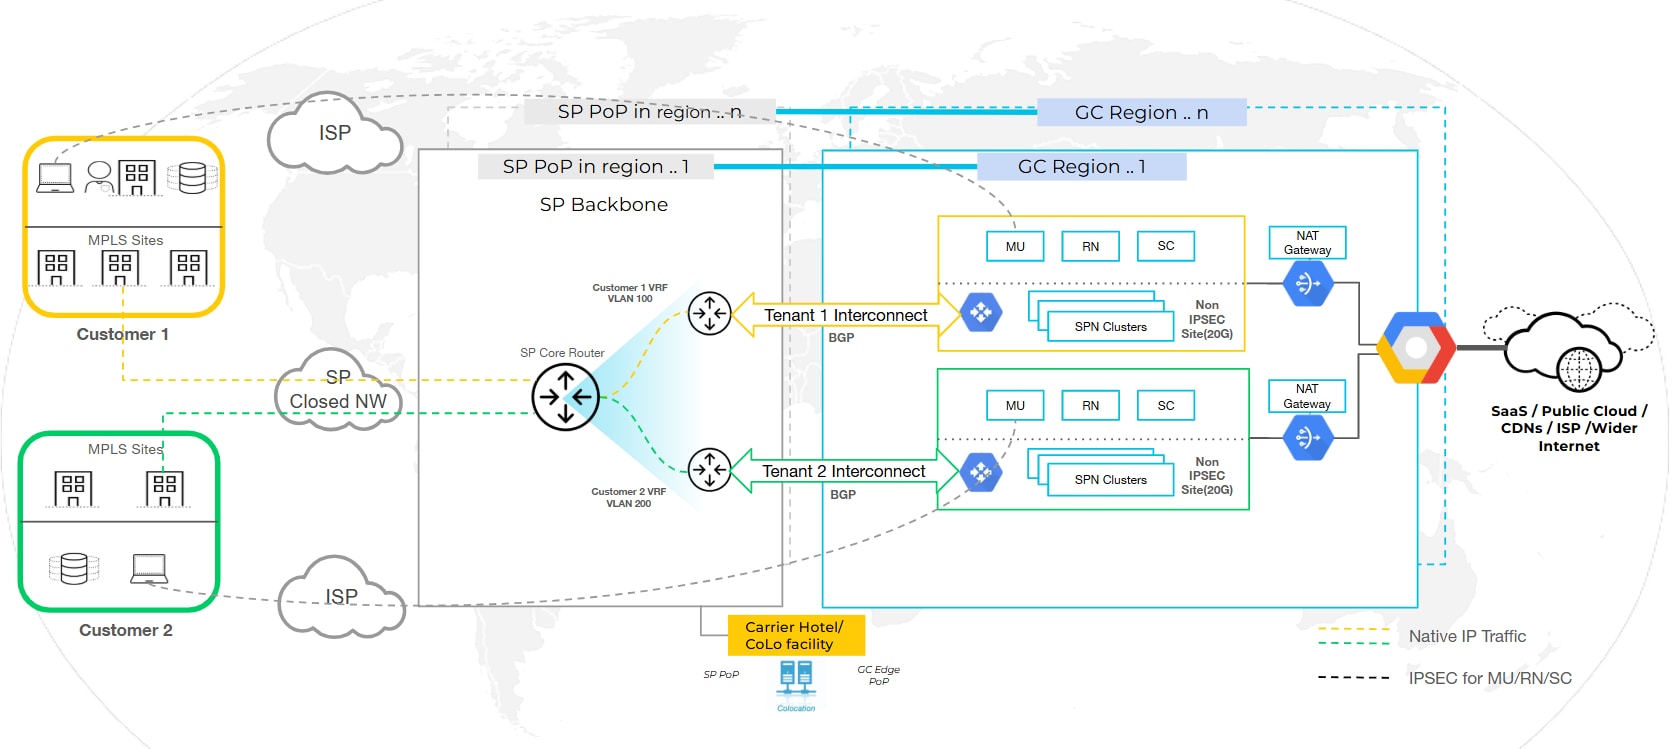
The "SP Interconnect (SPI)" adopted by KDDI this time is a next-generation architecture that directly interconnects telecommunications carriers' high-quality networks with our Prisma SASE. This integration makes it possible to directly connect traffic from closed networks (KDDI Wide Area Virtual Switch 2: WVS2)โ€”which remain highly demanded among Japanese enterprisesโ€”to SASE, in addition to internet connections. In particular, the latest SPI achieves the flexibility and performance required to meet the strict requirements of the Japanese market, including the elimination of IPsec connection overhead . As a result, an ideal infrastructure foundation has been completed that uncompromisingly balances the communication quality of the carrier backbone and the latest security of Palo Alto Networks, allowing unified management under a single policy engine.

Executive Perspective: KDDI Leadership on Next-Gen Security

Regarding this release, Junji Hori, General Manager of Product Management at KDDI Corporation, stated:


"With the launch of Prisma SASE with SP Interconnect, the convergence of closed networks and the internet has accelerated. This service serves as the core first-phase solution in the Security-as-a-Service domain under KDDIโ€™s 'AccelWaves Vision,' and we position it as a major milestone toward realizing 'KDDI AccelWaves Network,' an autonomous network service for enterprises scheduled for release in 2028.

By simply unifying the individual design and management of security across both closed networks and the internet, this newly announced service reduces the operational burden on security and networking while contributing to rapid response in the event of an incident. This is an advanced initiative made possible by combining the long-standing partnership and expertise cultivated between both companies.

Equipped with AI security capabilities, we are confident this service will deliver new value not only to existing WVS2 customers, but also to customers aiming to centralize security operations and optimize their networks.

KDDI will continue to further strengthen its partnership with Palo Alto Networks and strive to deliver innovative services that accelerate our customers' AI implementation."
ย 

Key Architectural Advantages of SP Interconnectย 

The SP Interconnect that underpins the "SASE Gateway" offers the following outstanding benefits to customers:ย 

  • Direct Connection to KDDI's Closed Network and Ensuring Reliability: Achieves a low-latency and stable communication environment through the high SLA and cloud scale of Prisma SASE, and closed connection with KDDI's high-quality, wide-band backbone.
  • Realization of Comprehensive ZTNA: Consistently applies best-in-class Zero Trust security to access SaaS and private applications, regardless of the line type (closed network, Internet, etc.).
  • Securing the AI-Driven Enterprise: By routing high-speed closed network traffic through Prisma SASE, organizations can safely adopt GenAI and agentic AI tools. SP Interconnect enablesย  this traffic to benefit from machine-speed inline inspection, stopping automated, frontier AI attacks (like machine-scale vulnerability scanning and prompt injections) while enforcing complete visibility, identity control, and advanced data loss prevention (DLP).
  • Proactive IT Operations Powered by AI: Accelerate time-to-value by transforming reactive IT support into proactive, self-healing operations. It leverages AIOps and ADEM (Autonomous Digital Experience Management) to comprehensively visualize and manage transport networks across branches, clouds, and data centers, predicting and resolving network issues before users even notice them.
Figure: Interconnection with KDDI Backbone via the Latest SP Interconnect

Furthermore, to realize a platform-based approach to security, KDDI offers the "SASE Gateway" service alongside the extensibility to introduce advanced security solutions such as our "Cortex XDR" and "Prisma Browser" (a secure enterprise browser). Additionally, to provide end-to-end support for customers' security operations and management, this offering can be combined with SOC and IR (Incident Response) services provided by LAC Co., Ltd.ย 

Palo Alto Networks is confident that this "SASE Gateway" will become an essential business foundation supporting secure DX (Digital Transformation) for many Japanese enterprises advancing AI adoption, hybrid work and cloud migration. Through our strong alliance with KDDI, we look forward to further deepening our technical collaboration and greatly expect them to powerfully lead the expansion of sales and adoption among enterprise companies as a strong core solution for KDDI's "AccelWaves Vision".

KDDIโ€™s SASE Gateway with Palo Alto Networks is now available as part of the companiesโ€™ joint integrated security portfolio.

Modernize Your Closed Network Security Today

Ready to simplify your hybrid network management and protect your organization against AI-driven threats? Contact us to schedule a custom architecture review or explore how KDDI SASE Gateway can fit into your cloud strategy.

The post โ€œSASE Gatewayโ€ provided by KDDI : How SP Interconnect Simplifies Closed Network Zero Trust appeared first on Palo Alto Networks Blog.

โŒ