AI policy wonks declare 'sovereign agents' a threat to civilization
The government’s surveillance powers grew rapidly after Sept. 11, 2001, some in public view and some in secret. EFF suspected but couldn’t prove that the National Security Agency was spying on Americans' communications. The New York Times sat on a story about it for over a year, finally publishing it in December 2005. Then, in January 2006, a retired AT&T technician named Mark Klein walked into EFF's office with a manila folder of documents that blew the story wide open.
Welcome to the third episode of “Privacy’s Defenders,” a podcast about the people – lawyers, journalists, hackers, and others – who’ve fought to secure your digital liberties since before most people even knew what the internet was.
(You can also find this episode on YouTube.)
In this episode, former EFF Executive Director Cindy Cohn talks with former EFF lawyer Kevin Bankston, who was at his desk drafting a lawsuit against AT&T when Klein showed up. Less than two weeks later, EFF sued the phone company on behalf of its own customers in Hepting v. AT&T. Cindy speaks again with now-retired Justice Department lawyer Tony Coppolino, who asked for the opportunity to defend the case. He called EFF with a warning after Klein’s documents were filed in court: If they were classified, EFF would be in big trouble. You’ll also hear from Klein himself, and from Carolyn Jewel, a romance novelist and AT&T customer who became the lead plaintiff in EFF's related case against the NSA.
It's the story of a secret room in a San Francisco phone company building, a heroic whistleblower, and the people who refused to let mass surveillance stay hidden.
The “Privacy’s Defenders” podcast is a follow-up to Cindy’s book, “Privacy’s Defender: My Thirty-Year Fight Against Digital Surveillance,” bringing to life pivotal moments in the voices of those who fought for your rights. Sales of “Privacy’s Defender” benefit EFF, so pick up your copy today!
Joanne Elgart Jennings co-produced and created this podcast.
Jarrod Sport co-produced, mixed, and mastered it.
Corinne Ruff is our story editor.
We had additional help from Rachel Estabrook and Alison Broverman.
The original music was composed and performed by Nat Keefe of Hot Buttered Rum with Ben Andrews on the fiddle.

Google said today it worked with industry partners to dismantle a botnet made up of more than 1.3 million Android TV set-top boxes that ship with malicious software which secretly rents the user’s Internet connection out to strangers and conducts advertising fraud. Experts involved in the takedown say the action is likely to sever the botnet’s access to more than 10 million additional compromised systems, including other Internet of Things (IoT) products such as Android-based healthcare devices and karaoke machines.
A report from the Google Threat Intelligence Group (GTIG) said Google has severed ties with Videostrong Technology Co., a TV box manufacturer in China that GTIG and other industry experts concluded was responsible for including malware that enrolled more than 1.3 million set-top boxes in a botnet dubbed “XCPE” (named after one of the malware’s core code components).
The global distribution of XCPE botnet infections. Image: Google Threat Intelligence Group.
The report said the XCPE botnet loaded the user’s device with software that makes their Internet address available for resale by multiple “residential proxy” services, which allow customers to rent Internet addresses as a way to anonymize their web traffic or spoof their true location. As detailed in several stories here over the past year, residential proxy services are a major source of unwanted and often malicious traffic, including account takeover activity, advertising fraud, and mass content scraping for AI projects.
“Videostrong monetized the backdoor by selling access to criminal affiliates and loading those affiliates’ malware modules onto infected devices,” the GTIG post reads, noting that Google took legal action to take down the domains and servers Videostrong used to control the botnet and install additional malware. “A device manufacturer intentionally infecting their users with malware is an unacceptable breach of trust, and represents a serious risk to those users. Without users’ knowledge or consent, infected devices were offered as a distribution mechanism for a wide array of criminal actors.”
The report notes that while TV boxes made up the the majority of the botnet, the same XCPE malware was found in other Android-based IoT products, including telehealth devices, karaoke machines, and even digital signage systems.
Google said it requires all Android device makers to pass compatibility and security tests to ensure their products don’t harm users, but that Videostrong nevertheless found a way to load their malicious software immediately after a user boots up one of these devices for the first time (Google says it has since addressed that weakness).
The GTIG report calls out a number of residential proxy providers whose software development kits were routinely downloaded by devices infected by the XCPE botnet. Those include AppSalt, also known as Honeygain, which is owned by the Vilnius, Lithuania-based Oxylabs. In October 2026, Oxylabs was relaunched under a new brand called Source, after receiving $130 million in funding from private equity firm Warburg Pincus that reportedly valued the business at $3.6 billion. Oxylabs did not respond to a request for comment.
Another provider linked to the botnet was NetNut, a once sprawling residential proxy company operated by the publicly-traded Israeli company Alarum Technologies. In July 2026, the FBI worked with industry partners to seize hundreds of domains associated with NetNut, saying the company was responsible for operating a separate botnet called Popa that enslaved TV boxes as residential proxies. Other proxy providers named in the GTIG report include EarnFM, Traffmonetizer, Jaguar, LINKFOG, BMW/IPWeb and GaGaNode.
Google’s announcement credits a number of industry partners, including Synthient, a startup that tracks proxy providers. In January 2026, Synthient published research into the rapid spread of the Kimwolf botnet, which at the time was hammering networks worldwide with record-smashing DDoS attacks. Synthient documented how Kimwolf infected millions of Android set-top boxes virtually overnight, using a widespread vulnerability in these residential proxy services to compromise other Android-based devices inside the local networks of unsuspecting TV box users.
Synthient’s research caused dozens of residential proxy providers to patch their networks, which helped to fragment the Kimwolf botnet into much smaller pieces that made its incessant and disruptive DDoS attacks far easier for network operators to manage. It also attracted the attention of the Motion Picture Association (MPA), a trade group representing the major Hollywood studios, which partnered with Synthient to purchase and tear apart a number of popular Android TV set-top boxes — including some that were being infected by Kimwolf and other IoT botnets.
In a report published today, Synthient examined a popular, pre-infected TV box sold under the brand MECOOL by a publicly traded company in China called Skyworth Technology, concluding that MECOOL also bundled the malware from Videostrong Technology Co. and likewise installed AppSalt/Honeygain and other proxy components.
The MECOOL storefront and marketing. Image: Synthient.com.
Synthient founder Ben Brundage told KrebsOnSecurity that Videostrong’s malware also distributed software for the proxy service Grass. In our November 2025 story, “Is Your Android TV Streaming Box Part of a Botnet?” we quoted a researcher from Censys who found the popular Superbox TV streaming device bundled Grass’s residential proxy software. We also quoted the Grass founder, who denied any affiliation with the TV box maker.
That November 2025 story noted that Superbox and similar Android TV set-top boxes gain new customers primarily by engaging influencers on Tiktok and other social networks who praise the product’s ability to offer hundreds of (pirated) pay TV streaming services for a one-time fee.
Likewise, Synthient’s report observes that the MECOOL set-top boxes exploded in popularity after the product was mentioned in 2023 by the Youtube channel Linus Tech Tips, which has an audience of nearly 17 million subscribers [Linus Tech Tips said in a statement shared with Synthient that it has since updated the video to explicitly frame the product as a scam and have removed all associated affiliate links].
The popular Youtube channel Linus Tech Tips discussing MECOOL TV streaming boxes.
The GTIG report estimates the XCPE botnet takedown should sever access to at least 10 million additional compromised devices, noting that the various proxy and ad fraud affiliates of Videostrong “each have diversified distribution channels for their modules beyond XCPE.”
Synthient’s Brundage echoed that conclusion, calling the 1.3 million number “highly conservative.”
“The scale of affected devices is likely way higher,” he said. “This is probably the largest operation against backdoored TV boxes that we’ve seen.”
Further reading:
Plume Security Labs white paper on the XCPE botnet (PDF)
Black Lotus Labs writeup on LinkedIn
TrendAI’s analysis
Synthient’s list of affected devices, broken down by model number

On November 11, Lina Attalah, founder and editor-in-chief of the independent Egyptian news outlet Mada Masr, will face trial for the second time in just two weeks. This time, she faces charges of spreading false news, an accusation that has become one of the Egyptian government's most frequently used tools for prosecuting journalists.
The trial follows a conviction on October 27, when Attalah was found guilty of managing an unlicensed news website. The Mada Masr team had repeatedly applied for a license, but their attempts went unacknowledged. The proceedings took place in a single hearing, which Mada Masr states included serious violations of her right to a fair trial. She was sentenced to the maximum fine of 3 million Egyptian pounds (approximately 55,000 USD), forcibly removed from the courtroom, and held for seven hours until the fine was paid. The court also ordered Mada Masr's closure and the confiscation of all equipment belonging to the organization.
The current wave of repression has also targeted Matsada2sh, a fact-checking and open-source intelligence initiative. Its entire six-person newsroom was violently arrested, illegally detained, and interrogated under torture before being charged with terrorism-related offenses and spreading false news. The team remains in pretrial detention.
According to CPJ, at least 25 other journalists are currently incarcerated in Egypt.
Governments seeking to control the flow of information increasingly rely on a combination of legal harassment, financial pressure, criminal prosecution, and restrictions on the infrastructure that makes independent publishing possible. Egypt's media licensing regime is a particularly troubling example. Requiring news organizations to obtain government authorization to operate creates an obvious mechanism for restricting who gets to publish and whose voices are allowed to reach the public.
The charge of spreading false news is similarly dangerous. Governments around the world have increasingly invoked the language of misinformation to justify restrictions on speech, often without meaningful safeguards against political abuse, as we laid out in our recent submission to the United Nations Office of the High Commissioner for Human Rights. Governments should never be the arbiters of which reporting is permissible, particularly when that reporting concerns their own conduct.
Founded in 2013, Mada Masr has spent more than a decade doing the kind of journalism that authoritarian governments find most threatening: documenting abuses, amplifying marginalized voices, and reporting on issues that powerful institutions would prefer remain hidden.
Its reporting has given torture survivors and the families of political prisoners a platform. It has opened space for debate about reproductive rights. It has brought frontline reporting from Sudan and Gaza, and stood alongside refugees facing xenophobic attacks and security crackdowns.
Emerging as a digital-first publication, in a media environment where traditional outlets were increasingly constrained, being purely digital allowed Mada Masr’s founders to build an independent publication outside the structures of legacy media.
At a time when only 43% of Egyptians had access to the internet, going fully digital meant taking a big risk, but it was one that has been rewarding: Despite being blocked by the Egyptian government since 2017, Mada Masr has continued to reach Egyptian and global audiences, and Attalah has received numerous accolades, including the Knight International Journalism Award, the Ordre des Arts et des Lettres, and a spot in TIME Magazine’s 100 most influential people (2020).
Mada Masr has also consistently engaged with technology and advocated for a free and independent internet for the global majority. It has covered dozens of hot-button tech stories in recent years, from Egypt’s Cybercrime Bill and Israel’s use of AI weaponry in Gaza, to stories about the “privacy chaos” caused by biometrics to more personal essays about the importance of the internet and tech. In August, they launched an open call for proposals on original critical reporting on artificial intelligence.
Mada Masr may be thoroughly Egyptian, but it doesn’t belong just to Egypt. Its team has made into a publication that represents the kind of independent, local, grounded journalism that international audiences need, particularly at a time when international reporting on state repression is lacking. They built on-the-ground networks to center local voices in Sudan (publishing in both English and Arabic on the conflict) and Gaza out of a sense of cross-border responsibility and solidarity.
This is precisely why its potential closure should concern everyone who cares about a free press. The ability to publish independently, investigate powerful institutions, and to share information without government interference is fundamental to the exercise of free expression.
The international community has repeatedly expressed concern about restrictions on press and internet freedom in Egypt. More than 100 organizations have now joined statements of solidarity with Mada Masr, and with Matsada2sh.
These expressions of support matter, particularly when journalists are increasingly isolated and under threat—but solidarity must also translate into sustained political and institutional pressure.
The international governments and institutions that maintain relationships with Egypt—including those in the European Union, the United Kingdom, and the United States—should make clear that the prosecution of journalists and the forced closure of independent media outlets are unacceptable.
The cases against Lina Attalah, Mada Masr, and Matsada2sh must be dropped. The journalists who remain in detention must be released. And Egypt's licensing regime, with its profound chilling effects on access to information and independent knowledge production, must be brought to an end.
There is a particular urgency to defending independent media at a moment when governments are finding ever more ways to restrict the circulation of information. Whether through internet shutdowns, platform restrictions, surveillance, or the criminalization of reporting, the result is often the same: fewer opportunities for people to understand what is happening around them, to challenge official narratives, and to hold power accountable.
We cannot allow the closure of one of Egypt's most important independent newsrooms and the prosecution of its editor-in-chief to become another routine episode in the global erosion of press freedom. Nor should we wait until the last independent journalists have been silenced before recognizing what has been lost.
To learn more about Lina Attalah in her own reads, you can read our Speaking Freely interview from January 2026.

If you operate a website, you’re already aware that a single unpatched vulnerability can render your site inaccessible, compromise your reputation, or necessitate extensive remediation following an attack. Most security breaches we observe originate from automated attacks that exploit known software vulnerabilities, often the same ones that have been previously reported and disclosed.
To assist in maintaining your security posture, we have compiled this month’s summary of essential security updates and vulnerability patches pertinent to the WordPress ecosystem.
Continue reading Vulnerability & Patch Roundup — October 2026 at Sucuri Blog.
In courts across the country, publishers and creators are suing large AI companies for training generative AI models on copyrighted works. It’s easy to see these cases as a David-and-Goliath showdown between authors and publishers fighting for a cut of Big Tech company profits. But this fight is actually much larger. It affects billions of people who aren’t represented in the case at all, including researchers, artists, activists, journalists, people with disabilities, and anyone who accesses and shares content online.
That’s why EFF is stepping in to defend the public’s rights in these cases. Today, EFF filed an amicus brief in In re OpenAI, explaining how the court’s ruling on fair use could impact people worldwide. If fair use gets narrowed, it will impede work that benefits the public, like medical research and investigative journalism, and even limit access to privacy protection tools.
Let’s be clear: creators and workers deserve support as AI changes their fields, and Big Tech companies must be held accountable for the harms they cause. But giving copyright holders more control over the web won’t accomplish either of these goals. If the plaintiffs prevail in these cases, courts would have to rewrite copyright law in ways that hurt everyone except powerful media and tech companies.
Copyright exists for one reason: to stimulate creativity and innovation in service of the greater public good. Unfortunately, the plaintiffs in this lawsuit are arguing to limit everyone’s fair use rights, in ways that would thwart the basic purpose of copyright. The harms of shrinking fair use will go far beyond generative AI, impacting everyone.
Initial speculation that AI models would be infringement machines, churning out works highly similar to those on which they were trained, has proven unfounded. And courts have already found fair use in cases where copyrighted works were used to train generative AI models, recognizing that training uses those works for a fundamentally different purpose.
Plaintiffs in these cases argue that, even if the use is transformative, using their works to train AI is still unfair, because the AI models could generate new, non-infringing works that might compete with plaintiffs’ own works. They also argue that scraping or downloading the data without permission—or in some cases, from websites containing infringing copies—was independently infringing and/or rendered any subsequent uses of that data unfair.
These arguments would put beneficial research and reporting at risk. First, if copying without permission rules out fair use, the law will never protect transformative uses that benefit us all. Researchers, journalists, and other watchdog groups gather information the same way AI companies do—but they do it to serve the public interest, and often to hold Big Tech itself accountable. For example, journalists and nonprofit researchers have used “crawling” or “scraping” to investigate potentially anticompetitive practices by tech companies, and research misinformation and hateful content posted on X. Their data acquisition techniques are virtually identical to those used by AI giants—but they lack those companies’ deep pockets.
Requiring users to show that copyrighted material was lawfully obtained would also threaten everyday internet use. As EFF’s brief explained, that requirement would “cast legal doubt on the billions of copies we collectively make every day through routine online activities like opening emails, clicking on an embedded link, visiting websites, sharing pictures, streaming music, and watching videos. All of this activity requires intermediate copying.”
Fair use is what lets us all use the internet without being compelled to track the source of every image, video, and article that we click on, and make sure the rights are all cleared.
Additionally, while rightsholders are understandably concerned about competition from AI generated works, copyright law exists to promote new creation, not protect authors who published first. Under the plaintiffs’ theory, no one could stand upon the shoulders of giants. Copyright could prevent people from writing new books inspired by themes in a favorite novel or genre, or prevent academic researchers from publishing literature reviews that distill insights from prior research—simply because readers might prefer those new publications over those that came first.
Finally, general-purpose AI models are neither designed nor usually used to create works targeted at any particular market. These models have been used to generate new insights and tools for medicine, science, journalism, art, and accessibility. For instance, an AI-powered tool called Be My AI uses Open AI’s GPT models to provide visual descriptions for people who are blind or have low vision. Generative tools have also accelerated scientific research, and researchers have used these tools to develop new medical treatments and medications for conditions previously thought to be incurable.
Some creators and publishers argue that AI developers should just get a license. But requiring permission for every work used would give the largest companies massive advantages over small competitors and impede academic research. As Professor Lawrence Lessig recently noted:
If all training requires a license, then none but a handful of tech giants will be able to afford the costs of training. That’s not because authors are greedy but because the copyright system is the least efficient property system known to man.
Moreover, creators are unlikely to benefit from these licensing arrangements in many cases. Media and entertainment giants have exploited the imbalance between themselves and underpaid working artists for decades. Trying to help creators by giving them more rights under copyright is, as Cory Doctorow has written, like trying to help a bullied kid by giving them more lunch money for the bully to take. Artists aren’t getting good deals from record labels or publishers now; there’s no reason to think these companies, which already own the copyrights, will treat artists more fairly once they control the data that powers AI.
AI technologies will affect all of us, and copyright law is ill-equipped to address many of these consequences. The rules governing these technologies should be rules that serve the public—not just the small number of companies that can afford to litigate copyright battles for decades, or settle for billions.

Developers of virtual private network (VPN) apps are reporting that their products are again being pulled from Apple’s App Store in Russia. This is an unacceptable crackdown on a vital tool to protect privacy and speech online.
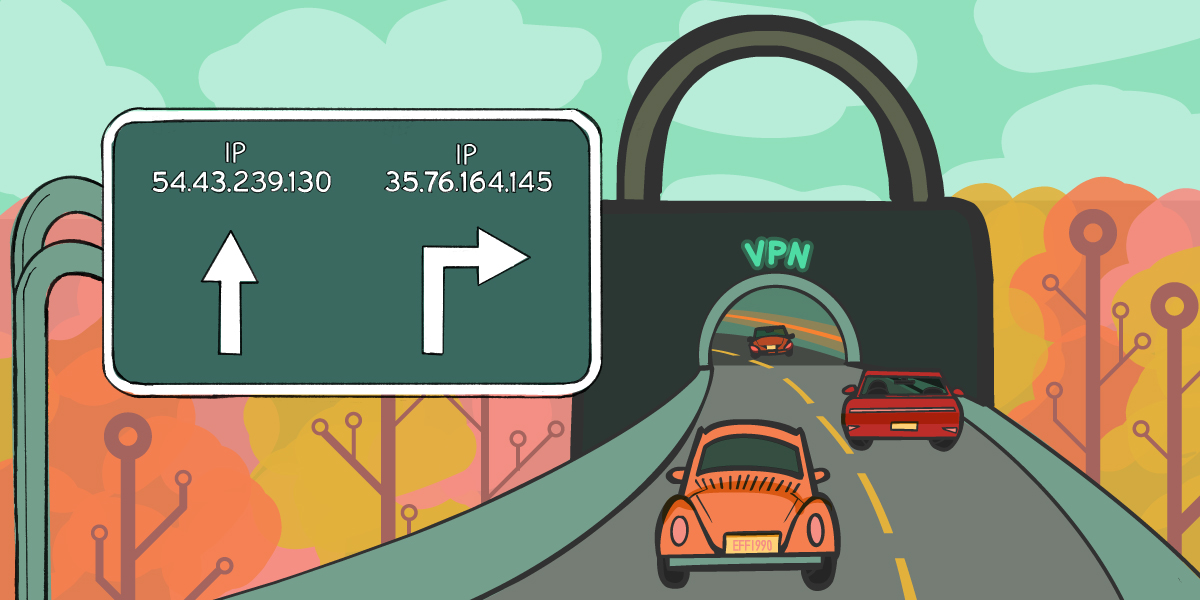
Why? VPNs give people a way to control their own online activities. When you visit a website through a VPN, that website only sees the VPN server's location (well, IP address) rather than your actual location. It's like sending a letter through a P.O. box so the recipient doesn't know where you really live. It can also disguise where you’re accessing information from, which can make it possible to access information banned by your government.
This is an unacceptable crackdown on a vital tool to protect privacy and speech online.
Going after tools that give people the space to communicate and access information freely is a common tactic from the totalitarian playbook. This latest demand comes after several steps the Russian government’s taken to surveil speech specifically on Apple products. In 2024, the Moscow Times reported that Russia’s state media watchdog, Roskomnadzor, went after VPN apps on the Apple App Store, after banning access to Western social media platforms and blacklisting opposition media sites. Russia then blocked Apple’s FaceTime software in 2025, according to Apple Insider.
Bloomberg also recently reported that the Russian government has added Apple and Microsoft to its state surveillance registry. This gives Roskomnadzor access to local users’ correspondence, Apple Insider reported, and puts both companies in a position to turn over customer information to the country’s security services as required.
With government control encroaching on their devices and less access to tools that give them alternate methods, people in Russia are left with shrinking options to communicate online or find information that isn’t state-sanctioned.
While Russia’s actions offer a more extreme vision of what happens when the government tries to enforce speech rules by attacking vital privacy tools, it is far from the only government doing so. Several states in the U.S., bent on making it difficult to circumvent invasive age-gating laws, have suggested banning VPNs—either to access certain content or in some cases to simply ban them outright. EFF has publicly (and loudly) criticized these proposals, because going after VPNs is a dangerous step down the road of censorship.
Attacks on speech and privacy online are deeply troubling, no matter where they happen. What those in power may see as a “loophole” in their invasive laws is actually an expression of user control. We’ll continue to speak out when we see governments going after them to take that control away.