❌

Normal view

mSecure tells users to change passwords but won’t say why [updated]

4 November 2026 at 18:02

Password manager mSecure has warned current and former customers to protect the confidential information stored in its app after detecting “suspicious activity.”

But its advice about what users should do comes without an explanation of what happened or whose information might be at risk.

The warning leaves users to decide whether to replace credentials—and whether it’s safe to store replacements in mSecure.

While those are perfectly reasonable questions, mSecure’s warning does not answer them.

In an email published by The Hacker News and sent to customers on November 3, mSecure’s developer, mSeven Software, said:

“mSeven Software (‘mSeven’) recently learned of suspicious activity associated with the mSecure password management application. In response, mSeven quickly launched an investigation, took steps to mitigate the issue, and engaged external cybersecurity experts to assist.”

The notice recommends that customers “immediately take steps to protect all confidential information” stored in mSecure. Those steps:

“may include changing passwords, resetting or re-enrolling two-factor authentication methods, or removing existing passkeys.”

But the notice does not identify the suspicious activity, when it occurred, which systems were involved, or whether anyone accessed customers’ stored information. The Register, which also reviewed the email, noted that the company had not explained whether customers’ secrets were exposed.

How to be safe

Because the scope of the incident is unknown, we recommend prioritizing your most important accounts while mSeven investigates.

Changing your mSecure password alone may not be enough if someone has already accessed your account. mSecure’s documentation explicitly warns that someone may already have made a backup of its contents. That guidance does not establish what happened in this incident.

Users should not have to wait for a completed forensic investigation before receiving useful guidance. They need to know who should act, which credentials need attention, and whether the tool they would normally use to manage those changes remains safe to use.

Until mSeven provides those answers, our advice is to prioritize your most important accounts, replace the relevant credentials through official services, and avoid destructive account resets:

  • Change passwords through each service’s official website or app, beginning with your primary email, financial accounts, work accounts, and accounts used to recover access to other services. Use a new, different, strong password for each.
  • Review two-factor authentication stored in the vault. If that could be compromised by unauthorized access, consider re-enrolling that account’s authenticator through the service’s security settings.
  • For passkeys stored in mSecure, use each website or app’s account-security settings to remove the old registration and create a replacement with a different provider as a precaution. But make sure another working sign-in method is available first.
  • Think carefully about where replacement credentials go. The notice does not establish whether saving new credentials in mSecure is safe. For users rotating important accounts now, using a different password manager temporarily is a reasonable precaution.

We’ll keep you posted if we learn more about this incident, so stay tuned.

Update November 6, 2026

According to follow-up messages attributed to mSecure support and reproduced by multiple customers on the company’s forum, the incident affects only users who synchronized with mSecure Cloud. We have not located a directly published company statement confirming that scope.


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

Revolve card breach: 1.5 million people may be affected

3 November 2026 at 12:26
.kadence-column484007_649ea4-04 > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column484007_649ea4-04 > .kt-inside-inner-col{flex-direction:column;}.kadence-column484007_649ea4-04 > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column484007_649ea4-04 > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column484007_649ea4-04{position:relative;}@media all and (max-width: 1024px){.kadence-column484007_649ea4-04 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column484007_649ea4-04 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}
.kadence-column484007_683ec9-3f > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column484007_683ec9-3f > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column484007_683ec9-3f > .kt-inside-inner-col{flex-direction:column;}.kadence-column484007_683ec9-3f > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column484007_683ec9-3f > .kt-inside-inner-col{background-color:rgba(255, 229, 229, 0.83);}.kadence-column484007_683ec9-3f > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column484007_683ec9-3f{position:relative;}@media all and (max-width: 1024px){.kadence-column484007_683ec9-3f > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column484007_683ec9-3f > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}

In this article

  • Fashion retailer Revolve said customers’ payment card numbers and expiration dates were stolen
  • Data at risk includes card numbers and expiration dates, customer names and addresses
  • Affected customers should watch their statements and consider asking issuers for new cards

Online fashion retailer Revolve Group said customers’ payment card numbers and expiration dates were stolen. In its customer notification letter filed with the Massachusetts Attorney General, Revolve told recipients the incident involved their names, addresses, and payment card details.

What was stolen?

The at-risk data includes customer names and contact information, payment card numbers, and card expiration dates. The breach only affected customers who had saved their payment card as a payment method in their Revolve account.

A filing on the Texas attorney general data breach website lists 127,200 affected Texans, but not a nationwide total. We found the figure of 1,515,073 in data returned by the site when searching for Revolve. That data labels it as the total number of people affected, but the figure isn’t displayed on the public listing. Other sites have repeated it, though they appear to rely on the same Texas record. The SEC filing did not give a number of affected people, and Revolve has not confirmed the total.

Revolve’s SEC filing does not mention card verification value (CVV) numbers. These three-digit security codes printed on the back of payment cards (four digits on the front for American Express cards) are an extra layer of security for card-not-present transactions.

It is also unclear whether the card numbers were fully visible or masked, or whether Revolve or a third-party payment processor held them.

Even without a CVV, card numbers and expiration dates may be enough to make purchases at some online stores. And scammers who know your real card details and contact information may be able to send more convincing phishing messages to trick you into revealing your CVV.

How did they get the data?

Revolve has not said how the attackers accessed the saved payment data. In its SEC filing, Revolve said it believes an unauthorized actor may have obtained the data “through automated means.” Records on the Texas attorney general’s site indicate that the incident happened on September 11 and was discovered on September 29.

No group has publicly claimed responsibility for the theft.

What Revolve customers can do now

Revolve said it has taken extra security measures following the breach, although didn’t say what those are.


Breaches happen every day. Don’t be the last to know.


If you have saved payment information in your Revolve account, your details may have been among those stolen. Fraud can often begin within days of a breach. If you’re concerned about your card details being exposed:

  • Read your statements line by line to identify even small charges that you don’t recognize. Criminals will often make a small charge using stolen card details to see if the card works.
  • Look for unfamiliar merchant names on your statement.
  • Report unauthorized charges to the card issuer immediately.
  • Consider removing saved cards from shopping accounts. You could use a password manager instead, some of which will store autofill data for payment cards.
  • Ask your card issuer to cancel your card and reissue with a new number so that the old number becomes unusable.

Also, don’t immediately trust calls, texts, or emails about the incident. Scammers can use stolen information to make themselves sound convincing. If someone claims to be calling from your card issuer, call the number printed on your card to check.

If you’re unsure about a message or link, check it with Malwarebytes Scam Guard.


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

Applebee’s customer data exposed by password left in app

2 November 2026 at 15:22

Applebee’s has fixed a security flaw that exposed customers’ personal information after a researcher discovered a database password embedded in the restaurant chain’s Android app.

The researcher, Robert Wiggins, found the password with help from AI. It gave him access to an internal Applebee’s customer database. A password written directly into an app’s code or configuration is known as a hardcoded credential. Anyone who extracts it may be able to use it to access the system.

The exposed database contained:

  • Names, email addresses, and email-verification status
  • Dates of birth, phone numbers, and ZIP codes
  • Veteran status
  • Account-creation dates and login counts
  • IP addresses from customers’ most recent logins, which can indicate their approximate location

TechCrunch independently checked Wiggins’ findings. It created an Applebee’s account with dummy information, which Wiggins successfully retrieved from the database.

According to TechCrunch, Wiggins could not find a suitable way to report the issue to Applebee’s or its parent company, Dine Brands, so he asked the publication to help contact them. TechCrunch held its story until the fix was confirmed. Applebee’s confirmed on October 29 that it had addressed the issue.

It’s unclear how many customers’ records were in the database. Dine Brands says it has not found evidence of unauthorized access, but its investigation is ongoing.

How to stay safe

The database fields described by TechCrunch did not include payment card details or account passwords. That does not tell us whether anyone accessed the database before the fix, so customers should watch for targeted scams.

Names, email addresses, phone numbers, and other personal details could help scammers make messages look relevant and convincing.

  • Be wary of unexpected Applebee’s-themed emails, texts, or calls. Be especially skeptical of messages offering refunds or compensation, warning that your account will be closed, or asking you to “verify” payment details.
  • Check security notices through a route you trust. Open the app directly or visit Applebee’s website yourself rather than following a link in an unexpected message. If necessary, contact the company using details you find independently.
  • Unsure whether a message is a scam? Check it with Malwarebytes’ Scam Guard for an assessment and advice on what to do next.
  • When sharing personal information, consider why the company needs it and whether you trust it to keep the information safe.

Link Checker

Unsure where a link goes? We’ll check it.


Hackers steal and publish data on 41,000 Homeland Security workers

30 October 2026 at 12:33
.kadence-column482644_f2c16d-bc > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column482644_f2c16d-bc > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column482644_f2c16d-bc > .kt-inside-inner-col{flex-direction:column;}.kadence-column482644_f2c16d-bc > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column482644_f2c16d-bc > .kt-inside-inner-col{background-color:#ffe5e5;}.kadence-column482644_f2c16d-bc > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column482644_f2c16d-bc{position:relative;}@media all and (max-width: 1024px){.kadence-column482644_f2c16d-bc > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column482644_f2c16d-bc > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}

In this article

  • Hackers published work details and internal group memberships for more than 41,000 DHS workers.
  • The data could enable targeted scams, harassment, stalking, or physical threats.
  • DHS employees should follow agency guidance, verify unexpected contact, and report threats to security.

A group of hackers calling themselves the Department of Peace says it stole and published the personal details of more than 41,000 people working for the US Department of Homeland Security (DHS). The department says it is aware of a potential breach.

The group, which also claimed the theft of contract documents from the DHS in March, gave the data to Swiss hacktivist maia arson crimew, who published it in collaboration with the transparency collective DDoSecrets. The latter also published the BlueLeaks data dump that listed law enforcement officers’ details in 2020.

The aim of publishing the data was to replace “anonymity with accountability,” DDoSecrets co-founder Emma Best said in an online statement.

According to TechCrunch, timestamps on the records suggest the data was taken around mid-August. The group said it had launched the attack in response to a July 17 statement by DHS Secretary Markwayne Mullin, in which he promised to “turn up the heat” with traffic stops.

What was stolen?

The data files published online, which the publishers have called “Icepick,” span staff at nearly 7,000 offices. They include the names, work email addresses, phone numbers, office addresses, job titles and membership in internal DHS groups. The employees impacted include almost 6,600 Immigration and Customs Enforcement (ICE) employees. ICE is the DHS unit responsible for immigration enforcement and deportations in the US.

The dataset also carried details of over 21,000 Customs and Border Protection (CBP) employees, along with information on people who work at the Cybersecurity and Infrastructure Security Agency (CISA).

The data dump revealed less information than the ShinyHunters’ FBI data heist in September, which reportedly contained Social Security numbers, emergency contacts, medical records and home addresses. Nevertheless, this is more than just a phone book of folks in the DHS.

For one thing, it doesn’t take much to cross-reference data. Reuters matched six DHS employees’ data to credit bureau records and breach data from a dark web intelligence platform. Online activists regularly use open-source intelligence (OSINT) to “doxx” people from very few clues, meaning that even a leak of basic identity information can put someone in danger. In fact, the creators of a separate searchable version say they added information through automated and manual research. So some details shown in that version may not have come from the data stolen from DHS.


Breaches happen every day. Don’t be the last to know.


The data in this case also included membership of groups within Active Directory, a Microsoft tool that contains identity information about computer users. Active Directory controls who can access different internal tools, services, and third-party software within an organization.

The files listed over 200 CBP users in a group that could access the facial recognition tool Mobile Fortify. Other groups reference a service called Penlink, which the company claims can track the location data of hundreds of millions of mobile devices.

According to the Guardian, job titles in the data dump show which agents were assigned to sensitive jobs such as special operations, surveillance, and undercover work.

How did they get the data?

The Department of Peace said that it got to the information via a single sign-on (SSO) service provided by identity company Okta. SSO is a prized target for hackers because a single authentication can get a user into many different workplace services and applications.

Okta says it has no evidence its data or systems were compromised, but that doesn’t rule out someone abusing a DHS account with stolen credentials.

DHS told reporters it was aware of a potential breach. One DHS employee whose data showed up in the breach told Reuters they hadn’t heard anything about it.

What DHS employees can do now

The leaked records include work contact details and internal group memberships. This information could help attackers create convincing messages or calls, and may expose some employees to unwanted attention or threats. DHS has warned about the risk of harassment, stalking, and physical harm. It is not yet clear whether the leak has led to specific threats or affected any operations.

If you work for DHS:

  • Follow security advice and instructions from the DHS.
  • Treat unexpected calls, emails, and texts about your role or colleagues with caution. Verify them through a contact method you already trust, and never share passwords or MFA codes.
  • Change any personal passwords you’ve reused for work, and turn on MFA where available. Follow your agency’s process for work accounts.
  • Report suspicious contact or threats to your agency’s security team. If you believe there’s an immediate danger, contact law enforcement.

Do you think your information might have been leaked in a data breach? Check out the Malwarebytes Identity Theft Protection service.


Someone’s got their eye on your personal information. Make sure it’s us.


Patient records exposed in Quest breach: What you need to know

26 October 2026 at 12:34

Quest Diagnostics has confirmed that an unauthorized party accessed a system healthcare providers use to order laboratory tests and view results, affecting personal information and patient records.

Quest is a major US laboratory testing company whose services help healthcare professionals diagnose and monitor medical conditions. Those services range from routine laboratory testing to specialized testing in areas such as cancer, infectious diseases, and neurology.

What happened and what was stolen?

The company learned of unauthorized access to its Quanum Lab Services Manager, or LSM, on October 21. The compromised platform lets healthcare professionals order tests, access results, review historical trends, and order supplies. Quest paused access to the platform and began investigating. Quest says its core business operations remain up and running.

An investigation is ongoing. Quest has not yet published a count of affected patients or a complete list of the information accessed. It says it will notify affected patients, healthcare providers, and health plans.

The company said:

“personal information and patient records were affected.”

It confirms that health information and personally identifiable information were involved, but has not specified whether these included Social Security numbers, insurance identifiers, payment information, particular test results, or account passwords.

What patients can do now

Quest says it will send notification letters to affected patients once its investigation is complete. Those letters will describe available resources, including credit and identity monitoring. If you receive one, read it carefully and follow the instructions. You can also check the FAQs posted in Quest’s breach notice for updates.


Someone’s watching your accounts. Make sure it’s us.


A breach does not automatically mean someone has misused your information, but you can take these precautions while you wait for more details:

  • Verify unexpected messages independently. Don’t let a message about the breach rush you into clicking a link, sharing sensitive information, or making a payment. Go to Quest’s official website yourself or use contact details you already trust.
  • Review medical bills and insurance statements. Look for appointments, tests, prescriptions, or services you did not receive. The Federal Trade Commission (FTC) identifies unfamiliar medical bills and unexpected items on an Explanation of Benefits statement, which explains how your insurer processed a claim, as warning signs of medical identity theft. Report discrepancies to your healthcare provider and your insurer.
  • Review your credit reports. Look for unfamiliar accounts or debts and dispute errors. Free reports are available through AnnualCreditReport.com.
  • Act if you find signs of identity theft. Visit IdentityTheft.gov for a recovery plan. If someone has received care in your name, ask the providers involved for copies of your medical records and request corrections in writing.

Medical identity theft is not just a financial problem; it can also affect your care. Someone using your identity to obtain treatment or submit insurance claims could introduce incorrect information into your health records. Checking medical statements and reporting anything unfamiliar can help you catch that misuse.


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 
Resident Evil maker Capcom warns of phishing after 11.7 million records exposed

23 October 2026 at 15:07
.kadence-column480618_38f885-ca > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column480618_38f885-ca > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column480618_38f885-ca > .kt-inside-inner-col{flex-direction:column;}.kadence-column480618_38f885-ca > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column480618_38f885-ca > .kt-inside-inner-col{background-color:#ffe5e5;}.kadence-column480618_38f885-ca > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column480618_38f885-ca{position:relative;}@media all and (max-width: 1024px){.kadence-column480618_38f885-ca > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column480618_38f885-ca > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}

In this article

  • Capcom’s breach exposed 11.7 million account records.
  • Leaked details could fuel convincing phishing messages.
  • Passwords on 196 accounts were changed without permission.
  • Use CAPCOM ID? Check your account and enable two-factor authentication.

Gamers are being warned to watch their inboxes after someone gained unauthorized access to Capcom’s online membership service.

Capcom, the Japanese video game developer and publisher behind Resident Evil, Monster Hunter, and Street Fighter, disclosed a breach affecting more than 11.7 million CAPCOM ID records worldwide.

The exposed information includes email addresses, account activity details, and IP addresses. A much smaller number of records also contained personal details such as dates of birth.

The company says credit card information was not affected, and it has not confirmed that passwords originally chosen by customers were compromised, but someone changed the passwords on 196 accounts without authorization. Capcom has since reset those passwords.

CAPCOM ID is the company’s unified account system for its websites and services, including online features in certain games. Users can also link it to gaming platform accounts, including PlayStation, Xbox, Steam, Epic Games, and Nintendo accounts.

For players, the exposed information could help scammers make fake Capcom messages more convincing, potentially tricking them into handing over passwords or verification codes.

Capcom discovered the incident on October 19, and says it has addressed the attack method. Games and services remain available, and the company plans to notify affected customers.

The 11.7 million figure refers to affected records, so it may not represent that many individual users. Capcom is still investigating the impact, including how the passwords on 196 accounts were changed without permission and whether any other unauthorized activity occurred on those accounts.

How to stay safe

As with any breach, watch for phishing messages, particularly those using the breach to create urgency. If an email claims your account needs attention, open your browser and go to cid.capcom.com independently to check it. Capcom warns users not to follow URLs or open attachments in suspicious messages.

You can also take these steps:

  • Enable CAPCOM ID’s two-factor authentication: This adds an authenticator-app code to the sign-in process, helping protect your account if someone obtains your password. Set it up from your Account page using a smartphone or tablet. Capcom recommends Google Authenticator or Microsoft Authenticator.
  • Check your account, especially if you received an unexpected password-change notice: Review your registered information and linked platform accounts from your Account page. If you cannot sign in, use Forgot your password? on the login page. See Capcom’s support page for instructions.
  • Use official support channels if you need help: Find the appropriate regional contact in Capcom’s breach notice, rather than trusting contact details in an unexpected message.

Pro tip: Unsure whether a message is a scam? Malwarebytes’ Scam Guard can help you assess it and suggest what to do next.


Something feel off? Check it before you click.  

Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.  

Available with Malwarebytes Premium Security for all your devices, and in the Malwarebytes app for iOS and Android.  

Try it free → 

Crime Stoppers chapter freezes tips after breach breaks anonymity promise

23 October 2026 at 11:57

A breach exposed personal information in supposedly anonymous crime reports. Now one Crime Stoppers chapter has stopped accepting tips because it cannot guarantee anonymity.

Toronto Crime Stoppers, which works with the community, police, and media to help solve crimes, has paused phone, website, and app submissions while it seeks a safer system.

The breach occurred in March and involved P3 Global Intel, the Texas-based tip-management platform owned by Navigate360. Its software is used by Crime Stoppers programs and other organizations in the US and elsewhere.

An October CBC investigation revealed the Canadian impact: More than 1.5 million tips spanning 25 years were exposed, with over 850,000 containing personal information. That included addresses, phone numbers, email addresses, and some banking details associated with rewards. The exposed details belonged to tipsters, people named in allegations, and others, including police and Crime Stoppers staff.

Following CBC’s reporting, Toronto Crime Stoppers acknowledged that its promise of anonymity had been broken for some users. The organization stopped accepting tips, saying it could no longer guarantee users’ anonymity.

In an October 21 statement, the organization says identifying details are normally removed before tips reach investigators, but some original submissions containing potentially identifying information were stolen from P3.

For affected tipsters, exposure could create a risk of retaliation, intimidation, or extortion. Scammers could also use details of a genuine tip to make an approach more convincing.

Unfortunately, the pause removes a reporting option for people afraid to approach police. Toronto police still accept reports directly, but warn that those channels are not anonymous.

How to stay safe

Toronto Crime Stoppers warned people worried about exposure to watch for impersonators. It says it will never contact them first to request a tip number, password, or other information.

The statement did not describe an individual notification process or offer a way to check whether a particular tip was affected. For anyone wanting to submit a new tip, the organization’s message was clear:

“Until we have a safer way to protect you, please do not send us tips by phone, online, or through the app.”

Anyone in immediate danger should call 911. During the pause, non-emergency reports in Toronto should go directly to Toronto police, with the understanding that those channels are not anonymous.

If you use a different Crime Stoppers program, check its official website for updates and advice about its reporting system.

For more general advice if your information may have been exposed, read our blog “Involved in a data breach? Here’s what you need to know.”


What do cybercriminals know about you?

Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.

Woman faces years in prison over a Cash App account she says she never opened

22 October 2026 at 13:27

A Cash App account opened in her name has left Amanda Smith facing criminal charges and potentially up to six years in prison.

404 Media reports that Smith says someone used her Social Security number (SSN) and date of birth to create an account that received money from a Facebook Marketplace scam.

Allegedly, a buyer sent $1,000 for items that weren’t really for sale. A scammer had taken over someone else’s Facebook account and directed the buyer to pay a Cash App account in Smith’s name.

Investigators obtained account information from Block, Cash App’s parent company. That information included Smith’s Social Security number and date of birth. Police subsequently arrested her in Pennsylvania over the alleged crime in Arkansas, a state she says she had never visited.

She spent three nights in jail. But 404 Media’s review of account records found that several account details, including the address and network used, did not match her own.

Smith also described a frustrating obstacle when she tried to investigate:

“Cash App refused to provide me with any information about the account, because I couldn’t prove that I was the owner.”

The account was associated with her closely enough to contribute to her arrest, yet she said she could not get information directly from the company. She later received account records through the criminal case.

It’s a disturbing reminder that the consequences of identity theft can go well beyond an unfamiliar charge on your bank statement. You could also find yourself accused of a crime committed using your details.


Breaches happen every day. Don’t be the last to know.


Smith suspects that information exposed in a data breach may have been used to impersonate her. When investigating, 404 Media found the phone number used for the account linked to an Amanda Smith in older breach data. They also found someone made a Venmo account using the same phone number but under another name entirely.

The source of her Social Security number and date of birth hasn’t been established, and her case is ongoing. Her experience highlights why it matters to know which of your details have been exposed.

How to protect yourself

The practical lesson is to look beyond the headline that a company “lost customer data.” What matters is which information was exposed, because different exposures call for different responses. Our guide for how to handle being involved in a data breach recommends checking the affected company’s official information before deciding what to do next.

The steps depend on the type of data that was stolen or leaked:

  • Email addresses and phone numbers: Be alert for phishing messages and scam calls, including messages that refer to the breach.
  • Passwords: Change the affected password and anywhere else you reused it. Enable multifactor authentication where available.
  • Payment or banking details: Contact the relevant financial institution and review your accounts for unauthorized activity.
  • Social Security numbers and other identifying information: Check your credit reports for unfamiliar accounts. In the US, you can freeze your credit for free with each of the three major credit bureaus: Equifax, Experian, and TransUnion. This helps prevent new credit accounts being opened in your name, but does not prevent every type of identity misuse.

If you discover an account opened in your name, contact the company’s fraud department through its official website and report the identity theft (in the US you can do that at IdentityTheft.gov). Keep copies of your reports and correspondence, and ask for written confirmation when the fraudulent account is closed.

A breach-checking service can help you identify known exposures linked to your information. Malwarebytes’ Digital Footprint Scan, for example, checks for exposures associated with your email address.


What do cybercriminals know about you?

Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.

Hackers steal protective order and foster care records from Arizona courts

30 September 2026 at 17:29

“Arizona’s court system was targeted by a cyber attack from criminal hackers or their bots.”

This is how the Arizona Supreme Court announced that hackers had attacked the state’s court system and stolen the personal information of “many Arizonans.”

The court says the attack began with a phishing email containing a malicious link that a court employee clicked. The attackers copied sensitive backup files containing records related to protective orders and foster care cases.

The court says it has no evidence, so far, that information about jurors, witnesses, or court employees was included in the copied files. It has not identified the attackers or a motive. It says the case is under investigation with the FBI, and no ransomware group has publicly claimed responsibility.

In an update, the court revealed that the attackers copied more than 150,000 recommendation reports created by Arizona’s Foster Care Review Board. The reports cover current and past cases involving children’s care and protection, dating back to 2010.

Those documents can include information about children, names of involved parties, case materials considered by the board, findings, and recommendations for courts, parents, and the Arizona Department of Child Safety. The court says the reports do not contain contact information such as addresses or telephone numbers.

The copied files were backups stored in a highly compressed format, kept for recovery after ransomware and other destructive incidents.

Information associated with protective orders can raise particularly serious safety and privacy concerns. These orders can protect people from abuse, harassment, or threats. Even where some records are public, combining names, case details, locations, and other sensitive context could create risks for people who are trying to limit their exposure to an abusive or threatening individual.


Breaches happen every day. Don’t be the last to know.


The court currently says it has no evidence that the information has been shared. As with many breach investigations, however, this can change as investigators determine exactly what was taken and monitor for publication, sale, or misuse of the data.

Arizona has about 8,000 children currently in foster care, according to the court. It is contacting people believed to have been affected.

What to do if you’re affected

  • Check the court’s advice. Every breach is different, so check its dedicated webpage for updates and follow any specific advice it offers.
  • Watch out for impersonators. Cybercriminals may contact you posing as the Arizona Supreme Court, another government agency, or someone you know. Verify anyone who contacts you through a separate, trusted channel.
  • Take your time. Phishing attacks often impersonate people or brands you know and pressure you to act urgently, using themes such as missed deliveries, account suspensions, and security alerts.
  • Get an early warning if your information appears on the dark web. If you’ve been notified that your information was copied in the Arizona court breach, identity monitoring can help you watch for signs of exposure and get support if you become a victim of identity theft.

Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

FBI agents’ blood tests and doctors’ notes surface after breach

28 September 2026 at 11:28

BBC News reports it has seen samples of stolen FBI agents’ medical examinations. The “fitness-for-work” reports identify FBI agents by name and address, and reveal even more personal details. They include blood and urine test results and doctors’ notes mentioning high cholesterol, blood in the urine, and even a shellfish and banana allergy.

As we reported last week, extortion group ShinyHunters claims to have breached the FBI. After reportedly taking over ransomware group Clop’s leak site, ShinyHunters says it attacked the FBI to punish the agency for spreading what it calls false information about the group.

The BBC’s findings raise the stakes: The alleged theft includes highly sensitive medical records, not just staff identity and contact data. ShinyHunters shared samples with journalists as proof of its claims.

The BBC states:

“The samples shared with journalists appear genuine and include names, addresses, phone numbers, badge numbers, job titles and information about spouses.”

ShinyHunters claims it accessed several systems, including FBI MedLink, which stores medical records, and FBI BEAST, which handles background checks on employees and applicants, but the FBI has not confirmed these claims. The FBI has acknowledged an incident affecting FBIJobs-related systems and says it is investigating whether its own environment or a third-party provider was compromised.

The group’s stated demand remains non-financial: It wants the FBI to retract or remove a May advisory that ShinyHunters calls false and defamatory. It says it will release the data within five days if its demands are not met.

The cybercriminals also raised the number of affected people. ShinyHunters nows claims to hold sensitive information on around 60,000 current and former FBI staff. Medical histories could make affected people vulnerable long after the immediate incident: Unlike a stolen password, a medical record cannot be changed.

What to do if you’re affected

The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:

  • Check the FBI’s advice. Every breach is different, so check FBI.gov for updates and follow any specific advice it offers.
  • Change your password. If you have an FBI Jobs account and reuse its password elsewhere, change it on those other accounts. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
  • Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
  • Watch out for impersonators. Cybercriminals may contact you posing as the FBI, another government agency, or someone you know. Verify the identity of anyone who contacts you.
  • Take your time. Phishing attacks often impersonate people or brands you know and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
  • Set up identity monitoring. This can alert you if your personal information is found being traded illegally online and help you recover afterward.

Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 
ShinyHunters claims FBI breach was revenge for “false” report

23 September 2026 at 14:03

Extortion group ShinyHunters is not afraid to make enemies. Now it claims to have breached the FBI.

After reportedly taking over ransomware group Clop’s leak site, ShinyHunters says it attacked the FBI to punish the agency for spreading what it calls false information about the group.

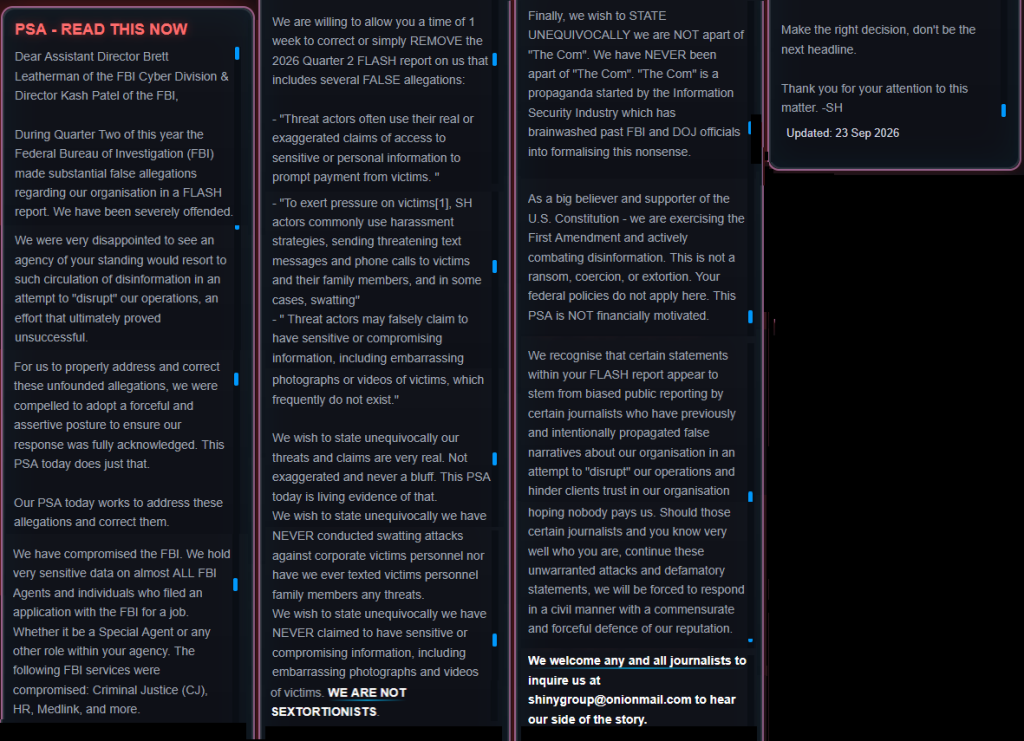
In a very long post on its leak site, the group outlines its grievances:

ShinyHunters PSA

“PSA – READ THIS NOW

Dear Assistant Director Brett Leatherman of the FBI Cyber Division & Director Kash Patel of the FBI,

During Quarter Two of this year the Federal Bureau of Investigation (FBI) made substantial false allegations regarding our organisation in a FLASH report. We have been severely offended.

We were very disappointed to see an agency of your standing would resort to such circulation of disinformation in an attempt to “disrupt” our operations, an effort that ultimately proved unsuccessful.

For us to properly address and correct these unfounded allegations, we were compelled to adopt a forceful and assertive posture to ensure our response was fully acknowledged. This PSA today does just that.

Our PSA today works to address these allegations and correct them.

We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job. Whether it be a Special Agent or any other role within your agency. The following FBI services were compromised: Criminal Justice (CJ), HR, Medlink, and more.

We are willing to allow you a time of 1 week to correct or simply REMOVE the 2026 Quarter 2 FLASH report on us that includes several FALSE allegations:

  • “Threat actors often use their real or exaggerated claims of access to sensitive or personal information to prompt payment from victims.”
  • “To exert pressure on victims[1], SH actors commonly use harassment strategies, sending threatening text messages and phone calls to victims and their family members, and in some cases, swatting”
  • “Threat actors may falsely claim to have sensitive or compromising information, including embarrassing photographs or videos of victims, which frequently do not exist.”

We wish to state unequivocally our threats and claims are very real. Not exaggerated and never a bluff. This PSA today is living evidence of that.

We wish to state unequivocally we have NEVER conducted swatting attacks against corporate victims personnel nor have we ever texted victims personnel family members any threats.

We wish to state unequivocally we have NEVER claimed to have sensitive or compromising information, including embarrassing photographs and videos of victims. WE ARE NOT SEXTORTIONISTS.

Finally, we wish to STATE UNEQUIVOCALLY we are NOT apart of “The Com”. We have NEVER been apart of “The Com”. “The Com” is a propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalising this nonsense.

As a big believer and supporter of the U.S. Constitution – we are exercising the First Amendment and actively combating disinformation. This is not a ransom, coercion, or extortion. Your federal policies do not apply here. This PSA is NOT financially motivated.

We recognise that certain statements within your FLASH report appear to stem from biased public reporting by certain journalists who have previously and intentionally propagated false narratives about our organisation in an attempt to “disrupt” our operations and hinder clients trust in our organisation hoping nobody pays us. Should those certain journalists and you know very well who you are, continue these unwarranted attacks and defamatory statements, we will be forced to respond in a civil manner with a commensurate and forceful defence of our reputation.

We welcome any and all journalists to inquire us at shinygroup@onionmail[.]com to hear our side of the story.

Make the right decision, don’t be the next headline.

Thank you for your attention to this matter. -SH

Updated: 23 Sep 2026“

The post is essentially a hostile “correction notice” directed at FBI leaders Brett Leatherman and Kash Patel. Its central grievance is an FBI advisory that says ShinyHunters commonly harasses victims and their families, including through threatening messages, phone calls, and, in some cases, swatting.

It also warns that threat actors may exaggerate their access to personal information or falsely claim to possess compromising photos or videos. The advisory does not use the word “sextortion,” but ShinyHunters appears to have interpreted the reference to compromising material that way. The group denies much of the FBI’s account while simultaneously using coercive language of its own.

The document it appears to mean is the FBI/IC3 public advisory “ShinyHunters: Cyber Criminal Group Attacks Learning Management System,” issued on May 15, 2026. Despite ShinyHunters calling it a “2026 Quarter 2 FLASH report,” the publicly accessible document is labeled a Public Service Announcement (PSA), not a FLASH.

The picture may have been further confused by a sextortionist who pretended to be ShinyHunters. ShinyHunters declares:

“WE ARE NOT SEXTORTIONISTS.”

It also denies carrying out swatting attacks or sending threatening messages to the family members of people working for its corporate victims.

The group also denies being part of The Com, a decentralized network linked to cybercrime and violence. It calls that connection:

“propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalizing this nonsense.”

The group then threatens journalists it accuses of spreading these “false narratives.”

The most worrying part of the message is the group’s claim that it stole sensitive data on:

“almost ALL FBI Agents, and ​individuals who filed an application with the FBI for a job.”

According to 404 Media, ShinyHunters provided a sample containing information on roughly 5,000 FBI agents, including names, home addresses, phone numbers, and details about their spouses. The publication reportedly verified portions of the sample, but the full dataset and the wider claims about the breach have not been independently confirmed.

The group also reportedly defaced the FBI’s jobs website. The FBI says it is aware of claims involving unauthorized activity affecting FBIjobs.gov and is investigating, although “broken” does not necessarily mean “breached.”

What to do if you’re affected

The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:

  • Check the FBI’s advice. Every breach is different, so check FBI.gov for updates and follow any specific advice it offers.
  • Change your password. If you have an FBI Jobs account and reuse its password elsewhere, change it on those other accounts. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
  • Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
  • Watch out for impersonators. Cybercriminals may contact you posing as the FBI, another government agency, or someone you know. Verify the identity of anyone who contacts you.
  • Take your time. Phishing attacks often impersonate people or brands you know and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
  • Set up identity monitoring. This can alert you if your personal information is found being traded illegally online and help you recover afterward.

Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 
Revolut gave customer IDs and financial data to a government impostor

14 September 2026 at 13:15

Revolut has acknowledged that it disclosed sensitive customer records to an unauthorized party. The company had accepted fraudulent information requests sent from an email address on a legitimate government agency domain, according to TechCrunch.

Revolut is a London-based banking and financial platform with more than 80 million customers globally, according to the company.

Revolut describes this as an external impersonation scam, not an intrusion into its systems. It also says customer funds were not affected. Revolut has not identified the government agency or disclosed its email domain.

The attacker appears to have abused the trust attached to a real government email domain to make bogus requests for customer information. Revolut detected the activity, blocked the sending address, and says it notified the relevant agency, law enforcement, data protection authorities, and financial regulators.

“Upon detection, we immediately blocked the address and alerted the relevant government agency as well as enforcement agencies, data protection, and financial regulators.”

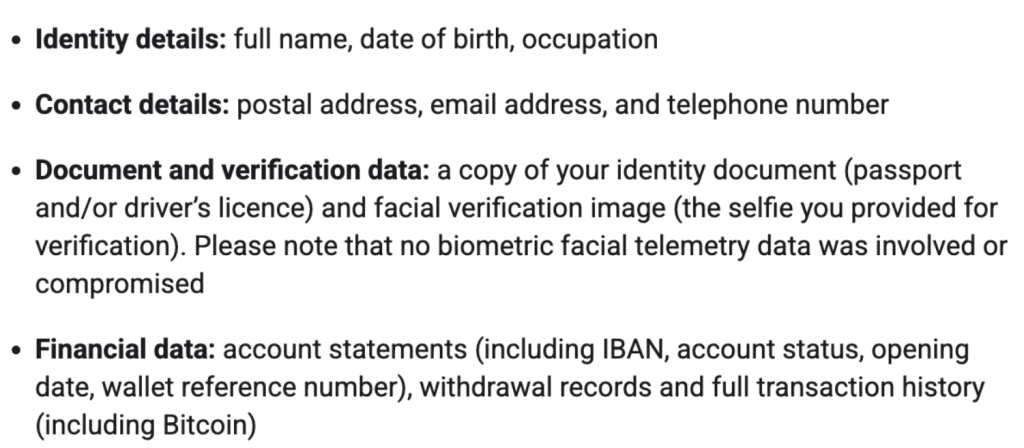
Through this social engineering attack, rather than by gaining access to Revolut’s systems, the criminals obtained the following types of information about customers:

  • Identity and contact information like dates of birth, postal address, email address, and phone number.
  • Copies of IDs such as passports and driver’s licenses.
  • Verification selfies.
  • Account statements and transaction histories.

Revolut has said only that a “limited” or “very limited” number of customers were affected, and that it contacted them directly.

Those customers have received or will receive an email specifying which of their personal data was disclosed:

Affected Revolut customers will be told what type of data was disclosed.

How to stay safe

The likely consumer impact will be second-stage fraud attempts rather than immediate unauthorized transfers. Here are some guidelines to help keep your money safe:

Treat any unexpected Revolut-related contact as suspicious, especially calls, emails, WhatsApp messages, or text messages claiming you need to “secure” an account, reverse a transfer, or replace documents. Do not use links or phone numbers supplied in the message. Revolut advises ending contact with suspected scammers and contacting the company through official channels.

IDs and other exposed information could be used for identity theft. Monitor your accounts and credit reports for unfamiliar account openings or credit applications, and consider placing a fraud alert or using credit monitoring where available in your country.

If you received a notification email, check your balances, cards, beneficiaries, recent transfers, account statements, and linked devices. Report any unfamiliar activity immediately through Revolut’s secure in-app chat.

If you were involved in a data breach, read our blog Involved in a data breach? Here’s what you need to know for more recommendations. 

Pro tip: Use Malwarebytes Scam Guard to analyze any suspicious communications. It can help you determine whether a message is a scam and advise you on what to do next.


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

24 billion stolen records exposed online. Here’s what to do

17 June 2026 at 12:56

A newly discovered database containing 24 billion stolen records is a reminder that personal information from data breaches, phishing campaigns, and infostealer infections continues to circulate online.

The collection was exposed on the internet before being taken offline. While researchers can’t confirm exactly whose information was included, the discovery is a good opportunity to check whether your email addresses, passwords, or other personal data have already been exposed.

What happened?

Researchers at Cybernews found a publicly exposed database holding more than 8.3 TB of data.

The data, consisting of 24 billion credential records, reportedly came from 36 sources, including numerous Telegram channels, prior breach compilations, collections of infostealer logs, and some datasets apparently exported directly from live servers.

Because the data came from different sources there are some differences in what the records contain and how they are organized.

Some records were structured infostealer logs containing usernames, email addresses, and plaintext passwords, and the associated login URL. Infostealers are a type of malware designed to steal sensitive information from infected devices, such as your home computer.

An infostealer log from a single infected device can include passwords stored across all browsers, active session cookies and tokens (including those that bypass multi-factor authentication), autofill data, device fingerprints, and sometimes crypto wallets or messaging accounts. The complete bundle is what ends up in logs such as those seen by the Cybernews researchers.

Roughly 1.7 billion of the records came from hacking-related Telegram channels, mainly English and Russian, including at least one that was focused on stolen credit card data.

The exposed database was hosted on an Elasticsearch cluster. Elasticsearch is a tool used to quickly store and search lots of data. If an Elasticsearch server lacks passwords, authentication, or network restrictions, it can be accessed by anyone who finds it online. Without protections such as passwords or a firewall, anyone can read, copy, change, or even delete its data.

Other documents in the dataset contained information about known vulnerabilities, articles about breaches, and social media posts about cyberattacks. This suggests the owner actively monitors security news and vulnerabilities and enriches the credential hoard with fresh breach information, either for a commercial “monitoring” service or for offensive use.

A few years ago, we wrote about what was called the “mother of all breaches,” where the source of the dataset was later identified as data breach search engine Leak-Lookup.

This newly discovered 24 billion record exposure is in the same league as that previous mega‑dump, but appears more heavily weighted toward fresh infostealer logs, rather than older, static breach data.

Since the data was taken out of public view soon after the discovery, the researchers were unable to fully retrace everything they had found or determine how many duplicate records it contained. That’s reassuring because it reduces the chances of cybercriminals finding the database, but reused passwords may still put accounts at risk. And we still don’t know the purpose for the data collection in the first place.

What to do now

It’s good to be aware of how much information about you is out there and who’s gathering it, but it’s even more important to know exactly which information they have, since that is what they can use against you.

1. Check if your data has been exposed online using our Digital Footprint Portal.

2. If you discover exposed passwords, change them immediately and make sure you aren’t reusing the same password across multiple accounts. Prioritize updating your important accounts such as email, banking, shopping, and social media accounts.

3. Turn on multi-factor authentication (MFA) wherever possible, since it can help protect accounts even if a password has been exposed.

How to protect your data

Infostealers often spread through malicious ads, fake browser updates, and one-click downloads. Avoid clicking sponsored ads, and instead visit official websites directly. Download software only from trusted sources such as official vendor sites or app stores.

Another increasingly popular technique is ClickFix, a social engineering attack that tricks users into infecting their own devices. Never run commands or scripts copied from websites, emails, or messages unless you trust the source and understand what they do.

Pirated software, game cheats, cracked tools, and shady browser extensions remain common sources of infostealer infections. Stick to reputable software and extensions, and be wary of anything asking for excessive permissions.

Lastly, phishing emails are still a major threat. Be cautious of unexpected attachments, links, and urgent requests. If you’re unsure whether a message is legitimate, verify it through the company’s official website rather than the link in the message.

You can also use Malwarebytes Scam Guard to check individual messages. Just upload a screenshot and we’ll let you know if it’s a scam.


Breaches happen every day. Don’t be the last to know.


Cardiac patients’ medical data stolen and held to ransom

16 June 2026 at 14:49

Cardiac monitoring provider iRhythm has been hit by a data theft followed by an extortion attempt.

In a filing with the Securities and Exchange Commission (SEC), iRhythm revealed it was contacted by someone on June 9 who claimed to have stolen sensitive information, including proprietary data, patient PHI, and other personal information. That person demanded payment in exchange for not publishing the data.

iRhythm provides ambulatory cardiac monitoring and analysis (for example using the Zio patch) and has reportedly processed over two billion hours of heartbeat data from more than twelve million patients.

In the filing, the company said the data was obtained through social engineering and is from “certain third-party-hosted business applications”, without revealing any further details about the amount of data.

On its own website, iRhythm also doesn’t disclose much about the nature of the stolen data, but does seem to imply no financial data was affected:

“We have not identified any impact to our products, our clinical or medical device systems, our connections to customers, our manufacturing and distribution operations, patient safety, or our ability to meet patient needs. In addition, we do not store or retain individual financial account information or payment card information. 

 As we actively investigate, we will notify individuals affected by this incident in accordance with applicable law and take steps as needed to protect and remediate the impact to them.“

However, the SEC filing adds that iRhythm determined that the incident is significant, “in light of the volume of the potentially affected data.” Together with the extortionist’s claims that they have patients’ medical data, that makes the breach one worth noting if you have used iRhythm’s services.

Even without payment data, healthcare breaches have serious downstream effects:

  • Attackers can craft highly convincing emails, texts, or calls that reference specific procedures or monitoring episodes (for example, “about your recent Zio patch recording”) to trick patients into sharing more data or paying fake bills.
  • The breached data can be used to create a fake identity, insurance fraud, or medical identity theft.
  • Exposure of cardiac and other health‑related information can be deeply sensitive and may have employment/insurance ramifications, especially if data is posted publicly or sold to data brokers.

Healthcare breach data tends to circulate for years, and victims may face sporadic fraud and phishing attempts long after the headlines fade.

How to stay safe

If you’ve used iRhythm’s services, keep an eye on your post, email, and patient portals for official breach notifications from iRhythm or your healthcare provider.

In the US, breaches of protected health information that meet certain criteria must be reported to patients and regulators. iRhythm has promised to “notify individuals affected by this incident in accordance with applicable law and take steps as needed to protect and remediate the impact to them.”

To stay out of the hands of phishers and scammers:

  • When you receive a communication about the data breach, verify through other channels that it really came from iRhythm. Go directly to iRhythm’s official website or patient portal, or call a known phone number to confirm the communication is genuine.
  • Be extra suspicious of emails or texts that claim to offer compensation, refunds, or other financial consequences related to this incident.
  • Change passwords for your iRhythm‑linked portals and your cardiology or hospital patient portals, especially if you reused those passwords elsewhere.
  • Log into your health insurer’s portal and check claims on a regular basis.
  • If you see anything suspicious, report it immediately to your insurer and provider and ask them to flag your account for possible identity theft.
  • Do not provide personal or financial information over the phone just because the caller knows details about you which they may have obtained from the stolen data.

Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 
VRChat says reported data breach never happened

11 June 2026 at 13:31

A data breach notice has been filed with the Maine Attorney General, saying more than 2.4 million users of VRChat have had their data breached.

The question is, was it VRChat who filed the breach notice, or did someone pretending to represent the company post it instead? On Reddit, a VRChat representative posted:

VRChat did not submit this Notice of Data Incident, and we have no reason to believe that our systems have been compromised. We are in the process of contacting the Maine Attorney General’s office to have this removed.

The breach notice states that VRChat experienced unauthorized access to some account data between May 10 and May 12, 2026. The access supposedly happened in VRChat’s cloud environment and involved user profile and login-related data.

According to the notice, the information exposed varied by account, but may have included:

  • VRChat username
  • Email address associated with the VRChat account
  • VRChat+ subscription status
  • Login history, including device information, hardware identifiers, and IP addresses

VRChat is a social platform designed primarily for virtual reality headsets, allowing users to interact with others through user-created 3D avatars and worlds. Users can access VRChat through Steam for PC, the Meta Quest Store, or as an Android app for compatible devices.

The notice states that no passwords or payment card data was exposed. However, even without passwords or card details, there are still potential risks when it comes to other breached data.

Phishing

Cybercriminals may use usernames and email addresses in targeted phishing attempts. For example, users may receive phishing emails or in‑platform messages claiming to be from “Support,” with fake security alerts or prompts to “confirm your age” via a malicious link.

Knowledge of subscription status could make scams more convincing. A scammer could send tailored lures like “billing issue with your subscription” or refund scams, which tend to have higher click-through rates among paying users.

Account takeover

Cybercriminals may combine usernames and email addresses from one breach with passwords stolen in other data breaches and try them against accounts. This technique, known as credential stuffing, takes advantage of people who reuse passwords across multiple sites.

Valuable accounts may then be sold to other players or used for scams.

Identity correlation

Steam and Meta user IDs linked to breached accounts can help cybercriminals connect identities across gaming and social platforms, especially if the same email or profile name is reused.

IP addresses, login history, device information, and other identifiers can also help build a more detailed advertising or tracking profile of a user.

How to stay safe

Whether or not the breach turns out to be an actual breach, here are some steps you can take to protect yourself:

First and foremost, be cautious of emails, texts, or calls claiming to come from VRChat or the gaming platforms you used it on, as cybercriminals often exploit breaches with phishing scams.

If you’ve used your VRChat password anywhere else, change those accounts immediately, and set up two-factor authentication (2FA) on your VRChat account if you haven’t already.

More general advice can be found in our article on what to do when you find out you’re involved in a data breach.

Update June 11, 2026: Article was updated to reflect VRChat’s post on Reddit.

Before publishing our original article, we tried to contact VRChat on two separate email addresses but received no meaningful response.


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

23andMe exposed genetic information of millions, lawsuit says

2 June 2026 at 11:53

California has sued the former shell of DNA testing company 23andMe over alleged security failures and misleading statements surrounding its 2023 data breach.

On May 27, 2026, Attorney General Rob Bonta filed suit in San Francisco Superior Court against Chrome Holding Co., the company now handling 23andMe’s remaining assets following its bankruptcy.

California’s complaint accuses 23andMe of failing to implement reasonable security measures to protect sensitive data and alleges violations of several state privacy and consumer protection laws. It also accuses the company of making misleading statements about its security practices.

The 2023 breach used old-school credential-stuffing tactics against 23andMe’s login page. Attackers operated inside the systems for roughly five months without anyone noticing. The direct compromise was modest, affecting about 14,000 accounts, but that was all the attackers needed to steal the data of just under seven million customers.

The intruders pivoted from those accounts through DNA Relatives, the platform’s headline feature, which enabled people to determine who they were connected with through DNA similarity. The lawsuit alleges a critical coding error in that feature enabled the perpetrators to scrape data from millions of other users connected by biological kinship.

The victim-blaming defense became evidence

After the breach went public, 23andMe sent victims’ legal representatives a letter blaming users for reusing passwords from sites that had been compromised earlier. The exposed data, the company suggested, had been shared of the users’ own free will and would not cause “pecuniary harm.”

The harms stemming from genetic data theft extend far beyond financial losses, however. The genetic information that was stolen enabled thieves to determine an individual’s genetic origins.

The data was reportedly offered for sale on the dark web with this information as a selling point, enabling sellers to offer records on Asian American Pacific Islander (AAPI) or Jewish customers, for example. Bonta’s office pointed out that antisemitic violence was on the rise at the time.

In spite of the letter’s attempt to blame users, only about 14,000 accounts were directly compromised through password reuse. The rest of the data was allegedly exposed through 23andMe’s own product. According to the complaint, the coding error in DNA Relatives exposed the data of anyone who had opted into the service, not just those linked to the 14,000 compromised accounts.

Can the state recover damages?

California is seeking statutory penalties ranging from $1,000 to $7,500 per violation. With 855,541 Californians among the affected users, the costs could mount up quickly.

The question is how much of it the state will collect if it wins its case. 23andMe filed for Chapter 11 bankruptcy in March 2025, then sold most of its assets, including the genomic data of more than 15 million customers, to TTAM Research Institute, a nonprofit founded by former 23andMe CEO Anne Wojcicki. California and several other states opposed the sale on Genetic Information Privacy Act grounds, but a federal bankruptcy judge approved it. The states are now appealing that decision.

Chrome Holding Co., the corporate shell that remains of 23andMe, received $305 million from that sale. But others have already been picking over what’s left.

Other regulators have already had their turn. The UK Information Commissioner’s Office fined 23andMe £2.31 million in June last year following a joint investigation with the Privacy Commissioner of Canada. A federal court initially approved a $30 million class-action settlement covering most US customer claims. That settlement later grew to $50 million and received final approval in January 2026.

What customers can do

If you tested with 23andMe, the standard breach hygiene still applies. Reset any password you reused on other sites and turn on multi-factor authentication wherever it’s offered. Credential stuffing only works on usernames and passwords that have already been exposed elsewhere. Also watch for phishing attacks that name-drop 23andMe or the breach itself. And maybe weigh the benefits of using DNA testing services against the security risks.

Because there’s one part of this that no fine and no settlement can solve: stolen genetic data sold on the dark web cannot be taken back. Passwords can be changed. DNA can’t.


Browse like no one’s watching. 

Malwarebytes Privacy VPN encrypts your connection and never logs what you do, so the next story you read doesn’t have to feel personal. Try it free → 

Carnival confirms data breach impacting nearly 6 million

28 May 2026 at 14:04

Carnival Corporation, parent of Carnival Cruise Line, is sending out fresh “Notice of Cybersecurity Event” letters dated May 27, 2026. If you feel like you’ve read that sentence before, you’re not imagining things. Over the last decade, the world’s largest cruise operator has accumulated a worrying track record of breaches, ransomware incidents, and regulatory penalties, with this 2026 incident adding yet another entry to an already lengthy cybersecurity history.

There are several data breaches involving Carnival Corporation or one of its subsidiaries in our database.

Between 2019 and 2021 alone, Carnival reported four separate cybersecurity events to the New York Department of Financial Services. These included two ransomware attacks and a phishing incident in which attackers deployed malware, accessed and encrypted internal systems, and stole personal customer and employee information.

In this latest case, an attacker used social engineering to trick a Carnival employee into granting access to part of the company’s IT systems on April 14, 2026. By April 22, they used a compromised account to access a “limited portion” of Carnival’s IT systems, where they were able to copy personal data before being blocked.

According to the data breach notice filed in Maine, a total of 5,995,277 people were affected. Carnival determined that the intruder had illegally copied files containing personal information and is now writing to affected individuals to tell them that “data elements” relating to them were obtained.

Researchers cited by Gblock say the stolen data appears to include:

  • Full names
  • Email addresses
  • Dates of birth
  • Genders
  • Mariner Society membership status and tier
  • Internal customer identifiers

The template letter does not list specific data fields. Instead, it uses a placeholder:

“We have determined that your <<data elements>> were obtained.”

This strongly suggests that Carnival is populating each letter with data categories relevant to that particular individual, a common pattern in large breaches where people may have provided different information at different times.

Furthermore, the letters contain the usual content about the speed with which the company acted, involving third‑party experts, and frame the affected systems as a limited subset of the environment. For recipients, the important fact is not how limited the breach was from the company’s point of view, but whether the exposed information could be used for identity theft, fraud, or highly convincing phishing attacks.


Breaches happen every day. Don’t be the last to know.


We do know from past Carnival incidents that exposed data has included names, addresses, dates of birth, passport numbers, health information, and payment details. In previous breaches affecting cruise lines, compromised data has ranged from basic contact details to Social Security numbers and credit card information. Carnival has not publicly disclosed the full categories of data involved in the 2026 incident, but given that this 2026 event again involves “personal information” copied from internal systems, it is reasonable to treat it as a serious privacy incident, even if the exact mix of data varies per person.

The attack was claimed by extortion group ShinyHunters, which is known to steal data and then ask for a ransom. If the victim does not agree to the terms, the data will be published and/or sold to the highest bidder.

ShinyHunters offers Carnival data for download

From a cybercriminal’s perspective, cruise industry data is highly prized. Cruise passengers are often relatively wealthy, and passenger records can combine identity data (names, addresses, dates of birth, passport numbers), contact data (emails, phone numbers), and potentially payment data (card numbers and sometimes bank details), making them valuable for identity theft, targeted phishing, and fraud.

What to do if you’re affected

To mitigate the fallout, Carnival is offering a complimentary 24‑month TransUnion credit‑monitoring package, delivered via the MyTrueIdentity platform and supported by Cyberscout for fraud assistance.

Be cautious of emails, texts, or calls claiming to come from Carnival or credit-monitoring providers, as cybercriminals often exploit breaches with phishing scams. Read our advice on what to do when you find out you’re involved in a data breach.


What do cybercriminals know about you?

Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.

Biometrics, diagnoses, and bank details exposed in major healthcare breach

19 May 2026 at 17:56

NYC Health + Hospitals (NYC H+H) posted a data breach notice about a months‑long breach via a third‑party vendor that exposed highly sensitive patient and employee data for at least 1.8 million people, including medical records, government IDs, geolocation data, and even fingerprint and palm‑print biometrics.

NYC H+H detected suspicious activity on February 2, 2026, and later confirmed that an unauthorized actor had access to parts of its network from roughly late November 2025 through February 2026.

During this window, attackers copied files containing personal, medical, financial, and biometric information. The incident was reported to the US Department of Health and Human Services (HHS) on March 24, 2026, and currently affects at least 1.8 million individuals, making it one of the largest healthcare breaches of 2026 so far.

HHS filing

NYC H+H attributes the intrusion to a breach at an unnamed third‑party vendor that had access to its systems. This fits the current pattern of supply-chain compromises, where a vendor becomes the entry point for attackers to gain access to their clients’ systems or data.

Incidents like these are a textbook example of how deeply personal health data can fuel long‑term fraud, stalkerware‑like abuse, and permanent privacy loss.


Digital Footprint Scan

See if your personal data has been exposed.


Types of data

According to NYC H+H’s notice and related write‑ups, the exposed dataset is unusually broad and detailed.

We can divide the data into three distinct layers:

  • Classical PII, which can be combined with other leaked datasets: Full names and contact details. Government‑issued identifiers, including Social Security Numbers, driver’s license and passport numbers, other government ID numbers, taxpayer IDs, and IRS identity protection PINs. The breach also exposed billing and payment records, plus bank and card data, which can be used for direct financial theft and highly convincing social engineering.
  • Medical and insurance data: Detailed diagnoses, medication lists, and test results expose conditions people may have kept private from employers, family, or insurers, enabling blackmail, targeted scams, and discrimination. Insurance and claims data can be abused to submit fraudulent claims, redirect reimbursements, or impersonate existing identities in healthcare systems.
  • Biometrics: These are at least as sensitive as medical history because they tend to stay with you for life. They are not easy to erase or replace. Once compromised, large biometric databases become long‑term liabilities for everyone who relies on them as trustworthy identifiers.

Unfortunately, this is part of a broader pattern. The FBI’s Internet Crime Complaint Center (IC3) reports that healthcare was the most targeted critical infrastructure sector for ransomware in 2025, with 460 ransomware incidents and 182 reported healthcare data breaches.

The Change Healthcare ransomware attack alone exposed medical and billing data for more than 190 million Americans, highlighting how a single healthcare intermediary can disrupt an entire system.

What to do if you’re involved

If you’ve interacted with NYC Health + Hospitals, there’s a possibility your personal information could be affected.

NYC Health + Hospitals is making identity theft prevention and mitigation services, including credit monitoring, available through Kroll Information Assurance, LLC for a period of 24 months at no cost to all individuals who have worked for or been a patient of NYC Health + Hospitals. For more details check its data breach notice.

If you think you’ve been affected by a data breach, here are steps you can take to protect yourself:

  • Check the company’s advice. Every breach is different, so check with the company to find out what’s happened and follow any specific advice it offers.
  • Change your password. You can make a stolen password useless to thieves by changing it. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
  • Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
  • Watch out for impersonators. The criminals may contact you posing as the breached platform. Check the official website to see if it’s contacting victims and verify the identity of anyone who contacts you using a different communication channel.
  • Take your time. Phishing attacks often impersonate people or brands you know, and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
  • Consider not storing your card details. It’s definitely more convenient to let sites remember your card details, but it increases risk if a retailer suffers a breach.
  • Set up identity monitoring, which alerts you if your personal information is found being traded illegally online and helps you recover after.

Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

1 in 8 employees have sold company logins or know someone who has

12 May 2026 at 11:21

UK anti-fraud non-profit Cifas just published research that should bother anyone who runs a business, or buys from one: One in eight workers at large enterprises have either sold their company login credentials or know someone who did.

The internet is awash with compromised credentials that employees use to access company systems. Threat intelligence company KELA tracked nearly 2.9 billion compromised credentials globally in 2025. Most of these come from phishing attacks and infostealers. But thanks to employees wanting to make a quick buck, cyber criminals can just make people an offer.

The insiders nobody’s watching

Cifas interviewed 2,000 employees of companies with at least 1,000 staff. Of these, 13% admitted to selling their corporate access credentials in the last 12 months, or knowing someone who did. Amazingly, as the report says, the sellers did so “often under the belief it’s harmless.”

Newsflash: Selling your account credentials isn’t harmless. Criminals want them so they can take over the account and do nefarious things with it. Account takeovers in the US surged 6% to over 78,000 last year, according to Verizon.

Many hijacked accounts are personal ones for services ranging from social media to online streaming sites, and of course bank accounts. But many others are accounts for business systems like Microsoft 365, Salesforce, and other platforms that hold sensitive company data. Those secrets are valuable commodities for criminals who can then trade them on the open market.

Your boss is more likely to sell than you

Ideally, this is where a common technique called “least-privilege access” should come in.

The idea is that a corporate online account should only have access to what it needs. So Jim in the canteen should have access to the food ordering system, but not to the entire customer database. That way, even if Jim’s account gets compromised, the worst the attackers could do is deprive you of sausages tomorrow.

The problem is that, according to the report, higher-ups are even more comfortable selling their account credentials than low-level employees. Thirty-two percent of senior managers find it justifiable, along with 36% of directors, 43% of C-suite executives, and, stunningly, four in five business owners. Their roles mean that even with least-privilege access, their accounts can still open routes to sensitive system functions and data.

This isn’t just a UK problem

The Cifas research is UK-specific, but that’s likely not where it ends. We’ve seen employees at several companies selling access to either company accounts or records. For example, cryptocurrency company Coinbase revealed last year that employees at a Bangladesh-based outsourcing company sold customer records to hackers.

Compromised credentials are widespread. Our own research found that in a single 30-day window, 111 Fortune 500 companies had employee credentials leaked. Long-term, 363 of those firms (that’s 73%) have lost control of at least one employee credential.

Employees selling their access credentials isn’t just bad for the companies that employ them. It’s also bad for customers.

When a director’s password goes up for sale, a customer file might not be far behind, although it likely won’t be the director selling it. Malwarebytes found that 91% of Fortune 500 companies have had their customers’ credentials leaked, and hijacked accounts are a great way to get at them.

So insider risk isn’t just a corporate issue. It’s also a consumer one. That makes us less likely to hand over our personal information to large enterprises without questioning why they need it.


Your name, address, and phone number are probably already for sale.  

Data brokers collect and sell your personal details to anyone willing to pay. Malwarebytes Personal Data Remover finds them and gets your information removed, then keeps watch so it stays that way. 

ShinyHunters escalates Canvas attacks with school login defacements

8 May 2026 at 14:00

Days after confirming a major data breach, Instructure is now facing a second blow.

Earlier this week, Instructure confirmed a major data breach affecting its cloud‑hosted Canvas environment, with the ShinyHunters group claiming it stole hundreds of millions of records tied to thousands of schools and universities worldwide. As discussed in our earlier blog, that incident involved data such as student and staff records, enrollment details, and private messages allegedly accessed through Canvas export features and APIs. At that stage, the focus was on large‑scale data theft and the long‑term risks for affected students and families, including identity fraud and highly targeted phishing.

According to new reporting, ShinyHunters has now hit Instructure again, this time moving from quiet data theft to very visible extortion. Using another vulnerability in Instructure’s systems, the attackers were able to modify Canvas login portals for hundreds of educational institutions, defacing both web logins and the Canvas app with an on‑screen ransom message.

applying extra pressure
Image credit: vx-underground

The message both claimed responsibility for the earlier breach and set a deadline of May 12 for Instructure and affected schools to contact the gang or risk the public release of stolen data.

This second wave matters for two reasons. First, it confirms that ShinyHunters still has meaningful access to Instructure’s environment, or at least to components that control the look and behavior of school login pages. Second, it marks a clear escalation in pressure tactics, from leaked claims and dark web posts to messages shown directly to students, parents, and staff trying to access their courses.

How to deal with this data breach

For students and families, the practical advice from our original blog still applies:

  • Reset Canvas‑related passwords
  • Enable multi‑factor authentication where possible
  • Monitor financial and credit activity as children get older
  • Stay wary of highly personalized phishing that references real schools, courses, or teachers

For schools and districts, this latest extortion campaign underlines the need to coordinate closely with Instructure, review single sign-on (SSO) integrations, and prepare clear communications so that any future defacements or data leaks do not catch staff and parents by surprise.


CNET Editors' Choice Award 2026

“One of the best cybersecurity suites on the planet.” 

According to CNET. Read their review →


❌