Microsoft today pushed software updates to fix a staggering 167 security vulnerabilities in its Windows operating systems and related software, including a SharePoint Server zero-day and a publicly disclosed weakness in Windows Defender dubbed “BlueHammer.” Separately, Google Chrome fixed its fourth zero-day of 2026, and an emergency update for Adobe Reader nixes an actively exploited flaw that can lead to remote code execution.
Redmond warns that attackers are already targeting CVE-2026-32201, a vulnerability in Microsoft SharePoint Server that allows attackers to spoof trusted content or interfaces over a network.
Mike Walters, president and co-founder of Action1, said CVE-2026-32201 can be used to deceive employees, partners, or customers by presenting falsified information within trusted SharePoint environments.
“This CVE can enable phishing attacks, unauthorized data manipulation, or social engineering campaigns that lead to further compromise,” Walters said. “The presence of active exploitation significantly increases organizational risk.”
Microsoft also addressed BlueHammer (CVE-2026-33825), a privilege escalation bug in Windows Defender. According to BleepingComputer, the researcher who discovered the flaw published exploit code for it after notifying Microsoft and growing exasperated with their response. Will Dormann, senior principal vulnerability analyst at Tharros, says he confirmed that the public BlueHammer exploit code no longer works after installing today’s patches.
Satnam Narang, senior staff research engineer at Tenable, said April marks the second-biggest Patch Tuesday ever for Microsoft. Narang also said there are indications that a zero-day flaw Adobe patched in an emergency update on April 11 — CVE-2026-34621 — has seen active exploitation since at least November 2025.
Adam Barnett, lead software engineer at Rapid7, called the patch total from Microsoft today “a new record in that category” because it includes nearly 60 browser vulnerabilities. Barnett said it might be tempting to imagine that this sudden spike was tied to the buzz around the announcement a week ago today of Project Glasswing — a much-hyped but still unreleased new AI capability from Anthropic that is reportedly quite good at finding bugs in a vast array of software.
But he notes that Microsoft Edge is based on the Chromium engine, and the Chromium maintainers acknowledge a wide range of researchers for the vulnerabilities which Microsoft republished last Friday.
“A safe conclusion is that this increase in volume is driven by ever-expanding AI capabilities,” Barnett said. “We should expect to see further increases in vulnerability reporting volume as the impact of AI models extend further, both in terms of capability and availability.”
Finally, no matter what browser you use to surf the web, it’s important to completely close out and restart the browser periodically. This is really easy to put off (especially if you have a bajillion tabs open at any time) but it’s the only way to ensure that any available updates get installed. For example, a Google Chrome update released earlier this month fixed 21 security holes, including the high-severity zero-day flaw CVE-2026-5281.
For a clickable, per-patch breakdown, check out the SANS Internet Storm CenterPatch Tuesday roundup. Running into problems applying any of these updates? Leave a note about it in the comments below and there’s a decent chance someone here will pipe in with a solution.
Vannacht was het zover. Hackgroep Shinyhunters deelde de geclassificeerde informatie die zij wisten te stelen van Rockstar Games, de ontwikkelaar van Grand Theft Auto VI. Wie hoopte op een nieuwe trailer van de game, is waarschijnlijk teleurgesteld. Wel bracht de hack inzicht in hoe waanzinnig veel geld GTA Online nog oplevert.
At the core of every modern enterprise is a fundamental need: The ability to innovate across hybrid environments without sacrificing security. For over five years, Palo Alto Networks and Nutanix have partnered to meet this need, building a collaborative ecosystem where industry-leading infrastructure meets the world’s most comprehensive AI-powered security.
As we look toward the future of the enterprise at Nutanix .NEXT 2026, our focus remains on a shared vision for the "Secure Nutanix Cloud."
2026 Global Security Partner of the Year
We are deeply honored to be named the Nutanix 2026 Global Security Partner of the Year. This recognition reflects our commitment to delivering integrated, automated security that feels like a native part of the Nutanix experience. Together, we have helped thousands of joint customers move from reactive security to a proactive, zero trust posture that spans the data center, the edge and the public cloud.
The Existing Partnership Is the Foundation of Trust
Our partnership is built on the belief that security should be invisible, automated and inseparable from the infrastructure it protects. We’ve worked alongside Nutanix to enable enterprises to scale their hybrid multicloud, and their security posture scales with it. Current integrations provide zero trust protection across the Nutanix environment:
VM-Series Virtual Firewalls – Seamlessly integrated with Nutanix AHV and Flow Network Security, our virtual firewalls provide Layer 7 visibility and advanced threat prevention for east-west traffic. This integration leverages Nutanix Flow service chaining to automatically steer traffic through VM-Series firewalls for deep packet inspection without manual reconfiguration. It delivers full functional parity and operational continuity for Nutanix AHV environments, allowing security teams to maintain high-performance standards using familiar Panorama® management and persistent, tag-based policies that migrate with workloads across clusters.
Hybrid Cloud Security – We provide consistent security for Nutanix Cloud Clusters (NC2) on both AWS and Azure, enabling your policies to follow your workloads wherever they reside.
Automation & Orchestration – Leveraging the Panorama® plugin for Nutanix, teams can automate security provisioning and use Dynamic Address Groups to sync application attributes instantly.
New Integration Secures Nutanix Enterprise AI (NAI)
Building on this foundation, the highlight of this year’s show is our groundbreaking integration designed to accelerate Enterprise AI adoption. NAI provides a simplified, cloud-native stack that allows organizations to deploy and scale large language models (LLMs) across their choice of infrastructure with push-button simplicity. We are collaborating on a first-of-its-kind, end-to-end security solution for NAI.
This integration, launching soon, will bring AI Model Security and AI Red Teaming directly into the NAI, creating a seamless experience where security is built in, not bolted on. By allowing only Prisma AIRS™ validated models to reach production, we eliminate security friction at the start of the AI lifecycle. Every model will undergo rigorous scans for known vulnerabilities before deployment, providing a "clean room" environment for AI development. Providing a proactive test of AI defenses, Prisma AIRS AI Red Teaming will be available within NAI as an autonomous solution that integrates seamlessly into the development pipeline, utilizing a combination of a profiler and an attacker agent to perform contextual iterative simulations that mirror real-world attacker behavior. By providing detailed reports that map vulnerabilities directly to the OWASP Top 10 for LLMs and NIST AI RMF, it equips teams with the precise context needed to secure AI applications continuously and effectively.
By proactively identifying and neutralizing emerging threats, we will give organizations the confidence to deploy AI bravely, knowing their innovation is anchored in the world’s most robust security platform.
Powered by Prisma AIRS, this integration will bring a "security-first" approach to your AI deployments:
AI Model Security – Scans AI models during the download phase to block malicious code and hidden backdoors before they reach your environment.
AI Red Teaming – Provides continuous, autonomous vulnerability hunting on models, application and agent endpoints, testing your AI behavior against more than 750 real-world attack scenarios and contextual agentic risk assessment.
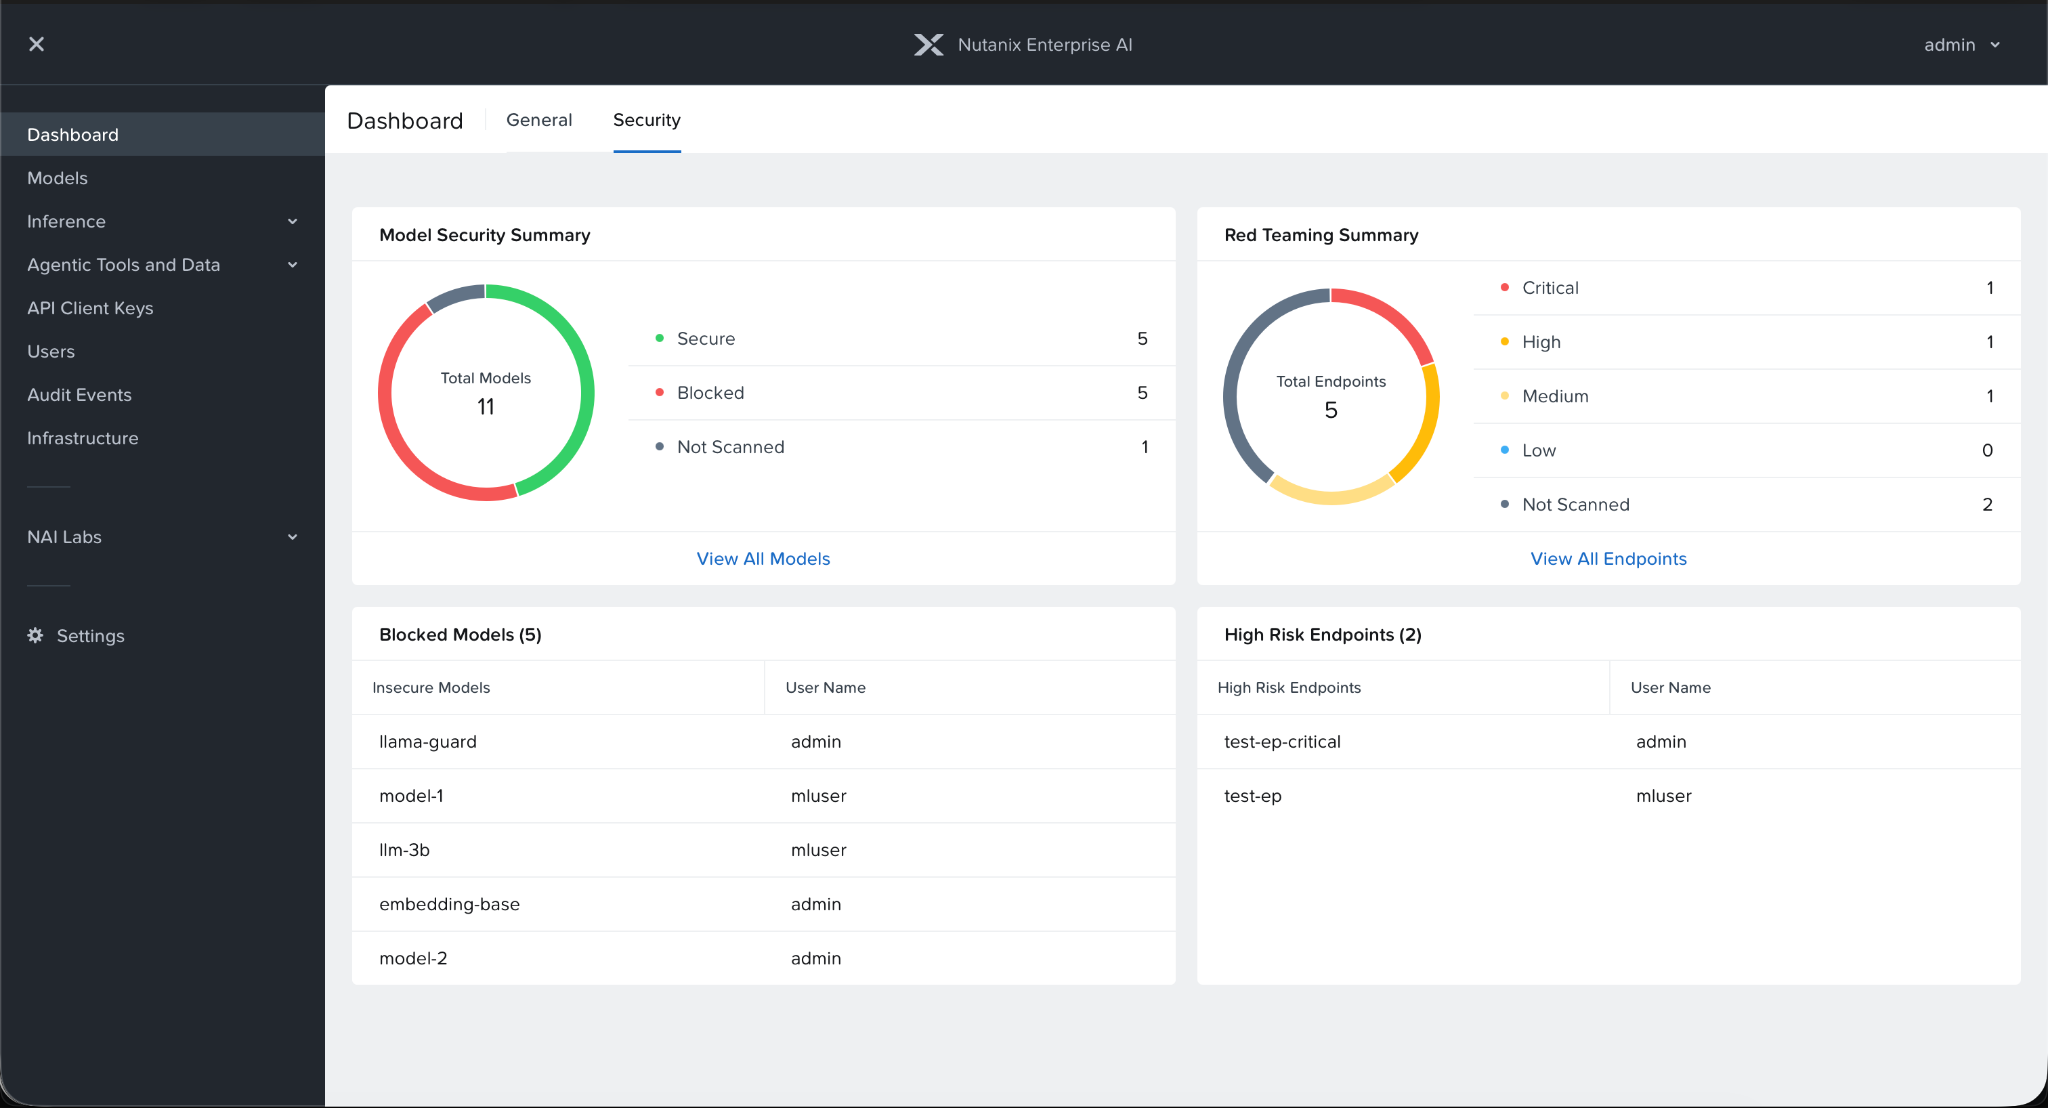
Unified Visibility – Provides a complete overview of your AI risk posture and scan summaries directly within your NAI dashboards.
Unified Security Dashboard with AI Model Security and AI Red Teaming
Benefits:
Seamless and Frictionless Deployment
We will prioritize a fast and frictionless deployment experience, ensuring that robust AI security does not come at the cost of development speed. By integrating these controls directly into the NAI workflow, organizations will be able to deploy and scale their AI initiatives with "push-button" simplicity, removing the traditional complexity and friction associated with securing large language models.
Proactive Protection Against Emerging Threats
Leveraging our deep expertise in threat prevention, this solution will proactively identify and block vulnerable or malicious models before they can impact the enterprise environment. By scanning models for hidden backdoors and malicious code during the initial download phase, we will stop threats at the perimeter, allowing only validated, secure models to ever reach your production environment.
A Comprehensive Enterprise Cloud AI Solution
This integration will deliver a comprehensive enterprise cloud AI solution, merging Nutanix’s industry-leading infrastructure with our next-generation security controls. The result will be a unified, cloud-native stack where security is built in rather than bolted on after the workload deployment, providing a secured deployment environment, which is consistent across the data center, the edge and public cloud.
Evolving Insights and Real-Time Remediation
The vulnerability insights from AI Red Teaming are coupled with remediation insights. The platform will provide a prioritized list of remediation steps that are tailor-made for the endpoint. This allows organizations to battle-test their inference endpoints before deploying them at scale.
Key Takeaways
A Proven, Award-Winning Partnership: Celebrating five years of collaboration, Palo Alto Networks has been named the Nutanix 2026 Global Security Partner of the Year, highlighting a shared commitment to delivering native, automated zero trust security for hybrid multicloud environments.
Seamless Zero Trust for Hybrid Workloads: Through deep integrations with VM-Series virtual firewalls and Nutanix Cloud Clusters (NC2), organizations can maintain consistent Layer 7 visibility and tag-based security policies that automatically follow workloads across on-premises data centers and public clouds.
Securing the AI Lifecycle with Prisma AIRS: The new integration with NAI, launching soon, will bring a security-first approach to AI adoption, utilizing Prisma AIRS to scan LLMs for vulnerabilities during download, and perform autonomous Red Teaming to neutralize emerging threats before they reach production.
Don’t Miss Our Speaking Session
Want to see the integration in action? Join our experts, Shrikant Brahmbhatt (Palo Alto Networks) and Ashwini Vasanth (Nutanix), on Tuesday April 7 3:30-4pm for an exclusive look at how we are securing the "Challenge of Hybrid AI." We’ll dive into the architecture that allows you to discover, assess and protect your entire AI ecosystem (apps, agents and models alike).
Visit Us at Booth #G2
Stop by the Palo Alto Networks booth (#G2) to meet our team of over 19,000 active threat researchers and see live demos of our joint solutions. Whether you are building the next generation of agentic AI or securing your virtual desktop infrastructure (VDI), we have the tools to help you innovate at machine speed.
This blog contains forward-looking statements that involve risks, uncertainties and assumptions, including, without limitation, statements regarding the benefits, impact, or performance or potential benefits, impact or performance of our products and technologies or future products and technologies. These forward-looking statements are not guarantees of future performance, and there are a significant number of factors that could cause actual results to differ materially from statements made in this blog, including, without limitation: developments and changes in general market, political, economic, and business conditions; risks associated with managing our growth; risks associated with new products and subscription and support offerings; shifts in priorities or delays in the development or release of new offerings, or the failure to timely develop, release and achieve market acceptance of new products and subscriptions as well as existing products and subscription and support offerings; failure of our business strategies; rapidly evolving technological developments in the market for security products and subscription and support offerings; our customers’ purchasing decisions and the length of sales cycles; our competition; our ability to attract and retain new customers; and our ability to acquire and integrate other companies, products, or technologies. We identify certain important risks and uncertainties that could affect our results and performance in our most recent Annual Report on Form 10-K, our most recent Quarterly Report on Form 10-Q, and our other filings with the U.S. Securities and Exchange Commission from time-to-time, each of which are available on our website at investors.paloaltonetworks.com and on the SEC's website at www.sec.gov. All forward-looking statements in this blog are based on information available to us as of the date hereof, and we do not assume any obligation to update the forward-looking statements provided to reflect events that occur or circumstances that exist after the date on which they were made.

 Login