❌

Reading view

Advancing Agentic AI Security with Palo Alto Networks and NVIDIA

AI is moving from answering questions to taking action. Agents can use tools, access enterprise data, and carry out work across systems on our behalf or autonomously. This creates opportunities for businesses to move faster, but it also changes what security must protect. An agent’s identity, the authority it carries, and the actions it takes all become security decisions.

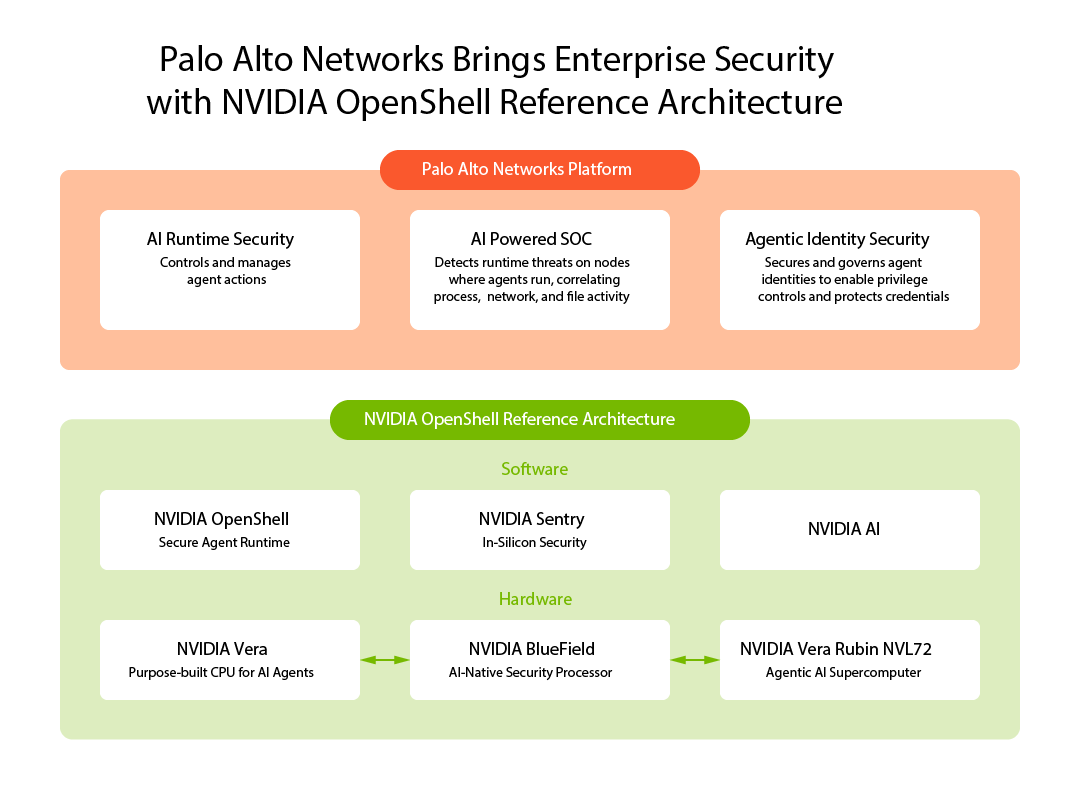
As enterprises put agents into production, they need controls that keep pace without hindering the work those agents are designed to do. Palo Alto Networks is working with NVIDIA to advance this goal across five connected areas in support of the NVIDIA OpenShell Reference Architecture for safe AI agents: an AI gateway on NVIDIA Vera CPU systems; runtime protection on NVIDIA BlueField DPUs; agent identity governance on NVIDIA Sentry; AI factory visibility through an AI-driven, agentic security operations center (SOC); and partner services that help customers implement a secure architecture.

Palo Alto Networks AI Runtime Security Extends Protection Across the AI Factory and Edge

Until now, the AI factory conversation has centered primarily on compute capacity and token generation. But as autonomous agents execute higher-stakes workloads, runtime security has become just as essential. Agents can be steered past their guardrails, and a compromised host cannot be trusted to accurately report what occurred. To be effective, security teams require visibility and enforcement that operate independently of the host environment.

Palo Alto Networks AI Runtime Security on NVIDIA BlueField DPUs isolates security processing in a dedicated infrastructure domain. Because BlueField sits in the path between agents and the models, data, and services they access, security policies are enforced in silicon — beyond the reach of a compromised host. This capability safeguards both GPU-accelerated AI workloads and CPU-based agent runtimes and is now generally available across AI factory and industrial edge deployments. Offloading security from the host node delivers two critical benefits: increased token throughput and stronger runtime protection across the entire AI factory.

Deployment at scale must be manageable. Our work with Spectro Cloud manages the deployment and operation of AI Runtime Security on BlueField DPUs, enabling consistent management across the AI factory infrastructure — from the data center to distributed edge environments. 
Idira Governs the Identity Behind Every Agent Action

Runtime protection answers what an agent is doing. Identity governance helps determine whether it is authorized to do it.

An agent may act for a person, a team, or an autonomous business process, often requiring access to multiple tools and data sources across the organization. Granting an agent broad, persistent access creates risk, while making access too restrictive limits its usefulness. To achieve the optimal balance of control and agent access, Palo Alto Networks is advancing an integration between agentic identity security and NVIDIA Sentry on BlueField — bringing identity and delegated authority closer to where agent interactions are governed.

The goal is to give each agent a verifiable identity, grant access appropriate to its task, and make its actions attributable. Once available, this solution will deliver zero-trust protection and tamper-resistant auditing for agents by moving the security controls — including identity — to the NVIDIA Bluefield DPU, separate from the host operating system. This addresses an immediate business need — enabling enterprises to scale agent deployments while retaining control over whose authority agents use and which resources they can reach.

Bringing AI Factory Signals into Cortex

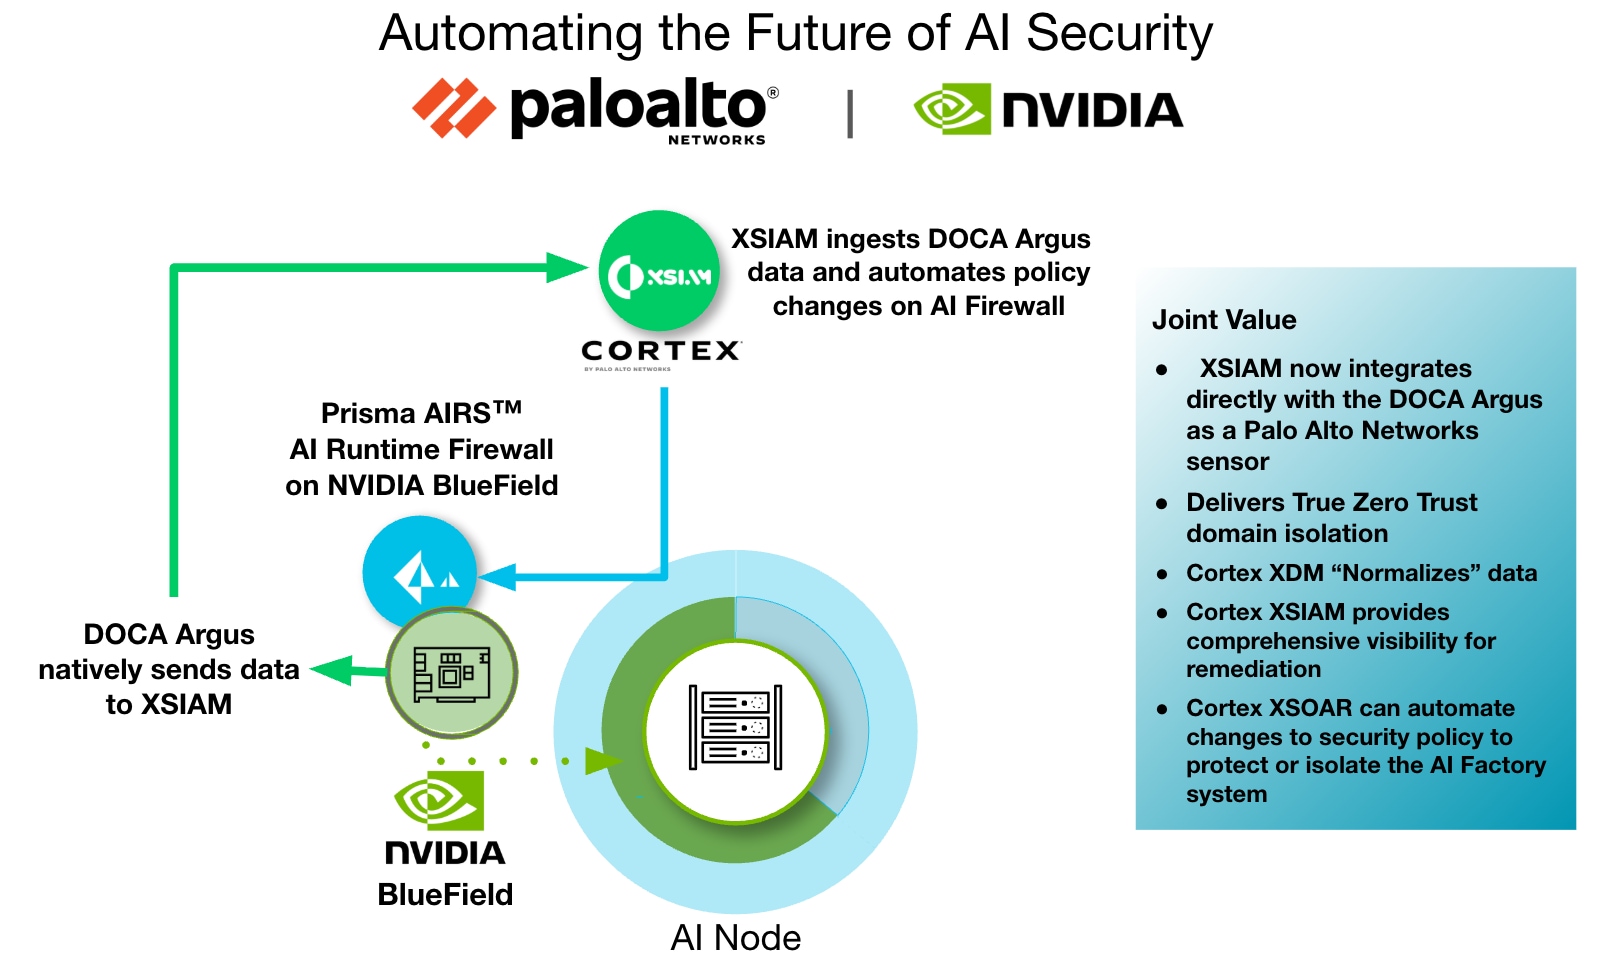
Security teams need visibility into activity across the infrastructure that runs AI agents. Palo Alto Networks has announced an integration of Cortex XSIAM with NVIDIA DOCA Argus, which monitors host activity from BlueField’s independent trust domain. This provides security operations teams with runtime signals that do not rely on an agent installed on the host being monitored.

By bringing those signals together with network, cloud, and identity data in an AI-driven SOC, security teams can investigate AI infrastructure in the context of the broader enterprise. Palo Alto Networks is continuing to develop this foundation to support broader fleet visibility and more comprehensive response workflows — enabling security teams to identify unusual activity and act with greater confidence as AI deployments grow.

AI agents run within the NVIDIA OpenShell secure runtime, operated directly on the NVIDIA Vera CPU within the NVIDIA OpenShell Platform. Security observability is completely offloaded to the NVIDIA BlueField DPU. Operating out-of-band, NVIDIA Sentry, built on DOCA Argus, provides real-time memory and network inspection to detect threats without slowing AI inference. When malicious events or policy violations occur, DOCA Argus streams high-fidelity alerts directly to Palo Alto Networks Cortex XSIAM, where they can be automatically correlated and surfaced for rapid threat response. 

Turning Secure AI Factory Designs into Deployments

Customers need more than an architecture diagram to bring an AI factory into production. They need a practical path to design, validate, and operate security across compute, networking, applications, and the SOC.

Palo Alto Networks is working with strategic vendors , including Deloitte and World Wide Technology (WWT), to help customers plan and deploy secure NVIDIA AI factories. Deloitte’s Silicon-to-Service (S2S) offering, combined with its Secure AI Foundations, helps organizations implement AI use cases on NVIDIA AI infrastructure through validated architectures and managed services. By building security into the full AI factory stack, Deloitte helps clients balance performance, safety, and cost as they scale from pilot to production.  

WWT’s AI Proving Ground allows customers to evaluate and test an integrated stack before committing to production deployment.These engagements can help enterprises move from individual security components to a repeatable approach tailored to their environments and requirements.

Building Confidence into the Next Phase of Agentic AI

The value of agentic AI depends on an enterprise’s ability to give agents useful access while maintaining control over their actions. This requires runtime protection, governed identities, independent visibility, and a unified way to manage controls across the enterprise. 

Palo Alto Networks delivers comprehensive security across every layer of the AI factory through a unified platform. In collaboration with NVIDIA, we support the NVIDIA OpenShell Reference Architecture for enterprise governance, isolation, and security.  Together, we deliver the continuous protection needed to move safely from AI agent pilots to full-scale enterprise production.

To learn more about the general availability of AI Runtime Security on the BlueField DPU, read our blog, Palo Alto Networks Announces Support for NVIDIA Enterprise AI Factory. 

The post Advancing Agentic AI Security with Palo Alto Networks and NVIDIA appeared first on Palo Alto Networks Blog.
  •  

Reinventing Security for the Agentic NVIDIA AI Factory

Building on the momentum of NVIDIA GTC Taipei at COMPUTEX  2026, the conversation has moved beyond AI experimentation to the industrialization of intelligence. Organizations are rapidly deploying AI Factories – high-performance, purpose-built computing infrastructures designed to manufacture intelligence at an unprecedented scale. AI’s next phase is agentic. Autonomous AI agents are reshaping enterprise operations—and demand security architectures that can keep pace with the speed and scale of innovation.  We are proud to announce the integration of Palo Alto Networks Cortex XSIAM with the NVIDIA DOCA Argus framework, a breakthrough that brings real-time, AI-powered security operations directly into the heart of the NVIDIA AI factory. 

By operating on the NVIDIA BlueField data processor, DOCA Argus provides situational awareness through real-time memory analysis at the silicon level. This allows Cortex XSIAM to detect kernel-level rootkits and "living-off-the-land" attacks without installing security agents on the host system.

This innovation builds upon our proven foundation with Palo Alto Networks Prisma AIRS, where AI Runtime Security is deployed natively on NVIDIA BlueField, and powered by NVIDIA DOCA, bringing defense in depth. This integration enables offload , isolation and acceleration of security in AI factories.  

Purpose-Built Observability for the AI Factory

Deployed consistently across the AI factory, DOCA Argus monitors and correlates AI application processes, network telemetry, and data access to detect sophisticated anomalies that traditional tools miss. With this integration, Cortex XSIAM recognizes the high-fidelity data from DOCA Argus as a native Palo Alto Networks sensor, allowing for better decisions with the new intelligence gathered directly from the host.

By integrating Cortex XSIAM with the NVIDIA DOCA Argus framework, we leverage the innovations of two industry leaders to deliver a seamless, high-performance SecOps ecosystem for your most valuable AI assets.

Why This Integration Is a Game-Changer for SecOps

  • Process Introspection: Residing on NVIDIA BlueField, DOCA Argus has the unique ability to correlate network telemetry with deep process inspection.
  • Anomaly Detection: By analyzing traffic and host behavior simultaneously, XSIAM can detect sophisticated anomalies (e.g., lateral movement or data exfiltration) that traditional tools miss.
  • Unified Intelligence: Cortex XSIAM recognizes the security and alert information in this high-fidelity data, providing security teams with end-to-end visibility and dedicated security dashboards specifically for their AI infrastructure.


Native integration of DOCA Argus with XSIAM


Palo Alto Networks Prisma AIRS Across the NVIDIA AI Factory

The inclusion of Prisma AIRS in NVIDIA AI Factory validated design delivers a unified security platform, providing proactive, defense-in-depth security across critical layers of the AI ecosystem. 

Serving as the network enforcement engine for this architecture, Prisma AIRS secures the infrastructure of the modern AI Factory. By unifying protection and visibility into a single automated fabric, it eliminates the traditional trade-off between security and agility, allowing organizations to innovate at machine speed without compromising performance or governance. 

Beyond enforcement, the broader Prisma AIRS platform acts as the security blueprint for the entire enterprise AI ecosystem—consolidating fragmented point-tools to slash total cost of ownership while providing end-to-end observability from the data plane to the model layer. The platform scales dynamically alongside your AI clusters to safeguard raw datasets, build Layer 7 micro-perimeters around autonomous agents, and protect proprietary model weights from external threats—all without throttling mission-critical performance.

By deploying the AI Runtime Firewall directly on NVIDIA BlueField, we establish a foundational network security layer that is fully offloaded, isolated, and accelerated. This provides pervasive protection across the Enterprise AI Factory without sacrificing critical compute resources.

Securing the NVIDIA AI factory requires the entire Prisma AIRS suite, which secures the AI lifecycle through five specialized pillars:

  • AI Model Security: Protects against model tampering, malicious scripts and data exfiltration attacks before deployment.
  • AI Red Teaming: Advanced threat simulation and vulnerability discovery to enable the safety, security and integrity of your AI and Agents deployments.
  • AI Runtime Security Firewall: Protects against prompt injection, data leakage, abuse and AI-specific runtime threats across distributed inference flows.
  • AI Agent Gateway acts as the control plane for the AI enterprise – governing tool calls, model access and external connections. Every agent interaction is enforced through centralized policies.
  • Agent Identity Security assigns each agent a governed identity with precise permissions and full traceability, ensuring actions are attributable and enforceable.


A Forward-Looking Architecture: Embracing Vera NVIDIA BlueField-4 STX

Looking ahead to the next frontier of enterprise-scale agentic AI, Palo Alto Networks is closely aligning its platform approach with the NVIDIA Vera BlueField-4 STX architecture, extending protections to AI data storage infrastructure. As AI data demands surge, high-throughput, large-scale environments require a move toward hardware-isolated, performance-neutral protection to support the rapid growth of critical AI applications.

Operating within an isolated trust domain on future BlueField-4 silicon, our inline security capabilities will maintain strict, policy-driven controls independently of the host operating system and storage systems. This co-design enables critical forward-looking innovations for data, agents, and context memory, ensuring security is offloaded, isolated and accelerated to support the next generation of the AI Factory.


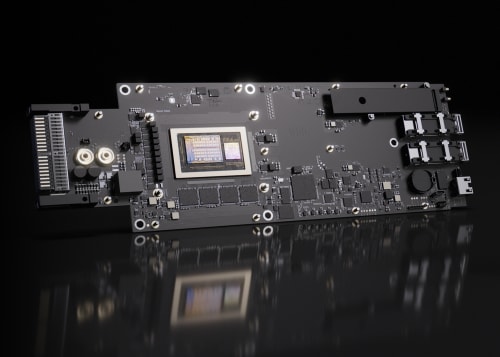
NVIDIA BlueField-4


Key Takeaways

Our ongoing collaboration with NVIDIA focuses on these essential pillars for reimagining AI security:

  • Deliver the industry-leading security platform reinvented for the unique demands of the AI factory. High-throughput, large-scale environments require a move toward hardware-isolated and performance-neutral protection to support the rapid growth of critical AI applications. By offloading AI Runtime Firewall directly to the NVIDIA BlueField, we enable zero-latency protection and strict data governance that neutralizes threats (like model theft) while maintaining peak performance and the integrity of your proprietary models.This architecture embeds security directly into the infrastructure, out of the way of app developers.
  • Transform the SOC and achieve deep visibility across AI environments by leveraging Cortex XSIAM to provide real-time detections and automated response. By connecting infrastructure protection with this centralized intelligence, you can secure the AI journey, from development in the factory to operations at the secure industrial edge.
  • Zero-Trust for AI Infrastructure: This helps ensure that as your operations scale toward multi-agent architectures, your security footprint is fully offloaded, isolated, and accelerated to protect advanced inference flows, autonomous agents, and data pipelines without throttling performance.
  • Unified Platform Architecture: Beyond standalone point tools, the Prisma AIRS platform serves as a unified security fabric that spans the entire AI lifecycle—from safeguarding raw data to autonomous agents.

Deploy Bravely

The Palo Alto Networks platform approach delivers a comprehensive solution to secure an enterprise's entire AI ecosystem. By integrating Cortex XSIAM with the NVIDIA DOCA Argus framework, we are extending this comprehensive, deep visibility and protection to the very heart of the AI Factory. With this integration, security teams can leverage an agentless approach via DOCA Argus to gain deep visibility into AI systems hosts by simply downloading the content pack from the Cortex Marketplace.

The Palo Alto Networks platform secures the entire AI journey, protecting the infrastructure, intelligent applications, agents and data it produces. With the inclusion of Prisma AIRS in NVIDIA Enterprise AI Factory Validated Design, we have delivered the blueprint for secure AI. 

Palo Alto Networks and NVIDIA are redefining security for the AI factory. Together, we are ensuring your security architecture is as fast, scalable and innovative as the intelligence it protects, empowering you to scale AI production with reduced latency and stronger governance.

Discover more through the Palo Alto Networks partner directory, or read the official press release from NVIDIA for more details.

The post Reinventing Security for the Agentic NVIDIA AI Factory appeared first on Palo Alto Networks Blog.
  •  

Palo Alto Networks at Nutanix .NEXT 2026

Securing the AI-Powered Hybrid Multicloud

At the core of every modern enterprise is a fundamental need: The ability to innovate across hybrid environments without sacrificing security. For over five years, Palo Alto Networks and Nutanix have partnered to meet this need, building a collaborative ecosystem where industry-leading infrastructure meets the world’s most comprehensive AI-powered security.

As we look toward the future of the enterprise at Nutanix .NEXT 2026, our focus remains on a shared vision for the "Secure Nutanix Cloud."

2026 Global Security Partner of the Year

We are deeply honored to be named the Nutanix 2026 Global Security Partner of the Year. This recognition reflects our commitment to delivering integrated, automated security that feels like a native part of the Nutanix experience. Together, we have helped thousands of joint customers move from reactive security to a proactive, zero trust posture that spans the data center, the edge and the public cloud.

The Existing Partnership Is the Foundation of Trust

Our partnership is built on the belief that security should be invisible, automated and inseparable from the infrastructure it protects. We’ve worked alongside Nutanix to enable enterprises to scale their hybrid multicloud, and their security posture scales with it. Current integrations provide zero trust protection across the Nutanix environment:

  • VM-Series Virtual Firewalls – Seamlessly integrated with Nutanix AHV and Flow Network Security, our virtual firewalls provide Layer 7 visibility and advanced threat prevention for east-west traffic. This integration leverages Nutanix Flow service chaining to automatically steer traffic through VM-Series firewalls for deep packet inspection without manual reconfiguration. It delivers full functional parity and operational continuity for Nutanix AHV environments, allowing security teams to maintain high-performance standards using familiar Panorama® management and persistent, tag-based policies that migrate with workloads across clusters.
  • Hybrid Cloud Security – We provide consistent security for Nutanix Cloud Clusters (NC2) on both AWS and Azure, enabling your policies to follow your workloads wherever they reside.
  • Automation & Orchestration – Leveraging the Panorama® plugin for Nutanix, teams can automate security provisioning and use Dynamic Address Groups to sync application attributes instantly.

New Integration Secures Nutanix Enterprise AI (NAI)

Building on this foundation, the highlight of this year’s show is our groundbreaking integration designed to accelerate Enterprise AI adoption. NAI provides a simplified, cloud-native stack that allows organizations to deploy and scale large language models (LLMs) across their choice of infrastructure with push-button simplicity. We are collaborating on a first-of-its-kind, end-to-end security solution for NAI.

This integration, launching soon, will bring AI Model Security and AI Red Teaming directly into the NAI, creating a seamless experience where security is built in, not bolted on. By allowing only Prisma AIRS™ validated models to reach production, we eliminate security friction at the start of the AI lifecycle. Every model will undergo rigorous scans for known vulnerabilities before deployment, providing a "clean room" environment for AI development. Providing a proactive test of AI defenses, Prisma AIRS AI Red Teaming will be available within NAI as an autonomous solution that integrates seamlessly into the development pipeline, utilizing a combination of a profiler and an attacker agent to perform contextual iterative simulations that mirror real-world attacker behavior. By providing detailed reports that map vulnerabilities directly to the OWASP Top 10 for LLMs and NIST AI RMF, it equips teams with the precise context needed to secure AI applications continuously and effectively.

By proactively identifying and neutralizing emerging threats, we will give organizations the confidence to deploy AI bravely, knowing their innovation is anchored in the world’s most robust security platform.

Powered by Prisma AIRS, this integration will bring a "security-first" approach to your AI deployments:

  • AI Model Security – Scans AI models during the download phase to block malicious code and hidden backdoors before they reach your environment.
  • AI Red Teaming – Provides continuous, autonomous vulnerability hunting on models, application and agent endpoints, testing your AI behavior against more than 750 real-world attack scenarios and contextual agentic risk assessment.
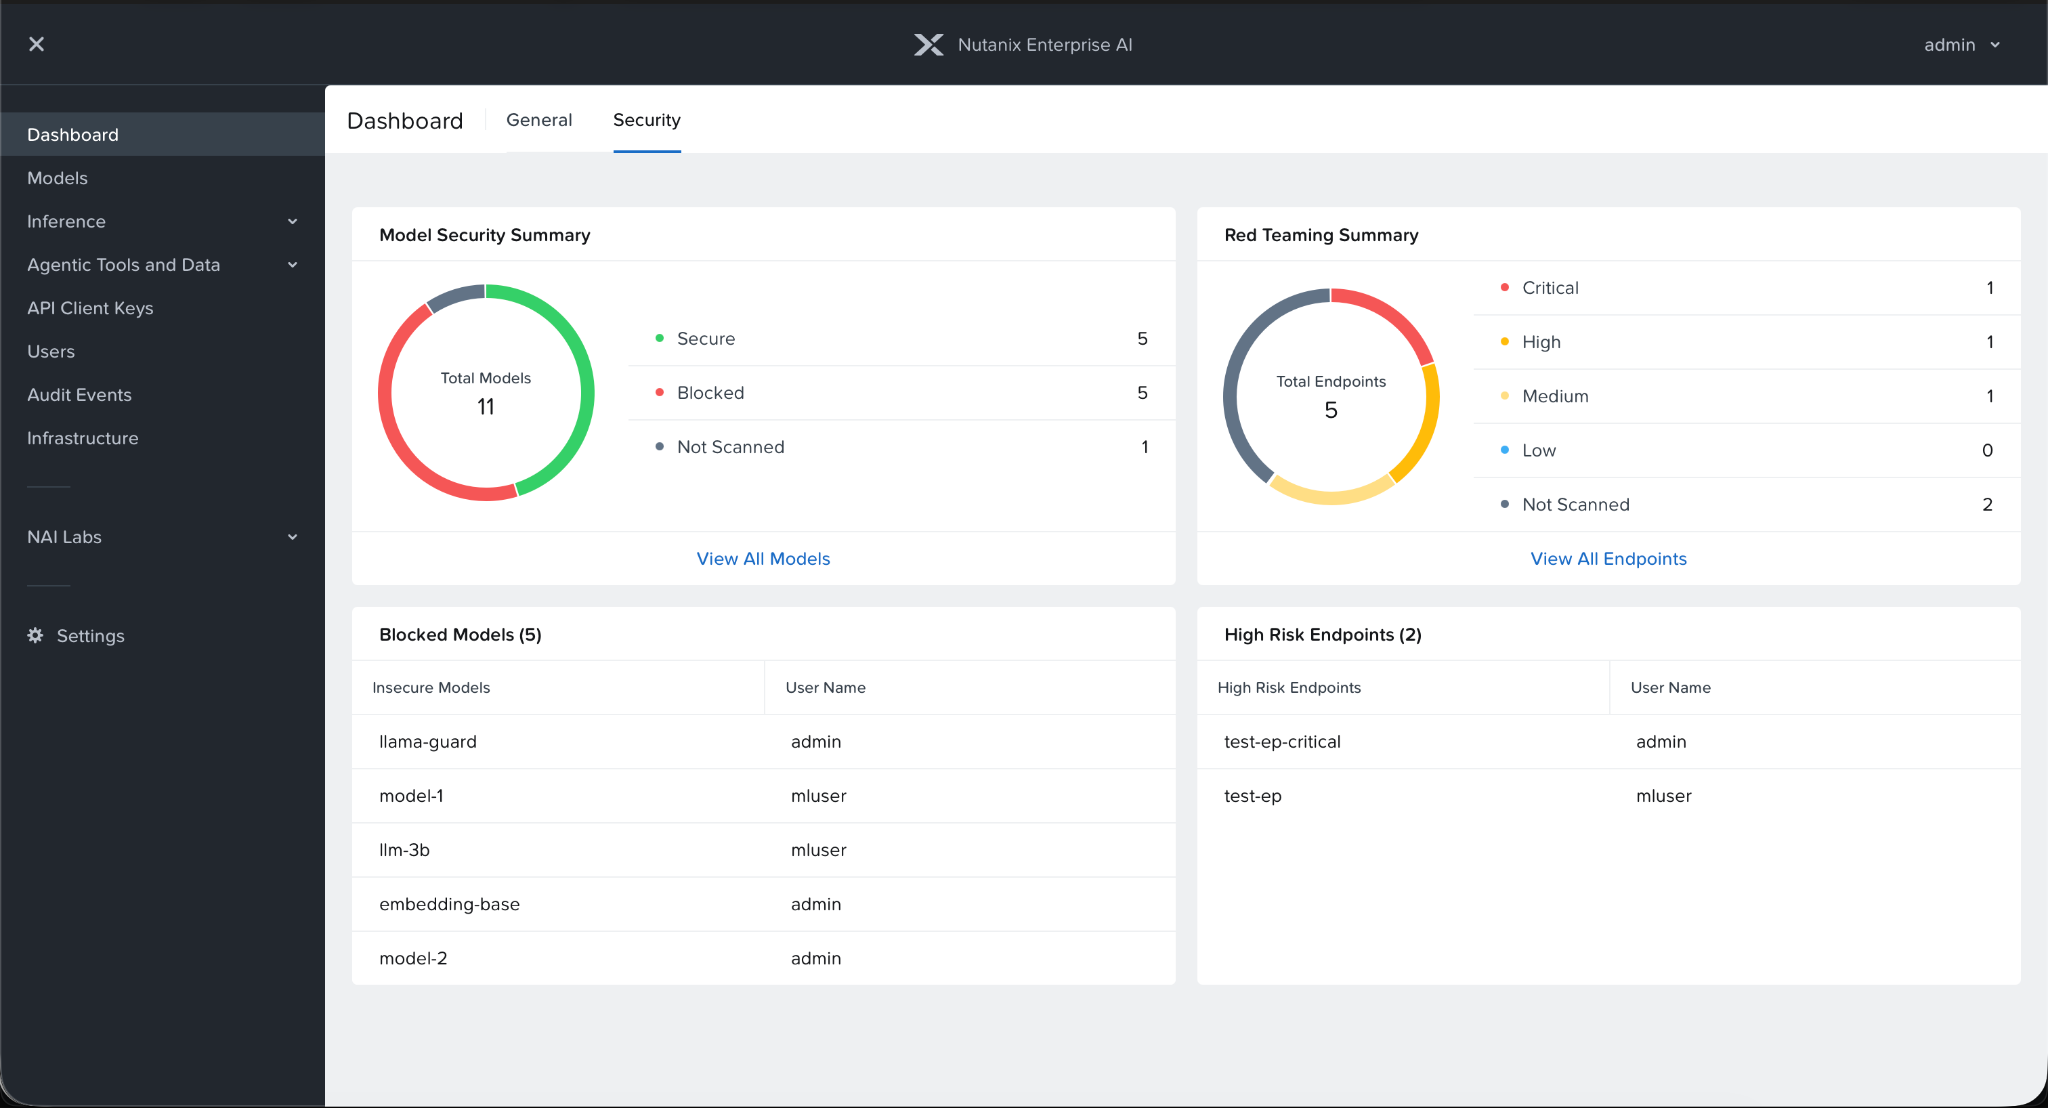
  • Unified Visibility – Provides a complete overview of your AI risk posture and scan summaries directly within your NAI dashboards.
Screenshot of Nutanix Enterprise AI dashboard.
Unified Security Dashboard with AI Model Security and AI Red Teaming

Benefits:

Seamless and Frictionless Deployment

We will prioritize a fast and frictionless deployment experience, ensuring that robust AI security does not come at the cost of development speed. By integrating these controls directly into the NAI workflow, organizations will be able to deploy and scale their AI initiatives with "push-button" simplicity, removing the traditional complexity and friction associated with securing large language models.

Proactive Protection Against Emerging Threats

Leveraging our deep expertise in threat prevention, this solution will proactively identify and block vulnerable or malicious models before they can impact the enterprise environment. By scanning models for hidden backdoors and malicious code during the initial download phase, we will stop threats at the perimeter, allowing only validated, secure models to ever reach your production environment.

A Comprehensive Enterprise Cloud AI Solution

This integration will deliver a comprehensive enterprise cloud AI solution, merging Nutanix’s industry-leading infrastructure with our next-generation security controls. The result will be a unified, cloud-native stack where security is built in rather than bolted on after the workload deployment, providing a secured deployment environment, which is consistent across the data center, the edge and public cloud.

Evolving Insights and Real-Time Remediation

The vulnerability insights from AI Red Teaming are coupled with remediation insights. The platform will provide a prioritized list of remediation steps that are tailor-made for the endpoint. This allows organizations to battle-test their inference endpoints before deploying them at scale.

Key Takeaways

  • A Proven, Award-Winning Partnership: Celebrating five years of collaboration, Palo Alto Networks has been named the Nutanix 2026 Global Security Partner of the Year, highlighting a shared commitment to delivering native, automated zero trust security for hybrid multicloud environments.
  • Seamless Zero Trust for Hybrid Workloads: Through deep integrations with VM-Series virtual firewalls and Nutanix Cloud Clusters (NC2), organizations can maintain consistent Layer 7 visibility and tag-based security policies that automatically follow workloads across on-premises data centers and public clouds.
  • Securing the AI Lifecycle with Prisma AIRS: The new integration with NAI, launching soon, will bring a security-first approach to AI adoption, utilizing Prisma AIRS to scan LLMs for vulnerabilities during download, and perform autonomous Red Teaming to neutralize emerging threats before they reach production.

Don’t Miss Our Speaking Session

Want to see the integration in action? Join our experts, Shrikant Brahmbhatt (Palo Alto Networks) and Ashwini Vasanth (Nutanix), on Tuesday April 7 3:30-4pm for an exclusive look at how we are securing the "Challenge of Hybrid AI." We’ll dive into the architecture that allows you to discover, assess and protect your entire AI ecosystem (apps, agents and models alike).

Visit Us at Booth #G2

Stop by the Palo Alto Networks booth (#G2) to meet our team of over 19,000 active threat researchers and see live demos of our joint solutions. Whether you are building the next generation of agentic AI or securing your virtual desktop infrastructure (VDI), we have the tools to help you innovate at machine speed.

Ready to secure your journey? Visit the Palo Alto Networks partner directory or learn more about Prisma AIRS.

Forward-Looking Statements

This blog contains forward-looking statements that involve risks, uncertainties and assumptions, including, without limitation, statements regarding the benefits, impact, or performance or potential benefits, impact or performance of our products and technologies or future products and technologies. These forward-looking statements are not guarantees of future performance, and there are a significant number of factors that could cause actual results to differ materially from statements made in this blog, including, without limitation: developments and changes in general market, political, economic, and business conditions; risks associated with managing our growth; risks associated with new products and subscription and support offerings; shifts in priorities or delays in the development or release of new offerings, or the failure to timely develop, release and achieve market acceptance of new products and subscriptions as well as existing products and subscription and support offerings; failure of our business strategies; rapidly evolving technological developments in the market for security products and subscription and support offerings; our customers’ purchasing decisions and the length of sales cycles; our competition; our ability to attract and retain new customers; and our ability to acquire and integrate other companies, products, or technologies. We identify certain important risks and uncertainties that could affect our results and performance in our most recent Annual Report on Form 10-K, our most recent Quarterly Report on Form 10-Q, and our other filings with the U.S. Securities and Exchange Commission from time-to-time, each of which are available on our website at investors.paloaltonetworks.com and on the SEC's website at www.sec.gov. All forward-looking statements in this blog are based on information available to us as of the date hereof, and we do not assume any obligation to update the forward-looking statements provided to reflect events that occur or circumstances that exist after the date on which they were made.

The post Palo Alto Networks at Nutanix .NEXT 2026 appeared first on Palo Alto Networks Blog.
  •  
❌