 Login

Malicious npm Packages That Evade Defenses
This is an impressive piece of malware. Its sophistication says nation-state to me, but there is no direct evidence and certainly no attribution.

This is an impressive piece of malware. Its sophistication says nation-state to me, but there is no direct evidence and certainly no attribution.
Cybersecurity is in the middle of a generational shift. AI has disrupted a 30-year balance of power between defenders and adversaries.
Armed with agentic AI tools and open-weight models stripped of safety guardrails, threat actors are discovering, validating, and chaining exposures at machine speed. In a recent Unit 42 investigation, the attacker used more than 50 MITRE ATT&CK techniques to reduce weeks of methodical intrusion tradecraft into less than 10 hours—97% faster than a skilled red team could have done. Time-to-exfiltration has compressed to under an hour in real-world attacks. And when new CVEs are publicly disclosed, automated adversary scanners are weaponizing them within 15 minutes.
Defending at human speed is no longer viable. Organizations must close years of accumulated exposure while securing the AI they are rapidly adopting. That demands action on five fronts: continuously find and fix vulnerabilities, reduce exposure, secure AI infrastructure, unify attack prevention, and automate detection and response at machine speed.
Today, we are announcing Unit 42 Continuous Frontier AI Defense to put the first two priorities into practice. Powered by Anthropic's Mythos models and OpenAI's latest GPT cyber models, this always-on, agentic service combines our offensive security experts with proprietary multi-model harnesses to discover vulnerabilities, validate real-world exploitability, and accelerate remediation across applications, identities, cloud infrastructure, and network assets.
Led by our offensive security experts, this service discovers, validates and remediates exposures before they can be exploited. We use proprietary AI harnesses and gated capability models—powerful models restricted from public use—to discover vulnerabilities, prove real-world exploitability, and accelerate remediation across applications, identities, cloud infrastructure, and network assets as an organization’s environment changes.
Continuous Frontier AI Defense builds on Unit 42’s Frontier AI Defense, which launched in April and introduced Frontier AI Exposure Analysis, a point-in-time exposure analysis, and a security blueprint that benchmarks current capabilities to help organizations modernize their cybersecurity systems. In August, Unit 42 expanded the list of frontier AI models to include OpenAI’s GPT-5.6-Cyber and Anthropic's Claude Mythos 5, giving organizations access to additional AI capabilities.
Frontier models are powerful, but no single AI model is a cybersecurity silver bullet and the models require equally powerful AI scanning harnesses.
Unit 42 research evaluation of model performance across enterprise codebases and live environments revealed two stark operational realities:
To solve the single model gaps, Continuous Frontier AI Defense runs on proprietary multi-model harnesses. These harnesses act as an intelligent orchestration layer, routing specific offensive testing tasks to the model best suited for the job. This approach aligns model strengths, eliminates individual gaps, and keeps compute spend economical.
We combine these frontier models with Unit 42 threat intelligence, and frontline security expertise to turn raw vulnerability data into verified, actionable protection. Zero Data Retention (ZDR) architectures protect enterprise source code and telemetry, so customer data is never retained or used to train public models.
We did not build this service on theoretical assumptions. We built and validated it internally across Palo Alto Networks and across more than 100 customer engagements.
During our internal deployment, continuous Mythos-based scanning achieved over a year’s worth of traditional penetration testing results in just three weeks. The harness identified 3.2 times more high and critical vulnerabilities per product than legacy testing methods, and helped engineering teams cut mean time to remediate by 51%.
When we executed the service across customer environments, the frontline data delivered a clear warning:
Finding weaknesses without fixing them only creates noise. And, security teams do not lack findings; they already have more alerts than they can act on. The bigger challenge is knowing which weaknesses an attacker can actually exploit and chain into a viable path to compromise, and then remediating them.
Unit 42 Continuous Frontier AI Defense translates findings directly into risk reduction:
Unit 42 Continuous Frontier AI Defense is available worldwide today on an annual subscription basis. Register for our upcoming virtual Threat Briefing to see how we apply Frontier AI, our proprietary multi-model harness, and offensive security expertise to protect Palo Alto Networks and our customers.
To learn more about Unit 42 Continuous Frontier AI Defense, register for the upcoming Virtual Threat Briefing here.
The post Introducing Unit 42 Continuous Frontier AI Defense appeared first on Palo Alto Networks Blog.
Canadian authorities on Wednesday arrested a 23-year-old Ottawa man on suspicion of building and operating Kimwolf, a fast spreading Internet-of-Things botnet that enslaved millions of devices for use in a series of massive distributed denial-of-service (DDoS) attacks over the past six months. KrebsOnSecurity publicly named the suspect in February 2026 after the accused launched a volley of DDoS, doxing and swatting campaigns against this author and a security researcher. He now faces criminal hacking charges in both Canada and the United States.
A criminal complaint unsealed today in an Alaska district court charges Jacob Butler, a.k.a. “Dort,” of Ottawa, Canada with operating the Kimwolf DDoS botnet. A statement from the Department of Justice says the complaint against Butler was unsealed following the defendant’s arrest in Canada by the Ontario Provincial Police pursuant to a U.S. extradition warrant. Butler is currently in Canadian custody awaiting an initial court hearing scheduled for early next week.
The government said Kimwolf targeted infected devices which were traditionally “firewalled” from the rest of the internet, such as digital photo frames and web cameras. The infected systems were then rented to other cybercriminals, or forced to participate in record-smashing DDoS attacks, as well as assaults that affected Internet address ranges for the Department of Defense. Consequently, the DoD’s Defense Criminal Investigative Service is investigating the case, with assistance from the FBI field office in Anchorage.
“KimWolf was tied to DDoS attacks which were measured at nearly 30 Terabits per second, a record in recorded DDoS attack volume,” the Justice Department statement reads. “These attacks resulted in financial losses which, for some victims, exceeded one million dollars. The KimWolf botnet is alleged to have issued over 25,000 attack commands.”
On March 19, U.S. authorities joined international law enforcement partners in seizing the technical infrastructure for Kimwolf and three other large DDoS botnets — named Aisuru, JackSkid and Mossad — that were all competing for the same pool of vulnerable devices.
On February 28, KrebsOnSecurity identified Butler as the Kimwolf botmaster after digging through his various email addresses, registrations on the cybercrime forums, and posts to public Telegram and Discord servers. However, Dort continued to threaten and harass researchers who helped track down his real-life identity and dramatically slow the spread of his botnet.
Dort claimed responsibility for at least two swatting attacks targeting the founder of Synthient, a security startup that helped to secure a widespread critical security weakness that Kimwolf was using to spread faster and more effectively than any other IoT botnet out there. Synthient was among many technology companies thanked by the Justice Department today, and Synthient’s founder Ben Brundage told KrebsOnSecurity he’s relieved Butler is in custody.
“Hopefully this will end the harassment,” Brundage said.
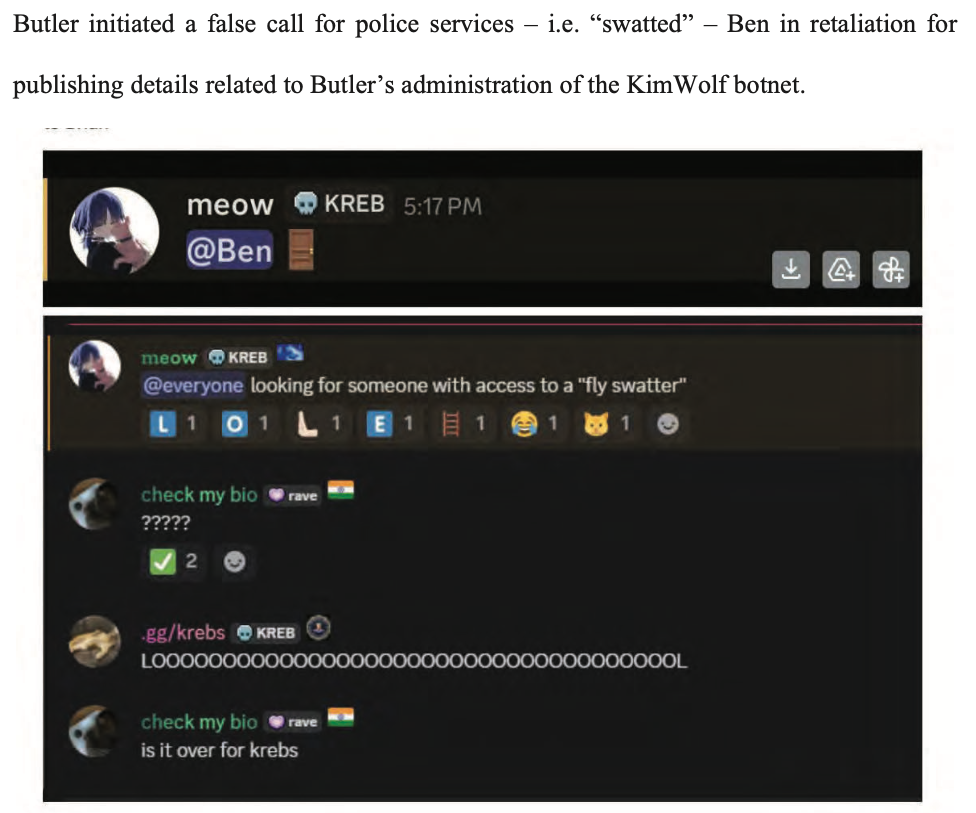
An excerpt from the criminal complaint against Butler, detailing how he ordered a swatting attack against Ben Brundage, the founder of the security firm Synthient.
The government says investigators connected Butler to the administration of the KimWolf botnet through IP address, online account information, transaction records, and online messaging application records obtained through the issuance of legal process. The criminal complaint against Butler (PDF) shows he did little to separate his real-life and cybercriminal identities (something we demonstrated in our February unmasking of Dort).
In April, the Justice Department joined authorities across Europe in seizing domain names tied to nearly four-dozen DDoS-for-hire services, although because of a bureaucratic mix-up the list of seized domains has remain sealed until today. The DOJ said at least one of those services collaborated with Butler’s Kimwolf botnet.
A statement from the Ontario Provincial Police said a search warrant was executed on March 19 at Butler’s address in Ottawa, where they seized multiple devices. As a result of that investigation, Butler was arrested and charged this week with unauthorized user of computer; possession of device to obtain unauthorized use of computer system or to commit mischief; and mischief in relation to computer data. He is scheduled to remain in custody until a hearing on May 26.
In the United States, Butler is facing one count of aiding and abetting computer intrusion. If extradited, tried and convicted in a U.S. court, Butler could face up to 10 years in prison, although that maximum sentence would likely be heavily tempered by considerations in the U.S. Sentencing Guidelines, which make allowances for mitigating factors such as youth, lack of criminal history and level of cooperation with investigators.
For the last several months, we have had early, unbounded access to the latest frontier AI models. What we’ve seen from that vantage point has made it clear that the window for organizations to get ahead of what’s coming is shorter than most leaders realize.
We have moved past the era of incremental AI improvements into a threat landscape shift. Our testing has revealed a step-change in capability that demonstrates an intuitive understanding of software vulnerabilities. This is more than faster code generation, it is a shift from AI as an assistant to AI as an autonomous agent capable of discovering and chaining flaws at a scale that most defenders aren’t prepared for.
These capabilities will not stay confined to controlled environments for long. When Mythos first launched, we predicted a six-month window before attackers gained access. We now believe that timeline has accelerated significantly.
To meet this inflection point, defense must operate at the speed of the adversary. That is why Palo Alto Networks has introduced Frontier AI Defense. This initiative unites our AI-native security platforms with Unit 42® consulting and threat expertise with strategic partners to deliver continuous protection, prioritized risk mitigation and autonomous remediation.
The latest frontier models, including OpenAI’s GPT-5.5-Cyber, Anthropic’s Mythos and Claude Opus 4.7, and the specialized variants emerging across major labs, represent roughly a 50% improvement in coding efficiency over their predecessors. That number sounds incremental, but in practice, it’s the threshold at which AI crosses from a helpful assistant into an autonomous operator.
Based on our testing and review, we found four key developments that, taken together, redefine the modern threat landscape:
These emerging threats form the foundation of how we have architected our platform response for the agentic era – Frontier AI Defense. Our approach moves beyond traditional, reactive defense to provide a comprehensive framework built to outpace frontier-AI-enabled attackers. This initiative is defined by:
The capabilities we tested under early-access conditions are expected to become widely available over the next several months. Success in this new environment requires adapting your cybersecurity stack before these tools are in the hands of every adversary.
The threat has never been more sophisticated. The window to prepare for this shift is closing. And we're here to help secure your future at the edge of the frontier.
Visit Palo Alto Networks Frontier AI Defense to learn more.
The post A New Era of Security: Frontier AI Defense appeared first on Palo Alto Networks Blog.
As Frontier AI crosses new thresholds, the landscape for both attackers and defenders is shifting. At Palo Alto Networks, we are committed to ensuring defenders maintain the advantage.
To deliver this critical edge, our Unit 42 Frontier AI Defense will now leverage Anthropic’s Claude Security, powered by Opus 4.7. By integrating one of the world’s most advanced AI models, we are empowering our customers to outpace automated threats. Through Frontier AI Defense, organizations can rapidly assess their security posture, remediate vulnerabilities and harden their infrastructure against next-generation, AI-driven attacks.
We are utilizing Claude Security’s deep technical reasoning to enable our customers to find and fix vulnerabilities with unprecedented speed. This includes:
Palo Alto Networks is also participating in Anthropic's Cyber Verification Program, which credentials security teams for legitimate defensive use of frontier models.
The threat timeline is accelerating. Within months, AI-driven attack capabilities will become a standard fixture of the threat landscape. Palo Alto Networks is dedicated to ensuring our global customers are equipped with the modern frontier AI models necessary to stay secure both today and tomorrow.
The post Enhancing AI-Driven Defense with Anthropic’s Claude Opus 4.7 appeared first on Palo Alto Networks Blog.
Frontier AI is changing what is possible for attackers. To meet this escalating threat, Palo Alto Networks is teaming up with Armadin, the new offensive security company founded by Kevin Mandia. This partnership expands our newly introduced Unit 42 Frontier AI Defense service, scaling our ability to identify and remediate AI-driven exposures, and accelerating protection across the enterprise.
Over the past few weeks, we’ve spoken with hundreds of CISOs who universally feel the urgency on the frontlines. Security leaders need to know exactly where they stand against the AI-driven attacks happening right now, and the ones coming in the next six months.
For organizations seeking to actively pressure-test their perimeter, this partnership introduces an autonomous, AI-driven offensive assessment of your external attack surface.
This added layer identifies real attack paths and proves exploitability across internet-facing assets. The platform begins with passive discovery, validating publicly exposed assets, cloud resources and secrets. Next, Armadin deploys a coordinated swarm of autonomous AI attack agents, operating at machine speed across your external footprint.
These agents execute active reconnaissance, launch attacks and exploit vulnerabilities in parallel, using over 50,000 templates. Upon initial access, the swarm simulates post-exploitation behavior to demonstrate impact, logging every attack chain as decision-grade evidence of exploitable risk.
With this added layer of autonomous simulation, Unit 42 Frontier AI Defense provides an even more rigorous, pressure-tested view of an organization's external attack surface. This allows our experts to accurately simulate the tradecraft of the most capable, AI-equipped threat actors, compressing complex attack lifecycles from days into minutes.
AI may change what is possible for attackers, but in the hands of defenders, it becomes a decisive advantage. This partnership is another important step in making sure that advantage stays with the defenders.
A member of Project Glasswing and OpenAI’s Trusted Access for Cyber (TAC) program, Palo Alto Networks remains the only company equipped to deliver this strategic level of partnership through Unit 42 Frontier AI Defense and the Frontier AI Alliance, driven to integrate cutting-edge technologies into our products and services.
Get started with Unit 42 Frontier AI Defense today.
The post Unit 42 Expands Frontier AI Defense with Armadin Partnership appeared first on Palo Alto Networks Blog.
With the imminent release of unbounded frontier models, the barrier to entry for sophisticated cyberattacks has vanished. Anthropic’s Mythos represents a 50% leap in coding capability over previous models. It’s a leap that, as Lee Klarich stated, translates into autonomous agents capable of both surfacing a massive surge of vulnerabilities and exploiting them faster than we’ve ever seen or imagined.
In this new era, business continuity requires more than just better tools; it requires a unified ecosystem of experts capable of orchestrating a defense that matches this new pace of attack.
As we drive the industry standard for addressing these emerging risks with our Unit 42® Frontier AI Defense, we’ve united an alliance of global transformation leaders, starting with Accenture, Deloitte, IBM, NTT DATA and PwC, and will continue to scale these alliances to ensure every enterprise has a rapid path to AI resilience.
By combining the world’s most advanced AI security platform with deep industry expertise, we are delivering the security assessment and rapid protection needed to help customers stop emerging threats and keep their business resilient.
Rex Thexton,
Chief Technology Officer, Accenture Cybersecurity:
As AI-driven attacks accelerate to machine speed, organizations must rethink how they protect critical assets. Together with Palo Alto Networks, we're helping clients automate protection and reduce risk. By enabling an autonomous defense posture that detects and responds in minutes, we can empower organizations to scale their AI innovation with confidence.
Deborah Golden,
principal, Deloitte:
As AI-driven threats accelerate, our mission is to help clients move even faster. By combining Deloitte's implementation experience with Palo Alto Networks' AI blueprint, we are rapidly delivering more complete security coverage to clients with near-real-time responsiveness, turning potential vulnerabilities into a foundation for resilient innovation.
Mark Hughes,
Global Managing Partner of Cybersecurity Services, IBM Consulting:
In an environment where frontier models let attackers move faster than ever, organizations need defenses that can keep up. Joining the Frontier AI Alliance strengthens our commitment to helping organizations prepare for this new class of agentic, machine speed threats. IBM Autonomous Security plus Palo Alto Networks technologies bring together interoperable, vendor-agnostic digital workers that operate across an organization's full security stack, enabling security programs to act as a system rather than a collection of disconnected tools.
Sandip Gupta,
Head of Global Strategic Alliances, NTT DATA:
Frontier AI is reshaping the economics of cyber defense. As threat actors move faster and operate with greater automation, organizations need a more resilient and adaptive approach to protecting business continuity. Through the Frontier AI Alliance, NTT DATA is combining Palo Alto Networks' innovation with its global cybersecurity solutions and deep industry experience to help clients close critical security gaps, reduce complexity and strengthen resilience against AI-powered threats.
Morgan Adamski,
Principal and Cyber, Data, & Technology Risk Leader, PwC:
As AI-enabled cyber risk accelerates in both speed and scale, organizations cannot remediate issues fast enough through traditional approaches. Palo Alto Networks Unit 42 Frontier AI Defense combines Palo Alto Networks innovation in vulnerability discovery with PwC's expertise to prioritize what matters, accelerate remediation, and build governance and resilience frameworks that operate at machine speed.
By engaging directly with Palo Alto Networks, or working with our partners through the Frontier AI Alliance, our customers can move past the complexity of building an AI-ready defense from scratch and gain:
The threat of Mythos-class models is imminent, but the path to resilience is clear. Whether you are looking for an immediate strategic assessment or a deep operational overhaul, the Frontier AI Alliance is ready to move at the speed of your business.
The post The AI Ecosystem Edge — Introducing Our Frontier AI Alliance appeared first on Palo Alto Networks Blog.
The release of the newest frontier AI models marks a turning point for cybersecurity. Palo Alto Networks has conducted early testing of the latest frontier AI models, including Anthropic’s Mythos model as part of Project Glasswing and OpenAI’s latest models as part of Trusted Access for Cyber program. The conclusion is clear: They are extraordinarily capable at finding vulnerabilities and generating corresponding exploits.
This generational improvement in coding ability directly translates to a significant advance in vulnerability discovery and exploit generation. These capabilities, however guardrailed, will not stay contained. Similar advances will appear across other major AI labs, Chinese models, and open source models. Attackers will find the seams in those guardrails. They will use advanced AI to discover zero-day vulnerabilities at scale, generate exploits in near real time, and develop autonomous attack agents unlike anything the industry has faced.
Within six months, advanced AI models with deep cybersecurity capabilities will become commonplace. Organizations that have not put appropriate safeguards in place will face an entirely new class of risk across their enterprise and critical infrastructure.
As you have probably already seen, the latest unbounded models like Mythos represent roughly a 50% improvement in coding efficiency over Anthropic’s previous leading model. Palo Alto Networks has had early access to unbounded models and we’ve been able to leverage this vast improvement in coding to a quantum leap in scanning and offensive capability.
Hundreds of our best security engineers have been assessing these capabilities and developing best practices for using it effectively. The results revealed several core truths:
Attackers have been using LLMs for years, but based on our testing of frontier AI models, there are three key areas where they will have a significant impact on the cybersecurity landscape:
The framework for defending against AI-driven threats is not completely new, but the standard for execution must be absolute. Organizations that are “mostly protected” are effectively unprotected. What follows is a phased approach – assessment, protection and platformization – that organizations should pursue in parallel to close gaps before attackers exploit them.
Assessment: Every organization should use the latest AI models to assess its entire code and application landscape and build a comprehensive asset and exposure inventory.
Key priorities:
Protect & Remediation: Remediating and reducing exposure is table-stakes. What in the past may have been difficult due to cross-organizational friction of finding and fixing at pace should now be accelerated with the c-suite attention of these new AI models. But this must go further and extend to comprehensive deployment of best-in-class attack prevention capabilities where the new standard is 100% coverage and optimization.
Real-Time Security Operations: With attack cycle times shrinking rapidly, the legacy approach to security operations simply doesn’t work. Disparate tools analyzing data in silos overlaid with manual processes must be replaced with AI and automation throughout. Cortex XSIAM, our AI-driven SOC platform, is what I consider to be the gold standard for how to take a next-generation approach to deliver MTTD and MTTR in single digit minutes.
Achieving this level of resilience requires the right platforms and the right expertise.
To help you navigate this shift, we are introducing Unit 42 Frontier AI Defense. This new offering is designed to discover and remediate your current exposure before attackers do, strengthen controls that reduce exposure and contain impact and modernize operations so teams can detect and respond at machine speed.
This is the moment we’ve been preparing for. The threat has never been more sophisticated, but the path forward has never been clearer, and we’re here to partner with you on what comes next.
The post Defender's Guide to the Frontier AI Impact on Cybersecurity appeared first on Palo Alto Networks Blog.
Frontier AI models have given the security industry a preview of what comes next. As they become weaponized, attackers will automate the discovery and chaining of vulnerabilities in near real-time – compressing timelines, increasing scale and outpacing human-led defense.
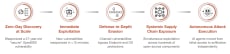
Until now, defenders have had time to detect activity, investigate signals and contain threats before exposures were chained into full attacks. AI is quickly closing this window.
Defending against AI-driven threats means engineering a resilient architecture that limits how easily attackers can exploit discovered weaknesses, that contains the blast radius when they do, and enables faster response at scale. It also means using AI to accelerate the security program itself, from vulnerability discovery and code review to triage, remediation and incident response.
The transition should cover three areas. First, discover and remediate your current exposure before attackers do. Second, strengthen controls that reduce exposure and contain impact. Third, modernize operations so teams can detect and respond in real-time.
To help organizations make this shift, Palo Alto Networks is launching Unit 42® Frontier AI Defense.
Powered by the latest AI models, Unit 42 Frontier AI Defense helps organizations answer a critical question: Are your defenses ready for AI-powered attacks?
Unit 42 Frontier AI Defense combines three core components delivered by expert consultants, coupled with 6 months of complimentary access to Cortex® XDR, Cortex Xpanse® and Koi Agentic Security.
Frontier AI Exposure Analysis: Identify and validate the exposures most likely to be chained into real attacks before attackers weaponize them.
Actions
Outputs
Autonomous Security Blueprint: Benchmark current capabilities and define the changes required for machine-speed defense.
Actions
Outputs
Agentic Defense Transformation: Implement the prioritized architecture, control and operating changes needed to modernize defenses for AI-driven threats.
Actions
Outputs
AI is the biggest security inflection point since enterprises moved to the cloud. Organizations that act now will be the ones that are ready. Those that wait will be forced to respond under maximum pressure on the worst possible day.
Frontier AI is changing what is possible for attackers. In the hands of defenders, it can become a decisive advantage.
Human-speed security is no longer enough. A modern security approach is required. Get started with Unit 42 Frontier AI Defense today.
*The complimentary offer is not available to public sector customers or current Cortex XDR, Cortex Xpanse or Koi customers.
The post Introducing Unit 42 Frontier AI Defense appeared first on Palo Alto Networks Blog.
This article on the walls of Constantinople is fascinating.
The system comprised four defensive lines arranged in formidable layers:
- The brick-lined ditch, divided by bulkheads and often flooded, 15-20 meters wide and up to 7 meters deep.
- A low breastwork, about 2 meters high, enabling defenders to fire freely from behind.
- The outer wall, 8 meters tall and 2.8 meters thick, with 82 projecting towers.
- The main wall—a towering 12 meters high and 5 meters thick—with 96 massive towers offset from those of the outer wall for maximum coverage.
Behind the walls lay broad terraces: the parateichion, 18 meters wide, ideal for repelling enemies who crossed the moat, and the peribolos, 15–20 meters wide between the inner and outer walls. From the moat’s bottom to the highest tower top, the defences reached nearly 30 meters—a nearly unscalable barrier of stone and ingenuity.
OpenAI is in and Anthropic is out as a supplier of AI technology for the US defense department. This news caps a week of bluster by the highest officials in the US government towards some of the wealthiest titans of the big tech industry, and the overhanging specter of the existential risks posed by a new technology powerful enough that the Pentagon claims it is essential to national security. At issue is Anthropic’s insistence that the US Department of Defense (DoD) could not use its models to facilitate “mass surveillance” or “fully autonomous weapons,” provisions the defense secretary Pete Hegseth derided as “woke.”
It all came to a head on Friday evening when Donald Trump issued an order for federal government agencies to discontinue use of Anthropic models. Within hours, OpenAI had swooped in, potentially seizing hundreds of millions of dollars in government contracts by striking an agreement with the administration to provide classified government systems with AI.
Despite the histrionics, this is probably the best outcome for Anthropic—and for the Pentagon. In our free-market economy, both are, and should be, free to sell and buy what they want with whom they want, subject to longstanding federal rules on contracting, acquisitions, and blacklisting. The only factor out of place here are the Pentagon’s vindictive threats.
AI models are increasingly commodified. The top-tier offerings have about the same performance, and there is little to differentiate one from the other. The latest models from Anthropic, OpenAI and Google, in particular, tend to leapfrog each other with minor hops forward in quality every few months. The best models from one provider tend to be preferred by users to the second, or third, or 10th best models at a rate of only about six times out of 10, a virtual tie.
In this sort of market, branding matters a lot. Anthropic and its CEO, Dario Amodei, are positioning themselves as the moral and trustworthy AI provider. That has market value for both consumers and enterprise clients. In taking Anthropic’s place in government contracting, OpenAI’s CEO, Sam Altman, vowed to somehow uphold the same safety principles Anthropic had just been pilloried for. How that is possible given the rhetoric of Hegseth and Trump is entirely unclear, but seems certain to further politicize OpenAI and its products in the minds of consumers and corporate buyers.
Posturing publicly against the Pentagon and as a hero to civil libertarians is quite possibly worth the cost of the lost contracts to Anthropic, and associating themselves with the same contracts could be a trap for OpenAI. The Pentagon, meanwhile, has plenty of options. Even if no big tech company was willing to supply it with AI, the department has already deployed dozens of open weight models—whose parameters are public and are often licensed permissively for government use.
We can admire Amodei’s stance, but, to be sure, it is primarily posturing. Anthropic knew what they were getting into when they agreed to a defense department partnership for $200m last year. And when they signed a partnership with the surveillance company Palantir in 2024.
Read Amodei’s statement about the issue. Or his January essay on AIs and risk, where he repeatedly uses the words “democracy” and “autocracy” while evading precisely how collaboration with US federal agencies should be viewed in this moment. Amodei has bought into the idea of using “AI to achieve robust military superiority” on behalf of the democracies of the world in response to the threats from autocracies. It’s a heady vision. But it is a vision that likewise supposes that the world’s nominal democracies are committed to a common vision of public wellbeing, peace-seeking and democratic control.
Regardless, the defense department can also reasonably demand that the AI products it purchases meet its needs. The Pentagon is not a normal customer; it buys products that kill people all the time. Tanks, artillery pieces, and hand grenades are not products with ethical guard rails. The Pentagon’s needs reasonably involve weapons of lethal force, and those weapons are continuing on a steady, if potentially catastrophic, path of increasing automation.
So, at the surface, this dispute is a normal market give and take. The Pentagon has unique requirements for the products it uses. Companies can decide whether or not to meet them, and at what price. And then the Pentagon can decide from whom to acquire those products. Sounds like a normal day at the procurement office.
But, of course, this is the Trump administration, so it doesn’t stop there. Hegseth has threatened Anthropic not just with loss of government contracts. The administration has, at least until the inevitable lawsuits force the courts to sort things out, designated the company as “a supply-chain risk to national security,” a designation previously only ever applied to foreign companies. This prevents not only government agencies, but also their own contractors and suppliers, from contracting with Anthropic.
The government has incompatibly also threatened to invoke the Defense Production Act, which could force Anthropic to remove contractual provisions the department had previously agreed to, or perhaps to fundamentally modify its AI models to remove in-built safety guardrails. The government’s demands, Anthropic’s response, and the legal context in which they are acting will undoubtedly all change over the coming weeks.
But, alarmingly, autonomous weapons systems are here to stay. Primitive pit traps evolved to mechanical bear traps. The world is still debating the ethical use of, and dealing with the legacy of, land mines. The US Phalanx CIWS is a 1980s-era shipboard anti-missile system with a fully autonomous, radar-guided cannon. Today’s military drones can search, identify and engage targets without direct human intervention. AI will be used for military purposes, just as every other technology our species has invented has.
The lesson here should not be that one company in our rapacious capitalist system is more moral than another, or that one corporate hero can stand in the way of government’s adopting AI as technologies of war, or surveillance, or repression. Unfortunately, we don’t live in a world where such barriers are permanent or even particularly sturdy.
Instead, the lesson is about the importance of democratic structures and the urgent need for their renovation in the US. If the defense department is demanding the use of AI for mass surveillance or autonomous warfare that we, the public, find unacceptable, that should tell us we need to pass new legal restrictions on those military activities. If we are uncomfortable with the force of government being applied to dictate how and when companies yield to unsafe applications of their products, we should strengthen the legal protections around government procurement.
The Pentagon should maximize its warfighting capabilities, subject to the law. And private companies like Anthropic should posture to gain consumer and buyer confidence. But we should not rest on our laurels, thinking that either is doing so in the public’s interest.
This essay was written with Nathan E. Sanders, and originally appeared in The Guardian.
Unit 42 research reveals most OT attacks begin in IT. Learn how edge-driven defense stops threats early and turns dwell time into advantage.
The post Bring the Fight to the Edge: Turning Time Into an Advantage in OT Security appeared first on Unit 42.
85% of daily work occurs in the browser. Unit 42 outlines key security controls and strategies to make sure yours is secure.
The post The Browser Defense Playbook: Stopping the Attacks That Start on Your Screen appeared first on Unit 42.
Many web application firewalls (WAFs) can be bypassed by simply sending large amounts of extra data in the request body along with your payload. Most WAFs will only process requests up to a certain size limit. How the WAF is configured to handle these large requests determines exploitability, but some common WAFs will allow it by default.
The post Bypassing WAFs Using Oversized Requests appeared first on Black Hills Information Security, Inc..
One tool that I can't live without when performing a penetration test in an Active Directory environment is called NetExec. Being able to efficiently authenticate against multiple systems in the network is crucial, and NetExec is an incredibly powerful tool that helps automate a lot of this activity.
The post Getting Started with NetExec: Streamlining Network Discovery and Access appeared first on Black Hills Information Security, Inc..
Jordan Drysdale // Overview The following description of some of Impacket’s tools and techniques is a tribute to the authors, SecureAuthCorp, and the open-source effort to maintain and extend the code. […]
The post Impacket Defense Basics With an Azure Lab appeared first on Black Hills Information Security, Inc..
In this BHIS webcast, we cover some new techniques and tactics on how to track attackers via various honey tokens. We cover how to track with Word Web Bugs in ADHD and […]
The post BHIS Webcast: Tracking Attackers. Why Attribution Matters and How To Do It. appeared first on Black Hills Information Security, Inc..

Jordan Drysdale & Kent Ickler// Jordan and Kent are back with more blue team madness! The shameless duo continue their efforts to wrangle decades old attacks against wireless networks. The […]
The post WEBCAST: Stop Sucking at Wireless appeared first on Black Hills Information Security, Inc..
John Strand// In this webcast John talks about the new ACDC law and what it means exactly. There has been quite a bit of anger and great GIFs about hacking […]
The post WEBCAST: Proper Active Defense and the New ACDC Active Defense Law appeared first on Black Hills Information Security, Inc..
John Strand // I wanted to take a few moments and address the “Hacking Back” law that is working people up. There is a tremendously well-founded fear that this law […]
The post Debating the Active Defense Law.. Because Arguing is Fun appeared first on Black Hills Information Security, Inc..
