❌

Reading view

Millions of PHP Instances Exposed - What Organizations Need To Do Right Now

Two critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619) have been published. Both vulnerabilities carry a severe CVSS score of 9.2 (more technical details are in the Unit 42 Threat Brief). 

This is not just another high-severity vulnerability disclosure, it marks the opening chapter in a massive acceleration of cyberthreats that will define the foreseeable future. Because PHP is widely used globally (by some estimates, more than half of all websites), the sheer scale of this is massive. Navigating this new reality demands immediate imperatives, including continuous, proactive vulnerability discovery before adversaries weaponize code, and a modern defense strategy that pairs traditional patching with real-time virtual patching. At a footprint of 22 million exposed instances, relying on manual remediation cycles alone is not a viable defense.

For context, exposures are typically in the thousands, for example around 50,000 potentially vulnerable exposed instances for recent NetScaler vulnerabilities, and about 16,000 exposed instances of BeyondTrust, potentially vulnerable to CVE-2026-1731. Pervasive open-source software introduces an exposure footprint on an entirely different order of magnitude. 

This situation illustrates what I shared in Defender’s Guide to the Frontier AI Impact on Cybersecurity. We’re officially in a new reality, and this is going to be an ongoing cycle.

An Accelerating Cycle

The latest frontier AI models are extraordinarily capable at finding vulnerabilities in code. We’ll see these models continue to surface critical issues at a pace faster than ever before.

But here’s the challenge: As soon as patches for vulnerabilities are available, attackers will reverse engineer the patch, locate the root flaw, and target them in near real time. It simply takes too long to apply patches to every system. This vulnerability deluge demands urgency and new technologies, such as virtual patching, are needed.

What Organizations Should Do Now

(1) Assess Your Open Source Inventory

Given the unprecedented speed at which new, critical vulnerabilities are being found with frontier AI, organizations need the ability to understand their true exposure at a moment’s notice. Attack surface management solutions have never been more critical for finding these blind spots across your entire codebase and supply chain. You can’t protect what you can’t see.

Additionally, services like Unit 42 Continuous Frontier AI Defense put defender-grade AI models in the hands of defenders to find and fix vulnerabilities before attackers can weaponize them.

(2) Prioritize Remediation Based on Reachability

You have to reduce what is reachable by attackers. You can't instantly patch everything everywhere, so prioritize what needs to be fixed first based on attack-path reachability. Secure what must be accessible to the public internet, and evaluate your environments to understand which of those exposed PHP instances carry the most immediate risk. For example, Cortex Xpanse and exposure management are great tools for determining reachability and automating remediation.

(3) Secure your AI deployments

While not the main focus for these PHP vulnerabilities, rapid deployment of AI across organizations is expanding the attack surface. All AI deployments must be secure AI deployments.

(4) Mitigate and Ensure Attack Protections

While you coordinate patching with your development teams, ensure best-in-class protections are in place to block the actual exploits. Mitigate against potential attacks immediately through proactive virtual patching and reducing overall exposure. Deploying high-fidelity virtual patches across your network and cloud security provides the mitigation layer necessary to give your teams the time they need to update the actual software safely.

Our new Frontier Virtual Patching capability delivered preemptive coverage for these PHP vulnerabilities ahead of today’s public disclosure. Additionally, Palo Alto Networks customers are protected from exploitation of these vulnerabilities by Advanced Threat Prevention available on our next-generation firewalls and Prisma Access.

(5) Deploy Real-Time Security Operations

Autonomous AI-driven attacks will drive attack lifecycles to minutes requiring every SOC to achieve single-digit mean time to detect (MTTD) and mean time to respond (MTTR).

The Path Forward: Institutionalize Defenses

This isn’t a one-and-done situation. With frontier AI compressing the patch-to-exploit window to minutes, assessing exposure, prioritizing reachability, mitigating and ensuring attack protections must become a continuous, automated motion.

This is a pivotal moment. While the scale of the challenge presented by frontier AI is real, I’m confident in our ability to solve it. Take the steps to secure your organization today, and build the foundation needed to ensure the advantage remains with the defender.

Mitigating Critical PHP Vulnerabilities (CVSS 9.2) at Machine Speed

When frontier AI models accelerate both vulnerability discovery and reverse-engineering of patches, traditional remediation creates an unavoidable window of exposure. Get started with Frontier Virtual Patching in Advanced Threat Prevention Plus to solve this structural delay.
Get Started

The post Millions of PHP Instances Exposed - What Organizations Need To Do Right Now appeared first on Palo Alto Networks Blog.
  •  

Putting OpenAI Cyber Models to Work for Defenders

Unit 42 is putting the latest frontier cyber models to work across customer environments to find, validate and help remediate the attack paths that matter most.

In May, we introduced Frontier AI Defense with a warning: the window to get ahead of AI-enabled attacks was shorter than most people realized. Since then, we have briefed more than 1,000 security teams around the world and introduced our Frontier AI Defense service to hundreds of customers.

Today, through our partnership with OpenAI, we are expanding Unit 42 Frontier AI Exposure Analysis to put advanced frontier cyber models directly to work in customer environments. Under Unit 42 direction, these models can find exposures, test whether they are exploitable, validate attack paths and help customers prioritize what to fix first.

Our early work shows why this approach matters: 36% of the exposures we identified map to no known CVE, often because they involve multiple gaps that have to be discovered, chained and tested together.

Bringing the Latest Frontier Cyber Capabilities to Defenders

Palo Alto Networks has been among a limited group of organizations with early access to advanced cyber capabilities from the leading frontier AI labs. Through our partnership with OpenAI, Unit 42 can now bring its latest advanced cyber capabilities, including GPT-5.6 Daybreak, to security testing and validation for our customers. Until now, GPT-5.6 Daybreak has not been available for commercial use.

Frontier models have helped inform the work of our experts. Now they can increasingly perform complex offensive security tasks directly, at machine speed and under Unit 42 direction. That allows us to go deeper than traditional vulnerability discovery by testing exploitability, reasoning across multiple weaknesses and determining how an attacker could use them to achieve an objective.

There is no single best model for every cyber task. Our research has shown that different models have different strengths and find vulnerabilities others miss. A multi-model harness routes work to the model best suited for the task, improving efficacy and coverage while managing the cost of frontier AI at scale. As stronger models emerge, we can incorporate them without rebuilding the offering around a single model or provider.

Unit 42 experts remain central to the process. We combine frontier models with our offensive security expertise, Palo Alto Networks telemetry and Unit 42 Threat Intelligence to validate findings, connect exposures into attack paths and understand what an attacker could ultimately achieve.

Built to Find What Attackers Can Exploit

The expanded service brings five capabilities together:

  • Leading cyber models: Apply the latest advanced cyber models to improve exposure discovery, testing and validation.
  • Multi-model harness: Use the right model for the right task to improve efficacy, expand coverage and optimize cost.
  • Exposure discovery: Find vulnerabilities, misconfigurations, leaked credentials, unmanaged attack surface and other posture gaps across applications and network assets.
  • Advanced adversary simulation: Actively test exploitability and validate end-to-end attack paths to understand how an attacker could compromise the environment.
  • Custom remediation plan: Prioritize the fixes that break the most important attack paths and feed those findings into existing IT, development and security workflows.

Most security teams already have more findings than they can act on. The harder problem is knowing which ones create a real path to compromise. Attackers look across applications, infrastructure, identity and cloud for weaknesses they can combine to achieve an objective. Frontier AI Exposure Analysis applies that same adversarial perspective, helping defenders understand which paths matter and what to fix first.

The Asymmetry Runs Both Ways Now

For the past several months, frontier AI has been a story about what is coming for defenders: vulnerability discovery at scale, exploit chaining that sees full-stack logic no scanner catches, and attack cycles compressed to seconds from initial access to exfiltration.

All of that is still true. Our answer has been to put everything we learn testing these frontier models into the hands of defenders. Today, that gets more direct: not just what frontier models have taught us, but the models themselves, working in your environment for your defenders before those same capabilities are working for the attacker.

The window is still closing. We intend to spend it building on the side of the defenders.

Visit Palo Alto Networks Frontier AI Defense to learn more.

The post Putting OpenAI Cyber Models to Work for Defenders appeared first on Palo Alto Networks Blog.
  •  

How AI and Evasion Demand a Radical Shift in Network Threat Prevention

The Future of Threat Defense Resides at the IP Layer

For years, network security operated on a relatively predictable premise: inspect traffic, identify malicious content, and block it. Because deep content inspection created a seemingly robust defense in depth, relatively static legacy approaches—like reliance on threat intelligence feeds—were allowed to simply persist in the background.

The weaponization of agentic AI and highly evasive techniques has fundamentally shattered that model. Attackers are no longer just iterating on old threats. They are launching attacks at staggering velocity, completely outpacing threat feeds, and employing evasion tactics that actively starve legacy prevention solutions of the content they rely on to inspect.

Our new research report from Unit 42, Attackers Are Evading Threat Prevention at the Internet Edge, reveals how adversaries are actively exploiting the contextual vacuum at the IP layer to bypass standard security controls. For security leaders, understanding this shift is no longer optional. As the nature of the threat fundamentally changes, our strategic approach to network security must definitively change with it.

The AI-Accelerated, Evasive Attack Lifecycle

To understand why legacy defenses are failing, we must look at how adversaries are accelerating and obfuscating every stage of the attack lifecycle. As these threats progress, the commonly used network indicators we have long relied upon are vanishing, collapsing traditional defenses and leaving defenders with little to act on.

Powered by frontier AI, adversaries now automate reconnaissance and exploitation at huge scale and speed, while using anonymizers to mask their intent. Once an intrusion is launched, orchestration shifts to highly evasive command and control (C2). Attackers hide communications using advanced encryption and AI-built malware-less techniques. They’re also bypassing traditional web and DNS inspection entirely by routing traffic directly to IP addresses—a tactic Unit 42 found in 23% of modern malware

Ultimately, the takeaway is clear: network threat prevention can no longer rely solely on detecting malicious payloads. As AI-driven attacks continue to minimize their footprint, security strategies must augment content inspection with real-time IP layer monitoring to left-shift threat detection and counter these rapid, machine-speed threats at the network foundation.

Existing Approaches Aren’t Working

Where content-based detection falls short, many security vendors and organizations still rely on IP threat intelligence feeds to pick up the slack in an attempt to filter out malicious connections on the network layer. However, after years of operating under this model, the results are in—the traditional feed is showing its age.

Attackers have long relied on proxies, anonymizers, residential routers and public cloud providers as a tactic to evade detection. However, agentic AI morphs this process, enabling rapid infrastructure rotation and stealth at an unprecedented scale. As this autonomous evasion accelerates, experienced network defenders continue to run into the well-known limitations of classic IP blocklists:

  • Too slow to keep pace: Unit 42 found an average 20-day lag time before new threats hit popular feeds. Because agentic AI enables adversaries to autonomously rotate proxy IPs in hours, these lists are obsolete at the moment of delivery.
  • Fundamentally incomplete: IP feeds are unable to see a massive portion of the modern attack surface. Unit 42 research indicates that 52% of malicious IPs used for direct-to-IP connections are completely absent from these lists.
  • Unactionable on shared infrastructure: Even known threats are often impossible to block. The Unit 42 team reports that 37% of direct-to-IP traffic uses reputable CDNs and cloud providers. IP feeds cannot distinguish malicious connections from legitimate ones, making blocking too risky for business continuity.
  • A management nightmare: Among the security teams that Unit 42 polled, 30% indicate resource-intensive vetting and false-positive triage as their top pain point. To avoid breaking legitimate traffic, feeds are frequently relegated to an alert-only mode, defeating the entire purpose of prevention.

If modern and agentic AI-enabled attacks can outrun traditional network payload-based detections, we need a new weapon in the network defender’s arsenal. We can no longer depend on yesterday’s IP feeds to secure such an extremely agile threat environment.

The Blueprint for Modernizing the Internet Edge

To outpace the impact of agentic AI and advanced evasion on network threat prevention, security leaders must redefine their defense strategy and shift-left to track the attacker infrastructure itself—monitoring the exact IP layer locations where adversaries build and control their campaigns. Deep content inspection remains essential, but securing the modern edge requires establishing the context and intent of a connection before a session is established.

To achieve this goal, organizations must move beyond the limitations of static defense and adopt a modern security blueprint:

  • Proactive protection against attacker infrastructure: While high-quality threat feeds remain essential for SOC investigations and incident response, relying on them for frontline, real-time prevention creates major blind spots. Instead, security teams must use real-world, global telemetry to proactively identify and block connections to attacker-controlled hosts before requesting a URL or file.
  • Zero trust principles applied to the network layer: An IP address without a negative reputation does not equal a safe connection. Continuous verification requires extending zero trust down to the network foundation. It validates the real-time behavior and intent of every single session to ensure attackers cannot hide in the contextual vacuum of the IP layer.  
  • Reducing the attack surface with rich contextual attributes: Traditional IP blocking is like a blunt instrument that creates unacceptable false positives and alert fatigue. To modernize the edge, security teams need deep, attribute-based visibility across the entire Internet address space to reduce noise and replace legacy IP feeds entirely.  

By moving away from point-in-time assumptions and embracing real-time, inline protection, security leaders can reclaim the advantage at the network foundation.

To see how these evasion tactics operate in the wild, read the latest Unit 42 report, Attackers Are Evading Threat Prevention at the Internet Edge. You’ll find this report valuable in understanding the systemic gaps in legacy risk models and learning why continuous verification must be our new mandate.

The post How AI and Evasion Demand a Radical Shift in Network Threat Prevention appeared first on Palo Alto Networks Blog.
  •  

Beyond the Frontier — Expanding the Ecosystem for Autonomous Defense

Over the past few weeks, we have reached a critical turning point in cybersecurity. Following the launch of our Frontier AI Defense initiative, we’ve continued testing the latest frontier models (including Anthropic’s Mythos and Claude Opus 4.7, as well as OpenAI’s GPT-5.5-Cyber) as part of the Trusted Access for Cyber program.

The urgency to innovate continues to ramp up. As Lee Klarich recently detailed in his Defender's Guide to the Frontier AI Impact on Cybersecurity, our current landscape is defined by a brief three-to-five-month window to gain a strategic advantage over attackers. To outsmart AI-based exploits, enterprises must decisively address vulnerabilities across their code and stand up the right security stack to enable real-time, automated defenses.

With such a ticking clock in front of us, acting rapidly and at-scale to support our customers is paramount. Today, we exponentially grow our scale of delivery by expanding our Frontier AI Alliance.

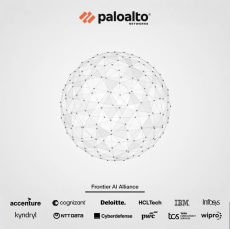
Since introducing this initiative, our collaboration with initial partners – Accenture, Deloitte, IBM, NTT DATA, and PwC – has already begun changing the defensive math for our customers. This is a moment that calls for radical collaboration across the entire security ecosystem, so today we are proud to welcome a new cohort of strategic partners – Cognizant, HCLTech, Kyndryl, TCS, Infosys, McKinsey & Company, Orange Cyberdefense, and Wipro – who will join us in delivering AI readiness at scale.

Frontier AI Alliance

While this expansion significantly increases our reach, this is only the beginning. We are committed to a continuous evolution of this alliance and will be adding more critical partners in the future across the globe to ensure our customers have the most robust defense network possible.

By combining our technology with these partners’ deep consulting expertise, we are delivering:

  • Machine-Speed Security: Natively integrating Frontier AI to provide real-time, automated defense against autonomous threats.
  • Intelligence-Led Resilience: Leveraging Unit 42® experts to fast-track the discovery and remediation of exposures at machine speed.
  • Hardened Defenses: Utilizing early access to frontier models from partners like OpenAI and Anthropic to simulate and block attack chains before they hit the mainstream.

The stakes are high. The attack cycle has compressed with the time from initial access to data exfiltration collapsing to just 39 seconds. Machine-speed MTTR (mean time to respond) is no longer an ambitious goal, it is a requirement.

This initiative underscores our commitment to providing every client with integrated, real-time protection.

Discover further details: Palo Alto Networks Frontier AI Defense.

Forward-Looking Statements

This blog contains forward-looking statements that involve risks, uncertainties and assumptions, including, without limitation, statements regarding the benefits, impact, or performance or potential benefits, impact or performance of our products and technologies or future products and technologies. These forward-looking statements are not guarantees of future performance, and there are a significant number of factors that could cause actual results to differ materially from statements made in this blog. We identify certain important risks and uncertainties that could affect our results and performance in our most recent Annual Report on Form 10-K, our most recent Quarterly Report on Form 10-Q, and our other filings with the U.S. Securities and Exchange Commission from time-to-time, each of which are available on our website at investors.paloaltonetworks.com and on the SEC's website at www.sec.gov.  All forward-looking statements in this blog are based on information available to us as of the date hereof, and we do not assume any obligation to update the forward-looking statements provided to reflect events that occur or circumstances that exist after the date on which they were made.

The post Beyond the Frontier — Expanding the Ecosystem for Autonomous Defense appeared first on Palo Alto Networks Blog.
  •  
❌