Login

What SecureIQLab Cloud WAAP 5.0 means for your application security
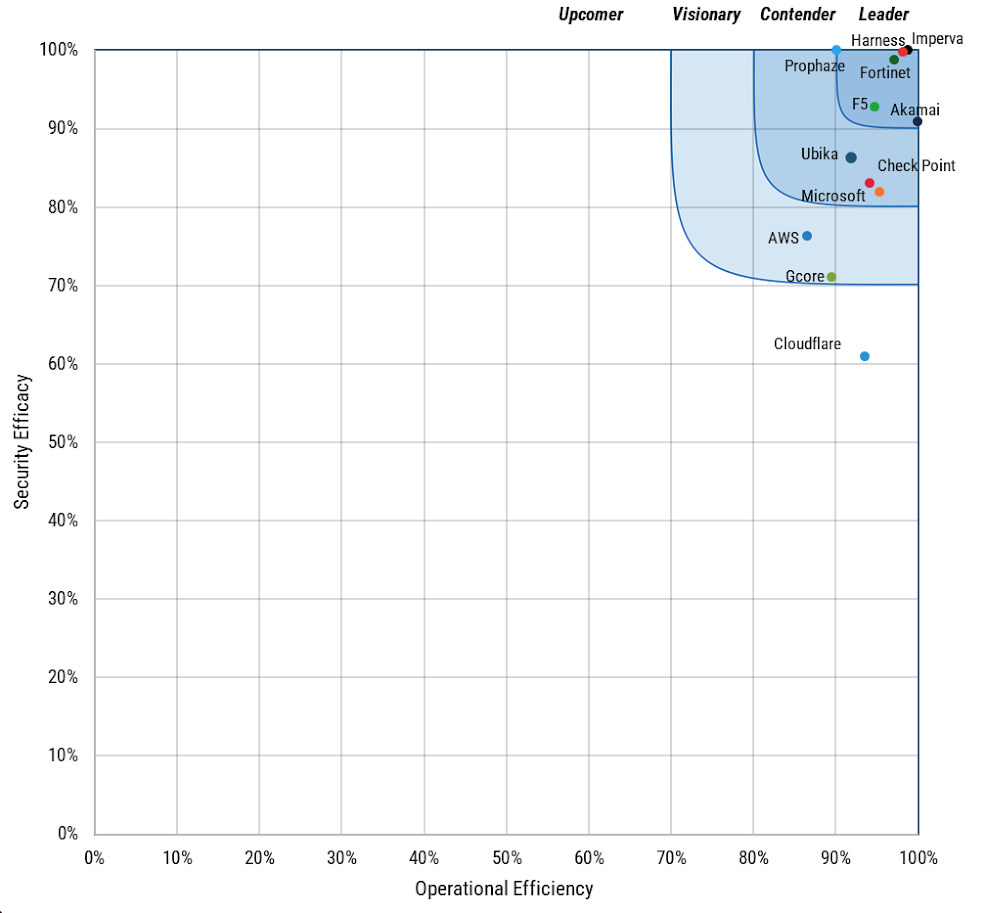
You cannot verify a vendor’s security claims from their own datasheet, including ours. That is why independent validation matters. In our recent guide to the best WAAP solutions (Best WAAP Solutions 2026: Enterprise Buyer Guide), we argued that every serious shortlist should include independent third-party testing across both web and API threats. SecureIQ Lab’s Cloud WAAP v5.0 CyberRisk Validation, published this week, delivers exactly that: twelve leading cloud WAAP platforms, 1,608 attack scenarios, and 1,487 false-positive traps, all run under identical, adversarial conditions, with every vendor’s results published in full.
This blog is the follow up to that buyer guide and explains what the new report says and how to read any benchmark.
Balancing security efficacy and false positives
A high security-efficacy score, on its own, is easy. Tune any WAF aggressively enough and it will stop every attack, along with a meaningful share of your customers. That is the trap: security efficacy and false positives pull against each other, and false positives are never a rounding error.
Every legitimate transaction blocked is lost revenue, an abandoned cart, a support ticket, a SOC triage, another tuning cycle, and operational cost on top of the license. At scale, teams respond to false-positive pain by loosening policies or dropping rules into detect-only mode. The efficacy number you thought you were buying quietly disappears in production.
The genuinely hard engineering problem, the one that determines your real protection and your real total cost of ownership, is holding maximum efficacy and near-zero false positives at the same time.
That is the equation to grade this report on. Imperva WAF and API Security was placed in the Leader category with a perfect 100% Complete Security Score, the only perfect score of the twelve vendors, across every tested category: all OWASP web test cases, all ten OWASP API categories on all five protocols, every bot, AI-assisted bot, and Layer 7 DoS scenario, every evasion vector, and the full vulnerability assessment.
Against 1,452 legitimate-transaction test cases mixed into live traffic, Imperva achieved that balance of maximum efficacy and zero false positives. No other vendor in the field held a perfect score on both sides of the equation. This evaluation validated protection you do not have to trade away to keep your customers moving.
API security matters: Imperva scored 20% above average
Most vendors now score well on classic web attacks. The OWASP WAF group average was 89.96%, and five vendors scored 99.5% or better. APIs are a different story. Across the OWASP API Security Top 10, tested over five protocols, published scores ranged from 45.5% to 100%, around a group average of 80.3%.
Imperva scored 100% on every API category and every protocol tested, including WebSockets, where the twelve-vendor group averaged just 48%. If your evaluation shortlist is driven by web-attack demos, the API results are where you should spend more time. That was one of the main recommendations in the WAAP buyer guide, and the new numbers reinforce it.
New in 5.0: AI security and compliance
The 5.0 methodology adds AI application security: 35 attack scenarios aligned with OWASP LLM01 (Prompt Injection) and LLM05 (Improper Output Handling), scored independently of the headline results. Here is the honest reading: nine of the twelve vendors, Imperva included, scored 100% on that attack set. Runtime LLM attack-blocking is already table stakes.
Where the field separates is operating AI protection at enterprise scale. SecureIQ Lab’s GenAI & LLM Operational Efficiency rating looks at the ability to deploy, govern, and observe AI protections in production. Scores ranged from 0% to 100%, around a 73% group average. Imperva was one of five vendors rated 100%.
The second new dimension is compliance. SecureIQ Lab ran a five-layer assessment across regulatory, data-protection, audit, governance, and AI frameworks (NIST, ISO/IEC 27001 and 42001, PCI DSS, GDPR, HIPAA, and more). Imperva’s 87% was the highest score of all twelve vendors, against a 63.95% group average, including 100% on the AI security layer.
If your security purchases have to survive an audit committee, which is true for most enterprises, this is the part of the report to share with your GRC team.
In summary:
- 100% OWASP LLM score: Imperva blocked all tested LLM01 and LLM05 attack scenarios.
- Zero LLM false positives: legitimate AI interactions in the LLM test set were not blocked.
- 100% GenAI & LLM Operational Efficiency: Imperva scored 100% versus a 73% group average.
- Operational readiness matters: the rating reflects capabilities such as vulnerability coverage, sensitive data protection, full-stack LLM observability, SDK-based guardrail integration, and system-prompt-based context guardrails.
AI protection cannot stop at attack blocking. As organizations bring LLM-backed applications into production, they also need visibility, guardrails, integration, and governance that teams can operate day to day.
Imperva’s AI results show both sides of that equation: tested protection against key LLM threats and validated operational readiness to help enterprises adopt AI more securely and manageably.
WAAP Operational Efficiency in Real Life
Operational efficiency determines how practical a WAAP will be for real-world application teams.
In the SecureIQ Lab Cloud WAAP 5.0 validation, Imperva achieved a 98.8% WAAP Operational Efficiency rating, outperforming the 94.1% group average while also delivering perfect security efficacy and 100% false positive avoidance.
That combination matters because modern security teams are not only judged by whether they stop attacks, but by whether they can do so without slowing deployments, creating unnecessary tuning work, or interrupting legitimate business traffic.
The nine operational security categories tested were:
- Ease of deployment
- Ease of management
- Ease of risk management
- Logging & auditing capabilities
- Visibility & analytics
- Support & documentation
- API Gateway efficiency
- Integration capabilities
- Geolocation based security features
Imperva scored 98.8% against a 94.1% group average, with perfect scores in every category except API Gateway Efficiency (94.4%), where JWT validation has been identified as an improvement opportunity.
The operational results show strength across the day-to-day capabilities that determine whether a WAAP can be run confidently at an enterprise scale.
Imperva was rated 100% in ease of deployment, ease of management, ease of risk management, logging and auditing, visibility and analytics, support and documentation, integration capabilities, and geolocation-based security features.
These categories translate directly into practitioner outcomes: faster setup, simpler policy reuse, stronger role and user management, clearer threat analytics, easier SIEM and SOAR integration, more flexible logging, and better tools for reducing false-positive risk.
The only operational category below 100% was API Gateway Efficiency, where Imperva scored 94.4% against a roughly 95% group average, with JWT validation identified as an area for improvement.
The takeaway for buyers: operational efficiency is not a secondary metric. A WAAP that is difficult to deploy, difficult to tune, or noisy in production becomes an operational burden even if its detection rates look strong.
Imperva’s results show that protection can be both highly effective and highly manageable — giving security, application, and platform teams independent validation that they can strengthen defenses without adding unnecessary friction to the business.
In summary: Four rules for reading any WAAP benchmark
- Read efficacy and false positives as one result, not two separate ones. A perfect block rate with a high false-positive rate does not deliver security. That combination is an outage generator with a dashboard, and its real-world efficacy will be tuned away within a quarter.
- Go to the API results before the web results. Web scores tend to cluster near the top across the industry; API scores are where architecture differences show up.
- Check which deployment model was tested. A SaaS cloud service and a self-managed virtual appliance are different operational propositions; the report calls out the model for each vendor.
- Ask every shortlisted vendor for their current published results, and for the categories where they did not lead. A vendor who cannot name one has not read their own report or needs to check their points.
The full report and methodology are public.
If you are still shaping a shortlist or building evaluation criteria, go back to the earlier Best WAAP solutions blog, Best WAAP Solutions 2026: Enterprise Buyer Guide. It is a practical playbook for what to look for in WAAP architecture, operations, and economics. SecureIQ Lab’s Cloud WAAP 5.0 results now give you independently validated numbers to plug into that playbook.
Source for all figures: SecureIQ Lab Cloud WAAP CyberRisk Validation v5.0, 2026 (AMTSO-certified). Placements and competitor scores from the published comparative report.
The post What SecureIQLab Cloud WAAP 5.0 means for your application security appeared first on Blog.