Reporting on cyberattacks against Japanese entities rose 48% between Q2 and Q3 2026, encompassing ransomware, exploitation of vulnerabilities, credential leaks, and service disruptions. Significant incidents exposed millions of customer records and disrupted operations across multiple sectors, with attacks on shared service providers extending the impact to downstream organizations. Further incidents in October 2026 indicate that these trends have persisted into Q4. This report examines potential contributing factors, including demand for Japanese personal information, legacy systems, software vulnerabilities, weak API controls, and AI’s likely role in lowering technical and language barriers. New incident-reporting requirements under Japan’s Active Cyber Defense (ACD) law, effective October 1, may further increase the number of disclosures of incidents affecting Japanese organizations.
Two critical remote code execution vulnerabilities in the PHP engine, CVE-2026-109618 and CVE-2026-109619 (nicknamed “PHP2Shell”), are reportedly being targeted in active exploitation attempts following the leak of technical details ahead of PHP’s October 21, 2026, security release. Because the flaws affect PHP itself rather than a specific application, websites running vulnerable PHP versions may be exposed, including those built on WordPress, Drupal, and Joomla.
This post covers PHP’s advisories, exploitation reports, public proof-of-concept exploits, exposure data, and patching guidance, along with details from the TTP Instance Insikt Group® published to customers. Attack Surface Intelligence signatures for CVE-2026-109618 and CVE-2026-109619 are available to Recorded Future customers. Organizations running PHP should patch immediately.
The threat actor linked to recent AI-assisted attacks on South Korean financial institutions was testing infrastructure and assembling attack tools as early as August 2026, weeks before the banking campaign became public, according to new research from Recorded Future’s Insikt Group. Subsequent public reporting indicated that the breaches exposed personal data belonging to at least 68,000 people across at least seven financial institutions.
Insikt Group’s investigation expands the known timeline and capabilities of the actor, tracked as TAG-217. Insikt Group uncovered tools designed to steal cryptocurrency wallet files, gain greater access to Linux systems, and test weaknesses in mobile devices. The findings illustrate the “jagged edge” of AI-enabled attacks: threat actors realizing significant gains while committing basic operational security mistakes. AI helps attackers pursue more targets across more environments, but does not prevent them from making the security mistakes that allowed Recorded Future to uncover preparations and capabilities beyond the reported banking campaign. Those mistakes give defenders opportunities to identify related activity and disrupt operations.
Targeting South Korean Banks
In early October 2026, South Korea’s Financial Services Commission (FSC) disclosed that multiple financial institutions had been hit by cyberattacks. The attacks had compromised different systems and allowed unauthorized access to different data at each victim entity, with one breach exposing the personal information of an outsourced developer and another resulting in the theft of customer data. Industry sources reported that the attacks involved the use of ARTEX, a Chinese-language, open-source AI penetration testing framework. The variety of targets at each financial institution likely demonstrates an advantage of AI over human operators: the ability to opportunistically test for weaknesses at scale until a valuable target is found.
On October 7, 2026, public analysis of the incident identified that the threat actor, suspected to be a Chinese speaker, used several AI tools as part of their campaign, including Claude Code, DeepSeek, Grok, and Zhipu AI. Other reports shared network infrastructure indicators used in the campaign, including a primary server running ARTEX and the use of residential proxies, likely to obfuscate the origin of the activity.
Recorded Future investigated this infrastructure to better understand the actor’s operations and tracked this activity under the designation TAG-217.
Putting Together a More Complete Timeline for TAG-217
Differentiating between agentic and human-operated attacks can be difficult, especially when skilled threat actors use AI to enhance operational effectiveness. Agentic attacks use the same tactics and techniques as human operators, though faster and at scale. In the case of TAG-217, operational security mistakes allowed Insikt Group to piece together how the threat actor used AI tools to amplify their intrusion attempts across multiple environments and to uncover earlier preparations and a broader set of capabilities than public reporting revealed.
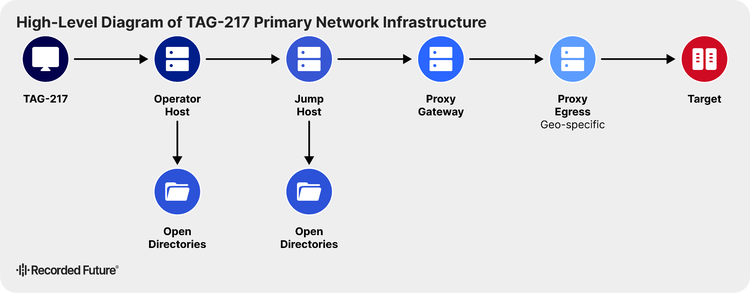
TAG-217 routed its traffic through residential internet connections, likely to reduce the chances of detection. Recorded Future analysts used open directories within TAG-217 infrastructure to further understand its operations (Source: Recorded Future)
Although Recorded Future was founded by Swedish scientists and innovators, our HQ has always been a key part of the Somerville and Boston tech startup scene. Recognized for our award-winning platform and amazing culture, the team and our HQ have changed quite a bit over the years.
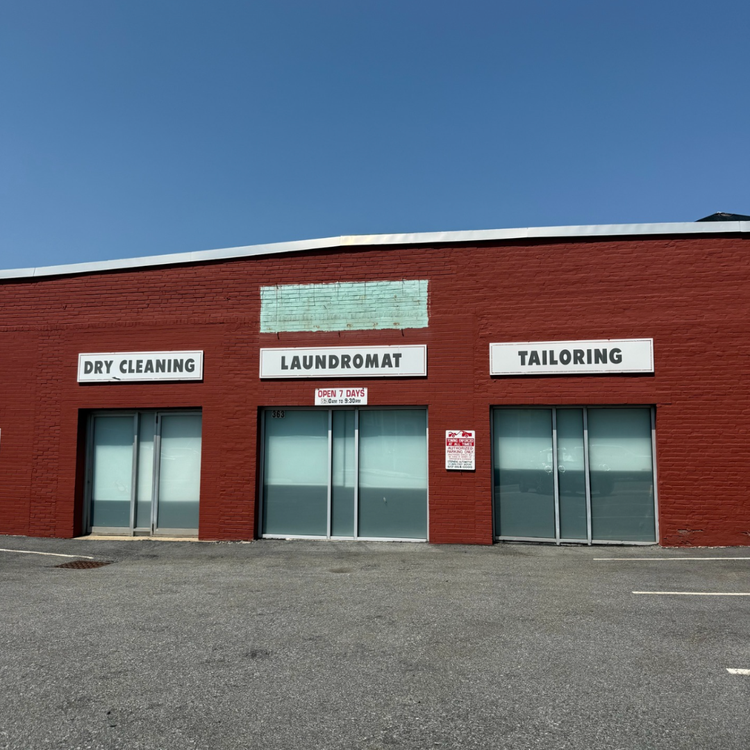
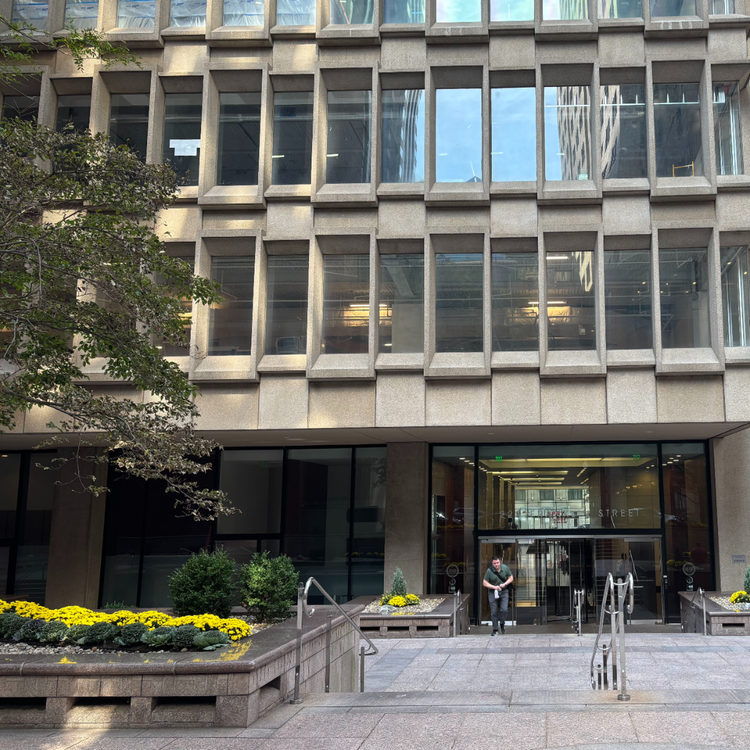
Initially established in Somerville, MA, north of Boston, the Futurists' headquarters was once a laundromat. Twelve years after we set up camp there, it is time for the next chapter. Our HQ has moved to downtown Boston in Post Office Square — and we’re ready to make new memories there.
Somerville Office laundromat sign | Boston Office (Current) on Franklin Street
Key functions operate out of our Boston-based office, including customer success, security, data engineering, product, and marketing. Nearly 200 Futurists call the Boston office their home base, and many others travel for team meetings and strategic onsites.
“In 2019, when I started, we were about 300 people globally — now we’re almost 200 just in the Boston office!”
Lacey Maddalena
Global Office Operations & Facilities Director
“We’ve grown to more than 1,000 employees, and let’s just say the days of one-person teams are behind us!”
Since mid-2025, the Kremlin has intensified restrictions on digital communications and infrastructure, very likely to suppress the organization of domestic political dissent and conduct digital surveillance within Russia. Increasingly strict measures targeting virtual private networks (VPNs), state-managed internet shutdowns, limitations on civilian communications platforms, and monitoring of domestic and foreign entities very likely represent an escalation from the approaches to censorship and surveillance pursued prior to 2024.
However, despite intensifying internet restrictions, technical and political limitations will likely prevent the Kremlin from achieving its long-held objective of a fully “sovereign internet” in the near term. The most likely scenario is that Moscow exerts extensive censorship and monitoring of online activity with increasingly strict –– though not absolute –– controls on circumvention and anonymizing tools.
Insikt Group assesses that the Kremlin’s primary objectives regarding internet restrictions are twofold: facilitating extensive surveillance of online activity to support control over the domestic information space while maintaining connectivity to the global internet, and developing national internet infrastructure under Kremlin control, enabling isolation from the global internet if the Kremlin so chooses. Efforts in support of these objectives have almost certainly provided the Kremlin with enhanced ability to control and monitor domestic online discourse.
In this environment, individuals and organizations operating in Russia are subject to increasing operational risks, including surveillance and exposure of sensitive data, challenges in conducting emergency communications, disruptions to corporate tools and digital applications, and legal risks. Entities with indirect exposure to Russia face an increased likelihood of supply-chain disruptions and sanctions violations and, over the longer term, face challenges in assessing the political and economic situation in Russia, as restrictions limit the availability of high-quality open sources.
Key Findings
The Kremlin is very likely using managed internet shutdowns across Russia to test and improve its ability to isolate the Russian internet, though technical and political limitations make it unlikely that it will achieve its objective of establishing a fully “sovereign internet” in the near term.
In the near- to medium-term, a combination of falling approval ratings for Russian President Vladimir Putin, declining public opinion amid economic strain, and ongoing Ukrainian drone strikes very likely incentivize Moscow to impose further internet restrictions, regardless of reported public dissatisfaction with some of these measures.
The Kremlin will very likely continue to pursue strategies to deter VPN use by forcing platforms to support VPN blocks and making VPN use more expensive and inconvenient, though likely avoiding direct punitive measures against individual users.
Kremlin Systematically Tightening Internet Restrictions
Since July 2025, the Kremlin has systematically tightened access to widely used civilian communications applications and VPNs, caused regular mobile internet outages across Russia, and instituted requirements that place Russian and foreign individuals and firms under increased government surveillance. The Kremlin likely views these measures as necessary to make it more difficult for Russian elites or the public to coordinate political dissent, and for the Ukrainian government to launch drone strikes against Russian critical infrastructure.
Restrictions Represent Marked Escalation in Control Over Russian Internet
Insikt Group assesses that, since 2012, Russians have seen their ability to operate without restriction on the internet decline in several waves, primarily driven by the Kremlin's calculation that Russians were using the internet to organize anti-government political actions.
2000–2012: Little Government Oversight
Laissez-Faire State Policy
During this period, the Kremlin generally viewed the internet as politically non-threatening, in part due to low internet penetration rates in Russia (from 1.8% in 2000 to 58% in 2011).
Thriving Media and Social Platforms
Individual expression on the internet was relatively free, with independent news sites such as Lenta, Novaya Gazeta, Ekho Moskvy, and Gazeta able to operate largely without government interference.
In addition, platforms such as LiveJournal and VKontakte (VK) –– Russia’s Facebook mirror –– operated largely without government control.
Minimal Government Regulation
Russian state telecommunications regulator Roskomnadzor was founded in 2008, but primarily handled telecommunications licensing rather than censorship or content filtering.
2012–2015: Blocklists and Platform Takeovers Following Mass Protests
Laws Passed Creating Blocklists of Websites
In 2012, following the largest protests in Russia since the fall of the Soviet Union, the Kremlin passed law No. 139-FZ, titled “On Introducing Amendments to the Law on Protection of Children from Information Harmful to Their Health and Development,” which created the Unified Register of Banned Websites. This introduced internet service provider (ISP)-level technical infrastructure, enabling the Russian government to block domains and IP addresses through domain name system (DNS) tampering.
In 2014, the Kremlin passed the Lugovoy Law (No. 398-FZ), allowing for extrajudicial blocking of websites the government considered “extreme” or which called for unauthorized protests.
Platform Takeovers by the Kremlin
The Russian Government started taking over platforms it considered politically threatening. For example, VKontakte founder Pavel Durov was forced out of Russia in 2014 after refusing to hand over data to the Federal Security Service (FSB). The Kremlin facilitated the transfer of control of VK to state-aligned businessmen, including Vladimir Kiriyenko, who is currently VK's CEO.
Data Localization Targeting Foreign Internet Companies
In 2014, the Russian government passed the Data Localization Law (No. 242-FZ), mandating that foreign internet companies store Russian citizens’ personal data on physical servers inside Russia, likely to make it easier for the Kremlin to access that data for surveillance purposes.
2016–2021: Surveillance Mandates and Attempts to Block Platforms
Laws Passed to Mandate Data Sharing, Restrict VPNs, and Pursue Sovereign Internet
In 2016, the Kremlin passed the Yarovaya Law (No. 374-FZ and No. 375-FZ), which forced ISPs and communication providers to retain metadata for up to three years and message and audio content for six months, and to provide that information to Russian security services without a warrant.
In 2017, the Kremlin passed the Anonymizers Law (No. 276-FZ), formally prohibiting the use of VPNs to circumvent blocked websites.
In 2019, the Kremlin passed the Sovereign Internet Law (No. 90-FZ), which required Russian ISPs to install TSPU (technical means of counteracting threats, технические средства противодействия угрозам) controlled by Roskomnadzor, thereby giving the state the power to throttle or sever external traffic to a platform.
Attempts to Block Platforms Have Mixed Results
In 2018, Roskomnadzor attempted to block Telegram by IP-banning millions of cloud servers. The attempt failed, disrupting banking and retail systems without shutting down Telegram.
In 2021, the Kremlin launched its first large-scale deployment of TSPU –– deep packet inspection (DPI) hardware –– to throttle a mainstream social media platform, thereby demonstrating technical maturity in the Kremlin’s ability to throttle platforms.
2022–2024: Crackdown on Independent Media, VPN Blocks
Mass Blocking and Shutdown of Independent Media
Following Russia’s full-scale invasion of Ukraine, the Kremlin blocked hundreds of independent news outlets (including Meduza, BBC, Radio Free Europe, and Ekho Moskvy) by pushing DNS and SNI (Server Name Indication)-level blocks to TSPU devices across all ISPs simultaneously. In addition, the Kremlin throttled, before outright blocking access to, social media platforms such as Facebook and Instagram. This was accomplished via TSPU's packet-dropping mechanism before full blocks were applied in March 2022.
In 2024, Roskomnadzor began throttling YouTube to near-unusable levels, likely to force users onto state-controlled video platforms.
Anti-VPN Actions
In 2023–2024, Roskomnadzor began blocking underlying VPN protocols, including OpenVPN, WireGuard, and Shadowsocks, via DPI hardware.
In 2024, the VPN Advertising Ban (No. 406-FZ) took effect, prohibiting the advertising of VPNs and other tools that circumvent blocks on certain websites and platforms.
Table 1:Russian approaches to internet restrictions from 2000–2024 (Source: Recorded Future)
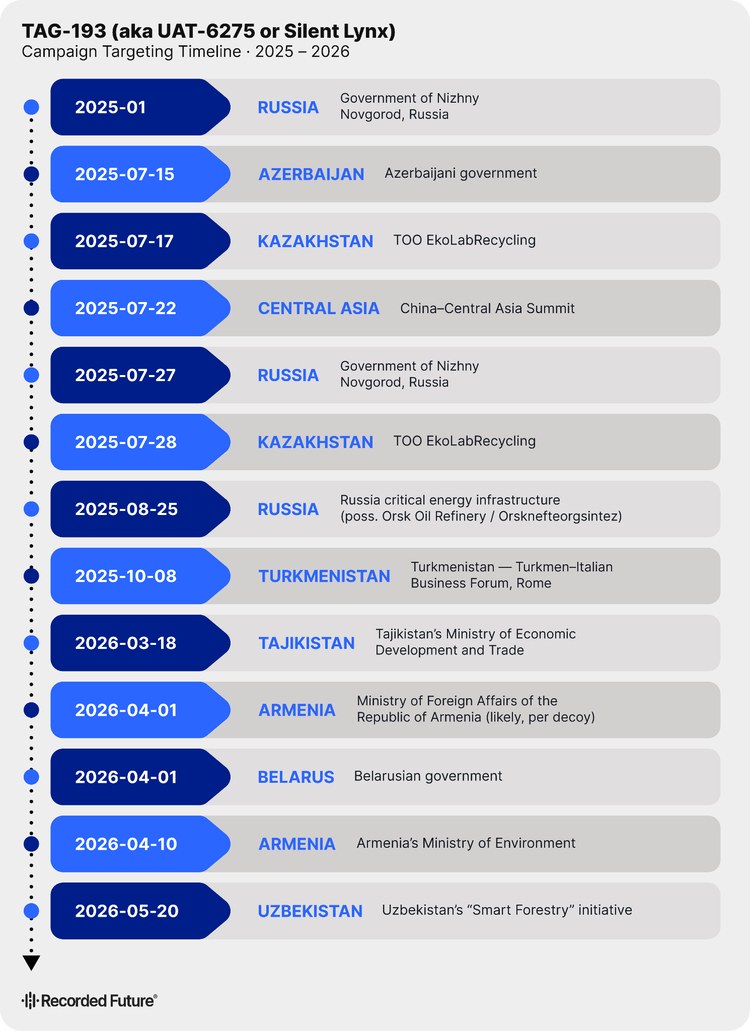
Joint research by Cisco Talos and Recorded Future’s Insikt Group examined sustained cyber-espionage activity by TAG-193 targeting government organizations across Central Asia and the wider Commonwealth of Independent States (CIS). Tracked by Cisco Talos as UAT-6275 and also known as Silent Lynx, TAG-193 combines diplomatic and economic targeting with an interest in environmental policy, water resources, and forestry. Exposed infrastructure provided new visibility into its malware, operational practices, and evolving delivery techniques. The findings point to possible links to Kazakhstan, but questions remain about the group’s origins. This post highlights how TAG-193’s operations reflect the intelligence value of regional diplomacy and resource management, and how its expanding toolkit supports that mission.
Government Targeting across the Region
TAG-193’s targeting extends across government institutions responsible for diplomacy, economic development, agriculture, and environmental management. These organizations hold information that can inform negotiations, economic planning, and regional security decisions. Across Central Asia, shared river systems and interconnected energy and transport infrastructure give such information particular strategic value.
In September 2026, Insikt Group® identified 94 high-impact vulnerabilities to prioritize for remediation, 59 of which had a Very Critical Recorded Future Risk Score. This represents a 29% increase from last month. 43 of these vulnerabilities were surfaced through the US Cybersecurity and Infrastructure Security Agency (CISA)’s Known Exploited Vulnerabilities (KEV) catalog, 37 were reported in open sources and validated by Insikt Group, and 14 were exclusively surfaced through honeypot data.
The 94 vulnerabilities identified affected products from 58 vendors, with Linux and Microsoft together accounting for approximately 13% of the vulnerabilities. The remaining exposures spanned network edge and security management appliances; operating systems (OS) and mobile devices; collaboration, content management, and enterprise platforms; artificial intelligence (AI), developer, and automation tools; and operational technology and industrial systems.
September reporting also highlighted zero-day exploitation of CVE-2026-88771 and CVE-2026-88772 (NetScaler), as well as renewed exploitation of CVE-2026-35273 (PeopleSoft) against unpatched systems.
Quick reference: September 2026 vulnerability table
All 80 vulnerabilities below were actively exploited or operationally weaponized in September 2026.This table does not include the 14 CVEs that were exclusively surfaced through honeypot data, which are available to Recorded Future Intelligence Platform customers via the CVE Monthly report.The table below also provides examples of public PoCs identified by Insikt Group. These PoCs were not tested for accuracy or efficacy. Vulnerability management teams should exercise caution and verify the validity of PoCs before testing.
Table 1:List of vulnerabilities that were actively exploited in September 2026 based on Recorded Future data (excluding honeypot-sourced CVEs).
Key trends: September 2026
September reporting linked NightEagle and UNC3569 to GhostContainer and GRAYRABBIT deployments, while Cisco FMC exploitation by three threat clusters led to credential theft, Cyclops Blink deployment, and Qilin ransomware.
A suspected Chinese-speaking actor used a SecFlow-based environment with Claude-, Qwen-, and DeepSeek-backed workers, and a suspected Russian-speaking actor used hundreds of AI agents to compromise at least 440 PaperCut NG/MF instances associated with 395 organizations.
47 of the 94 vulnerabilities enabled remote code execution (RCE). Network-edge and security-management products were the most affected product type. Apache and Google represented the largest share of vendors, with three RCE vulnerabilities each.
Insikt Group identified public proof-of-concept (PoC) exploits or scanners for 75 of the 94 vulnerabilities identified in September.
The most common weakness class was CWE-306 (Missing Authentication for Critical Function), with seven vulnerabilities, followed by CWE-22 (Path Traversal), with six. CWE-78 (OS Command Injection), CWE-89 (SQL Injection), and CWE-94 (Code Injection) each affected five vulnerabilities.
Eight of the 94 vulnerabilities were at least five years old, and the oldest was approximately 12 years old.
Trend analysis
AI-assisted campaigns combine older flaws with post-compromise tooling
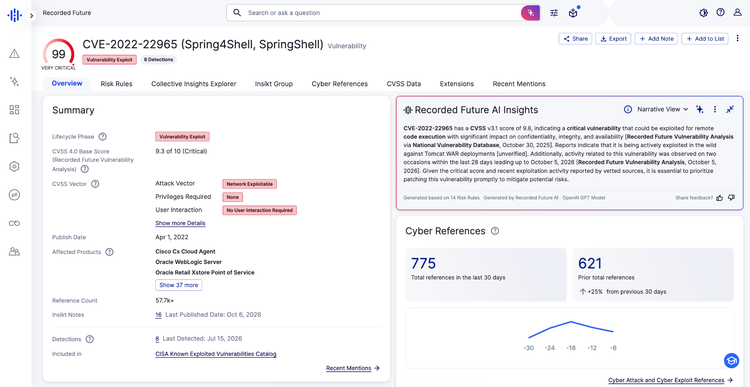
Insikt Group detailed a suspected Chinese-speaking actor using a SecFlow-based operations environment with Claude-, Qwen-, and DeepSeek-backed workers to support reconnaissance, exploitation, post-exploitation, and collection across Asian targets. The threat actor tested or staged workflows for CVE-2014-6271, CVE-2020-1938, CVE-2022-22965, CVE-2016-4437, CVE-2021-43798, CVE-2024-4956, CVE-2021-29441, and CVE-2021-44228. The workflow routed candidate findings to vulnerability-specific playbooks, but not every attempt produced confirmed access.
A separate September report described a suspected Russian-speaking threat actor using hundreds of AI agents in a campaign targeting PaperCut NG/MF. The campaign exploited CVE-2026-81578 and CVE-2026-82078, compromising at least 440 instances associated with 395 organizations.
Figure 1:Risk Rules history on theVulnerability Intelligence Card®for CVE-2022-22965 in Recorded Future (Source: Recorded Future)
One malware hash can turn a vague alert into a concrete investigation. Analysts can search endpoints for the exact file, trace where it appeared, and determine whether related activity exists elsewhere. But if the attacker changes the file, the hash changes too. Domains and Internet Protocol (IP) addresses can also lose relevance as attackers rotate infrastructure.
This is why malware indicators of compromise work best as evidence within a larger investigation, not as isolated entries on a blocklist. Their value grows when analysts can establish where an indicator came from, how recently it was observed, what threats are connected to it, and whether those connections matter to their organization.
Malware indicators of compromise are technical artifacts or observations that suggest malicious activity. They help security teams detect, investigate, and contain threats, but an IoC is most useful when analysts can assess its source, timing, confidence, and relationship to other threat activity.
Key takeaways
Malware indicators can include file-based artifacts, network infrastructure, and other technical evidence associated with malicious activity.
IoCs do not exclusively describe past attacks. They can point to malicious activity that may be underway or has already occurred.
Indicator types have different defensive lifespans. An IP address may quickly lose relevance, while a file hash remains an exact identifier for the same sample even if attackers create a new version.
Threat intelligence can add context that helps analysts prioritize IoCs, connect related activity, and move from an isolated match toward a wider investigation.
What are malware indicators of compromise?
An indicator of compromise (IoC) is a technical artifact or observable that suggests malicious activity. The National Institute of Standards and Technology (NIST) defines IoCs broadly enough to include signs that an attack may be imminent, underway, or that a compromise may already have occurred.
For a security operations center (SOC) analyst or incident responder, an IoC can help answer a practical question: Have we seen evidence associated with this threat in our environment?
Analysts can use malware IoCs to validate an alert, search logs and endpoints for related activity, or scope an incident after malicious activity is confirmed. They can also use an indicator as a starting point for investigating connected infrastructure, malware, or attacker behavior.
An IoC does not automatically prove that an organization has been compromised. Context matters. Finding a malware hash executing on an endpoint carries a different meaning from finding the same hash in an intelligence feed.
IoCs and TTPs serve different purposes
Indicators of compromise identify observable evidence associated with malicious activity. Tactics, techniques, and procedures (TTPs) describe how an adversary operates.
A specific command-and-control domain is an IoC. The techniques an attacker repeatedly uses to establish persistence or move through a network are TTPs.
Atomic indicators are often easier to match against security telemetry, but attackers may be able to change them quickly. TTP-based detection can be harder to evade when it focuses on established attacker behavior, but it can also demand richer telemetry and more detection engineering.
Security teams do not need to choose one or the other. An IoC can provide the first concrete lead, while TTPs can help analysts search for related activity after an attacker changes a domain or recompiles malware.
The most common types of malware indicators
Malware indicators generally appear either in files and host activity or in network communications. Each gives analysts a different view of what the malware has done.
File-based IoCs
File hashes such as SHA-256 fingerprints allow security tools to identify an exact known file. They provide a precise match, but attackers can alter a malware sample and generate a new hash.
Other file and host artifacts can reveal how malware operates after reaching a system. Analysts may examine suspicious file names and paths along with changes malware makes to the operating system, such as registry activity or mutex creation.
These artifacts can help investigators determine whether the same malware has appeared elsewhere in the environment.
Network-based IoCs
Network indicators show where malware connects or where malicious content is hosted.
These may include IP addresses associated with command-and-control infrastructure, domains used to distribute malware, or URLs connected to malicious activity. Analysts can also examine characteristics of network traffic when those characteristics are specific enough to the threat.
Network IoCs can help teams find infected systems that contacted known malicious infrastructure. Their usefulness can change over time because infrastructure may be abandoned, reassigned, or shared with legitimate services.
Why raw IoCs have limits
The main problem with raw malware indicators is not that they are useless. It is that the indicator alone often does not tell an analyst enough to make a good decision.
Indicators can lose defensive value quickly
Threat actors can move command-and-control infrastructure, register new domains, or change malware files to avoid known indicators. This makes some IoCs highly time-sensitive.
It is more accurate to think in terms of defensive lifespan than to assume every IoC simply expires. A hash continues to identify the same file, for example, but it stops detecting new versions once an attacker changes the sample.
A malicious label does not provide organizational context
An IP address listed as malicious does not tell a SOC whether its own systems communicated with it, whether the activity is current, or what defensive action is appropriate.
This is where raw feeds can create unnecessary analyst work. Teams must investigate why an indicator was flagged and decide whether that evidence applies to their environment.
Recorded Future recommends combining external indicator context with internal network data and subjecting indicators to organizational vetting before using them for detection in its guidance on indicators of compromise.
More indicators can create more noise
Threat intelligence feeds can contain overlapping, stale, or irrelevant information. Adding feeds without a way to assess their quality can increase alert volume without giving analysts better evidence.
Volume can still matter when a source provides useful threat coverage. It should not serve as the only measure of intelligence quality. Timeliness, confidence, provenance, and relevance also affect whether an indicator deserves attention.
IoCs do not provide complete threat visibility
Threat intelligence can tell analysts a great deal about an indicator that has already been observed. It cannot provide context for infrastructure or malware that its collection sources have never seen.
Better information about known IoCs can improve interpretation, but it does not guarantee complete threat visibility.
How threat intelligence makes malware indicators more useful
Security teams can get more value from IoCs by connecting individual observations to evidence that explains why they matter.
Recorded Future malware intelligence connects malware samples with associated IoCs and threat context. It also supports automated YARA rule generation for malware hunting.
Add context before taking action
Useful context can show when an indicator was observed, what malware is associated with it, and what other infrastructure or activity is connected to it.
Recorded Future uses Risk Scores to help analysts prioritize indicators. These scores can help determine what deserves attention, but they should inform security decisions rather than replace organizational context.
Automate repetitive IoC work
Large indicator volumes make manual lookup difficult. Application programming interfaces (APIs) and security integrations can automate IoC lookup, add threat context, and bring external intelligence into existing security workflows.
Recorded Future Cyber Operations supports these workflows through threat intelligence, APIs, and integrations.
Automation does not need to mean automatic blocking. Teams can automate research and prioritization while applying stronger requirements before an indicator triggers a direct enforcement action.
Turn individual indicators into threat-hunting leads
An IoC often becomes more useful when it leads analysts to related activity.
A malware sample can point investigators toward related variants, behaviors, and infrastructure. Recorded Future malware intelligence includes Auto YARA, which analyzes malware samples for distinctive patterns and generates YARA rules that analysts can use in malware hunting.
This lets teams move beyond searching only for a known hash and look for related files that share useful characteristics. Recorded Future University's guide to malware hunting provides more detail on how threat hunters approach that work.
Best practices for an IoC-driven security program
A useful IoC program should focus on the quality of security decisions rather than the size of the indicator database.
Check context before enforcement. Establish the source, confidence, and timing of an indicator before deciding whether it should trigger blocking or containment.
Match automation to the consequence. Automating lookup and prioritization carries less operational risk than automatically blocking infrastructure. Raise the confidence requirement as the action becomes harder to reverse.
Connect external intelligence with internal evidence. External threat data can show why an indicator deserves attention. Internal telemetry shows whether that threat has reached systems that matter to your organization.
Review active indicator sets over time. An indicator that no longer belongs in an active detection or blocking rule may still have value for historical investigation. Removing it from active enforcement does not mean deleting the intelligence.
Recorded Future's research into malware and vulnerability trends provides further context on changing malware activity and the threats defenders need to watch.
The future of IoC detection
Attackers can change hashes, IP addresses, and domains to evade known indicators. Security teams, therefore, need ways to connect individual IoCs to related malware activity and attacker behavior.
Automated malware analysis and detection-rule generation can help teams move from a new observation to a broader hunt with less manual work. This does not make atomic indicators obsolete. It gives teams another way to use them alongside behavioral detections and threat context.
Recorded Future combines malware analysis with threat intelligence so security teams can investigate individual IoCs in the context of related malware, infrastructure, and behavior.
Ready to spend less time chasing stale or low-value indicators? Request a demo to see how Recorded Future can help your team add context to malware IoCs and put threat intelligence into existing security workflows.
FAQs about using malware IoCs in security operations
Are YARA rules the same as malware IoCs?
No. An IoC is an observable artifact or piece of evidence associated with malicious activity. A YARA rule is detection logic that searches files or other data for defined patterns. Analysts can create YARA rules from characteristics found during malware analysis, allowing them to search for related samples rather than relying on one exact file hash.
How are malware indicators of compromise collected and shared?
IoCs can come from malware analysis, incident investigations, security telemetry, threat research, and intelligence-sharing communities. Organizations can share structured threat information using standards such as Structured Threat Information Expression (STIX), while Trusted Automated Exchange of Intelligence Information (TAXII) supports the exchange of that information between systems.
Are indicators of attack the same as indicators of compromise?
No, although the distinction is not simply that one predicts an attack and the other describes the past. Indicators of attack (IoAs) focus on behaviors or activity associated with attacker intent or an attack in progress. IoCs identify technical evidence associated with malicious activity, which may relate to activity that is ongoing or has already occurred.
Can two intelligence sources assess the same IoC differently?
Yes. Intelligence sources may rely on different observations, collection methods, scoring systems, and timeframes. Infrastructure can also change ownership or use over time. Analysts should consider the source, supporting evidence, and observation dates rather than assuming every malicious classification carries the same meaning.
Today, Recorded Future is announcing AI Infrastructure Indicator Lists, curated datasets for security teams to identify, monitor, and implement controls for AI-related network traffic. AI Infrastructure Indicator Lists are included for free for Recorded Future customers with a Cyber Operations license.
Artificial intelligence has increasingly become enterprise infrastructure and organizations are now confronting unsanctioned tool use (also known as shadow AI), data exposure, and autonomous behavior that their controls cannot always see.
Recorded Future's AI Infrastructure Indicator Lists focus on closing this gap across risk, IT, and GRC teams whether the goal is policy enforcement, data loss prevention, or detecting shadow AI.
AI is accumulating security debt
The hidden risks of an abundance of AI within an organization are often overshadowed by the daily threats that have to be prioritized by a security team. Last year, we reported on how security debt has been accrued by almost every organization, and the unaddressed risks are piling up faster than teams can service them. As a result, blind spots in AI governance are also increasing.
Take, for example, agentic AI. Its adoption is accelerating rapidly and agents are operating across interconnected systems, giving threat actors more room to exploit vulnerabilities at the organizational level and across supply chains.
Consider a free, viral AI assistant that an employee discovers on social media and installs on their own machine to boost productivity. No procurement process, no security review, no IT visibility.
That's not a hypothetical. OpenClaw, a free open-source AI assistant, saw explosive adoption earlier this year with almost no organizational oversight. Multiply that across a workforce and security teams left trying to govern tools they don't know exist.
By 2027, an estimated 75% of employees are expected to adopt or build technology outside IT governance. As agents become more ubiquitous, defenders need to ensure they can identify which technologies are living on their networks, and begin to track and manage access permissions for autonomous processes in the same way they manage permissions for human users.
Introducing AI Infrastructure Indicator Lists
While many threat feeds give you a wall of indicators and leave you to figure out what they are and whether to trust them, Recorded Future’s AI Infrastructure Indicator Lists do the opposite.
AI Infrastructure Indicator Lists are curated, regularly refreshed datasets that map the AI infrastructure your users, developers, and adversaries are actually reaching for. Indicators include IP addresses, CIDR ranges, and domains, carrying their own Risk Scores and comment fields with service attribution.
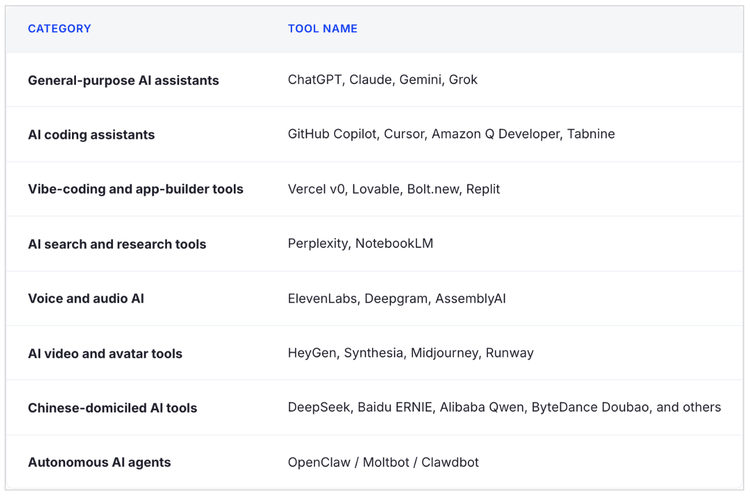
Recorded Future provides two distinct AI-related lists: the AI infrastructure list and the Chinese AI infrastructure list. The lists cover a comprehensive range of tools, including general-purpose AI assistants, AI coding assistants, vibe-coding tools, AI search tools, voice and audio AI tools, AI video tools, Chinese-domiciled AI tools, and autonomous AI agents.
Figure 1: List of AI tools monitored in AI Infrastructure Indicator Lists
Japan’s Active Cyber Defense (ACD) framework shifts the country from voluntary information sharing and post-incident investigation to mandatory reporting, preventive communications analysis, and limited disruption of attack infrastructure. Beginning October 1, 2026, designated critical infrastructure operators must notify the government about covered systems and report qualifying incidents; those with existing systems have six months to submit initial notifications. New authorities that allow the government to collect and act on communications information (通信情報) will not take effect until November 23, 2027.
The transition comes amid persistent Chinese strategic collection, North Korean revenue-driven cyber operations, and Russian cyber espionage. In cases directly linked to Japan, indicators related to these threat activities were frequently observed among victims, overseas affiliates, vendors, carriers, hosting providers, and government agencies. We assess with moderate confidence that connecting those indicators quickly enough to identify broader campaigns, warn potentially affected organizations, and coordinate defensive action will be ACD’s principal operational constraint. Its practical reach will extend beyond designated operators: overseas compromises may trigger Japanese reporting duties when they reach covered systems; vendors should expect remediation requests; carriers may be required to assist government measures; and hosting providers may encounter action against malicious systems operating on their infrastructure.
We further assess that improved visibility within covered organizations will likely make foreign subsidiaries, non-designated suppliers, employees, and external platforms comparatively attractive access paths for threat actors without reducing overall attack volume (because initial activity along these routes likely falls outside ACD’s mandatory-reporting perimeter or precedes recognition of a qualifying incident). Companies should therefore treat ACD not as a narrow compliance requirement, but as a change to incident escalation, contracting, evidence preservation, and public-private intelligence sharing across their operations and supply chains.
Key Findings
Japan’s Active Cyber Defense is a two-statute framework — Acts 42 and 43 of 2025 — organized around four principal pillars: public-private collaboration, government use of communications information, access and neutralization of cyber threats, and institutional restructuring and independent oversight. Act 42 establishes the reporting, information-sharing, communications-analysis, and oversight framework, while Act 43 amends existing laws to authorize neutralization measures and reorganize Japan’s cybersecurity institutions.
Japan's mandatory cyber incident reporting begins October 1, 2026, but the government's communications-information collection capacity will not enter force until November 23, 2027 — a gap of roughly 13 months between the reporting duty and the detection capability intended to support it.
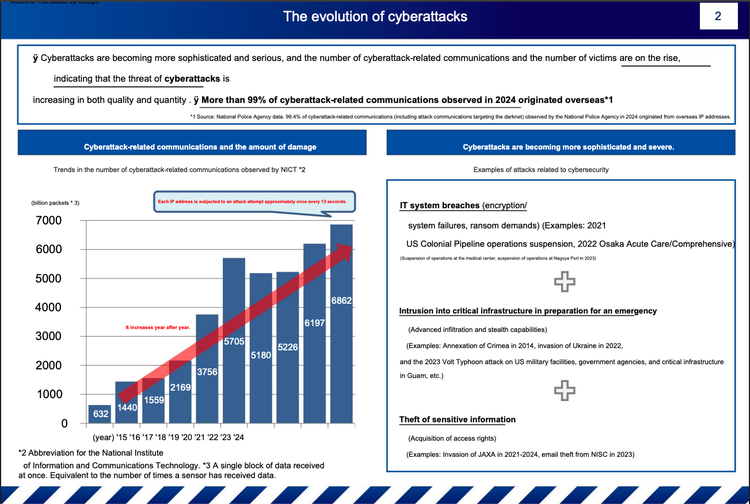
Japanese agencies recorded an eleven-fold increase in cyberattack-related packets from 63.2 billion in 2015 to 686.2 billion in 2024, while 99.4% of observed attack packets used overseas source IP addresses. This is equivalent to roughly one attempted attack per IP address every thirteen seconds.
Chinese, Russian, and North Korean cyber operations targeting Japan reflect distinct primary drivers: China pursues enduring strategic intelligence collection, North Korea prioritizes sanctions-driven revenue generation, and Russia combines standing espionage requirements with disruption that can track Japanese policy decisions.
Threat actors will likely emphasize five access paths likely to maintain limited visibility under ACD after reporting begins on October 1, 2026: foreign subsidiaries, non-designated suppliers, individual employees, consumer platforms, and short-lived infrastructure distributed across hosting providers. Organizations occupying these positions may consequently face greater targeting despite having no direct ACD reporting obligation.
Background
Japan’s Active Cyber Defense framework (能動的サイバー防御, “ACD”) is a package of legal and institutional reforms intended to prevent serious cyberattacks against government and critical infrastructure. The ACD establishes mechanisms for public-private collaboration (官民連携), government use of specified communications information (通信情報の利用), and narrowly defined authority to access and neutralize systems being used to conduct cyberattacks (アクセス・無害化措置) before they cause significant harm or damage. The framework also restructures the government’s central cybersecurity institutions and establishes independent oversight of the framework’s most sensitive authorities.
The framework is principally established through two statutes passed by the National Diet (国会) on May 16, 2025, and promulgated on May 23, 2025:
Cyber Response Capability Strengthening Act (サイバー対処能力強化法), Act No. 42 of 2025 Full statutory title: Act on the Prevention of Damage from Unauthorized Acts against Important Computers (重要電子計算機に対する不正な行為による被害の防止に関する法律). This statute establishes the critical-infrastructure reporting, communications information use, public-private information-sharing, and independent oversight framework.
Cyber Response Capability Strengthening Act Arrangement Act (サイバー対処能力強化法整備法), Act No. 43 of 2025 Full statutory title: Act on the Arrangement of Related Laws Accompanying Enforcement of the Act on the Prevention of Damage from Unauthorized Acts against Important Computers (重要電子計算機に対する不正な行為による被害の防止に関する法律の施行に伴う関係法律の整備等に関する法律). This companion statute amends existing legislation, including the Police Duties Execution Act (警察官職務執行法), Self-Defense Forces Act (自衛隊法), and the 2014 Basic Act on Cybersecurity (サイバーセキュリティ基本法). These amendments authorize access-and-neutralization measures, restructure the government’s cybersecurity institutions, and strengthen interagency coordination.
Implementation is phased; the reorganization of the government’s central cybersecurity institutions took effect on July 1, 2025, and the independent Japan Active Cyber Defense Oversight Commission (サイバー通信情報監理委員会) was established on April 1, 2026. The public-private reporting and access-and-neutralization provisions will take effect on October 1, 2026. Supplementary Article 1(4) of Act No. 42 requires the communications-information use provisions to enter force within two years and six months of promulgation, by November 23, 2027.
The Four Pillars
For explanatory purposes, this overview organizes the ACD framework into four principal pillars:
Public-Private Collaboration (官民連携)
Government Use of Communications Information (通信情報の利用)
Government Access and Neutralization Measures (アクセス・無害化措置)
Institutional Restructuring and Independent Oversight (組織・体制整備・独立監督)
Together, the pillars summarize the framework’s principal government authorities, institutional changes, oversight mechanisms, and legal obligations for public- and private-sector organizations. They reflect a fundamental shift in Japan’s cybersecurity posture toward earlier detection, structured public-private cooperation, and preventive disruption, while placing the framework’s most sensitive authorities under specialized independent oversight. They do not encompass every provision within the two statutes.
Pillar 1 — Public-Private Collaboration (官民連携)
Pillar 1 creates mandatory reporting requirements and a consent-based information-sharing framework. For ACD reporting purposes, “designated operators” (特別社会基盤事業者) are critical-infrastructure operators designated under the Economic Security Promotion Act that use covered systems — Specified Important Computers (特定重要電子計算機). These include qualifying operators in sectors such as electricity, telecommunications, transport, and finance. Designated critical-infrastructure operators must notify the responsible government minister when they introduce covered systems — Specified Important Computers — and report qualifying cyber incidents (特定侵害事象等) to that minister and the prime minister. The prime minister will establish a statutory council (協議会)for information sharing and countermeasures to prevent damage to Important Computers (重要電子計算機) — the law’s broader category of protected computer systems, including Specified Important Computers — from specified unauthorized acts. This statutory council will replace and strengthen the existing 2019 Cybersecurity Council (サイバーセキュリティ協議会). Council members may be required to provide relevant materials and must comply with statutory confidentiality requirements.
In practice, two things change under Pillar 1. First, ACD-specific reporting becomes a statutory duty for designated critical-infrastructure operators that use covered systems — including operators in sectors such as electricity, telecommunications, transport, and finance — thereby reducing the government’s dependence on voluntary disclosure once a qualifying incident is detected. Second, government-to-industry sharing enters a protected statutory framework designed to support the distribution of sensitive threat and mitigation information. Pillar 1, therefore, aims to give the government broader visibility into threats while providing participating organizations with actionable warnings. Joining the council is voluntary, but participating members must comply with statutory information-handling and confidentiality obligations and may be required to provide relevant materials.
Pillar 2 — Government Use of Communications Information (通信情報の利用)
Pillar 2 authorizes the government to obtain and analyze specified communications information through two principal pathways:
Voluntary agreements with participating organizations (当事者協定)
Defined government measures involving certain foreign-related communications (国外関係通信)
The latter includes foreign-to-foreign communications transiting Japan, as well as limited foreign-to-domestic or domestic-to-foreign communications associated with specified cyber threats. Before a government employee may review acquired data, automated selection (自動選別) must retain only defined mechanical information (機械的情報), such as IP addresses, timestamps, and command information, and delete the remainder. Government measures not based on consent generally require prior approval from the Japan Active Cyber Defense Oversight Commission.
In practice, two things change under Pillar 2. First, the government gains a standing statutory framework for obtaining and analyzing communications information for preventive cyber defense: Japan’s pre-ACD Communications Interception Act authorized interception only for criminal investigations of specified offenses and pursuant to a judge-issued warrant, and Japan lacked a comparable framework for systematic preventive collection and analysis. Second, the limit on what may be retained is enforced by the collection architecture rather than by rules governing analyst conduct. Officials set the selection criteria, but no person may examine the acquired data before the selection is complete, and unselected material must be deleted immediately.
Pillar 3 — Government Access and Neutralization Measures (アクセス・無害化措置)
Pillar 3 establishes access-and-neutralization authority through amendments to the Police Duties Execution Act and Self-Defense Forces Act. Specially designated Cyber Harm Prevention Measure Enforcement Officers (サイバー危害防止措置執行官) may order an administrator to take necessary measures against a computer associated with communications or electronic records identified as being used in malicious cyber activity, or may take those measures directly. Depending on the circumstances, those measures could include:
Changing system settings to prevent an attacker from continuing to control compromised infrastructure
The authority applies when an urgent need exists to prevent serious harm to life, physical safety, or property. Measures generally require prior approval from the Japan Active Cyber Defense Oversight Commission. When circumstances leave no time for advance approval, a measure may proceed, but the Commission must be notified promptly afterward and confirm whether the measure was appropriate.
In practice, Pillar 3 gives designated officers legal authority to intervene against attack infrastructure — including through actions that could otherwise constitute unauthorized access under the 1999 Act on Prohibition of Unauthorized Computer Access — rather than relying on criminal investigation or voluntary remediation. The authority can reach infrastructure outside Japan, but overseas operations are subject to additional restrictions. Police measures against systems not reasonably believed to be in Japan may be conducted only by officers of the National Police Agency (NPA) following consultation with the minister for foreign affairs. In cases involving highly organized and planned threats by a person outside Japan, the prime minister may order the Japan Self-Defense Forces (JSDF) to conduct Communications Protection Measures (通信防護措置) jointly with police, but only when the JSDF’s specialized technology or information is indispensable, and the National Public Safety Commission has requested or consented to JSDF involvement.
Pillar 4 — Institutional Restructuring and Independent Oversight (組織・体制整備・独立監督)
Pillar 4 restructures the government's cybersecurity institutions and creates an independent body to oversee the authorities established in Pillars 2 and 3. The reforms include:
The National Cybersecurity Office (国家サイバー統括室, NCO) replaces the former National Center of Incident Readiness and Strategy for Cybersecurity (内閣サイバーセキュリティセンター, NISC).
A new cabinet cyber officer (内閣サイバー官) leads the NCO and coordinates cybersecurity policy across the government.
The restructured Cybersecurity Strategy Headquarters (サイバーセキュリティ戦略本部) is headed by the prime minister (内閣総理大臣) rather than the chief cabinet secretary, with all other ministers of state as members.
The Japan Active Cyber Defense Oversight Commission (サイバー通信情報監理委員会) grants prior approvals, conducts ongoing inspections, reviews emergency measures taken without advance approval, and may issue recommendations.
In practice, two things change under Pillar 4. First, central coordination is elevated: the Strategy Headquarters is now chaired by the prime minister rather than the chief cabinet secretary, while the cabinet cyber officer and NCO support government-wide coordination. Second, the sensitive authorities in Pillars 2 and 3 are reviewed by a commission separate from the agencies implementing them. Rather than requiring judicial warrants, the framework uses independent administrative review: the Japan Active Cyber Defense Oversight Commission approves nonconsensual communications acquisition and ordinarily approves neutralization measures, conducts continuing inspections, and receives notification of emergency measures. It may issue recommendations and must report annually to the National Diet through the prime minister and publish a summary. Pillar 4 does not establish a separate offensive cyber authority; cross-border neutralization remains governed by Pillar 3.
Key Limits on ACD Authority
The ACD framework expands Japan’s preventive cybersecurity authorities but does not provide an unrestricted mandate for surveillance or offensive cyber operations. Its principal statutory boundaries include:
Communications analysis is not general content surveillance. Human review is limited to automatically selected mechanical information, including technical data such as IP addresses, timestamps, and computer commands, meeting statutory criteria. Purely domestic communications are not a category that the government may target without the parties’ consent. If included in data provided under a Party Agreement (当事者協定), they must be excluded through automated selection and deleted without human review. Separate laws continue to govern warrant-based interception for criminal investigations.
Access and neutralization authority is tied to specific mission objectives outlined in the ACD, rather than blanket provisions for government operators. Measures must address communications or electronic records used or reasonably suspected of being used in malicious activity and must be urgently necessary to prevent serious harm to life, physical safety, or property. Overseas measures carry additional procedural and international-law requirements.
The JSDF cannot independently initiate Communications Protection Measures. Its involvement is limited to highly organized and planned threats by a person outside Japan that present a high risk of serious, difficult-to-recover disruption, and requires a case-by-case finding that the JSDF’s technology or information is essential in preventing that disruption. Qualifying action requires a prime ministerial order, a request from or the consent of the National Public Safety Commission, and joint implementation with the police.
Reporting obligations are not universal. They apply to designated critical-infrastructure operators and covered systems, not to every Japanese organization or local government. Local governments instead fall under the separate Local Autonomy Act, which has required them, since April 1, 2026, to establish cybersecurity policies and implement corresponding measures. Qualifying local-government systems may still receive protection under the ACD framework.
Tokyo’s Rationale For the ACD
The ACD framework originates in Japan's 2022 National Security Strategy (NSS), which identified a rapidly deteriorating cyber threat environment and concluded that Japan’s legal authorities and institutional capabilities required expansion. The NSS stated that the “threat of cyberattacks, in which the risk of exposure is relatively low and attackers have an advantage, is growing rapidly.” In essence, cyberattacks were seen as low-risk (for the attackers), potentially high-impact means of disrupting operations, stealing information, or advancing strategic and financial objectives while complicating detection, attribution, and timely government response. The NSS set the objective that Japan’s cybersecurity response capabilities should be “strengthened equal to or surpassing the level of leading Western countries.” Tokyo’s rationale can be organized around three overlapping pressures: a sharp increase in malicious cyber activity observed by Japanese authorities; several high-profile cyberattacks that disrupted Japanese public- and private-sector operations; and gaps in the government’s legal authorities and institutional capabilities for sharing information, analyzing threats, and taking preventive action.
First, Japanese authorities have identified an increase in foreign-origin cyberattacks against Japanese public- and private-sector entities. A September 2025 Japanese NCO briefing document reported, citing the NPA, that 99.4% of observed attack packets in 2024 originated from overseas IP addresses (Figure 1). The same document, citing the National Institute of Information and Communications Technology (NICT), reported an approximately elevenfold increase in cyberattack-related communications between 2015 and 2024, from 63.2 billion observed packets in 2015 to 686.2 billion in 2024. The briefing described this volume as equivalent to approximately one attempted attack per IP address every thirteen seconds, although the underlying measurement represents packets received by sensors rather than confirmed, discrete attacks. Neither dataset identifies actors or intent, and the same briefing explains why the overseas share does not establish that the actors themselves are specifically based overseas: attacks are routed through chains of compromised intermediary machines, so tracing even a domestic-looking source usually leads to an overseas relay. Nevertheless, these figures indicate sustained growth in hostile traffic reaching the Japanese address space.
We know attackers are already using AI to operate at machine speed, running more frequent and more effective attacks. They're automating reconnaissance, standing up infrastructure, and pivoting faster than human analysts can triage an alert. We have seen the cyber kill chain that used to unfold step by step now happens in the blink of an eye, and defenders are struggling to keep up in a fight that no longer gives them time to react.
It's clear that organizations need to reduce risk, defend pre-attack, and act at machine speed. But beyond just moving faster, they may need to rethink defense entirely. Imagine not scrambling to keep pace with the threat landscape, but moving with it: changing as it changes and acting as fast as the attacker acts. That's a world where an autonomous defense system works alongside defenders, applying intelligence at the speed and scale today's threats demand.
Today at Mastercard RiskX in Arizona, we premiered an autonomous defense platform built into Recorded Future. The age of AI action has arrived, and we're excited to show you what's next. Read on to see how this capability came to be, why it's a fundamentally different way to defend, and how you can be a part of it.
From answers to actions
AI for threat intelligence has come a long way. In a short time, analysts and security leaders have gone from searching for answers to finding them fast, thanks to capabilities like AI Insights and Sessions in Recorded Future AI. At the core of it all is the Intelligence Graph®, which turns large sums of data and information into actionable insights, and gives Recorded Future AI the context to deliver the right answer to analysts in seconds.
That success created a new demand: Analysts and business leaders wanted this same intelligence, at the same speed, everywhere they worked — not just inside the Recorded Future Platform. That's why we built Recorded Future Model Context Protocol (MCP). Agents, whether ours or our customers', run across many tools and platforms. This gives them direct, standardized, and cost-efficient access to Recorded Future intelligence.
The Intelligence Graph®, Recorded Future AI's Insights and Sessions, and Recorded Future MCP have laid the foundation for what comes next: defending at the pace adversaries set. To keep up with adversaries, analysts need to act at their speed, confidently taking 10 actions where they once had time for one. They need to spend their time focused on business outcomes, not buried in process. Ultimately, they need a fundamentally different way to use intelligence and act. That's why we're building autonomous defense.
What autonomous defense can do
This is a different way to think about the day-to-day analyst workflow. Analysts can task Recorded Future’s autonomous defense with a goal, not just a question, and it will go from there: drawing on the Intelligence Graph®, deciding what the situation calls for, and delivering outputs directly into your team's existing tools across over 100 integrations. It can act on your behalf, clearing away work so your team can focus on the outcome, not the process.
Autonomous defense runs on the Intelligence Graph® with over 15 years of threat intelligence and analyst research, combined with your own organizational context through your Private Graph, so the system knows what's relevant before anything happens. It's the same intelligence layer customers already use across cyber operations, third-party risk, digital risk protection, and counter-fraud, now can be put to work taking agentic action. When your threat priorities shift or a new vulnerability surfaces, agents already understand why it matters to your environment and start acting in real time.
What this looks like from start to finish: A trigger like a new high-priority threat actor, a malicious website notification, or a critical third-party vulnerability starts the workflow. The Platform reasons through what matters, pulling intelligence and building a hunting package, checking a site's ownership to assess takedown eligibility, or drafting outreach and confirming approvals. Then it can act, including running the hunt and blocking the threat, initiating and monitoring a takedown, or notifying your third party and tracking remediation.
Agents default to fully autonomous execution, because defending at machine speed requires it, but teams that want human review first can dial back to managed autonomy. The result is a system, not just a model, that connects detection, investigation, and response into a single workflow. But a capability like this only matters if you can trust it, which is where Recorded Future’s autonomous defense sets itself apart.
A fundamentally different approach
AI security tools have exploded, but much of the industry feels oversold. Dashboards relabeled. SOAR engines rebranded, chatbots dressed up in analyst clothing. Security teams have grown skeptical of the pattern, and rightly so.
What makes Recorded Future's autonomous defense different?
Reasoning models and agent frameworks are becoming commodities. Nearly any vendor can wire up an agent loop. What's scarce is trustworthy, structured intelligence for those agents to reason over. That's what we've spent over 15 years building, and it's the foundation every Recorded Future agent runs on. Frontier models generally lack this training on relevant data.
It's grounded in the deepest threat intelligence available. Claims about a threat actor's infrastructure, a vulnerability's exploitation status, or a campaign's targeting come from the Intelligence Graph®: continuous analysis across open, dark, and technical web sources, enriched by Insikt Group's analysts. Not plausible-sounding guesses from general training data. Real intelligence, sourced, traceable, and trustworthy.
It's architecturally agentic, not superficially so. Most agents have to poll the world to notice that something has changed. Recorded Future agents subscribe to changes in the Intelligence Graph® and get real-time triggers the moment something relevant moves, so they act on signals instead of burning cycles searching for them. This isn't a chat interface bolted onto a search box. It's purpose-built for how security work actually happens.
Every output is auditable. Security teams can't operate on black-box AI. Trust requires transparency. Recorded Future shows its work, so every source, step, and conclusion can be traced. When it flags a threat as high priority, you can see exactly why.
Intelligence that ends in a chat window has limited value. Recorded Future delivers outputs into SIEM platforms, ticketing systems, communication tools, and the rest of your security stack where the work actually happens.
This is the beginning
We believe that what we're announcing today is a real leap in what security teams can accomplish: workflows that can eliminate critical threats, hours returned to the analyst, and coverage that wasn't previously achievable. And we're not stopping here.
We're already building expanded multi-agent architectures, where AI agents collaborate on complex, long-running investigations. We're building toward AI that monitors threat groups and updates intelligence continuously over weeks, not sessions. And we're extending the integration layer so Recorded Future AI doesn't just deliver intelligence into your stack, it participates in it.
This is a new era of defense, and we know that many of our customers are as excited about it as we are. If you're a Recorded Future customer and want to be part of what's next, apply for early access here. Autonomous defense is planned for general availability early next year.
Most AI-enabled social engineering can still be addressed through existing defenses, but synthetic media attacks require organizations to adapt those defenses and stop treating a familiar face or voice as proof of identity.
Many uses of AI in social engineering, including personalizing phishing messages, building fraudulent websites, and automating responses, make established techniques faster, cheaper, and easier to scale. Although organizations must adapt their defenses to address the volume and sophistication of these threats, current evidence indicates that established security controls, such as filtering, verification procedures, and repeated training, still reduce the success of these attacks.
That said, synthetic media such as deepfakes and voice alteration present an exception. Synthetic media weakens the audiovisual and biometric signals that people and identity systems previously treated as evidence of legitimate identity. Research has found that both people and detection systems struggle to reliably identify deepfakes, especially those presented outside of controlled settings. As a result, defenses that rely on recognizing a familiar voice, face, or identity document are often insufficient on their own.
This distinction matters. Treating all AI-enabled threats as equivalent risks gives organizations a false sense of security while leaving them vulnerable to attacks that existing controls fail to prevent.
Recorded Future MCP is now generally available, giving AI agents and LLM workflows direct access to Recorded Future's Intelligence Graph® and enabling precise, trustworthy, and cost-effective decision-making at machine speed and scale.
Ransomware does not start when files are encrypted. By then, an attacker may already have obtained valid credentials, entered the network, moved between systems and established a command-and-control (C2) channel.
That gives defenders an earlier window to act. Ransomware threat intelligence helps security teams identify the actors, infrastructure and access methods connected to ransomware activity before an attack reaches its final stage. Instead of waiting for an endpoint alert or ransom note, teams can look for exposed credentials, malicious infrastructure and known attacker behavior, then act on the threats most relevant to their organization.
The need for that earlier view is growing. Modern ransomware operations may use Ransomware-as-a-Service (RaaS) models and double- or triple-extortion tactics, giving defenders more reason to identify warning signs before encryption.
Key takeaways
Ransomware threat intelligence can expose signs of an attack before encryption, including compromised access and attacker infrastructure.
IOCs remain useful, but TTPs provide longer-lasting context because attacker behavior changes less quickly than individual IP addresses or file hashes.
Early disruption can focus on closing initial access paths or cutting communication between compromised systems and known C2 infrastructure.
Recorded Future assists in connecting ransomware intelligence with organizational exposure, threat actor context and existing security workflows so teams can better prioritize action.
Why reactive ransomware defense is not enough
Reactive controls remain important, but they often cannot provide the external context security teams need to identify which ransomware threats are most likely to reach their environment.
Endpoint detection and response (EDR), network monitoring, and backups all have a role in ransomware defense. The problem is timing. If a team only acts after malicious behavior appears inside its environment, the attacker may already have gained access or started moving toward systems that matter.
This is where modern ransomware detection benefits from external intelligence. Security teams can compare what they see internally with information about active ransomware groups, infrastructure and exploitation activity outside their network.
IOCs show what happened. TTPs help anticipate what comes next.
Indicators of compromise (IOCs), such as malicious IP addresses, domains, and file hashes, can help security controls identify known threats. They also typically have a short shelf life when attackers rotate infrastructure or alter malware.
Tactics, techniques, and procedures (TTPs) describe how an adversary operates. MITRE ATT&CK organizes those behaviors across stages such as initial access, lateral movement and command and control.
A ransomware actor can quickly replace an IP address. Changing a working attack method takes more effort. Tracking both IOCs and TTPs gives defenders a stronger basis for deciding what to block now and what behavior to watch for next.
The goal is not to replace IOC-based detection. It is to add enough context to understand who may be behind an indicator, how it fits into an attack, and what the adversary is likely to attempt next.
How does Threat Intelligence help prevent ransomware attacks?
The best time to disrupt ransomware is before the attacker reaches the impact stage. Threat intelligence creates opportunities to act during initial access and C2 activity rather than relying on recovery after encryption.
External intelligence can reveal parts of the ransomware operation that are difficult to see from internal telemetry alone. That includes activity in criminal marketplaces as well as infrastructure connected to known threat actors.
Phase 1: Track the adversary outside your network
Initial access is often a business in its own right. Initial access brokers (IABs) obtain access to compromised organizations and advertise it to other criminals. Threat intelligence can surface compromised credentials and exposed Remote Desktop Protocol (RDP) access associated with an organization. It can also monitor IAB listings, actor chatter, and target discussions for warning signs before that access is used.
Monitoring those sources can give security teams a warning that credentials or access associated with their organization are exposed. A credential discovered for sale does not prove that a ransomware attack will follow, but it creates a specific risk that defenders can investigate before someone uses that access.
Threat intelligence can also connect ransomware groups with domains, IP addresses, and other infrastructure associated with their operations. Malware analysis and controlled sandbox testing can add newly observed indicators and behavioral information.
C2 intelligence is especially useful because command-and-control gives attackers a way to communicate with systems they have compromised. If defenders know the infrastructure associated with an active threat actor, they can look for related connections within their own network rather than waiting for the ransomware payload to execute.
Phase 2: Act at the point of disruption
Tracking only matters if the intelligence changes what the security team does.
At initial access, one priority is removing the opportunity before an attacker can use it. If exposed corporate credentials appear in criminal sources, the organization can investigate the affected account, reset credentials where needed, and review authentication activity for signs of misuse.
The same principle applies to vulnerabilities. A large vulnerability backlog does not indicate which flaw an attacker is likely to exploit first. Vulnerability intelligence adds evidence of exploitation activity, enabling teams to respond faster to weaknesses associated with active threats rather than relying on severity scores alone.
C2 creates another intervention point. High-confidence indicators associated with malicious infrastructure can be supplied to security controls so connections are blocked or detected earlier. If an endpoint begins communicating with known C2 infrastructure, the security team can investigate and isolate the affected system before the attacker progresses further.
Disruption does not always require taking criminal infrastructure offline. For an individual organization, breaking the attacker's access to its environment can be enough to stop that attack path.
These controls should sit alongside broader guidance on how to prevent ransomware, including identity protection, patching, and recovery planning. Threat intelligence makes those efforts more targeted by showing teams where an active threat is most likely to intersect with their environment.
Recorded Future turns ransomware intelligence into action
Recorded Future helps security teams connect external ransomware activity with their own exposure so they can spend less time sorting through threat data and more time acting on relevant risks.
Recorded Future’s ransomware mitigation capabilities bring together threat research, dark web intelligence and information about an organization's attack surface. Threat actor, industry and TTP context helps teams narrow their attention to ransomware threats that warrant attention.
Reduce research time with the Intelligence GraphⓇ
A large feed of indicators can contribute to alert fatigue if analysts must investigate each item manually. Recorded Future's Intelligence GraphⓇ connects information about threat actors with associated malware, infrastructure, and vulnerabilities.
That context helps analysts move from an isolated indicator to the relationships around it. Rather than treating every IOC as equally important, teams can assess how an indicator relates to an active threat and whether that threat is relevant to their organization.
Recorded Future uses AI to collect, process, and correlate threat data within the Intelligence Graph. This helps reduce repetitive research and enables teams to prioritize relevant findings.
Focus on the ransomware actors most relevant to your organization
Not every ransomware group has the same targets. Industry, geography and previous victim patterns can help analysts understand where a threat actor tends to focus.
Recorded Future's Ransomware Risk Profile provides a view of an organization's ransomware exposure. Victimology insights help teams understand which ransomware groups and TTPs are most relevant based on targeting patterns such as industry and geography.
This allows SOC and threat intelligence teams to tune detection and hunting around ransomware groups whose past activity makes them more relevant to the business rather than treating the entire ransomware landscape as equally urgent.
Put intelligence into existing security workflows
Threat intelligence loses value when an analyst has to move findings manually from one tool to another.
Recorded Future can deliver intelligence through APIs and integrations with security information and event management (SIEM), security orchestration, automation, and response (SOAR), and endpoint detection and response (EDR) tools. Depending on the configured workflow, intelligence can add context to alerts and support automated blocking of malicious infrastructure.
Build an intelligence-driven ransomware defense
Ransomware threat intelligence changes the point at which defenders can respond. Instead of treating encryption as the first clear sign of an attack, teams can look for the access, infrastructure and behavior that come earlier.
This does not replace EDR, access controls or backups. It gives those defenses external context. A vulnerability becomes more urgent when a ransomware actor is actively exploiting it. An exposed credential becomes an immediate investigation point when criminals are offering access to the organization. A C2 indicator becomes more useful when analysts can connect it to the actor and TTPs behind it.
That earlier context can reduce both the likelihood of a successful attack and the damage an attacker can cause. Given how ransomware affects businesses, moving the disruption point earlier in the attack lifecycle can protect far more than encrypted files.
Ready to stop ransomware before a breach occurs? Explore our product tours to get a feel for how Recorded Future automates the tracking and disruption of the most relevant threat actors targeting your industry.
Ransomware Threat Intelligence FAQs
What is the primary difference between a reactive and a threat intelligence-led disruption strategy for ransomware?
A reactive strategy focuses on detecting and recovering from ransomware after malicious activity reaches the environment. A threat intelligence-led strategy looks for earlier warning signs, such as exposed access, known threat actor behavior and malicious infrastructure, so teams can intervene before encryption occurs.
Is paying a ransom ever considered an effective disruption strategy?
Paying a ransom occurs after an organization has already been compromised, so it is generally not a preemptive disruption strategy. Threat intelligence-led disruption focuses on stopping the attacker earlier in the ransomware lifecycle.
Which stages of the ransomware attack lifecycle offer the best opportunities for external disruption via threat intelligence?
Reconnaissance and command and control (C2) provide valuable opportunities for disruption. Threat intelligence can identify exposed credentials, access being advertised by initial access brokers and infrastructure associated with known ransomware actors before those resources are used against the organization.
How does Recorded Future use AI to accelerate ransomware disruption?
Recorded Future uses AI to collect, process and correlate threat data within the Intelligence Graph. This helps analysts connect indicators with threat actors, infrastructure and TTPs, reducing manual research and helping teams identify ransomware threats that require attention faster.
Can Recorded Future help our organization identify and mitigate our most critical ransomware exposure points?
Recorded Future combines vulnerability and attack surface intelligence with external threat context to help teams identify exposures associated with active ransomware threats. This can help security teams prioritize remediation based on evidence of exploitation and organizational risk rather than severity scores alone.
What is victimology in the context of ransomware intelligence, and how is it used to protect an organization?
Victimology examines the types of organizations ransomware groups have targeted, including patterns related to industry and geography. Security teams can use those patterns alongside threat actor TTPs to identify ransomware groups that may be more relevant to their organization and adjust detection and hunting accordingly.
How is the rise of Ransomware-as-a-Service impacting the way organizations use threat intelligence for tracking?
Ransomware-as-a-Service can separate ransomware operators from the affiliates carrying out attacks. Threat intelligence teams therefore need to track more than a single malware family, including affiliate behavior, initial access activity and criminal-market sources that may reveal how attacks are being prepared.
Since Russia’s full-scale invasion of Ukraine in February 2022, Russia has escalated its use of hybrid, asymmetric warfare across Europe, far beyond the former Soviet Union, where Russia historically focused its aggression. These tactics fall under a Russian military strategy known as New Generation Warfare (NGW). Insikt Group assesses that Russia is likely to escalate NGW tactics over the next two years, potentially culminating in a full-scale NGW campaign. Europe-based private and public sector entities are very likely at risk of physical and cyber sabotage as Russia deploys NGW tactics. Critical infrastructure entities in Europe are at high risk of being targeted, potentially resulting in data loss, physical damage to facilities, or injury or death of personnel.
Recorded Future's Insikt GroupⓇ has been tracking ClickFix, a social engineering technique that turns a familiar logo or verification prompt into the entry point for an attack. Here's what that research reveals about catching it, and why it's now running inside Malicious Site Monitoring, part of our newly launched Digital Risk Protection solution.
Recorded Future's Insikt GroupⓇ, our team of threat intelligence analysts and security researchers, has been tracking a technique called ClickFix as it works its way into a growing number of brand impersonation campaigns. We recently hosted a webinar digging into that research, and what stood out wasn't just the technique itself. There's no malware automatically installed, no exploit, just a page convincing enough that the victim ends up doing the damage themselves. It is also a strong example of the detection capabilities built into Malicious Site Monitoring, a new use case included in Digital Risk Protection, and a good way to show what those capabilities are actually built to catch.
How ClickFix actually works
ClickFix works by mimicking the visual language people already trust, a CAPTCHA prompt, a familiar logo, a "verify you're human" screen, and using that trust to get someone to run a command on their own machine. There's no code being smuggled past a firewall. The victim is the delivery mechanism.
That's also what makes it hard to catch with traditional tools. A page built to look exactly like a real verification screen doesn't behave like malware, and it doesn't trip the same alarms as a page trying to exploit a browser. It succeeds because the person on the other end believes they're completing something routine.
It's not static, either. The instructions can change depending on the operating system a victim is running, one path for Windows, a different one for macOS, which means the "fix" itself adapts to the target. A single signature or a one-off takedown was never going to keep up with that. Catching this at scale means watching for the pattern, not waiting to recognize a specific file.
Malicious Site Monitoring
This kind of research and the product built to act on it aren't two separate things. Digital Risk Protection's Malicious Site Monitoring is built to catch this exact category of infrastructure, phishing domains, lookalike sites, brand impersonation, fast enough to matter. Disposable infrastructure like this is designed to do its damage and disappear before anyone gets around to reporting it, so speed isn't just a nice-to-have here, it's a necessity.
Underneath that speed is a detection process built in layers. Analyst-built signatures catch known patterns with precision. Content similarity analysis can catch campaigns that move in clusters. Attackers often reuse the same page template across dozens of disposable domains, so even though each domain name looks unrelated, the pages themselves share the same structure underneath. A separate component flags a familiar logo or brand mark through screenshot analysis and Optical Character Recognition (OCR). Machine learning is often able to catch what the other methods might miss, sites that don't resemble any known signature or template, by predicting risk from the page's characteristics rather than requiring a direct match. That layered approach is what makes it possible to evaluate a massive volume of candidate domains and URLs every single day without generating excessive false positives.
From detection to takedown
Finding a threat fast doesn't help much if the next steps are still manual. The real shift in how Digital Risk Protection operates is this: detection, triage, and action now live in the same workflow.
Not every detection needs a human to look at it immediately, and that distinction matters. A multi-stage detection funnel helps filter raw monitoring volume down to those that could need a response, and for malicious sites specifically, an AI Triage Agent reviews flagged detections and delivers a verdict before anything reaches an analyst's queue. Instead of triaging a wall of alerts, teams are looking at a shortlist of things that already have context attached, what was found, why it matters, and what to do about it.
And when something does need action, takedown doesn't require a separate process. Coordination happens directly from the alert, one click, instead of manually chasing down registrars and hosting providers one by one.
What this means going forward
ClickFix is one campaign type. It won't be the last one built this way, and it almost certainly won't be the most sophisticated one we see this year. The interesting story isn't any single technique, it's that the same detection engine tracking it in a research report is the one running in production, watching for the next one before it has a name.
If you want to see that detection-to-action workflow in practice, not just malicious sites, but the full picture across dark web monitoring, code repository exposure, impersonation, and identity monitoring, take a self-guided click-through of Digital Risk Protection or request a demo. If you're already a customer, your account team can walk you through what this looks like against your own brand.
Frequently asked questions
Is ClickFix something Digital Risk Protection can actually detect, or just something Insikt Group writes about?
Both. The detection methodology behind the ClickFix research, layered signature, similarity, and machine learning analysis, is the same engine running inside Malicious Site Monitoring today. The research isn't separate from the product; it's built on it.
Is the AI Triage Agent available for this use case?
Yes. Malicious Site Monitoring is one of two use cases, alongside Dark Web Brand Monitoring, where the AI Triage Agent is live today. It reviews flagged detections and delivers a verdict before anything reaches an analyst's queue.
How do I get access to Digital Risk Protection?
It's available as a standalone solution or as part of Recorded Future's Core, Professional, and Elite platform packages. If you already use Recorded Future for brand monitoring, it's available to activate directly in the platform. If you're new to Recorded Future, request a demo to see it in action.
The intelligence community has always done things the same way: Identify a potential source (a target); make a recruitment (an agent); train, brief, and run the agent in place to collect intelligence of value to decision makers.
A great agent gives the decision maker insight into intent, and a reasoning and decision advantage over his or her adversaries. In some circumstances, this advantage shapes destiny. Control over destiny is commonly called sovereignty.
AI has rapidly made reasoning ubiquitous; a commodity accessible to all at ever-decreasing marginal cost. In the age of AI, advantage accrues to those who use reason most effectively, make good decisions most quickly, and take actions most confidently. And who will do the bulk of this reasoning, make these decisions, and take these actions? Agents.
Agent Running in the Age of AI
Historically, agents were sources of intelligence but, in the age of AI, the new consumer of intelligence is an agent. Agents will be dependent on the quality and timeliness of the intelligence they receive to give them context, shape their priorities, drive their behavior, and ensure the quality of their actions. Every agent will need an intelligence layer it can trust. Recorded Future is that layer.
Recruiting and running human agents is hard and expensive, and very few have the resources and the expertise to do it well. One experienced MI6 officer might run a handful of agents at any one time. But the human-to-agent ratio is about to change dramatically as decision-making shifts from carbon to silicon, driving down the costs of agent running, but dramatically increasing our reliance on agent decisions and actions.
The best military and political outcomes often result from the seamless integration of different sources and types of intelligence to produce a true understanding of the threat or the objective to be met, enabling good decision-making and decisive actions. The Cuban Missile Crisis combined geospatial, human, and signals intelligence; the D-Day Landings combined signals, human, and meteorological intelligence. As frontier AI capabilities diffuse, and as agentic systems incorporate these capabilities into multi-agent workflows, the performance of these systems relative to others, and thus their ability to deliver advantage, will be determined by ongoing access to high-fidelity, multi-source intelligence.
This is already the case in the domain of cyber security. Intelligence-enriched systems and workflows learn more quickly, adapt more nimbly, and operate more efficiently and effectively than those they are competing with. The adoption rate of Recorded Future’s AI triage capabilities proves this hands down.
Intelligence platforms like Recorded Future, which shed light on threat actor tactics, techniques, and procedures (TTPs) in real time, and which scale with AI and agent capabilities, are the foundation for effective agentic systems. Intelligence-driven agent running will ensure better agentic decisions and actions, delivering an enduring advantage over adversaries.
As former CIA Director Bill Burns put it, “The foundation for good policy choices is good intelligence wisely used.” In the age of AI, agents will make those choices, and the value of good intelligence will be greater than ever.
Recorded Future was just named a Leader in The Forrester Wave™: External Threat Intelligence Service Providers, Q3 2026.
We’re incredibly proud of this acknowledgment, just as we are of every recognition we’ve received over the years. Behind every one of these industry evaluations is a lot of work that readers never see — including product demonstrations, customer reference calls, briefing presentations, and formal questionnaire submissions — all of it condensed into a single final report. But the most interesting part of any industry recognition is all the details and information that resides in the demos, decks, and responses, so we wanted to share some additional context on the factors that we believe contributed to our ranking this year.
Use this blog post as a companion guide when reading your complimentary copy of the Forrester Wave™ report, which you’ll find in the link below.
Superior support for Priority Intelligence Requirements
Priority Intelligence Requirements (PIRs) are foundational in helping security teams achieve meaningful outcomes, because they help shape data collection strategy and support the effective decision-making that enables machine-speed defense.
Recorded Future received the highest possible score in the PIR criterion. Forrester’s evaluation describes this score as for vendors that offer “superior support for features such as mechanisms to translate external PIRs meaningfully, advanced querying for building/optimizing PIRs, and structured management of General Intelligence Requirements.”
We’ve made PIRs a particular focus in the Recorded Future Platform, adding prebuilt PIRs and enabling customers to use them or define their own in our Impact and Metrics Dashboard. The dashboard surfaces metrics based on those requirements, so teams can more easily measure and better report on how successfully their programs are answering the key questions business leadership wants answered.
Extensive intelligence collection sources and deep and dark web monitoring
Intelligence is at the core of the modern security stack, and good intelligence is often what separates reactive security teams from proactive ones that can defend themselves pre-attack, at the first sign of threat.
To us, Forrester’s evaluation criteria show how important comprehensive intelligence collection is in providing security teams with full visibility across the threat landscape. Here are the different types of data sources we primarily index and analyze and how these data sources can be used for a multitude of use cases:
Technical intelligence — network traffic analysis across billions of daily data points from over 200 points of presence, internet-wide scanning and infrastructure monitoring, malware detonation and behavioral analysis, and vulnerability exploitation tracking
Underground intelligence — data gathered from criminal forums, marketplaces, and adversaries that can help identify stolen data and credentials, emerging attack techniques, threat actor intent, and ransomware victimology
Community intelligence — aggregated detections across customers that reveal patterns and campaign-level activity no single organization would usually catch on its own
Open-source intelligence — broader context from data leakage detection, code repository monitoring, social media monitoring, and web/HTML/DOM analysis to help catch brand abuse, impersonation, and exposed data
Threat hunting, vulnerability intelligence, third-party risk management, and more We believe that receiving the highest possible scores in the Forrester Wave in criteria around multiple cybersecurity disciplines — including brand protection, third-party and supply chain intelligence, fraud intelligence, and threat hunting and vulnerability intelligence — demonstrate our commitment to providing powerful threat intelligence and defensive capabilities across the entire attack surface.
Figure 1: Unified threat intelligence visibility across the critical attack surfaces
Global security frameworks are evolving: Security organizations are increasingly leveraging global frameworks to navigate the complexities of AI-enabled threats, balancing the need for standardized best practices with the necessity of business-specific risk decisions.
Intelligence-led defense is essential: Modern, intelligence-led defense generally requires operationalizing security at machine speed by integrating enriched, contextual threat data, which better enables strategic, risk-based vulnerability prioritization rather than reacting to every threat.
Effective security requires data quality and relevance: Organizations must prioritize the quality and "fit for purpose" of the intelligence feeding into their threat intelligence solutions so they can make quick, accurate decisions and avoid the risks of moving fast with bad information.
As both human-directed and autonomous AI-powered attacks accelerate, security organizations, policymakers, and industry groups around the world are rethinking traditional approaches to defense.
Recorded Future CISO Jason Steer and Mastercard VP of Government Affairs and Policy Christian Ohanian recently sat down with Recorded Future’s Jon Miller to discuss how to build threat intelligence programs that can defend at machine speed, how emerging policy frameworks can help, and why high-quality intelligence is increasingly essential in this new era.
Evolving security standards and frameworks Globally, security frameworks like the National Institute of Standards and Technology (NIST) Cyber AI Profile and Singapore’s cybersecurity guidelines are evolving to help organizations keep pace with new threats. According to Christian Ohanian, the goal is to encourage the adoption of AI to bolster resilience while also providing guidance on the kinds of AI-enabled threats organizations now face.
However, Ohanian pointed out that creating these standards involves debate. While some argue that frameworks should provide a clear, prioritized checklist to help resource-strapped teams improve their security programs, others believe that a "one-size-fits-all" approach fails to account for the unique risk profiles of different industries and organizations.
Jason Steer noted that while standards create a helpful taxonomy, the burden remains on CISOs to translate that language into business-specific risk decisions. “This is why intelligence is important,” he noted. “Every industry, every geography, has its own subtleties of attack, so leaning into ‘What are the real risks to my business?’ becomes the hardest part.”
The role of high-quality, purpose-fit intelligence Ohanian noted that global security standards increasingly recognize that threat intelligence is a foundational component of modern defense. They’re also beginning to acknowledge that security organizations need to use AI and other autonomous solutions to improve the way they operationalize their intelligence. Framework discussions, he said, are now focused on “the importance of organizations looking really closely at how they can increase the speed of the way they’re using threat intelligence, how they can increase the accuracy of the prioritization of the alerts and warnings they’re getting.”
Ohanian emphasized that organizations must move beyond the simple acquisition of data and evaluate the intelligence sources feeding into their threat intelligence solutions. They need to look at "fit for purpose," ensuring that the intelligence aligns with the organization’s specific risk profile and governance requirements.
Steer agreed. “Coverage and collection at fast speed enable information to be brought together for people to assess the impact to their business,” he said. “But then it's only good if that information gets to the right people in the right tools.”
When it does, he said, high-quality intelligence can better fulfill its ultimate goal of providing “decision advantage”—enabling even less experienced SOC analysts to make quick, effective decisions.
Operationalizing security at machine speed To begin operationalizing intelligence, organizations need to first know what they’re defending. Do they run software on-premise, in the cloud, or a combination of the two? Once they have a complete picture of the mission-critical systems they need to defend, Steer said, they’ll better understand the threats that might be targeting them.
Then, in order to achieve machine-speed defense against AI-driven attacks, organizations need the right API integrations. That way, they can send enriched, contextual threat data to their vulnerability tools and use AI to identify the clusters of high-risk activity where vulnerabilities intersect with active exploitation.
Steer noted that this shift will eventually allow security leaders to move away from trying to patch every single vulnerability—an impossible task—and toward a strategic, risk-based prioritization model. “Vulnerability prioritization is absolutely primed for AI to streamline and accelerate contextual decision-making at executive levels,” he said.
Driving toward an intelligence-led defense future The consensus from the panel was clear: The future of cybersecurity lies in the convergence of AI, intelligence-led defense, and robust governance. While the X-factor of new threats—the ones that disrupt even the best-laid plans—will always exist, the goal is to reduce reactive panic and focus on strategic risk reduction.
For security practitioners, the takeaway is two-fold. First, they need to keep a close watch on the evolution of global security frameworks, as these documents will define industry expectations and communication standards, and they’ll give organizations a better understanding of where modern security is going in light of AI.
Second, practitioners need to focus on the quality of intelligence over quantity. By ensuring that their tools are enriched with actionable context, they can empower their teams to move from a state of constant, reactive chaos to one of calculated, proactive defense.
As Jon Miller noted, intelligence-led defense is the best way to ensure that when you move at machine speed, you’re moving in the right direction. “Speed without intelligence just means you're wrong, faster,” he said.
To get a customized walkthrough of Recorded Future’s machine-speed defense in action, take our interactive tour.
This report provides insights and analysis to better understand the role of third-party vendors and guarantee marketplaces from the perspective of Tajin Group, a third-party vendor that advertises and provides services on two Telegram-based Chinese-language guarantee marketplaces, Dabai Guarantee and Xinbi Guarantee. This includes operational challenges, perspectives regarding the competition from other threat groups, and how Tajin Group adapts to changes in its operating environment.
Additionally, we identified that Chinese-language guarantee marketplace users and third-party vendors are increasingly using third-party services to purchase and sell Telegram usernames and anonymous virtual numbers. Through these services, Chinese-speaking criminals can link multiple Telegram usernames and an anonymous virtual number (in lieu of SIM cards) to a single Telegram account. This activity indicates a continued evolution and adaptability among these threat actors, who are strengthening their operational security (OPSEC) measures through tactics such as using anonymous virtual numbers to create Telegram accounts to avoid detection and reach a wider audience.
The phishing, payment card theft, and money laundering activities of Tajin Group, guarantee marketplaces, and their third-party vendors can negatively impact banks, fund transfer services providers, cryptocurrency exchanges, and individuals vulnerable to scam and fraud-related campaigns. As Tajin Group is a single third-party vendor, the potential financial gains in the global payment industry are likely to incentivize other threat groups operating on Chinese-language guarantee marketplaces to conduct campaigns by replicating Tajin Group’s tactics, techniques, and procedures (TTPs) on a global scale.
Key Findings
Tajin Group is mainly involved in phishing, payment card theft, and money laundering. The group actively targeted mainland Chinese citizens and Chinese banks and demonstrated a nuanced understanding of the prerequisites required to transfer funds overseas or use other payment cards remotely.
Tajin Group conducts extensive testing involving payment cards belonging to multiple countries on the financial platforms CCAvenue and Geidea. They are well-versed in financial crimes and have listed multiple Bank Identification Numbers (BINs) for payment cards from twelve countries.
Tajin Group constantly seeks cooperation with other threat groups to use direct payment channels that accept UnionPay, VISA, Mastercard, JCB, and Apple Pay; exploit 2D, 3D, and other payment gateways; and UAE Dirhams and electronic gift cards for their financial theft and money-laundering operations.
Tajin Group has pivoted from Dabai Guarantee to Xinbi Guarantee, showcasing that third-party vendors do not necessarily stay loyal to a single guarantee marketplace platform. The threat group also detailed their operational challenges, intense competition from competitors, and trust issues with their previous payment card suppliers.
Operators of Tajin Group have sold and bought at least 100 Telegram usernames and multiple phone numbers from Fragment Market, a platform that facilitates the buying and selling of virtual, anonymous phone numbers and Telegram usernames, further anonymizing their operations.
Background
Guarantee marketplaces have become increasingly popular among Chinese cybercriminals as viable alternatives to Chinese-language dark web marketplaces since Huione Guarantee and its business model gained prominence around 2021. Based on our research and previous reports, we have observed that multiple third-party vendors who are usually involved in advertising the sale of malware, databases, phishing kits, and money laundering services on dark web marketplaces have also begun to use Telegram-based guarantee marketplaces to advertise their services or seek cooperation on these platforms. These marketplaces act as a powerful force multiplier to strengthen cooperation among Chinese-speaking threat groups in recruitment, crowdsourcing information, sharing resources, and deploying personnel to commit crimes that require in-person interactions. For additional insights, see our previous report “Evolution of Chinese-Language Guarantee Telegram Marketplaces”.
We noted that these Chinese-language guarantee marketplaces typically consist of hundreds to thousands of third-party vendors, each operated by different Chinese-speaking threat actors (some syndicates) across the globe. To better understand how third-party vendors operate on these guarantee marketplaces and how they contribute to cybercriminal activities, Insikt Group analyzed the activities of Tajin Group, a threat group that conducts phishing campaigns, payment fraud, money laundering, carding, and exploits 3D and 2D payment gateways, among others. Chinese-language guarantee marketplaces typically follow a strict rule requiring that third-party vendors use only one guarantee marketplace at any given time, and we identified that Tajin Group complied with this rule by ceasing activities on Dabai Guarantee before pivoting to Xinbi Guarantee. Tajin Group observed Chinese etiquette and showed respect for the Chinese-language guarantee marketplace ecosystem, demonstrating that there is likely a common understanding between the operators of these guarantee marketplaces by having a system where no third-party vendors are allowed to make use of multiple platforms to advertise and conduct their campaigns.
Overview of Tajin Group
Tajin Group (踏金集团;踏金 [Tajin] translates to “stepping on gold” in Mandarin) is a Chinese-speaking threat group that focuses on phishing, carding, financial fraud, and money laundering. Insikt Group observed that Tajin Group used to be a third-party vendor operating on Dabai Guarantee from May 2025 to April 2026, but pivoted to Xinbi Guarantee around May 2026. Dabai and Xinbi guarantee marketplaces are known to be populated with third-party vendors that provide various services that facilitate cybercriminal activities, including money-laundering methods and services, the sale of compromised social media and e-commerce accounts, SIM cards, data containing personally identifiable information (PII), malware-as-a-service (MaaS), deepfake technology, know-your-customer (KYC) bypass services, and other illegal activities.
As guarantee marketplaces typically require their vendors to stake cryptocurrency as deposits, Tajin Group claimed to have deposited 208,848 in Tether (USDT) on Xinbi Guarantee. The deposit amount often indicates vendors’ scale of operations, where larger deposit amounts reflect larger-scale operations. By comparison, most vendors on Chinese-language Telegram guarantee marketplaces typically deposit only a few hundred to a thousand USDT. As shown in Figure 1, the deposit amount of 208,848 USDT is significantly larger than that of most other third-party vendors.
Figure 1:Tajin Group’s channel @ttjt claimed that the group is a vendor on Xinbi Guarantee with the corresponding channel @xb8848, and that the group has deposited 208,848 USDT into Xinbi Guarantee Marketplace (Source: Telegram)

 Login