❌

Reading view

Why VPNs Are Worth Defending

Developers of virtual private network (VPN) apps are reporting that their products are again being pulled from Apple’s App Store in Russia. This is an unacceptable crackdown on a vital tool to protect privacy and speech online.

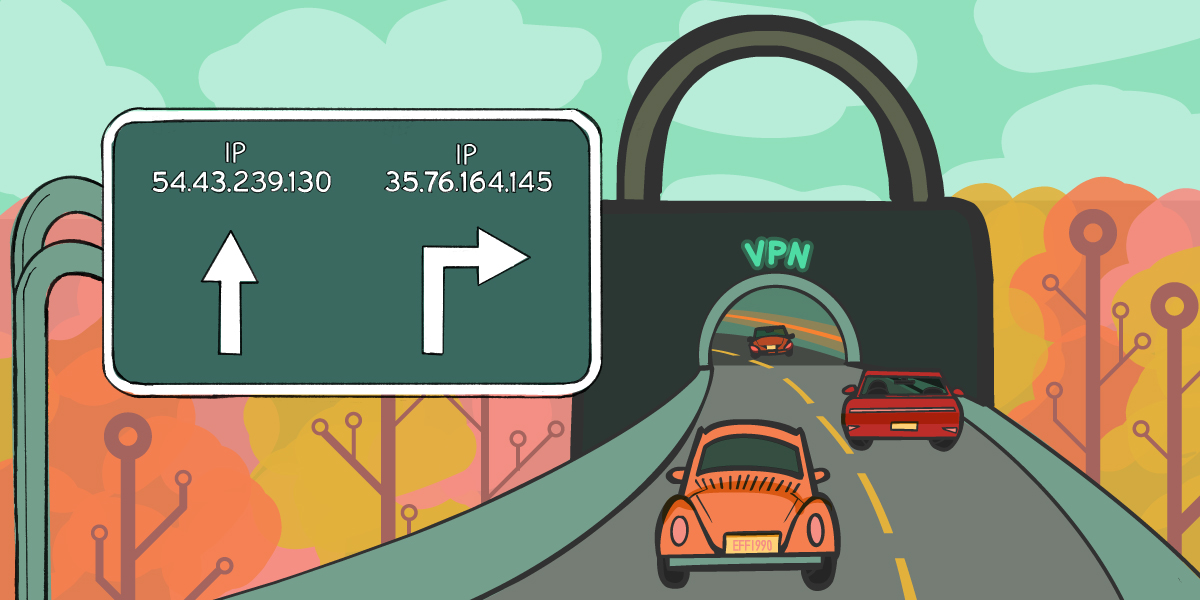
Why? VPNs give people a way to control their own online activities. When you visit a website through a VPN, that website only sees the VPN server's location (well, IP address) rather than your actual location. It's like sending a letter through a P.O. box so the recipient doesn't know where you really live. It can also disguise where you’re accessing information from, which can make it possible to access information banned by your government.

This is an unacceptable crackdown on a vital tool to protect privacy and speech online.

Going after tools that give people the space to communicate and access information freely is a common tactic from the totalitarian playbook. This latest demand comes after several steps the Russian government’s taken to surveil speech specifically on Apple products. In 2024, the Moscow Times reported that Russia’s state media watchdog, Roskomnadzor, went after VPN apps on the Apple App Store, after banning access to Western social media platforms and blacklisting opposition media sites. Russia then blocked Apple’s FaceTime software in 2025, according to Apple Insider.

Bloomberg also recently reported that the Russian government has added Apple and Microsoft to its state surveillance registry. This gives Roskomnadzor access to local users’ correspondence, Apple Insider reported, and puts both companies in a position to turn over customer information to the country’s security services as required.

With government control encroaching on their devices and less access to tools that give them alternate methods, people in Russia are left with shrinking options to communicate online or find information that isn’t state-sanctioned.

While Russia’s actions offer a more extreme vision of what happens when the government tries to enforce speech rules by attacking vital privacy tools, it is far from the only government doing so. Several states in the U.S., bent on making it difficult to circumvent invasive age-gating laws, have suggested banning VPNs—either to access certain content or in some cases to simply ban them outright. EFF has publicly (and loudly) criticized these proposals, because going after VPNs is a dangerous step down the road of censorship.

Attacks on speech and privacy online are deeply troubling, no matter where they happen. What those in power may see as a “loophole” in their invasive laws is actually an expression of user control. We’ll continue to speak out when we see governments going after them to take that control away.
  •  

When No ID Means No Internet: Age Verification and the Right to Access Information

This post was co-authored by Sheila B. Lalwani, a doctorate student and recent COMPASS Fellow hosted by EFF.

Age verification proposals are often presented as a simple tradeoff: sacrifice a little privacy to better safeguard children online. But that framing overlooks a more fundamental question. What happens to people who cannot verify their age at all? This is particularly a problem when users are required to prove their age with identity documents.

Age-related restrictions are developing quickly around the world. While they differ radically across jurisdictions, in the past year, we’ve witnessed a sharp uptick toward mandatory age assurance for social media access but also for other high-risk digital services.

For example:

  • In late 2025, Australia became the first country to implement a minimum age requirement for prohibiting children under age 16 from creating or holding social media accounts. 
  • India passed the Digital Personal Data Protection (DPDP) Act that includes mandatory verifiable parental consent and has undertaken ongoing discussions for social media restriction.
  • The United Kingdom passed the Online Safety Act requiring age verification across a swath of services hosting content considered harmful to users under 18. More than half the states across the U.S. have enacted age verification laws. 
  • An EU Commission’s expert report recommends a ban on social media access for users under 13. It also recommends mandatory age verification for platforms to ensure that users are ‘age appropriate.’ 

The Access Problem 

Age verification laws that are predicated on the necessity of users possessing a current passport, driver’s license, credit card, or similar documents proving their identity exclude critical sections of populations.  And this problem is global in nature: Millions of people lack government-issued identification or encounter regular challenges to obtaining or updating it. 

Roughly 15 million adult U.S. citizens lack a driver’s license, and a further 2.6 million lack any government photo ID; leaving large groups blocked from online content or services. The UK has a similar predicament: proof-of-age checks are often reliant on passports, driver’s licenses, or other recognized alternatives, which can pose unique challenges to people without these documents.

Much of the advocacy around age verification discusses the privacy harms of age verification. Yet these measures also threaten something more fundamental: equal access to information and the ability to exercise the right to freedom of expression. 

Unfortunately, age verification systems foster unequal access to information and provide an asymmetric solution to find essential information, build community, and weigh in on public discourse. As governments and companies increasingly require users to prove their age before accessing online services, these individuals risk being excluded from large parts of the internet altogether. 

Effects on Global Majority Countries 

Age verification laws reshape who can speak, who can access information, and who gets excluded from the digital public sphere. In other words, age verification is not a neutral safety measure: it presents a structural barrier to disproportionately exclude certain groups—particularly those in the global majority—and alters the architecture of global online expression. Some of these groups are already marginalized offline, and age verification extends that exclusion into digital spaces.

For instance, 850 million people globally do not have ID. Most of these individuals exist in primarily low and middle income countries in Sub-Saharan Africa and South Asia. The World Bank points out that many are members of marginalized groups and more than half of those lacking access to identity documentation also have children whose births have not been registered. Women are particularly vulnerable and are 8% less likely than men to have an ID. Other vulnerable groups, such as adults in low income countries, are less likely to have an ID when they fall below 25 years, as are those with a primary school education or less or those in rural areas. 

A policy paper from EDRi points out that age verification laws provide quick tech solutions but overlook longstanding structural challenges and undermine the universality of the internet. The analysis finds that age verification laws have serious human rights implications and ironically harm the very individuals they deem to protect. Moreover, these laws depend on the collection of harmful mass data that human rights organizations, including EFF, is fighting against—and has for decades. 

For example:

  • In Morocco, a push to restrict children’s access would ban under-13s from creating accounts on gaming platforms. This could potentially create challenges for those with IDs that have incomplete information concerning the year of birth. In addition, this push would also impact those who attempt to leave Morocco.
  • In Egypt, the lack of ID cards has created challenges for minority groups such as the Baha’i.
  • Stateless individuals would also struggle under age verification laws. The Rohingya, the world’s largest population of stateless people, often lack IDs. 
  • Kuwait’s Bidoon population also lacks proper identification materials. According to Amnesty International, this leads many to rely on standard civil identity cards, which can be restrictive.  
  • Nigeria launched a national program to provide ID cards to its population in 2007. Since then, 64.4 million have registered, but that represents just over 30% of the national population.
  • The Kafala system, a practice in several countries across the Middle East, also introduces challenges for age verification laws. Under this legal framework, migrant workers’ legal residency and employment status are bound to a specific employer. This potentially leaves stateless persons or migrant workers vulnerable to forced labor and restricted movements. 

No ID, No Access

Age verification laws are less about confirming the age of a user and more about creating barriers to online participation that many people cannot reliably scale. The net result is reduced access, more data collection, and an increased chance of unequal or mistaken exclusion from accessing information online. 

Nobody doubts the importance of protecting children online. While proponents assert that age verification laws protect minors from harmful material, online harassment, and digital addiction, these laws are not the solution. They subvert fundamental freedom of expression rights and pose significant privacy risks.  

EFF has long warned against age-gating the internet. Age verification technology itself is often inaccurate and privacy-invasive, and as more countries considering implementing ID-based checks, the risks move beyond censorship and surveillance toward excluding some people entirely. That’s why we’re working with groups in the U.S. and around the world to push back against these laws, and why we hope you join our effort.

For more information on how to fight back against dangerous age verification laws, visit our resource hub at eff.org/age

  •  

EFF Joins 18 Civil Rights Organizations Calling on Governor Hochul to Reject the Stealth Crawler Prohibition Act

EFF joined a group of 18 civil society organizations to send a letter encouraging New York Governor Kathy Hochul to veto Senate Bill 9934A, the New York Stealth Crawler Prohibition Act. The letter states:

While framed as a measure to protect local journalism, this legislation harms free expression and establishes a dangerous precedent by effectively deanonymizing and criminalizing automated access to the open web. By requiring all web crawlers to disclose their identity and explicit purpose, and by granting media outlets unchecked authority to obtain judicial subpoenas to unmask unidentified automated web traffic without any showing of misconduct or actual injury, this bill threatens digital privacy, compromises the foundational architecture of the internet, and will ultimately stifle the very independent journalism it seeks to protect.

As we’ve previously explained, so-called “stealth crawlers” are simply automated tools to access and collect public web data—without disclosing the user’s identity. Private crawlers like these facilitate all kinds of important work that benefits the public, including investigative reporting, academic research, cybersecurity protection, and EFF’s own Privacy Badger. As we illustrate in the letter: 

Anonymous crawling fuels important investigative journalism. For example, The Markup, a non-profit news site, used anonymous crawlers to investigate potentially anti-competitive practices by tech companies, such as Amazon’s tendency to prioritize Amazon brands and Amazon-exclusive products over competitors with higher ratings. The crawlers identified themselves as ordinary Firefox browsers to web servers, which allowed The Markup to understand how Amazon search results pages would appear to ordinary users. Similarly, ProPublica used an automated tool designed to simulate an ordinary Amazon customer to reveal that the site steered shoppers to more expensive products over cheaper alternatives. 

Anonymous web scraping is also crucial for cybersecurity professionals, who use automated tools to monitor the web for information that helps them protect against malicious attackers. Privacy tools, including EFF’s Privacy Badger, also crawl sites anonymously to identify trackers without compromising user privacy.

Laws like S9934A sweep far beyond AI, targeting anonymity rather than the real technical issue: overaggressive crawling that can overtax technological infrastructure. Unmasking crawlers won't fix these server strains, but it will chill vital public-interest research and compromise digital privacy. Addressing the harms of web scraping requires narrow technical solutions—not policies that give publishers veto power over the open web. This is why we are calling on Governor Hochul to veto S9934A.

You can read the full letter here. For a deeper dive into why crawlers and scrapers are vital for the open web, check out this blog post.

  •  

“Stealth Crawlers” Are Not a Threat to the Open Web. Bills Targeting Them Would Be.

There’s a new boogeyman in the battles over AI: so-called “stealth crawlers.” We’ll admit it—the term “stealth crawlers” sounds quite nefarious. In reality, they’re anything but.

“Stealth crawlers” are simply automated tools to access and collect public web data—without disclosing the user’s identity. Private crawlers like these facilitate all kinds of important work that benefits the public, including investigative reporting, academic research, cybersecurity protection, and more.

Anonymous crawling enables some of the most publicly beneficial uses of the open web.

Many publishers want to unmask crawlers anyways—and are pushing for new legislation that would give them new powers to do so. These legislative proposals threaten the open web, user privacy, and valuable research without directly addressing the problems they’re supposedly intending to solve.

Alarmingly, these harmful proposals are gaining traction. The New York state legislature has already passed such a bill, the NY Stealth Crawler Protection Act, which is now on Governor Hochul’s desk. We expect to see similar bills introduced in other states, and potentially in Congress. That’s a big problem for the open web—and the many benefits it provides.

Anonymous crawling is worth protecting

Anonymous crawling enables some of the most publicly beneficial uses of the open web. Researchers, journalists, and other watchdog groups use unidentified automated tools to gather the information necessary to hold powerful institutions accountable and protect the public.

Anonymous crawling fuels important investigative journalism. For example, The Markup, a non-profit news site, used anonymous crawlers to investigate potentially anti-competitive practices by tech companies, such as Amazon’s tendency to prioritize Amazon brands and Amazon-exclusive products over competitors with higher ratings. The crawlers identified themselves as ordinary Firefox browsers to web servers, which allowed The Markup to understand how Amazon search results pages would appear to ordinary users. Similarly, ProPublica used an automated tool designed to simulate an ordinary Amazon customer to reveal that the site steered shoppers to more expensive products over cheaper alternatives.

Anonymous web scraping is also crucial for cybersecurity professionals, who use automated tools to monitor the web for information that helps them protect against malicious attackers. Privacy tools, including EFF’s own Privacy Badger, also crawl sites anonymously to identify trackers without compromising user privacy.

However, without the ability to scrape anonymously, these tools would likely be blocked. Sites can—and do—block crawlers operated by researchers, journalists, and activists who criticize them. For example, Facebook shut down accounts belonging to researchers who used automated tools to study misinformation on the platform and demanded that they take down published research. Many sites block automated access by anyone who hasn’t paid to crawl public webpages.    

Unmasking crawlers threatens the open web

News publishers—and their allies in government—say that unmasking crawlers is necessary to protect news organizations from technological strain caused by AI-related crawling, and fears that AI could reduce news sites’ traffic and ad revenue. These are legitimate concerns.

But enacting broad, reactionary restrictions on automated access is not the answer. Legislation targeting anonymous crawling threatens the open web, user privacy, and valuable research without actually addressing these technological and potential economic harms of scraping.

The New York state legislature recently passed the NY Stealth Crawler Protection Act, a law that would make it illegal to crawl news websites without revealing who is operating the crawler and all possible future uses of the data collected by the crawler. The law would give websites the power to obtain court orders that unmask anyone using an unidentified crawler—without any evidence that they broke the law.

Laws like the New York bill sweep far beyond AI, and do not meaningfully address the technological or potential harms of AI-related web scraping. These policies would chill beneficial crawling by allowing publishers to veto lawful public access, giving them the power to block not just bad actors, but also security professionals, researchers, dissidents, or anyone who has not paid for a license to view public text. This needlessly undermines the free and open internet.

Digital news publishers—like most websites—face real technological challenges in the AI era. While web crawling has been around for decades, with the proliferation of AI, crawlers now collect far more public web data than they used to. This pushes servers closer to their maximum capacity, and if some bots collect information too aggressively, they may strain web servers to the point that it degrades site performance. The problem is not anonymity—so unmasking crawlers won’t solve it. The real problem is overaggressive crawling, which can be effectively addressed with technical measures that target harmful conduct without impeding anonymous access to information.

A better path forward

There are other, far less harmful ways to protect publishers from the harms these “stealth crawler” laws claim to target. Addressing the harms of AI-related crawling requires policies that narrowly target the causes of these issues–without undermining free expression and the open web. Policies that target crawlers and scrapers are anything but.

  •  

Google Broke Its Promise to Me. Now ICE Has My Data.

In September 2024, Amandla Thomas-Johnson was a Ph.D. candidate studying in the U.S. on a student visa when he briefly attended a pro-Palestinian protest. In April 2025, Immigration and Customs Enforcement (ICE) sent Google an administrative subpoena requesting his data. The next month, Google gave Thomas-Johnson's information to ICE without giving him the chance to challenge the subpoena, breaking a nearly decade-long promise to notify users before handing their data to law enforcement. 

Google names a handful of exceptions to this promise (such as if Google receives a gag order from a court) that do not apply to Thomas-Johnson's case. While ICE “requested” that Google not notify Thomas-Johnson, the request was not enforceable or mandated by a court. Today, the Electronic Frontier Foundation sent complaints to the California and New York Attorneys General asking them to investigate Google for deceptive trade practices for breaking that promise. You can read about the complaints here. Below is Thomas-Johnson's account of his ordeal. 

Out of touch but not out of reach 

I thought my ordeal with U.S. immigration authorities was over a year ago, when I left the country, crossing into Canada at Niagara Falls.  

A photo of Amandla Thomas-Johnson

By that point, the Trump administration had effectively turned federal power against international students like me. After I attended a pro-Palestine protest at Cornell University—for all of five minutes—the administration’s rhetoric about cracking down on students protesting what we saw as genocide forced me into hiding for three months. Federal agents came to my home looking for me. A friend was detained at an airport in Tampa and interrogated about my whereabouts. 

I’m currently a Ph.D. student. Before that, I was a reporter. I’m a dual British and Trinadad and Tobago citizen. I have not been accused of any crime. 

I believed that once I left U.S. territory, I had also left the reach of its authorities. I was wrong. 

The email

Weeks later, in Geneva, Switzerland, I received what looked like a routine email from Google. It informed me that the company had already handed over my account data to the Department of Homeland Security. 

At first, I wasn’t alarmed. I had seen something similar before. An associate of mine, Momodou Taal, had received advance notice from Google and Facebook that his data had been requested. He was given advanced notice of the subpoenas, and law enforcement eventually withdrew them before the companies turned over his data. 

Google had already disclosed my data without telling me.

I assumed I would be given the same opportunity. But the language in my email was different. It was final: “Google has received and responded to legal process from a law enforcement authority compelling the release of information related to your Google Account.” 

Google had already disclosed my data without telling me. There was no opportunity to contest it. 

Google’s broken promise

To be clear, this should not have happened this way. Google promises that it will notify users before their data is handed over in response to legal processes, including administrative subpoenas. That notice is meant to provide a chance to challenge the request. In my case, that safeguard was bypassed. My data was handed over without warning—at the request of an administration targeting students engaged in protected political speech. 

Months later, my lawyer at the Electronic Frontier Foundation obtained the subpoena itself. On paper, the request focused largely on subscriber information: IP addresses, physical address, other identifiers, and session times and durations. 

But taken together, these fragments form something far more powerful—a detailed surveillance profile. IP logs can be used to approximate location. Physical addresses show where you sleep. Session times would show when you were communicating with friends or family. Even without message content, the picture that emerges is intimate and invasive.  

State power meets private data

What this experience has made clear is that anyone can be targeted by law enforcement. And with their massive stores of data, technology companies can facilitate those arbitrary investigations. Together, they can combine state power, corporate data, and algorithmic inference in ways that are difficult to see—and even harder to challenge. 

The consequences of what happened to me are not abstract. I left the United States. But I do not feel that I have left its reach. Being investigated by the federal government is intimidating. Questions run through your head. Am I now a marked individual? Will I face heightened scrutiny if I continue my reporting? Can I travel safely to see family in the Caribbean? 

Who, exactly, can I hold accountable?

Update: This post has been updated to include more information about Google's exceptions to their notification policy, none of which applied to the subpoena targeting Thomas-Johnson.

  •  

Open Letter to Tech Companies: Protect Your Users From Lawless DHS Subpoenas

We are calling on technology companies like Meta and Google to stand up for their users by resisting the Department of Homeland Security's (DHS) lawless administrative subpoenas for user data. 

In the past year, DHS has consistently targeted people engaged in First Amendment activity. Among other things, the agency has issued subpoenas to technology companies to unmask or locate people who have documented ICE's activities in their community, criticized the government, or attended protests.   

These subpoenas are unlawful, and the government knows it. When a handful of users challenged a few of them in court with the help of ACLU affiliates in Northern California and Pennsylvania, DHS withdrew them rather than waiting for a decision. 

These subpoenas are unlawful, and the government knows it.

But it is difficult for the average user to fight back on their own. Quashing a subpoena is a fast-moving process that requires lawyers and resources. Not everyone can afford a lawyer on a moment’s notice, and non-profits and pro-bono attorneys have already been stretched to near capacity during the Trump administration.  

 That is why we, joined by the ACLU of Northern California, have asked several large tech platforms to do more to protect their users, including: 

  1.  Insist on court intervention and an order before complying with a DHS subpoena, because the agency has already proved that its legal process is often unlawful and unconstitutional;  
  2. Give users as much notice as possible when they are the target of a subpoena, so the user can seek help. While many companies have already made this promise, there are high-profile examples of it not happening—ultimately stripping users of their day in court;  
  3. Resist gag orders that would prevent companies from notifying their users that they are a target of a subpoena. 

 We sent the letter to Amazon, Apple, Discord, Google, Meta, Microsoft, Reddit, SNAP, TikTok, and X.  

Recipients are not legally compelled to comply with administrative subpoenas absent a court order 

 An administrative subpoena is an investigative tool available to federal agencies like DHS. Many times, these are sent to technology companies to obtain user data. A subpoena cannot be used to obtain the content of communications, but they have been used to try and obtain some basic subscriber information like name, address, IP address, length of service, and session times.  

Unlike a search warrant, an administrative subpoena is not approved by a judge. If a technology company refuses to comply, an agency’s only recourse is to drop it or go to court and try to convince a judge that the request is lawful. That is what we are asking companies to do—simply require court intervention and not obey in advance. 

It is unclear how many administrative subpoenas DHS has issued in the past year. Subpoenas can come from many places—including civil courts, grand juries, criminal trials, and administrative agencies like DHS. Altogether, Google received 28,622 and Meta received 14,520 subpoenas in the first half of 2025, according to their transparency reports. The numbers are not broken out by type.   

DHS is abusing its authority to issue subpoenas 

In the past year, DHS has used these subpoenas to target protected speech. The following are just a few of the known examples. 

On April 1, 2025, DHS sent a subpoena to Google in an attempt to locate a Cornell PhD student in the United States on a student visa. The student was likely targeted because of his brief attendance at a protest the year before. Google complied with the subpoena without giving the student an opportunity to challenge it. While Google promises to give users prior notice, it sometimes breaks that promise to avoid delay. This must stop.   

In September 2025, DHS sent a subpoena and summons to Meta to try to unmask anonymous users behind Instagram accounts that tracked ICE activity in communities in California and Pennsylvania. The users—with the help of the ACLU and its state affiliates— challenged the subpoenas in court, and DHS withdrew the subpoenas before a court could make a ruling. In the Pennsylvania case, DHS tried to use legal authority that its own inspector general had already criticized in a lengthy report.  

In October 2025, DHS sent Google a subpoena demanding information about a retiree who criticized the agency’s policies. The retiree had sent an email asking the agency to use common sense and decency in a high-profile asylum case. In a shocking turn, federal agents later appeared on that person’s doorstep. The ACLU is currently challenging the subpoena.  

Read the full letter here

  •  
❌