❌

Reading view

Gremlin Stealer's Evolved Tactics: Hiding in Plain Sight With Resource Files

Unit 42 analyzes the evolution of Gremlin stealer. This variant uses advanced obfuscation, crypto clipping and session hijacking to compromise data.

The post Gremlin Stealer's Evolved Tactics: Hiding in Plain Sight With Resource Files appeared first on Unit 42.
  •  

The npm Threat Landscape: Attack Surface and Mitigations (Updated July 15)

Unit 42 analyzes npm supply chain evolution post-Shai Hulud. Discover wormable malware, CI/CD persistence, multi-stage attacks and more.

The post The npm Threat Landscape: Attack Surface and Mitigations (Updated July 15) appeared first on Unit 42.

  •  

When an Attacker Meets a Group of Agents: Navigating Amazon Bedrock's Multi-Agent Applications

Unit 42 research on multi-agent AI systems on Amazon Bedrock reveals new attack surfaces and prompt injection risks. Learn how to secure your AI applications.

The post When an Attacker Meets a Group of Agents: Navigating Amazon Bedrock's Multi-Agent Applications appeared first on Unit 42.
  •  

Why Use a Macro Pad?

Compression is everywhereβ€”in files, videos, storage, and networksβ€”so it’s only natural it should also be in your workflow too. You can β€œcompress” a series of tedious, repetitive tasks requiring multiple steps and several configurations into a single button press with a macro pad such as the Stream Deck or a fully software-customizable mechanical keyboard.Β 

The post Why Use a Macro Pad? appeared first on Black Hills Information Security, Inc..

  •  

Attack Tactics 9: Shadow Creds for PrivEsc w/ Kent & Jordan

In this video, Kent Ickler and Jordan Drysdale discuss Attack Tactics 9: Shadow Credentials for Primaries, focusing on a specific technique used in penetration testing services at Black Hills Information Security

The post Attack Tactics 9: Shadow Creds for PrivEsc w/ Kent & Jordan appeared first on Black Hills Information Security, Inc..

  •  

PlumHound Reporting Engine for BloodHoundAD

Kent Ickler // It’s been over two years since Jordan and I talked about a Blue Team’s perspective on Red Team tools.Β Β  A Blue Team’s Perspective on Red Team Hack […]

The post PlumHound Reporting Engine for BloodHoundAD appeared first on Black Hills Information Security, Inc..

  •  

How to Weaponize the Yubikey

Michael Allen // A couple of years ago, I had a YubiKey that was affected by a security vulnerability, and to fix the issue, Yubico sent me a brand new […]

The post How to Weaponize the Yubikey appeared first on Black Hills Information Security, Inc..

  •  
  •  

How To Disable LLMNR & Why You Want To

Kent Ickler // Link-Local Multicast Name Resolution (LLMNR) This one is a biggie, and you’ve probably heard Jordan, John, me, and all the others say it many many times. LLMNR […]

The post How To Disable LLMNR & Why You Want To appeared first on Black Hills Information Security, Inc..

  •  
  •  

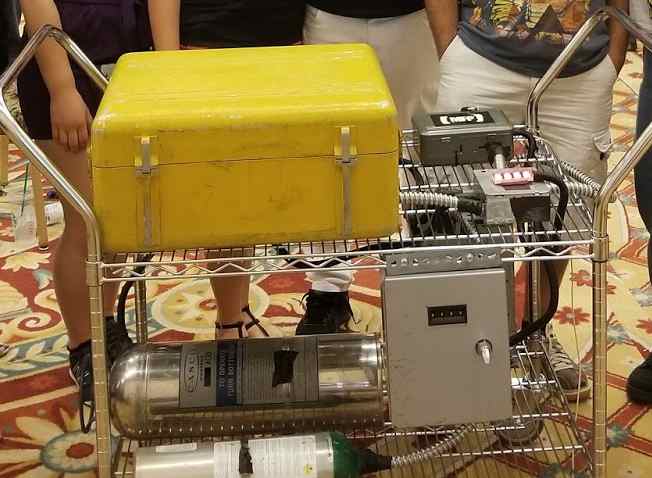
Defusing a Bomb Through Trigger Bypasses and Sensors

Mike Felch // MeetΒ β€˜The Box’ Bomb For the last few years at the security conference DEF CON in Las Vegas, the Tamper Resistant Village has hosted a challenging contest called […]

The post Defusing a Bomb Through Trigger Bypasses and Sensors appeared first on Black Hills Information Security, Inc..

  •  

How to Build Super Secure Active Directory Infrastructure*

CJ Cox // We frequently get requests from customers asking us if we provide consultation defending their systems. The other day I got a question from a customer asking us […]

The post How to Build Super Secure Active Directory Infrastructure* appeared first on Black Hills Information Security, Inc..

  •  
❌