❌

Reading view

Why set up a VPN on your router | Kaspersky official blog

VPN use is growing around the world, with the worldwide average holding steady at 20% growth per year. Users have come to appreciate everything a VPN offers: it encrypts your connection, shields you from relentless ISP tracking (and the targeted ads that often come with it), hides your IP address and location, and lets you keep using your favorite paid services while traveling. This matters most at big public events, like international football tournaments, the Olympics, or concerts by popular performers, where the odds of scammers intercepting an unprotected Wi-Fi connection go up sharply.

That said, VPNs come with their own frustrations. One of the biggest is that many smart devices – including TVs, game consoles, streaming boxes, and smart-home gadgets – can’t run a VPN at all. On top of that, you usually have to set up the VPN separately on every single device in your home. Installing the VPN directly on your home router solves both problems at once: it protects your entire home network, including newly added devices. Here’s a closer look at what benefits that setup gives you.

1. Every device gets VPN protection

Turn on a VPN on your router, and every device connected to your home Wi-Fi automatically sends its traffic through that protected, encrypted connection. There’s nothing extra to do: connect your phone, laptop, or TV to the Wi-Fi, and its traffic is already routed through the VPN.

Many paid VPN services cap the number of devices you can use under a single subscription. But your router only counts as one device on that list, even though it might be protecting a dozen or more gadgets in your home at once.

It’s worth noting that installing a VPN on a router is usually only possible with paid VPN services. Free plans typically don’t offer this option, or only allow it in a very limited way.

2. Set it up and forget it

Setting up a VPN on every phone and computer in the house can get tedious fast. And if your home devices run on a mix of operating systems, you’ve to start by locating the VPN settings on each one, since Android, Windows, iOS, and macOS all handle this differently.

With a router setup, you configure the VPN once, and it automatically covers any new device you connect later too.

3. Protection even for devices that don’t support VPN

Plenty of devices can’t run a VPN at all. That includes smart TVs, streaming boxes, game consoles, and nearly every piece of smart-home tech out there, from baby monitors to robot vacuums. A VPN on your router protects all of them, and you don’t have to tinker with your vacuum cleaner or smart bulb’s settings separately.

4. No need to worry about turning the VPN on and off

Many people want to make sure that not a single byte of their data leaves their device before the VPN kicks in. The problem is that there’s always a short gap between turning on a computer or phone and the VPN firing up, and during that window, data travels over the internet unencrypted.

The usual fixes are to turn on special features – such as Always On VPN or a VPN kill switch – in the operating system or VPN app. A more effective option though is running the VPN on the router itself. That way, “not a byte without the VPN” becomes true automatically for every device on your home network. But for complete peace of mind, you’ll still want to set up a kill switch on the router too, so that if the VPN ever disconnects (say, the VPN server becomes temporarily unavailable), your devices lose their internet connection entirely rather than falling back to an unprotected one.

5. Working remotely with two VPNs at once

Another common headache is needing to run two VPN services at the same time. This usually comes up with remote work: you need a corporate VPN to connect to your company’s network, while also wanting a personal VPN for everything else. On many devices, running two VPN connections at once for different purposes is either a real hassle to configure or not possible at all. Constantly switching between the two isn’t convenient either, and it opens up privacy and security gaps.

A VPN on your router solves this too. You simply turn on the corporate VPN on your work computer, and it runs on top of your Wi-Fi connection, which is already protected by your personal VPN on the router. In effect, you end up with one VPN nested inside the other (corporate VPN → Wi-Fi → VPN → internet), but this layered setup rarely causes any issues.

6. Getting around apps that block VPNs

Some banking and streaming apps can detect when a VPN app is running on your device and simply refuse to work. Usually, they can’t tell what kind of VPN it is or why you’re using it. They just object to any VPN connection being active at all. If the VPN runs on your router instead of on the device itself, this problem disappears.

7. Protecting guests on your home network

Any device belonging to friends or family that connects to your Wi-Fi automatically gets VPN protection too, with no setup required on their end.

8. Less strain on your devices

Since the router handles the encryption workload, your phones, tablets, and other lightweight devices can use less computing power and drain less battery than they would if running a VPN themselves.

9. Simplified VPN management

Need to switch VPN servers, change protocols, or tweak other settings? Just do it once, on the router. There’s no need to reconfigure every device separately.

Precautions and things to keep in mind

For all its advantages, running a VPN on your router does come with a few trade-offs worth knowing about.

  • Encrypting traffic for an entire network takes real processing power, so on an underpowered router, your connection speed may end up limited.
  • Some routers don’t support VPNs at all, or only work with older, less secure protocols like PPTP.
  • If your router was issued by your ISP, you may not have enough permissions to install a VPN on it.

In any of these cases, you can buy a more capable router that supports VPNs, and use it either instead of, or alongside the ISP-issued box, setting up your home network and VPN on your own hardware.

With this setup, your devices connect as follows: device → Wi-Fi or Ethernet → personal VPN on router → internet. For computers that also connect to a corporate VPN, the path looks slightly different: corporate VPN on computer → Wi-Fi or Ethernet → personal VPN on router → internet.

If you can’t connect your own router directly to your ISP’s network because your model lacks the right port (for example, with a fiber connection), you can use an Ethernet cable to plug your personal router’s input into your provider’s box. In that case, you can either switch the ISP-issued router into bridge mode or simply turn off its Wi-Fi so it doesn’t add unnecessary wireless clutter, since its only job now is connecting to the provider’s network and passing that connection along to your own router.

It’s also worth noting that some online services – like banks, government sites, online stores, and streaming platforms – may restrict or block access entirely when they detect a foreign IP address through a VPN. To get around this, you can either turn off Wi-Fi on your phone and use your mobile data instead, or take a more sophisticated approach to your router setup, as described below.

Most modern routers let you create more than one Wi-Fi network, usually supporting at least a separate home and guest network, each with their own settings. You can use this to create two networks: one with the VPN always on, and one without. Then, for services that don’t play well with VPNs, you can simply switch to the unsecured Wi-Fi network instead.

If you’re willing to spend some more time on setup, there’s an even more convenient option, known as split tunneling: individually configuring certain services or websites to bypass the VPN while sending everything else through your secure VPN connection as usual. To do this, you’ll need to specify the addresses of the sites that should skip the VPN.

Many feature-rich routers also let you divide your home devices into groups and set different connection rules for each group. That way, you could set things up so your smart TV reaches streaming services without a VPN, while your smart home devices, computers, and phones only ever connect to the internet through the protected channel.

How to set up a VPN on your router

Setting up a VPN on your router might sound more complicated than installing it on individual devices, but it delivers far more comfort and protection for your whole home network.

To do this, you’ll need a router that supports VPNs, and a subscription to a VPN service that can generate configuration files for routers using modern VPN protocols. Kaspersky VPN supports the two most widely used VPN protocols – OpenVPN and WireGuard – for connecting routers to the service.

You can create a Kaspersky VPN configuration file for your router by following our detailed guide. For instructions specific to your router model, we recommend searching online or asking an AI assistant something like “how to set up a VPN on {your router model}“.
  •  

Study on the Wi-Fi security situation in Mexico | Kaspersky official blog

One of the biggest football (soccer) events of this summer is the World Cup 2026. The tournament is co-hosted by three countries: the U.S., Canada, and Mexico. Unfortunately, events of this scale attract not just fans, but also scammers from all over the globe. We’ve already covered how cybercriminals are prepping for the World Cup online, and today we’re talking about digital security for fans on the ground in Mexico.

The country will host 13 matches and welcome millions of tourists. They’ll be staying in hotels, heading to games, checking out restaurants, navigating airports, and visiting popular tourist spots — and everywhere they go, the temptation to connect to public Wi-Fi will be high.

We’ve surveyed more than 84 500 (!) public Wi-Fi access points in Mexico City, Guadalajara, and Monterrey — and we have a lot to share about their security. Spoiler alert: many networks are still using outdated security standards, so you really shouldn’t go on vacation without reliable protection and an eSIM.

What and how we tested

Walking across Mexico looking for public Wi-Fi access points would have been a bit tough, though that’s exactly what we did for a similar Wi-Fi security survey in Paris. You can check out the results of that in our post, How safe is Wi-Fi in Paris?

This time the mission was far more demanding: mapping the wireless landscape of three major metropolises. That’s why we went wardriving — scanning for and logging wireless networks from a moving vehicle while equipped with a smartphone or laptop. It’s similar to searching for Wi-Fi on your phone, where the device constantly listens for nearby networks. Except instead of connecting to them, we just collect data about them.

All information was used strictly for passive observation and infrastructure analysis. Beyond receiving publicly broadcast service information, the experts of Kaspersky’s Global Research and Analysis Team (GReAT) didn’t attempt to authenticate, intercept traffic, exploit systems, or otherwise interact with the wireless networks they discovered. Mobile access points deployed in cars and on mobile devices were excluded from the sample.

Our main target was Mexico City — the capital and one of the most densely populated cities in Latin America. We took a drive through popular tourist spots: Mexico City Stadium, Mexico City International Airport, Zócalo, Paseo de la Reforma, Colonia Roma, La Condesa, Polanco, Coyoacán.

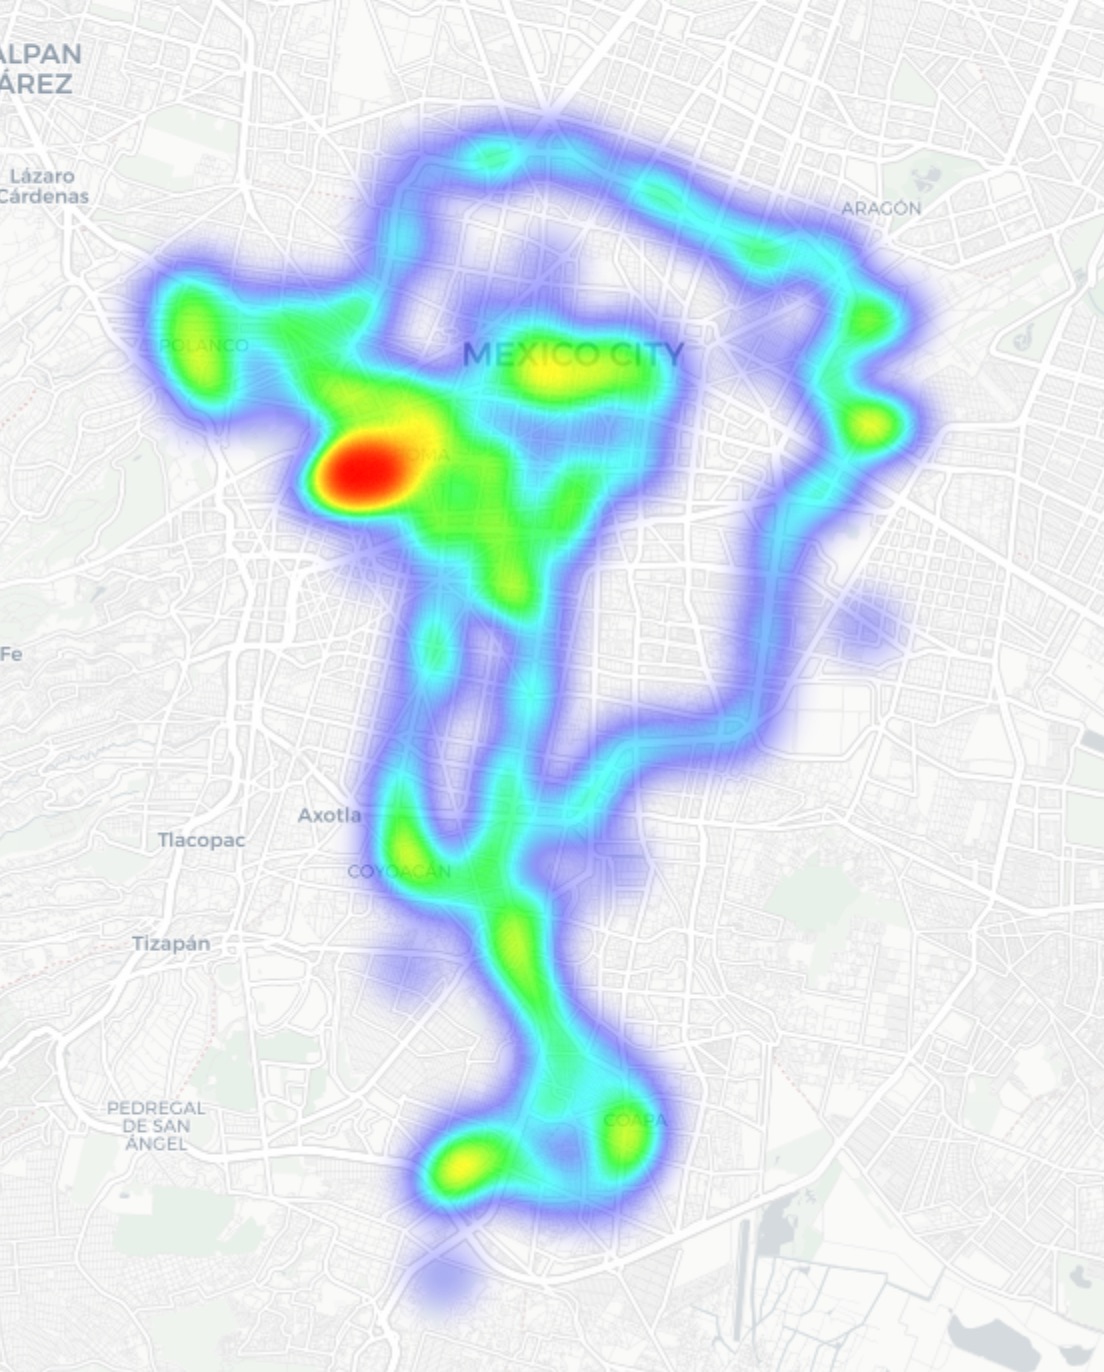
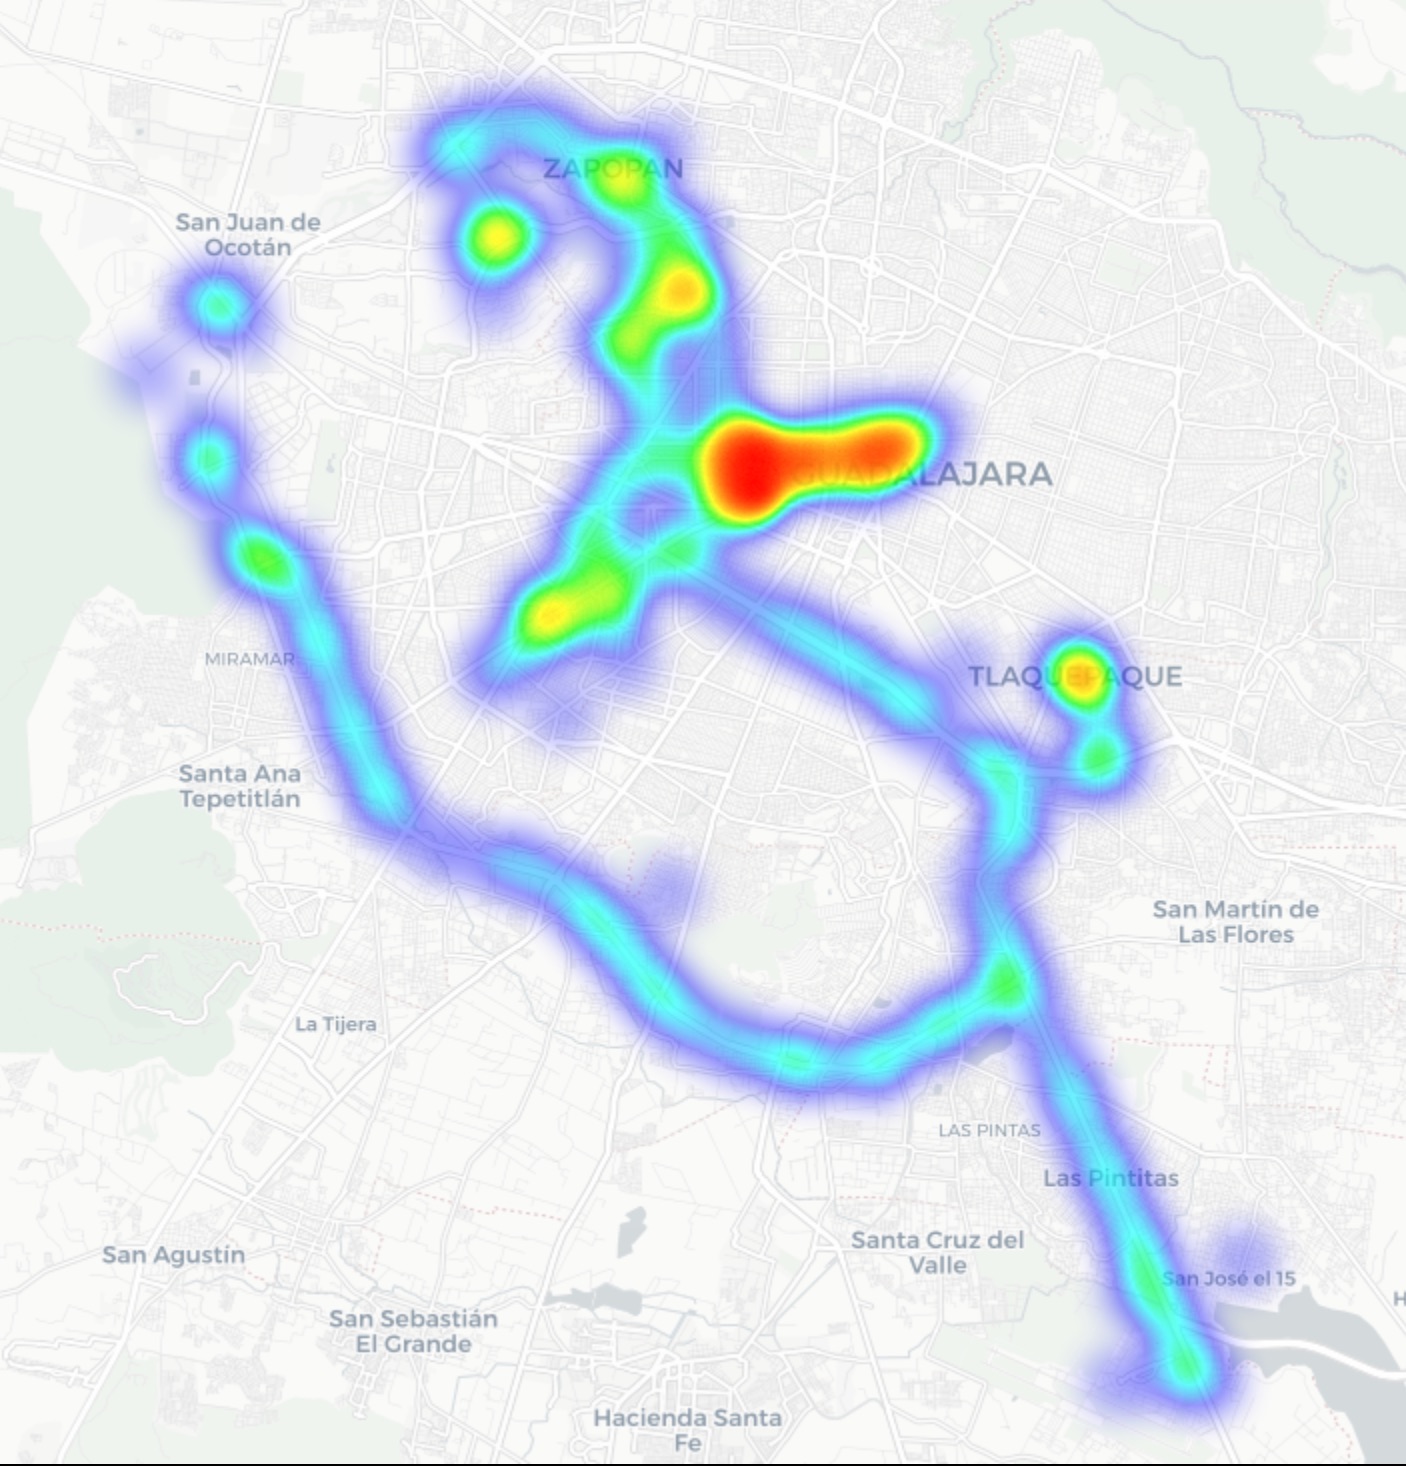
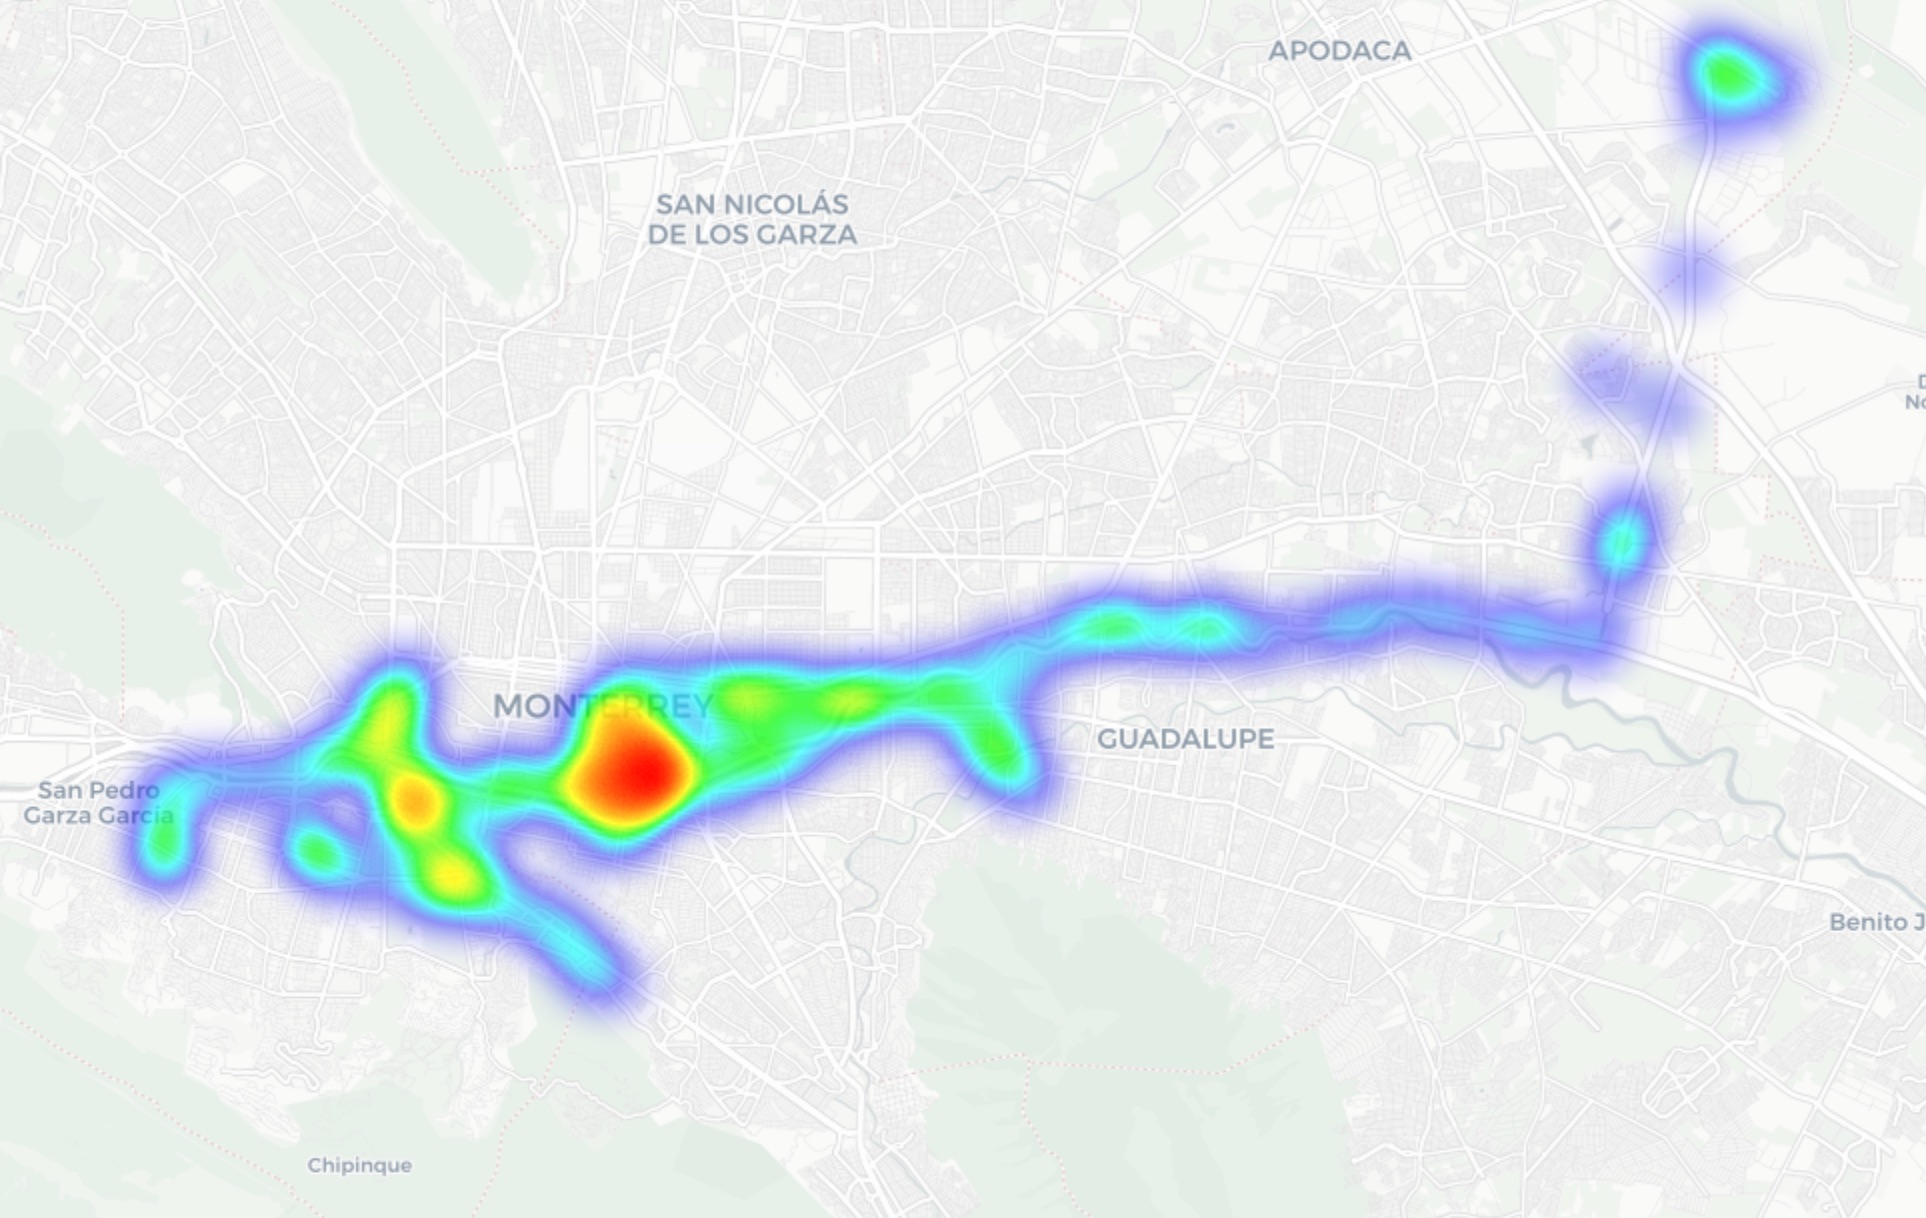
In Guadalajara and Monterrey, we drove similar routes: stadiums, main avenues, airports, and popular neighborhoods. Below you can see a heatmap of the areas we covered, ranging from red for areas with the highest density of public access points, through yellow and green, to blue for the lowest concentration.

Heatmap showing the locations of all Wi-Fi access points we covered in Mexico City
Heatmap showing the locations of all Wi-Fi access points we covered in Guadalajara
Heatmap showing the locations of all Wi-Fi access points we covered in Monterrey

We used passive radio reconnaissance to log 84 500 signals and 69 500 unique network identifiers across these three cities. The majority of the signals were caught in Mexico City (61.4%), followed by Guadalajara (23.6%) and Monterrey (14.8%).

What we analyzed:

  • Wireless network identifiers (SSIDs): the names that show up in your list of available Wi-Fi networks
  • Information that can be gleaned from these identifiers
  • Default router configurations and how ISPs deploy their networks
  • Frequencies used and signal characteristics
  • Channel load and radio frequency spectrum usage
  • Wireless network security configurations:
    • Open and insecure networks
    • Networks with WPS enabled
    • Secure networks (WPA2/WPA3) with WPS activated

You can find the full version of the study on the Securelist blog.

Telltale public Wi-Fi access point names

Network names (SSIDs) can tell you a lot by unintentionally revealing information about hardware manufacturers, ISPs, deployment methods, and whether an access point belongs to a business or a private user.

About 34% of the public Wi-Fi networks we logged didn’t bother changing their names at all, either sticking with the factory SSIDs from the router manufacturers or using standard naming conventions from their ISPs. For attackers, this can be a pretty solid hint, since this kind of network name lets them know which provider owns a given access point, what hardware is being used, and how it’s likely configured by default.

Another troubling nuance is the large number of Wi-Fi networks (over 30%) that use the access point’s MAC address (BSSID) as the visible network name. The first few bytes of a BSSID contain an Organizationally Unique Identifier (OUI), which gives away the router’s manufacturer. This is a useful lead for bad actors: they can find out who made the hardware and test for vulnerabilities specific to that brand’s models.

Is Mexican Wi-Fi well-protected?

An access point secured with WPA2/WPA3 can be considered more or less safe. All other authentication mechanisms yield much weaker results. We grouped the public Wi-Fi networks into four categories:

  • Secure (WPA2/WPA3)
  • Unsecured (open/WEP)
  • Weak (WPA)
  • Undetermined

The results are roughly the same across all three cities: about 82% of all analyzed access points are protected by secure standards. The outdated and insecure WPA protocol was practically nonexistent. However, more than 10% of the access points turned out to be completely unsecured. Connecting to these networks carries the risk of traffic interception and hidden surveillance.

But security isn’t evaluated by WPA protocols alone. We also checked for the presence of WPS, the infamous feature for quickly connecting to a network without entering a password, which is highly vulnerable to attacks. It turned out that WPS is enabled on nearly half (47%) of the access points in Mexico City, 43% in Guadalajara, and 41% in Monterrey. On average, 45% of the access points are potentially vulnerable to WPS-related attacks — sacrificing security for the sake of convenience.

What’s more, this feature frequently remained active even on seemingly secure WPA2/WPA3 networks — about half of them utilized WPS. This shows that having WPA2/WPA3 is still not enough to consider a Wi-Fi access point safe, as additional features like WPS can still leave the door open to attacks.

What else every tourist needs to know

Digital risks on a trip aren’t limited to public Wi-Fi alone, especially now that many are shifting away from public Wi-Fi to an eSIM. There are still plenty of threats in crowded places: public USB chargers, QR codes with swapped links, NFC and Bluetooth attacks, and, of course, social engineering tactics. Let’s break it all down.

Charging stations. Public USB chargers can also be dangerous: bad actors could potentially gain access to the data on your device or try to install malware. We covered these attacks in detail in our post, Data theft during smartphone charging.

Dangerous QR codes. Criminals can plant phishing QR codes in popular tourist spots. The pretexts can vary wildly; for instance, ads for team-specific fan “events”, or links supposedly offering discounts or restaurant menus. In reality, any QR code posted on the street can be considered insecure by default, and you shouldn’t scan them with your smartphone unless you have a QR code threat analyzer installed.

Fake broadcasts, tickets, and betting pools. Earlier, we described cases where bad actors were distributing malware via fake IPTV apps to capitalize on the WC26 hype. Remember, even if you plan to watch the tournament from home, you still need to stay alert and not trust the first sites that pop up advertising free broadcasts, offering betting pools, or promising unbelievably generous payouts.

NFC and Bluetooth attacks. Leaving Bluetooth enabled in crowded places can also cause problems: someone might try to discover your device, track you, or initiate an unwanted pairing request. NFC services with contactless payments create additional risks too — especially when paying in sketchy spots.

How to protect yourself and your devices

Despite the prevalence of secure WPA2/WPA3 public Wi-Fi access points in Mexico City, Guadalajara, and Monterrey, our study shows that public Wi-Fi networks remain vulnerable. It’s also important to remember that attackers can create fake networks — so-called evil twins — disguised as legitimate public Wi-Fi in airports, hotels, cafés, and tourist spots.

For the average user, it’s practically impossible to tell how safe a specific access point is when trying to connect. That’s why the safest option is to use cellular data to access the internet — completely eliminating the need for Wi-Fi. Besides, there’s no need to research the nuances of local laws, rates, and other cellular details for every country you plan to visit; you can just buy a global eSIM online in two clicks. We explained how to make the entire process hassle-free in our post, Internet on the go with Kaspersky eSIM Store.

If you still plan on connecting to public Wi-Fi, always use a VPN to secure your device and data when connecting to unfamiliar — especially unsecured — Wi-Fi networks. This creates an encrypted tunnel between your device and the VPN server, making it impossible to intercept your data along the way. Haven’t picked a VPN yet? Try Kaspersky VPN Secure Connection, which is included with both Kaspersky Premium and Kaspersky Plus subscriptions.

Now, if you still plan to attend the World Cup without any cybersecurity solution, at least follow these basic rules of digital hygiene:

  • Don’t use public USB chargers
  • Don’t send sensitive information over connections that aren’t secure
  • Don’t log in to banking, email, or social media accounts over unsecured Wi-Fi
  • Turn off Bluetooth and NFC while walking around in crowded places
  • Don’t trust QR codes posted on the street
  • Connect to public Wi-Fi only when absolutely necessary

What else to read to make sure cheering for your favorite team isn’t only exciting, but also safe:

  •  

Securing the Cloud: A Story of Research, Discovery, and Disclosure

Jordan Drysdale // tl;dr BHIS made some interesting discoveries while working with a customer to audit their Amazon Web Services (AWS) infrastructure. At the time of the discovery, we found […]

The post Securing the Cloud: A Story of Research, Discovery, and Disclosure appeared first on Black Hills Information Security, Inc..

  •  
❌