❌

Normal view

Argamal RAT: attackers distributing a remote access Trojan through hentai games | Kaspersky official blog

By: GReAT
9 June 2026 at 18:57

In April 2026, we discovered a new campaign targeting users of hentai games. Attackers are embedding a remote access Trojan named Argamal into game installers. While concealing its presence, it can remotely control the computer and steal files and personal data.

Here’s how to avoid falling victim to this new Trojan — and how to safely and anonymously enjoy spicy content with (or without) anime girls.

How computers get infected with Argamal

Most of the infected games are distributed through adult game and torrent sites. In some cases, they are posted for download on file-sharing services and linked on gaming websites.
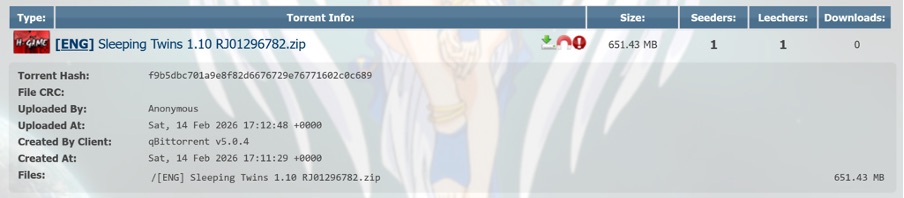
Trojanized hentai game Sleeping Twins hosted on AniRena

Example of a trojanized game hosted on the AniRena torrent tracker

Interestingly, instead of finding a dummy file inside the archive — as is often the case — the user gets the actual game built on popular engines like RenPy or RPG Maker. Infected pirated versions usually turn out to be scams: games fail to launch, folders are full of files with bizarre extensions, making it rather easy to put two and two together. Here, however, the user gets the actual gameplay they expected. Meanwhile, the Trojan lets itself in and keeps a completely low profile.
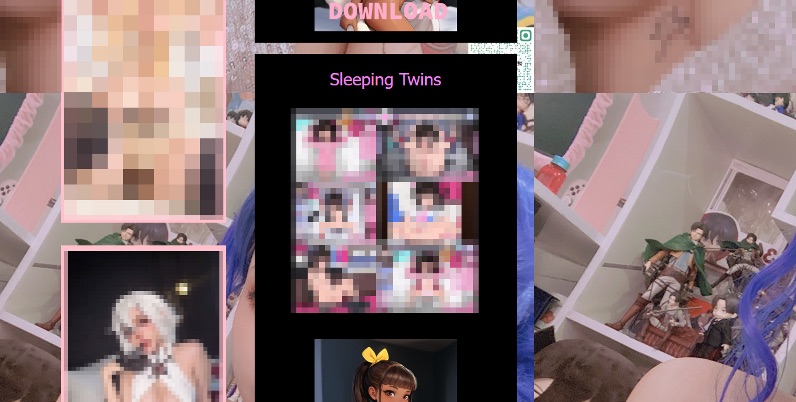
Malicious website featuring a library of trojanized hentai games

Example of a trojanized game hosted on the AniRena torrent tracker

Tucked right alongside the legitimate files in the archive is a DLL that the game relies on to run, but it’s been rigged: as soon as the user launches the game, the infected DLL automatically loads into memory. There are no outward signs of infection: neither an installer popping up in the background, nor a scary window or prompt asking you to disable your antivirus.

Argamal takes things real slow: instead of immediately rushing to steal files and passwords or throwing a digital rager on your computer, the Trojan first checks whether it’s running in a virtual machine or sandbox, and then goes into standby mode.

During this time, the malware writes hidden parameters to the system, conceals the paths to its DLLs, and delays its own execution. Three days later, the computer connects to GitHub, downloads an encrypted file, decrypts it, and turns it into a working Trojan module.

To ensure persistence, the attackers register the malware under the WindowsColorSystem Calibration Loader system task, a built-in Windows feature that triggers at every user logon to load monitor color profiles. Before shutting down, the malware deletes temporary files and covers its tracks to make it even harder to detect.

What makes Argamal dangerous?

Argamal is a remote access Trojan (RAT), which means attackers can use it to remotely control the victim’s computer. Here’s just a short list of what it may entail:

  • Executing arbitrary commands on the computer
  • Downloading and running files
  • Checking if an antivirus is installed on the PC (by the way, our security solution detects and neutralizes Argamal before it can harm you)
  • Searching for and exfiltrating sensitive data from files and system settings
  • Taking screenshots and streaming video from the device
  • Sending data to the attackers’ server
  • Monitoring user activity
  • Shutting down or restarting the device

Essentially, the infected computer turns into a remotely controlled machine. The owner may keep calmly going about their day, completely unaware that their device has been compromised. Yet the consequences of such an infection can be devastating.

For example, a single password stolen from a text note can lead to multiple compromised accounts at once if the victim reuses the same credentials across different sites. That’s why we recommend storing strong and unique passwords in an encrypted vault of a password manager rather than in plain text files.

Beyond hijacking accounts, the Trojan lets attackers literally spy on the user — reading their chats, digging into secret files, studying their sexual preferences… The cybercriminals can then use this highly sensitive information for subsequent attacks, blackmail, and extortion. We’ve covered what to do if you find yourself being targeted by extortionists in a previous post.

Another common scenario involves quietly stealing or substituting financial data — for instance, intercepting credentials from banking apps or replacing crypto-wallet addresses in the clipboard, which sends all your money straight to the attackers’ accounts.

In short, there’s a whole laundry list of ways attackers can exploit a victim’s device and data.

Argamal, yamete kudasai! How to protect yourself from similar threats

If you’ve decided to become the proud owner of “Waifu Simulator Ultra Definitive Edition”, stay on your guard:

  • Use security software that runs in real time and catches sophisticated malware. Despite the attackers’ best efforts to make the Trojan invisible, Kaspersky Premium instantly detects and removes Argamal from users’ devices.
  • Avoid downloading adult apps, installation files, and spicy content from untrusted sources. Clicking a “free XXX game, no signup needed” is a surefire way to invite malware onto your device. That said, even official platforms like Google Play and the App Store unfortunately let infected apps slip through the cracks at times. To stop worrying about accidentally downloading a Trojan or an infostealer, use Kaspersky Premium on all your devices.
  • Don’t share more data than you absolutely have to. If an adult game or website insists you sign up, enter personal data, or link third-party accounts instead of just checking your birth date, that’s a huge red flag. Sites rarely collect sensitive data for no reason. In the best-case scenario, it ends up with marketers and ad trackers. In the worst-case, it falls into the hands of bad actors who will use it for blackmail, phishing, or breaking into your other accounts.
  • Don’t click ad banners on adult websites. Even the most popular platforms like Pornhub occasionally host ads laced with malware. If you find it hard to hold back, use a security solution that will block malware downloads and prevent redirects to suspicious sites.

How fake Android IPTV apps are stealing users’ money and data | Kaspersky official blog

Threat actors are already gearing up for this year’s biggest football (soccer) event, the World Cup 2026. With millions of fans looking for ways to stream matches online, many will turn to IPTV apps to watch live TV broadcasts over the internet. It’s no surprise, then, that cybersecurity researchers have discovered multiple campaigns over the past few months where malware was disguised as fake Android IPTV apps.

In this post, we discuss what IPTV apps are, how criminals use fake versions to spread malware, what this malware is capable of, and, most importantly, how to avoid becoming a victim.

What are IPTV apps?

IPTV stands for Internet Protocol Television. This technology delivers TV content over the internet instead of through cable, over-the-air antennas, or satellites. Naturally, the simplest and most common examples of IPTV are the official platforms of TV networks, which can include both websites and dedicated apps.

However, alongside official options, pirate IPTV services also exist. They usually lure users with free or dirt-cheap access to content that can otherwise be hard to find without expensive subscriptions — most notably broadcasts of various sporting events; football matches in particular.

As is typically the case with pirated content, these apps are blocked from official app stores, forcing users to download them from third-party sites. Consequently, the risk of using these services isn’t tied to IPTV technology itself, but rather to the fake apps and modified APK files distributed under the guise of well-known platforms — both official and pirated.

Massiv banking Trojan disguised as IPTV apps

For instance, in February researchers found the Massiv banking Trojan distributed under the guise of fake IPTV apps. Even then, experts noted that this wasn’t the only malware leveraging this tactic — several others were also spotted in the wild. The primary targets of these IPTV-mimicking malicious fakes have mostly been users in Portugal, Spain, France, and Türkiye.

In most cases, the discovered fake IPTV apps lacked the advertised functionality, so users didn’t get access to any content after installing the apps. Instead, the fake app would open the website of a legitimate IPTV service in a built-in browser to mimic normal functioning and avoid raising user suspicion.

Of course, the most interesting activity happened out of the user’s sight. These are some of the features the malware did have:

  • Displaying fake windows on top of legitimate ones: fake forms for entering bank details or signing in to official services, as shown in the screenshot below.
  • Activating a keylogger: recording and transmitting screen keyboard taps to the attackers.
  • Hijacking control of the compromised device.
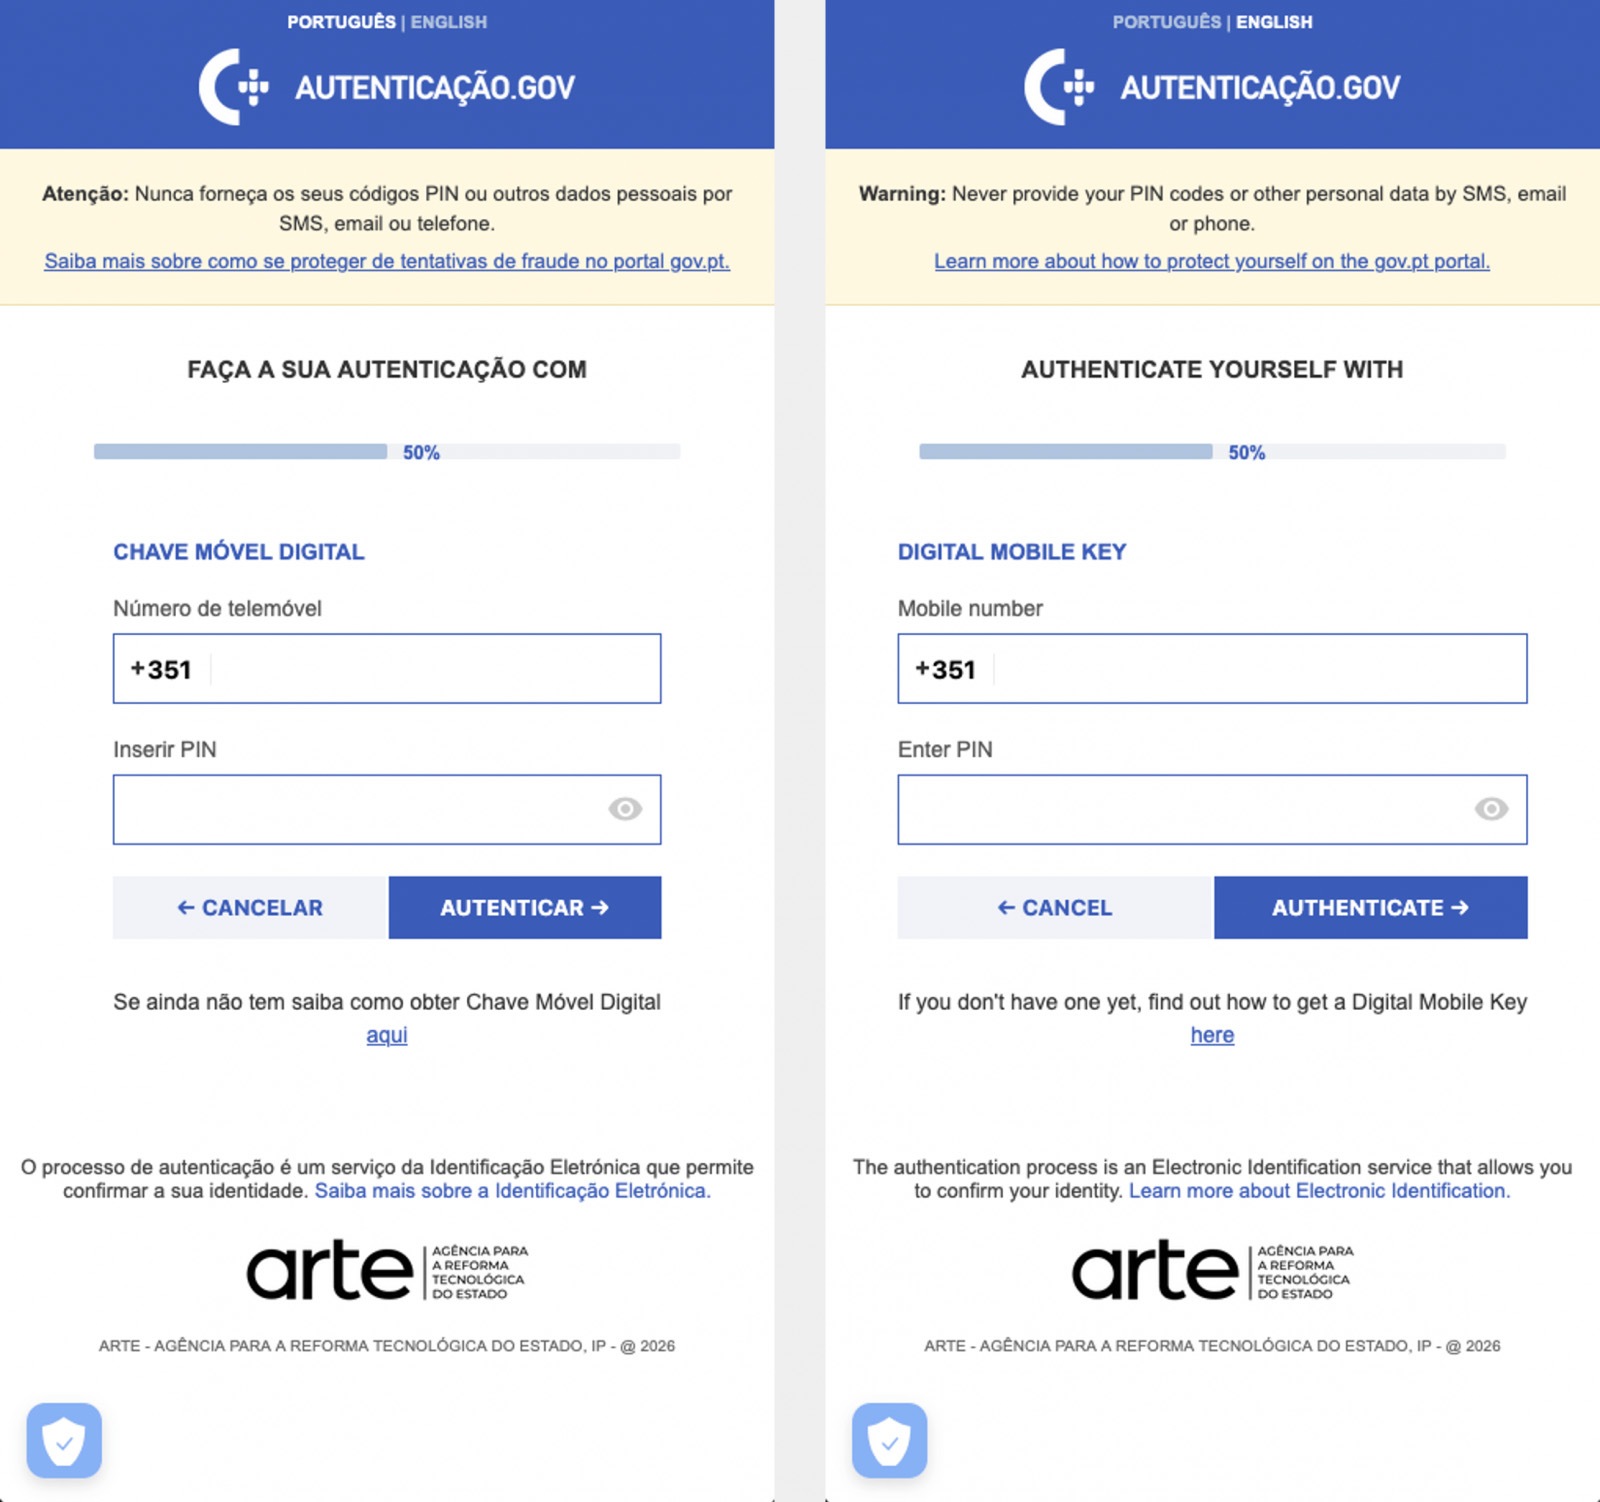
Massiv Trojan steals Chave Móvel Digital data

The Massiv banking Trojan mimics the interface of the Portuguese government app Chave Móvel Digital in a fake pop-up window, looking even more convincing than the official version from Google Play. Source

Perseus steals valuable information from users’ notes

In March, researchers reported on a new campaign where several fake IPTV apps were used to distribute an even more advanced and feature-rich malware strain: Perseus.

Research into Perseus shows that the malware is based on the source code of an Android banking Trojan called Cerberus, which leaked nearly six years ago. Perseus comes in two different versions: Turkish and English. The English-language version is more advanced and shows clear signs of AI-driven refinement.

Perseus abuses Accessibility Services, a set of Android features originally designed to make life easier for users with severe visual impairments. Fraudsters learned long ago how to leverage this tool to steal data from Android devices — a topic we’ve covered in detail across several of our posts.

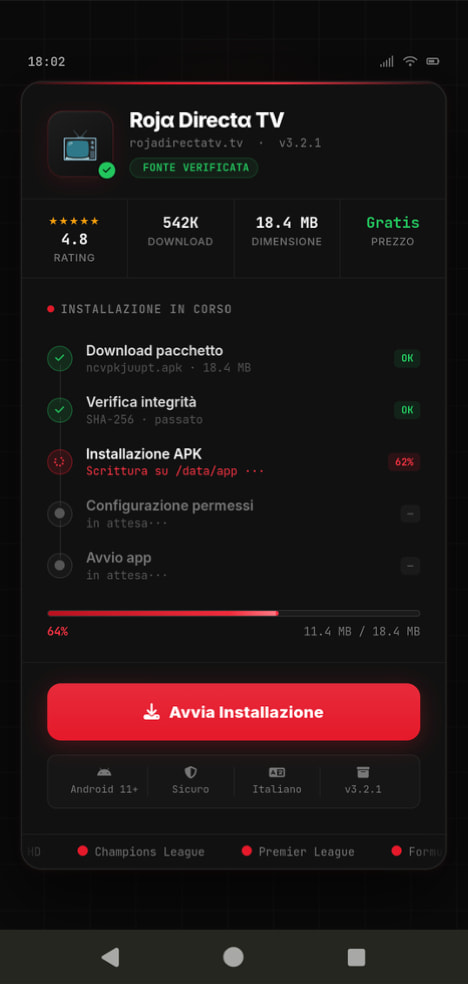
Fake IPTV app used for distributing Perseus

An example of a malicious APK disguised as Roja Directa TV, another IPTV app. Source

By abusing Accessibility Services, Perseus gains remote control over the victim’s device. Here’s what it can do:

  • Continuously capture and exfiltrate screenshots.
  • Send a structured map of the device’s UI for remote manipulation.
  • Mimic taps, swipes, text input, long presses, and other UI interactions.
  • Turn on the screen, launch apps, and block them from running.
  • Trigger a pitch-black screen overlay to hide its activities.
  • Log keystrokes.

On top of that, the English-language version of Perseus boasts another notable feature. The malware can hunt for sensitive information like passwords, recovery phrases, and financial data across an entire range of note-taking apps: Google Keep, Xiaomi Notes, Samsung Notes, ColorNote, Evernote, Microsoft OneNote, and Simple Notes.

All of these capabilities help criminals drain football fans’ money not just from various banking services, but from cryptocurrency apps as well.

How not to let cybercrooks ruin your World Cup

The World Cup is just around the corner, and millions of fans worldwide will definitely want to tune in to this year’s premier football event. Past experience shows that cybercriminals frequently cash in on major spectacles like this. So, how can you watch the  matches safely?

  • Don’t download apps from unofficial stores.
  • Even when downloading an app from an official store — since malware occasionally slips through the cracks there, too— read the reviews carefully. Users who have been burned by fakes and malware often leave comments to warn others.
  • Install a robust security app to keep all your devices safe from malware.
  • Avoid storing passwords or other sensitive information in note-taking apps. To ensure your data and finances stay secure, use a reliable password manager. By the way, Kaspersky Password Manager includes an encrypted note-taking feature, allowing you to store your valuable information safely.

You can’t even watch TV safely anymore these days! Check out other threats facing TV lovers:

❌