Quest Diagnostics has confirmed that an unauthorized party accessed a system healthcare providers use to order laboratory tests and view results, affecting personal information and patient records.
Quest is a major US laboratory testing company whose services help healthcare professionals diagnose and monitor medical conditions. Those services range from routine laboratory testing to specialized testing in areas such as cancer, infectious diseases, and neurology.
What happened and what was stolen?
The company learned of unauthorized access to its Quanum Lab Services Manager, or LSM, on October 21. The compromised platform lets healthcare professionals order tests, access results, review historical trends, and order supplies. Quest paused access to the platform and began investigating. Quest says its core business operations remain up and running.
An investigation is ongoing. Quest has not yet published a count of affected patients or a complete list of the information accessed. It says it will notify affected patients, healthcare providers, and health plans.
The company said:
“personal information and patient records were affected.”
It confirms that health information and personally identifiable information were involved, but has not specified whether these included Social Security numbers, insurance identifiers, payment information, particular test results, or account passwords.
What patients can do now
Quest says it will send notification letters to affected patients once its investigation is complete. Those letters will describe available resources, including credit and identity monitoring. If you receive one, read it carefully and follow the instructions. You can also check the FAQs posted in Quest’s breach notice for updates.
Someone’s watching your accounts. Make sure it’s us.
A breach does not automatically mean someone has misused your information, but you can take these precautions while you wait for more details:
Verify unexpected messages independently. Don’t let a message about the breach rush you into clicking a link, sharing sensitive information, or making a payment. Go to Quest’s official website yourself or use contact details you already trust.
Review medical bills and insurance statements. Look for appointments, tests, prescriptions, or services you did not receive. The Federal Trade Commission (FTC) identifies unfamiliar medical bills and unexpected items on an Explanation of Benefits statement, which explains how your insurer processed a claim, as warning signs of medical identity theft. Report discrepancies to your healthcare provider and your insurer.
Review your credit reports. Look for unfamiliar accounts or debts and dispute errors. Free reports are available through AnnualCreditReport.com.
Act if you find signs of identity theft. Visit IdentityTheft.gov for a recovery plan. If someone has received care in your name, ask the providers involved for copies of your medical records and request corrections in writing.
Medical identity theft is not just a financial problem; it can also affect your care. Someone using your identity to obtain treatment or submit insurance claims could introduce incorrect information into your health records. Checking medical statements and reporting anything unfamiliar can help you catch that misuse.
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
.kadence-column480618_38f885-ca > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column480618_38f885-ca > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column480618_38f885-ca > .kt-inside-inner-col{flex-direction:column;}.kadence-column480618_38f885-ca > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column480618_38f885-ca > .kt-inside-inner-col{background-color:#ffe5e5;}.kadence-column480618_38f885-ca > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column480618_38f885-ca{position:relative;}@media all and (max-width: 1024px){.kadence-column480618_38f885-ca > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column480618_38f885-ca > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}
In this article
Capcom’s breach exposed 11.7 million account records.
Leaked details could fuel convincing phishing messages.
Passwords on 196 accounts were changed without permission.
Use CAPCOM ID? Check your account and enable two-factor authentication.
Gamers are being warned to watch their inboxes after someone gained unauthorized access to Capcom’s online membership service.
Capcom, the Japanese video game developer and publisher behind Resident Evil, Monster Hunter, and Street Fighter, disclosed a breach affecting more than 11.7 million CAPCOM ID records worldwide.
The exposed information includes email addresses, account activity details, and IP addresses. A much smaller number of records also contained personal details such as dates of birth.
The company says credit card information was not affected, and it has not confirmed that passwords originally chosen by customers were compromised, but someone changed the passwords on 196 accounts without authorization. Capcom has since reset those passwords.
CAPCOM ID is the company’s unified account system for its websites and services, including online features in certain games. Users can also link it to gaming platform accounts, including PlayStation, Xbox, Steam, Epic Games, and Nintendo accounts.
For players, the exposed information could help scammers make fake Capcom messages more convincing, potentially tricking them into handing over passwords or verification codes.
Capcom discovered the incident on October 19, and says it has addressed the attack method. Games and services remain available, and the company plans to notify affected customers.
The 11.7 million figure refers to affected records, so it may not represent that many individual users. Capcom is still investigating the impact, including how the passwords on 196 accounts were changed without permission and whether any other unauthorized activity occurred on those accounts.
How to stay safe
As with any breach, watch for phishing messages, particularly those using the breach to create urgency. If an email claims your account needs attention, open your browser and go to cid.capcom.com independently to check it. Capcom warns users not to follow URLs or open attachments in suspicious messages.
You can also take these steps:
Enable CAPCOM ID’s two-factor authentication: This adds an authenticator-app code to the sign-in process, helping protect your account if someone obtains your password. Set it up from your Account page using a smartphone or tablet. Capcom recommends Google Authenticator or Microsoft Authenticator.
Check your account, especially if you received an unexpected password-change notice: Review your registered information and linked platform accounts from your Account page. If you cannot sign in, use Forgot your password? on the login page. See Capcom’s support page for instructions.
Use officialsupport channels if you need help: Find the appropriate regional contact in Capcom’s breach notice, rather than trusting contact details in an unexpected message.
Pro tip: Unsure whether a message is a scam? Malwarebytes’ Scam Guard can help you assess it and suggest what to do next.
Something feel off? Check it before you click.
Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.
A breach exposed personal information in supposedly anonymous crime reports. Now one Crime Stoppers chapter has stopped accepting tips because it cannot guarantee anonymity.
Toronto Crime Stoppers, which works with the community, police, and media to help solve crimes, has paused phone, website, and app submissions while it seeks a safer system.
The breach occurred in March and involved P3 Global Intel, the Texas-based tip-management platform owned by Navigate360. Its software is used by Crime Stoppers programs and other organizations in the US and elsewhere.
An October CBC investigation revealed the Canadian impact: More than 1.5 million tips spanning 25 years were exposed, with over 850,000 containing personal information. That included addresses, phone numbers, email addresses, and some banking details associated with rewards. The exposed details belonged to tipsters, people named in allegations, and others, including police and Crime Stoppers staff.
Following CBC’s reporting, Toronto Crime Stoppers acknowledged that its promise of anonymity had been broken for some users. The organization stopped accepting tips, saying it could no longer guarantee users’ anonymity.
In an October 21 statement, the organization says identifying details are normally removed before tips reach investigators, but some original submissions containing potentially identifying information were stolen from P3.
For affected tipsters, exposure could create a risk of retaliation, intimidation, or extortion. Scammers could also use details of a genuine tip to make an approach more convincing.
Unfortunately, the pause removes a reporting option for people afraid to approach police. Toronto police still accept reports directly, but warn that those channels are not anonymous.
How to stay safe
Toronto Crime Stoppers warned people worried about exposure to watch for impersonators. It says it will never contact them first to request a tip number, password, or other information.
The statement did not describe an individual notification process or offer a way to check whether a particular tip was affected. For anyone wanting to submit a new tip, the organization’s message was clear:
“Until we have a safer way to protect you, please do not send us tips by phone, online, or through the app.”
Anyone in immediate danger should call 911. During the pause, non-emergency reports in Toronto should go directly to Toronto police, with the understanding that those channels are not anonymous.
If you use a different Crime Stoppers program, check its official website for updates and advice about its reporting system.
A Cash App account opened in her name has left Amanda Smith facing criminal charges and potentially up to six years in prison.
404 Media reports that Smith says someone used her Social Security number (SSN) and date of birth to create an account that received money from a Facebook Marketplace scam.
Allegedly, a buyer sent $1,000 for items that weren’t really for sale. A scammer had taken over someone else’s Facebook account and directed the buyer to pay a Cash App account in Smith’s name.
Investigators obtained account information from Block, Cash App’s parent company. That information included Smith’s Social Security number and date of birth. Police subsequently arrested her in Pennsylvania over the alleged crime in Arkansas, a state she says she had never visited.
She spent three nights in jail. But 404 Media’s review of account records found that several account details, including the address and network used, did not match her own.
Smith also described a frustrating obstacle when she tried to investigate:
“Cash App refused to provide me with any information about the account, because I couldn’t prove that I was the owner.”
The account was associated with her closely enough to contribute to her arrest, yet she said she could not get information directly from the company. She later received account records through the criminal case.
It’s a disturbing reminder that the consequences of identity theft can go well beyond an unfamiliar charge on your bank statement. You could also find yourself accused of a crime committed using your details.
Breaches happen every day. Don’t be the last to know.
Smith suspects that information exposed in a data breach may have been used to impersonate her. When investigating, 404 Media found the phone number used for the account linked to an Amanda Smith in older breach data. They also found someone made a Venmo account using the same phone number but under another name entirely.
The source of her Social Security number and date of birth hasn’t been established, and her case is ongoing. Her experience highlights why it matters to know which of your details have been exposed.
How to protect yourself
The practical lesson is to look beyond the headline that a company “lost customer data.” What matters is which information was exposed, because different exposures call for different responses. Our guide for how to handle being involved in a data breach recommends checking the affected company’s official information before deciding what to do next.
The steps depend on the type of data that was stolen or leaked:
Email addresses and phone numbers: Be alert for phishing messages and scam calls, including messages that refer to the breach.
Passwords: Change the affected password and anywhere else you reused it. Enable multifactor authentication where available.
Payment or banking details: Contact the relevant financial institution and review your accounts for unauthorized activity.
Social Security numbers and other identifying information: Check your credit reports for unfamiliar accounts. In the US, you can freeze your credit for free with each of the three major credit bureaus: Equifax, Experian, and TransUnion. This helps prevent new credit accounts being opened in your name, but does not prevent every type of identity misuse.
If you discover an account opened in your name, contact the company’s fraud department through its official website and report the identity theft (in the US you can do that at IdentityTheft.gov). Keep copies of your reports and correspondence, and ask for written confirmation when the fraudulent account is closed.
A breach-checking service can help you identify known exposures linked to your information. Malwarebytes’ Digital Footprint Scan, for example, checks for exposures associated with your email address.
What do cybercriminals know about you?
Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.
“Arizona’s court system was targeted by a cyber attack from criminal hackers or their bots.”
This is how the Arizona Supreme Court announced that hackers had attacked the state’s court system and stolen the personal information of “many Arizonans.”
The court says the attack began with a phishing email containing a malicious link that a court employee clicked. The attackers copied sensitive backup files containing records related to protective orders and foster care cases.
The court says it has no evidence, so far, that information about jurors, witnesses, or court employees was included in the copied files. It has not identified the attackers or a motive. It says the case is under investigation with the FBI, and no ransomware group has publicly claimed responsibility.
In an update, the court revealed that the attackers copied more than 150,000 recommendation reports created by Arizona’s Foster Care Review Board. The reports cover current and past cases involving children’s care and protection, dating back to 2010.
Those documents can include information about children, names of involved parties, case materials considered by the board, findings, and recommendations for courts, parents, and the Arizona Department of Child Safety. The court says the reports do not contain contact information such as addresses or telephone numbers.
The copied files were backups stored in a highly compressed format, kept for recovery after ransomware and other destructive incidents.
Information associated with protective orders can raise particularly serious safety and privacy concerns. These orders can protect people from abuse, harassment, or threats. Even where some records are public, combining names, case details, locations, and other sensitive context could create risks for people who are trying to limit their exposure to an abusive or threatening individual.
Breaches happen every day. Don’t be the last to know.
The court currently says it has no evidence that the information has been shared. As with many breach investigations, however, this can change as investigators determine exactly what was taken and monitor for publication, sale, or misuse of the data.
Arizona has about 8,000 children currently in foster care, according to the court. It is contacting people believed to have been affected.
What to do if you’re affected
Check the court’s advice. Every breach is different, so check its dedicated webpage for updates and follow any specific advice it offers.
Watch out for impersonators. Cybercriminals may contact you posing as the Arizona Supreme Court, another government agency, or someone you know. Verify anyone who contacts you through a separate, trusted channel.
Take your time. Phishing attacks often impersonate people or brands you know and pressure you to act urgently, using themes such as missed deliveries, account suspensions, and security alerts.
Get an early warning if your information appears on the dark web. If you’ve been notified that your information was copied in the Arizona court breach, identity monitoring can help you watch for signs of exposure and get support if you become a victim of identity theft.
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
BBC News reports it has seen samples of stolen FBI agents’ medical examinations. The “fitness-for-work” reports identify FBI agents by name and address, and reveal even more personal details. They include blood and urine test results and doctors’ notes mentioning high cholesterol, blood in the urine, and even a shellfish and banana allergy.
As we reported last week, extortion group ShinyHunters claims to have breached the FBI. After reportedly taking over ransomware group Clop’s leak site, ShinyHunters says it attacked the FBI to punish the agency for spreading what it calls false information about the group.
The BBC’s findings raise the stakes: The alleged theft includes highly sensitive medical records, not just staff identity and contact data. ShinyHunters shared samples with journalists as proof of its claims.
The BBC states:
“The samples shared with journalists appear genuine and include names, addresses, phone numbers, badge numbers, job titles and information about spouses.”
ShinyHunters claims it accessed several systems, including FBI MedLink, which stores medical records, and FBI BEAST, which handles background checks on employees and applicants, but the FBI has not confirmed these claims. The FBI has acknowledged an incident affecting FBIJobs-related systems and says it is investigating whether its own environment or a third-party provider was compromised.
The group’s stated demand remains non-financial: It wants the FBI to retract or remove a May advisory that ShinyHunters calls false and defamatory. It says it will release the data within five days if its demands are not met.
The cybercriminals also raised the number of affected people. ShinyHunters nows claims to hold sensitive information on around 60,000 current and former FBI staff. Medical histories could make affected people vulnerable long after the immediate incident: Unlike a stolen password, a medical record cannot be changed.
What to do if you’re affected
The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:
Check the FBI’s advice. Every breach is different, so check FBI.gov for updates and follow any specific advice it offers.
Change your password. If you have an FBI Jobs account and reuse its password elsewhere, change it on those other accounts. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
Watch out for impersonators. Cybercriminals may contact you posing as the FBI, another government agency, or someone you know. Verify the identity of anyone who contacts you.
Take your time. Phishing attacks often impersonate people or brands you know and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
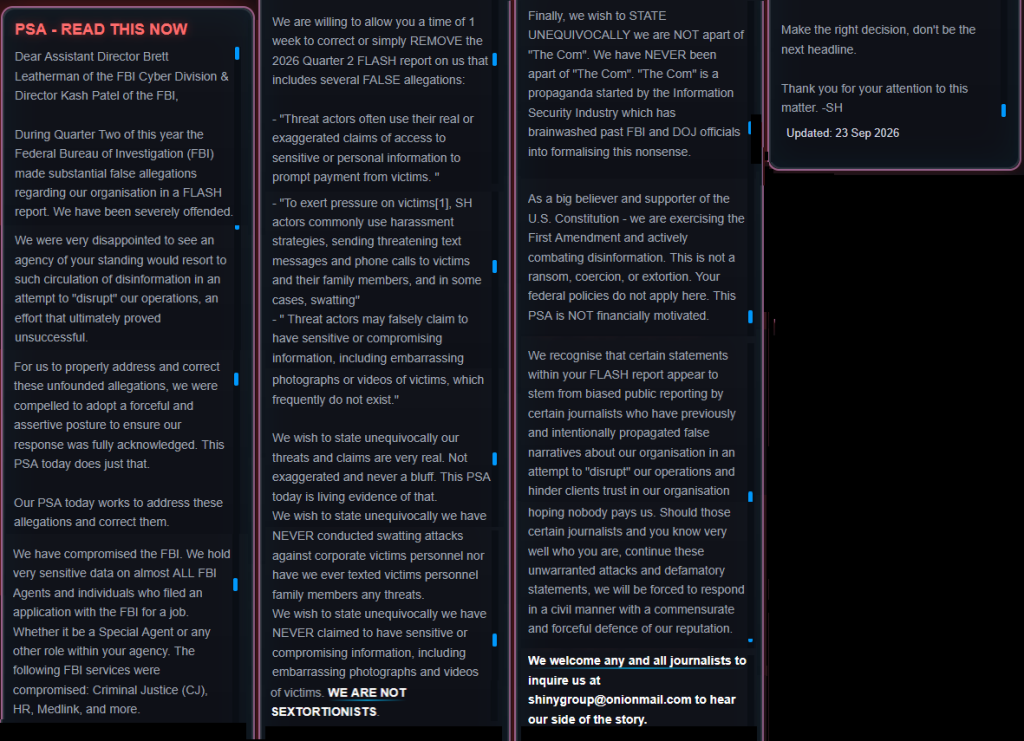
In a very long post on its leak site, the group outlines its grievances:
“PSA – READ THIS NOW
Dear Assistant Director Brett Leatherman of the FBI Cyber Division & Director Kash Patel of the FBI,
During Quarter Two of this year the Federal Bureau of Investigation (FBI) made substantial false allegations regarding our organisation in a FLASH report. We have been severely offended.
We were very disappointed to see an agency of your standing would resort to such circulation of disinformation in an attempt to “disrupt” our operations, an effort that ultimately proved unsuccessful.
For us to properly address and correct these unfounded allegations, we were compelled to adopt a forceful and assertive posture to ensure our response was fully acknowledged. This PSA today does just that.
Our PSA today works to address these allegations and correct them.
We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job. Whether it be a Special Agent or any other role within your agency. The following FBI services were compromised: Criminal Justice (CJ), HR, Medlink, and more.
We are willing to allow you a time of 1 week to correct or simply REMOVE the 2026 Quarter 2 FLASH report on us that includes several FALSE allegations:
“Threat actors often use their real or exaggerated claims of access to sensitive or personal information to prompt payment from victims.”
“To exert pressure on victims[1], SH actors commonly use harassment strategies, sending threatening text messages and phone calls to victims and their family members, and in some cases, swatting”
“Threat actors may falsely claim to have sensitive or compromising information, including embarrassing photographs or videos of victims, which frequently do not exist.”
We wish to state unequivocally our threats and claims are very real. Not exaggerated and never a bluff. This PSA today is living evidence of that.
We wish to state unequivocally we have NEVER conducted swatting attacks against corporate victims personnel nor have we ever texted victims personnel family members any threats.
We wish to state unequivocally we have NEVER claimed to have sensitive or compromising information, including embarrassing photographs and videos of victims. WE ARE NOT SEXTORTIONISTS.
Finally, we wish to STATE UNEQUIVOCALLY we are NOT apart of “The Com”. We have NEVER been apart of “The Com”. “The Com” is a propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalising this nonsense.
As a big believer and supporter of the U.S. Constitution – we are exercising the First Amendment and actively combating disinformation. This is not a ransom, coercion, or extortion. Your federal policies do not apply here. This PSA is NOT financially motivated.
We recognise that certain statements within your FLASH report appear to stem from biased public reporting by certain journalists who have previously and intentionally propagated false narratives about our organisation in an attempt to “disrupt” our operations and hinder clients trust in our organisation hoping nobody pays us. Should those certain journalists and you know very well who you are, continue these unwarranted attacks and defamatory statements, we will be forced to respond in a civil manner with a commensurate and forceful defence of our reputation.
We welcome any and all journalists to inquire us at shinygroup@onionmail[.]com to hear our side of the story.
Make the right decision, don’t be the next headline.
Thank you for your attention to this matter. -SH
Updated: 23 Sep 2026“
The post is essentially a hostile “correction notice” directed at FBI leaders Brett Leatherman and Kash Patel. Its central grievance is an FBI advisory that says ShinyHunters commonly harasses victims and their families, including through threatening messages, phone calls, and, in some cases, swatting.
It also warns that threat actors may exaggerate their access to personal information or falsely claim to possess compromising photos or videos. The advisory does not use the word “sextortion,” but ShinyHunters appears to have interpreted the reference to compromising material that way. The group denies much of the FBI’s account while simultaneously using coercive language of its own.
The document it appears to mean is the FBI/IC3 public advisory “ShinyHunters: Cyber Criminal Group Attacks Learning Management System,” issued on May 15, 2026. Despite ShinyHunters calling it a “2026 Quarter 2 FLASH report,” the publicly accessible document is labeled a Public Service Announcement (PSA), not a FLASH.
It also denies carrying out swatting attacks or sending threatening messages to the family members of people working for its corporate victims.
The group also denies being part of The Com, a decentralized network linked to cybercrime and violence. It calls that connection:
“propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalizing this nonsense.”
The group then threatens journalists it accuses of spreading these “false narratives.”
The most worrying part of the message is the group’s claim that it stole sensitive data on:
“almost ALL FBI Agents, and individuals who filed an application with the FBI for a job.”
According to 404 Media, ShinyHunters provided a sample containing information on roughly 5,000 FBI agents, including names, home addresses, phone numbers, and details about their spouses. The publication reportedly verified portions of the sample, but the full dataset and the wider claims about the breach have not been independently confirmed.
The group also reportedly defaced the FBI’s jobs website. The FBI says it is aware of claims involving unauthorized activity affecting FBIjobs.gov and is investigating, although “broken” does not necessarily mean “breached.”
What to do if you’re affected
The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:
Check the FBI’s advice. Every breach is different, so check FBI.gov for updates and follow any specific advice it offers.
Change your password. If you have an FBI Jobs account and reuse its password elsewhere, change it on those other accounts. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
Watch out for impersonators. Cybercriminals may contact you posing as the FBI, another government agency, or someone you know. Verify the identity of anyone who contacts you.
Take your time. Phishing attacks often impersonate people or brands you know and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
Revolut has acknowledged that it disclosed sensitive customer records to an unauthorized party. The company had accepted fraudulent information requests sent from an email address on a legitimate government agency domain, according to TechCrunch.
Revolut is a London-based banking and financial platform with more than 80 million customers globally, according to the company.
Revolut describes this as an external impersonation scam, not an intrusion into its systems. It also says customer funds were not affected. Revolut has not identified the government agency or disclosed its email domain.
The attacker appears to have abused the trust attached to a real government email domain to make bogus requests for customer information. Revolut detected the activity, blocked the sending address, and says it notified the relevant agency, law enforcement, data protection authorities, and financial regulators.
“Upon detection, we immediately blocked the address and alerted the relevant government agency as well as enforcement agencies, data protection, and financial regulators.”
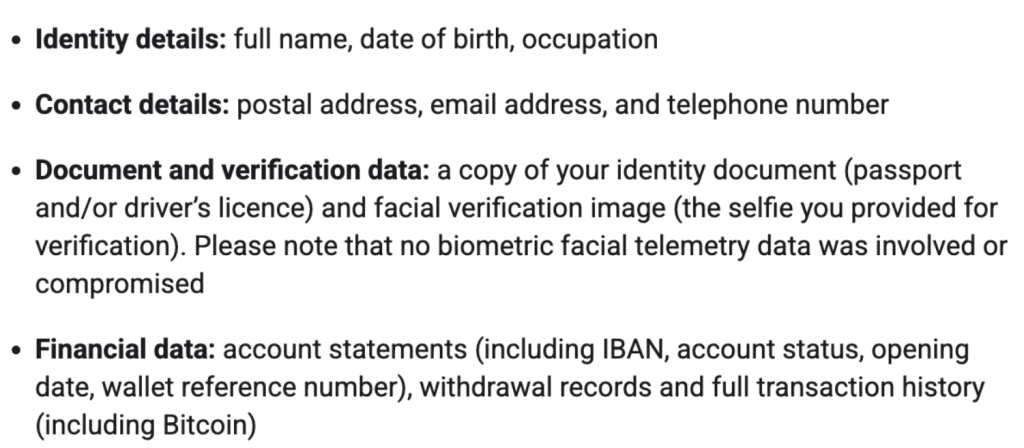
Through this social engineering attack, rather than by gaining access to Revolut’s systems, the criminals obtained the following types of information about customers:
Identity and contact information like dates of birth, postal address, email address, and phone number.
Copies of IDs such as passports and driver’s licenses.
Verification selfies.
Account statements and transaction histories.
Revolut has said only that a “limited” or “very limited” number of customers were affected, and that it contacted them directly.
Those customers have received or will receive an email specifying which of their personal data was disclosed:
How to stay safe
The likely consumer impact will be second-stage fraud attempts rather than immediate unauthorized transfers. Here are some guidelines to help keep your money safe:
Treat any unexpected Revolut-related contact as suspicious, especially calls, emails, WhatsApp messages, or text messages claiming you need to “secure” an account, reverse a transfer, or replace documents. Do not use links or phone numbers supplied in the message. Revolut advises ending contact with suspected scammers and contacting the company through official channels.
IDs and other exposed information could be used for identity theft. Monitor your accounts and credit reports for unfamiliar account openings or credit applications, and consider placing a fraud alert or using credit monitoring where available in your country.
If you received a notification email, check your balances, cards, beneficiaries, recent transfers, account statements, and linked devices. Report any unfamiliar activity immediately through Revolut’s secure in-app chat.
Pro tip: Use Malwarebytes Scam Guard to analyze any suspicious communications. It can help you determine whether a message is a scam and advise you on what to do next.
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.

 Login